Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
DotSecutiry - Counter Spells and the Art of Kee...
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
ingrid epure
April 21, 2017
Programming
740
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
DotSecutiry - Counter Spells and the Art of Keeping your Application Safe
dotSecurity Paris 2017
ingrid epure
April 21, 2017
More Decks by ingrid epure
See All by ingrid epure
Counter spells and the art of keeping you application safe
ingride
0
680
Making good testing decisions
ingride
0
140
Other Decks in Programming
See All in Programming
海上で動くGoサーバー: goroutineとchannelでさばく航行データストリーム
atsuki_seo
0
980
UPDATE をやめる — EF Core でマスタをバージョン管理する
panda728
PRO
0
940
Everything will be SERVERLESS — 信じて運用した10年の経験値 / Everything Will be Serverless — Lessons Learned from 10 Years of Operational Experience
seike460
PRO
1
560
そのリトライ、死んだコネクションを使い回していませんか ── GoのHTTPクライアントとHTTP/2を実プロダクト障害から学び直す
myus4a
0
320
カツオ、ご期待ください
suneo3476
0
110
App Intentsのビルドプロセスを支える技術
kntkymt
0
470
Verilogで学ぶCPU自作入門.pdf
uyuki234
8
3.7k
App Storeの外へ──日本のiOSサイドローディング入門 for iOSDC Japan 2026
yuukiw00w
0
270
すこし踏み込む CancellationToken
htkym
2
1.4k
テストを司るデーモンに会いに行く 〜隔離した仮想マシンでテストを通すまで〜
h1d3mun3
1
590
re:Inventに行く前に知っておきたい現地参加のノウハウ
nokomoro3
0
240
Streamlitで実現する自然言語データアプリ開発
ayumu_yamaguchi
1
320
Featured
See All Featured
SEO Brein meetup: CTRL+C is not how to scale international SEO
lindahogenes
2
2.9k
GraphQLとの向き合い方2022年版
quramy
50
15k
Templates, Plugins, & Blocks: Oh My! Creating the theme that thinks of everything
marktimemedia
31
2.9k
Principles of Awesome APIs and How to Build Them.
keavy
128
18k
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
1
340
Keith and Marios Guide to Fast Websites
keithpitt
413
23k
Why Your Marketing Sucks and What You Can Do About It - Sophie Logan
marketingsoph
0
410
Testing 201, or: Great Expectations
jmmastey
46
8.3k
Design of three-dimensional binary manipulators for pick-and-place task avoiding obstacles (IECON2024)
konakalab
0
600
Winning Ecommerce Organic Search in an AI Era - #searchnstuff2025
aleyda
2
2.2k
Agile that works and the tools we love
rasmusluckow
331
22k
The Myth of the Modular Monolith - Day 2 Keynote - Rails World 2024
eileencodes
28
3.7k
Transcript
counter-spells KEEPING YOUR APPLICATION SAFE and the art of
IN WHICH I REALLY WISH I DON’T DIE
None
story time
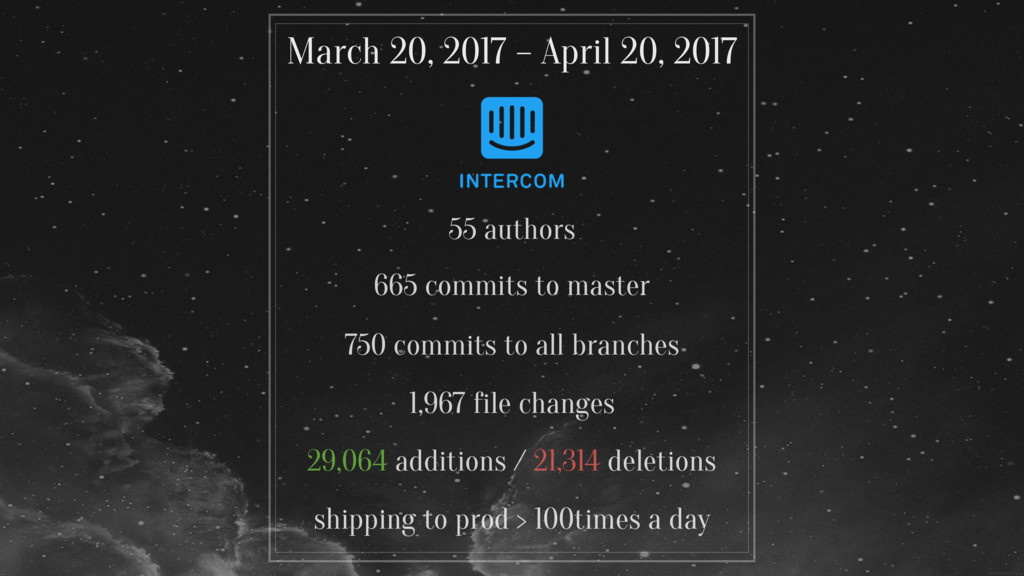
55 authors 665 commits to master 750 commits to all
branches March 20, 2017 – April 20, 2017 1,967 file changes 29,064 additions / 21,314 deletions shipping to prod > 100times a day
real-time editor that allows HTML input data sanitization is required
⚡
None
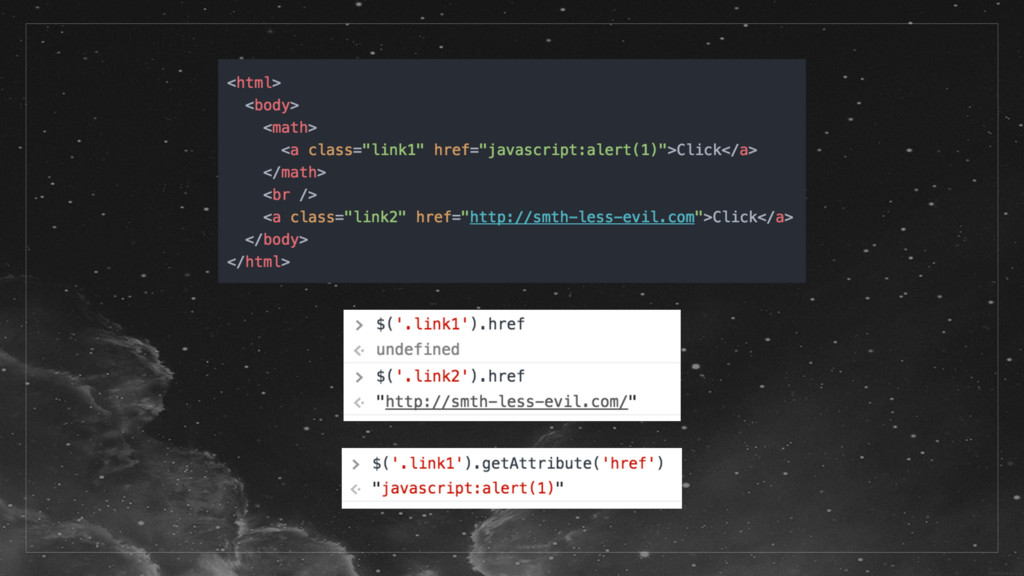
[ browsers are wonderful and weird ] ( really really
weird )
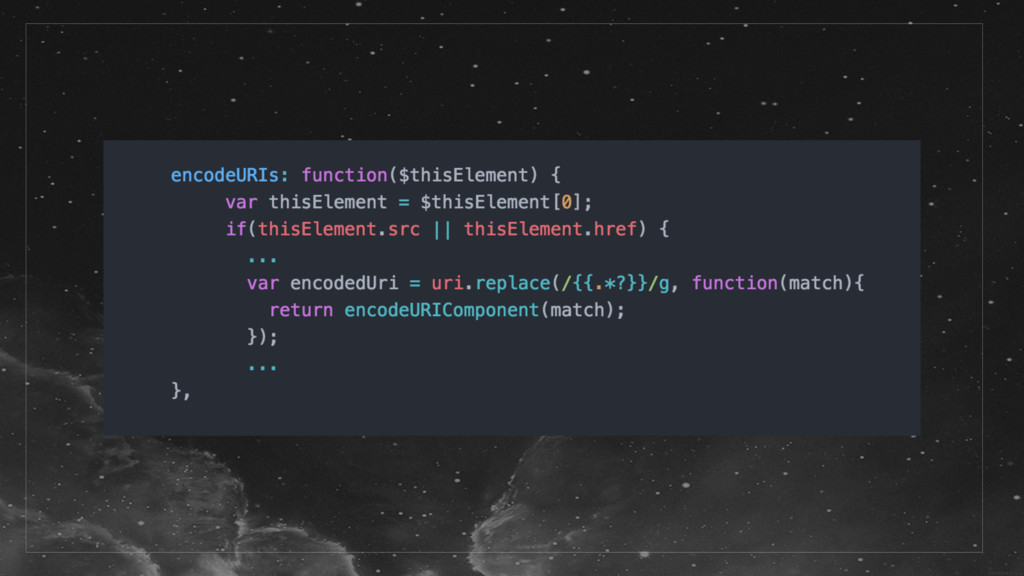
[ .href can sometimes be undefined even if present ]
None
None
[ know your enemy. ] ( and that might not
always be just users )
prepare for battle [ prepare your spells. ]
[ code that deals with weirdness better ] [ detect
& alert on weirdness ]
HTML templates JavaScript controllers components
Html Escaping Hypertextescaptus (hyper-text-ESC-aptus ) web framework’s rendering layer escape
HTML H Use for protection against XSS
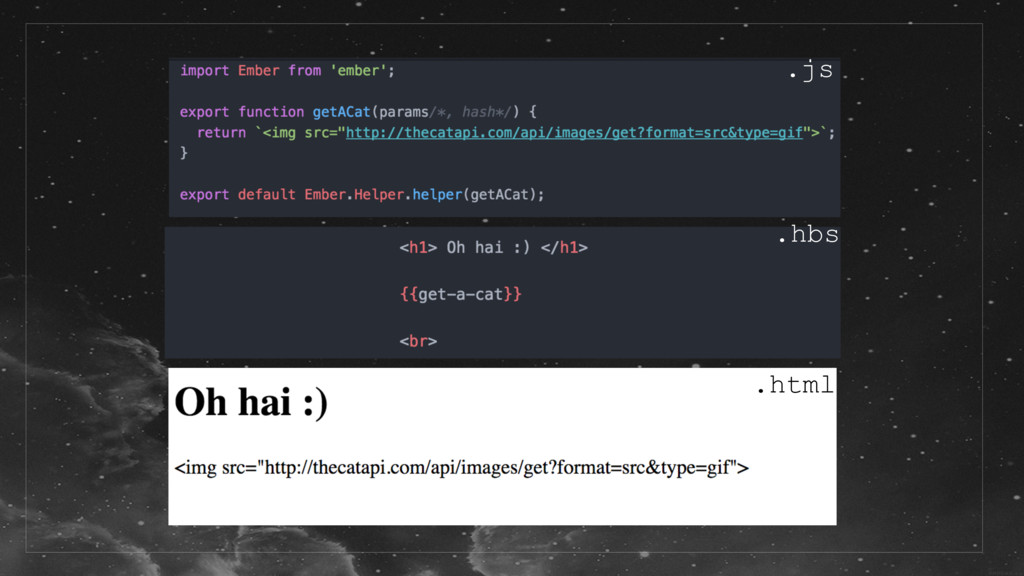
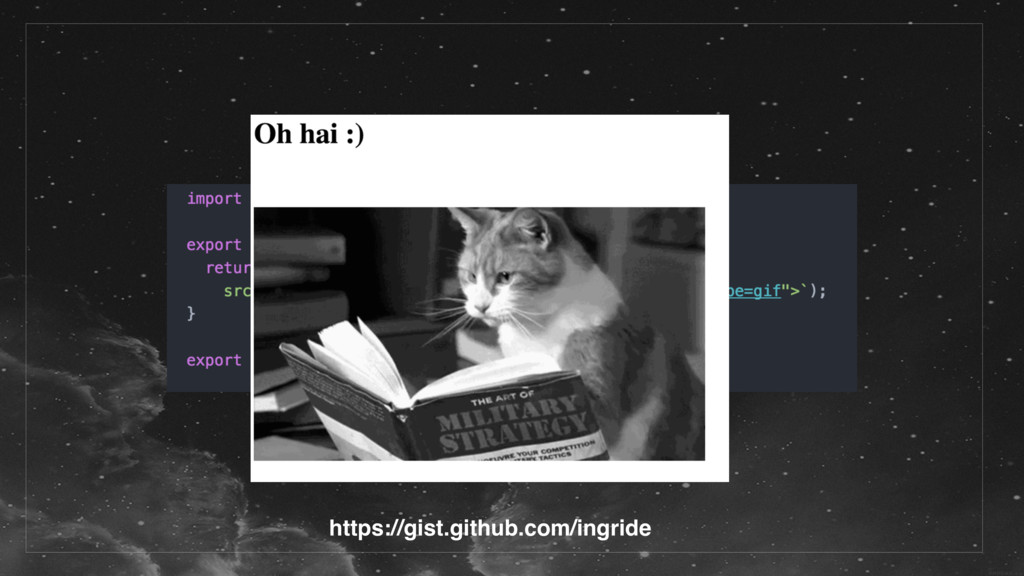
.js .hbs .html
https://gist.github.com/ingride
[ avoid having to decide if html is safe ]
dangerouslySetInnerHTML - React htmlSafe in Ember trustAsHtml - Angular
Good Components BonumPars (bonum-pars) GC make component arguments not be
de-facto public API smaller components
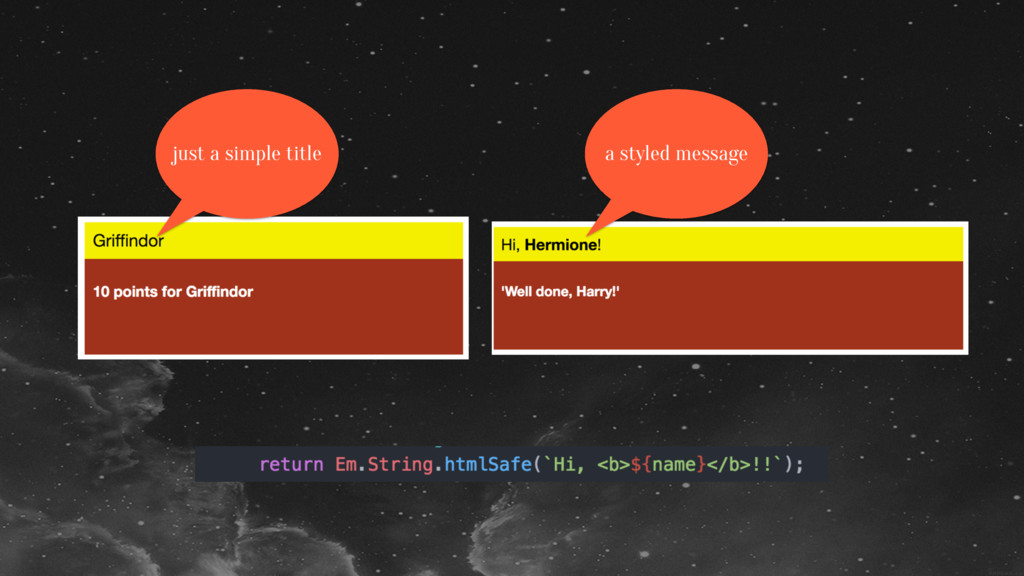
just a simple title a styled message
] - title component ] - body component super-card-component
each component decides on implementation while invocation remains the same
composition instead of inheritance better encapsulation and clarity
https://embermap.com/topics/contextual- components/flexible-interfaces https://facebook.github.io/react/docs/composition-vs- inheritance.html
Good Helpers BonumAuxilium (bonum-auxilium) GH prefer updating the DOM over
returning HTML
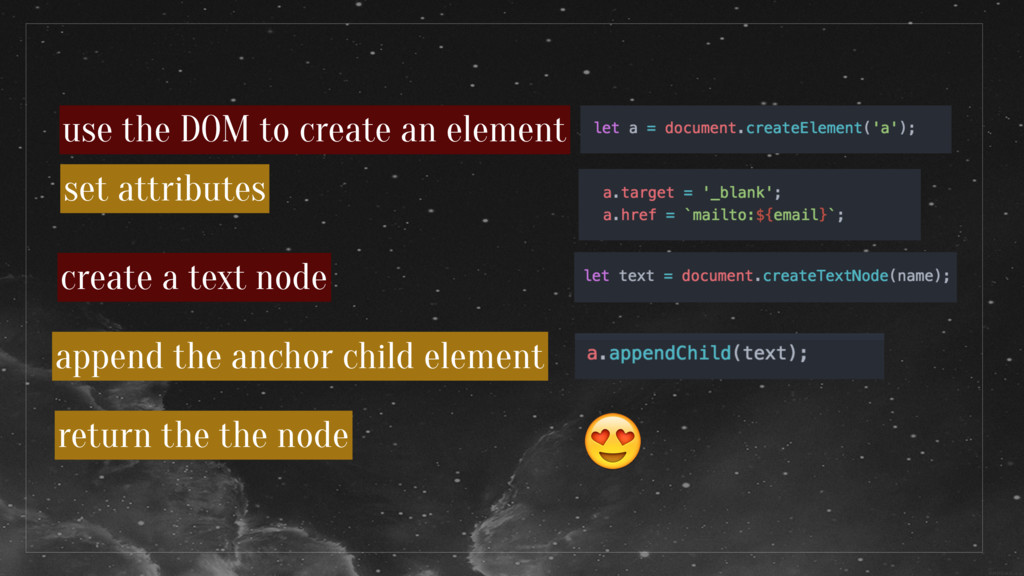
create a text node set attributes append the anchor child
element return the the node use the DOM to create an element
Avoid Triple Curlies TripliciCrispusExpellus (Tri-pli-ci-crispus ) using on direct user
input can introduce vulnerabilities {{{ {{{ = htmlSafe() for templates
good helpers + good components = ♥
Thou Shall Noopen NoopenerNoreferrerExpellus (apertus-tour-expellus) N always use noopener AND
noreferrer with target=‘_blank’
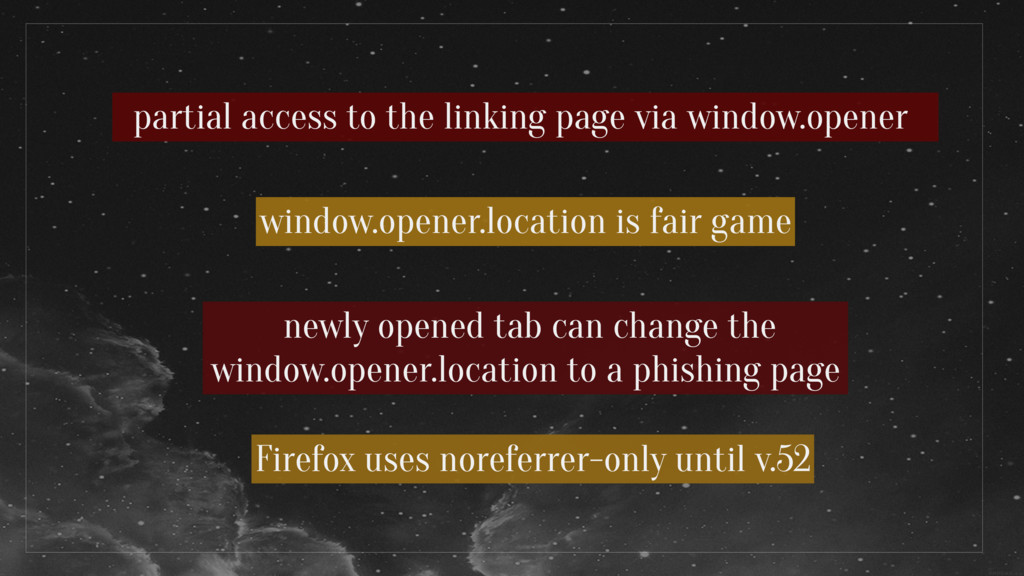
newly opened tab can change the window.opener.location to a phishing
page window.opener.location is fair game Firefox uses noreferrer-only until v.52 partial access to the linking page via window.opener
static analysers regexp are evil watermarks are ♥ Detect &
Alert esLint & template linters
use the abstract syntax tree ( AST ) for Mustache:
MustacheStatement target= ‘_blank’ / elements : ElementNode & node attributes plug it in with your cli
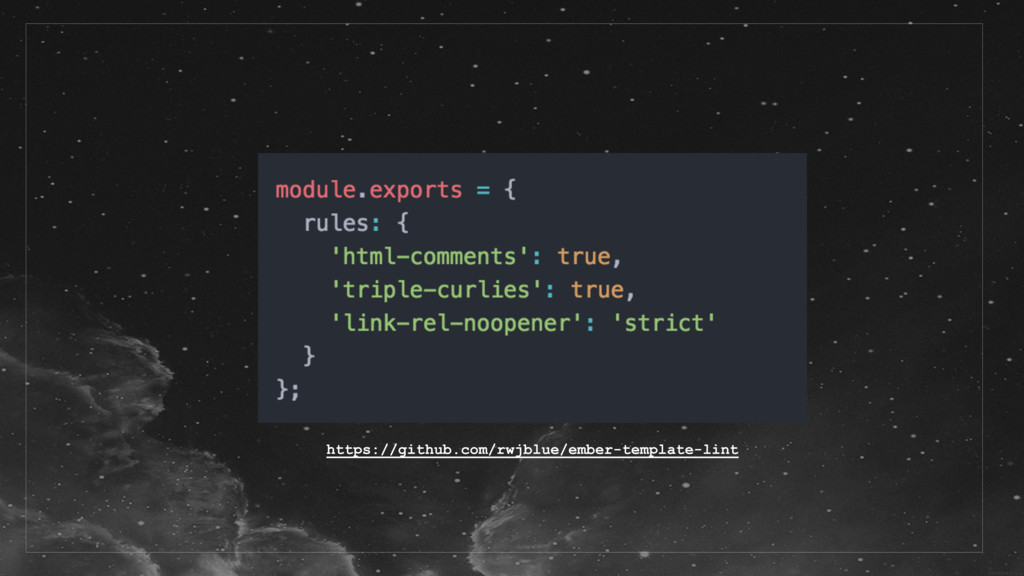
https://github.com/rwjblue/ember-template-lint
story time
[ before esLint there was… grep]
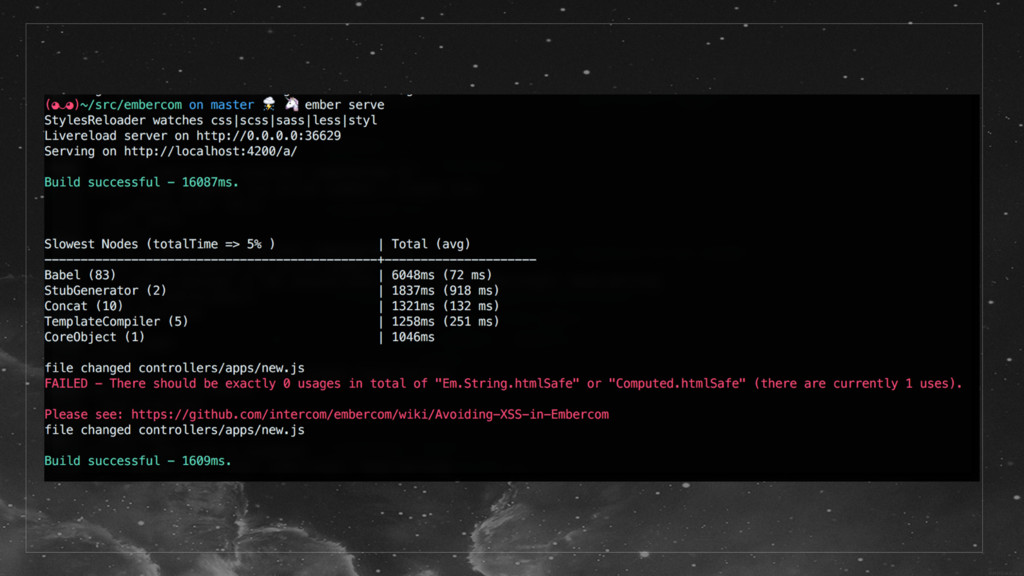
postBuild hook to get real-time feedback find + grep +
regexp + wc to get the count compare the count against a static limit fail the build if numbers don’t match
[ regexp are like black magic. They're powerful & get
the job done, but you also fear them and might have to sell your soul in the process ] [ regexp rage by ingride ]
EsLint BonumLintum (bonum-LINT-um) EL Introduce a line in the sand
for blacklisted methods Use linters for real-time feedback in dev
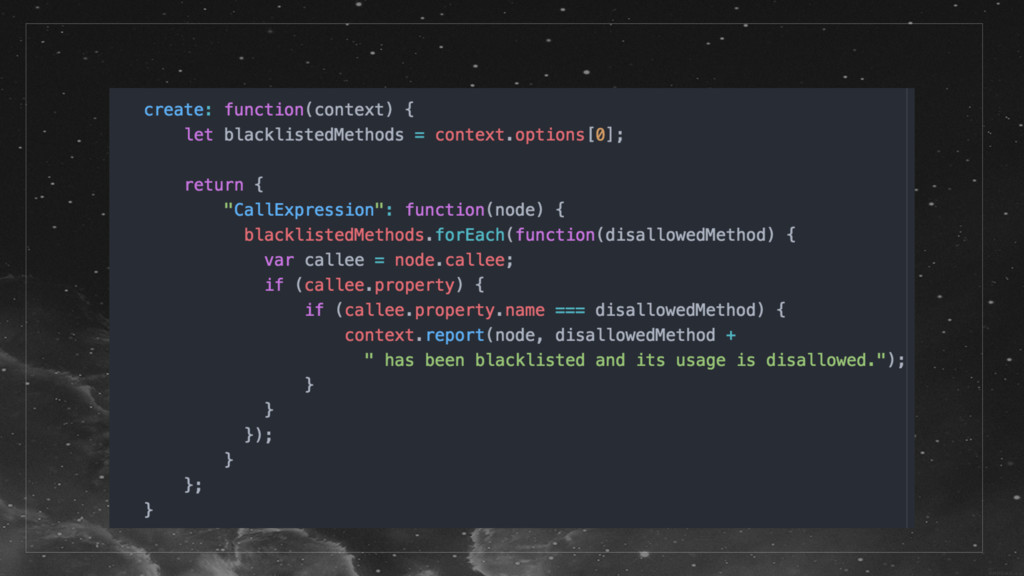
esLint plugin with a custom rule that checks for blacklisted
methods
None
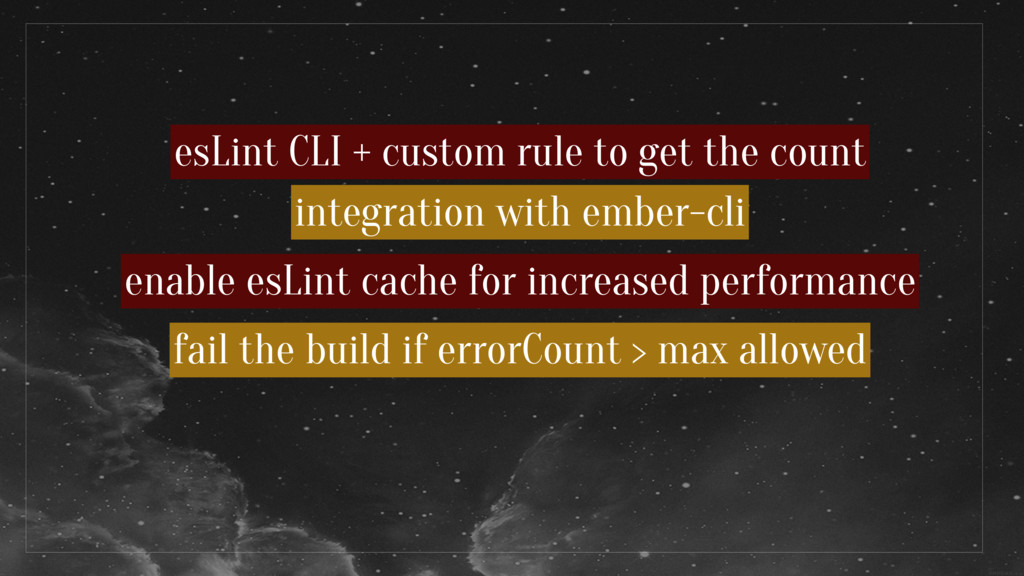
esLint CLI + custom rule to get the count fail
the build if errorCount > max allowed enable esLint cache for increased performance integration with ember-cli
None
from ♥ with [ blacklist methods addon coming soon ]
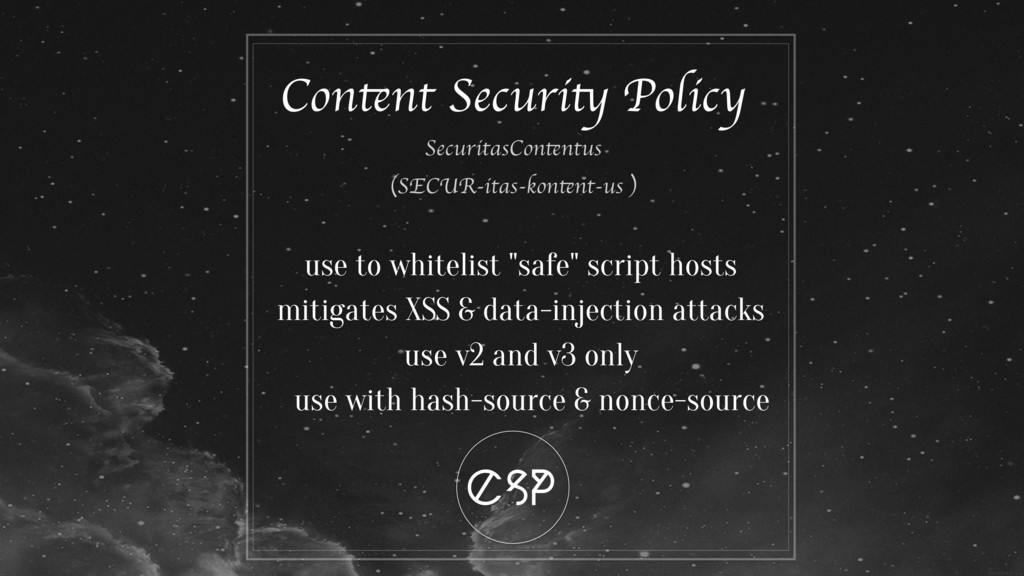
Content Security Policy SecuritasContentus (SECUR-itas-kontent-us ) mitigates XSS & data-injection
attacks CSP use to whitelist "safe" script hosts use v2 and v3 only use with hash-source & nonce-source
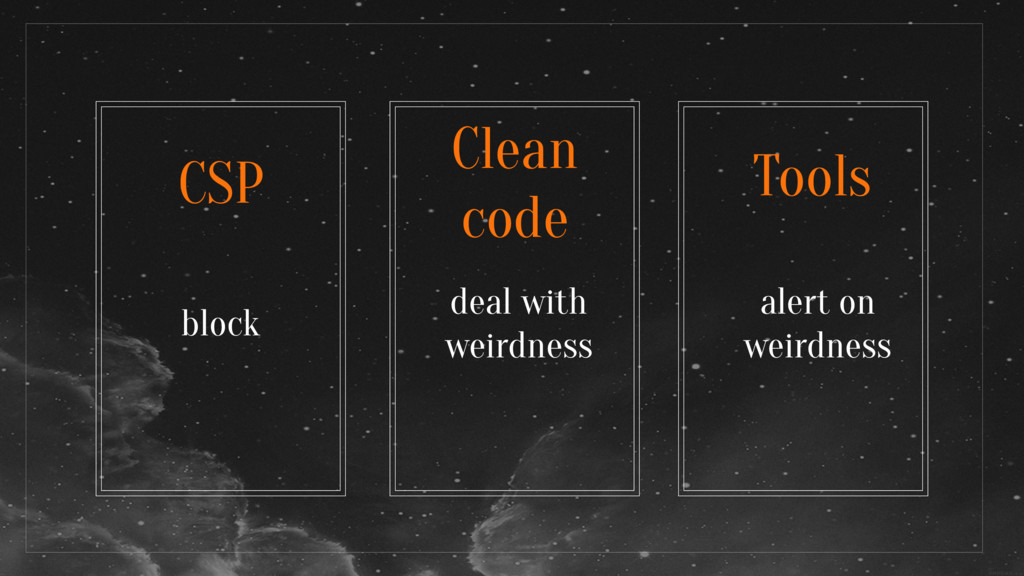
CSP Clean code Tools block deal with weirdness alert on
weirdness
[ thank you. ] @ingridepure @ingride

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 ingride
 atsuki_seo
 panda728
 seike460
 myus4a
 suneo3476
 kntkymt
 uyuki234
 yuukiw00w
 htkym
 h1d3mun3
 nokomoro3
 ayumu_yamaguchi
 lindahogenes
 quramy
 marktimemedia
 keavy
 helenjbeal
 keithpitt
 marketingsoph
 jmmastey
 konakalab
 aleyda
 rasmusluckow
 eileencodes





![] - title component ] - body component super-card-component](https://files.speakerdeck.com/presentations/d439668dea3142159168b1d2132f9141/slide_21.jpg)