Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
A history on security and how to win the battle
Search
Joshua Thijssen
August 26, 2012
110
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
A history on security and how to win the battle
Joshua Thijssen
August 26, 2012
More Decks by Joshua Thijssen
See All by Joshua Thijssen
RAFT: A story on how clusters of computers keep your data in sync
jaytaph
0
85
The first few milliseconds of HTTPS
jaytaph
0
310
Paradoxes and theorems every developer should know
jaytaph
0
370
Paradoxes and theorems every developer should know
jaytaph
0
810
The first few milliseconds of HTTPS - PHPNW16
jaytaph
1
310
compiler_-_php010.pdf
jaytaph
0
170
Paradoxes and theorems every developer should know
jaytaph
0
310
Introduction into interpreters, compilers and JIT
jaytaph
1
390
Paradoxes and theorems every developer should know
jaytaph
1
1k
Featured
See All Featured
Leo the Paperboy
mayatellez
9
2.3k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Facilitating Awesome Meetings
lara
57
7.1k
The Invisible Side of Design
smashingmag
301
52k
B2B Lead Gen: Tactics, Traps & Triumph
marketingsoph
0
240
Darren the Foodie - Storyboard
khoart
PRO
3
3.9k
Visualization
eitanlees
152
17k
For a Future-Friendly Web
brad_frost
183
10k
Side Projects
sachag
456
43k
Unlocking the hidden potential of vector embeddings in international SEO
frankvandijk
0
930
Building the Perfect Custom Keyboard
takai
2
870
Digital Projects Gone Horribly Wrong (And the UX Pros Who Still Save the Day) - Dean Schuster
uxyall
1
2.9k
Transcript
A history on security and how to win the battle...
Joshua Thijssen
Channeling and restricting flow
Sometimes channels don’t listen
Fighting against ourselves
Security is a business value
Let others take care of security
History of (computer) security
Security in the “old days”
I wasn’t kidding when I said: “old days”
5.25” high density disks
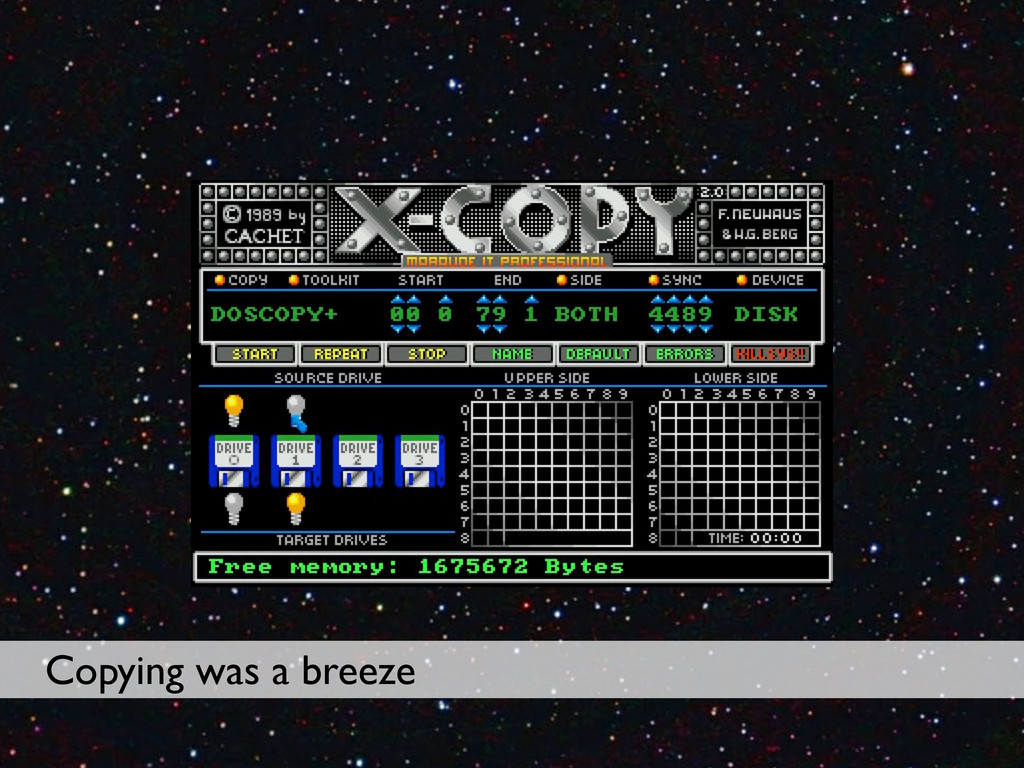
Copying was a breeze
Copy protection
Copy protection
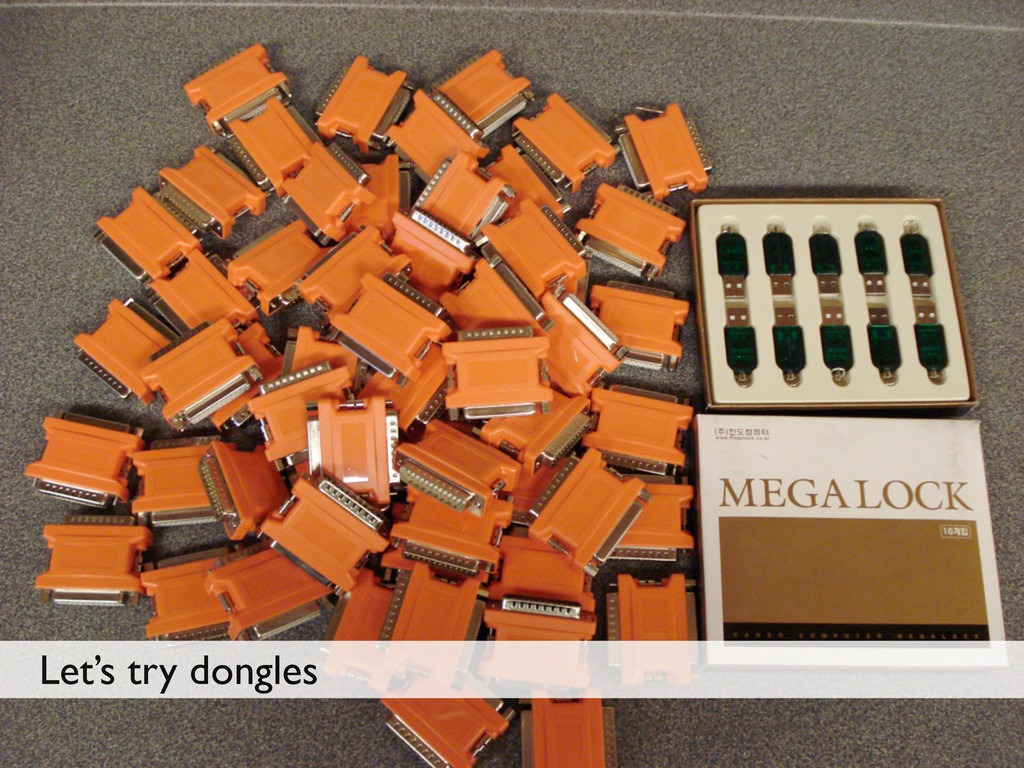
Let’s try dongles
NOPE!
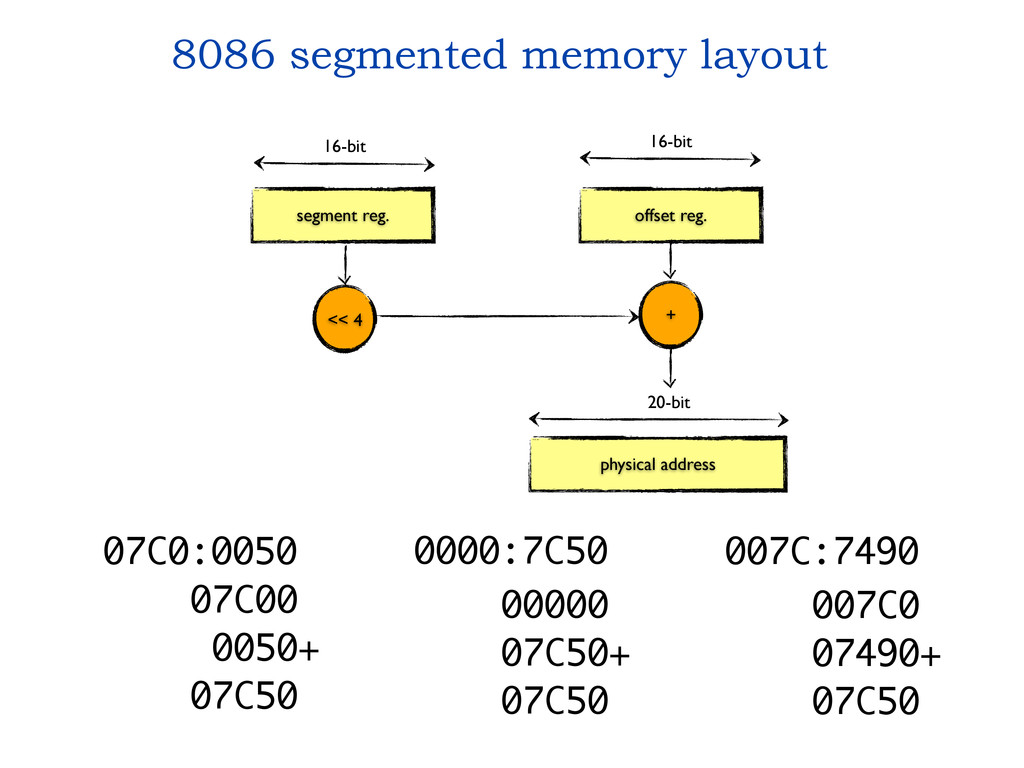
07C0:0050 07C00 0050+ 07C50 0000:7C50 00000 07C50+ 07C50 007C:7490 007C0
07490+ 07C50 8086 segmented memory layout segment reg. offset reg. << 4 + physical address 16-bit 16-bit 20-bit
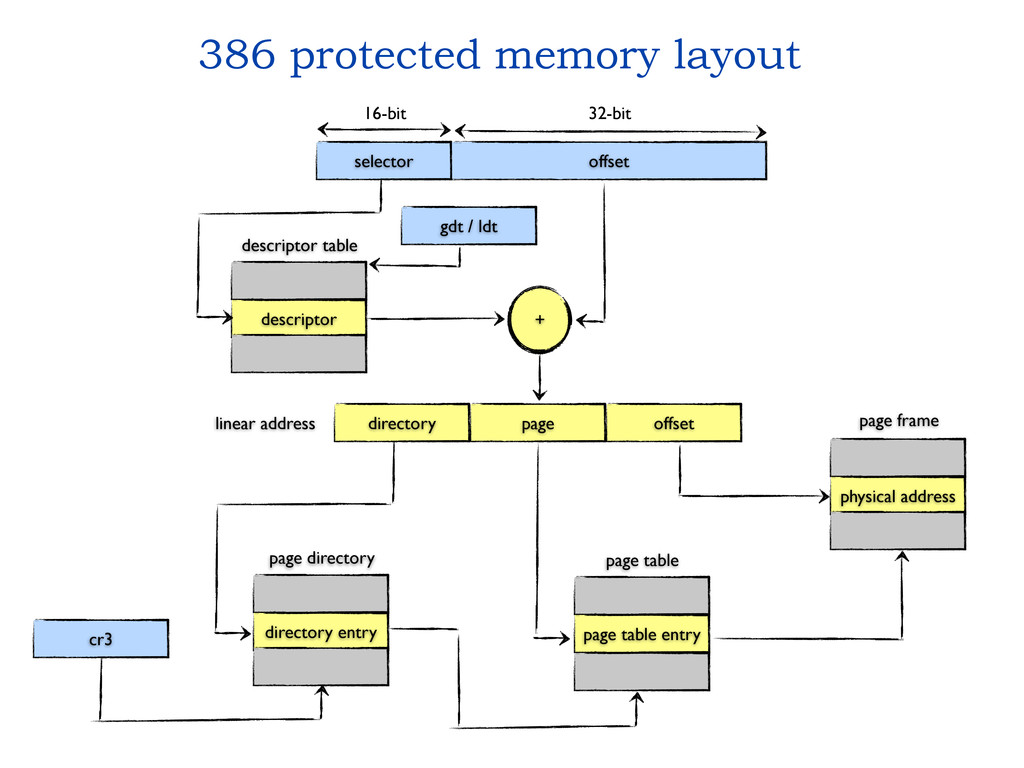
386 protected memory layout + descriptor directory entry page table
entry physical address directory page offset cr3 gdt / ldt page directory page table page frame linear address descriptor table selector offset 32-bit 16-bit
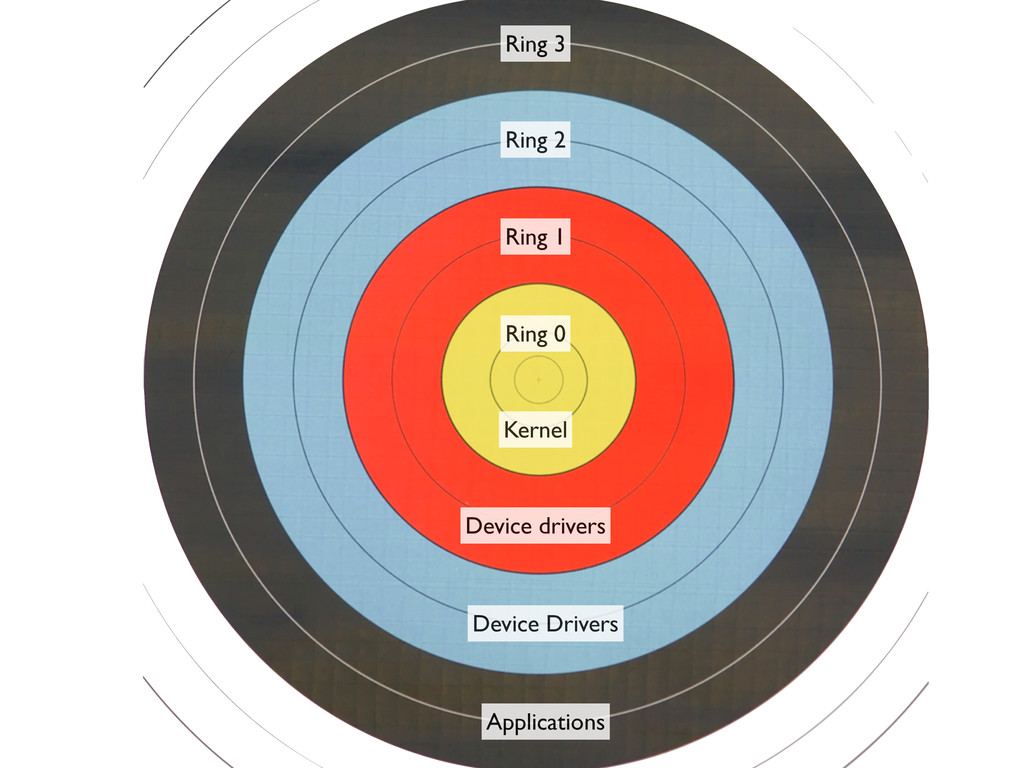
Ring 0 Kernel Ring 1 Device drivers Ring 2 Device
Drivers Ring 3 Applications
Security today
The weakest link
Humans
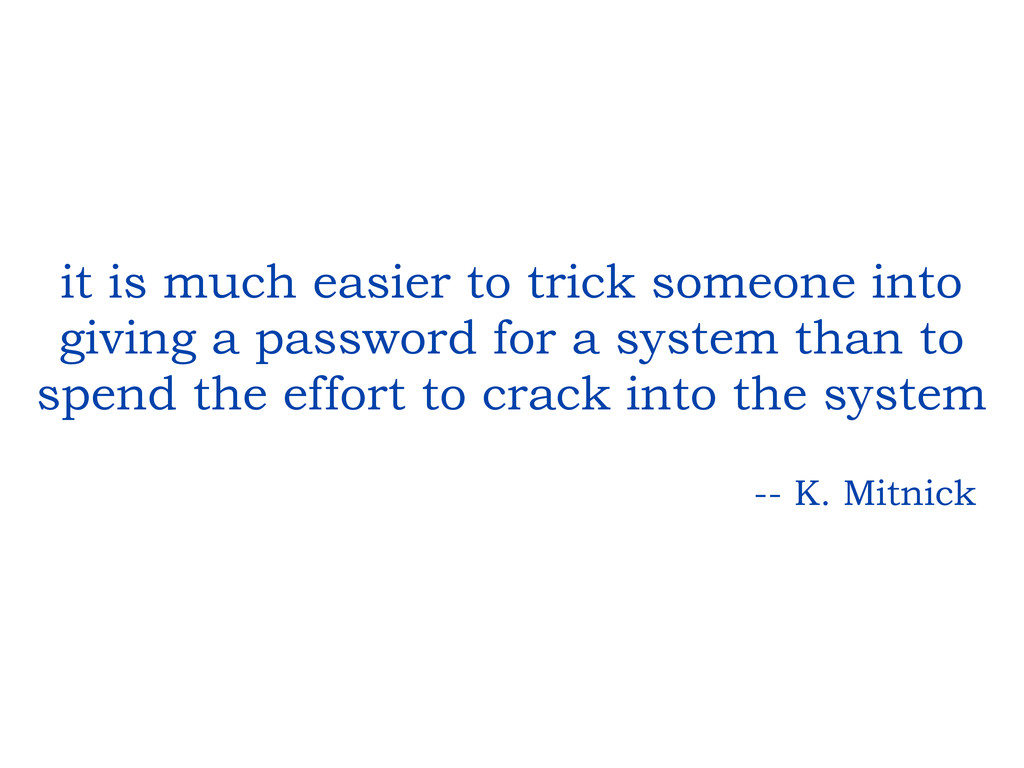
it is much easier to trick someone into giving a
password for a system than to spend the effort to crack into the system -- K. Mitnick
Raising awareness on browsers and users
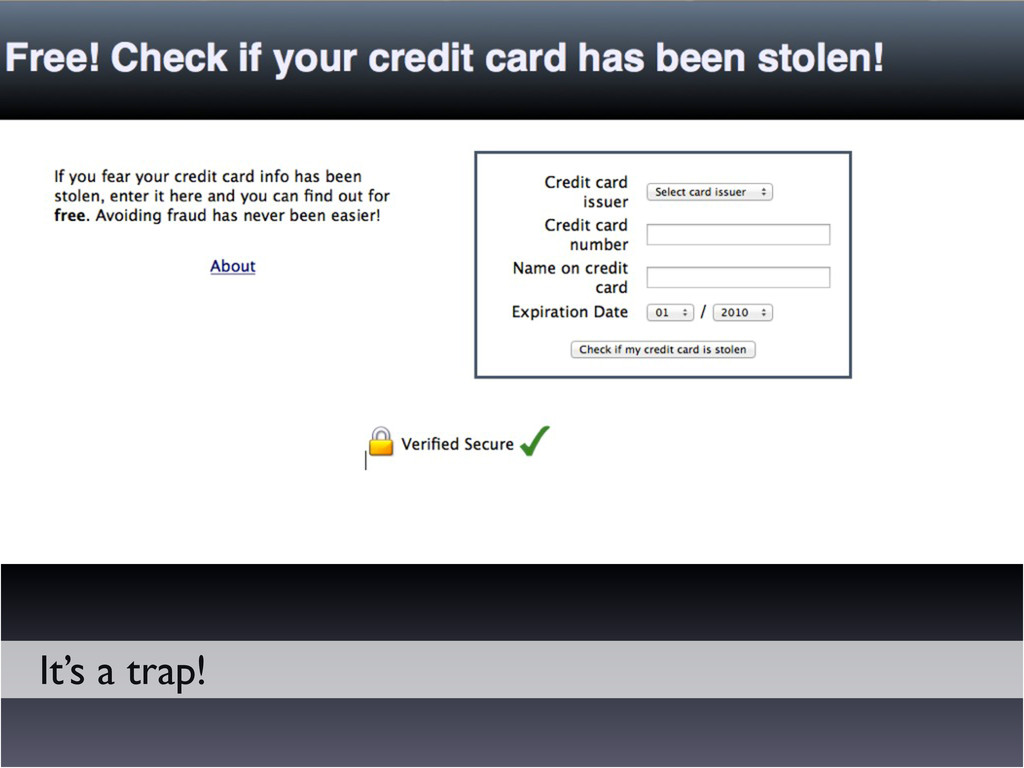
It’s a trap!
We’re curious
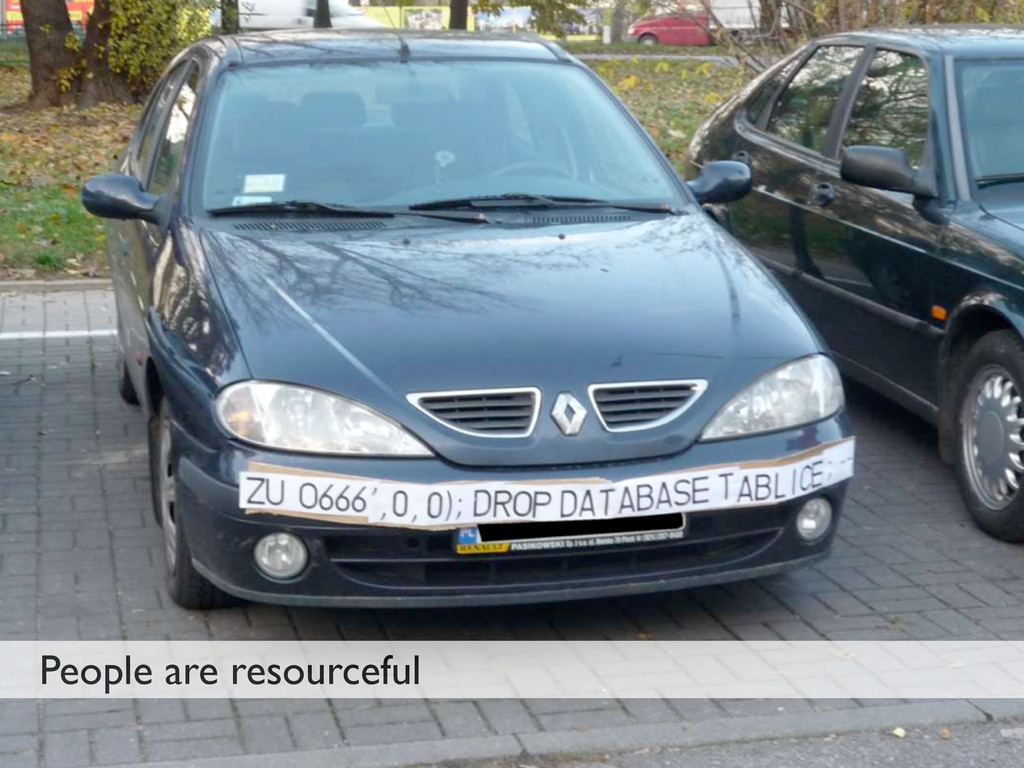
People are resourceful
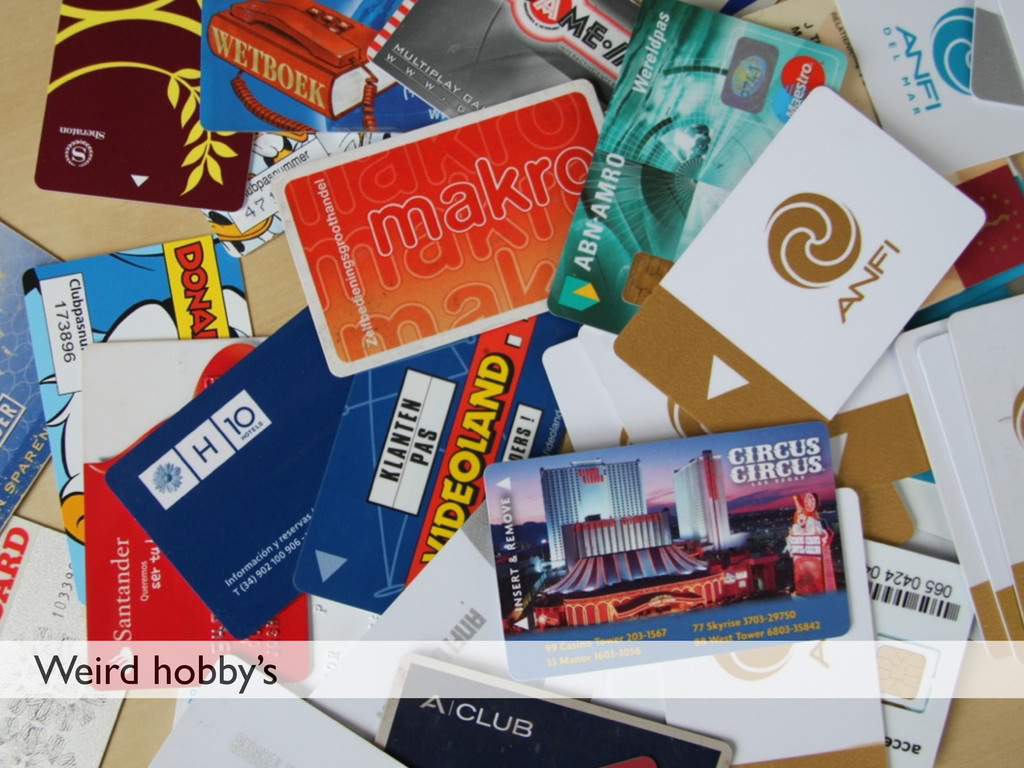
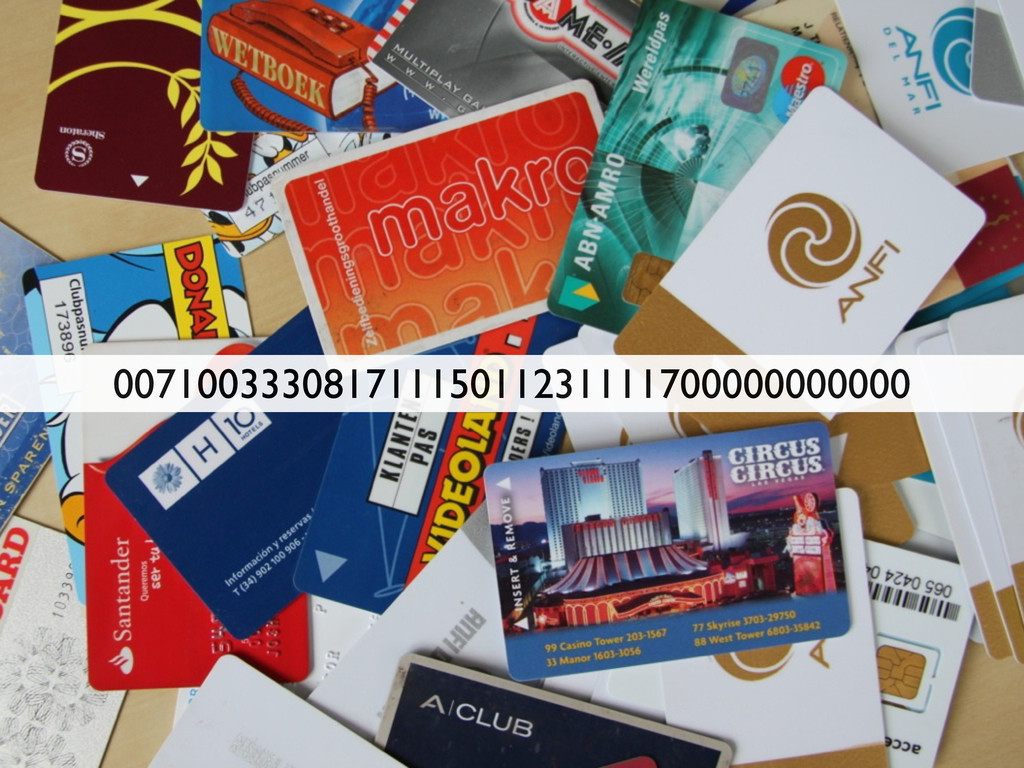
Weird hobby’s
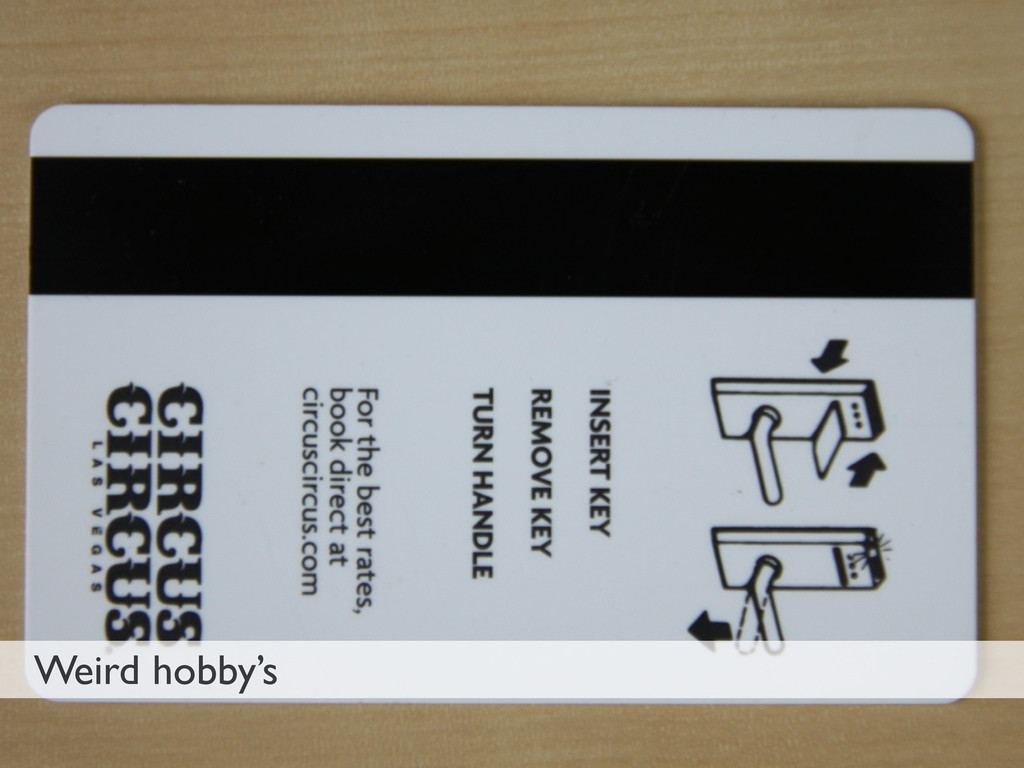
Weird hobby’s
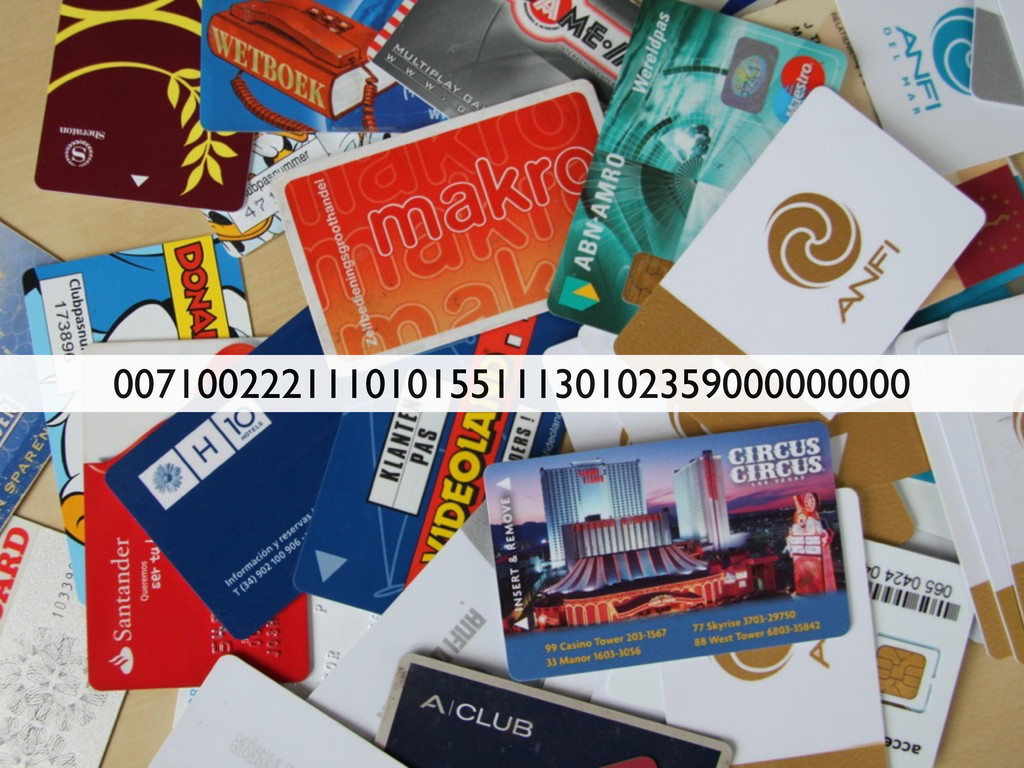
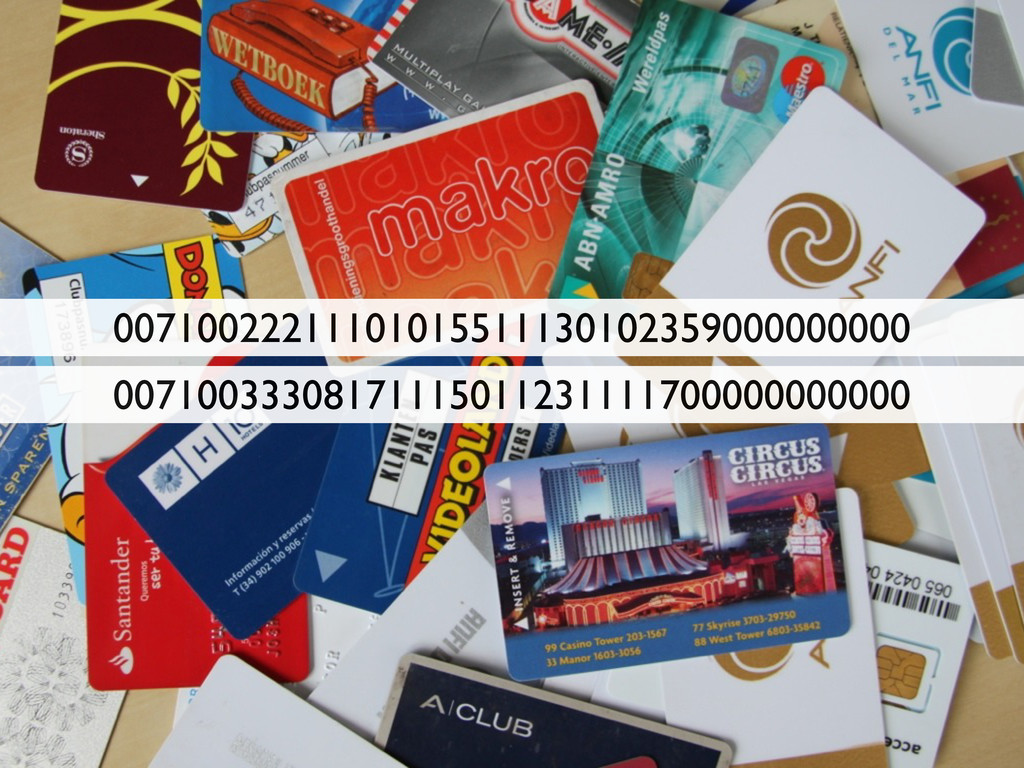
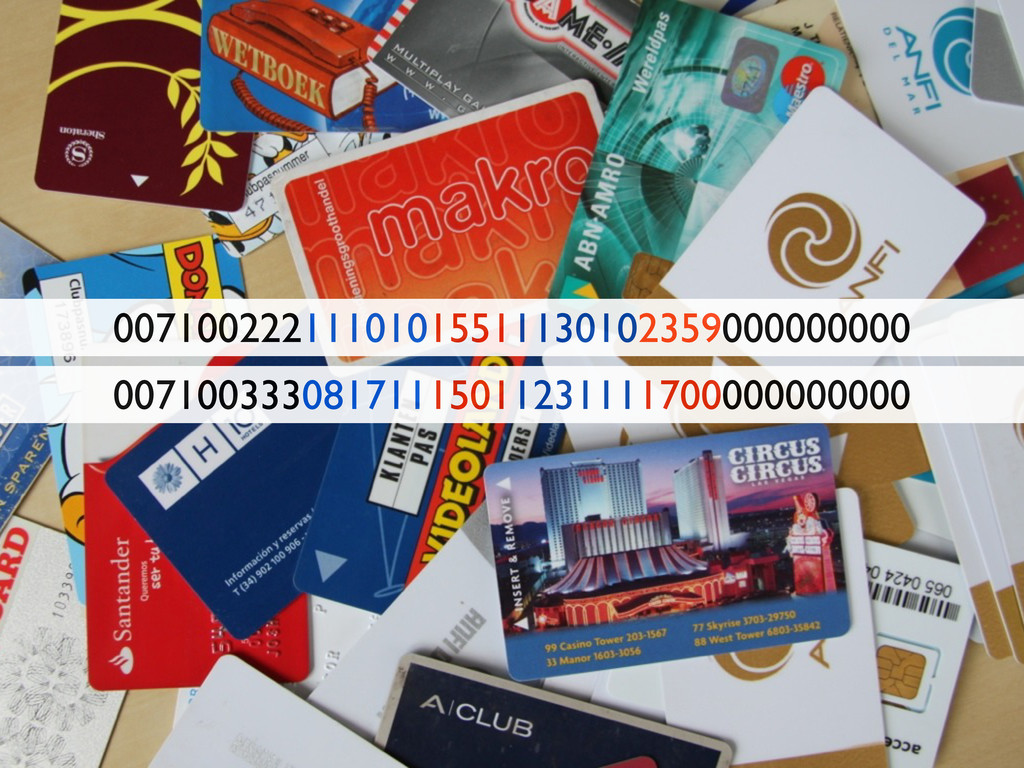
00710022211101015511130102359000000000
00710033308171115011231111700000000000
00710033308171115011231111700000000000 00710022211101015511130102359000000000
00710033308171115011231111700000000000 00710022211101015511130102359000000000
00710022211101015511130102359000000000 00710033308171115011231111700000000000
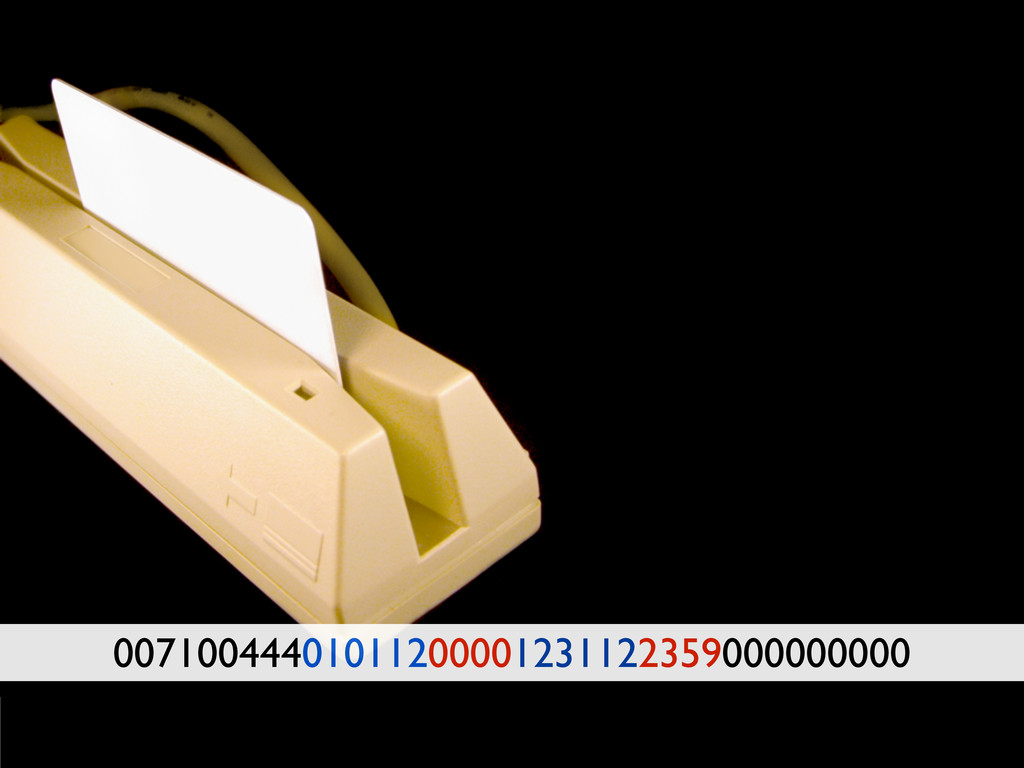
00710044401011200001231122359000000000
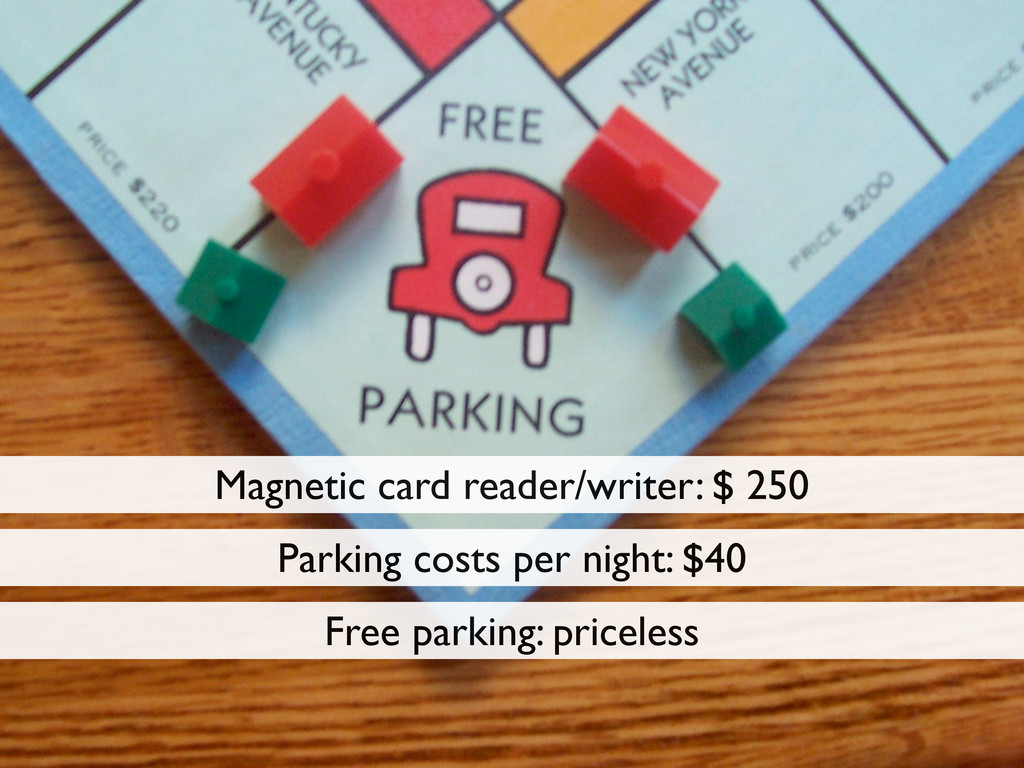
Magnetic card reader/writer: $ 250 Parking costs per night: $40
Free parking: priceless
How can we cure this problem?
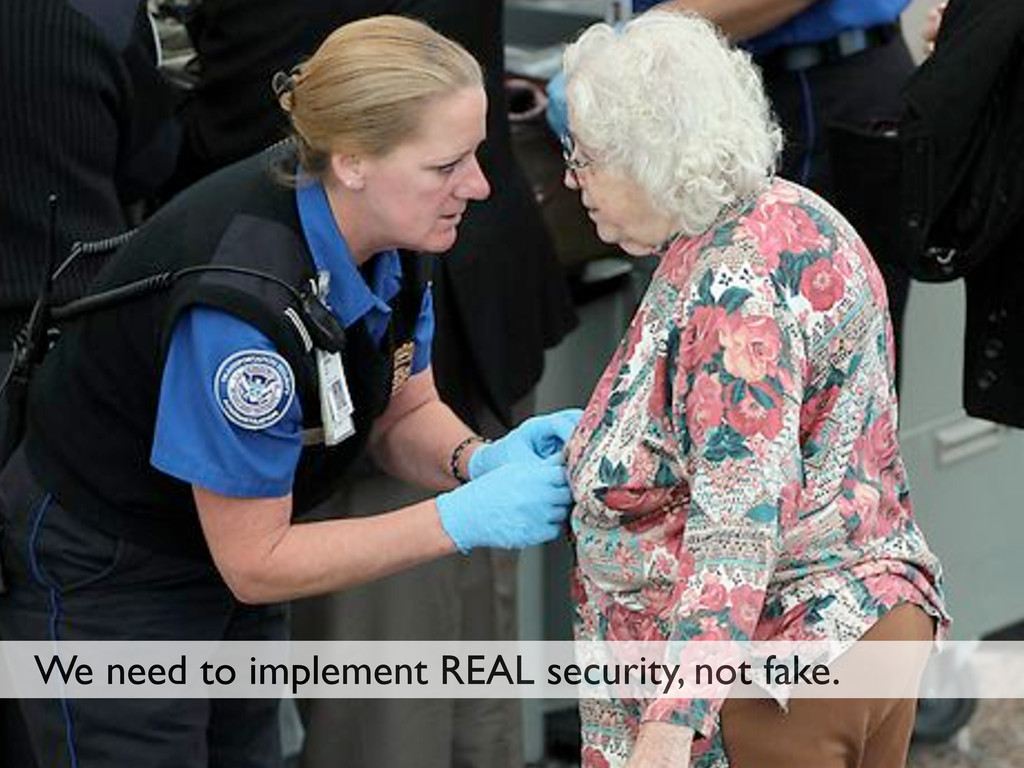
We need to implement REAL security, not fake.
How do we win the war? How do we win
the war?
If we as developers have to keep thinking about security,
we will lose...
We need to deflect *EVERY* attack, They only need *ONE*
to win...
99.999% of all programmers are NOT trained or have the
capability to identify security threats. The other 0.001% will not be able to identify them ALL OF THEM ALL THE TIME.
A day in the life of a PHP programmer...
$result = mysql_query('SELECT * FROM users WHERE username="'.$_GET['username'].'"');
You should use mysql_real_escape_string!
No, you shouldn’t!
You just put a developer who wasn’t aware of security
issues, in charge of security...
Let others handle security (PDO)
There is no (quick) solution. but we have to change
the way we deal with security radically, by not dealing with security...
Let others take care of security
Any questions (maximum 5)?
Find me on twitter: @jaytaph Find me for development and
training: www.noxlogic.nl Find me on email:
[email protected]
Find me for blogs: www.adayinthelifeof.nl Thank you!


 jaytaph
 mayatellez
 aki_iinuma
 lara
 smashingmag
 marketingsoph
 khoart
 eitanlees
 brad_frost
 sachag
 frankvandijk
 takai
 uxyall