Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Ethical Hacking Course in Trivandrum 2026 Batch

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →

Ethical Hacking Course in Trivandrum 2026 Batch

Join the 2026 batch of Ethical hacking course in Trivandrum—updated curriculum on AI threats and zero-days. Get certified and lead in cyber defense
https://tvm.offensoacademy.com/

Avatar for kuttanshoba395-debug

kuttanshoba395-debug

March 05, 2026

Other Decks in Education

Transcript

  1. Continuous Pentesting is the shift in Ethical hacking from rare

    security checks to non-stop monitoring. Forget yearly tests that miss weak spots in apps and networks for months. Now, teams find and patch them instantly. This blocks hackers and keeps systems safe 24/7. Master it via the Ethical Hacking Course in Trivandrum. Starting with Continuous Pentesting
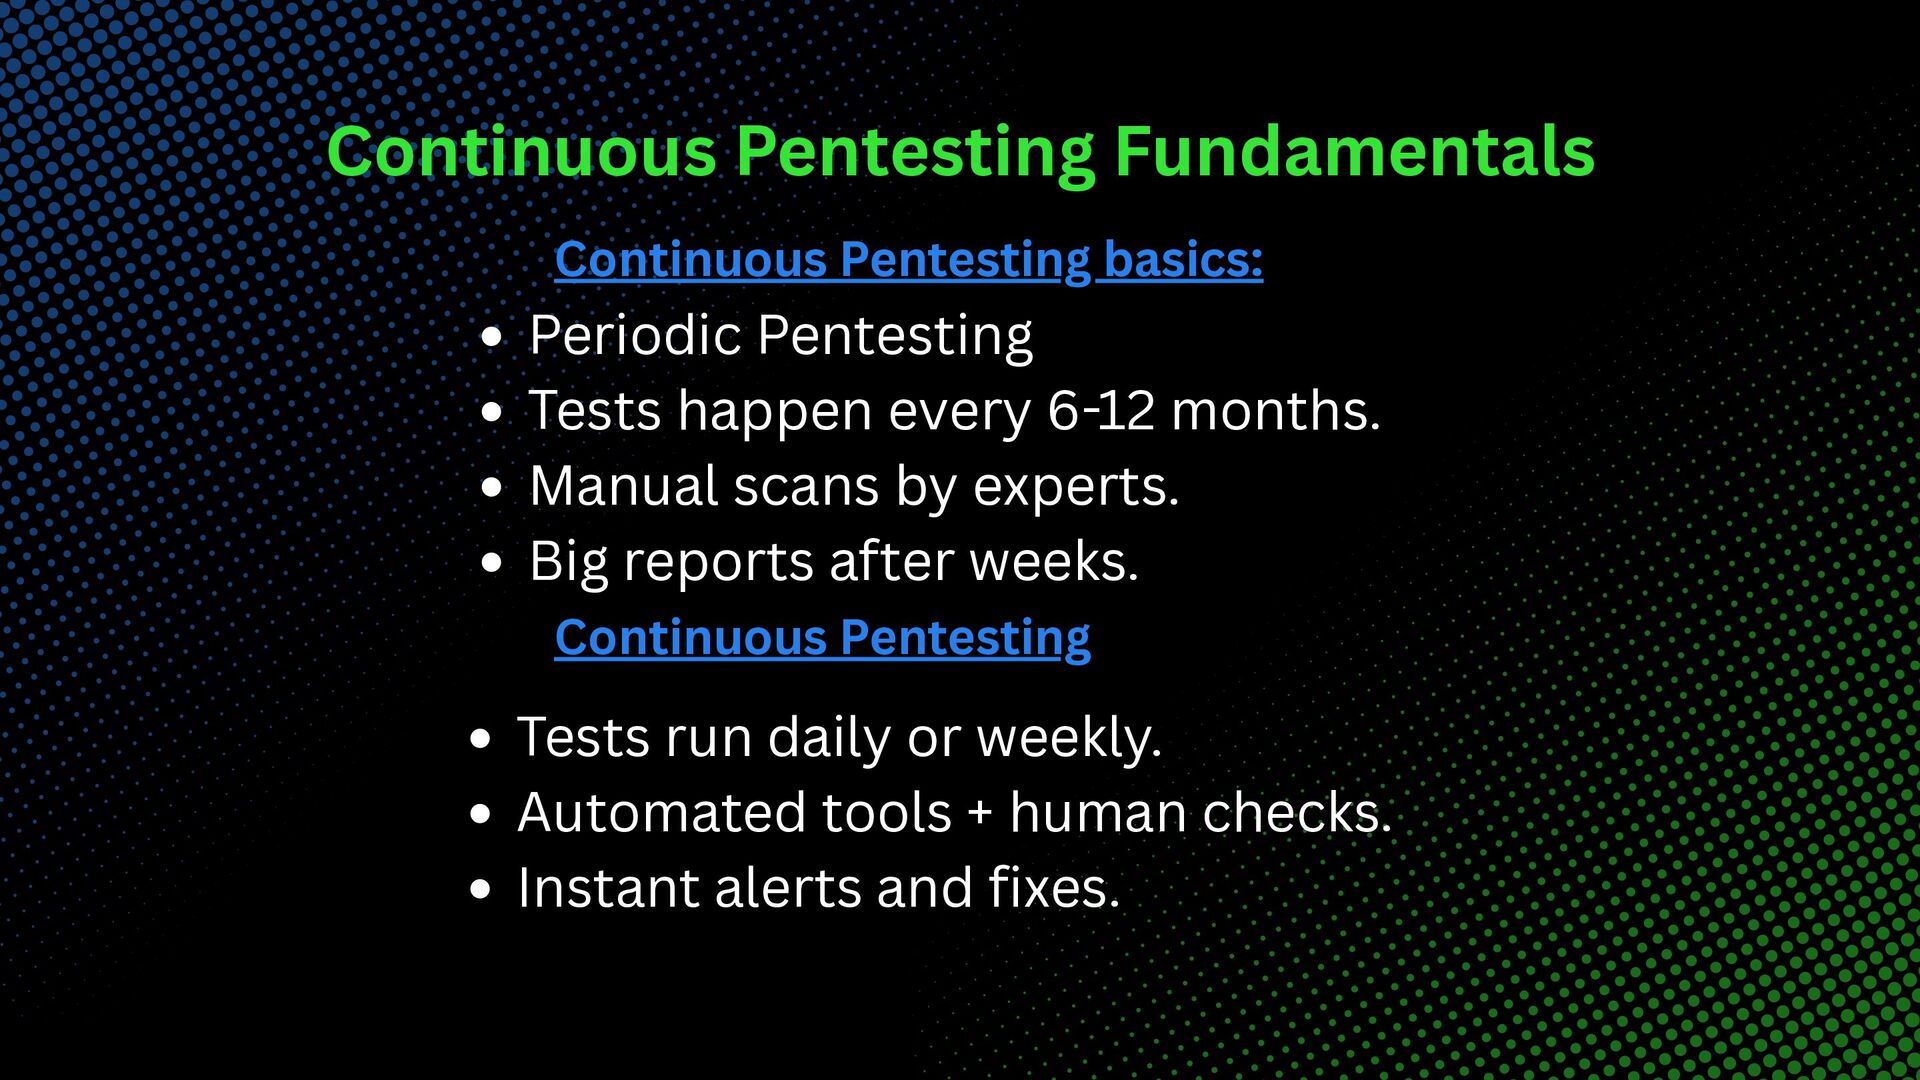
  2. Continuous Pentesting Fundamentals Continuous Pentesting basics: Periodic Pentesting Tests happen

    every 6-12 months. Manual scans by experts. Big reports after weeks. Continuous Pentesting Tests run daily or weekly. Automated tools + human checks. Instant alerts and fixes.
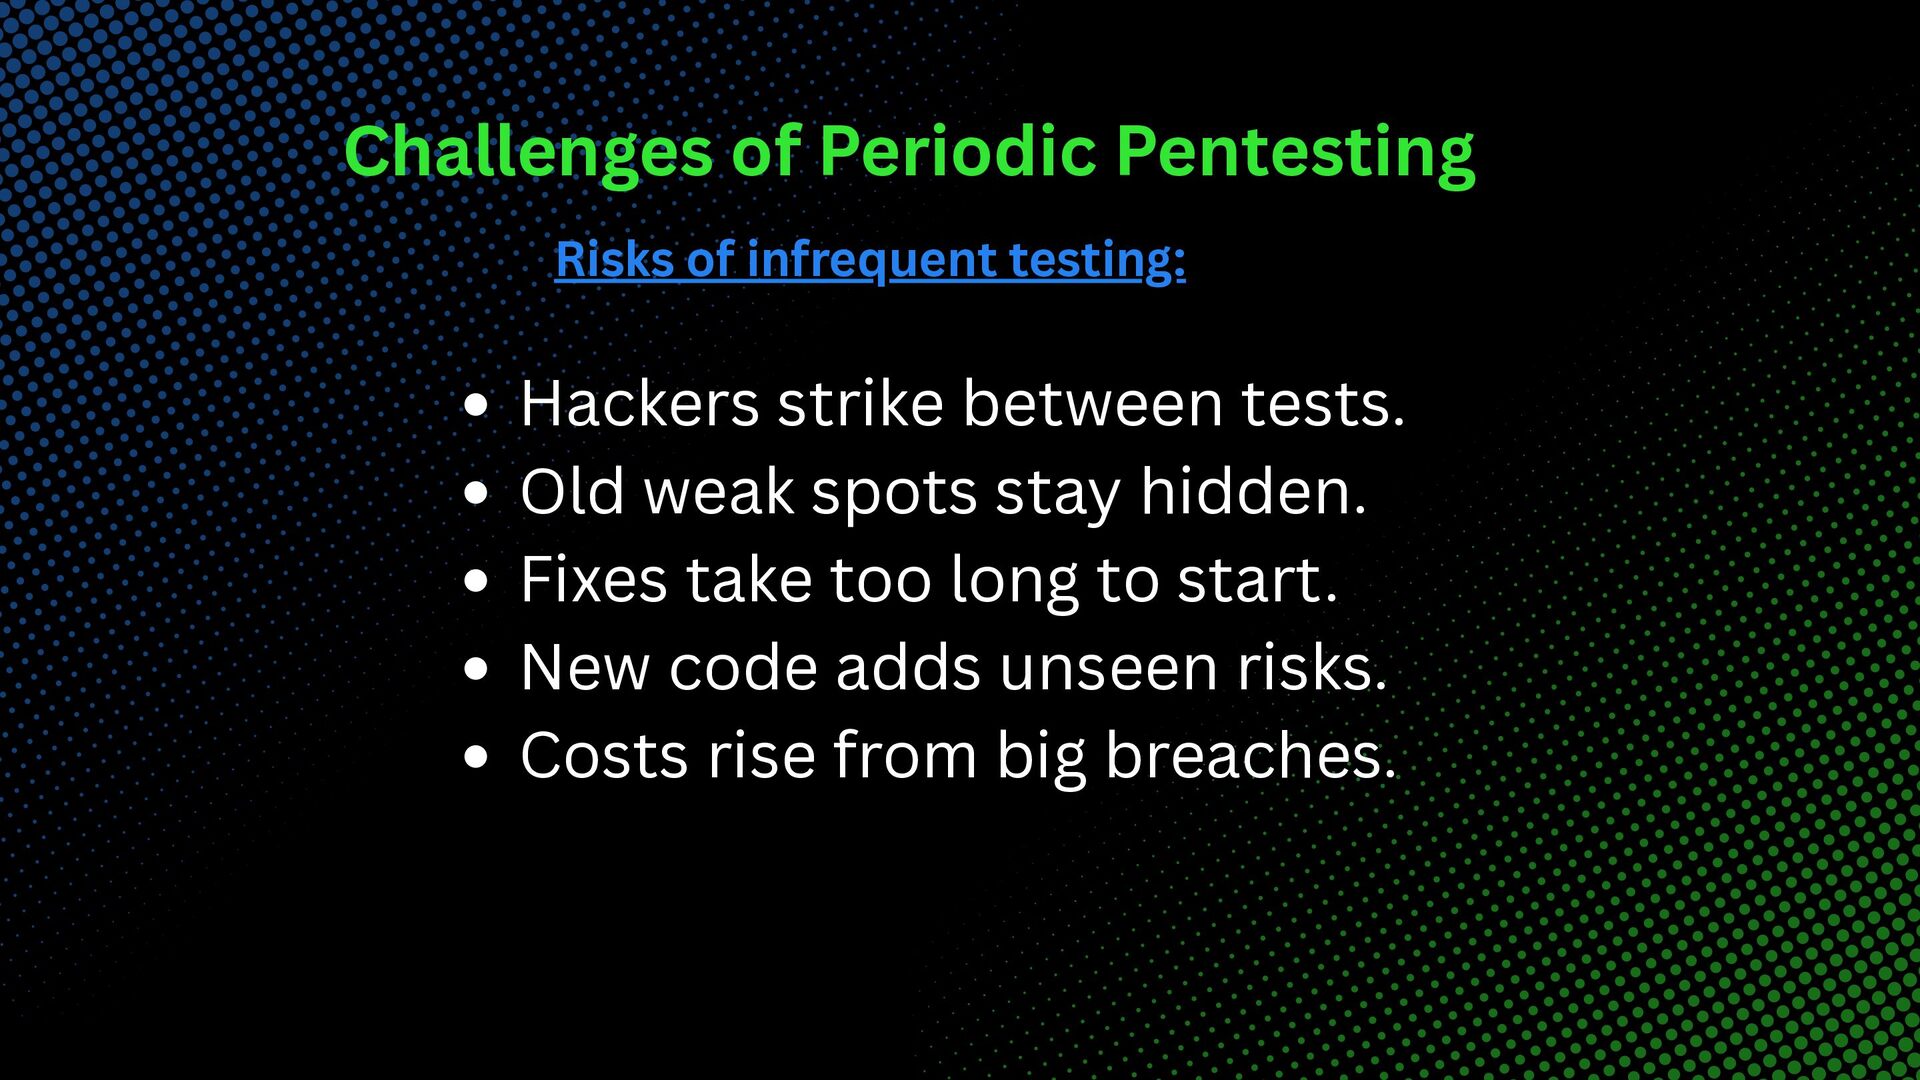
  3. Challenges of Periodic Pentesting Risks of infrequent testing: Hackers strike

    between tests. Old weak spots stay hidden. Fixes take too long to start. New code adds unseen risks. Costs rise from big breaches.
  4. Ongoing Exposure Management Benefits of continuous approach: Spots risks as

    they appear. Uses standard labels for all findings. Tracks fixes over time. Cuts breach chances by 70%. Standardized findings speed teamwork.
  5. Why Choose Ethical Hacking Ethical hacking teaches you real skills

    to find and fix system weak spots before bad guys do. You gain hands-on practice with tools pros use, building a strong career in cybersecurity jobs that pay well and stay in demand. The Ethical Hacking Course in Trivandrum connects this to live projects, like continuous pentesting, so you apply what you learn right away
  6. DevSecOps Integration How pentest results enable real-time fixes: Feed findings

    into code pipeline. Auto-scan new updates. Devs fix issues during builds. Sec teams approve fast.
  7. Real-World Penetration Testing Application in practice: Banks test apps daily

    for fraud holes. Apps scan logins non-stop. Teams use tools like Burp Suite live. Fixes deploy in hours, not months. Links to Ethical Hacking Course in Trivandrum training
  8. Key Advantages Security improvements: Fewer breaches from quick fixes. Always-updated

    threat views. Teams work faster together. Lower long-term costs. Builds hacker-proof habits
  9. Getting Started Steps to start Continuous Pentesting: Pick auto-tools like

    Nessus. Set standard finding labels. Link to DevSecOps flow. Train your team. Ethical Hacking Course in Trivandrum—enroll for hands-on start!
  10. Conclusion Steps to start Continuous Pentesting: Continuous Pentesting beats old

    ways by managing risks non- stop with standard findings and DevSecOps fixes. It keeps your systems safe from real threats every day. Boost your skills with the Ethical Hacking Course in Trivandrum and lead in cybersecurity