Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Real World Web Security
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
Florian Hirsch
March 18, 2016
Programming
63
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Real World Web Security
Developer Essentials
adorsys – 2016-03-18
Florian Hirsch
March 18, 2016
More Decks by Florian Hirsch
See All by Florian Hirsch
MVC – Back to the Server
lefloh
0
50
MVC – Back to the Server
lefloh
0
44
MVC – Back to the Server
lefloh
0
38
JavaScript Development Tools
lefloh
0
68
MVC – Nachwuchs im Hause Java EE
lefloh
0
29
MVC – Back to the Server
lefloh
0
44
Bullseye! – Let's play Dart
lefloh
0
63
Bullseye! – Ein Blick auf Dart
lefloh
0
46
Zur Hölle mit Responsive!
lefloh
0
36
Other Decks in Programming
See All in Programming
AIで開発が速くなった先で、開発チームは何を目指すか
shihochan
0
880
パズルゲームの作り方 / how to make puzzle games
kaityo256
PRO
2
290
Jetpack Compose Mechanisms
skydoves
3
820
【加筆修正版】Laravel のアプリケーションをどこにデプロイするか #phpcon_ehime
akase244
0
150
Findy - エンジニア向け会社紹介/Findy Company Deck
findyinc
6
400k
ChromeでローカルLLM
ryu1013
0
140
JIS keyboard support in Omarchy
lef237
0
110
外から家のPCの電源入れたい!をPHPで解決する
kawashimo0
1
130
Kotlinの15年とServer-Side Kotlin
n_takehata
1
150
[2026-09-26]空論ジェネリックプロセス~テスト資産とAIで紡ぐ、再現可能なパフォーマンスチューニングの話~
tosite
0
270
全ての永続トークンを、生まれる前に消し去りたい!
sylph01
2
880
C#の現在地 進化の歴史と、AI時代の.NET Everywhere
neuecc
5
5.2k
Featured
See All Featured
Building the Perfect Custom Keyboard
takai
2
910
Statistics for Hackers
jakevdp
799
230k
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
2
6.3k
Building Applications with DynamoDB
mza
96
7.2k
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.1k
Reflections from 52 weeks, 52 projects
jeffersonlam
356
22k
The #1 spot is gone: here's how to win anyway
tamaranovitovic
4
1.2k
Building Flexible Design Systems
yeseniaperezcruz
330
41k
10 Git Anti Patterns You Should be Aware of
lemiorhan
PRO
659
62k
My Coaching Mixtape
mlcsv
0
360
What's in a price? How to price your products and services
michaelherold
247
13k
Chasing Engaging Ingredients in Design
codingconduct
0
360
Transcript
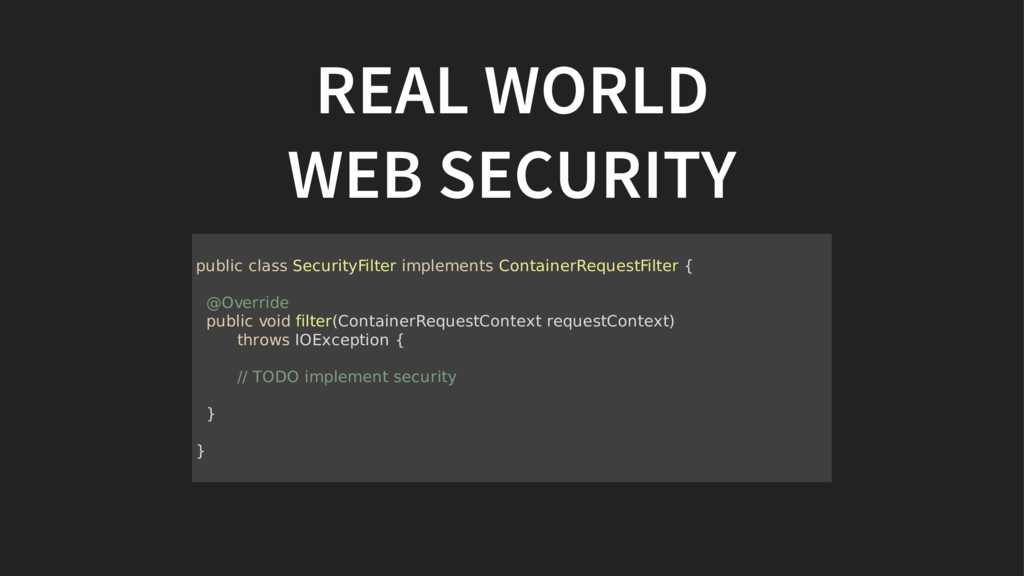
REAL WORLD WEB SECURITY public class SecurityFilter implements ContainerRequestFilter {
@Override public void filter(ContainerRequestContext requestContext) throws IOException { // TODO implement security } }
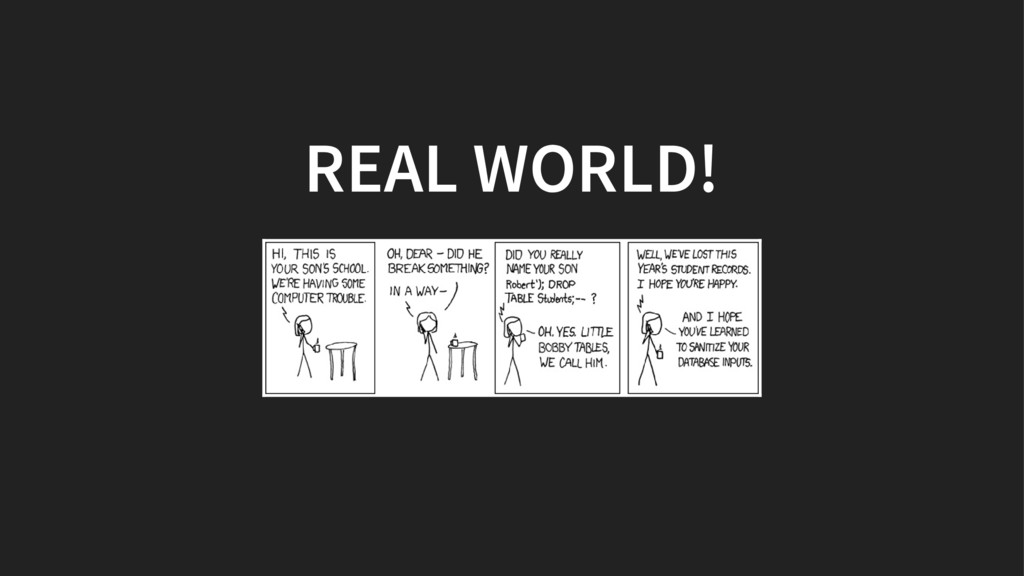
REAL WORLD!
SHAME ON YOU!
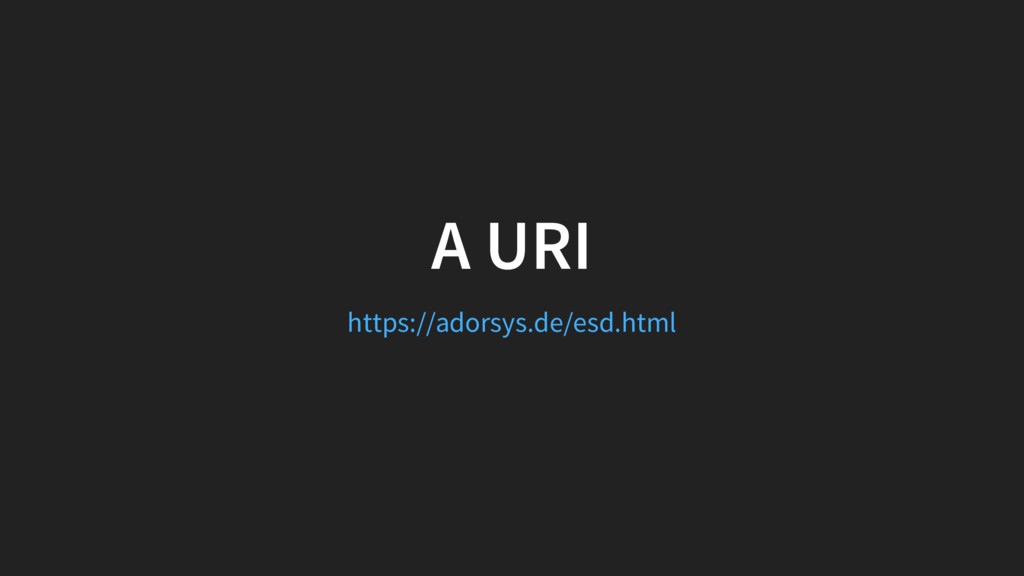
A URI https://adorsys.de/esd.html
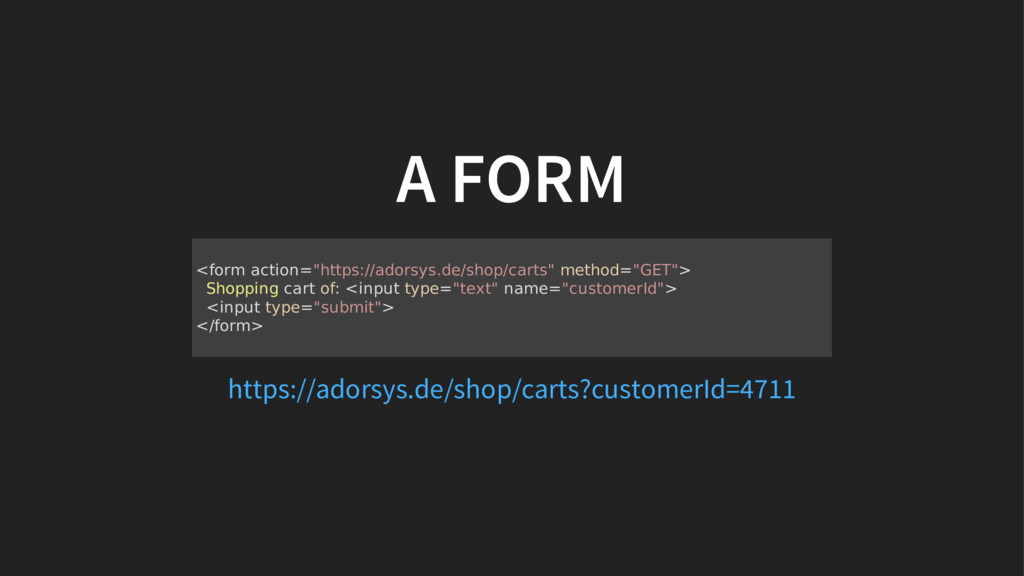
A FORM <form action="https://adorsys.de/shop/carts" method="GET"> Shopping cart of: <input type="text"
name="customerId"> <input type="submit"> </form> https://adorsys.de/shop/carts?customerId=4711
A REQUEST URI Body Header (Cookies)
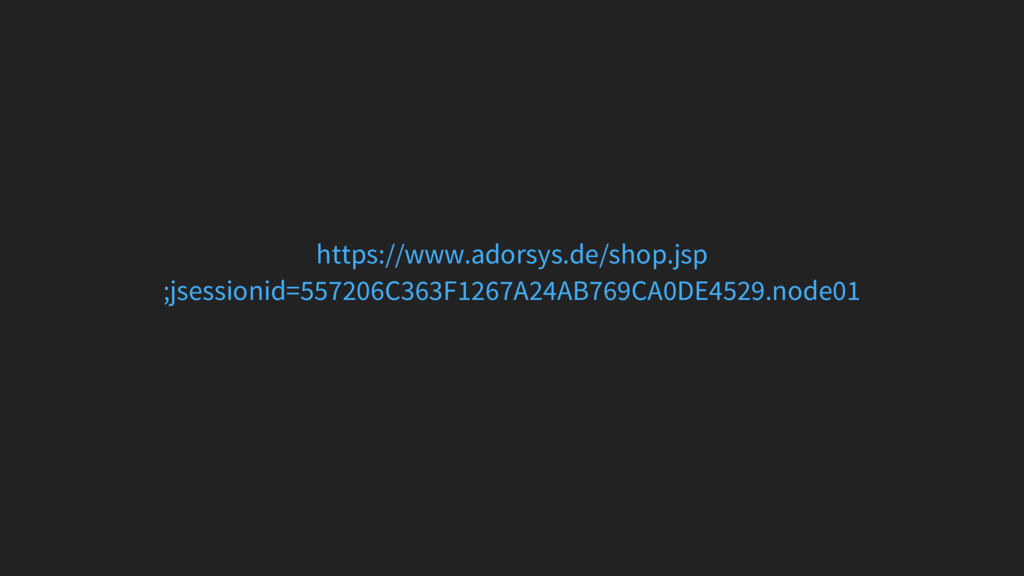
https://www.adorsys.de/shop.jsp ;jsessionid=557206C363F1267A24AB769CA0DE4529.node01
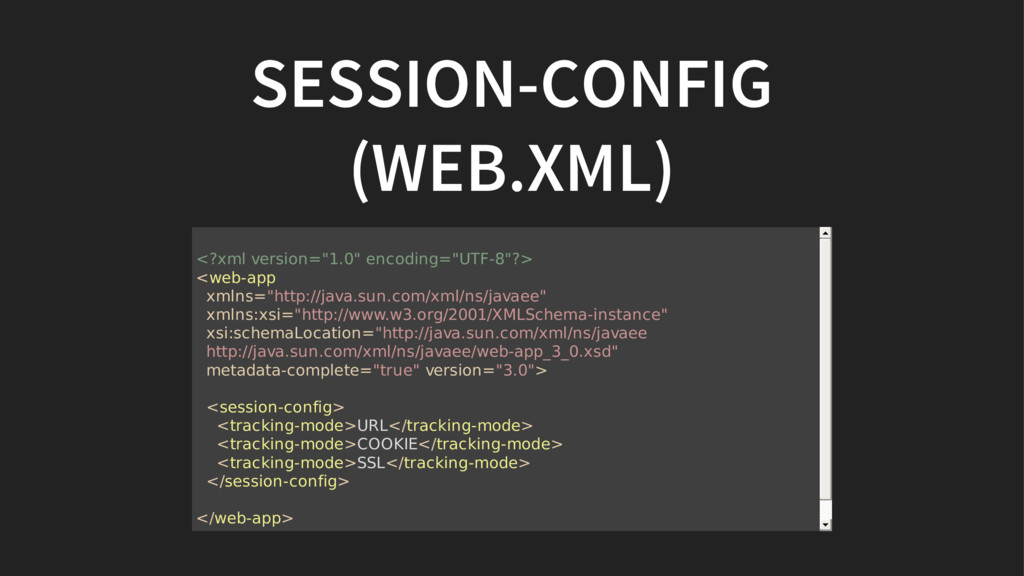
SESSION-CONFIG (WEB.XML) <?xml version="1.0" encoding="UTF-8"?> <web-app xmlns="http://java.sun.com/xml/ns/javaee" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance" xsi:schemaLocation="http://java.sun.com/xml/ns/javaee http://java.sun.com/xml/ns/javaee/web-app_3_0.xsd"
metadata-complete="true" version="3.0"> <session-config> <tracking-mode>URL</tracking-mode> <tracking-mode>COOKIE</tracking-mode> <tracking-mode>SSL</tracking-mode> </session-config> </web-app>
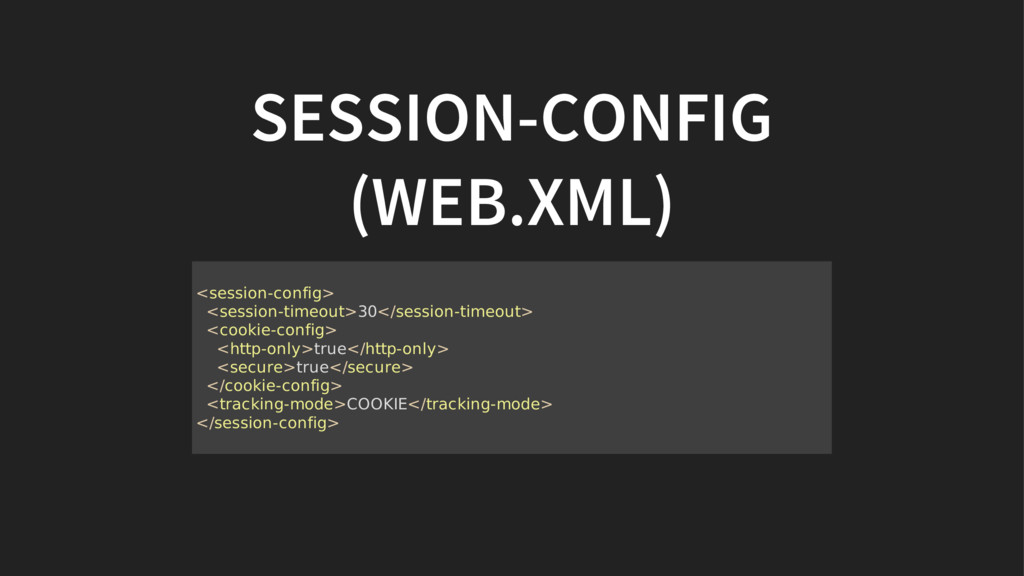
SESSION-CONFIG (WEB.XML) <session-config> <session-timeout>30</session-timeout> <cookie-config> <http-only>true</http-only> <secure>true</secure> </cookie-config> <tracking-mode>COOKIE</tracking-mode> </session-config>
@WebServlet("/login") public class LoginServlet extends HttpServlet { @Override protected void
doGet(HttpServletRequest req, HttpServletResponse res) throws ServletException, IOException { if (login(req.getParameter("user"), req.getParameter("pw"))) { response.sendRedirect("/home"); } else { response.sendRedirect("/login-failed"); } } }
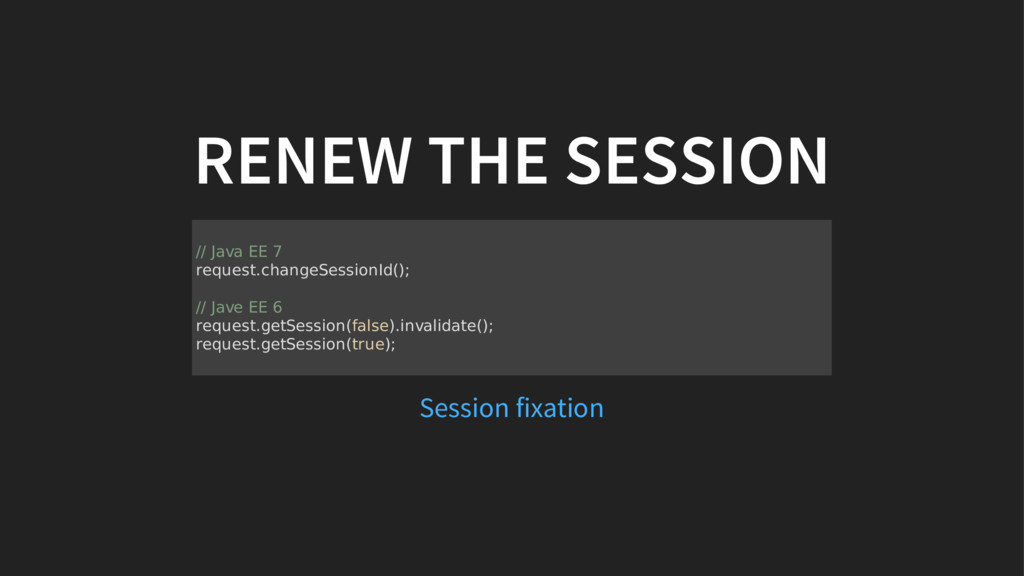
RENEW THE SESSION // Java EE 7 request.changeSessionId(); // Jave
EE 6 request.getSession(false).invalidate(); request.getSession(true); Session fixation
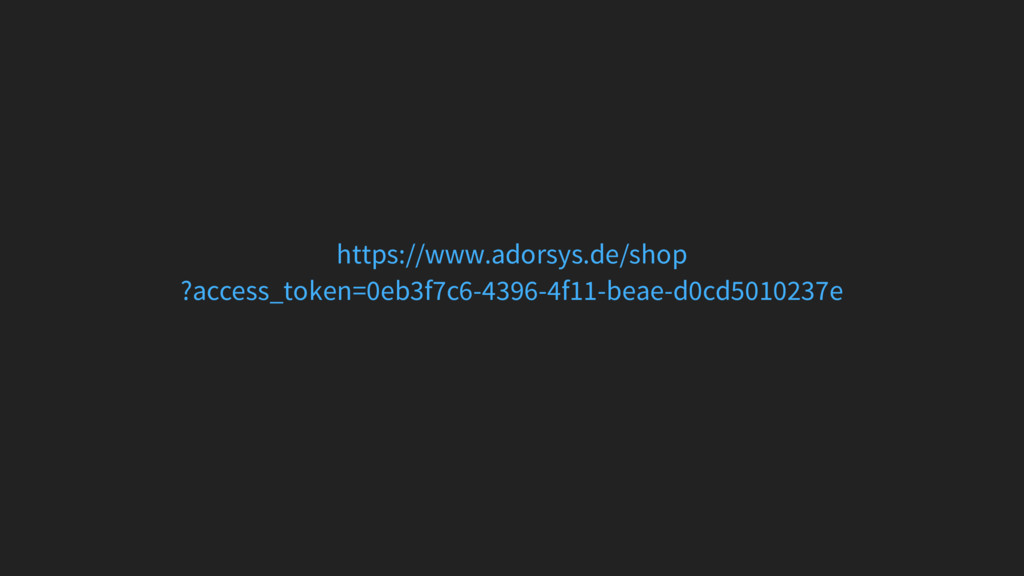
https://www.adorsys.de/shop ?access_token=0eb3f7c6-4396-4f11-beae-d0cd5010237e
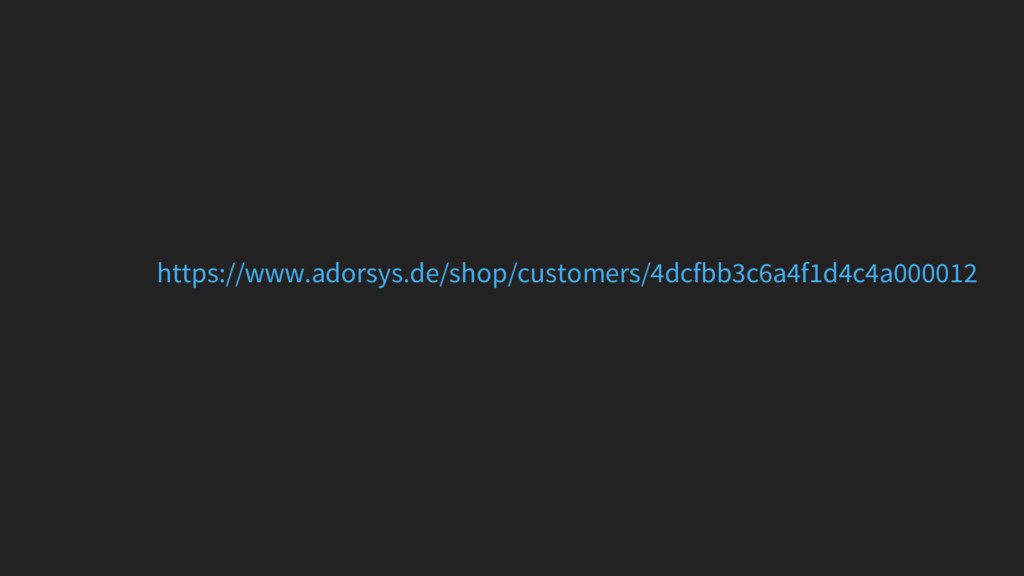
https://www.adorsys.de/shop/customers/4dcfbb3c6a4f1d4c4a000012
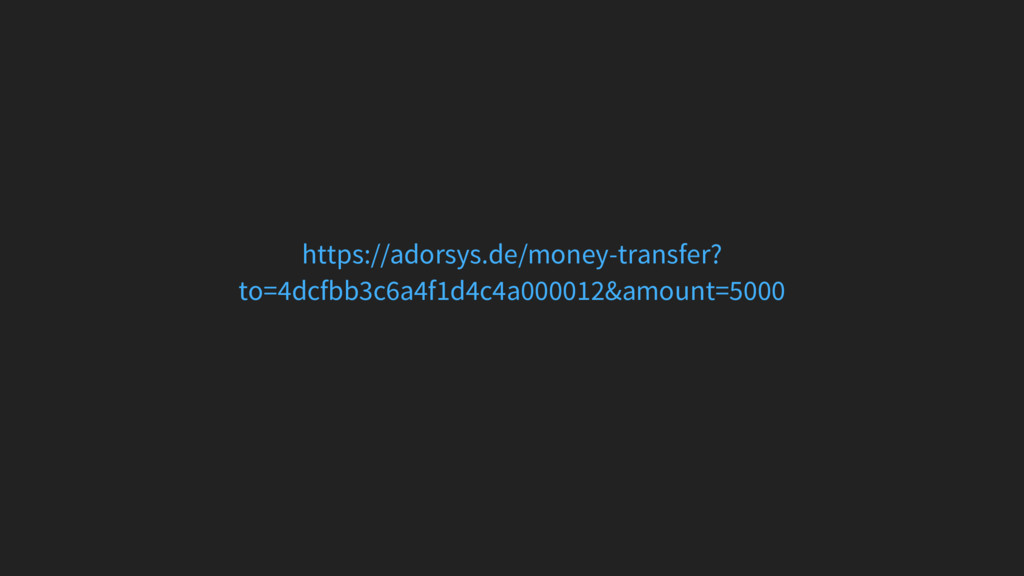
https://adorsys.de/money-transfer? to=4dcfbb3c6a4f1d4c4a000012&amount=5000
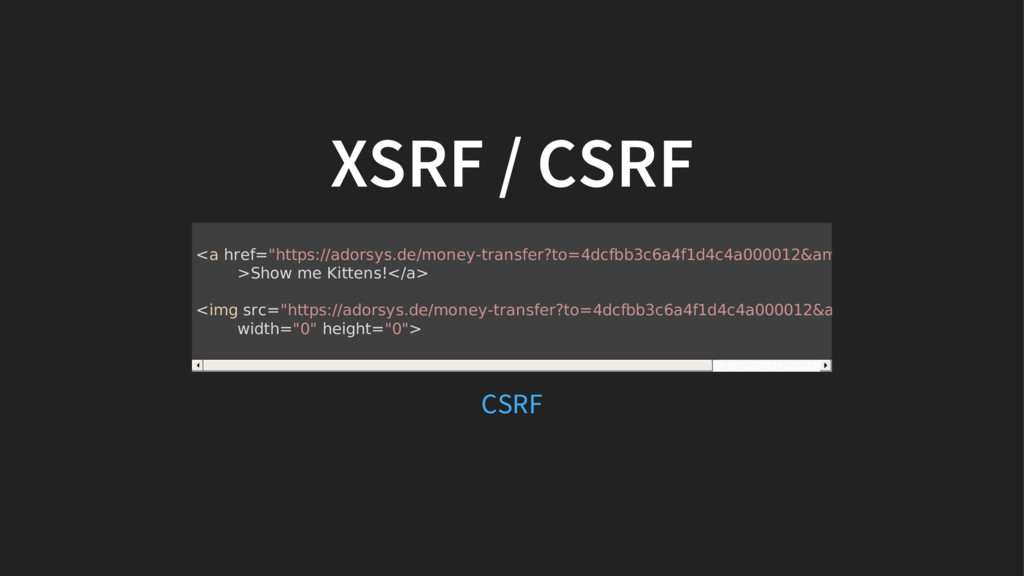
XSRF / CSRF <a href="https://adorsys.de/money-transfer?to=4dcfbb3c6a4f1d4c4a000012&amount=5000" >Show me Kittens!</a> <img src="https://adorsys.de/money-transfer?to=4dcfbb3c6a4f1d4c4a000012&amount=5000"
width="0" height="0"> CSRF
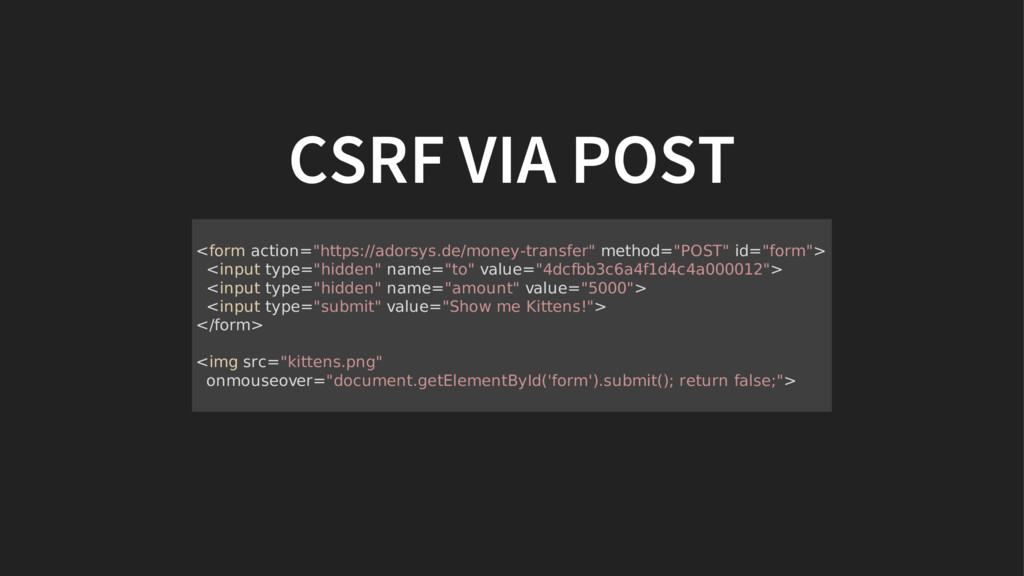
CSRF VIA POST <form action="https://adorsys.de/money-transfer" method="POST" id="form"> <input type="hidden" name="to"
value="4dcfbb3c6a4f1d4c4a000012"> <input type="hidden" name="amount" value="5000"> <input type="submit" value="Show me Kittens!"> </form> <img src="kittens.png" onmouseover="document.getElementById('form').submit(); return false;">
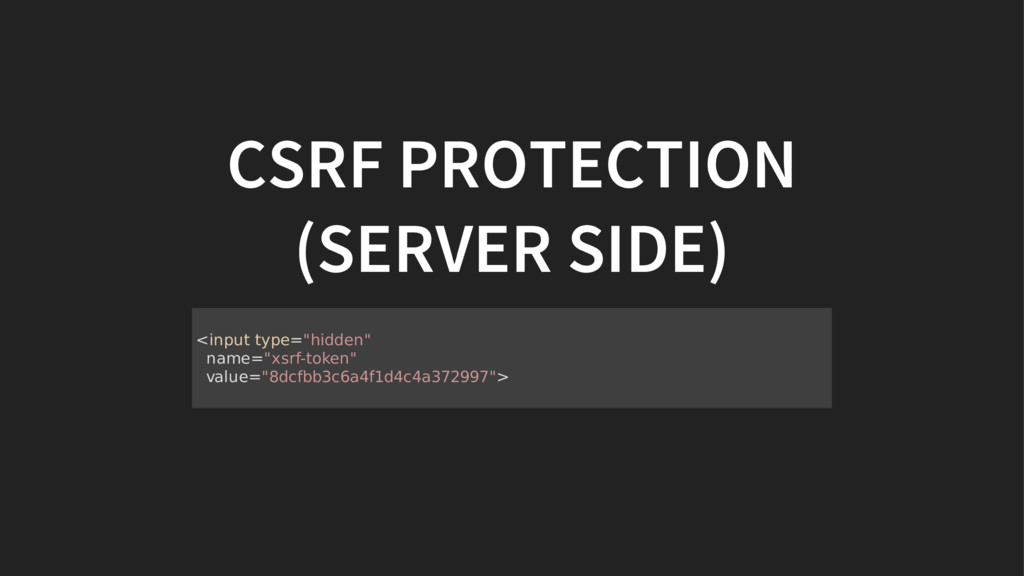
CSRF PROTECTION (SERVER SIDE) <input type="hidden" name="xsrf-token" value="8dcfbb3c6a4f1d4c4a372997">
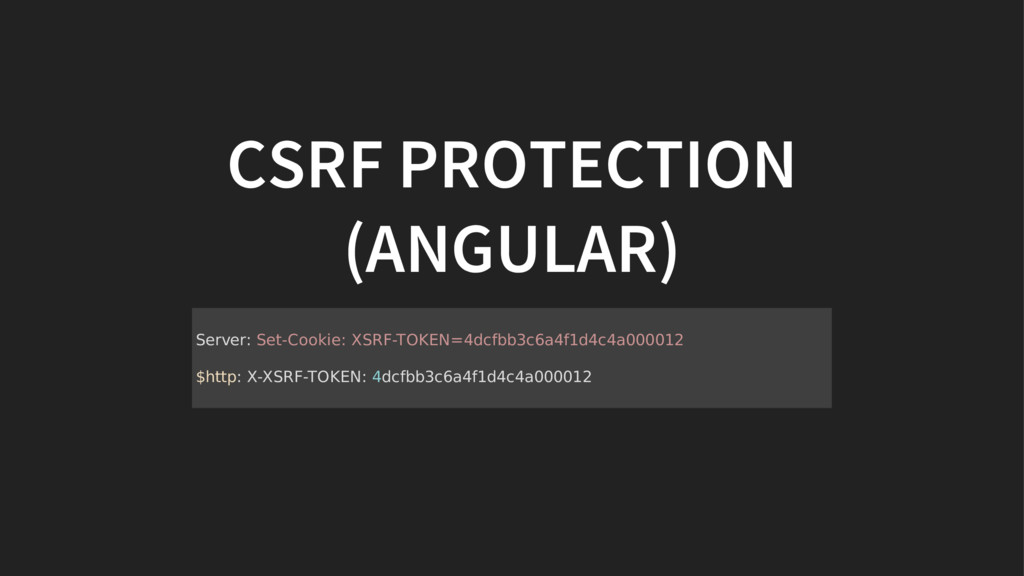
CSRF PROTECTION (ANGULAR) Server: Set-Cookie: XSRF-TOKEN=4dcfbb3c6a4f1d4c4a000012 $http: X-XSRF-TOKEN: 4dcfbb3c6a4f1d4c4a000012
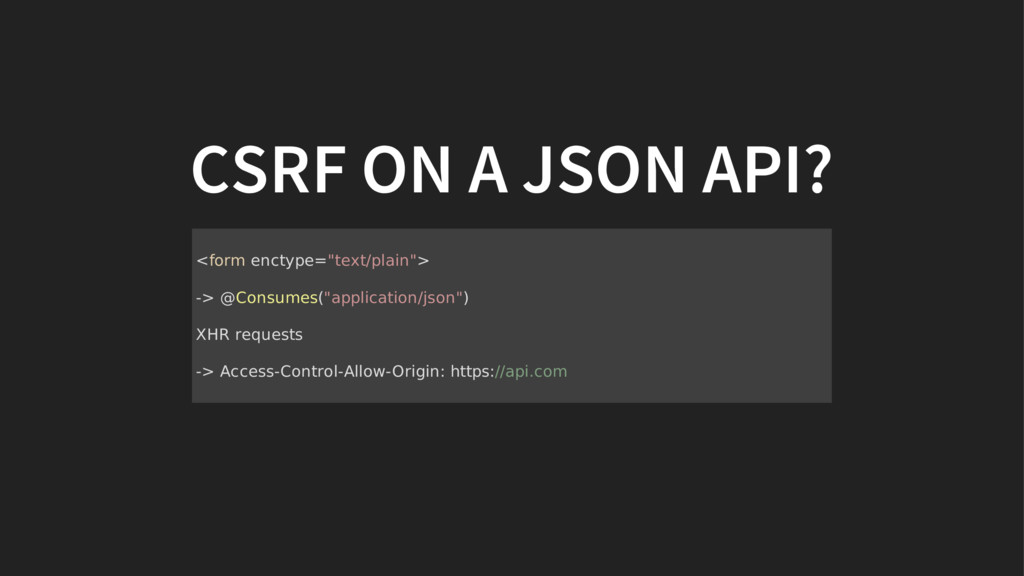
CSRF ON A JSON API? <form enctype="text/plain"> -> @Consumes("application/json") XHR
requests -> Access-Control-Allow-Origin: https://api.com
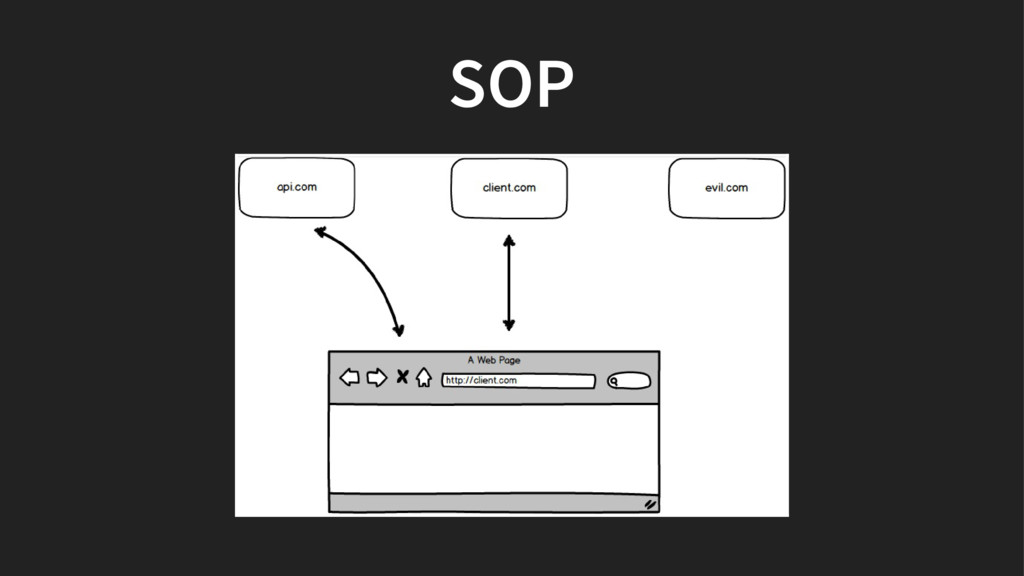
SOP
CORS HEADER Access-Control-Allow-Origin: *
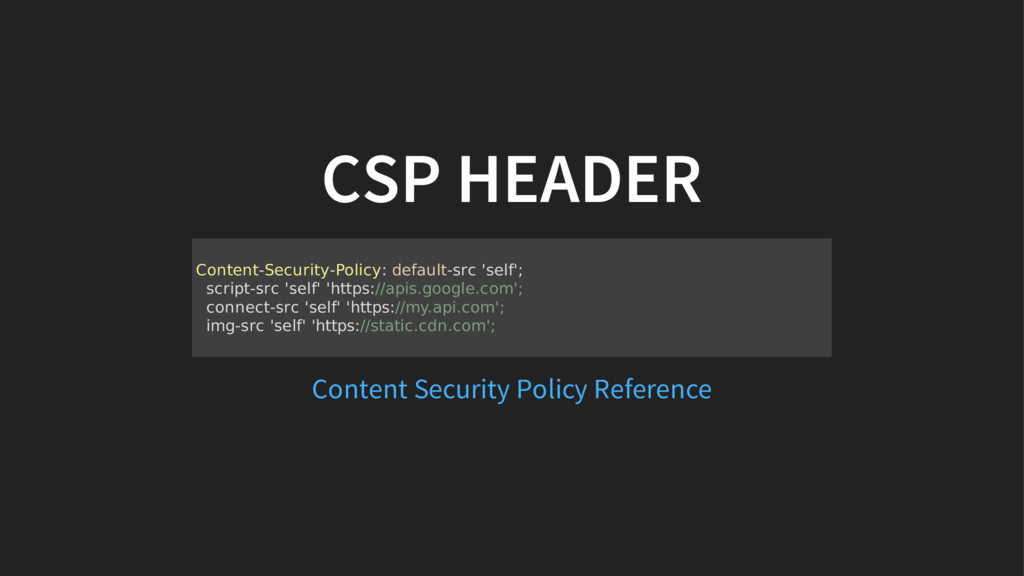
CSP HEADER Content-Security-Policy: default-src 'self'; script-src 'self' 'https://apis.google.com'; connect-src 'self'
'https://my.api.com'; img-src 'self' 'https://static.cdn.com'; Content Security Policy Reference
COOKIELESS LOGIN @Path("/login") public class LoginResource { @POST public Response
login(@Context HttpServletRequest req) { if (basicAuth(req)) { return Response.ok() .header("X-AUTH-TOKEN", UUID.randomUUID()).build(); } else { return Response.status(403).build(); } } }
TOKEN STORAGE $http.post('/login', credentials).then(function(response) { $httpProvider.defaults.headers.common['X-AUTH-TOKEN'] = response.data.token; // for
page reloads... $cookies.put('X-AUTH-TOKEN', response.data.token); $window.localStorage.setItem('X-AUTH-TOKEN', response.data.token); $window.sessionStorage.setItem('X-AUTH-TOKEN', response.data.token); });
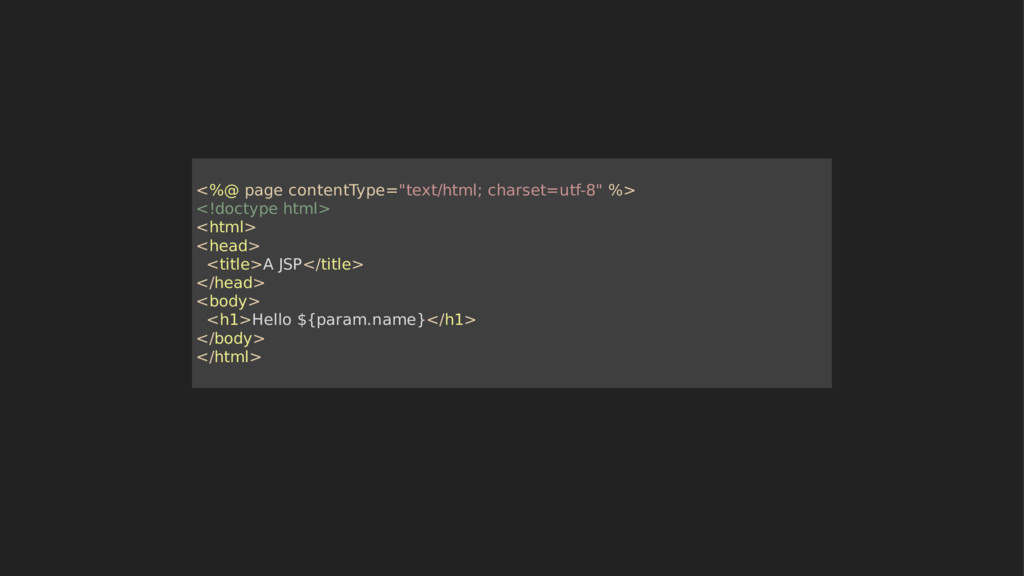
<%@ page contentType="text/html; charset=utf-8" %> <!doctype html> <html> <head> <title>A
JSP</title> </head> <body> <h1>Hello ${param.name}</h1> </body> </html>
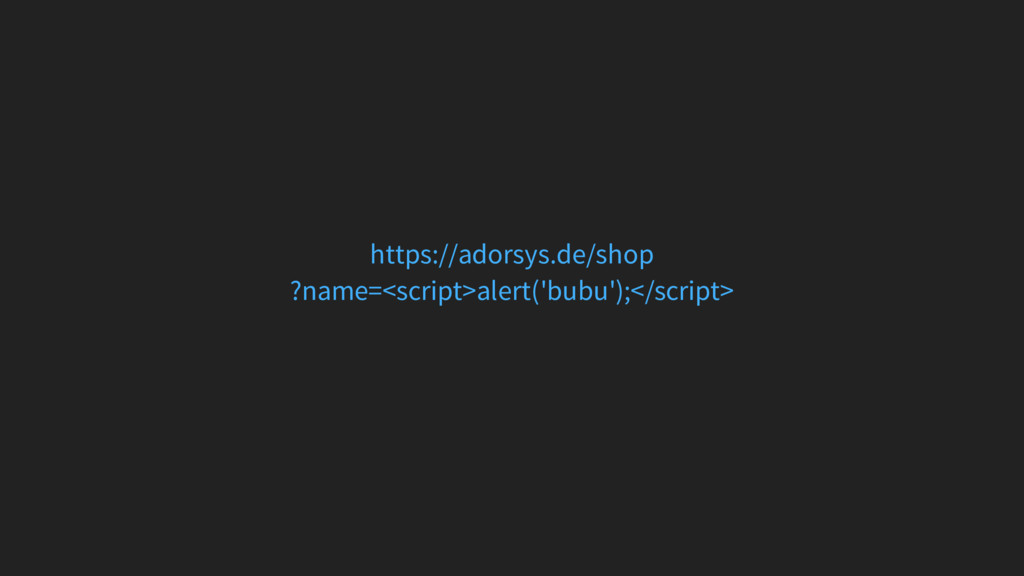
https://adorsys.de/shop ?name=<script>alert('bubu');</script>
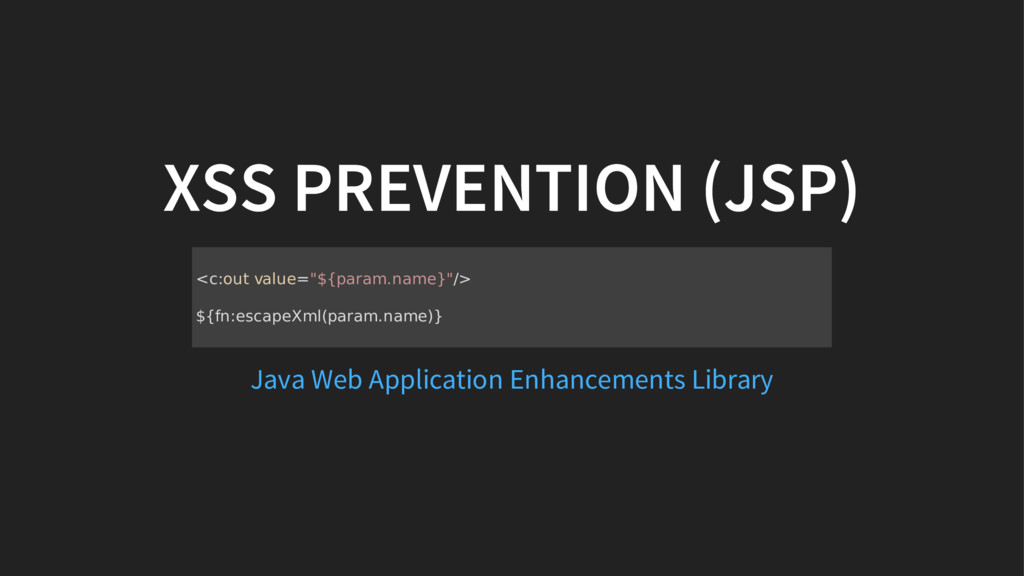
XSS PREVENTION (JSP) <c:out value="${param.name}"/> ${fn:escapeXml(param.name)} Java Web Application Enhancements
Library
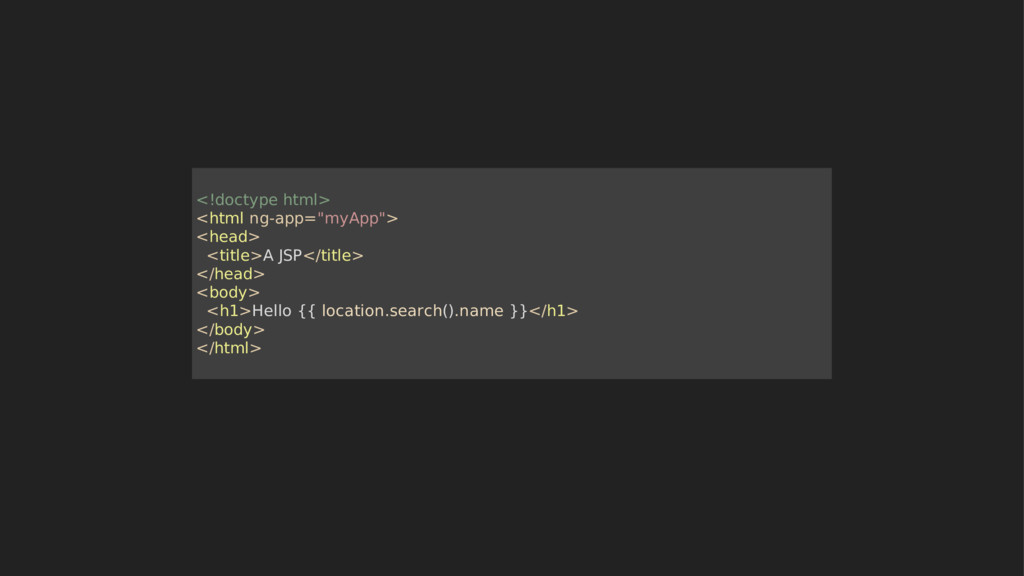
<!doctype html> <html ng-app="myApp"> <head> <title>A JSP</title> </head> <body> <h1>Hello
{{ location.search().name }}</h1> </body> </html>
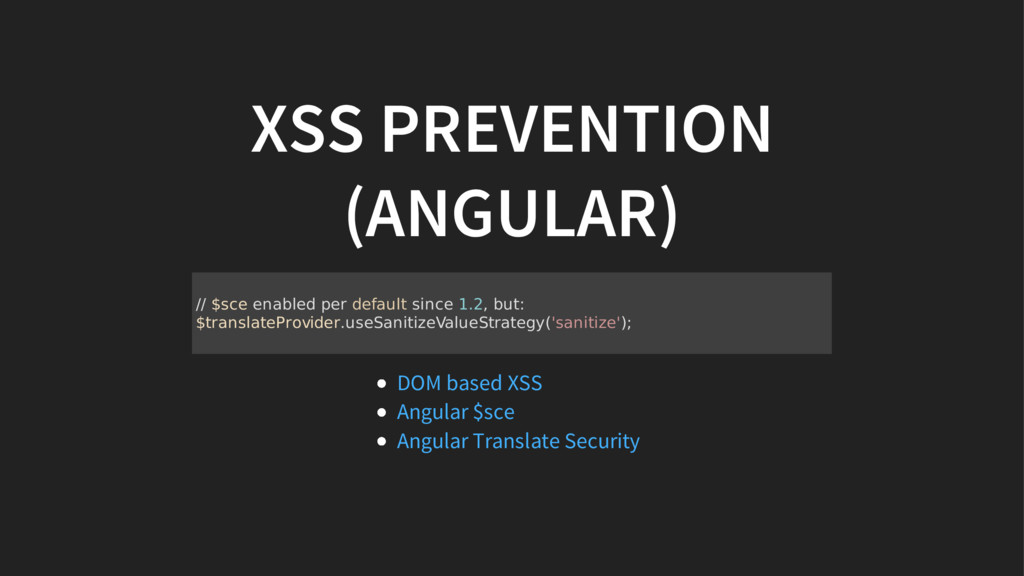
XSS PREVENTION (ANGULAR) // $sce enabled per default since 1.2,
but: $translateProvider.useSanitizeValueStrategy('sanitize'); DOM based XSS Angular $sce Angular Translate Security
app.post('/login', function(req, res) { db.users.find({ username: req.body.username, password: req.body.password },
function (err, users) { // login successful! }); });
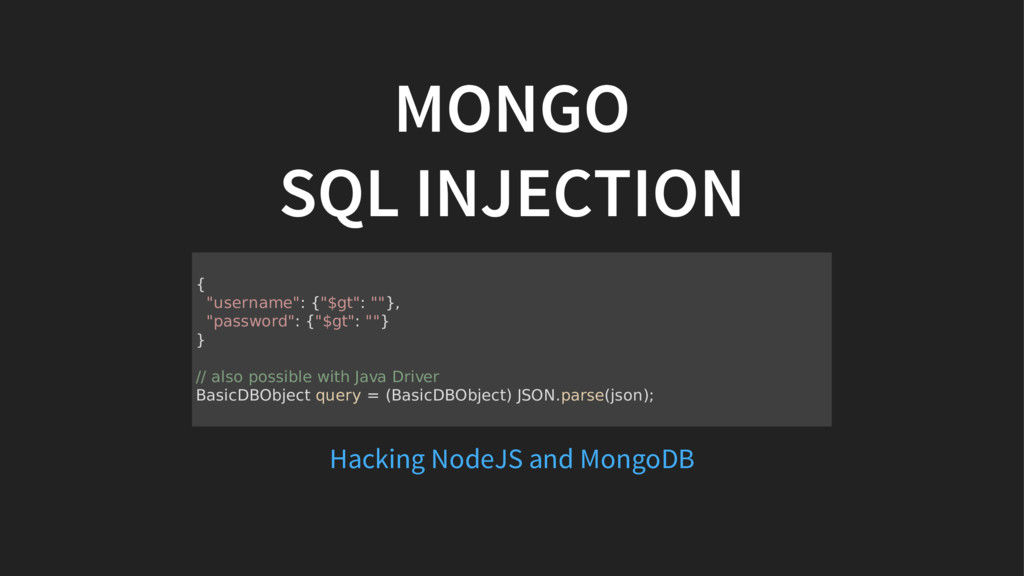
MONGO SQL INJECTION { "username": {"$gt": ""}, "password": {"$gt": ""}
} // also possible with Java Driver BasicDBObject query = (BasicDBObject) JSON.parse(json); Hacking NodeJS and MongoDB
BTW... 30.000 MongoDB Instances accessible over the Internet without any
authorization
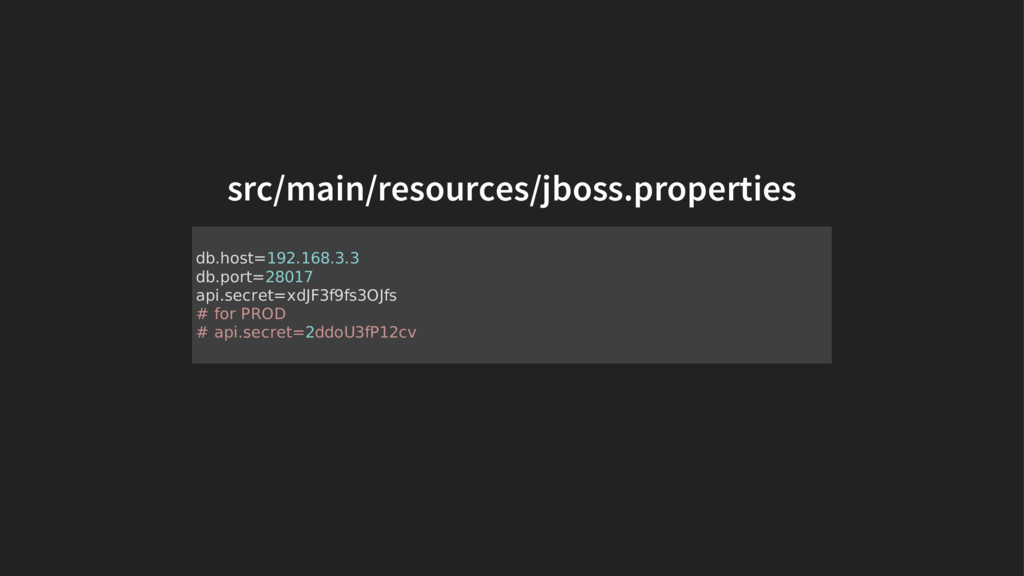
src/main/resources/jboss.properties db.host=192.168.3.3 db.port=28017 api.secret=xdJF3f9fs3OJfs # for PROD # api.secret=2ddoU3fP12cv
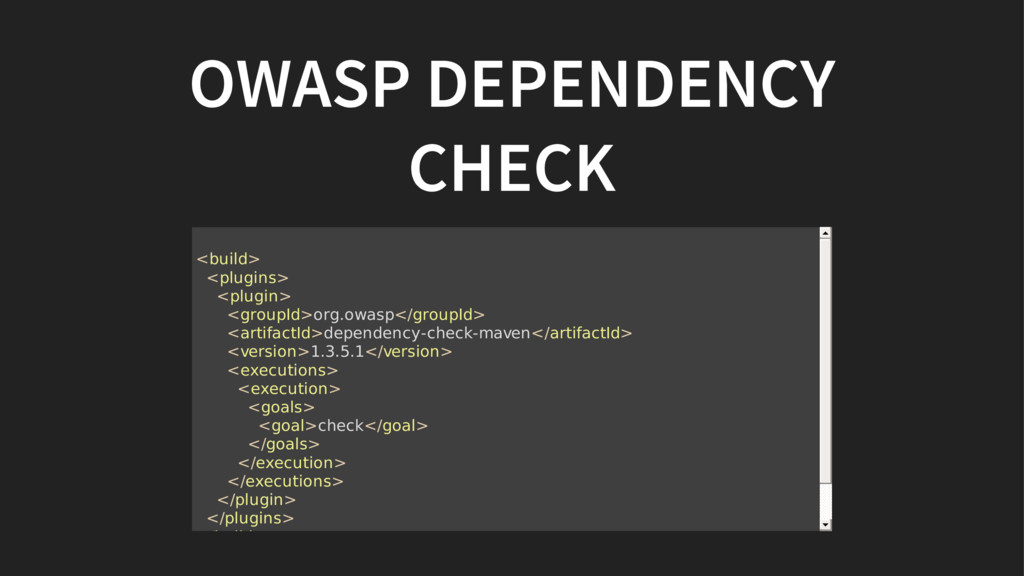
OWASP DEPENDENCY CHECK <build> <plugins> <plugin> <groupId>org.owasp</groupId> <artifactId>dependency-check-maven</artifactId> <version>1.3.5.1</version> <executions>
<execution> <goals> <goal>check</goal> </goals> </execution> </executions> </plugin> </plugins> </build>
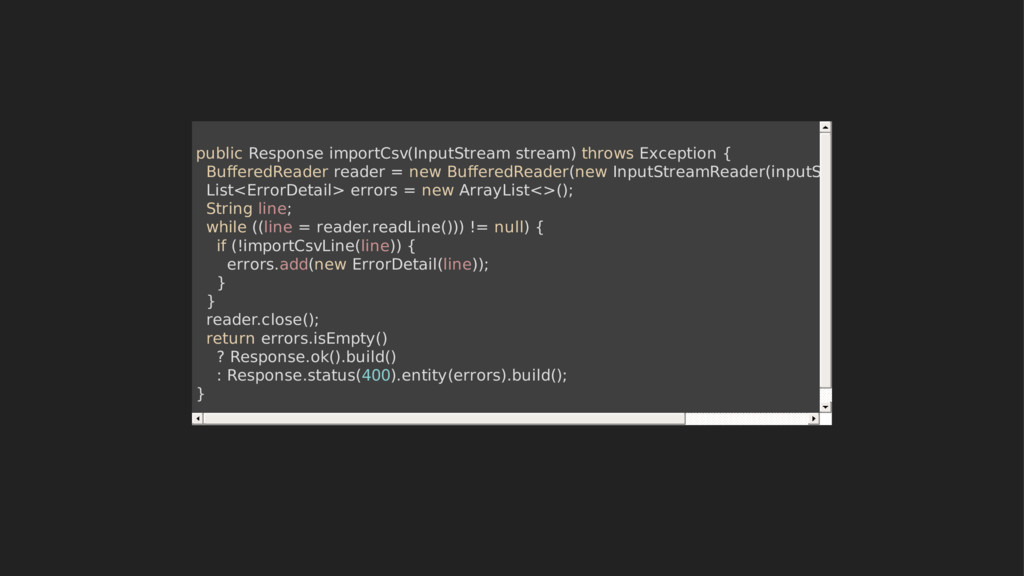
public Response importCsv(InputStream stream) throws Exception { BufferedReader reader =
new BufferedReader(new InputStreamReader(inputStream, "UTF-8")); List<ErrorDetail> errors = new ArrayList<>(); String line; while ((line = reader.readLine())) != null) { if (!importCsvLine(line)) { errors.add(new ErrorDetail(line)); } } reader.close(); return errors.isEmpty() ? Response.ok().build() : Response.status(400).entity(errors).build(); }
OWASP Top Ten 2013
JSR 375 Soteria
THANKS

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 lefloh
 shihochan
 kaityo256
 skydoves
 akase244
 findyinc
 ryu1013
 lef237
 kawashimo0
 n_takehata
 tosite
 sylph01
 neuecc
 takai
 jakevdp
 aleyda
 mza
 reverentgeek
 jeffersonlam
 tamaranovitovic
 yeseniaperezcruz
 lemiorhan
 mlcsv
 michaelherold
 codingconduct