Share
Secure Architecture and Programming 101
Security still is an underrated non-functional requirement in software engineering, often neglected or even forgotten during the construction and implementation of software systems. If things go wrong the reputation and business of your customers as well as yours might be at stake. Retrofitting security is laborious and expensive, it needs to be considered from day. Sounds hard? Not at all.
This presentation will show that writing secure code and constructing secure systems is not as hard as it may sound. First, we will briefly dissect some well-known security vulnerabilities which were the result of only minor programming errors and we will demonstrate how easy insecurely written Java code can be exploited.
However, writing secure code from day one is just as easy. For this we will present a handful of basic rules and tools every secure developer must know. This session will discuss the secure usage of open source software components in enterprise applications and describe patterns to securely incorporate these libraries. The session will further present basic patterns to construct secure components and system architectures.
This presentation has been presented at the O'Reilly Software Architecture Conference in London 2016. #OReillySACon
M.-Leander Reimer PRO
Transcript
55 slides
-
Secure Architecture and Programming 101 Mario-Leander Reimer, QAware GmbH O’Reilly
Software Architecture Conference in London 2016 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer $ whoami Mario-Leander Reimer Chief Technologist, QAware GmbH [email protected] https://github.com/lreimer/ https://slideshare.net/MarioLeanderReimer/ https://speakerdeck.com/lreimer/ https://twitter.com/leanderreimer/ 2 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Security seems to be the most underrated non functional requirement in software engineering. 3 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
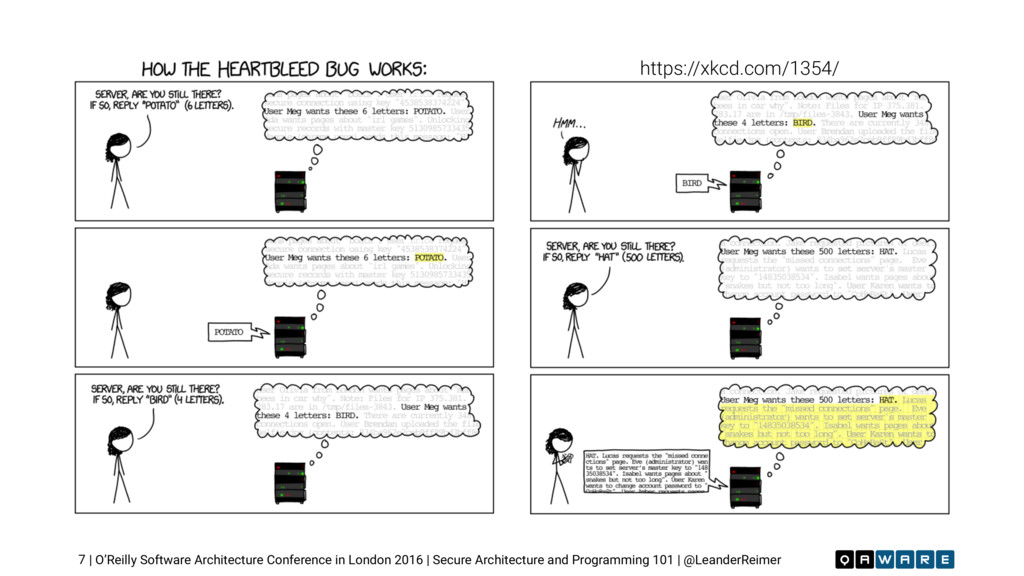
Architecture and Programming 101 | @LeanderReimer 7 https://xkcd.com/1354/ -
| O’Reilly Software Architecture Conference in London 2016 | Secure
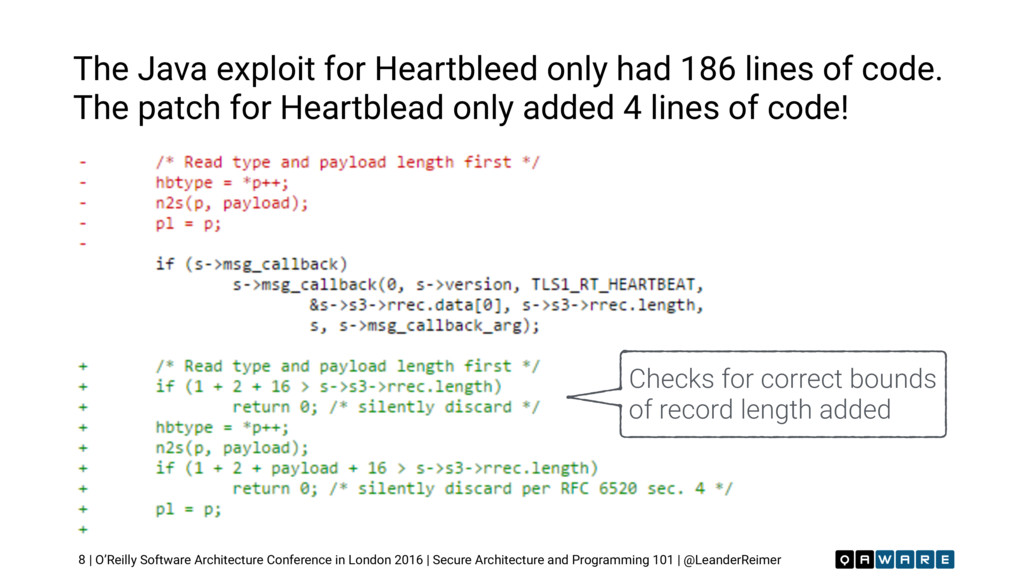
Architecture and Programming 101 | @LeanderReimer The Java exploit for Heartbleed only had 186 lines of code. The patch for Heartblead only added 4 lines of code! 8 Checks for correct bounds of record length added -
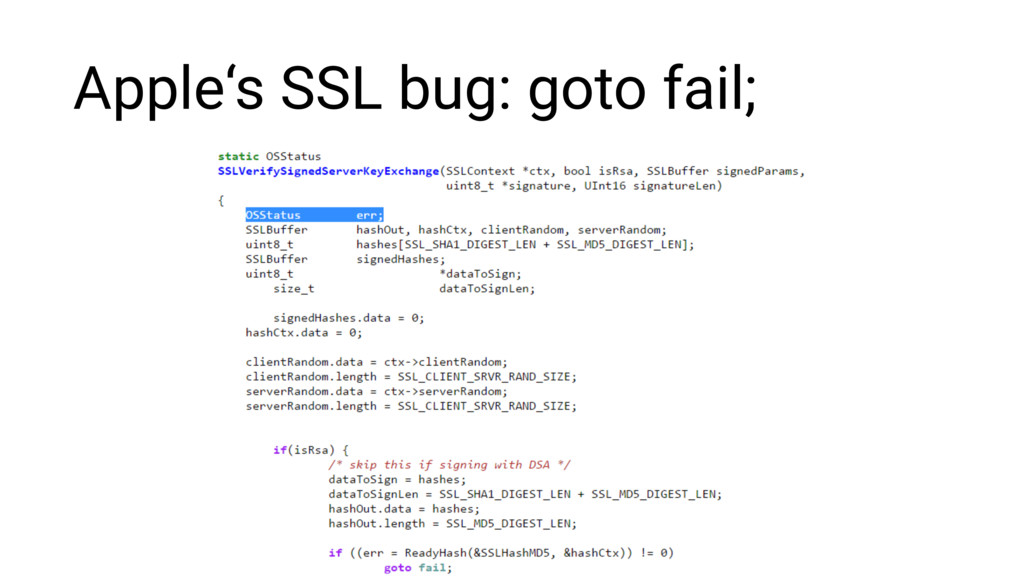
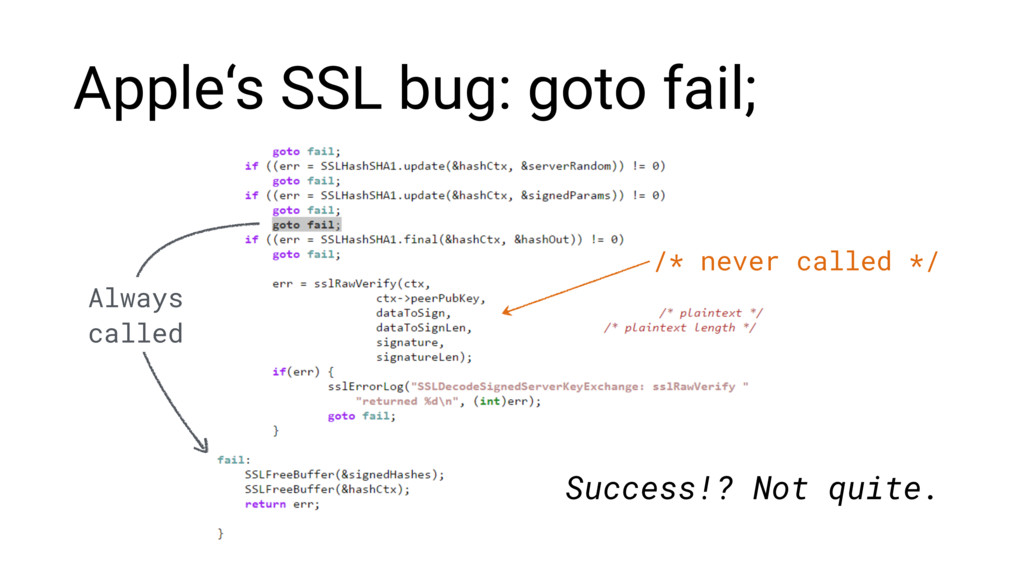
Apple‘s SSL bug: goto fail; Always called Success!? Not quite.
/* never called */ -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Probably all security vulnerabilities are caused by poor, negligent or just plain unsafe programming! 11 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
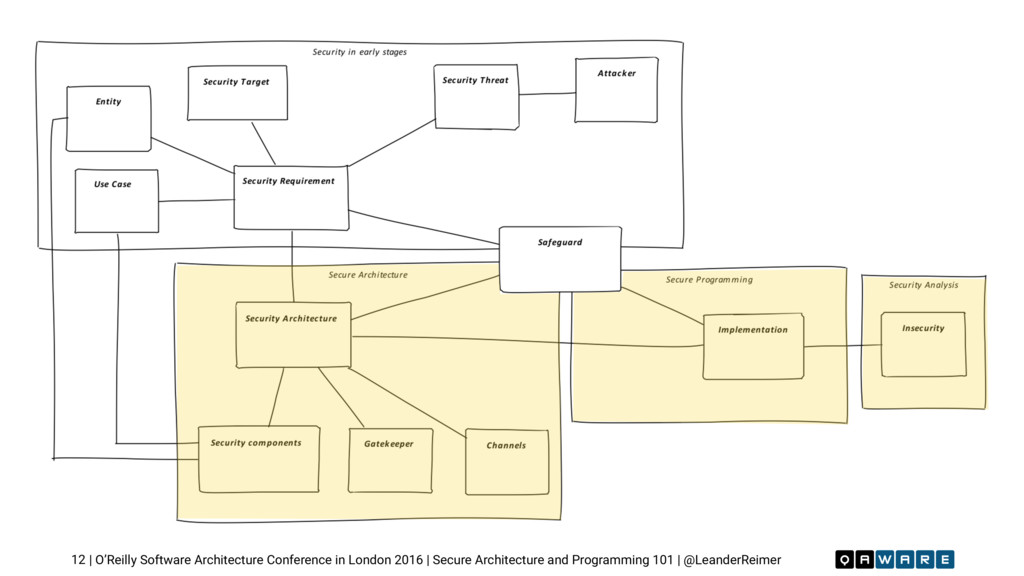
Architecture and Programming 101 | @LeanderReimer 12 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Know your attackers’ tools. • Have a look at http://sectools.org • Network scanners, Sniffers, Web Application Vulnerability Scanners, Exploit toolkits, Password crackers, … • Most of these security tools are freely available. • We can use some of these tools to test our own applications! • https://n0where.net/best-web-application-vulnerability-scanners/ 13 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer OWASP Zed Attack Proxy Demo. 14 https://www.owasp.org/index.php/OWASP_Zed_Attack_Proxy_Project -
| O’Reilly Software Architecture Conference in London 2016 | Secure
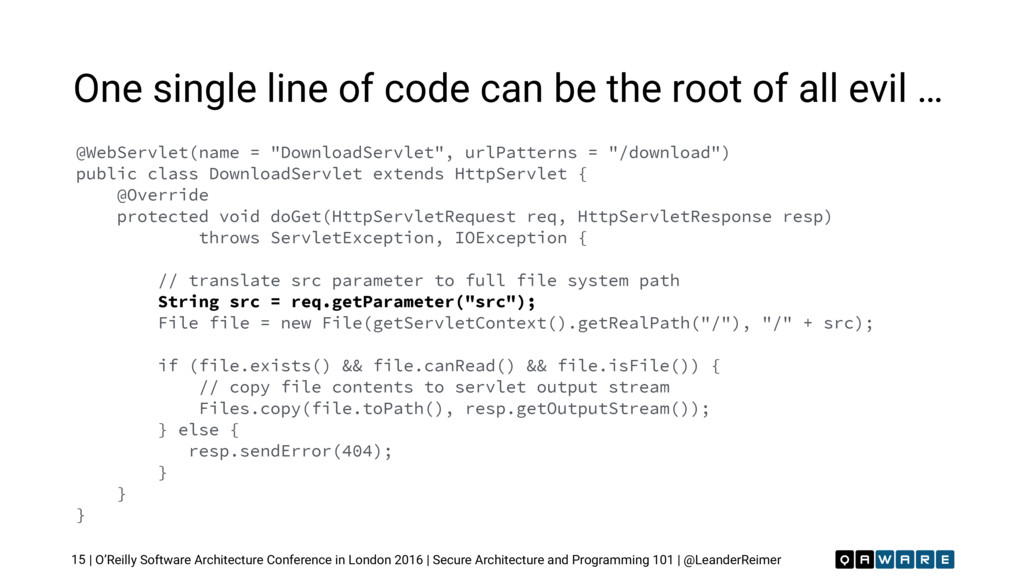
Architecture and Programming 101 | @LeanderReimer One single line of code can be the root of all evil … 15 @WebServlet(name = "DownloadServlet", urlPatterns = "/download") public class DownloadServlet extends HttpServlet { @Override protected void doGet(HttpServletRequest req, HttpServletResponse resp) throws ServletException, IOException { // translate src parameter to full file system path String src = req.getParameter("src"); File file = new File(getServletContext().getRealPath("/"), "/" + src); if (file.exists() && file.canRead() && file.isFile()) { // copy file contents to servlet output stream Files.copy(file.toPath(), resp.getOutputStream()); } else { resp.sendError(404); } } } -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer The OWASP Top 10 Security Risks. 16 A1-Injection A2-Broken Authentication and Session Management A3-Cross-Site Scripting (XSS) A4-Insecure Direct Object References A5-Security Misconfiguration A6-Sensitive Data Exposure A7-Missing Function Level Access Control A8-Cross-Site Request Forgery (CSRF) A9-Using Components with known Vulnerabilities A10- Unvalidated Redirects and https://www.owasp.org/index.php/Top_10_2013-Top_10 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer How can we do better? 17 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
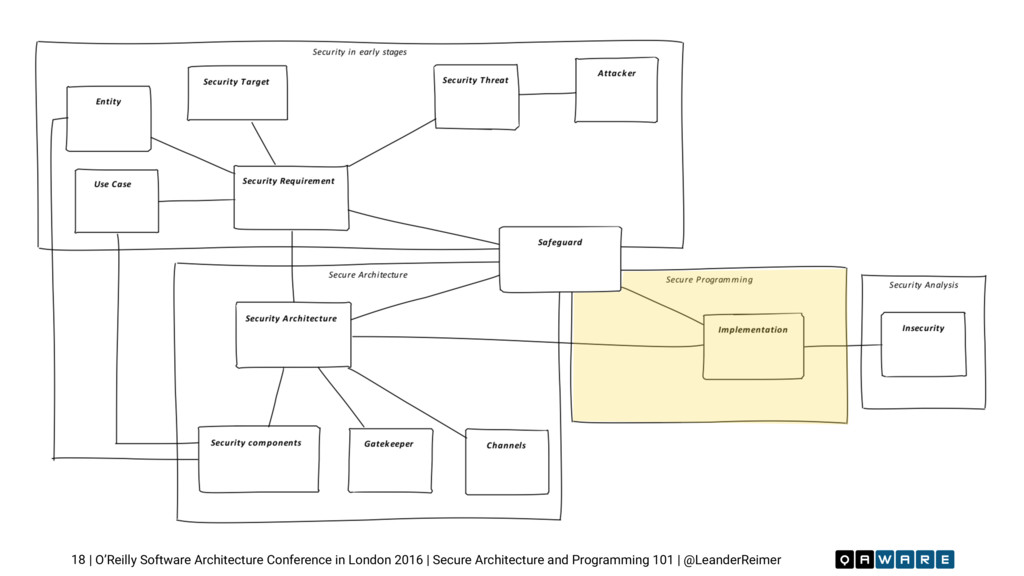
Architecture and Programming 101 | @LeanderReimer 18 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
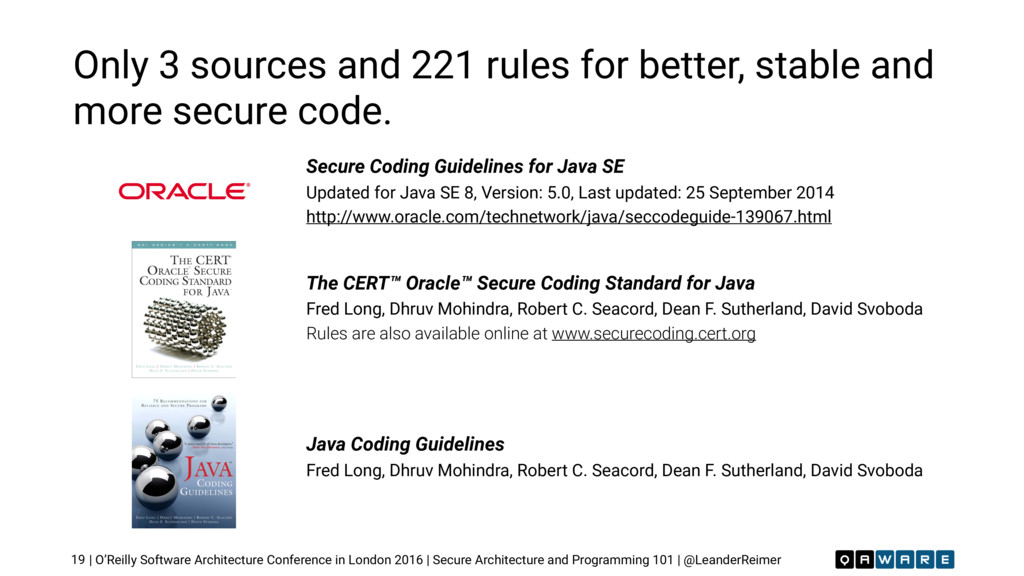
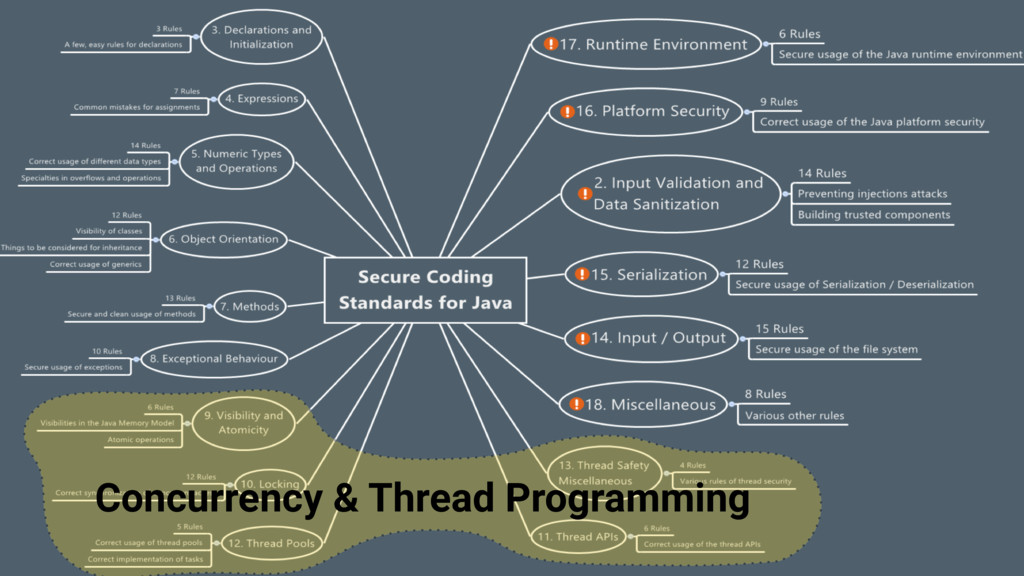
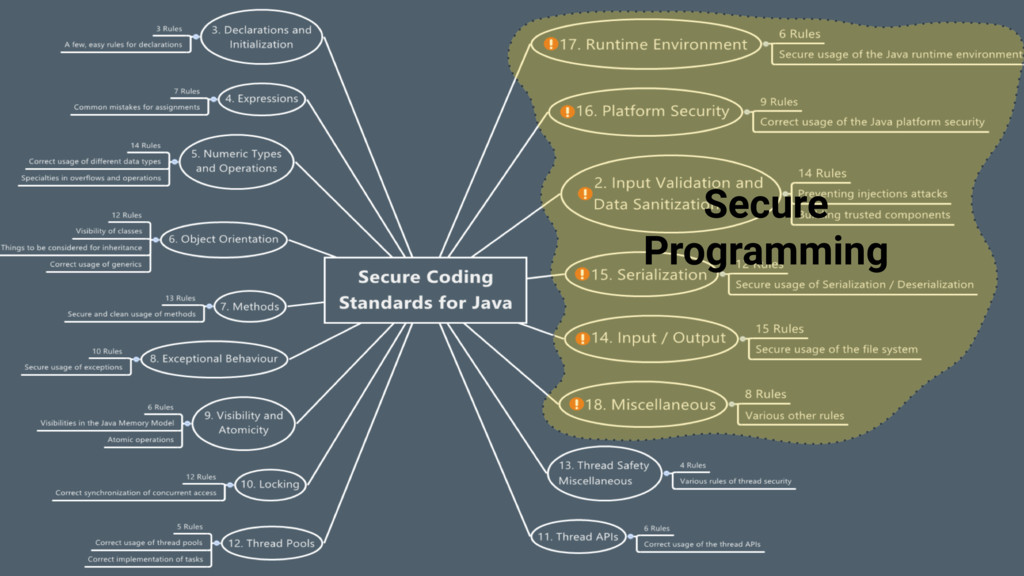
Architecture and Programming 101 | @LeanderReimer Only 3 sources and 221 rules for better, stable and more secure code. 19 Secure Coding Guidelines for Java SE Updated for Java SE 8, Version: 5.0, Last updated: 25 September 2014 http://www.oracle.com/technetwork/java/seccodeguide-139067.html The CERT™ Oracle™ Secure Coding Standard for Java Fred Long, Dhruv Mohindra, Robert C. Seacord, Dean F. Sutherland, David Svoboda Rules are also available online at www.securecoding.cert.org Java Coding Guidelines Fred Long, Dhruv Mohindra, Robert C. Seacord, Dean F. Sutherland, David Svoboda -
| O’Reilly Software Architecture Conference in London 2016 | Secure
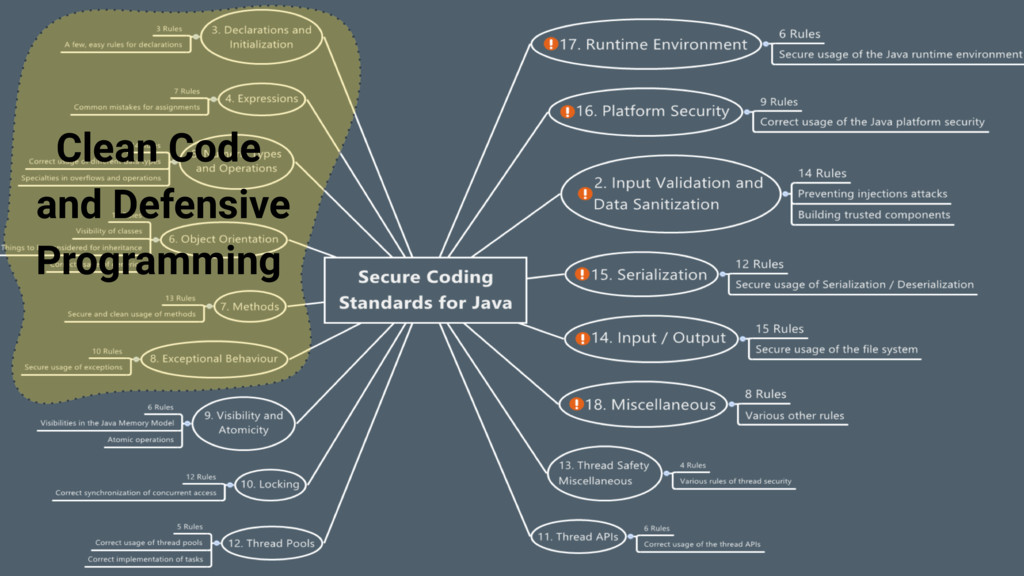
Architecture and Programming 101 | @LeanderReimer Practice good software craftsmanship. • Take pride in what you do and build. • Follow clean code principles. Program defensively. • Perform regular peer reviews. • Constantly measure software quality. • Make your software quality omnipresent. 22 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
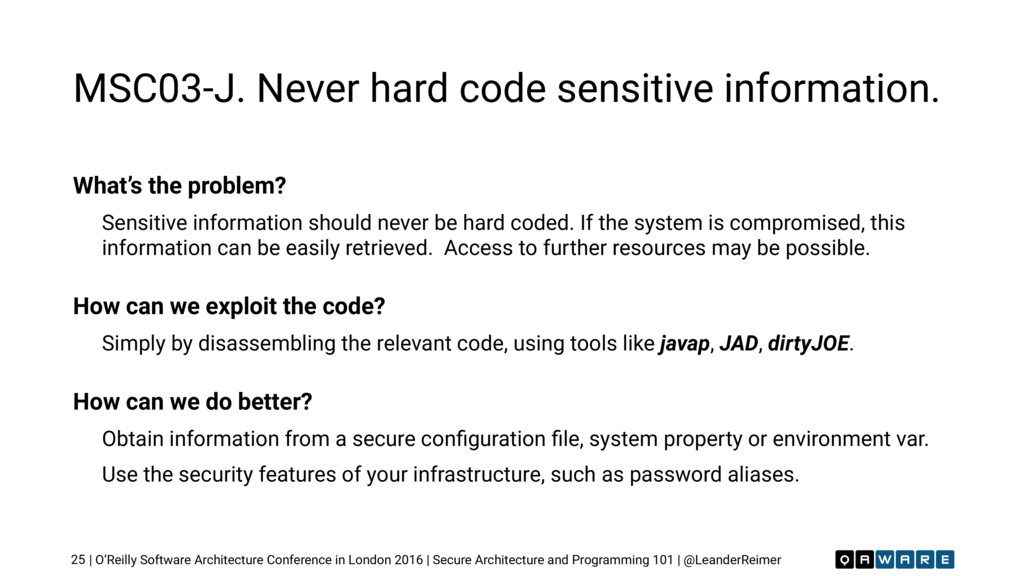
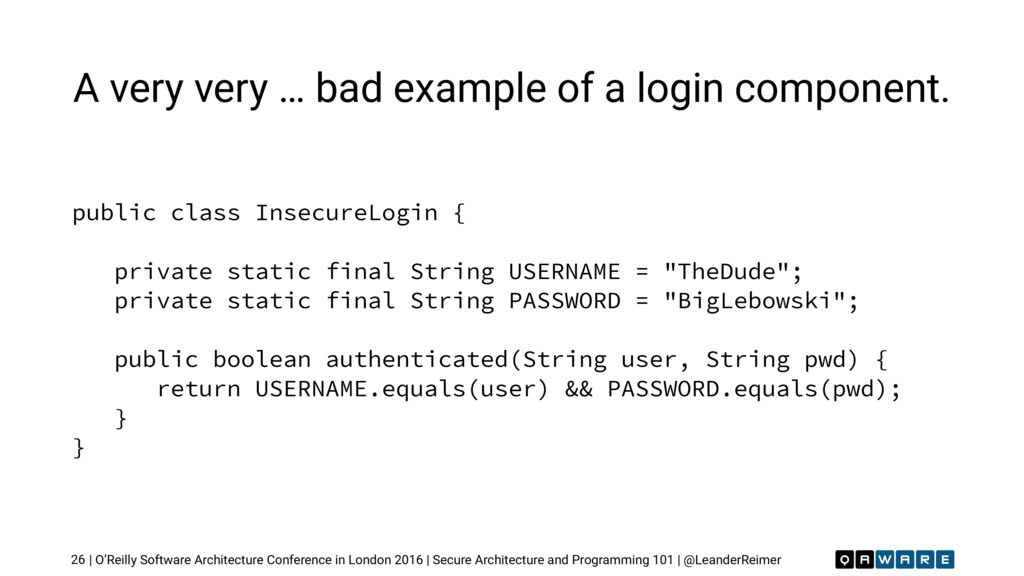
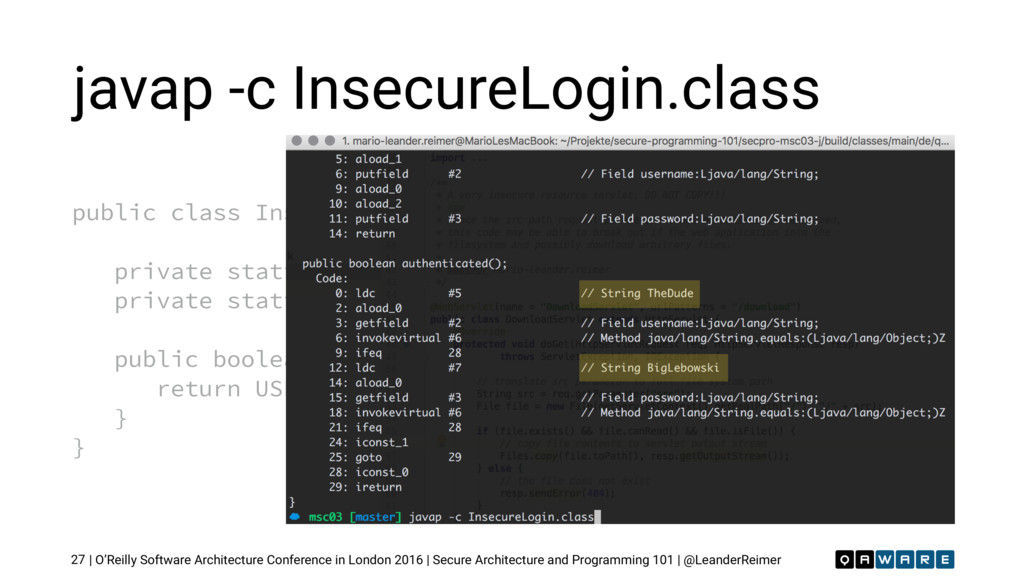
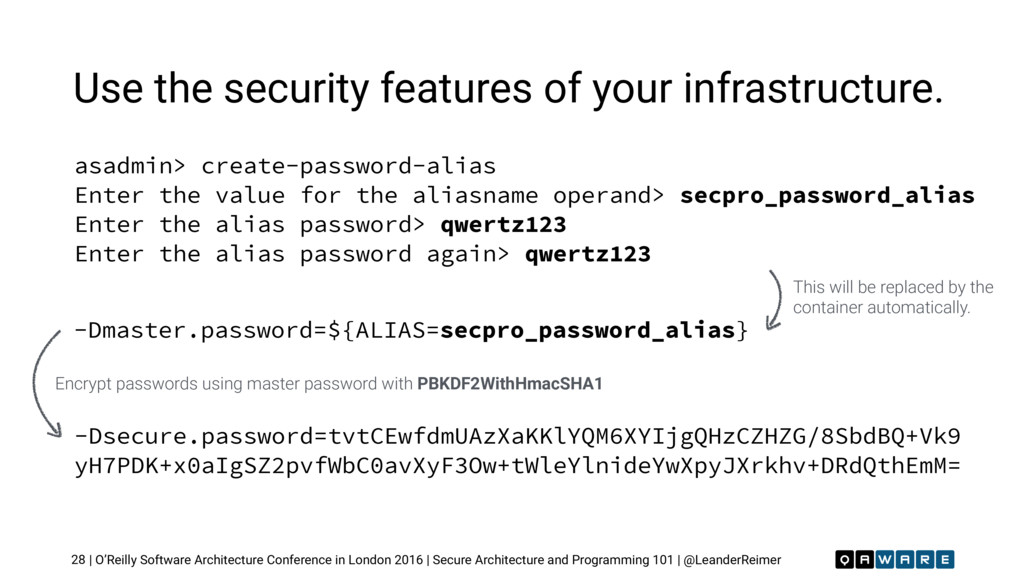
Architecture and Programming 101 | @LeanderReimer MSC03-J. Never hard code sensitive information. What’s the problem? Sensitive information should never be hard coded. If the system is compromised, this information can be easily retrieved. Access to further resources may be possible. How can we exploit the code? Simply by disassembling the relevant code, using tools like javap, JAD, dirtyJOE. How can we do better? Obtain information from a secure configuration file, system property or environment var. Use the security features of your infrastructure, such as password aliases. 25 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer A very very … bad example of a login component. 26 public class InsecureLogin { private static final String USERNAME = "TheDude"; private static final String PASSWORD = "BigLebowski"; public boolean authenticated(String user, String pwd) { return USERNAME.equals(user) && PASSWORD.equals(pwd); } } -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer javap -c InsecureLogin.class 27 public class InsecureLogin { private static final String USERNAME = "TheDude"; private static final String PASSWORD = "BigLebowski"; public boolean authenticated(String user, String pwd) { return USERNAME.equals(user) && PASSWORD.equals(pwd); } } -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Use the security features of your infrastructure. 28 asadmin> create-password-alias Enter the value for the aliasname operand> secpro_password_alias Enter the alias password> qwertz123 Enter the alias password again> qwertz123 -Dmaster.password=${ALIAS=secpro_password_alias} -Dsecure.password=tvtCEwfdmUAzXaKKlYQM6XYIjgQHzCZHZG/8SbdBQ+Vk9 yH7PDK+x0aIgSZ2pvfWbC0avXyF3Ow+tWleYlnideYwXpyJXrkhv+DRdQthEmM= This will be replaced by the container automatically. Encrypt passwords using master password with PBKDF2WithHmacSHA1 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
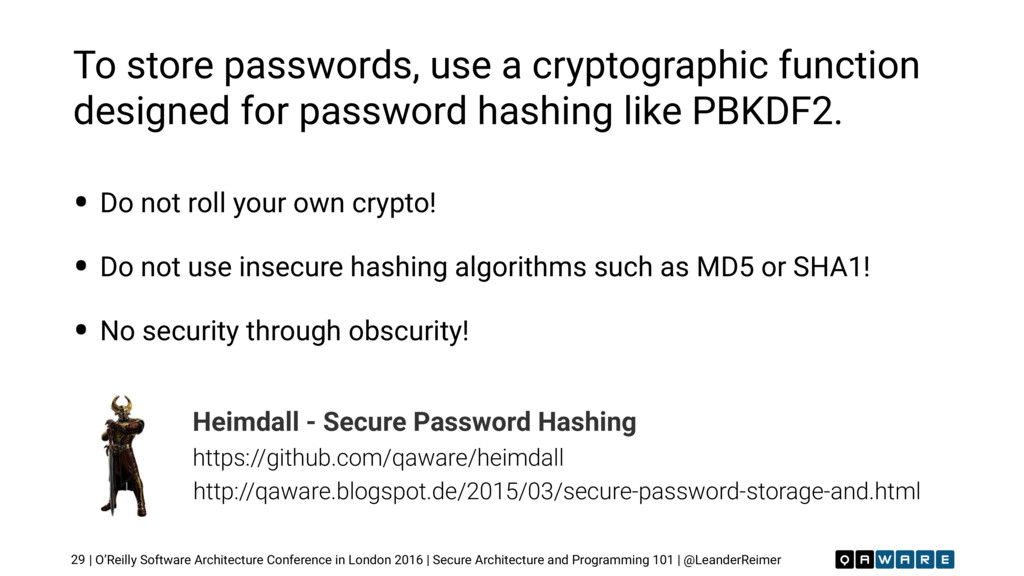
Architecture and Programming 101 | @LeanderReimer To store passwords, use a cryptographic function designed for password hashing like PBKDF2. • Do not roll your own crypto! • Do not use insecure hashing algorithms such as MD5 or SHA1! • No security through obscurity! 29 Heimdall - Secure Password Hashing https://github.com/qaware/heimdall http://qaware.blogspot.de/2015/03/secure-password-storage-and.html -
| O’Reilly Software Architecture Conference in London 2016 | Secure
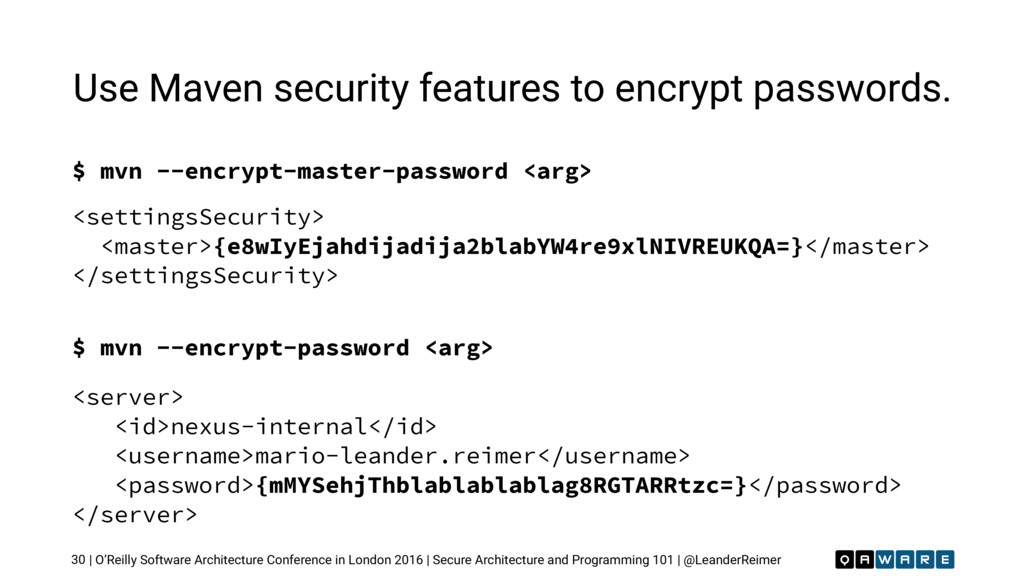
Architecture and Programming 101 | @LeanderReimer Use Maven security features to encrypt passwords. 30 <server> <id>nexus-internal</id> <username>mario-leander.reimer</username> <password>{mMYSehjThblablablablag8RGTARRtzc=}</password> </server> <settingsSecurity> <master>{e8wIyEjahdijadija2blabYW4re9xlNIVREUKQA=}</master> </settingsSecurity> $ mvn --encrypt-master-password <arg> $ mvn --encrypt-password <arg> -
| O’Reilly Software Architecture Conference in London 2016 | Secure
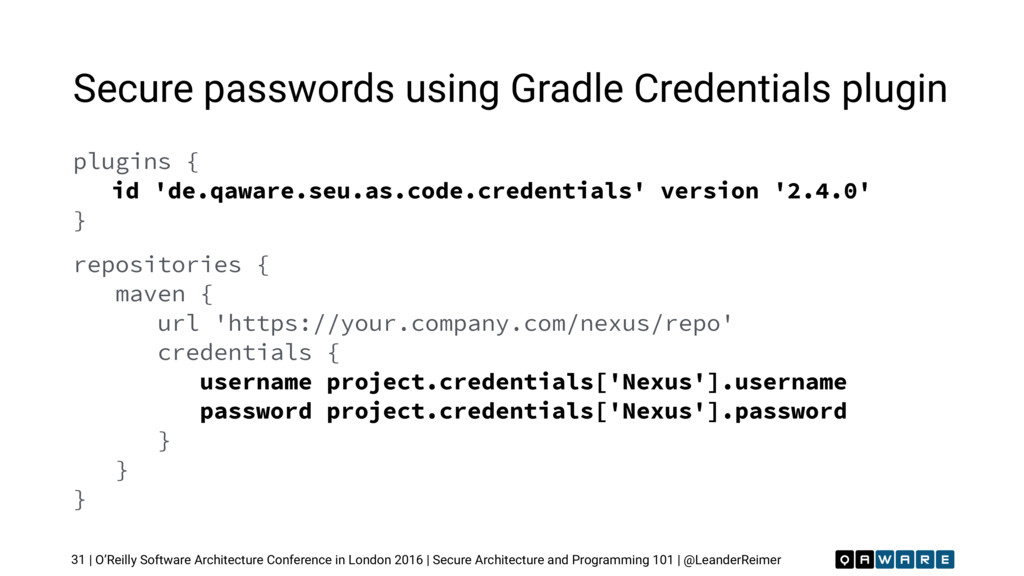
Architecture and Programming 101 | @LeanderReimer Secure passwords using Gradle Credentials plugin 31 plugins { id 'de.qaware.seu.as.code.credentials' version '2.4.0' } repositories { maven { url 'https://your.company.com/nexus/repo' credentials { username project.credentials['Nexus'].username password project.credentials['Nexus'].password } } } -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer 32 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Only up to 10% of the overall bytecode instructions in modern JEE applications are your code!!! 33 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer About 26% of the downloaded libraries on Maven Central contain known vulnerabilities! 34 https://www.owasp.org/index.php/OWASP_AppSec_DC_2012/The_Unfortunate_Reality_of_Insecure_Libraries -
| O’Reilly Software Architecture Conference in London 2016 | Secure
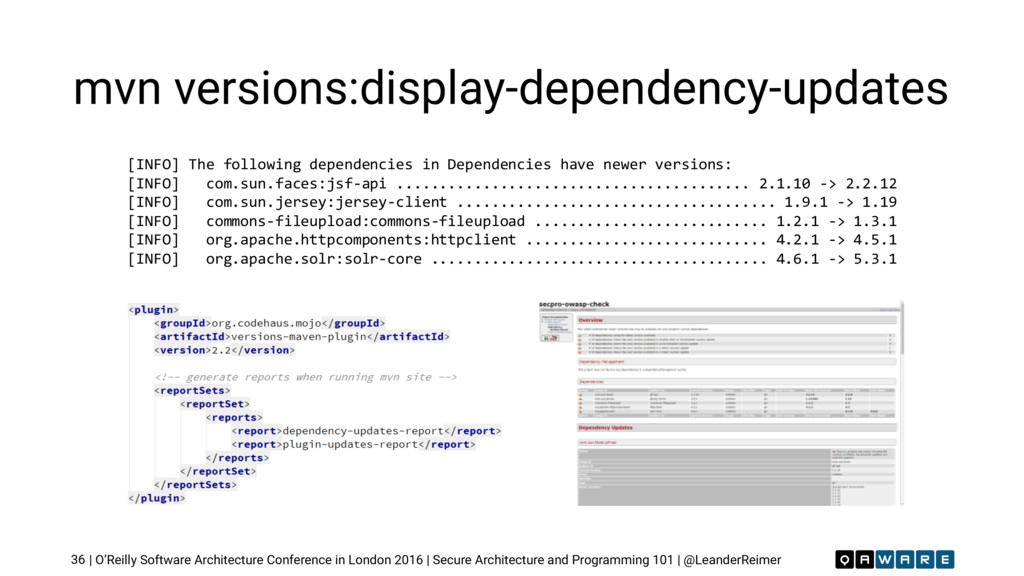
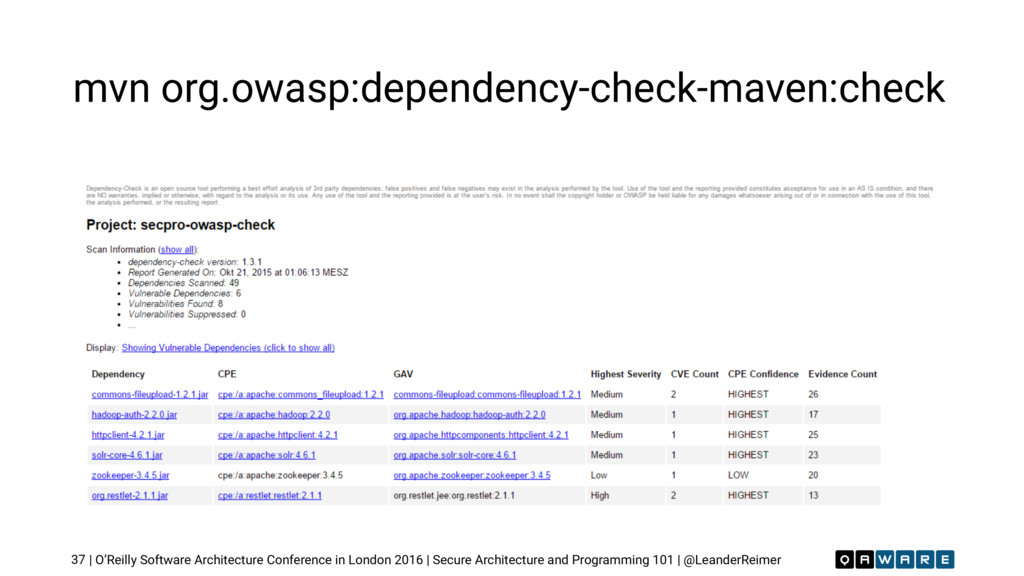
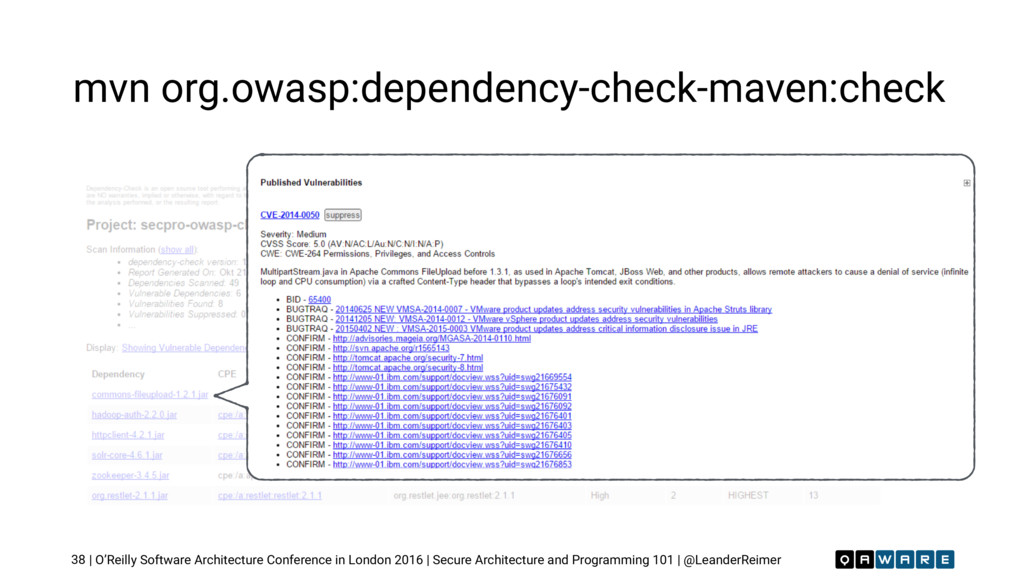
Architecture and Programming 101 | @LeanderReimer Know your dependencies! The secure usage of open source components and frameworks is key to application security. • How to secure an application against security issues in OSS? • Upgrading your dependencies to the latest versions is crucial. Urgent security fixes are usually only applied to the latest release. • Monitor security issues of used frameworks in public databases (CVE, NVD) and mailing lists. • Implement security decorators to disable or secure weak and unused framework functionality. 35 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer mvn versions:display-dependency-updates 36 [INFO] The following dependencies in Dependencies have newer versions: [INFO] com.sun.faces:jsf-api ......................................... 2.1.10 -> 2.2.12 [INFO] com.sun.jersey:jersey-client ..................................... 1.9.1 -> 1.19 [INFO] commons-fileupload:commons-fileupload ........................... 1.2.1 -> 1.3.1 [INFO] org.apache.httpcomponents:httpclient ............................ 4.2.1 -> 4.5.1 [INFO] org.apache.solr:solr-core ....................................... 4.6.1 -> 5.3.1 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer mvn org.owasp:dependency-check-maven:check 37 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer mvn org.owasp:dependency-check-maven:check 38 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
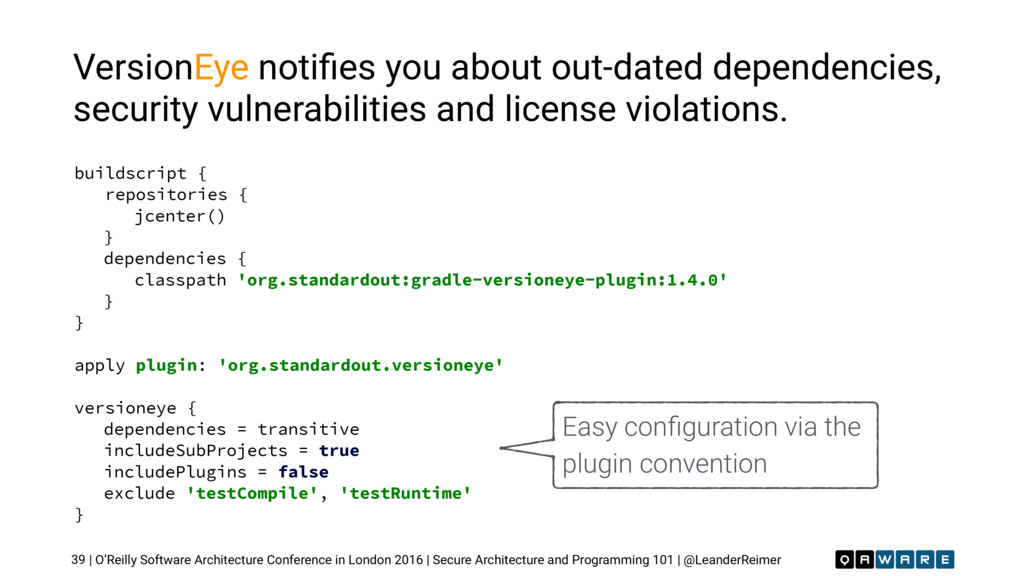
Architecture and Programming 101 | @LeanderReimer VersionEye notifies you about out-dated dependencies, security vulnerabilities and license violations. 39 buildscript { repositories { jcenter() } dependencies { classpath 'org.standardout:gradle-versioneye-plugin:1.4.0' } } apply plugin: 'org.standardout.versioneye' versioneye { dependencies = transitive includeSubProjects = true includePlugins = false exclude 'testCompile', 'testRuntime' } Easy configuration via the plugin convention -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer A quick VersionEye overview. 40 https://www.versioneye.com/user/projects/57af1de9b56d6b001694ab24 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
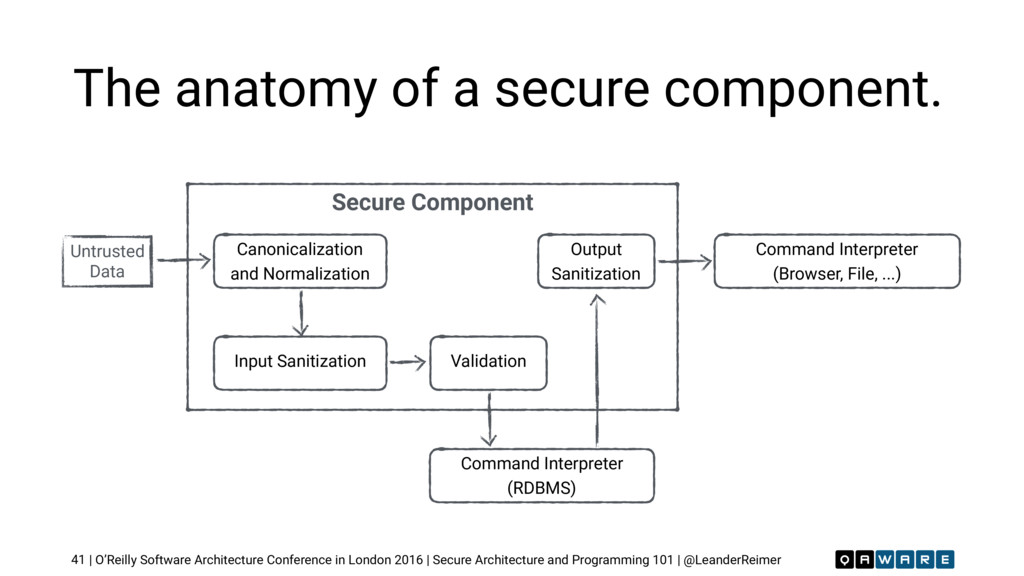
Architecture and Programming 101 | @LeanderReimer The anatomy of a secure component. 41 Secure Component Canonicalization and Normalization Input Sanitization Validation Output Sanitization Command Interpreter (RDBMS) Command Interpreter (Browser, File, ...) Untrusted Data -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer The internal design of secure components is influenced by security concerns. But the business logic should stay clean. 42 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
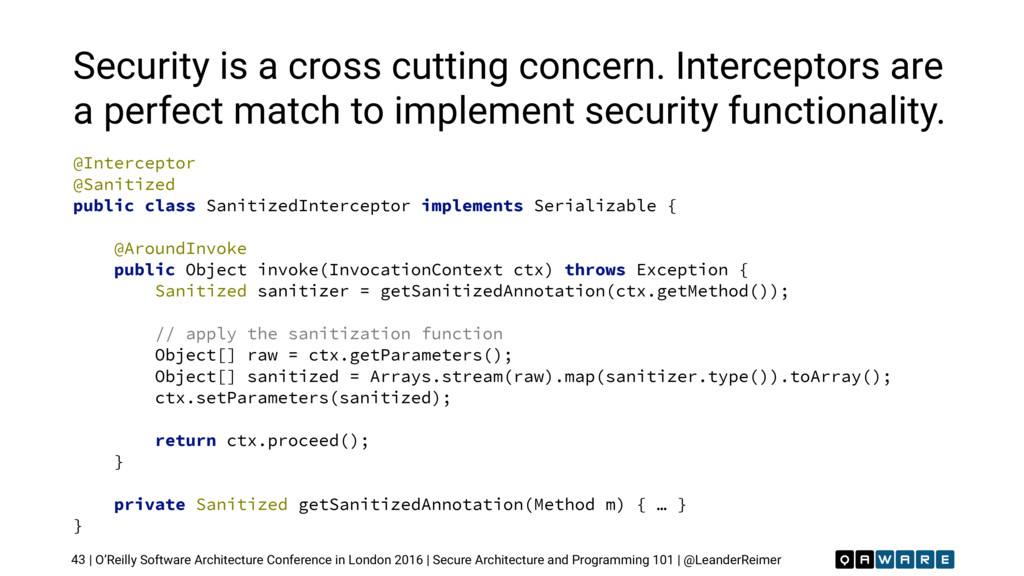
Architecture and Programming 101 | @LeanderReimer Security is a cross cutting concern. Interceptors are a perfect match to implement security functionality. 43 @Interceptor @Sanitized public class SanitizedInterceptor implements Serializable { @AroundInvoke public Object invoke(InvocationContext ctx) throws Exception { Sanitized sanitizer = getSanitizedAnnotation(ctx.getMethod()); // apply the sanitization function Object[] raw = ctx.getParameters(); Object[] sanitized = Arrays.stream(raw).map(sanitizer.type()).toArray(); ctx.setParameters(sanitized); return ctx.proceed(); } private Sanitized getSanitizedAnnotation(Method m) { … } } -
| O’Reilly Software Architecture Conference in London 2016 | Secure
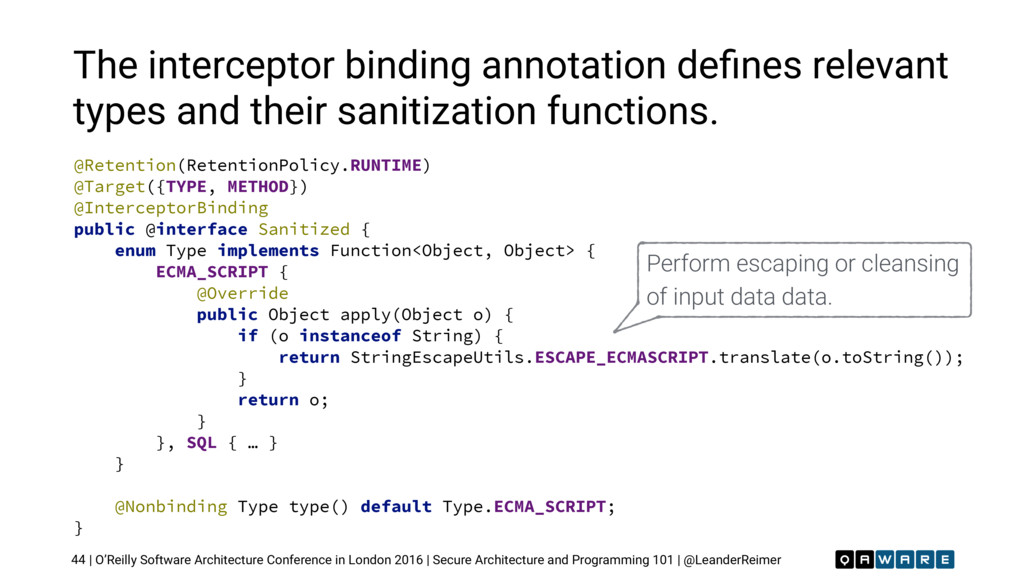
Architecture and Programming 101 | @LeanderReimer The interceptor binding annotation defines relevant types and their sanitization functions. 44 @Retention(RetentionPolicy.RUNTIME) @Target({TYPE, METHOD}) @InterceptorBinding public @interface Sanitized { enum Type implements Function<Object, Object> { ECMA_SCRIPT { @Override public Object apply(Object o) { if (o instanceof String) { return StringEscapeUtils.ESCAPE_ECMASCRIPT.translate(o.toString()); } return o; } }, SQL { … } } @Nonbinding Type type() default Type.ECMA_SCRIPT; } Perform escaping or cleansing of input data data. -
| O’Reilly Software Architecture Conference in London 2016 | Secure
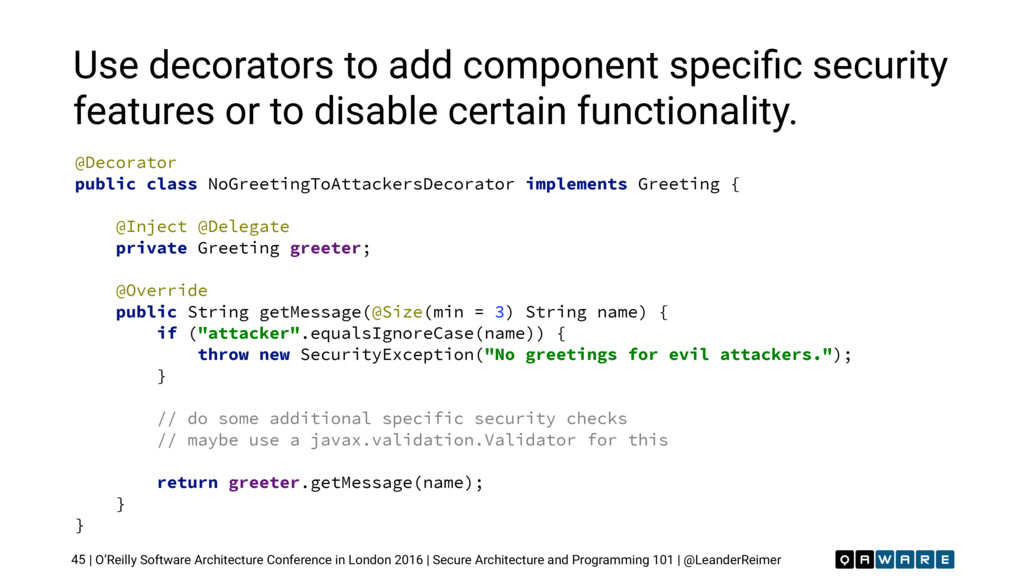
Architecture and Programming 101 | @LeanderReimer Use decorators to add component specific security features or to disable certain functionality. 45 @Decorator public class NoGreetingToAttackersDecorator implements Greeting { @Inject @Delegate private Greeting greeter; @Override public String getMessage(@Size(min = 3) String name) { if ("attacker".equalsIgnoreCase(name)) { throw new SecurityException("No greetings for evil attackers."); } // do some additional specific security checks // maybe use a javax.validation.Validator for this return greeter.getMessage(name); } } -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Apply Design by Contract (DbC) to your gate keeper and security components using the method validation API. 46 public interface Greeting { /** * @param name the name, at least 3 characters * @return the greeting message, never null */ @NotNull String getMessage(@Size(min = 3) String name); } @ApplicationScoped public class DefaultGreeting implements Greeting { @Override @NotNull public String getMessage(@Size(min = 3) String name) { return format("Hello %s!", name); } } Interface-as-a-Contract Defines pre and post conditions of a method using annotations. -
| O’Reilly Software Architecture Conference in London 2016 | Secure
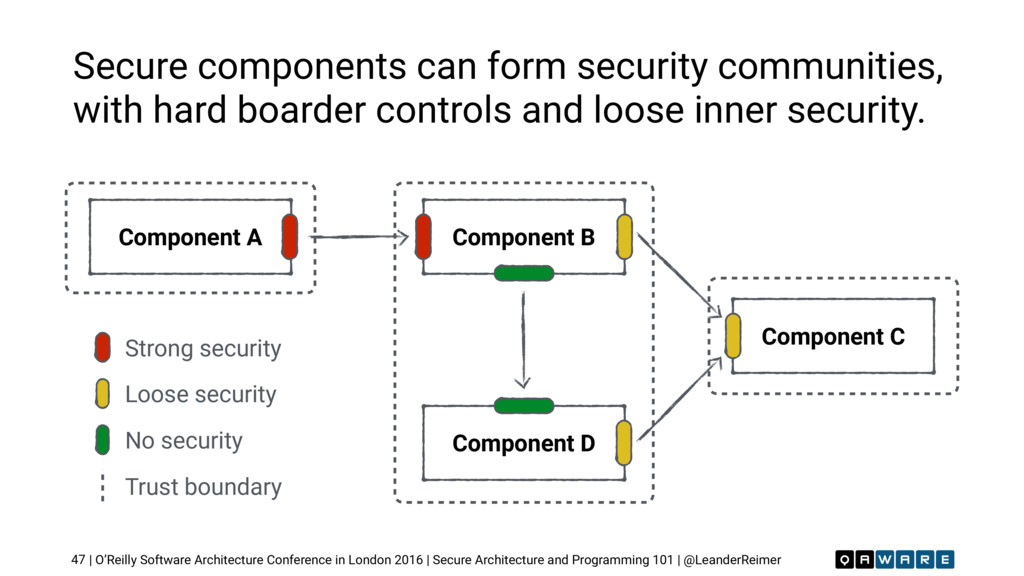
Architecture and Programming 101 | @LeanderReimer Secure components can form security communities, with hard boarder controls and loose inner security. 47 Component A Component B Component D Component C Strong security Loose security No security Trust boundary -
| O’Reilly Software Architecture Conference in London 2016 | Secure
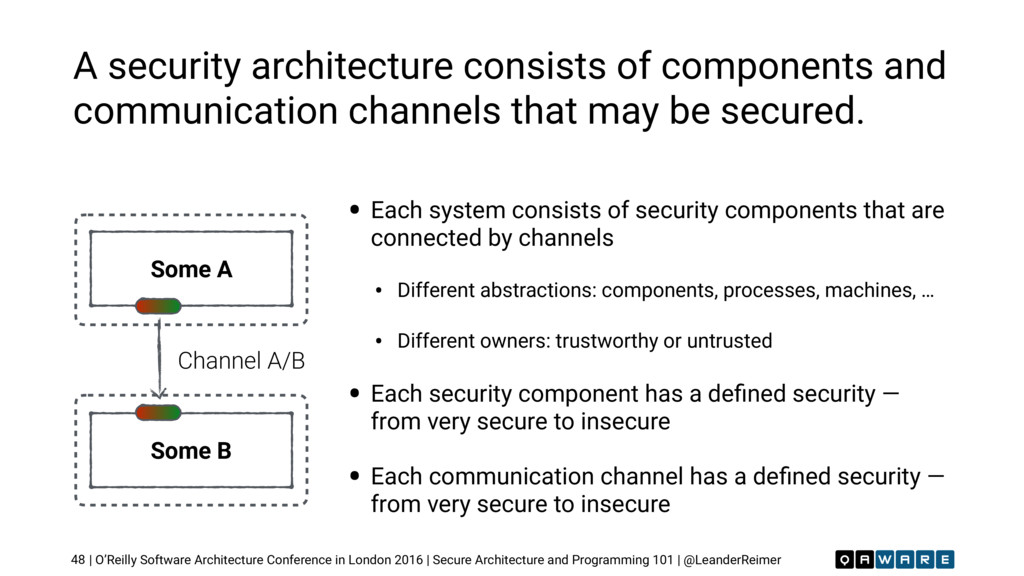
Architecture and Programming 101 | @LeanderReimer A security architecture consists of components and communication channels that may be secured. • Each system consists of security components that are connected by channels • Different abstractions: components, processes, machines, … • Different owners: trustworthy or untrusted • Each security component has a defined security — from very secure to insecure • Each communication channel has a defined security — from very secure to insecure 48 Some A Some B Channel A/B -
| O’Reilly Software Architecture Conference in London 2016 | Secure
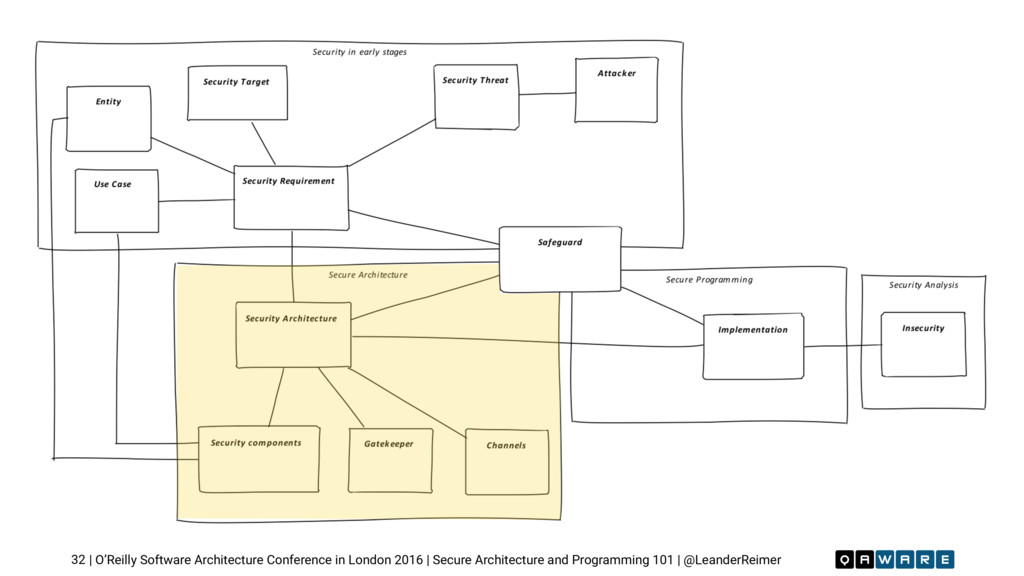
Architecture and Programming 101 | @LeanderReimer The security architecture of a system describes how the ordinary architecture is secured at different levels. 49 Secure Technical Infrastructure Technical Infrastructure Technical Architecture Secure Technical Architecture Application Architecture Secure Application Architecture Security Architecture Security Requirements Security Targets Security Targets -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer There is no 100% security. 50 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer It`s up to us developers and architects to build secure systems! 51 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
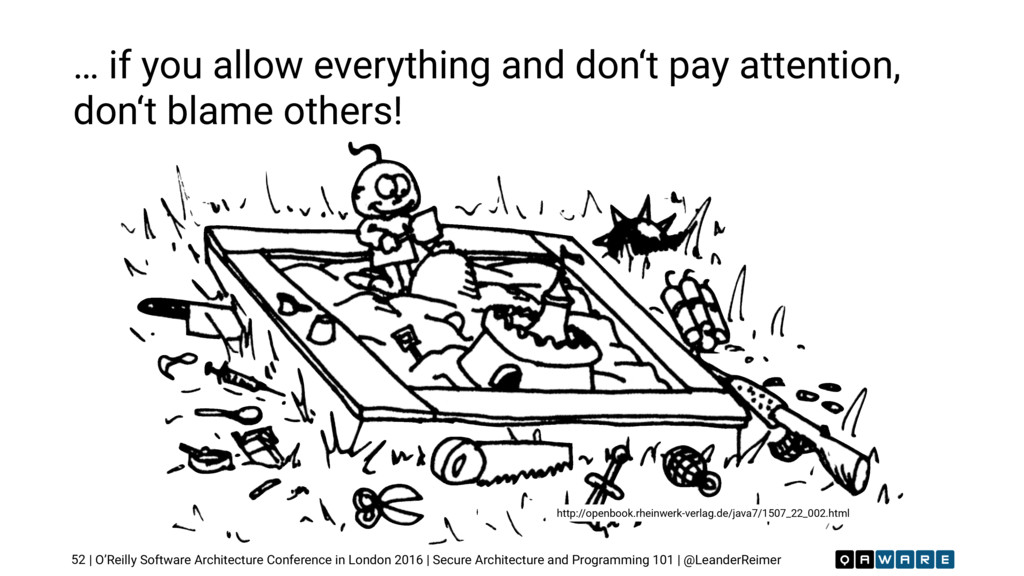
Architecture and Programming 101 | @LeanderReimer … if you allow everything and don‘t pay attention, don‘t blame others! 52 http://openbook.rheinwerk-verlag.de/java7/1507_22_002.html -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Incorporate security into your daily development process. 53 -
| O’Reilly Software Architecture Conference in London 2016 | Secure
Architecture and Programming 101 | @LeanderReimer Pay your employees well! Cater for a good work environment! 54