AWS Well-Arhitected Frameworkセキュリティの柱 について
Sponsored
·
 Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→

Share
Embed
AWS Well-Arhitected Frameworkセキュリティの柱 について

Kazuki Miura PRO
November 19, 2026
Transcript
66 slides
-
AWS Well-Architected Framework AWS Well-Arhitected Framework セキュリティの柱について Event Media-JAWS【第23回】 Date
2026.11.19 Speaker 株式会社ヘプタゴン 三浦 一樹 -
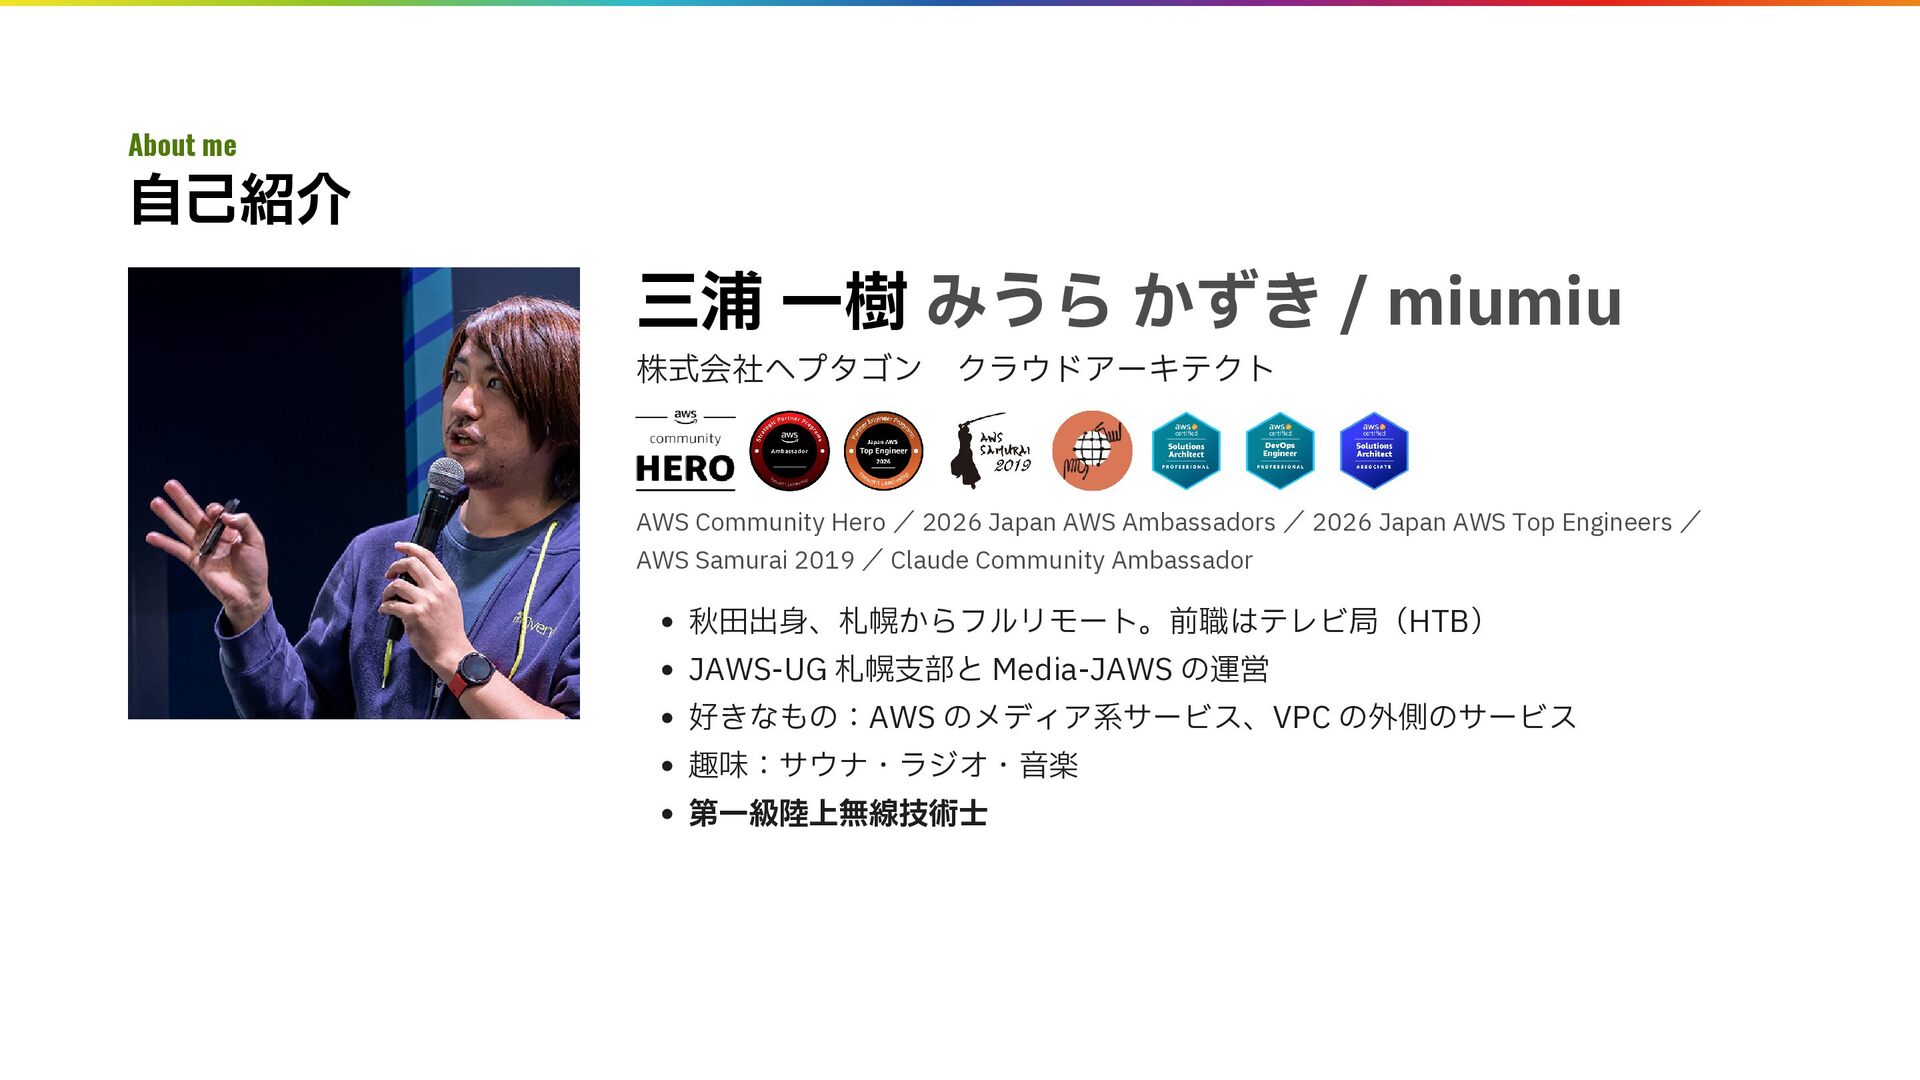
About me 自己紹介 三浦 一樹 みうら かずき / miumiu 株式会社ヘプタゴン
クラウドアーキテクト AWS Community Hero / 2026 Japan AWS Ambassadors / 2026 Japan AWS Top Engineers / AWS Samurai 2019 / Claude Community Ambassador 秋田出身、札幌からフルリモート。前職はテレビ局(HTB) JAWS-UG 札幌支部と Media-JAWS の運営 好きなもの:AWS のメディア系サービス、VPC の外側のサービス 趣味:サウナ・ラジオ・音楽 第一級陸上無線技術士 -
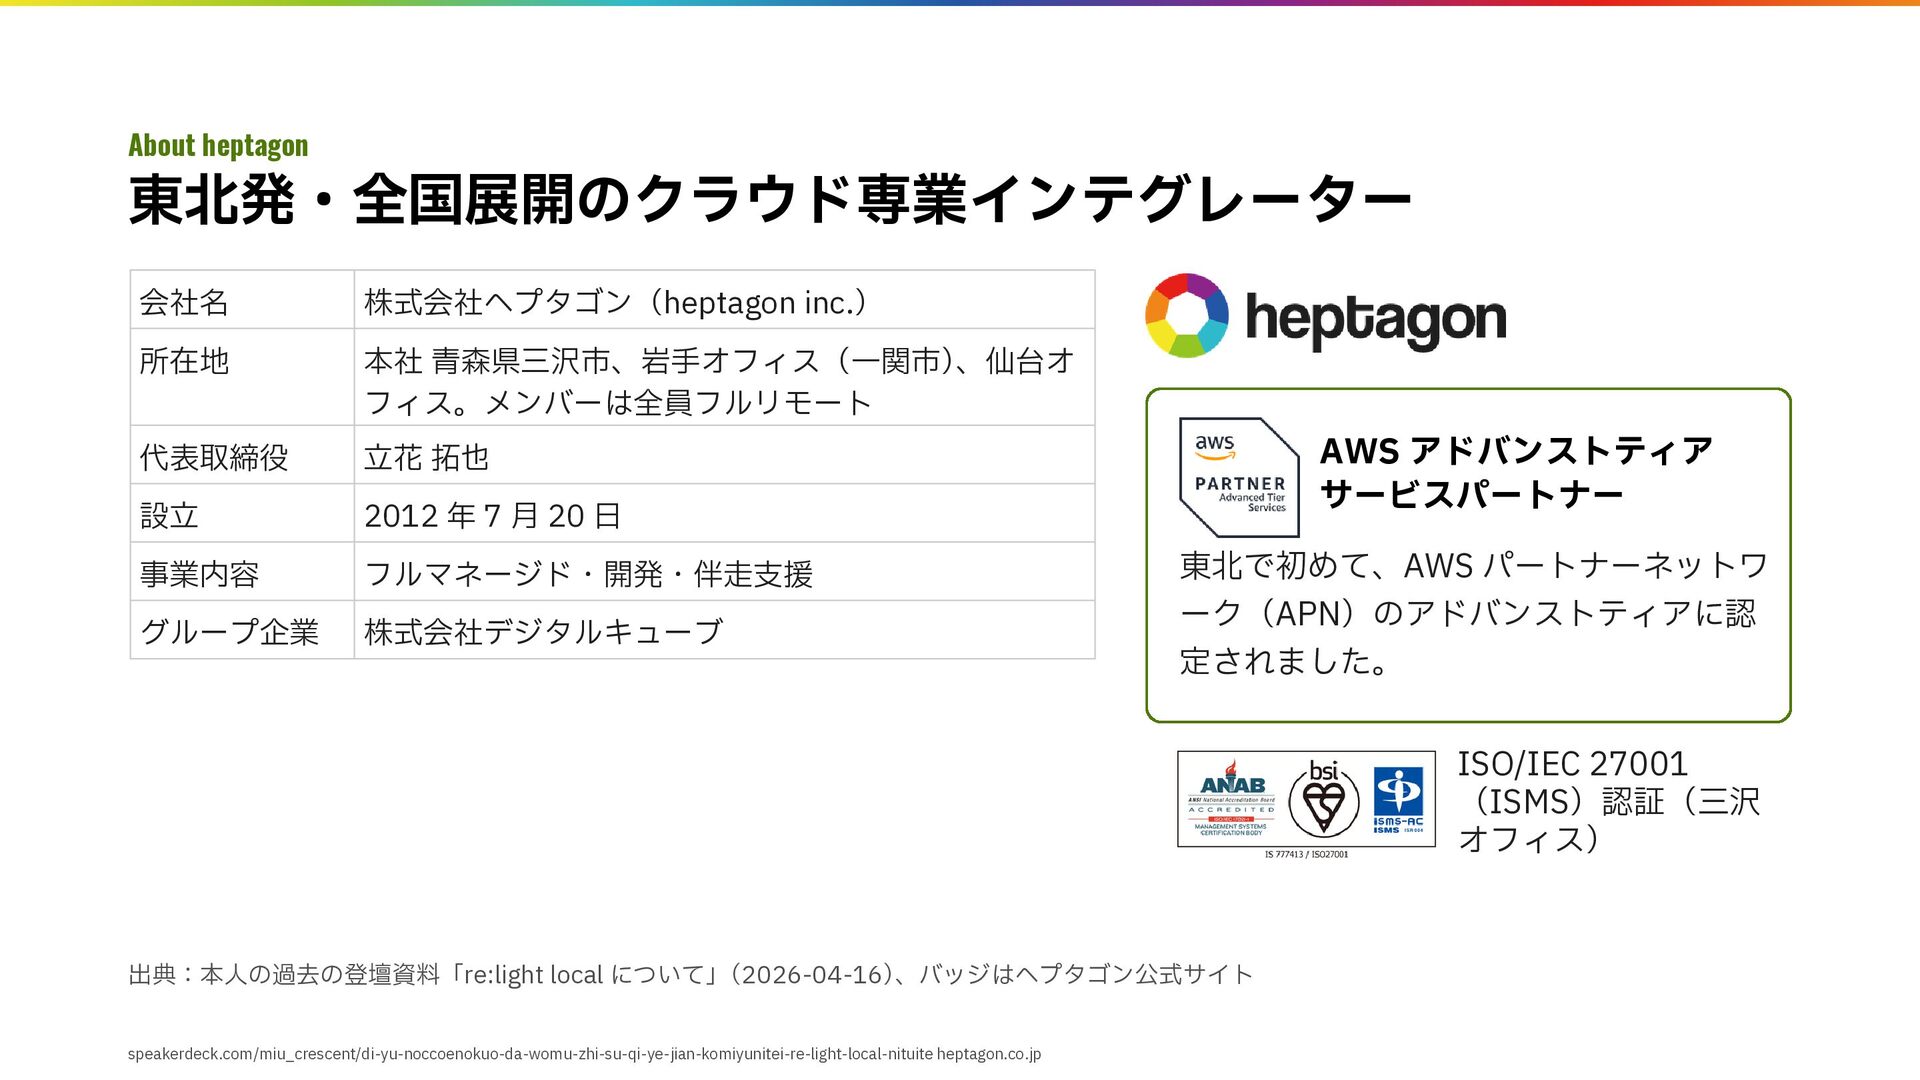
About heptagon 東北発・全国展開のクラウド専業インテグレーター 会社名 株式会社ヘプタゴン(heptagon inc.) 所在地 本社 青森県三沢市、岩手オフィス(一関市) 、仙台オ
フィス。メンバーは全員フルリモート 代表取締役 立花 拓也 設立 2012 年 7 月 20 日 事業内容 フルマネージド・開発・伴走支援 グループ企業 株式会社デジタルキューブ AWS アドバンストティア サービスパートナー 東北で初めて、AWS パートナーネットワ ーク(APN)のアドバンストティアに認 定されました。 ISO/IEC 27001 (ISMS)認証(三沢 オフィス) 出典:本人の過去の登壇資料「re:light local について」 (2026-04-16) 、バッジはヘプタゴン公式サイト speakerdeck.com/miu_crescent/di-yu-noccoenokuo-da-womu-zhi-su-qi-ye-jian-komiyunitei-re-light-local-nituite heptagon.co.jp -
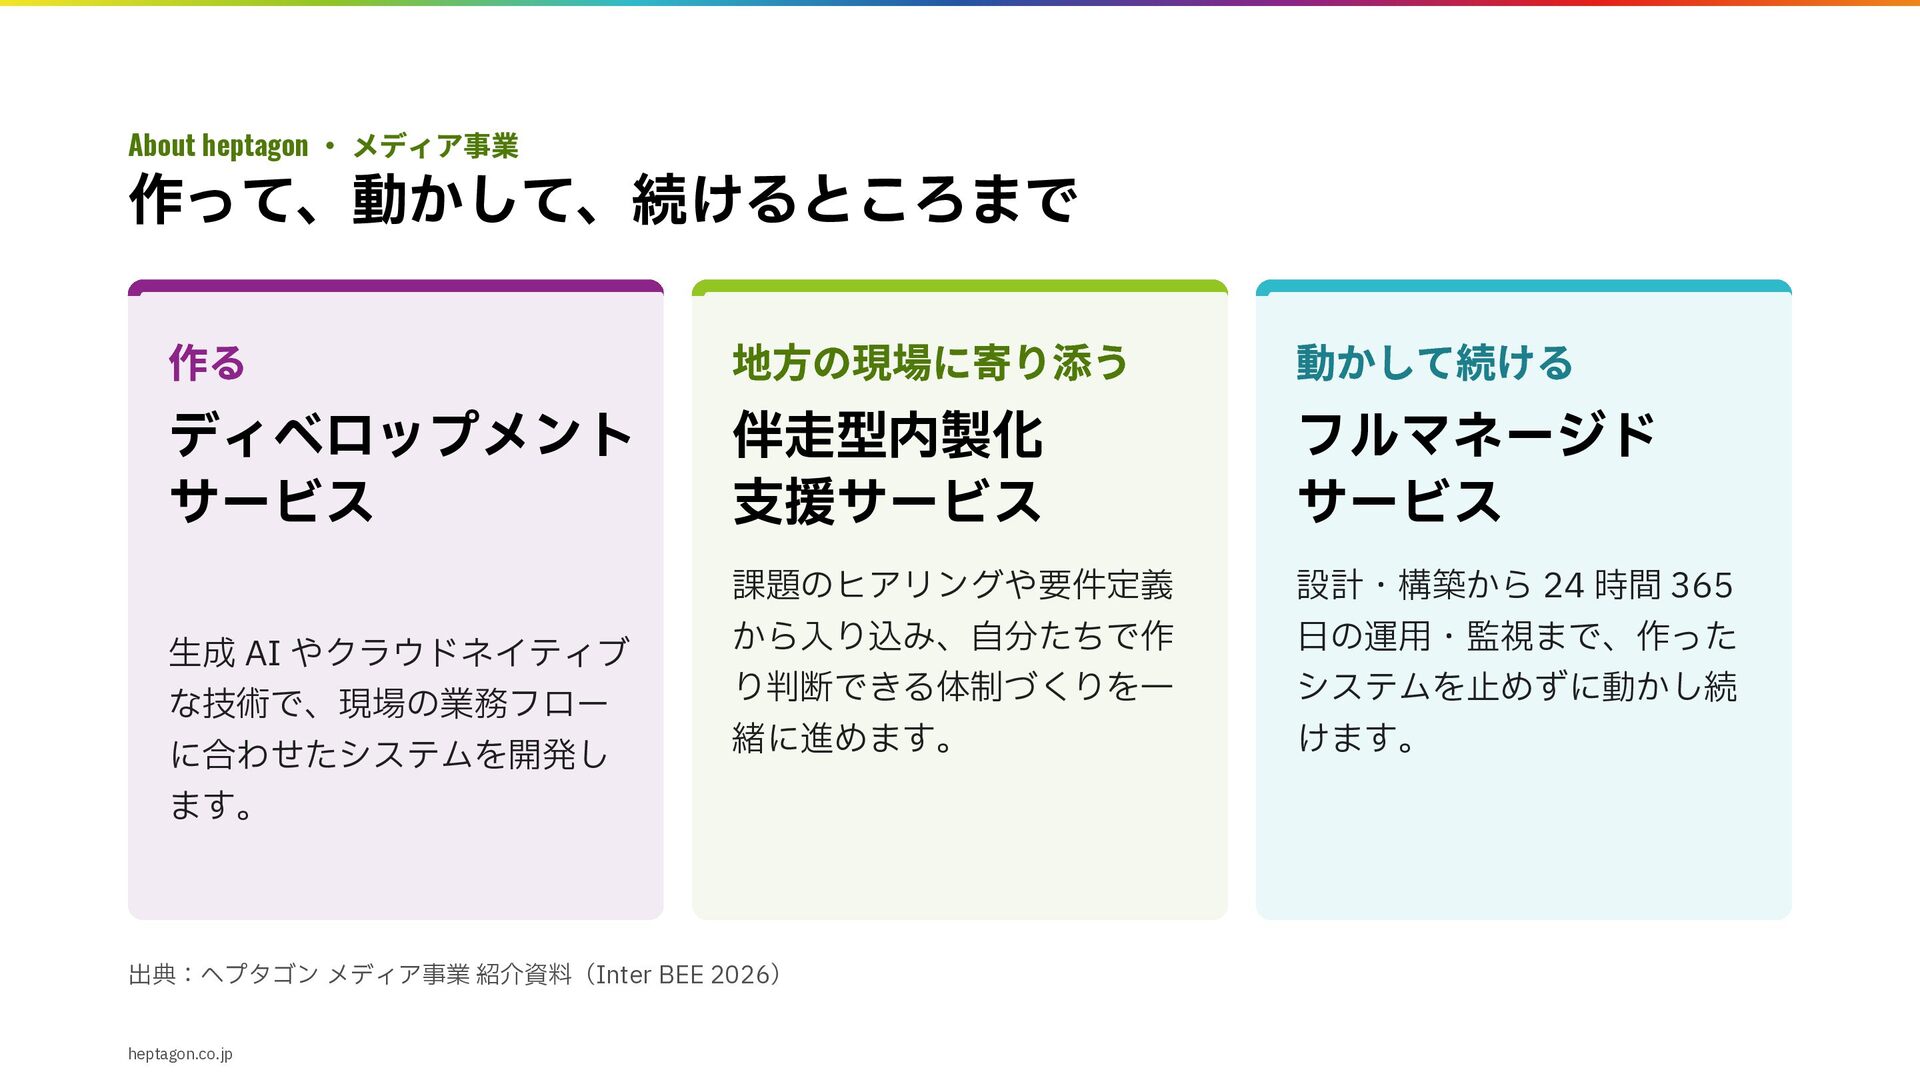
・ メディア事業 作って、動かして、続けるところまで About heptagon 作る ディベロップメント サービス 生成 AI
やクラウドネイティブ な技術で、現場の業務フロー に合わせたシステムを開発し ます。 地方の現場に寄り添う 動かして続ける 課題のヒアリングや要件定義 から入り込み、自分たちで作 り判断できる体制づくりを一 緒に進めます。 設計・構築から 24 時間 365 日の運用・監視まで、作った システムを止めずに動かし続 けます。 伴走型内製化 支援サービス 出典:ヘプタゴン メディア事業 紹介資料(Inter BEE 2026) heptagon.co.jp フルマネージド サービス -
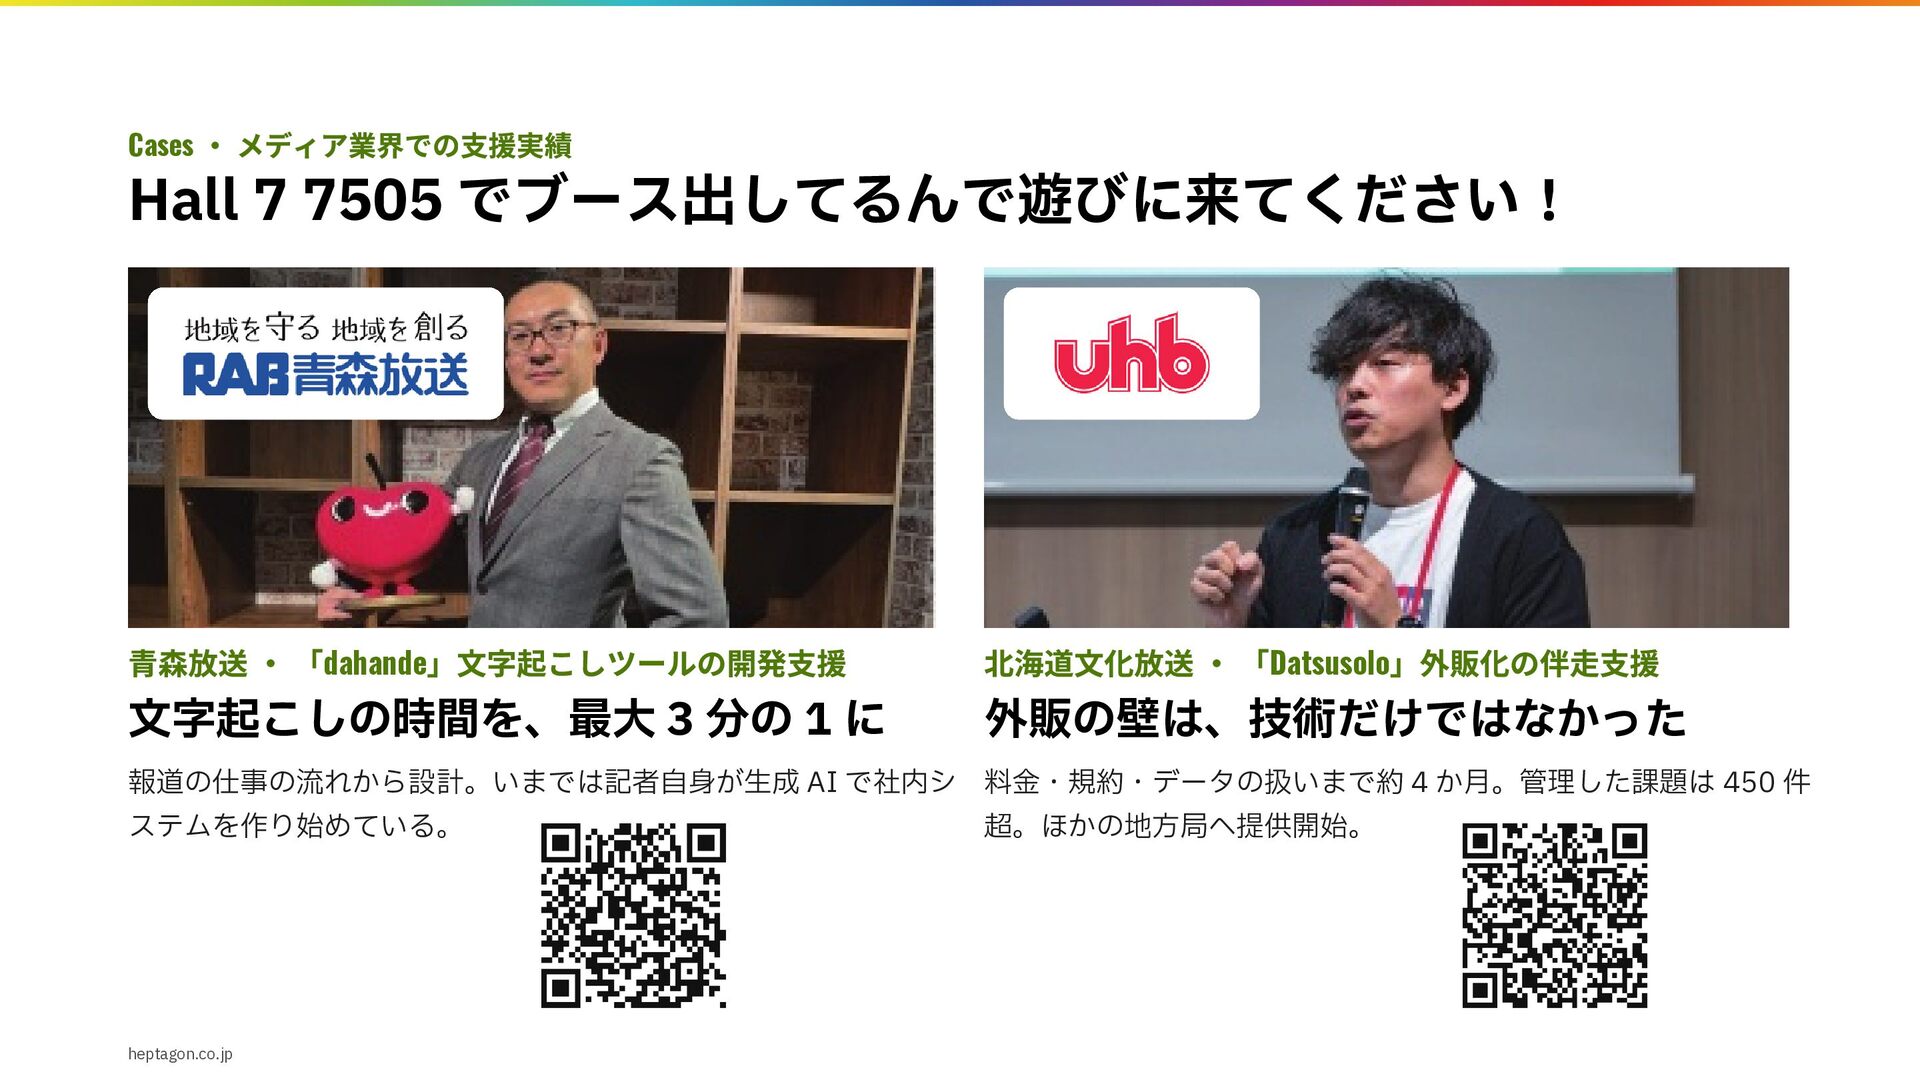
・ メディア業界での支援実績 Hall 7 7505 でブース出してるんで遊びに来てください! Cases 青森放送 ・ 「dahande」文字起こしツールの開発支援
文字起こしの時間を、最大 3 分の 1 に 北海道文化放送 ・ 「Datsusolo」外販化の伴走支援 外販の壁は、技術だけではなかった 報道の仕事の流れから設計。いまでは記者自身が生成 AI で社内シ 料金・規約・データの扱いまで約 4 か月。管理した課題は 450 件 ステムを作り始めている。 heptagon.co.jp 超。ほかの地方局へ提供開始。 -
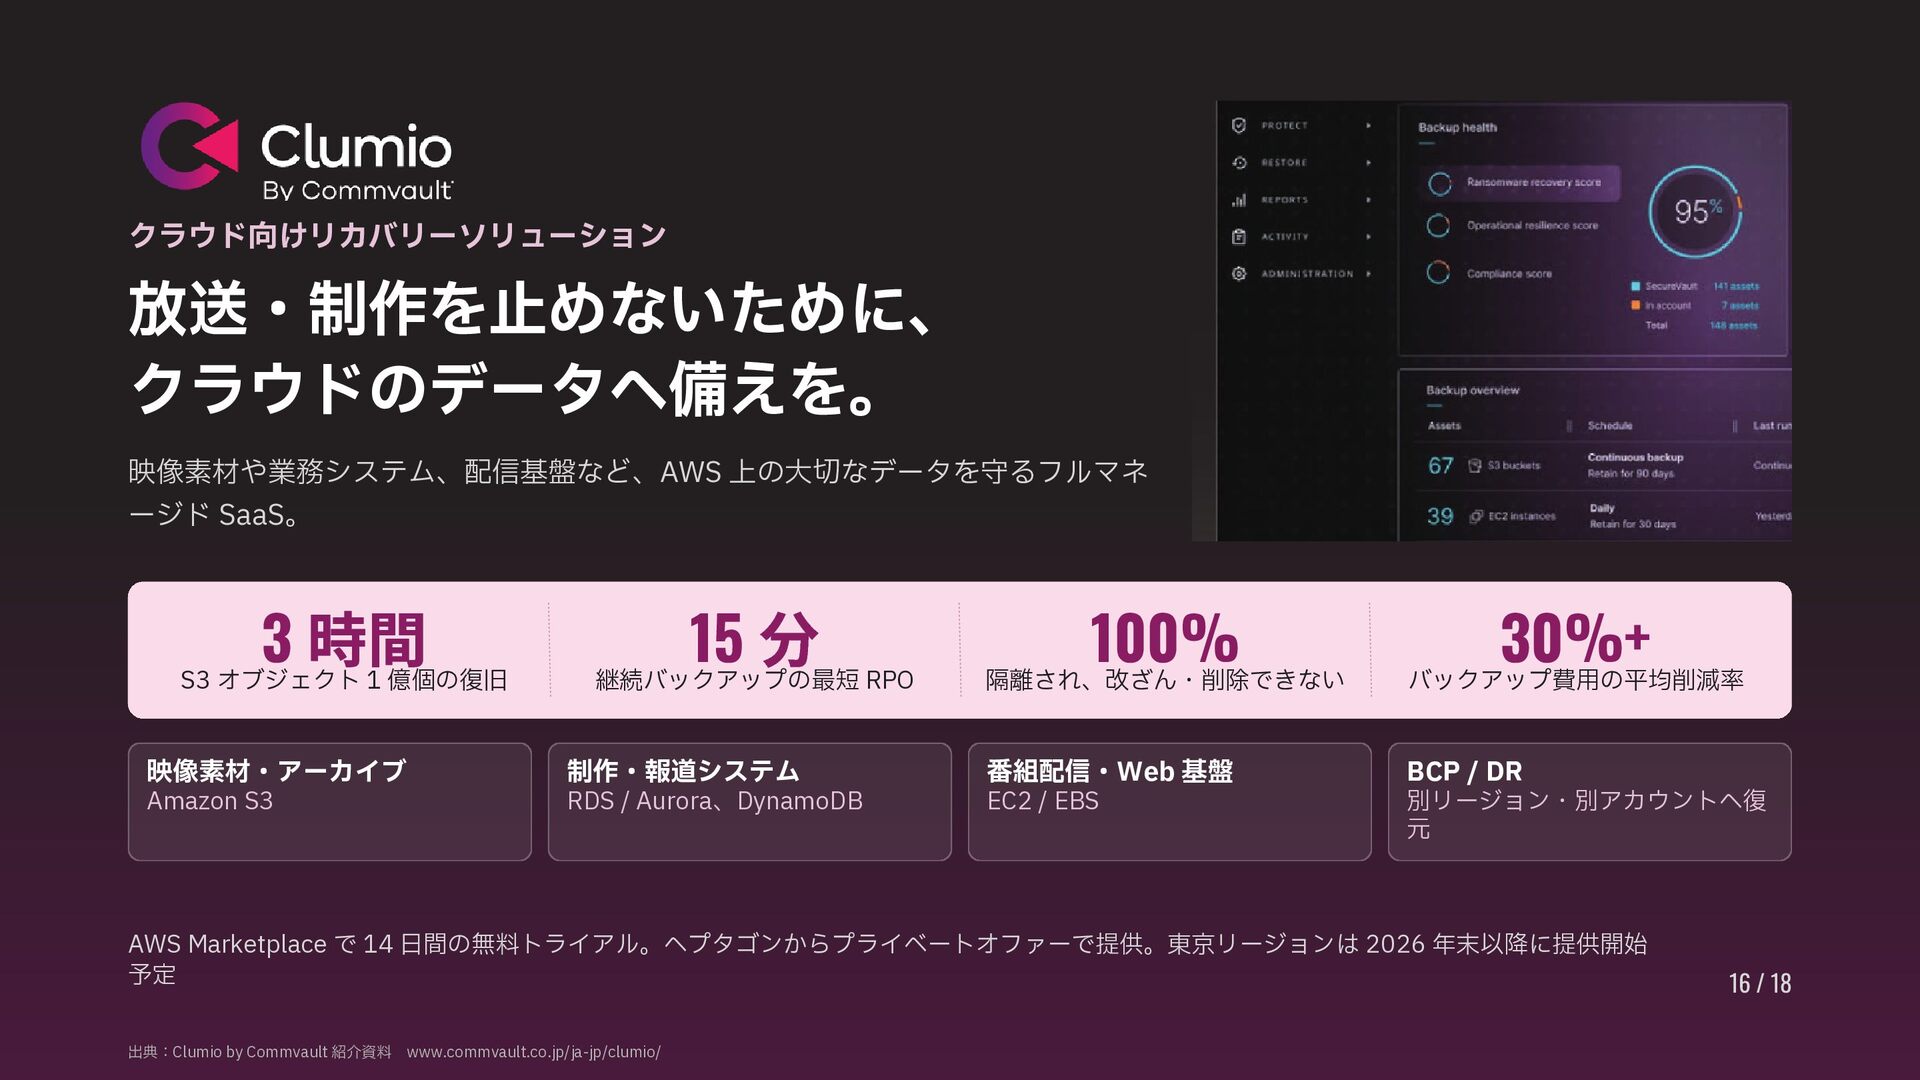
クラウド向けリカバリーソリューション 放送・制作を止めないために、 クラウドのデータへ備えを。 映像素材や業務システム、配信基盤など、AWS 上の大切なデータを守るフルマネ ージド SaaS。 3 時間 S3
オブジェクト 1 億個の復旧 映像素材・アーカイブ Amazon S3 15 分 継続バックアップの最短 RPO 制作・報道システム RDS / Aurora、DynamoDB 100% 30%+ 隔離され、改ざん・削除できない バックアップ費用の平均削減率 番組配信・Web 基盤 BCP / DR EC2 / EBS 別リージョン・別アカウントへ復 元 AWS Marketplace で 14 日間の無料トライアル。ヘプタゴンからプライベートオファーで提供。東京リージョンは 2026 年末以降に提供開始 予定 出典:Clumio by Commvault 紹介資料 www.commvault.co.jp/ja-jp/clumio/ 16 / 18 -
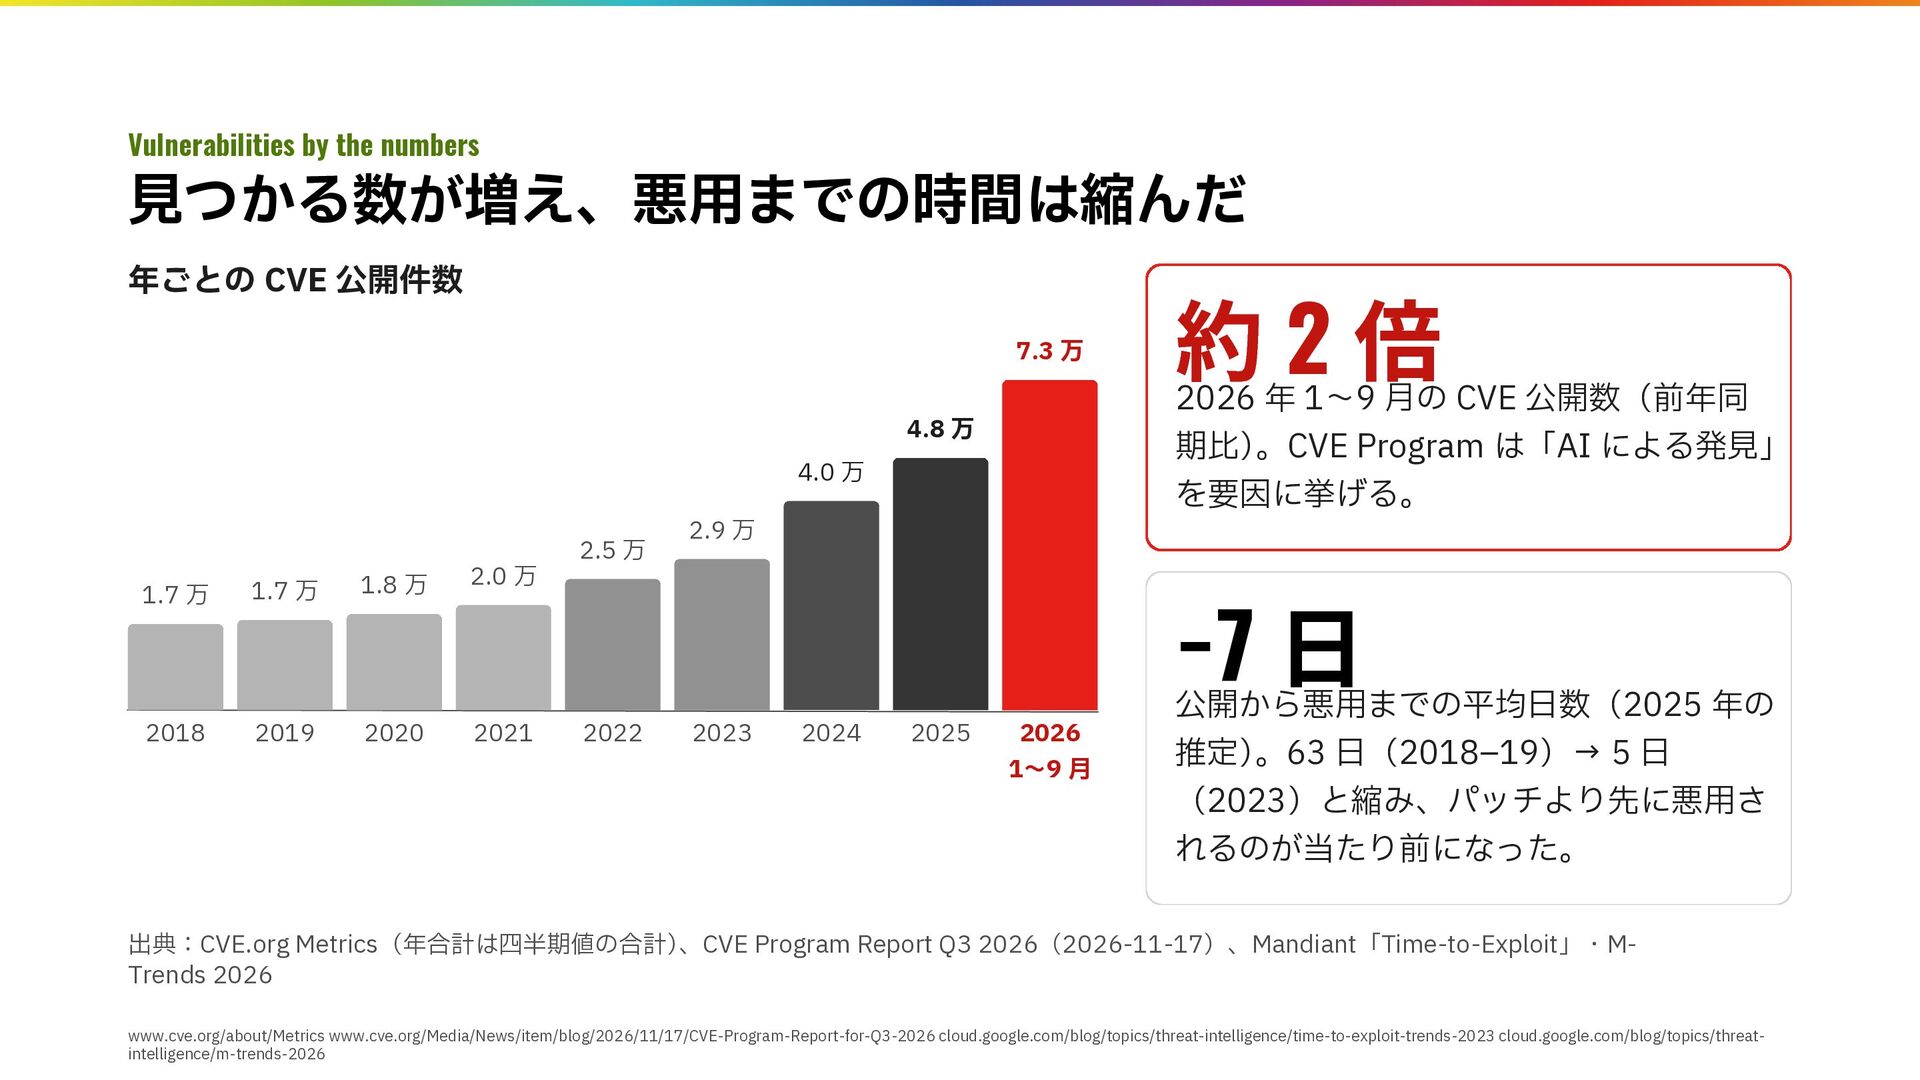
Vulnerabilities by the numbers 見つかる数が増え、悪用までの時間は縮んだ 年ごとの CVE 公開件数 7.3 万
2026 年 1〜9 月の CVE 公開数(前年同 期比)。CVE Program は「AI による発見」 4.8 万 4.0 万 1.7 万 2018 1.7 万 2019 1.8 万 2020 2.0 万 2021 2.5 万 約2倍 を要因に挙げる。 2.9 万 −7 2022 2023 2024 2025 2026 1〜9 月 日 公開から悪用までの平均日数(2025 年の 推定)。63 日(2018–19)→ 5 日 (2023)と縮み、パッチより先に悪用さ れるのが当たり前になった。 出典:CVE.org Metrics(年合計は四半期値の合計) 、CVE Program Report Q3 2026(2026-11-17)、Mandiant「Time-to-Exploit」・MTrends 2026 www.cve.org/about/Metrics www.cve.org/Media/News/item/blog/2026/11/17/CVE-Program-Report-for-Q3-2026 cloud.google.com/blog/topics/threat-intelligence/time-to-exploit-trends-2023 cloud.google.com/blog/topics/threatintelligence/m-trends-2026 -
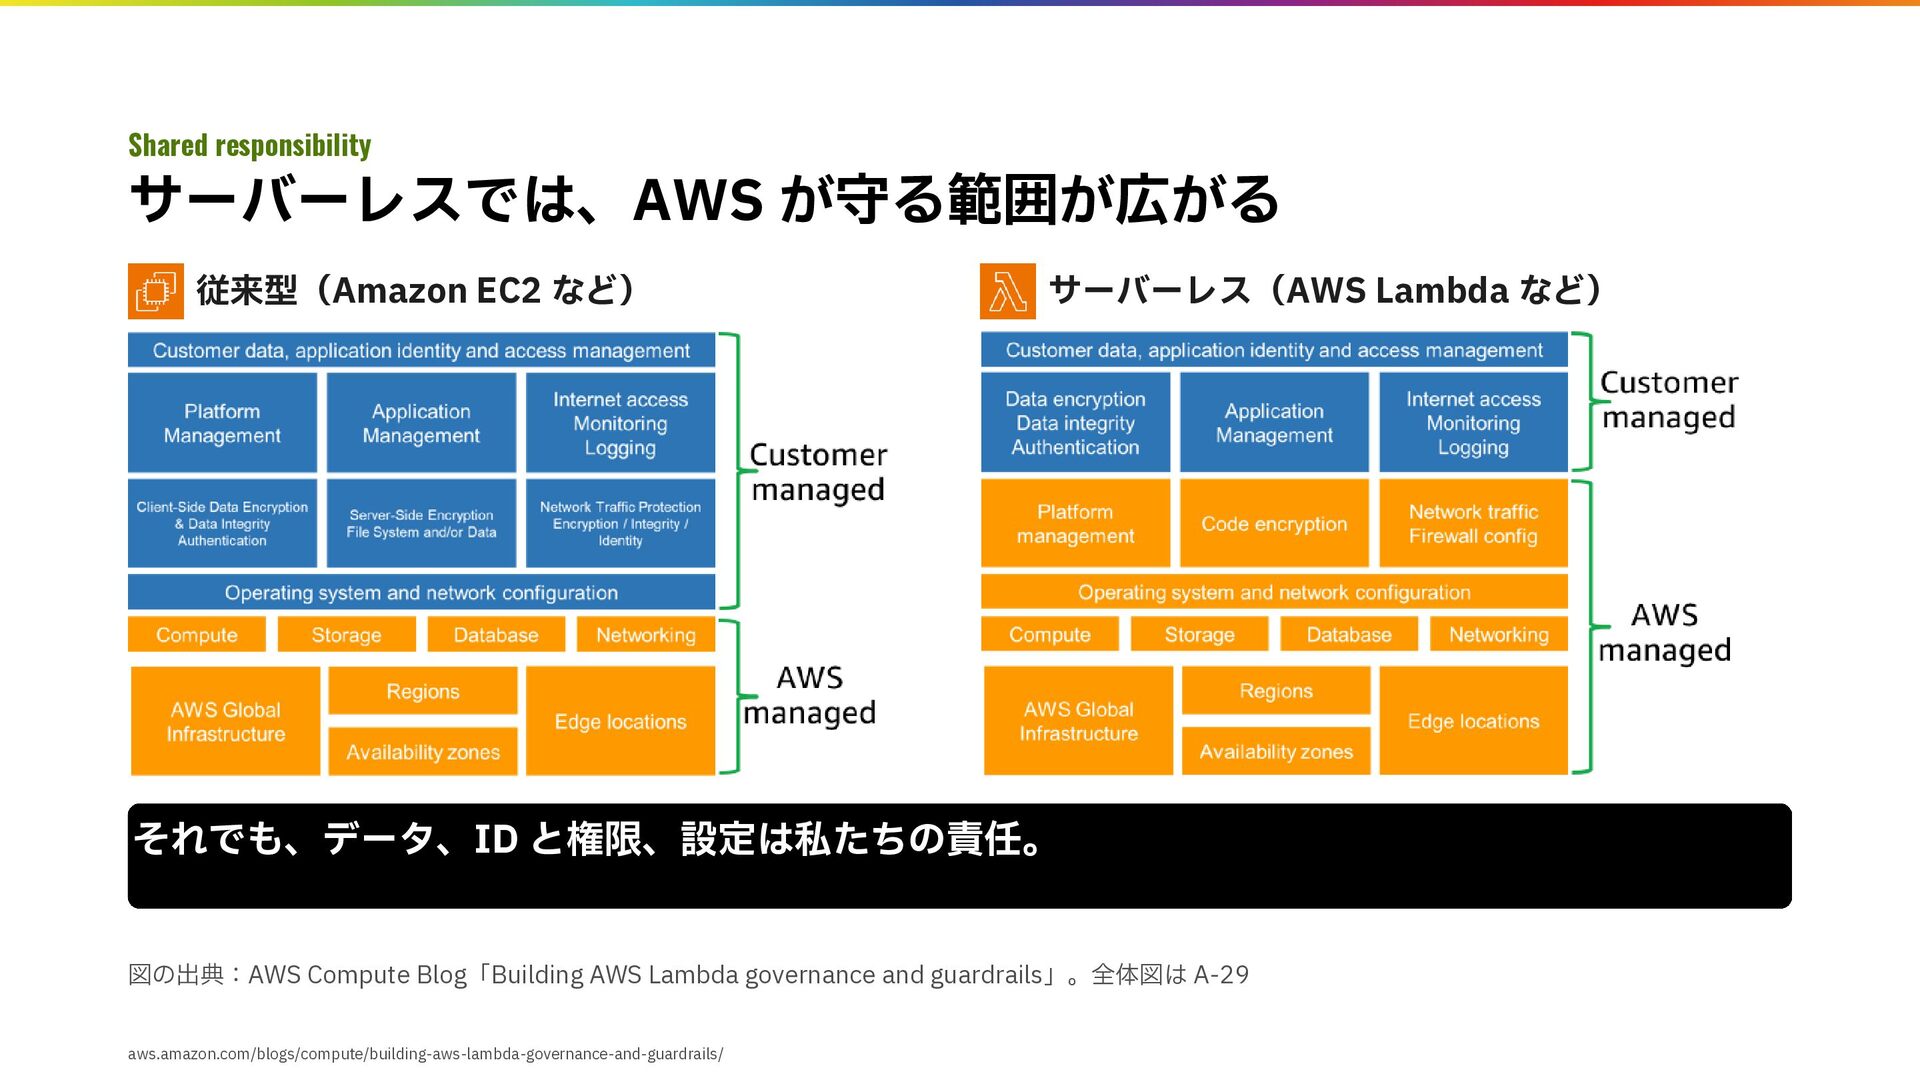
Shared responsibility サーバーレスでは、AWS が守る範囲が広がる 従来型(Amazon EC2 など) サーバーレス(AWS Lambda など)
それでも、データ、ID と権限、設定は私たちの責任。 図の出典:AWS Compute Blog「Building AWS Lambda governance and guardrails」。全体図は A-29 aws.amazon.com/blogs/compute/building-aws-lambda-governance-and-guardrails/ -
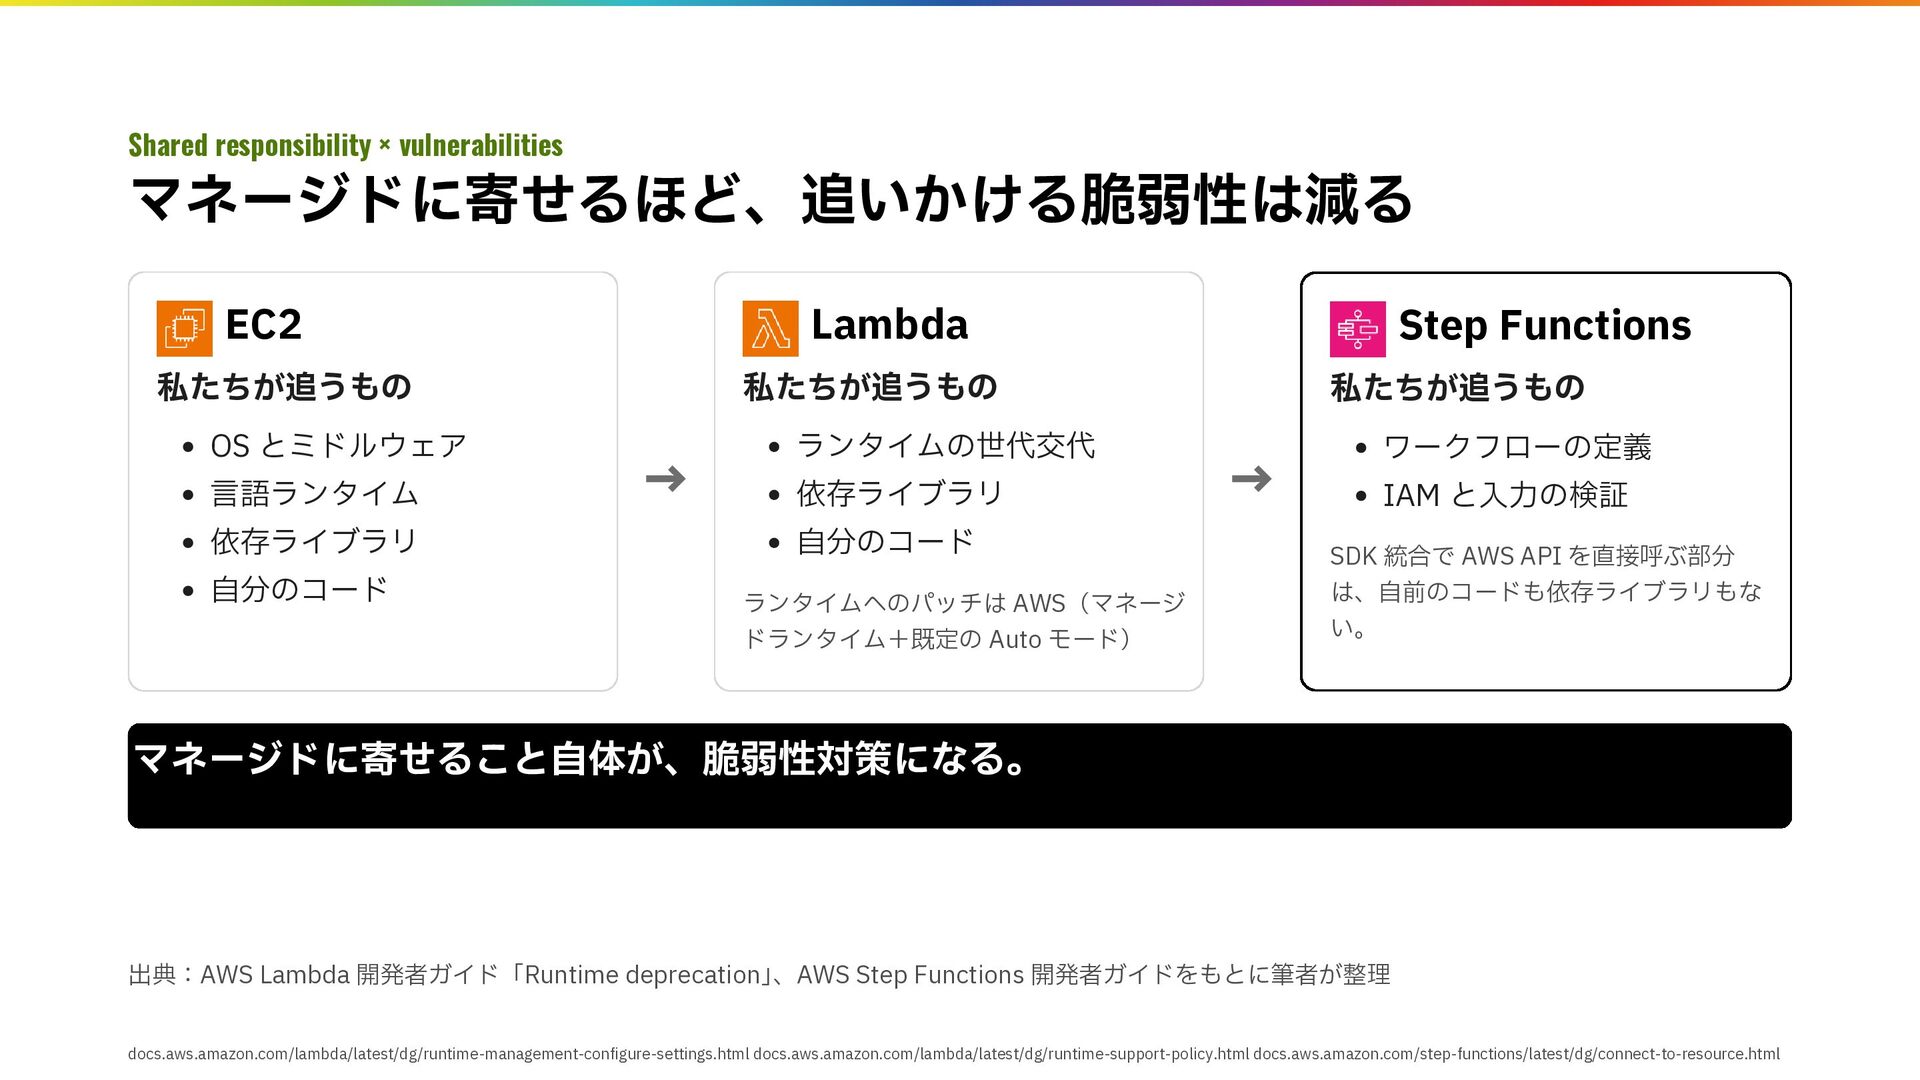
Shared responsibility × vulnerabilities マネージドに寄せるほど、追いかける脆弱性は減る EC2 Lambda 私たちが追うもの 私たちが追うもの OS
とミドルウェア 言語ランタイム 依存ライブラリ 自分のコード → ランタイムの世代交代 依存ライブラリ 自分のコード ランタイムへのパッチは AWS(マネージ ドランタイム+既定の Auto モード) Step Functions 私たちが追うもの ワークフローの定義 → IAM と入力の検証 SDK 統合で AWS API を直接呼ぶ部分 は、自前のコードも依存ライブラリもな い。 マネージドに寄せること自体が、脆弱性対策になる。 出典:AWS Lambda 開発者ガイド「Runtime deprecation」 、AWS Step Functions 開発者ガイドをもとに筆者が整理 docs.aws.amazon.com/lambda/latest/dg/runtime-management-configure-settings.html docs.aws.amazon.com/lambda/latest/dg/runtime-support-policy.html docs.aws.amazon.com/step-functions/latest/dg/connect-to-resource.html -
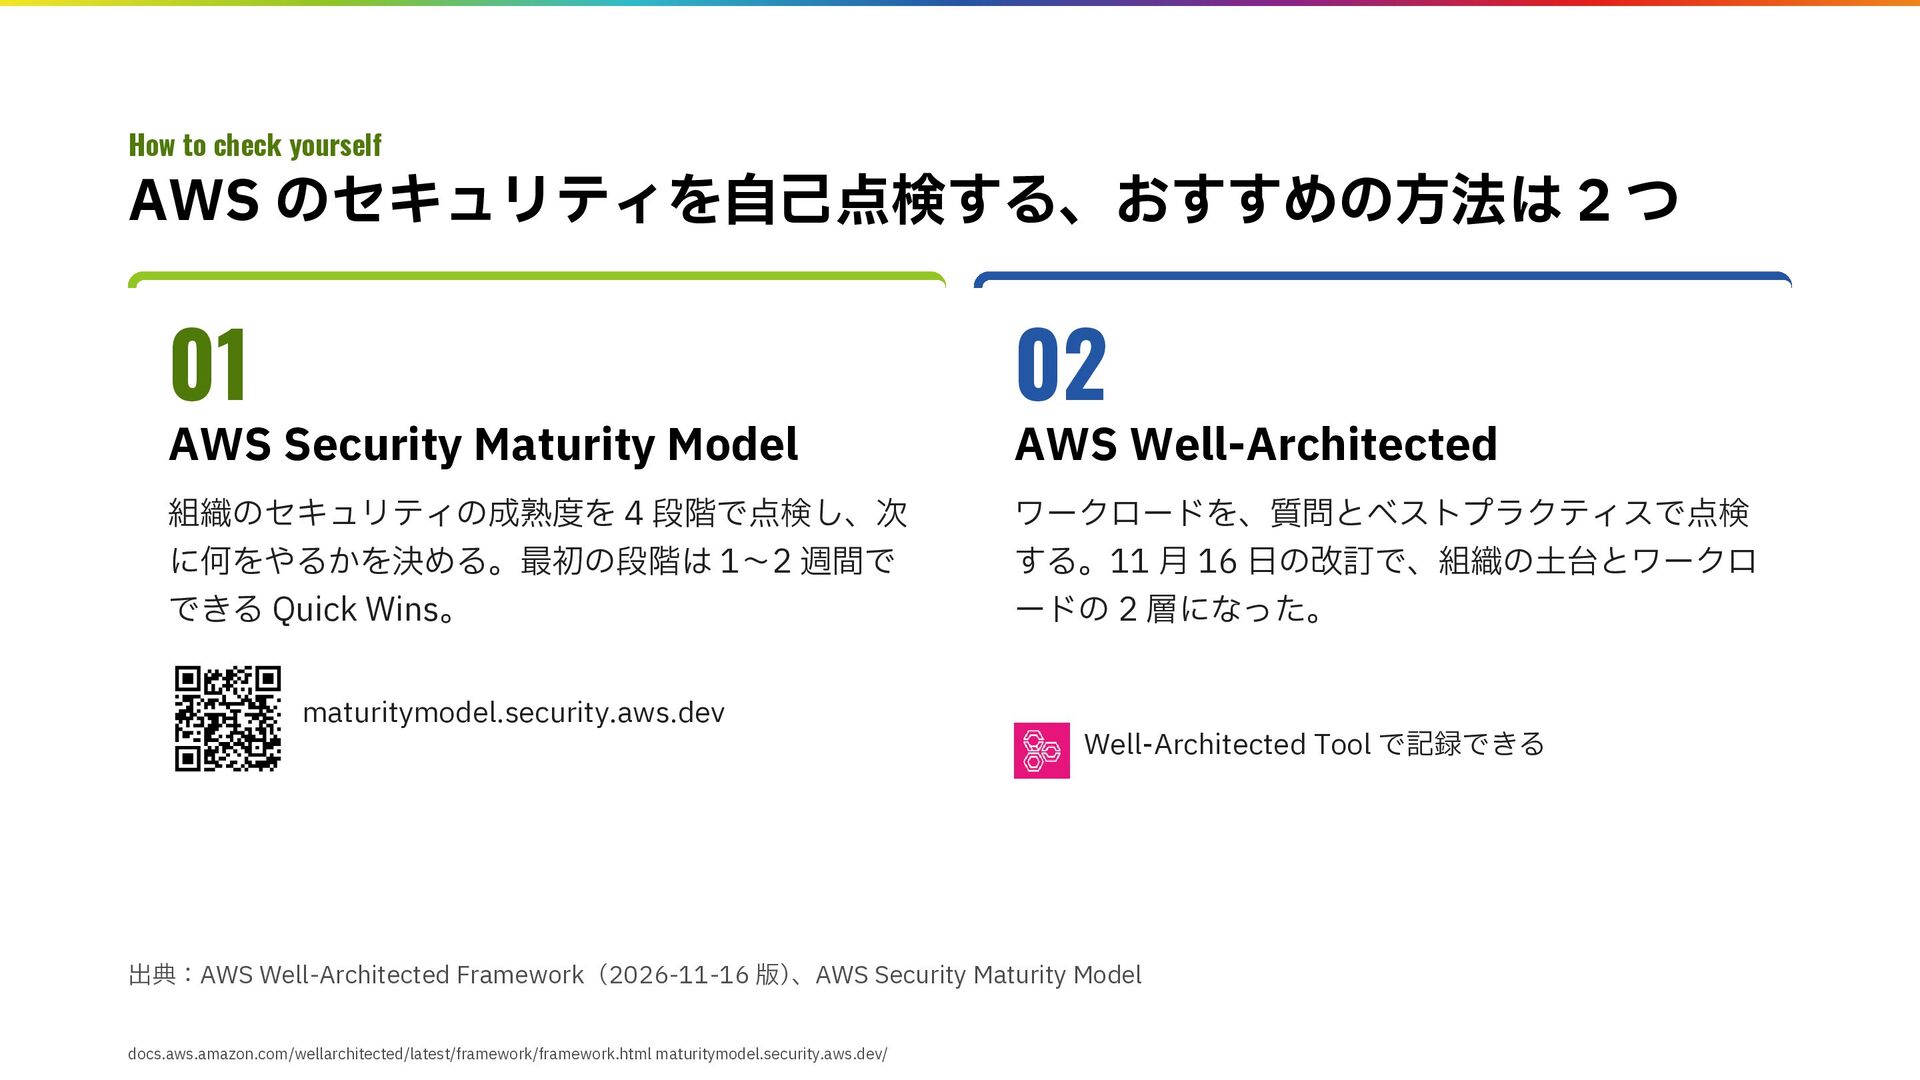
How to check yourself AWS のセキュリティを自己点検する、おすすめの方法は 2 つ 01 02
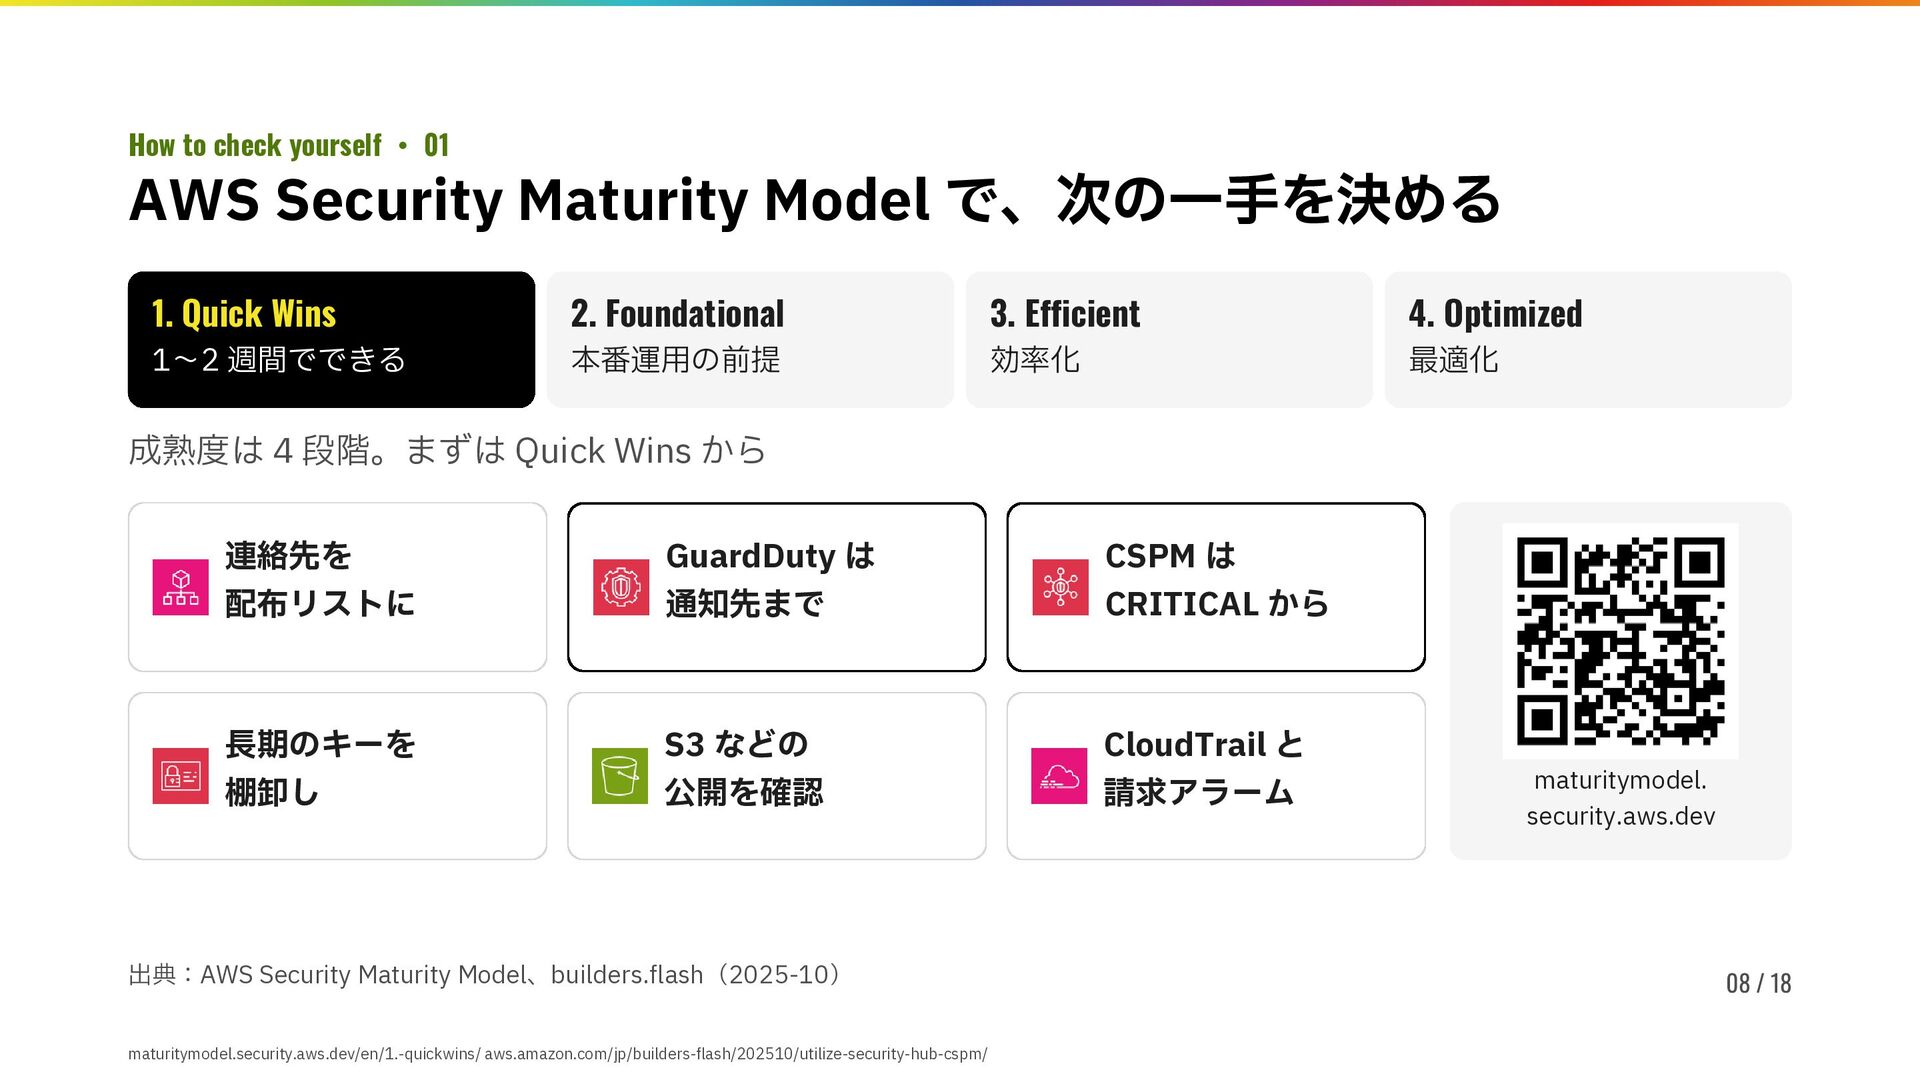
組織のセキュリティの成熟度を 4 段階で点検し、次 に何をやるかを決める。最初の段階は 1〜2 週間で できる Quick Wins。 ワークロードを、質問とベストプラクティスで点検 する。11 月 16 日の改訂で、組織の土台とワークロ ードの 2 層になった。 AWS Security Maturity Model maturitymodel.security.aws.dev AWS Well-Architected Well-Architected Tool で記録できる 出典:AWS Well-Architected Framework(2026-11-16 版) 、AWS Security Maturity Model docs.aws.amazon.com/wellarchitected/latest/framework/framework.html maturitymodel.security.aws.dev/ -
・ 01 AWS Security Maturity Model で、次の一手を決める How to check
yourself 1. Quick Wins 2. Foundational 3. Efficient 4. Optimized 1〜2 週間でできる 本番運用の前提 効率化 最適化 成熟度は 4 段階。まずは Quick Wins から 連絡先を 配布リストに GuardDuty は 通知先まで CSPM は CRITICAL から 長期のキーを 棚卸し S3 などの 公開を確認 CloudTrail と 請求アラーム 出典:AWS Security Maturity Model、builders.flash(2025-10) maturitymodel.security.aws.dev/en/1.-quickwins/ aws.amazon.com/jp/builders-flash/202510/utilize-security-hub-cspm/ maturitymodel. security.aws.dev 08 / 18 -
・ 01 AWS Security Maturity Model で、次の一手を決める How to check
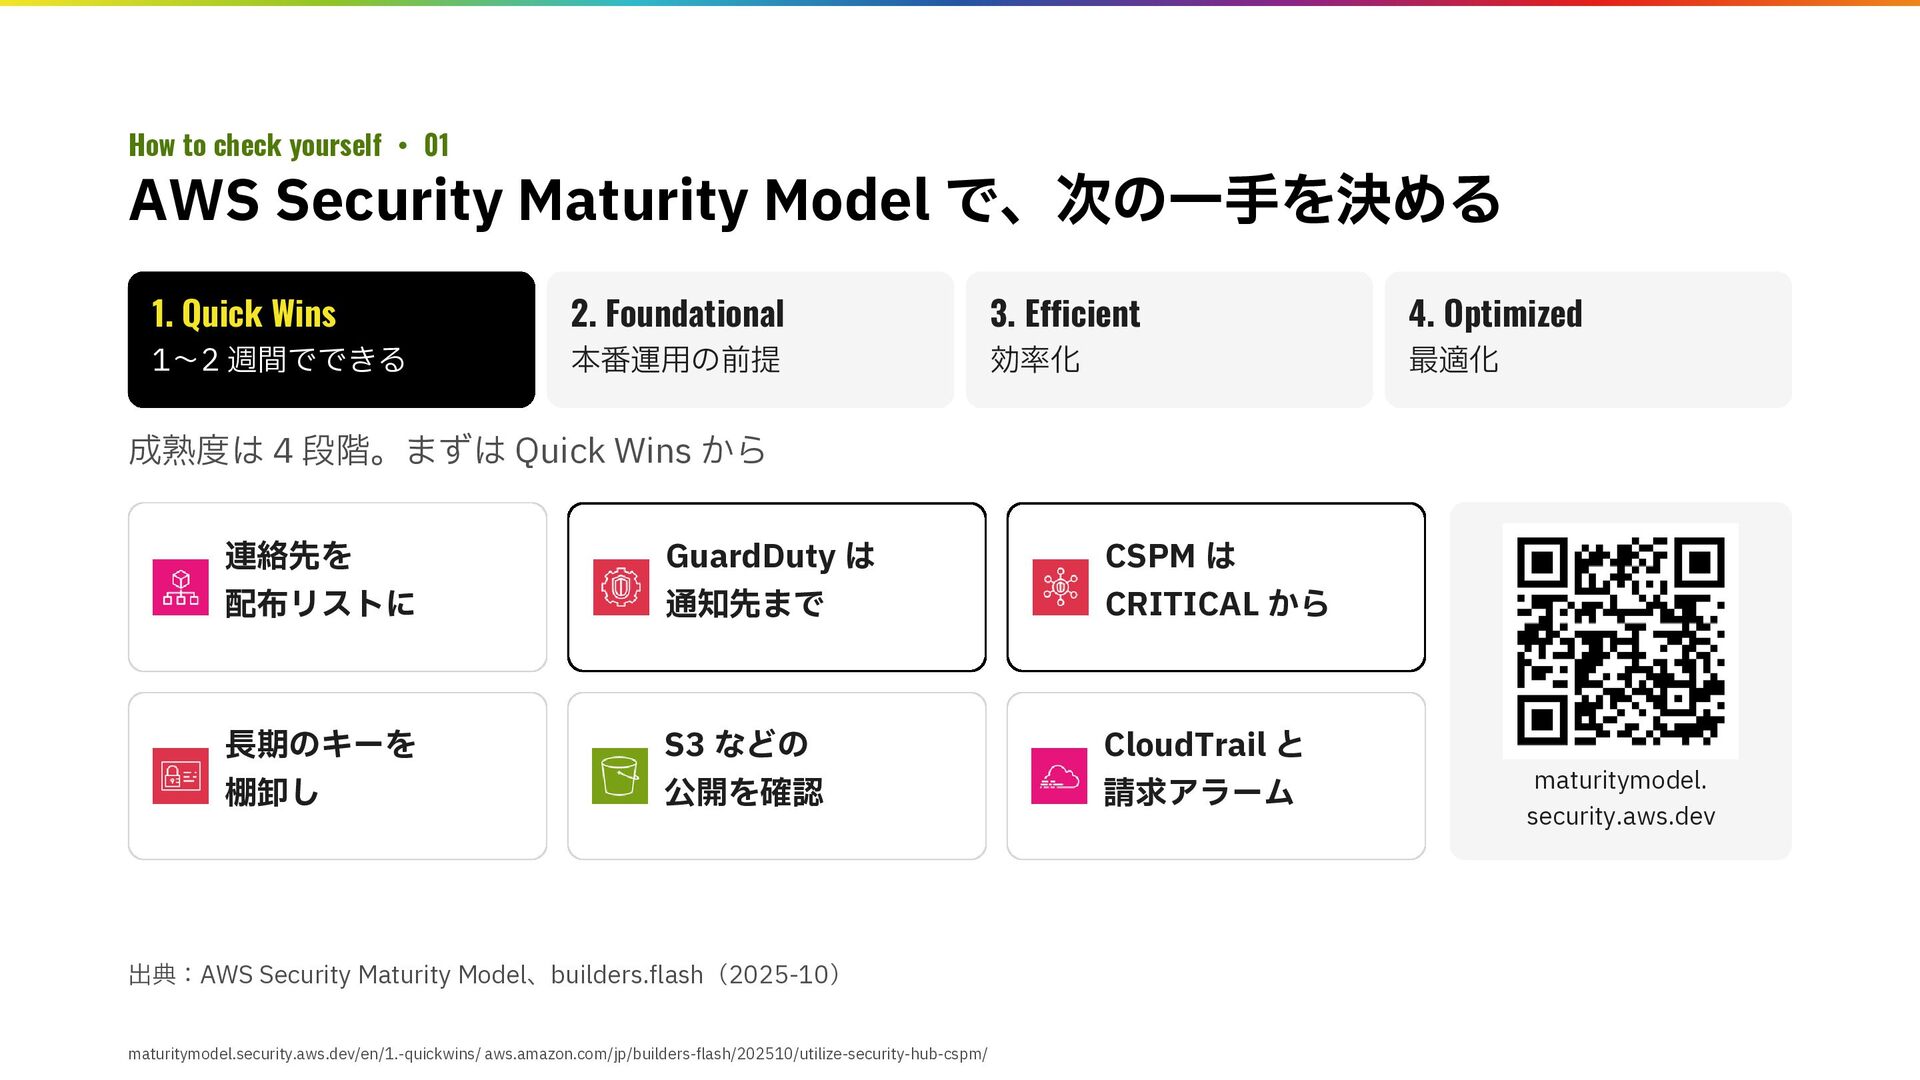
yourself 1. Quick Wins 2. Foundational 3. Efficient 4. Optimized 1〜2 週間でできる 本番運用の前提 効率化 最適化 成熟度は 4 段階。まずは Quick Wins から 連絡先を 配布リストに GuardDuty は 通知先まで CSPM は CRITICAL から 長期のキーを 棚卸し S3 などの 公開を確認 CloudTrail と 請求アラーム 出典:AWS Security Maturity Model、builders.flash(2025-10) maturitymodel.security.aws.dev/en/1.-quickwins/ aws.amazon.com/jp/builders-flash/202510/utilize-security-hub-cspm/ maturitymodel. security.aws.dev -
・ 2026.11.16 Well-Architected は 2 つの層に分かれました What's new 上の層:Cloud Workloads
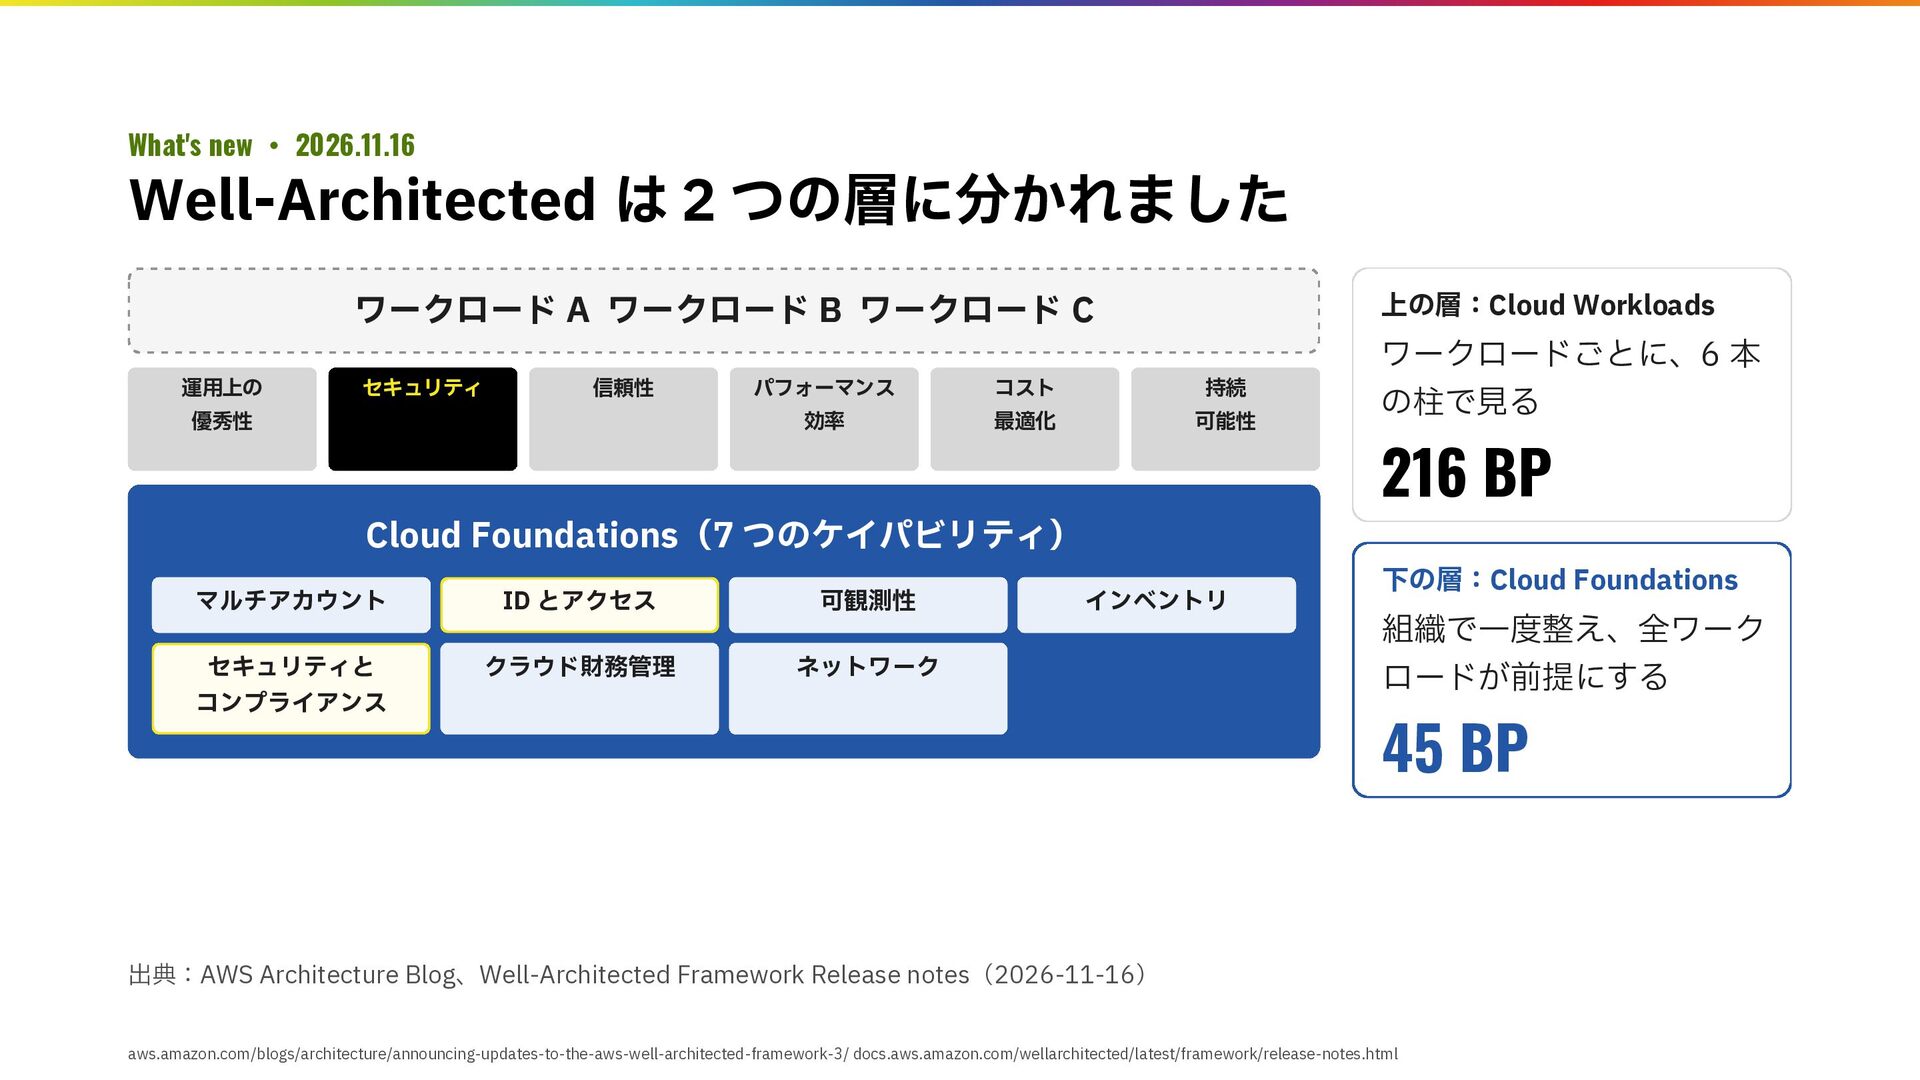
ワークロード A ワークロード B ワークロード C 運用上の セキュリティ 信頼性 優秀性 パフォーマンス コスト 持続 効率 最適化 可能性 Cloud Foundations(7 つのケイパビリティ) マルチアカウント ID とアクセス 可観測性 セキュリティと コンプライアンス クラウド財務管理 ネットワーク インベントリ ワークロードごとに、6 本 の柱で見る 216 BP 下の層:Cloud Foundations 組織で一度整え、全ワーク ロードが前提にする 45 BP 出典:AWS Architecture Blog、Well-Architected Framework Release notes(2026-11-16) aws.amazon.com/blogs/architecture/announcing-updates-to-the-aws-well-architected-framework-3/ docs.aws.amazon.com/wellarchitected/latest/framework/release-notes.html -
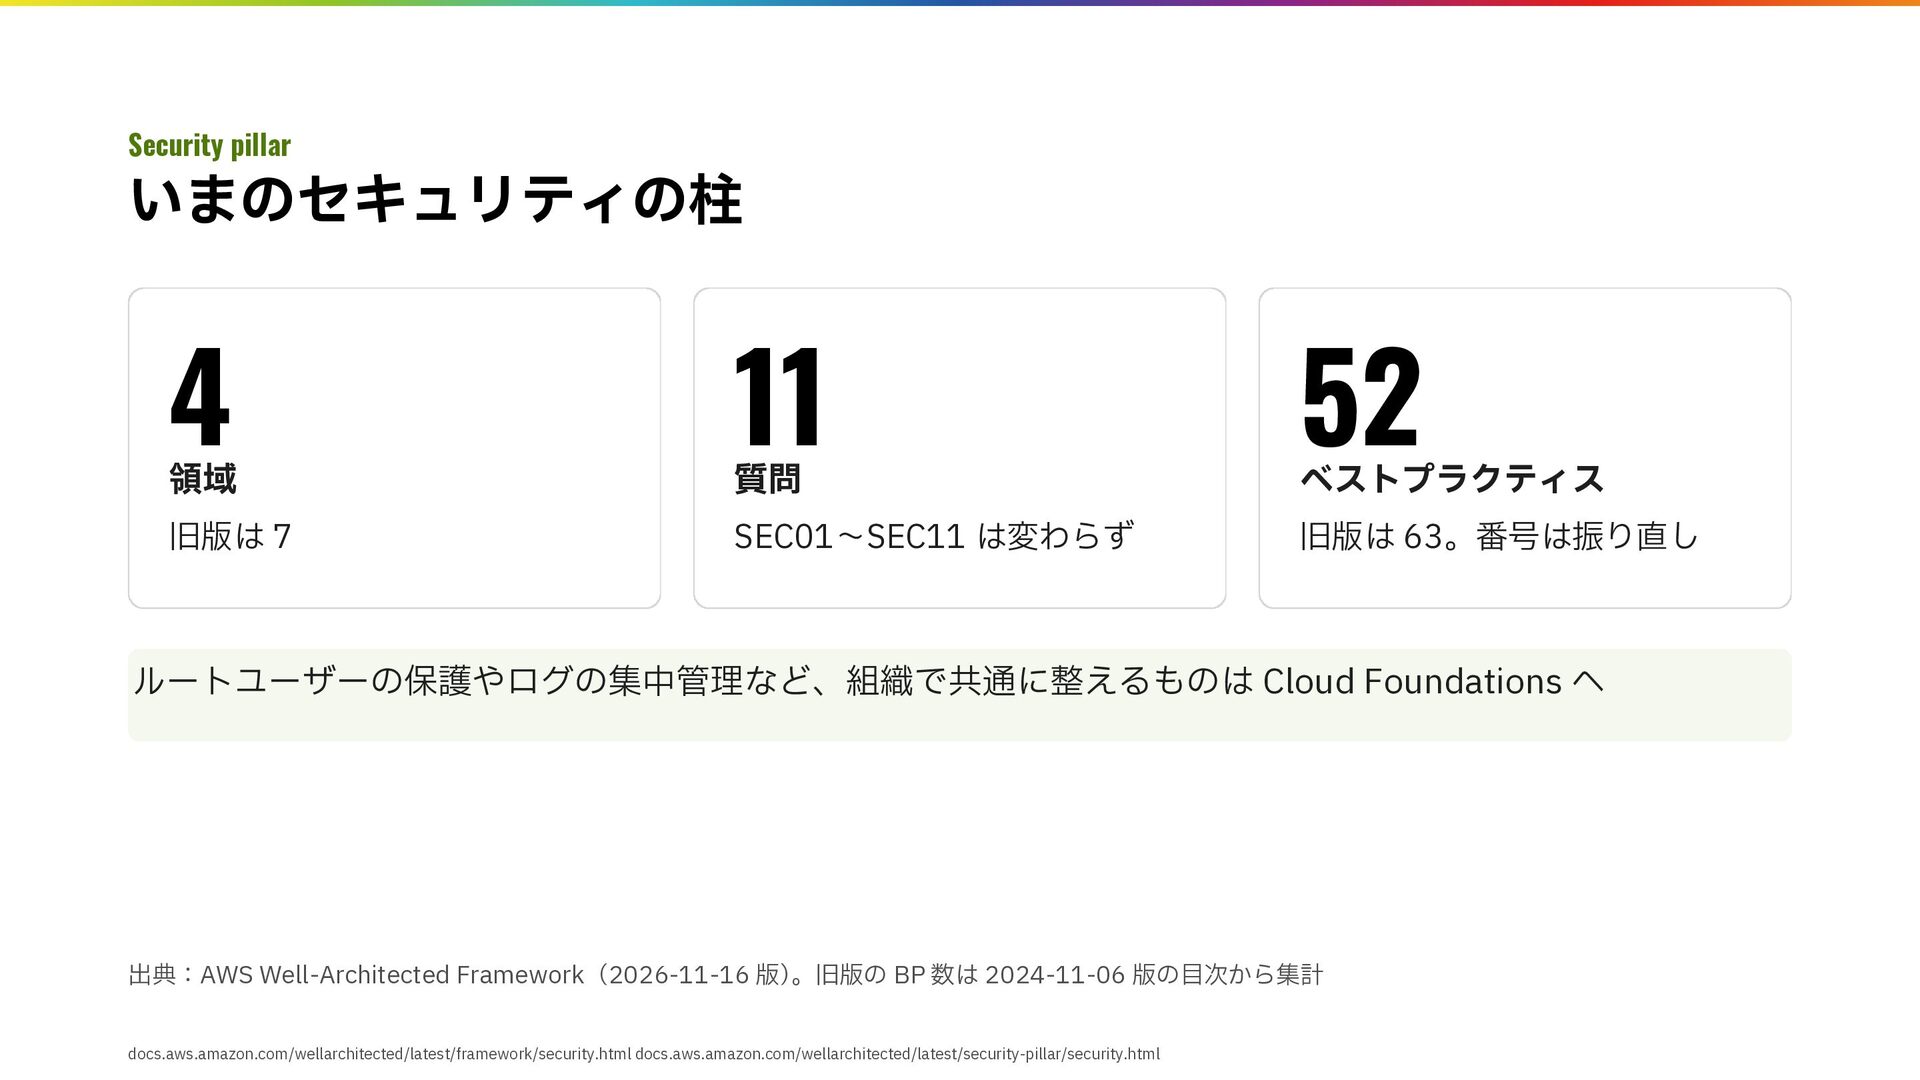
Security pillar いまのセキュリティの柱 4 11 52 旧版は 7 SEC01〜SEC11 は変わらず
旧版は 63。番号は振り直し 領域 質問 ベストプラクティス ルートユーザーの保護やログの集中管理など、組織で共通に整えるものは Cloud Foundations へ 出典:AWS Well-Architected Framework(2026-11-16 版) 。旧版の BP 数は 2024-11-06 版の目次から集計 docs.aws.amazon.com/wellarchitected/latest/framework/security.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/security.html -
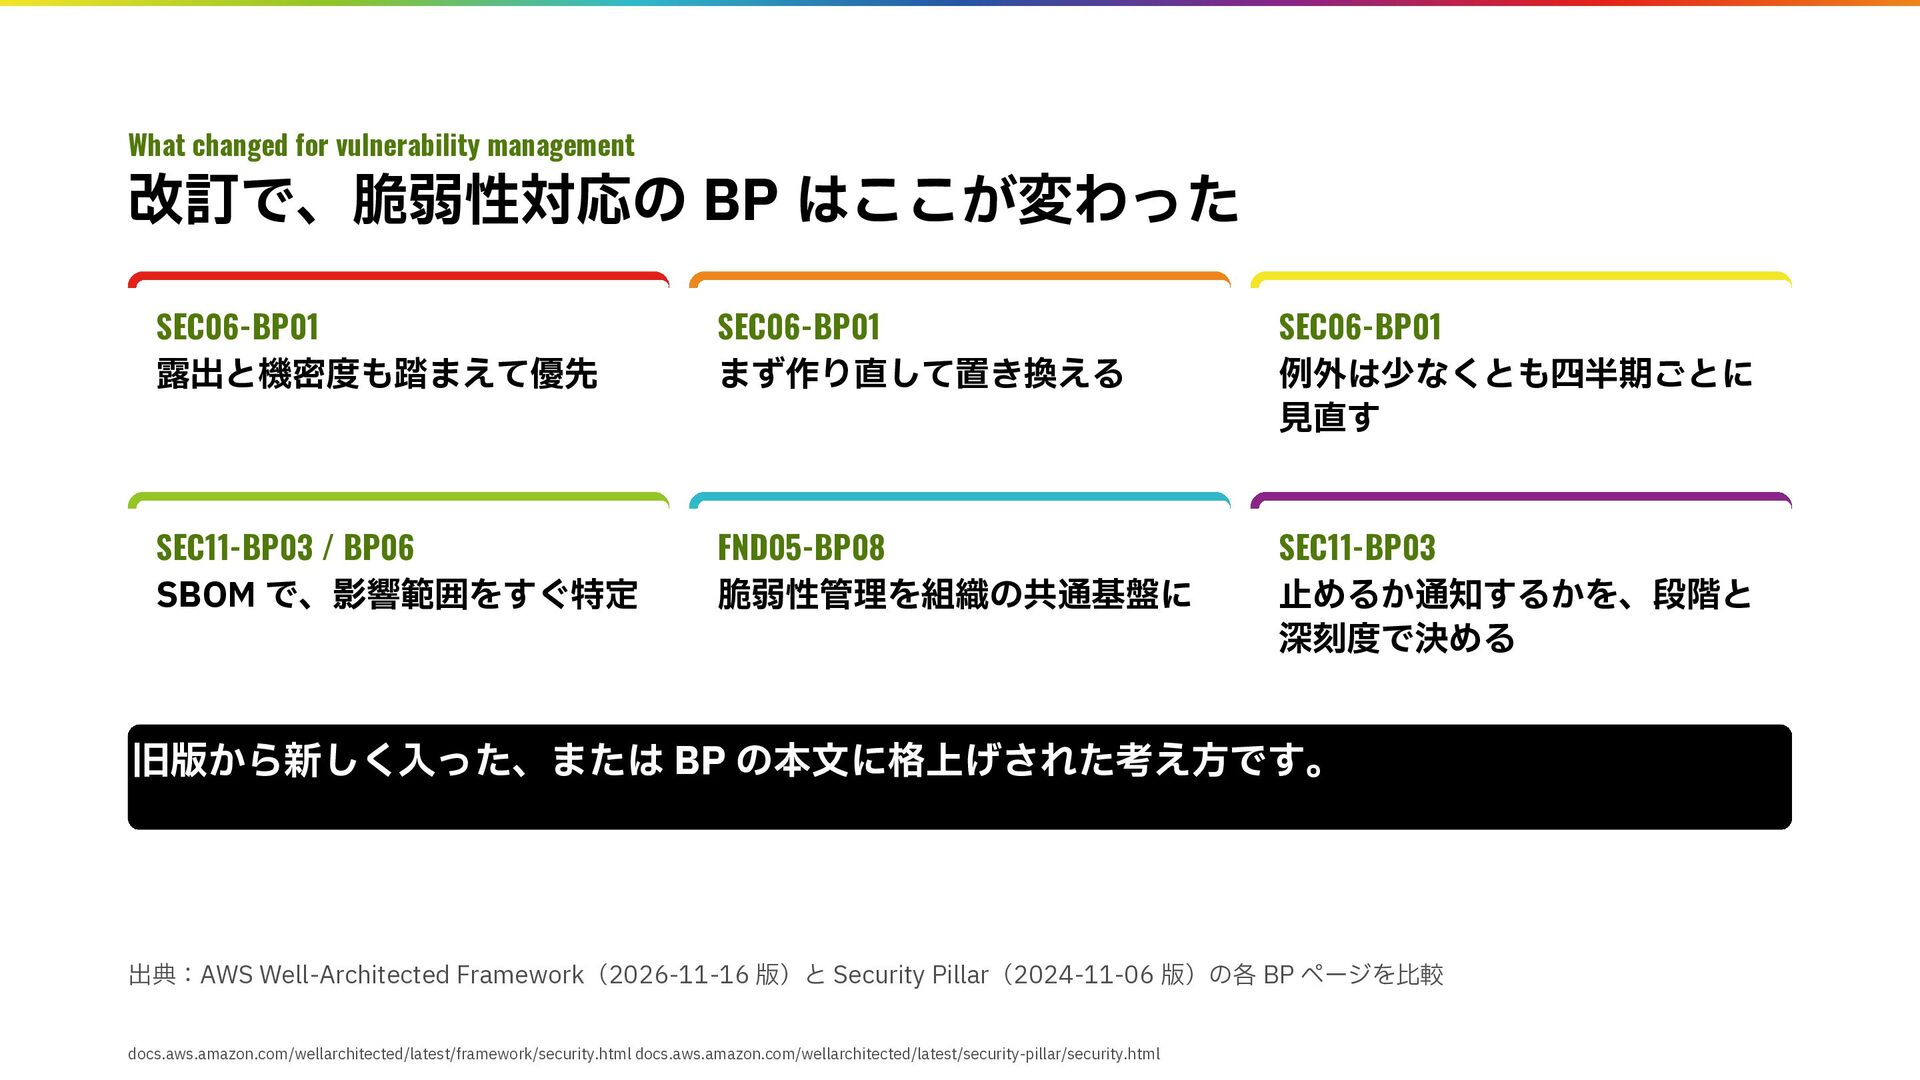
What changed for vulnerability management 改訂で、脆弱性対応の BP はここが変わった SEC06-BP01 SEC06-BP01
SEC06-BP01 露出と機密度も踏まえて優先 まず作り直して置き換える 例外は少なくとも四半期ごとに 見直す SEC11-BP03 / BP06 FND05-BP08 SEC11-BP03 SBOM で、影響範囲をすぐ特定 脆弱性管理を組織の共通基盤に 止めるか通知するかを、段階と 深刻度で決める 旧版から新しく入った、または BP の本文に格上げされた考え方です。 出典:AWS Well-Architected Framework(2026-11-16 版)と Security Pillar(2024-11-06 版)の各 BP ページを比較 docs.aws.amazon.com/wellarchitected/latest/framework/security.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/security.html -
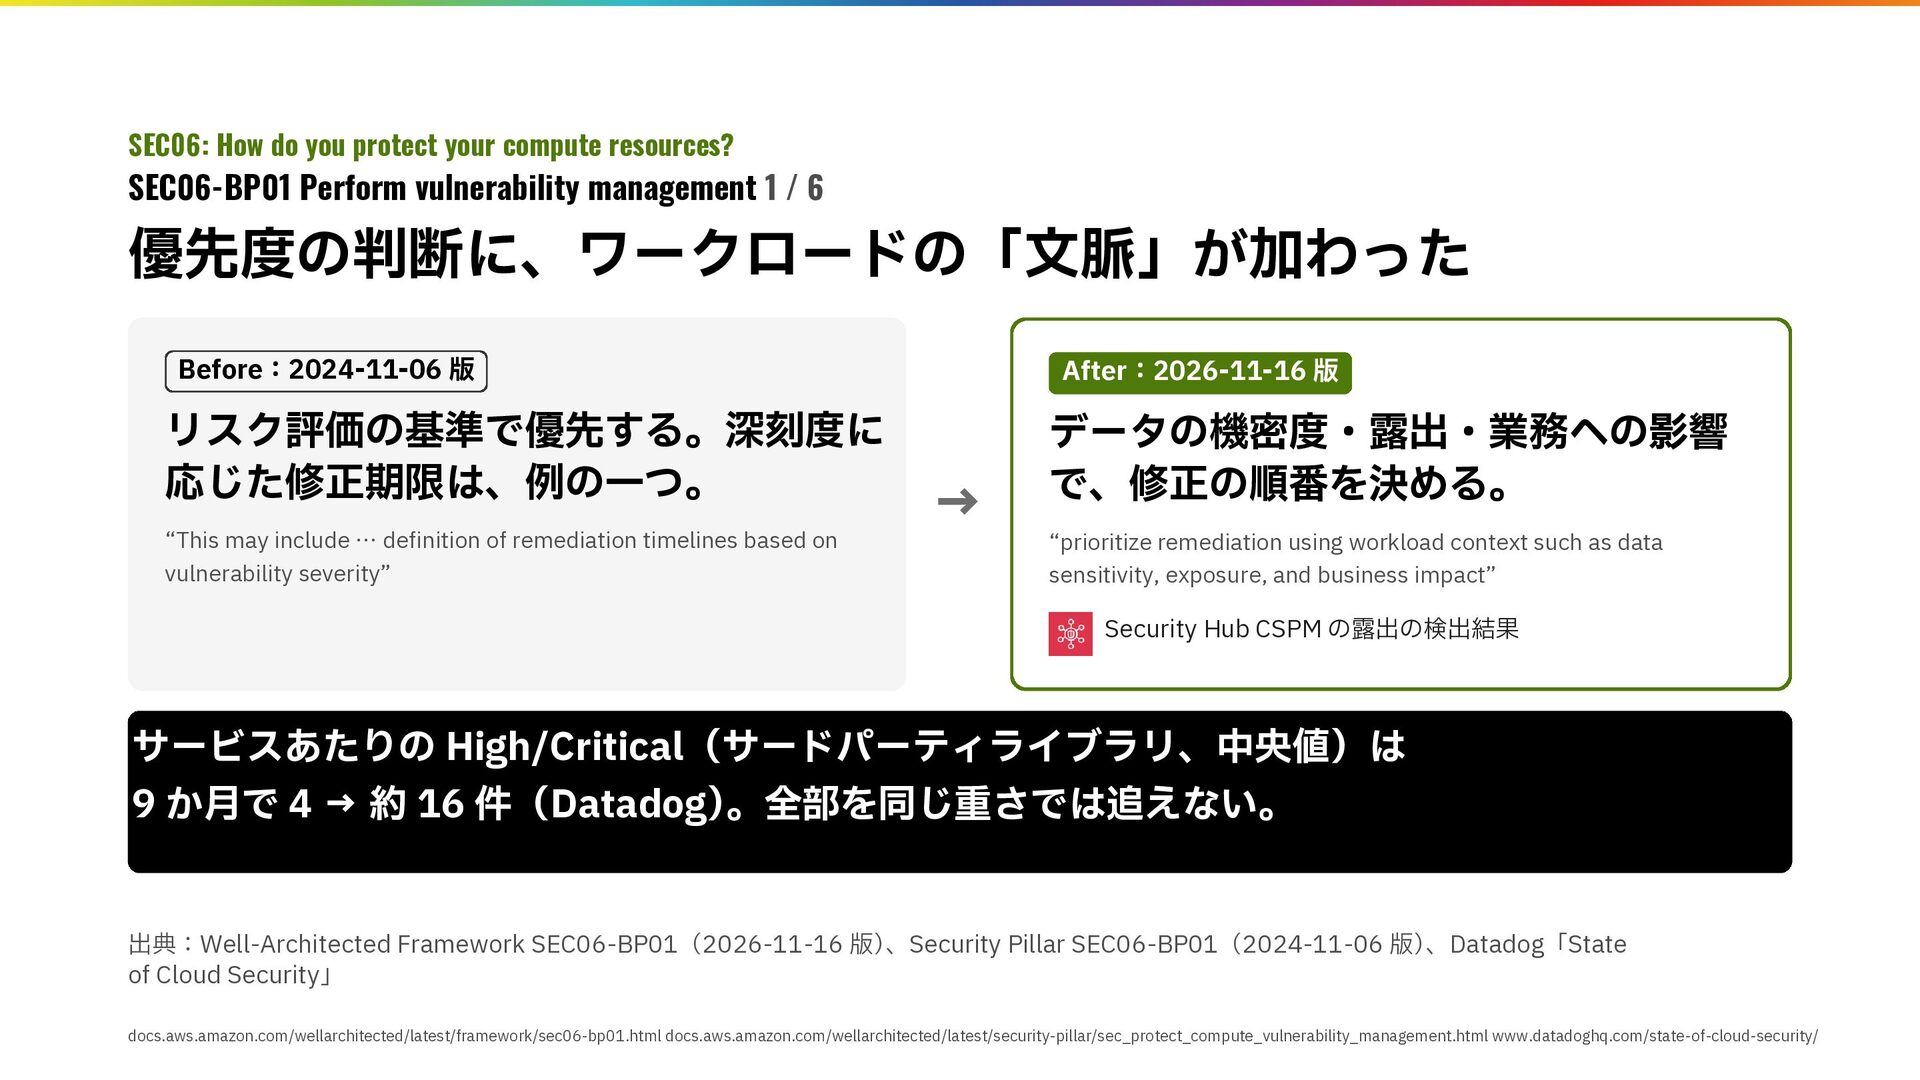
SEC06: How do you protect your compute resources? SEC06-BP01 Perform
vulnerability management 1 / 6 優先度の判断に、ワークロードの「文脈」が加わった Before:2024-11-06 版 After:2026-11-16 版 リスク評価の基準で優先する。深刻度に 応じた修正期限は、例の一つ。 データの機密度・露出・業務への影響 で、修正の順番を決める。 “This may include … definition of remediation timelines based on vulnerability severity” → “prioritize remediation using workload context such as data sensitivity, exposure, and business impact” Security Hub CSPM の露出の検出結果 サービスあたりの High/Critical(サードパーティライブラリ、中央値)は 9 か月で 4 → 約 16 件(Datadog)。全部を同じ重さでは追えない。 出典:Well-Architected Framework SEC06-BP01(2026-11-16 版) 、Security Pillar SEC06-BP01(2024-11-06 版)、Datadog「State of Cloud Security」 docs.aws.amazon.com/wellarchitected/latest/framework/sec06-bp01.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_protect_compute_vulnerability_management.html www.datadoghq.com/state-of-cloud-security/ -
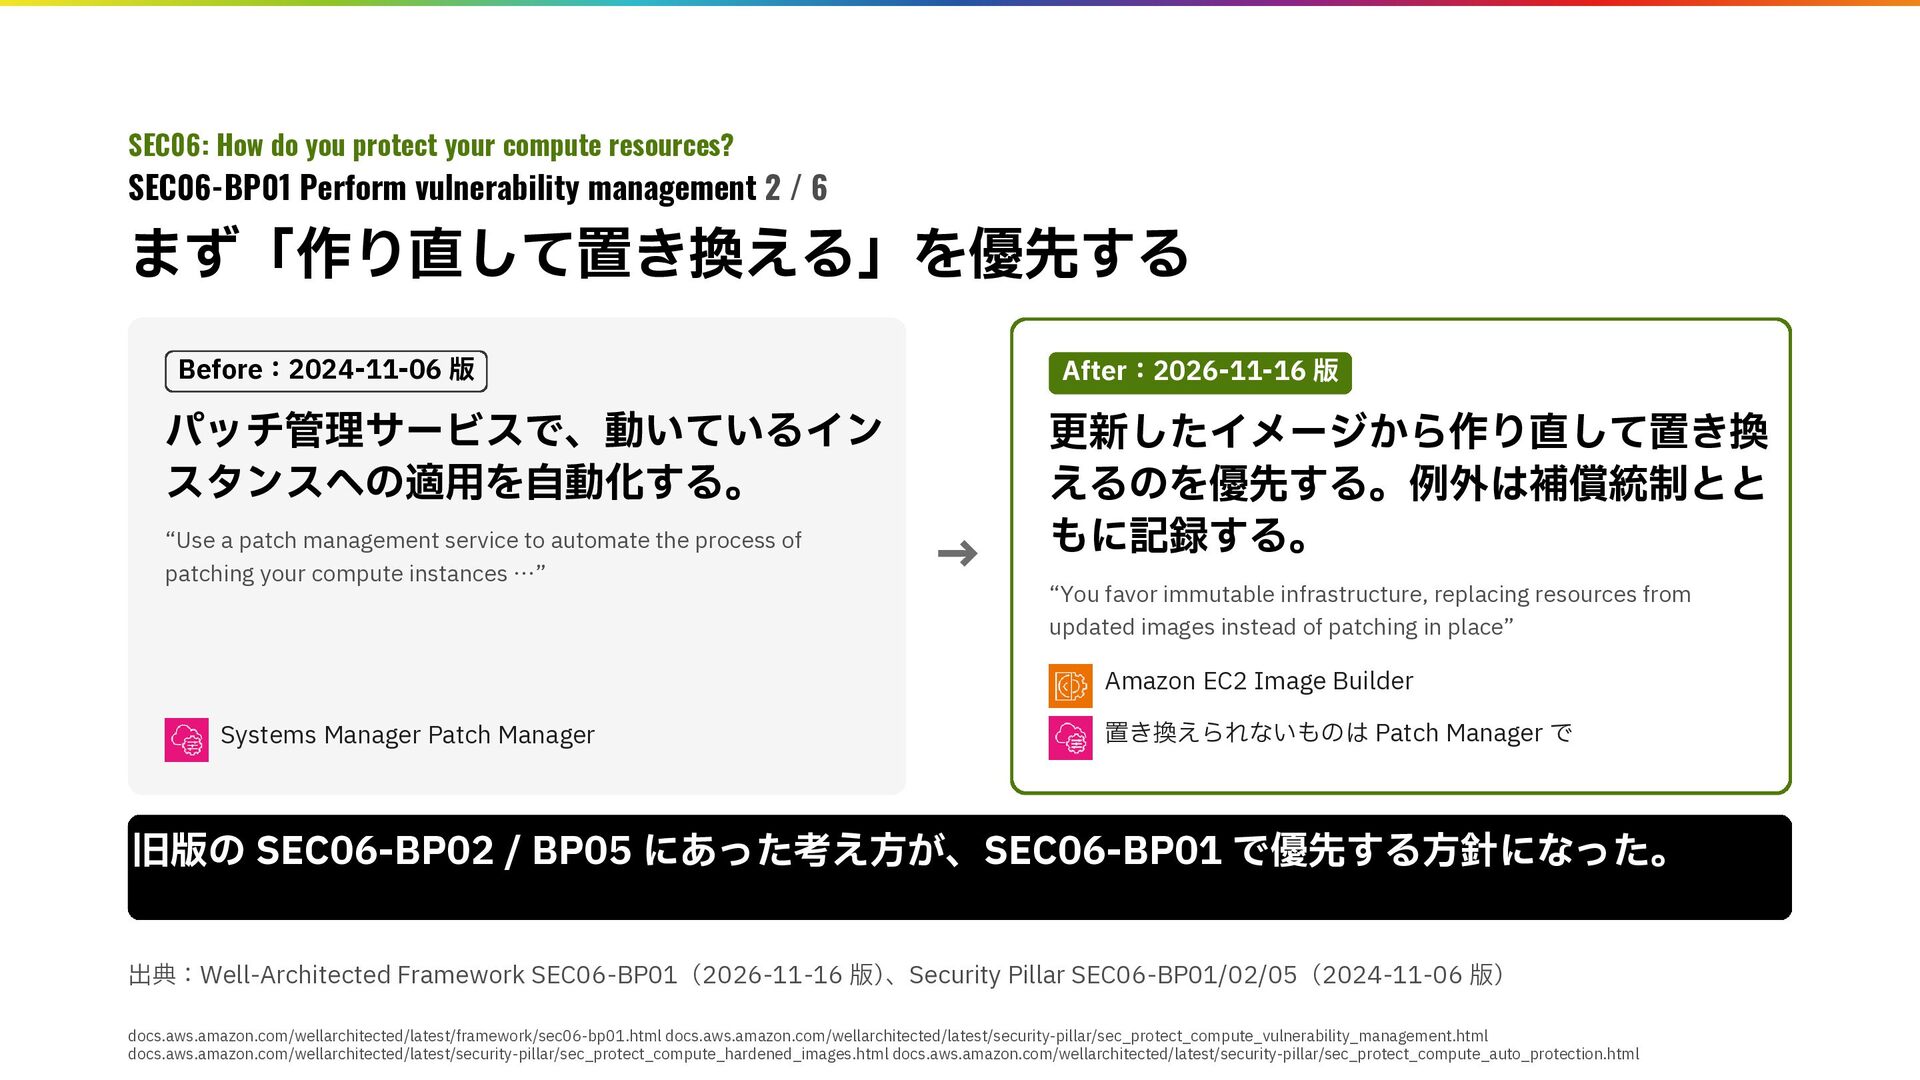
SEC06: How do you protect your compute resources? SEC06-BP01 Perform
vulnerability management 2 / 6 まず「作り直して置き換える」を優先する Before:2024-11-06 版 After:2026-11-16 版 パッチ管理サービスで、動いているイン スタンスへの適用を自動化する。 更新したイメージから作り直して置き換 えるのを優先する。例外は補償統制とと もに記録する。 “Use a patch management service to automate the process of patching your compute instances …” → “You favor immutable infrastructure, replacing resources from updated images instead of patching in place” Amazon EC2 Image Builder Systems Manager Patch Manager 置き換えられないものは Patch Manager で 旧版の SEC06-BP02 / BP05 にあった考え方が、SEC06-BP01 で優先する方針になった。 出典:Well-Architected Framework SEC06-BP01(2026-11-16 版) 、Security Pillar SEC06-BP01/02/05(2024-11-06 版) docs.aws.amazon.com/wellarchitected/latest/framework/sec06-bp01.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_protect_compute_vulnerability_management.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_protect_compute_hardened_images.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_protect_compute_auto_protection.html -
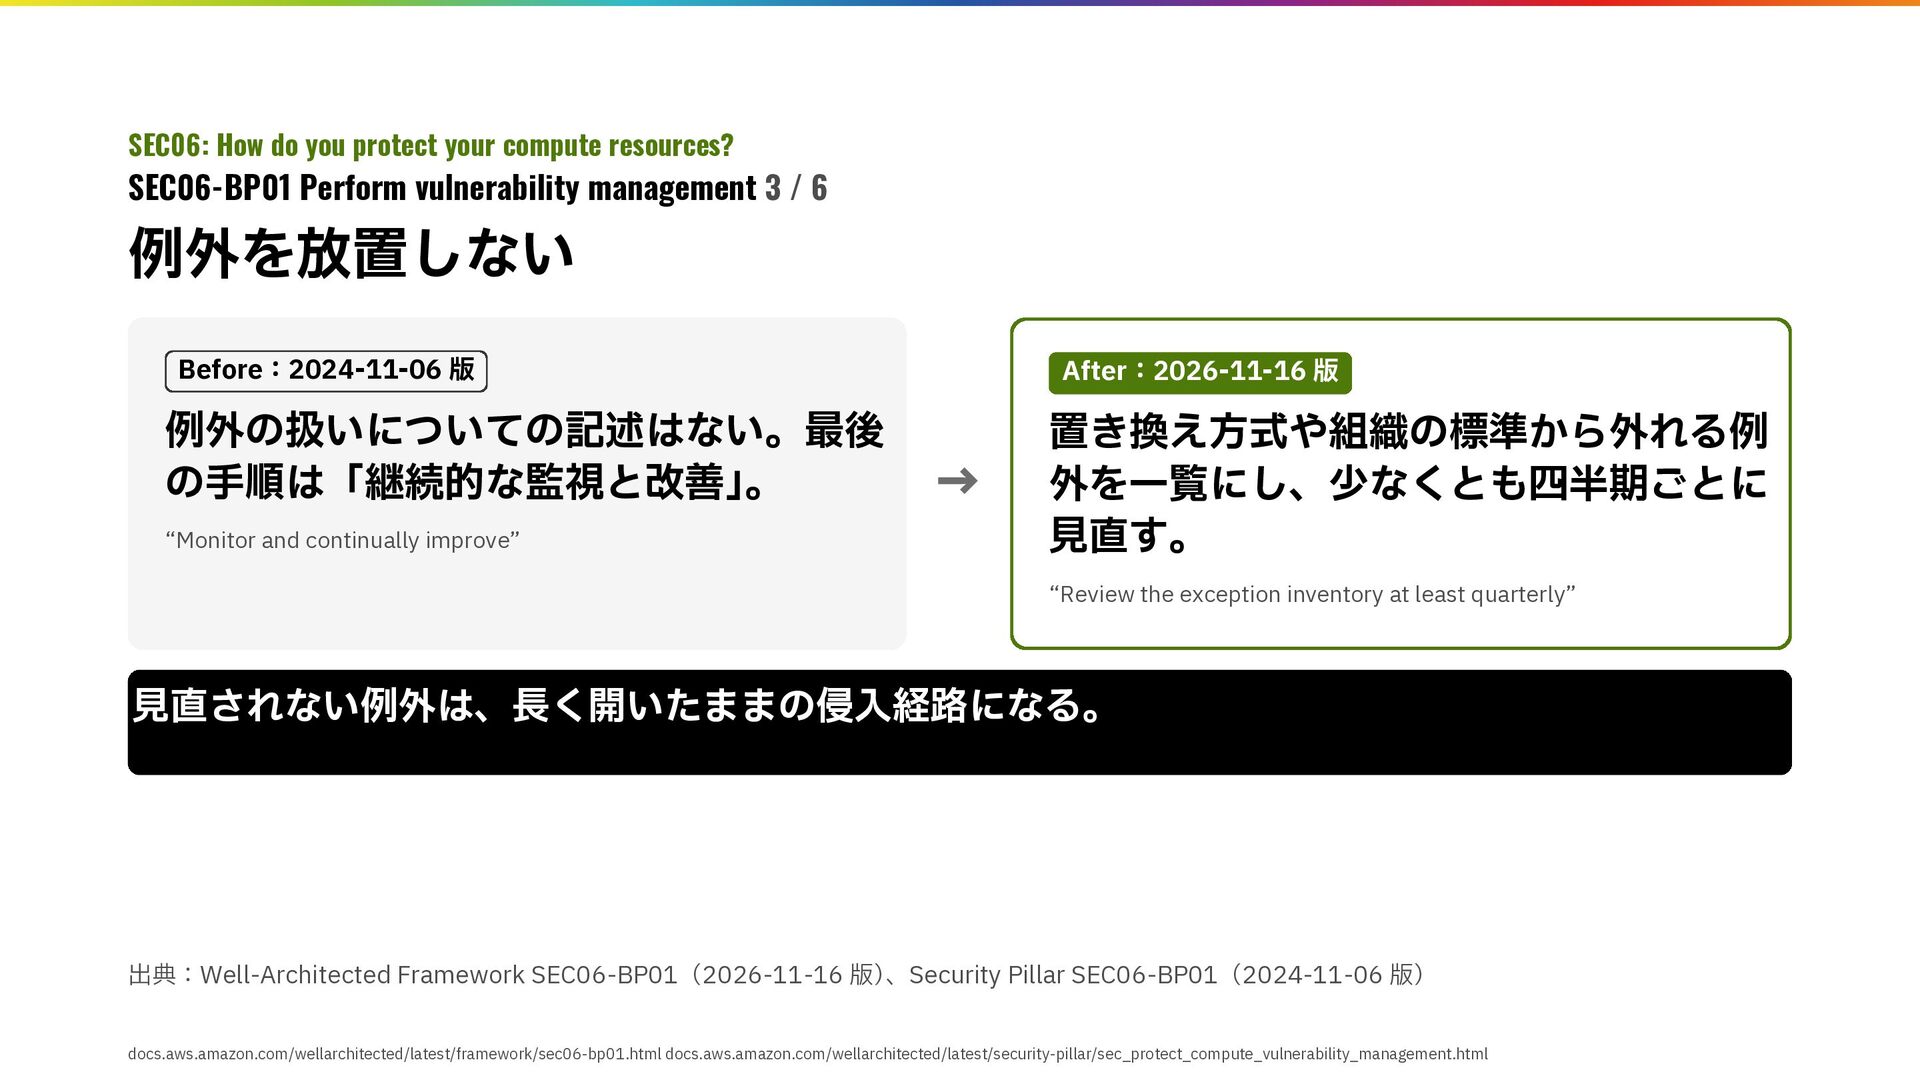
SEC06: How do you protect your compute resources? SEC06-BP01 Perform
vulnerability management 3 / 6 例外を放置しない Before:2024-11-06 版 After:2026-11-16 版 例外の扱いについての記述はない。最後 の手順は「継続的な監視と改善」 。 置き換え方式や組織の標準から外れる例 外を一覧にし、少なくとも四半期ごとに 見直す。 “Monitor and continually improve” → “Review the exception inventory at least quarterly” 見直されない例外は、長く開いたままの侵入経路になる。 出典:Well-Architected Framework SEC06-BP01(2026-11-16 版) 、Security Pillar SEC06-BP01(2024-11-06 版) docs.aws.amazon.com/wellarchitected/latest/framework/sec06-bp01.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_protect_compute_vulnerability_management.html -
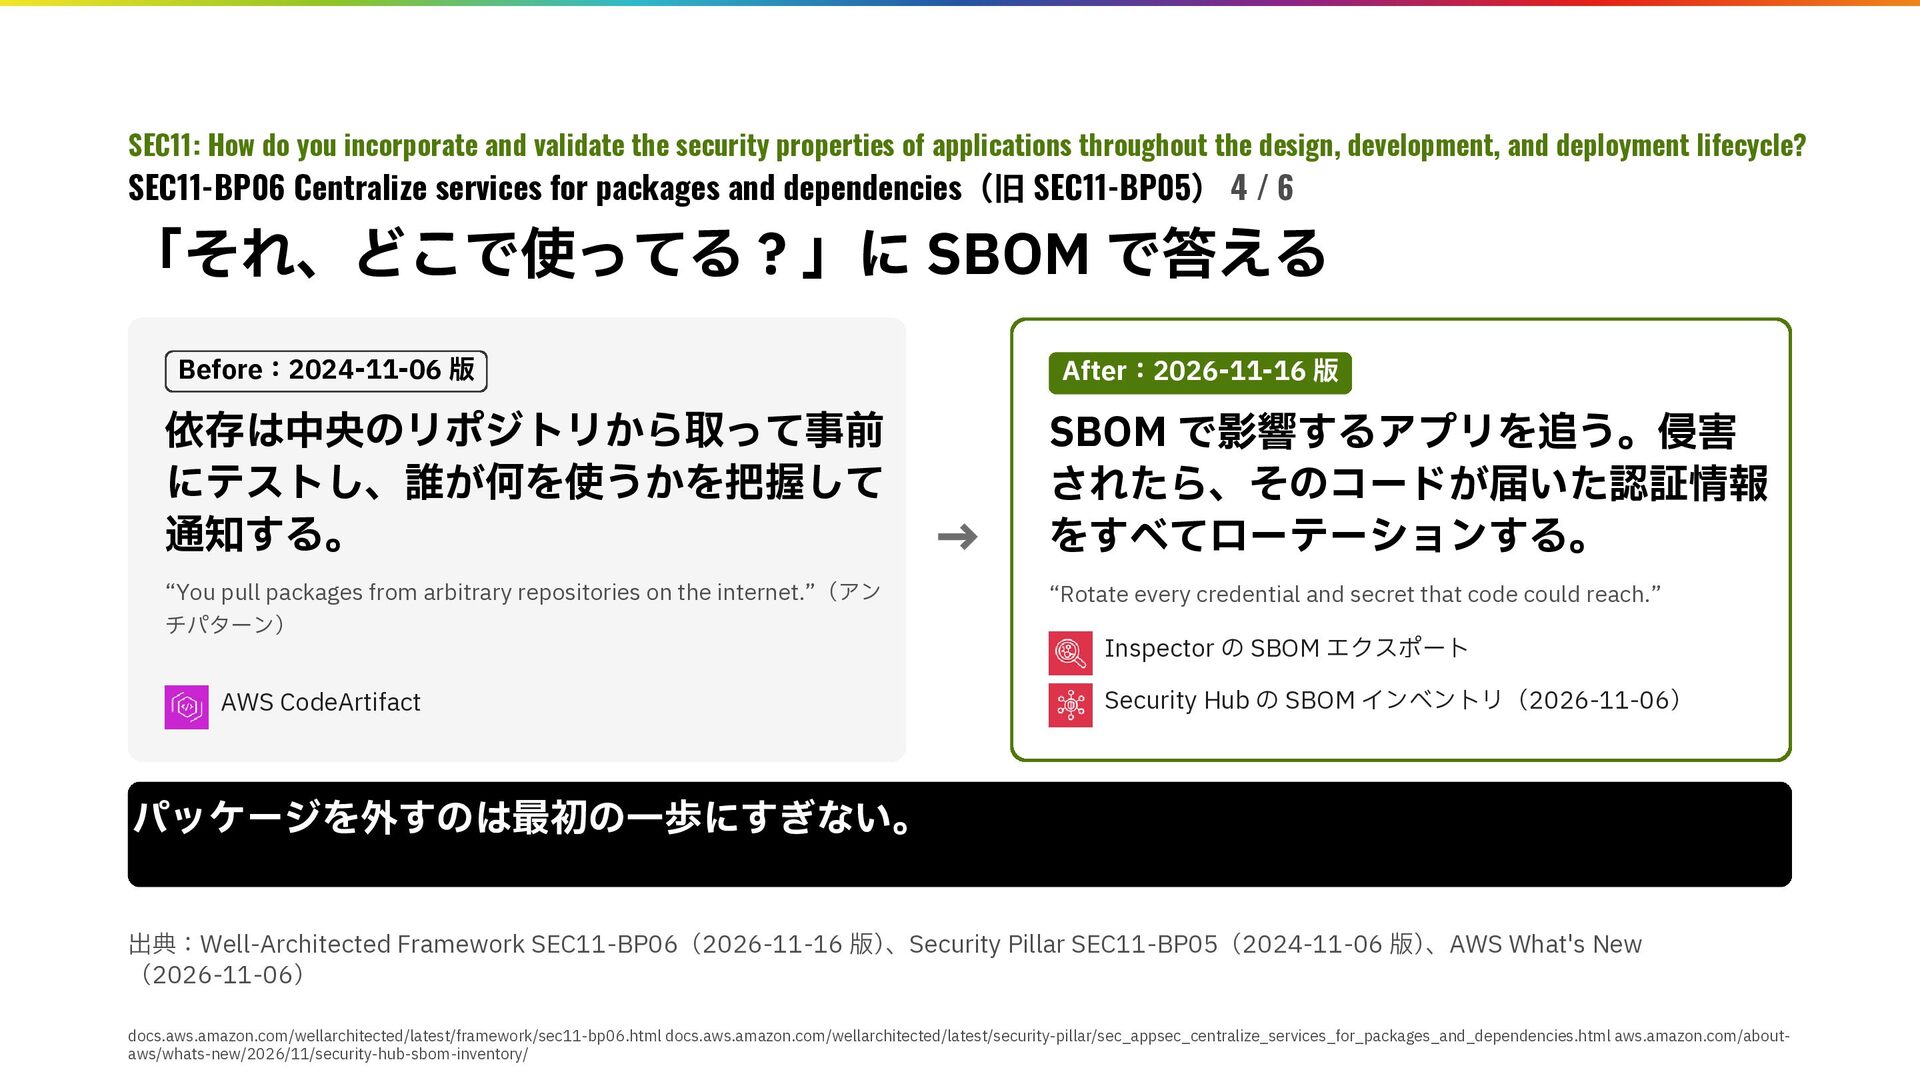
SEC11: How do you incorporate and validate the security properties
of applications throughout the design, development, and deployment lifecycle? SEC11-BP06 Centralize services for packages and dependencies (旧 SEC11-BP05) 4 / 6 「それ、どこで使ってる?」に SBOM で答える Before:2024-11-06 版 After:2026-11-16 版 依存は中央のリポジトリから取って事前 にテストし、誰が何を使うかを把握して 通知する。 SBOM で影響するアプリを追う。侵害 されたら、そのコードが届いた認証情報 をすべてローテーションする。 “You pull packages from arbitrary repositories on the internet.”(アン チパターン) AWS CodeArtifact → “Rotate every credential and secret that code could reach.” Inspector の SBOM エクスポート Security Hub の SBOM インベントリ(2026-11-06) パッケージを外すのは最初の一歩にすぎない。 出典:Well-Architected Framework SEC11-BP06(2026-11-16 版) 、Security Pillar SEC11-BP05(2024-11-06 版)、AWS What's New (2026-11-06) docs.aws.amazon.com/wellarchitected/latest/framework/sec11-bp06.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_appsec_centralize_services_for_packages_and_dependencies.html aws.amazon.com/aboutaws/whats-new/2026/11/security-hub-sbom-inventory/ -
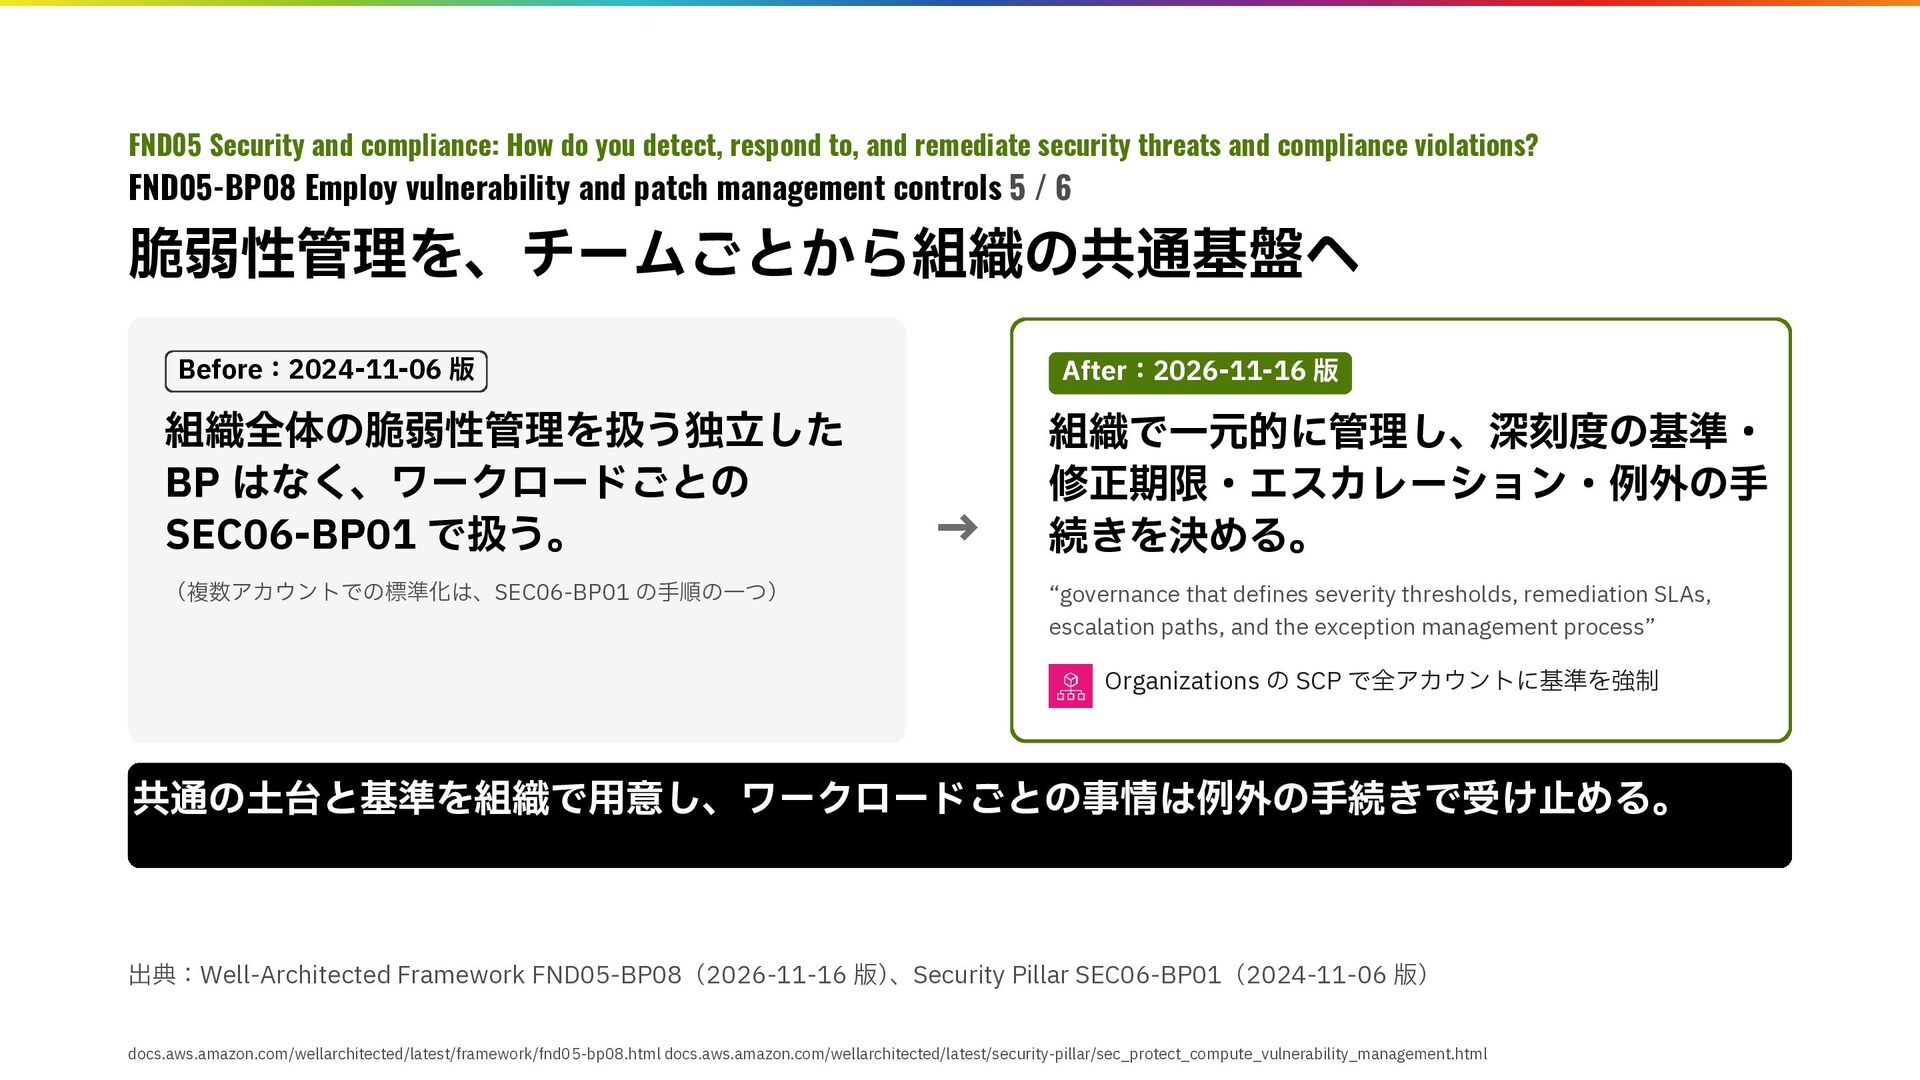
FND05 Security and compliance: How do you detect, respond to,
and remediate security threats and compliance violations? FND05-BP08 Employ vulnerability and patch management controls 5 / 6 脆弱性管理を、チームごとから組織の共通基盤へ Before:2024-11-06 版 After:2026-11-16 版 組織全体の脆弱性管理を扱う独立した BP はなく、ワークロードごとの SEC06-BP01 で扱う。 組織で一元的に管理し、深刻度の基準・ 修正期限・エスカレーション・例外の手 続きを決める。 (複数アカウントでの標準化は、SEC06-BP01 の手順の一つ) → “governance that defines severity thresholds, remediation SLAs, escalation paths, and the exception management process” Organizations の SCP で全アカウントに基準を強制 共通の土台と基準を組織で用意し、ワークロードごとの事情は例外の手続きで受け止める。 出典:Well-Architected Framework FND05-BP08(2026-11-16 版) 、Security Pillar SEC06-BP01(2024-11-06 版) docs.aws.amazon.com/wellarchitected/latest/framework/fnd05-bp08.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_protect_compute_vulnerability_management.html -
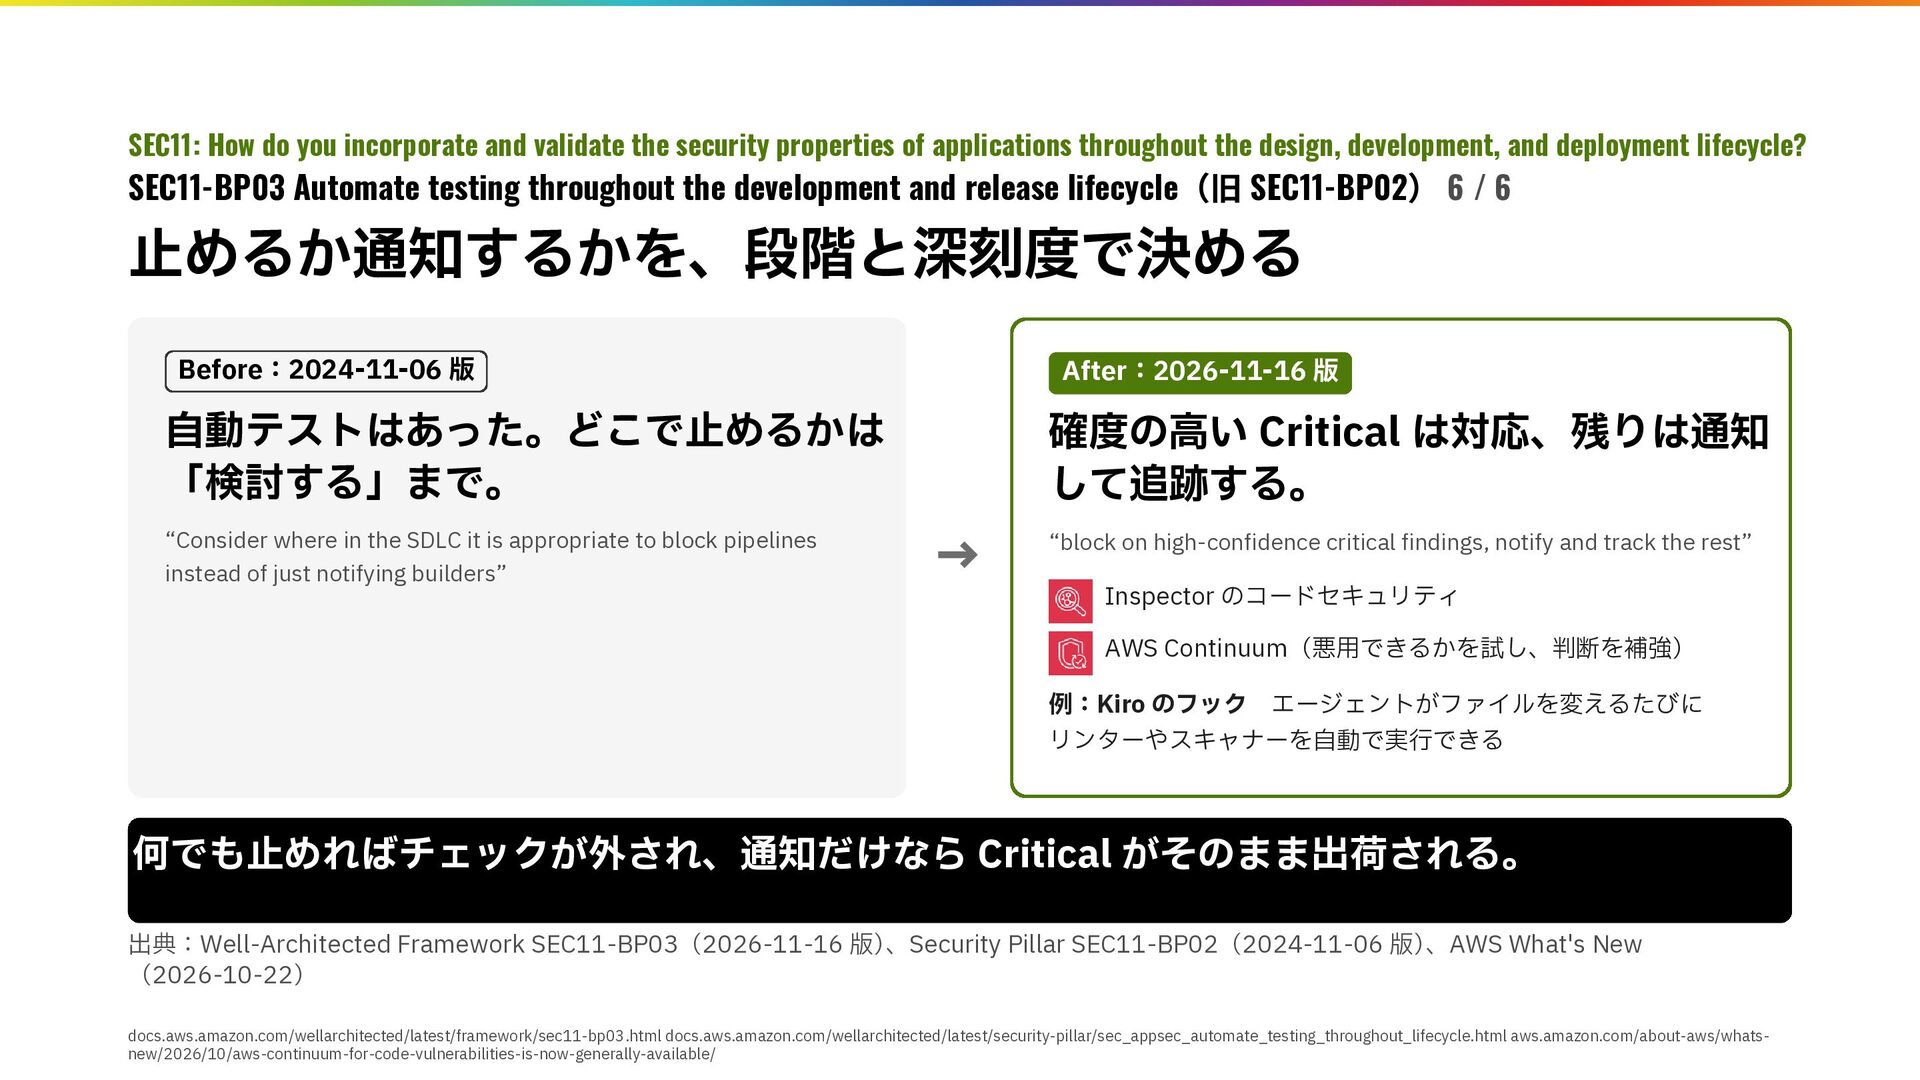
SEC11: How do you incorporate and validate the security properties
of applications throughout the design, development, and deployment lifecycle? SEC11-BP03 Automate testing throughout the development and release lifecycle (旧 SEC11-BP02) 6 / 6 止めるか通知するかを、段階と深刻度で決める Before:2024-11-06 版 After:2026-11-16 版 自動テストはあった。どこで止めるかは 「検討する」まで。 確度の高い Critical は対応、残りは通知 して追跡する。 “Consider where in the SDLC it is appropriate to block pipelines instead of just notifying builders” → “block on high-confidence critical findings, notify and track the rest” Inspector のコードセキュリティ AWS Continuum(悪用できるかを試し、判断を補強) 例:Kiro のフック エージェントがファイルを変えるたびに リンターやスキャナーを自動で実行できる 何でも止めればチェックが外され、通知だけなら Critical がそのまま出荷される。 出典:Well-Architected Framework SEC11-BP03(2026-11-16 版) 、Security Pillar SEC11-BP02(2024-11-06 版)、AWS What's New (2026-10-22) docs.aws.amazon.com/wellarchitected/latest/framework/sec11-bp03.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/sec_appsec_automate_testing_throughout_lifecycle.html aws.amazon.com/about-aws/whatsnew/2026/10/aws-continuum-for-code-vulnerabilities-is-now-generally-available/ -
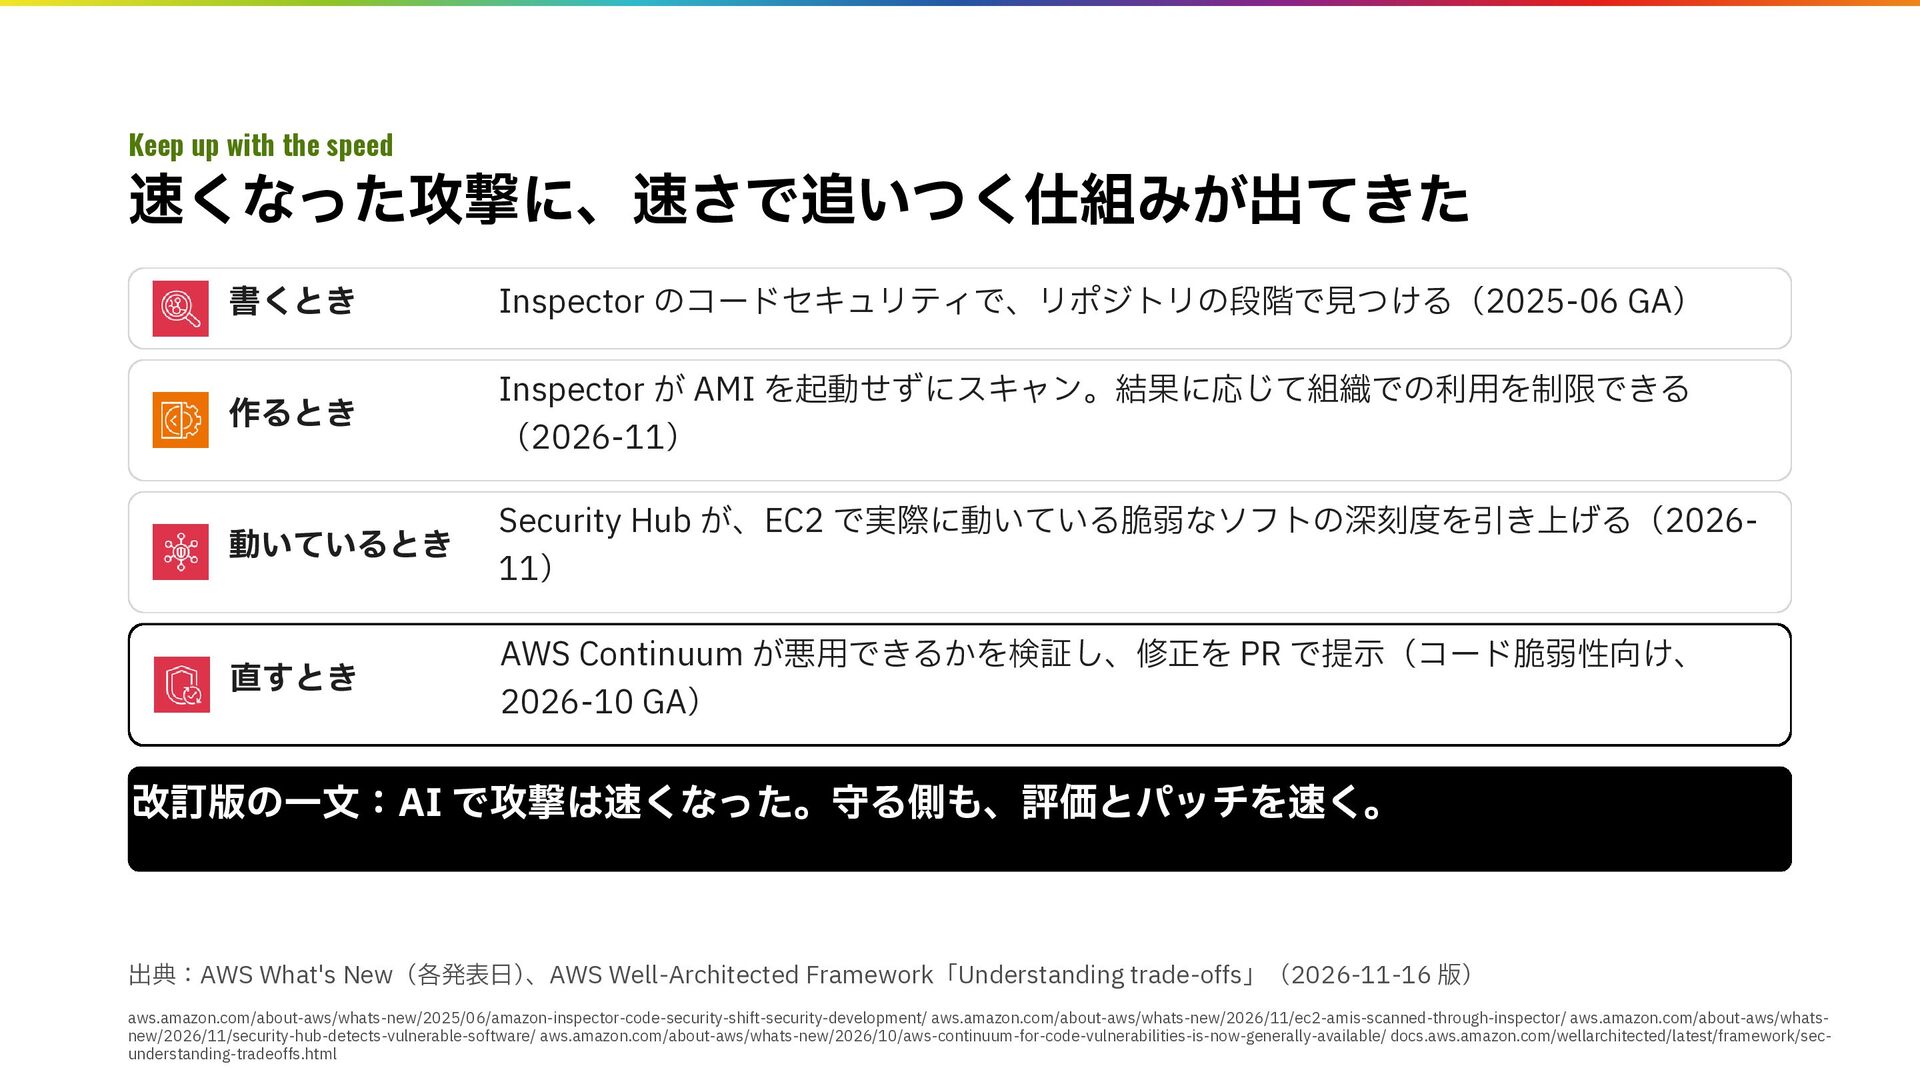
Keep up with the speed 速くなった攻撃に、速さで追いつく仕組みが出てきた 書くとき Inspector のコードセキュリティで、リポジトリの段階で見つける(2025-06 GA)
作るとき Inspector が AMI を起動せずにスキャン。結果に応じて組織での利用を制限できる (2026-11) 動いているとき Security Hub が、EC2 で実際に動いている脆弱なソフトの深刻度を引き上げる(202611) 直すとき AWS Continuum が悪用できるかを検証し、修正を PR で提示(コード脆弱性向け、 2026-10 GA) 改訂版の一文:AI で攻撃は速くなった。守る側も、評価とパッチを速く。 出典:AWS What's New(各発表日) 、AWS Well-Architected Framework「Understanding trade-offs」(2026-11-16 版) aws.amazon.com/about-aws/whats-new/2025/06/amazon-inspector-code-security-shift-security-development/ aws.amazon.com/about-aws/whats-new/2026/11/ec2-amis-scanned-through-inspector/ aws.amazon.com/about-aws/whatsnew/2026/11/security-hub-detects-vulnerable-software/ aws.amazon.com/about-aws/whats-new/2026/10/aws-continuum-for-code-vulnerabilities-is-now-generally-available/ docs.aws.amazon.com/wellarchitected/latest/framework/secunderstanding-tradeoffs.html -
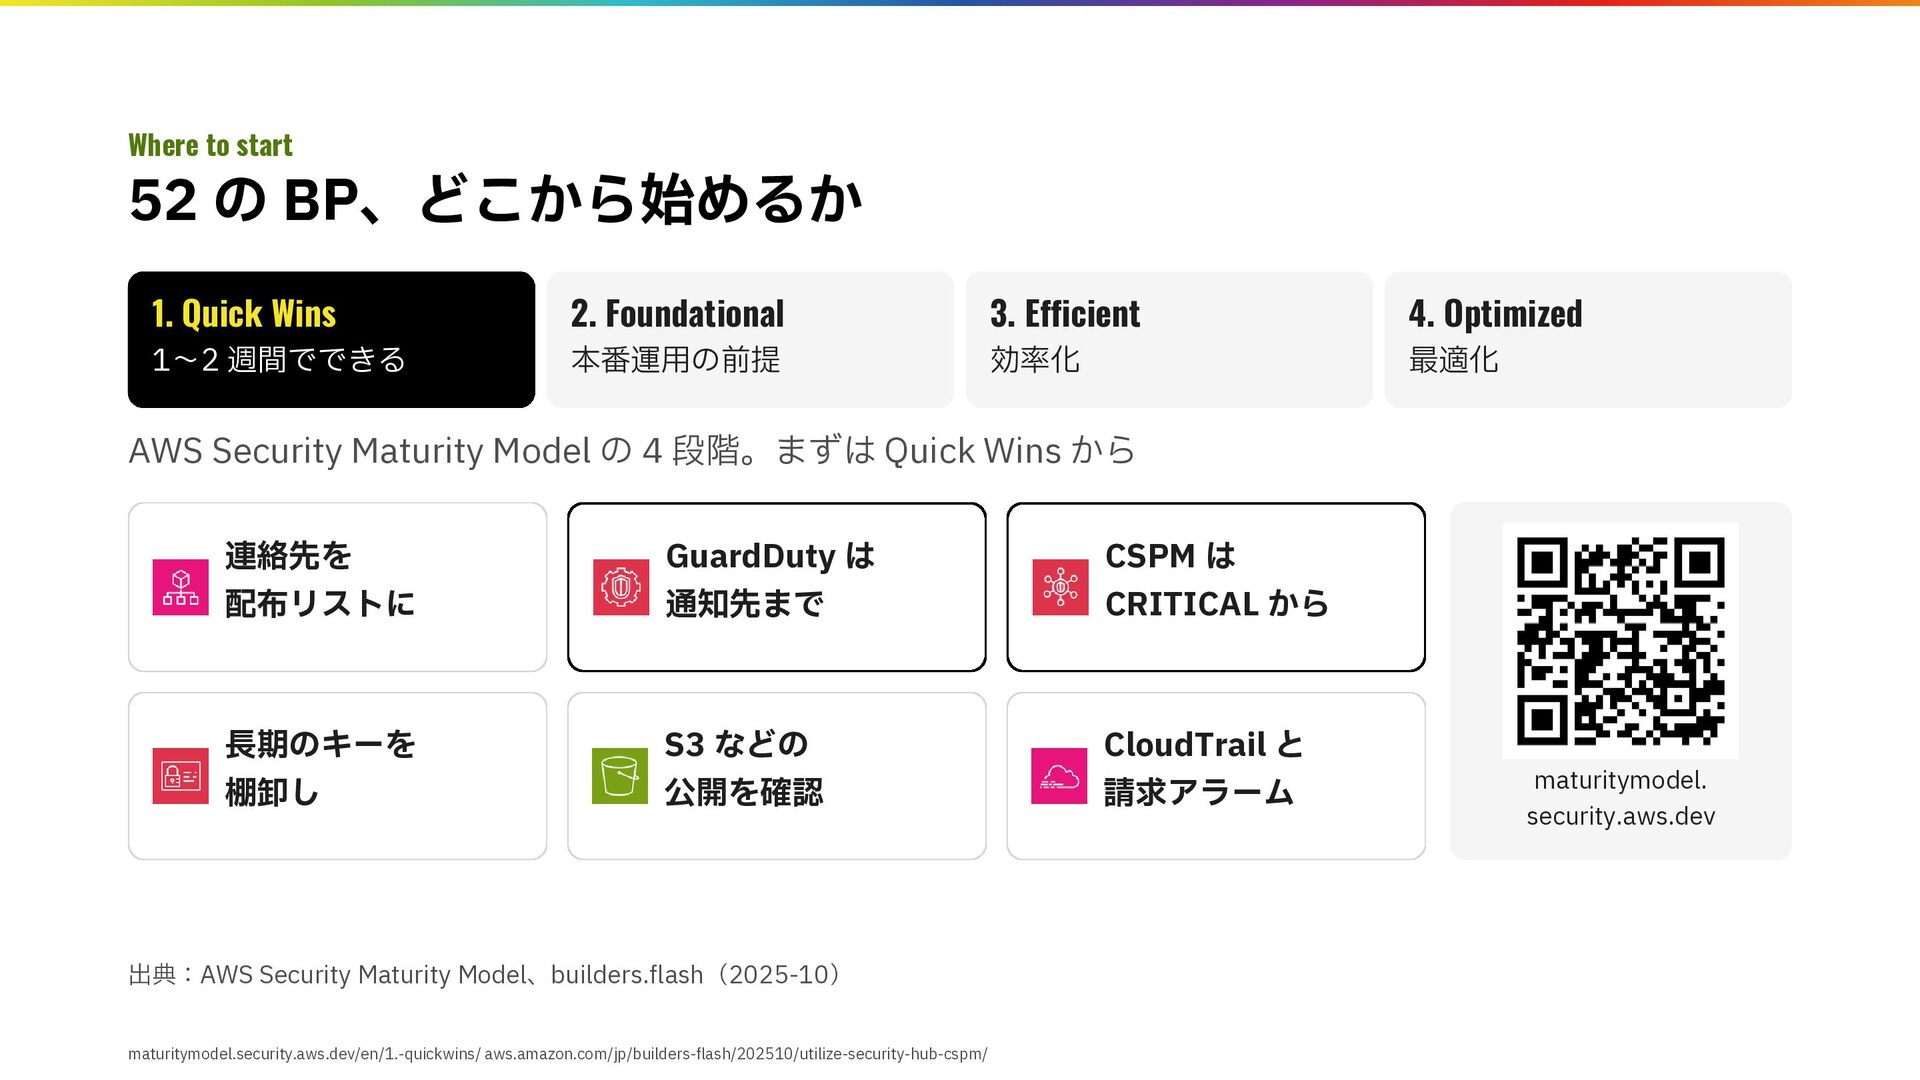
Where to start 52 の BP、どこから始めるか 1. Quick Wins 2.
Foundational 3. Efficient 4. Optimized 1〜2 週間でできる 本番運用の前提 効率化 最適化 AWS Security Maturity Model の 4 段階。まずは Quick Wins から 連絡先を 配布リストに GuardDuty は 通知先まで CSPM は CRITICAL から 長期のキーを 棚卸し S3 などの 公開を確認 CloudTrail と 請求アラーム 出典:AWS Security Maturity Model、builders.flash(2025-10) maturitymodel.security.aws.dev/en/1.-quickwins/ aws.amazon.com/jp/builders-flash/202510/utilize-security-hub-cspm/ maturitymodel. security.aws.dev -
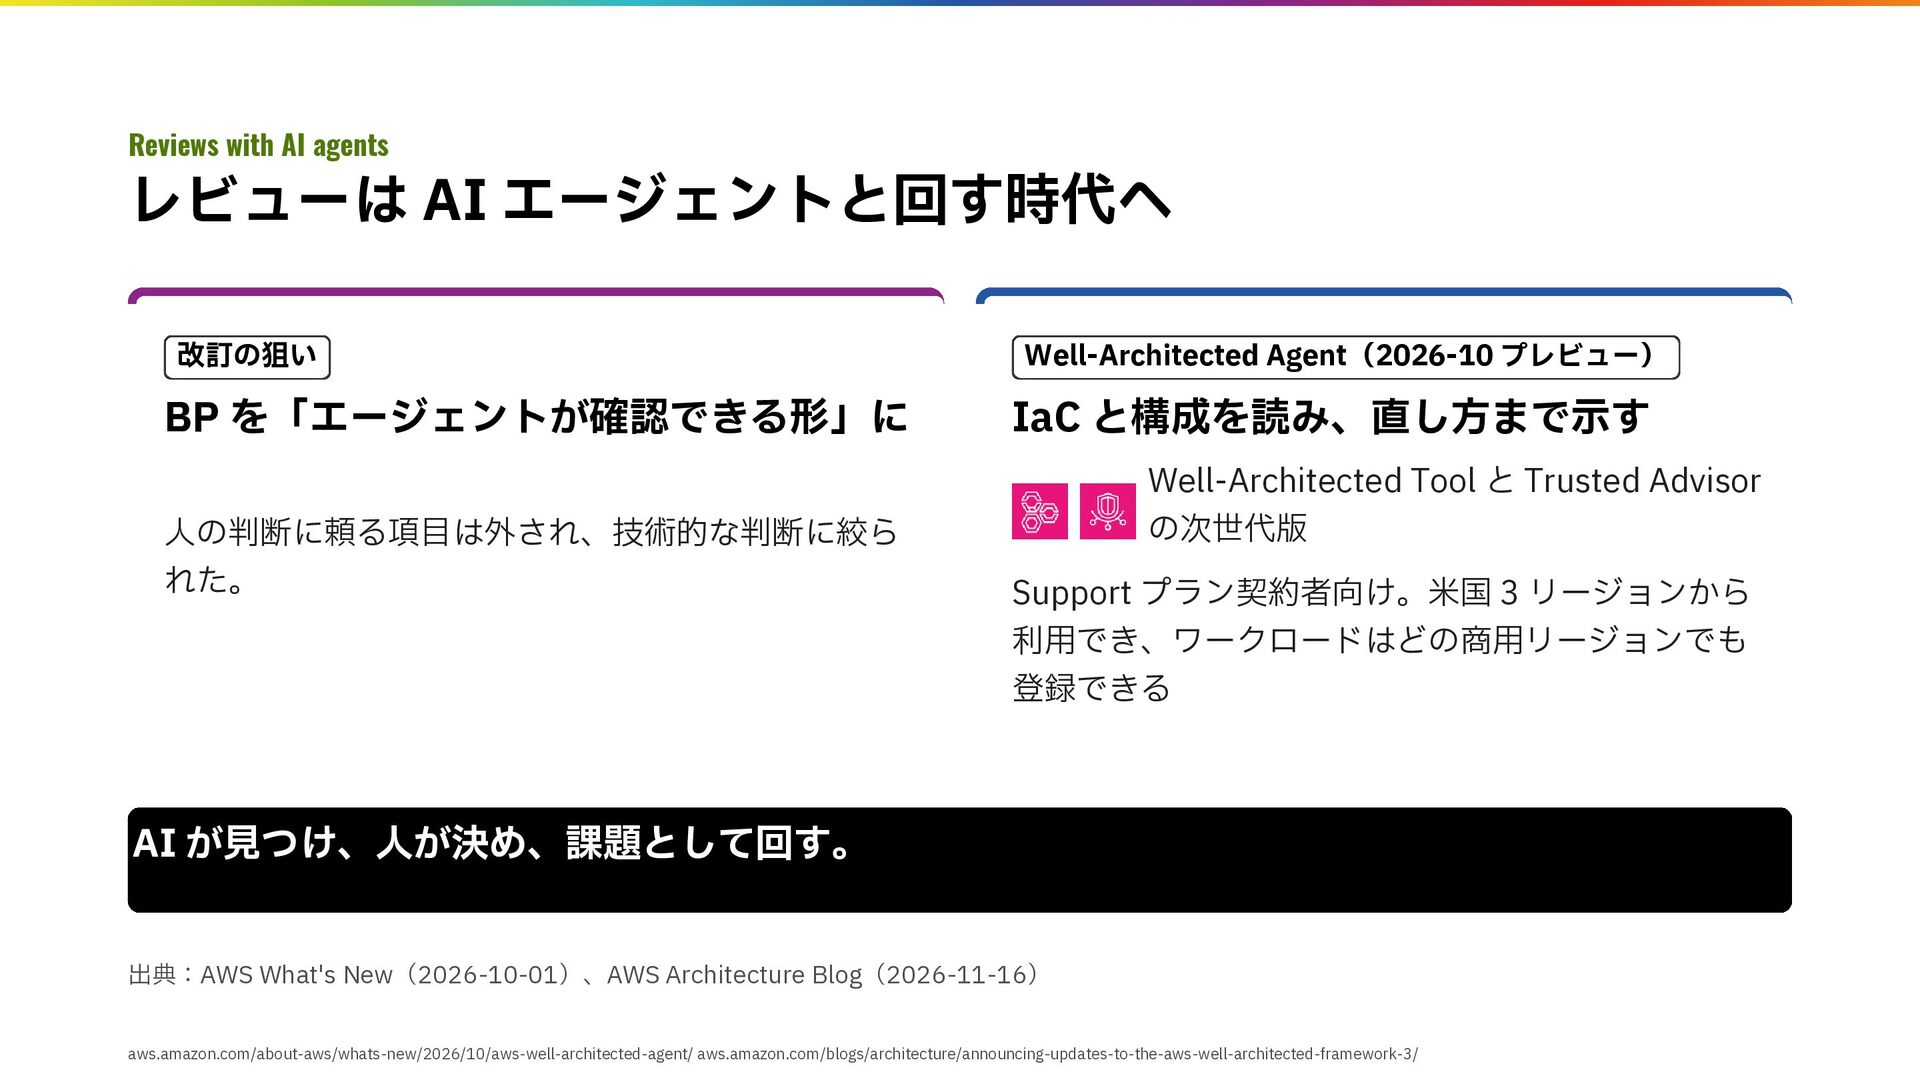
Reviews with AI agents レビューは AI エージェントと回す時代へ 改訂の狙い Well-Architected Agent(2026-10
プレビュー) BP を「エージェントが確認できる形」に IaC と構成を読み、直し方まで示す 人の判断に頼る項目は外され、技術的な判断に絞ら れた。 Well-Architected Tool と Trusted Advisor の次世代版 Support プラン契約者向け。米国 3 リージョンから 利用でき、ワークロードはどの商用リージョンでも 登録できる AI が見つけ、人が決め、課題として回す。 出典:AWS What's New(2026-10-01)、AWS Architecture Blog(2026-11-16) aws.amazon.com/about-aws/whats-new/2026/10/aws-well-architected-agent/ aws.amazon.com/blogs/architecture/announcing-updates-to-the-aws-well-architected-framework-3/ -
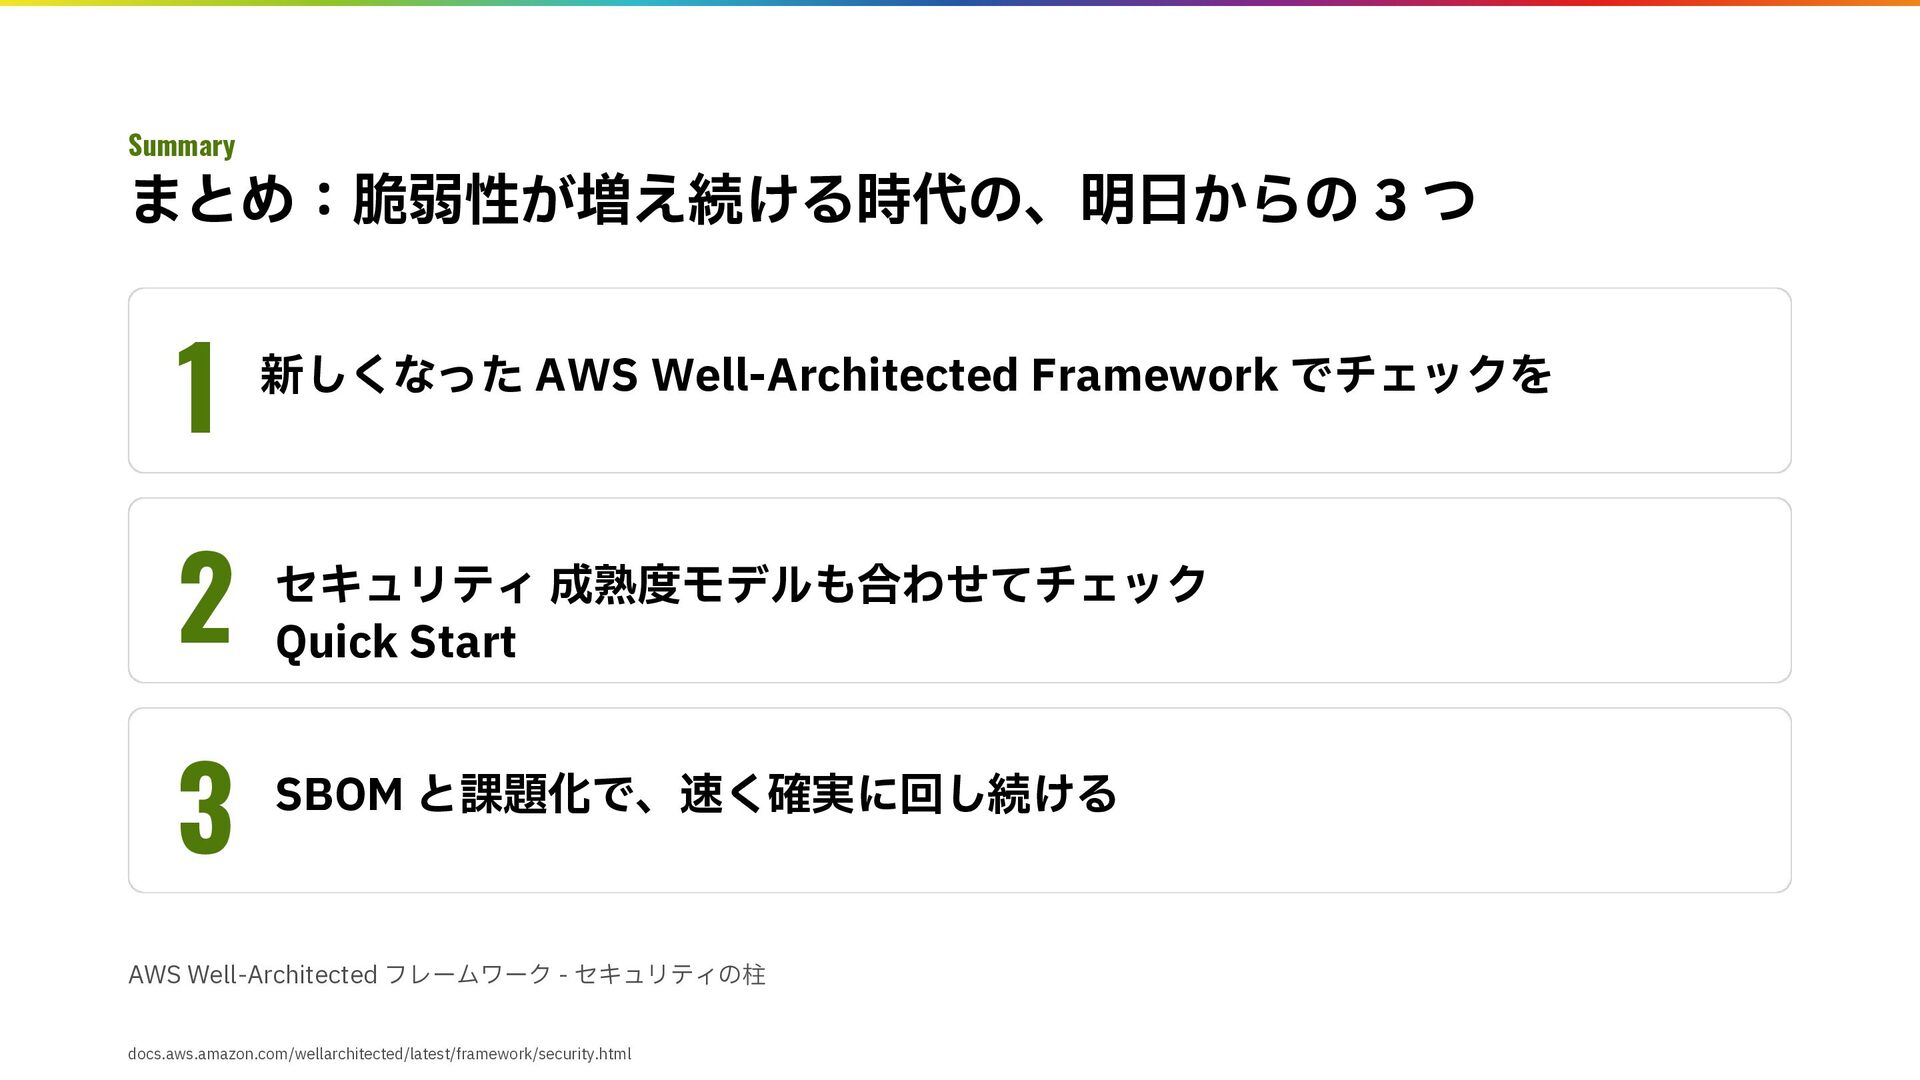
Summary まとめ:脆弱性が増え続ける時代の、明日からの 3 つ 1 2 3 新しくなった AWS Well-Architected
Framework でチェックを セキュリティ 成熟度モデルも合わせてチェック Quick Start SBOM と課題化で、速く確実に回し続ける AWS Well-Architected フレームワーク - セキュリティの柱 docs.aws.amazon.com/wellarchitected/latest/framework/security.html -
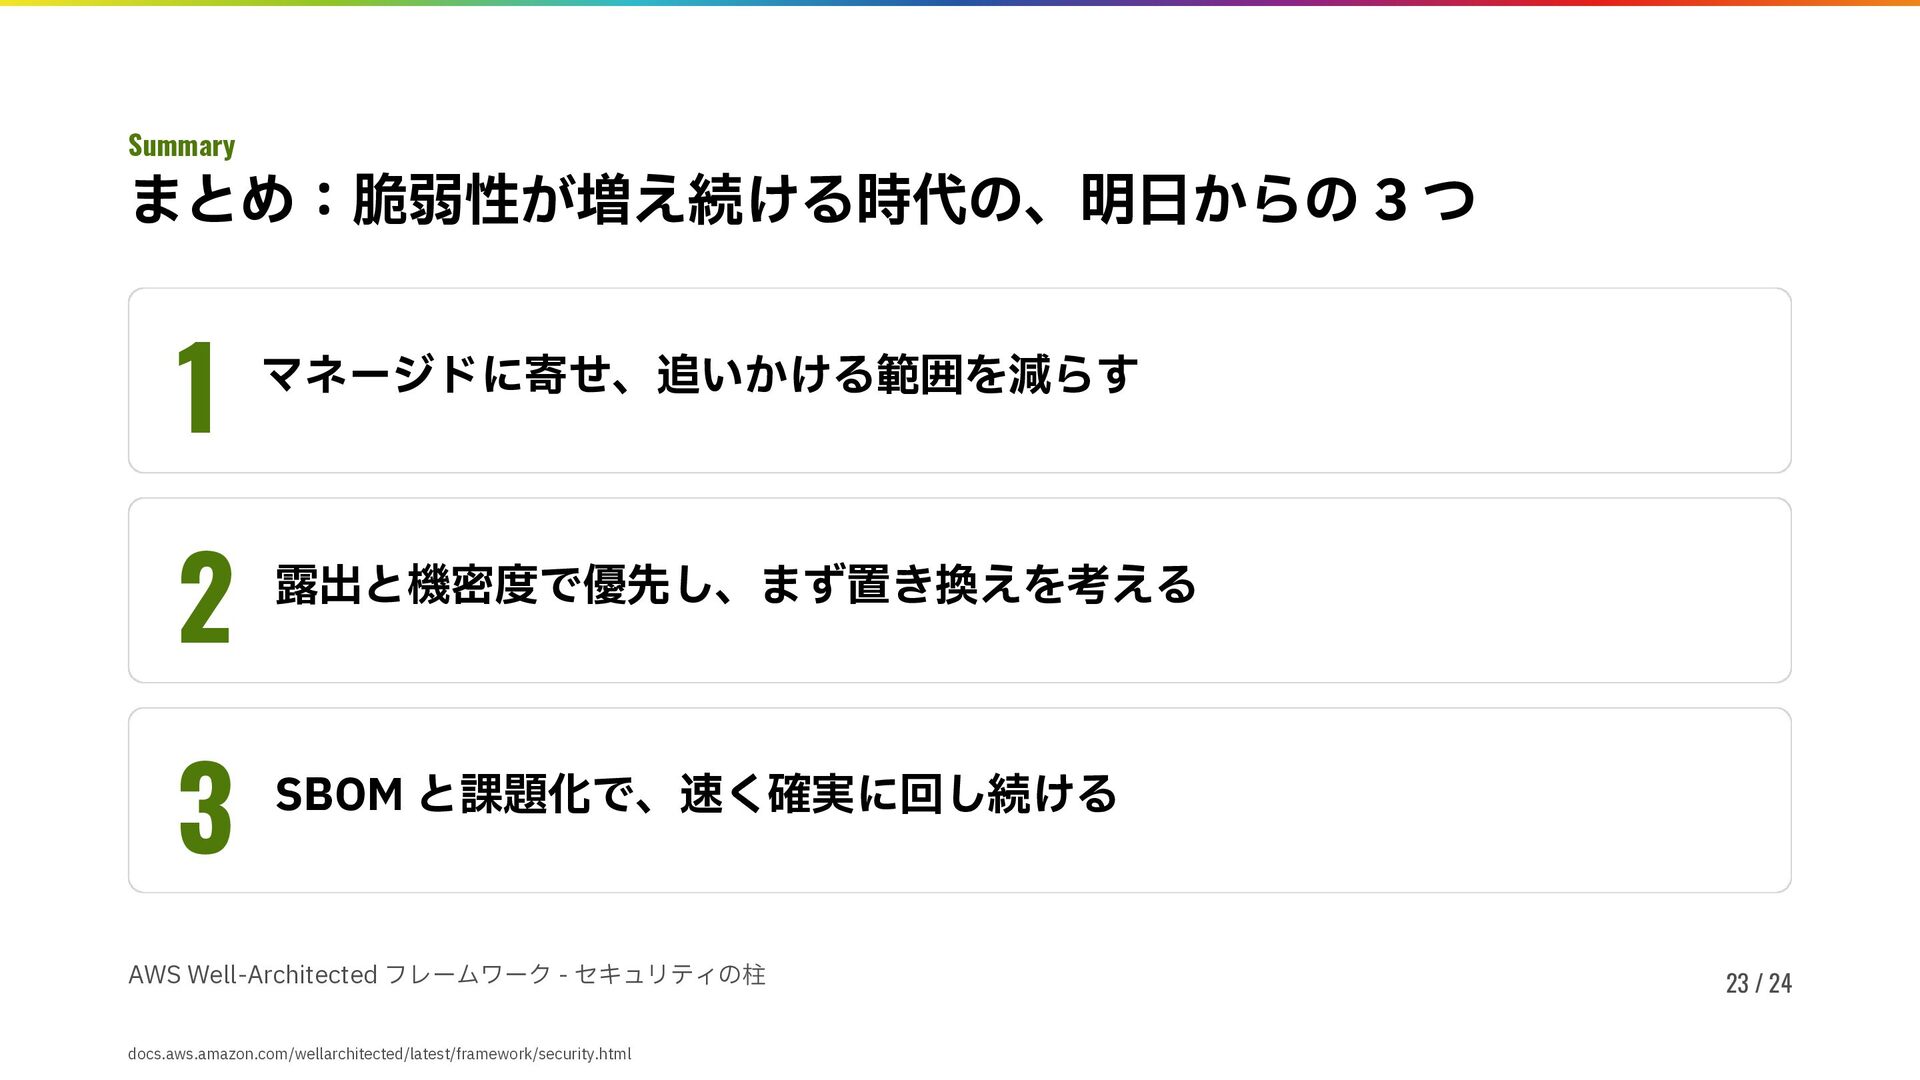
Summary まとめ:脆弱性が増え続ける時代の、明日からの 3 つ 1 マネージドに寄せ、追いかける範囲を減らす 2 露出と機密度で優先し、まず置き換えを考える 3 SBOM
と課題化で、速く確実に回し続ける AWS Well-Architected フレームワーク - セキュリティの柱 docs.aws.amazon.com/wellarchitected/latest/framework/security.html 23 / 24 -
Thank you ご清聴ありがとうございました 株式会社ヘプタゴン 地方の DX をリードするクラウド専業インテグレーター Hall 7 7505
で ブースも出してるので遊びに来てください! -
Appendix 補足資料 11 の質問・設計原則と 4 つの領域・優先度と SBOM の補足・全 52 BP
の確認の観点 新旧の対応表・Cloud Foundations の関連 BP・アップデートの年表・生成 AI・統計・Quick Wins・参考リンク -
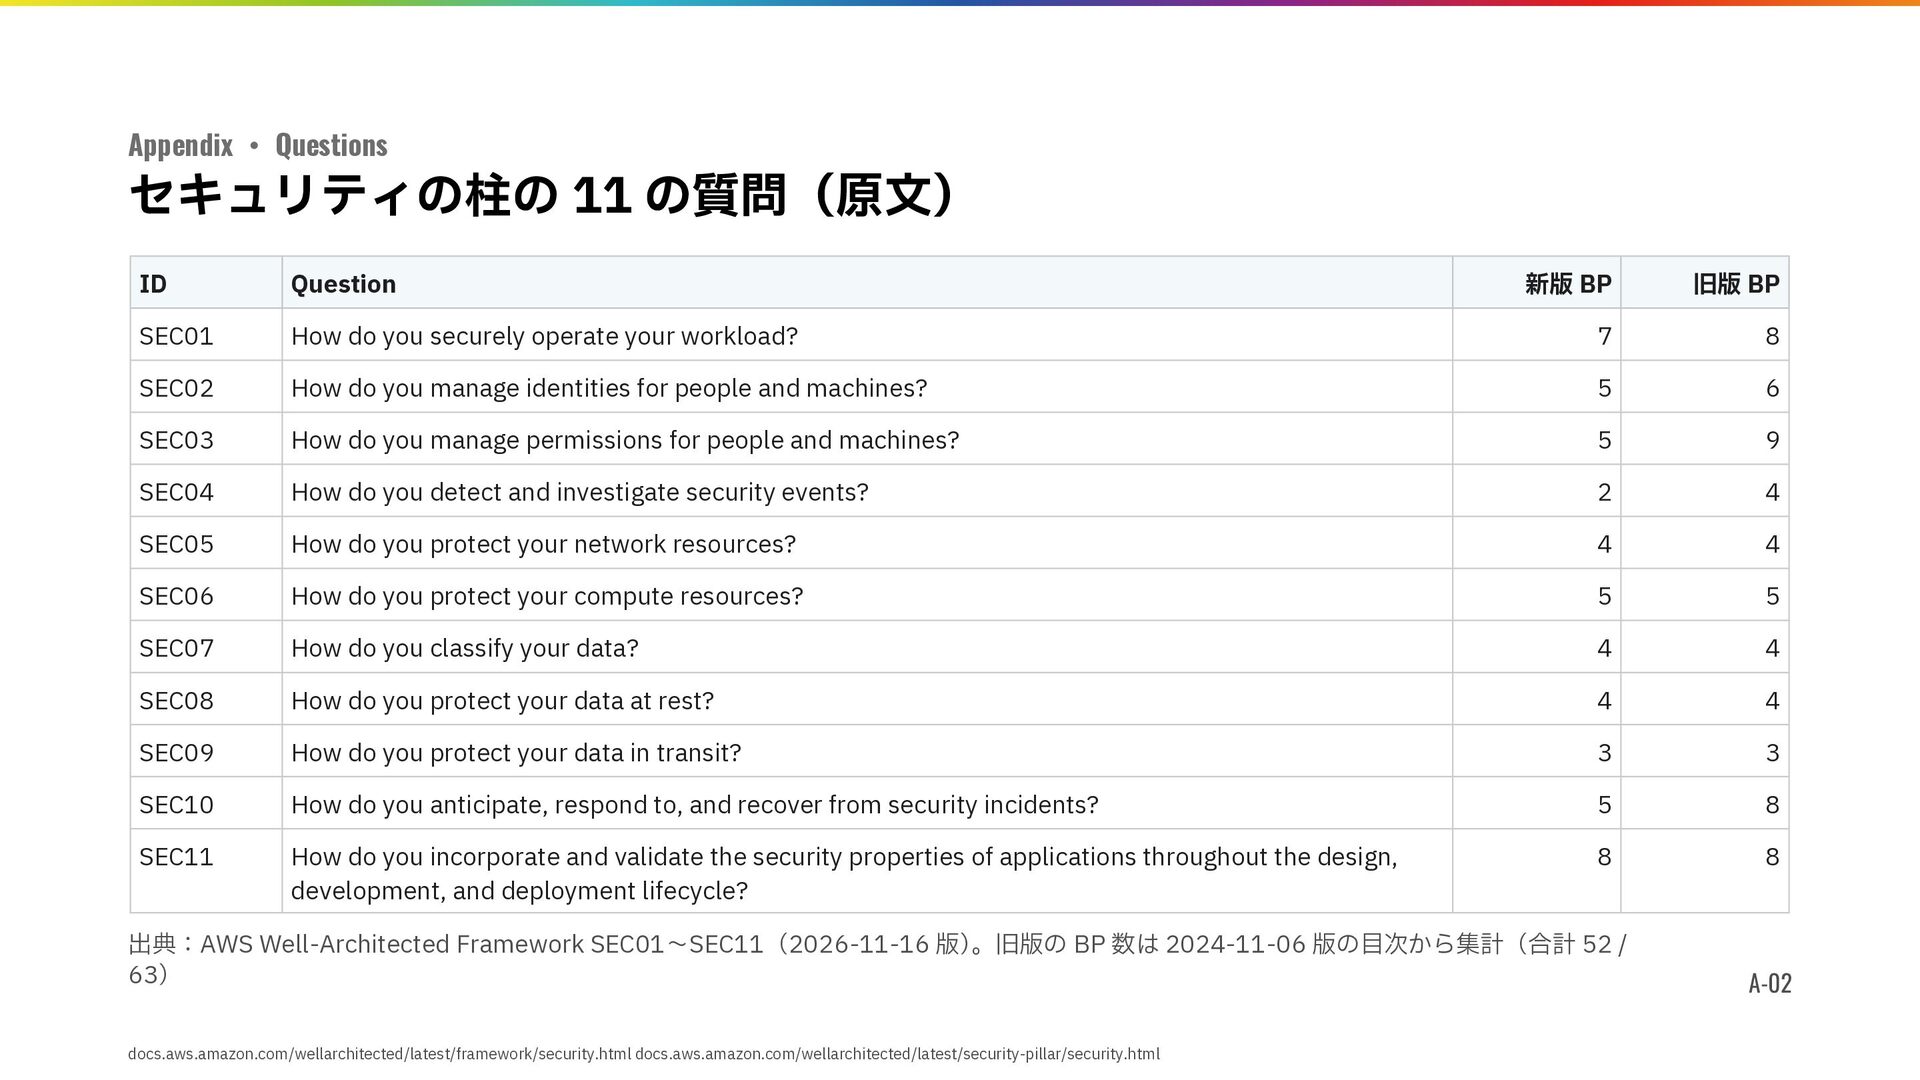
Appendix ・ Questions セキュリティの柱の 11 の質問(原文) ID Question 新版 BP
旧版 BP SEC01 How do you securely operate your workload? 7 8 SEC02 How do you manage identities for people and machines? 5 6 SEC03 How do you manage permissions for people and machines? 5 9 SEC04 How do you detect and investigate security events? 2 4 SEC05 How do you protect your network resources? 4 4 SEC06 How do you protect your compute resources? 5 5 SEC07 How do you classify your data? 4 4 SEC08 How do you protect your data at rest? 4 4 SEC09 How do you protect your data in transit? 3 3 SEC10 How do you anticipate, respond to, and recover from security incidents? 5 8 SEC11 How do you incorporate and validate the security properties of applications throughout the design, development, and deployment lifecycle? 8 8 出典:AWS Well-Architected Framework SEC01〜SEC11(2026-11-16 版) 。旧版の BP 数は 2024-11-06 版の目次から集計(合計 52 / 63) A-02 docs.aws.amazon.com/wellarchitected/latest/framework/security.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/security.html -
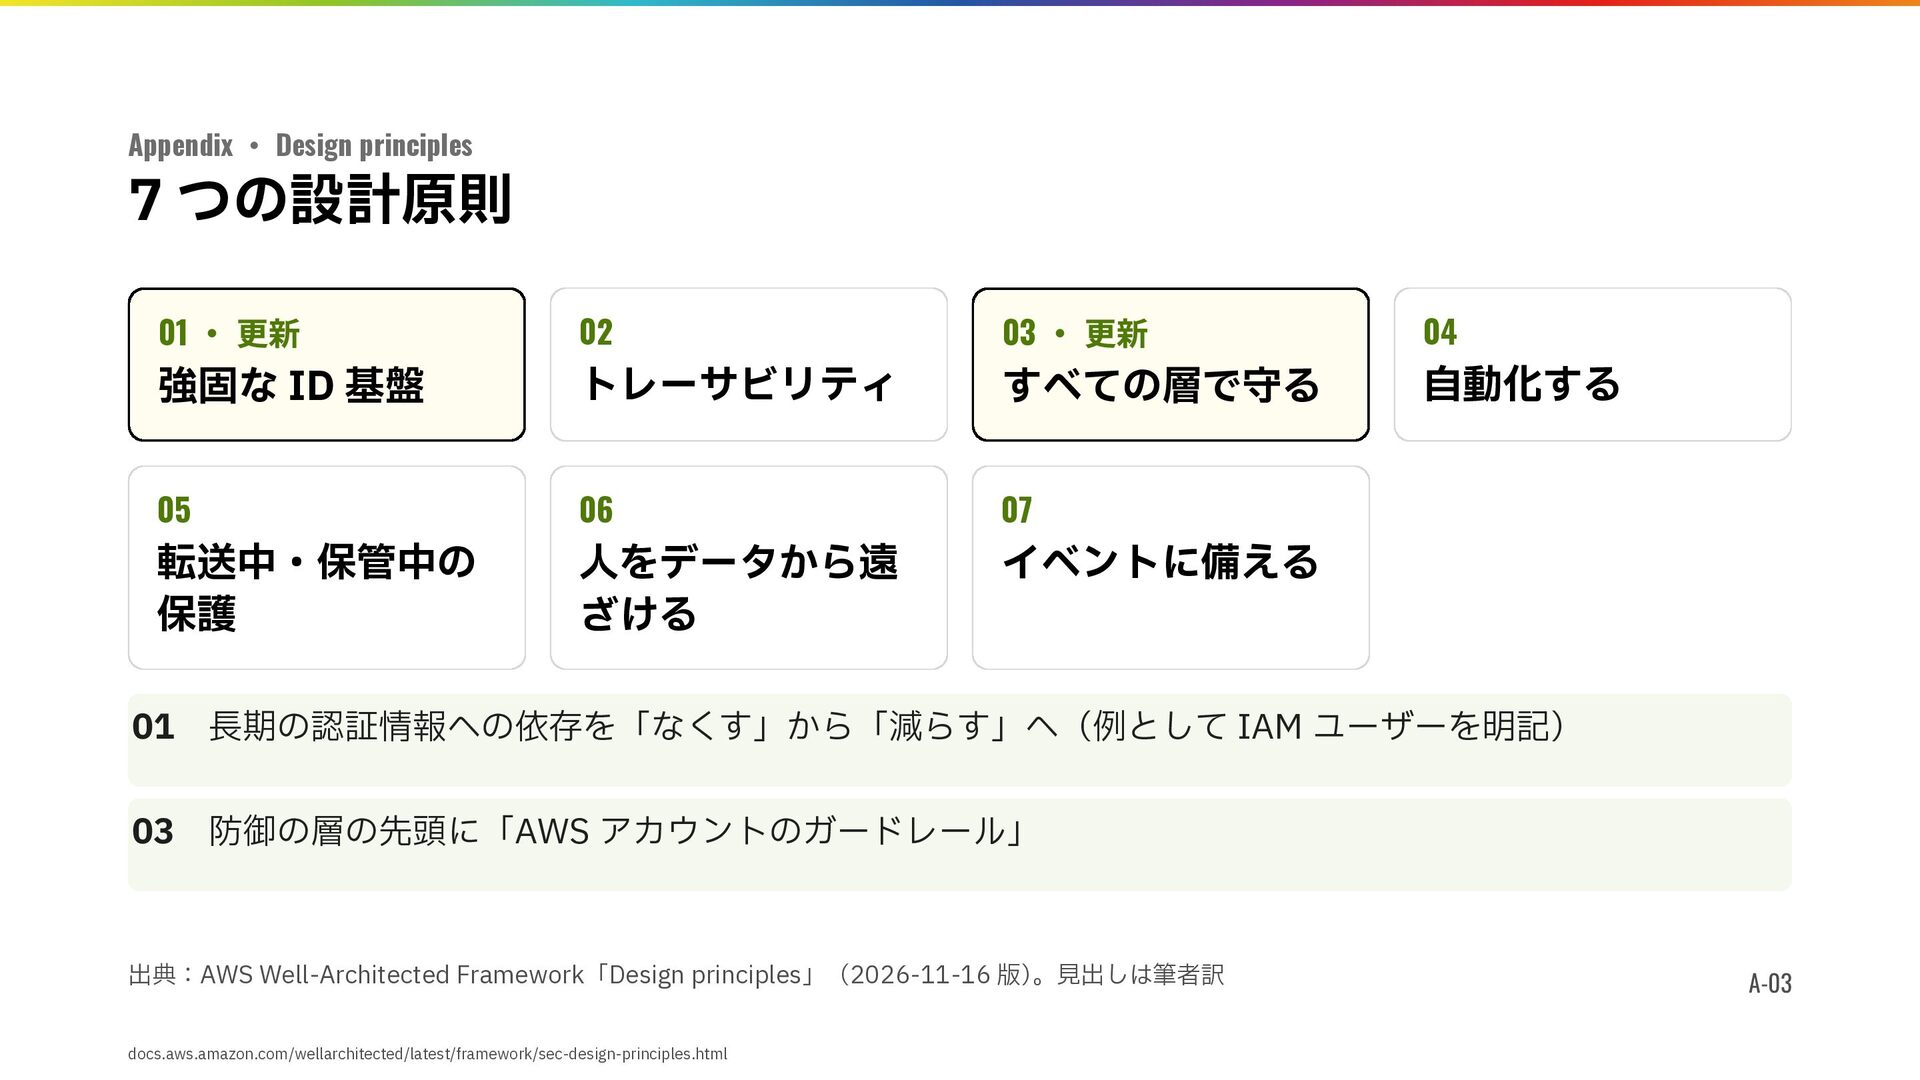
・ Design principles 7 つの設計原則 Appendix ・ 更新 ・ 更新
02 03 強固な ID 基盤 トレーサビリティ すべての層で守る 05 06 07 転送中・保管中の 保護 人をデータから遠 ざける イベントに備える 01 04 自動化する 01 長期の認証情報への依存を「なくす」から「減らす」へ(例として IAM ユーザーを明記) 03 防御の層の先頭に「AWS アカウントのガードレール」 出典:AWS Well-Architected Framework「Design principles」(2026-11-16 版) 。見出しは筆者訳 docs.aws.amazon.com/wellarchitected/latest/framework/sec-design-principles.html A-03 -
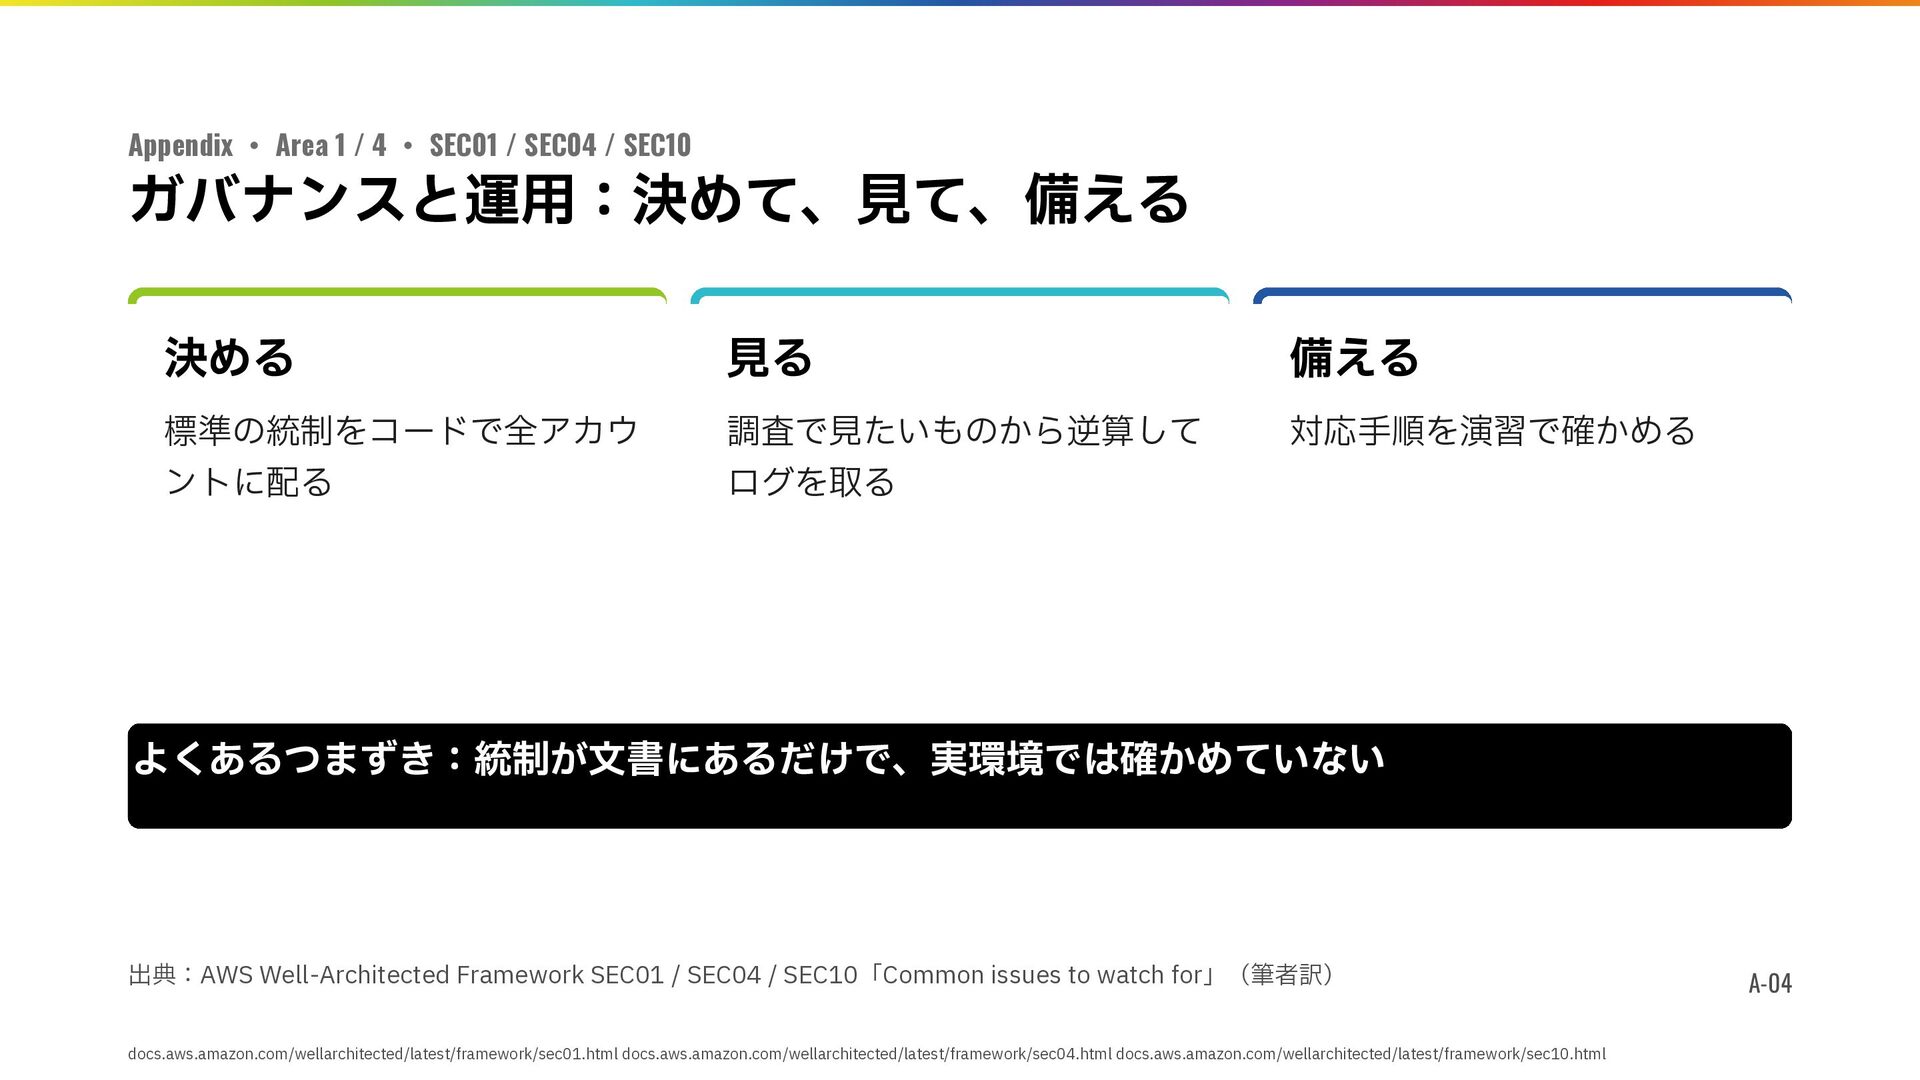
・ Area 1 / 4 ・ SEC01 / SEC04 /
SEC10 ガバナンスと運用:決めて、見て、備える Appendix 決める 見る 備える 標準の統制をコードで全アカウ ントに配る 調査で見たいものから逆算して ログを取る 対応手順を演習で確かめる よくあるつまずき:統制が文書にあるだけで、実環境では確かめていない 出典:AWS Well-Architected Framework SEC01 / SEC04 / SEC10「Common issues to watch for」(筆者訳) docs.aws.amazon.com/wellarchitected/latest/framework/sec01.html docs.aws.amazon.com/wellarchitected/latest/framework/sec04.html docs.aws.amazon.com/wellarchitected/latest/framework/sec10.html A-04 -
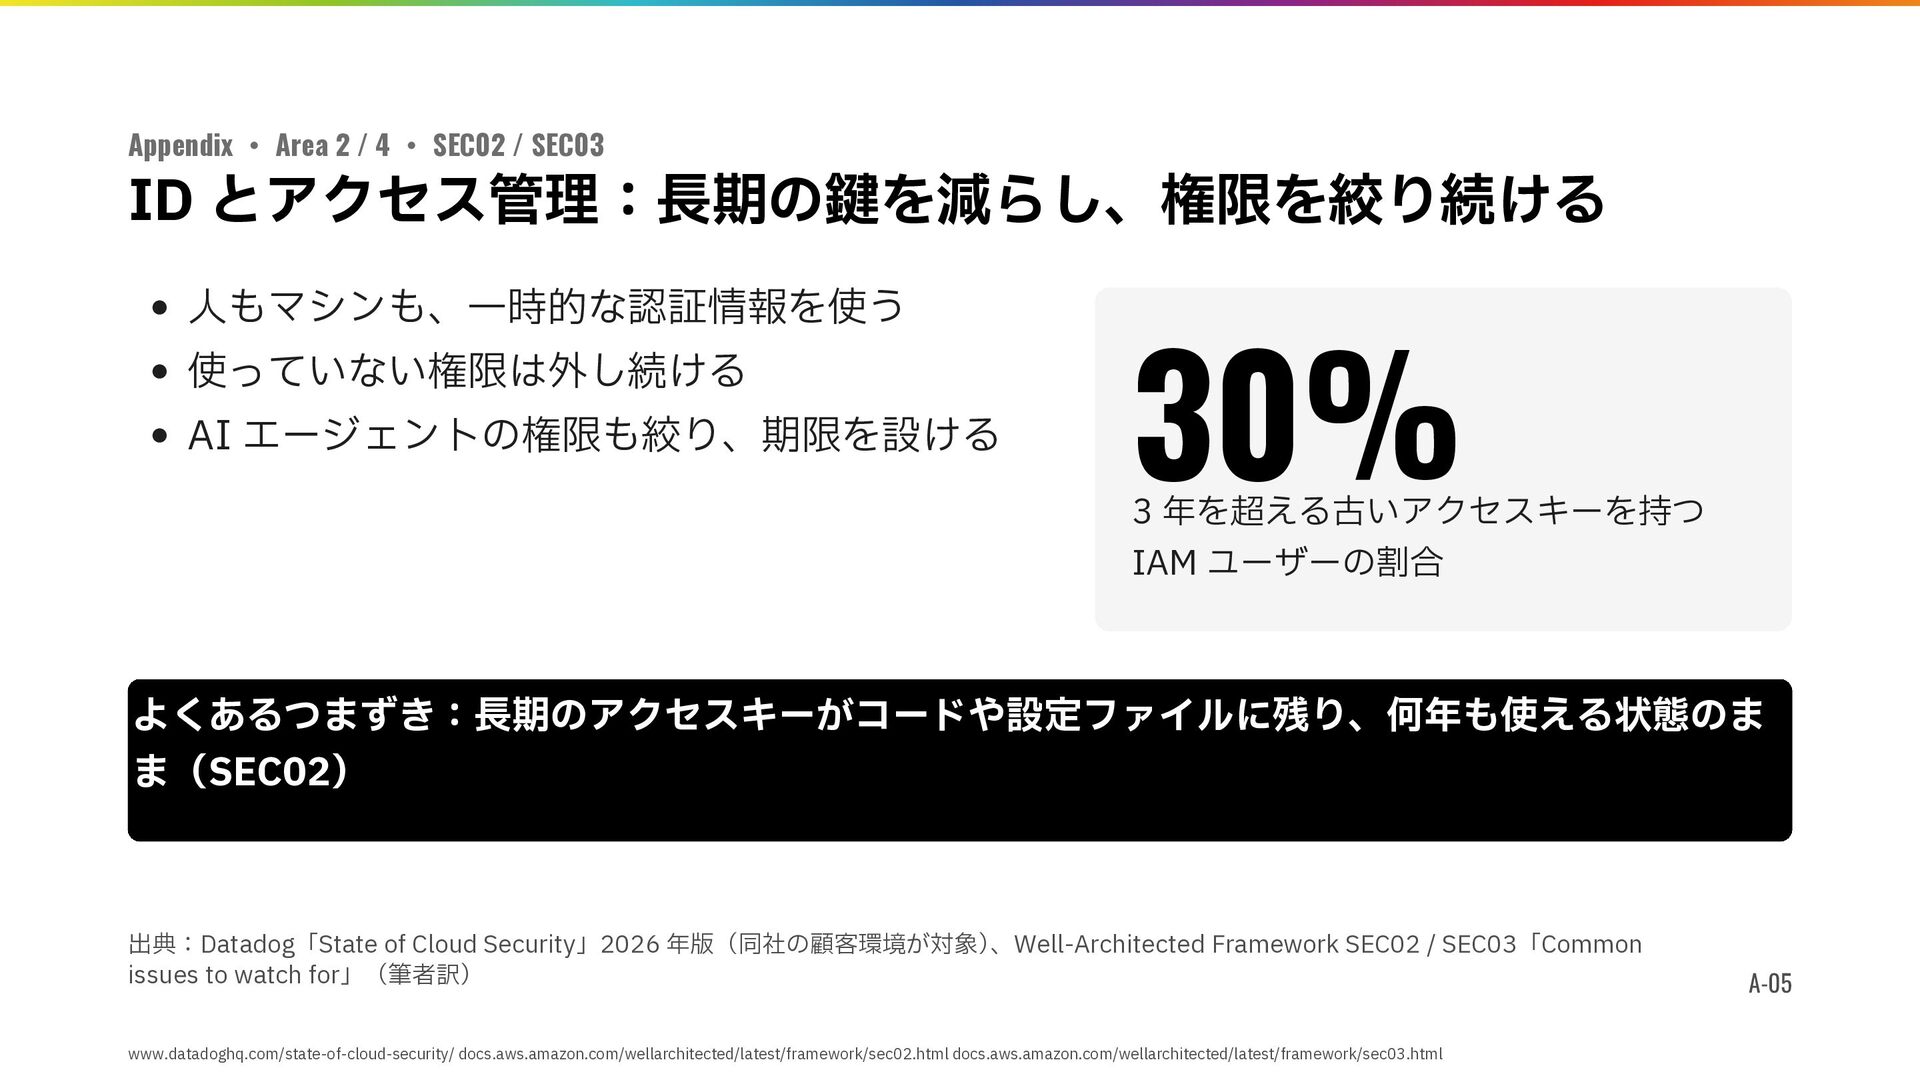
・ Area 2 / 4 ・ SEC02 / SEC03 ID
とアクセス管理:長期の鍵を減らし、権限を絞り続ける Appendix 人もマシンも、一時的な認証情報を使う 使っていない権限は外し続ける AI エージェントの権限も絞り、期限を設ける 30% 3 年を超える古いアクセスキーを持つ IAM ユーザーの割合 よくあるつまずき:長期のアクセスキーがコードや設定ファイルに残り、何年も使える状態のま ま(SEC02) 出典:Datadog「State of Cloud Security」2026 年版(同社の顧客環境が対象) 、Well-Architected Framework SEC02 / SEC03「Common issues to watch for」(筆者訳) www.datadoghq.com/state-of-cloud-security/ docs.aws.amazon.com/wellarchitected/latest/framework/sec02.html docs.aws.amazon.com/wellarchitected/latest/framework/sec03.html A-05 -
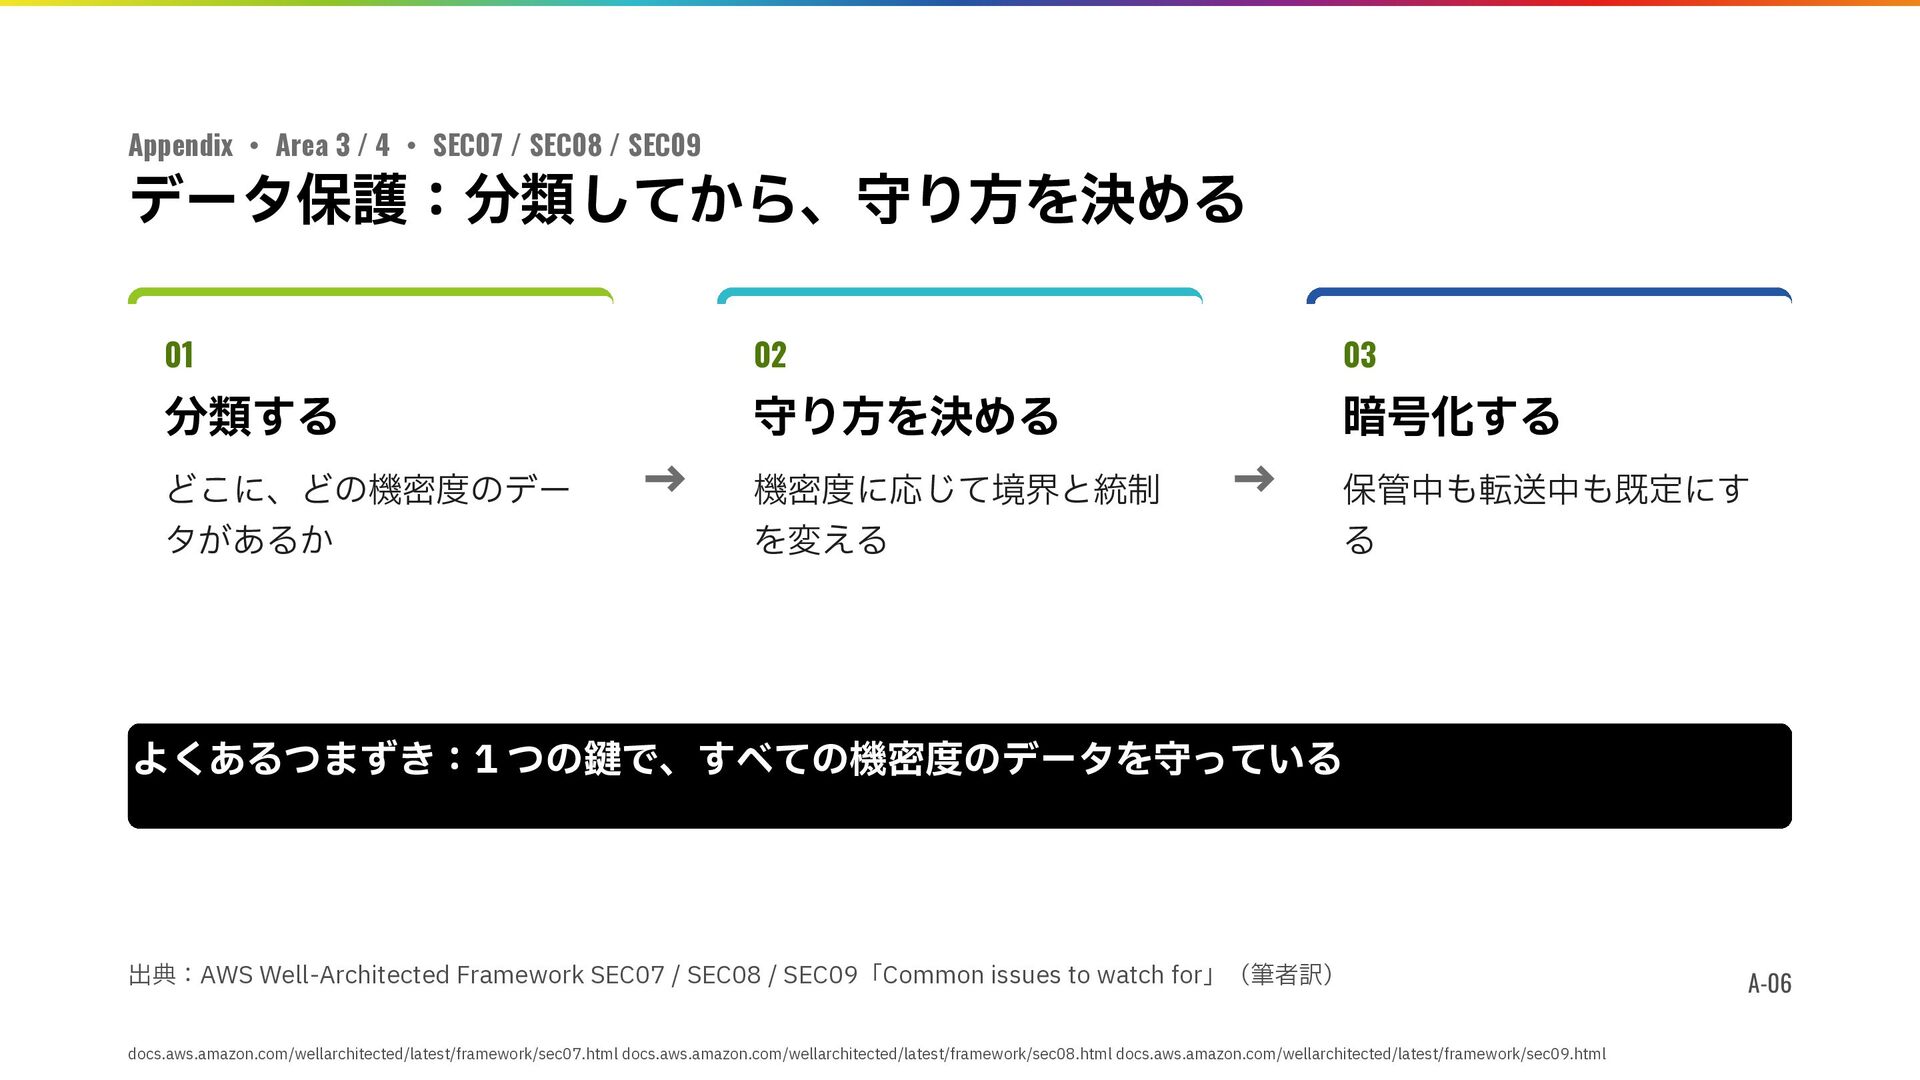
・ Area 3 / 4 ・ SEC07 / SEC08 /
SEC09 データ保護:分類してから、守り方を決める Appendix 01 02 03 分類する 守り方を決める 暗号化する どこに、どの機密度のデー タがあるか → 機密度に応じて境界と統制 を変える → 保管中も転送中も既定にす る よくあるつまずき:1 つの鍵で、すべての機密度のデータを守っている 出典:AWS Well-Architected Framework SEC07 / SEC08 / SEC09「Common issues to watch for」(筆者訳) docs.aws.amazon.com/wellarchitected/latest/framework/sec07.html docs.aws.amazon.com/wellarchitected/latest/framework/sec08.html docs.aws.amazon.com/wellarchitected/latest/framework/sec09.html A-06 -
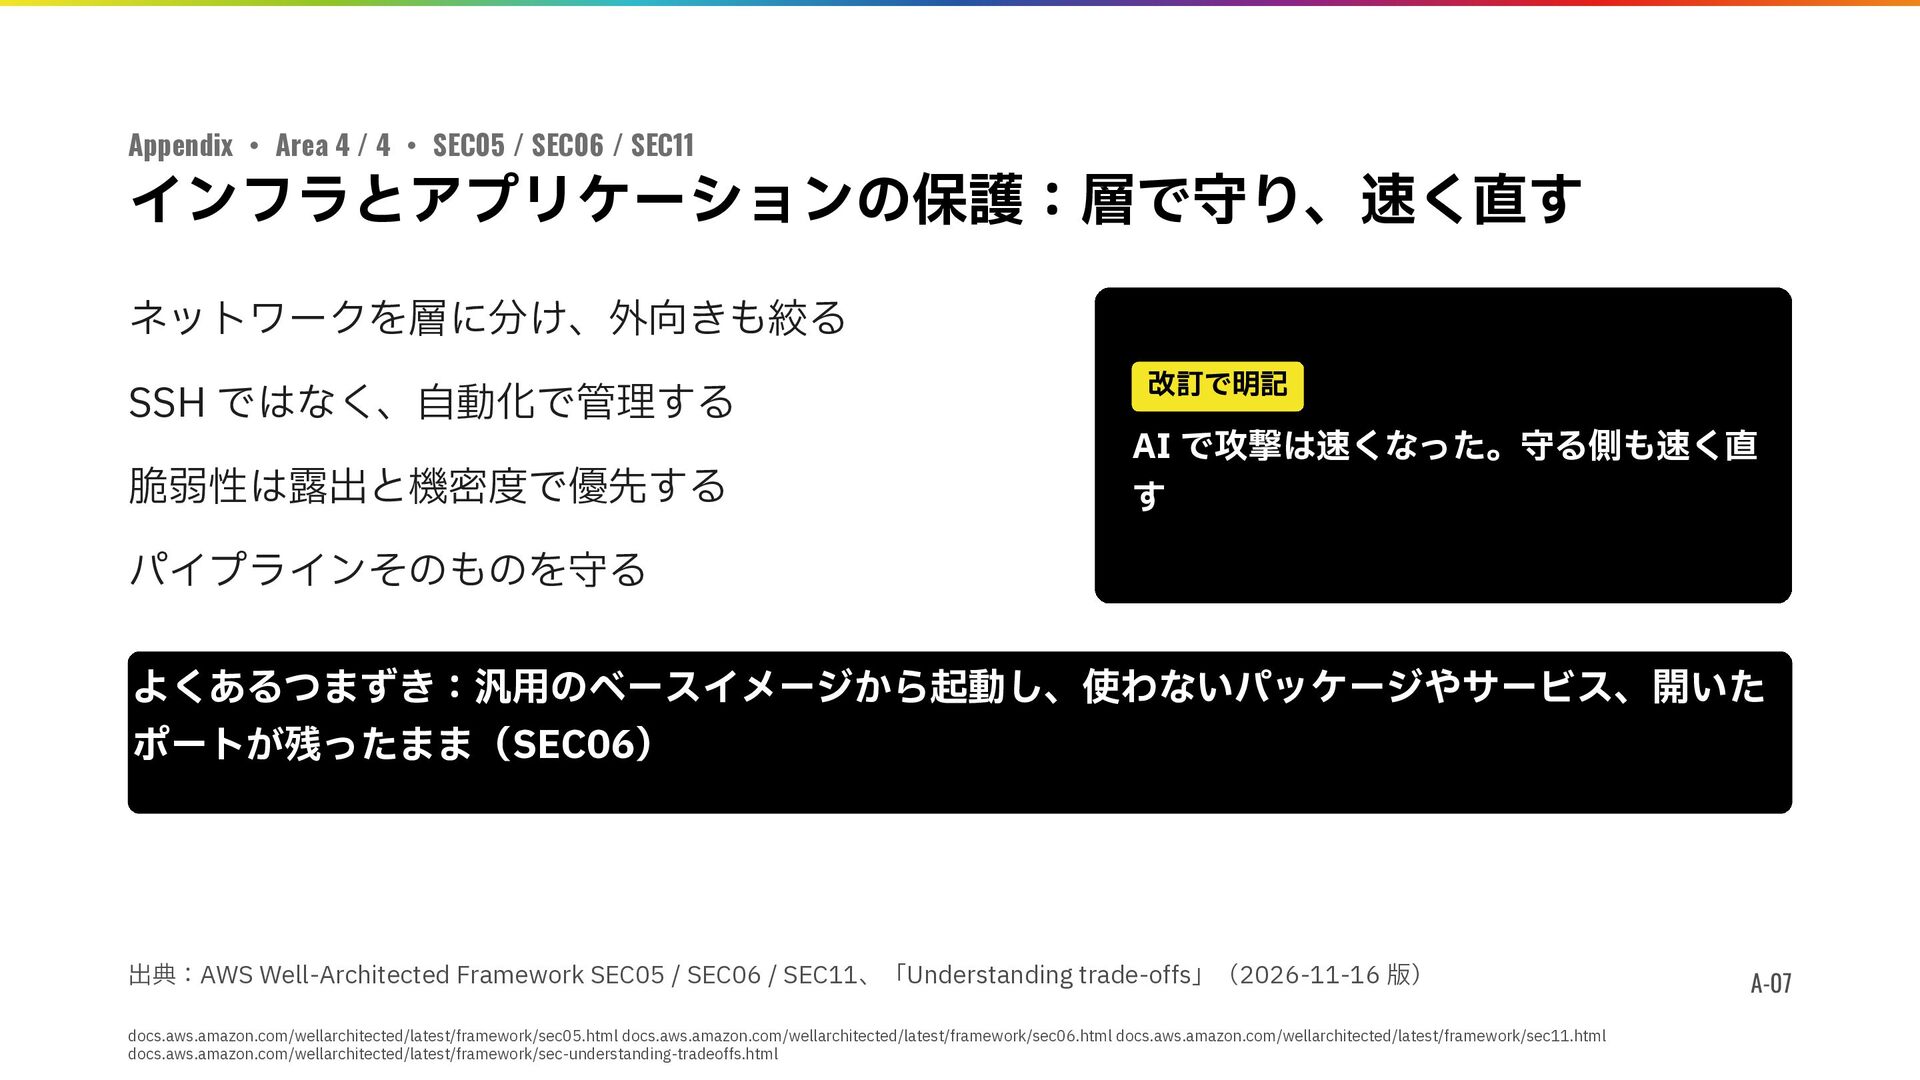
・ Area 4 / 4 ・ SEC05 / SEC06 /
SEC11 インフラとアプリケーションの保護:層で守り、速く直す Appendix ネットワークを層に分け、外向きも絞る SSH ではなく、自動化で管理する 脆弱性は露出と機密度で優先する 改訂で明記 AI で攻撃は速くなった。守る側も速く直 す パイプラインそのものを守る よくあるつまずき:汎用のベースイメージから起動し、使わないパッケージやサービス、開いた ポートが残ったまま(SEC06) 出典:AWS Well-Architected Framework SEC05 / SEC06 / SEC11、「Understanding trade-offs」(2026-11-16 版) docs.aws.amazon.com/wellarchitected/latest/framework/sec05.html docs.aws.amazon.com/wellarchitected/latest/framework/sec06.html docs.aws.amazon.com/wellarchitected/latest/framework/sec11.html docs.aws.amazon.com/wellarchitected/latest/framework/sec-understanding-tradeoffs.html A-07 -
・ Lessons 続けるために、現場で大切にしている 3 つのこと Appendix 01 02 03 「検査していない」を
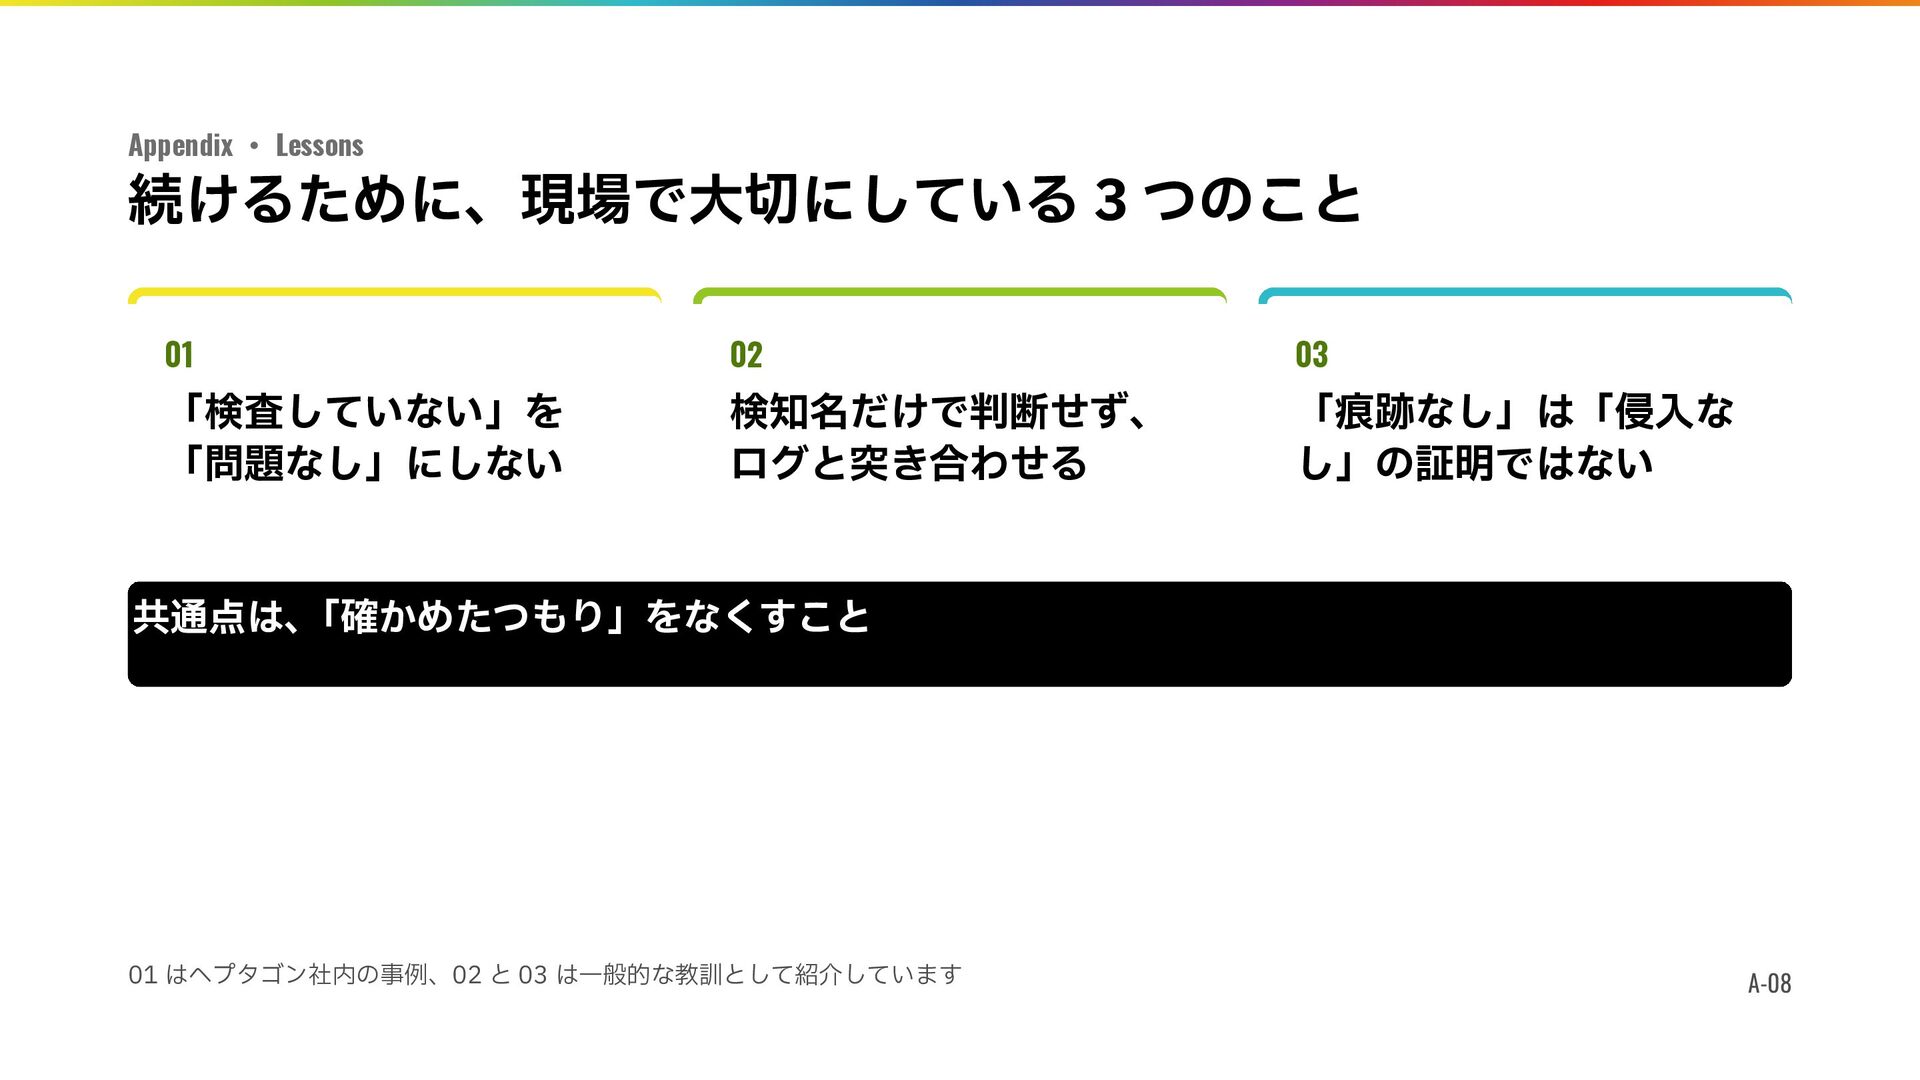
「問題なし」にしない 検知名だけで判断せず、 ログと突き合わせる 「痕跡なし」は「侵入な し」の証明ではない 共通点は、「確かめたつもり」をなくすこと 01 はヘプタゴン社内の事例、02 と 03 は一般的な教訓として紹介しています A-08 -
・ SEC06-BP01 ・ Perform vulnerability management 全部は直せない。だから、深刻度だけで決めない Appendix 原文 優先度を決める
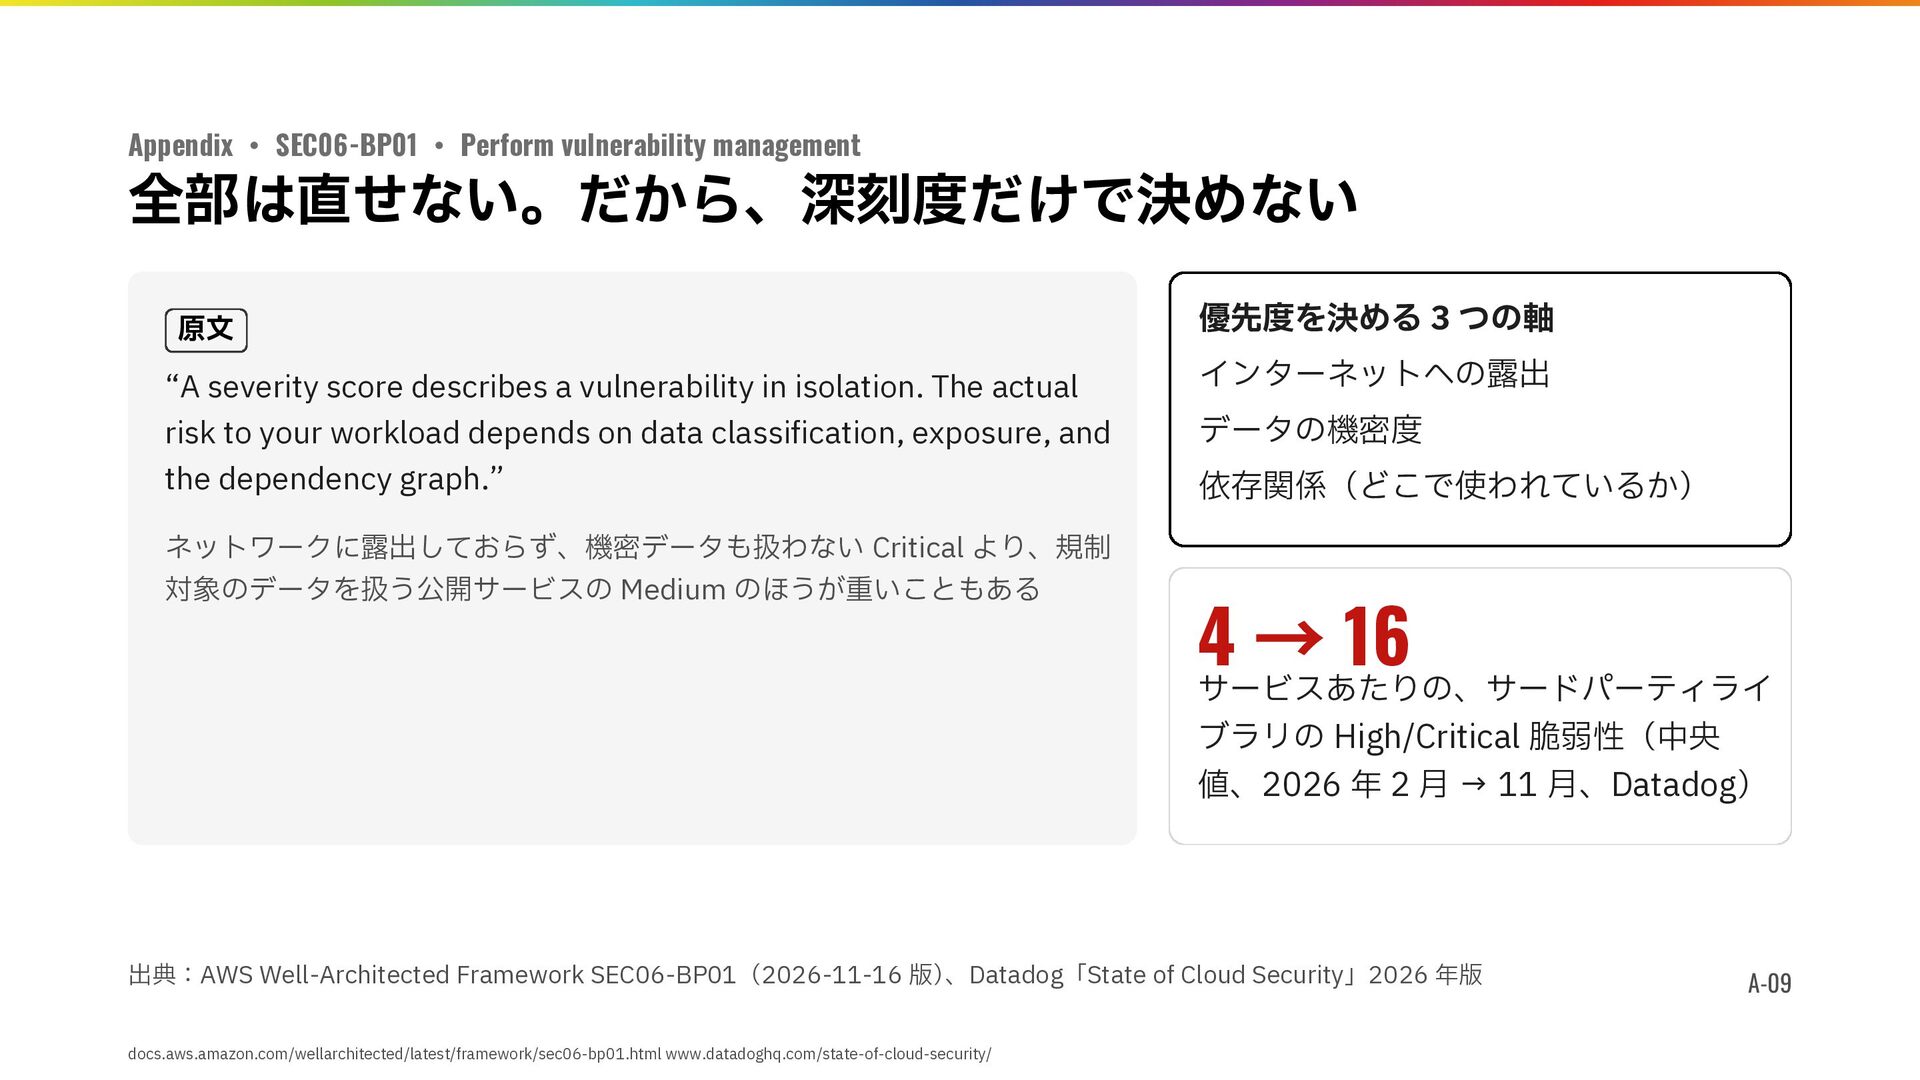
3 つの軸 “A severity score describes a vulnerability in isolation. The actual インターネットへの露出 risk to your workload depends on data classification, exposure, and データの機密度 the dependency graph.” 依存関係(どこで使われているか) ネットワークに露出しておらず、機密データも扱わない Critical より、規制 対象のデータを扱う公開サービスの Medium のほうが重いこともある → 4 16 サービスあたりの、サードパーティライ ブラリの High/Critical 脆弱性(中央 値、2026 年 2 月 → 11 月、Datadog) 出典:AWS Well-Architected Framework SEC06-BP01(2026-11-16 版) 、Datadog「State of Cloud Security」2026 年版 docs.aws.amazon.com/wellarchitected/latest/framework/sec06-bp01.html www.datadoghq.com/state-of-cloud-security/ A-09 -
・ SEC11-BP03 / BP06 ・ SBOM 「それ、どこで使ってる?」に即答できるか Appendix SBOM(ソフトウェア部品表) AWS
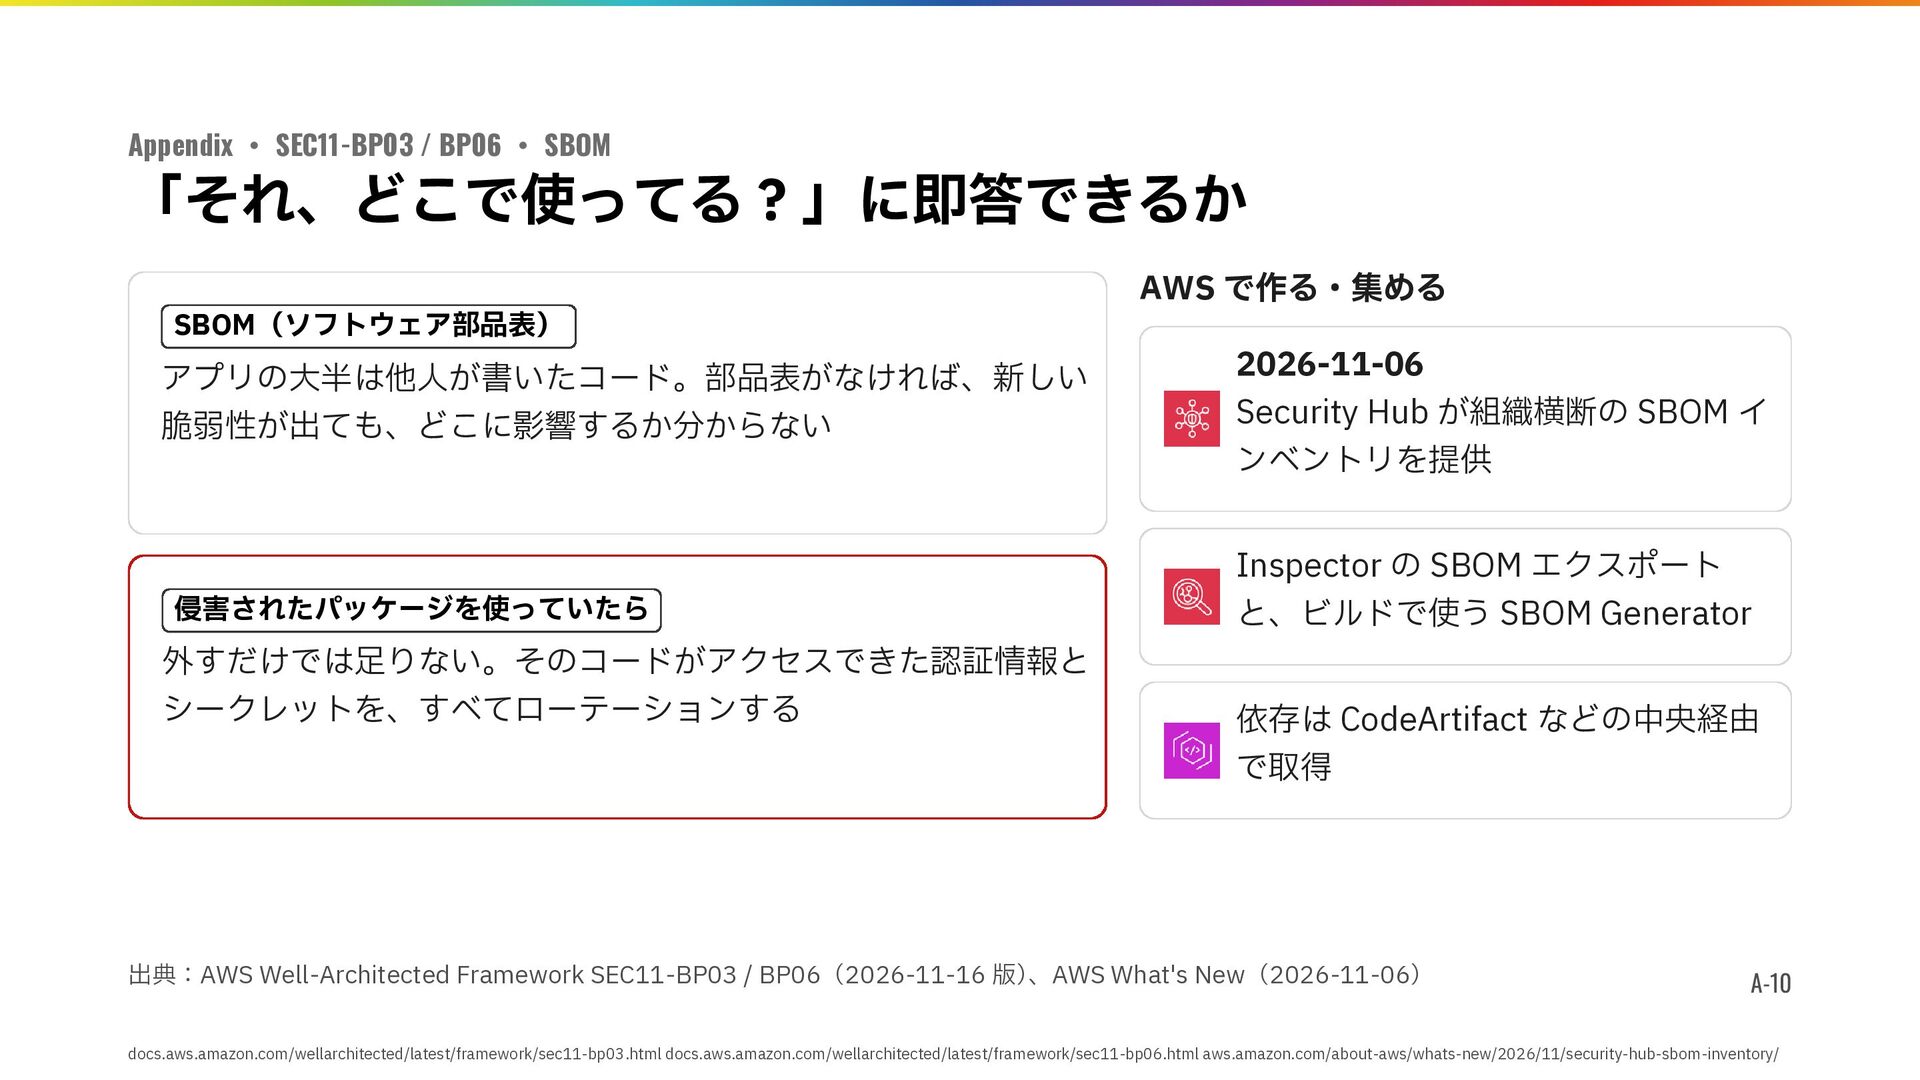
で作る・集める アプリの大半は他人が書いたコード。部品表がなければ、新しい 脆弱性が出ても、どこに影響するか分からない 2026-11-06 Security Hub が組織横断の SBOM イ 侵害されたパッケージを使っていたら Inspector の SBOM エクスポート と、ビルドで使う SBOM Generator 外すだけでは足りない。そのコードがアクセスできた認証情報と シークレットを、すべてローテーションする ンベントリを提供 依存は CodeArtifact などの中央経由 で取得 出典:AWS Well-Architected Framework SEC11-BP03 / BP06(2026-11-16 版) 、AWS What's New(2026-11-06) A-10 docs.aws.amazon.com/wellarchitected/latest/framework/sec11-bp03.html docs.aws.amazon.com/wellarchitected/latest/framework/sec11-bp06.html aws.amazon.com/about-aws/whats-new/2026/11/security-hub-sbom-inventory/ -
Appendix ・ Best practices ・ ガバナンスと運用 SEC01 Securely operate your
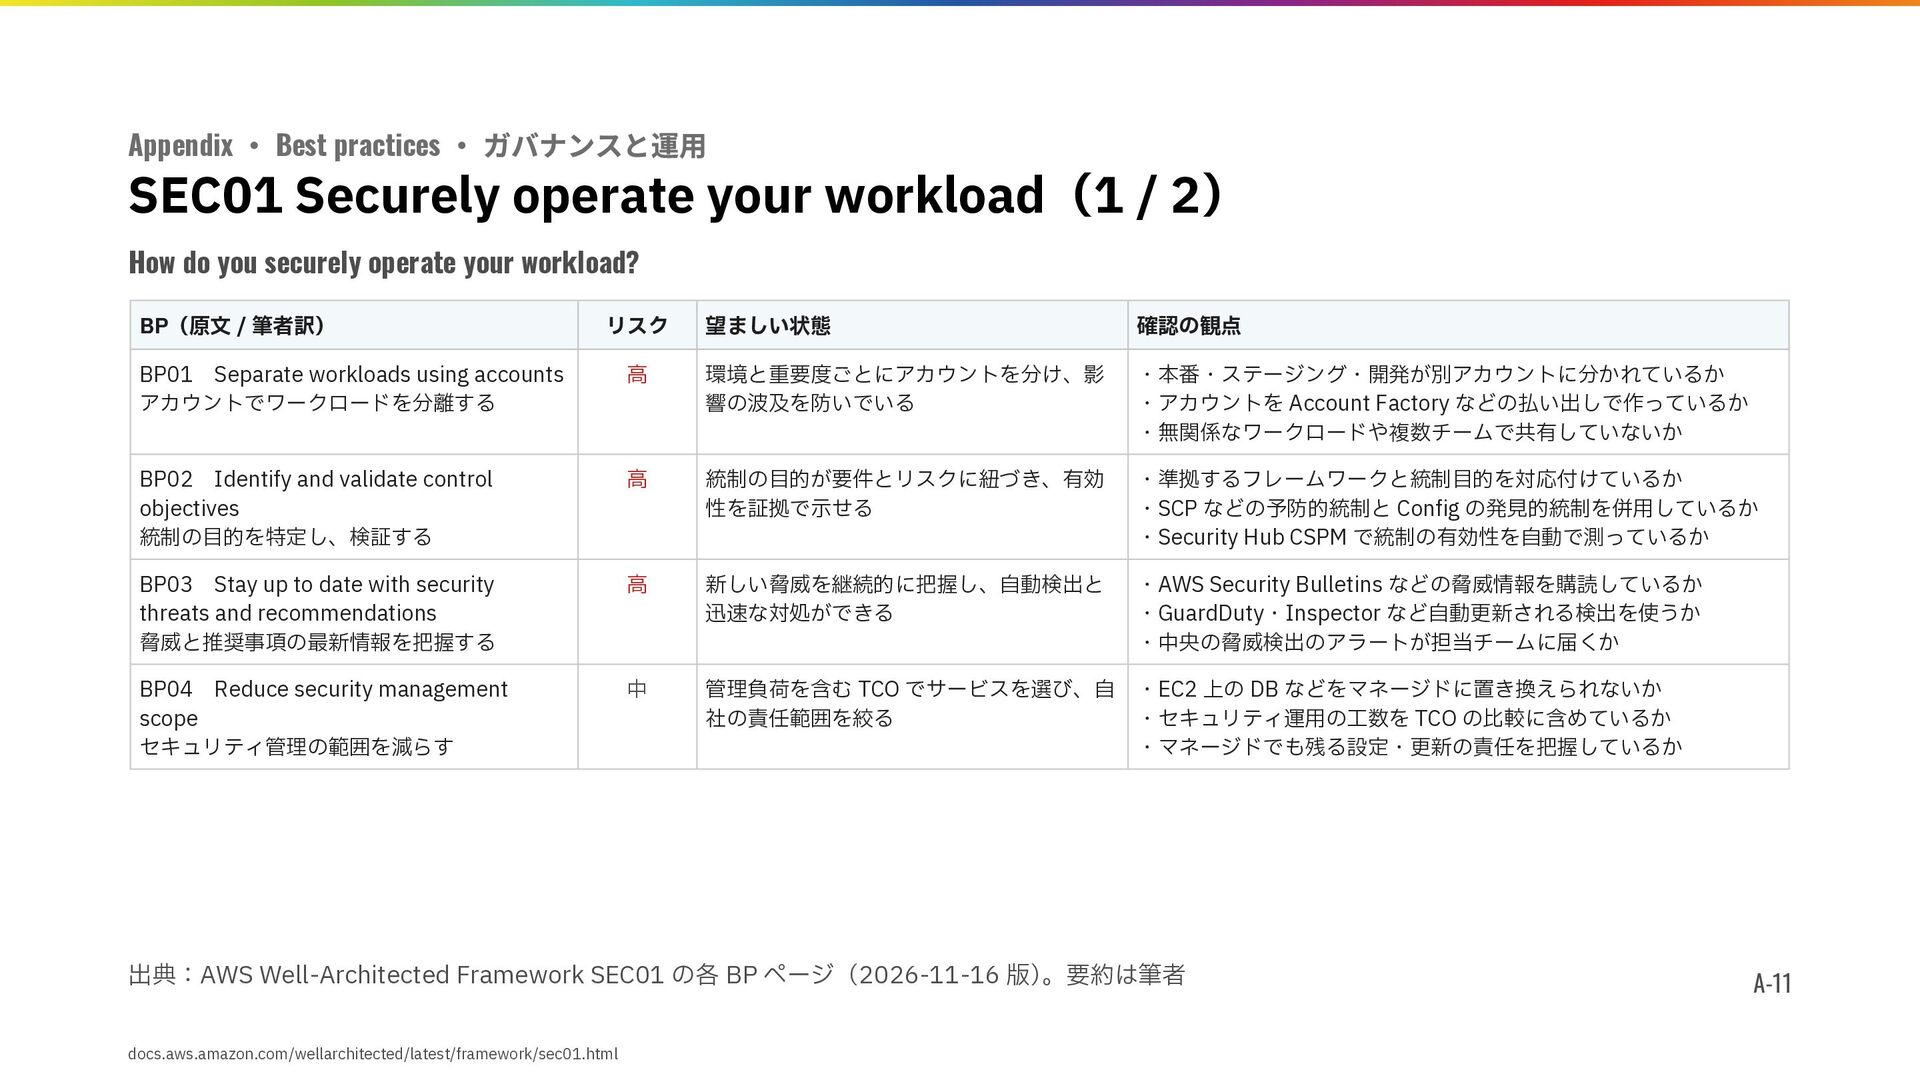
workload(1 / 2) How do you securely operate your workload? BP(原文 / 筆者訳) リスク 望ましい状態 確認の観点 BP01 Separate workloads using accounts アカウントでワークロードを分離する 高 環境と重要度ごとにアカウントを分け、影 響の波及を防いでいる ・本番・ステージング・開発が別アカウントに分かれているか ・アカウントを Account Factory などの払い出しで作っているか ・無関係なワークロードや複数チームで共有していないか BP02 Identify and validate control objectives 統制の目的を特定し、検証する 高 統制の目的が要件とリスクに紐づき、有効 性を証拠で示せる ・準拠するフレームワークと統制目的を対応付けているか ・SCP などの予防的統制と Config の発見的統制を併用しているか ・Security Hub CSPM で統制の有効性を自動で測っているか BP03 Stay up to date with security threats and recommendations 脅威と推奨事項の最新情報を把握する 高 新しい脅威を継続的に把握し、自動検出と 迅速な対処ができる ・AWS Security Bulletins などの脅威情報を購読しているか ・GuardDuty・Inspector など自動更新される検出を使うか ・中央の脅威検出のアラートが担当チームに届くか BP04 Reduce security management scope セキュリティ管理の範囲を減らす 中 管理負荷を含む TCO でサービスを選び、自 社の責任範囲を絞る ・EC2 上の DB などをマネージドに置き換えられないか ・セキュリティ運用の工数を TCO の比較に含めているか ・マネージドでも残る設定・更新の責任を把握しているか 出典:AWS Well-Architected Framework SEC01 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec01.html A-11 -
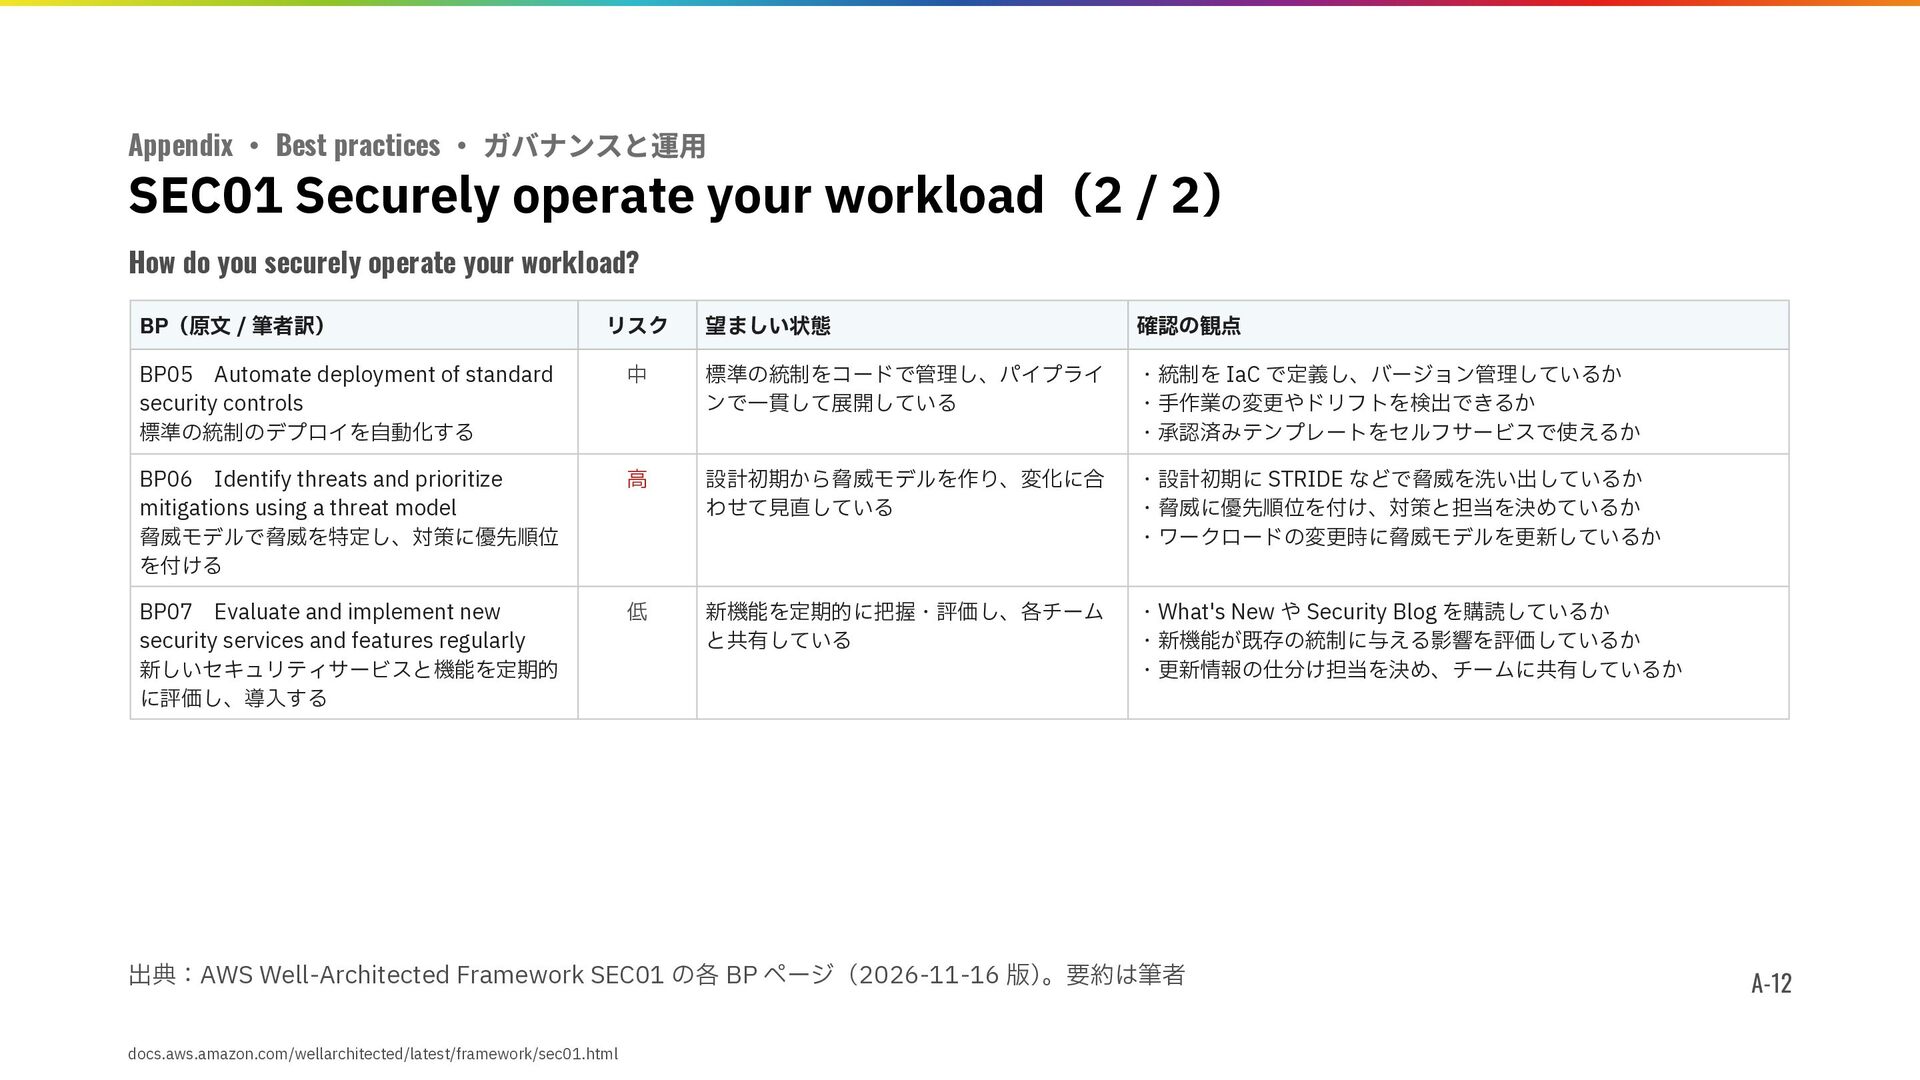
Appendix ・ Best practices ・ ガバナンスと運用 SEC01 Securely operate your
workload(2 / 2) How do you securely operate your workload? BP(原文 / 筆者訳) リスク 望ましい状態 確認の観点 BP05 Automate deployment of standard security controls 標準の統制のデプロイを自動化する 中 標準の統制をコードで管理し、パイプライ ンで一貫して展開している ・統制を IaC で定義し、バージョン管理しているか ・手作業の変更やドリフトを検出できるか ・承認済みテンプレートをセルフサービスで使えるか BP06 Identify threats and prioritize mitigations using a threat model 脅威モデルで脅威を特定し、対策に優先順位 を付ける 高 設計初期から脅威モデルを作り、変化に合 わせて見直している ・設計初期に STRIDE などで脅威を洗い出しているか ・脅威に優先順位を付け、対策と担当を決めているか ・ワークロードの変更時に脅威モデルを更新しているか BP07 Evaluate and implement new security services and features regularly 新しいセキュリティサービスと機能を定期的 に評価し、導入する 低 新機能を定期的に把握・評価し、各チーム と共有している ・What's New や Security Blog を購読しているか ・新機能が既存の統制に与える影響を評価しているか ・更新情報の仕分け担当を決め、チームに共有しているか 出典:AWS Well-Architected Framework SEC01 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec01.html A-12 -
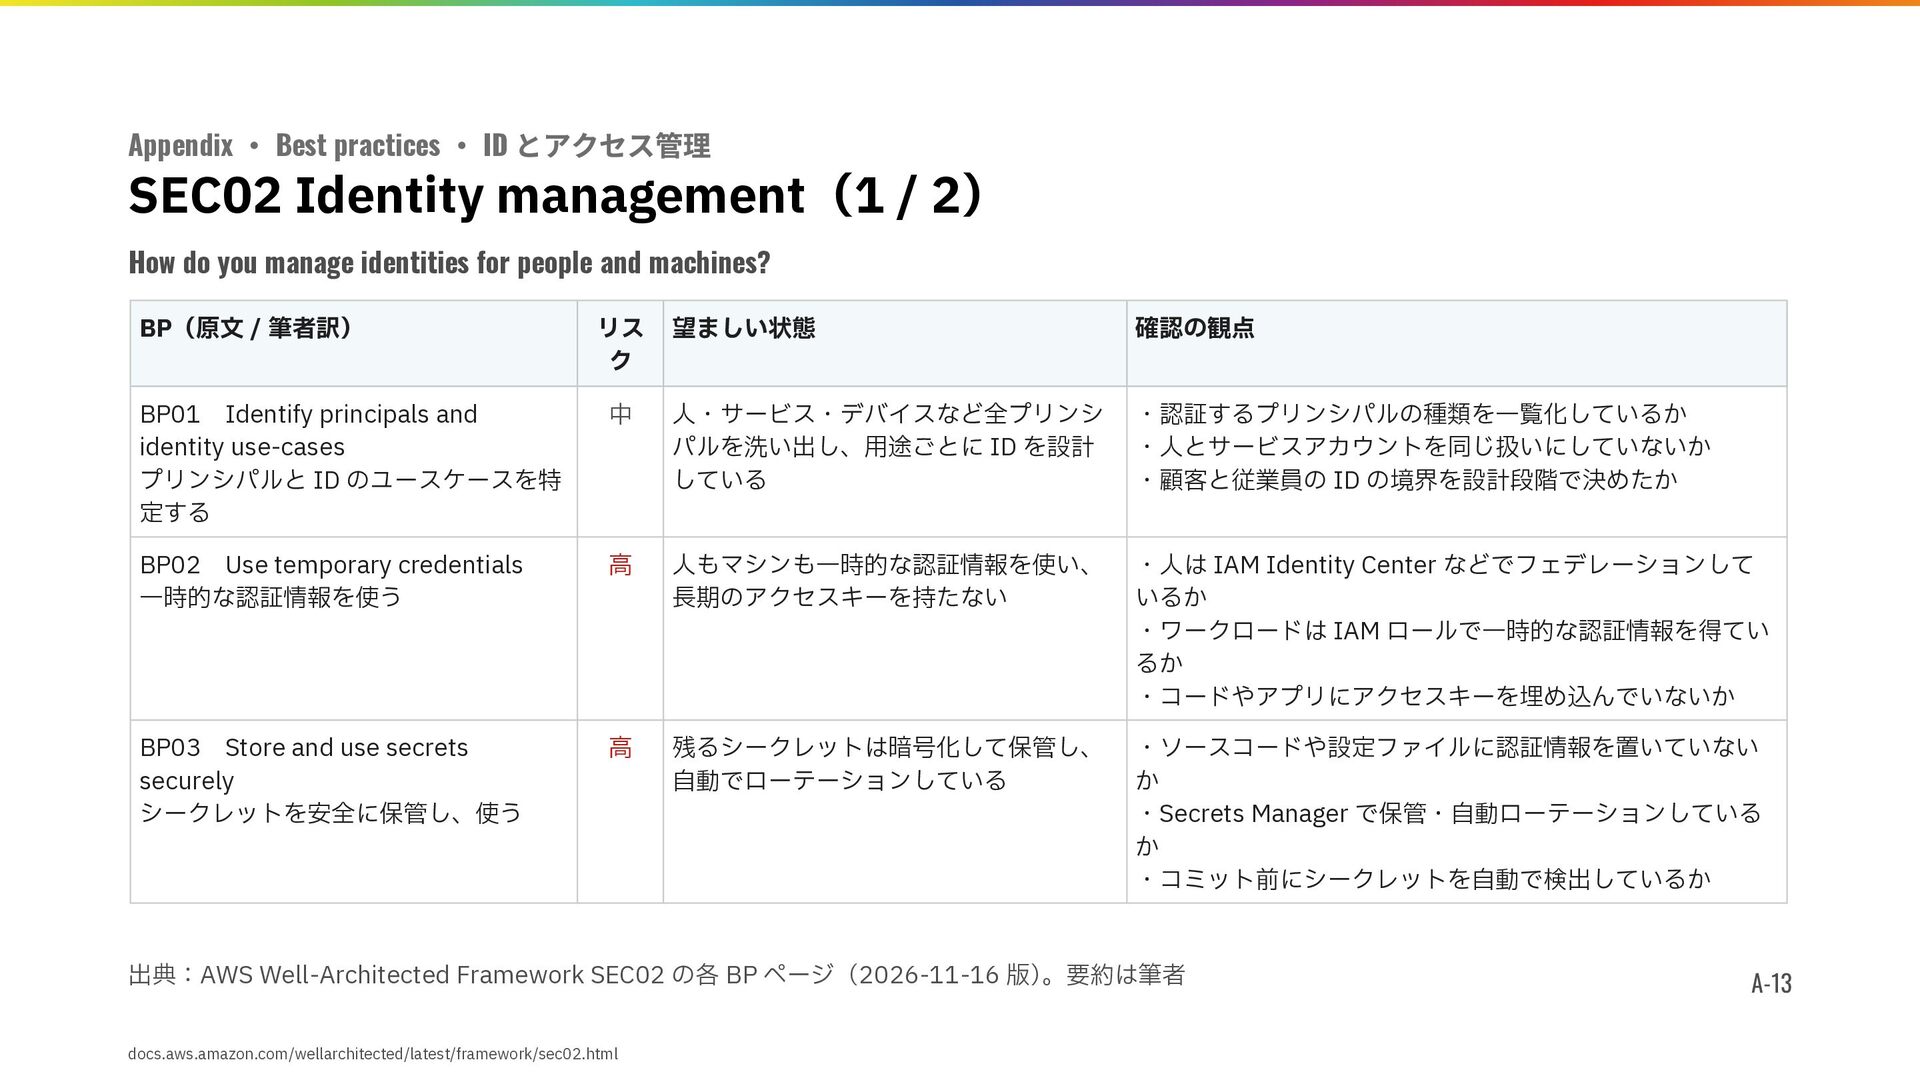
Appendix ・ Best practices ・ ID とアクセス管理 SEC02 Identity management(1
/ 2) How do you manage identities for people and machines? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP01 Identify principals and identity use-cases プリンシパルと ID のユースケースを特 定する 中 人・サービス・デバイスなど全プリンシ パルを洗い出し、用途ごとに ID を設計 している ・認証するプリンシパルの種類を一覧化しているか ・人とサービスアカウントを同じ扱いにしていないか ・顧客と従業員の ID の境界を設計段階で決めたか BP02 Use temporary credentials 一時的な認証情報を使う 高 人もマシンも一時的な認証情報を使い、 長期のアクセスキーを持たない ・人は IAM Identity Center などでフェデレーションして いるか ・ワークロードは IAM ロールで一時的な認証情報を得てい るか ・コードやアプリにアクセスキーを埋め込んでいないか BP03 Store and use secrets securely シークレットを安全に保管し、使う 高 残るシークレットは暗号化して保管し、 自動でローテーションしている ・ソースコードや設定ファイルに認証情報を置いていない か ・Secrets Manager で保管・自動ローテーションしている か ・コミット前にシークレットを自動で検出しているか 出典:AWS Well-Architected Framework SEC02 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec02.html A-13 -
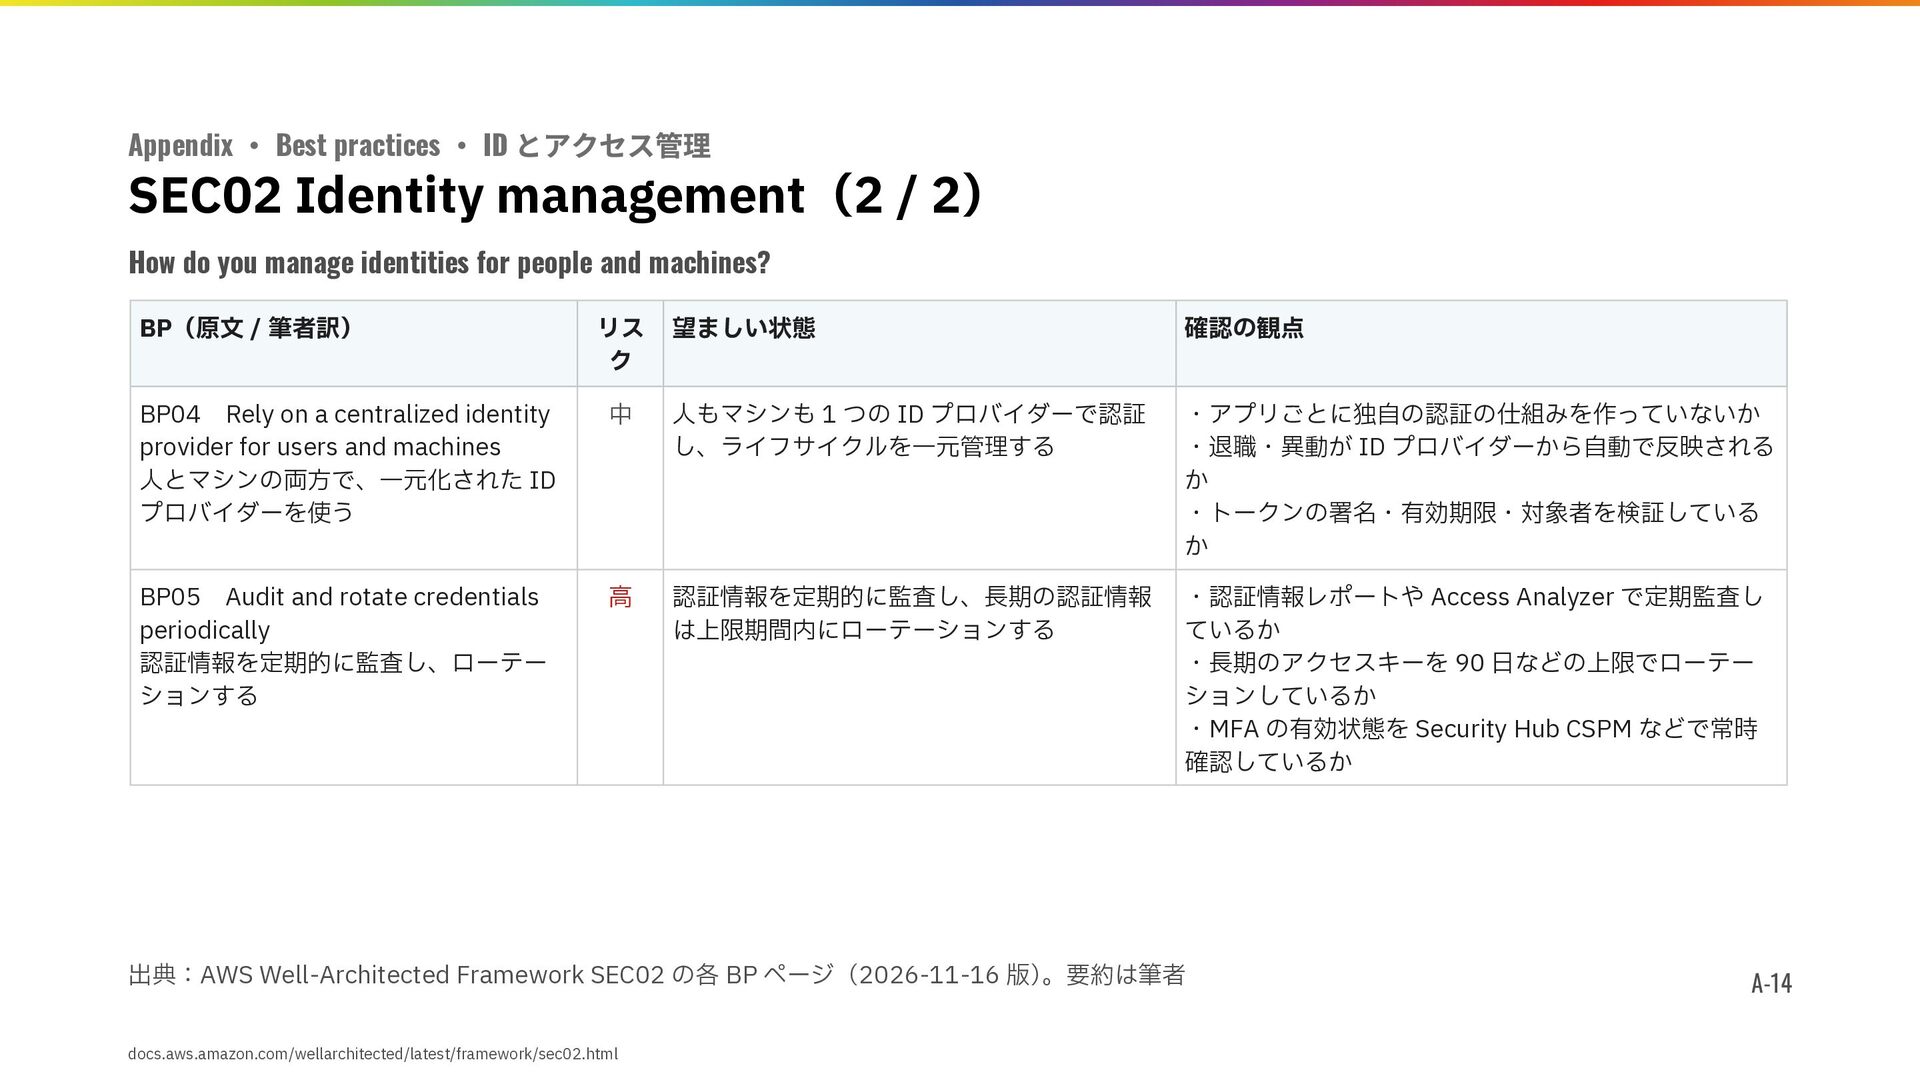
Appendix ・ Best practices ・ ID とアクセス管理 SEC02 Identity management(2
/ 2) How do you manage identities for people and machines? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP04 Rely on a centralized identity provider for users and machines 人とマシンの両方で、一元化された ID プロバイダーを使う 中 人もマシンも 1 つの ID プロバイダーで認証 し、ライフサイクルを一元管理する ・アプリごとに独自の認証の仕組みを作っていないか ・退職・異動が ID プロバイダーから自動で反映される か ・トークンの署名・有効期限・対象者を検証している か BP05 Audit and rotate credentials periodically 認証情報を定期的に監査し、ローテー ションする 高 認証情報を定期的に監査し、長期の認証情報 は上限期間内にローテーションする ・認証情報レポートや Access Analyzer で定期監査し ているか ・長期のアクセスキーを 90 日などの上限でローテー ションしているか ・MFA の有効状態を Security Hub CSPM などで常時 確認しているか 出典:AWS Well-Architected Framework SEC02 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec02.html A-14 -
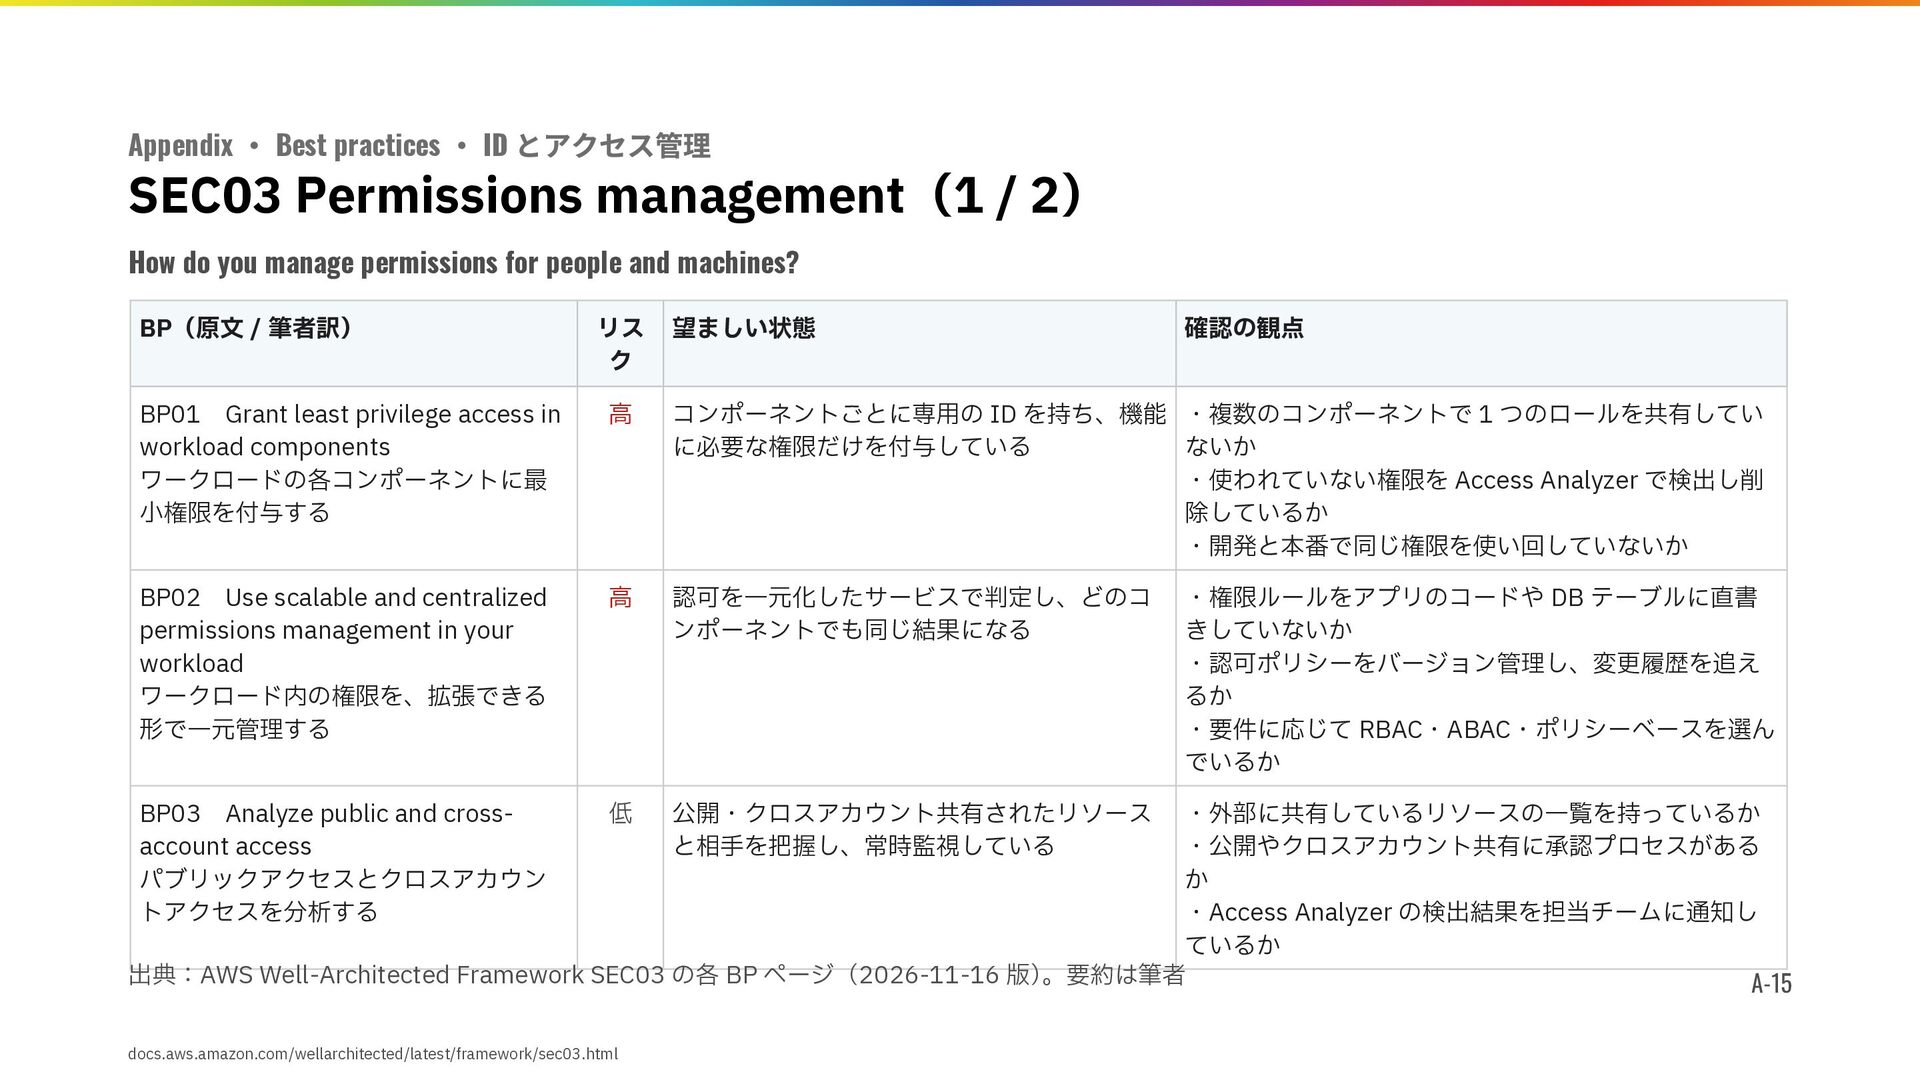
Appendix ・ Best practices ・ ID とアクセス管理 SEC03 Permissions management(1
/ 2) How do you manage permissions for people and machines? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP01 Grant least privilege access in workload components ワークロードの各コンポーネントに最 小権限を付与する 高 コンポーネントごとに専用の ID を持ち、機能 ・複数のコンポーネントで 1 つのロールを共有してい に必要な権限だけを付与している ないか ・使われていない権限を Access Analyzer で検出し削 除しているか ・開発と本番で同じ権限を使い回していないか BP02 Use scalable and centralized permissions management in your workload ワークロード内の権限を、拡張できる 形で一元管理する 高 認可を一元化したサービスで判定し、どのコ ンポーネントでも同じ結果になる BP03 Analyze public and crossaccount access パブリックアクセスとクロスアカウン トアクセスを分析する 低 公開・クロスアカウント共有されたリソース と相手を把握し、常時監視している ・権限ルールをアプリのコードや DB テーブルに直書 きしていないか ・認可ポリシーをバージョン管理し、変更履歴を追え るか ・要件に応じて RBAC・ABAC・ポリシーベースを選ん でいるか ・外部に共有しているリソースの一覧を持っているか ・公開やクロスアカウント共有に承認プロセスがある か ・Access Analyzer の検出結果を担当チームに通知し ているか 出典:AWS Well-Architected Framework SEC03 の各 BP ページ(2026-11-16 版) 。要約は筆者 A-15 docs.aws.amazon.com/wellarchitected/latest/framework/sec03.html -
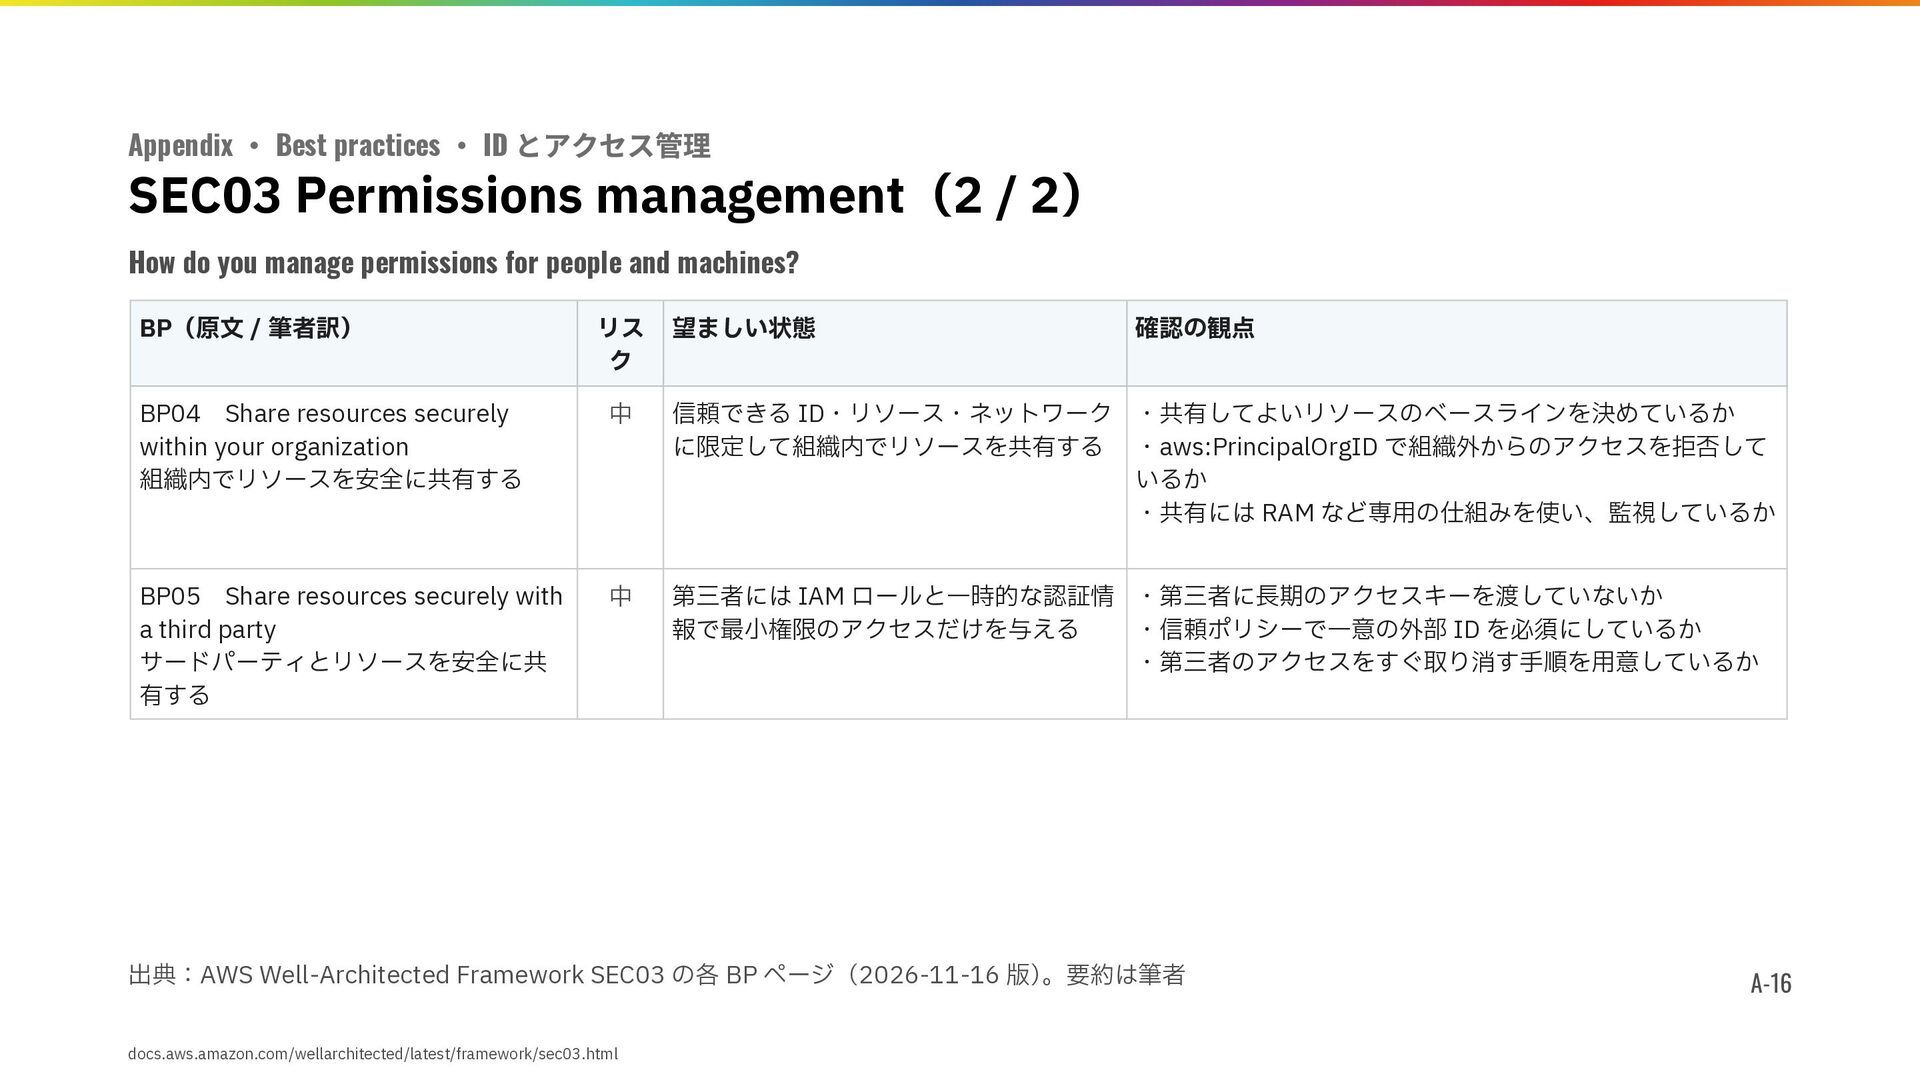
Appendix ・ Best practices ・ ID とアクセス管理 SEC03 Permissions management(2
/ 2) How do you manage permissions for people and machines? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP04 Share resources securely within your organization 組織内でリソースを安全に共有する 中 信頼できる ID・リソース・ネットワーク ・共有してよいリソースのベースラインを決めているか に限定して組織内でリソースを共有する ・aws:PrincipalOrgID で組織外からのアクセスを拒否して いるか ・共有には RAM など専用の仕組みを使い、監視しているか BP05 Share resources securely with a third party サードパーティとリソースを安全に共 有する 中 第三者には IAM ロールと一時的な認証情 ・第三者に長期のアクセスキーを渡していないか 報で最小権限のアクセスだけを与える ・信頼ポリシーで一意の外部 ID を必須にしているか ・第三者のアクセスをすぐ取り消す手順を用意しているか 出典:AWS Well-Architected Framework SEC03 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec03.html A-16 -
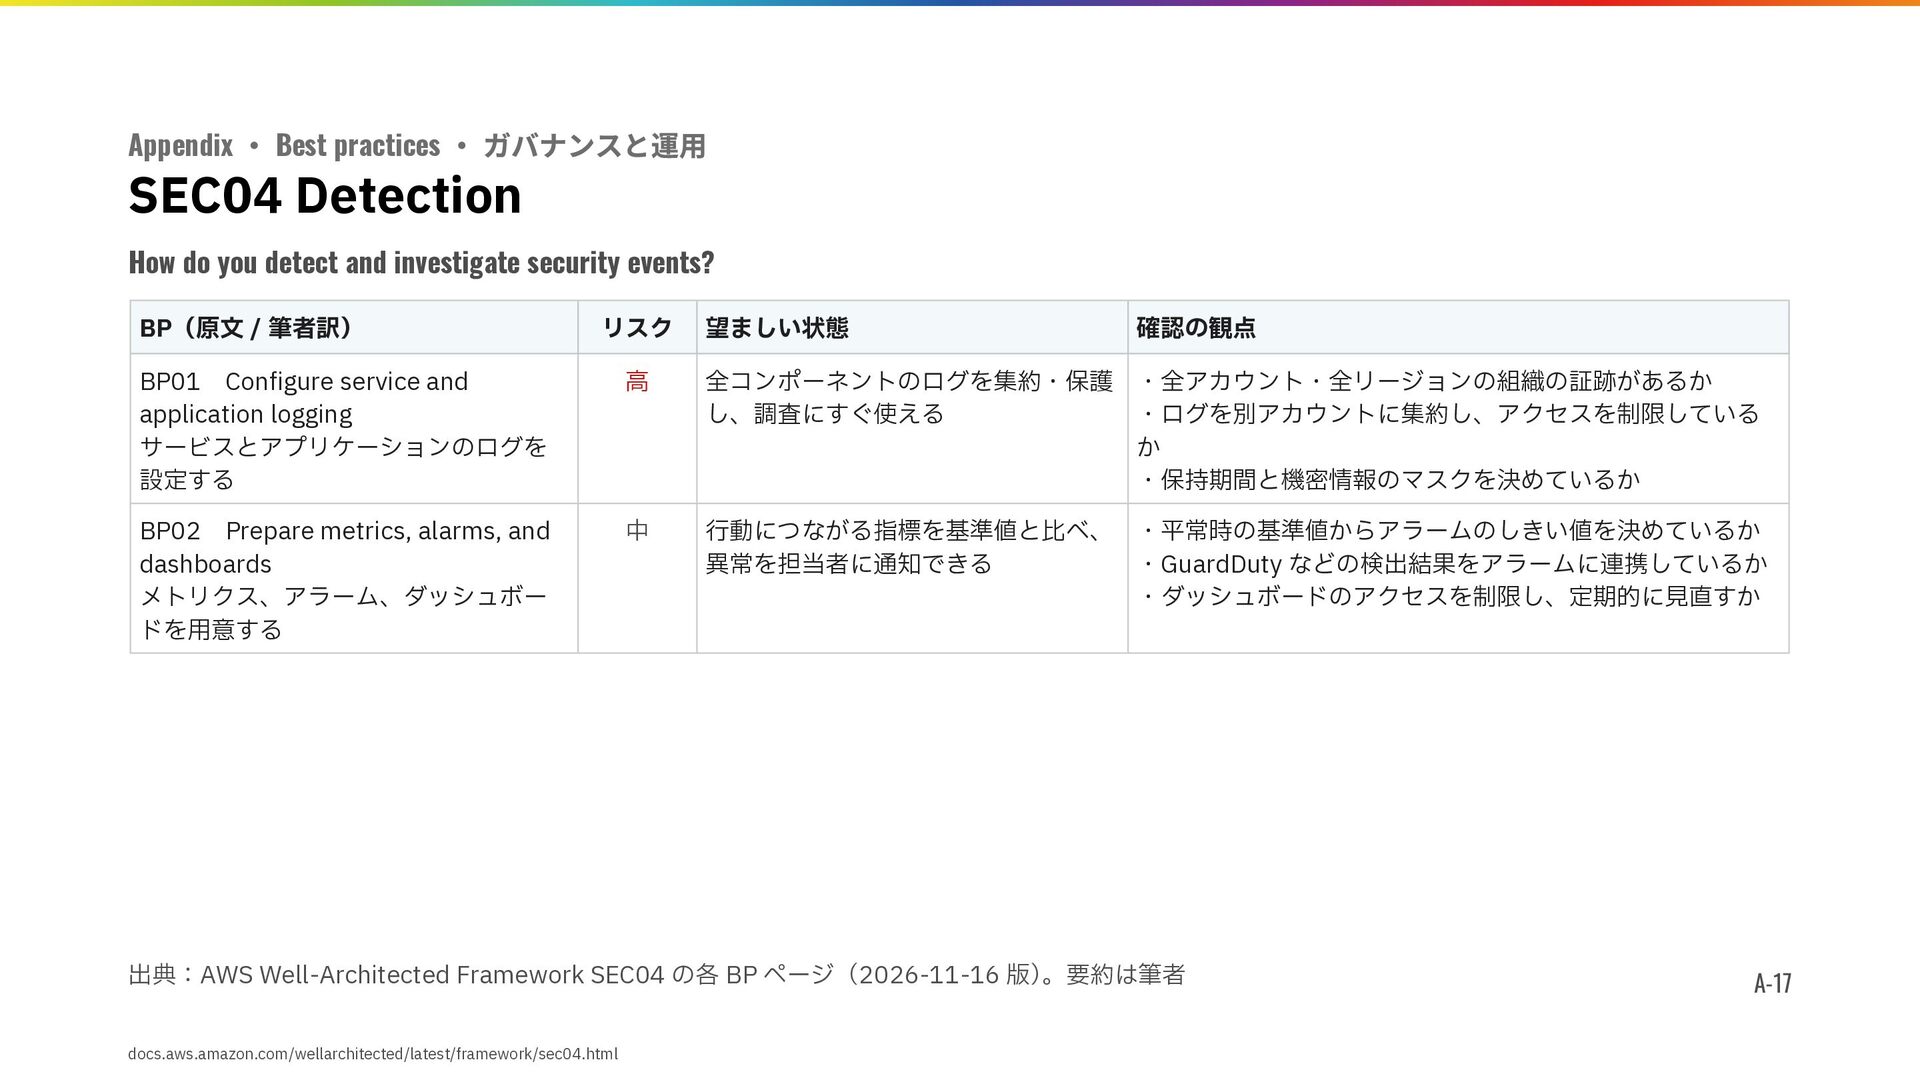
Appendix ・ Best practices ・ ガバナンスと運用 SEC04 Detection How do
you detect and investigate security events? BP(原文 / 筆者訳) リスク 望ましい状態 確認の観点 BP01 Configure service and application logging サービスとアプリケーションのログを 設定する 高 全コンポーネントのログを集約・保護 ・全アカウント・全リージョンの組織の証跡があるか し、調査にすぐ使える ・ログを別アカウントに集約し、アクセスを制限している か ・保持期間と機密情報のマスクを決めているか BP02 Prepare metrics, alarms, and dashboards メトリクス、アラーム、ダッシュボー ドを用意する 中 行動につながる指標を基準値と比べ、 ・平常時の基準値からアラームのしきい値を決めているか 異常を担当者に通知できる ・GuardDuty などの検出結果をアラームに連携しているか ・ダッシュボードのアクセスを制限し、定期的に見直すか 出典:AWS Well-Architected Framework SEC04 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec04.html A-17 -
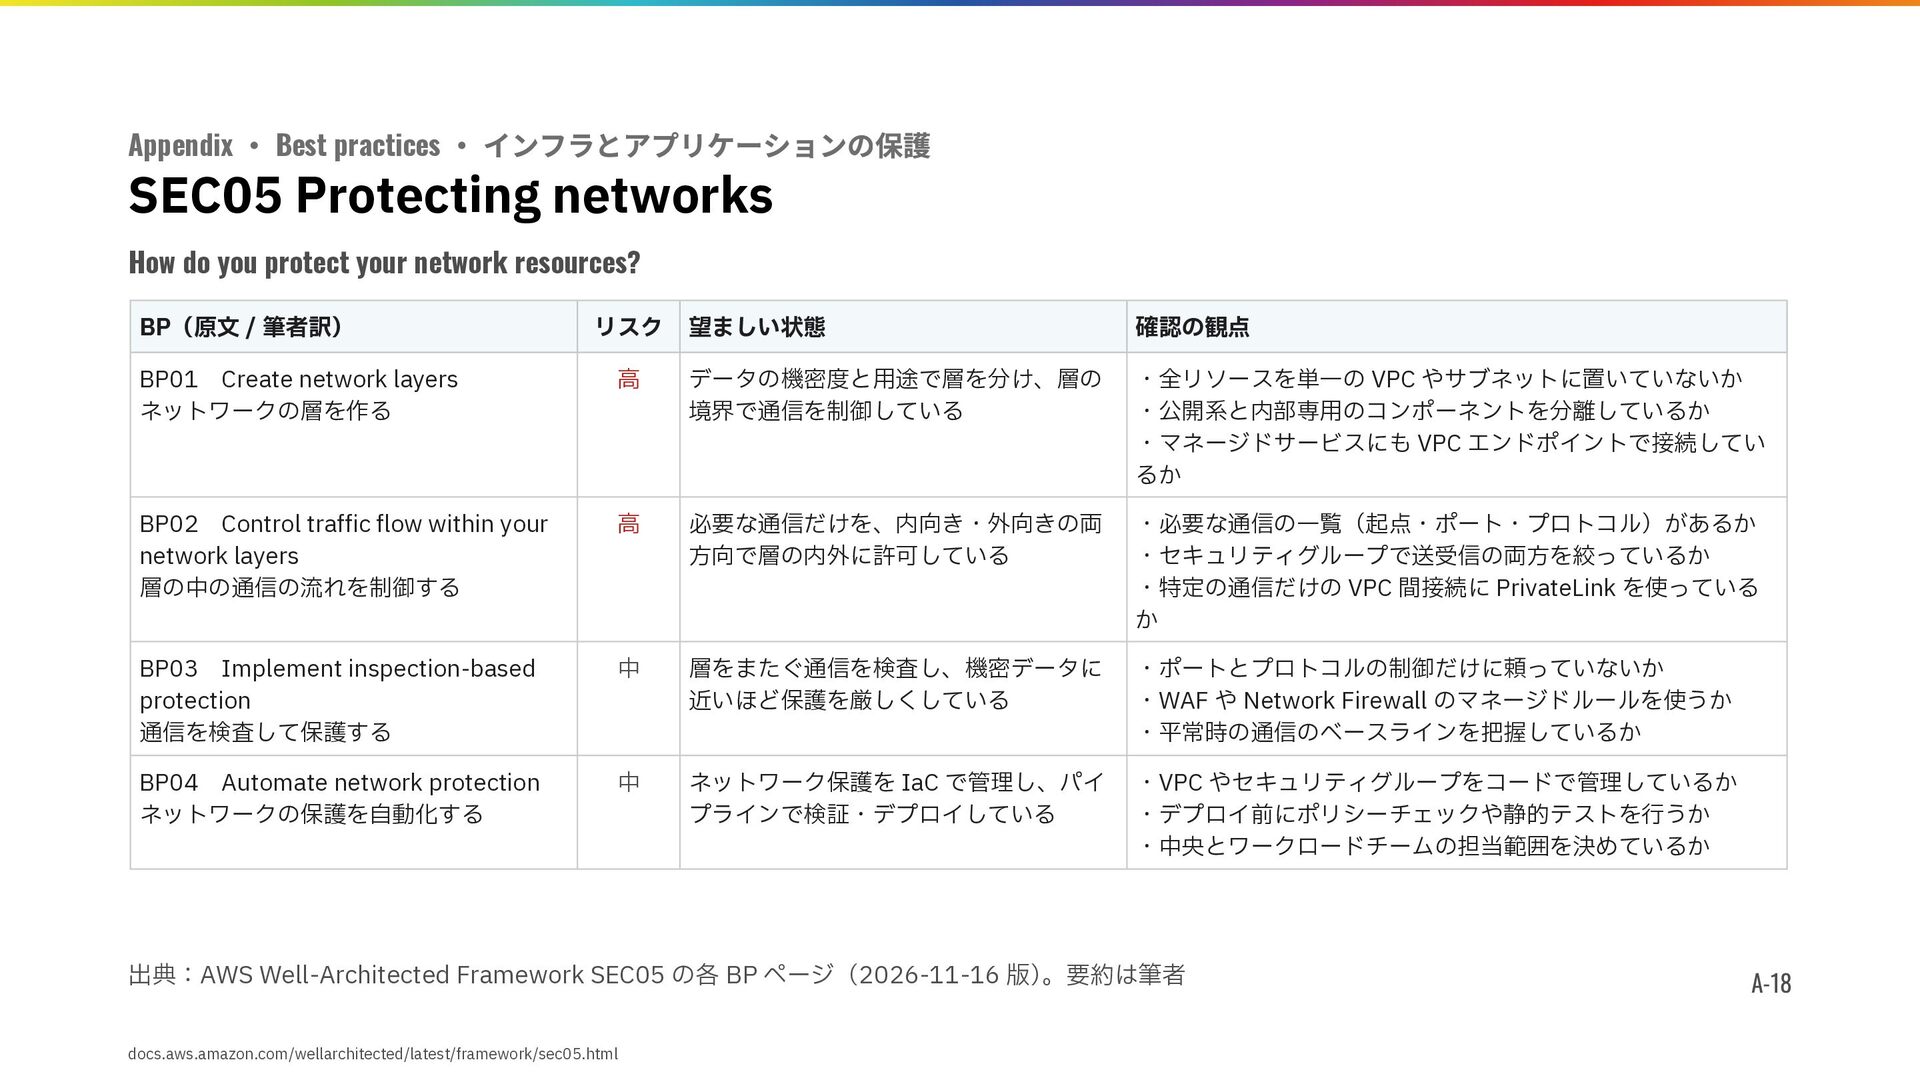
Appendix ・ Best practices ・ インフラとアプリケーションの保護 SEC05 Protecting networks How
do you protect your network resources? BP(原文 / 筆者訳) リスク 望ましい状態 確認の観点 BP01 Create network layers ネットワークの層を作る 高 データの機密度と用途で層を分け、層の 境界で通信を制御している ・全リソースを単一の VPC やサブネットに置いていないか ・公開系と内部専用のコンポーネントを分離しているか ・マネージドサービスにも VPC エンドポイントで接続してい るか BP02 Control traffic flow within your network layers 層の中の通信の流れを制御する 高 必要な通信だけを、内向き・外向きの両 方向で層の内外に許可している ・必要な通信の一覧(起点・ポート・プロトコル)があるか ・セキュリティグループで送受信の両方を絞っているか ・特定の通信だけの VPC 間接続に PrivateLink を使っている か BP03 Implement inspection-based protection 通信を検査して保護する 中 層をまたぐ通信を検査し、機密データに 近いほど保護を厳しくしている ・ポートとプロトコルの制御だけに頼っていないか ・WAF や Network Firewall のマネージドルールを使うか ・平常時の通信のベースラインを把握しているか BP04 Automate network protection ネットワークの保護を自動化する 中 ネットワーク保護を IaC で管理し、パイ プラインで検証・デプロイしている ・VPC やセキュリティグループをコードで管理しているか ・デプロイ前にポリシーチェックや静的テストを行うか ・中央とワークロードチームの担当範囲を決めているか 出典:AWS Well-Architected Framework SEC05 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec05.html A-18 -
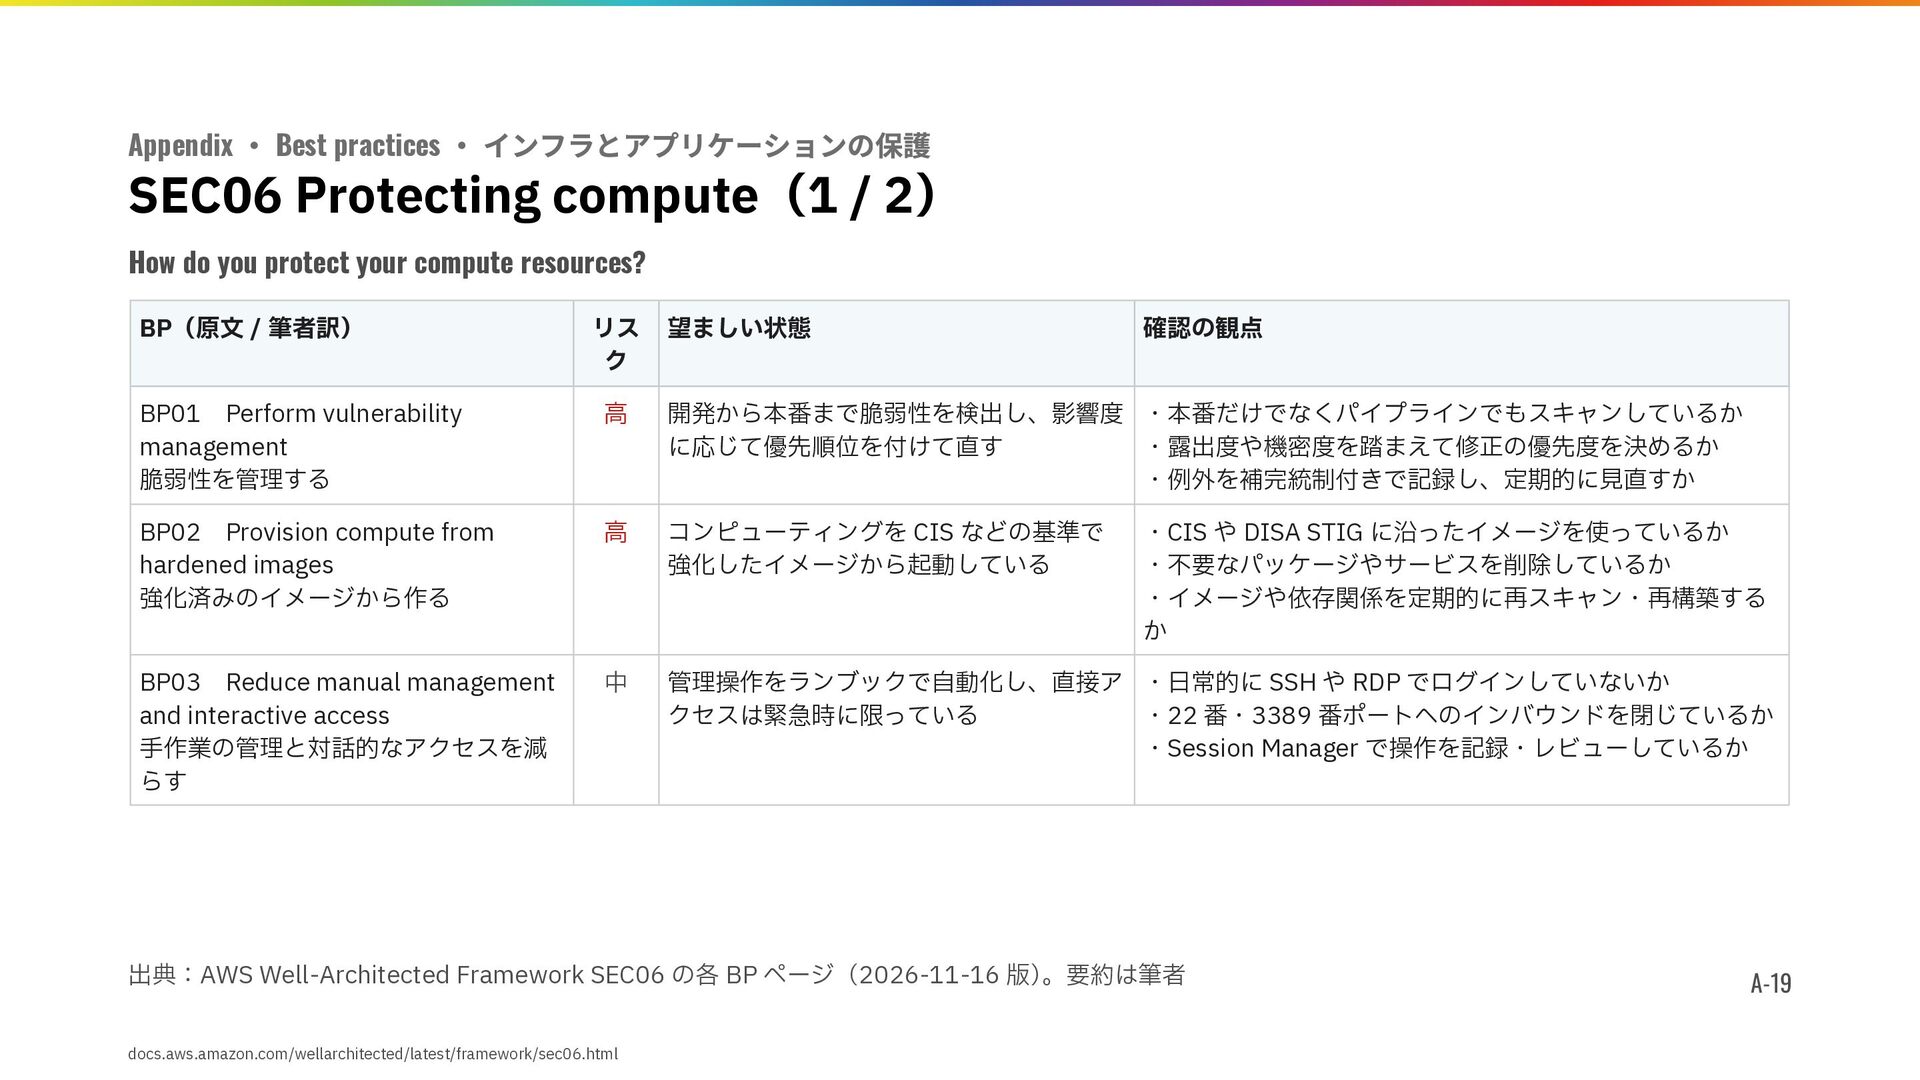
Appendix ・ Best practices ・ インフラとアプリケーションの保護 SEC06 Protecting compute(1 /
2) How do you protect your compute resources? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP01 Perform vulnerability management 脆弱性を管理する 高 開発から本番まで脆弱性を検出し、影響度 ・本番だけでなくパイプラインでもスキャンしているか に応じて優先順位を付けて直す ・露出度や機密度を踏まえて修正の優先度を決めるか ・例外を補完統制付きで記録し、定期的に見直すか BP02 Provision compute from hardened images 強化済みのイメージから作る 高 コンピューティングを CIS などの基準で 強化したイメージから起動している BP03 Reduce manual management and interactive access 手作業の管理と対話的なアクセスを減 らす 中 管理操作をランブックで自動化し、直接ア ・日常的に SSH や RDP でログインしていないか クセスは緊急時に限っている ・22 番・3389 番ポートへのインバウンドを閉じているか ・Session Manager で操作を記録・レビューしているか ・CIS や DISA STIG に沿ったイメージを使っているか ・不要なパッケージやサービスを削除しているか ・イメージや依存関係を定期的に再スキャン・再構築する か 出典:AWS Well-Architected Framework SEC06 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec06.html A-19 -
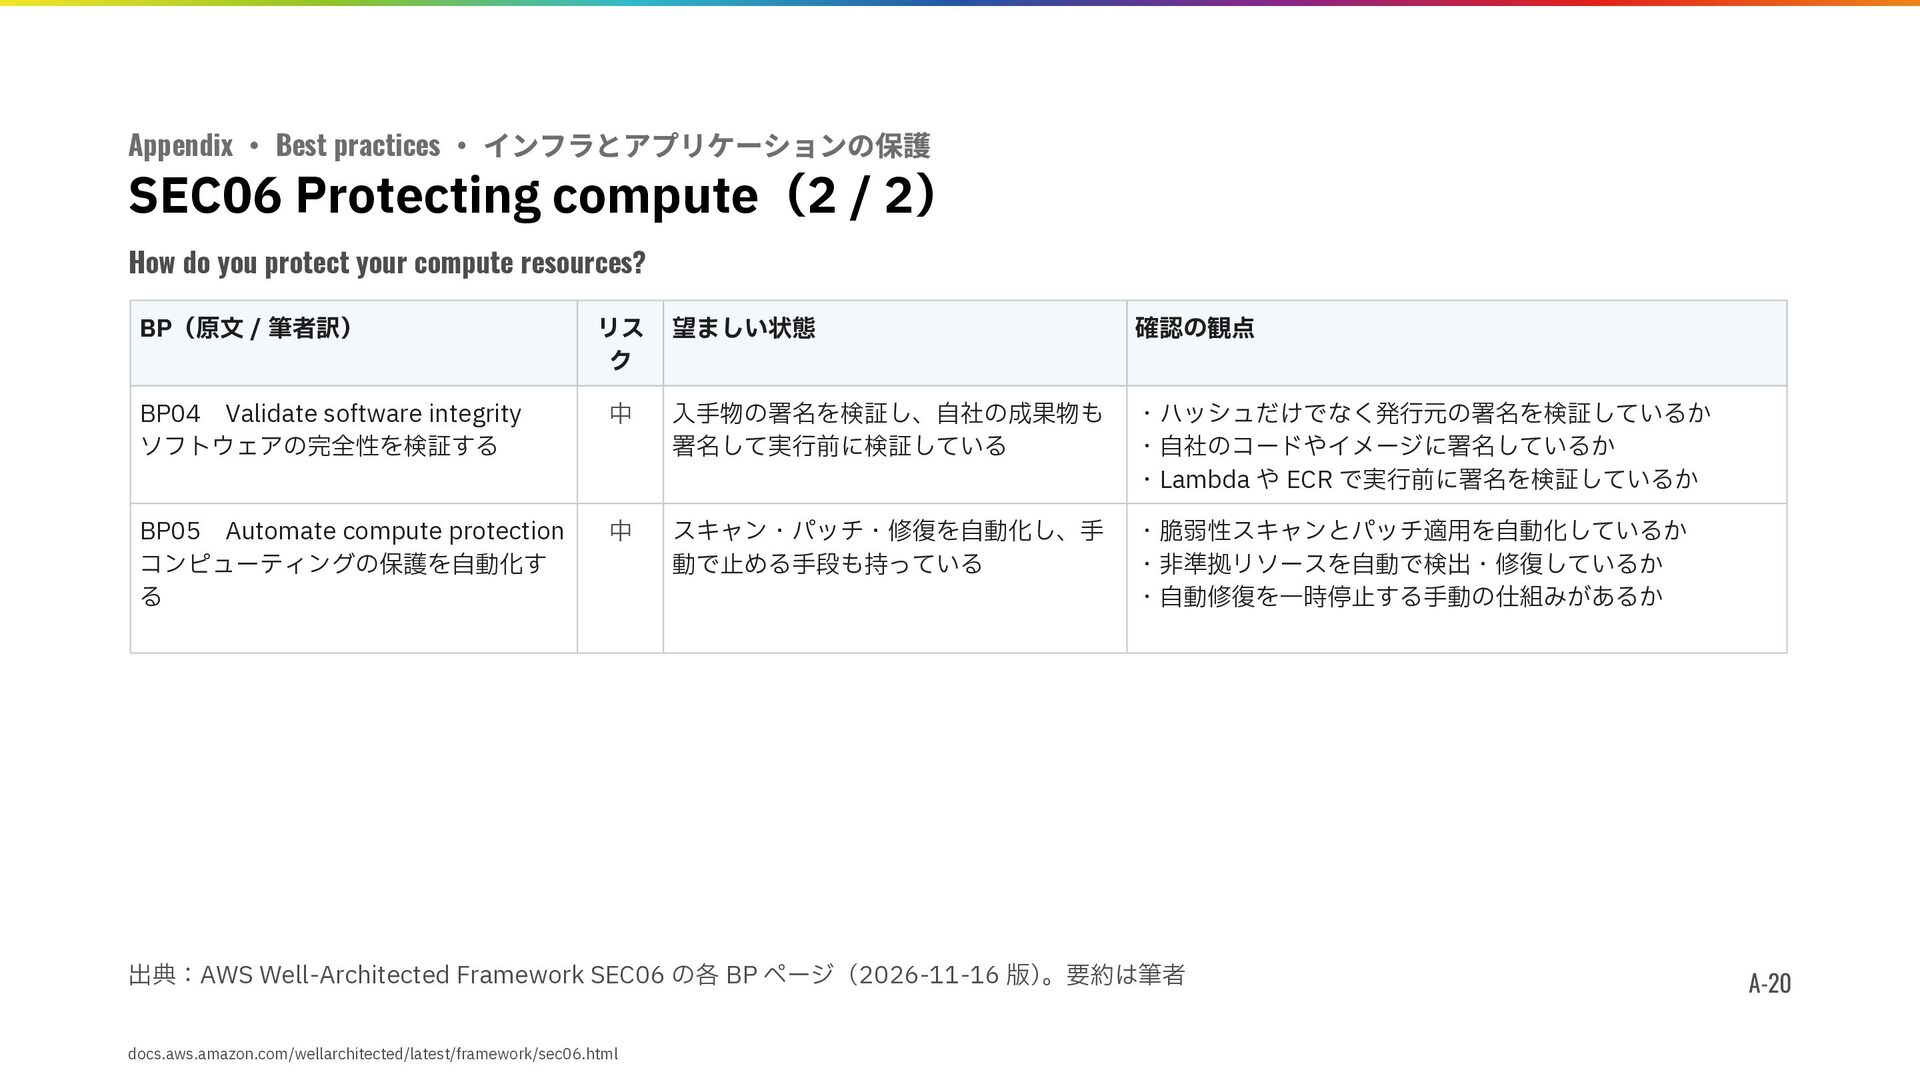
Appendix ・ Best practices ・ インフラとアプリケーションの保護 SEC06 Protecting compute(2 /
2) How do you protect your compute resources? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP04 Validate software integrity ソフトウェアの完全性を検証する 中 入手物の署名を検証し、自社の成果物も 署名して実行前に検証している ・ハッシュだけでなく発行元の署名を検証しているか ・自社のコードやイメージに署名しているか ・Lambda や ECR で実行前に署名を検証しているか BP05 Automate compute protection コンピューティングの保護を自動化す る 中 スキャン・パッチ・修復を自動化し、手 動で止める手段も持っている ・脆弱性スキャンとパッチ適用を自動化しているか ・非準拠リソースを自動で検出・修復しているか ・自動修復を一時停止する手動の仕組みがあるか 出典:AWS Well-Architected Framework SEC06 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec06.html A-20 -
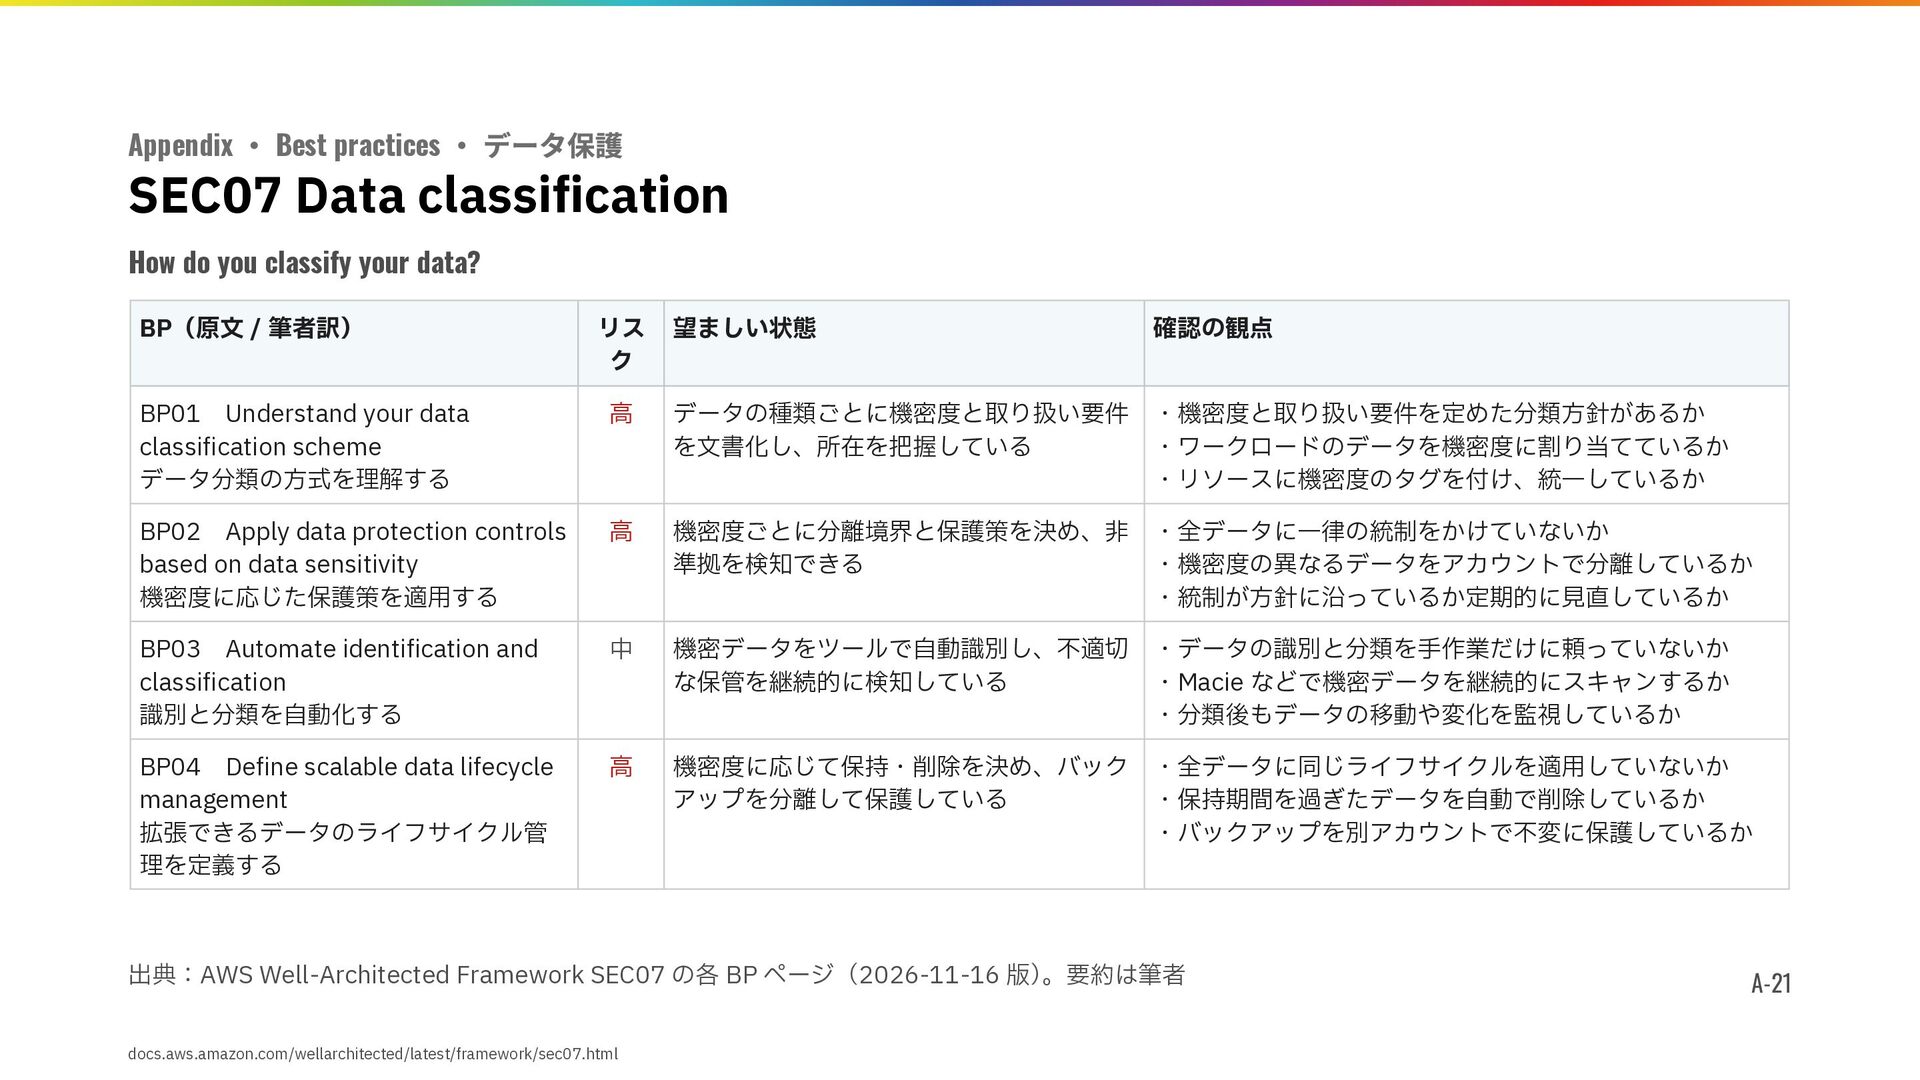
Appendix ・ Best practices ・ データ保護 SEC07 Data classification How
do you classify your data? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP01 Understand your data classification scheme データ分類の方式を理解する 高 データの種類ごとに機密度と取り扱い要件 を文書化し、所在を把握している ・機密度と取り扱い要件を定めた分類方針があるか ・ワークロードのデータを機密度に割り当てているか ・リソースに機密度のタグを付け、統一しているか BP02 Apply data protection controls based on data sensitivity 機密度に応じた保護策を適用する 高 機密度ごとに分離境界と保護策を決め、非 準拠を検知できる ・全データに一律の統制をかけていないか ・機密度の異なるデータをアカウントで分離しているか ・統制が方針に沿っているか定期的に見直しているか BP03 Automate identification and classification 識別と分類を自動化する 中 機密データをツールで自動識別し、不適切 な保管を継続的に検知している ・データの識別と分類を手作業だけに頼っていないか ・Macie などで機密データを継続的にスキャンするか ・分類後もデータの移動や変化を監視しているか BP04 Define scalable data lifecycle management 拡張できるデータのライフサイクル管 理を定義する 高 機密度に応じて保持・削除を決め、バック アップを分離して保護している ・全データに同じライフサイクルを適用していないか ・保持期間を過ぎたデータを自動で削除しているか ・バックアップを別アカウントで不変に保護しているか 出典:AWS Well-Architected Framework SEC07 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec07.html A-21 -
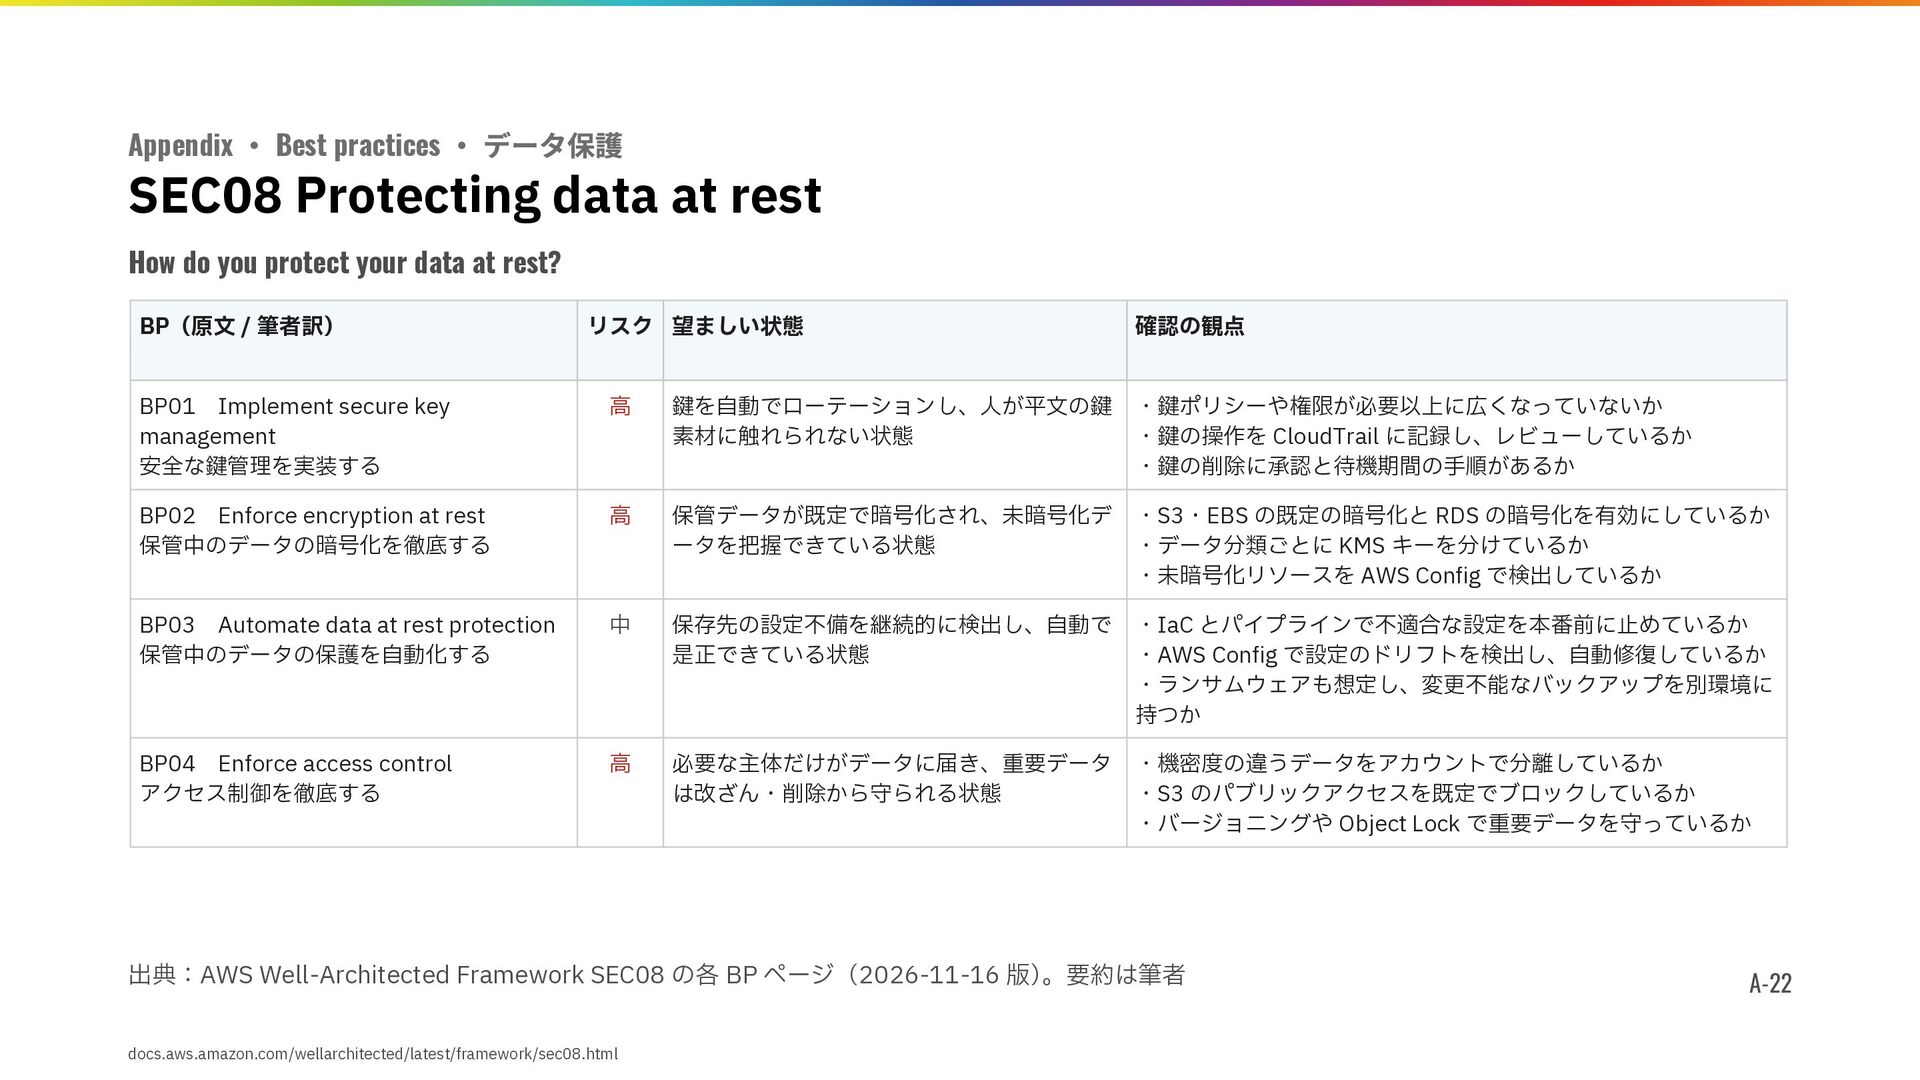
Appendix ・ Best practices ・ データ保護 SEC08 Protecting data at
rest How do you protect your data at rest? BP(原文 / 筆者訳) リスク 望ましい状態 確認の観点 BP01 Implement secure key management 安全な鍵管理を実装する 高 鍵を自動でローテーションし、人が平文の鍵 素材に触れられない状態 ・鍵ポリシーや権限が必要以上に広くなっていないか ・鍵の操作を CloudTrail に記録し、レビューしているか ・鍵の削除に承認と待機期間の手順があるか BP02 Enforce encryption at rest 保管中のデータの暗号化を徹底する 高 保管データが既定で暗号化され、未暗号化デ ータを把握できている状態 ・S3・EBS の既定の暗号化と RDS の暗号化を有効にしているか ・データ分類ごとに KMS キーを分けているか ・未暗号化リソースを AWS Config で検出しているか BP03 Automate data at rest protection 保管中のデータの保護を自動化する 中 保存先の設定不備を継続的に検出し、自動で 是正できている状態 ・IaC とパイプラインで不適合な設定を本番前に止めているか ・AWS Config で設定のドリフトを検出し、自動修復しているか ・ランサムウェアも想定し、変更不能なバックアップを別環境に 持つか BP04 Enforce access control アクセス制御を徹底する 高 必要な主体だけがデータに届き、重要データ は改ざん・削除から守られる状態 ・機密度の違うデータをアカウントで分離しているか ・S3 のパブリックアクセスを既定でブロックしているか ・バージョニングや Object Lock で重要データを守っているか 出典:AWS Well-Architected Framework SEC08 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec08.html A-22 -
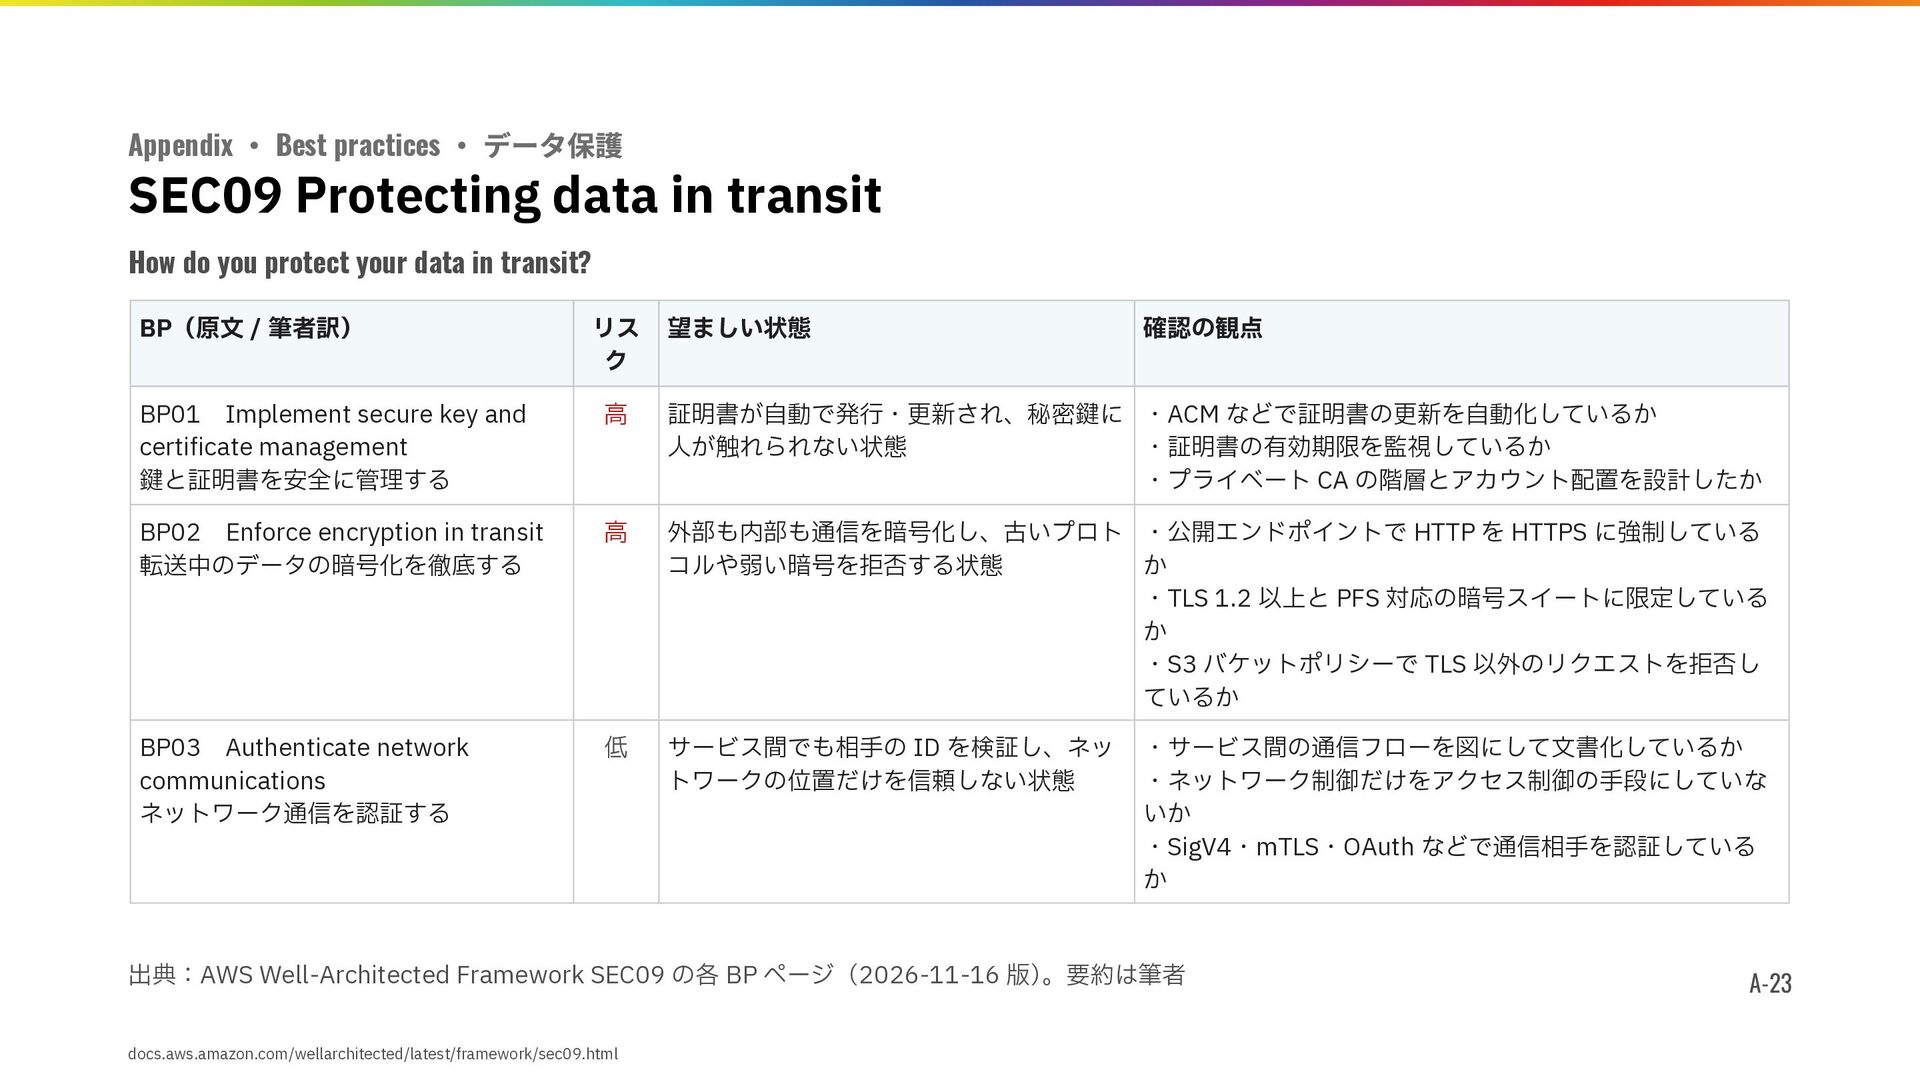
Appendix ・ Best practices ・ データ保護 SEC09 Protecting data in
transit How do you protect your data in transit? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP01 Implement secure key and certificate management 鍵と証明書を安全に管理する 高 証明書が自動で発行・更新され、秘密鍵に ・ACM などで証明書の更新を自動化しているか 人が触れられない状態 ・証明書の有効期限を監視しているか ・プライベート CA の階層とアカウント配置を設計したか BP02 Enforce encryption in transit 転送中のデータの暗号化を徹底する 高 外部も内部も通信を暗号化し、古いプロト ・公開エンドポイントで HTTP を HTTPS に強制している コルや弱い暗号を拒否する状態 か ・TLS 1.2 以上と PFS 対応の暗号スイートに限定している か ・S3 バケットポリシーで TLS 以外のリクエストを拒否し ているか BP03 Authenticate network communications ネットワーク通信を認証する 低 サービス間でも相手の ID を検証し、ネッ トワークの位置だけを信頼しない状態 ・サービス間の通信フローを図にして文書化しているか ・ネットワーク制御だけをアクセス制御の手段にしていな いか ・SigV4・mTLS・OAuth などで通信相手を認証している か 出典:AWS Well-Architected Framework SEC09 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec09.html A-23 -
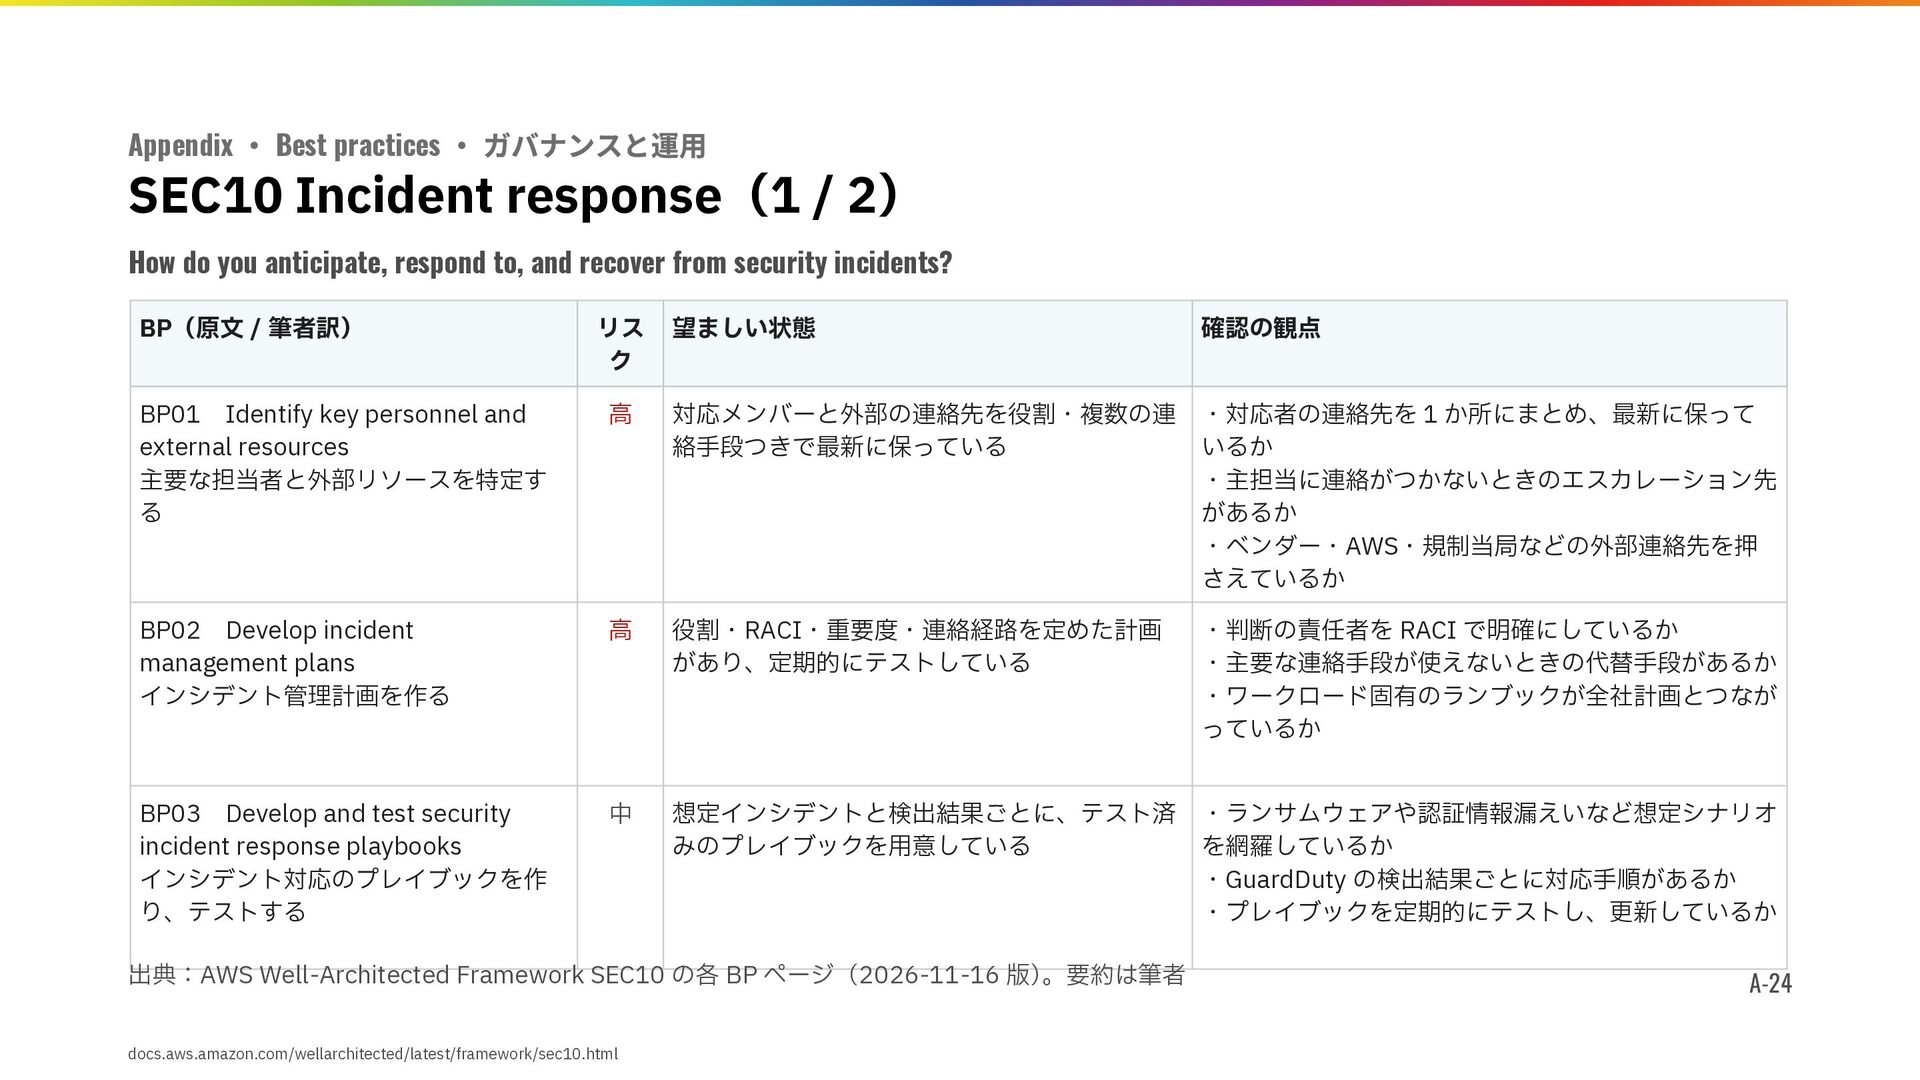
Appendix ・ Best practices ・ ガバナンスと運用 SEC10 Incident response(1 /
2) How do you anticipate, respond to, and recover from security incidents? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP01 Identify key personnel and external resources 主要な担当者と外部リソースを特定す る 高 対応メンバーと外部の連絡先を役割・複数の連 絡手段つきで最新に保っている ・対応者の連絡先を 1 か所にまとめ、最新に保って いるか ・主担当に連絡がつかないときのエスカレーション先 があるか ・ベンダー・AWS・規制当局などの外部連絡先を押 さえているか BP02 Develop incident management plans インシデント管理計画を作る 高 役割・RACI・重要度・連絡経路を定めた計画 があり、定期的にテストしている ・判断の責任者を RACI で明確にしているか ・主要な連絡手段が使えないときの代替手段があるか ・ワークロード固有のランブックが全社計画とつなが っているか BP03 Develop and test security incident response playbooks インシデント対応のプレイブックを作 り、テストする 中 想定インシデントと検出結果ごとに、テスト済 みのプレイブックを用意している ・ランサムウェアや認証情報漏えいなど想定シナリオ を網羅しているか ・GuardDuty の検出結果ごとに対応手順があるか ・プレイブックを定期的にテストし、更新しているか 出典:AWS Well-Architected Framework SEC10 の各 BP ページ(2026-11-16 版) 。要約は筆者 A-24 docs.aws.amazon.com/wellarchitected/latest/framework/sec10.html -
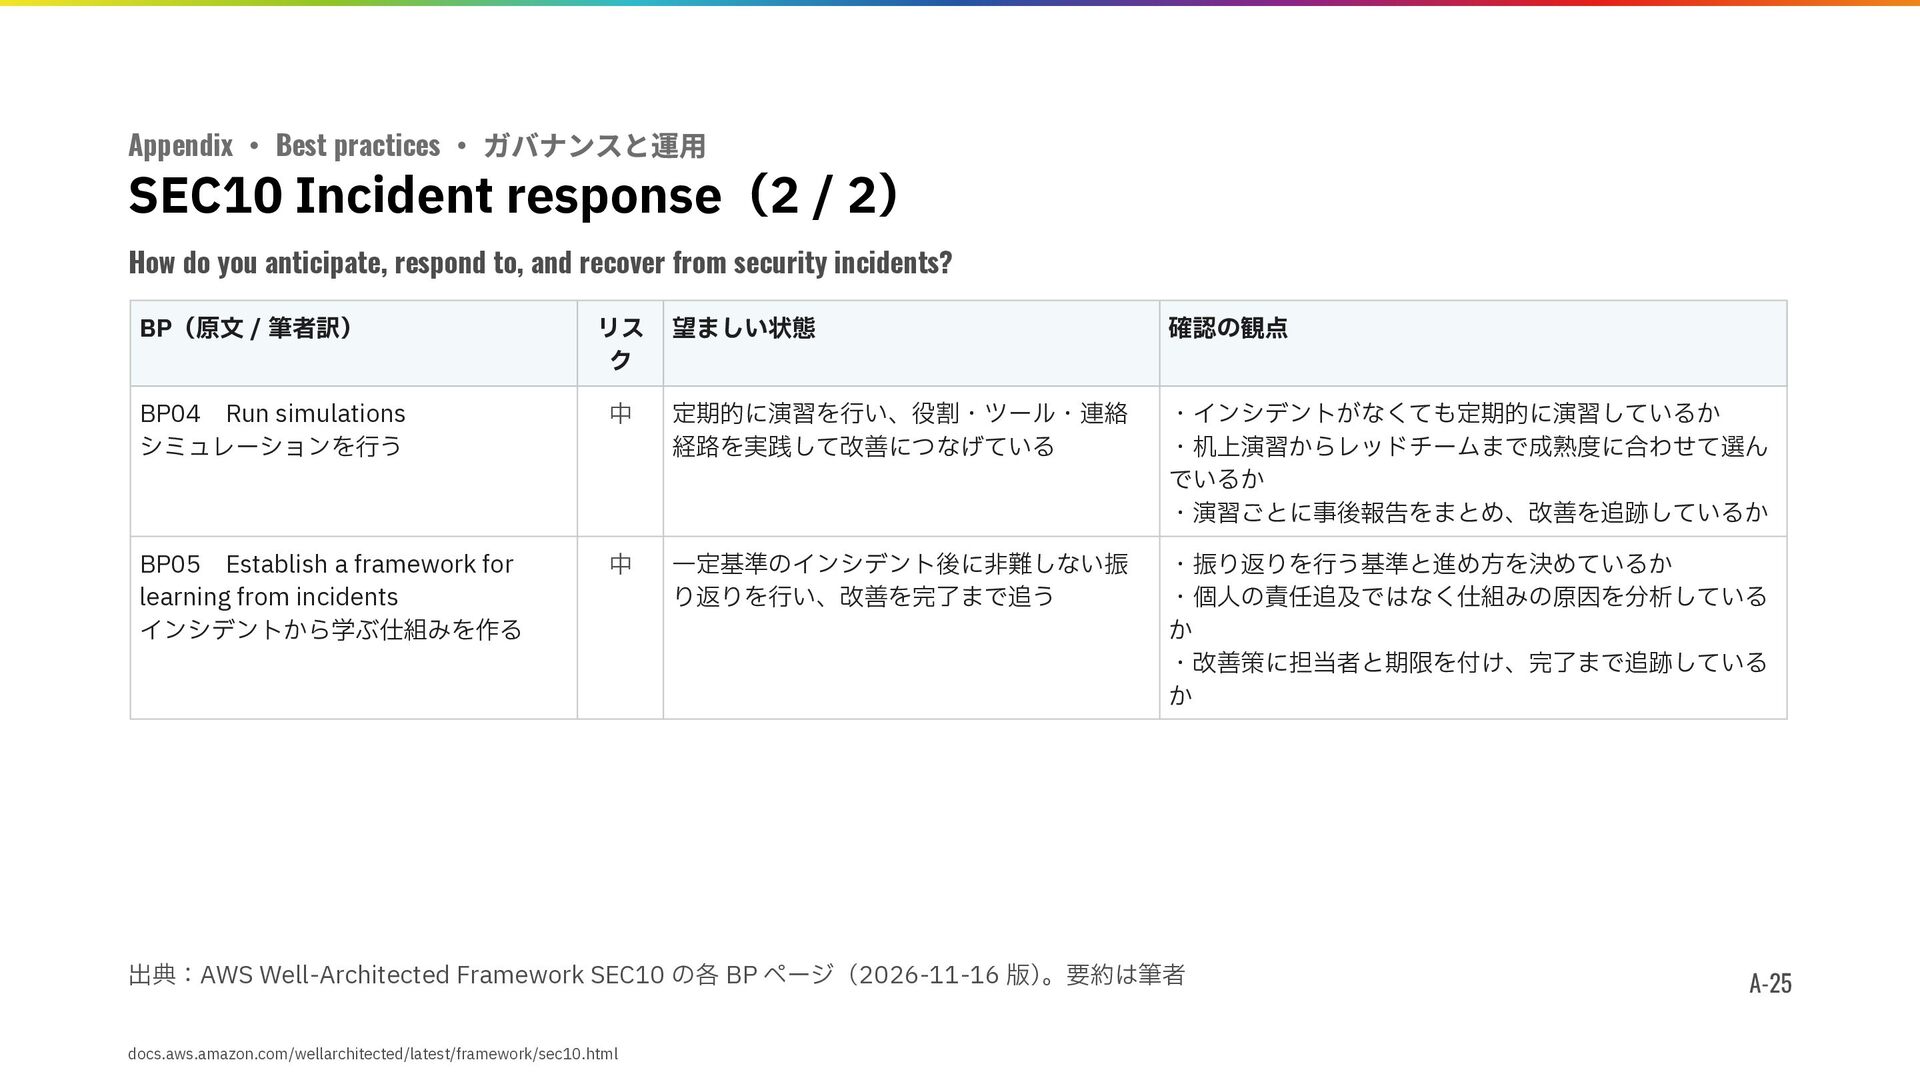
Appendix ・ Best practices ・ ガバナンスと運用 SEC10 Incident response(2 /
2) How do you anticipate, respond to, and recover from security incidents? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP04 Run simulations シミュレーションを行う 中 定期的に演習を行い、役割・ツール・連絡 経路を実践して改善につなげている ・インシデントがなくても定期的に演習しているか ・机上演習からレッドチームまで成熟度に合わせて選ん でいるか ・演習ごとに事後報告をまとめ、改善を追跡しているか BP05 Establish a framework for learning from incidents インシデントから学ぶ仕組みを作る 中 一定基準のインシデント後に非難しない振 り返りを行い、改善を完了まで追う ・振り返りを行う基準と進め方を決めているか ・個人の責任追及ではなく仕組みの原因を分析している か ・改善策に担当者と期限を付け、完了まで追跡している か 出典:AWS Well-Architected Framework SEC10 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec10.html A-25 -
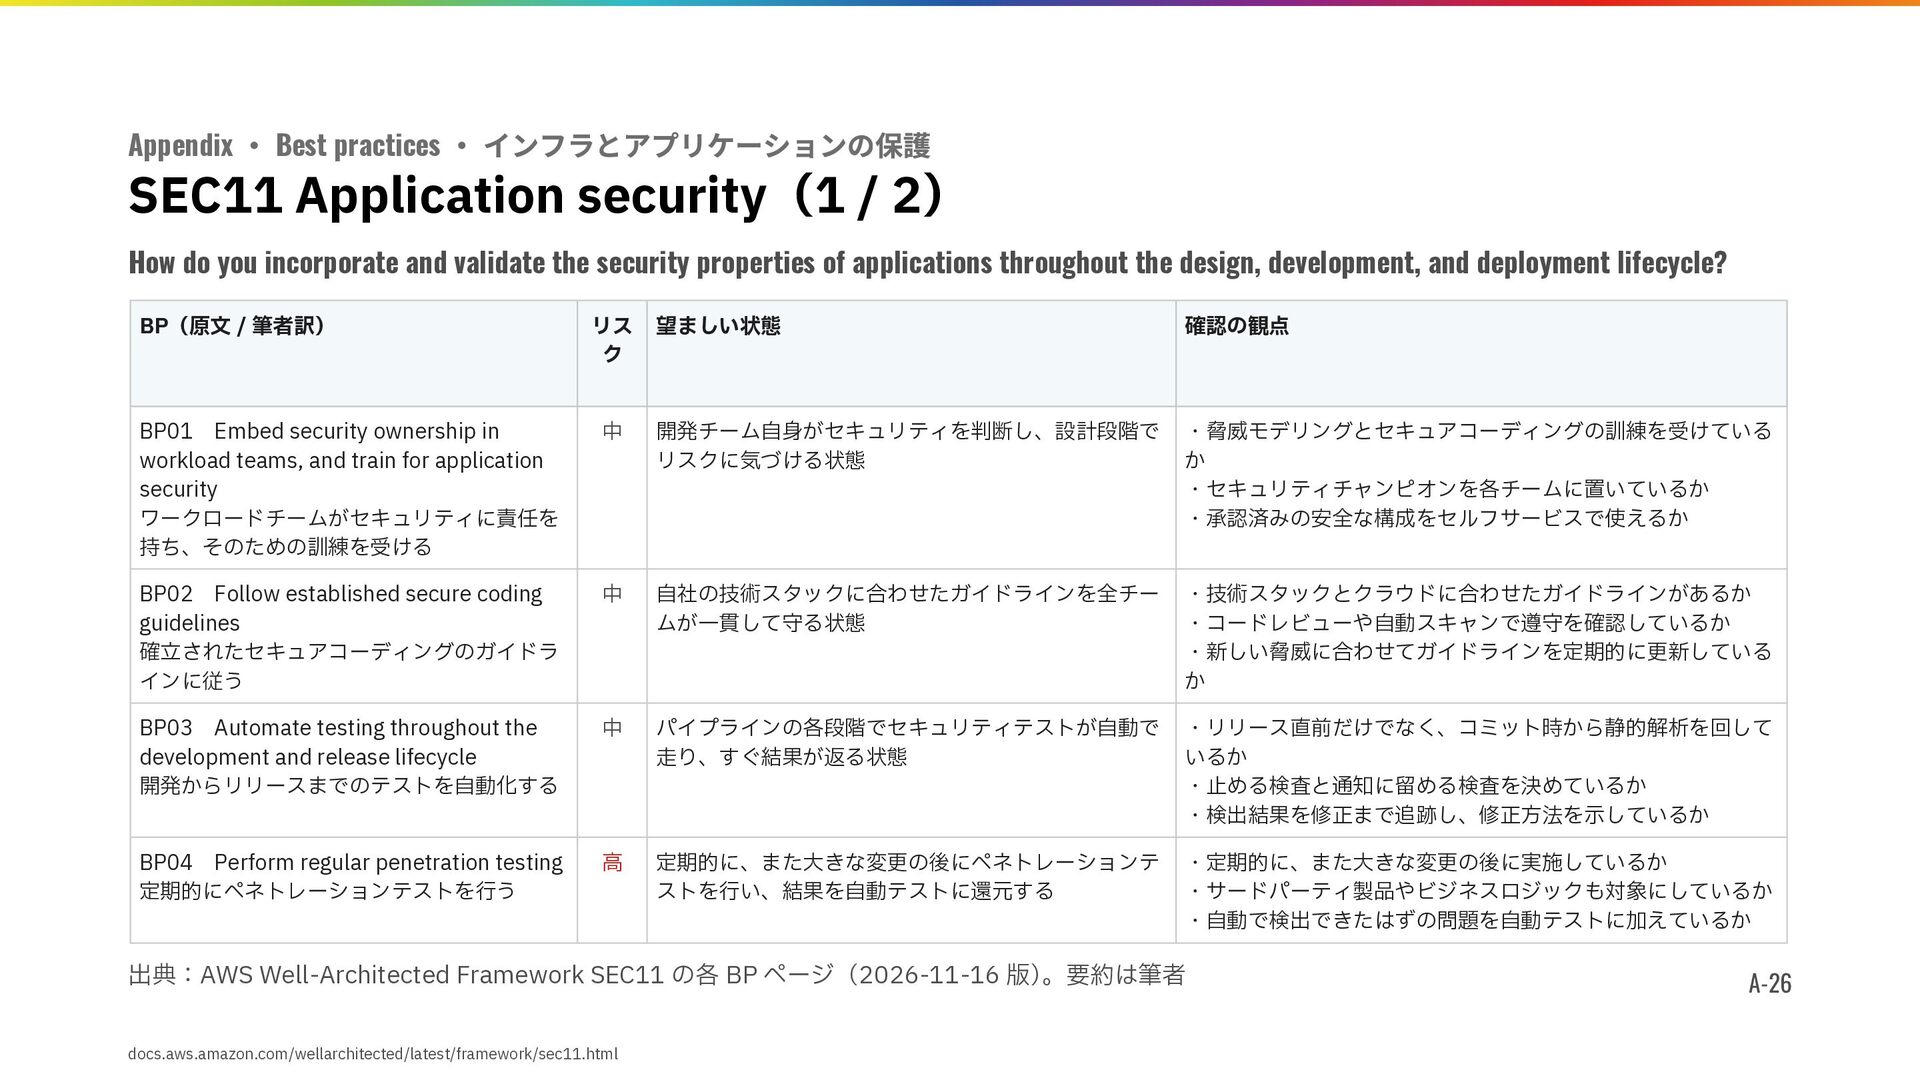
Appendix ・ Best practices ・ インフラとアプリケーションの保護 SEC11 Application security(1 /
2) How do you incorporate and validate the security properties of applications throughout the design, development, and deployment lifecycle? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP01 Embed security ownership in workload teams, and train for application security ワークロードチームがセキュリティに責任を 持ち、そのための訓練を受ける 中 開発チーム自身がセキュリティを判断し、設計段階で リスクに気づける状態 ・脅威モデリングとセキュアコーディングの訓練を受けている か ・セキュリティチャンピオンを各チームに置いているか ・承認済みの安全な構成をセルフサービスで使えるか BP02 Follow established secure coding guidelines 確立されたセキュアコーディングのガイドラ インに従う 中 自社の技術スタックに合わせたガイドラインを全チー ムが一貫して守る状態 ・技術スタックとクラウドに合わせたガイドラインがあるか ・コードレビューや自動スキャンで遵守を確認しているか ・新しい脅威に合わせてガイドラインを定期的に更新している か BP03 Automate testing throughout the development and release lifecycle 開発からリリースまでのテストを自動化する 中 パイプラインの各段階でセキュリティテストが自動で 走り、すぐ結果が返る状態 ・リリース直前だけでなく、コミット時から静的解析を回して いるか ・止める検査と通知に留める検査を決めているか ・検出結果を修正まで追跡し、修正方法を示しているか BP04 Perform regular penetration testing 定期的にペネトレーションテストを行う 高 定期的に、また大きな変更の後にペネトレーションテ ストを行い、結果を自動テストに還元する ・定期的に、また大きな変更の後に実施しているか ・サードパーティ製品やビジネスロジックも対象にしているか ・自動で検出できたはずの問題を自動テストに加えているか 出典:AWS Well-Architected Framework SEC11 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec11.html A-26 -
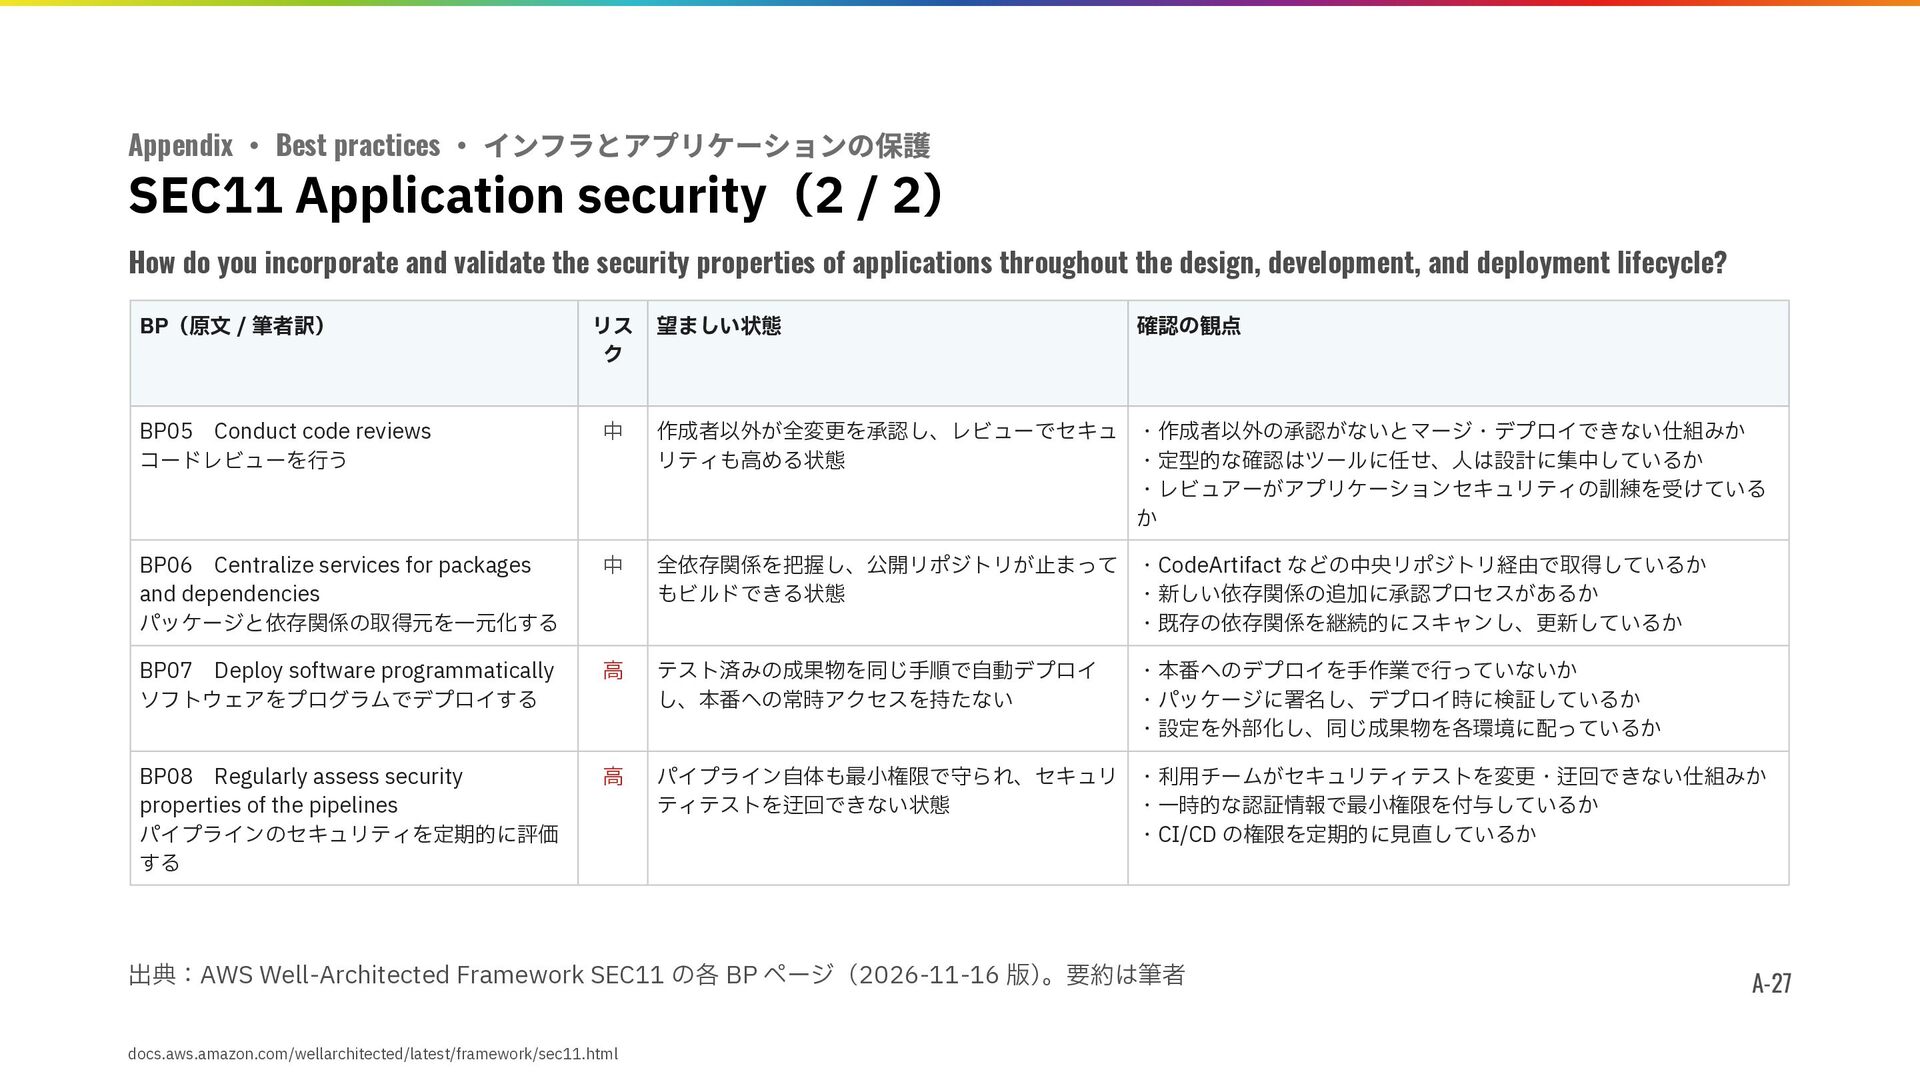
Appendix ・ Best practices ・ インフラとアプリケーションの保護 SEC11 Application security(2 /
2) How do you incorporate and validate the security properties of applications throughout the design, development, and deployment lifecycle? BP(原文 / 筆者訳) リス ク 望ましい状態 確認の観点 BP05 Conduct code reviews コードレビューを行う 中 作成者以外が全変更を承認し、レビューでセキュ ・作成者以外の承認がないとマージ・デプロイできない仕組みか リティも高める状態 ・定型的な確認はツールに任せ、人は設計に集中しているか ・レビュアーがアプリケーションセキュリティの訓練を受けている か BP06 Centralize services for packages and dependencies パッケージと依存関係の取得元を一元化する 中 全依存関係を把握し、公開リポジトリが止まって ・CodeArtifact などの中央リポジトリ経由で取得しているか もビルドできる状態 ・新しい依存関係の追加に承認プロセスがあるか ・既存の依存関係を継続的にスキャンし、更新しているか BP07 Deploy software programmatically ソフトウェアをプログラムでデプロイする 高 テスト済みの成果物を同じ手順で自動デプロイ し、本番への常時アクセスを持たない BP08 Regularly assess security properties of the pipelines パイプラインのセキュリティを定期的に評価 する 高 パイプライン自体も最小権限で守られ、セキュリ ・利用チームがセキュリティテストを変更・迂回できない仕組みか ティテストを迂回できない状態 ・一時的な認証情報で最小権限を付与しているか ・CI/CD の権限を定期的に見直しているか ・本番へのデプロイを手作業で行っていないか ・パッケージに署名し、デプロイ時に検証しているか ・設定を外部化し、同じ成果物を各環境に配っているか 出典:AWS Well-Architected Framework SEC11 の各 BP ページ(2026-11-16 版) 。要約は筆者 docs.aws.amazon.com/wellarchitected/latest/framework/sec11.html A-27 -
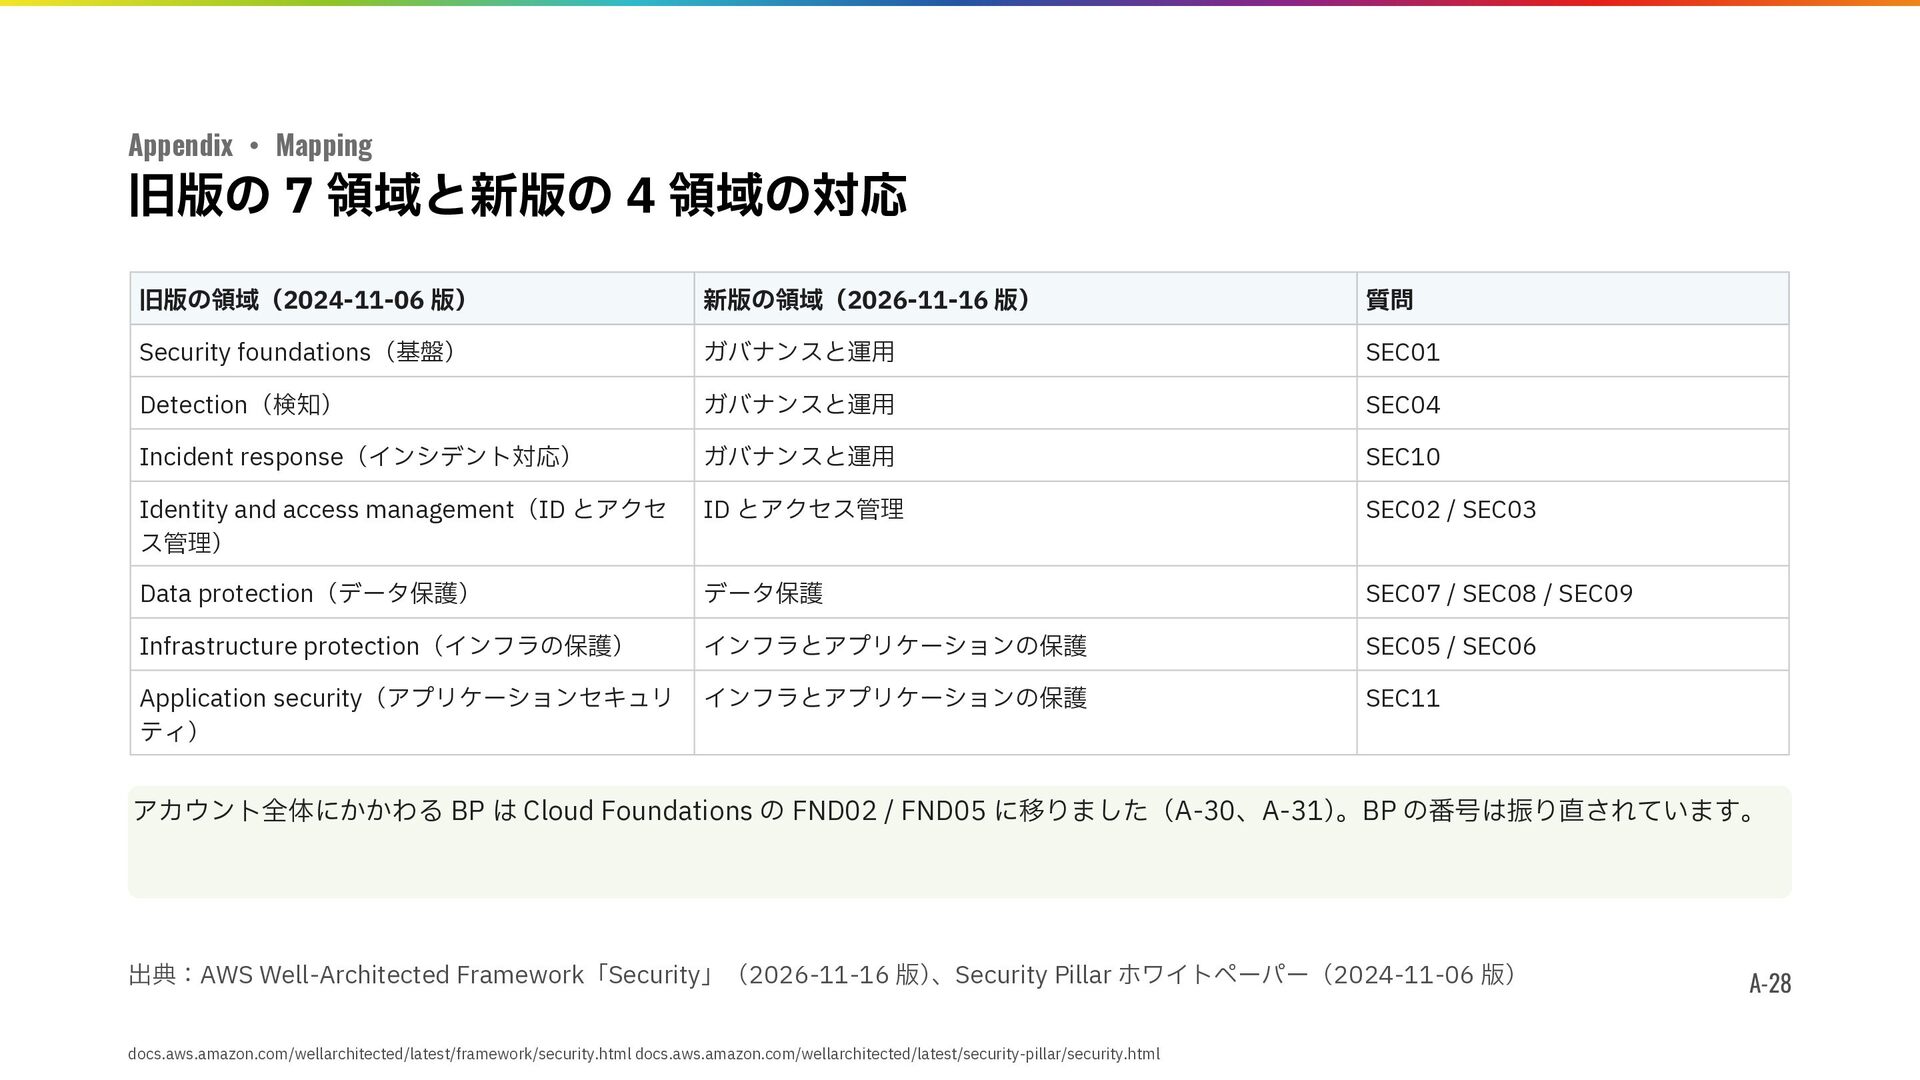
Appendix ・ Mapping 旧版の 7 領域と新版の 4 領域の対応 旧版の領域(2024-11-06 版)
新版の領域(2026-11-16 版) 質問 Security foundations(基盤) ガバナンスと運用 SEC01 Detection(検知) ガバナンスと運用 SEC04 Incident response(インシデント対応) ガバナンスと運用 SEC10 Identity and access management(ID とアクセ ス管理) ID とアクセス管理 SEC02 / SEC03 Data protection(データ保護) データ保護 SEC07 / SEC08 / SEC09 Infrastructure protection(インフラの保護) インフラとアプリケーションの保護 SEC05 / SEC06 Application security(アプリケーションセキュリ ティ) インフラとアプリケーションの保護 SEC11 アカウント全体にかかわる BP は Cloud Foundations の FND02 / FND05 に移りました(A-30、A-31)。BP の番号は振り直されています。 出典:AWS Well-Architected Framework「Security」(2026-11-16 版) 、Security Pillar ホワイトペーパー(2024-11-06 版) docs.aws.amazon.com/wellarchitected/latest/framework/security.html docs.aws.amazon.com/wellarchitected/latest/security-pillar/security.html A-28 -
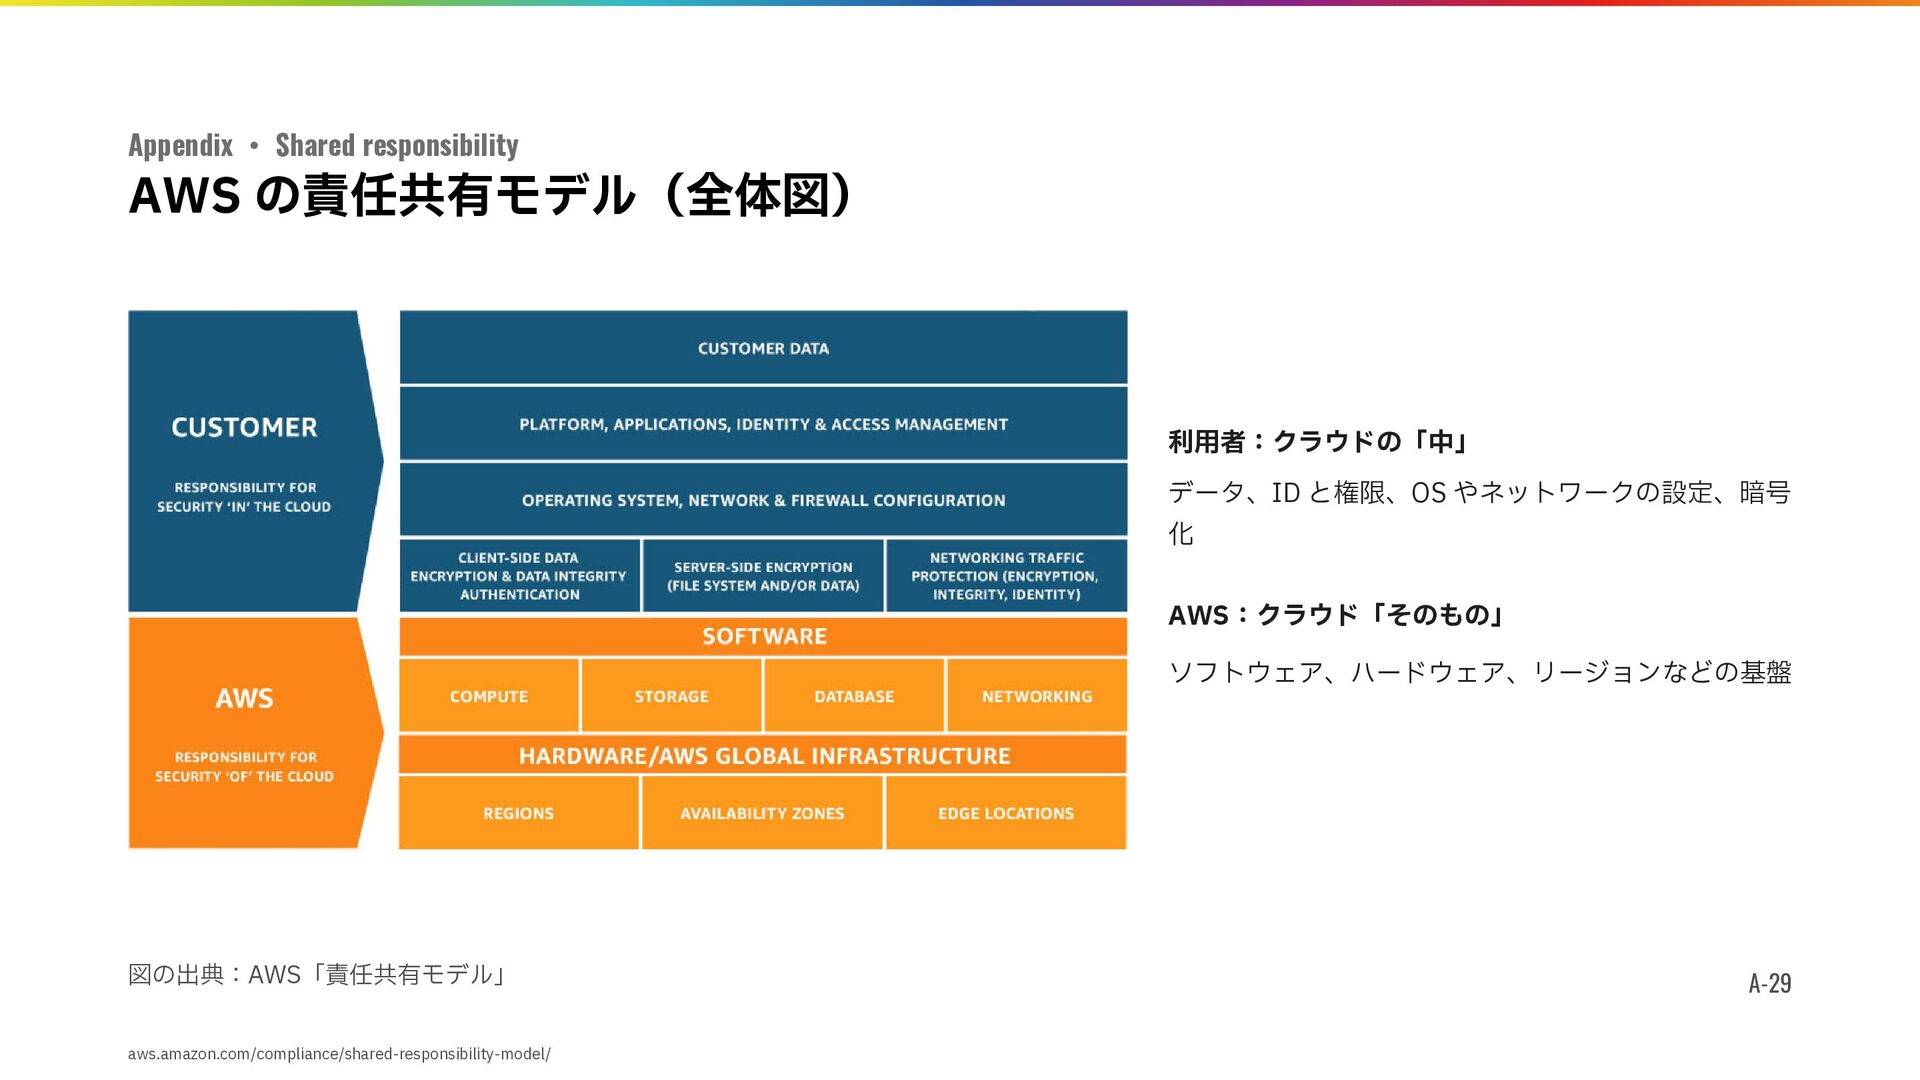
Appendix ・ Shared responsibility AWS の責任共有モデル(全体図) 利用者:クラウドの「中」 データ、ID と権限、OS やネットワークの設定、暗号
化 AWS:クラウド「そのもの」 ソフトウェア、ハードウェア、リージョンなどの基盤 図の出典:AWS「責任共有モデル」 aws.amazon.com/compliance/shared-responsibility-model/ A-29 -
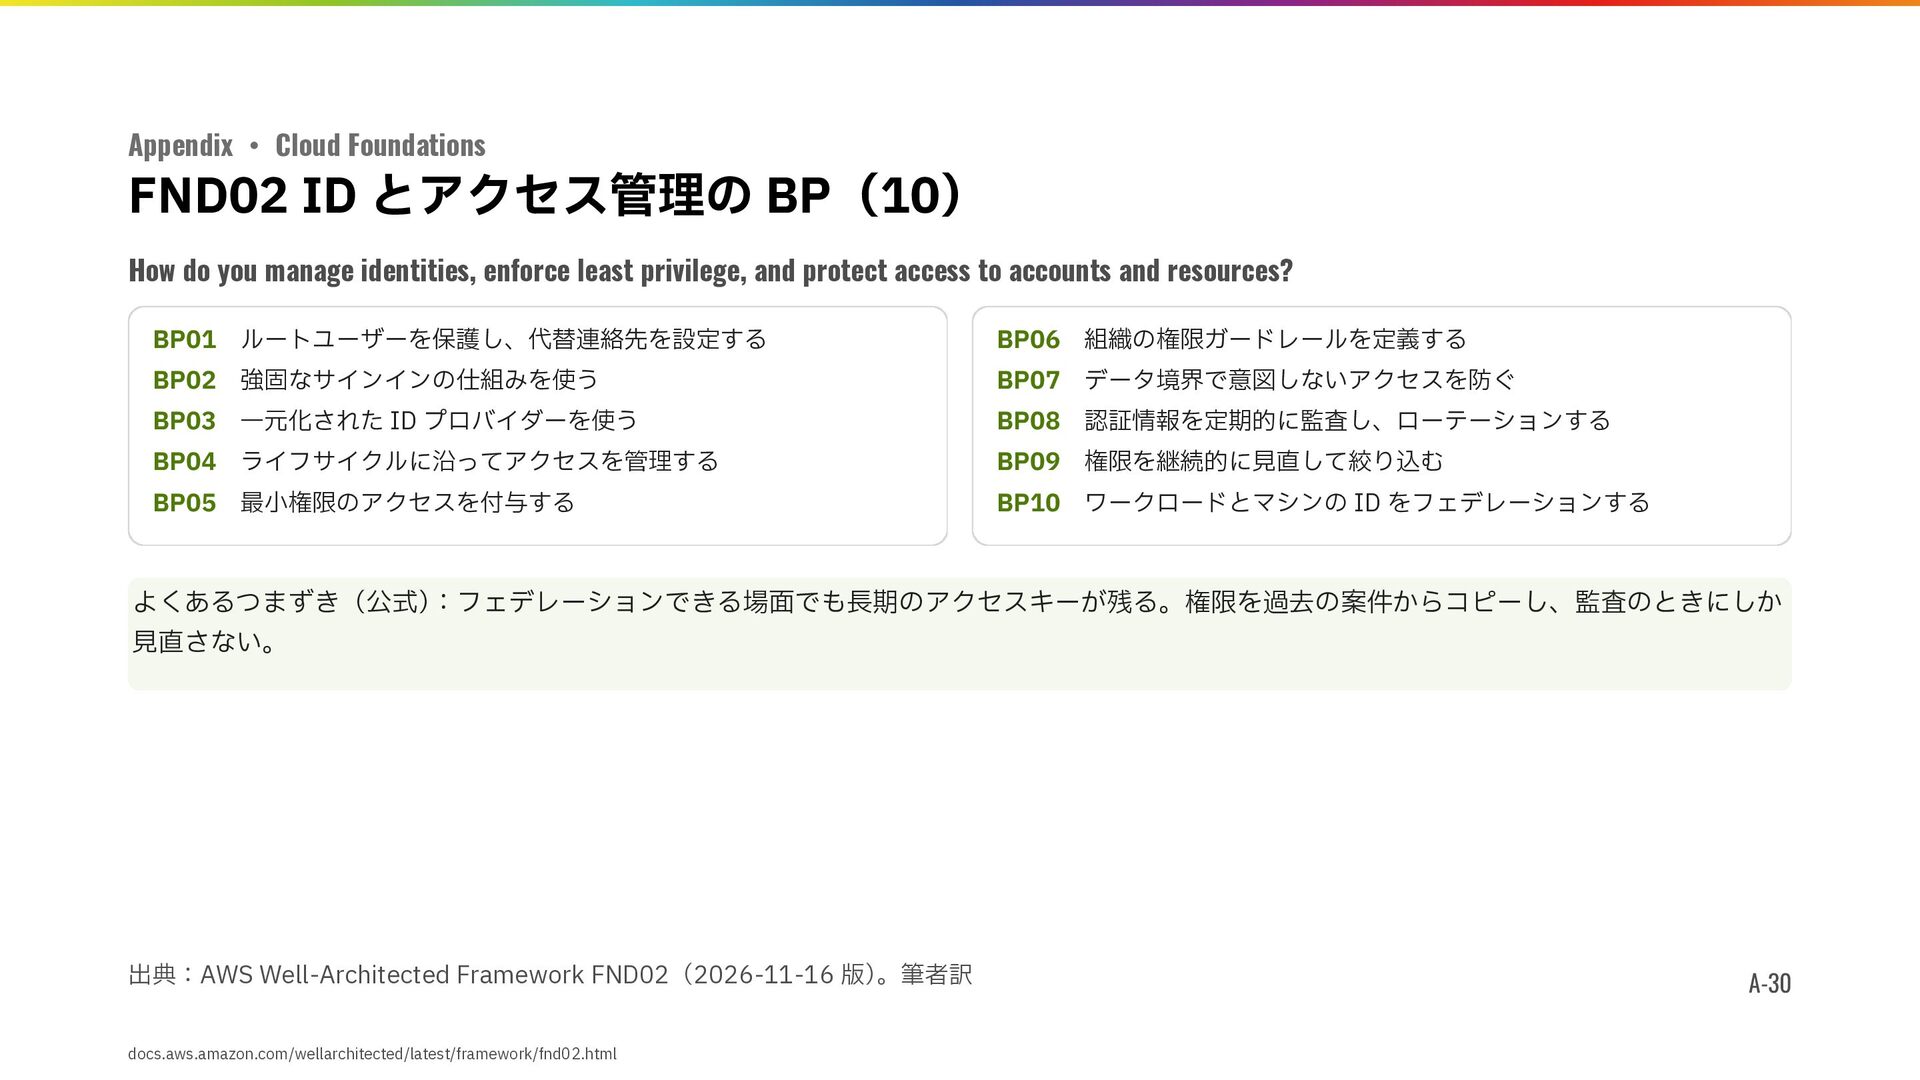
Appendix ・ Cloud Foundations FND02 ID とアクセス管理の BP(10) How do
you manage identities, enforce least privilege, and protect access to accounts and resources? BP01 ルートユーザーを保護し、代替連絡先を設定する BP06 組織の権限ガードレールを定義する BP02 強固なサインインの仕組みを使う BP07 データ境界で意図しないアクセスを防ぐ BP03 一元化された ID プロバイダーを使う BP08 認証情報を定期的に監査し、ローテーションする BP04 ライフサイクルに沿ってアクセスを管理する BP09 権限を継続的に見直して絞り込む BP05 最小権限のアクセスを付与する BP10 ワークロードとマシンの ID をフェデレーションする よくあるつまずき(公式):フェデレーションできる場面でも長期のアクセスキーが残る。権限を過去の案件からコピーし、監査のときにしか 見直さない。 出典:AWS Well-Architected Framework FND02(2026-11-16 版) 。筆者訳 docs.aws.amazon.com/wellarchitected/latest/framework/fnd02.html A-30 -
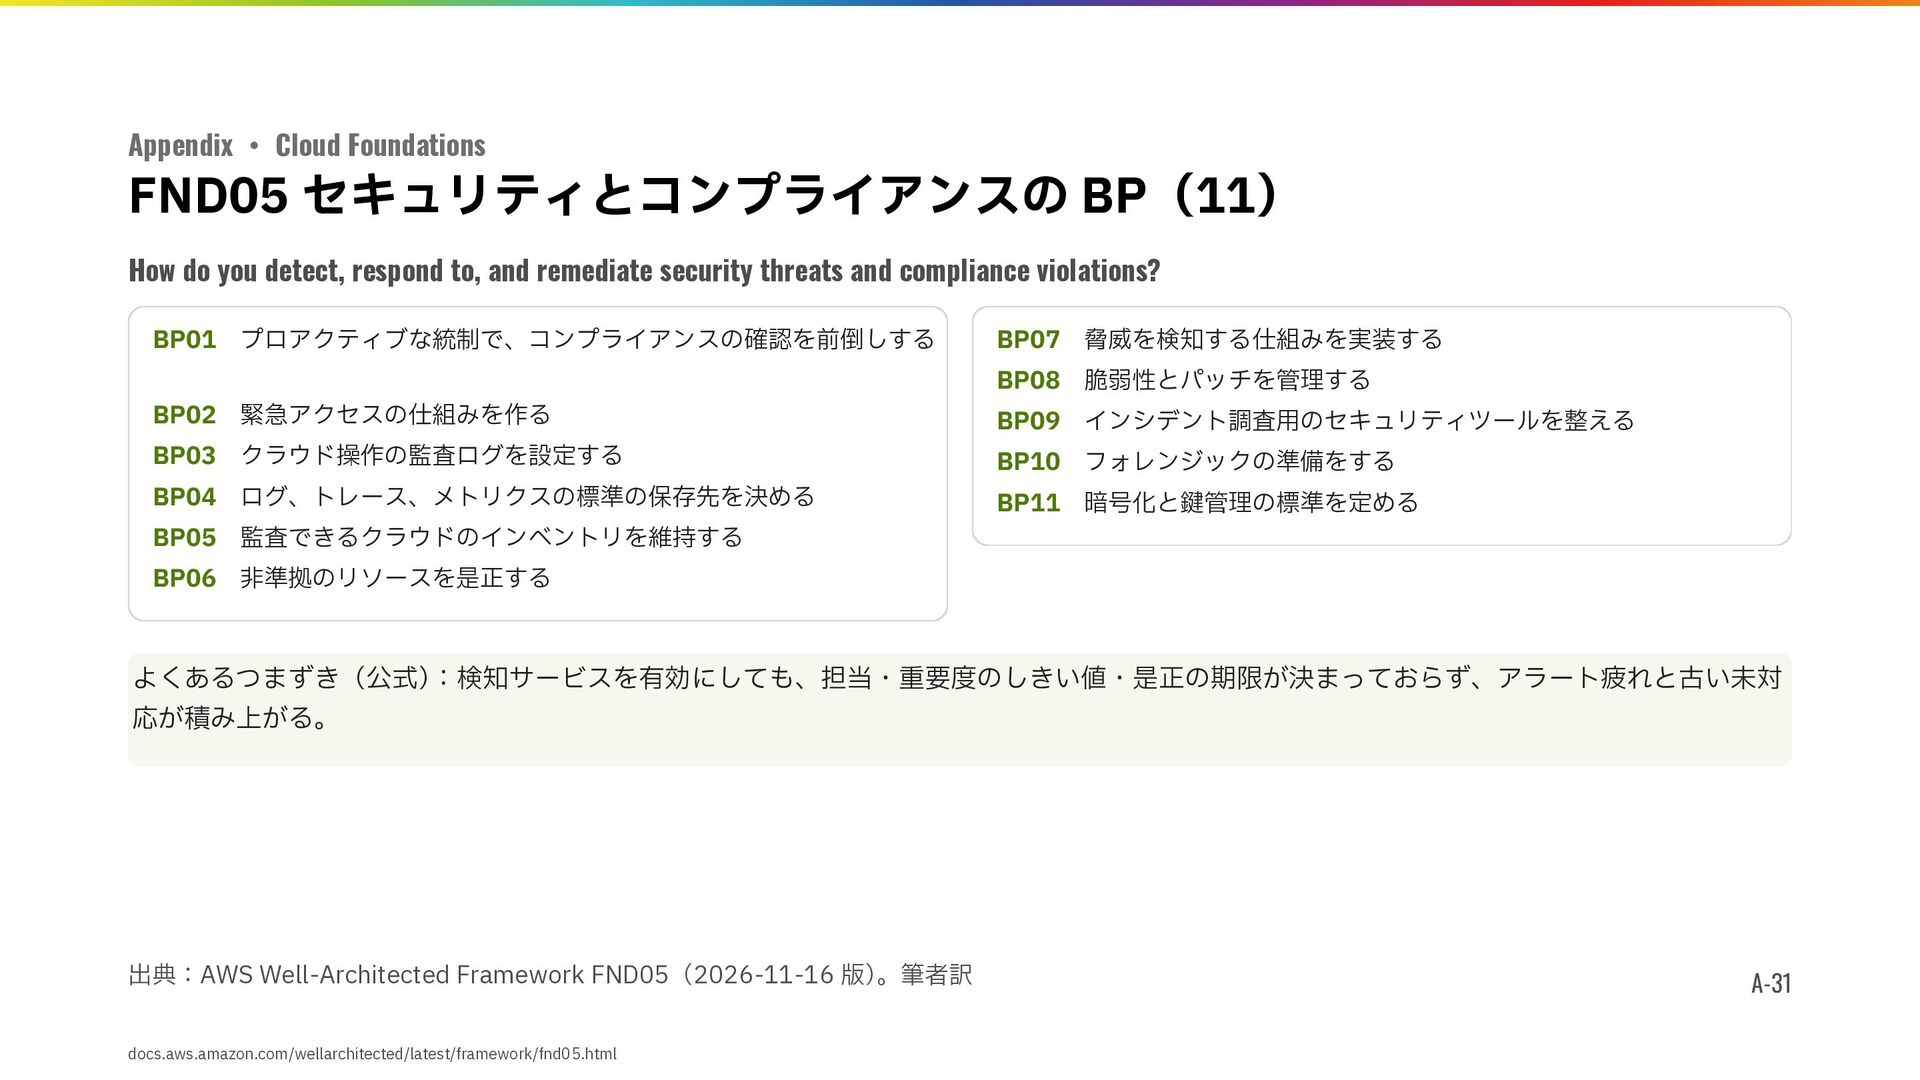
Appendix ・ Cloud Foundations FND05 セキュリティとコンプライアンスの BP(11) How do you
detect, respond to, and remediate security threats and compliance violations? BP01 プロアクティブな統制で、コンプライアンスの確認を前倒しする BP02 緊急アクセスの仕組みを作る BP03 クラウド操作の監査ログを設定する BP04 ログ、トレース、メトリクスの標準の保存先を決める BP05 監査できるクラウドのインベントリを維持する BP06 非準拠のリソースを是正する BP07 脅威を検知する仕組みを実装する BP08 脆弱性とパッチを管理する BP09 インシデント調査用のセキュリティツールを整える BP10 フォレンジックの準備をする BP11 暗号化と鍵管理の標準を定める よくあるつまずき(公式):検知サービスを有効にしても、担当・重要度のしきい値・是正の期限が決まっておらず、アラート疲れと古い未対 応が積み上がる。 出典:AWS Well-Architected Framework FND05(2026-11-16 版) 。筆者訳 docs.aws.amazon.com/wellarchitected/latest/framework/fnd05.html A-31 -
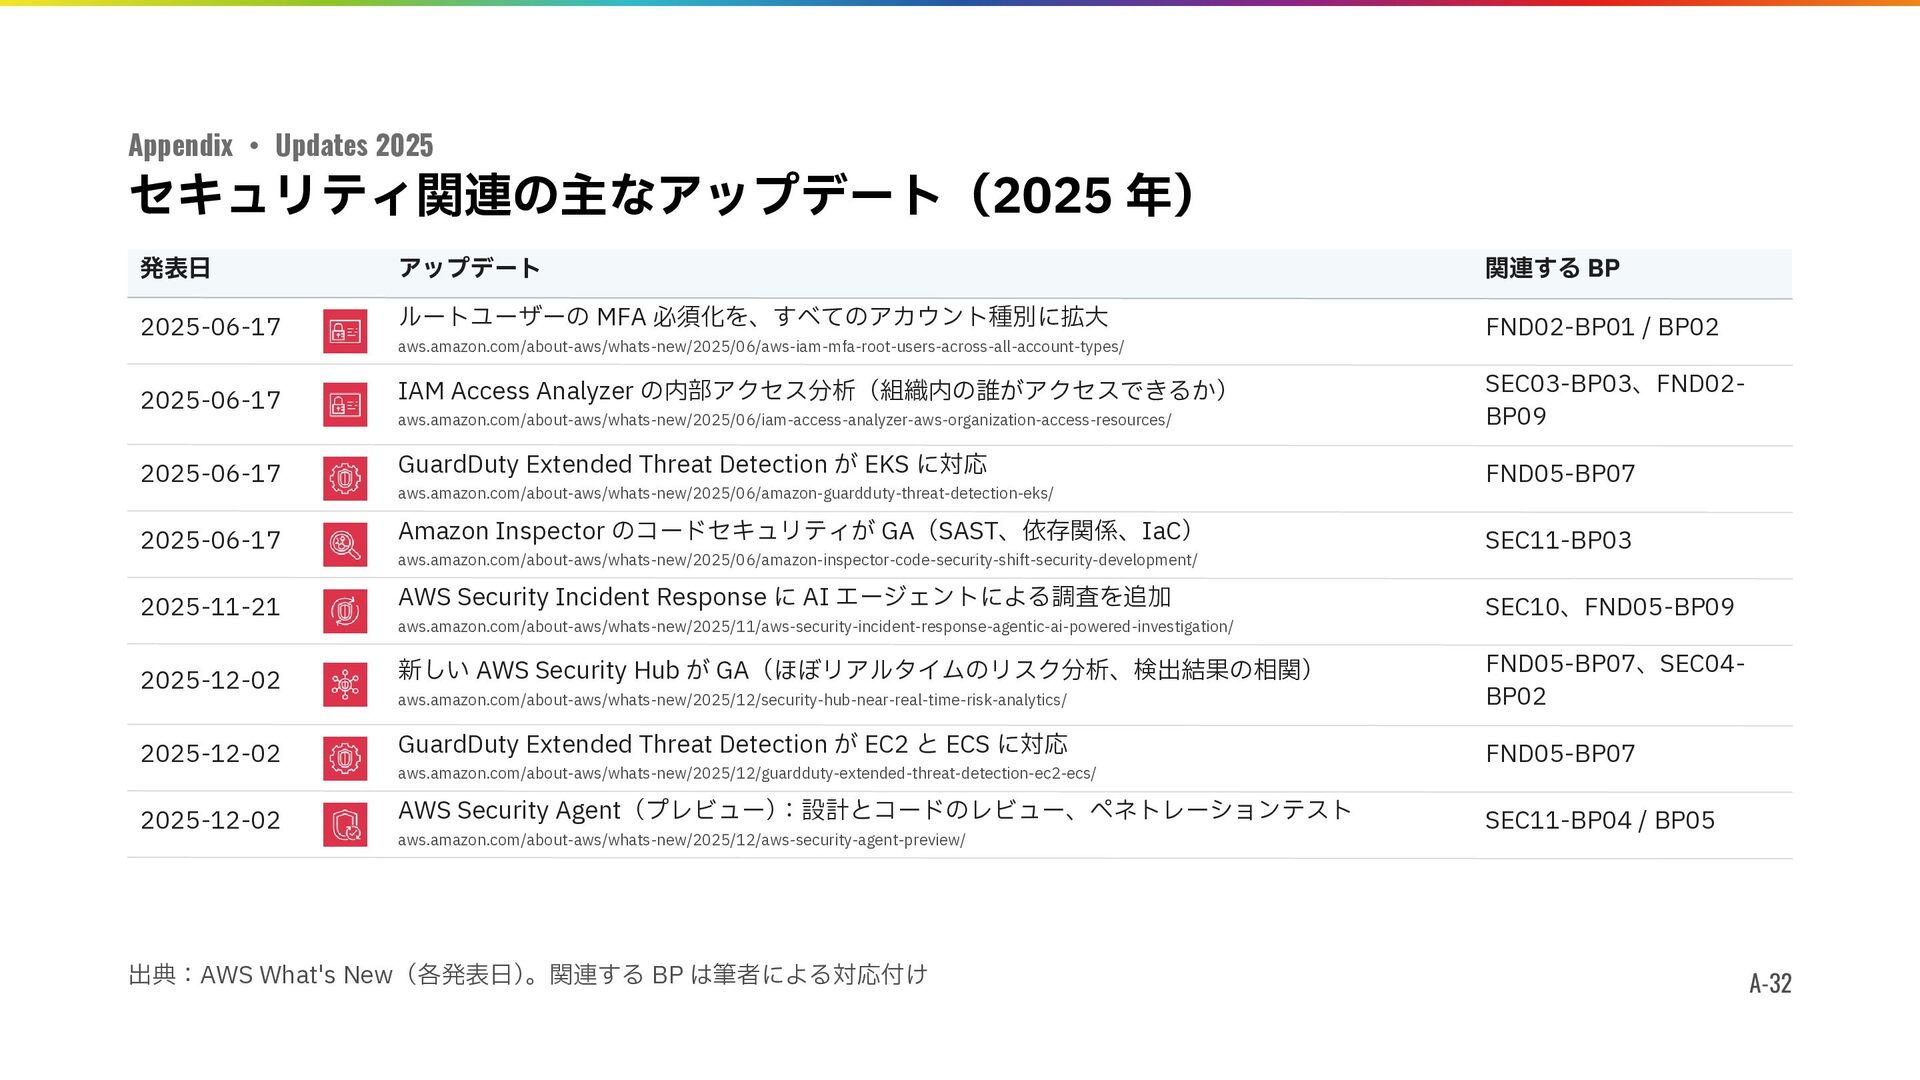
Appendix ・ Updates 2025 セキュリティ関連の主なアップデート(2025 年) 発表日 アップデート 関連する BP
2025-06-17 ルートユーザーの MFA 必須化を、すべてのアカウント種別に拡大 FND02-BP01 / BP02 2025-06-17 IAM Access Analyzer の内部アクセス分析(組織内の誰がアクセスできるか) SEC03-BP03、FND02BP09 2025-06-17 GuardDuty Extended Threat Detection が EKS に対応 FND05-BP07 2025-06-17 Amazon Inspector のコードセキュリティが GA(SAST、依存関係、IaC) SEC11-BP03 2025-11-21 AWS Security Incident Response に AI エージェントによる調査を追加 SEC10、FND05-BP09 2025-12-02 新しい AWS Security Hub が GA(ほぼリアルタイムのリスク分析、検出結果の相関) FND05-BP07、SEC04BP02 2025-12-02 GuardDuty Extended Threat Detection が EC2 と ECS に対応 FND05-BP07 2025-12-02 AWS Security Agent(プレビュー) :設計とコードのレビュー、ペネトレーションテスト SEC11-BP04 / BP05 aws.amazon.com/about-aws/whats-new/2025/06/aws-iam-mfa-root-users-across-all-account-types/ aws.amazon.com/about-aws/whats-new/2025/06/iam-access-analyzer-aws-organization-access-resources/ aws.amazon.com/about-aws/whats-new/2025/06/amazon-guardduty-threat-detection-eks/ aws.amazon.com/about-aws/whats-new/2025/06/amazon-inspector-code-security-shift-security-development/ aws.amazon.com/about-aws/whats-new/2025/11/aws-security-incident-response-agentic-ai-powered-investigation/ aws.amazon.com/about-aws/whats-new/2025/12/security-hub-near-real-time-risk-analytics/ aws.amazon.com/about-aws/whats-new/2025/12/guardduty-extended-threat-detection-ec2-ecs/ aws.amazon.com/about-aws/whats-new/2025/12/aws-security-agent-preview/ 出典:AWS What's New(各発表日) 。関連する BP は筆者による対応付け A-32 -
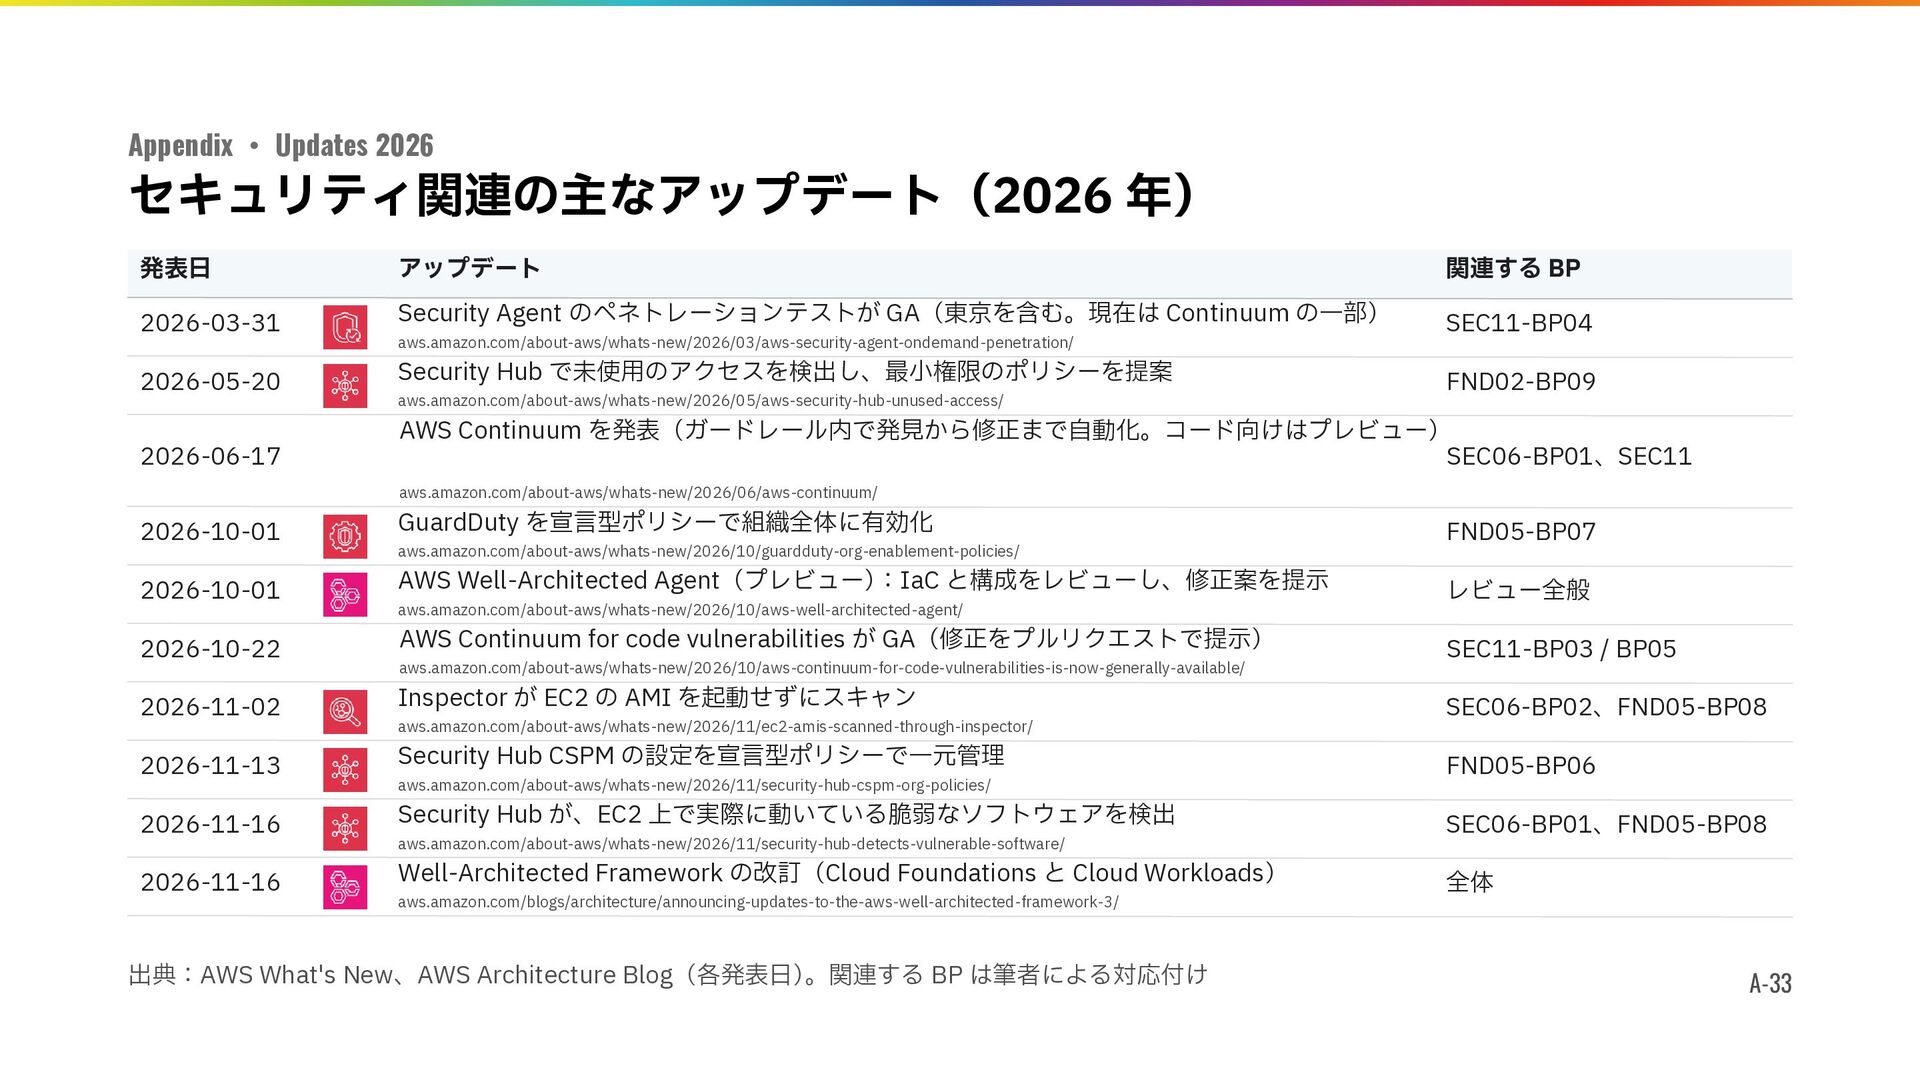
Appendix ・ Updates 2026 セキュリティ関連の主なアップデート(2026 年) 発表日 アップデート 関連する BP
2026-03-31 Security Agent のペネトレーションテストが GA(東京を含む。現在は Continuum の一部) SEC11-BP04 2026-05-20 Security Hub で未使用のアクセスを検出し、最小権限のポリシーを提案 FND02-BP09 2026-06-17 AWS Continuum を発表(ガードレール内で発見から修正まで自動化。コード向けはプレビュー) SEC06-BP01、SEC11 aws.amazon.com/about-aws/whats-new/2026/03/aws-security-agent-ondemand-penetration/ aws.amazon.com/about-aws/whats-new/2026/05/aws-security-hub-unused-access/ aws.amazon.com/about-aws/whats-new/2026/06/aws-continuum/ 2026-10-01 GuardDuty を宣言型ポリシーで組織全体に有効化 FND05-BP07 2026-10-01 AWS Well-Architected Agent(プレビュー) :IaC と構成をレビューし、修正案を提示 レビュー全般 2026-10-22 AWS Continuum for code vulnerabilities が GA(修正をプルリクエストで提示) SEC11-BP03 / BP05 2026-11-02 Inspector が EC2 の AMI を起動せずにスキャン SEC06-BP02、FND05-BP08 2026-11-13 Security Hub CSPM の設定を宣言型ポリシーで一元管理 FND05-BP06 2026-11-16 Security Hub が、EC2 上で実際に動いている脆弱なソフトウェアを検出 SEC06-BP01、FND05-BP08 2026-11-16 Well-Architected Framework の改訂(Cloud Foundations と Cloud Workloads) 全体 aws.amazon.com/about-aws/whats-new/2026/10/guardduty-org-enablement-policies/ aws.amazon.com/about-aws/whats-new/2026/10/aws-well-architected-agent/ aws.amazon.com/about-aws/whats-new/2026/10/aws-continuum-for-code-vulnerabilities-is-now-generally-available/ aws.amazon.com/about-aws/whats-new/2026/11/ec2-amis-scanned-through-inspector/ aws.amazon.com/about-aws/whats-new/2026/11/security-hub-cspm-org-policies/ aws.amazon.com/about-aws/whats-new/2026/11/security-hub-detects-vulnerable-software/ aws.amazon.com/blogs/architecture/announcing-updates-to-the-aws-well-architected-framework-3/ 出典:AWS What's New、AWS Architecture Blog(各発表日) 。関連する BP は筆者による対応付け A-33 -
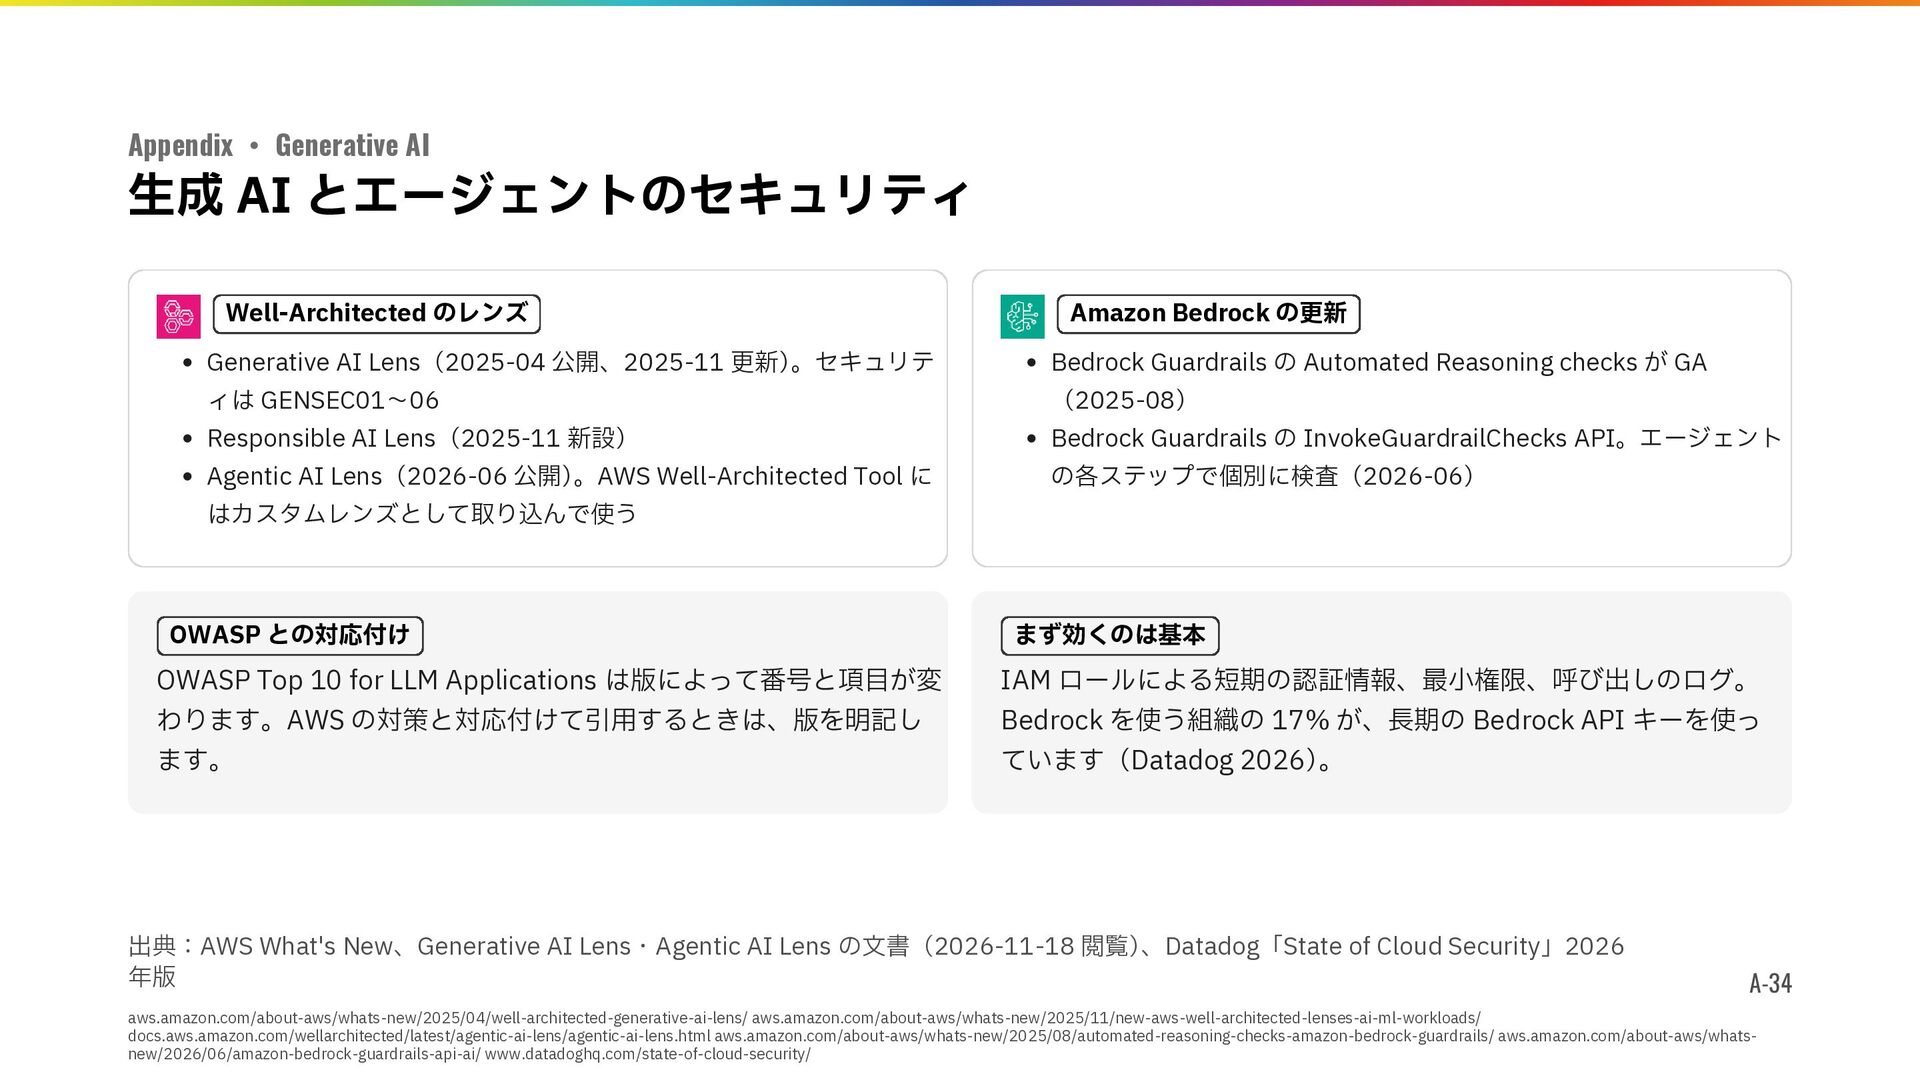
Appendix ・ Generative AI 生成 AI とエージェントのセキュリティ Well-Architected のレンズ Amazon
Bedrock の更新 Generative AI Lens(2025-04 公開、2025-11 更新) 。セキュリテ Bedrock Guardrails の Automated Reasoning checks が GA ィは GENSEC01〜06 (2025-08) Responsible AI Lens(2025-11 新設) Bedrock Guardrails の InvokeGuardrailChecks API。エージェント Agentic AI Lens(2026-06 公開) 。AWS Well-Architected Tool に の各ステップで個別に検査(2026-06) はカスタムレンズとして取り込んで使う OWASP との対応付け まず効くのは基本 OWASP Top 10 for LLM Applications は版によって番号と項目が変 IAM ロールによる短期の認証情報、最小権限、呼び出しのログ。 わります。AWS の対策と対応付けて引用するときは、版を明記し Bedrock を使う組織の 17% が、長期の Bedrock API キーを使っ ます。 ています(Datadog 2026)。 出典:AWS What's New、Generative AI Lens・Agentic AI Lens の文書(2026-11-18 閲覧) 、Datadog「State of Cloud Security」2026 年版 A-34 aws.amazon.com/about-aws/whats-new/2025/04/well-architected-generative-ai-lens/ aws.amazon.com/about-aws/whats-new/2025/11/new-aws-well-architected-lenses-ai-ml-workloads/ docs.aws.amazon.com/wellarchitected/latest/agentic-ai-lens/agentic-ai-lens.html aws.amazon.com/about-aws/whats-new/2025/08/automated-reasoning-checks-amazon-bedrock-guardrails/ aws.amazon.com/about-aws/whatsnew/2026/06/amazon-bedrock-guardrails-api-ai/ www.datadoghq.com/state-of-cloud-security/ -
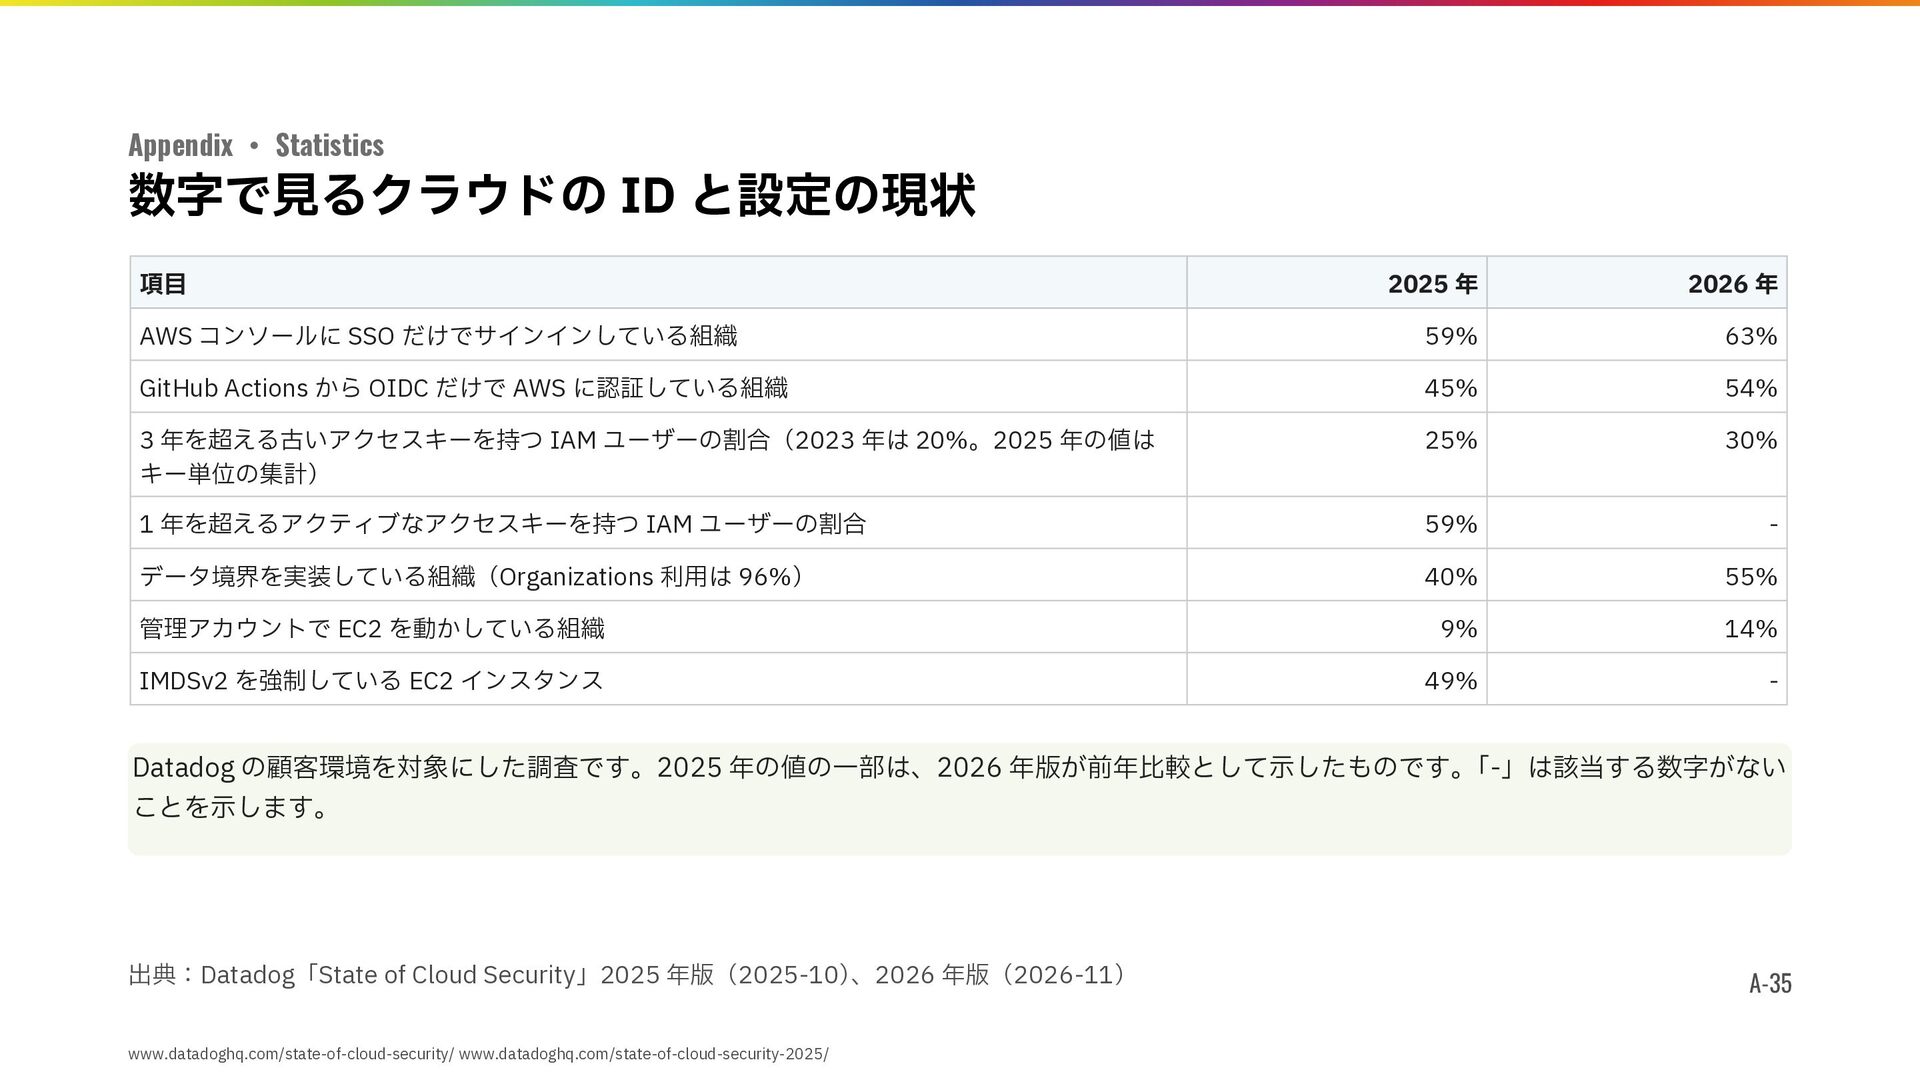
Appendix ・ Statistics 数字で見るクラウドの ID と設定の現状 項目 2025 年 2026
年 AWS コンソールに SSO だけでサインインしている組織 59% 63% GitHub Actions から OIDC だけで AWS に認証している組織 45% 54% 3 年を超える古いアクセスキーを持つ IAM ユーザーの割合(2023 年は 20%。2025 年の値は キー単位の集計) 25% 30% 1 年を超えるアクティブなアクセスキーを持つ IAM ユーザーの割合 59% - データ境界を実装している組織(Organizations 利用は 96%) 40% 55% 管理アカウントで EC2 を動かしている組織 9% 14% IMDSv2 を強制している EC2 インスタンス 49% - Datadog の顧客環境を対象にした調査です。2025 年の値の一部は、2026 年版が前年比較として示したものです。「-」は該当する数字がない ことを示します。 出典:Datadog「State of Cloud Security」2025 年版(2025-10) 、2026 年版(2026-11) www.datadoghq.com/state-of-cloud-security/ www.datadoghq.com/state-of-cloud-security-2025/ A-35 -
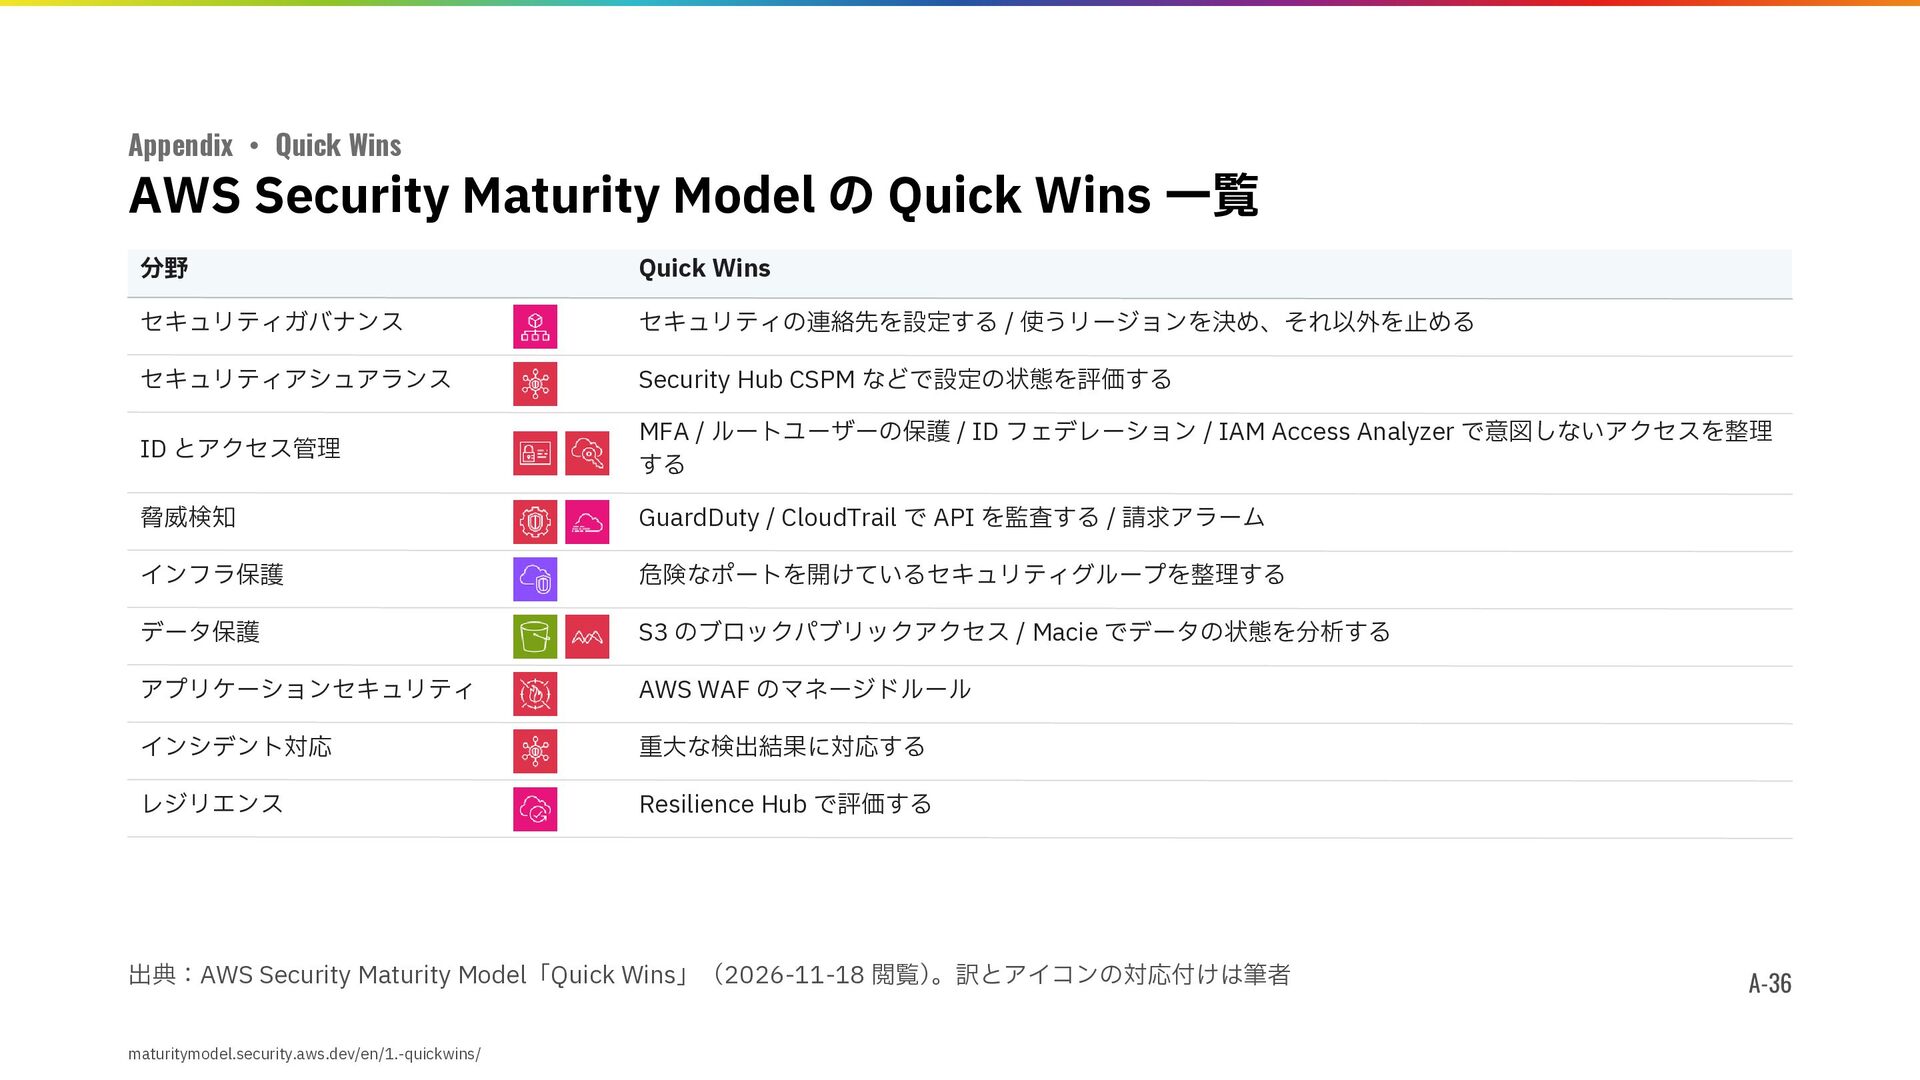
Appendix ・ Quick Wins AWS Security Maturity Model の Quick
Wins 一覧 分野 Quick Wins セキュリティガバナンス セキュリティの連絡先を設定する / 使うリージョンを決め、それ以外を止める セキュリティアシュアランス Security Hub CSPM などで設定の状態を評価する ID とアクセス管理 MFA / ルートユーザーの保護 / ID フェデレーション / IAM Access Analyzer で意図しないアクセスを整理 する 脅威検知 GuardDuty / CloudTrail で API を監査する / 請求アラーム インフラ保護 危険なポートを開けているセキュリティグループを整理する データ保護 S3 のブロックパブリックアクセス / Macie でデータの状態を分析する アプリケーションセキュリティ AWS WAF のマネージドルール インシデント対応 重大な検出結果に対応する レジリエンス Resilience Hub で評価する 出典:AWS Security Maturity Model「Quick Wins」(2026-11-18 閲覧) 。訳とアイコンの対応付けは筆者 maturitymodel.security.aws.dev/en/1.-quickwins/ A-36 -
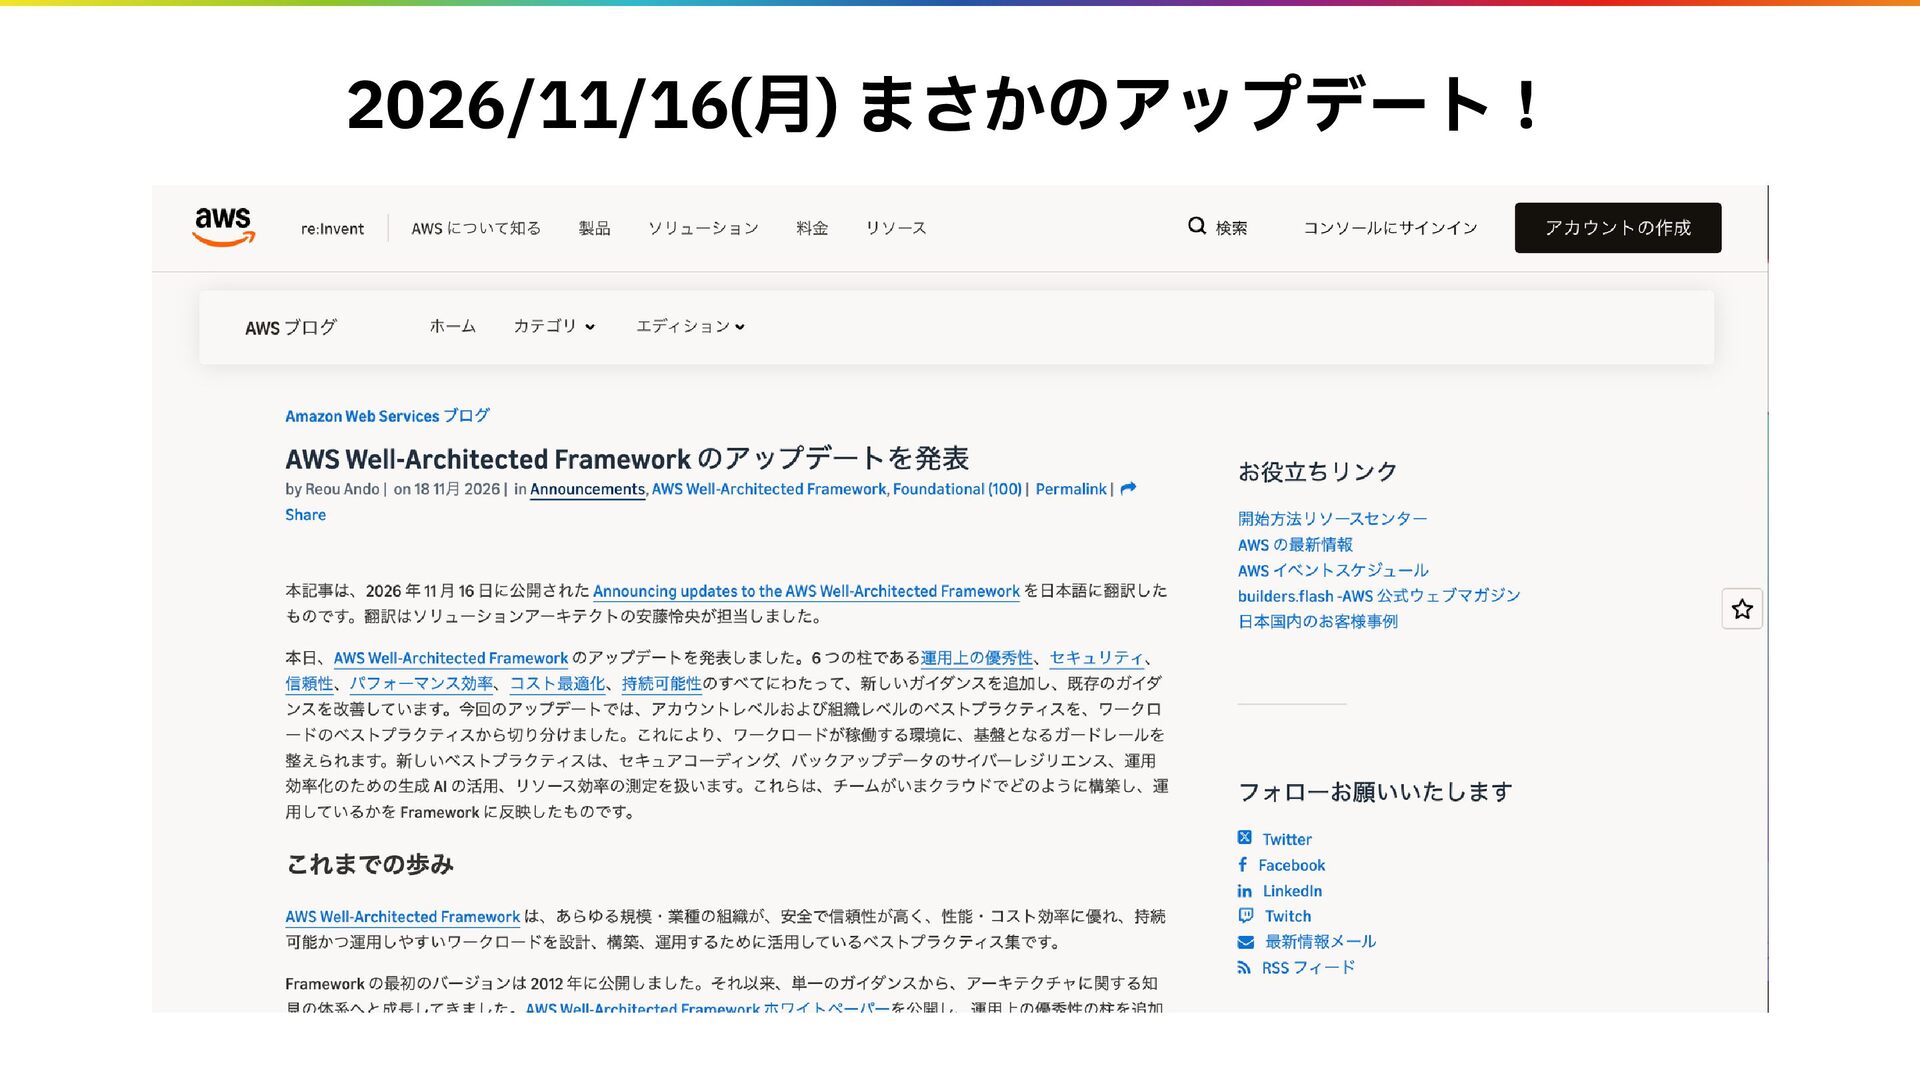
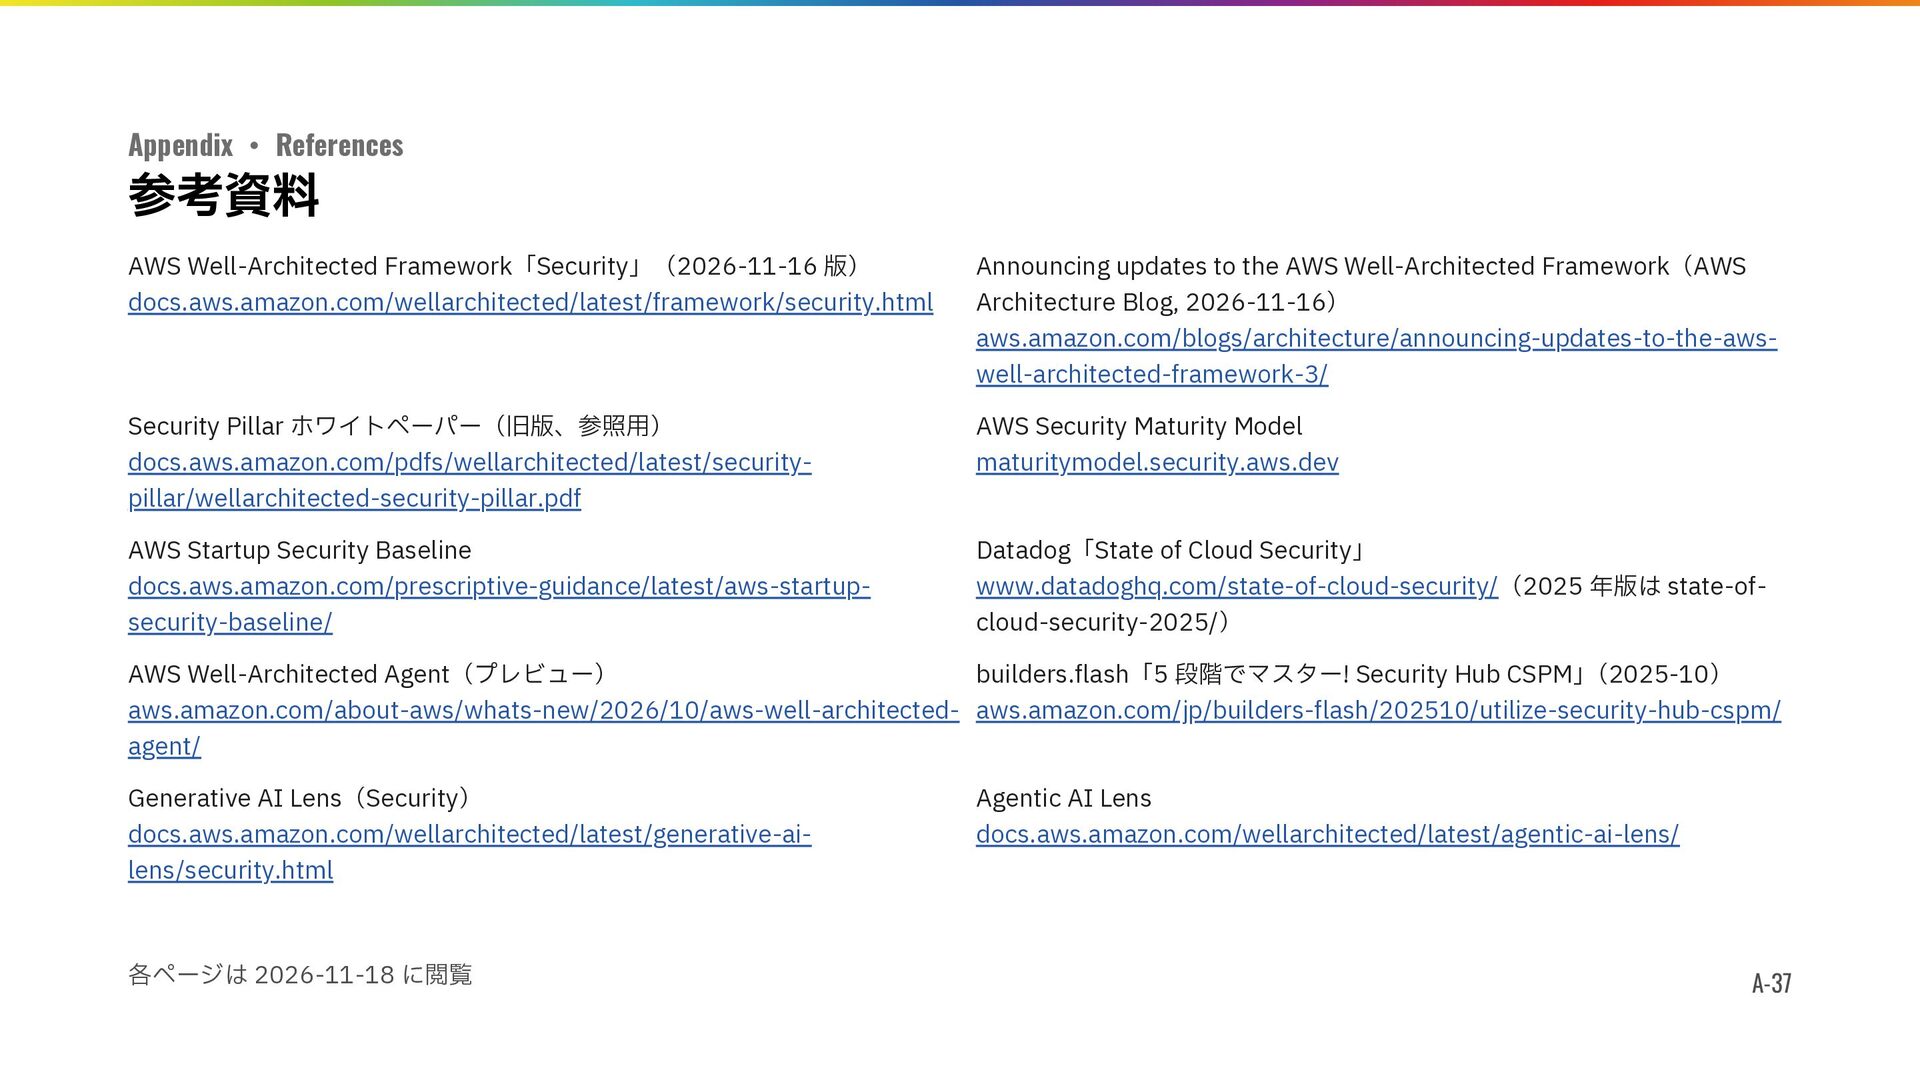
Appendix ・ References 参考資料 AWS Well-Architected Framework「Security」(2026-11-16 版) docs.aws.amazon.com/wellarchitected/latest/framework/security.html Announcing
updates to the AWS Well-Architected Framework(AWS Architecture Blog, 2026-11-16) aws.amazon.com/blogs/architecture/announcing-updates-to-the-awswell-architected-framework-3/ Security Pillar ホワイトペーパー(旧版、参照用) docs.aws.amazon.com/pdfs/wellarchitected/latest/securitypillar/wellarchitected-security-pillar.pdf AWS Security Maturity Model maturitymodel.security.aws.dev AWS Startup Security Baseline docs.aws.amazon.com/prescriptive-guidance/latest/aws-startupsecurity-baseline/ Datadog「State of Cloud Security」 www.datadoghq.com/state-of-cloud-security/(2025 年版は state-ofcloud-security-2025/) AWS Well-Architected Agent(プレビュー) builders.flash「5 段階でマスター! Security Hub CSPM」 (2025-10) Generative AI Lens(Security) Agentic AI Lens aws.amazon.com/about-aws/whats-new/2026/10/aws-well-architected- aws.amazon.com/jp/builders-flash/202510/utilize-security-hub-cspm/ agent/ docs.aws.amazon.com/wellarchitected/latest/generative-ailens/security.html 各ページは 2026-11-18 に閲覧 docs.aws.amazon.com/wellarchitected/latest/agentic-ai-lens/ A-37
 miu_crescent
 hagino3000
 ykimi
 maguroalternative
 fj_yoshimura_kosuke
 swdtkuy
 yuutosi
 amarelo_n24
 xkxaxkx
 say_no_w
 falken
 ivry_presentationmaterials
 munenick
 marktimemedia
 soudai
 csswizardry
 aleyda
 axbom
 mraible
 erikaheidi
 cassininazir
 tammyeverts
 kimpetersen
 eileencodes
 coloredviolet