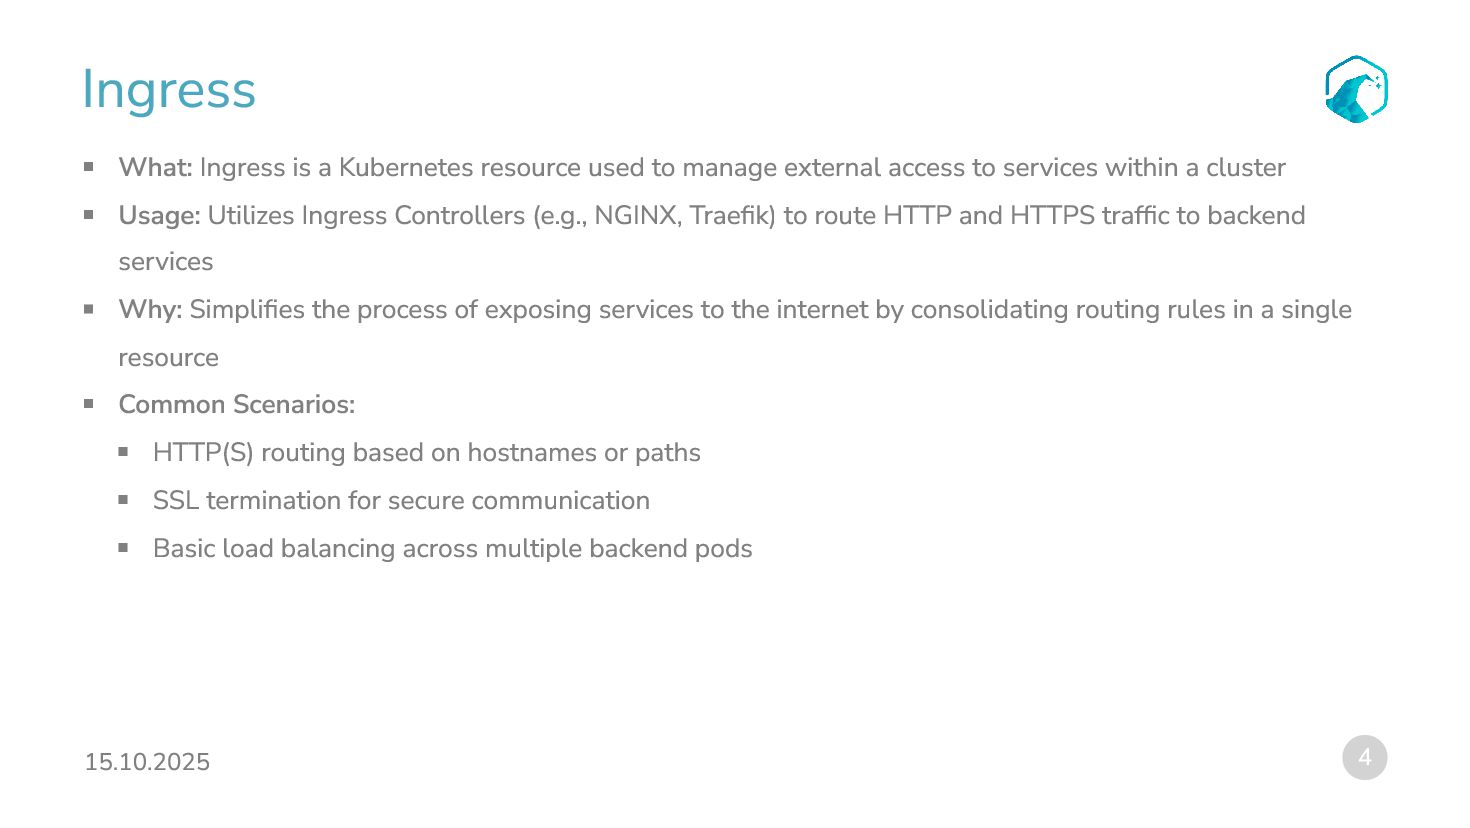
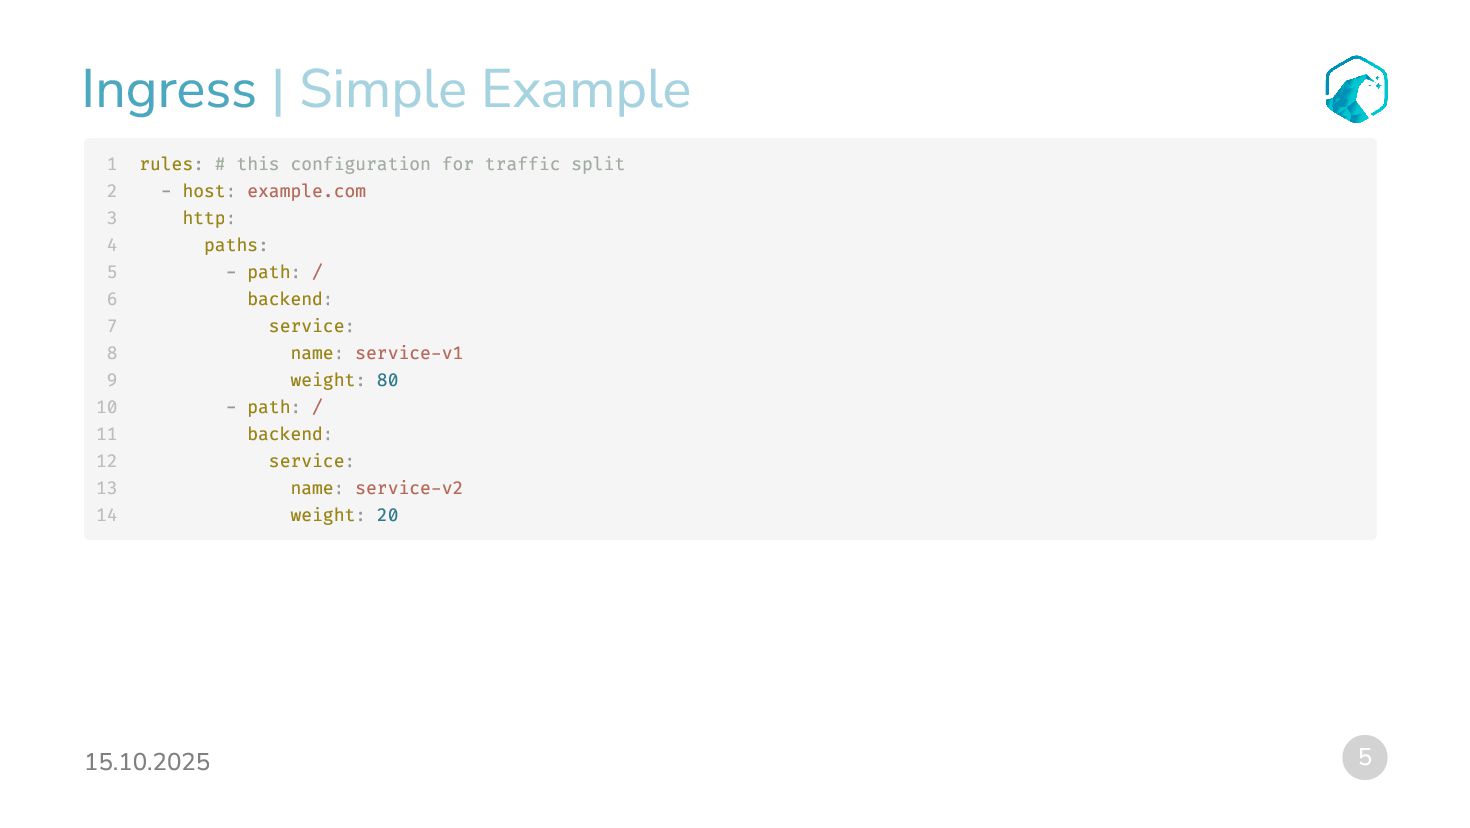
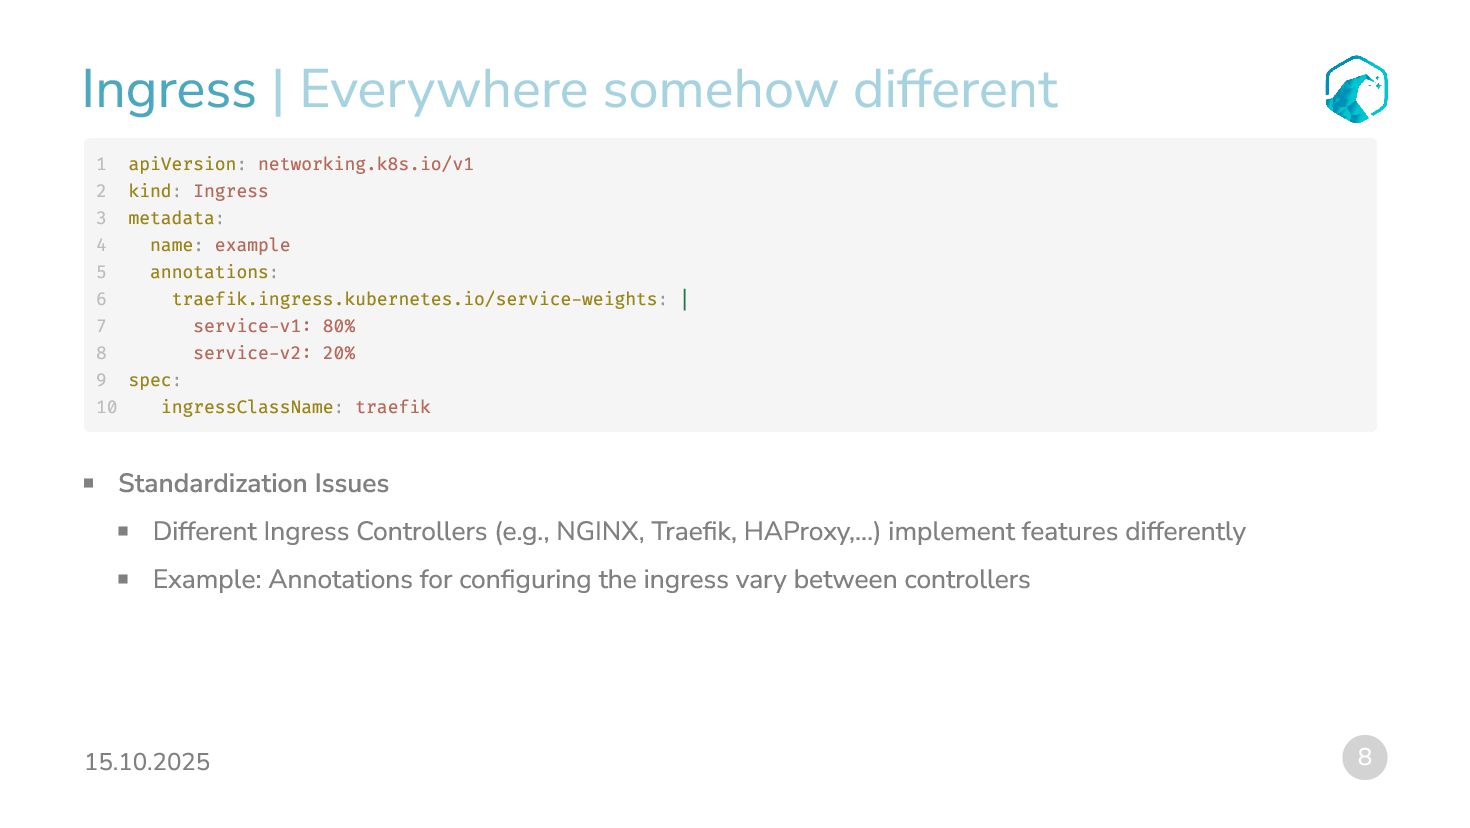
to manage external access to services within a cluster Usage: Utilizes Ingress Controllers (e.g., NGINX, Traefik) to route HTTP and HTTPS traffic to backend services Why: Simplifies the process of exposing services to the internet by consolidating routing rules in a single resource Common Scenarios: HTTP(S) routing based on hostnames or paths SSL termination for secure communication Basic load balancing across multiple backend pods
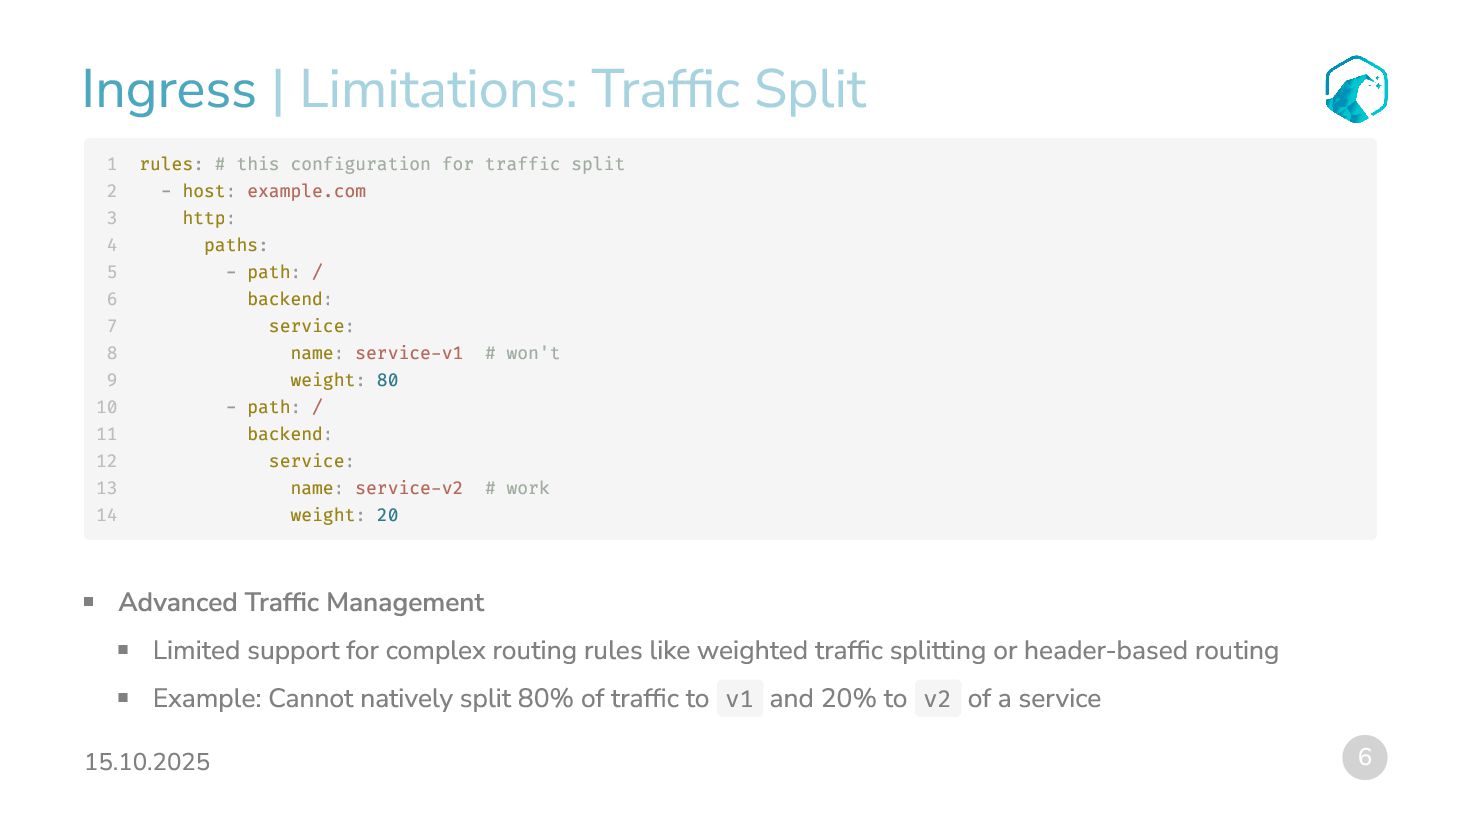
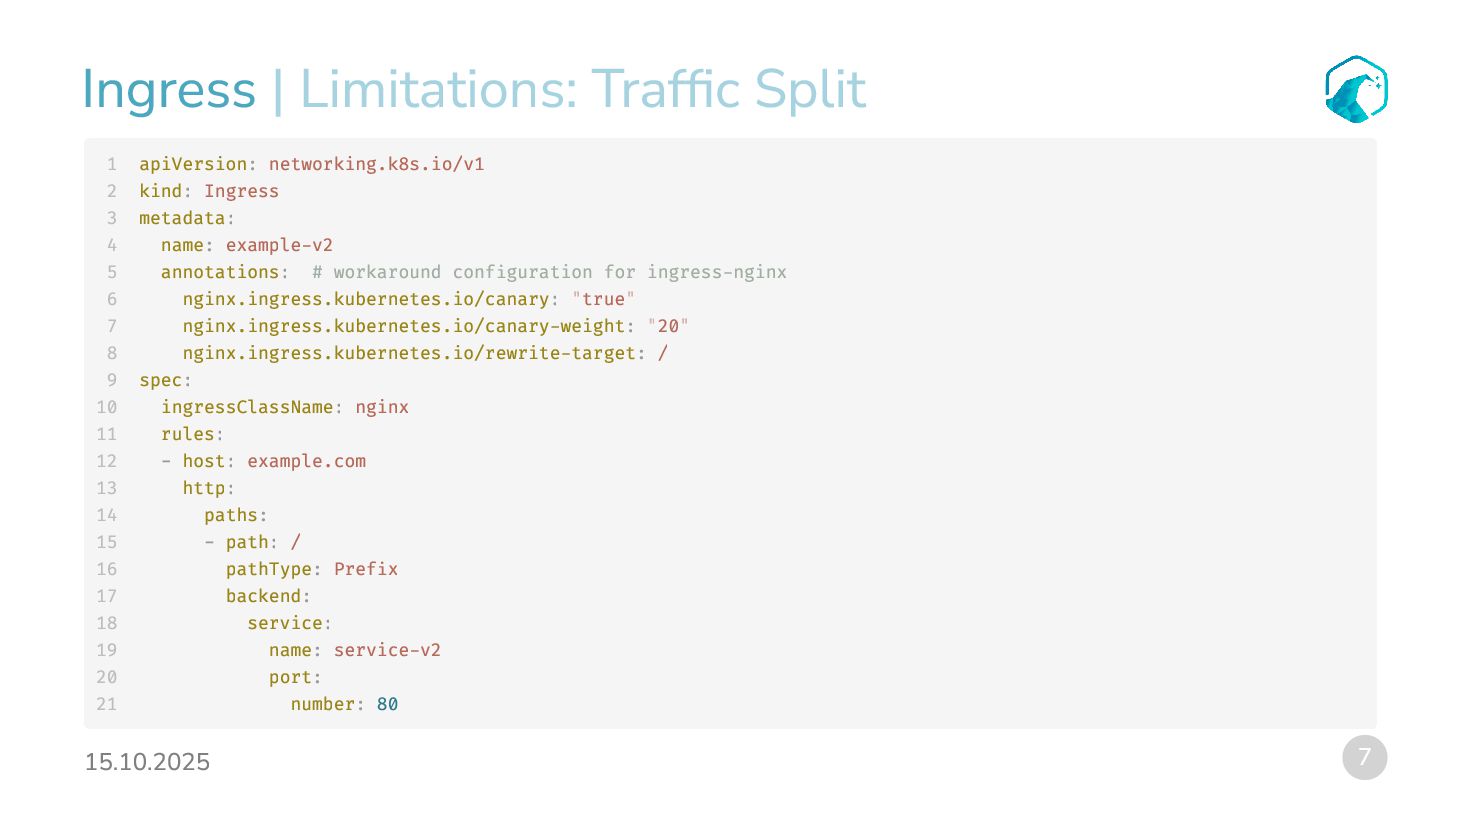
dynamic traffic patterns Example: Handling thousands of routes or services can lead to performance bottlenecks Security & Observability Lacks fine-grained security policies like per-route authentication or authorization Example: Cannot enforce mTLS or JWT validation directly in Ingress Limited observability tools for monitoring traffic metrics or debugging issues Extensibility Difficult to integrate new features or custom configurations Example: Adding support for advanced protocols like gRPC or WebSockets often requires workarounds | More Issues
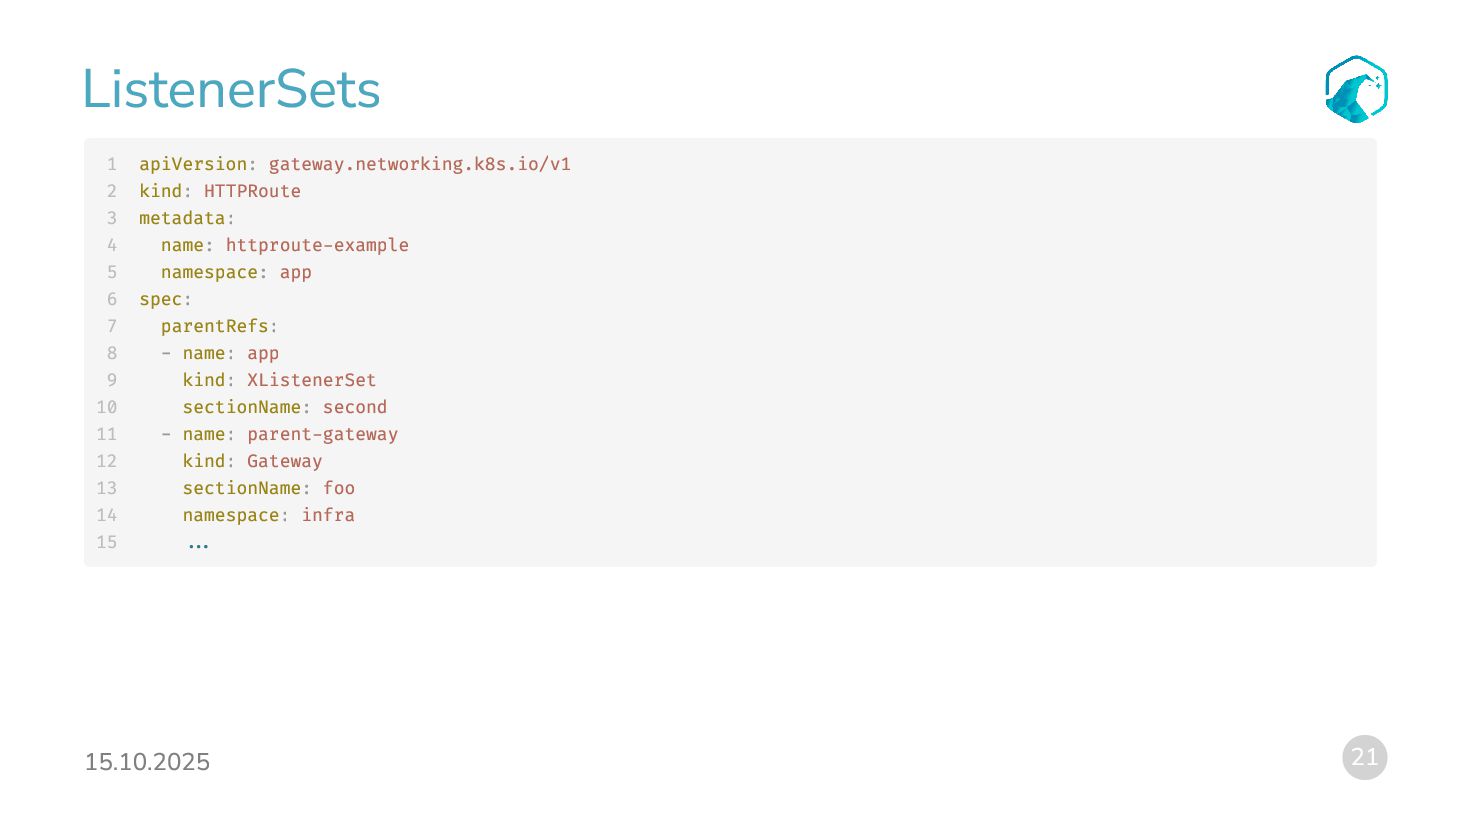
Kubernetes APIs designed to overcome Ingress limitations Improved Design: Offers a more flexible and expressive model for routing and traffic management Core Components: Gateway: Represents the actual load balancer or proxy Route: Defines how requests are routed to backend services Ecosystem: Built to work across different implementations with a standardized approach | What’s that?
and traffic policies Better Standardization: Uniform API across different vendors and implementations Scalability: Optimized to manage complex, large-scale environments Security & Observability: Improved mechanisms for enforcing security and monitoring traffic Future-Proofing: Designed to evolve with the growing needs of Kubernetes networking | Why use it?
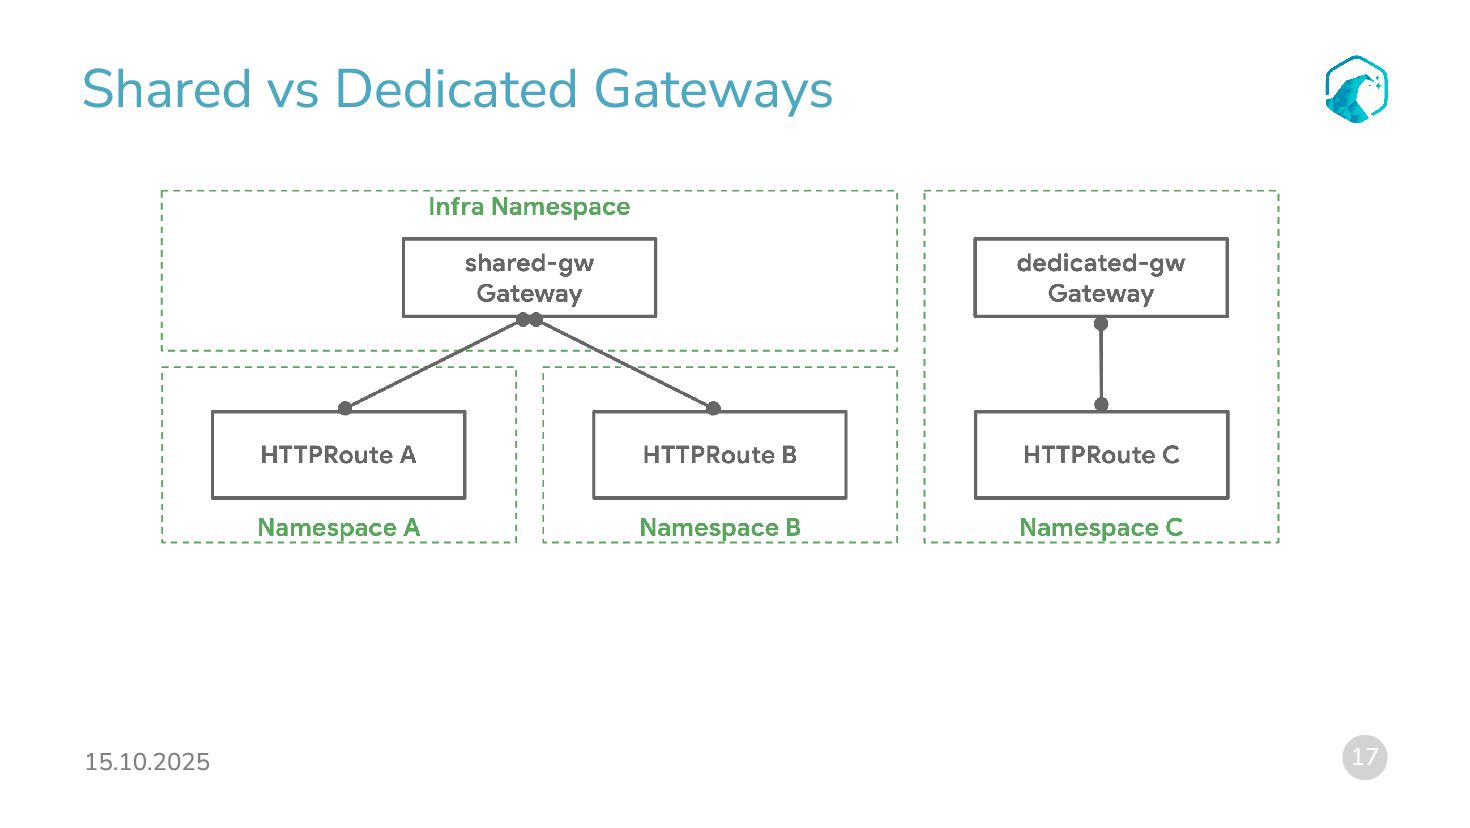
to configure how traffic is exposed. Both resources offer controls to restrict or allow attachments, supporting organizational policies. Attachment Models: One-to-one: Single owner for both Gateway and Route One-to-many: Gateway serves multiple Routes from different teams Many-to-one: Routes can also be bound to more than one Gateway, allowing a single Route to control application exposure simultaneously across different IPs, load balancers, or networks
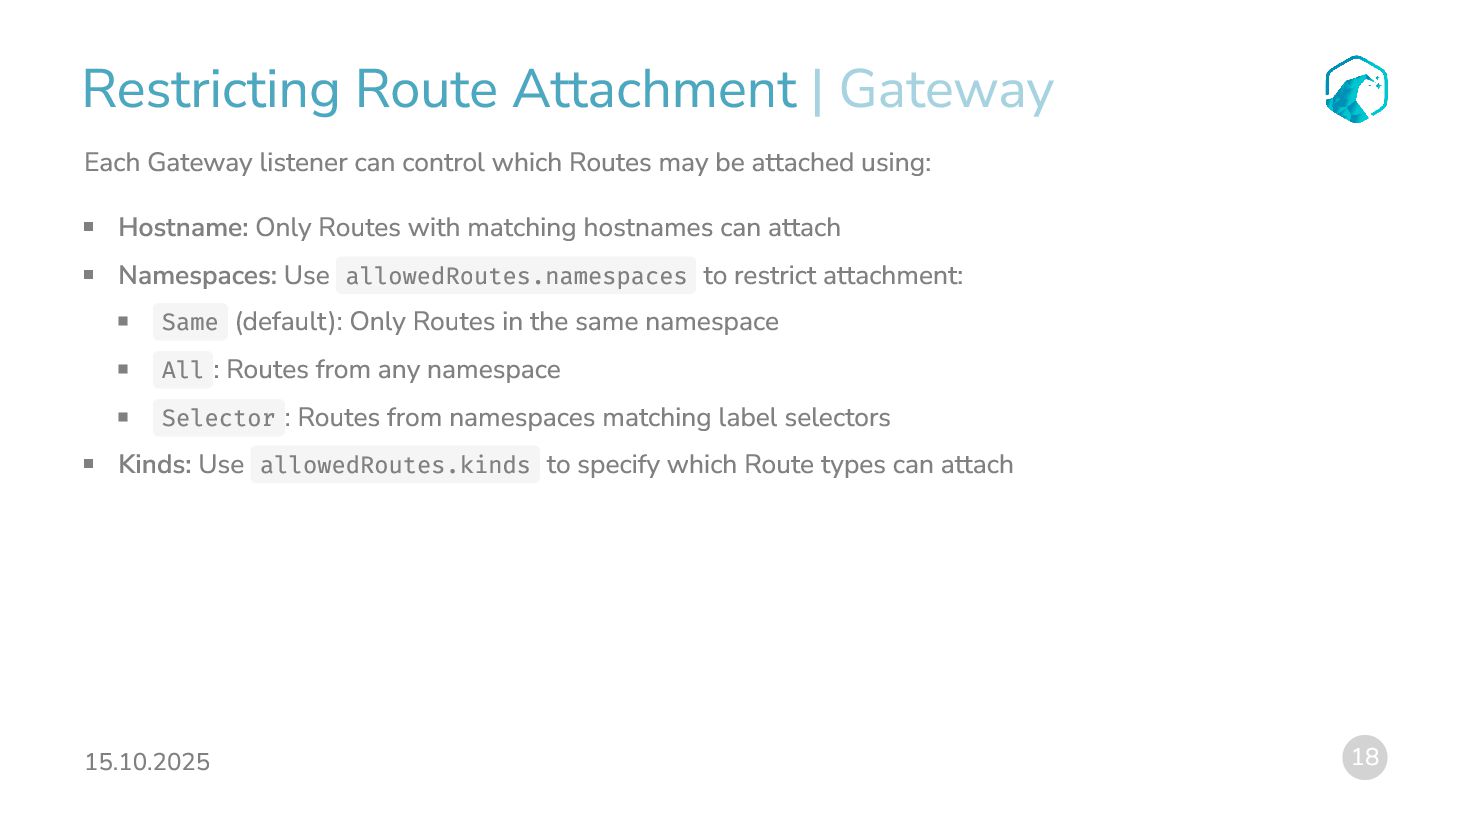
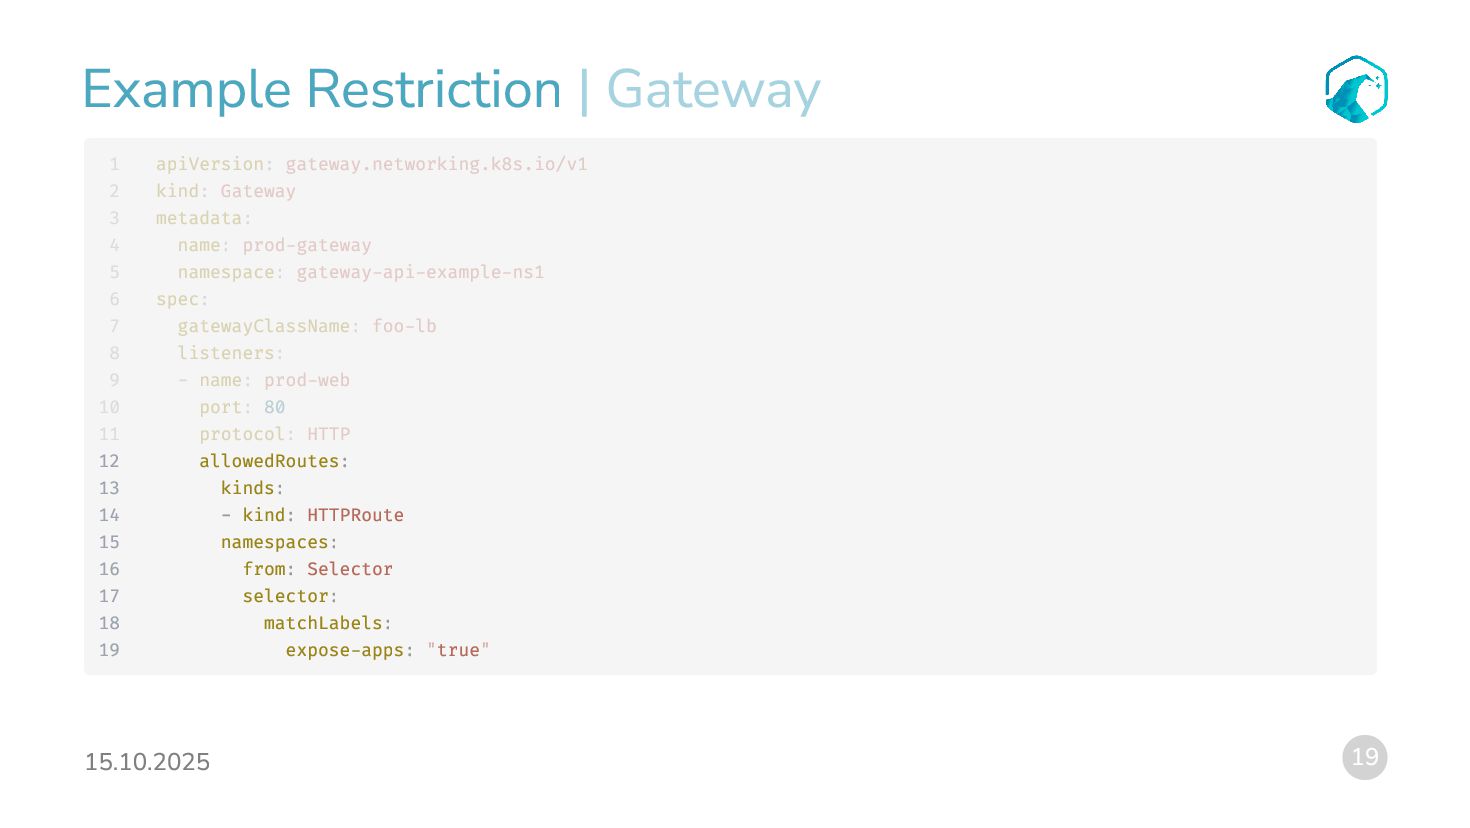
which Routes may be attached using: Hostname: Only Routes with matching hostnames can attach Namespaces: Use allowedRoutes.namespaces to restrict attachment: Same (default): Only Routes in the same namespace All : Routes from any namespace Selector : Routes from namespaces matching label selectors Kinds: Use allowedRoutes.kinds to specify which Route types can attach | Gateway
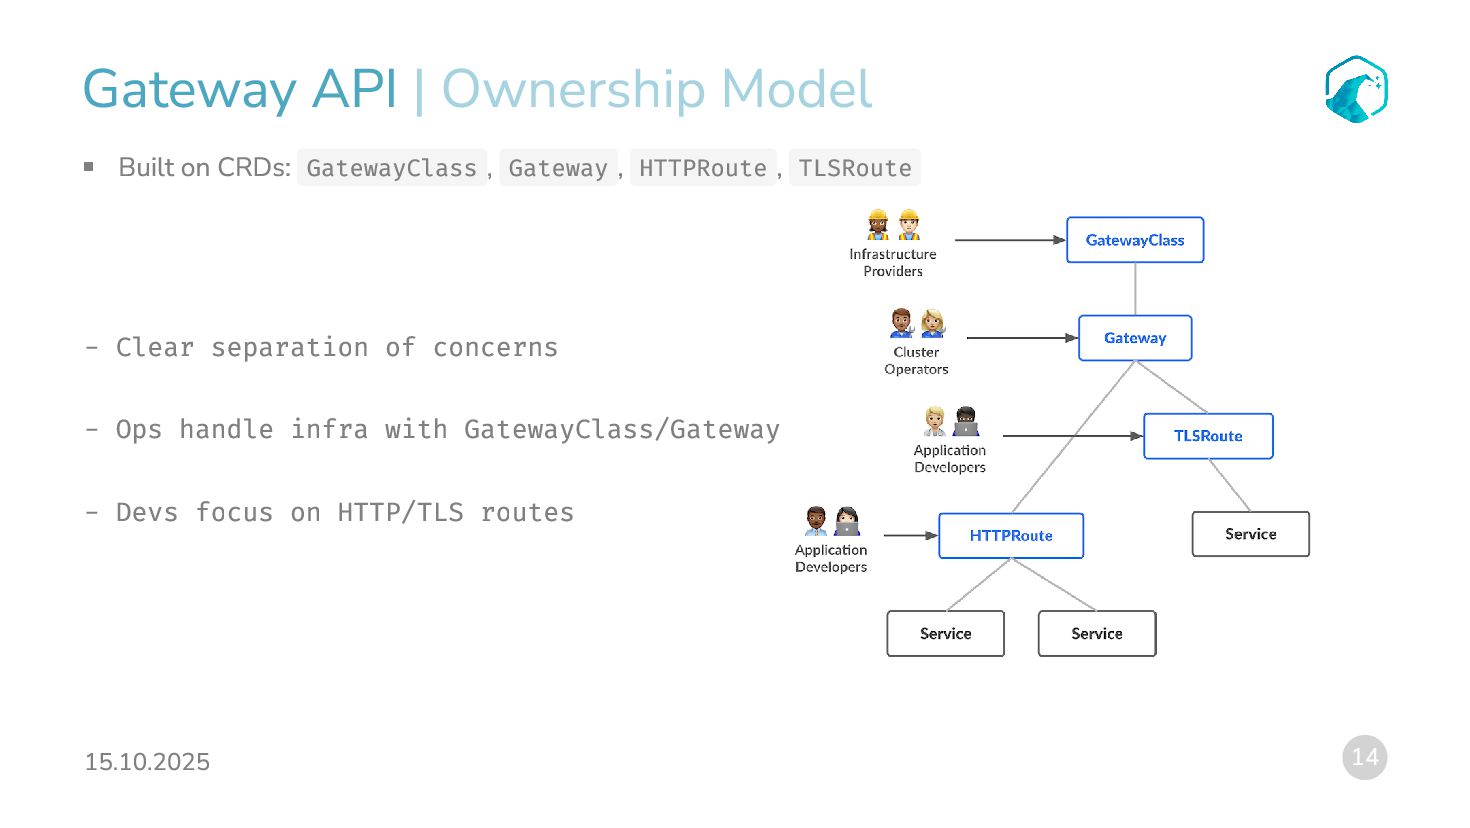
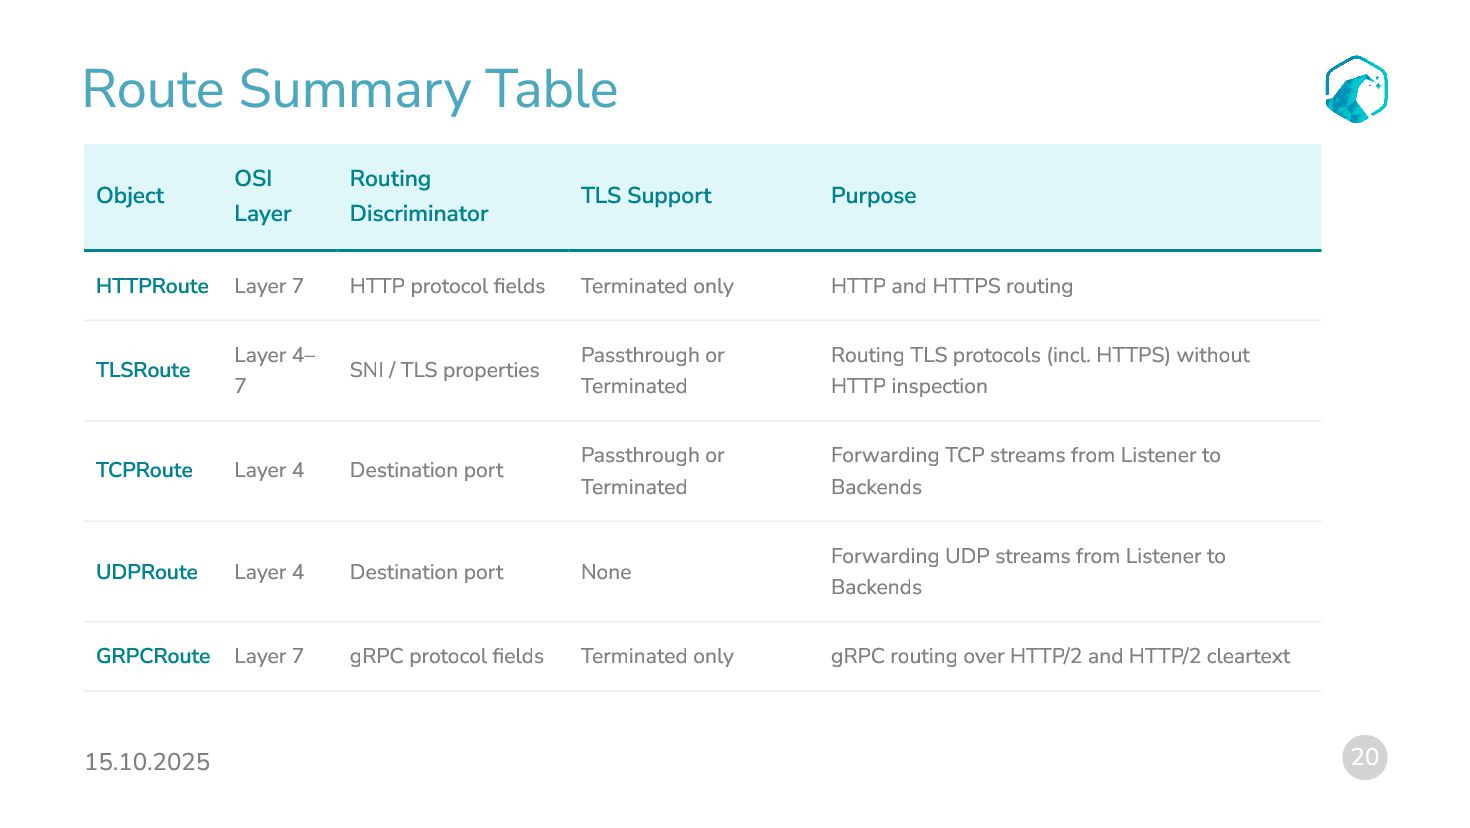
traffic management, standardization, scalability, security, and extensibility. Gateway API Evolution: Gateway API introduces a flexible, standardized, and scalable approach for Kubernetes traffic routing. Ownership Model: Separation of concerns between infrastructure, operations, and application development using CRDs ( GatewayClass , Gateway , HTTPRoute , TLSRoute ). Advanced Features: Fine-grained route attachment, listener sets, and support for multiple protocols (HTTP, TLS, TCP, UDP, gRPC). Why Gateway API: Enhanced flexibility, better security, improved observability, and future-proof networking for Kubernetes.

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 puhitaku
 4o1sobblue
 occhi
 willnet
 kaminashi
 yazm
 ezaki
 keeg
 greenmidori
 shogo4131
 persolserverworks
 satoshi7
 asonas
 addyosmani
 kneath
 inesmontani
 uxyall
 matthewcrist
 colly
 erikaheidi
 tanoku
 akademiya2063
 62gerente
 davetheseo