Share
Embed
Transcript
38 slides
-
Application Security at DevOps Speed and Portfolio Scale •
Dave Wichers" • OWASP Top 10 Project Lead" • OWASP Board Member (2004-2013)" • Cofounder, Aspect Security & Contrast Security, Maryland, U.S.A." -
• OWASP" – OWASP Top 10 Project Lead" – OWASP
Board Member 2004 thru 2013" – Conferences Chair for 2005 thru 2008" • Cofounder Aspect Security" – Application Security Consulting" • Cofounder Contrast Security" – IAST Vulnerability Detection Product" Dave Wichers" AppSec APAC 2014 -
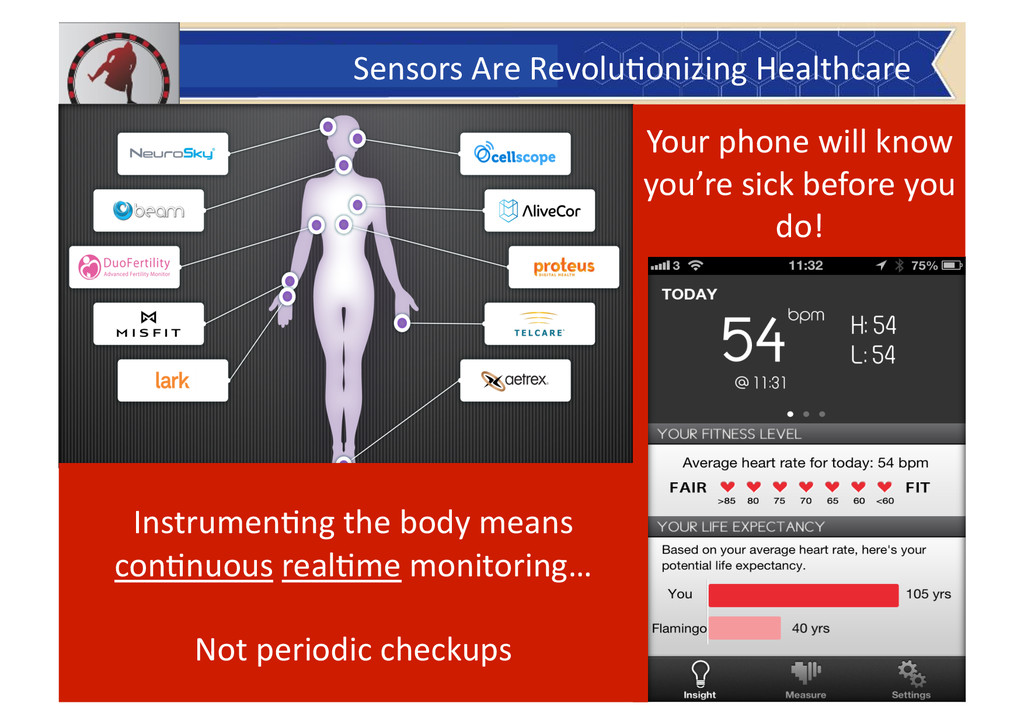
Sensors Are Revolu0onizing Healthcare Instrumen0ng the body means
con0nuous real0me monitoring… Not periodic checkups Your phone will know you’re sick before you do! -
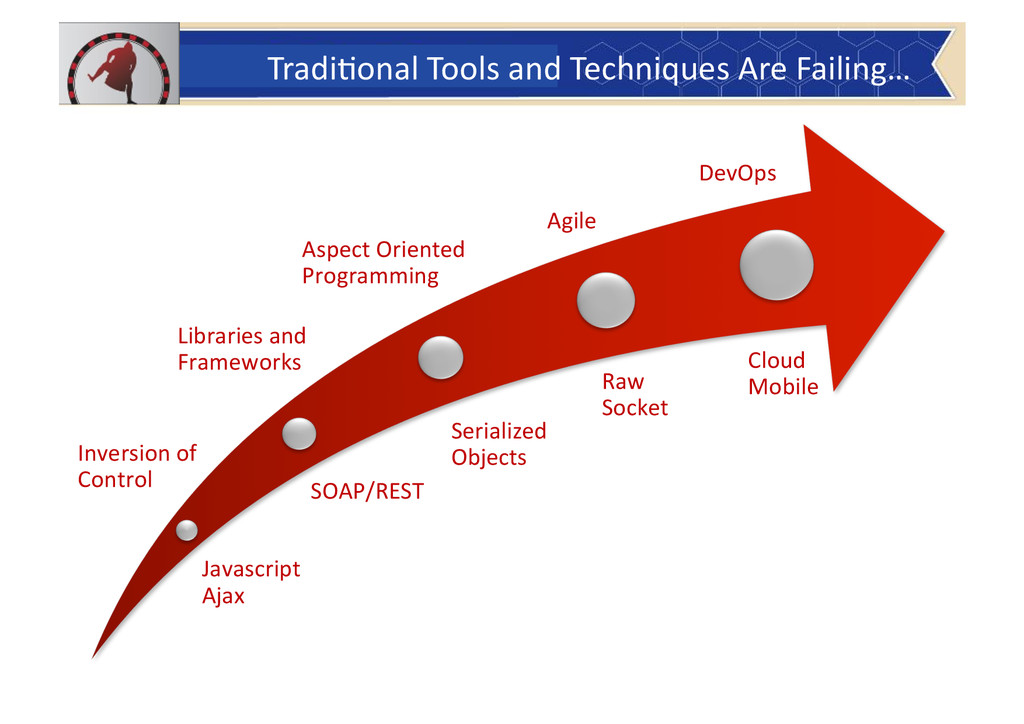
Tradi0onal Tools and Techniques Are Failing… Javascript Ajax
SOAP/REST Serialized Objects Raw Socket Inversion of Control Libraries and Frameworks Aspect Oriented Programming Agile DevOps Cloud Mobile -
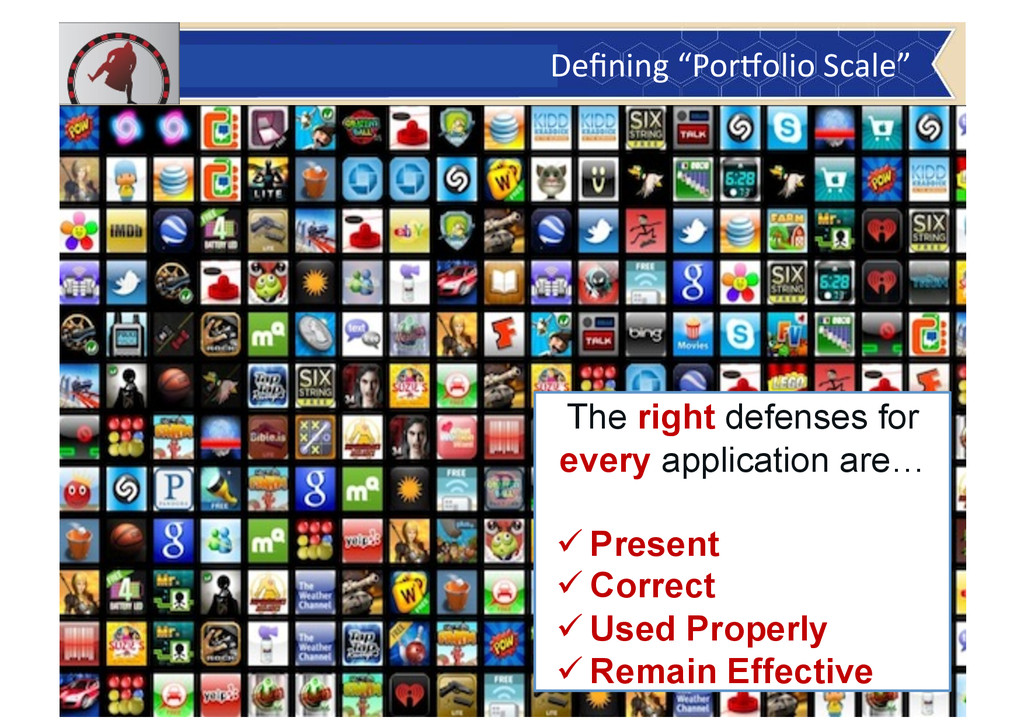
The right defenses for every application are… ! Present ! Correct ! Used
Properly ! Remain Effective Defining “PorXolio Scale” -
Is my por%olio protected against clickjacking? One
Thing at a Time… -
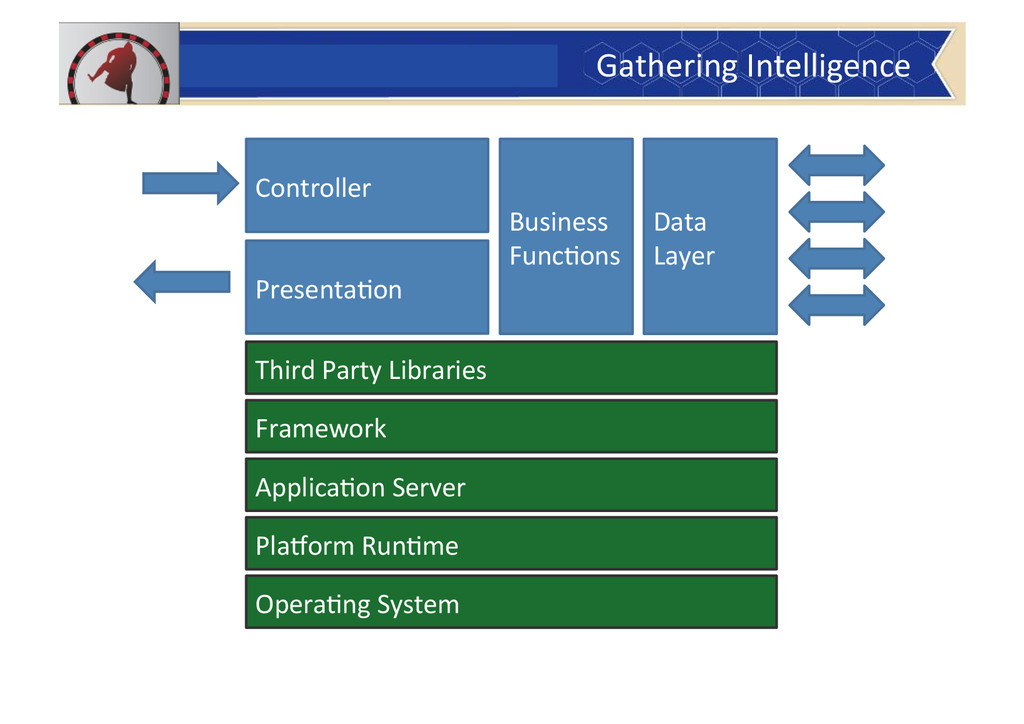
Gathering Intelligence Controller Presenta0on Business Func0ons
Data Layer Third Party Libraries Applica0on Server PlaXorm Run0me Framework Opera0ng System -
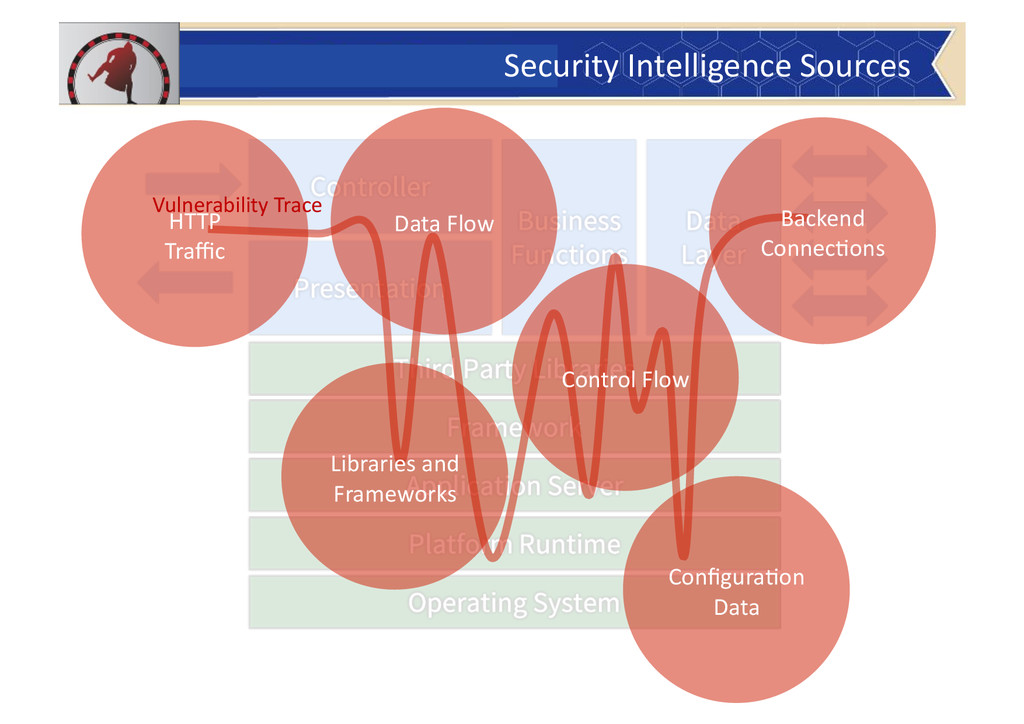
Security Intelligence Sources HTTP Traffic Backend
Connec0ons Configura0on Data Libraries and Frameworks Data Flow Control Flow Vulnerability Trace -
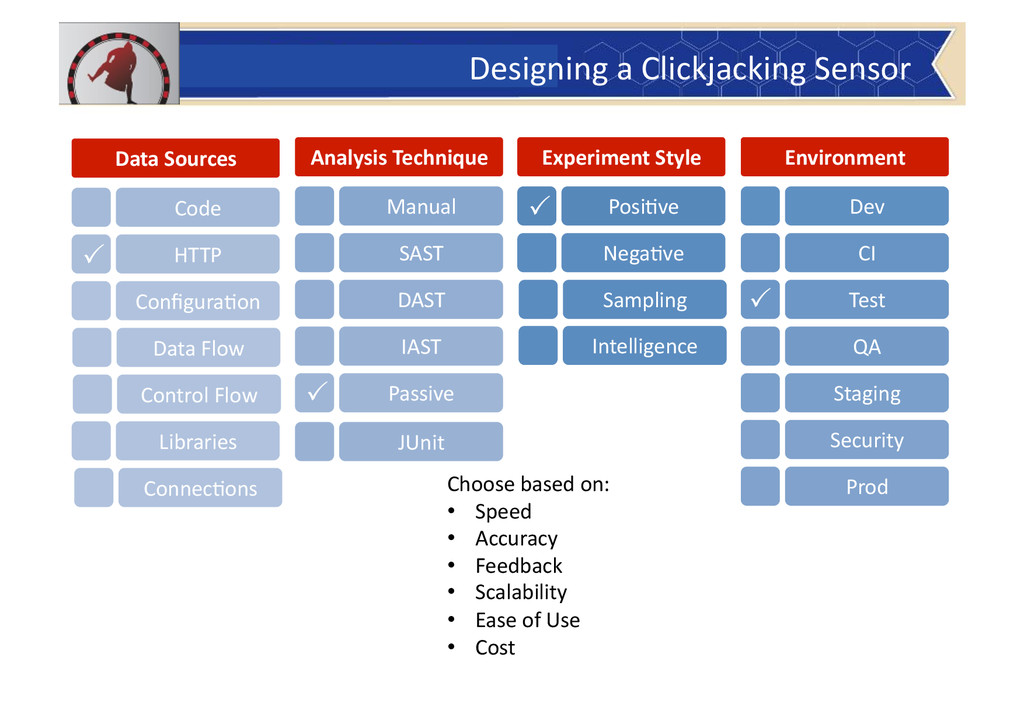
Designing a Clickjacking Sensor Experiment Style Posi0ve
Nega0ve Environment Dev CI Test QA Staging Security Analysis Technique Manual SAST DAST IAST Passive Data Sources Code HTTP Configura0on Choose based on: • Speed • Accuracy • Feedback • Scalability • Ease of Use • Cost ! ! ! ! Data Flow Control Flow Libraries Connec0ons Sampling Prod Intelligence JUnit -
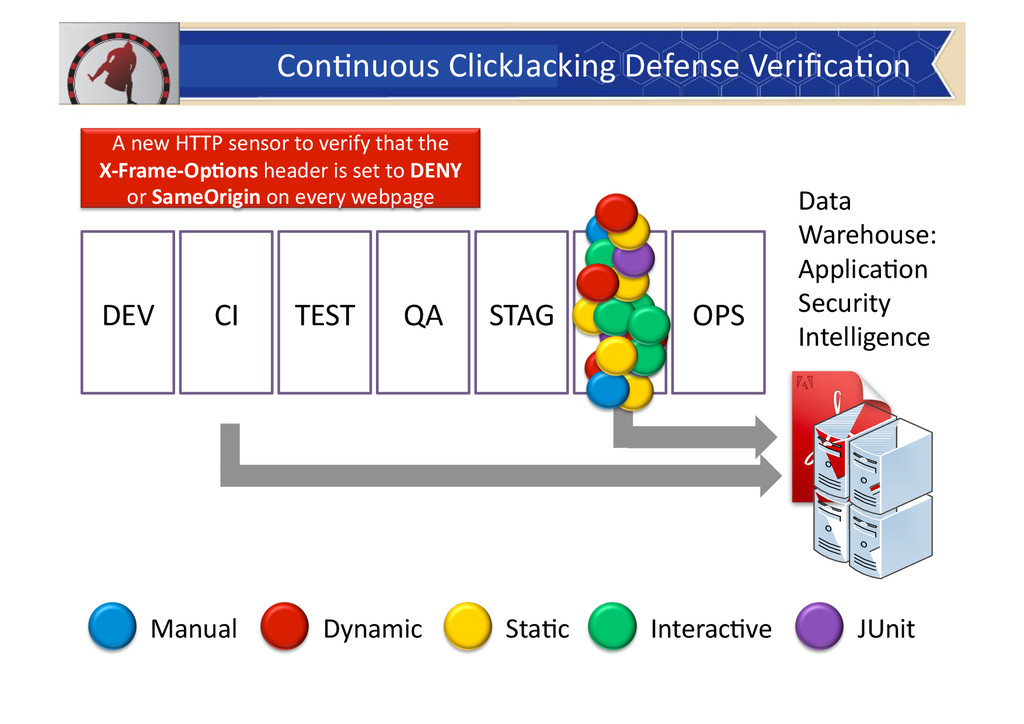
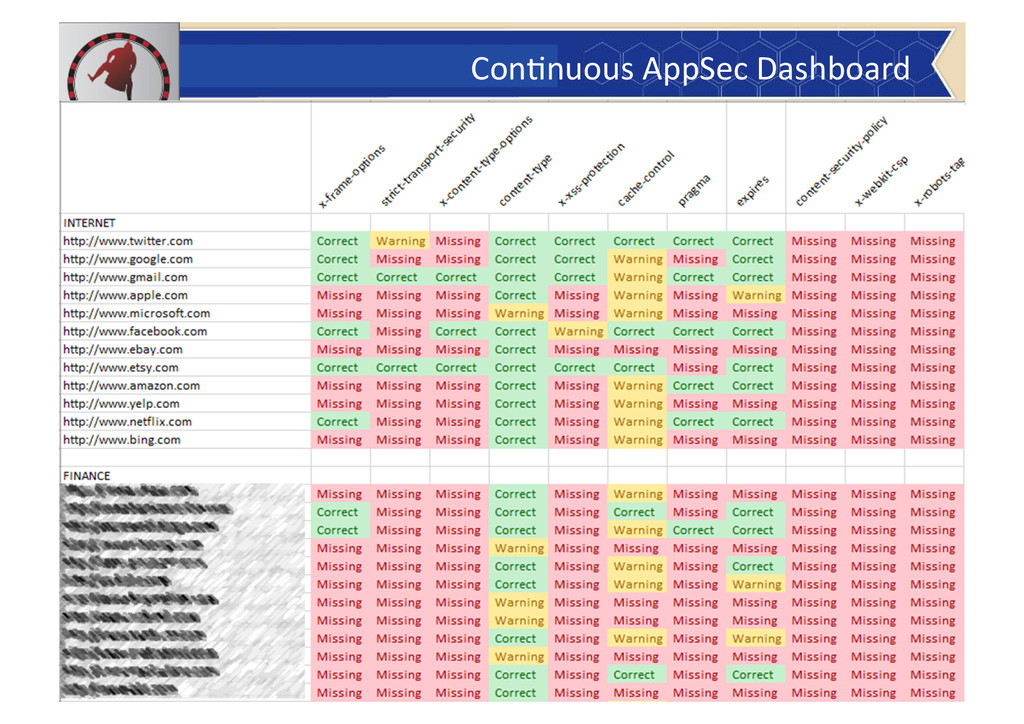
Con0nuous ClickJacking Defense Verifica0on A new HTTP sensor to
verify that the X-‐Frame-‐OpAons header is set to DENY or SameOrigin on every webpage Dynamic Interac0ve JUnit Manual Sta0c DEV CI TEST QA STAG OPS SEC Data Warehouse: Applica0on Security Intelligence -
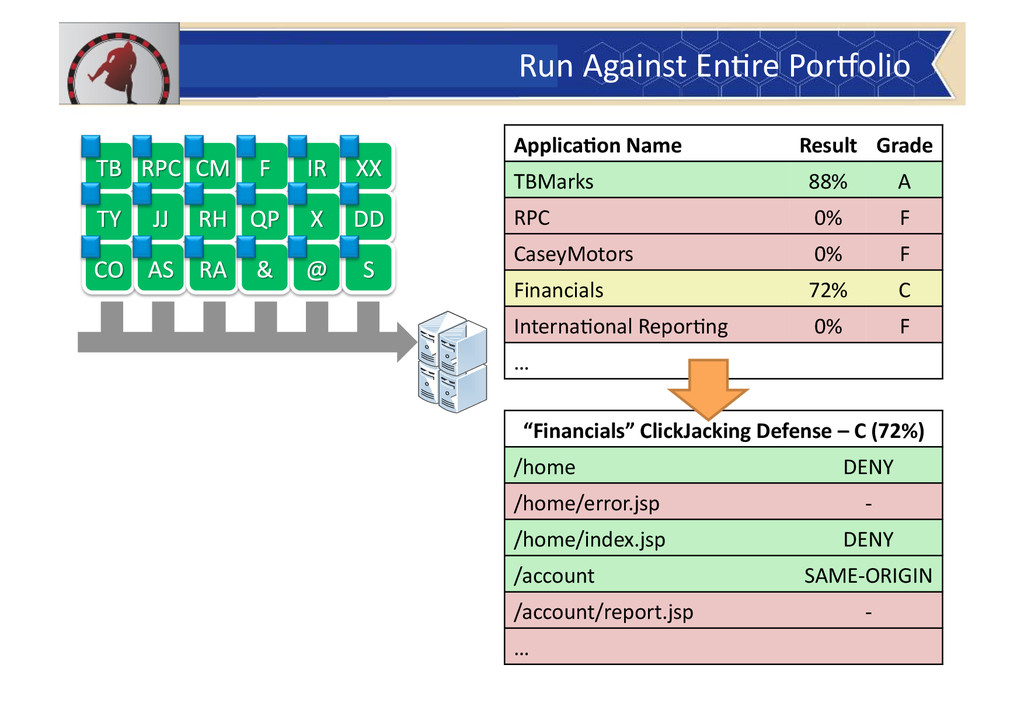
Run Against En0re PorXolio ApplicaAon Name Result
Grade TBMarks 88% A RPC 0% F CaseyMotors 0% F Financials 72% C Interna0onal Repor0ng 0% F … “Financials” ClickJacking Defense – C (72%) /home DENY /home/error.jsp -‐ /home/index.jsp DENY /account SAME-‐ORIGIN /account/report.jsp -‐ … -
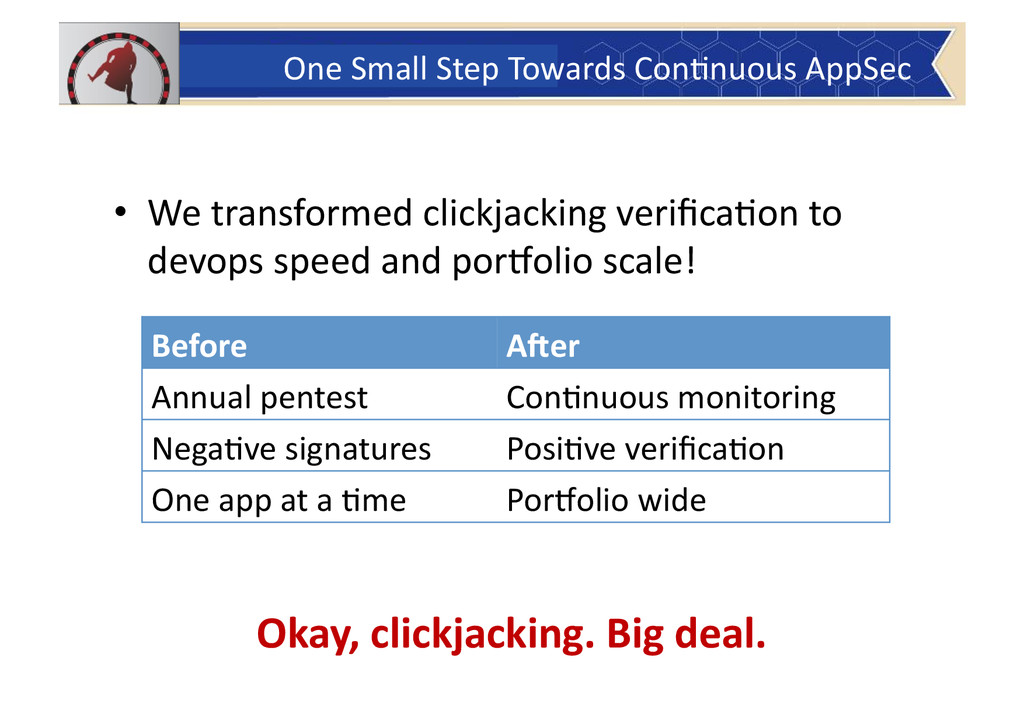
• We transformed clickjacking verifica0on to devops speed and
porXolio scale! One Small Step Towards Con0nuous AppSec Before ASer Annual pentest Con0nuous monitoring Nega0ve signatures Posi0ve verifica0on One app at a 0me PorXolio wide Okay, clickjacking. Big deal. -
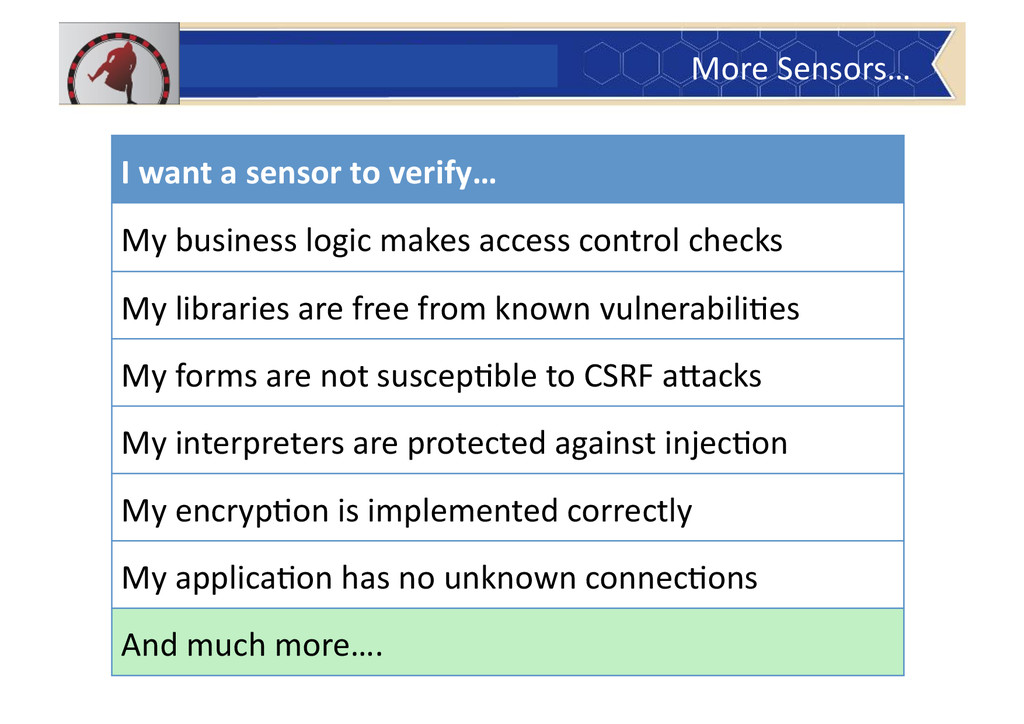
More Sensors… I want a sensor to verify…
My business logic makes access control checks My libraries are free from known vulnerabili0es My forms are not suscep0ble to CSRF ahacks My interpreters are protected against injec0on My encryp0on is implemented correctly My applica0on has no unknown connec0ons And much more…. -
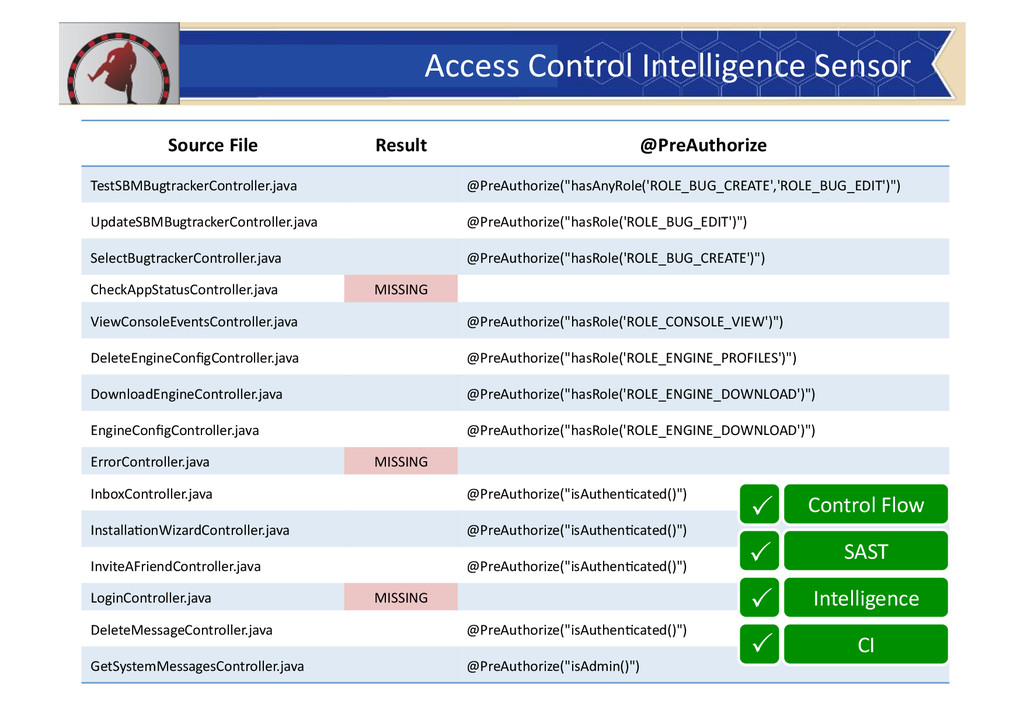
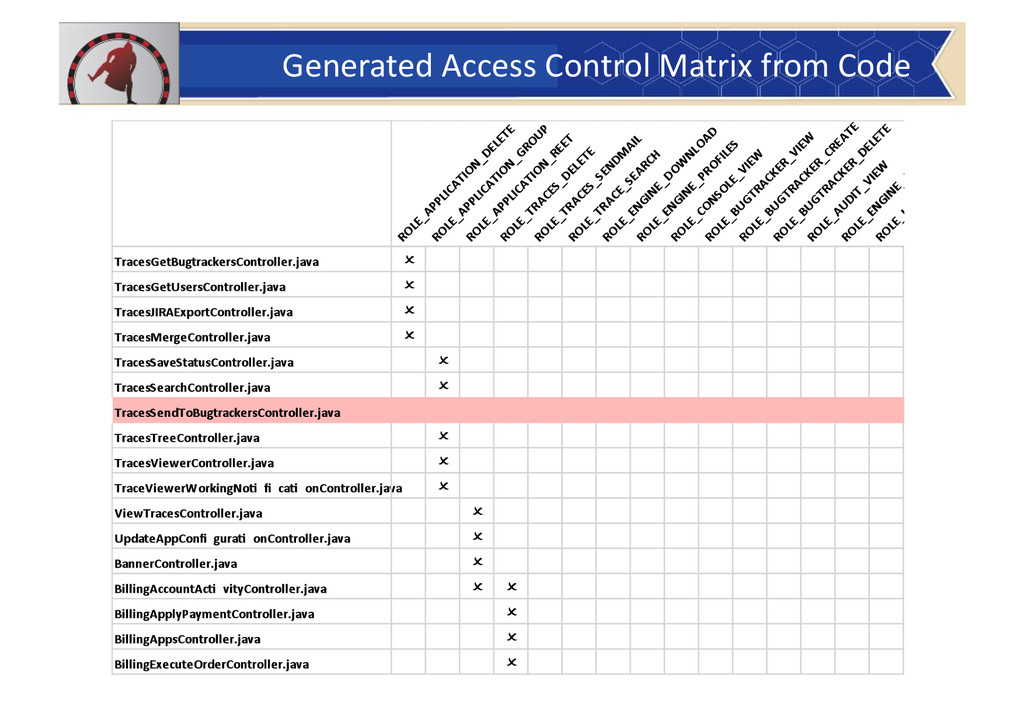
Source File Result @PreAuthorize TestSBMBugtrackerController.java @PreAuthorize("hasAnyRole('ROLE_BUG_CREATE','ROLE_BUG_EDIT')")
UpdateSBMBugtrackerController.java @PreAuthorize("hasRole('ROLE_BUG_EDIT')") SelectBugtrackerController.java @PreAuthorize("hasRole('ROLE_BUG_CREATE')") CheckAppStatusController.java MISSING ViewConsoleEventsController.java @PreAuthorize("hasRole('ROLE_CONSOLE_VIEW')") DeleteEngineConfigController.java @PreAuthorize("hasRole('ROLE_ENGINE_PROFILES')") DownloadEngineController.java @PreAuthorize("hasRole('ROLE_ENGINE_DOWNLOAD')") EngineConfigController.java @PreAuthorize("hasRole('ROLE_ENGINE_DOWNLOAD')") ErrorController.java MISSING InboxController.java @PreAuthorize("isAuthen0cated()") Installa0onWizardController.java @PreAuthorize("isAuthen0cated()") InviteAFriendController.java @PreAuthorize("isAuthen0cated()") LoginController.java MISSING DeleteMessageController.java @PreAuthorize("isAuthen0cated()") GetSystemMessagesController.java @PreAuthorize("isAdmin()") Access Control Intelligence Sensor Control Flow SAST Intelligence CI ! ! ! ! -
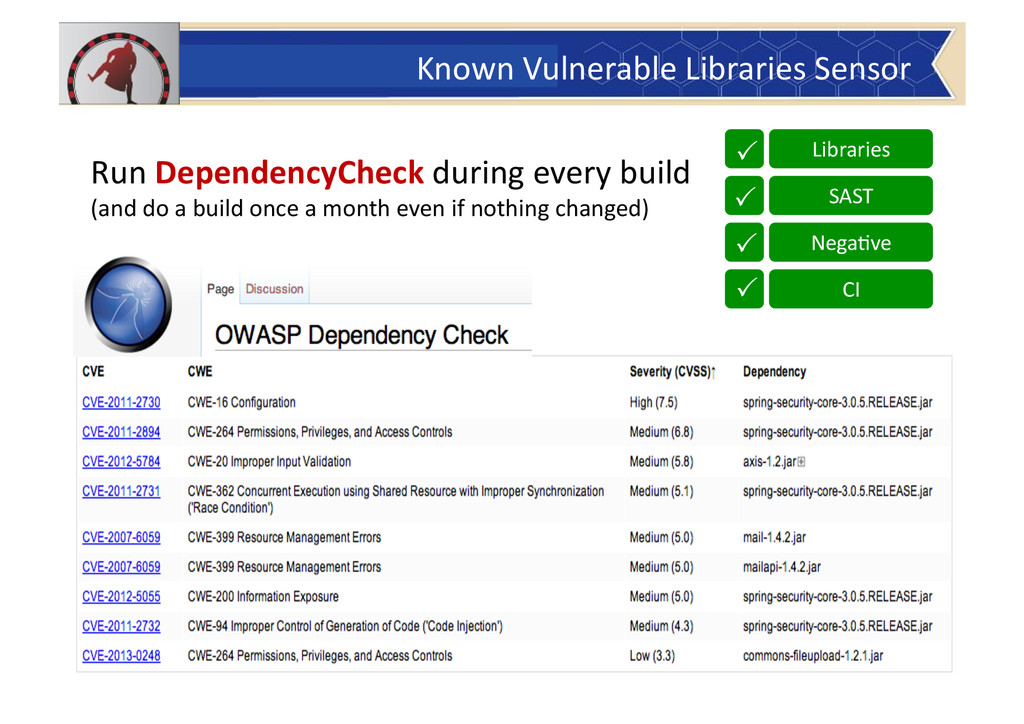
Known Vulnerable Libraries Sensor Libraries SAST Nega0ve
CI ! ! ! ! Run DependencyCheck during every build (and do a build once a month even if nothing changed) -
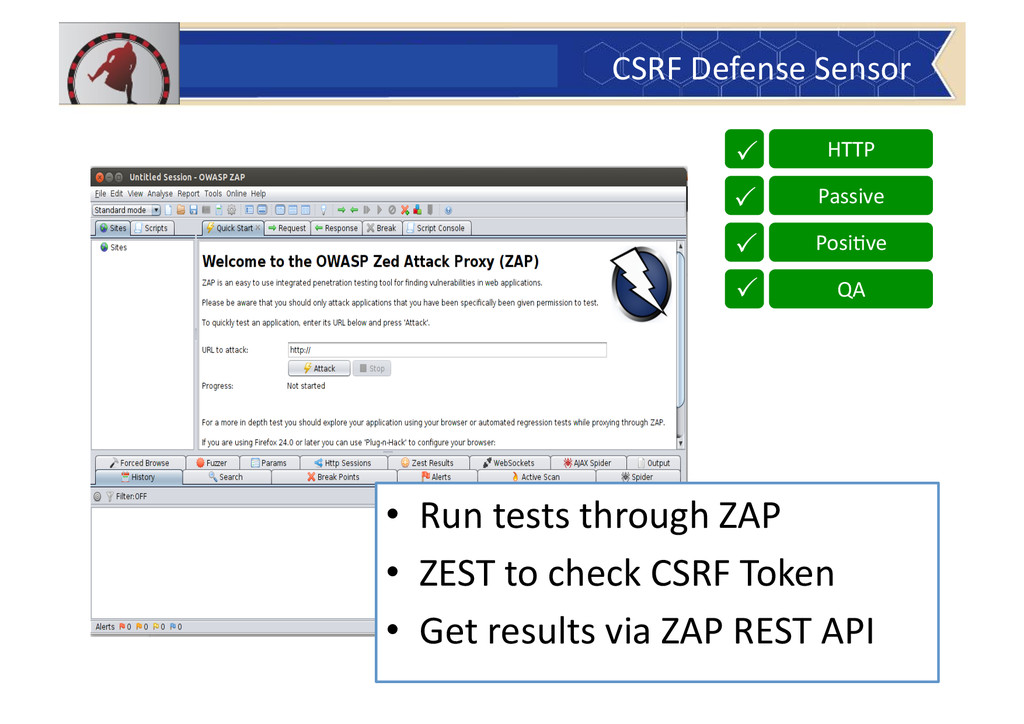
• Run tests through ZAP • ZEST to check
CSRF Token • Get results via ZAP REST API CSRF Defense Sensor HTTP Passive Posi0ve QA ! ! ! ! -
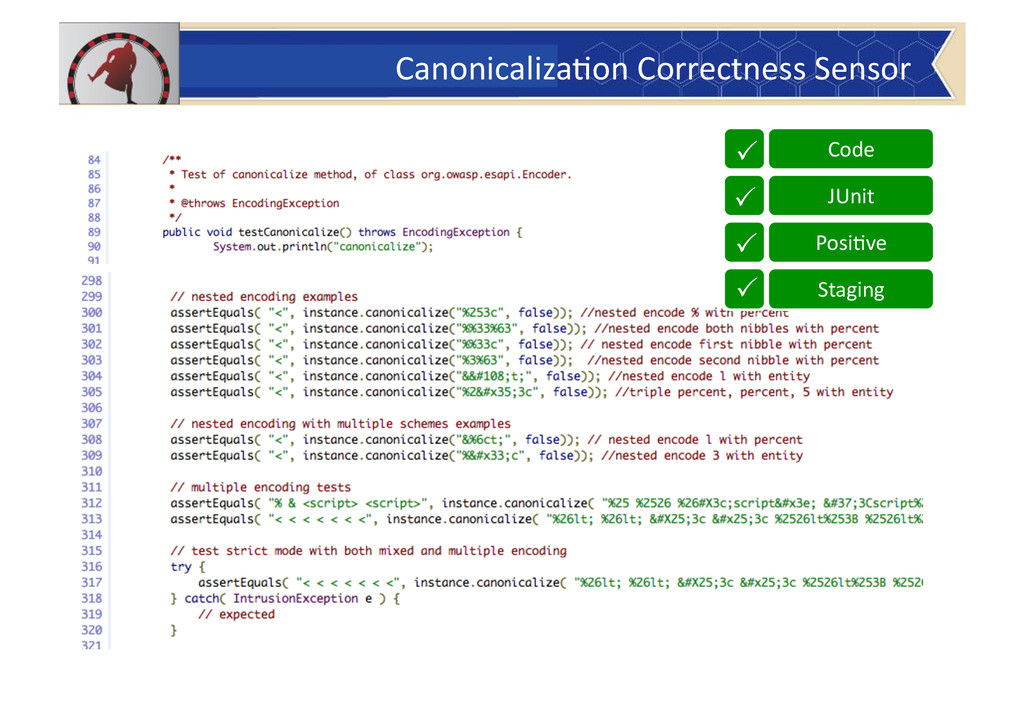
Canonicaliza0on Correctness Sensor Code JUnit Posi0ve
Staging ! ! ! ! -
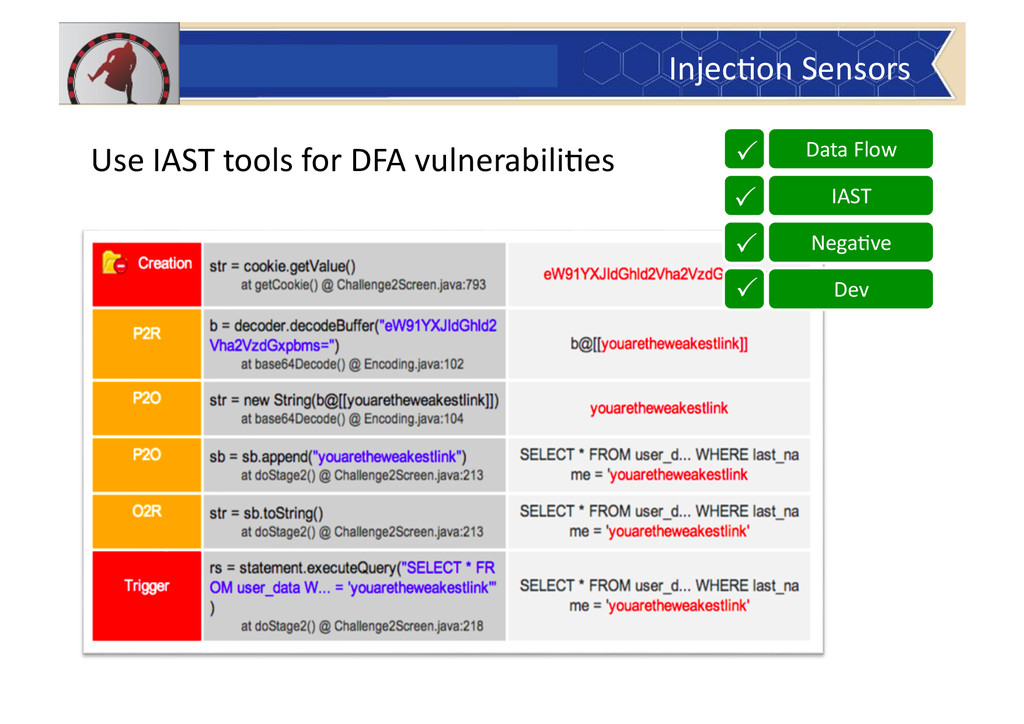
Injec0on Sensors Data Flow IAST Nega0ve
Dev ! ! ! ! Use IAST tools for DFA vulnerabili0es -
• What would you like to gather from all your
applica0ons? • Inventory? Architecture? Outbound connec0ons? Lines of code? Security components? • All possible…. and all at devops speed and porXolio scale Architecture, Inventory, and More… -
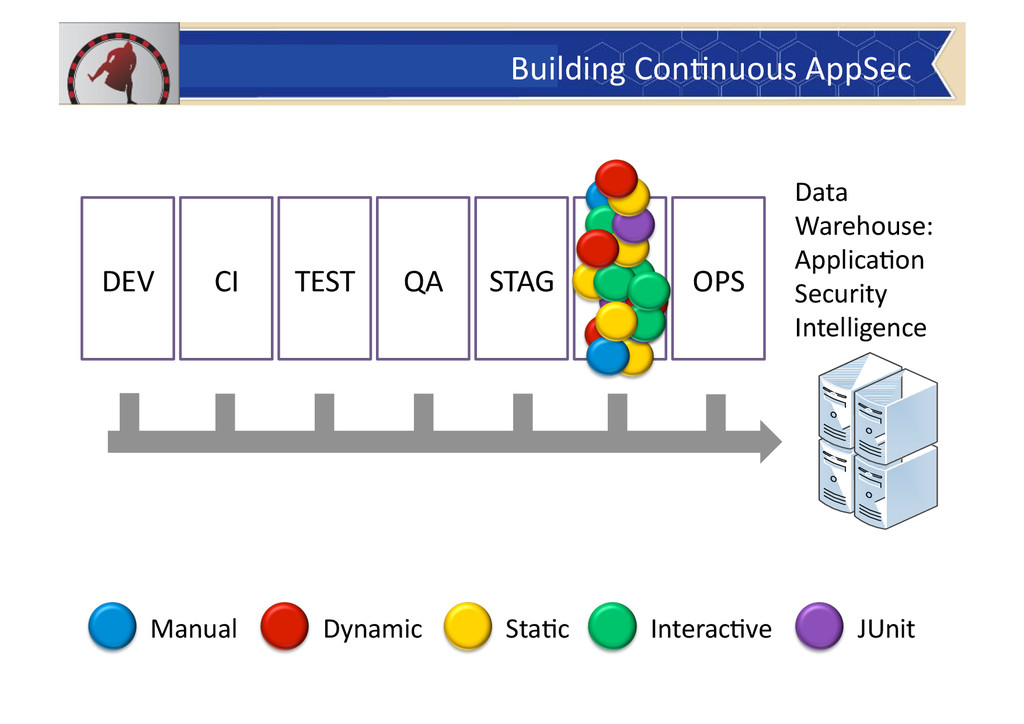
Building Con0nuous AppSec Dynamic Interac0ve JUnit
Manual Sta0c DEV CI TEST QA STAG OPS SEC Data Warehouse: Applica0on Security Intelligence -
Sensors? How do you know what sensors you need?
1) The OWASP Top Ten? 2) What your tools are good at? 3) What your pentester thinks is important? 4) Actually figure out what mahers? -
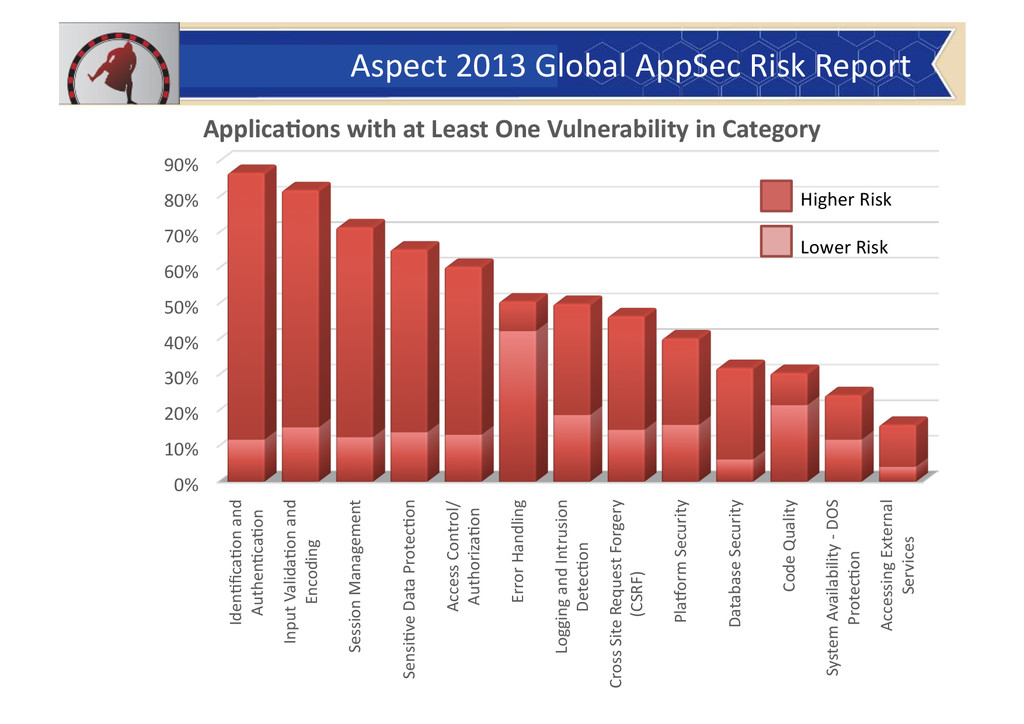
0% 10% 20% 30% 40%
50% 60% 70% 80% 90% Iden0fica0on and Authen0ca0on Input Valida0on and Encoding Session Management Sensi0ve Data Protec0on Access Control/ Authoriza0on Error Handling Logging and Intrusion Detec0on Cross Site Request Forgery (CSRF) PlaXorm Security Database Security Code Quality System Availability -‐ DOS Protec0on Accessing External Services ApplicaAons with at Least One Vulnerability in Category Higher Risk Lower Risk Aspect 2013 Global AppSec Risk Report -
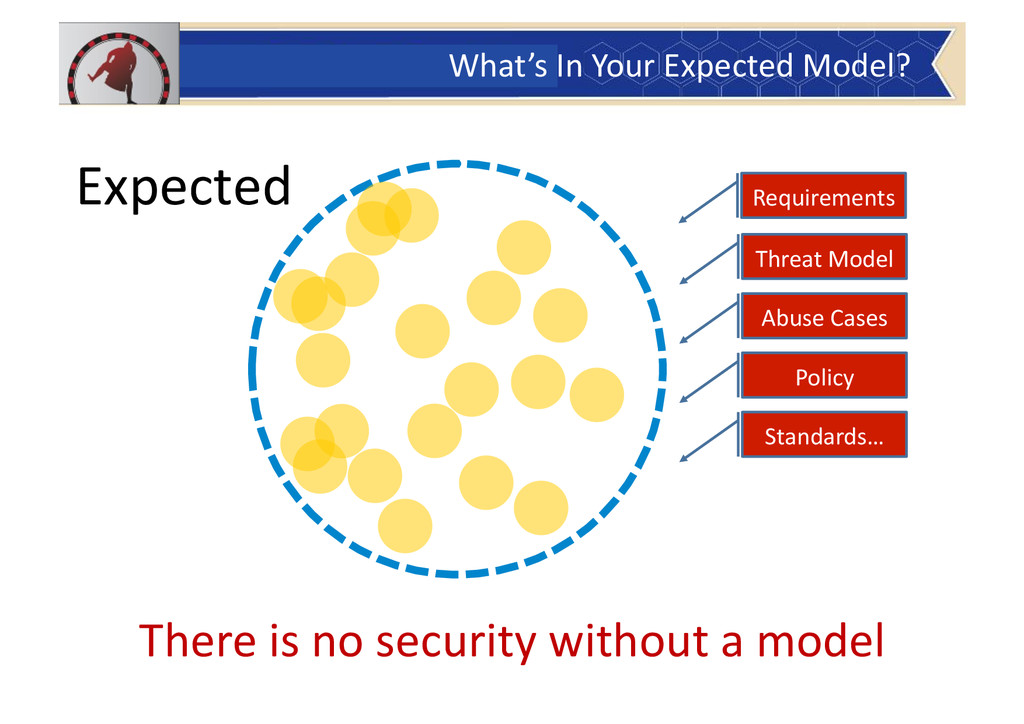
What’s In Your Expected Model? Expected Threat Model
Abuse Cases Policy Standards… Requirements There is no security without a model -
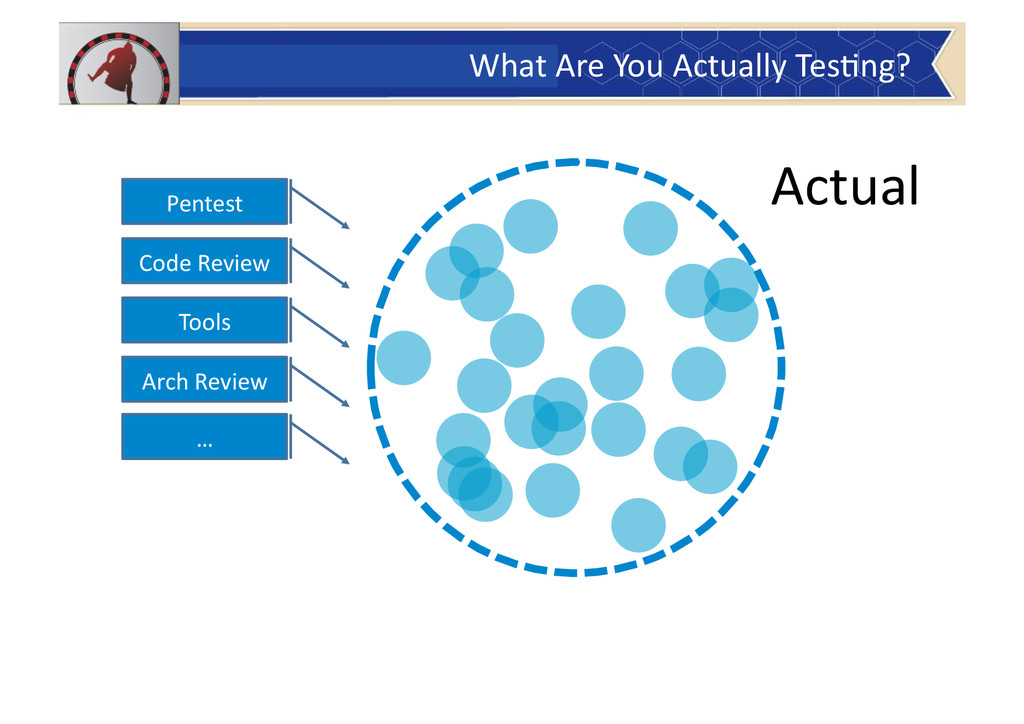
What Are You Actually Tes0ng? Actual Pentest
Code Review Tools Arch Review … -
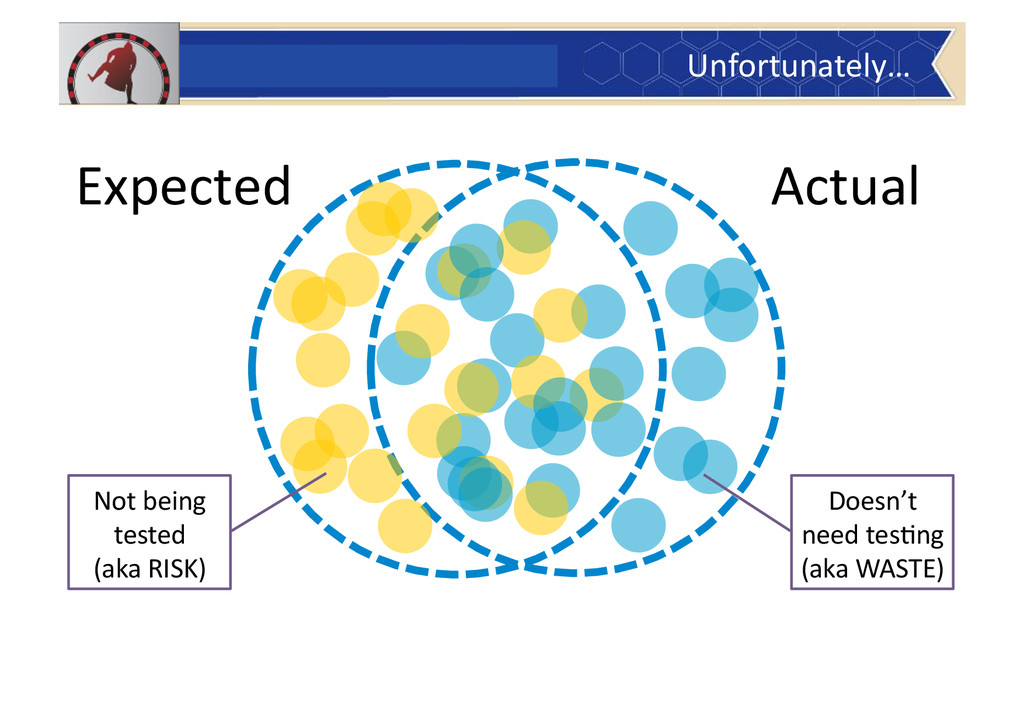
Unfortunately… Actual Expected Not being tested
(aka RISK) Doesn’t need tes0ng (aka WASTE) -
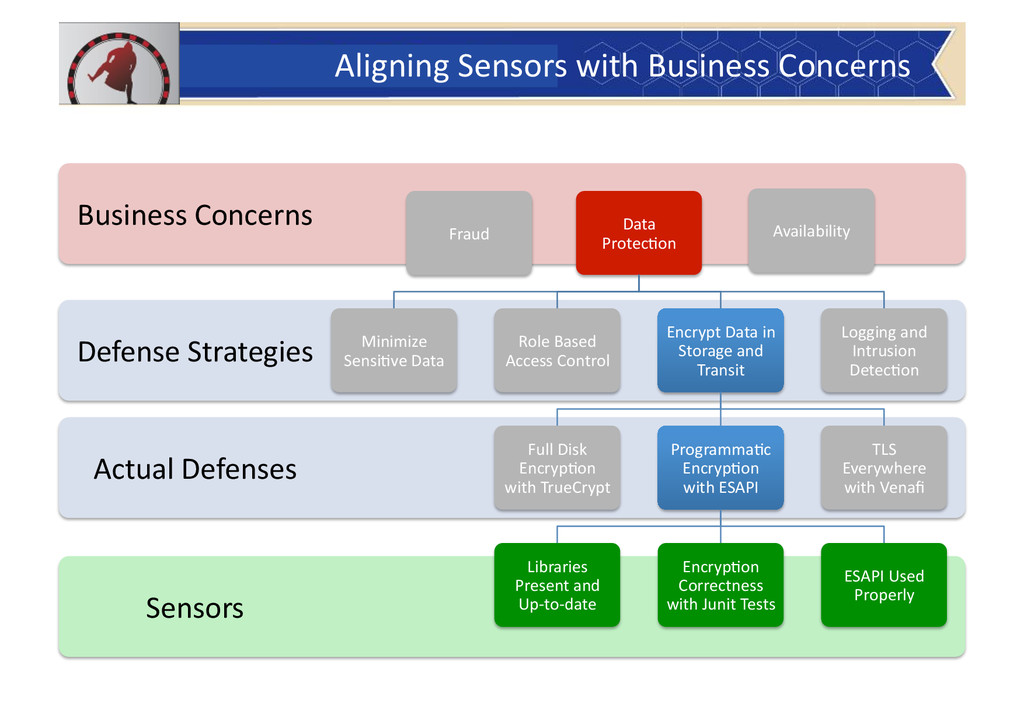
Sensors Actual Defenses Defense Strategies Business Concerns
Data Protec0on Minimize Sensi0ve Data Role Based Access Control Encrypt Data in Storage and Transit Full Disk Encryp0on with TrueCrypt Programma0c Encryp0on with ESAPI Libraries Present and Up-‐to-‐date Encryp0on Correctness with Junit Tests ESAPI Used Properly TLS Everywhere with Venafi Logging and Intrusion Detec0on Aligning Sensors with Business Concerns Fraud Availability -
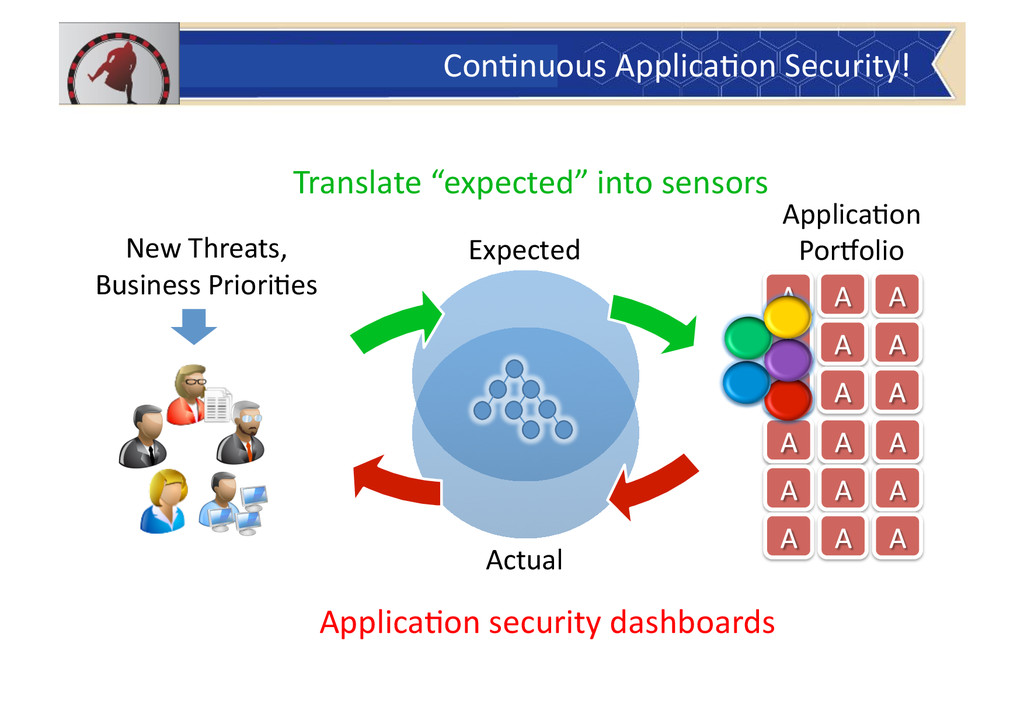
Con0nuous Applica0on Security! Expected Actual Applica0on
PorXolio Applica0on security dashboards Translate “expected” into sensors New Threats, Business Priori0es -
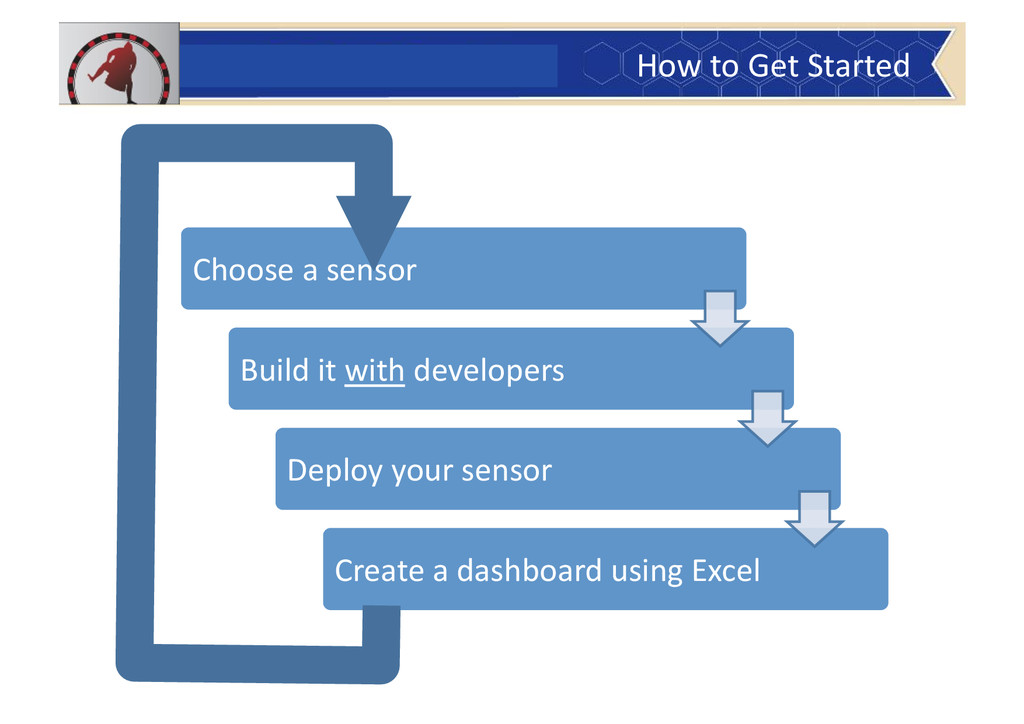
Choose a sensor Build it with developers Deploy
your sensor Create a dashboard using Excel How to Get Started -
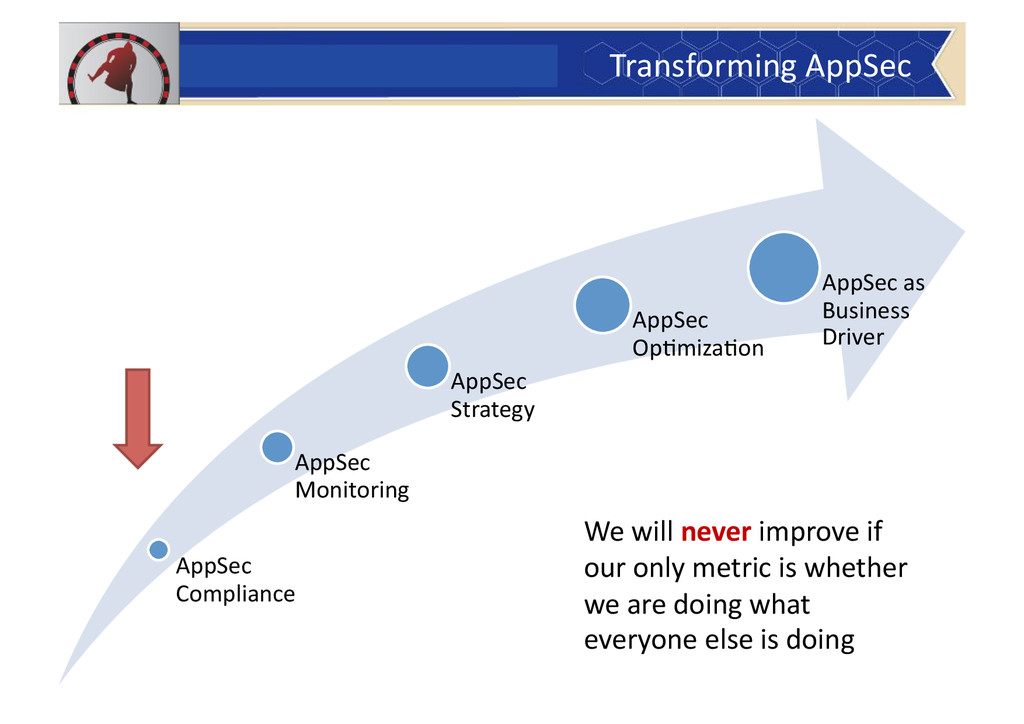
Transforming AppSec AppSec Compliance AppSec Monitoring
AppSec Strategy AppSec Op0miza0on AppSec as Business Driver We will never improve if our only metric is whether we are doing what everyone else is doing