Security Adapting AppSec for the Modern Internet, Alex Stamos, CSO, Facebook • Cybersecurity Partnership, Technology and Trust, Dr. Phyllis Schneck, DHS • 50 Shades of AppSec, Troy Hunt, Author, Pluralsite
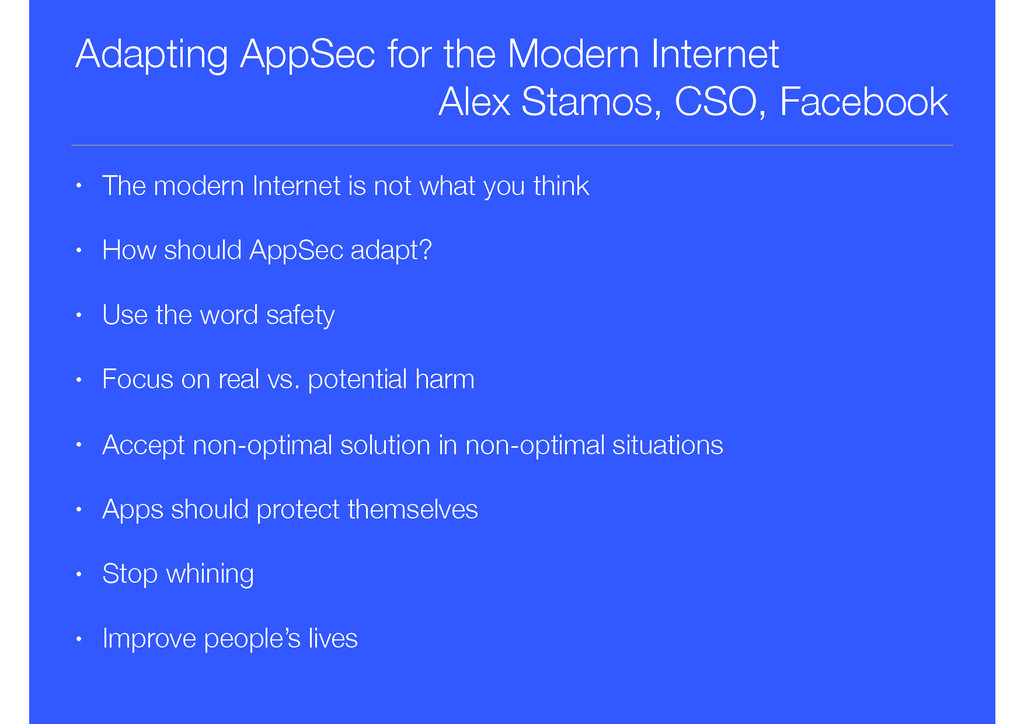
• The modern Internet is not what you think • How should AppSec adapt? • Use the word safety • Focus on real vs. potential harm • Accept non-optimal solution in non-optimal situations • Apps should protect themselves • Stop whining • Improve people’s lives
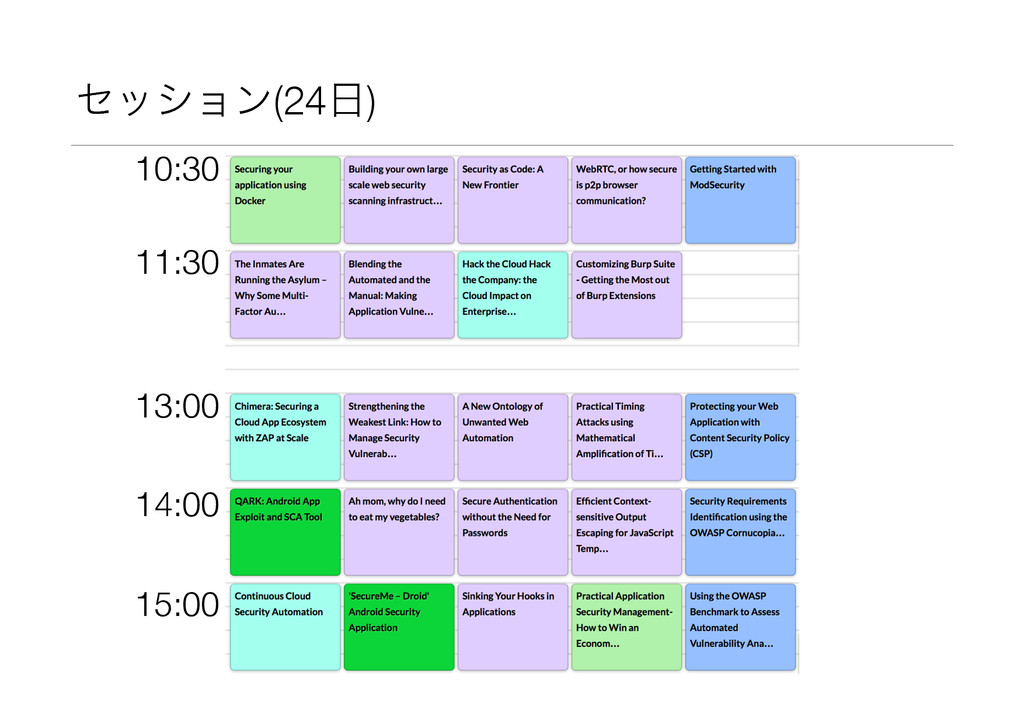
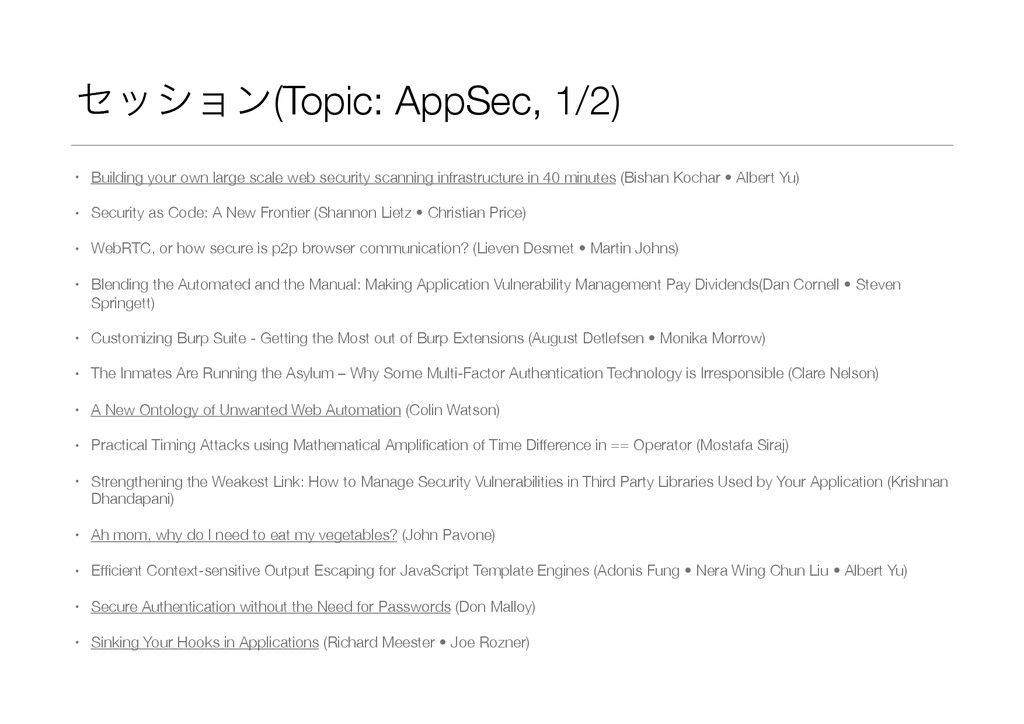
security scanning infrastructure in 40 minutes (Bishan Kochar • Albert Yu) • Security as Code: A New Frontier (Shannon Lietz • Christian Price) • WebRTC, or how secure is p2p browser communication? (Lieven Desmet • Martin Johns) • Blending the Automated and the Manual: Making Application Vulnerability Management Pay Dividends(Dan Cornell • Steven Springett) • Customizing Burp Suite - Getting the Most out of Burp Extensions (August Detlefsen • Monika Morrow) • The Inmates Are Running the Asylum – Why Some Multi-Factor Authentication Technology is Irresponsible (Clare Nelson) • A New Ontology of Unwanted Web Automation (Colin Watson) • Practical Timing Attacks using Mathematical Amplification of Time Difference in == Operator (Mostafa Siraj) • Strengthening the Weakest Link: How to Manage Security Vulnerabilities in Third Party Libraries Used by Your Application (Krishnan Dhandapani) • Ah mom, why do I need to eat my vegetables? (John Pavone) • Efficient Context-sensitive Output Escaping for JavaScript Template Engines (Adonis Fung • Nera Wing Chun Liu • Albert Yu) • Secure Authentication without the Need for Passwords (Don Malloy) • Sinking Your Hooks in Applications (Richard Meester • Joe Rozner)
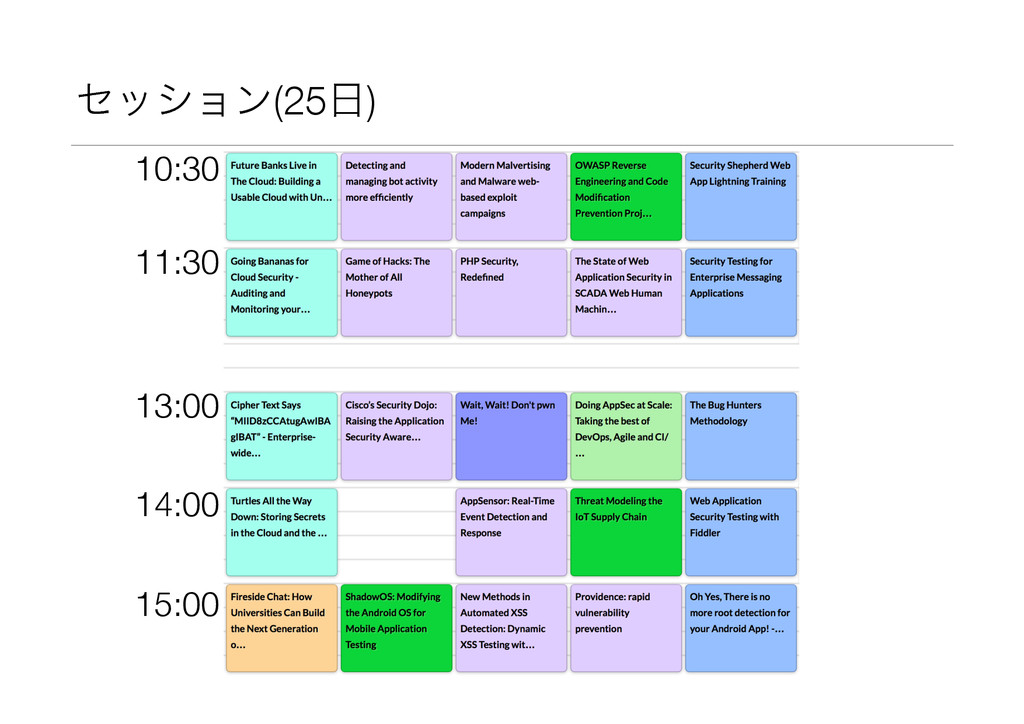
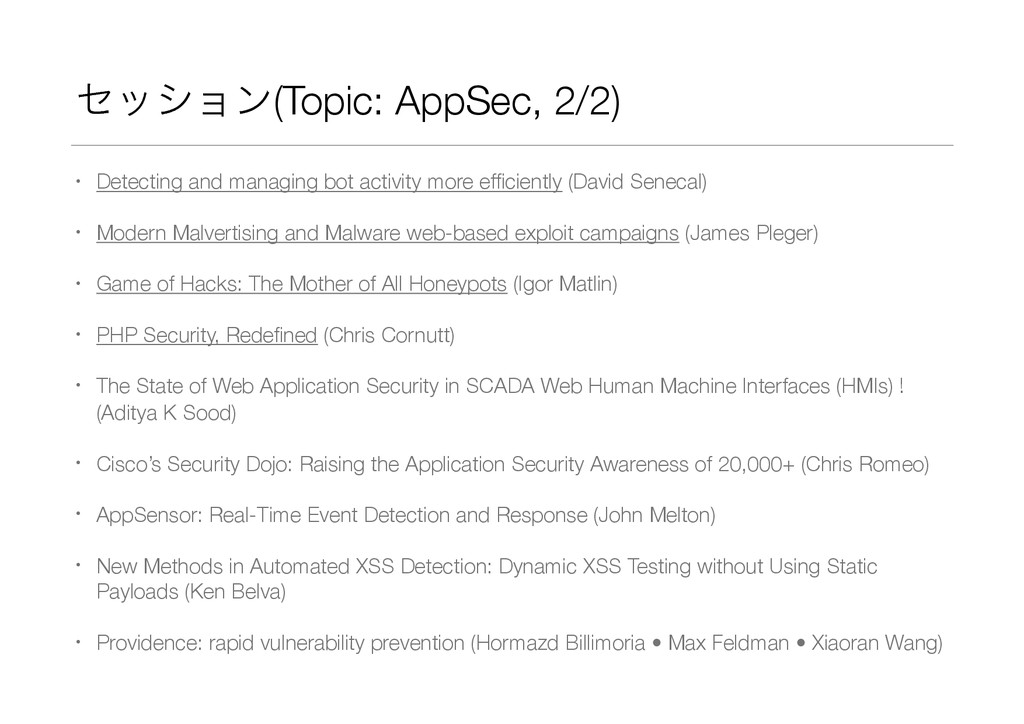
efficiently (David Senecal) • Modern Malvertising and Malware web-based exploit campaigns (James Pleger) • Game of Hacks: The Mother of All Honeypots (Igor Matlin) • PHP Security, Redefined (Chris Cornutt) • The State of Web Application Security in SCADA Web Human Machine Interfaces (HMIs) ! (Aditya K Sood) • Cisco’s Security Dojo: Raising the Application Security Awareness of 20,000+ (Chris Romeo) • AppSensor: Real-Time Event Detection and Response (John Melton) • New Methods in Automated XSS Detection: Dynamic XSS Testing without Using Static Payloads (Ken Belva) • Providence: rapid vulnerability prevention (Hormazd Billimoria • Max Feldman • Xiaoran Wang)
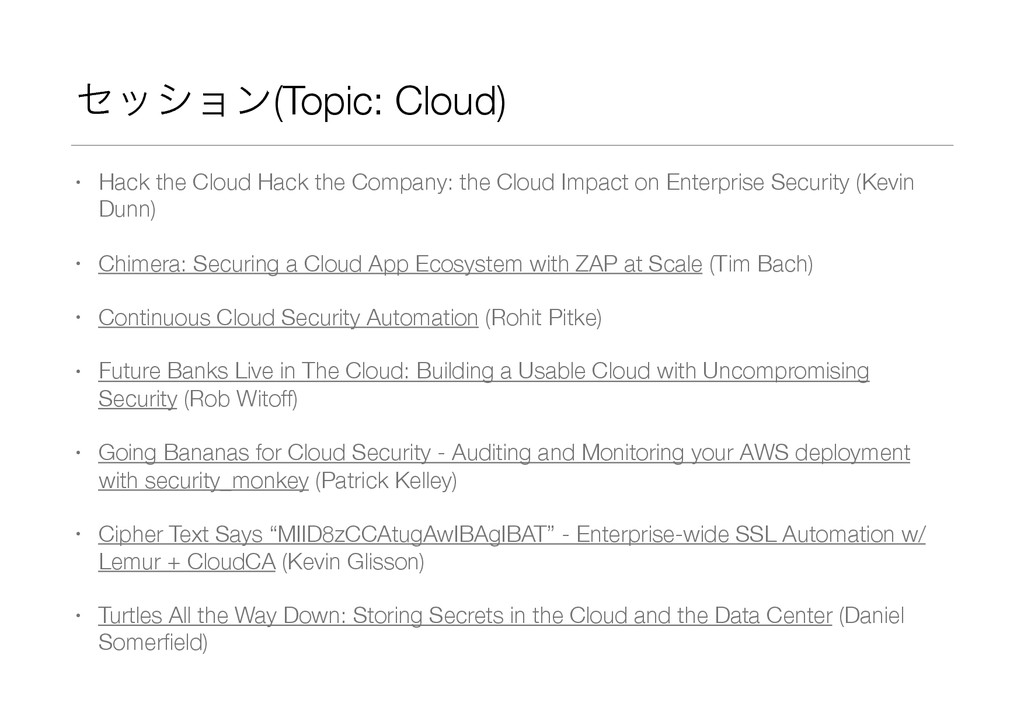
Cloud Impact on Enterprise Security (Kevin Dunn) • Chimera: Securing a Cloud App Ecosystem with ZAP at Scale (Tim Bach) • Continuous Cloud Security Automation (Rohit Pitke) • Future Banks Live in The Cloud: Building a Usable Cloud with Uncompromising Security (Rob Witoff) • Going Bananas for Cloud Security - Auditing and Monitoring your AWS deployment with security_monkey (Patrick Kelley) • Cipher Text Says “MIID8zCCAtugAwIBAgIBAT” - Enterprise-wide SSL Automation w/ Lemur + CloudCA (Kevin Glisson) • Turtles All the Way Down: Storing Secrets in the Cloud and the Data Center (Daniel Somerfield)
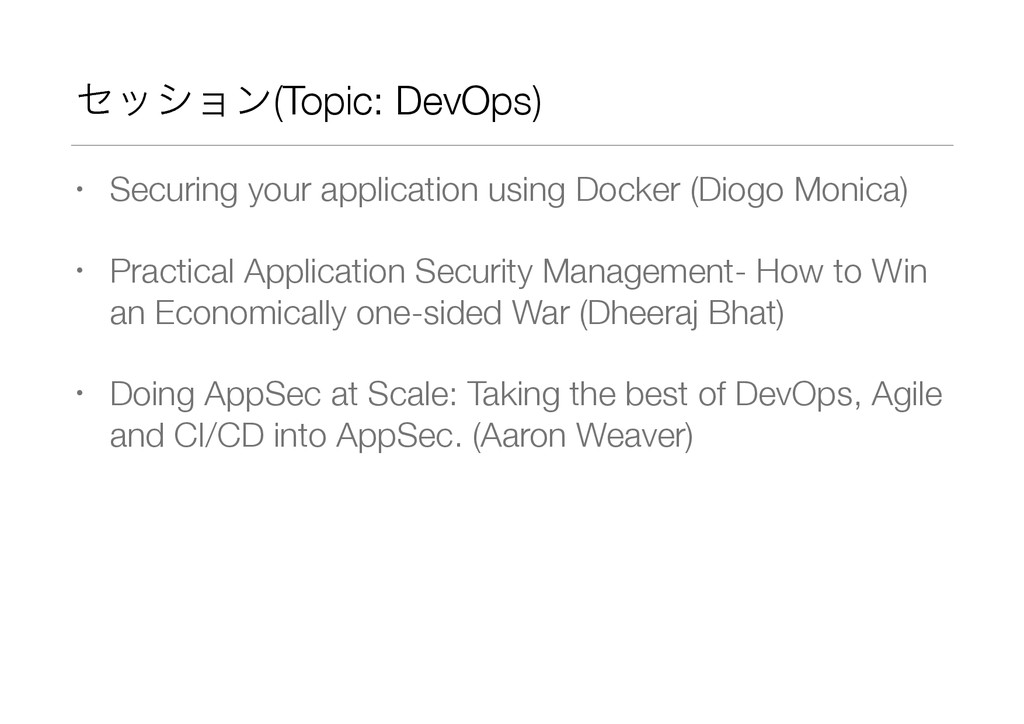
• Practical Application Security Management- How to Win an Economically one-sided War (Dheeraj Bhat) • Doing AppSec at Scale: Taking the best of DevOps, Agile and CI/CD into AppSec. (Aaron Weaver)
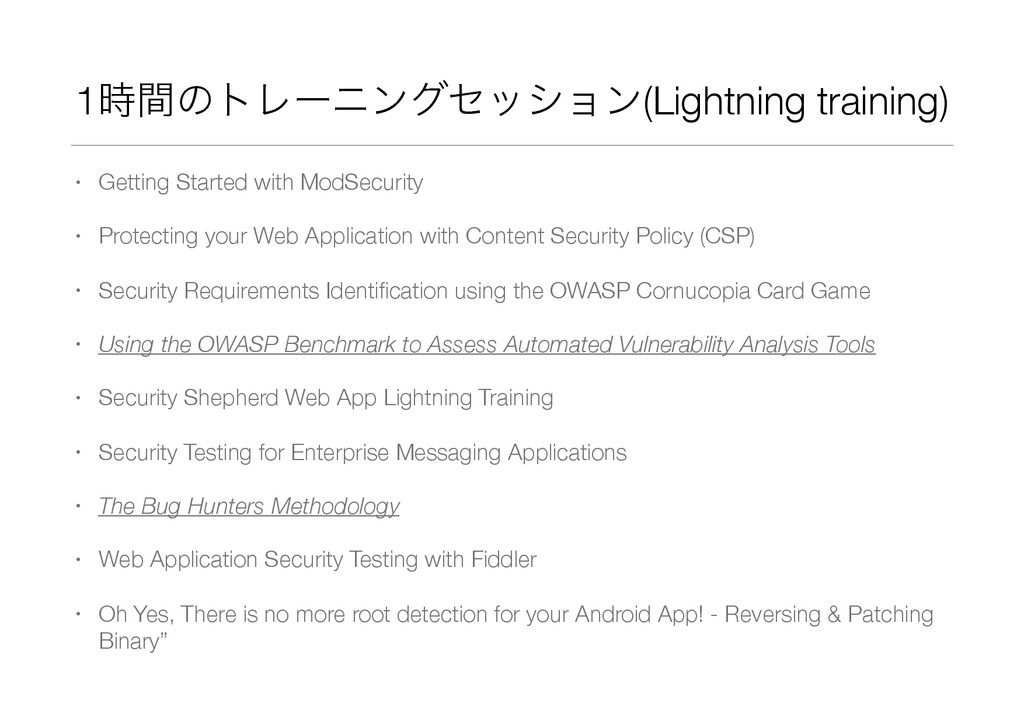
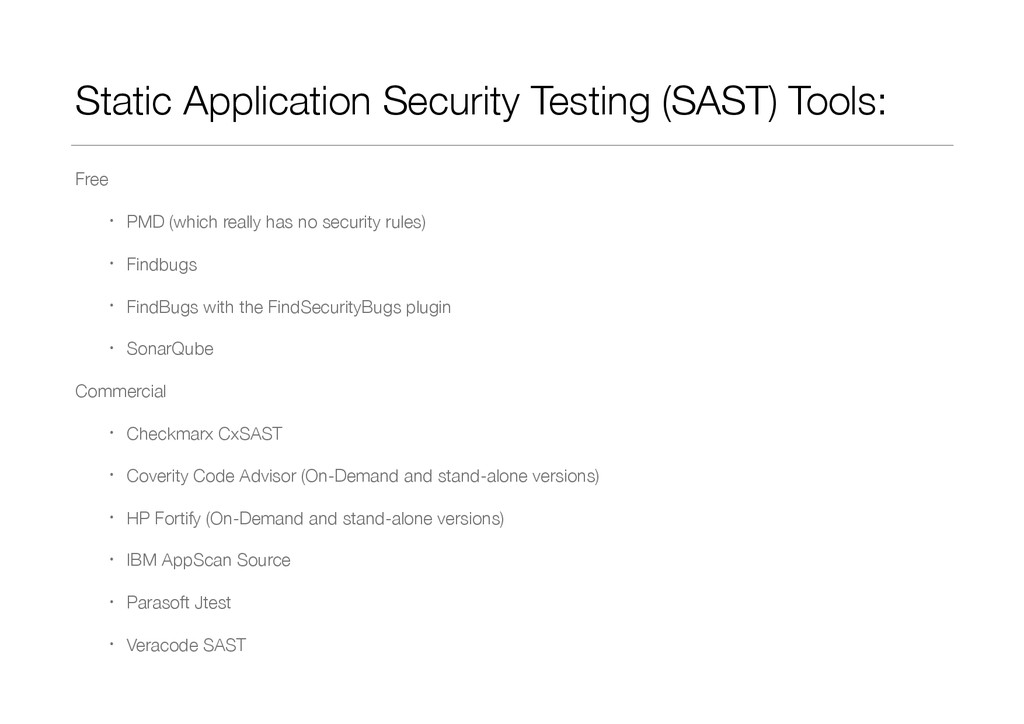
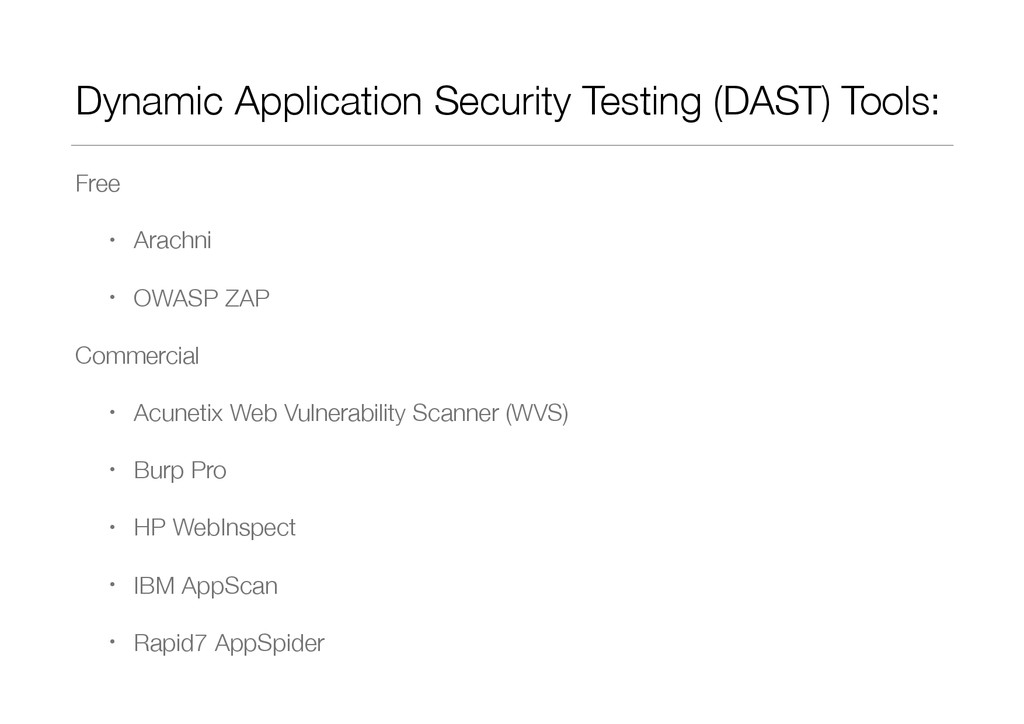
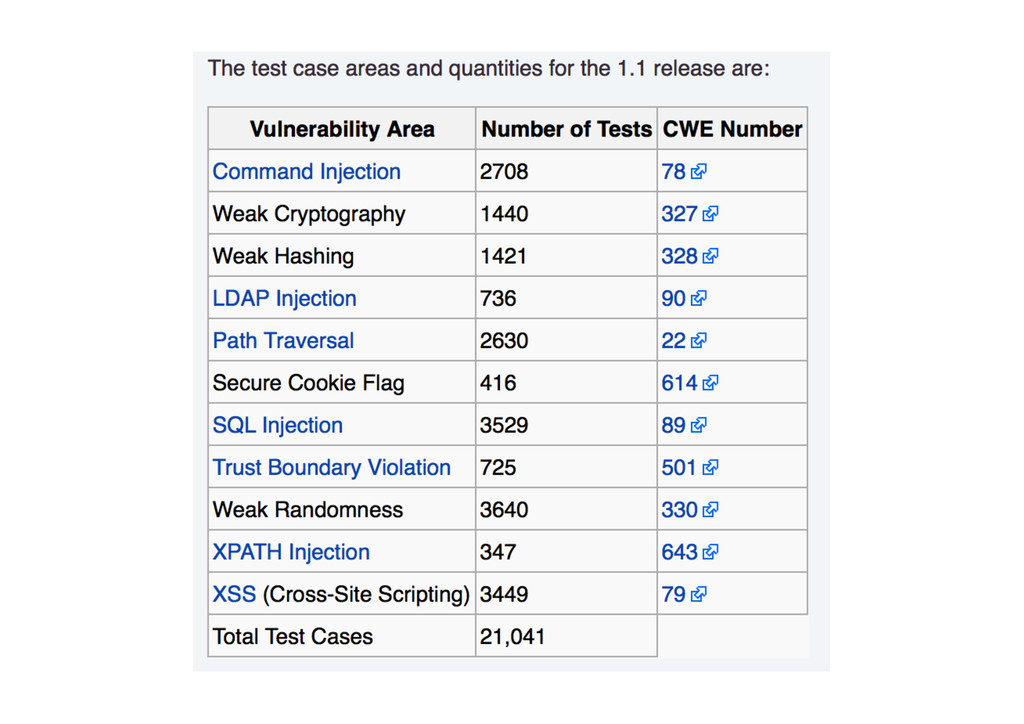
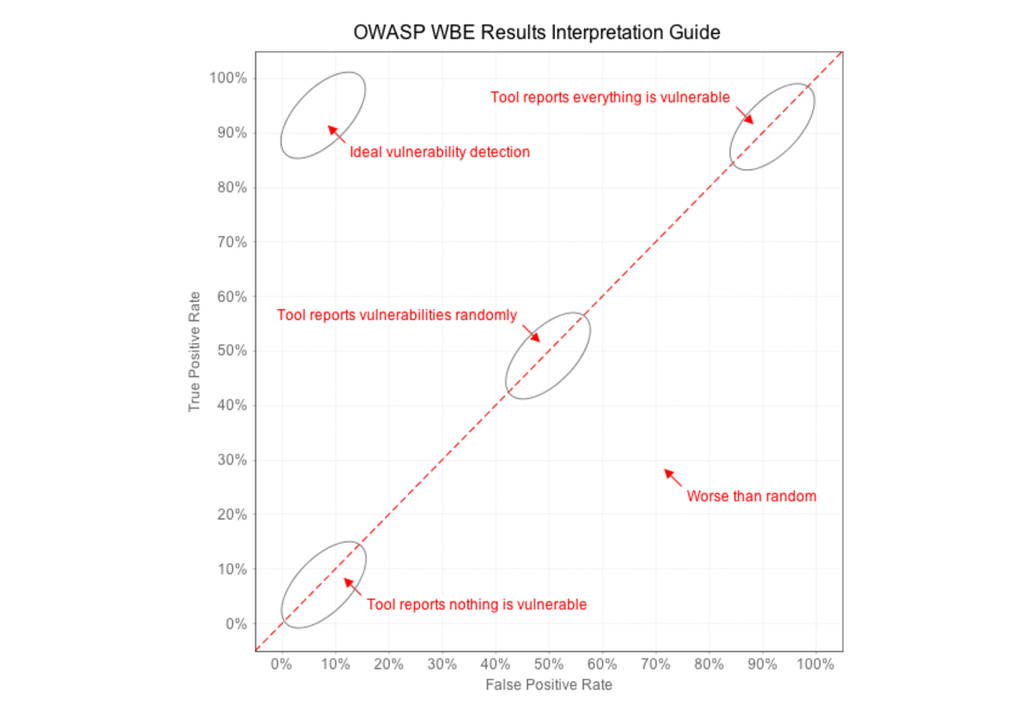
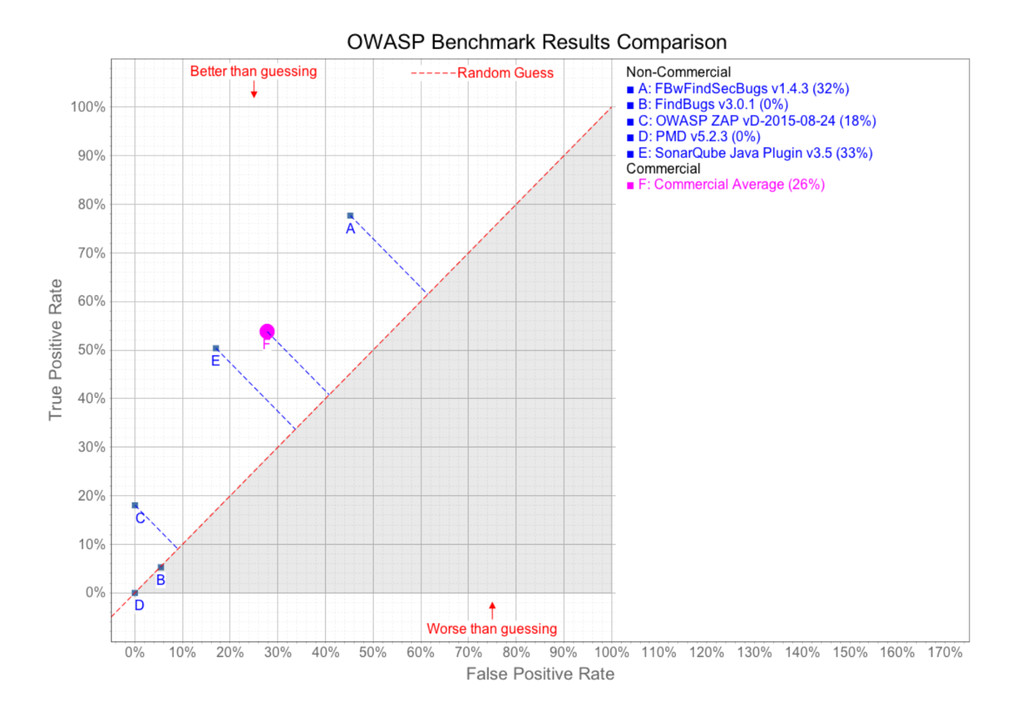
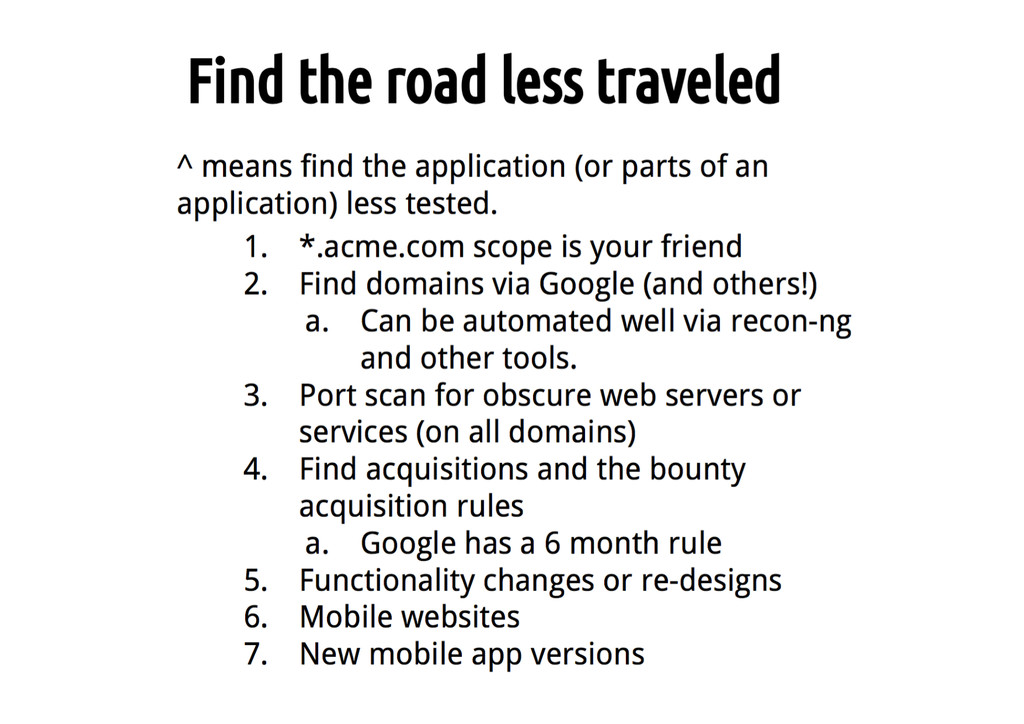
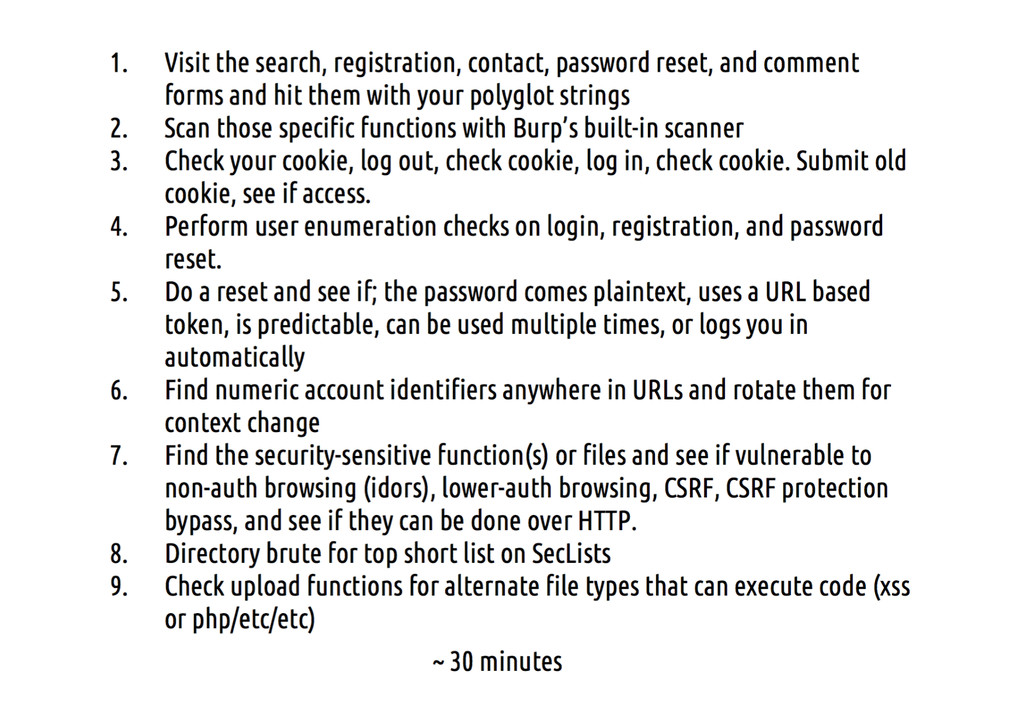
Web Application with Content Security Policy (CSP) • Security Requirements Identification using the OWASP Cornucopia Card Game • Using the OWASP Benchmark to Assess Automated Vulnerability Analysis Tools • Security Shepherd Web App Lightning Training • Security Testing for Enterprise Messaging Applications • The Bug Hunters Methodology • Web Application Security Testing with Fiddler • Oh Yes, There is no more root detection for your Android App! - Reversing & Patching Binary”


 owaspjapan
 maltzj
 keathley
 lcolladotor
 shlominoach
 rkendrick25
 leimatthew05
 tammyeverts
 addyosmani
 greggifford
 chriscoyier
 quramy
 tapps