Protection Regulation (GDPR) is a regulation in EU law on data protection and privacy for all individuals within the European Union. It also addresses the export of personal data outside the EU. ▸ Enforcement date: 25 May 2018. ▸ Quite unclear and confusing. ▸ Huge fines for non-compliance: up to 20 million EUR or 4% of the total worldwide annual turnover. https://en.wikipedia.org/wiki/General_Data_Protection_Regulation
‘personal data’ means any information relating to an identified or identifiable natural person (‘data subject’); an identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, an identification number, location data, an online identifier or to one or more factors specific to the physical, physiological, genetic, mental, economic, cultural or social identity of that natural person; ▸ …which is basically anything related to specific person.
Forces deep understanding of user data flows and serious security approach (OWASP is your friend). ▸ New features required to be available for users. ▸ Data minimisation (you should not collect more data than necessary). Required data retention and deletion schedules. ▸ Existing users must be transferred to new policy, data audit must be performed. ▸ Data exchange with 3rd party services must be controlled.
CONTROL? ▸ What data is being collected? ▸ Where is data being collected? ▸ What happens to the data (why it’s being collected)? ▸ Who has access to the data? ▸ For how long will the data exist and be processed?
controller - a person/organisation/company that requests and uses the data ▸ Data processor - a person/organisation/company which processes personal data on behalf of the controller
clear definition of what user data will be collected and how will it be used. ▸ Users will need to explicitly approve the policy for every data use case (including mechanisms like machine learning, profiling, automated decision making). ▸ Developers will have to implement a mechanism to obtain explicit consent and save it (giving right to change the decision later). Consider having separate DB table for consent history with timestamps, handle missing consent.
by the data subject ▸ Right to rectification ▸ Right to erasure (‘right to be forgotten’) ▸ Right to restriction of processing ▸ Right to data portability
access to ABSOLUTELY ALL the data that we have related to that person. ▸ Developers will provide a way to show the data. It can be a manual process, request has to be addressed within 30 days. ▸ Data should be available in human readable format (GUI, PDF, etc). ▸ Data from external services must be included.
his/her data to be updated. ▸ Developers will provide a way to edit user profile. Alternatively this can also be a manual process. Third party services should also be concerned.
can request his/her data to be erased. ▸ Developers will have to provide a way to delete user profile. ▸ Service to handle this by user ID. ▸ Strategy for foreign keys handling (nullify, anonymize, cascade erase). ▸ Marking users to be deleted async. ▸ Backups? Keep the forgetting history.
event sourcing, blockchain. ▸ Search engines for public profiles (return 404 to trigger removal). ▸ 3rd party services (data processors) must be notified to complete the process .
can request his/her data to be “frozen” for processing. ▸ Developers will have to provide a way to mark user profile as restricted for processing. ▸ Allow setting flag from both admin and user pages ▸ Similar to user profile erasing, but temporary
require export a copy of ABSOLUTELY ALL the data that we have related to that person. ▸ Developers will provide a way to export the data (however it can also be a cumbersome manual process). ▸ The same data set as for the “Right to access” ▸ Machine-readable format: CSV, JSON, XML ▸ Large data set - use background processing ▸ Idea behind this - allow migrating to other apps and limit vendor locking
16 cannot give the ‘Explicit Consent’ ▸ Age checking is required for new users (checkbox) ▸ For younger users only parent / legal guardian can be asked for consent ▸ Totally unclear how to do that ▸ Email? Matches regulation needs, but remains a fiction
overrides the ePrivacy directive. ▸ User behaviour on the website is a personal data. ▸ Website owner is a data controller, 3rd party service (Google, Facebook, …) is a data processor. ▸ The standard bar with “We use cookies” is no longer enough, explicit consent must be gained (checkbox). ▸ In future the consent can be moved to browser settings. ▸ Is it worth it…?
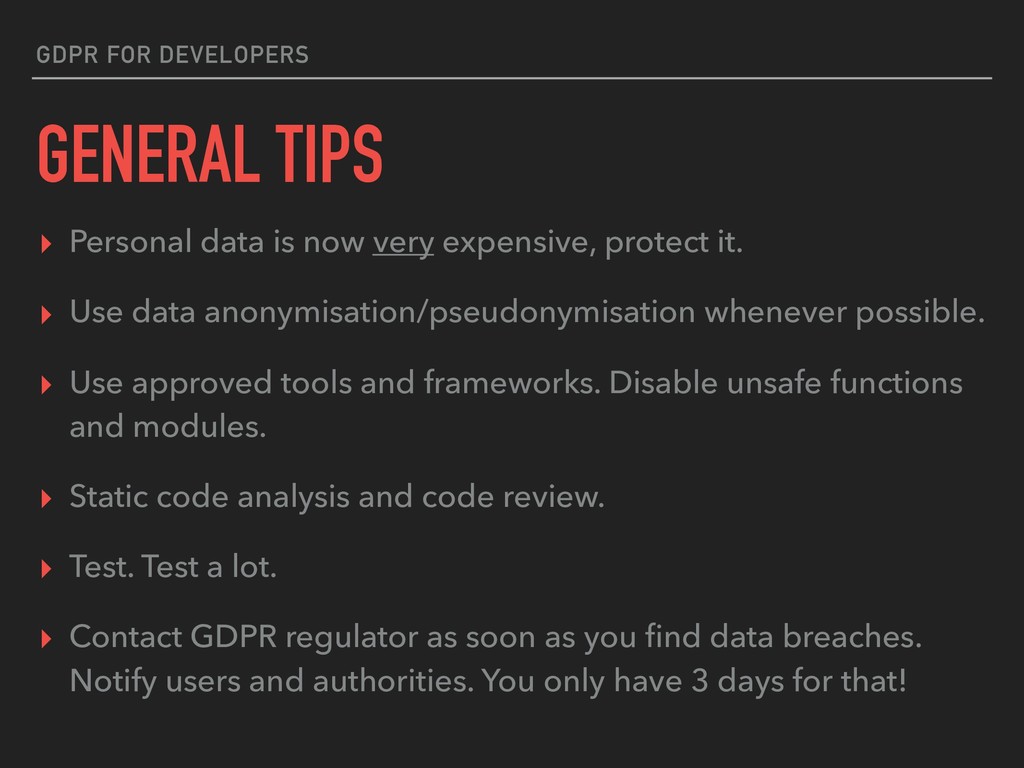
very expensive, protect it. ▸ Use data anonymisation/pseudonymisation whenever possible. ▸ Use approved tools and frameworks. Disable unsafe functions and modules. ▸ Static code analysis and code review. ▸ Test. Test a lot. ▸ Contact GDPR regulator as soon as you find data breaches. Notify users and authorities. You only have 3 days for that!


 pcylo
 pvcresin
 richargh
 giljongyu
 yosuke_furukawa
 yuta_onishi_97
 takahirosunaga
 tarao
 slobodan
 sodainc
 ivargrimstad
 kishida
 hal_spidernight
 popppiees
 sarafernandez
 uxyall
 codingconduct
 jonoalderson
 inesmontani
 schroneko
 kastner
 kneath
 katarinadahlin
 3n