by the day/Researcher by the night. • Love breaking stuff and witnessing the chaos. • Speaker at various cons around the world including owasp appsec usa,DEFCON , Bsides Las Vegas Disclaimer : Views expressed here are my own not that of my employer.
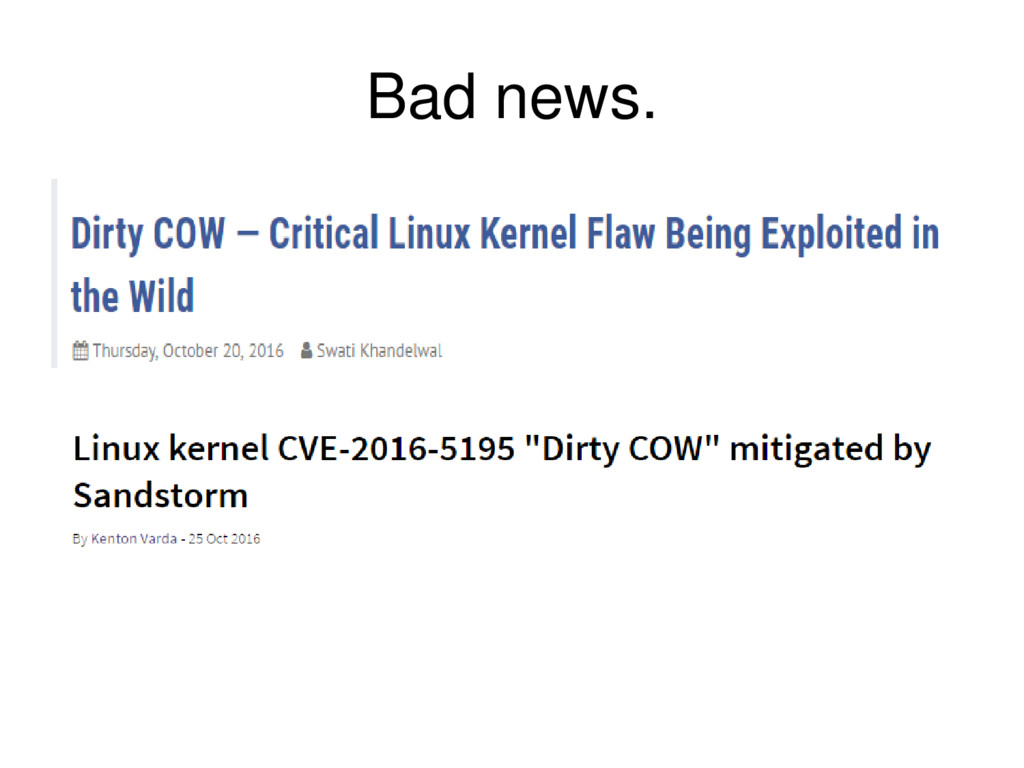
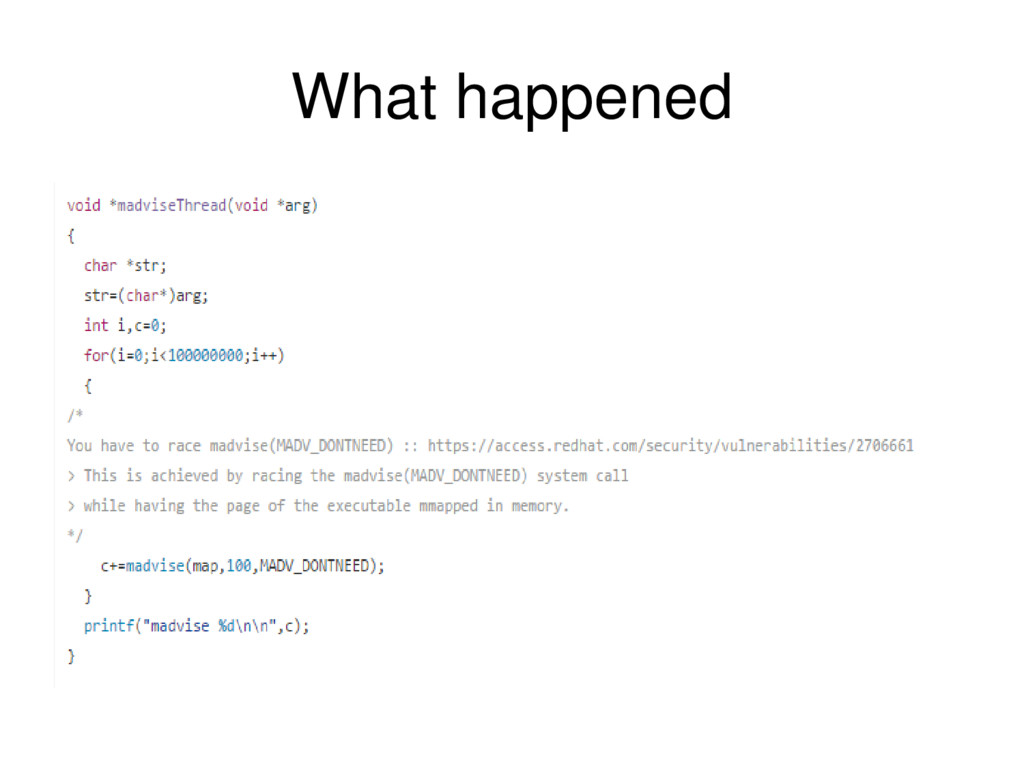
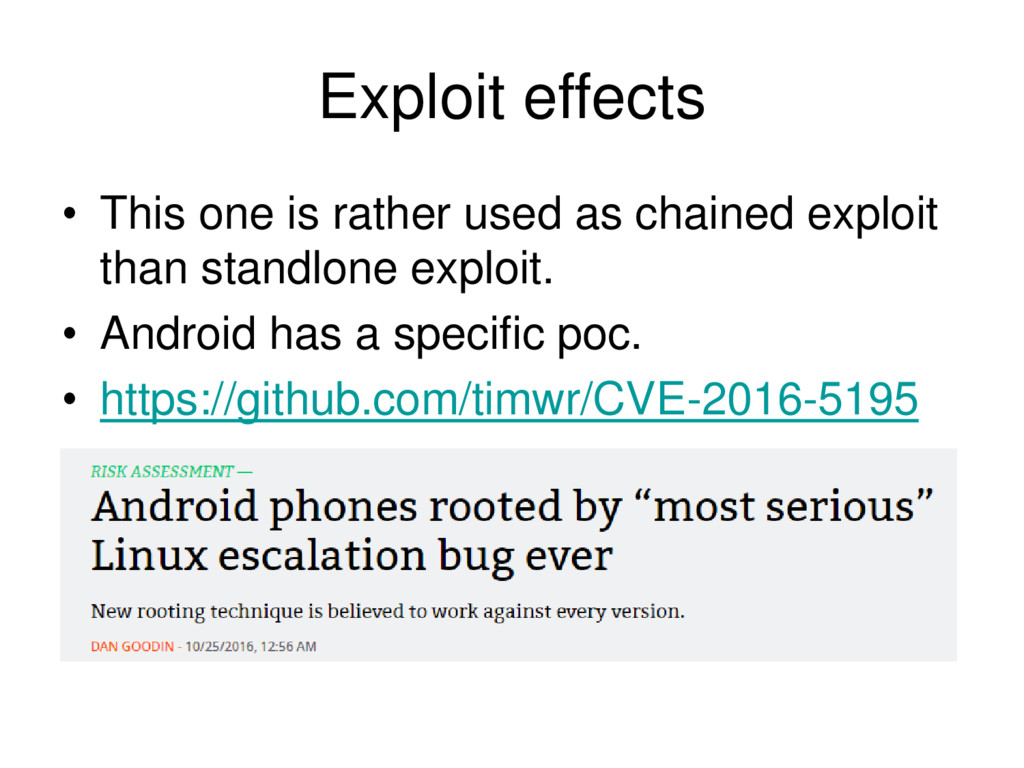
• Issues lies with how the memory mapping occurs with the linux operating system. • The bug existed from kernel version 2.6.22 aka from 2007 :P • Affects large number of linux based system including droids, iot etc.
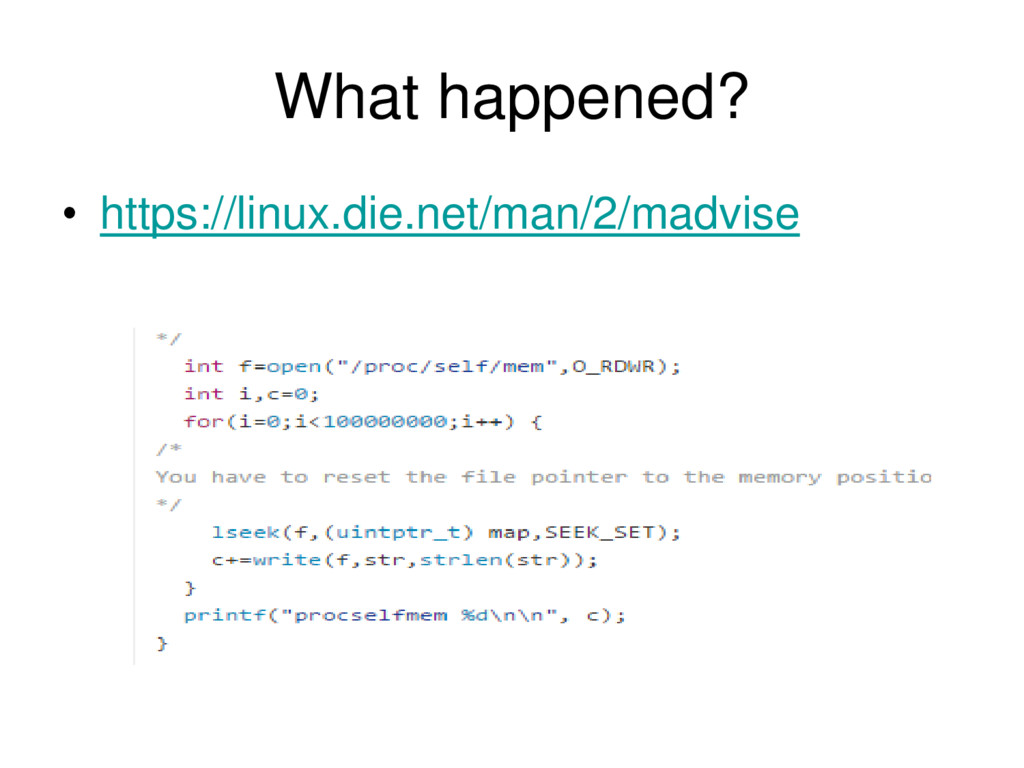
a file is linked to the virutal memory but not copied as a whole to the virtual memory. • This bug is a race condition exploit which means it wont happen in the ideal time but the race condition needs to be triggered for it to work .
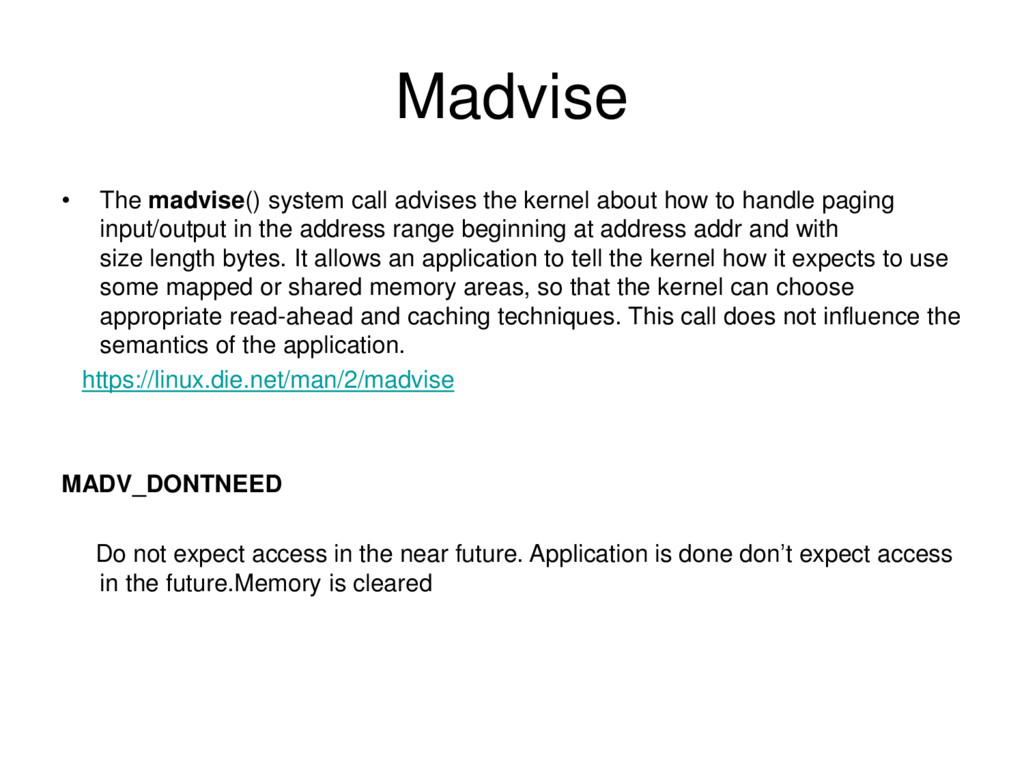
how to handle paging input/output in the address range beginning at address addr and with size length bytes. It allows an application to tell the kernel how it expects to use some mapped or shared memory areas, so that the kernel can choose appropriate read-ahead and caching techniques. This call does not influence the semantics of the application. https://linux.die.net/man/2/madvise MADV_DONTNEED Do not expect access in the near future. Application is done don’t expect access in the future.Memory is cleared
x.git/commit/?id=19be0eaffa3ac7d8eb6784ad9bdbc 7d67ed8e619 • New flag – FOLL_COW flag to stop the race condition. • Ubuntu and various other distributions released their patches along the way. • https://github.com/dirtycow/dirtycow.github.io/wiki/Pa tched-Kernel-Versions • You cant monitor this one in syslog.


 ezaki
 bitkey
 kairim0
 odashi
 teamlab
 tokuty
 yahonda
 puhitaku
 pfn
 masakiokuda
 satoshi7
 jmmastey
 aleyda
 codingconduct
 rakko
 raygrieselhuber
 coloredviolet
 soudai
 dougneiner
 techseoconnect
 wjessup
 honnibal