Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Securing Systems - Still Crazy After All These ...

Avatar for Sawaba Sawaba
March 13, 2019

Securing Systems - Still Crazy After All These Years

It's 2019 and we're still not sure if we have an accurate list of assets. We certainly can't guarantee they're all secure. The last penetration test was a bloodbath. Every day, we wonder if the breach will come.

The cycle of stress and worry CAN be broken, but each stage of securing systems has challenges. We'll analyze these challenges and provide strategies to address them. From asset discovery to hardening to vulnerability management - this talk will show how to build lasting confidence in the security we provide to our organizations.

Avatar for Sawaba

Sawaba

March 13, 2019

Other Decks in Technology

Transcript

  1. Securing Systems: Still Crazy After All These Years Scan the

    QR code for handouts, or email [email protected] with TacticalEdge2019 as the subject.
  2. whoami Defender - 9 years Financial Services Consultant - 5

    years Pen Testing, PCI Industry Analyst - 4 years 451 Research Research - 2 years Savage Security, Threatcare, NopSec @sawaba
  3. 3 Why is it so hard to secure systems? Can

    the cycle of stress and worry be broken?
  4. Constantly Changing Attackers/Threats Yesterday: Exploit Kits, Botnets Today: Ransomware, Cryptojacking

    Tomorrow: 5G? The CFO’s car? https://www.pentestpartners.com/security-blog/gone-in-six-seconds-exploiting-car-alarms/
  5. Emerging Technologies We still haven’t solved BYOD yet! But now

    we have: • cloud • IoT • privacy frameworks (e.g. GDPR) • SaaS versions of everything • cryptomining • supply chain tampering...
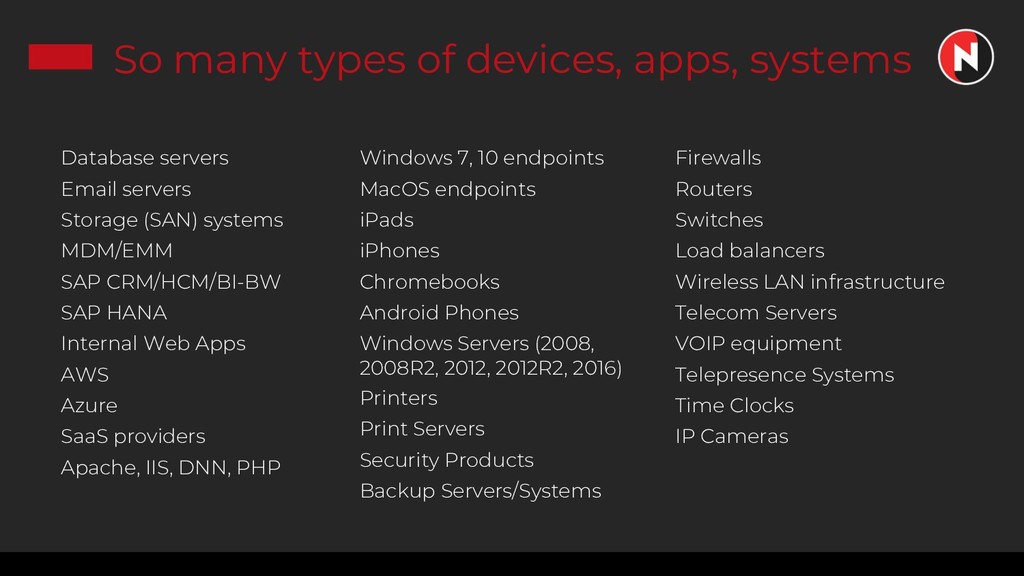
  6. So many types of devices, apps, systems Database servers Email

    servers Storage (SAN) systems MDM/EMM SAP CRM/HCM/BI-BW SAP HANA Internal Web Apps AWS Azure SaaS providers Apache, IIS, DNN, PHP Windows 7, 10 endpoints MacOS endpoints iPads iPhones Chromebooks Android Phones Windows Servers (2008, 2008R2, 2012, 2012R2, 2016) Printers Print Servers Security Products Backup Servers/Systems Firewalls Routers Switches Load balancers Wireless LAN infrastructure Telecom Servers VOIP equipment Telepresence Systems Time Clocks IP Cameras
  7. Inherited Problems and Challenges • Lack of support from board,

    executives, IT... • Employee retention • Abandoned projects • Poorly planned purchases • Legacy systems • Regulatory deadlines • Broken products and processes • Many more!
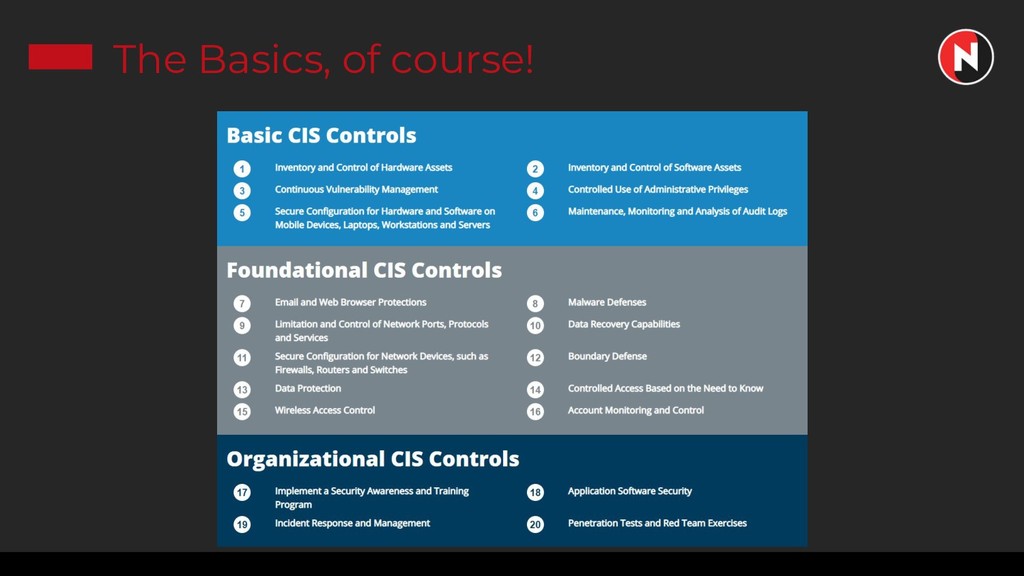
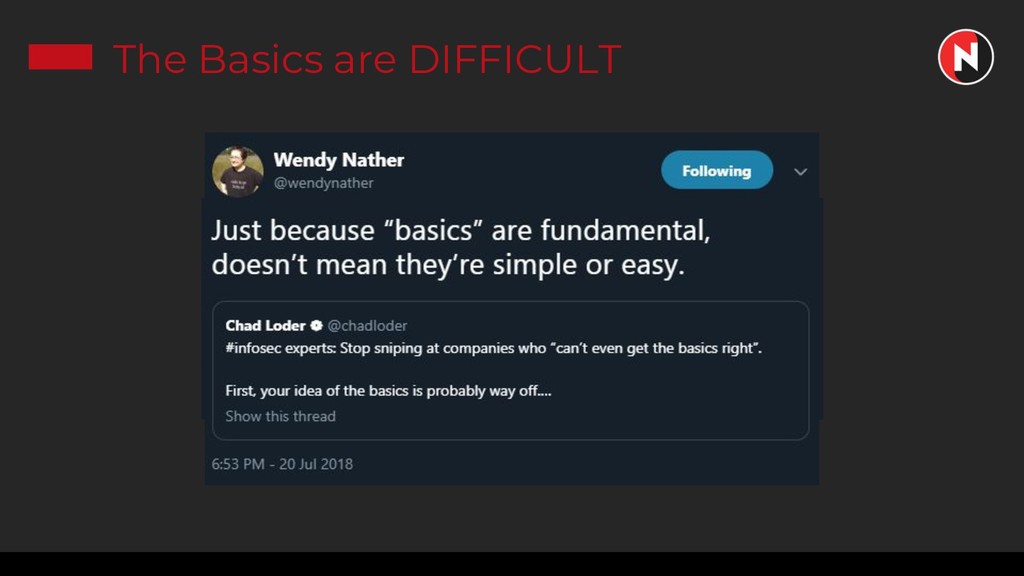
  8. There’s nothing basic about The Basics 1. Inventory and Control

    of Hardware Assets 2. Inventory and Control of Software Assets 3. Continuous Vulnerability Management 4. Controlled Use of Administrative Privileges 5. Secure Configuration for Hardware and Software on Mobile Devices, Laptops, Workstations and Servers 6. Maintenance, Monitoring and Analysis of Audit Logs BASIC?!?
  9. Let’s get MORE basic 1. Inventory and Control of Hardware

    Assets 2. Inventory and Control of Software Assets 3. Continuous Vulnerability Management 4. Controlled Use of Administrative Privileges 5. Secure Configuration for Hardware and Software on Mobile Devices, Laptops, Workstations and Servers 6. Maintenance, Monitoring and Analysis of Audit Logs
  10. Let’s get MORE basic 1. Asset Discovery and Management 2.

    Vulnerability Management 3. Hardening
  11. Don’t focus too much on any one area Some assets

    won’t be targets. Most vulnerabilities aren’t important. Some hardening is overkill. Products can kill progress.
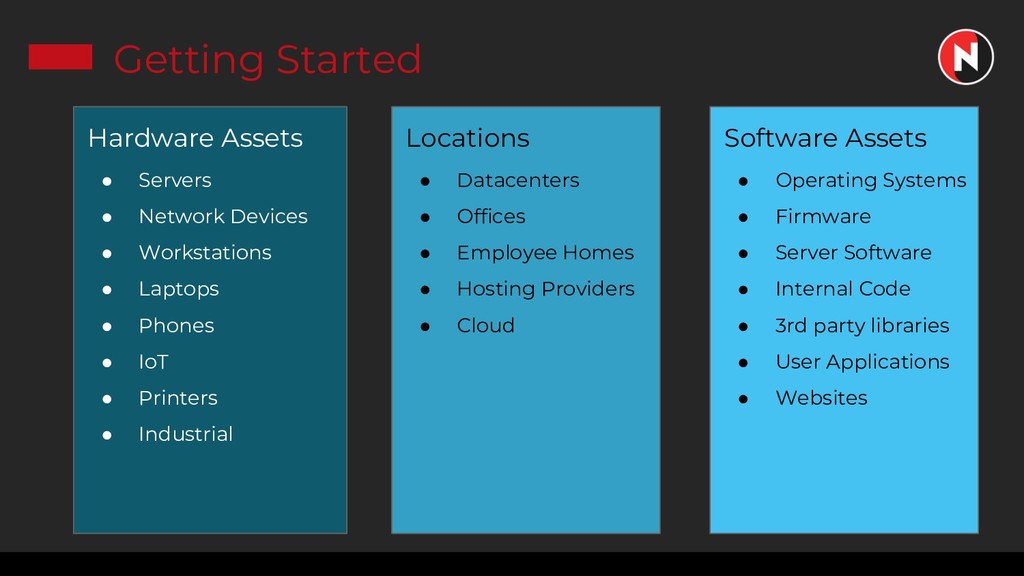
  12. Getting Started Hardware Assets • Servers • Network Devices •

    Workstations • Laptops • Phones • IoT • Printers • Industrial Locations • Datacenters • Offices • Employee Homes • Hosting Providers • Cloud Software Assets • Operating Systems • Firmware • Server Software • Internal Code • 3rd party libraries • User Applications • Websites
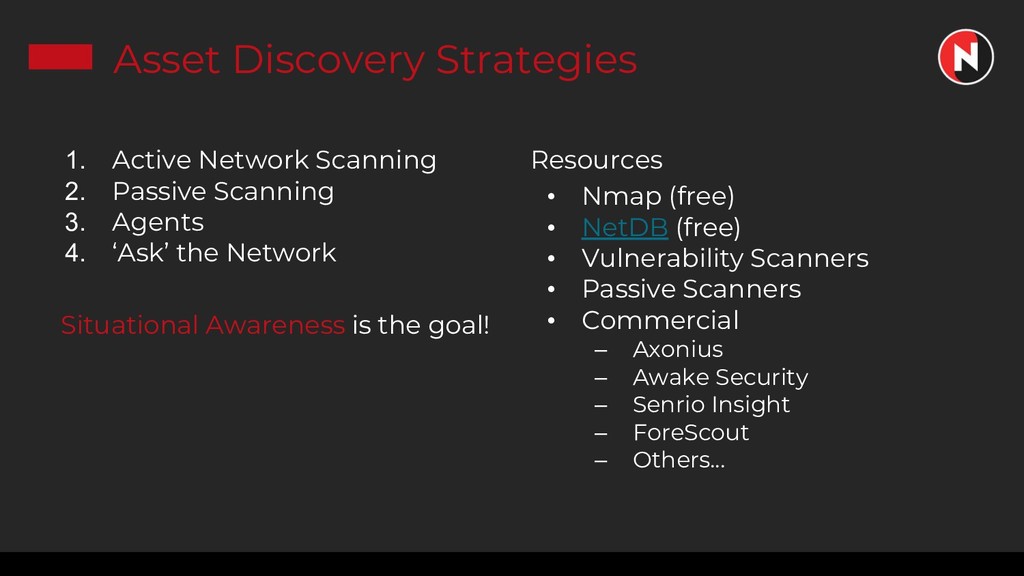
  13. Asset Discovery Strategies 1. Active Network Scanning 2. Passive Scanning

    3. Agents 4. ‘Ask’ the Network Situational Awareness is the goal! Resources • Nmap (free) • NetDB (free) • Vulnerability Scanners • Passive Scanners • Commercial – Axonius – Awake Security – Senrio Insight – ForeScout – Others...
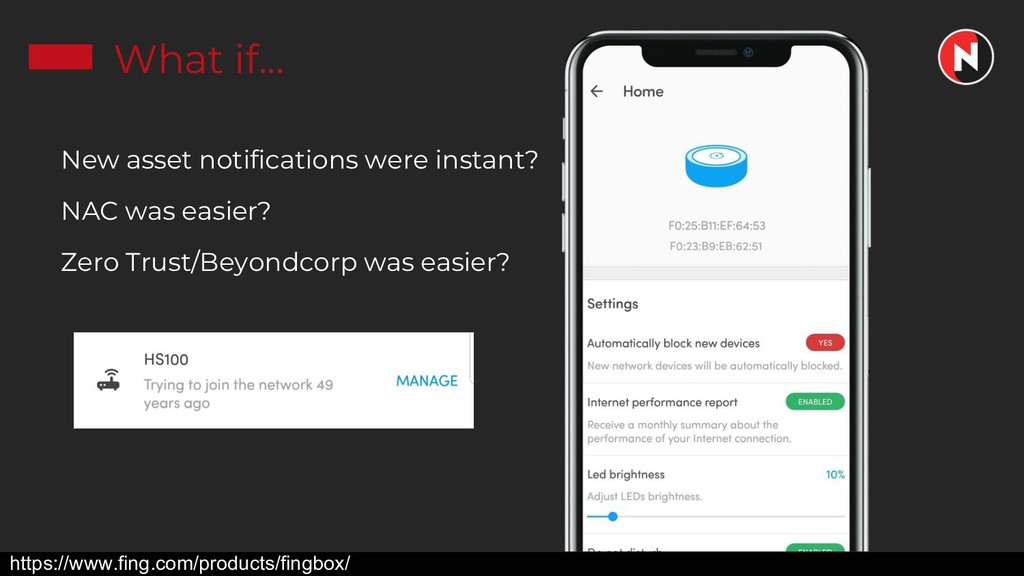
  14. What if... New asset notifications were instant? NAC was easier?

    Zero Trust/Beyondcorp was easier? https://www.fing.com/products/fingbox/
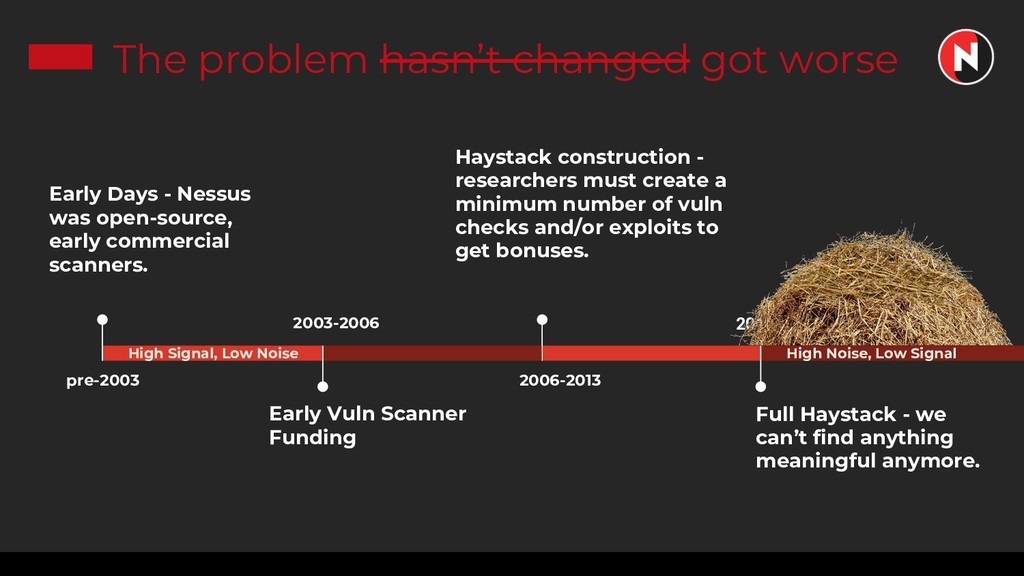
  15. The problem hasn’t changed got worse 2006-2013 Haystack construction -

    researchers must create a minimum number of vuln checks and/or exploits to get bonuses. 2013 - Full Haystack - we can’t find anything meaningful anymore. pre-2003 Early Days - Nessus was open-source, early commercial scanners. 2003-2006 Early Vuln Scanner Funding High Signal, Low Noise High Noise, Low Signal
  16. The problem hasn’t changed got worse Thousands of different kinds

    of assets Hundreds of thousands of unique vulnerabilities Millions of different potential misconfigurations Only a few dozen likely to result in a breach.
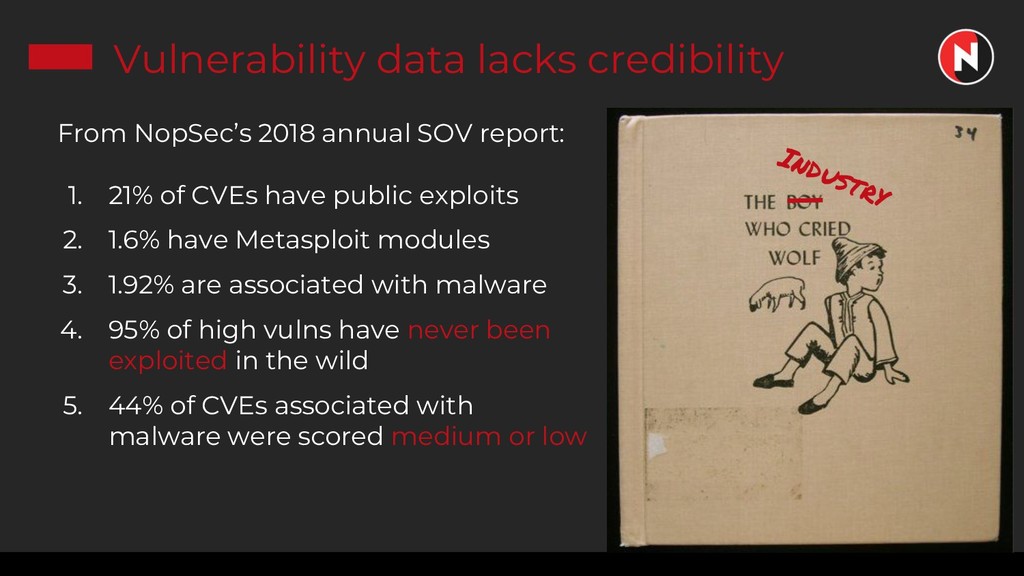
  17. Vulnerability data lacks credibility Industry From NopSec’s 2018 annual SOV

    report: 1. 21% of CVEs have public exploits 2. 1.6% have Metasploit modules 3. 1.92% are associated with malware 4. 95% of high vulns have never been exploited in the wild 5. 44% of CVEs associated with malware were scored medium or low
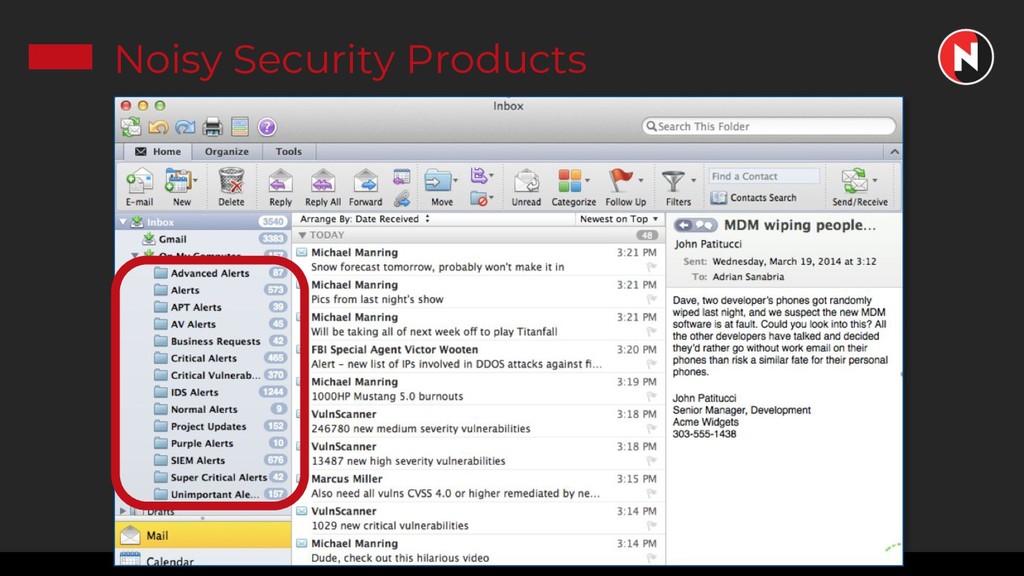
  18. Solutions? Prioritization Is it in Metasploit? Patch quickly when you

    can. Mitigate when you can’t. “Build systems as if there is always a zero day and the patch is never coming.”
  19. How important is hardening? SO IMPORTANT! It costs you nothing.

    It stops most of the attacks. It doesn’t stop zero-day attacks. You probably shouldn’t be worrying about zero-day attacks.
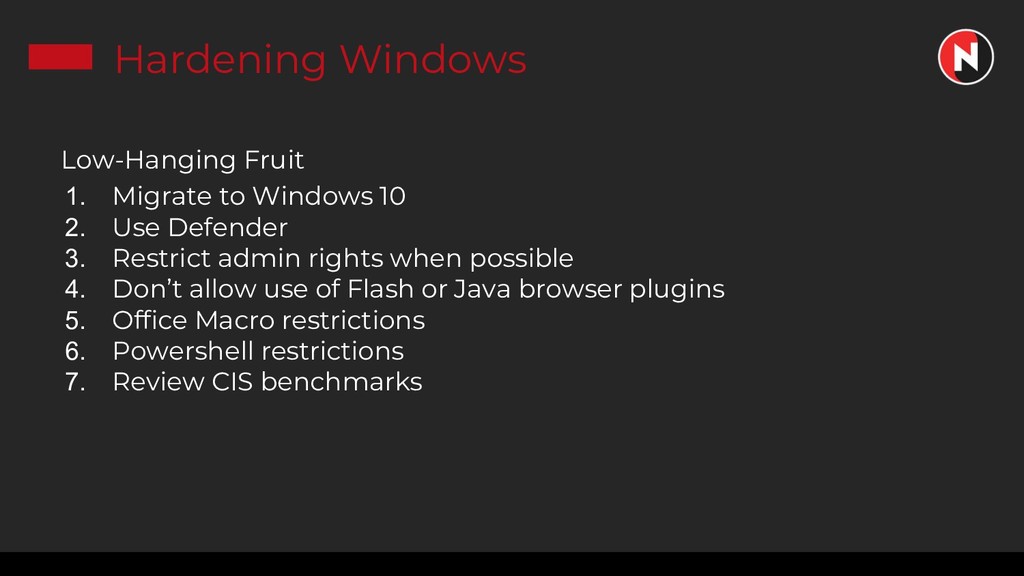
  20. Hardening Windows Low-Hanging Fruit 1. Migrate to Windows 10 2.

    Use Defender 3. Restrict admin rights when possible 4. Don’t allow use of Flash or Java browser plugins 5. Office Macro restrictions 6. Powershell restrictions 7. Review CIS benchmarks
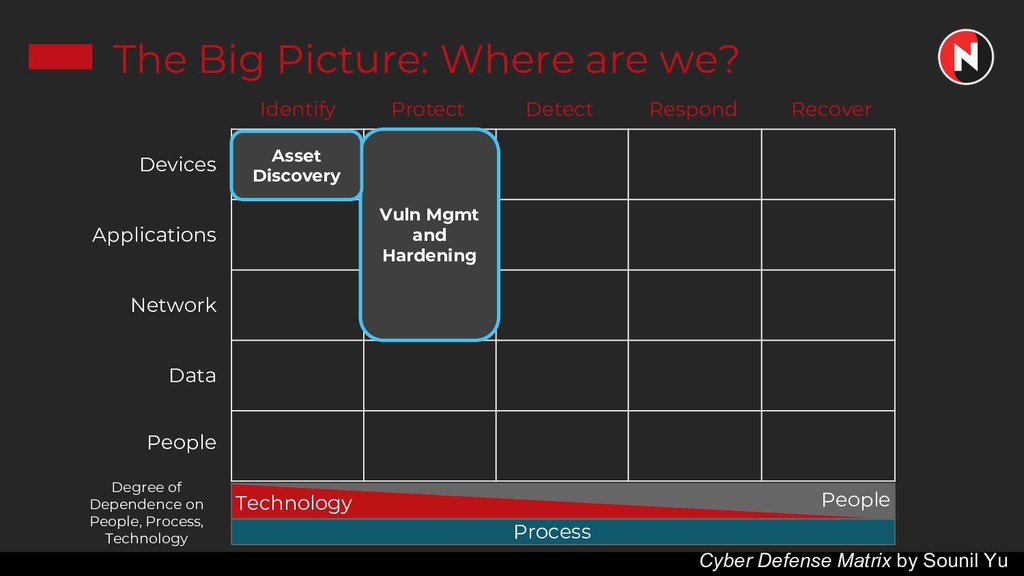
  21. The Big Picture: Where are we? Applications Devices Network Data

    People Identify Recover Respond Detect Protect Process Technology People Degree of Dependence on People, Process, Technology Cyber Defense Matrix by Sounil Yu Vuln Mgmt and Hardening Asset Discovery
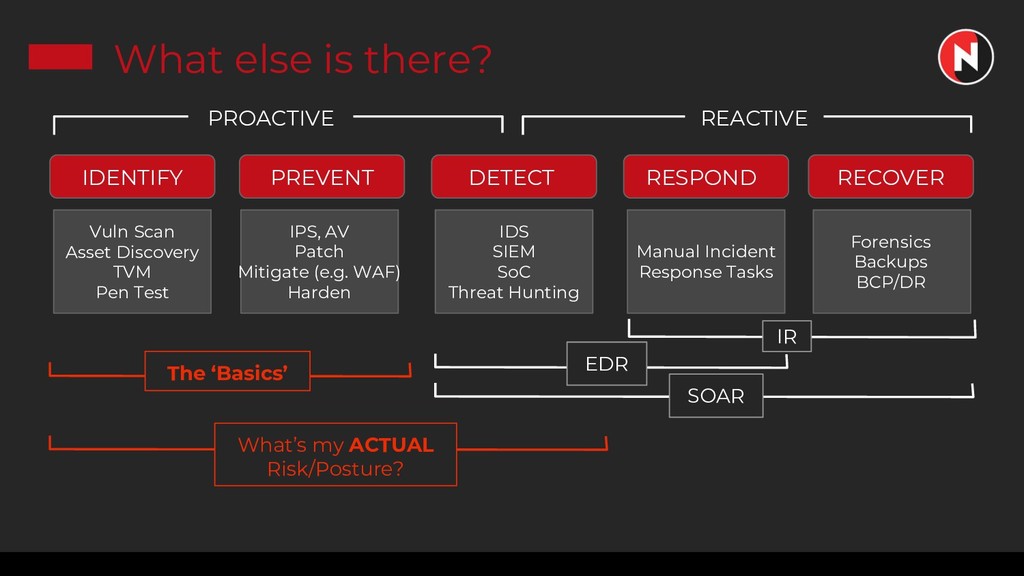
  22. What else is there? Vuln Scan Asset Discovery TVM Pen

    Test IDENTIFY PREVENT DETECT RESPOND RECOVER EDR PROACTIVE REACTIVE IPS, AV Patch Mitigate (e.g. WAF) Harden IDS SIEM SoC Threat Hunting Manual Incident Response Tasks Forensics Backups BCP/DR IR SOAR What’s my ACTUAL Risk/Posture? The ‘Basics’
  23. What else is there? Vuln Scanning, Asset mgmt, CMDB Anti-virus,

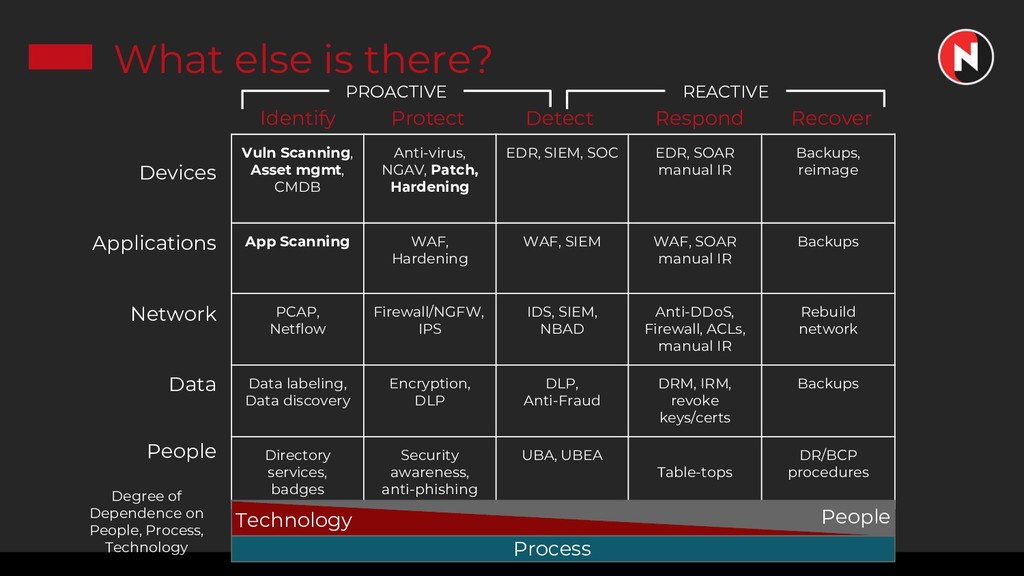
    NGAV, Patch, Hardening EDR, SIEM, SOC EDR, SOAR manual IR Backups, reimage App Scanning WAF, Hardening WAF, SIEM WAF, SOAR manual IR Backups PCAP, Netflow Firewall/NGFW, IPS IDS, SIEM, NBAD Anti-DDoS, Firewall, ACLs, manual IR Rebuild network Data labeling, Data discovery Encryption, DLP DLP, Anti-Fraud DRM, IRM, revoke keys/certs Backups Directory services, badges Security awareness, anti-phishing UBA, UBEA Table-tops DR/BCP procedures Applications Devices Network Data People Identify Recover Respond Detect Protect Process Technology People Degree of Dependence on People, Process, Technology PROACTIVE REACTIVE
  24. Change your perspective “Attackers only have to succeed once -

    defenders can never make a mistake!” “There’s two types of companies: those that have been breached and those that don’t yet know they’ve been breached.”
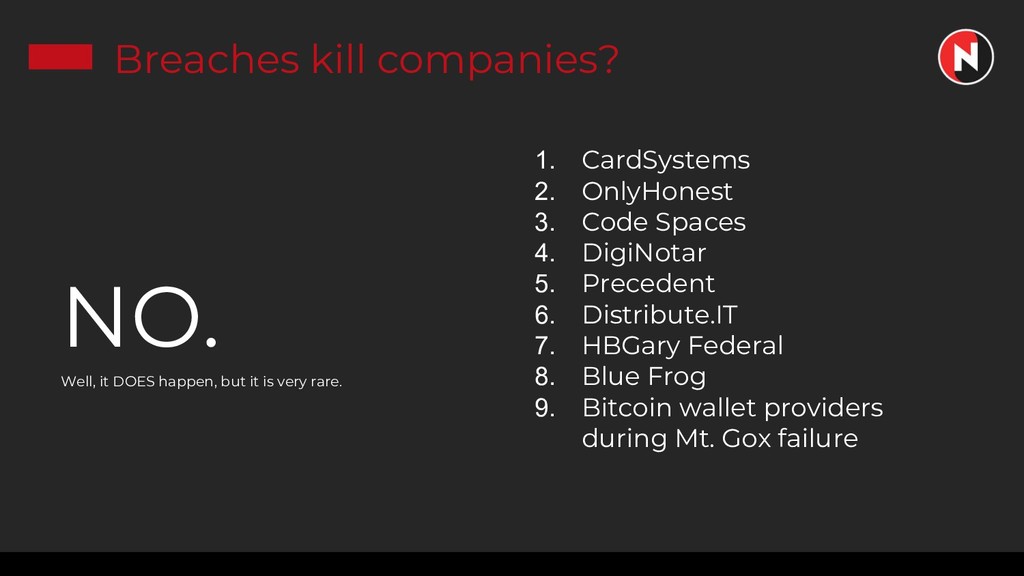
  25. Breaches kill companies? NO. Well, it DOES happen, but it

    is very rare. 1. CardSystems 2. OnlyHonest 3. Code Spaces 4. DigiNotar 5. Precedent 6. Distribute.IT 7. HBGary Federal 8. Blue Frog 9. Bitcoin wallet providers during Mt. Gox failure
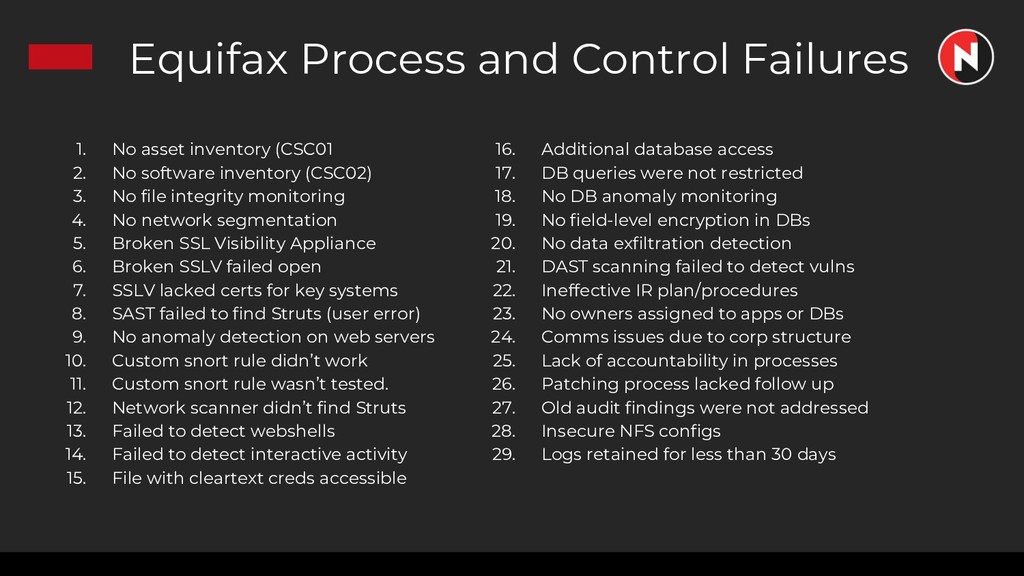
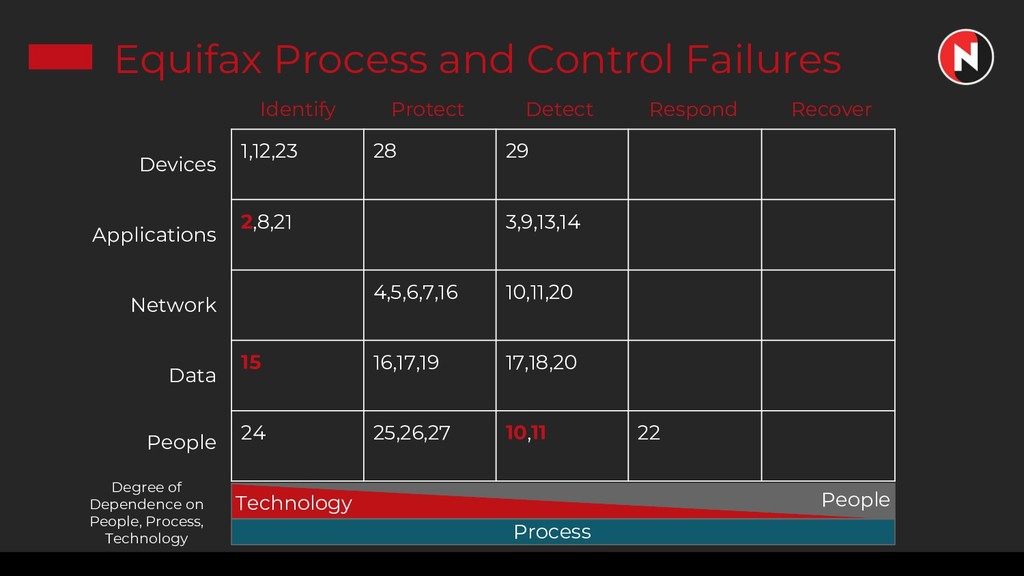
  26. Equifax Process and Control Failures 1. No asset inventory (CSC01

    2. No software inventory (CSC02) 3. No file integrity monitoring 4. No network segmentation 5. Broken SSL Visibility Appliance 6. Broken SSLV failed open 7. SSLV lacked certs for key systems 8. SAST failed to find Struts (user error) 9. No anomaly detection on web servers 10. Custom snort rule didn’t work 11. Custom snort rule wasn’t tested. 12. Network scanner didn’t find Struts 13. Failed to detect webshells 14. Failed to detect interactive activity 15. File with cleartext creds accessible 16. Additional database access 17. DB queries were not restricted 18. No DB anomaly monitoring 19. No field-level encryption in DBs 20. No data exfiltration detection 21. DAST scanning failed to detect vulns 22. Ineffective IR plan/procedures 23. No owners assigned to apps or DBs 24. Comms issues due to corp structure 25. Lack of accountability in processes 26. Patching process lacked follow up 27. Old audit findings were not addressed 28. Insecure NFS configs 29. Logs retained for less than 30 days
  27. Equifax Process and Control Failures 1,12,23 28 29 2,8,21 3,9,13,14

    4,5,6,7,16 10,11,20 15 16,17,19 17,18,20 24 25,26,27 10,11 22 Applications Devices Network Data People Identify Recover Respond Detect Protect Process Technology People Degree of Dependence on People, Process, Technology
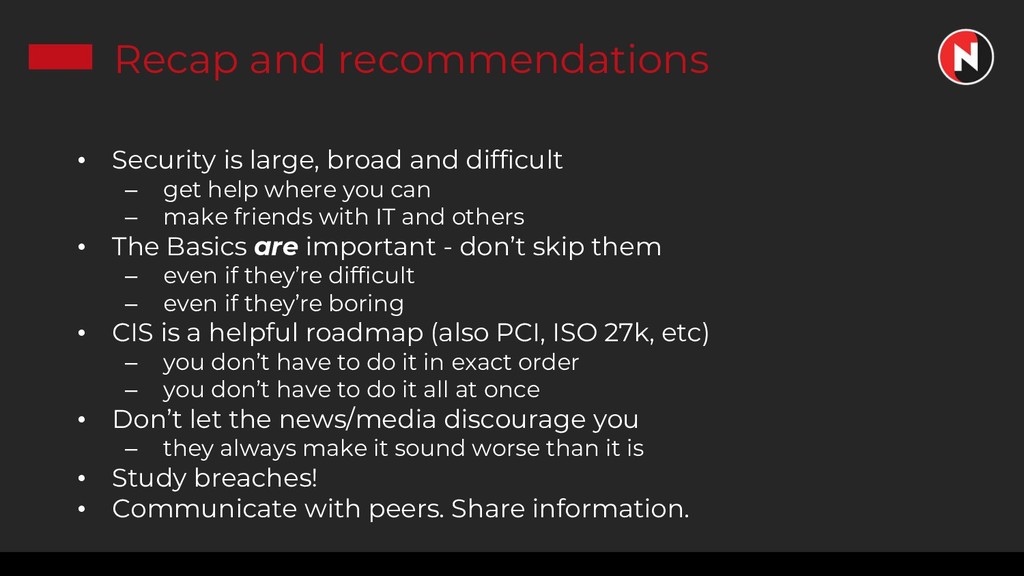
  28. Recap and recommendations • Security is large, broad and difficult

    – get help where you can – make friends with IT and others • The Basics are important - don’t skip them – even if they’re difficult – even if they’re boring • CIS is a helpful roadmap (also PCI, ISO 27k, etc) – you don’t have to do it in exact order – you don’t have to do it all at once • Don’t let the news/media discourage you – they always make it sound worse than it is • Study breaches! • Communicate with peers. Share information.
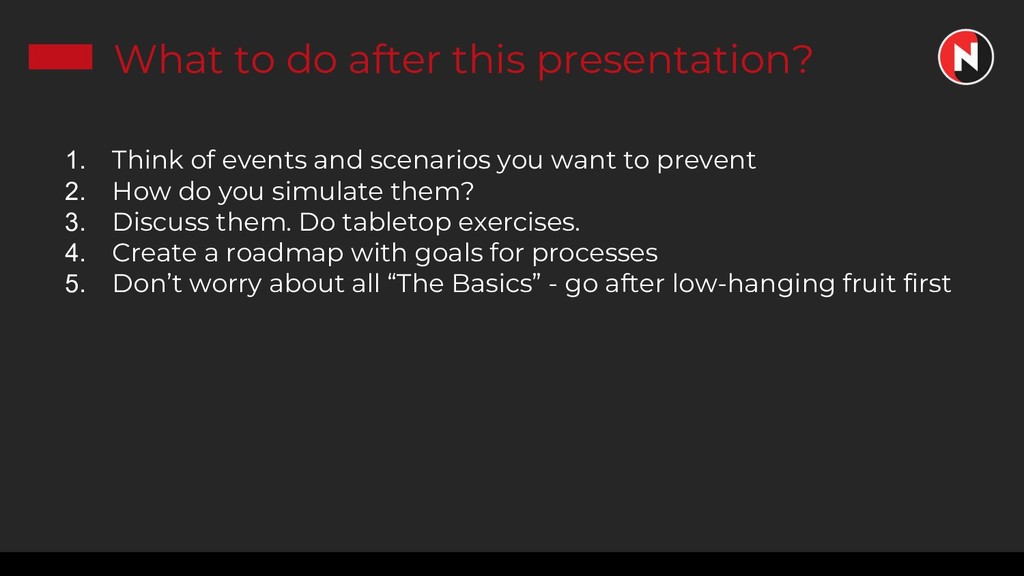
  29. What to do after this presentation? 1. Think of events

    and scenarios you want to prevent 2. How do you simulate them? 3. Discuss them. Do tabletop exercises. 4. Create a roadmap with goals for processes 5. Don’t worry about all “The Basics” - go after low-hanging fruit first
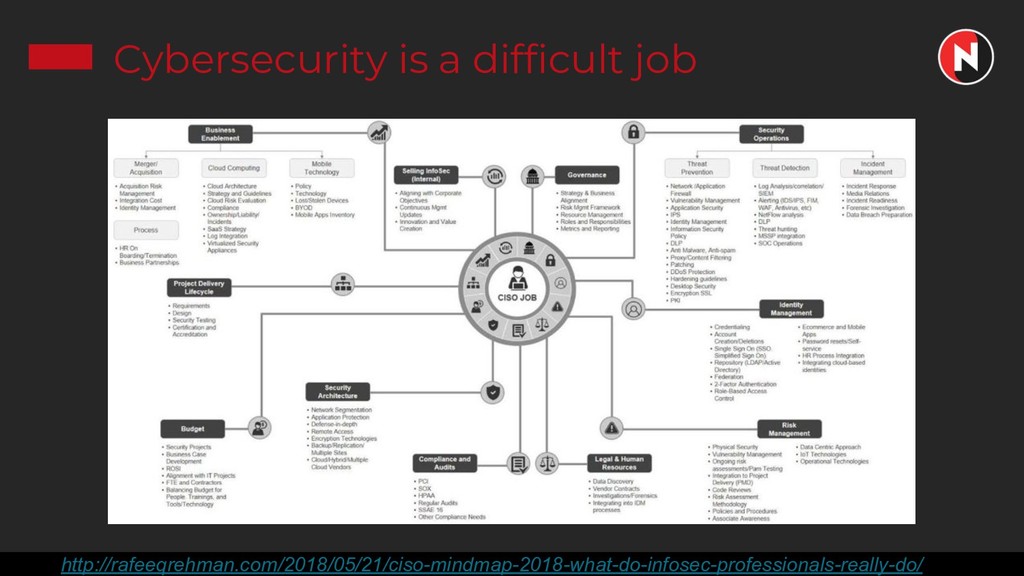
  30. Bonus Resources! Breach Impact Report Sample CISO Mind Map CISO

    Guide to Working with Startups Scan the QR code for handouts OR email [email protected] with TacticalEdge2019 as the subject.