Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Penetration Testing 101: A Complete Guide for B...

Avatar for SecurifyEdge SecurifyEdge
August 24, 2026
4

Penetration Testing 101: A Complete Guide for Businesses | Securify Edge

Learn the fundamentals of penetration testing and discover how businesses can identify and address real security weaknesses before attackers exploit them.

In this guide, you'll learn:

What penetration testing is
The difference between a vulnerability scan and a real pentest
Different types of penetration testing
The penetration testing process
How to properly scope a pentest
What a good penetration testing report should include
How often your business should conduct testing
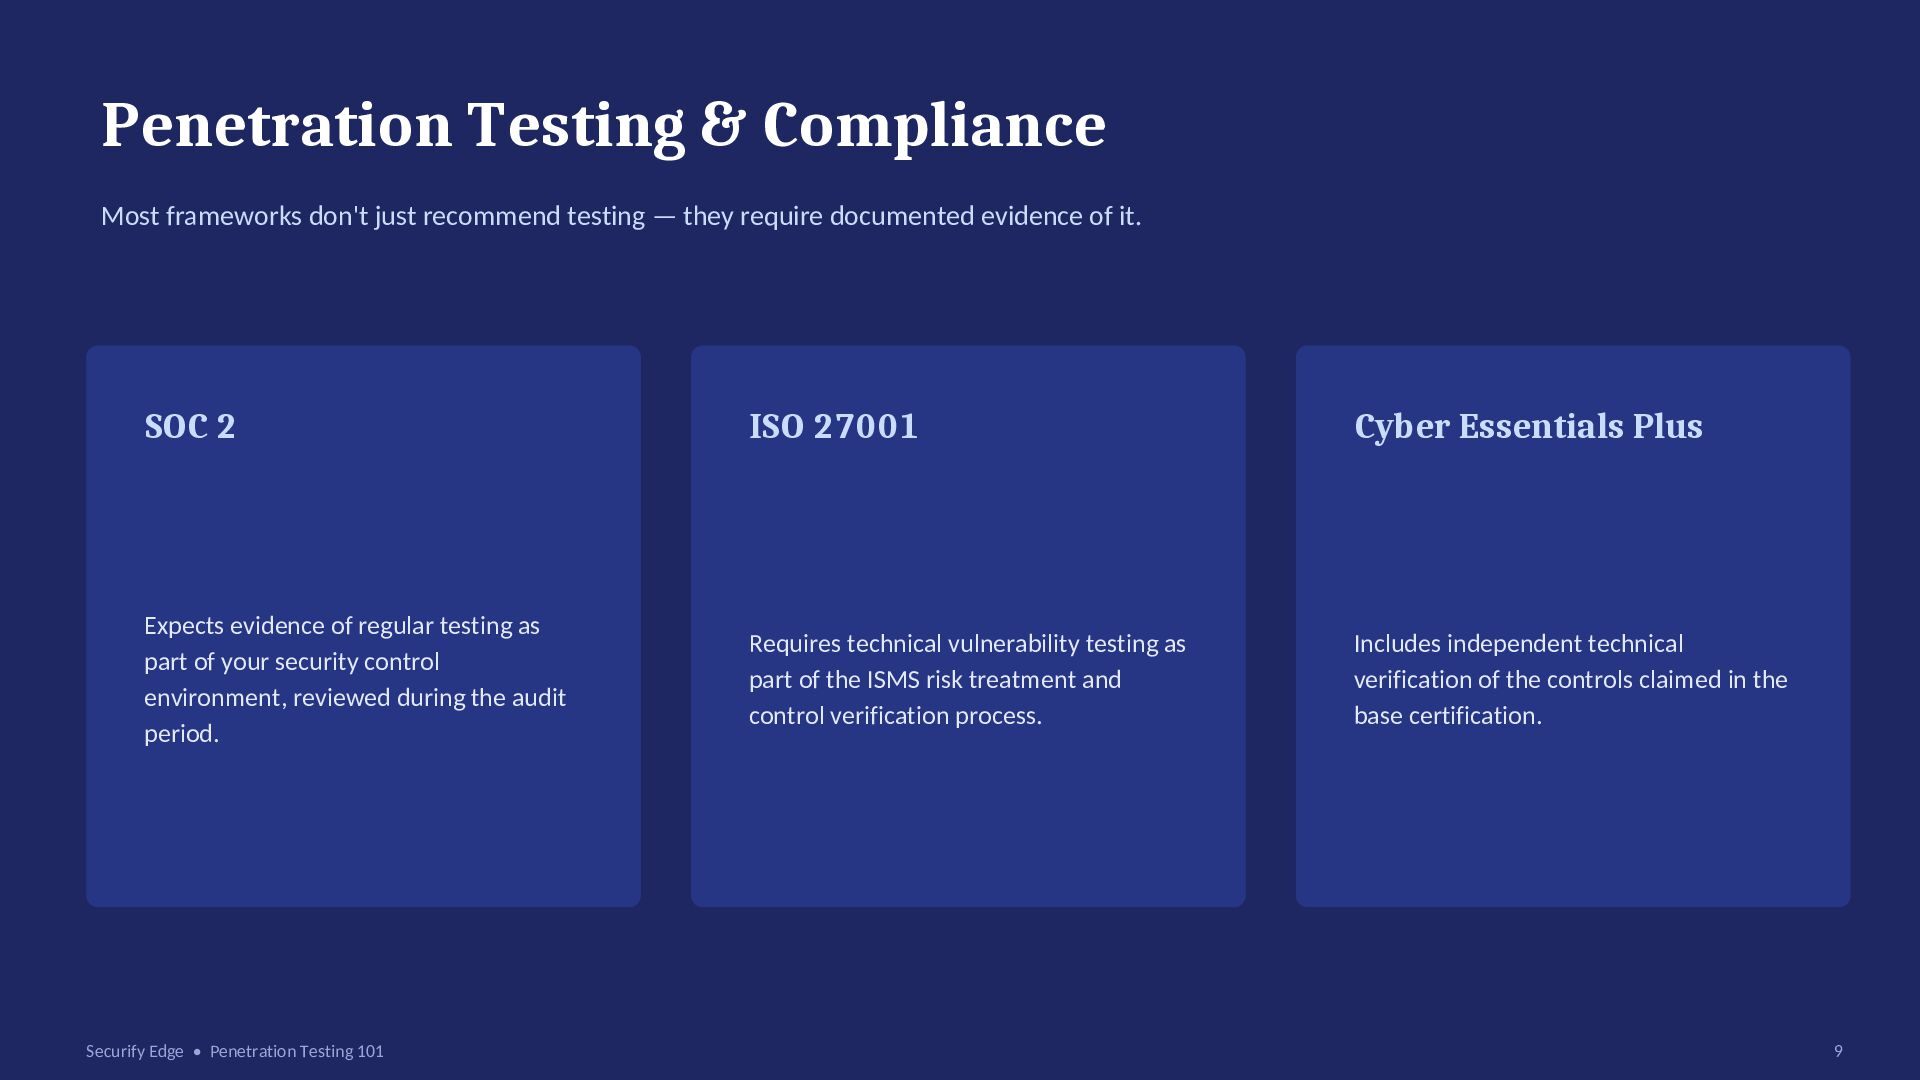
The role of penetration testing in SOC 2, ISO 27001, and Cyber Essentials compliance
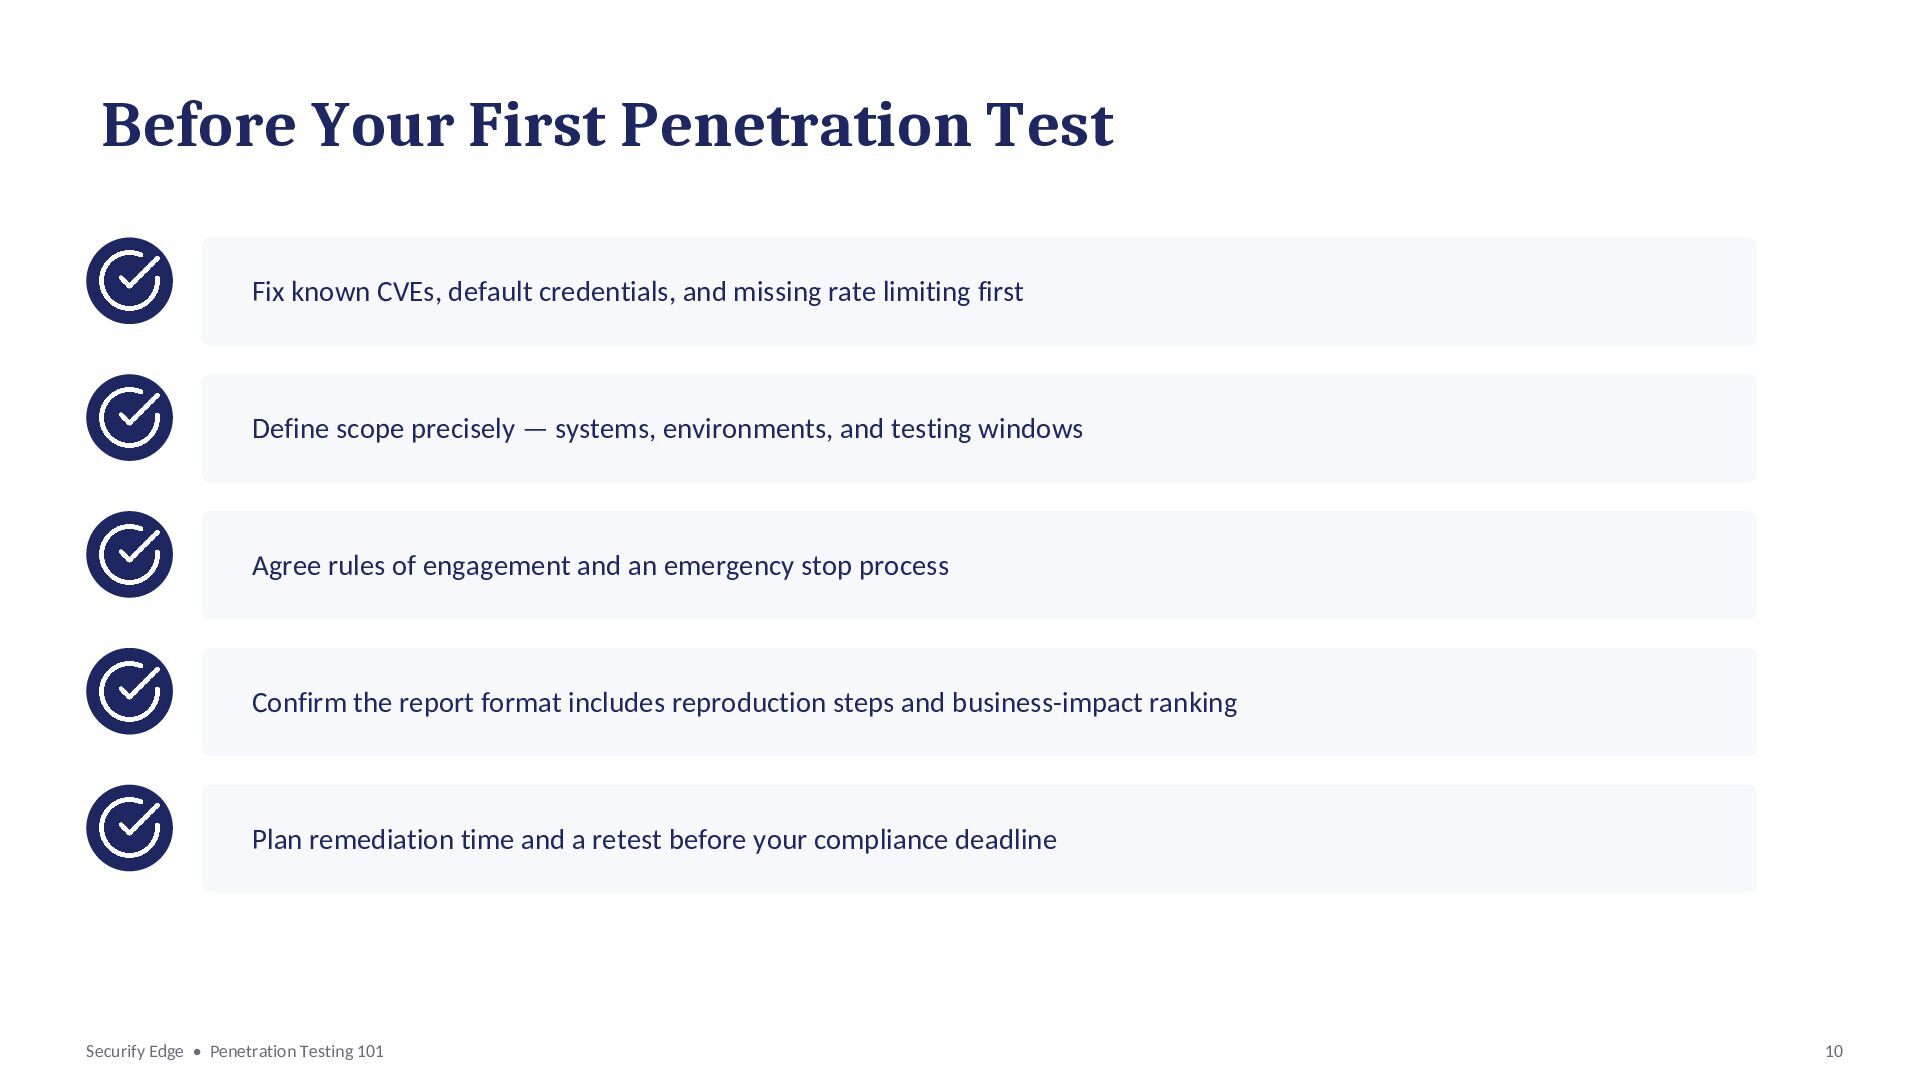
What to prepare before your first penetration test

Penetration testing is more than running an automated vulnerability scan. A real pentest uses controlled, human-led testing to identify how multiple weaknesses could be chained together and what impact they could have on your business.

Explore our Penetration Testing Services:
Securify Edge Penetration Testing Services

#PenetrationTesting #CyberSecurity #VAPT #InformationSecurity #SOC2 #ISO27001 #CyberSecurityAwareness #SecurifyEdge

Avatar for SecurifyEdge

SecurifyEdge

August 24, 2026

Transcript

  1. SECURIFY EDGE Penetration Testing 101 A practical guide for businesses

    evaluating, scoping, and acting on penetration testing securifyedge.com/services/penetration-testing-services/
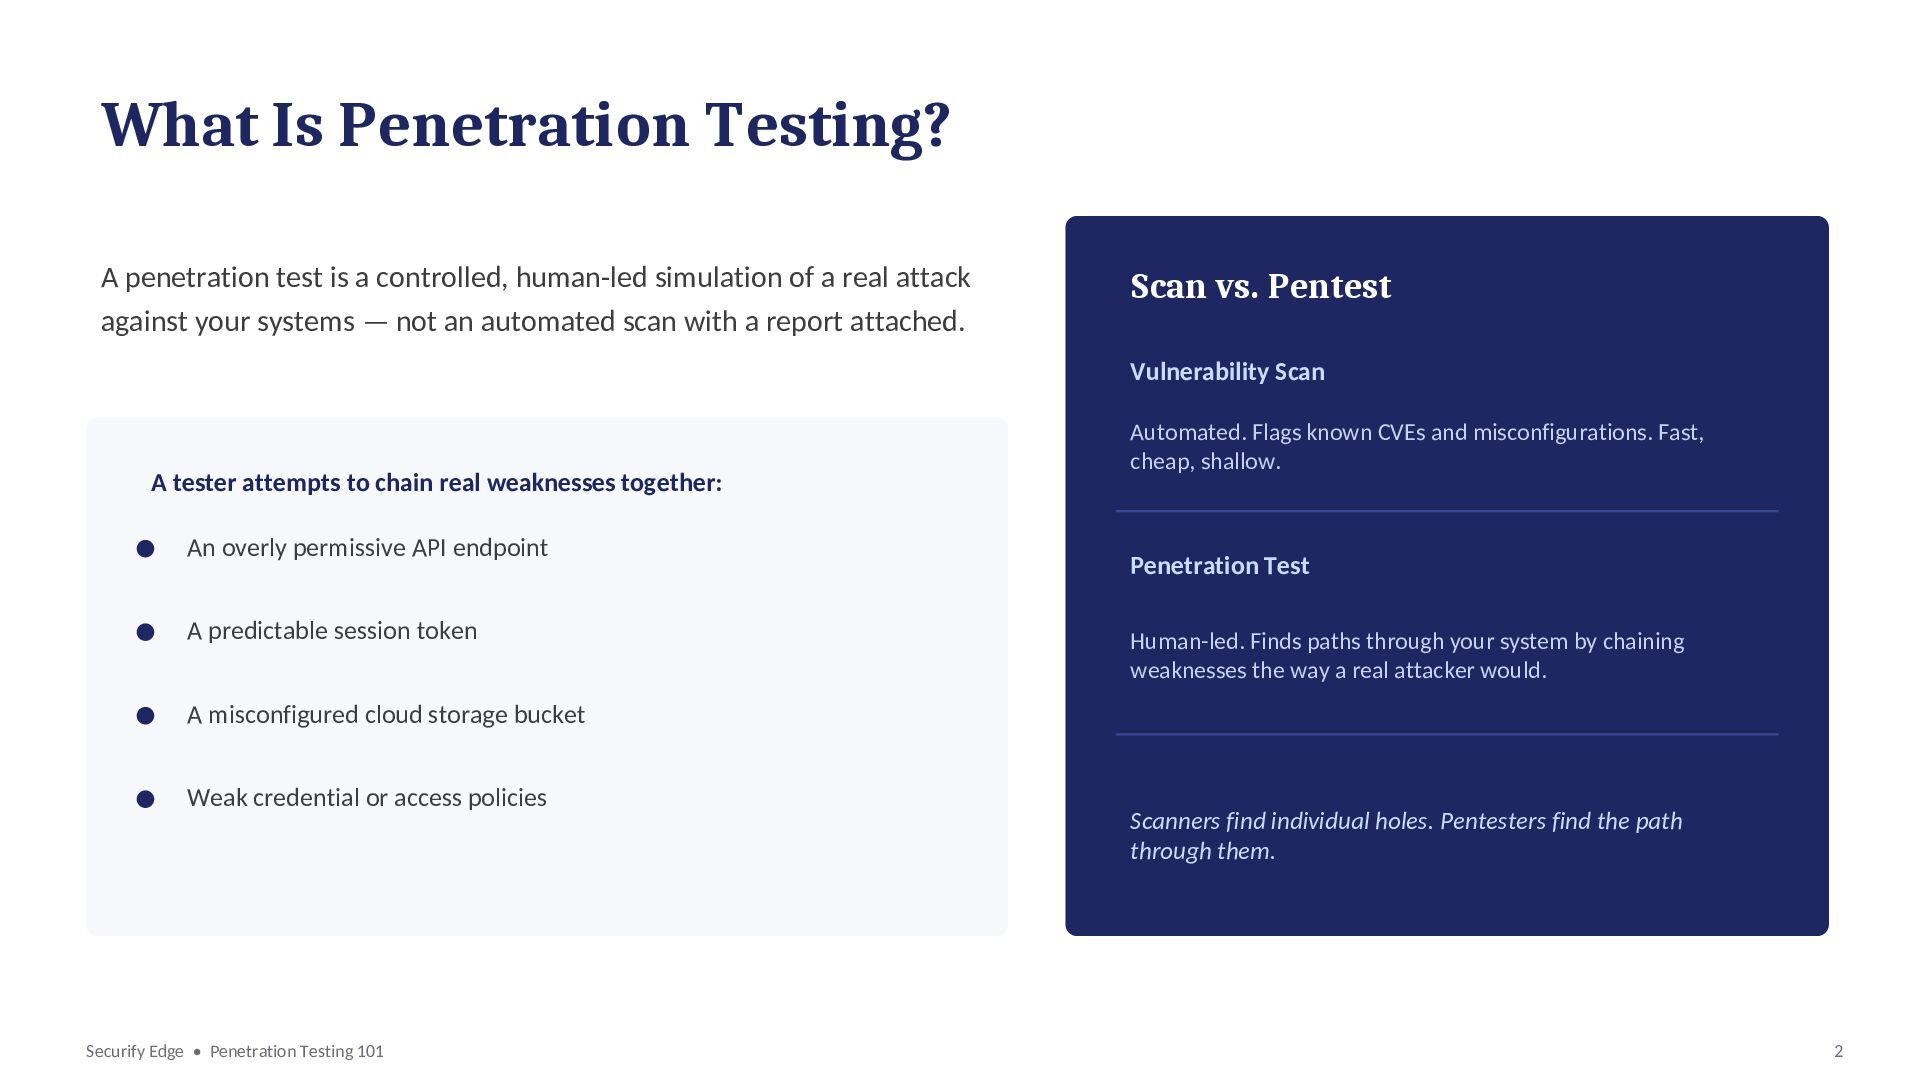
  2. What Is Penetration Testing? A penetration test is a controlled,

    human-led simulation of a real attack against your systems — not an automated scan with a report attached. A tester attempts to chain real weaknesses together: An overly permissive API endpoint A predictable session token A misconfigured cloud storage bucket Weak credential or access policies Securify Edge • Penetration Testing 101 Scan vs. Pentest Vulnerability Scan Automated. Flags known CVEs and misconfigurations. Fast, cheap, shallow. Penetration Test Human-led. Finds paths through your system by chaining weaknesses the way a real attacker would. Scanners find individual holes. Pentesters find the path through them. 2
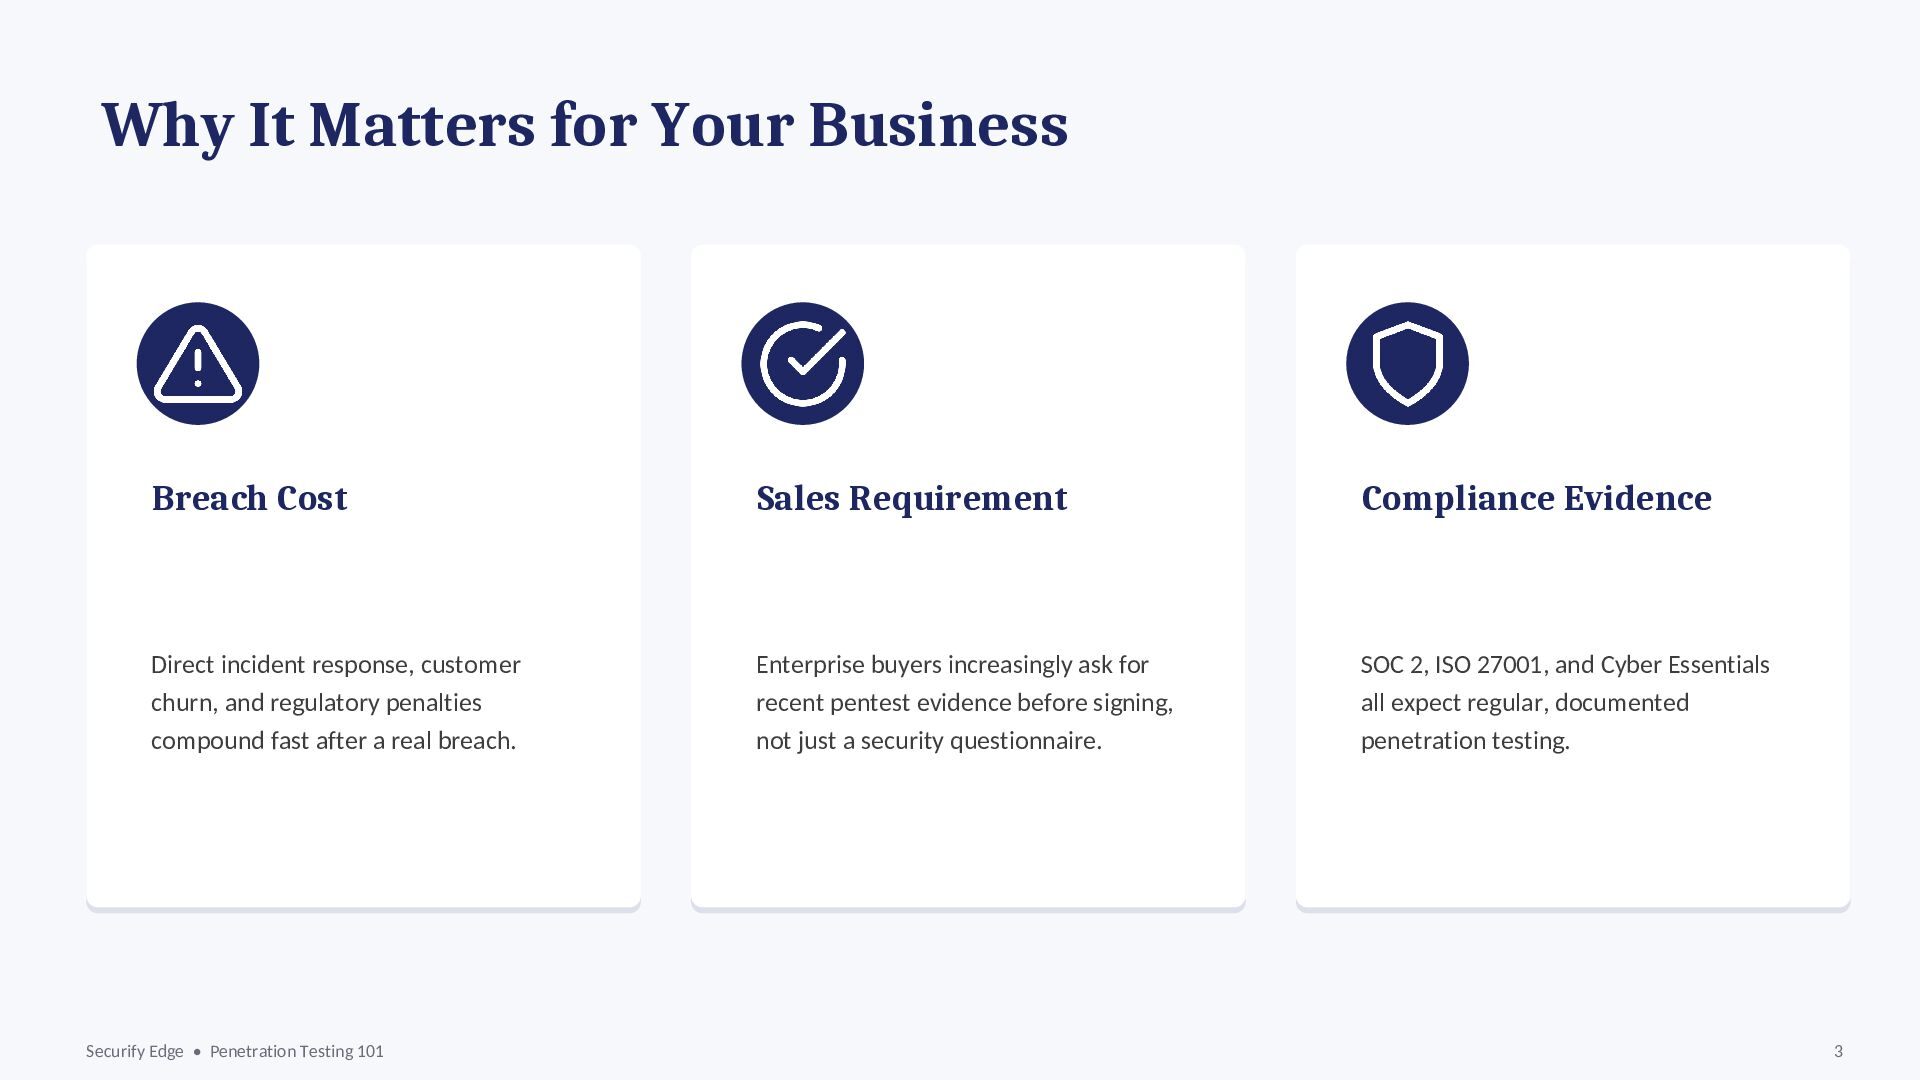
  3. Why It Matters for Your Business Breach Cost Sales Requirement

    Compliance Evidence Direct incident response, customer churn, and regulatory penalties compound fast after a real breach. Enterprise buyers increasingly ask for recent pentest evidence before signing, not just a security questionnaire. SOC 2, ISO 27001, and Cyber Essentials all expect regular, documented penetration testing. Securify Edge • Penetration Testing 101 3
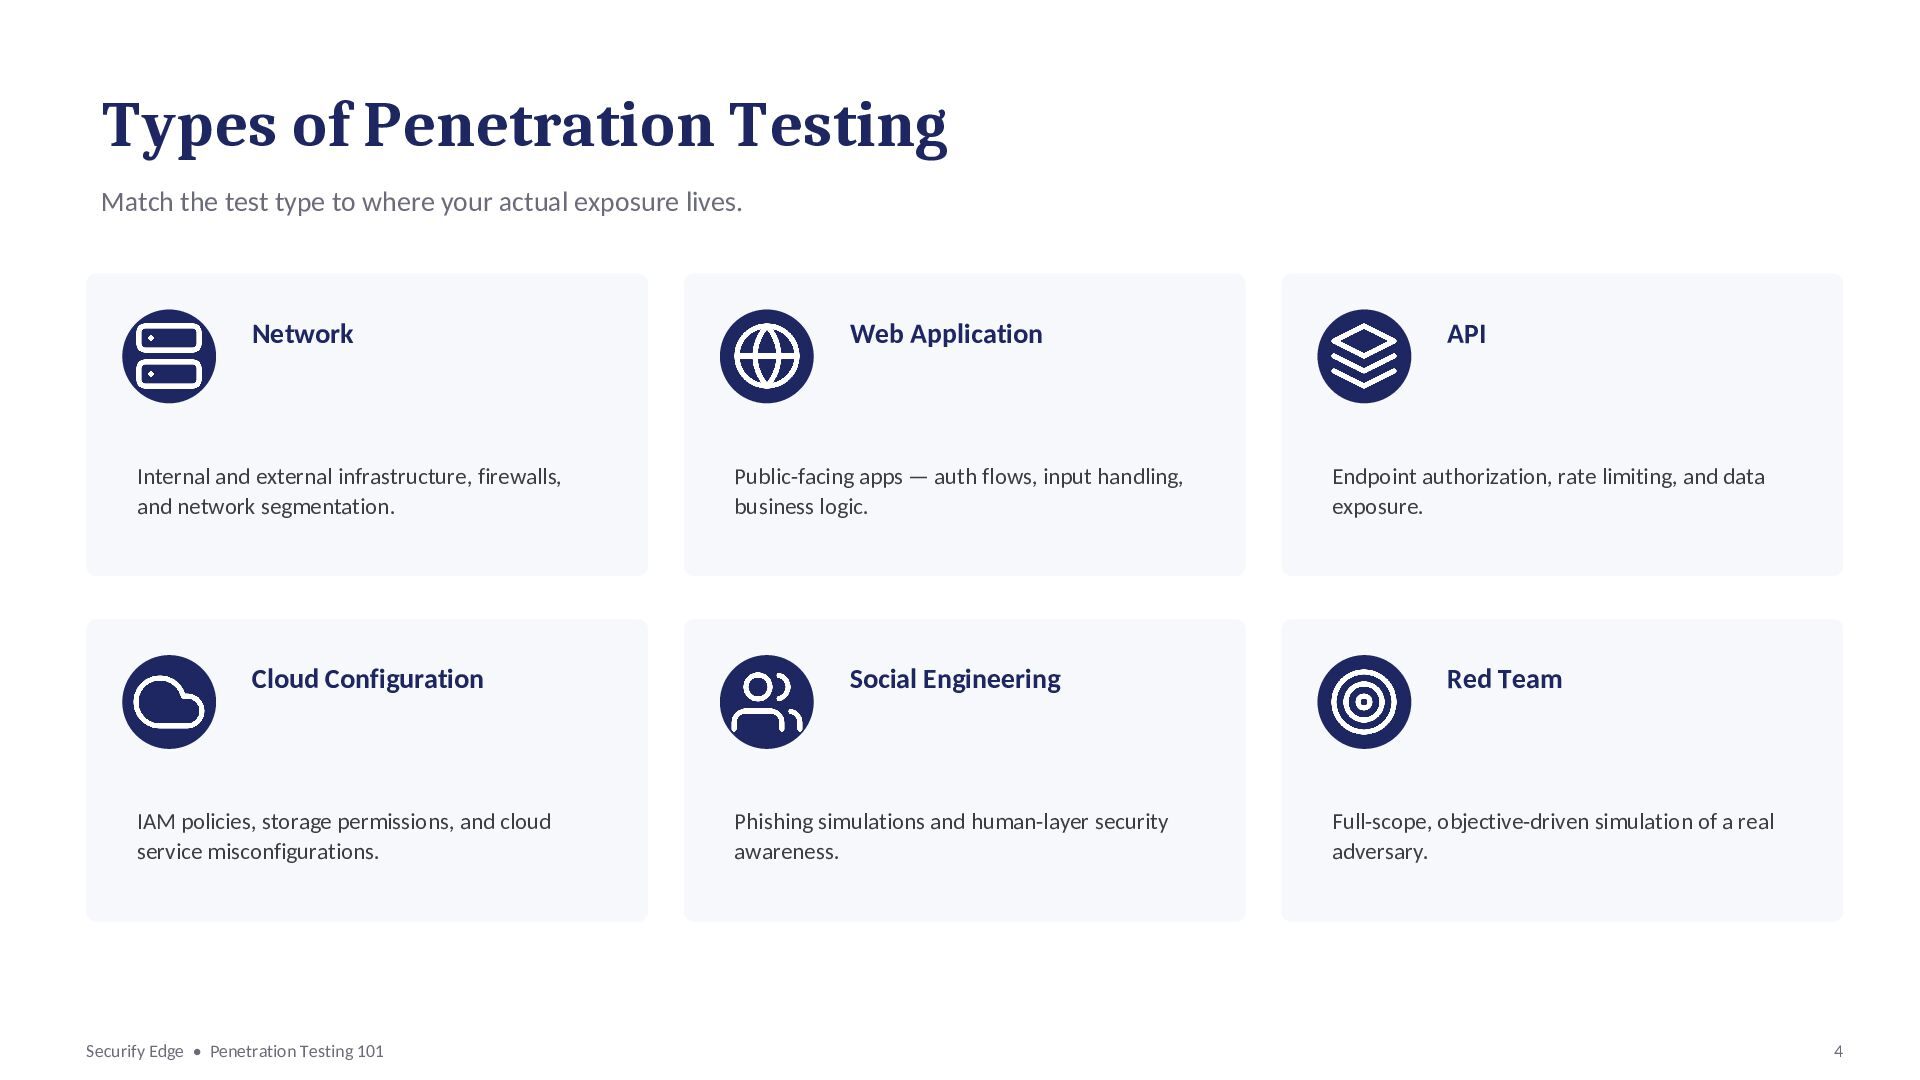
  4. Types of Penetration Testing Match the test type to where

    your actual exposure lives. Network Internal and external infrastructure, firewalls, and network segmentation. Cloud Configuration IAM policies, storage permissions, and cloud service misconfigurations. Securify Edge • Penetration Testing 101 Web Application Public-facing apps — auth flows, input handling, business logic. Social Engineering Phishing simulations and human-layer security awareness. API Endpoint authorization, rate limiting, and data exposure. Red Team Full-scope, objective-driven simulation of a real adversary. 4
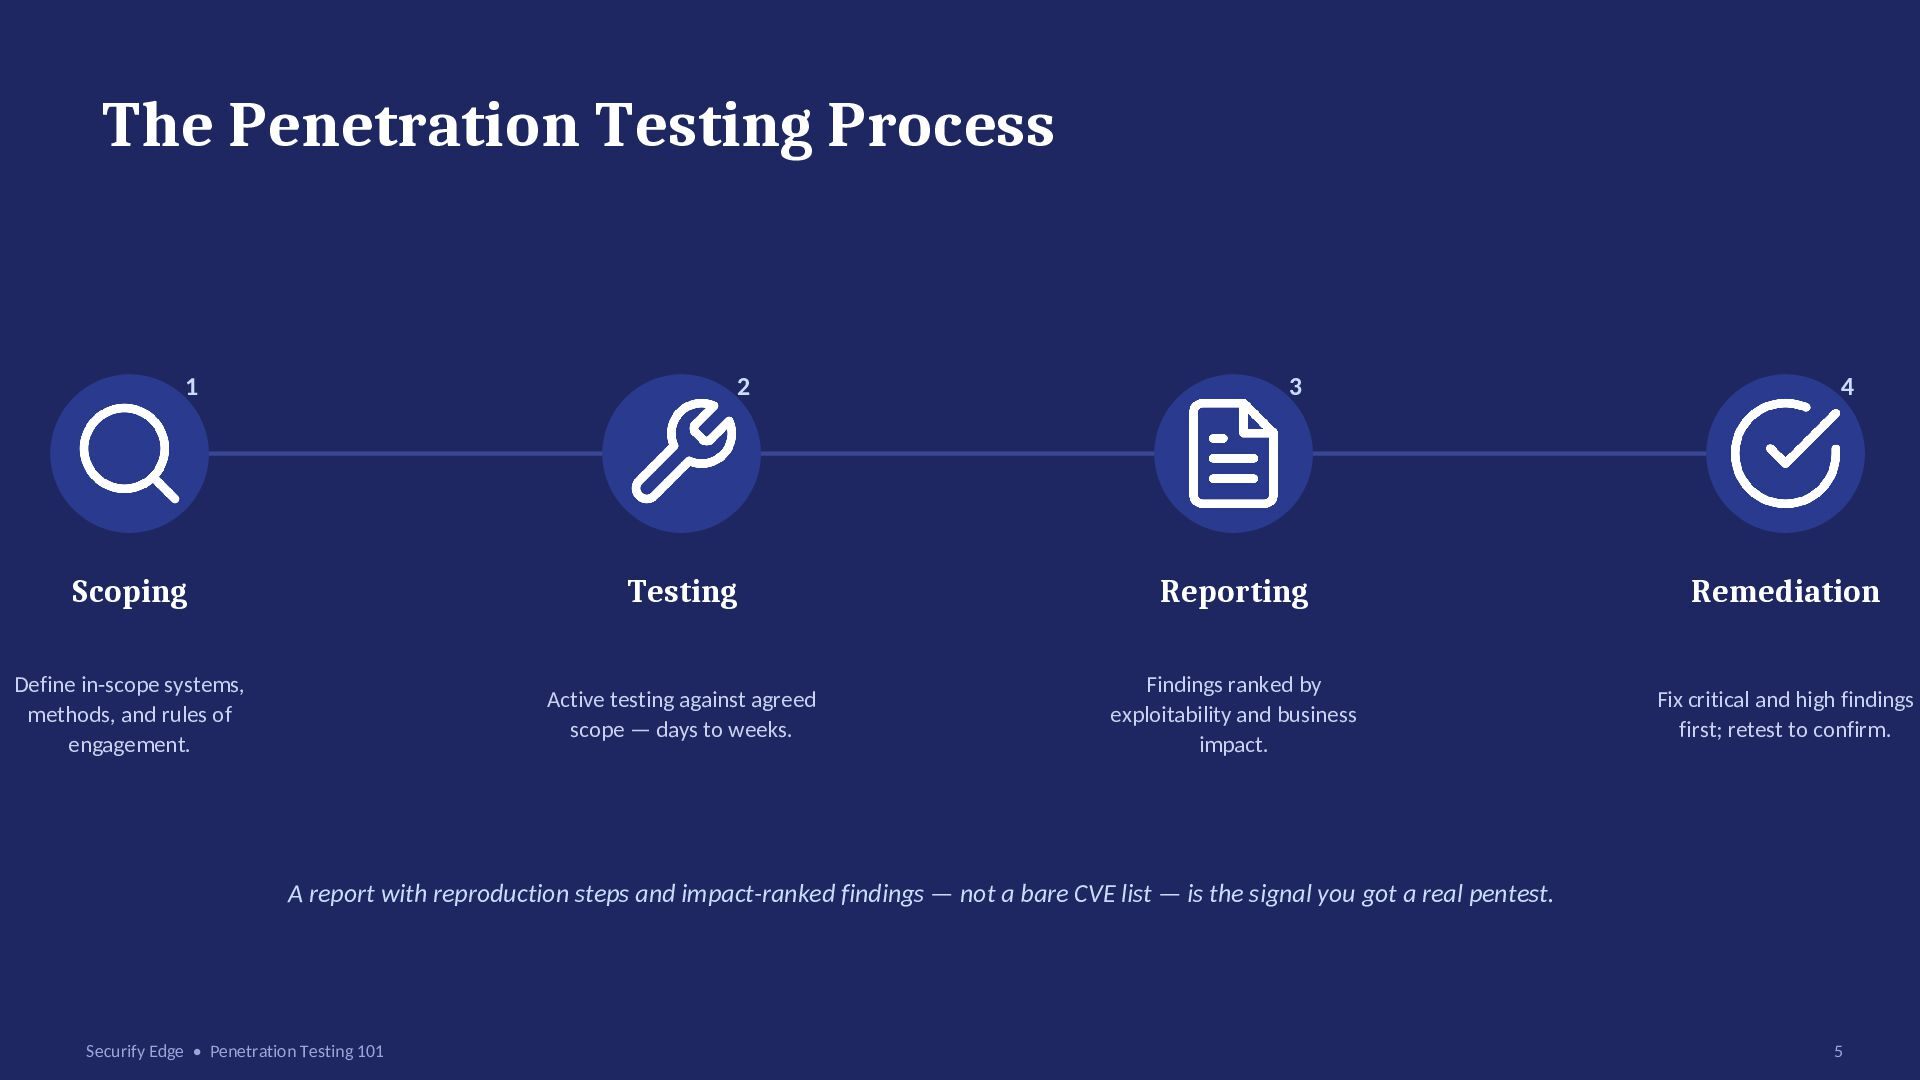
  5. The Penetration Testing Process 1 2 3 4 Scoping Testing

    Reporting Remediation Define in-scope systems, methods, and rules of engagement. Active testing against agreed scope — days to weeks. Findings ranked by exploitability and business impact. Fix critical and high findings first; retest to confirm. A report with reproduction steps and impact-ranked findings — not a bare CVE list — is the signal you got a real pentest. Securify Edge • Penetration Testing 101 5
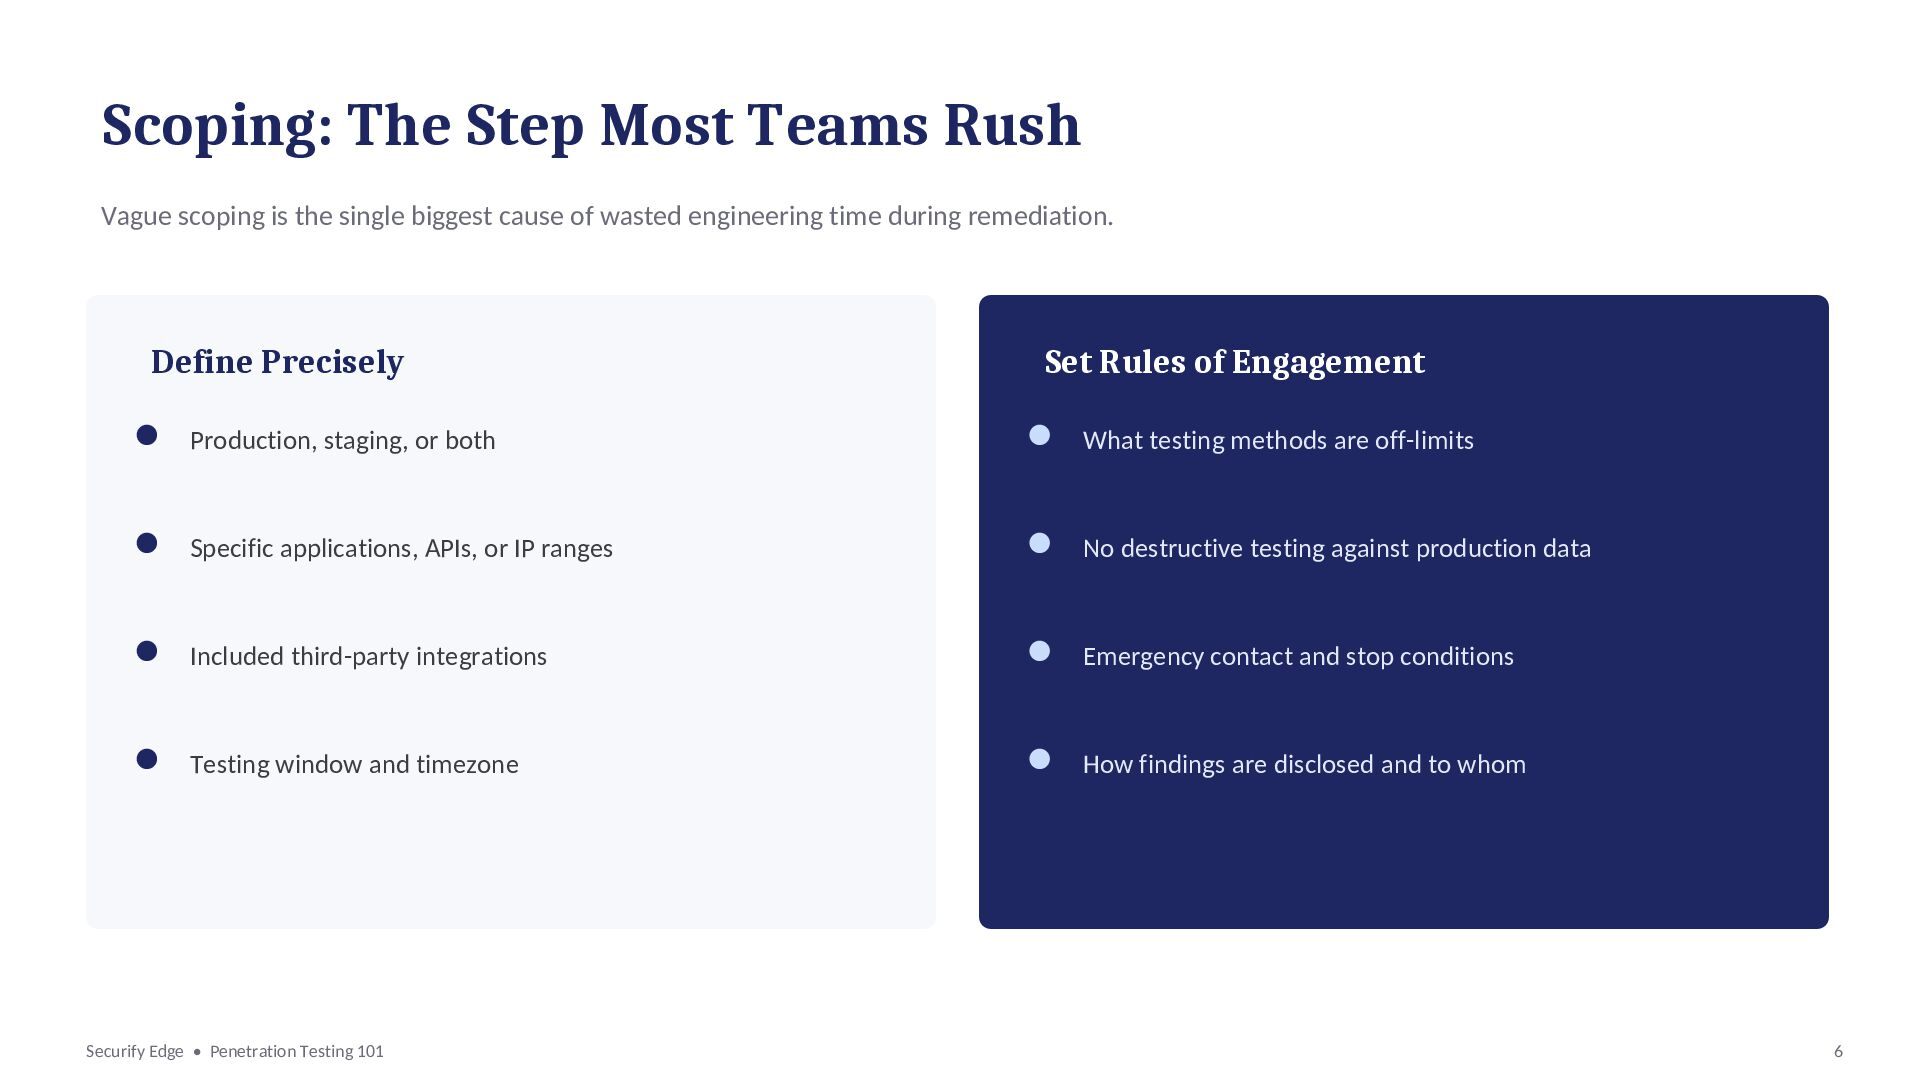
  6. Scoping: The Step Most Teams Rush Vague scoping is the

    single biggest cause of wasted engineering time during remediation. Define Precisely Set Rules of Engagement Production, staging, or both What testing methods are off-limits Specific applications, APIs, or IP ranges No destructive testing against production data Included third-party integrations Emergency contact and stop conditions Testing window and timezone How findings are disclosed and to whom Securify Edge • Penetration Testing 101 6
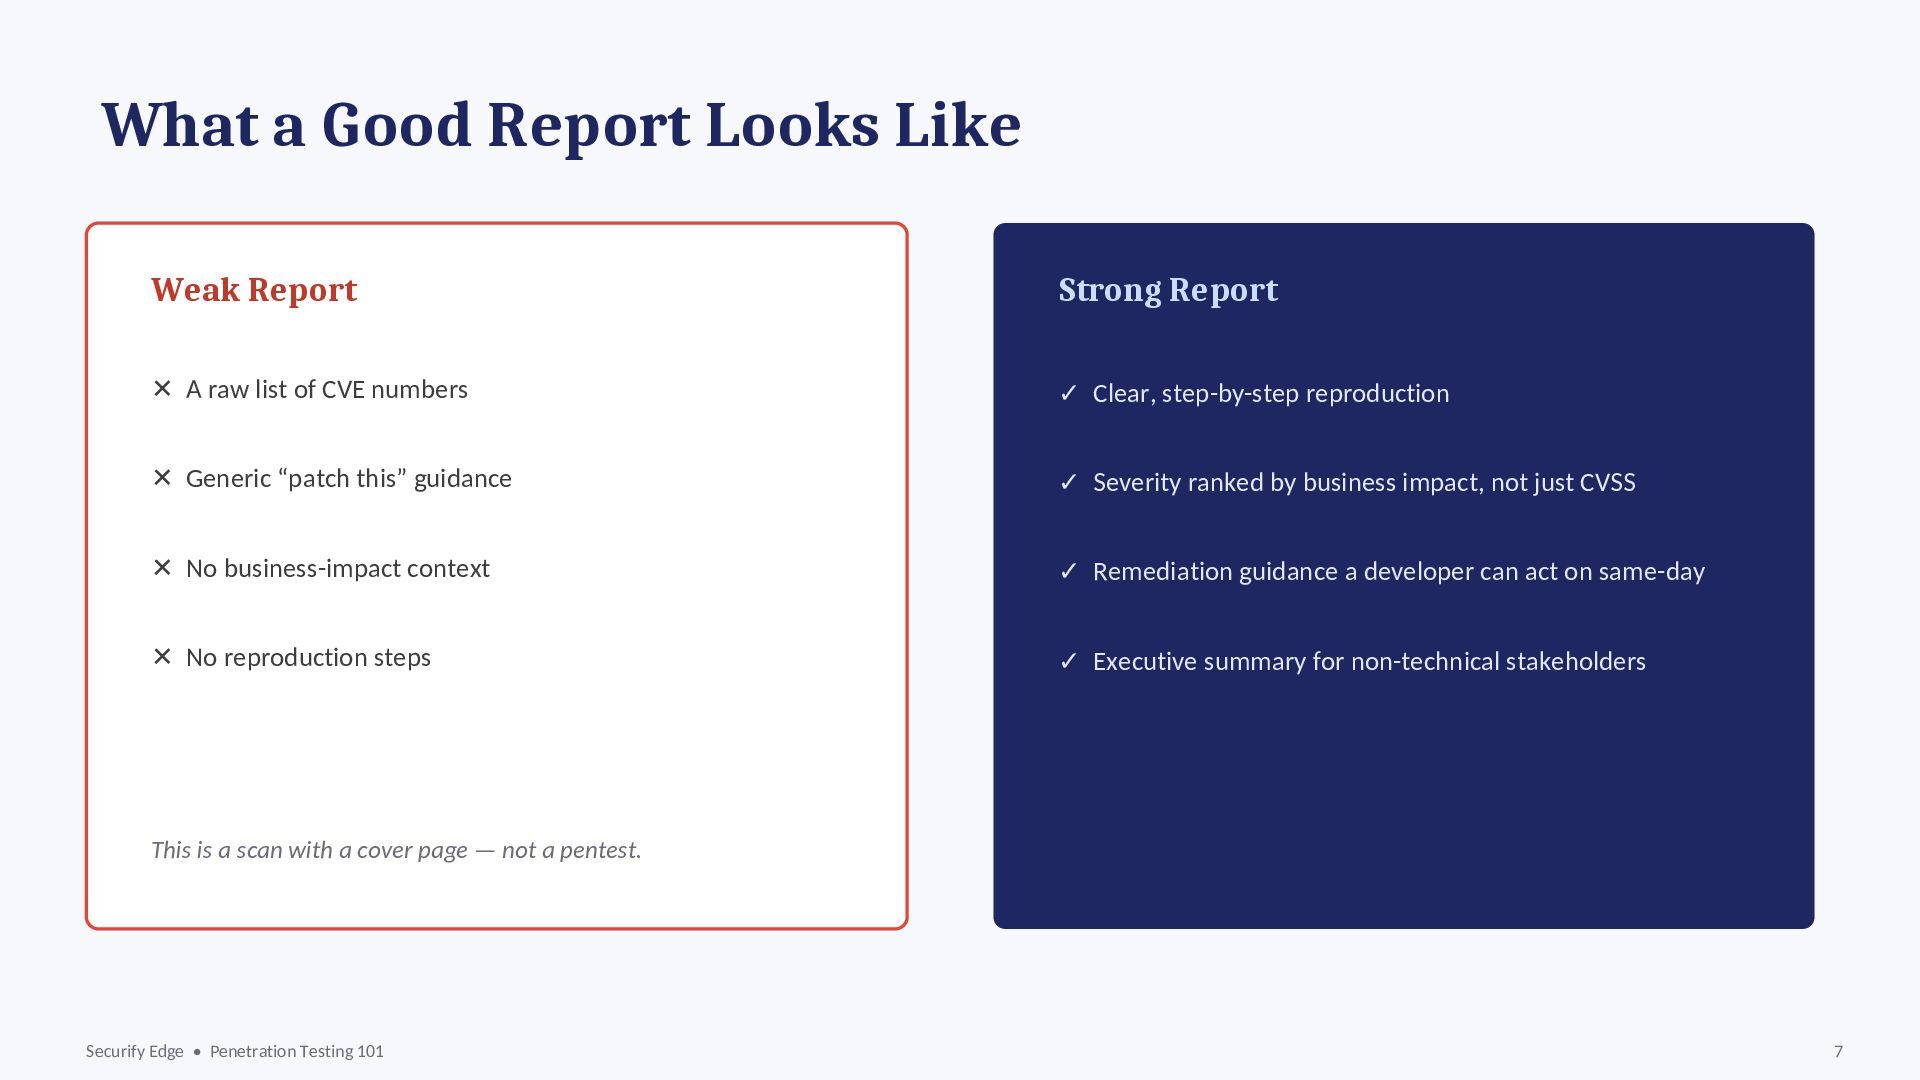
  7. What a Good Report Looks Like Weak Report Strong Report

    ✕ A raw list of CVE numbers ✓ Clear, step-by-step reproduction ✕ Generic “patch this” guidance ✓ Severity ranked by business impact, not just CVSS ✕ No business-impact context ✓ Remediation guidance a developer can act on same-day ✕ No reproduction steps ✓ Executive summary for non-technical stakeholders This is a scan with a cover page — not a pentest. Securify Edge • Penetration Testing 101 7
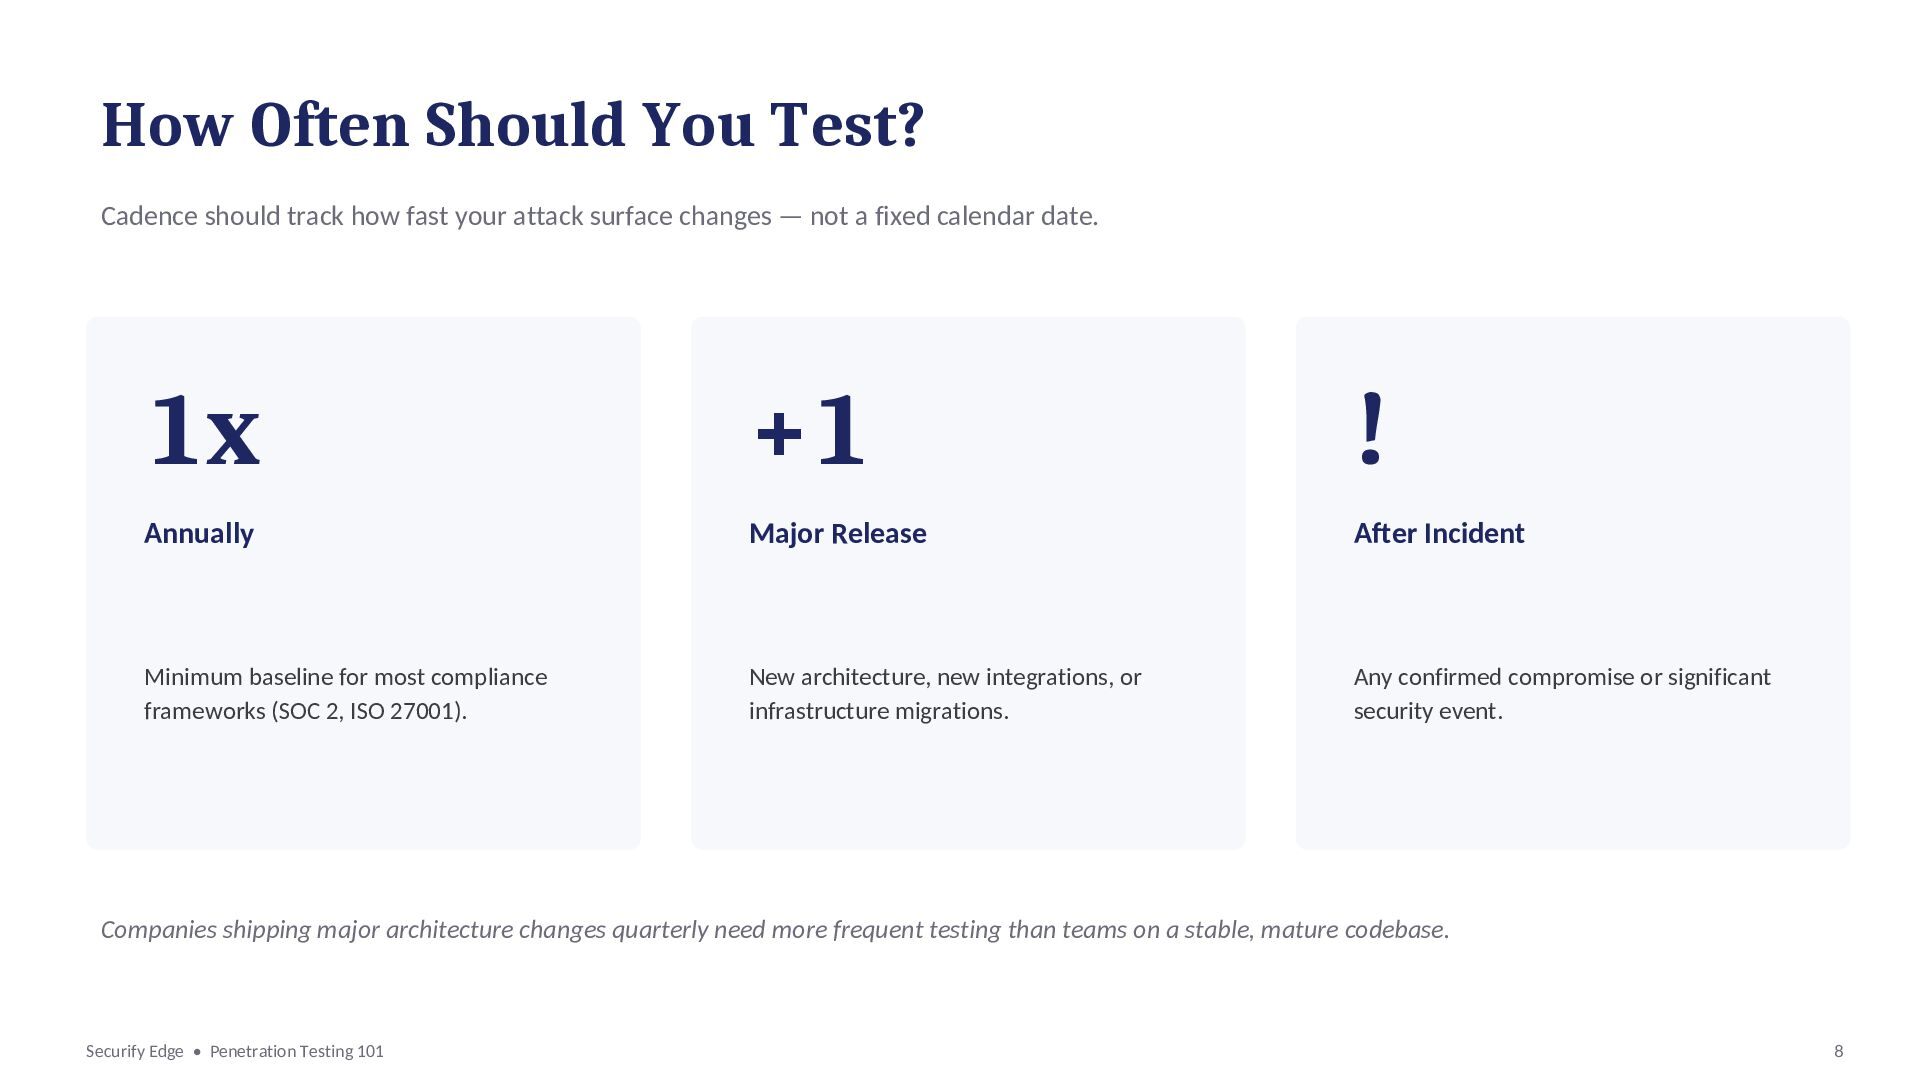
  8. How Often Should You Test? Cadence should track how fast

    your attack surface changes — not a fixed calendar date. 1x +1 ! Annually Major Release After Incident Minimum baseline for most compliance frameworks (SOC 2, ISO 27001). New architecture, new integrations, or infrastructure migrations. Any confirmed compromise or significant security event. Companies shipping major architecture changes quarterly need more frequent testing than teams on a stable, mature codebase. Securify Edge • Penetration Testing 101 8
  9. Penetration Testing & Compliance Most frameworks don't just recommend testing

    — they require documented evidence of it. SOC 2 ISO 27001 Cyber Essentials Plus Expects evidence of regular testing as part of your security control environment, reviewed during the audit period. Requires technical vulnerability testing as part of the ISMS risk treatment and control verification process. Includes independent technical verification of the controls claimed in the base certification. Securify Edge • Penetration Testing 101 9
  10. Before Your First Penetration Test Fix known CVEs, default credentials,

    and missing rate limiting first Define scope precisely — systems, environments, and testing windows Agree rules of engagement and an emergency stop process Confirm the report format includes reproduction steps and business-impact ranking Plan remediation time and a retest before your compliance deadline Securify Edge • Penetration Testing 101 10
  11. Ready to See Where You Stand? Explore our penetration testing

    services and methodology securifyedge.com/services/penetration-testing-services/ Securify Edge