Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Safely Application Deployment From Dream to Rea...

Avatar for Rachid Zarouali Rachid Zarouali
October 06, 2021
31

Safely Application Deployment From Dream to Reality

"We'll see about security later, we'll put it into production first and then we'll think about it later", how many times have we heard this sentence? Modern CI/CD tools offer more and more functionalities around security, yet this aspect is very often neglected, considered complex, rigid, too expensive, ... Dream or reality? Achievable or utopian? Affordable or expensive? Many questions asked when the ghost of security appears. I have a dream, to show that this ghost is called Casper and he's our best friend. I propose concrete and unadorned feedback of a CI/CD project where security became an ally, not an enemy. How few tools allowed to secure deployments without it being a burden for the dev teams. We'll talk about vulnerability scanning, consistency checking and a few tips and tricks. Dream or reality? Let's find out together :)

Avatar for Rachid Zarouali

Rachid Zarouali

October 06, 2021

Transcript

  1. ©2021 VMware, Inc. VMworld 2021 Title Slide Safely Application Deployment

    From Dream to Reality Rachid Zarouali Freelance Cloud Architect / Sevensphere #vmworld #session ID: CODE 2772 SESSION ID: CODE 2772
  2. ©2021 VMware, Inc. Who am I ? Freelance Cloud Architect

    @sevensphere Microsoft Azure MVP / Docker Captain Twitter: @xinity / @sevensphereio email: [email protected] website: https://sevensphere.io
  3. ©2021 VMware, Inc. What do I do ? Fields of

    Expertise: Cloud Architecture CI / CD Monitoring / Observability Security Container Automation (IaC) Technology: Azure / GCP / Aws Gitlab / Azure Devops / Drone Grafana Stack / Instana OpenPolicy / Snyk / sysdig K8S / Nomad Terraform / Ansible Community : Organizer: DockerLyon / CNCFLyon / Container Garage series Speaker: devopsrex / devoxxma / Cloud Native Universe Workshop organizer: Container / IaC / Security
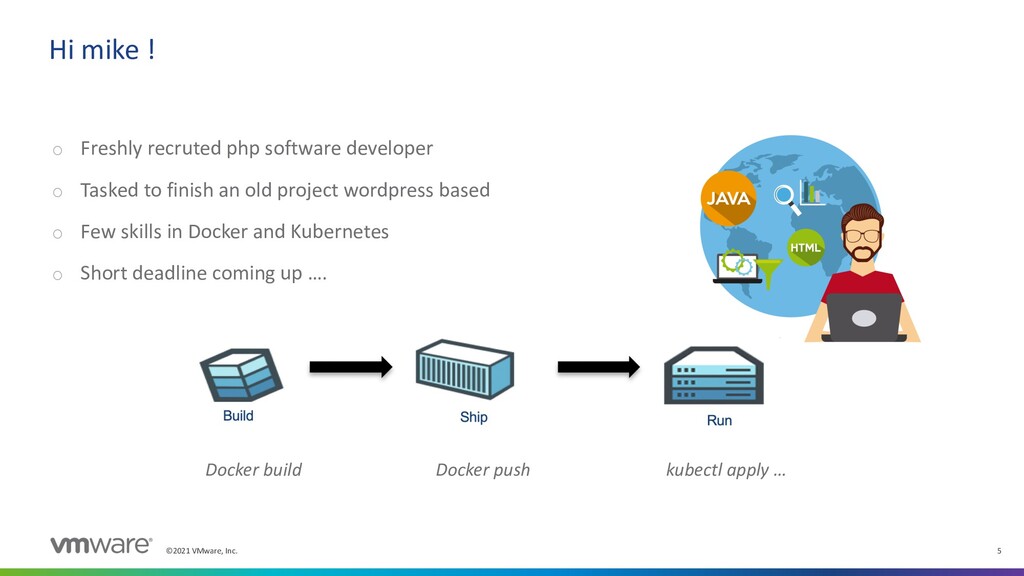
  4. ©2021 VMware, Inc. 5 Hi mike ! o Freshly recruted

    php software developer o Tasked to finish an old project wordpress based o Few skills in Docker and Kubernetes o Short deadline coming up …. Docker build Docker push kubectl apply …
  5. ©2021 VMware, Inc. 6 Hi mike ! please meet rachid

    ! o Freelance Cloud Architect o Tasked to audit the plateform and the app o And ….
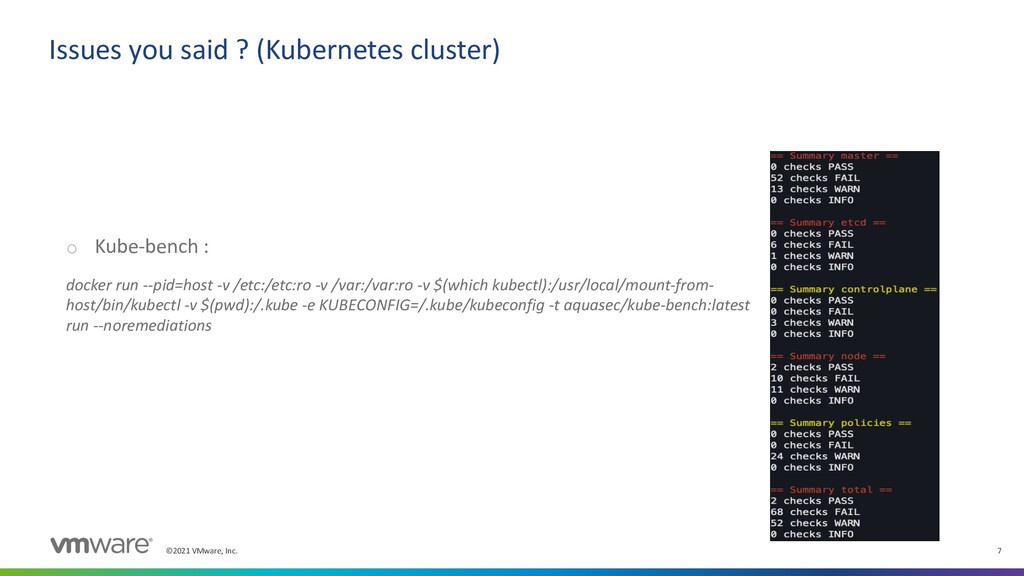
  6. ©2021 VMware, Inc. 7 Issues you said ? (Kubernetes cluster)

    o Kube-bench : docker run --pid=host -v /etc:/etc:ro -v /var:/var:ro -v $(which kubectl):/usr/local/mount-from- host/bin/kubectl -v $(pwd):/.kube -e KUBECONFIG=/.kube/kubeconfig -t aquasec/kube-bench:latest run --noremediations
  7. ©2021 VMware, Inc. 8 Issues you said ? (Kubernetes cluster)

    o Privileged pods allowed o No RBAC authorization model deployed o Kubernetes Api publicly accessible o No external authentication mechanism deployed o Secrets stored in kubernetes (base64 encoded) o … o mysql server opened on http/80 with root password from dictionnary
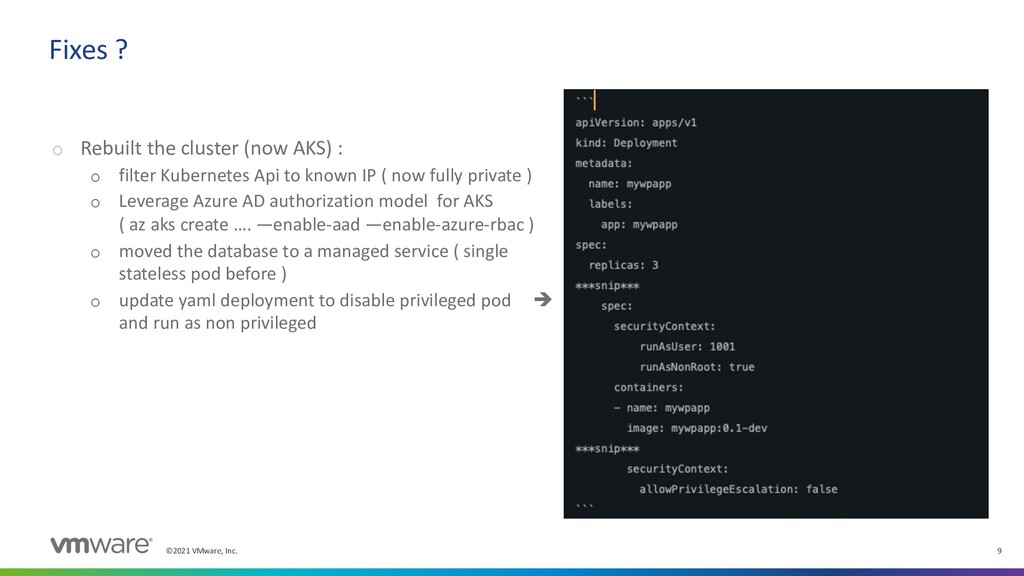
  8. ©2021 VMware, Inc. 9 Fixes ? o Rebuilt the cluster

    (now AKS) : o filter Kubernetes Api to known IP ( now fully private ) o Leverage Azure AD authorization model for AKS ( az aks create …. —enable-aad —enable-azure-rbac ) o moved the database to a managed service ( single stateless pod before ) o update yaml deployment to disable privileged pod è and run as non privileged
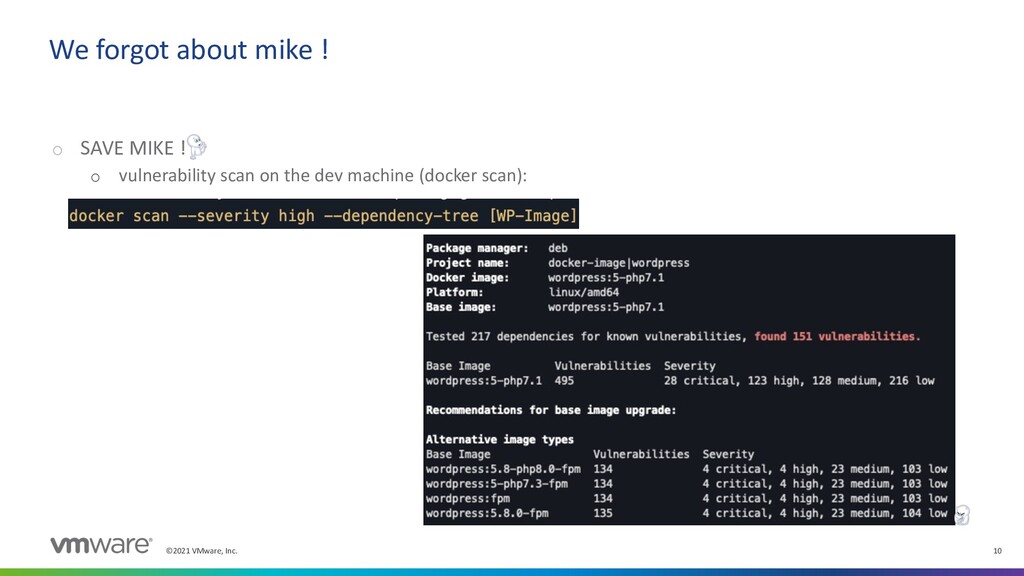
  9. ©2021 VMware, Inc. 10 We forgot about mike ! o

    SAVE MIKE ! o vulnerability scan on the dev machine (docker scan):
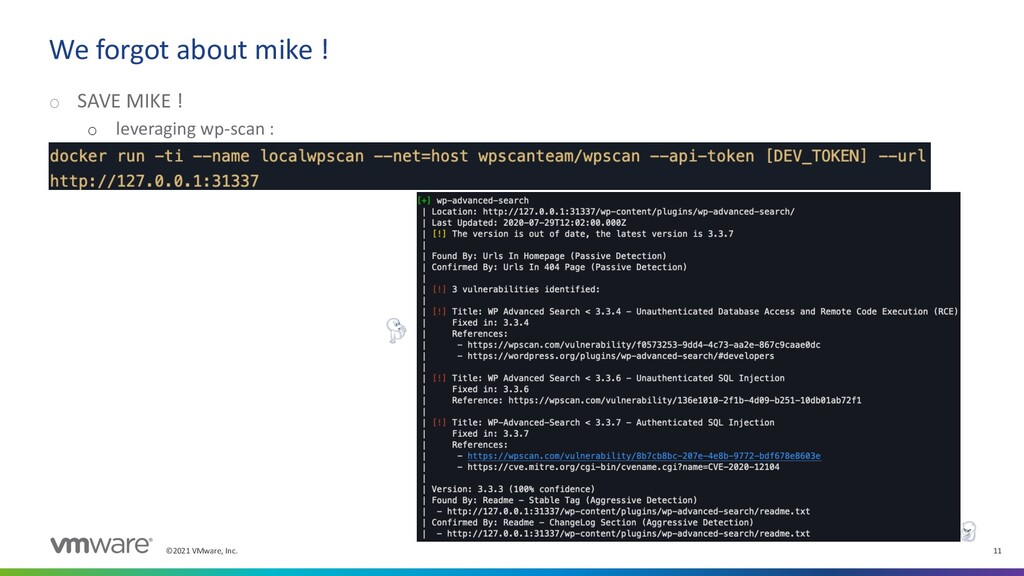
  10. ©2021 VMware, Inc. 11 We forgot about mike ! o

    SAVE MIKE ! o leveraging wp-scan :
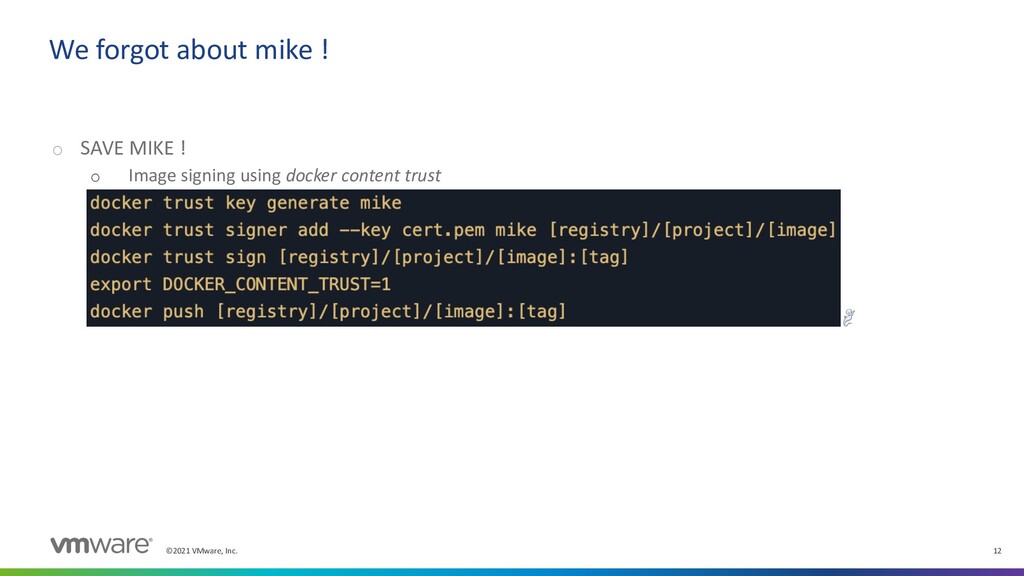
  11. ©2021 VMware, Inc. 12 We forgot about mike ! o

    SAVE MIKE ! o Image signing using docker content trust
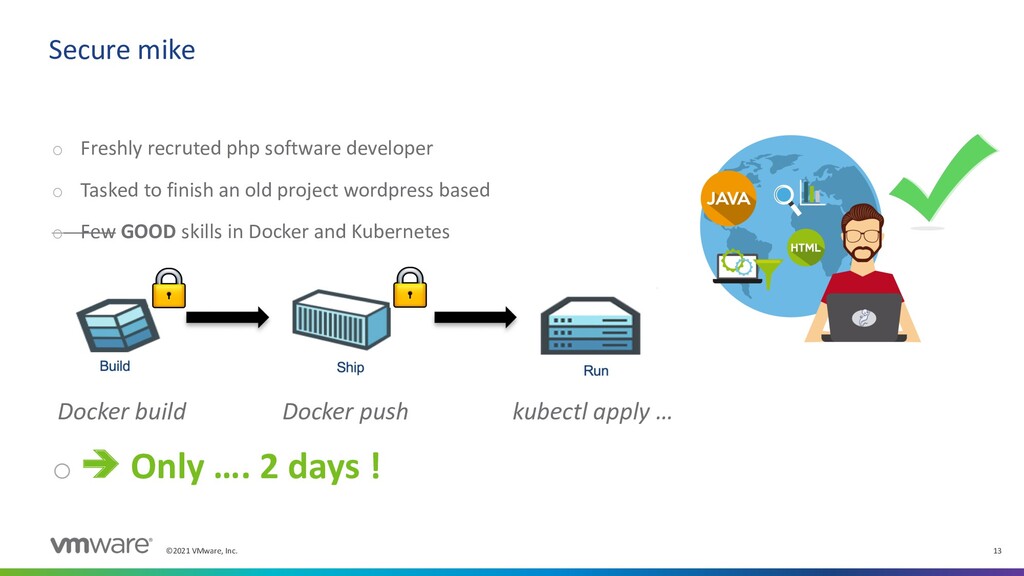
  12. ©2021 VMware, Inc. 13 Secure mike o Freshly recruted php

    software developer o Tasked to finish an old project wordpress based o Few GOOD skills in Docker and Kubernetes Docker build Docker push kubectl apply … o è Only …. 2 days !
  13. ©2021 VMware, Inc. 14 Dream to reality ? o Still

    long road to walk è MIKE To be Done
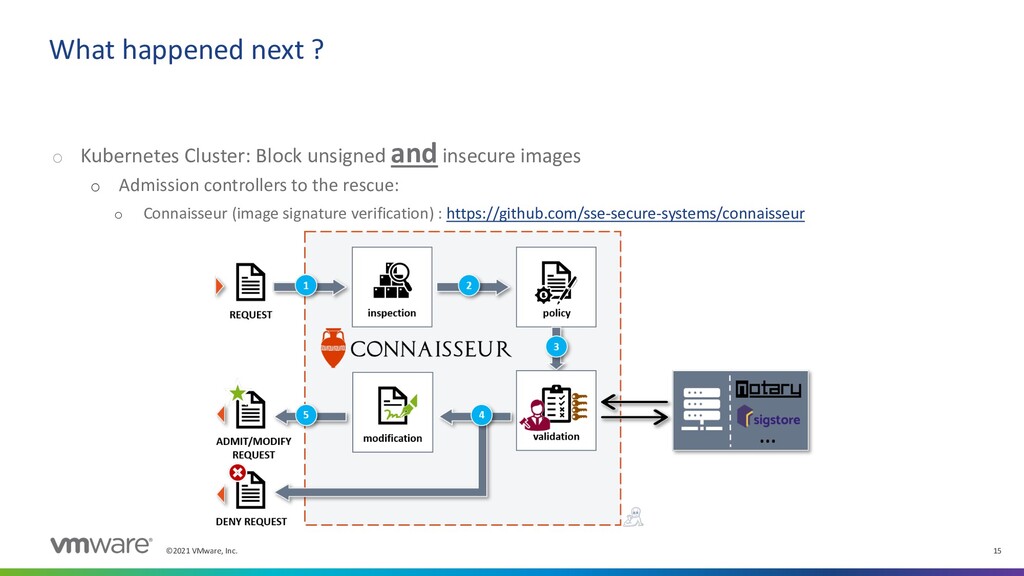
  14. ©2021 VMware, Inc. 15 What happened next ? o Kubernetes

    Cluster: Block unsigned and insecure images o Admission controllers to the rescue: o Connaisseur (image signature verification) : https://github.com/sse-secure-systems/connaisseur
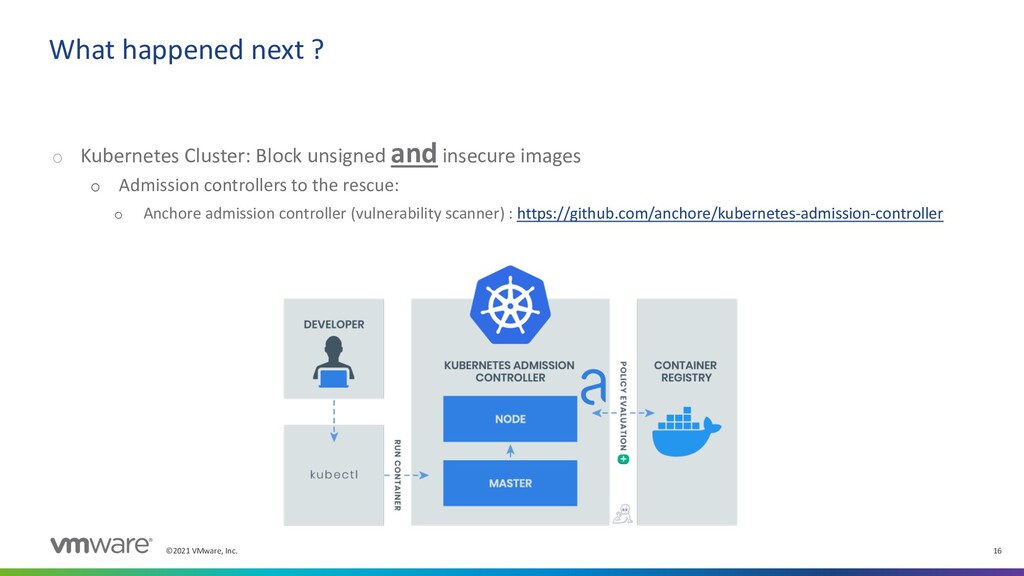
  15. ©2021 VMware, Inc. 16 What happened next ? o Kubernetes

    Cluster: Block unsigned and insecure images o Admission controllers to the rescue: o Anchore admission controller (vulnerability scanner) : https://github.com/anchore/kubernetes-admission-controller
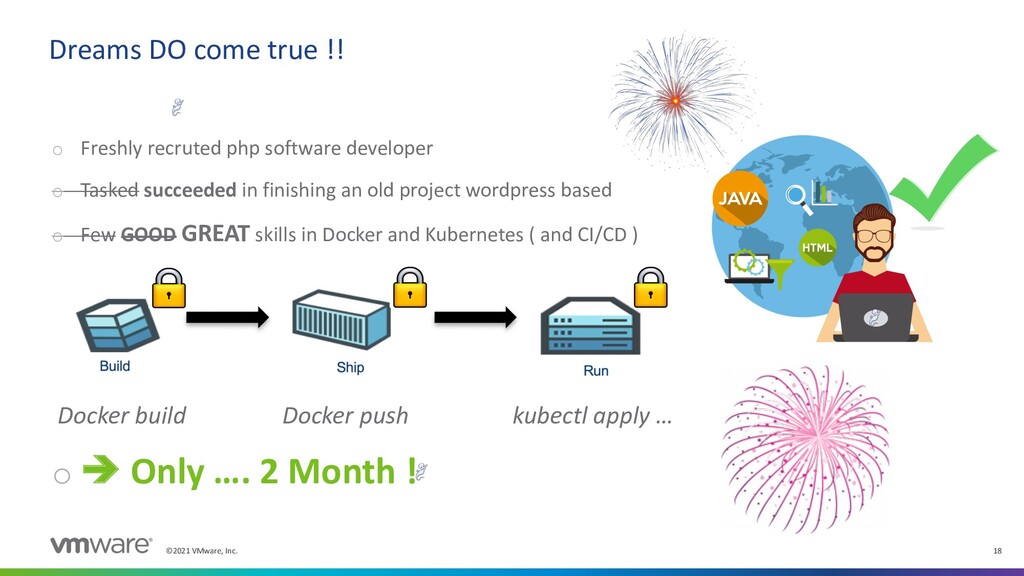
  16. ©2021 VMware, Inc. 18 Dreams DO come true !! o

    Freshly recruted php software developer o Tasked succeeded in finishing an old project wordpress based o Few GOOD GREAT skills in Docker and Kubernetes ( and CI/CD ) Docker build Docker push kubectl apply … o è Only …. 2 Month !
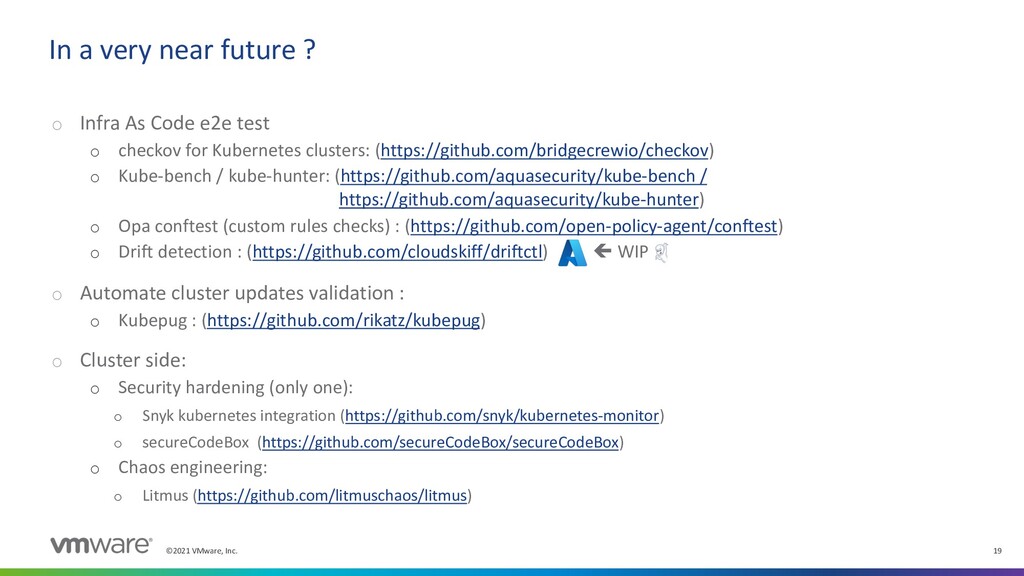
  17. ©2021 VMware, Inc. 19 In a very near future ?

    o Infra As Code e2e test o checkov for Kubernetes clusters: (https://github.com/bridgecrewio/checkov) o Kube-bench / kube-hunter: (https://github.com/aquasecurity/kube-bench / https://github.com/aquasecurity/kube-hunter) o Opa conftest (custom rules checks) : (https://github.com/open-policy-agent/conftest) o Drift detection : (https://github.com/cloudskiff/driftctl) ç WIP o Automate cluster updates validation : o Kubepug : (https://github.com/rikatz/kubepug) o Cluster side: o Security hardening (only one): o Snyk kubernetes integration (https://github.com/snyk/kubernetes-monitor) o secureCodeBox (https://github.com/secureCodeBox/secureCodeBox) o Chaos engineering: o Litmus (https://github.com/litmuschaos/litmus)
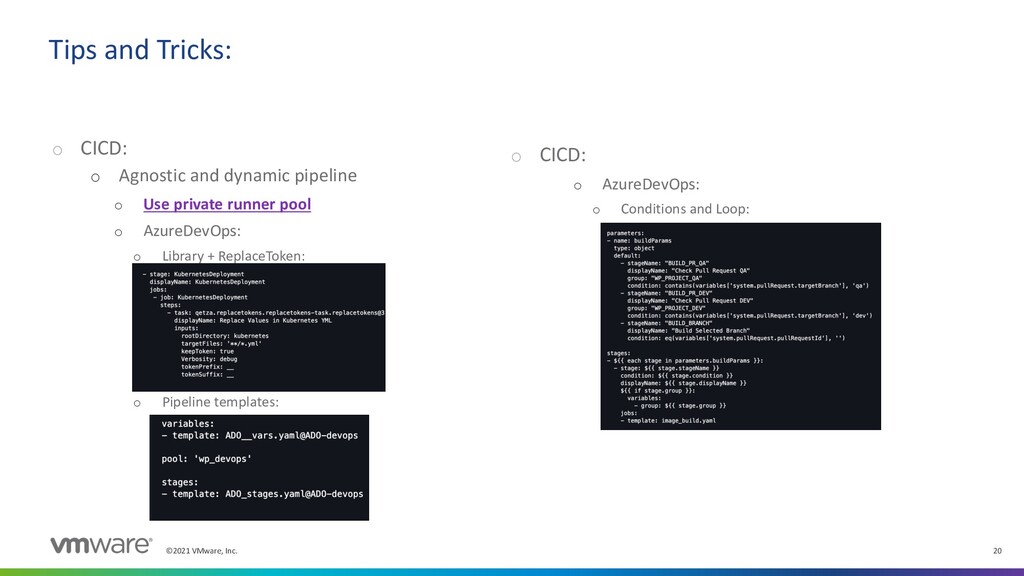
  18. ©2021 VMware, Inc. 20 Tips and Tricks: o CICD: o

    Agnostic and dynamic pipeline o Use private runner pool o AzureDevOps: o Library + ReplaceToken: o Pipeline templates: o CICD: o AzureDevOps: o Conditions and Loop:
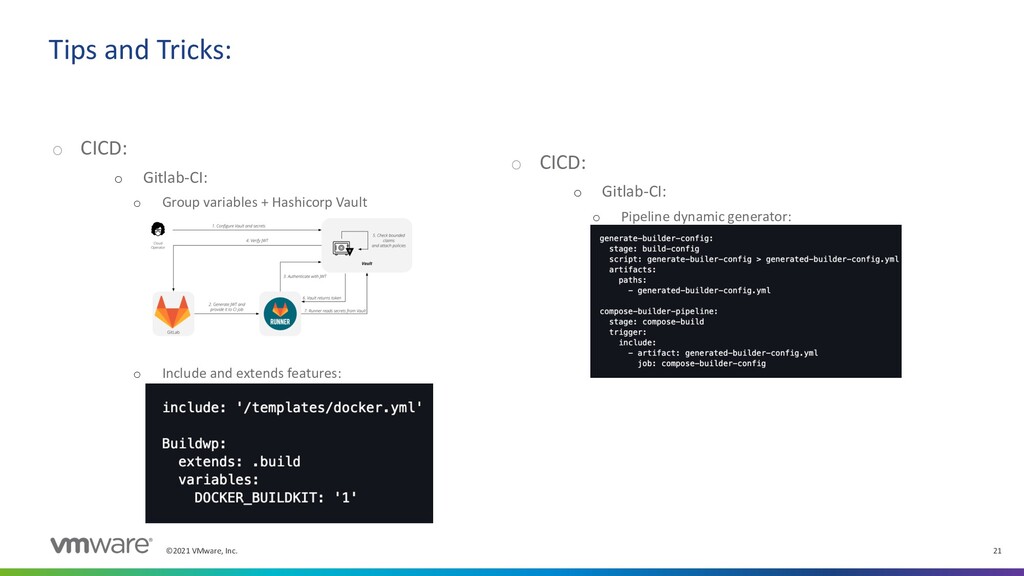
  19. ©2021 VMware, Inc. 21 Tips and Tricks: o CICD: o

    Gitlab-CI: o Group variables + Hashicorp Vault o Include and extends features: o CICD: o Gitlab-CI: o Pipeline dynamic generator:
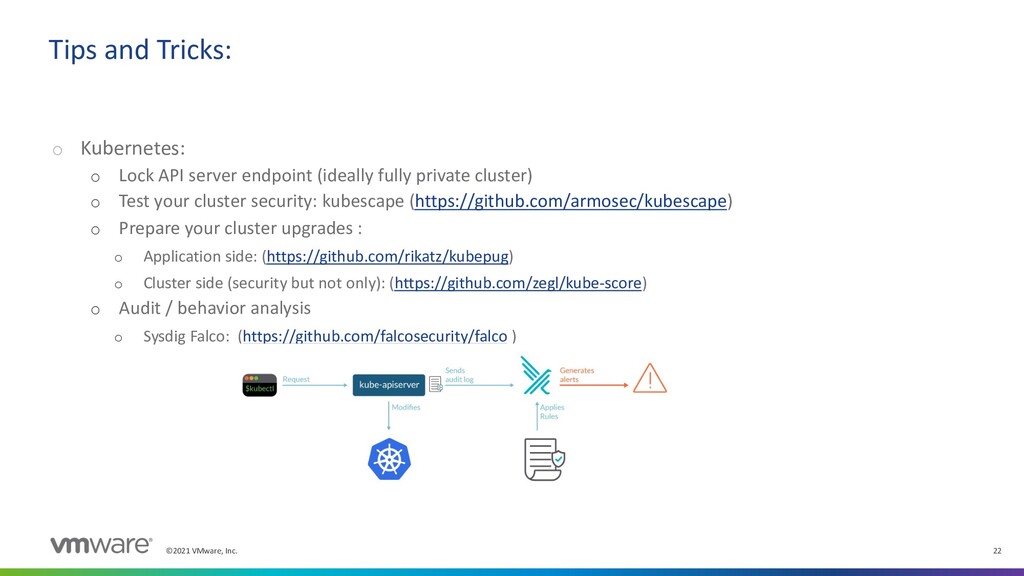
  20. ©2021 VMware, Inc. 22 Tips and Tricks: o Kubernetes: o

    Lock API server endpoint (ideally fully private cluster) o Test your cluster security: kubescape (https://github.com/armosec/kubescape) o Prepare your cluster upgrades : o Application side: (https://github.com/rikatz/kubepug) o Cluster side (security but not only): (https://github.com/zegl/kube-score) o Audit / behavior analysis o Sysdig Falco: (https://github.com/falcosecurity/falco )
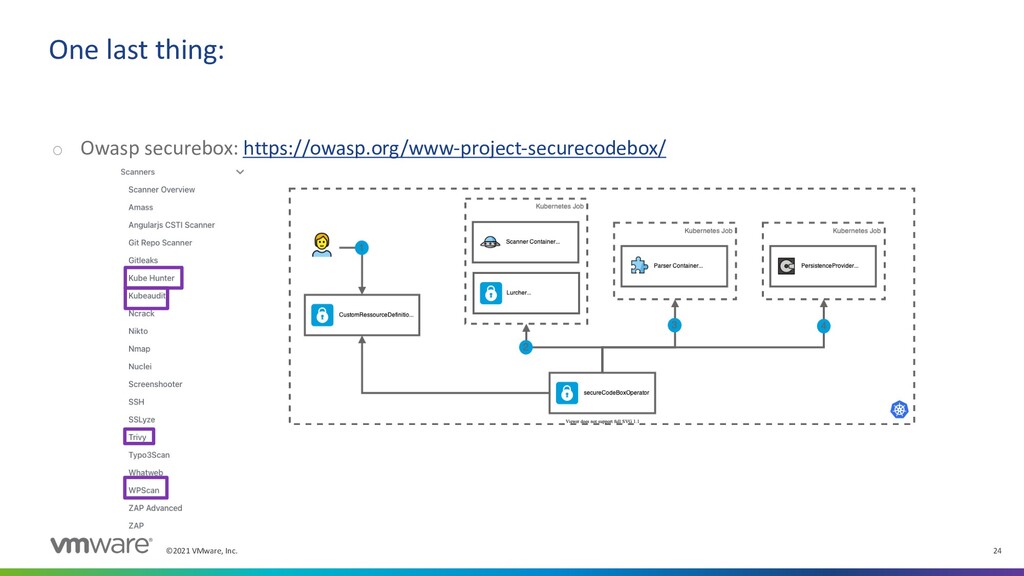
  21. ©2021 VMware, Inc. 24 One last thing: o Owasp securebox:

    https://owasp.org/www-project-securecodebox/
  22. ©2021 VMware, Inc. Who am I ? Freelance Cloud Architect

    @sevensphere Microsoft Azure MVP / Docker Captain Twitter: @xinity / @sevensphereio email: [email protected] website: https://sevensphere.io