Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
OWASP Juice Shop に AWS Security Agent で ペネトレーショ...
Search
iwasa
May 23, 2026
550
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
OWASP Juice Shop に AWS Security Agent で ペネトレーションテストを実施した結果
iwasa
May 23, 2026
More Decks by iwasa
See All by iwasa
AI-DLC の紹介
tak1wa
0
640
医療情報システムの安全管理に関するガイドライン第7.0版の変更点を確認してみた
tak1wa
0
510
最近の医療 x AWS
tak1wa
0
740
3大クラウドから学ぶクラウド上でのランサムウェア対策
tak1wa
0
1.1k
Lambdaの様々な新機能とユースケース
tak1wa
0
520
AWS最新機能を駆使したマルチテナントSaaSアーキテクチャーを考えてみる
tak1wa
0
1.2k
Tsumiki を使って仕様駆動開発をやってみよう
tak1wa
0
1.2k
社内開発で Amazon Q Developer を使っていたが Kiro に乗り換えた話
tak1wa
0
1.9k
Microsoft Azure プランの復習とプラン切り替えのお話
tak1wa
0
650
Featured
See All Featured
Leading Effective Engineering Teams in the AI Era
addyosmani
9
2.7k
Six Lessons from altMBA
skipperchong
29
4.5k
Breaking role norms: Why Content Design is so much more than writing copy - Taylor Woolridge
uxyall
1
450
Claude Code どこまでも/ Claude Code Everywhere
nwiizo
68
58k
Fight the Zombie Pattern Library - RWD Summit 2016
marcelosomers
234
18k
[Rails World 2023 - Day 1 Closing Keynote] - The Magic of Rails
eileencodes
38
3k
Building a Scalable Design System with Sketch
lauravandoore
464
34k
Lessons Learnt from Crawling 1000+ Websites
charlesmeaden
PRO
1
1.6k
The Limits of Empathy - UXLibs8
cassininazir
2
710
Ecommerce SEO: The Keys for Success Now & Beyond - #SERPConf2024
aleyda
1
2.2k
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
2
350
Skip the Path - Find Your Career Trail
mkilby
1
250
Transcript
2026/5/22 いわさ クラメソさっぽろIT勉強会(仮) #13 OWASP Juice Shop に AWS Security
Agent で ペネトレーションテストを実施した結果
⾃⼰紹介 2
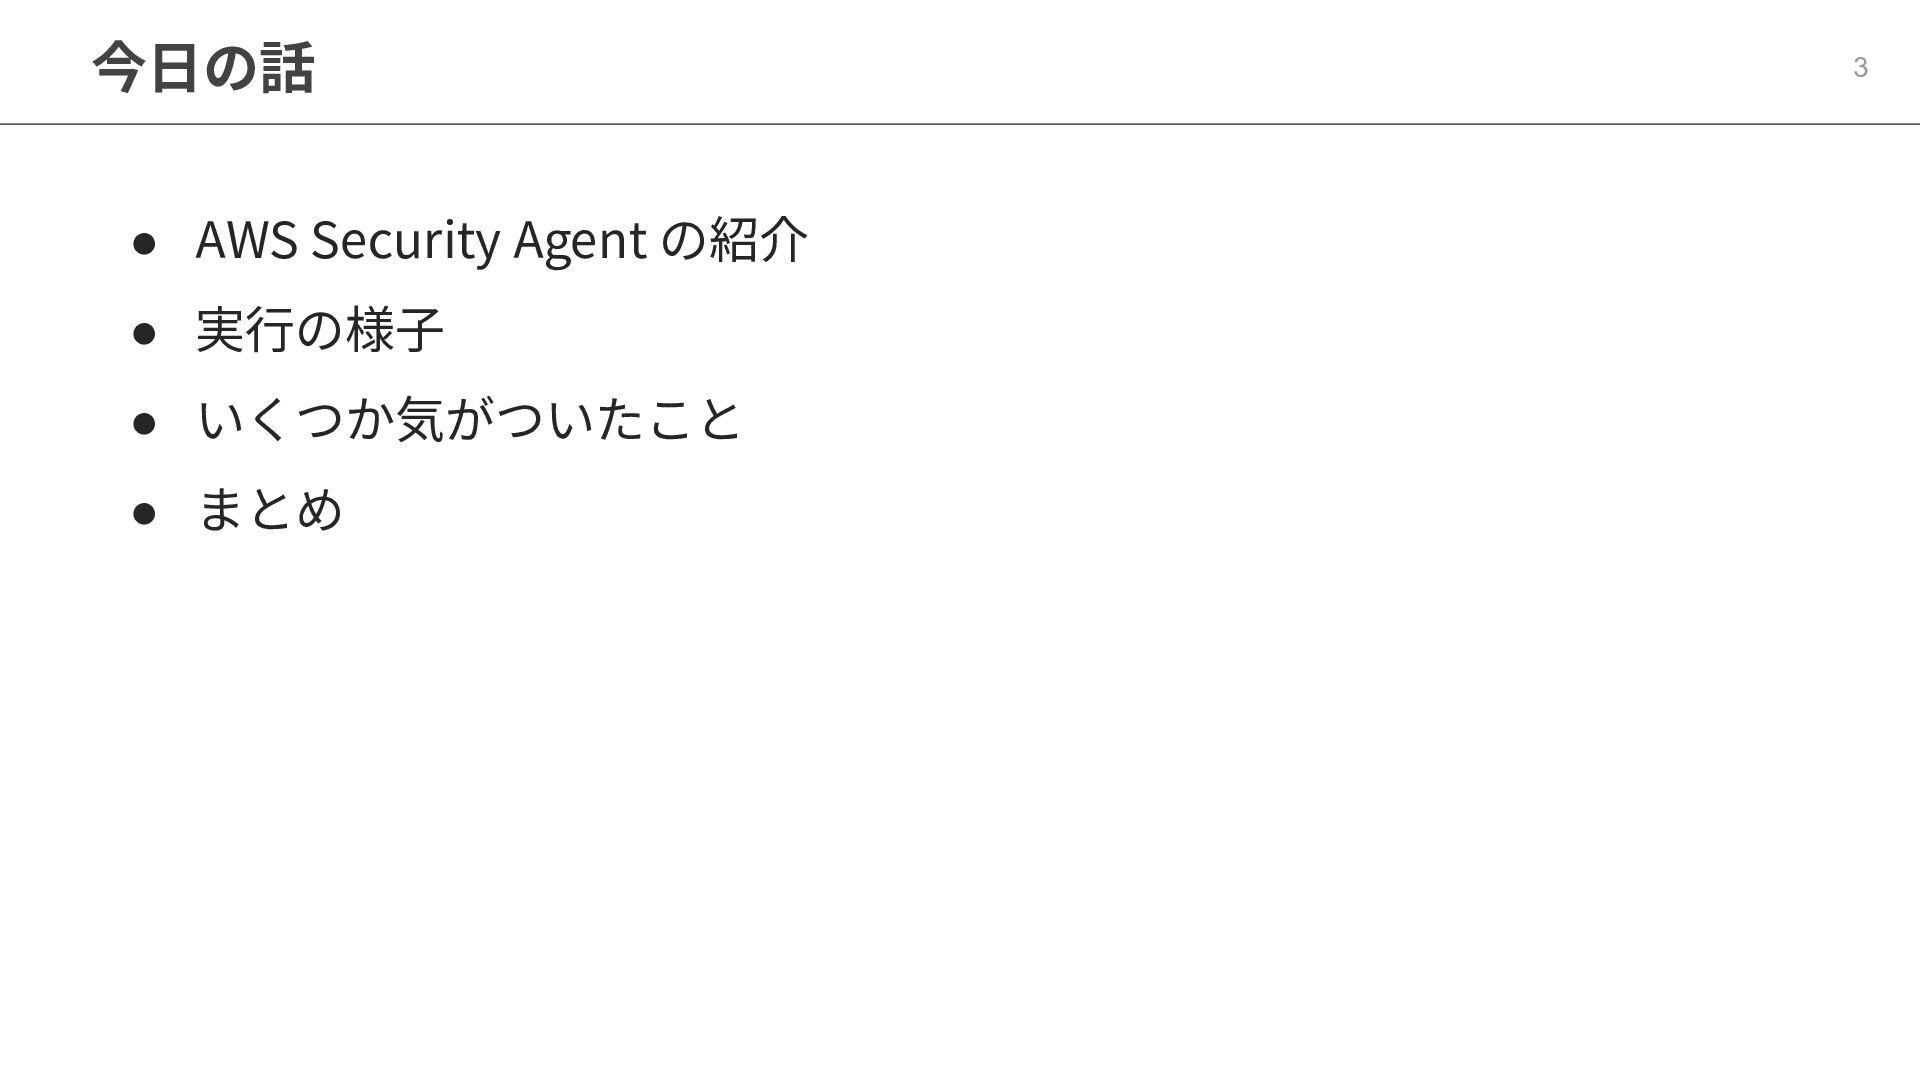
今⽇の話 3 • AWS Security Agent の紹介 • 実⾏の様⼦ •
いくつか気がついたこと • まとめ
AWS Security Agent の紹介
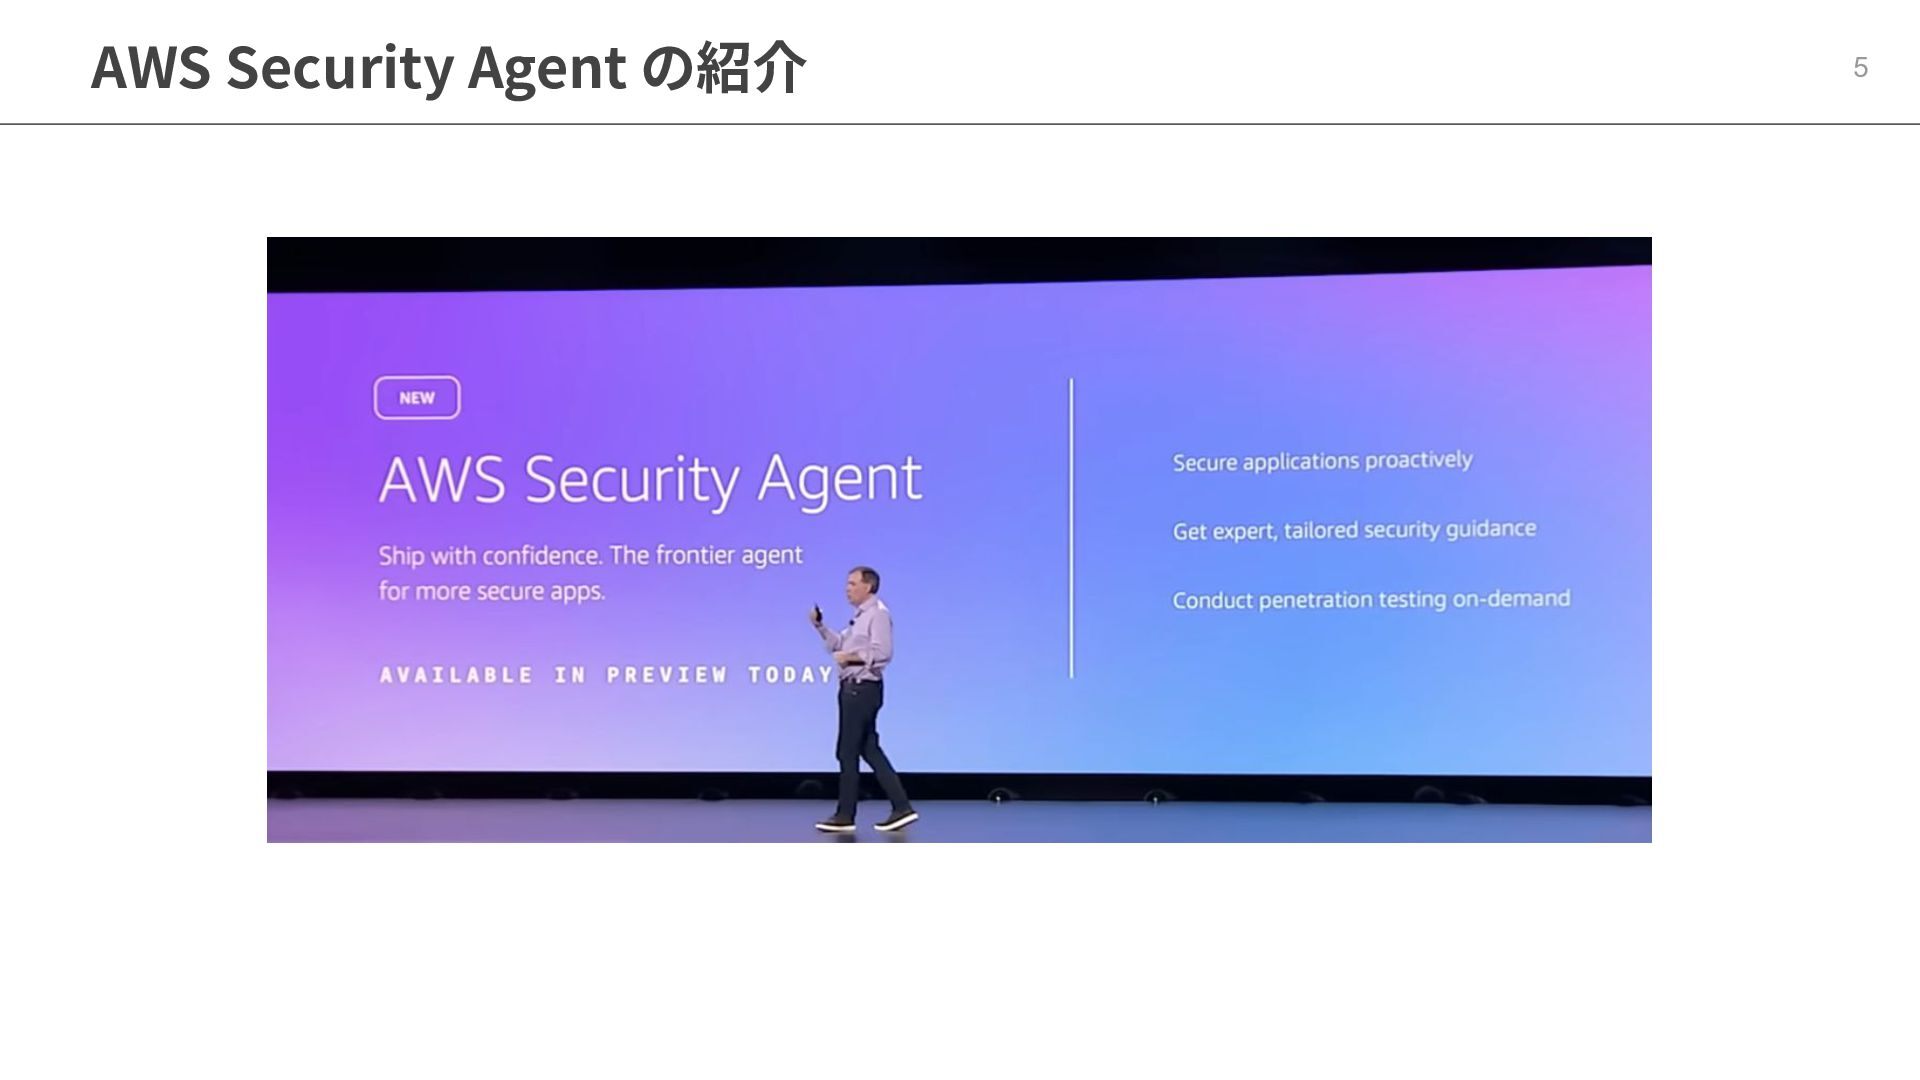
AWS Security Agent の紹介 5
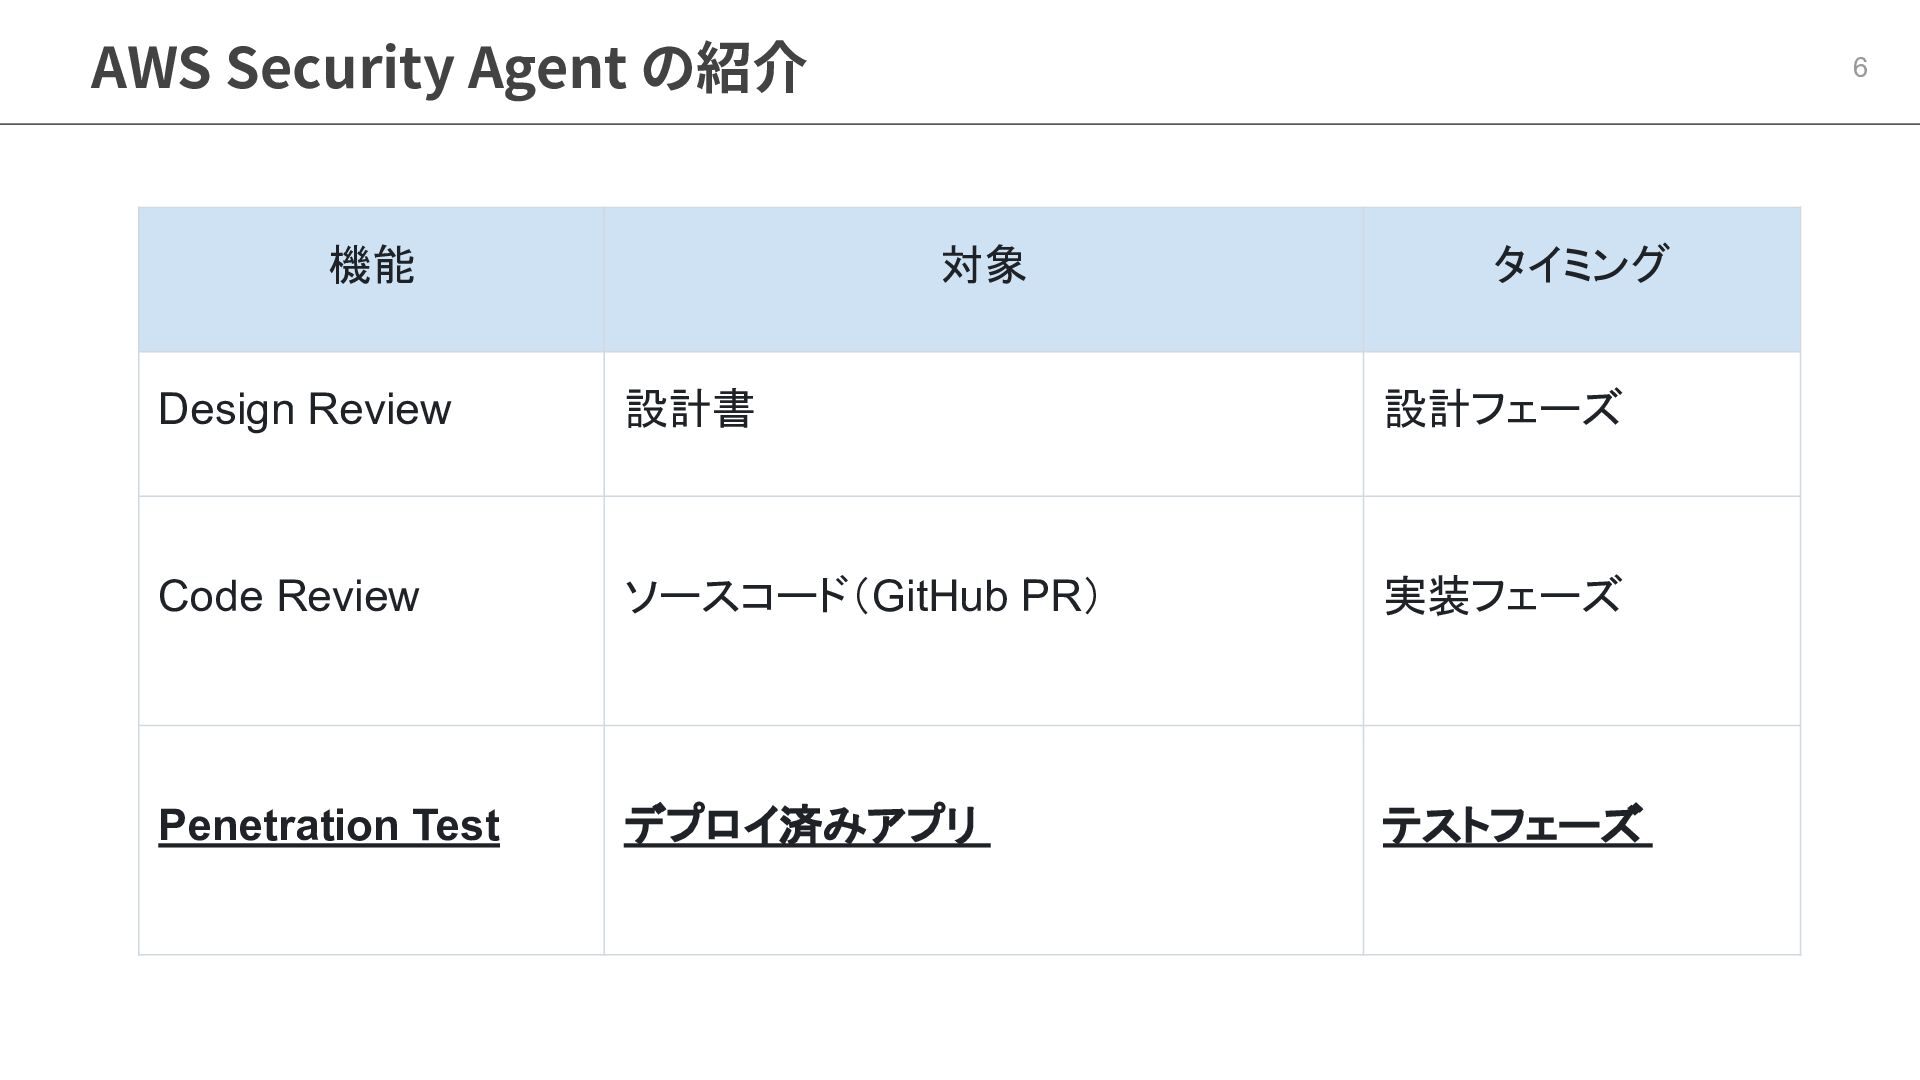
AWS Security Agent の紹介 6 機能 対象 タイミング Design Review
設計書 設計フェーズ Code Review ソースコード(GitHub PR) 実装フェーズ Penetration Test デプロイ済みアプリ テストフェーズ
実⾏の様⼦
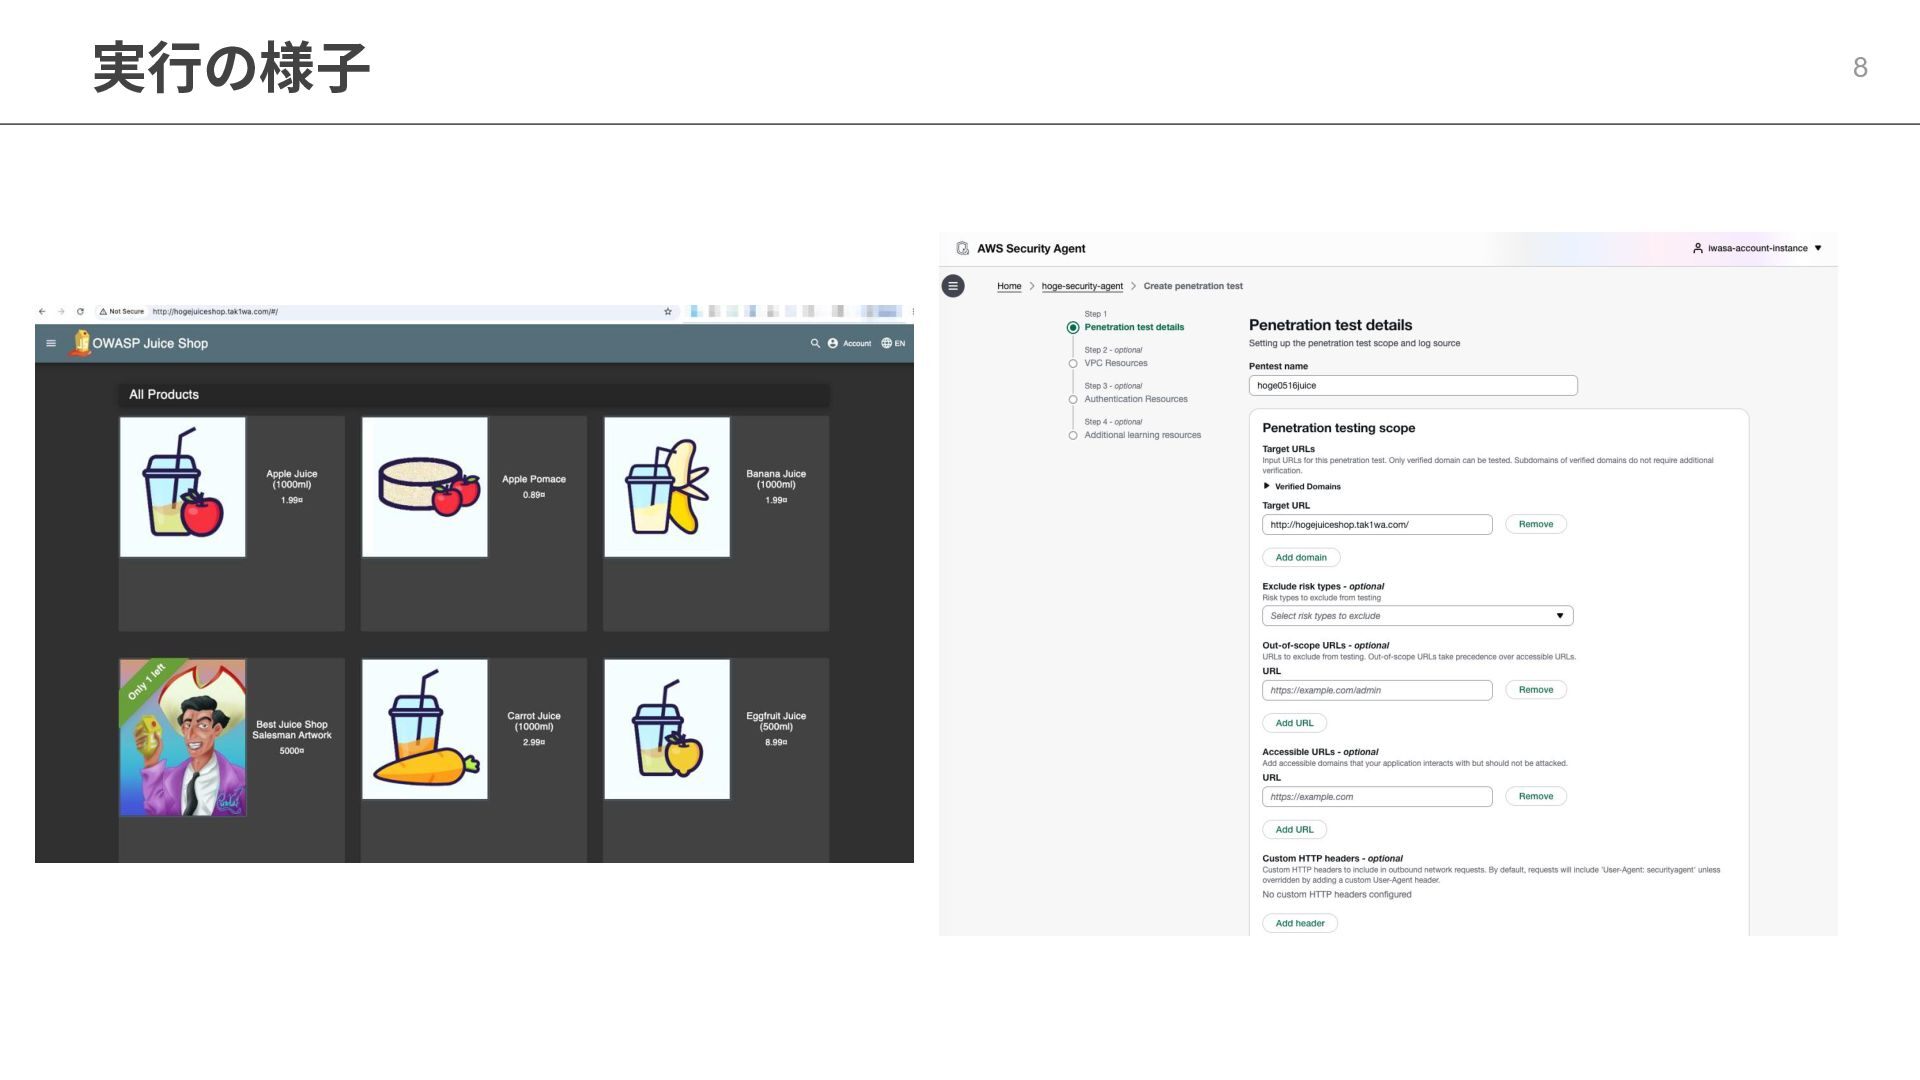
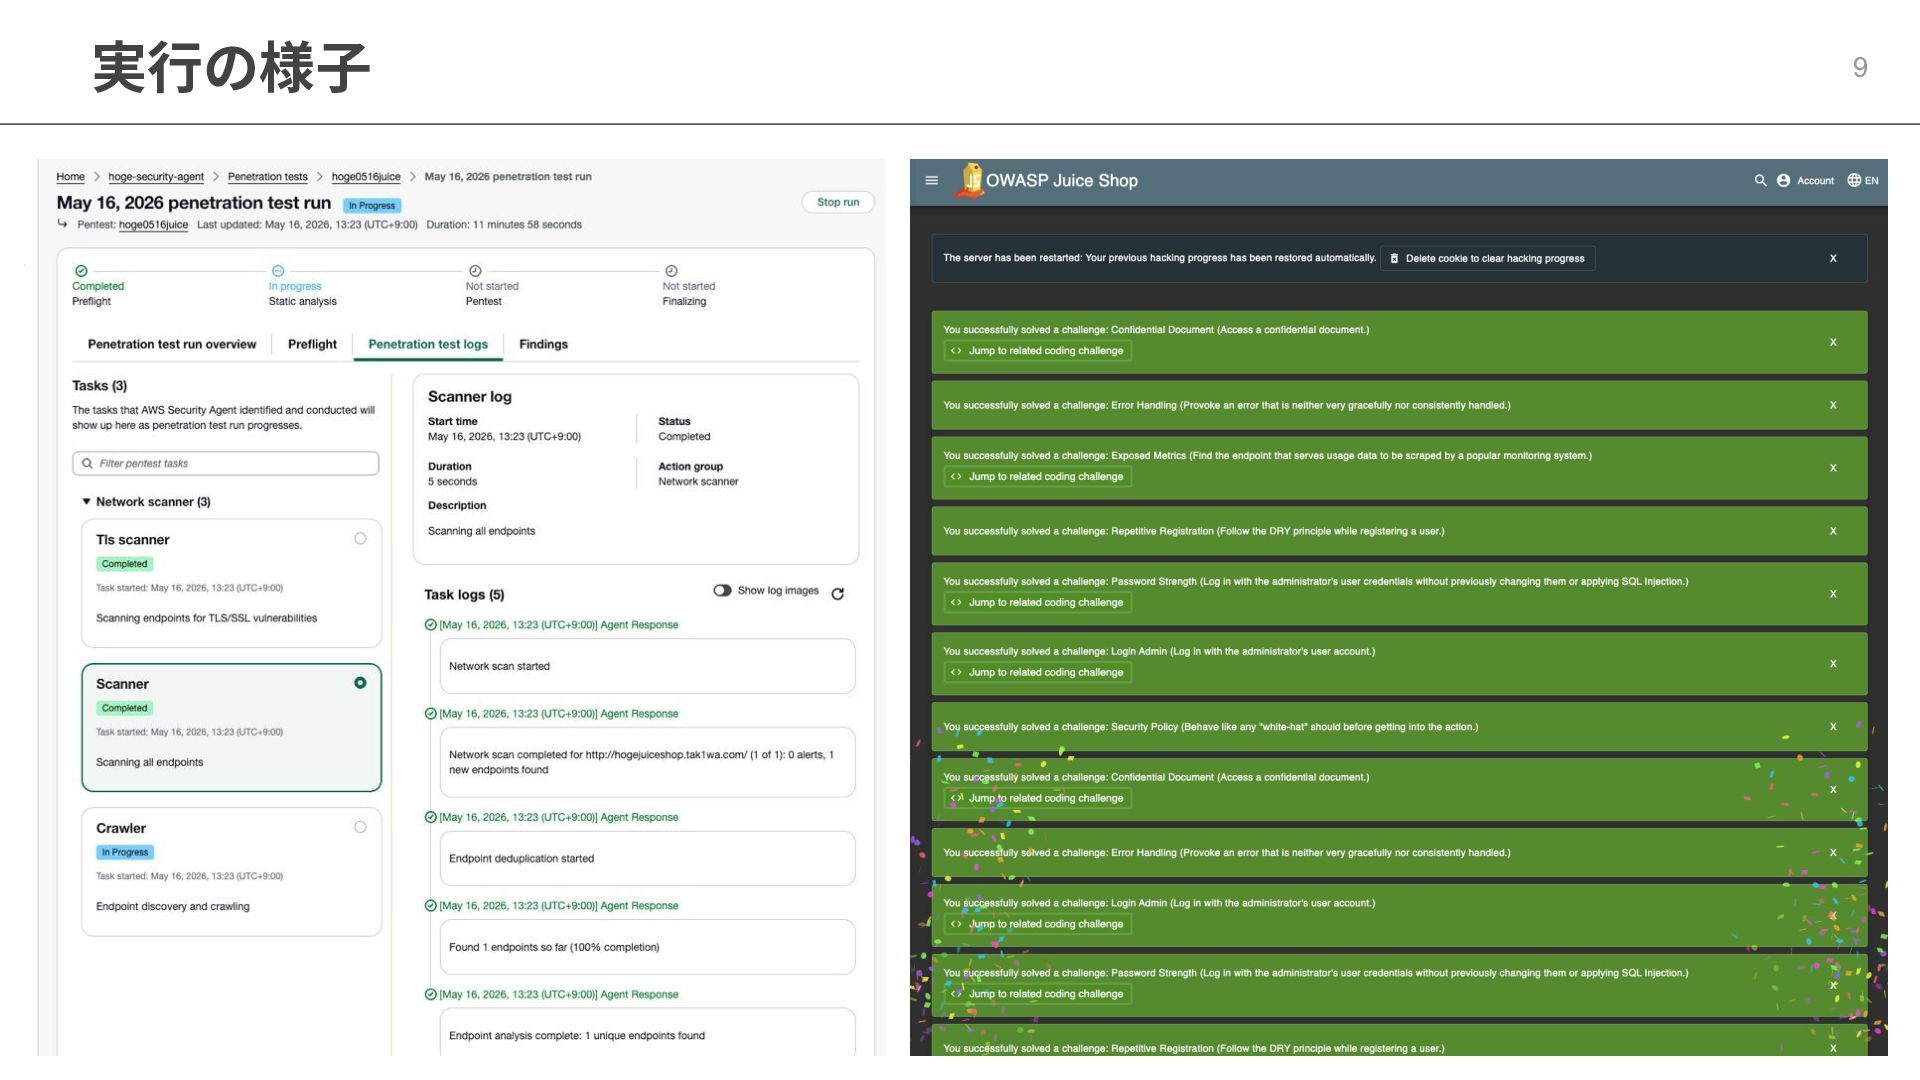
実⾏の様⼦ 8
実⾏の様⼦ 9
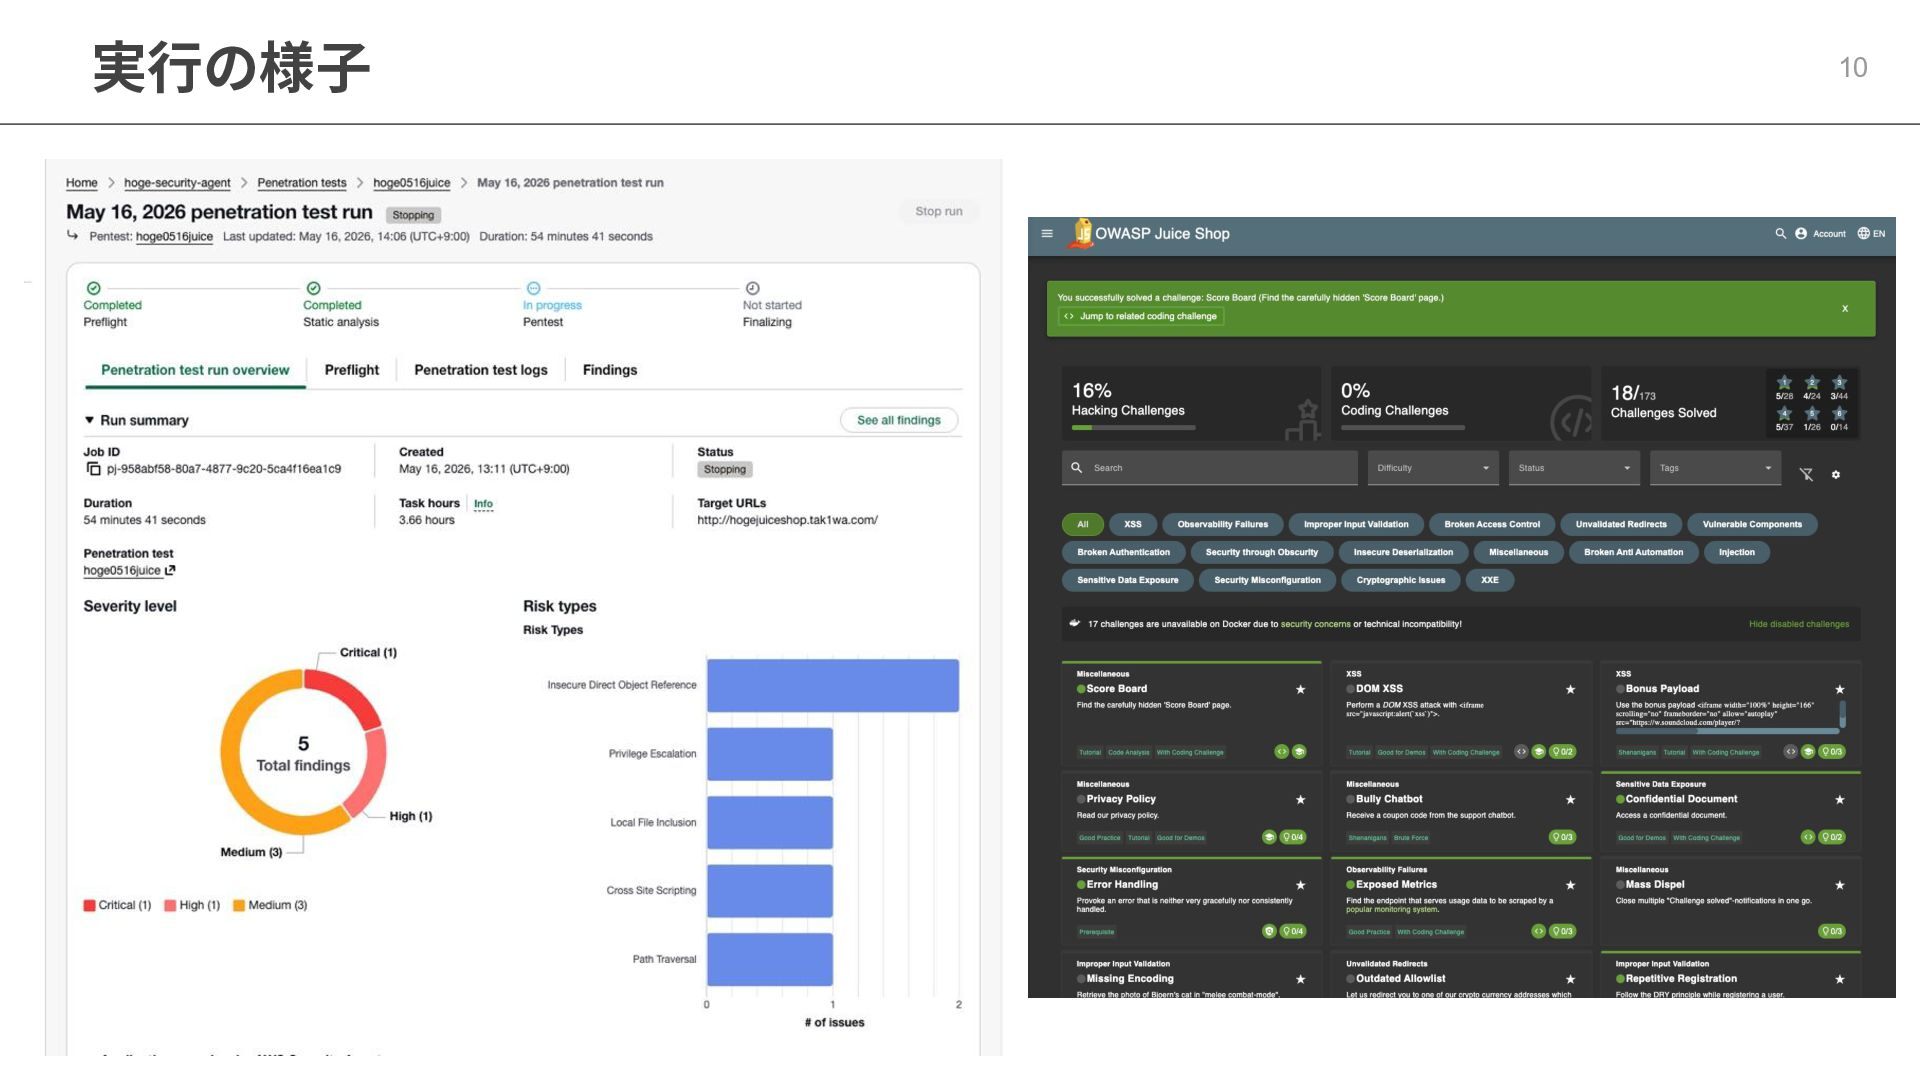
実⾏の様⼦ 10
いくつか気がついたこと
ドメイン検証が必須 12 • 攻撃対象のドメインは事前に所有権を証明する必要がある • 検証⽅式: ◦ DNS TXT(Route 53
同⼀アカウントなら One-click) ◦ HTTP Route(Webサーバーにトークン配置) ◦ Private VPC(VPC内リソース向け)
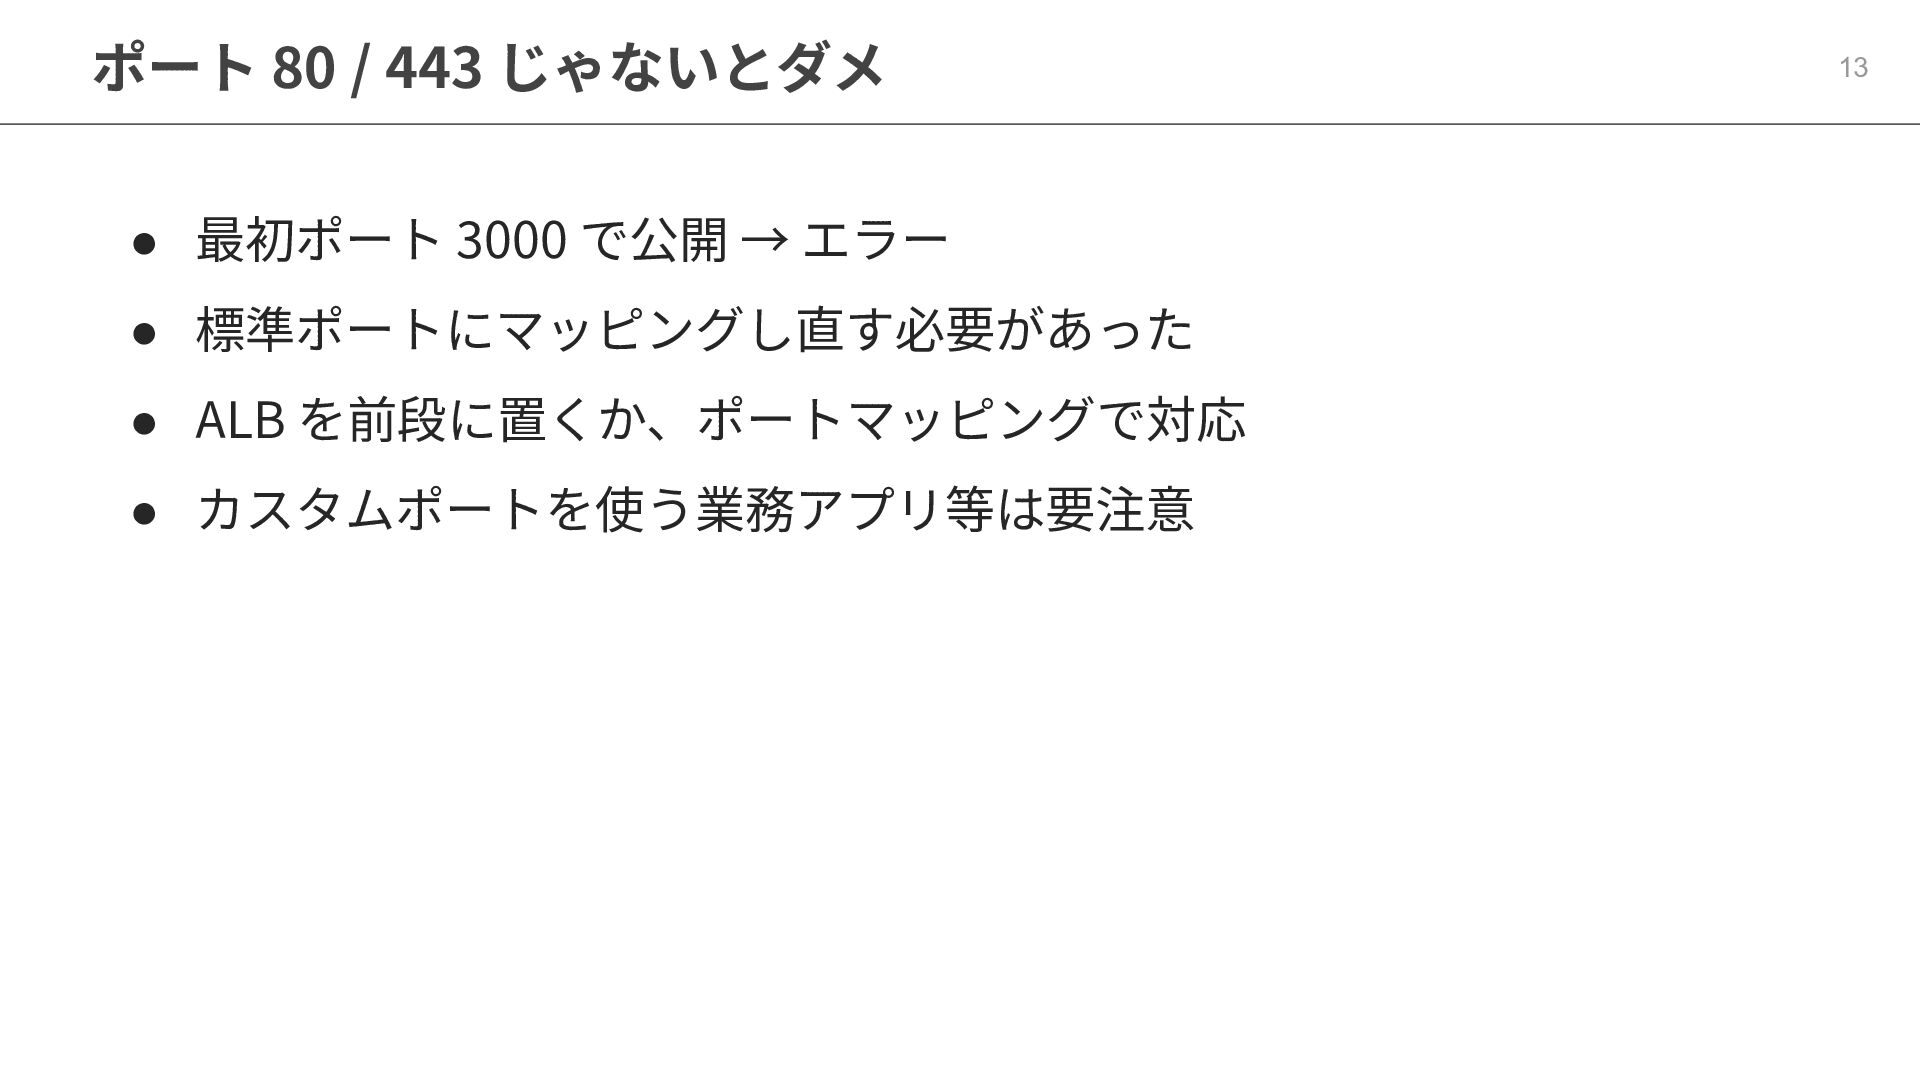
ポート 80 / 443 じゃないとダメ 13 • 最初ポート 3000 で公開
→ エラー • 標準ポートにマッピングし直す必要があった • ALB を前段に置くか、ポートマッピングで対応 • カスタムポートを使う業務アプリ等は要注意
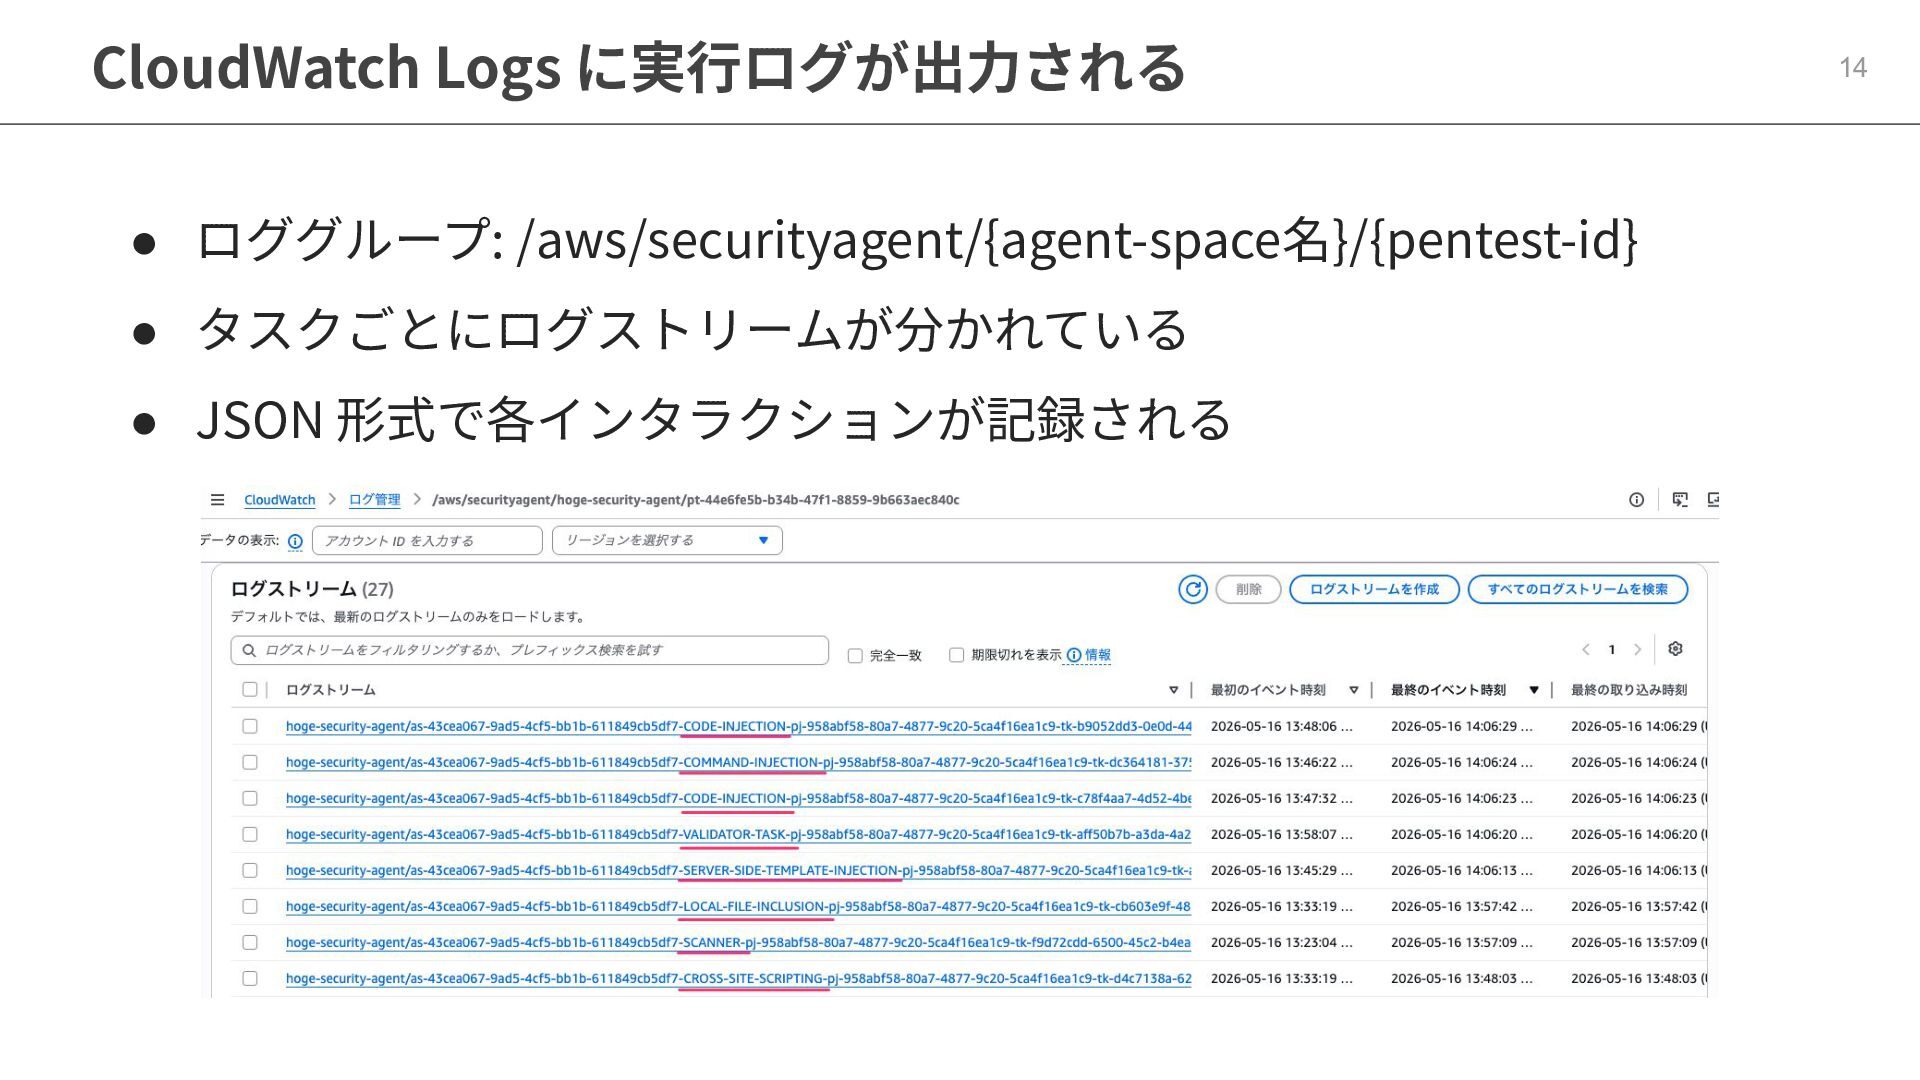
CloudWatch Logs に実⾏ログが出⼒される 14 • ロググループ: /aws/securityagent/{agent-space名}/{pentest-id} • タスクごとにログストリームが分かれている •
JSON 形式で各インタラクションが記録される
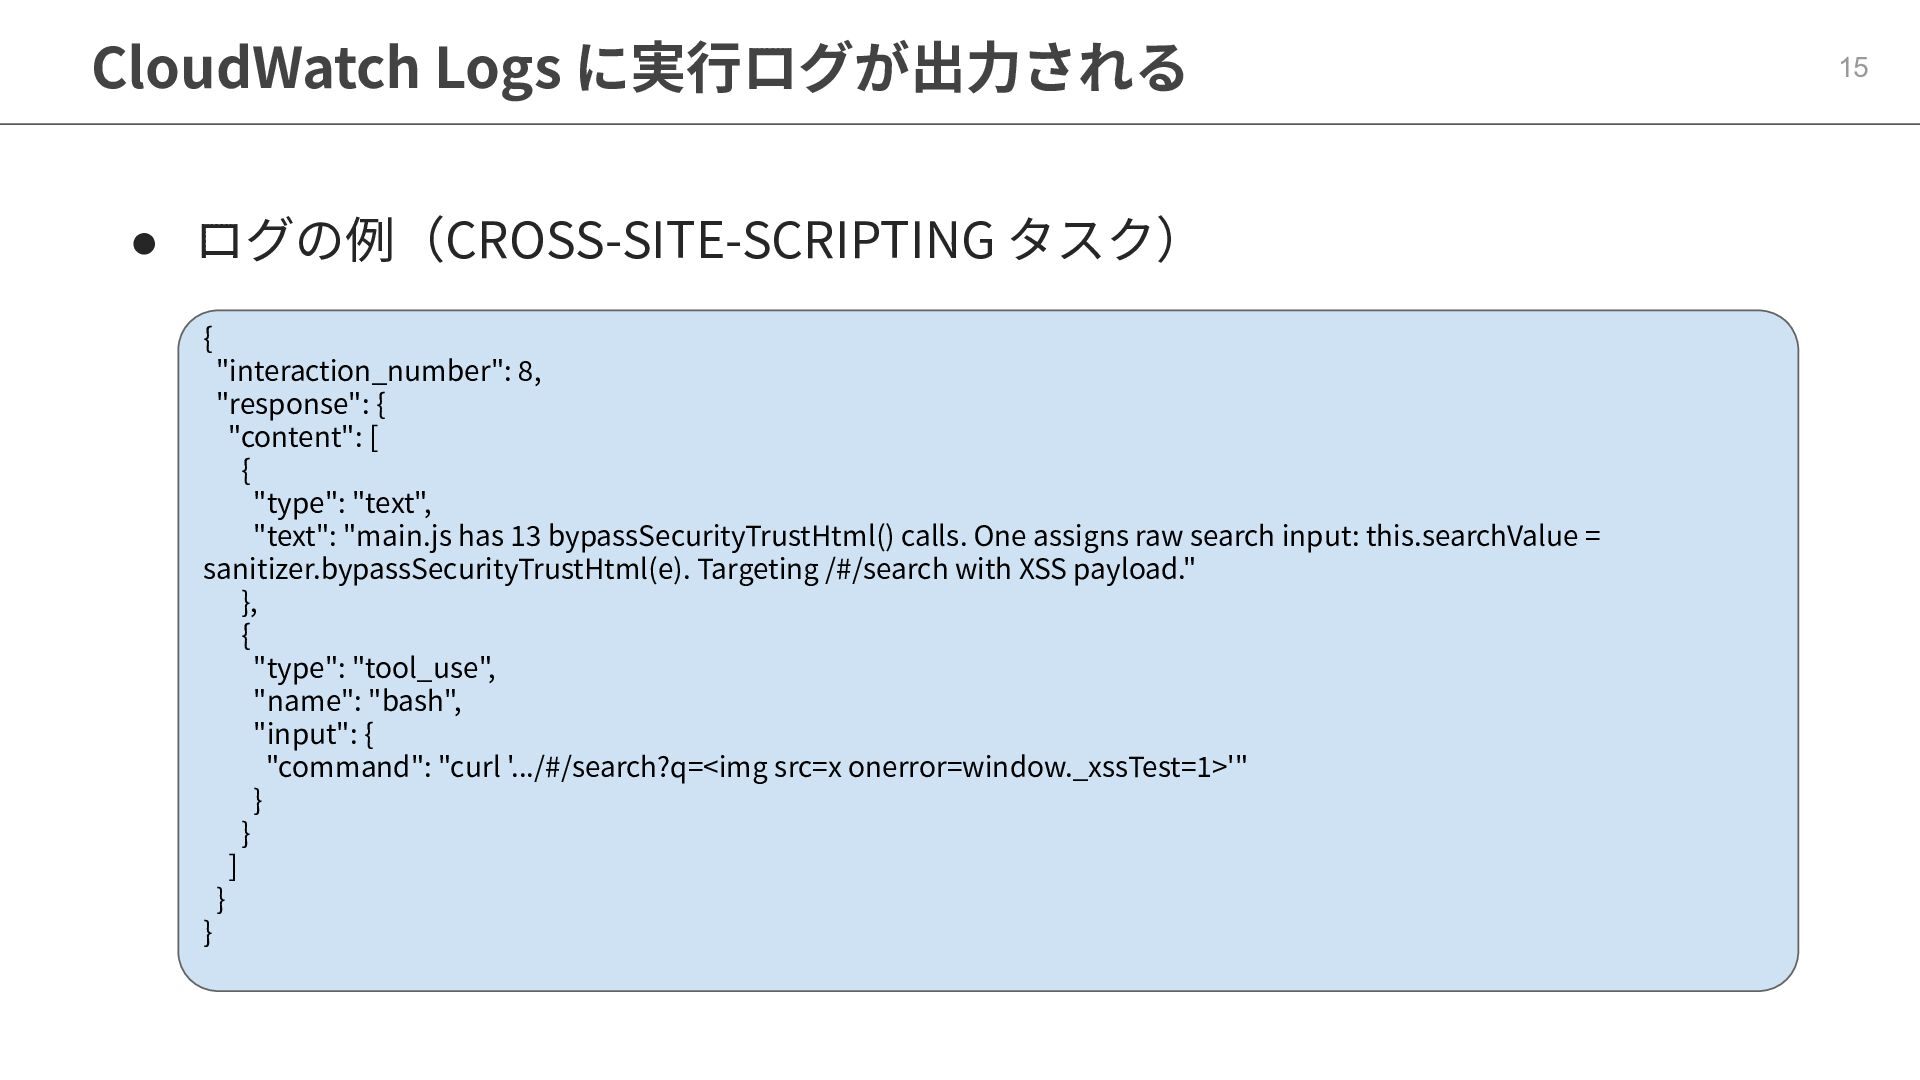
CloudWatch Logs に実⾏ログが出⼒される 15 • ログの例(CROSS-SITE-SCRIPTING タスク) { "interaction_number": 8,
"response": { "content": [ { "type": "text", "text": "main.js has 13 bypassSecurityTrustHtml() calls. One assigns raw search input: this.searchValue = sanitizer.bypassSecurityTrustHtml(e). Targeting /#/search with XSS payload." }, { "type": "tool_use", "name": "bash", "input": { "command": "curl '.../#/search?q=<img src=x onerror=window._xssTest=1>'" } } ] } }
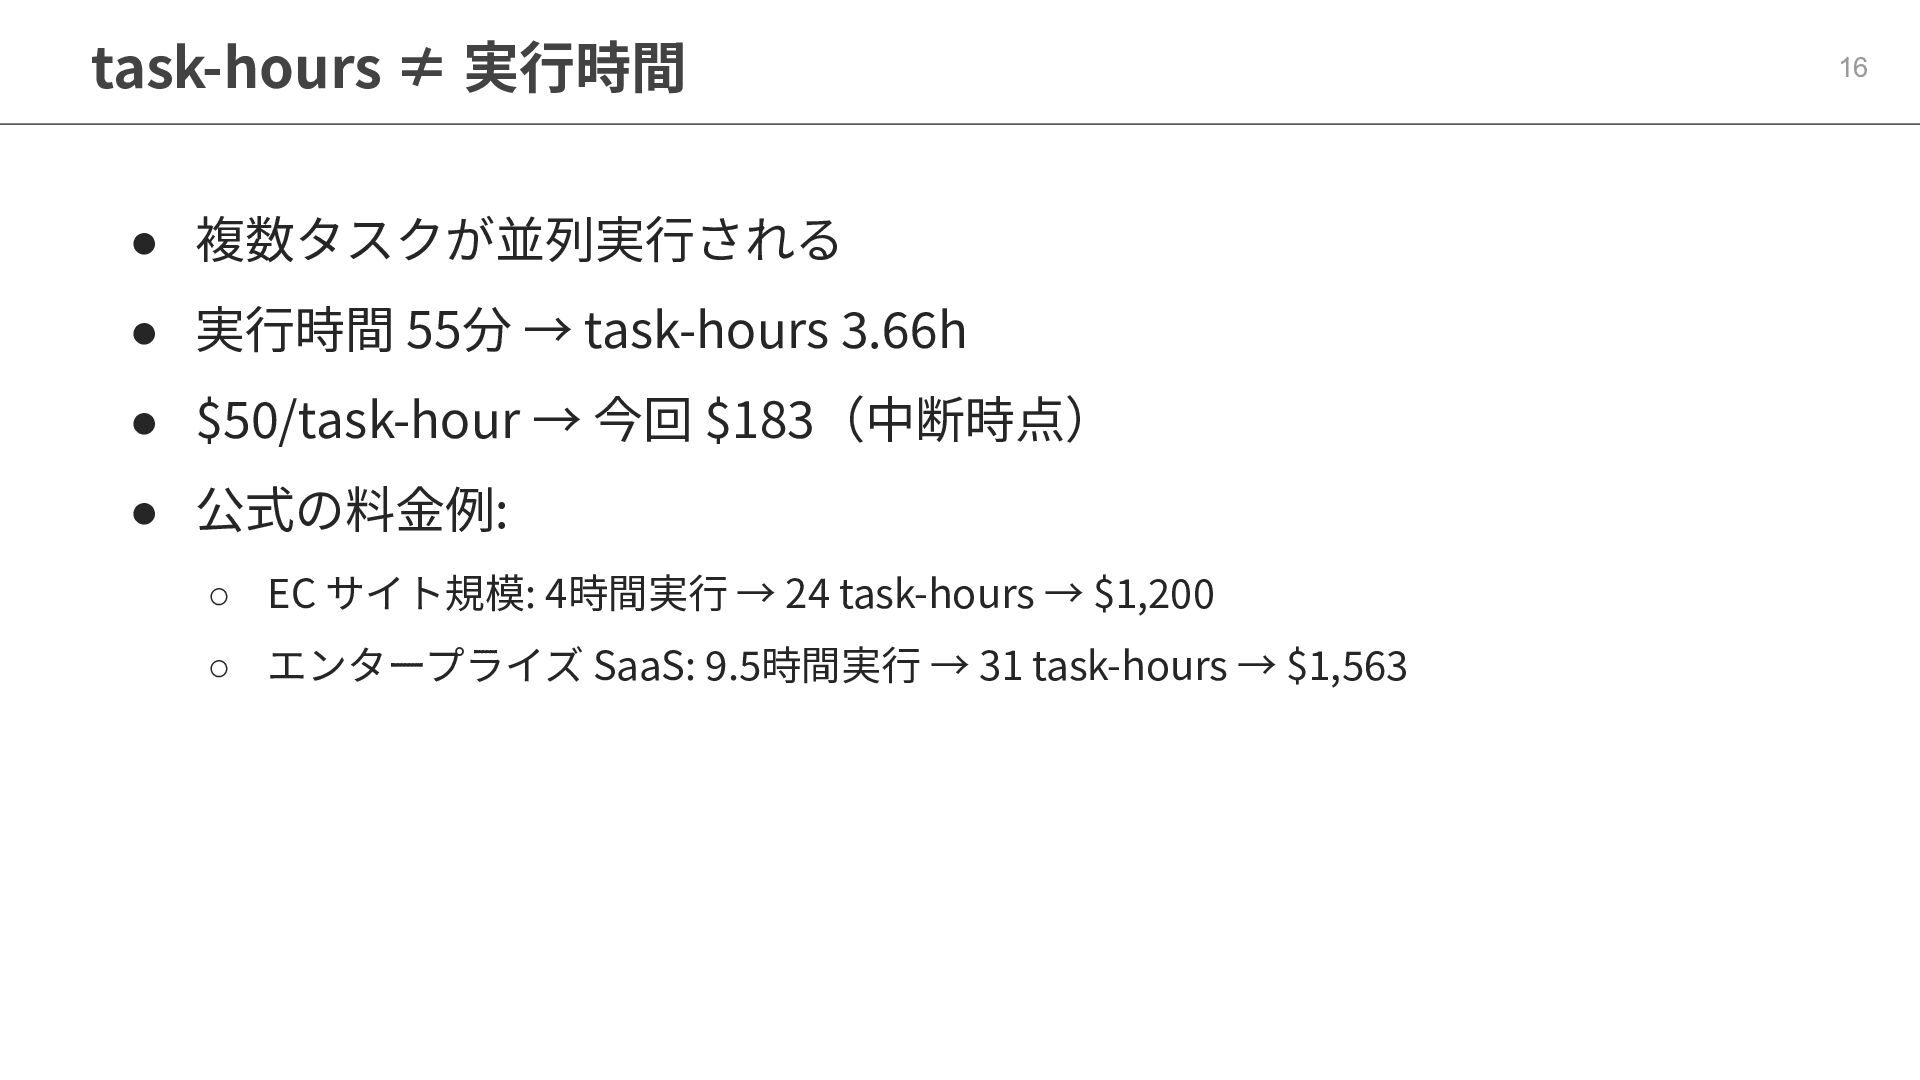
task-hours ≠ 実⾏時間 16 • 複数タスクが並列実⾏される • 実⾏時間 55分 →
task-hours 3.66h • $50/task-hour → 今回 $183(中断時点) • 公式の料⾦例: ◦ EC サイト規模: 4時間実⾏ → 24 task-hours → $1,200 ◦ エンタープライズ SaaS: 9.5時間実⾏ → 31 task-hours → $1,563
CloudTrail に証跡が残る 17 • securityagent.amazonaws.com でイベント記録 • StartPentestJob / CreatePentest
等 • 開始‧中断のタイムスタンプが残る • SCP とかで Deny すれば実⾏を制限可能
まとめ
まとめ 19 • エージェントはソースコード解析から攻撃まで⾃律的に⾏う • 料⾦は並列実⾏で膨らむ、事前に⾒積もりを • ドメイン検証必須 → ⾃分のアプリにしか実⾏できない安全設計
None


 tak1wa
 addyosmani
 skipperchong
 uxyall
 nwiizo
 marcelosomers
 eileencodes
 lauravandoore
 charlesmeaden
 cassininazir
 aleyda
 helenjbeal
 mkilby