Share
PyCon UK 2017: Everyday security issues and how to avoid them
Security is hard, yet vital for any software these days. After all you don't want to become the laughing stock on hacker news or cause your company to loose billions in shareholder value. This talk won't turn you into a security specialist over night, but you will learn how to avoid common mistakes in your daily work as developer or administrator.
I'm going to take you on a brief tour in secure software design, illustrate various attack vectors, and point you to helpful tools and resources. Topics include threat analysis, deployment, parsing, authentication, TLS/SSL, crypto, and user interaction, with some real life examples from my daily work as security engineer and Python core contributor.
http://2017.pyconuk.org/sessions/talks/everyday-security-issues-and-how-to-avoid-them/
Christian Heimes
Transcript
84 slides
-
Everyday security issues and how to avoid them PyCon UK
2017 / Cardiff Christian Heimes Senior Software Engineer [email protected] / [email protected] @ChristianHeimes -
Everyday security issues, PyCon UK 2017 2 Who am I?
• from Hamburg/Germany • Python dev since 2003 • Python core contributor since 2008 • PEP 370, 454, 456, 543 • maintainer of ssl and hashlib module -
Everyday security issues, PyCon UK 2017 3 Professional life •
Senior Software Engineer at Red Hat • Security Engineering • OpenShift security team • FreeIPA Identity Management • Dogtag PKI • Custudia secrets management -
Everyday security issues, PyCon UK 2017 5 • Motivation •
What is security? • Honourable mention • Security bottom-up • Python security • Files and I/O, • Parsing • Input validation • Cryptography • Summary Agenda -
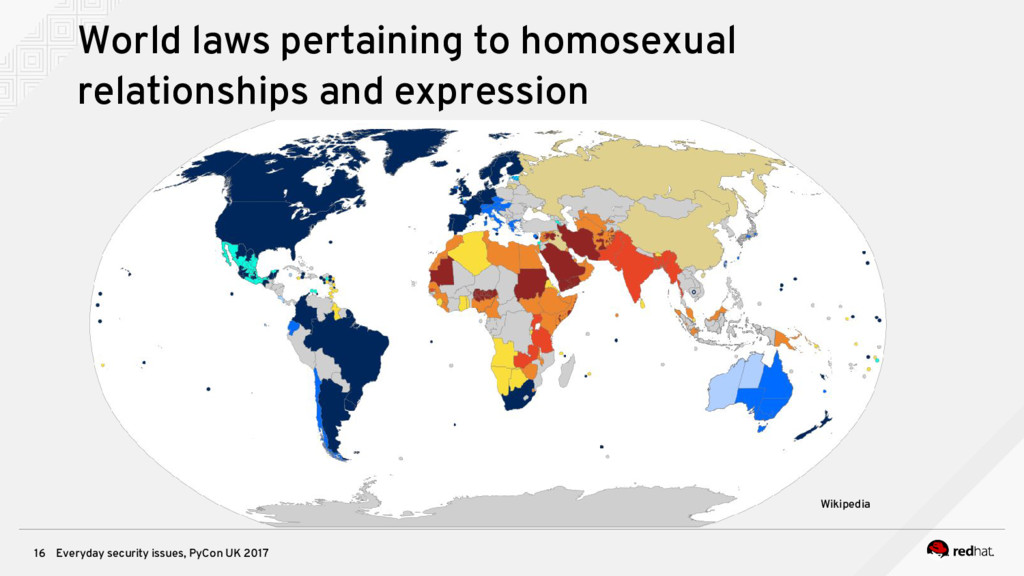
Everyday security issues, PyCon UK 2017 16 World laws pertaining
to homosexual relationships and expression Wikipedia -
Everyday security issues, PyCon UK 2017 18 Wikipedia definition Information
security is the practice of preventing unauthorized access, use, disclosure, disruption, modification, inspection, recording or destruction of information. -
Everyday security issues, PyCon UK 2017 19 Info Sec •
prevention • mitigation • auditing • recovery • privacy -
Everyday security issues, PyCon UK 2017 20 Why is security
hard? • complex systems • weakest link causes catastrophic failures • secure is not testable • design issues • multitude of attack vectors • threat analysis -
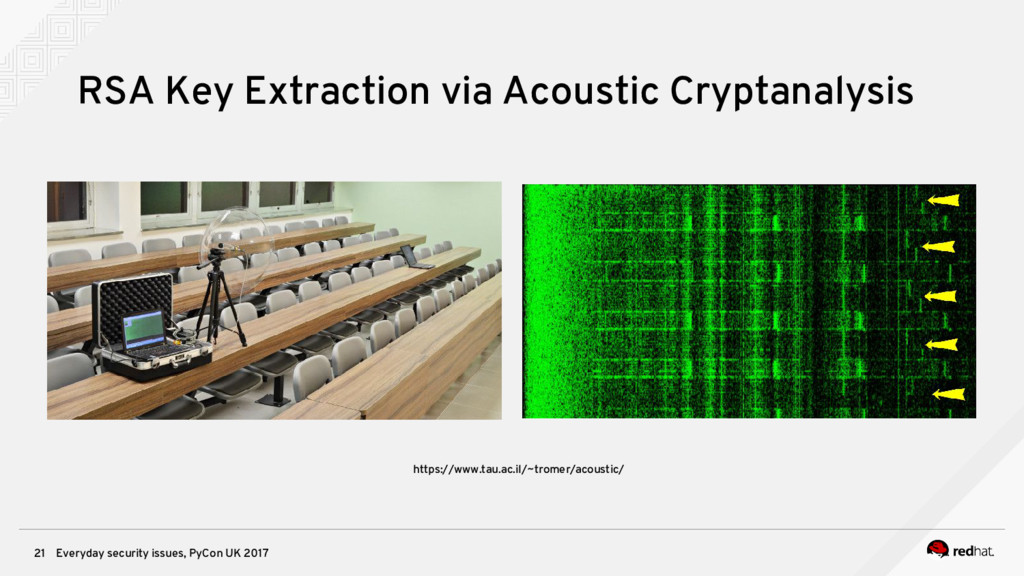
Everyday security issues, PyCon UK 2017 21 RSA Key Extraction
via Acoustic Cryptanalysis https://www.tau.ac.il/~tromer/acoustic/ -
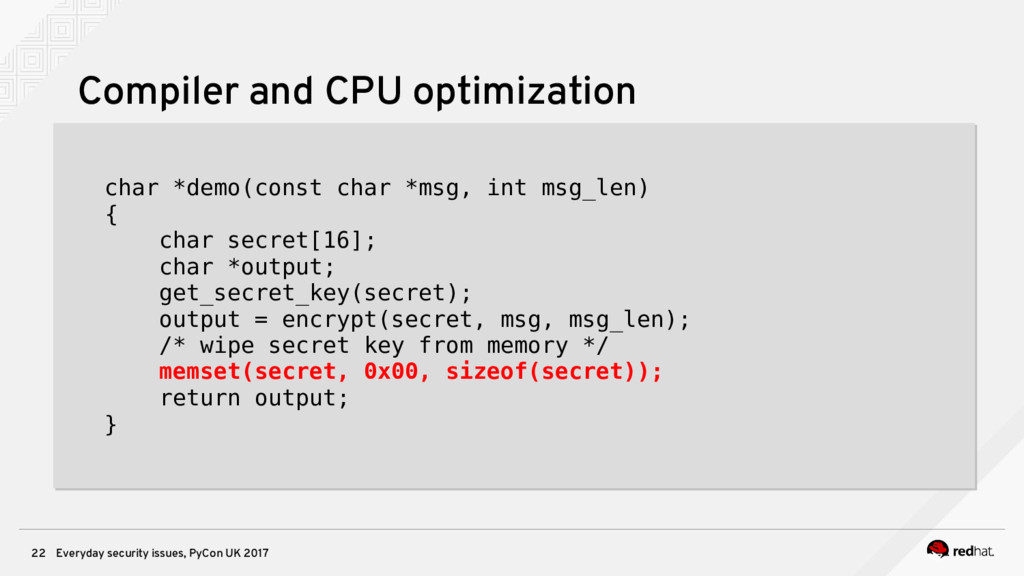
Everyday security issues, PyCon UK 2017 22 Compiler and CPU
optimization char *demo(const char *msg, int msg_len) { char secret[16]; char *output; get_secret_key(secret); output = encrypt(secret, msg, msg_len); /* wipe secret key from memory */ memset(secret, 0x00, sizeof(secret)); return output; } char *demo(const char *msg, int msg_len) { char secret[16]; char *output; get_secret_key(secret); output = encrypt(secret, msg, msg_len); /* wipe secret key from memory */ memset(secret, 0x00, sizeof(secret)); return output; } -
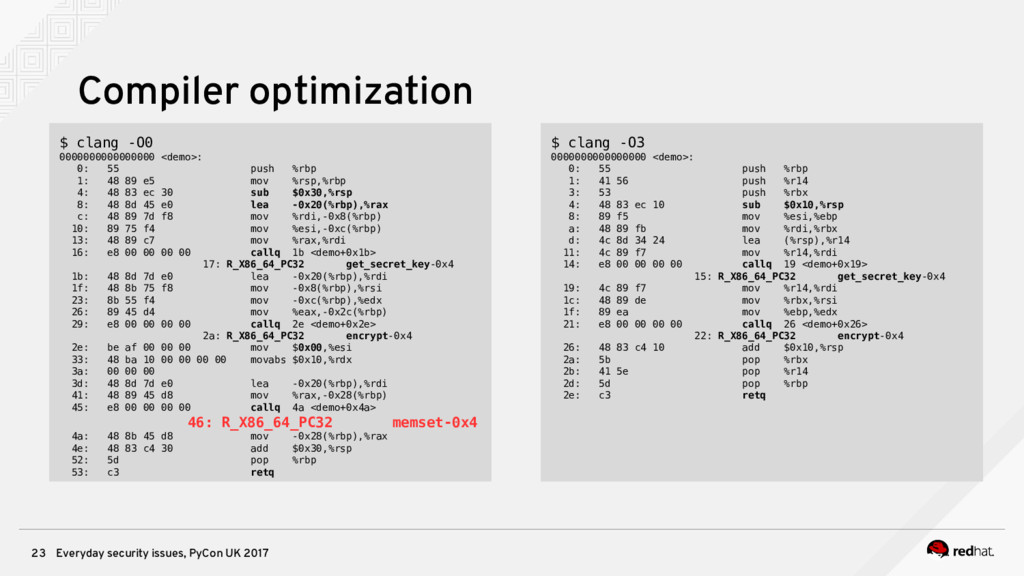
Everyday security issues, PyCon UK 2017 23 Compiler optimization $
clang -O3 0000000000000000 <demo>: 0: 55 push %rbp 1: 41 56 push %r14 3: 53 push %rbx 4: 48 83 ec 10 sub $0x10,%rsp 8: 89 f5 mov %esi,%ebp a: 48 89 fb mov %rdi,%rbx d: 4c 8d 34 24 lea (%rsp),%r14 11: 4c 89 f7 mov %r14,%rdi 14: e8 00 00 00 00 callq 19 <demo+0x19> 15: R_X86_64_PC32 get_secret_key-0x4 19: 4c 89 f7 mov %r14,%rdi 1c: 48 89 de mov %rbx,%rsi 1f: 89 ea mov %ebp,%edx 21: e8 00 00 00 00 callq 26 <demo+0x26> 22: R_X86_64_PC32 encrypt-0x4 26: 48 83 c4 10 add $0x10,%rsp 2a: 5b pop %rbx 2b: 41 5e pop %r14 2d: 5d pop %rbp 2e: c3 retq $ clang -O0 0000000000000000 <demo>: 0: 55 push %rbp 1: 48 89 e5 mov %rsp,%rbp 4: 48 83 ec 30 sub $0x30,%rsp 8: 48 8d 45 e0 lea -0x20(%rbp),%rax c: 48 89 7d f8 mov %rdi,-0x8(%rbp) 10: 89 75 f4 mov %esi,-0xc(%rbp) 13: 48 89 c7 mov %rax,%rdi 16: e8 00 00 00 00 callq 1b <demo+0x1b> 17: R_X86_64_PC32 get_secret_key-0x4 1b: 48 8d 7d e0 lea -0x20(%rbp),%rdi 1f: 48 8b 75 f8 mov -0x8(%rbp),%rsi 23: 8b 55 f4 mov -0xc(%rbp),%edx 26: 89 45 d4 mov %eax,-0x2c(%rbp) 29: e8 00 00 00 00 callq 2e <demo+0x2e> 2a: R_X86_64_PC32 encrypt-0x4 2e: be af 00 00 00 mov $0x00,%esi 33: 48 ba 10 00 00 00 00 movabs $0x10,%rdx 3a: 00 00 00 3d: 48 8d 7d e0 lea -0x20(%rbp),%rdi 41: 48 89 45 d8 mov %rax,-0x28(%rbp) 45: e8 00 00 00 00 callq 4a <demo+0x4a> 46: R_X86_64_PC32 memset-0x4 4a: 48 8b 45 d8 mov -0x28(%rbp),%rax 4e: 48 83 c4 30 add $0x30,%rsp 52: 5d pop %rbp 53: c3 retq -
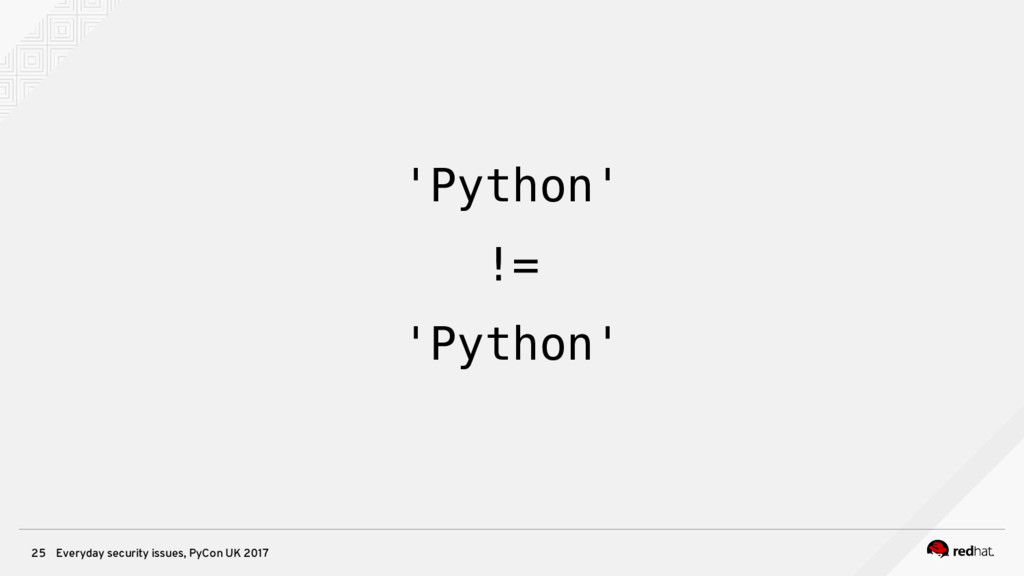
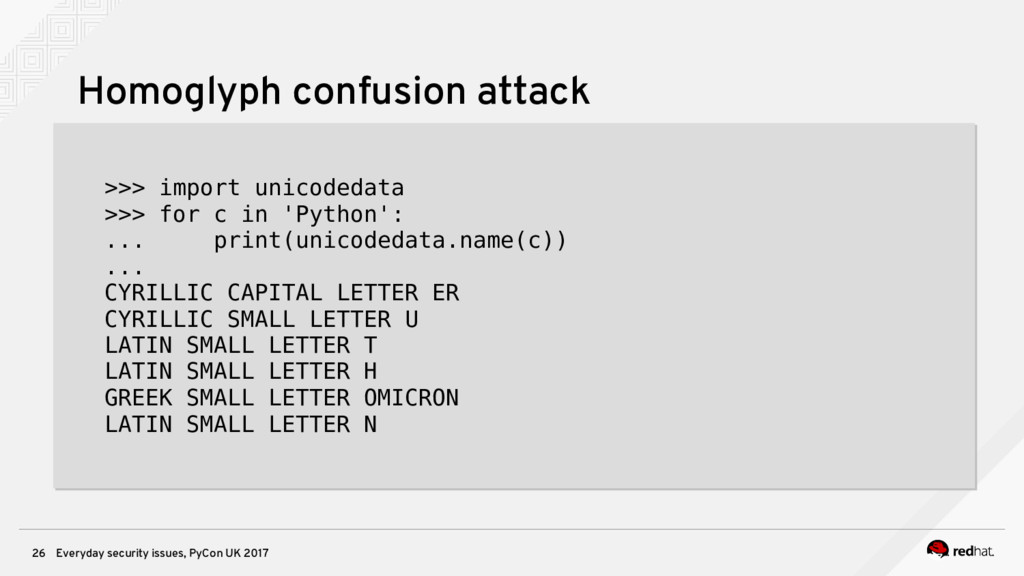
Everyday security issues, PyCon UK 2017 26 Homoglyph confusion attack
>>> import unicodedata >>> for c in 'Руthοn': ... print(unicodedata.name(c)) ... CYRILLIC CAPITAL LETTER ER CYRILLIC SMALL LETTER U LATIN SMALL LETTER T LATIN SMALL LETTER H GREEK SMALL LETTER OMICRON LATIN SMALL LETTER N >>> import unicodedata >>> for c in 'Руthοn': ... print(unicodedata.name(c)) ... CYRILLIC CAPITAL LETTER ER CYRILLIC SMALL LETTER U LATIN SMALL LETTER T LATIN SMALL LETTER H GREEK SMALL LETTER OMICRON LATIN SMALL LETTER N -
Everyday security issues, PyCon UK 2017 28 Out of scope
• legal requirements (e.g. EU privacy shield, FISMA) • data centre security • hardware security (e.g. Intel Management Engine) • browser / web security • ransomware • state sponsored actors • cyber war -
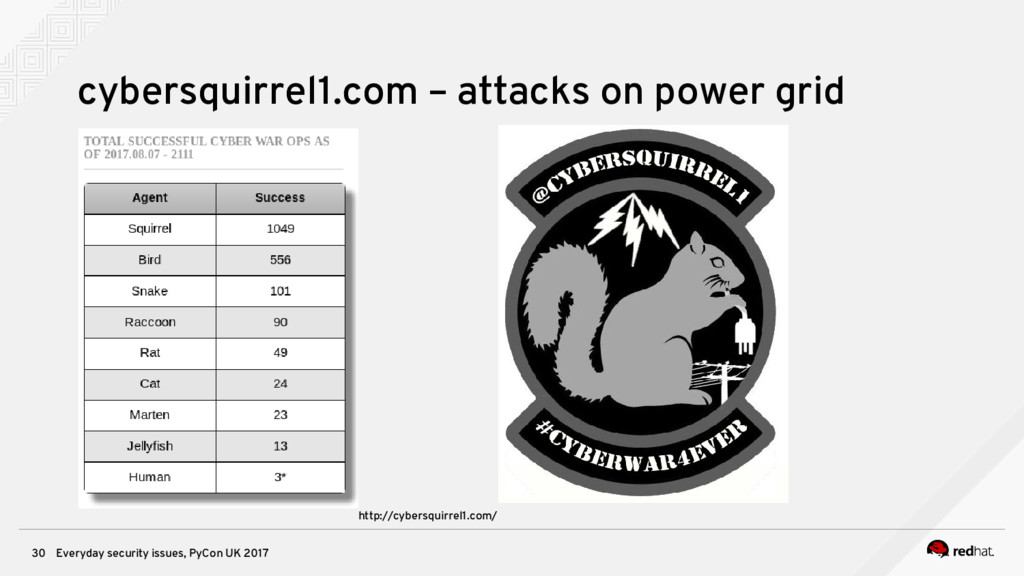
Everyday security issues, PyCon UK 2017 30 cybersquirrel1.com – attacks
on power grid http://cybersquirrel1.com/ -
Everyday security issues, PyCon UK 2017 31 Human factor •
Social engineer • CEO scam: Ubiquiti Networks victim of $39 million https://www.csoonline.com/article/2961066/supply-chain-security/ubiquiti-networks-victim-of-39-million-social- engineering-attack.html • Password in exchange for chocolate (up to 47.9%) Université du Luxembourg, Computers in Human Behavior, 2016; 61: 372 DOI: 10.1016/j.chb.2016.03.026 • dissatisfied employees • ignorant management -
Everyday security issues, PyCon UK 2017 33 IoT – Internet
of Things The “S” in “IoT” stands for security. The “P” in “IoT” stands for privacy. (Sorry, German humour) -
Everyday security issues, PyCon UK 2017 35 Hardware & OS
• Hardware from trustworthy vendor • validate OS image • UEFI secure boot (protect your MOK) • Firewall • update, update, update • SELinux / AppArmor don't: setenforce 0 do: semanage permissive -a myapp_t -
Everyday security issues, PyCon UK 2017 36 Application • don't
run as root or admin • Restrict and isolate separate user, group systemd: PrivateTmp, Protectsystem, RemoveIPC, CapabilityBoundingSet, … SecComp sandboxing • encrypt in transit (TLS/SSL), encrypt at rest • bind to localhost • strong authentication • update, update, update … and restart! -
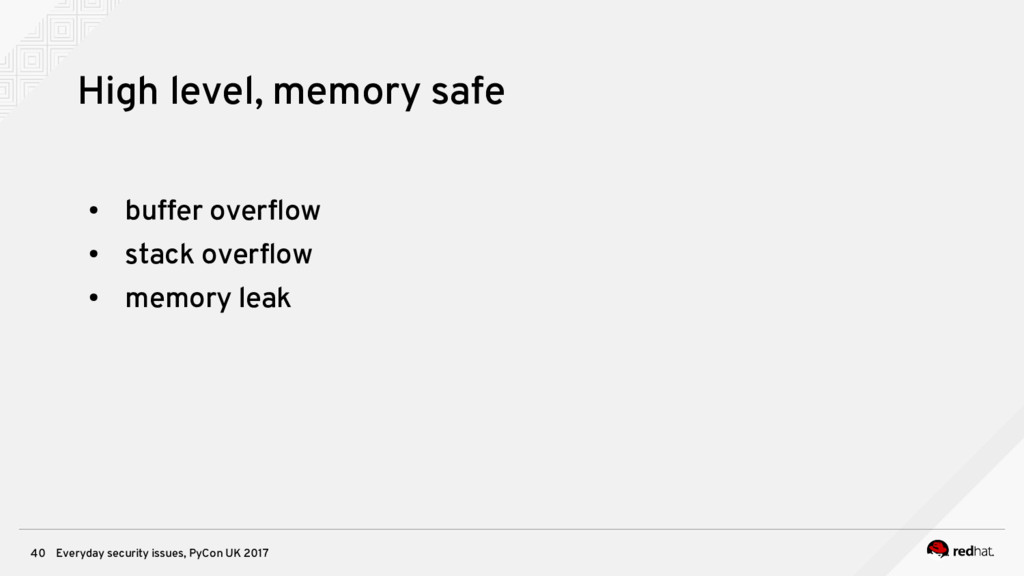
Everyday security issues, PyCon UK 2017 40 High level, memory
safe • buffer overflow • stack overflow • memory leak -
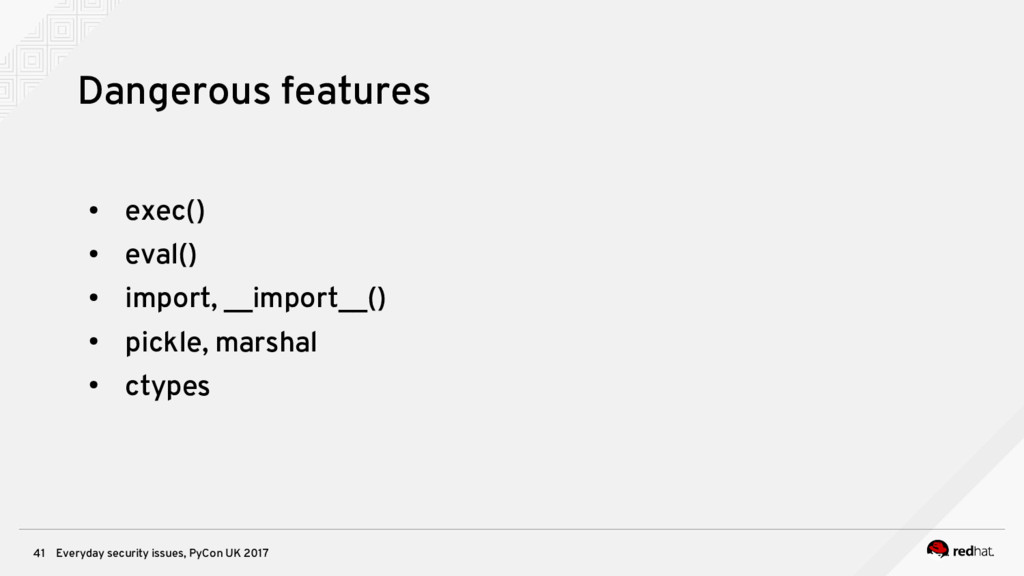
Everyday security issues, PyCon UK 2017 41 Dangerous features •
exec() • eval() • import, __import__() • pickle, marshal • ctypes -
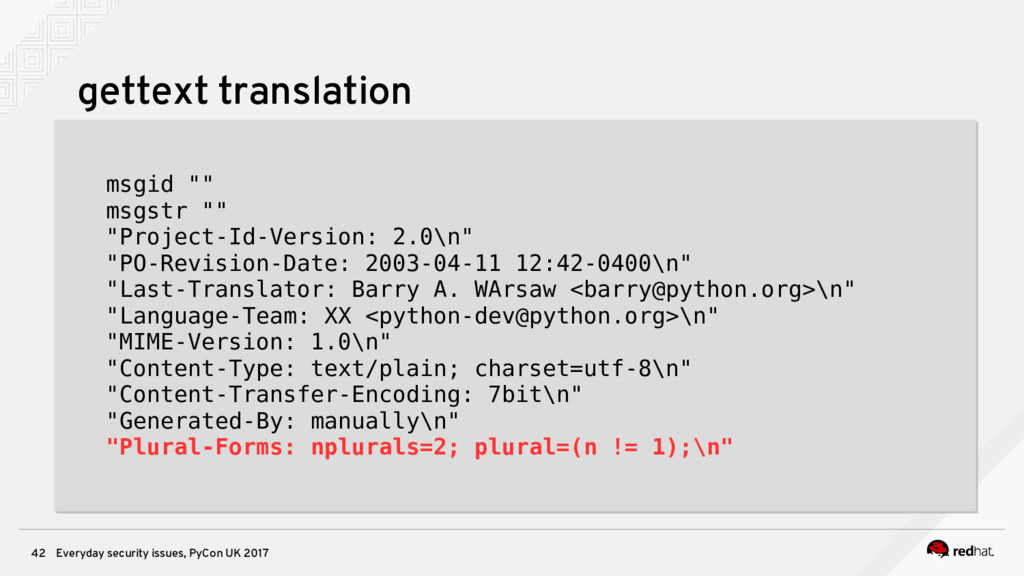
Everyday security issues, PyCon UK 2017 42 gettext translation msgid
"" msgstr "" "Project-Id-Version: 2.0\n" "PO-Revision-Date: 2003-04-11 12:42-0400\n" "Last-Translator: Barry A. WArsaw <[email protected]>\n" "Language-Team: XX <[email protected]>\n" "MIME-Version: 1.0\n" "Content-Type: text/plain; charset=utf-8\n" "Content-Transfer-Encoding: 7bit\n" "Generated-By: manually\n" "Plural-Forms: nplurals=2; plural=(n != 1);\n" msgid "" msgstr "" "Project-Id-Version: 2.0\n" "PO-Revision-Date: 2003-04-11 12:42-0400\n" "Last-Translator: Barry A. WArsaw <[email protected]>\n" "Language-Team: XX <[email protected]>\n" "MIME-Version: 1.0\n" "Content-Type: text/plain; charset=utf-8\n" "Content-Transfer-Encoding: 7bit\n" "Generated-By: manually\n" "Plural-Forms: nplurals=2; plural=(n != 1);\n" -
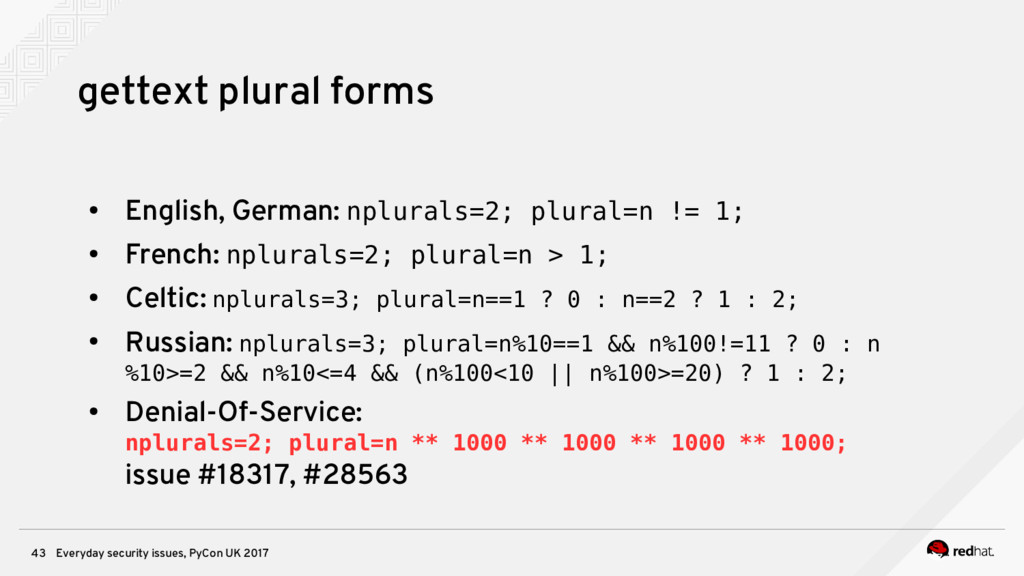
Everyday security issues, PyCon UK 2017 43 gettext plural forms
• English, German: nplurals=2; plural=n != 1; • French: nplurals=2; plural=n > 1; • Celtic: nplurals=3; plural=n==1 ? 0 : n==2 ? 1 : 2; • Russian: nplurals=3; plural=n%10==1 && n%100!=11 ? 0 : n %10>=2 && n%10<=4 && (n%100<10 || n%100>=20) ? 1 : 2; • Denial-Of-Service: nplurals=2; plural=n ** 1000 ** 1000 ** 1000 ** 1000; issue #18317, #28563 -
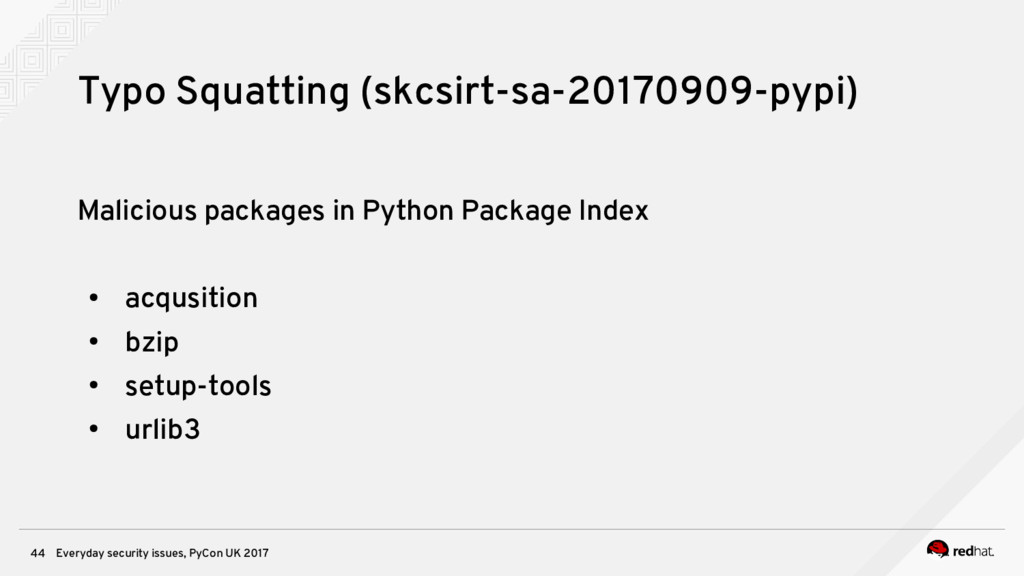
Everyday security issues, PyCon UK 2017 44 Typo Squatting (skcsirt-sa-20170909-pypi)
Malicious packages in Python Package Index • acqusition • bzip • setup-tools • urlib3 -
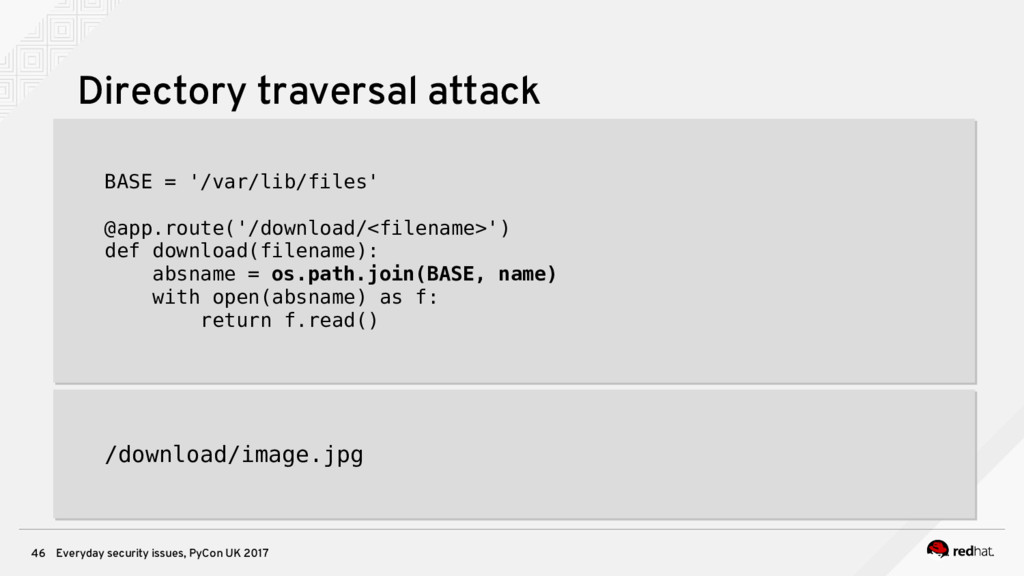
Everyday security issues, PyCon UK 2017 46 Directory traversal attack
BASE = '/var/lib/files' @app.route('/download/<filename>') def download(filename): absname = os.path.join(BASE, name) with open(absname) as f: return f.read() BASE = '/var/lib/files' @app.route('/download/<filename>') def download(filename): absname = os.path.join(BASE, name) with open(absname) as f: return f.read() /download/image.jpg /download/image.jpg -
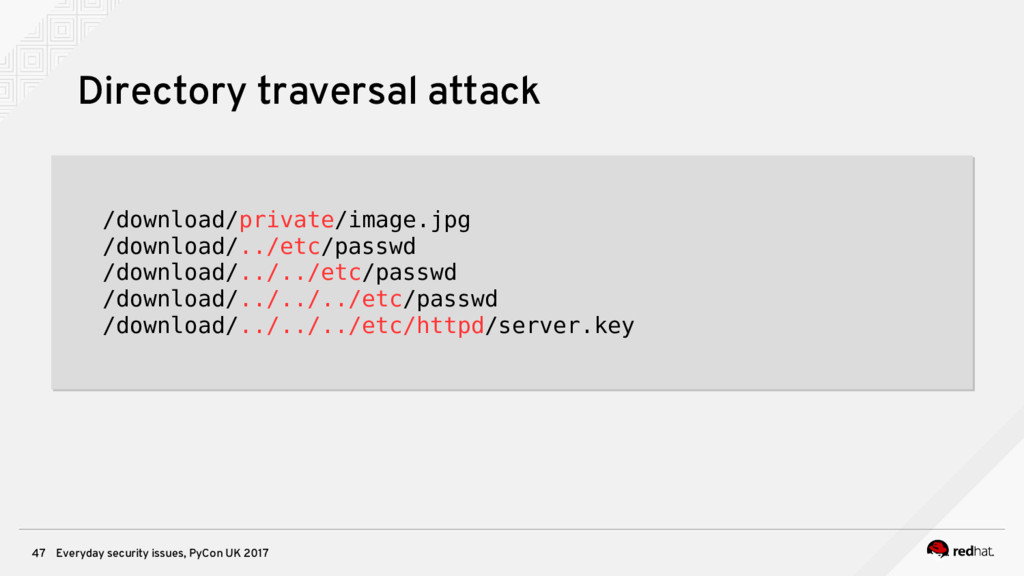
Everyday security issues, PyCon UK 2017 47 Directory traversal attack
/download/private/image.jpg /download/../etc/passwd /download/../../etc/passwd /download/../../../etc/passwd /download/../../../etc/httpd/server.key /download/private/image.jpg /download/../etc/passwd /download/../../etc/passwd /download/../../../etc/passwd /download/../../../etc/httpd/server.key -
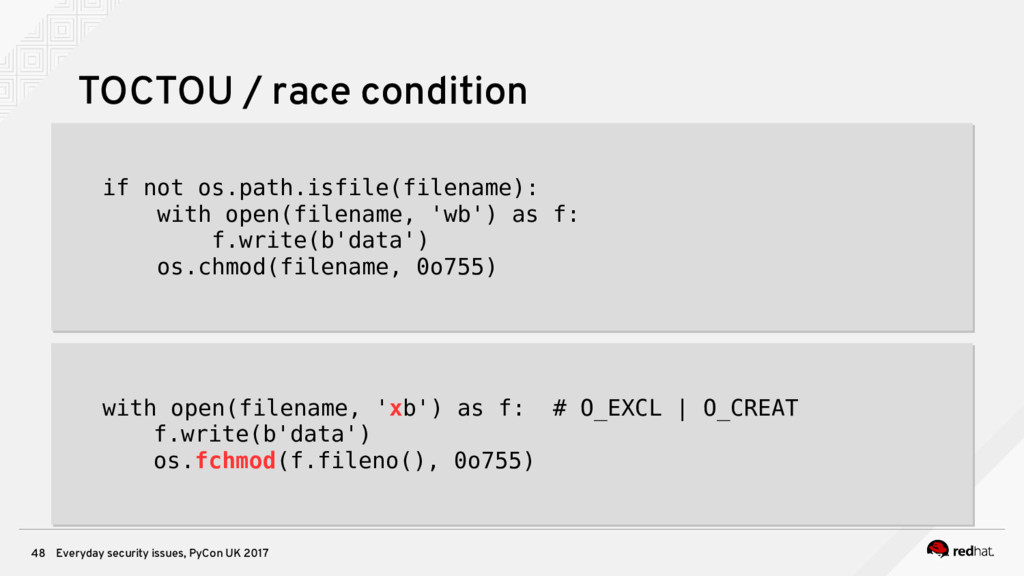
Everyday security issues, PyCon UK 2017 48 TOCTOU / race
condition if not os.path.isfile(filename): with open(filename, 'wb') as f: f.write(b'data') os.chmod(filename, 0o755) if not os.path.isfile(filename): with open(filename, 'wb') as f: f.write(b'data') os.chmod(filename, 0o755) with open(filename, 'xb') as f: # O_EXCL | O_CREAT f.write(b'data') os.fchmod(f.fileno(), 0o755) with open(filename, 'xb') as f: # O_EXCL | O_CREAT f.write(b'data') os.fchmod(f.fileno(), 0o755) -
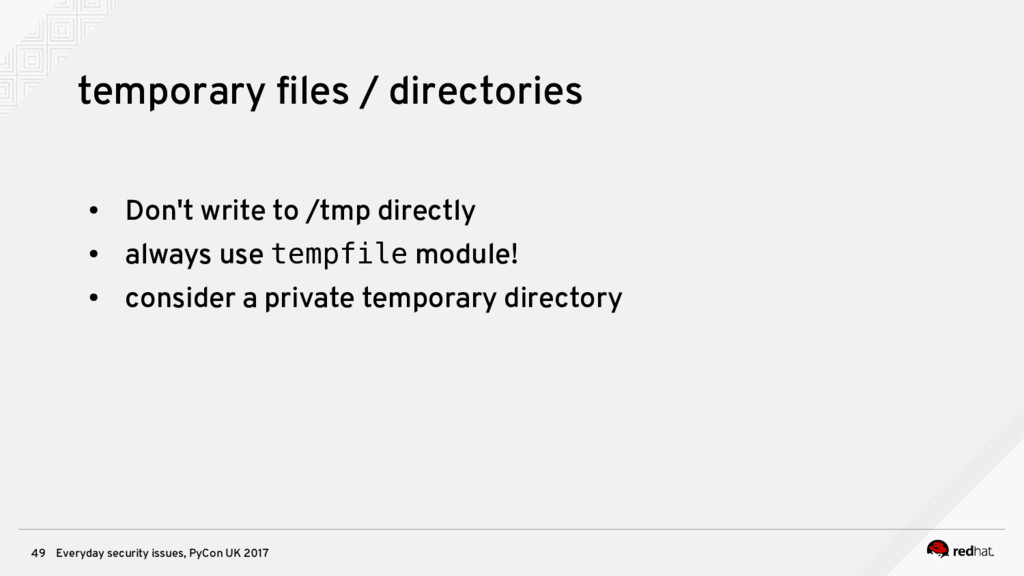
Everyday security issues, PyCon UK 2017 49 temporary files /
directories • Don't write to /tmp directly • always use tempfile module! • consider a private temporary directory -
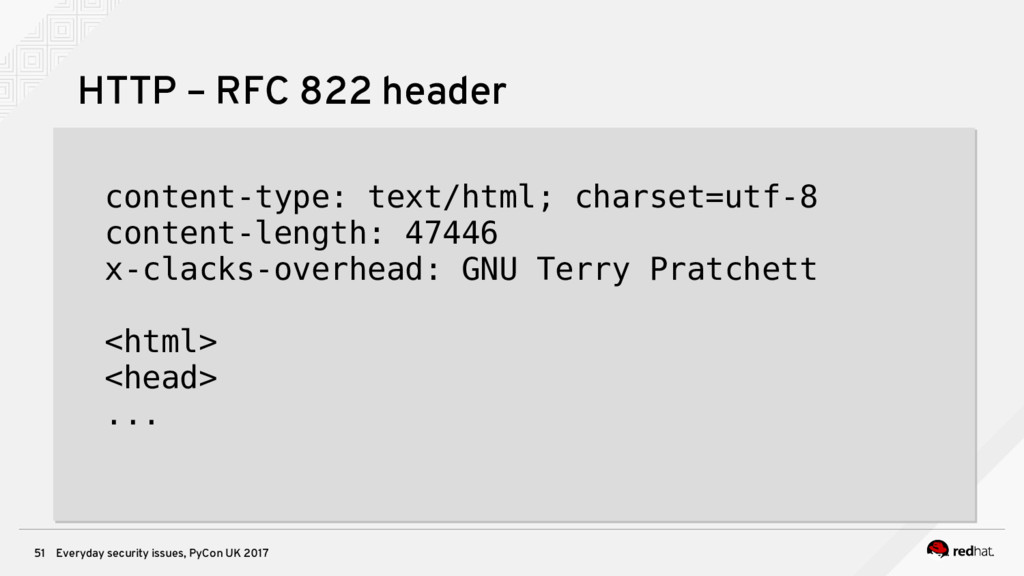
Everyday security issues, PyCon UK 2017 51 HTTP – RFC
822 header content-type: text/html; charset=utf-8 content-length: 47446 x-clacks-overhead: GNU Terry Pratchett <html> <head> ... content-type: text/html; charset=utf-8 content-length: 47446 x-clacks-overhead: GNU Terry Pratchett <html> <head> ... -
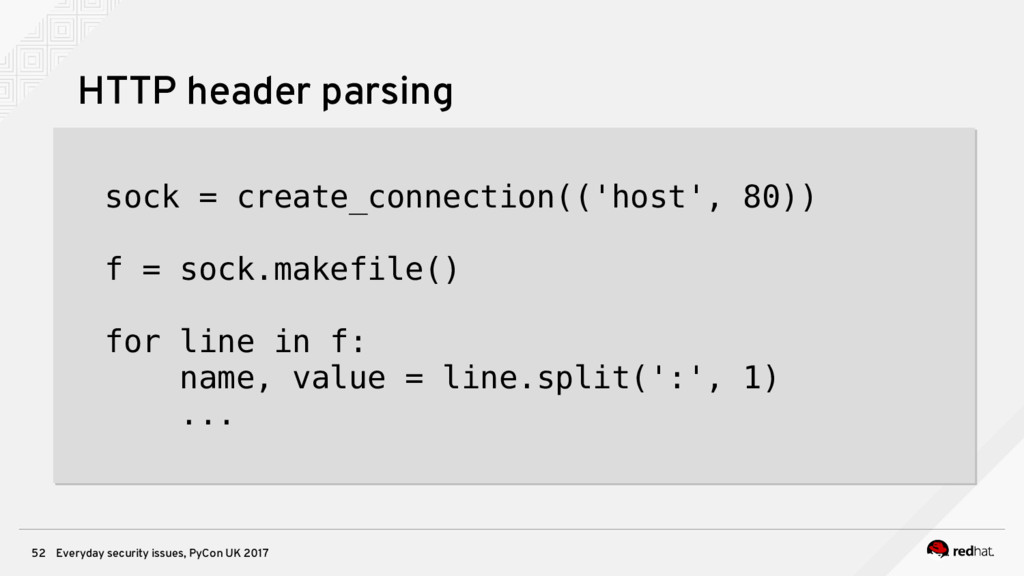
Everyday security issues, PyCon UK 2017 52 HTTP header parsing
sock = create_connection(('host', 80)) f = sock.makefile() for line in f: name, value = line.split(':', 1) ... sock = create_connection(('host', 80)) f = sock.makefile() for line in f: name, value = line.split(':', 1) ... -
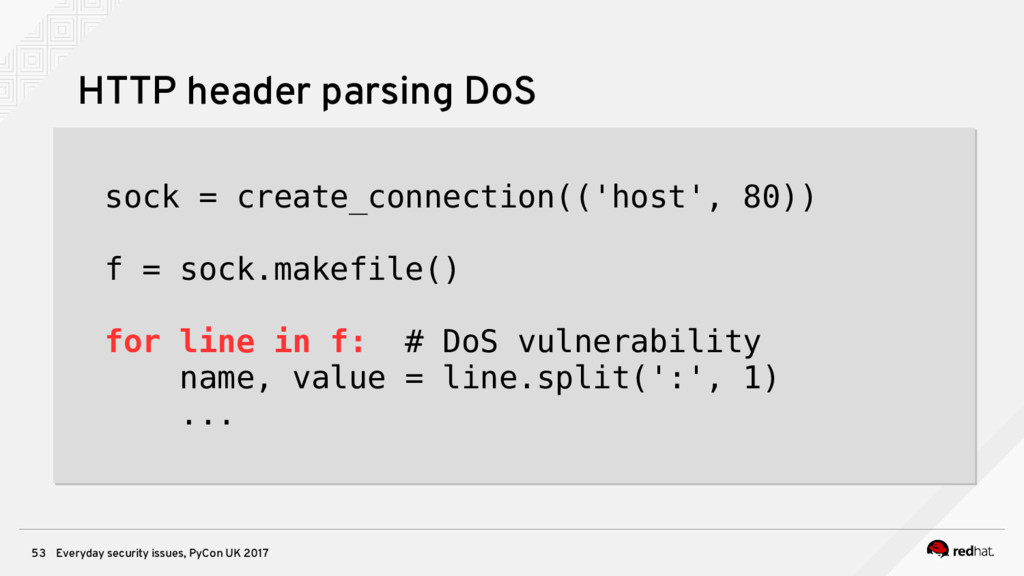
Everyday security issues, PyCon UK 2017 53 HTTP header parsing
DoS sock = create_connection(('host', 80)) f = sock.makefile() for line in f: # DoS vulnerability name, value = line.split(':', 1) ... sock = create_connection(('host', 80)) f = sock.makefile() for line in f: # DoS vulnerability name, value = line.split(':', 1) ... -
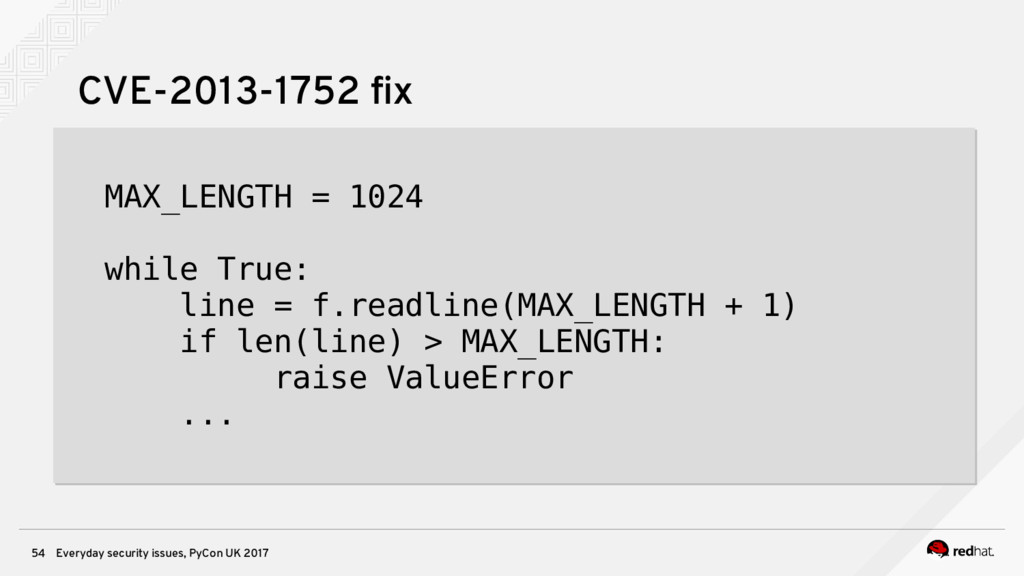
Everyday security issues, PyCon UK 2017 54 CVE-2013-1752 fix MAX_LENGTH
= 1024 while True: line = f.readline(MAX_LENGTH + 1) if len(line) > MAX_LENGTH: raise ValueError ... MAX_LENGTH = 1024 while True: line = f.readline(MAX_LENGTH + 1) if len(line) > MAX_LENGTH: raise ValueError ... -
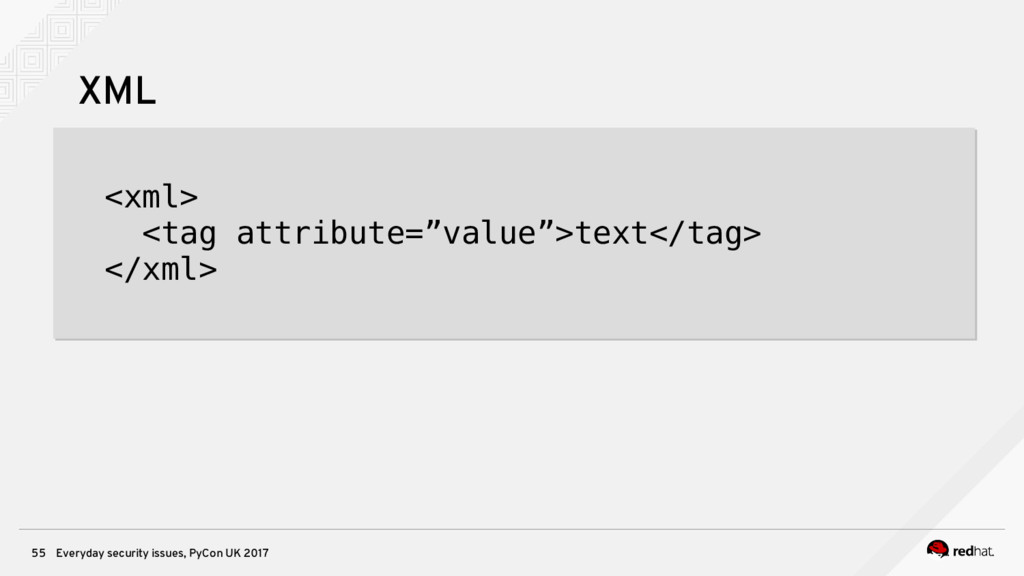
Everyday security issues, PyCon UK 2017 55 XML <xml> <tag
attribute=”value”>text</tag> </xml> <xml> <tag attribute=”value”>text</tag> </xml> -
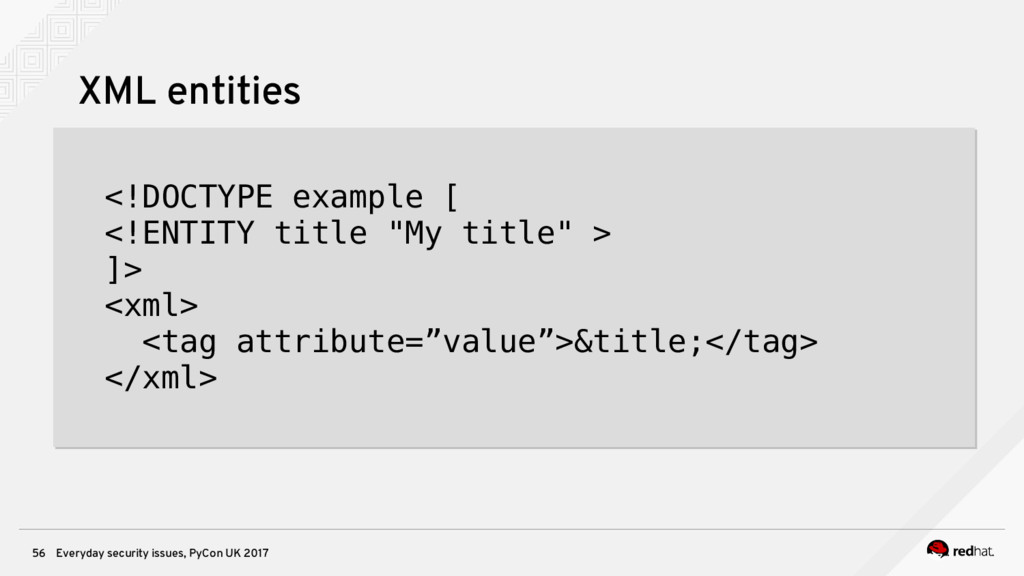
Everyday security issues, PyCon UK 2017 56 XML entities <!DOCTYPE
example [ <!ENTITY title "My title" > ]> <xml> <tag attribute=”value”>&title;</tag> </xml> <!DOCTYPE example [ <!ENTITY title "My title" > ]> <xml> <tag attribute=”value”>&title;</tag> </xml> -
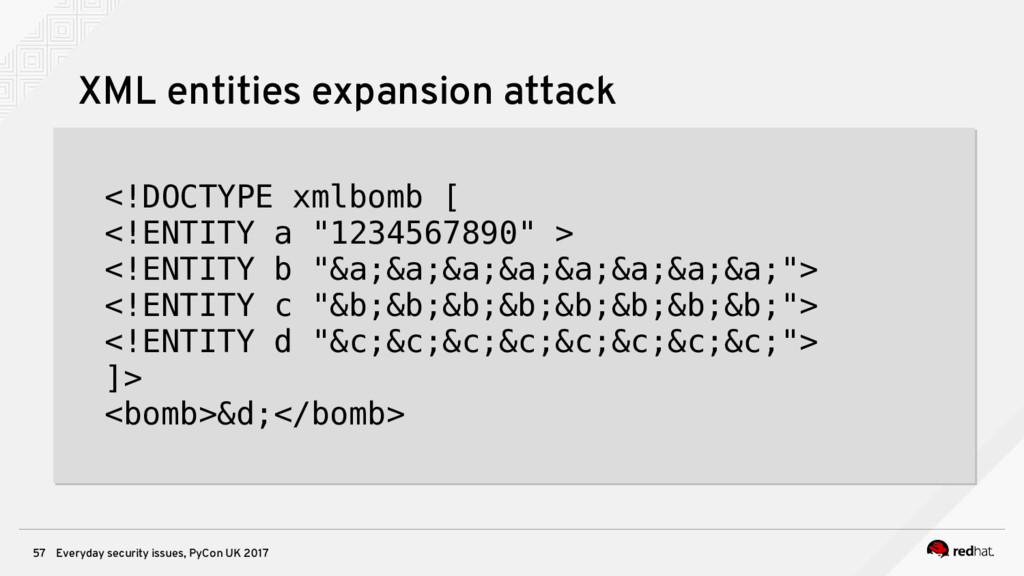
Everyday security issues, PyCon UK 2017 57 XML entities expansion
attack <!DOCTYPE xmlbomb [ <!ENTITY a "1234567890" > <!ENTITY b "&a;&a;&a;&a;&a;&a;&a;&a;"> <!ENTITY c "&b;&b;&b;&b;&b;&b;&b;&b;"> <!ENTITY d "&c;&c;&c;&c;&c;&c;&c;&c;"> ]> <bomb>&d;</bomb> <!DOCTYPE xmlbomb [ <!ENTITY a "1234567890" > <!ENTITY b "&a;&a;&a;&a;&a;&a;&a;&a;"> <!ENTITY c "&b;&b;&b;&b;&b;&b;&b;&b;"> <!ENTITY d "&c;&c;&c;&c;&c;&c;&c;&c;"> ]> <bomb>&d;</bomb> -
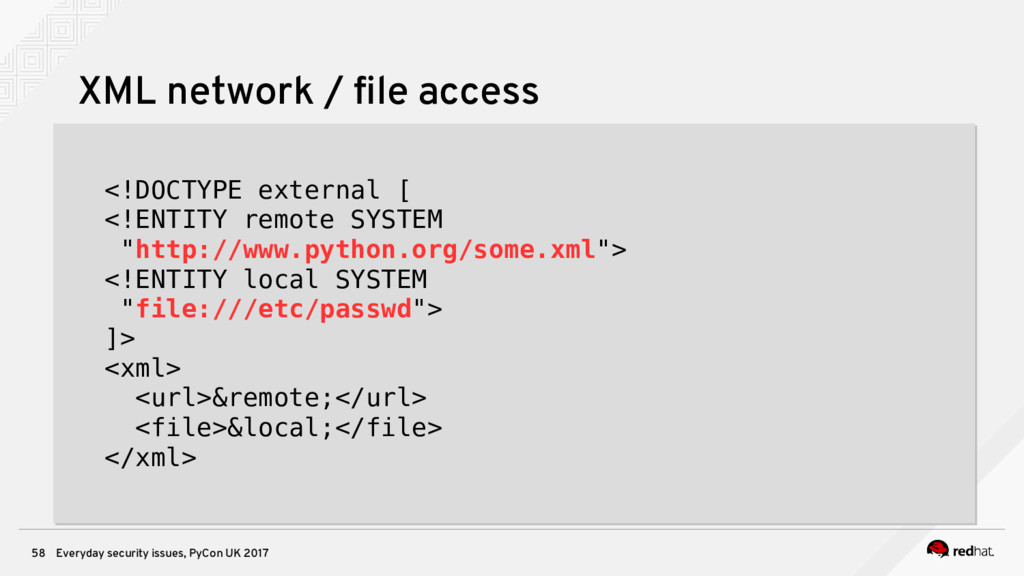
Everyday security issues, PyCon UK 2017 58 XML network /
file access <!DOCTYPE external [ <!ENTITY remote SYSTEM "http://www.python.org/some.xml"> <!ENTITY local SYSTEM "file:///etc/passwd"> ]> <xml> <url>&remote;</url> <file>&local;</file> </xml> <!DOCTYPE external [ <!ENTITY remote SYSTEM "http://www.python.org/some.xml"> <!ENTITY local SYSTEM "file:///etc/passwd"> ]> <xml> <url>&remote;</url> <file>&local;</file> </xml> -
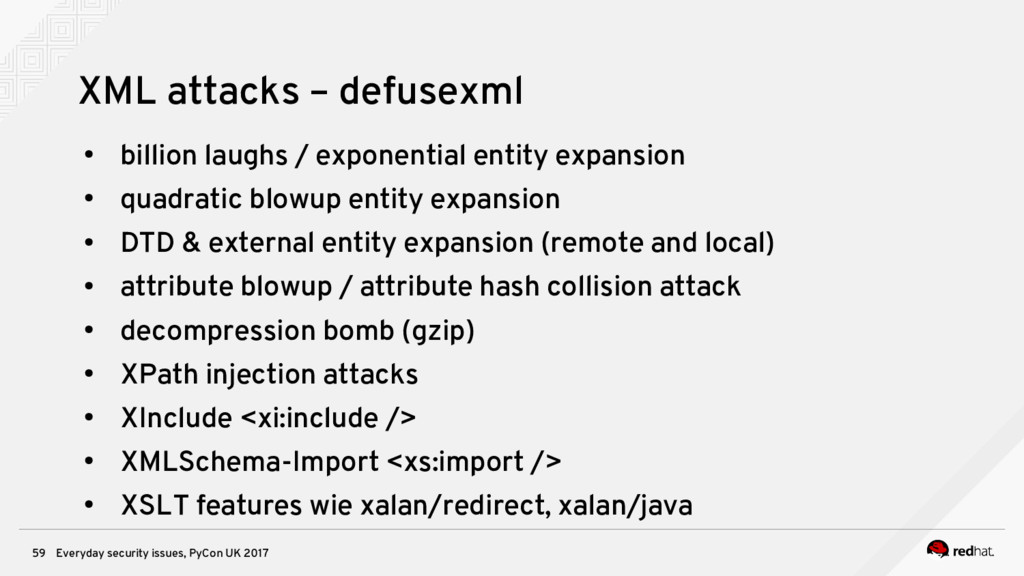
Everyday security issues, PyCon UK 2017 59 XML attacks –
defusexml • billion laughs / exponential entity expansion • quadratic blowup entity expansion • DTD & external entity expansion (remote and local) • attribute blowup / attribute hash collision attack • decompression bomb (gzip) • XPath injection attacks • XInclude <xi:include /> • XMLSchema-Import <xs:import /> • XSLT features wie xalan/redirect, xalan/java -
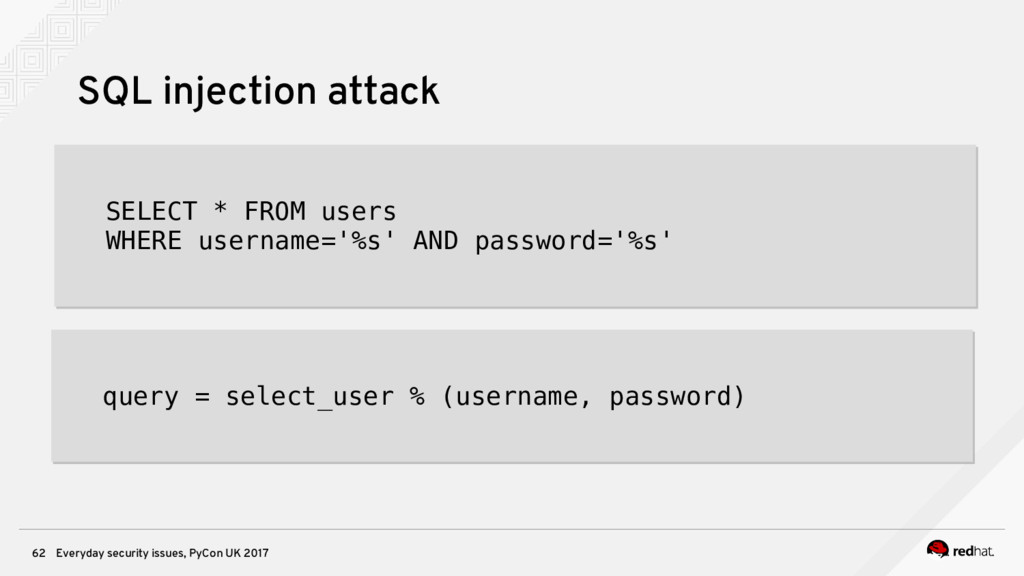
Everyday security issues, PyCon UK 2017 62 SQL injection attack
SELECT * FROM users WHERE username='%s' AND password='%s' SELECT * FROM users WHERE username='%s' AND password='%s' query = select_user % (username, password) query = select_user % (username, password) -
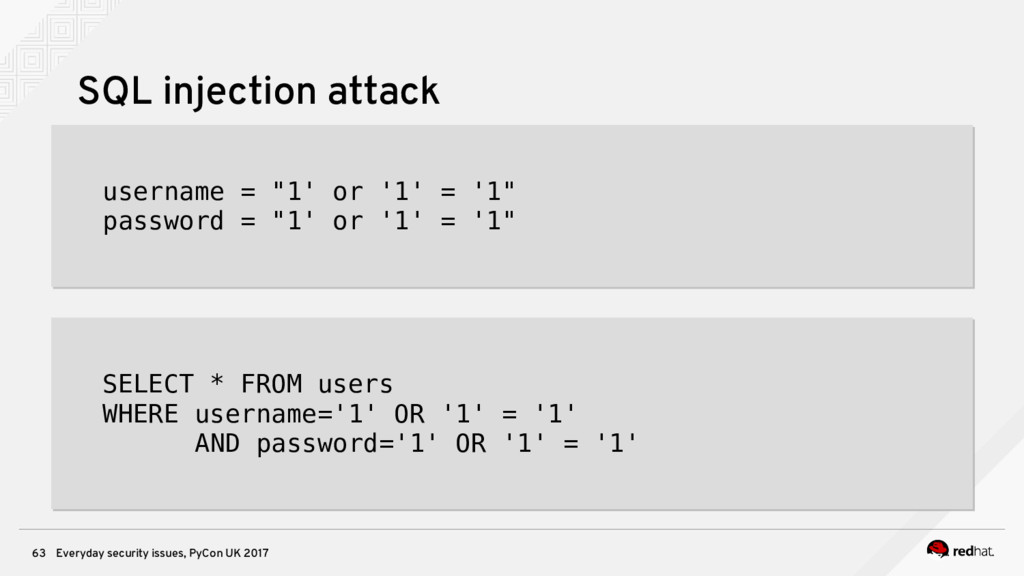
Everyday security issues, PyCon UK 2017 63 SQL injection attack
SELECT * FROM users WHERE username='1' OR '1' = '1' AND password='1' OR '1' = '1' SELECT * FROM users WHERE username='1' OR '1' = '1' AND password='1' OR '1' = '1' username = "1' or '1' = '1" password = "1' or '1' = '1" username = "1' or '1' = '1" password = "1' or '1' = '1" -
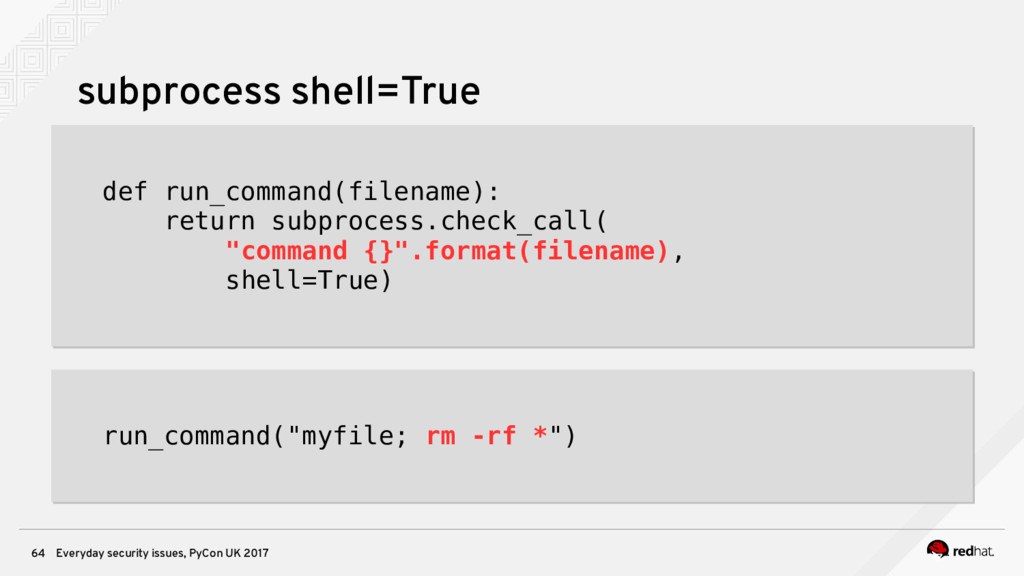
Everyday security issues, PyCon UK 2017 64 subprocess shell=True run_command("myfile;
rm -rf *") run_command("myfile; rm -rf *") def run_command(filename): return subprocess.check_call( "command {}".format(filename), shell=True) def run_command(filename): return subprocess.check_call( "command {}".format(filename), shell=True) -
Everyday security issues, PyCon UK 2017 65 More injection attacks
• SQL • shell • LDAP • XPath / XQuery • NoSQL databases -
Everyday security issues, PyCon UK 2017 67 The first rule
of cryptography: Don't implement your own crypto! -
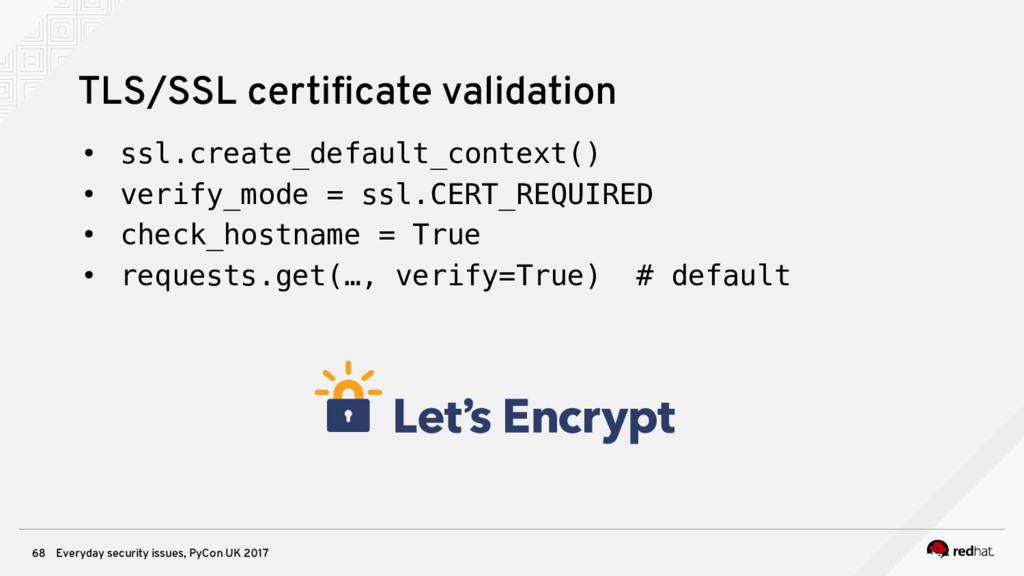
Everyday security issues, PyCon UK 2017 68 TLS/SSL certificate validation
• ssl.create_default_context() • verify_mode = ssl.CERT_REQUIRED • check_hostname = True • requests.get(…, verify=True) # default -
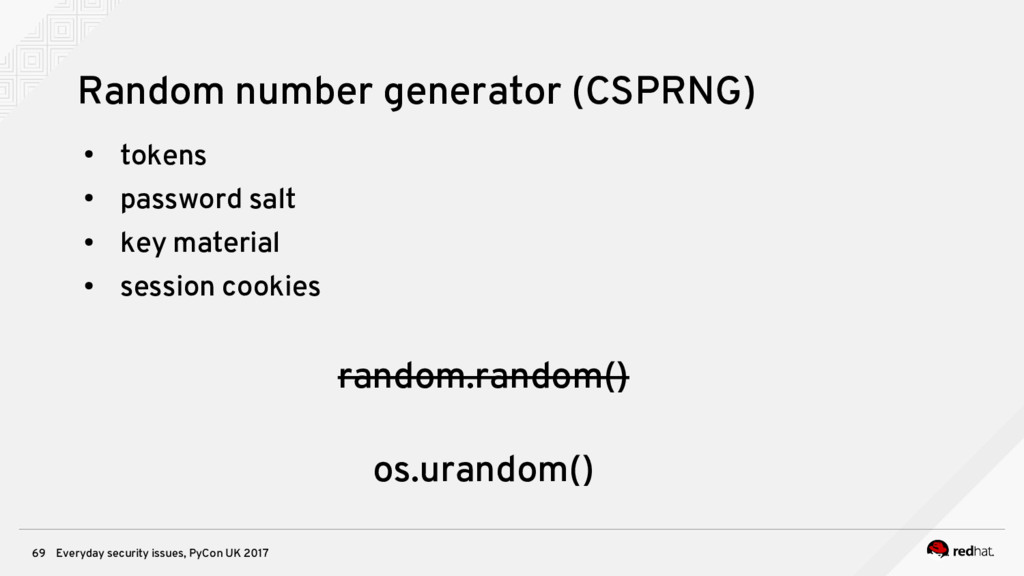
Everyday security issues, PyCon UK 2017 69 Random number generator
(CSPRNG) • tokens • password salt • key material • session cookies random.random() os.urandom() -
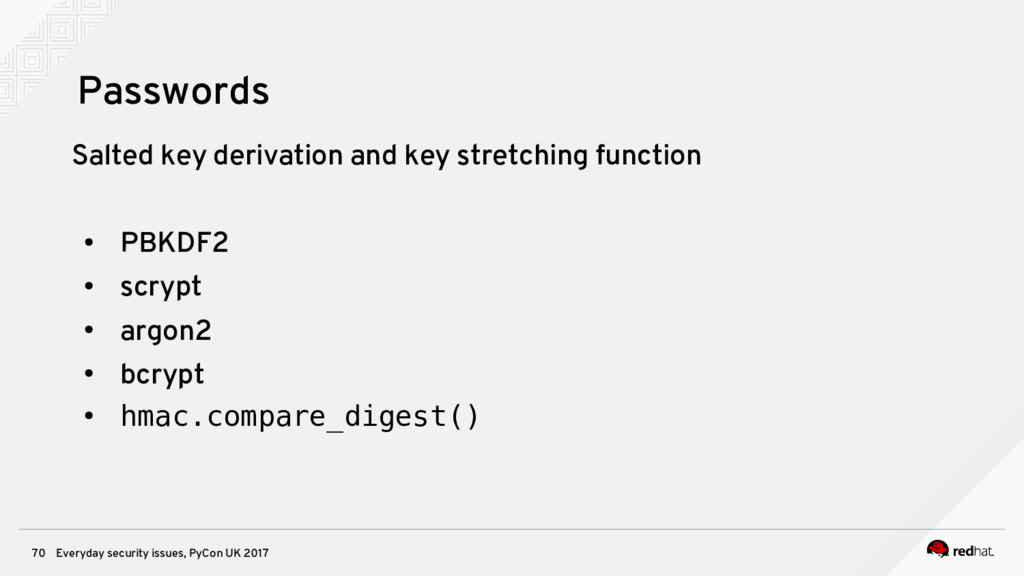
Everyday security issues, PyCon UK 2017 70 Passwords Salted key
derivation and key stretching function • PBKDF2 • scrypt • argon2 • bcrypt • hmac.compare_digest() -
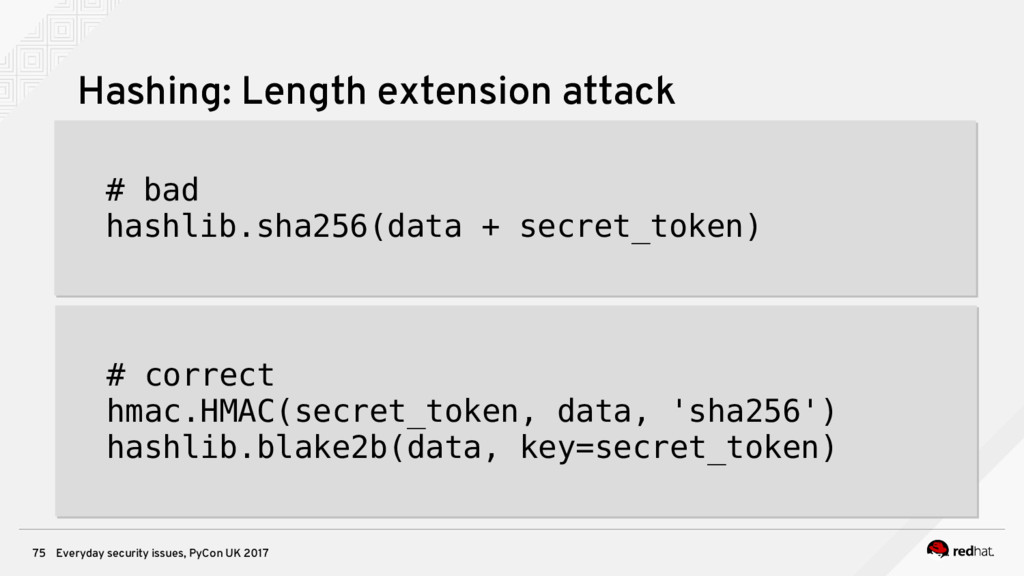
Everyday security issues, PyCon UK 2017 75 Hashing: Length extension
attack # bad hashlib.sha256(data + secret_token) # bad hashlib.sha256(data + secret_token) # correct hmac.HMAC(secret_token, data, 'sha256') hashlib.blake2b(data, key=secret_token) # correct hmac.HMAC(secret_token, data, 'sha256') hashlib.blake2b(data, key=secret_token) -
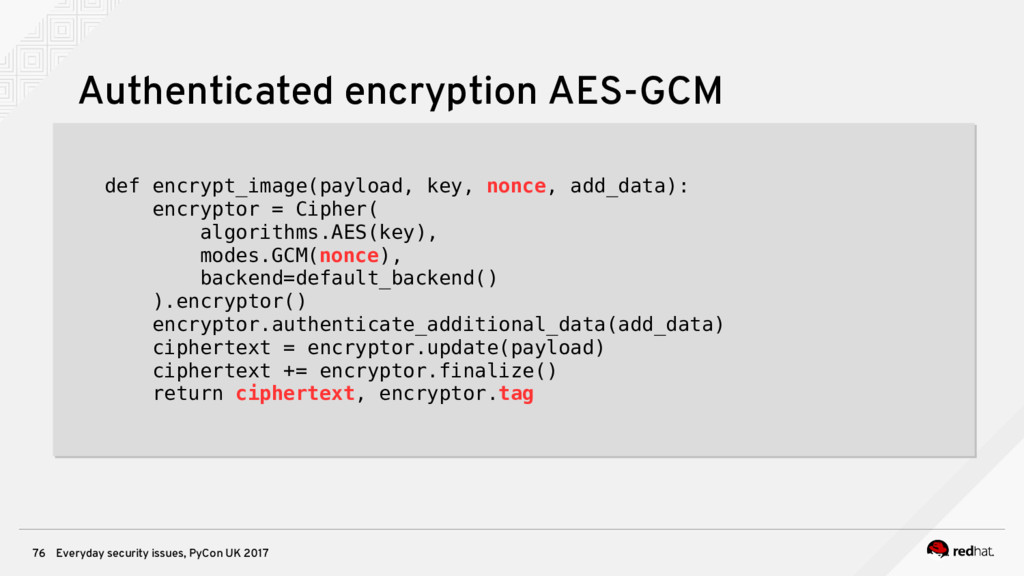
Everyday security issues, PyCon UK 2017 76 Authenticated encryption AES-GCM
def encrypt_image(payload, key, nonce, add_data): encryptor = Cipher( algorithms.AES(key), modes.GCM(nonce), backend=default_backend() ).encryptor() encryptor.authenticate_additional_data(add_data) ciphertext = encryptor.update(payload) ciphertext += encryptor.finalize() return ciphertext, encryptor.tag def encrypt_image(payload, key, nonce, add_data): encryptor = Cipher( algorithms.AES(key), modes.GCM(nonce), backend=default_backend() ).encryptor() encryptor.authenticate_additional_data(add_data) ciphertext = encryptor.update(payload) ciphertext += encryptor.finalize() return ciphertext, encryptor.tag -
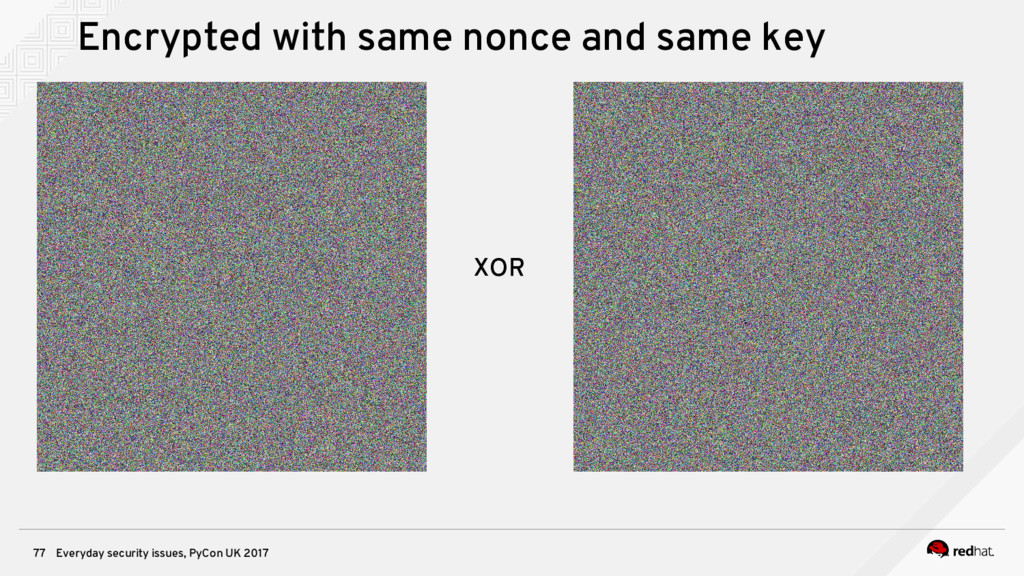
Everyday security issues, PyCon UK 2017 77 XOR Encrypted with
same nonce and same key -
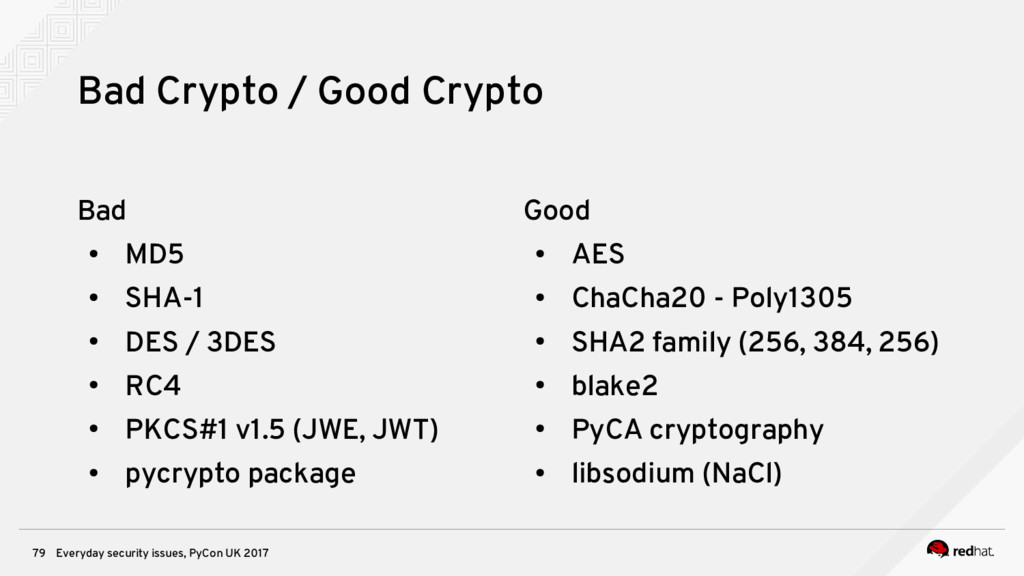
Everyday security issues, PyCon UK 2017 79 Bad Crypto /
Good Crypto Bad • MD5 • SHA-1 • DES / 3DES • RC4 • PKCS#1 v1.5 (JWE, JWT) • pycrypto package Good • AES • ChaCha20 - Poly1305 • SHA2 family (256, 384, 256) • blake2 • PyCA cryptography • libsodium (NaCl) -
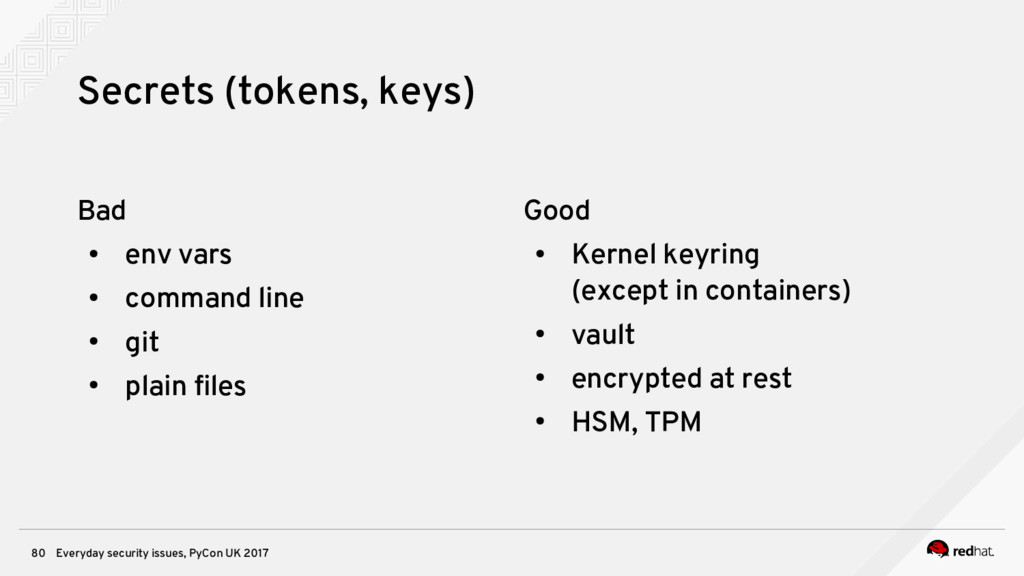
Everyday security issues, PyCon UK 2017 80 Secrets (tokens, keys)
Bad • env vars • command line • git • plain files Good • Kernel keyring (except in containers) • vault • encrypted at rest • HSM, TPM -
Everyday security issues, PyCon UK 2017 83 Summary • educate
• reuse • restrict • encrypt • update • privacy