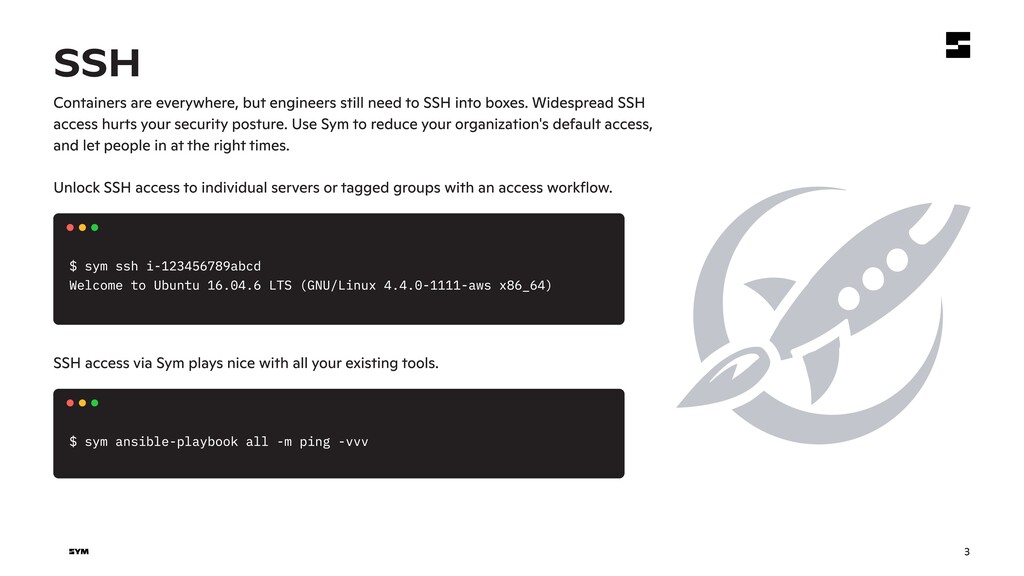
SSH into boxes. Widespread SSH access hurts your security posture. Use Sym to reduce your organization's default access, and let people in at the right times. SSH access via Sym plays nice with all your existing tools. Unlock SSH access to individual servers or tagged groups with an access workflow. $ sym ssh i-123456789abcd Welcome to Ubuntu 16.04.6 LTS (GNU/Linux 4.4.0-1111-aws x86_64) $ sym ansible-playbook all -m ping -vvv
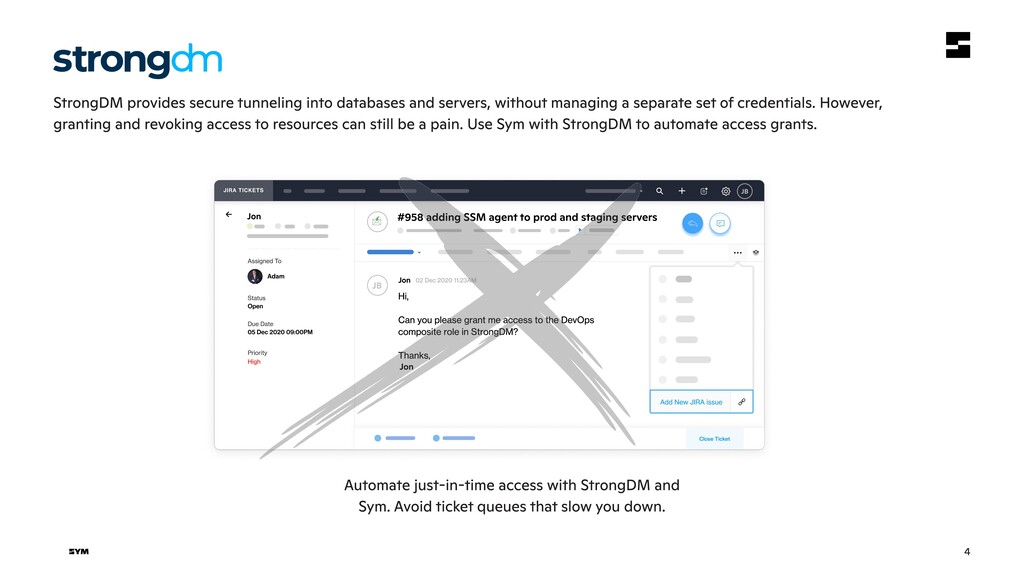
servers Jon Adam JB JB 4 StrongDM provides secure tunneling into databases and servers, without managing a separate set of credentials. However, granting and revoking access to resources can still be a pain. Use Sym with StrongDM to automate access grants. Automate just-in-time access with StrongDM and Sym. Avoid ticket queues that slow you down.
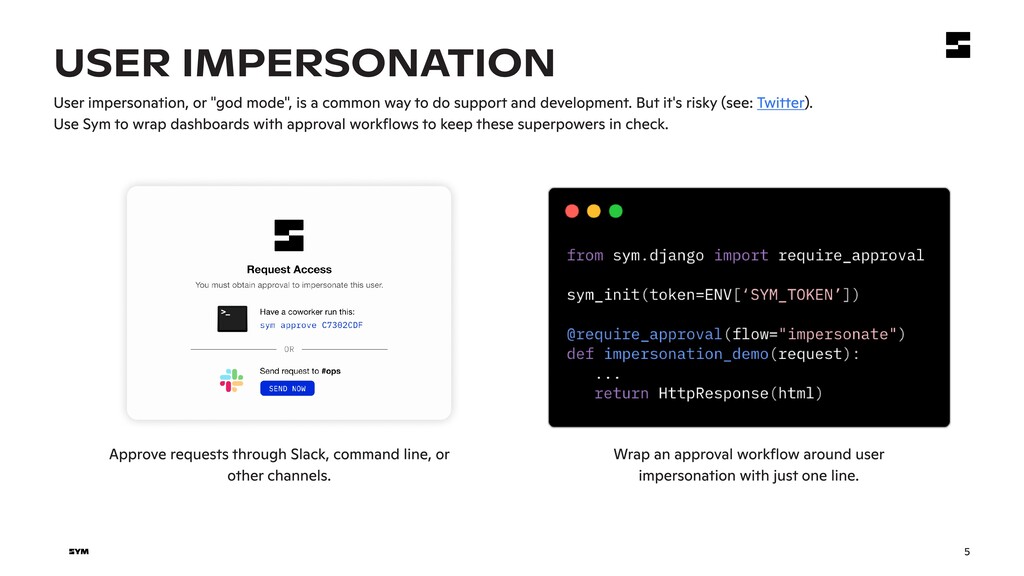
common way to do support and development. But it's risky (see: ). Use Sym to wrap dashboards with approval workflows to keep these superpowers in check. Twitter Wrap an approval workflow around user impersonation with just one line. Approve requests through Slack, command line, or other channels.
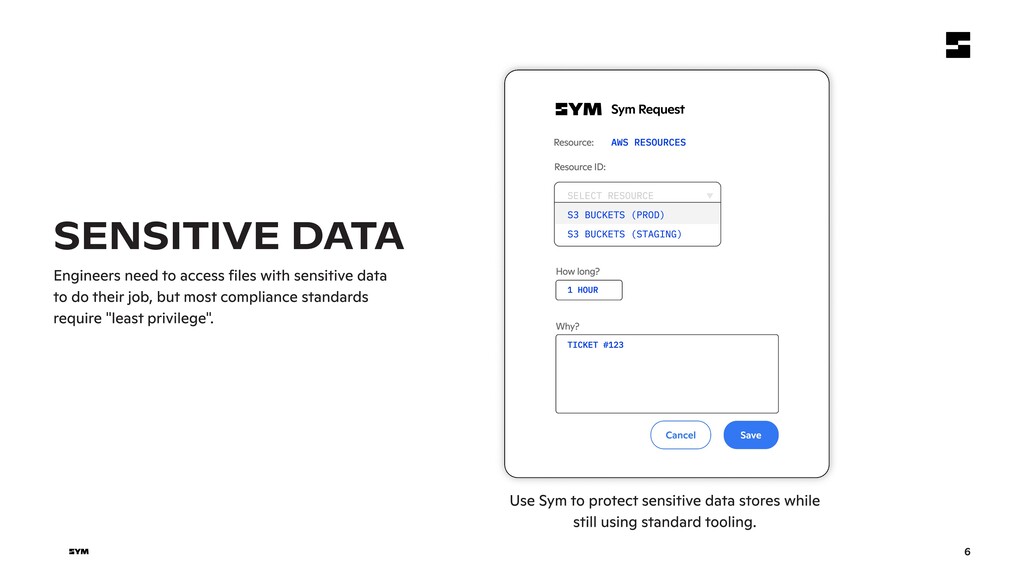
data to do their job, but most compliance standards require "least privilege". Use Sym to protect sensitive data stores while still using standard tooling. Sym Request Resource: Resource ID: How long? Why? Cancel Save AWS RESOURCES S3 BUCKETS (PROD) 1 HOUR TICKET #123 SELECT RESOURCE S3 BUCKETS (PROD) S3 BUCKETS (STAGING)
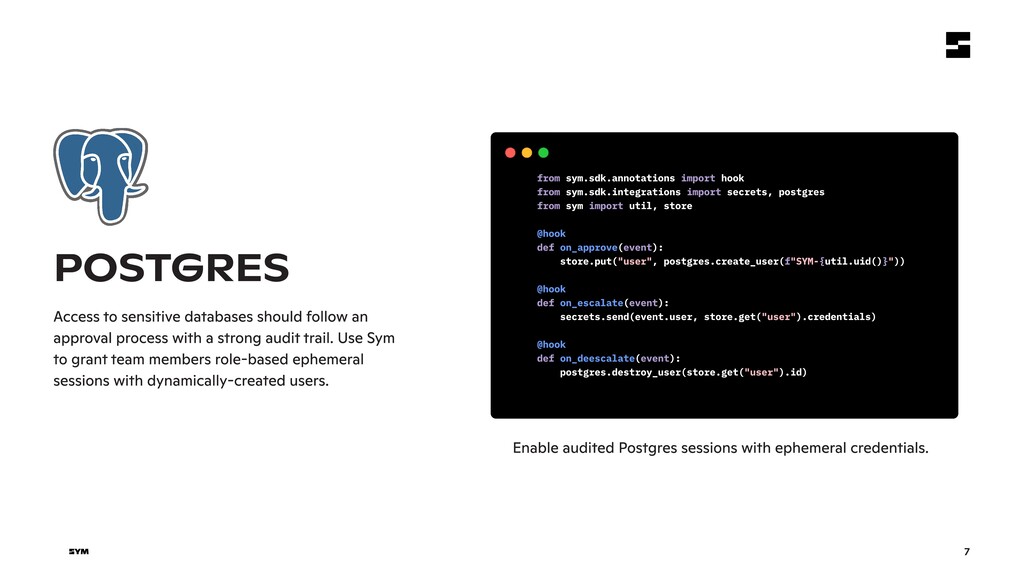
process with a strong audit trail. Use Sym to grant team members role-based ephemeral sessions with dynamically-created users. Enable audited Postgres sessions with ephemeral credentials. from import from import from import def event f { } def event def event sym.sdk.annotations hook sym.sdk.integrations secrets, postgres sym util, store ( ): store.put( , postgres.create_user( util.uid() )) ( ): secrets.send(event.user, store.get( ).credentials) ( ): postgres.destroy_user(store.get( ).id) @hook on_approve @hook on_escalate @hook on_deescalate "user" "SYM- " "user" "user"
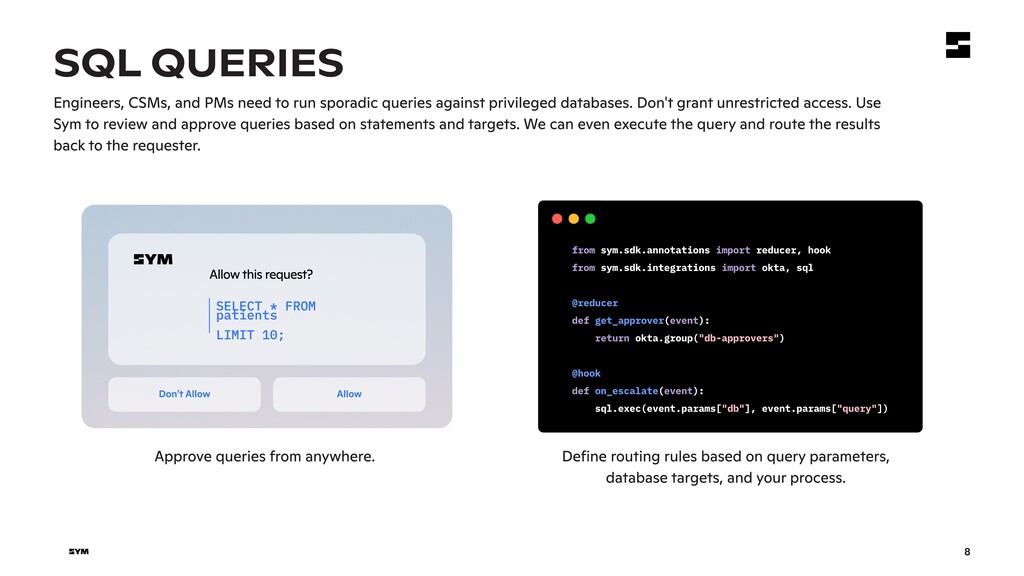
sporadic queries against privileged databases. Don't grant unrestricted access. Use Sym to review and approve queries based on statements and targets. We can even execute the query and route the results back to the requester. Define routing rules based on query parameters, database targets, and your process. Approve queries from anywhere. Allow this request? SELECT * FROM patients LIMIT 10; Allow Don’t Allow from import from import def event return def event sym.sdk.annotations reducer, hook sym.sdk.integrations okta, sql ( ): okta.group( ) ( ): sql.exec(event.params[ ], event.params[ ]) @reducer get_approver @hook on_escalate "db-approvers" "db" "query"
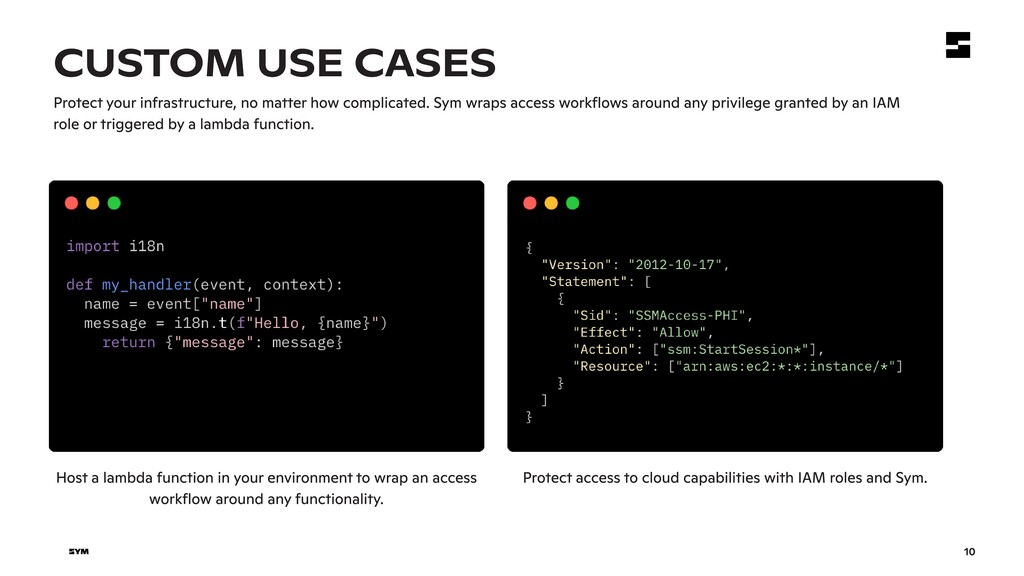
complicated. Sym wraps access workflows around any privilege granted by an IAM role or triggered by a lambda function. Host a lambda function in your environment to wrap an access workflow around any functionality. Protect access to cloud capabilities with IAM roles and Sym.
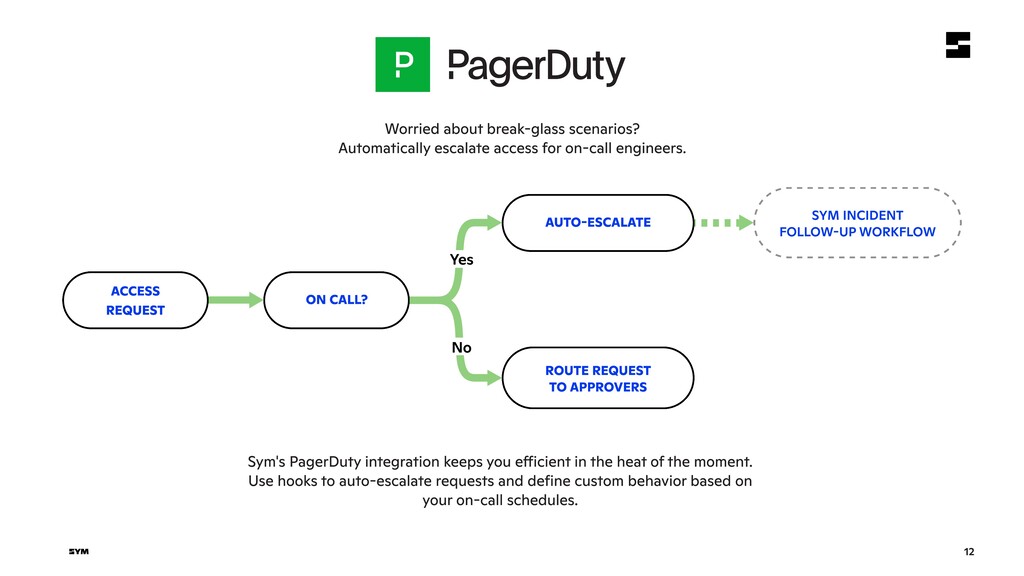
engineers. Sym's PagerDuty integration keeps you efficient in the heat of the moment. Use hooks to auto-escalate requests and define custom behavior based on your on-call schedules. ACCESS REQUEST AUTO-ESCALATE SYM INCIDENT FOLLOW-UP WORKFLOW ROUTE REQUEST TO APPROVERS ON CALL? No Yes
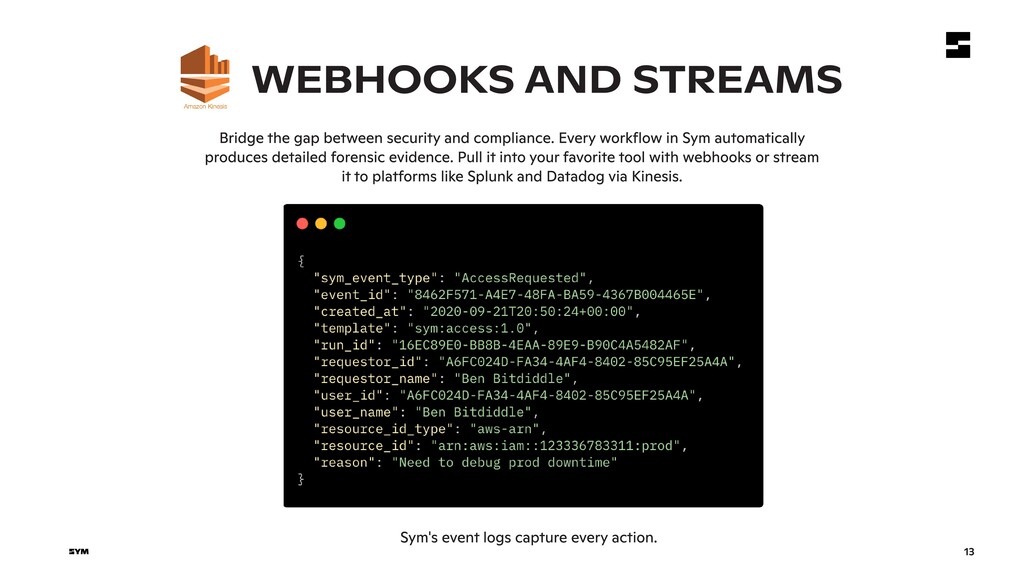
in Sym automatically produces detailed forensic evidence. Pull it into your favorite tool with webhooks or stream it to platforms like Splunk and Datadog via Kinesis. Webhooks and Streams Sym's event logs capture every action.
415-638-7016 [email protected] Sym is the security workflow platform made for engineers, by engineers. We solve the intent-to-execution gap between policies and workflows by providing fast-moving engineering teams with the just-right primitives to roll out best-practice controls. Sym lets teams meet their information security needs without breaking stride on development. 14


 maltzj
 mclloyd
 keavy
 mayatellez
 kristinabergwall1
 akashhashmi
 kimpetersen
 tapps
 reverentgeek
 oripsolob
 inesmontani
 palkan