Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Securing WordPress
Search
Sebastian Gräßl
September 24, 2013
Technology
65
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Securing WordPress
Sebastian Gräßl
September 24, 2013
Transcript
17 slides
Securing WordPress by @bastilian
What needs to be secure? • Server (Operating System) •
Dependencies (PHP, ImageMagick, etc.) • Web-Server • Database-Server
Keep everything up to date! Always!
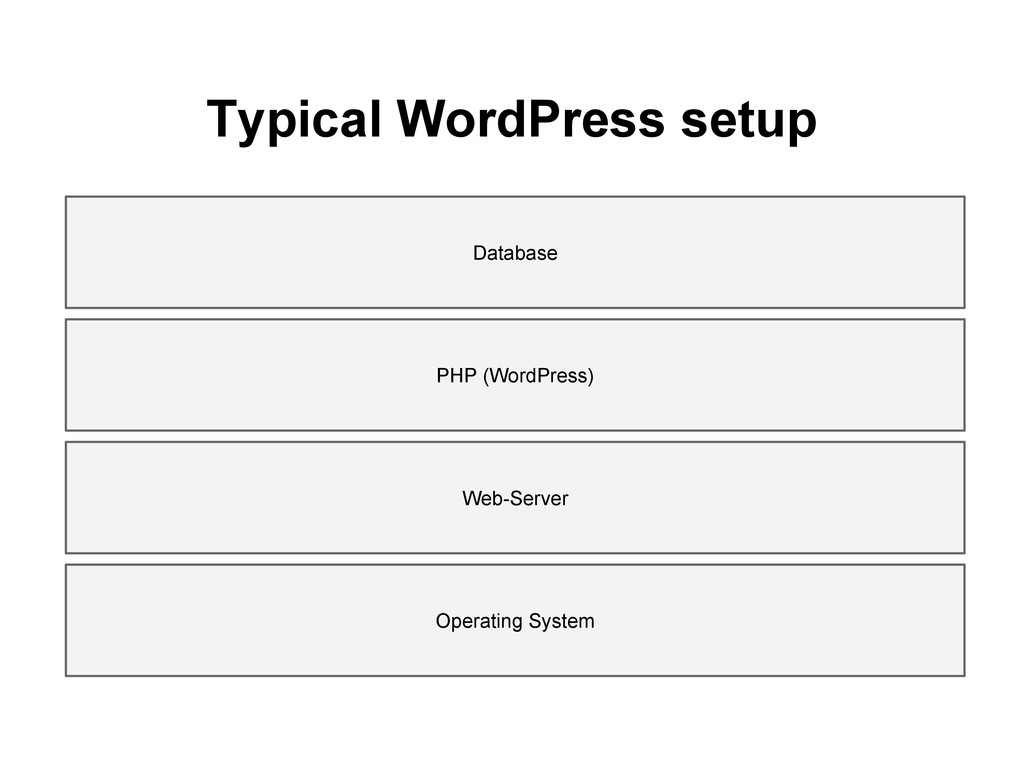
Typical WordPress setup Operating System Web-Server PHP (WordPress) Database
Operating System - First line of defense
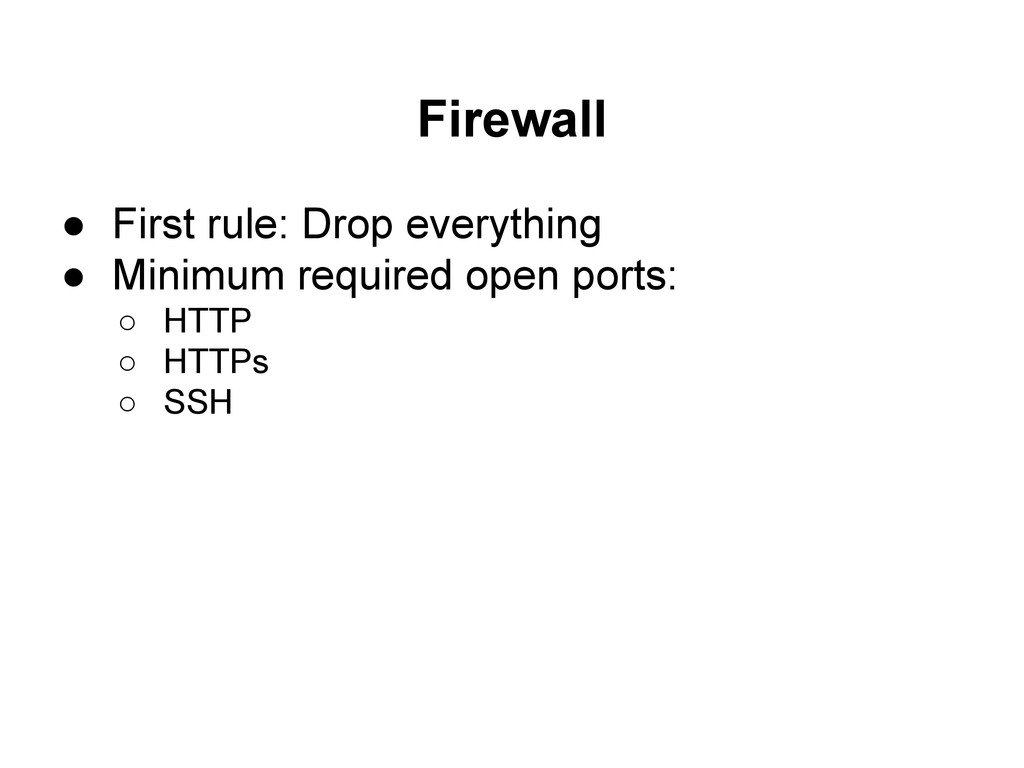
Firewall • First rule: Drop everything • Minimum required open
ports: ◦ HTTP ◦ HTTPs ◦ SSH
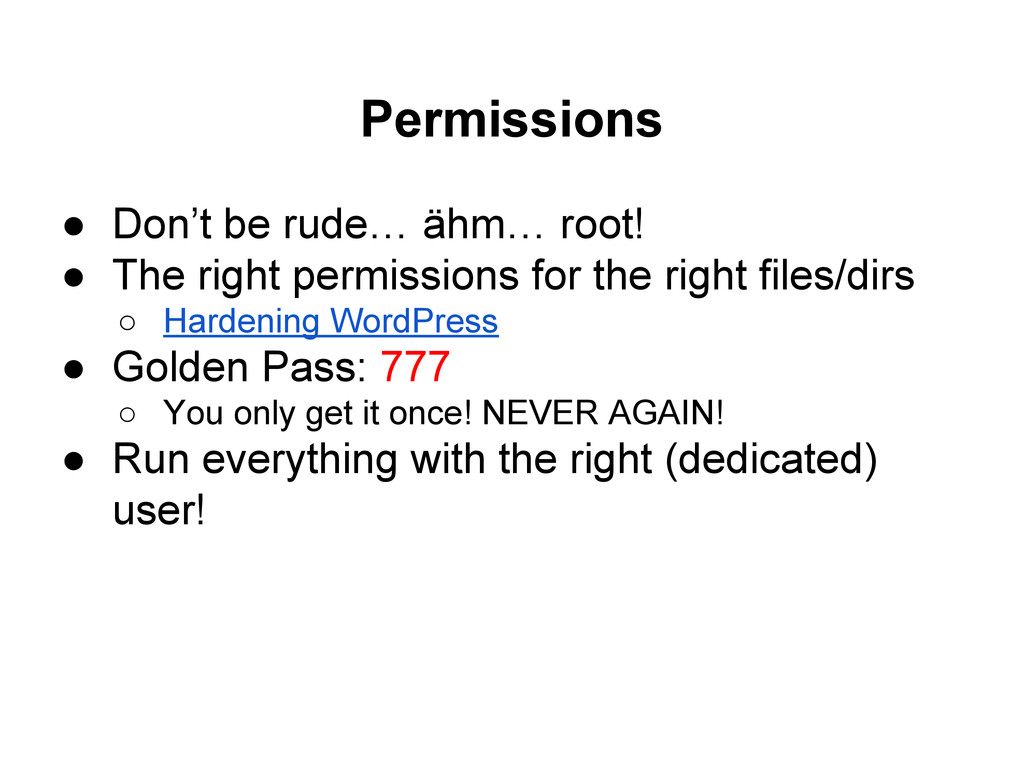
Permissions • Don’t be rude… ähm… root! • The right
permissions for the right files/dirs ◦ Hardening WordPress • Golden Pass: 777 ◦ You only get it once! NEVER AGAIN! • Run everything with the right (dedicated) user!
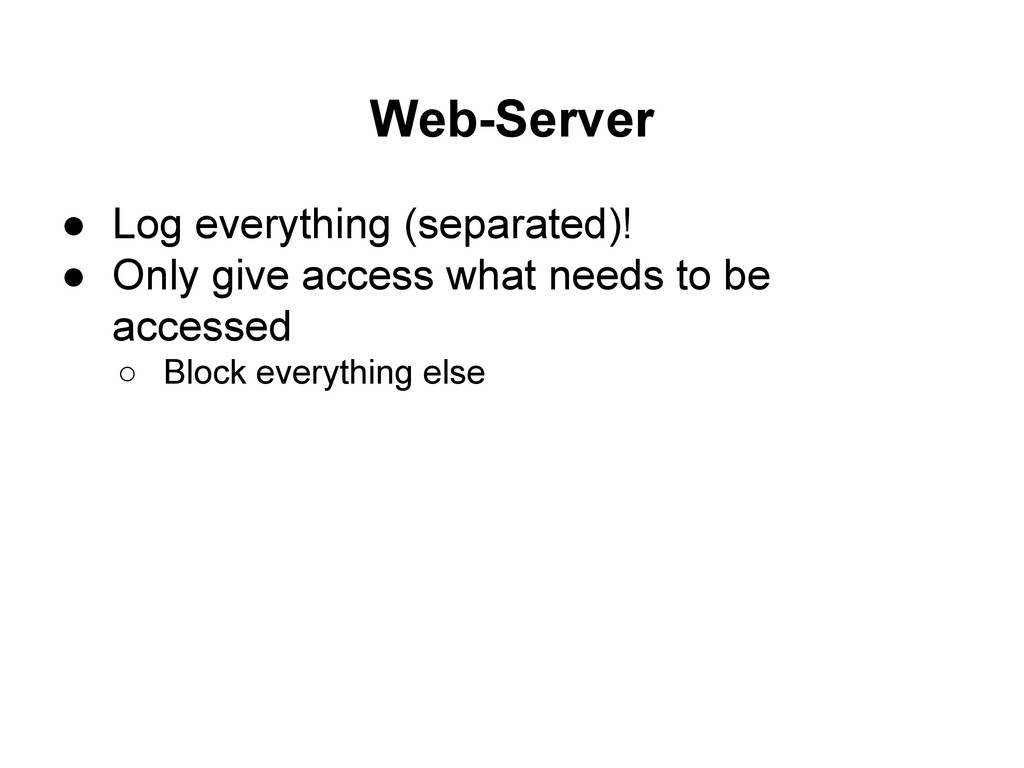
Web-Server • Log everything (separated)! • Only give access what
needs to be accessed ◦ Block everything else
Database • Again: don’t be root! • Separate databases •
Only accessible locally
PHP • No root for you!
WordPress
Plugins • Only install trustworthy Plugins • Read through it’s
code ◦ Any http-requests? ◦ Any file-operations? ◦ Any DB-operations?
Enable SSL (for wp-admin) • HTTPs will become standard (SPDY)
• SSL certs for free at StartSSL™ • Gives you a green lock icon.
Fail2Ban • Logs failed Authentications • Bans IPs on OS-level
DDoS - You bit** • U rich? throw money at
it. • If you can reroute internally. • Cross your fingers and hope it’s over soon.
Spam Comments? • Akismet
There is more. Thanks.
More Decks by Sebastian Gräßl
See All by Sebastian Gräßl
Microformats & Richsnippets
bastilian
0
43
CSS - The good stuff
bastilian
0
51
Other Decks in Technology
See All in Technology
[NW-JAWS DAY]「うちのAWS、インターネット出られないんで」― AWS外の自社サービスをPrivateLinkでシュッと公開する方法
ykimi
3
920
パスワードのない鍵で、 データを手元に置く
ginjihayashi
0
400
From vibe coding to reliable (agentic) development
jcabot
0
250
その修正で本当に速くなったのか? k6とOpenTelemetryで確かめる性能改善 / Performance review with k6 and OpenTelemetry
ymotongpoo
3
440
認知の質も文化醸成も。数年取り組んで見えてきた技術広報のKPI設計 / Tech PR KPIs: Lessons on Awareness Quality and Culture After Several Years
bitkey
PRO
0
220
社内アプリ基盤「Quartz」による、 非エンジニアとAIに本番デプロイを 任せても壊れないプラットフォームの設計
staka121
PRO
1
230
【Oracle AI SPOTLIGHT ウェビナー】AI時代、狙われるデータと止められない業務をどう守るか?
oracle4engineer
PRO
1
140
MCPでネットワーク障害調査を自動化する前に直すべき3つのこと
yama3133
1
660
メディアアートを〈拡張〉する——器官学と個体化論を手がかりに
_kotobuki_
0
130
新規事業開発でのAWS活用成功談&失敗談! 〜新規事業開発を専門に行うRelicならではのAWS活用〜
amixedcolor
1
140
gradle-best-practices 使ってみた
mikanichinose
0
230
閉域網でのAPI公開の選択肢全部比較!
takano0131
5
700
Featured
See All Featured
For a Future-Friendly Web
brad_frost
184
11k
StorybookのUI Testing Handbookを読んだ
zakiyama
31
7.1k
Embracing the Ebb and Flow
colly
88
5.2k
Navigating Algorithm Shifts & AI Overviews - #SMXNext
aleyda
1
1.7k
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
Claude Code のすすめ
schroneko
67
230k
Groundhog Day: Seeking Process in Gaming for Health
codingconduct
0
500
Helping Users Find Their Own Way: Creating Modern Search Experiences
danielanewman
31
3.4k
Navigating Team Friction
lara
192
16k
Music & Morning Musume
bryan
48
7.5k
Stop Working from a Prison Cell
hatefulcrawdad
274
21k
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k


 bastilian
 ykimi
 ginjihayashi
 jcabot
 ymotongpoo
 bitkey
 staka121
 oracle4engineer
 yama3133
 _kotobuki_
 amixedcolor
 mikanichinose
 takano0131
 brad_frost
 zakiyama
 colly
 aleyda
 panda_program
 schroneko
 codingconduct
 danielanewman
 lara
 bryan
 hatefulcrawdad
 eileencodes