Upgrade to Pro — share decks privately, control downloads, hide ads and more …

From Compliance Tax to Engineering Accelerator

From Compliance Tax to Engineering Accelerator

Security often feels like a tax on delivery: late findings, copied pipeline YAML, manual proof, and secret management. This talk shows how a platform approach turns compliance into an accelerator.

Avatar for Lalith Chaitanya Mangalagiri

Lalith Chaitanya Mangalagiri

October 18, 2026

Other Decks in Technology

Transcript

  1. From Compliance Tax to Engineering Accelerator Name: Lalith lakshmi Chaitanya

    kumar Mangalagiri LinkedIn: linkedin.com/in/lalith-chaitanya-mangalagiri-b31445170
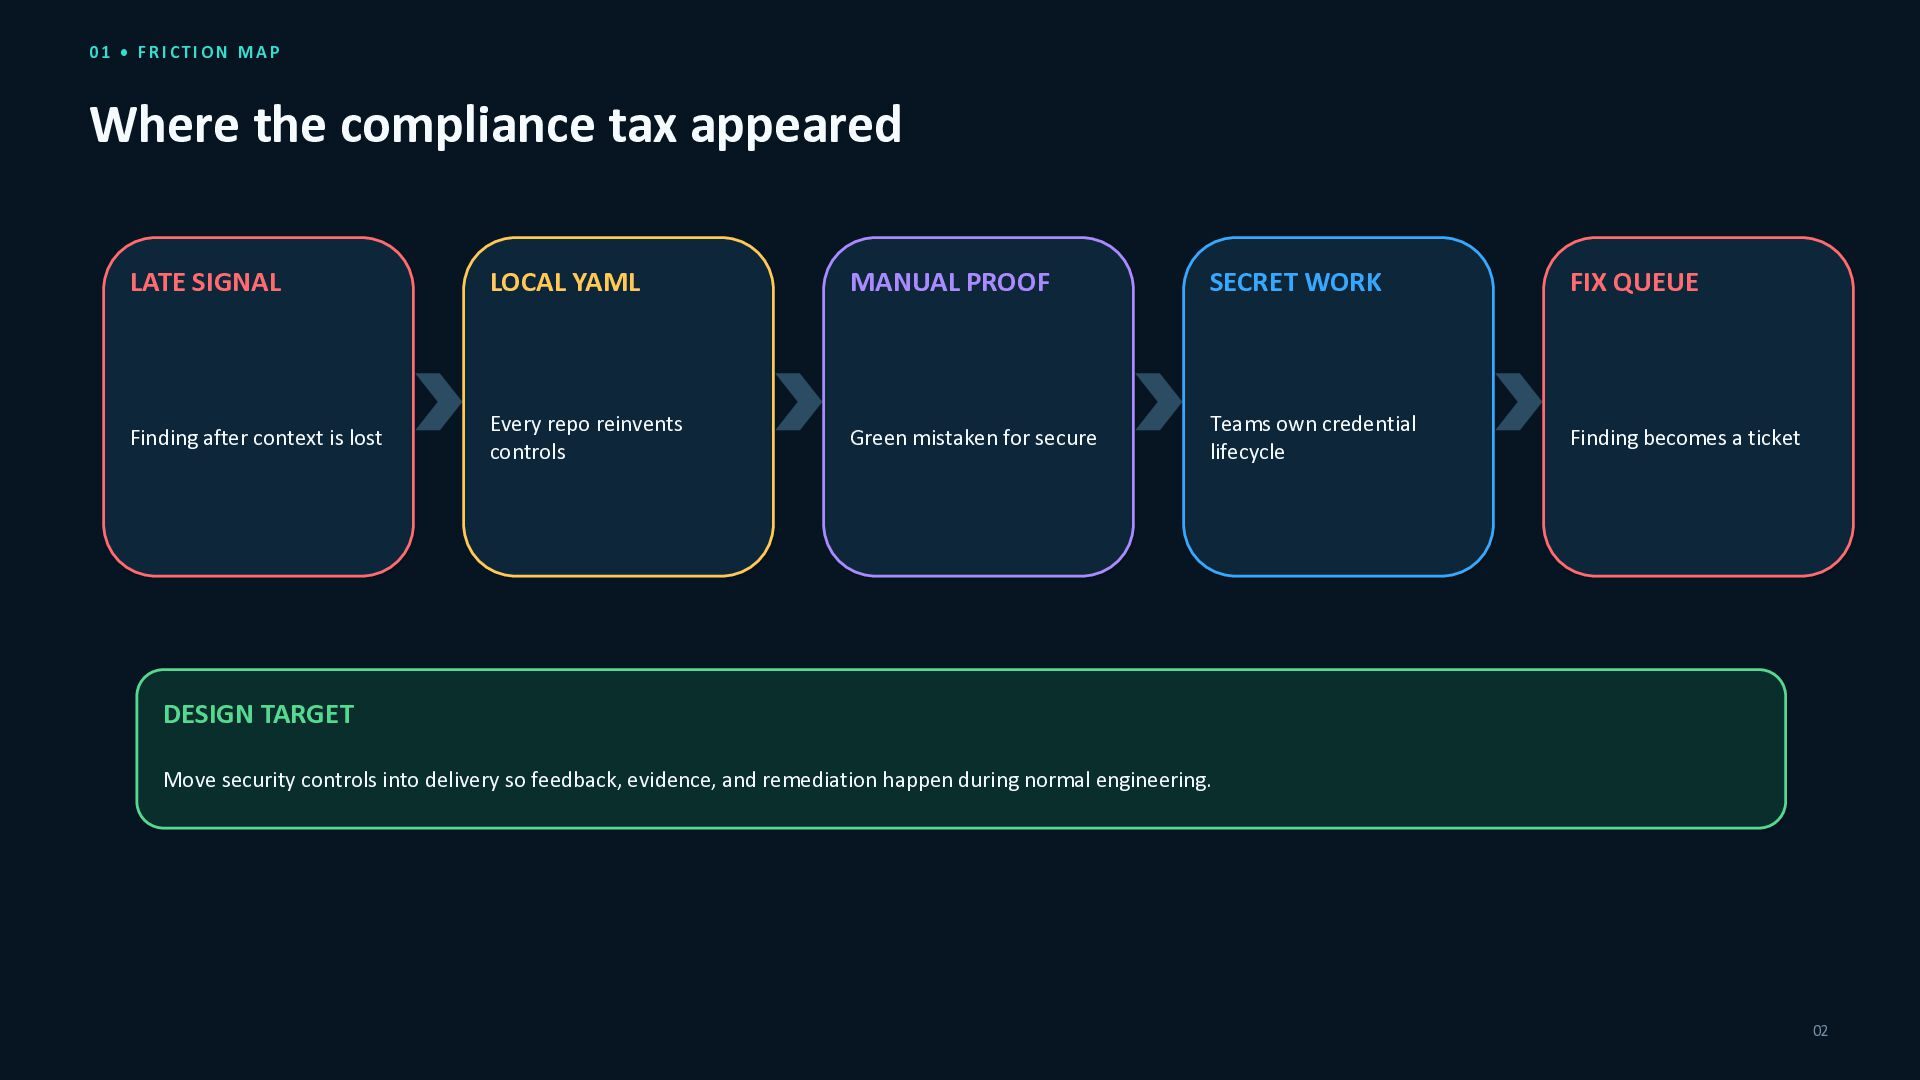
  2. 01 • FRICTION MAP Where the compliance tax appeared LATE

    SIGNAL LOCAL YAML MANUAL PROOF SECRET WORK FIX QUEUE Finding after context is lost Every repo reinvents controls Green mistaken for secure Teams own credential lifecycle Finding becomes a ticket DESIGN TARGET Move security controls into delivery so feedback, evidence, and remediation happen during normal engineering. 02
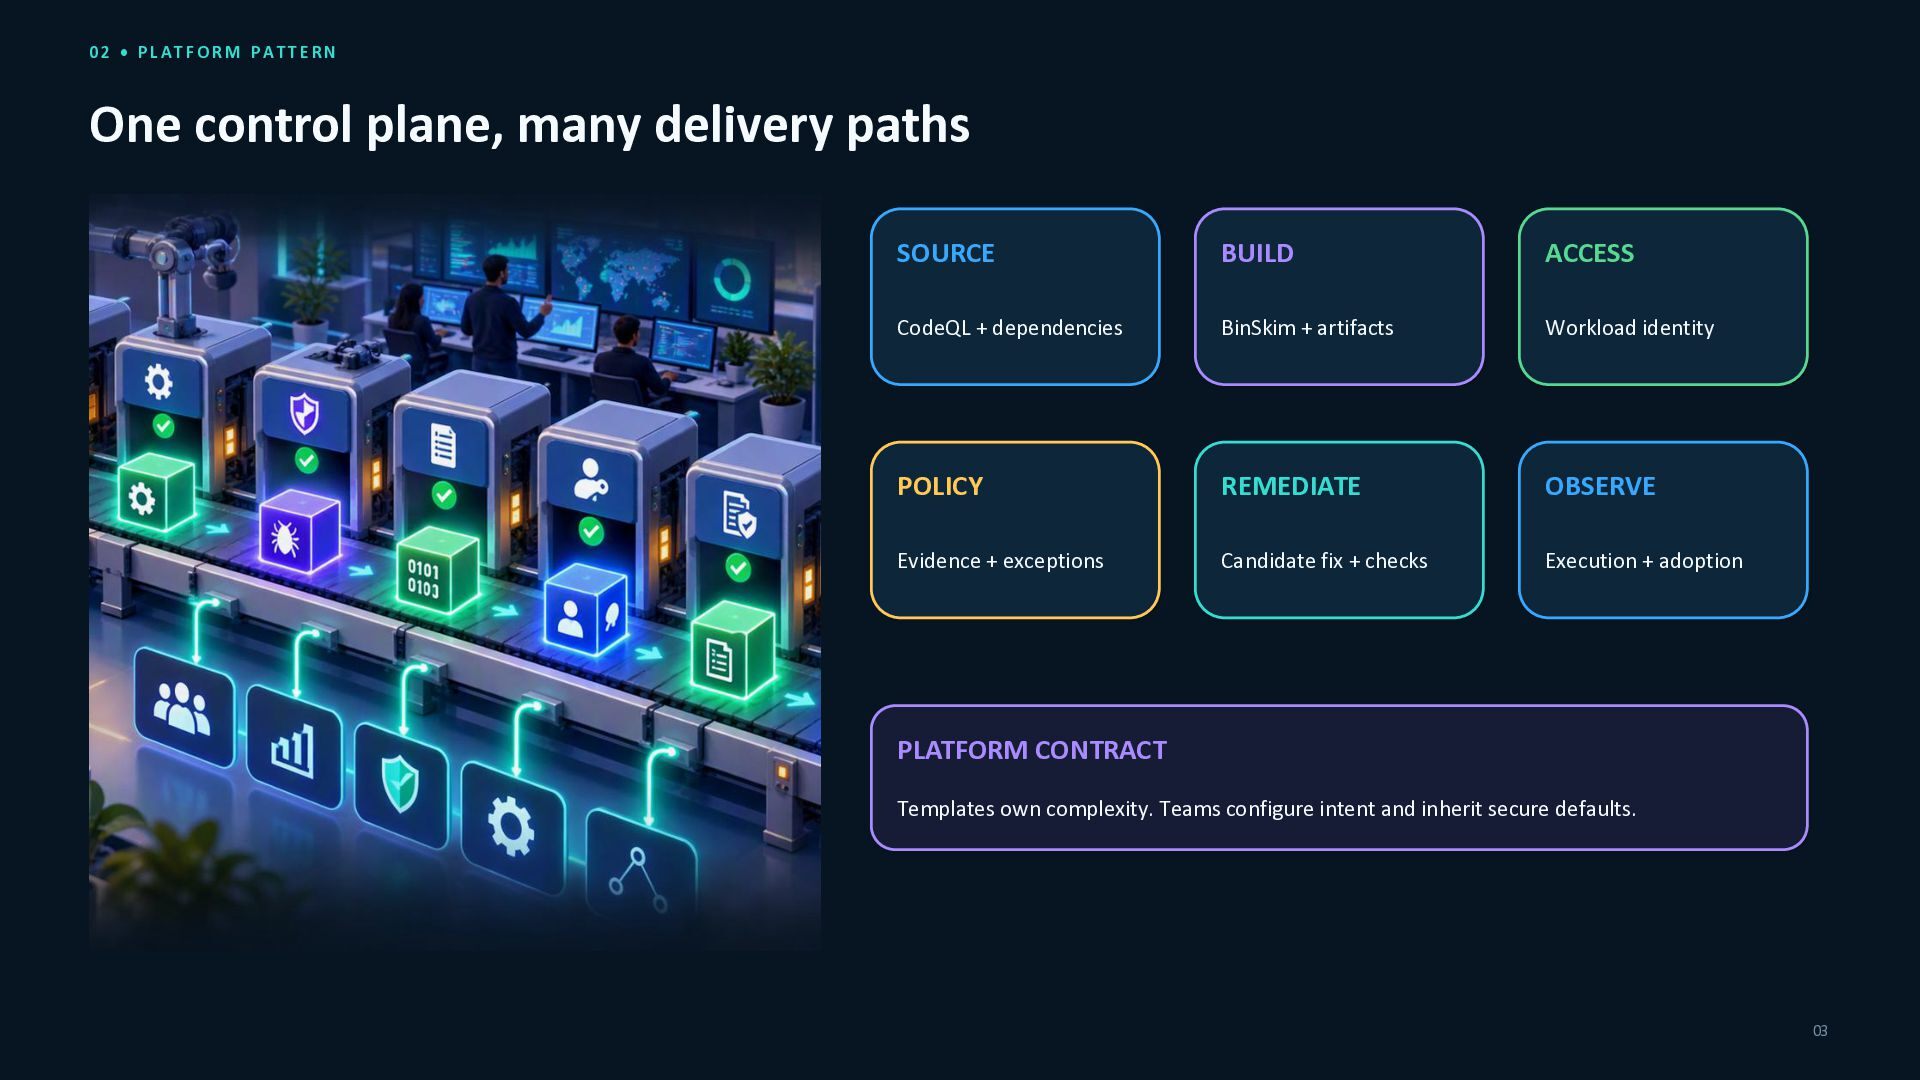
  3. 02 • PLATFORM PATTERN One control plane, many delivery paths

    SOURCE BUILD ACCESS CodeQL + dependencies BinSkim + artifacts Workload identity POLICY REMEDIATE OBSERVE Evidence + exceptions Candidate fix + checks Execution + adoption PLATFORM CONTRACT Templates own complexity. Teams configure intent and inherit secure defaults. 03
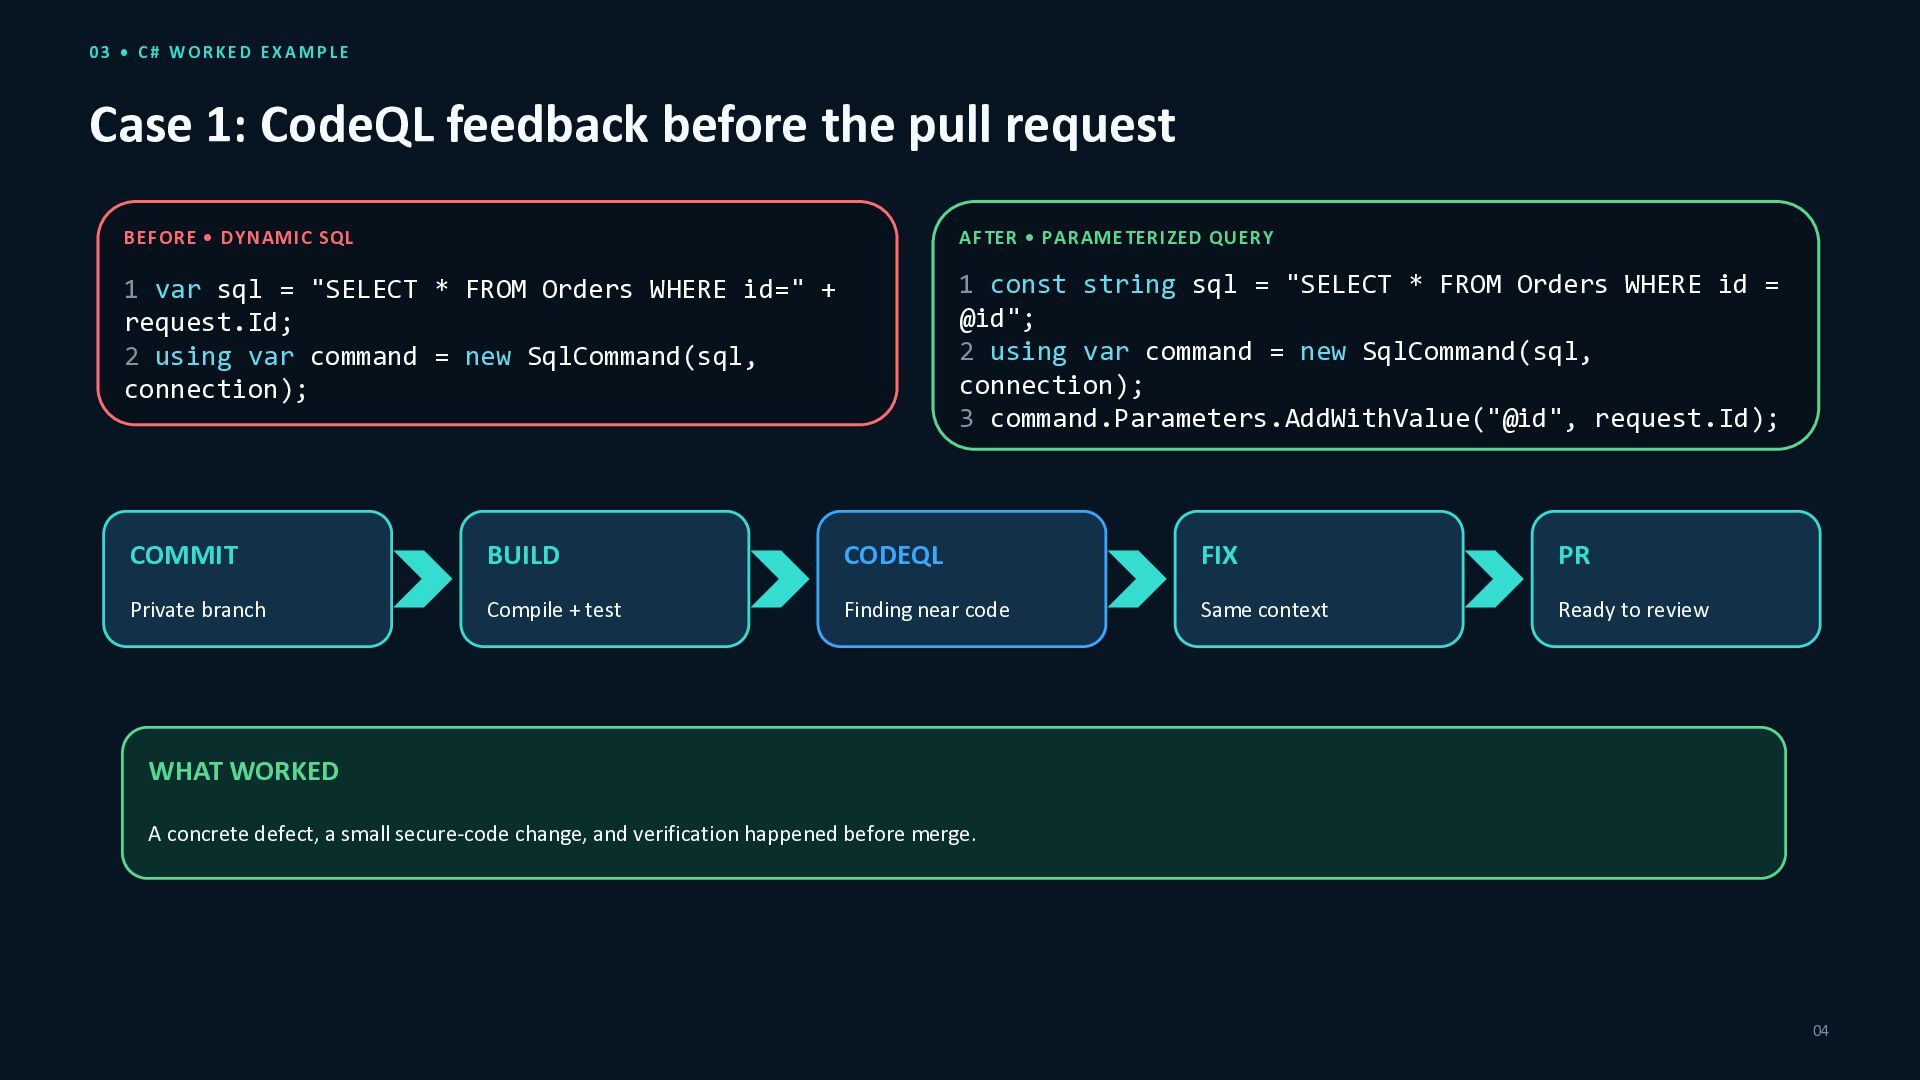
  4. 03 • C# WORKED EXAMPLE Case 1: CodeQL feedback before

    the pull request BEFORE • DYNAMIC SQL AFTER • PARAMETERIZED QUERY 1 var sql = "SELECT * FROM Orders WHERE id=" + request.Id; 2 using var command = new SqlCommand(sql, connection); 1 const string sql = "SELECT * FROM Orders WHERE id = @id"; 2 using var command = new SqlCommand(sql, connection); 3 command.Parameters.AddWithValue("@id", request.Id); COMMIT BUILD CODEQL FIX PR Private branch Compile + test Finding near code Same context Ready to review WHAT WORKED A concrete defect, a small secure-code change, and verification happened before merge. 04
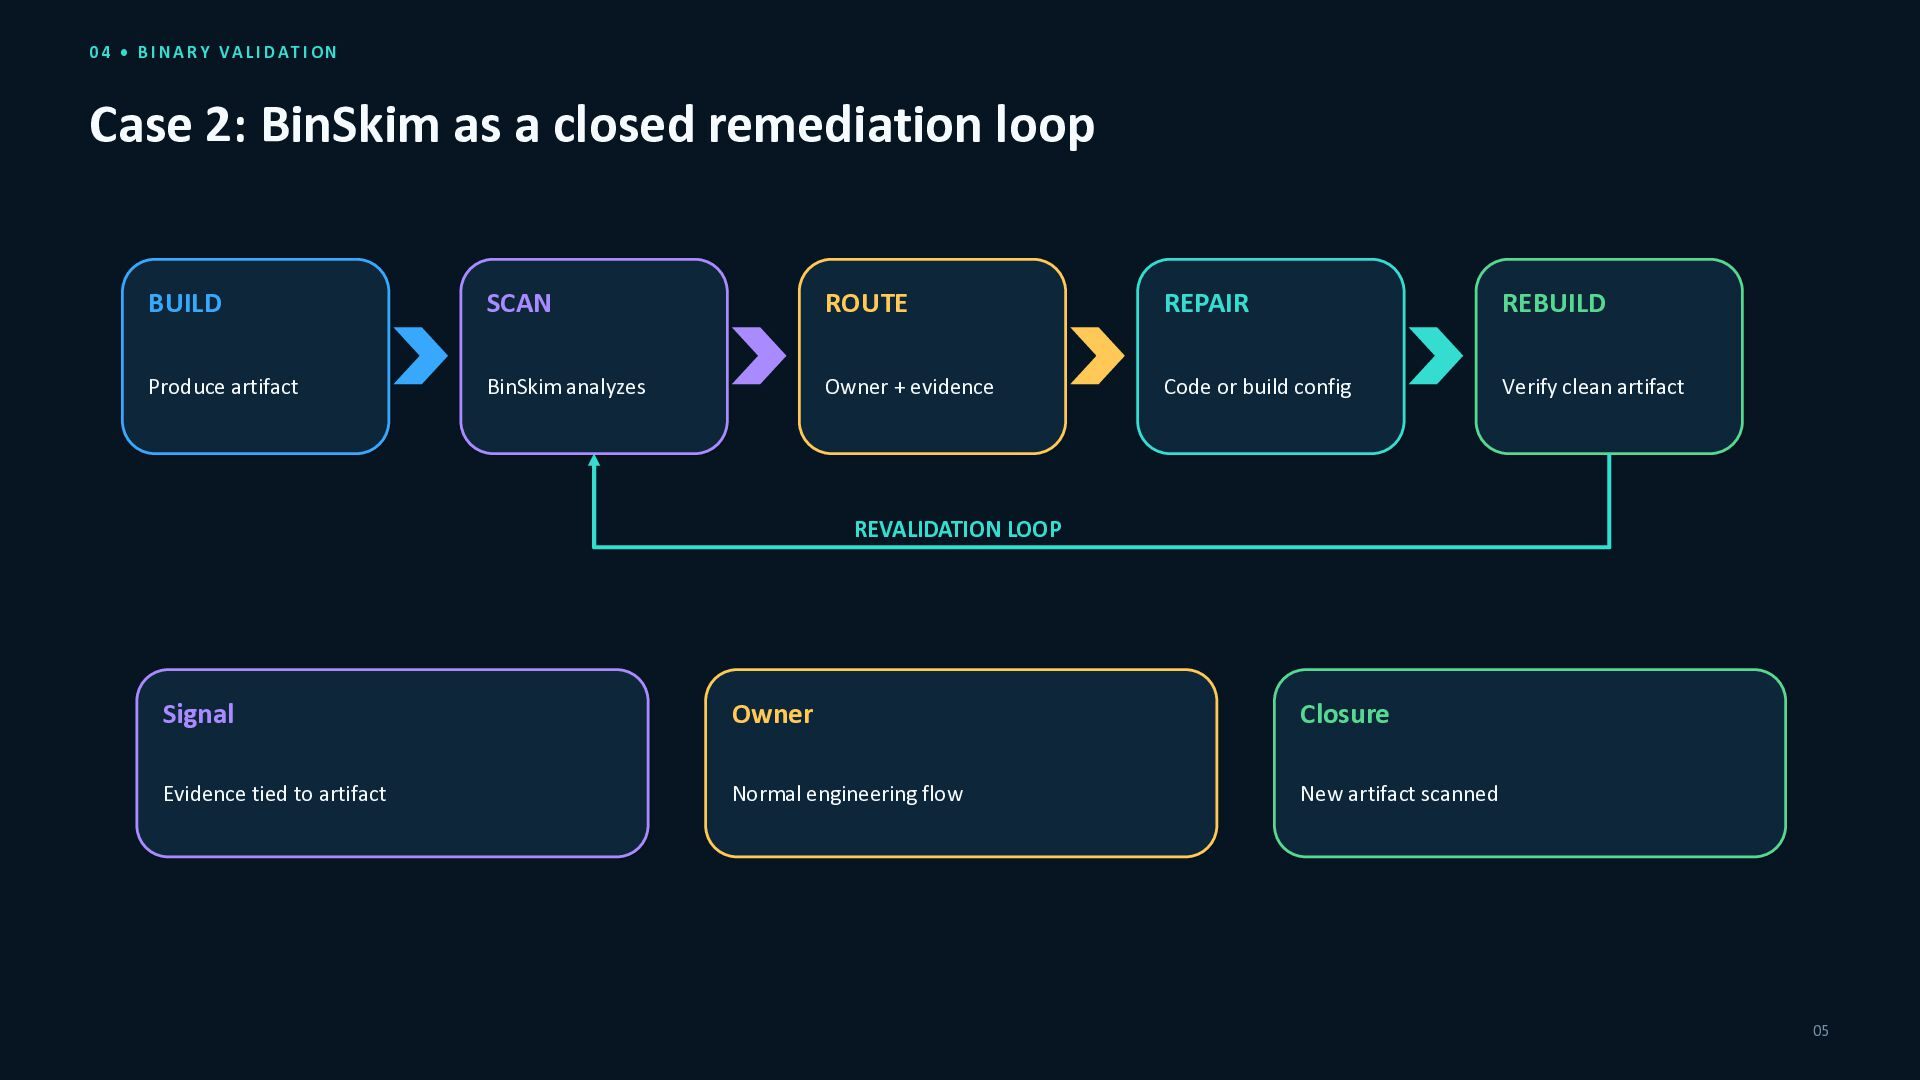
  5. 04 • BINARY VALIDATION Case 2: BinSkim as a closed

    remediation loop BUILD SCAN ROUTE REPAIR REBUILD Produce artifact BinSkim analyzes Owner + evidence Code or build config Verify clean artifact REVALIDATION LOOP Signal Owner Closure Evidence tied to artifact Normal engineering flow New artifact scanned 05
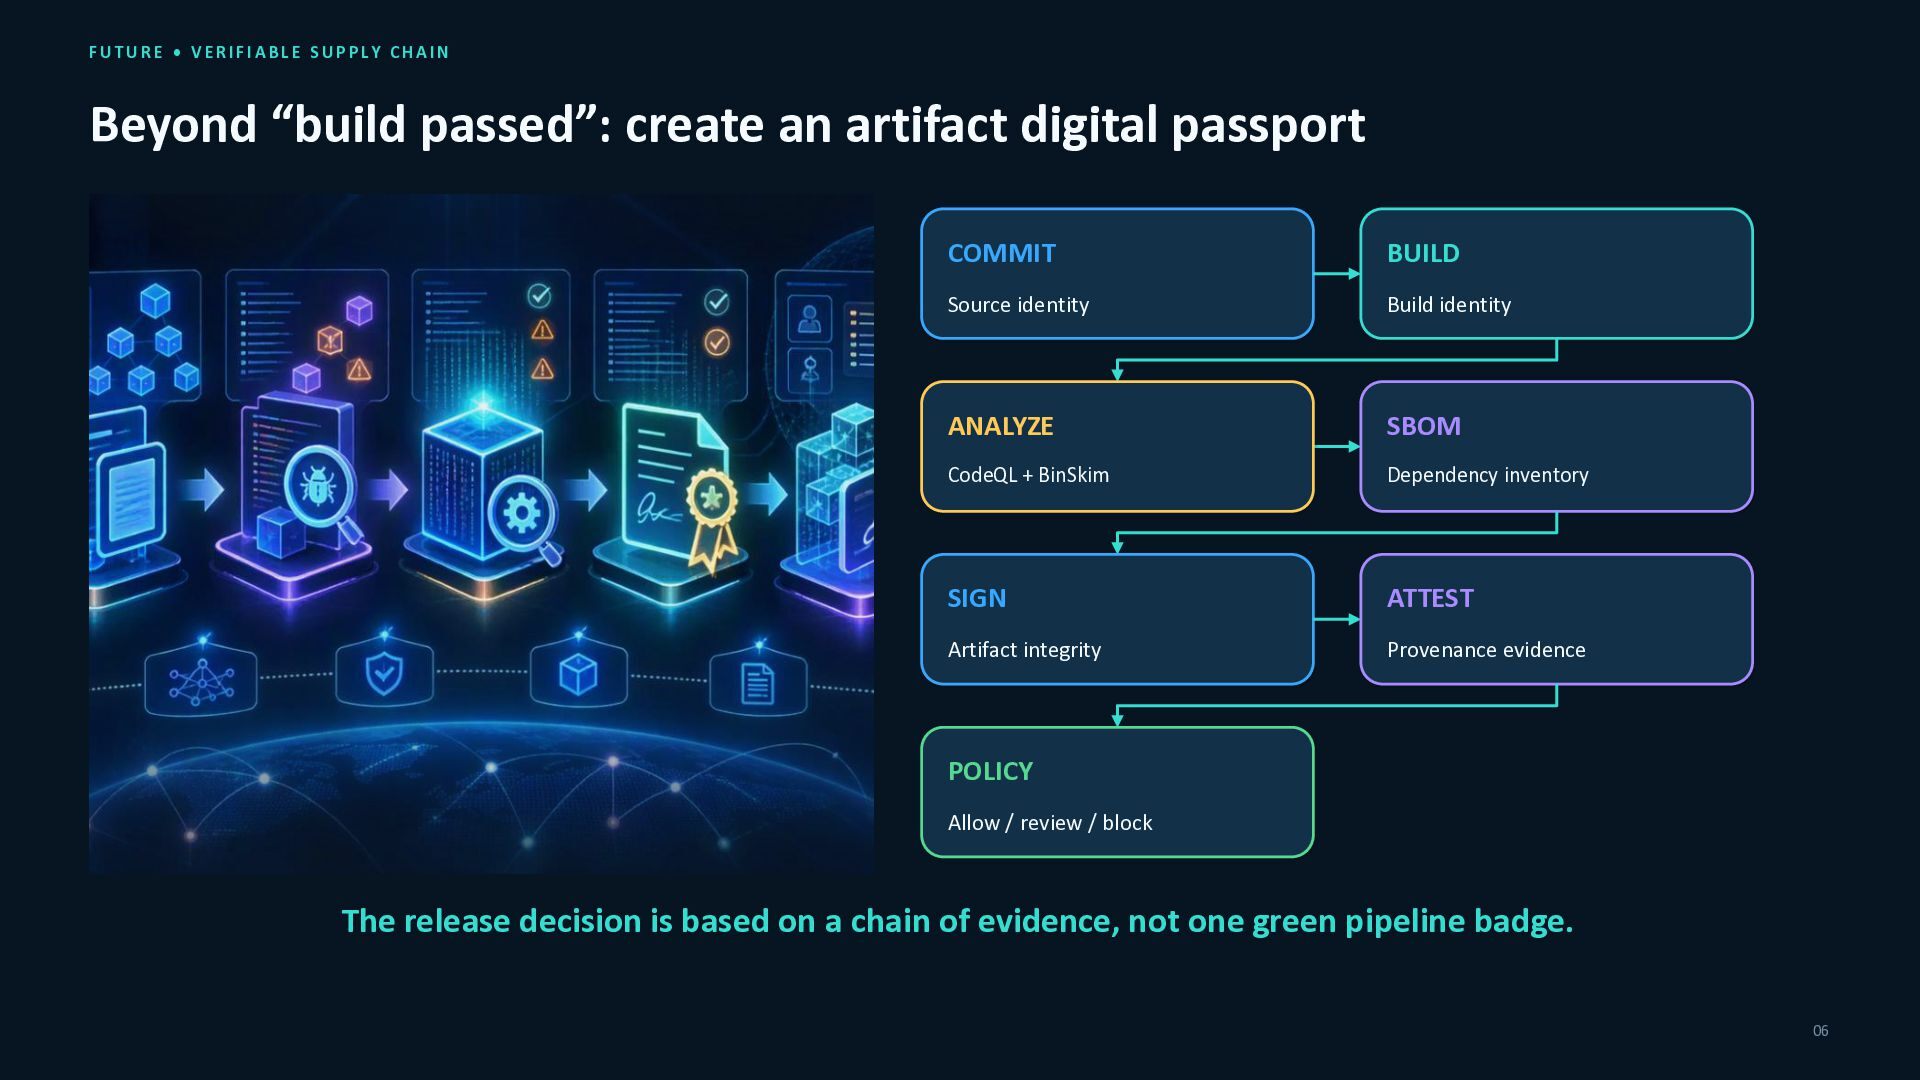
  6. FUTURE • VERIFIABLE SUPPLY CHAIN Beyond “build passed”: create an

    artifact digital passport COMMIT BUILD Source identity Build identity ANALYZE SBOM CodeQL + BinSkim Dependency inventory SIGN ATTEST Artifact integrity Provenance evidence POLICY Allow / review / block The release decision is based on a chain of evidence, not one green pipeline badge. 06
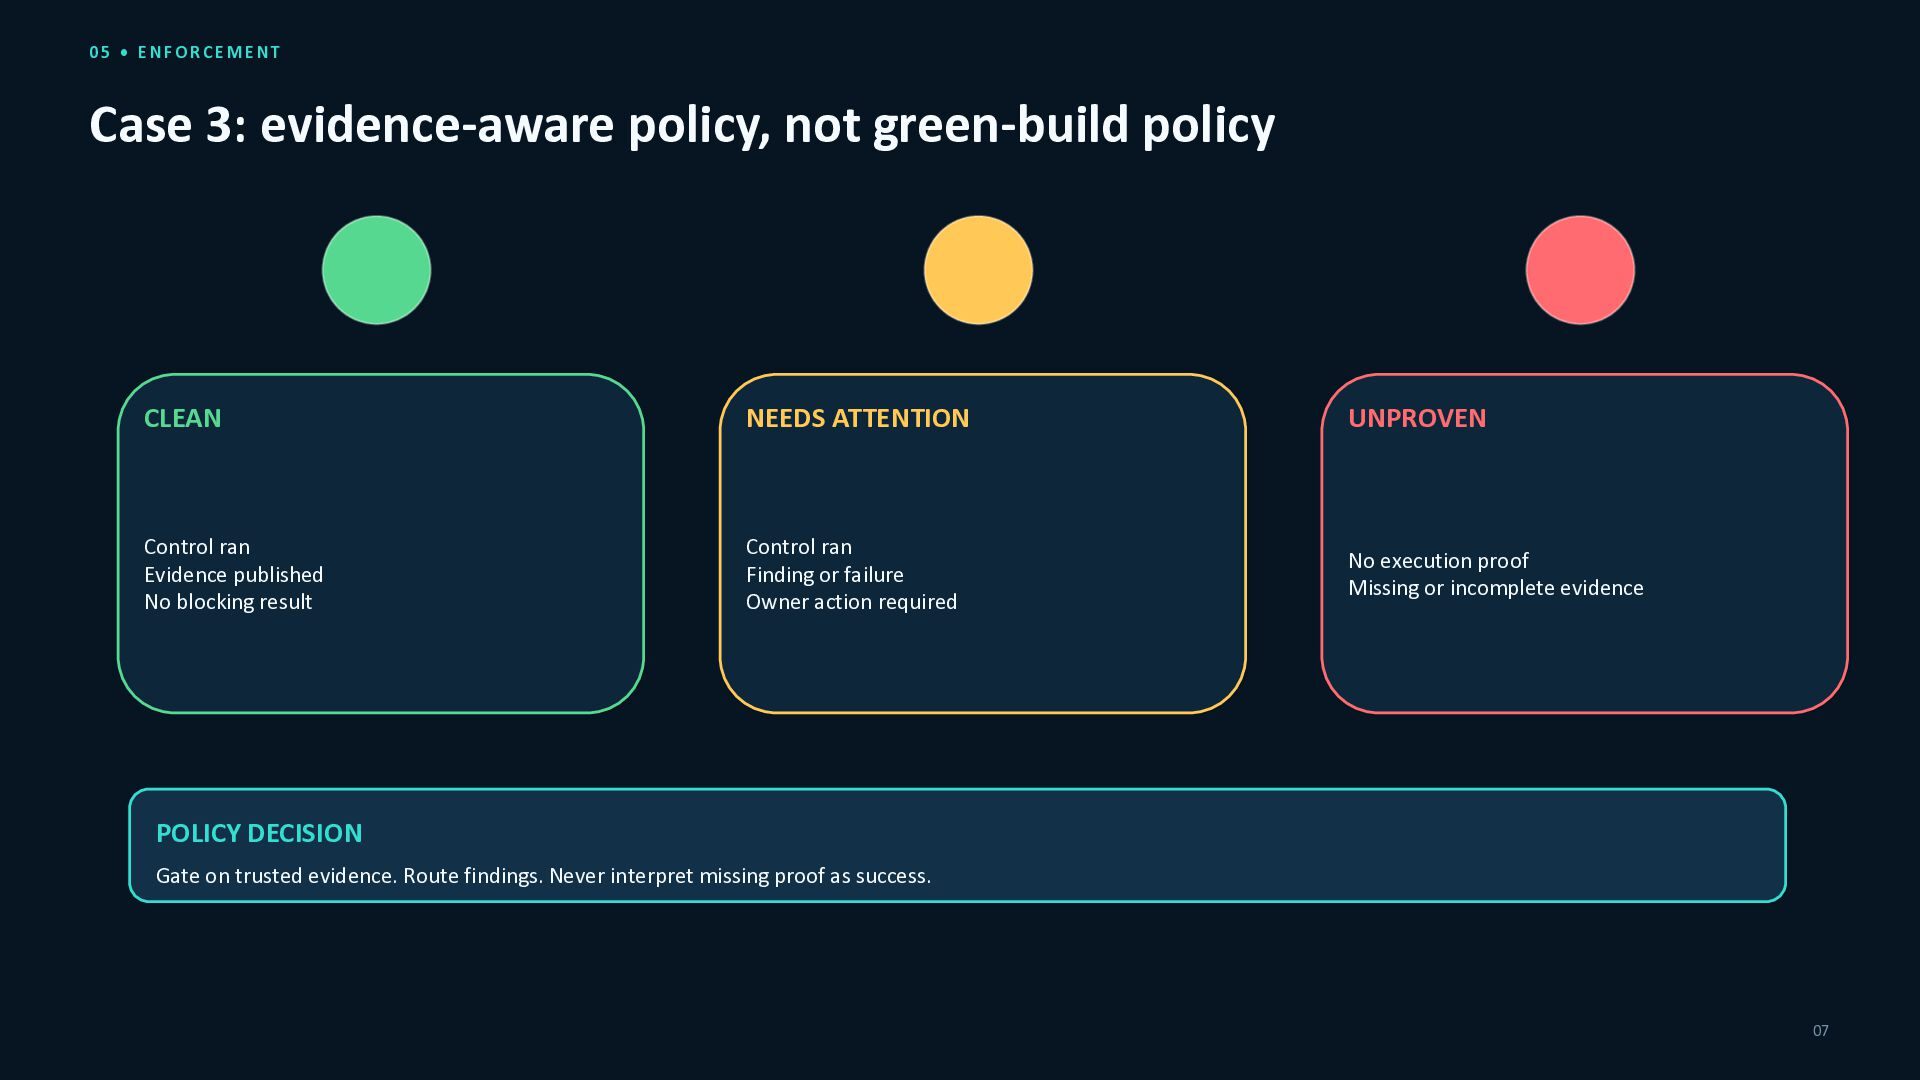
  7. 05 • ENFORCEMENT Case 3: evidence-aware policy, not green-build policy

    CLEAN NEEDS ATTENTION UNPROVEN Control ran Evidence published No blocking result Control ran Finding or failure Owner action required No execution proof Missing or incomplete evidence POLICY DECISION Gate on trusted evidence. Route findings. Never interpret missing proof as success. 07
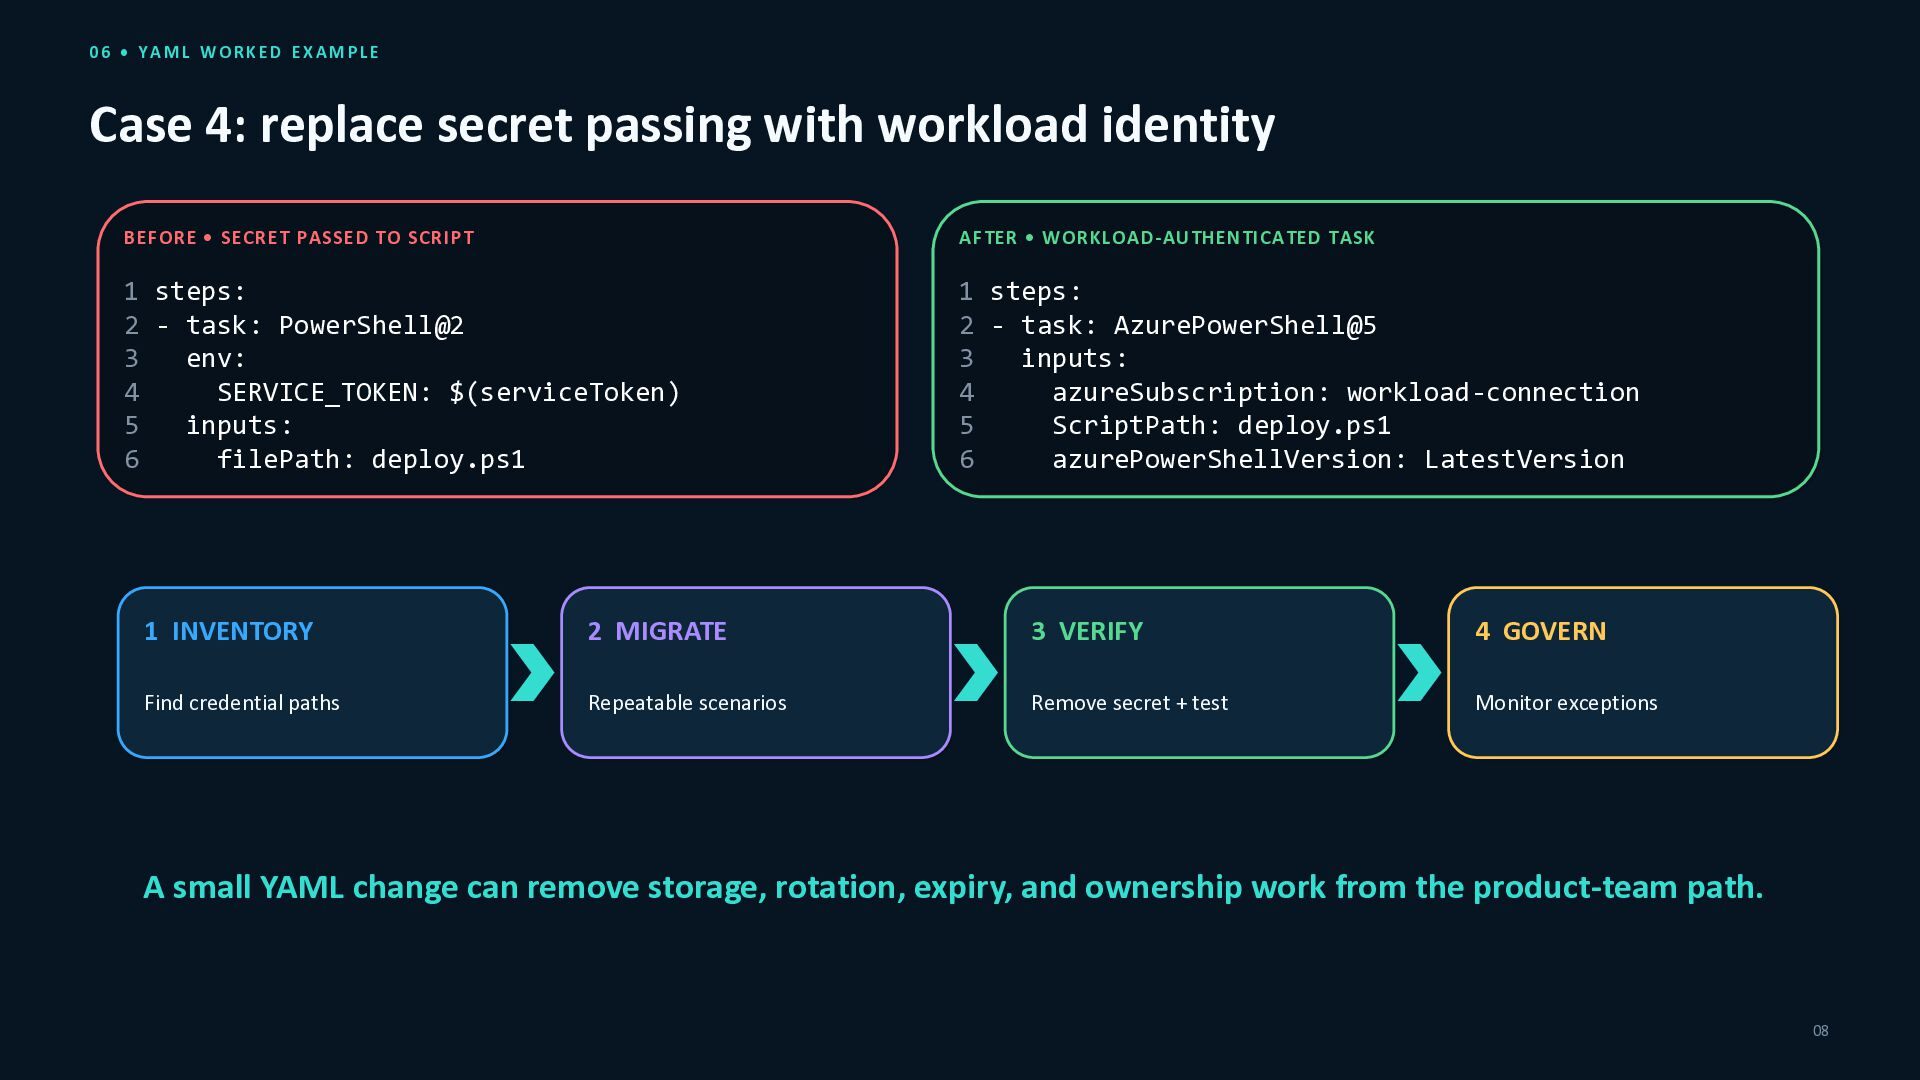
  8. 06 • YAML WORKED EXAMPLE Case 4: replace secret passing

    with workload identity BEFORE • SECRET PASSED TO SCRIPT AFTER • WORKLOAD-AUTHENTICATED TASK 1 steps: 2 - task: PowerShell@2 3 env: 4 SERVICE_TOKEN: $(serviceToken) 5 inputs: 6 filePath: deploy.ps1 1 steps: 2 - task: AzurePowerShell@5 3 inputs: 4 azureSubscription: workload-connection 5 ScriptPath: deploy.ps1 6 azurePowerShellVersion: LatestVersion 1 INVENTORY 2 MIGRATE 3 VERIFY 4 GOVERN Find credential paths Repeatable scenarios Remove secret + test Monitor exceptions A small YAML change can remove storage, rotation, expiry, and ownership work from the product-team path. 08
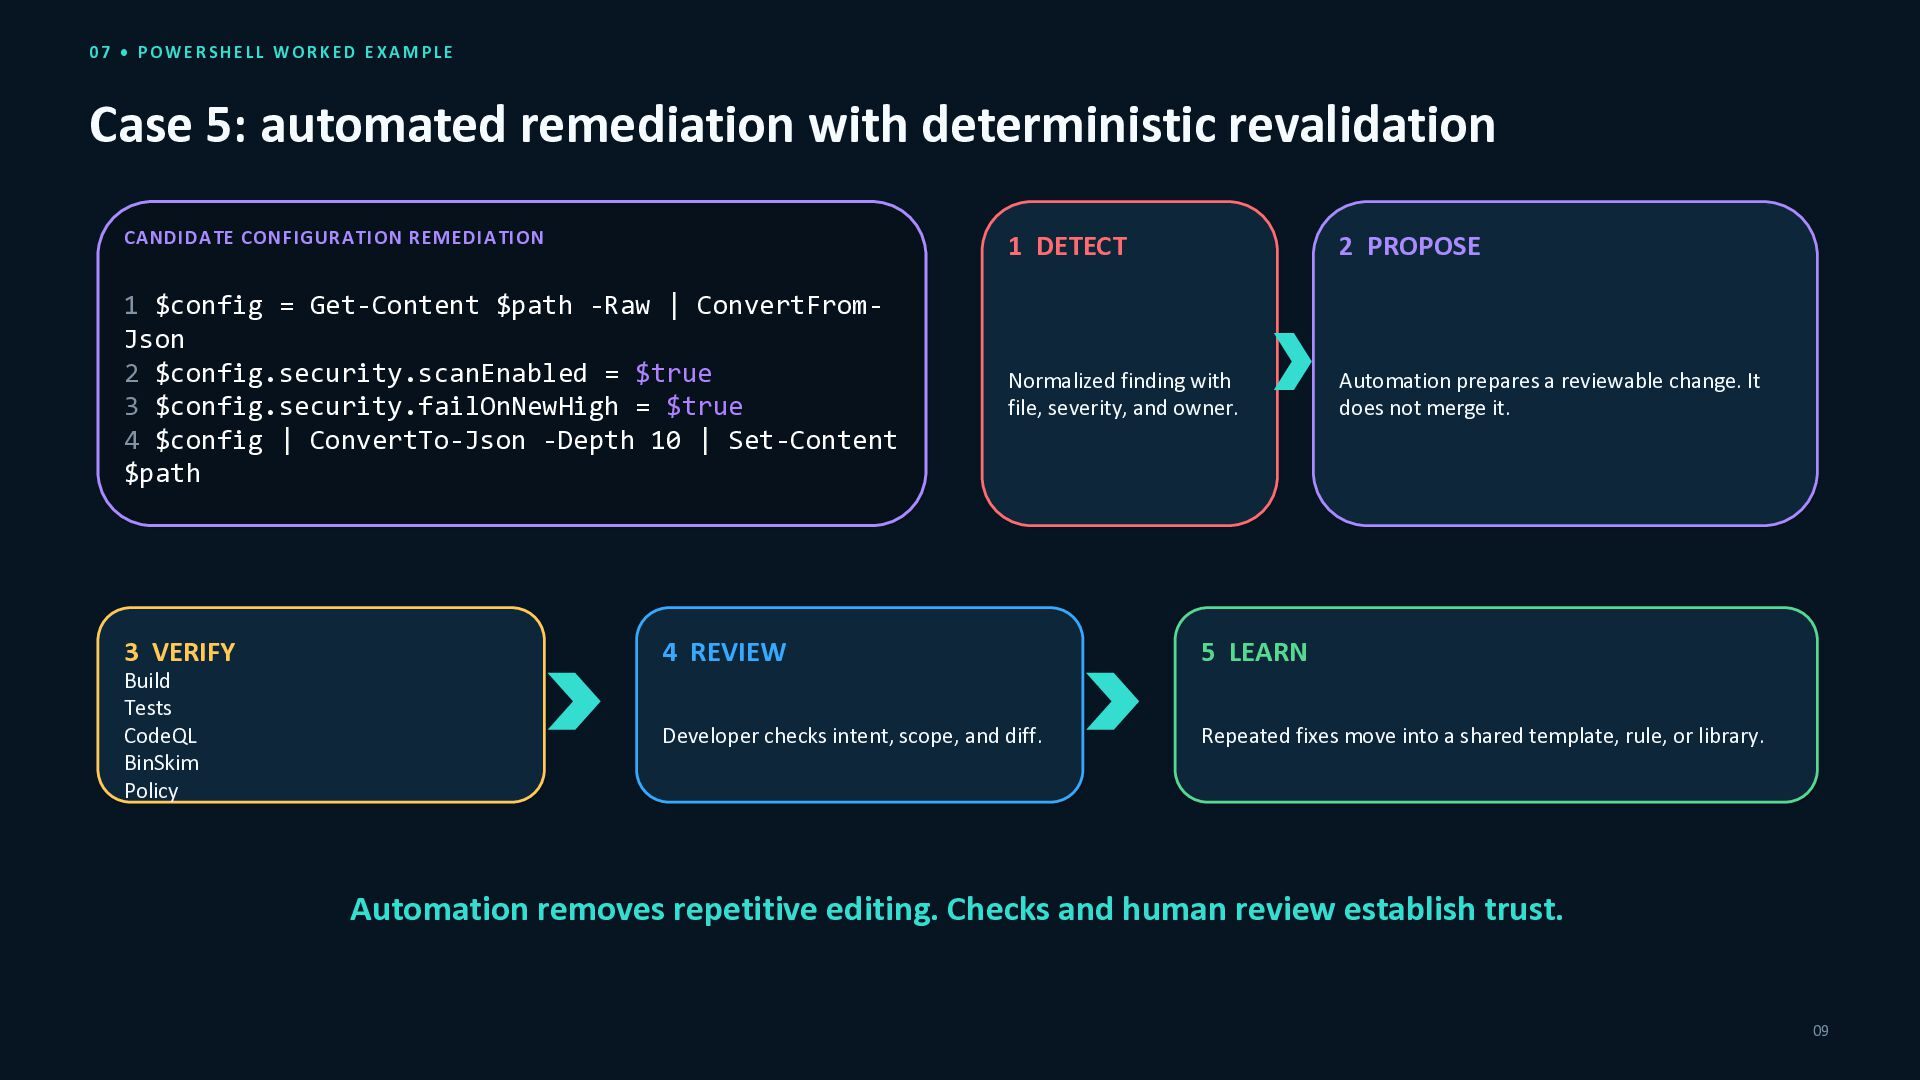
  9. 07 • POWERSHELL WORKED EXAMPLE Case 5: automated remediation with

    deterministic revalidation CANDIDATE CONFIGURATION REMEDIATION 1 DETECT 2 PROPOSE 1 $config = Get-Content $path -Raw | ConvertFromJson 2 $config.security.scanEnabled = $true 3 $config.security.failOnNewHigh = $true 4 $config | ConvertTo-Json -Depth 10 | Set-Content $path Normalized finding with file, severity, and owner. Automation prepares a reviewable change. It does not merge it. 3 VERIFY 4 REVIEW 5 LEARN Build Tests CodeQL BinSkim Policy Developer checks intent, scope, and diff. Repeated fixes move into a shared template, rule, or library. Automation removes repetitive editing. Checks and human review establish trust. 09
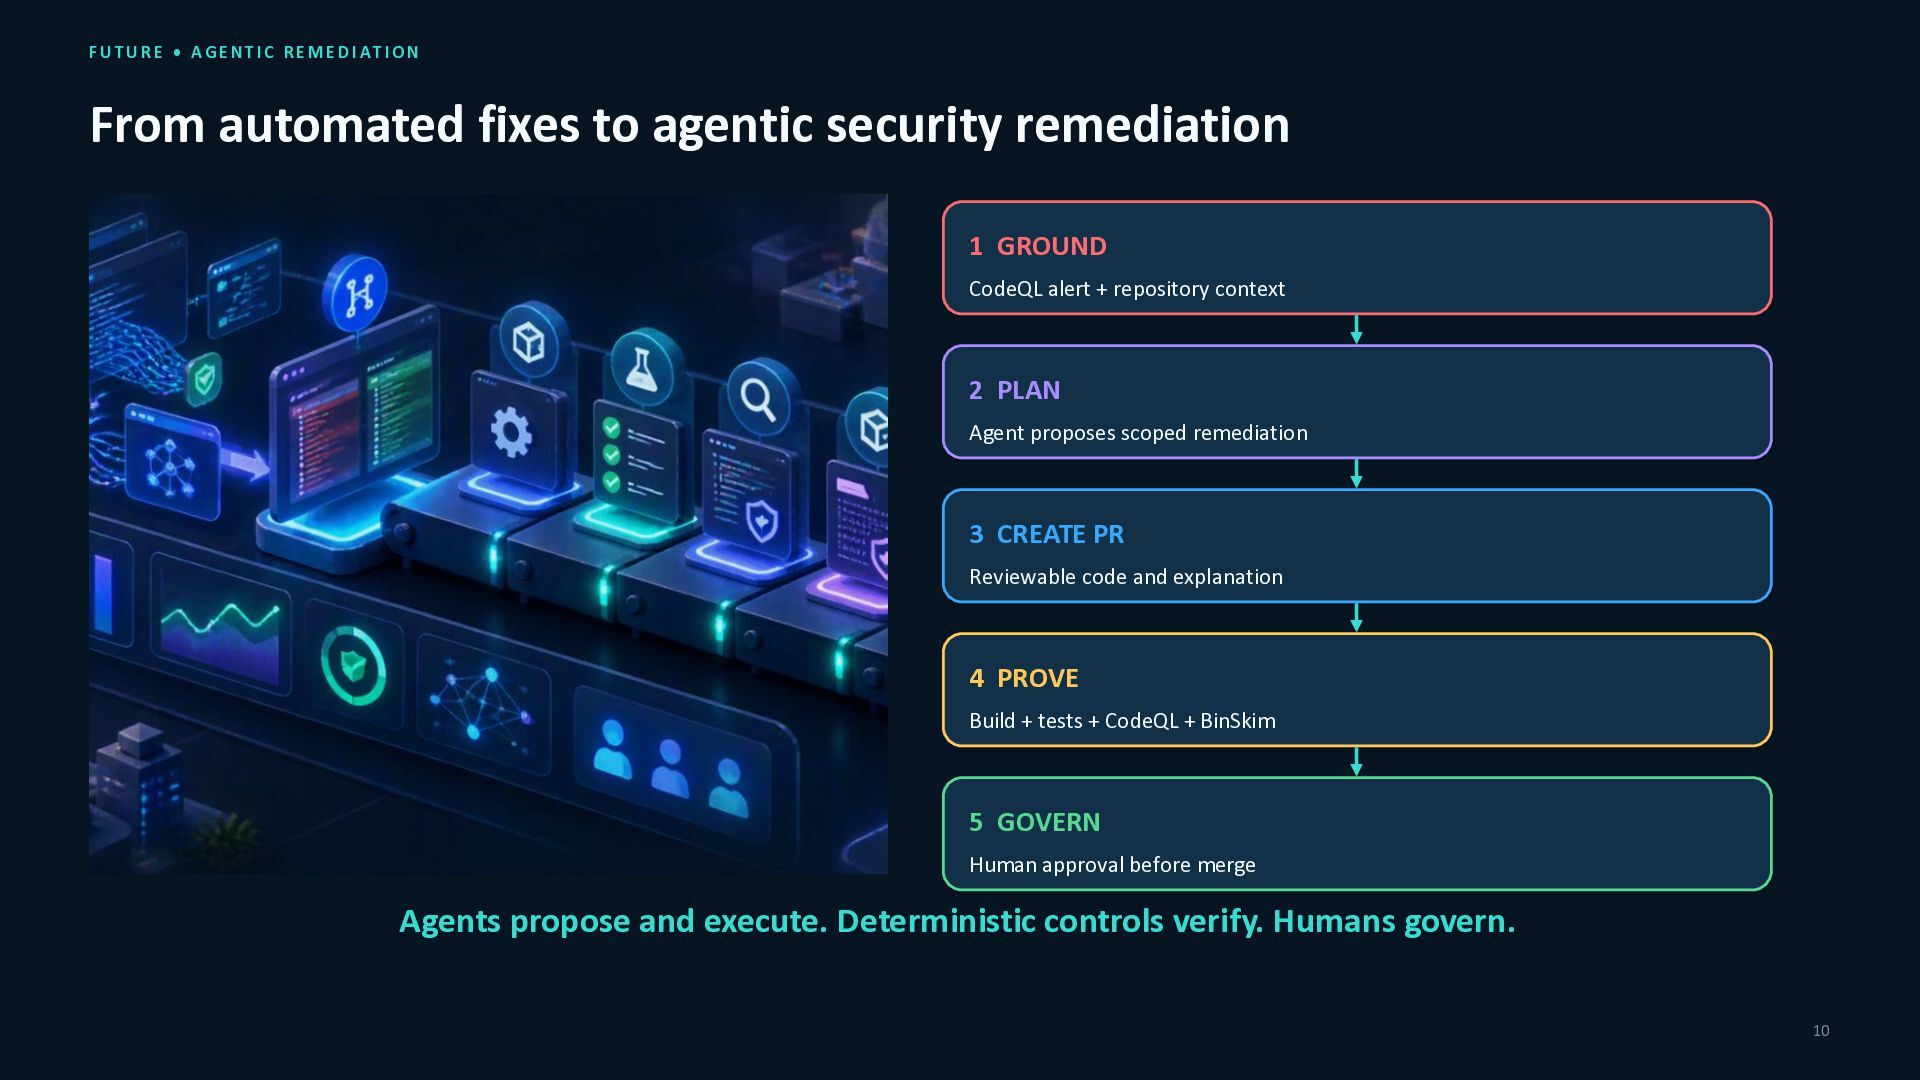
  10. FUTURE • AGENTIC REMEDIATION From automated fixes to agentic security

    remediation 1 GROUND CodeQL alert + repository context 2 PLAN Agent proposes scoped remediation 3 CREATE PR Reviewable code and explanation 4 PROVE Build + tests + CodeQL + BinSkim 5 GOVERN Human approval before merge Agents propose and execute. Deterministic controls verify. Humans govern. 10
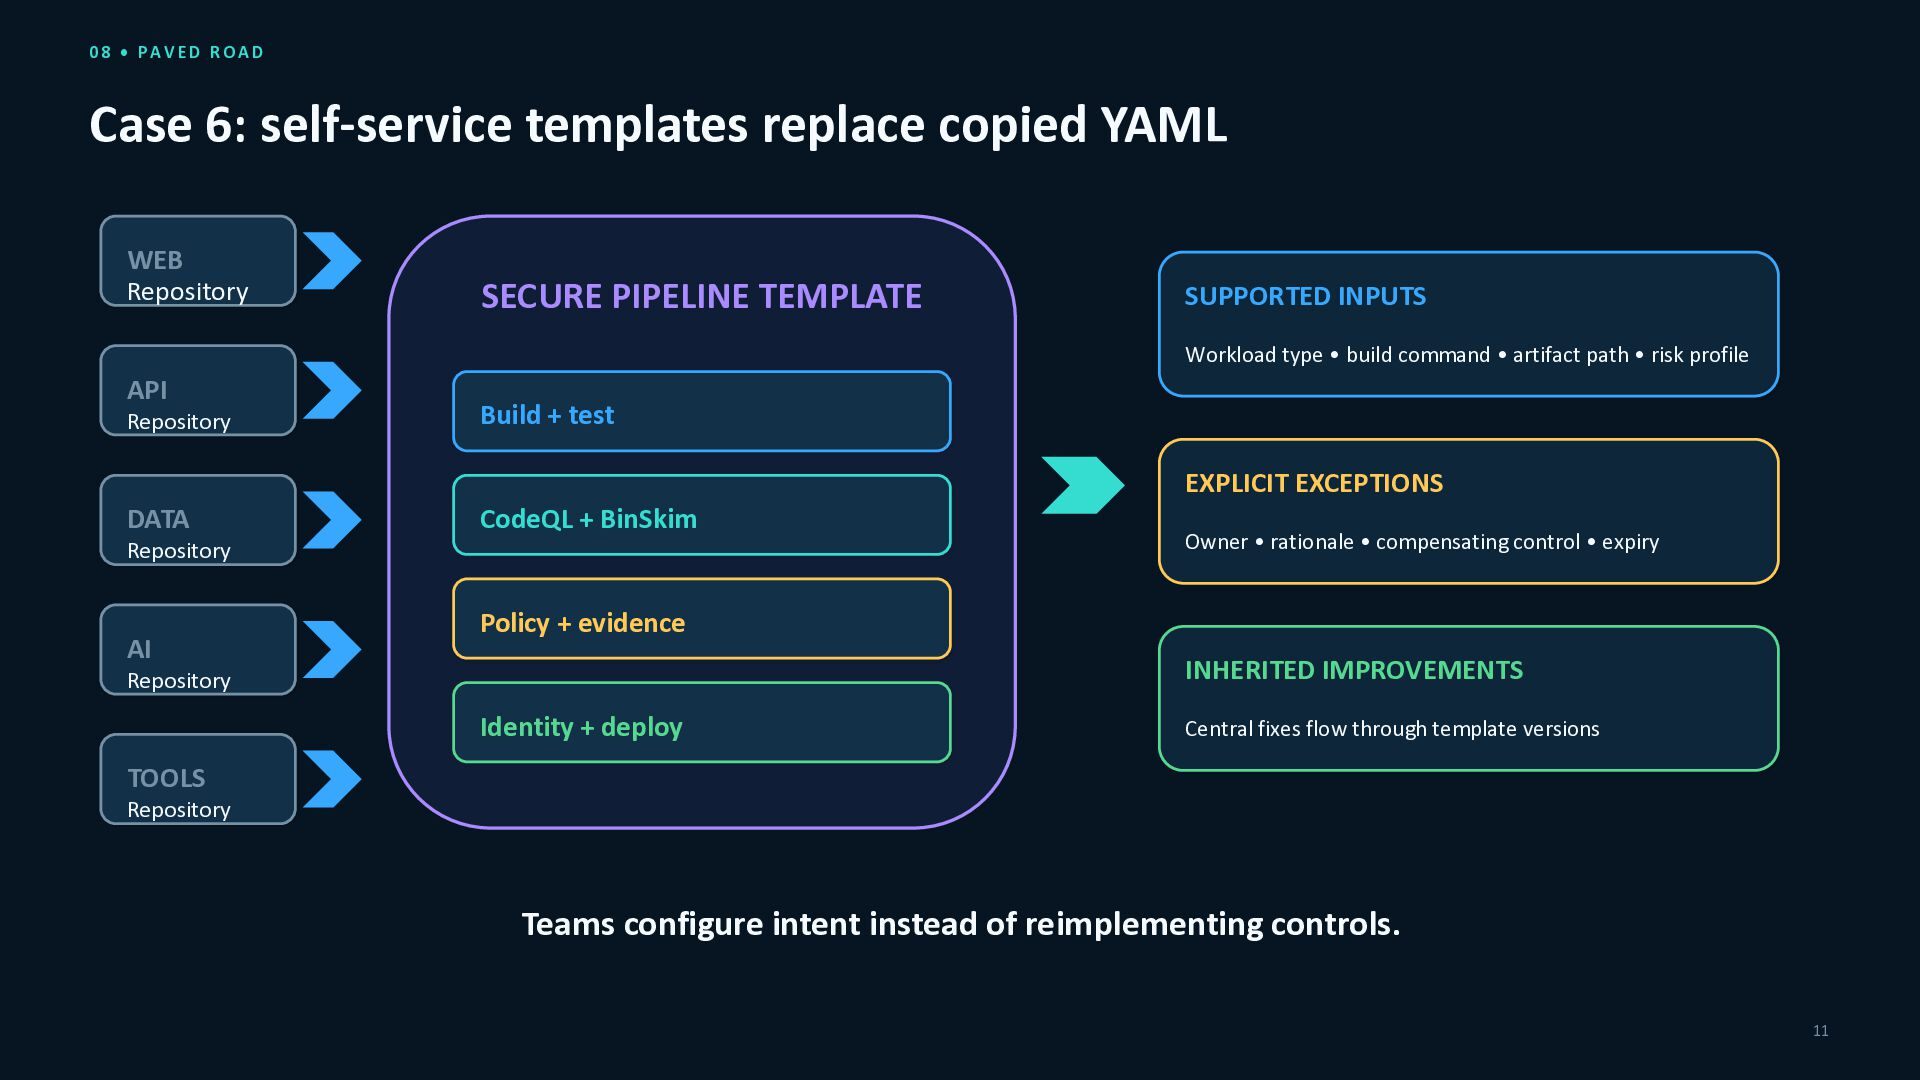
  11. 08 • PAVED ROAD Case 6: self-service templates replace copied

    YAML WEB Repository SECURE PIPELINE TEMPLATE SUPPORTED INPUTS Workload type • build command • artifact path • risk profile API Repository Build + test EXPLICIT EXCEPTIONS DATA CodeQL + BinSkim Repository AI Owner • rationale • compensating control • expiry Policy + evidence INHERITED IMPROVEMENTS Repository Identity + deploy Central fixes flow through template versions TOOLS Repository Teams configure intent instead of reimplementing controls. 11
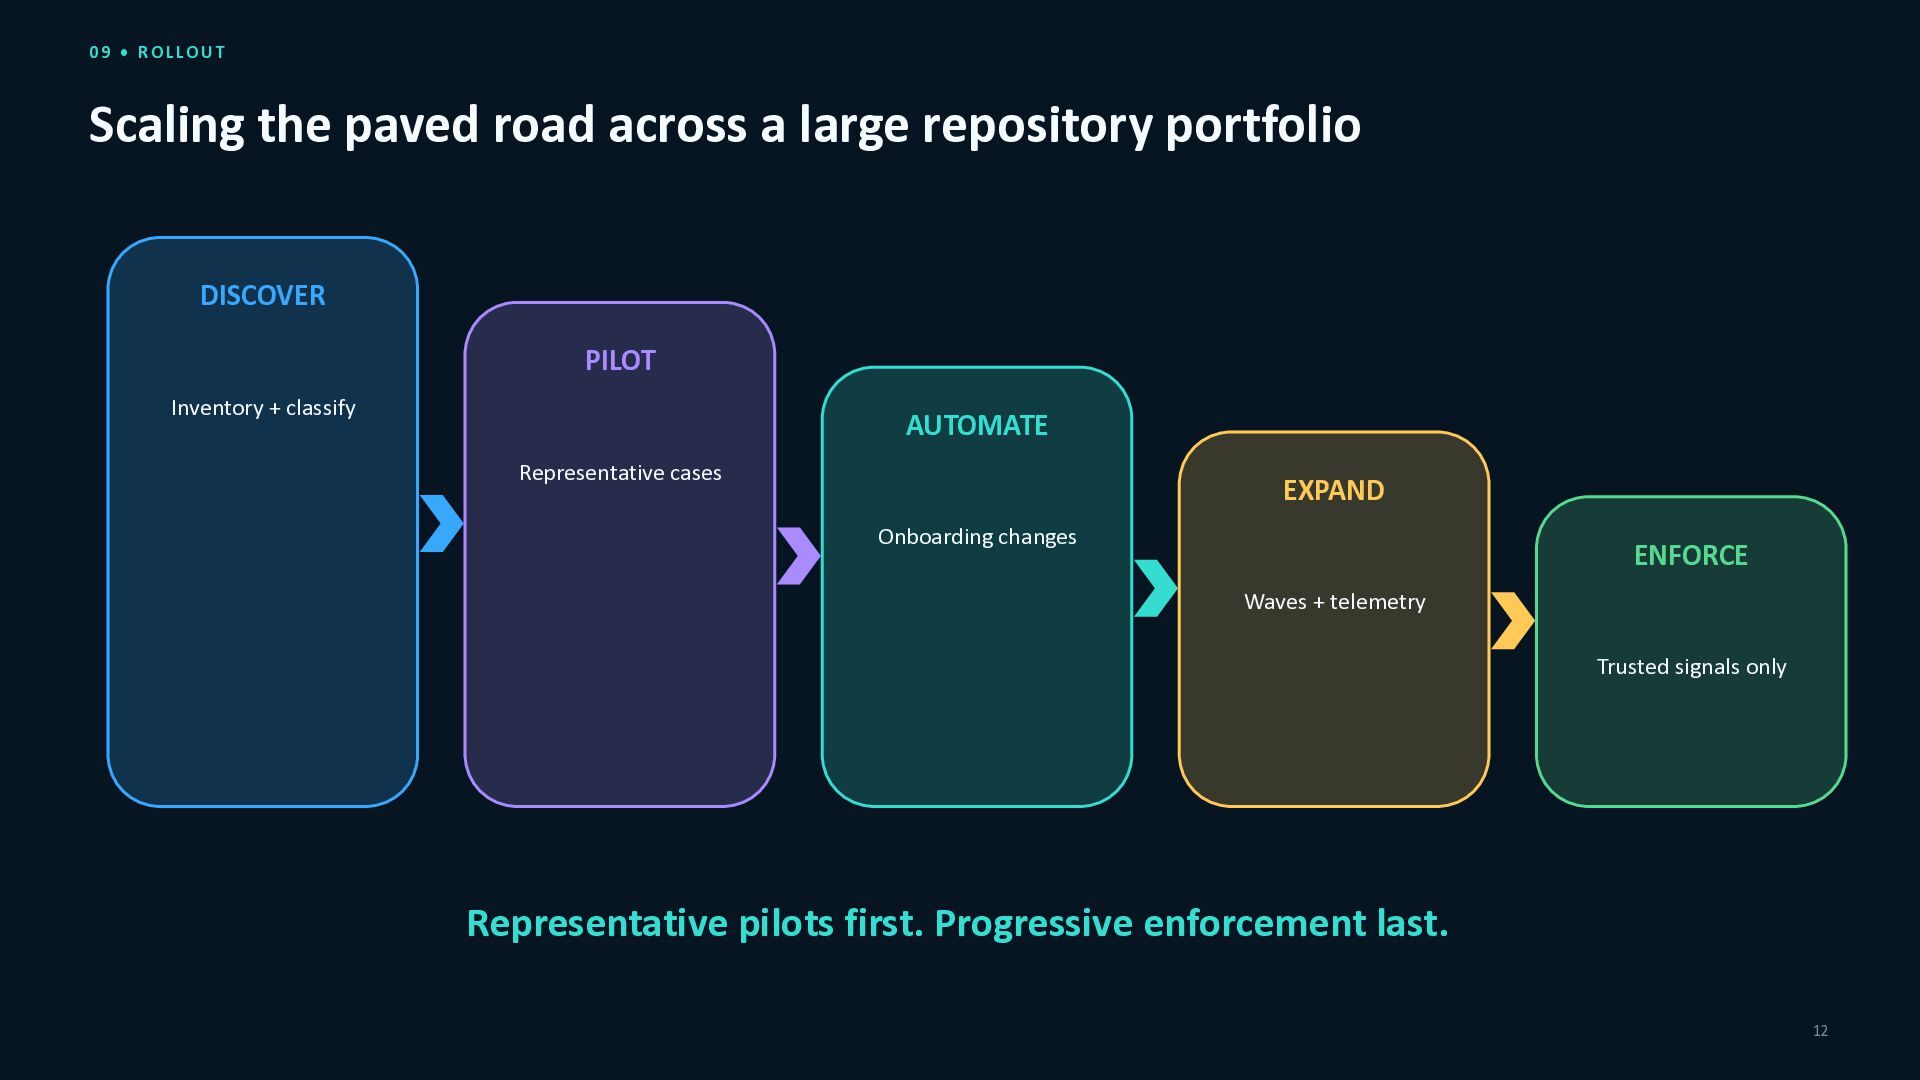
  12. 09 • ROLLOUT Scaling the paved road across a large

    repository portfolio DISCOVER PILOT Inventory + classify AUTOMATE Representative cases EXPAND Onboarding changes ENFORCE Waves + telemetry Trusted signals only Representative pilots first. Progressive enforcement last. 12
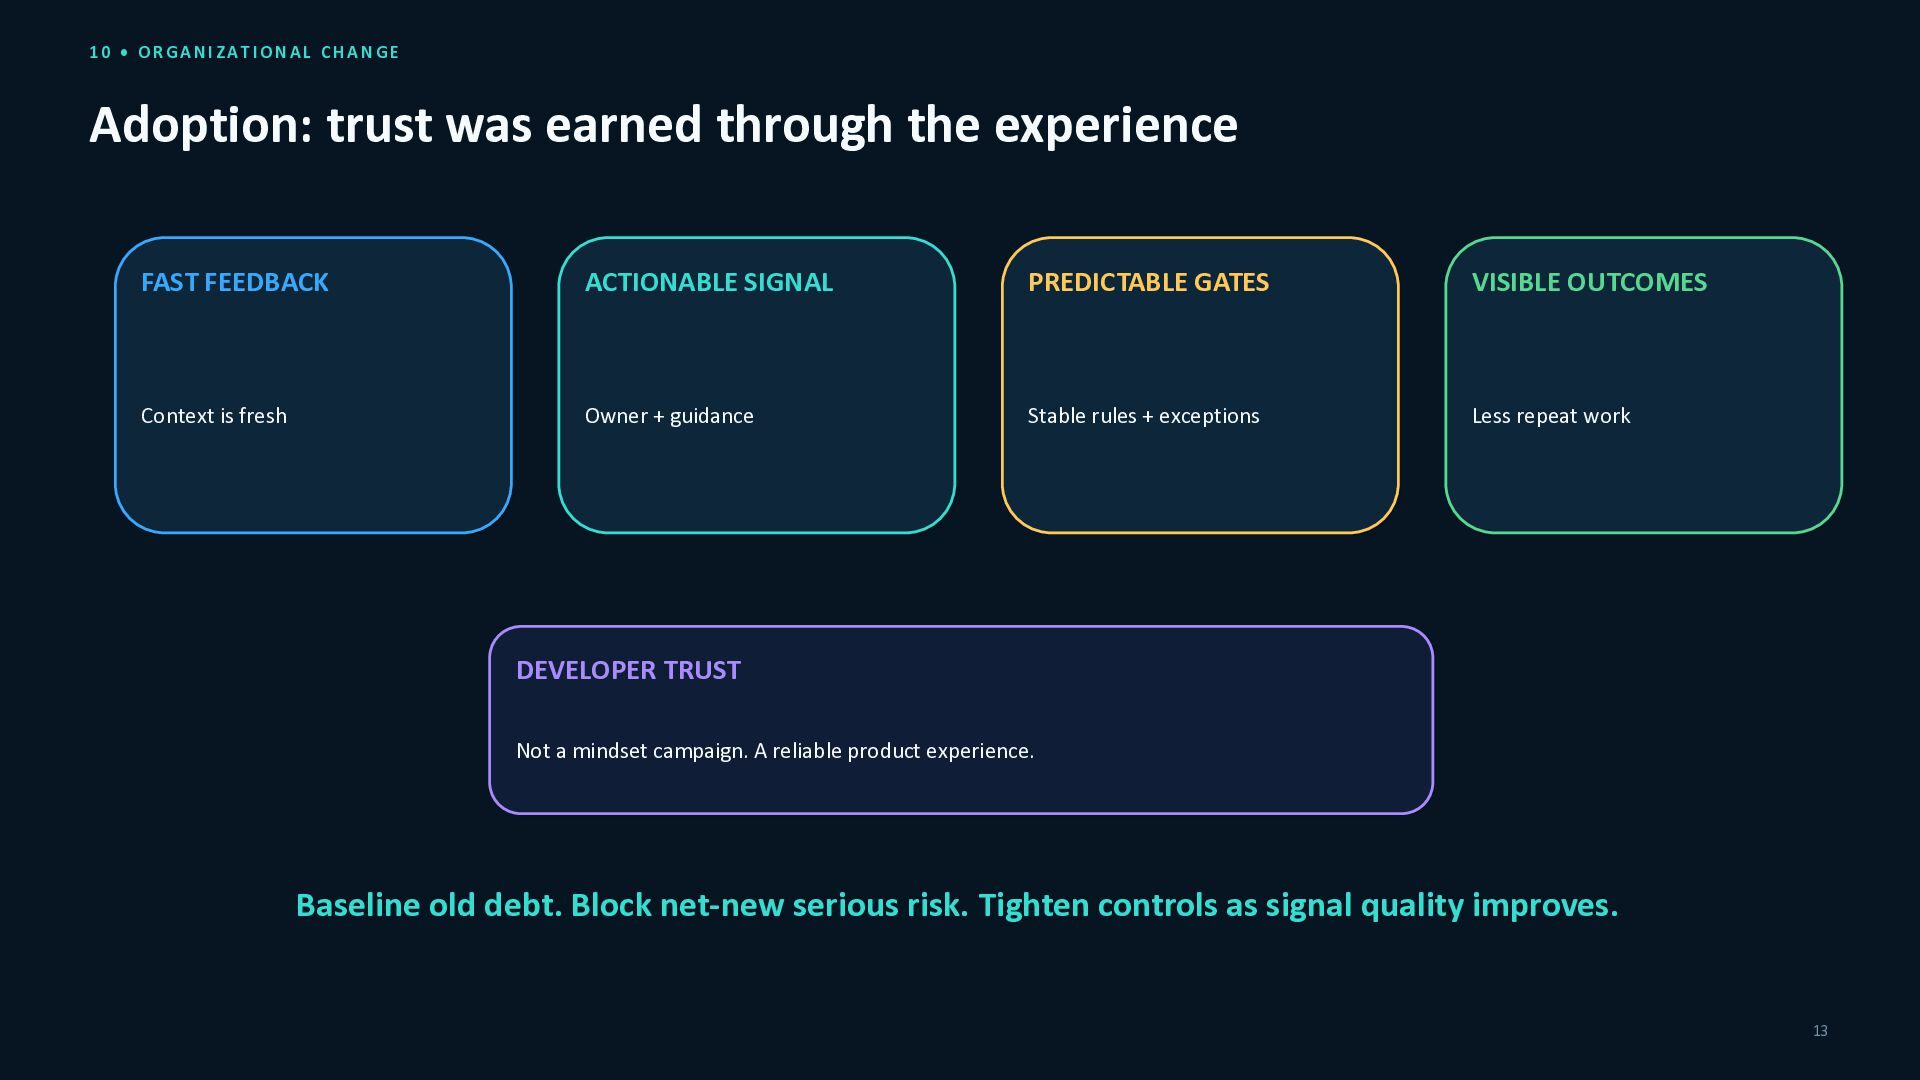
  13. 10 • ORGANIZATIONAL CHANGE Adoption: trust was earned through the

    experience FAST FEEDBACK ACTIONABLE SIGNAL PREDICTABLE GATES VISIBLE OUTCOMES Context is fresh Owner + guidance Stable rules + exceptions Less repeat work DEVELOPER TRUST Not a mindset campaign. A reliable product experience. Baseline old debt. Block net-new serious risk. Tighten controls as signal quality improves. 13
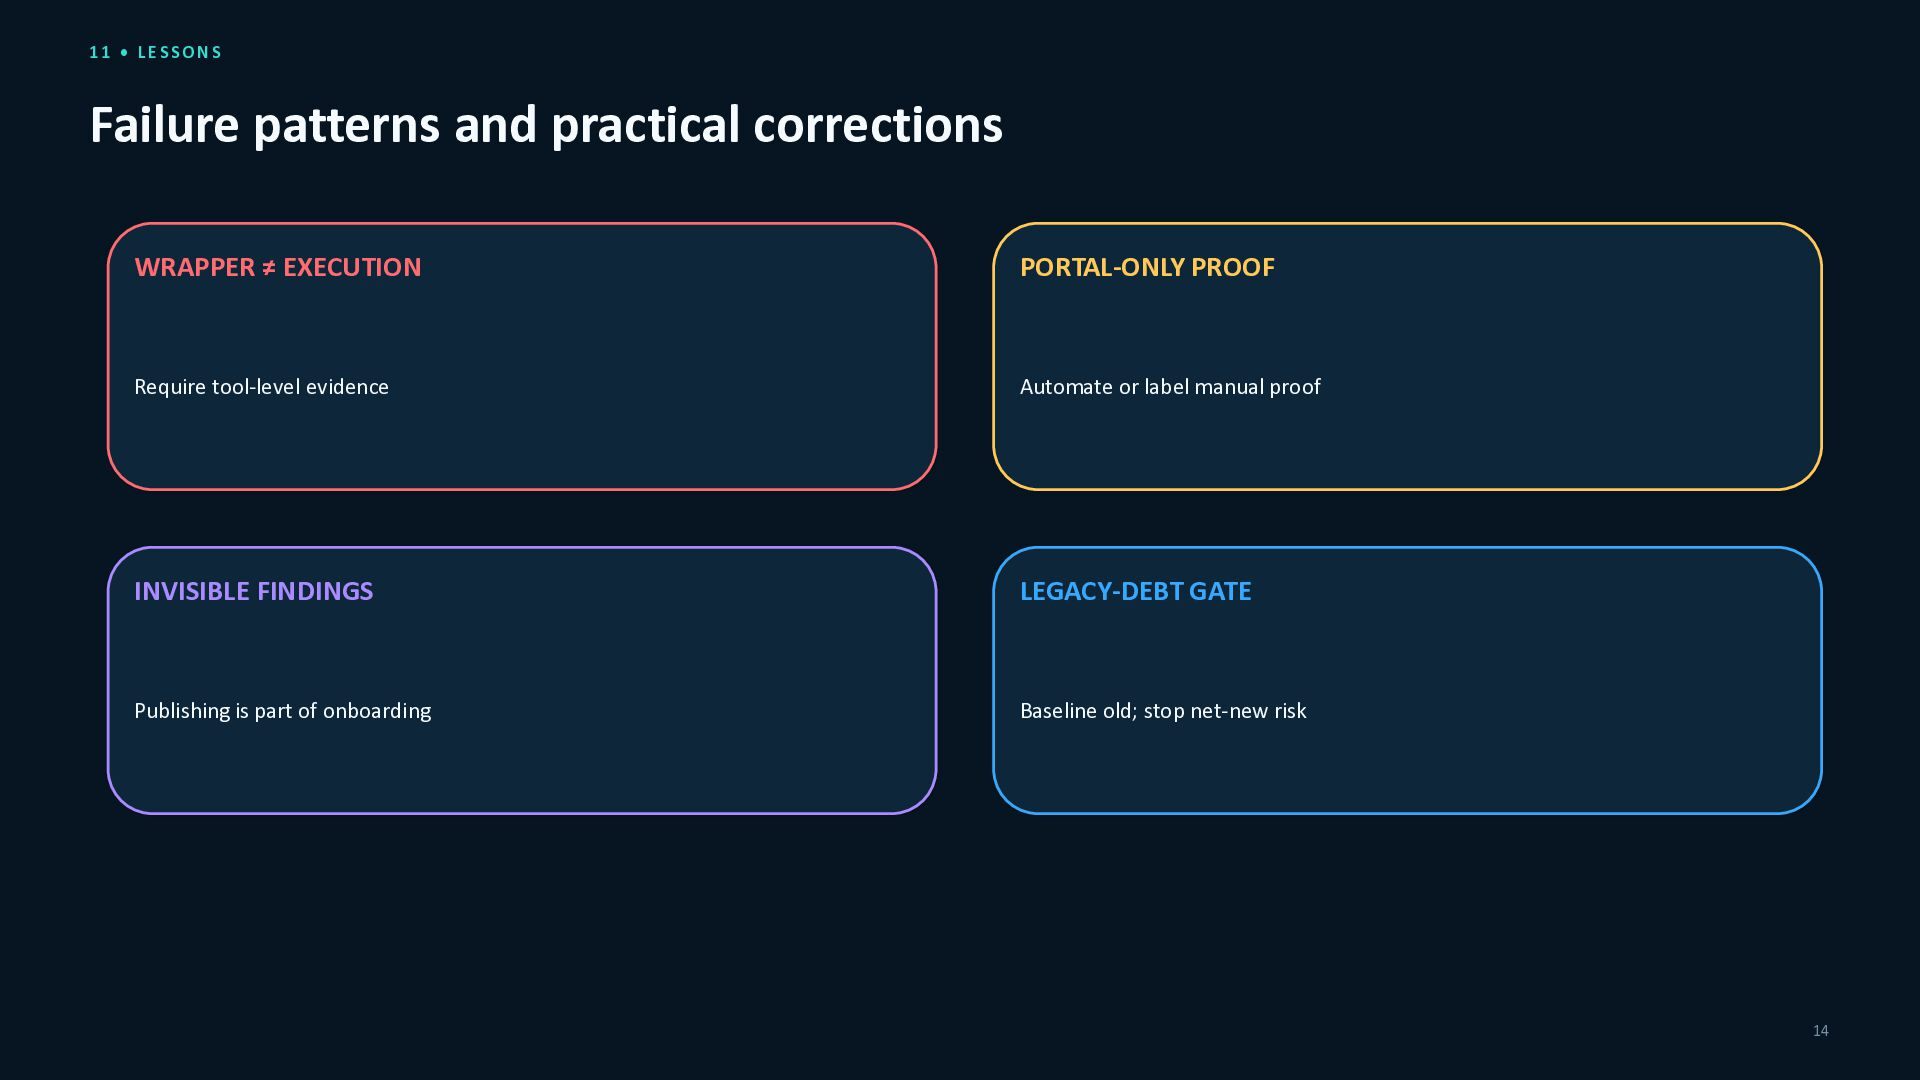
  14. 11 • LESSONS Failure patterns and practical corrections WRAPPER ≠

    EXECUTION PORTAL-ONLY PROOF Require tool-level evidence Automate or label manual proof INVISIBLE FINDINGS LEGACY-DEBT GATE Publishing is part of onboarding Baseline old; stop net-new risk 14
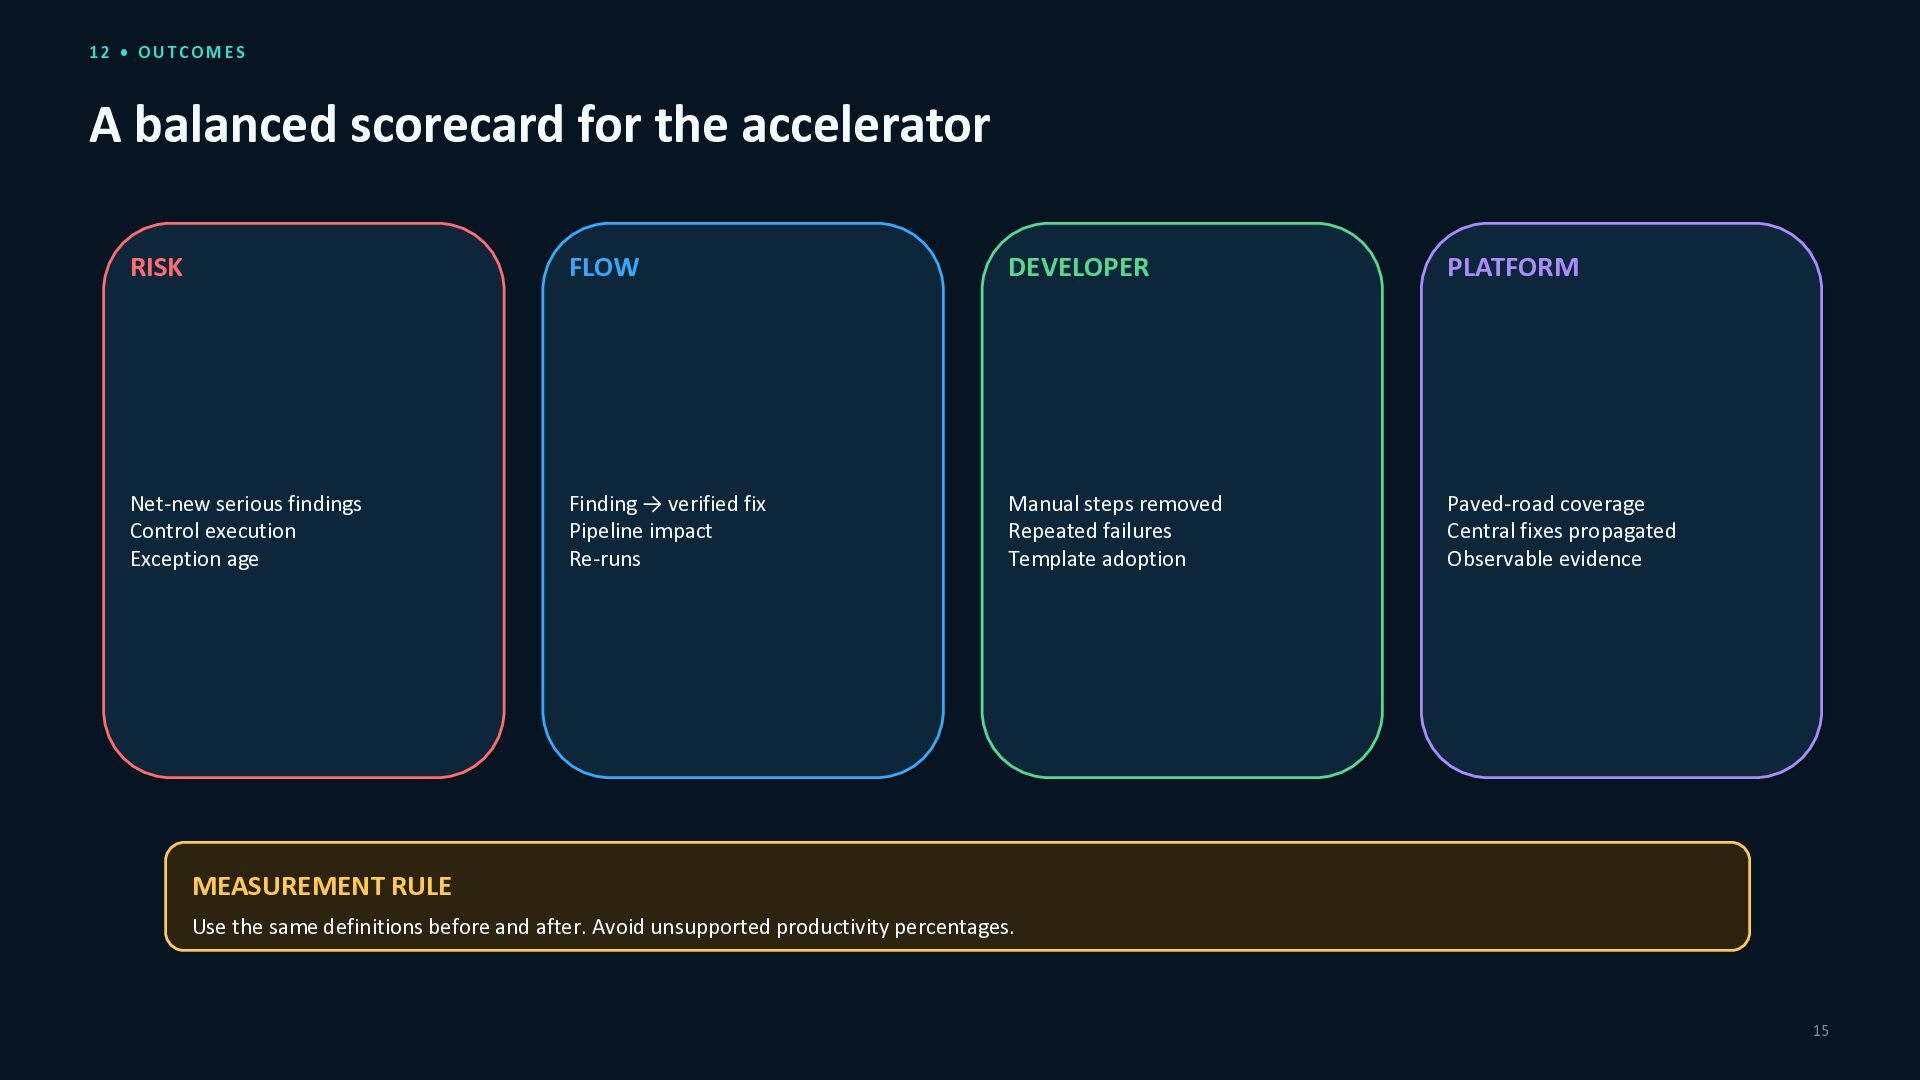
  15. 12 • OUTCOMES A balanced scorecard for the accelerator RISK

    FLOW DEVELOPER PLATFORM Net-new serious findings Control execution Exception age Finding → verified fix Pipeline impact Re-runs Manual steps removed Repeated failures Template adoption Paved-road coverage Central fixes propagated Observable evidence MEASUREMENT RULE Use the same definitions before and after. Avoid unsupported productivity percentages. 15
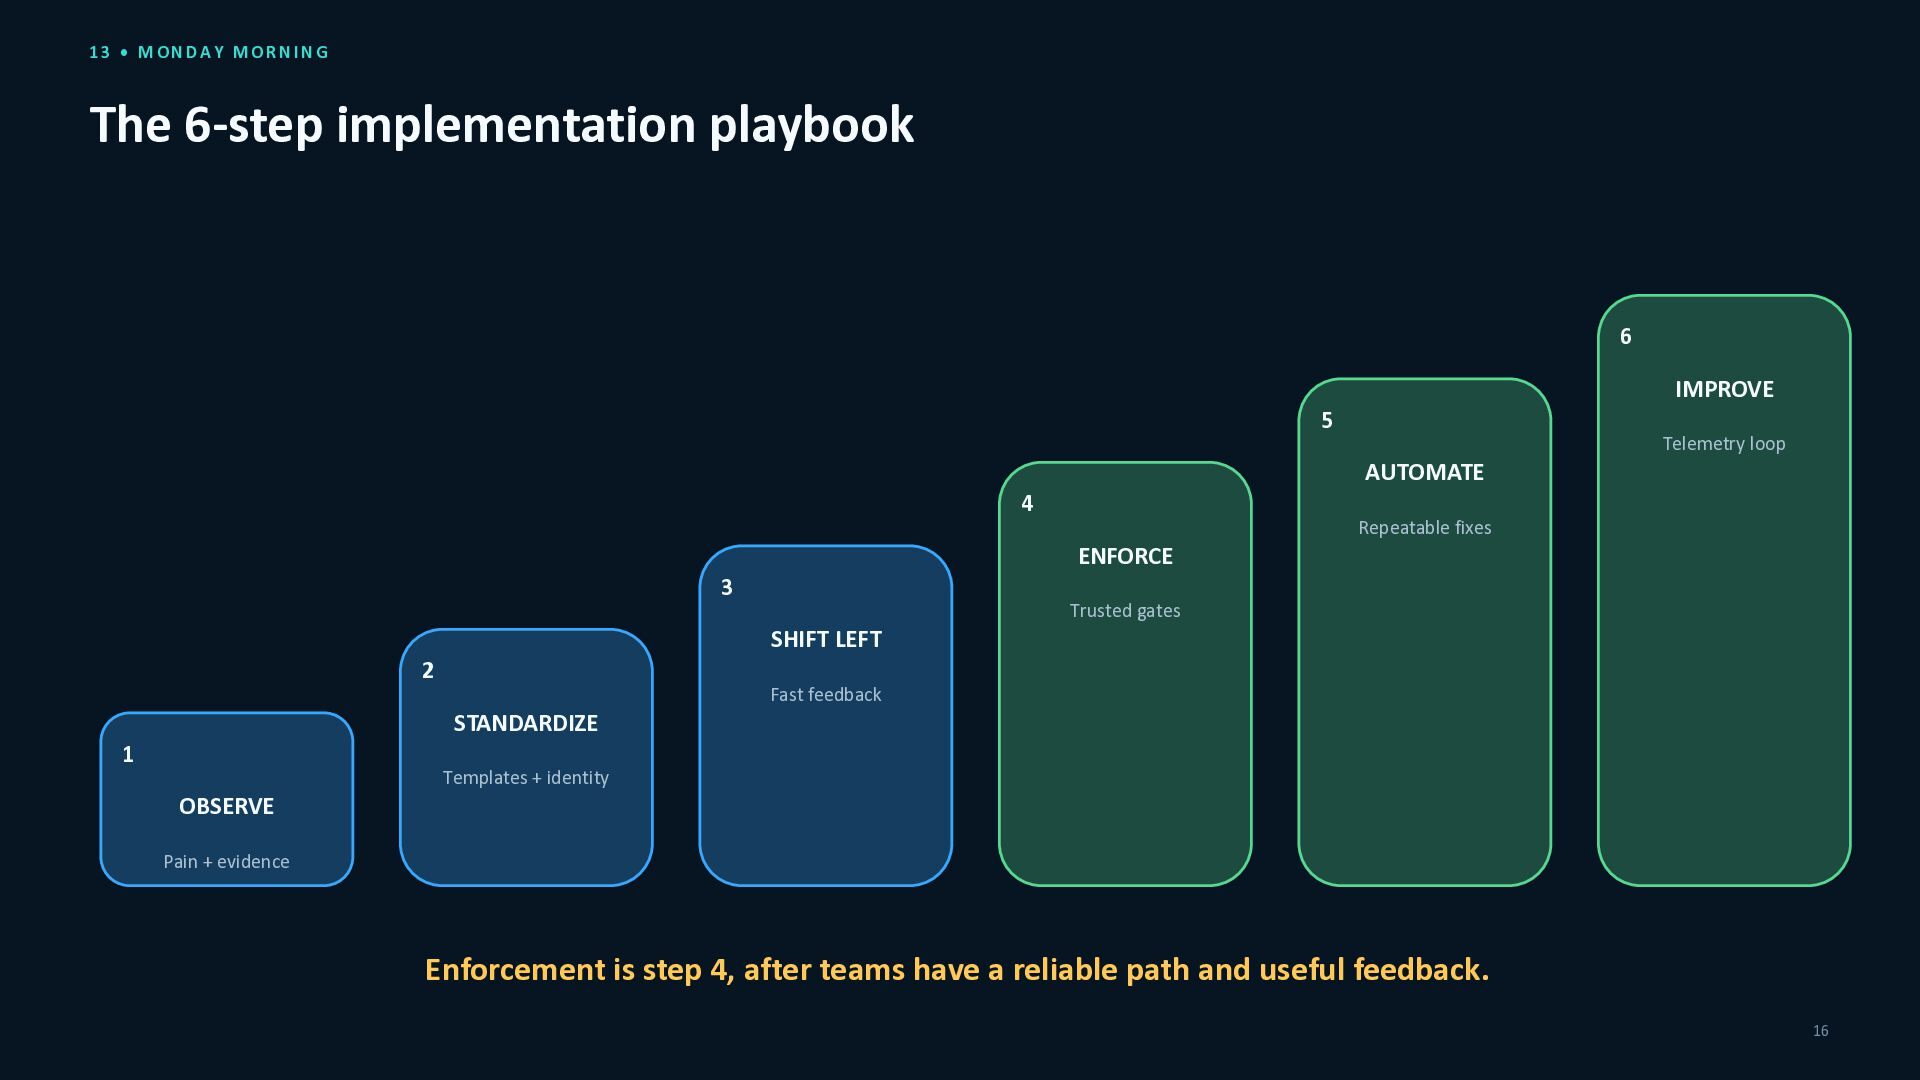
  16. 13 • MONDAY MORNING The 6-step implementation playbook 6 IMPROVE

    5 Telemetry loop AUTOMATE 4 Repeatable fixes ENFORCE 3 Trusted gates SHIFT LEFT 2 Fast feedback STANDARDIZE 1 Templates + identity OBSERVE Pain + evidence Enforcement is step 4, after teams have a reliable path and useful feedback. 16
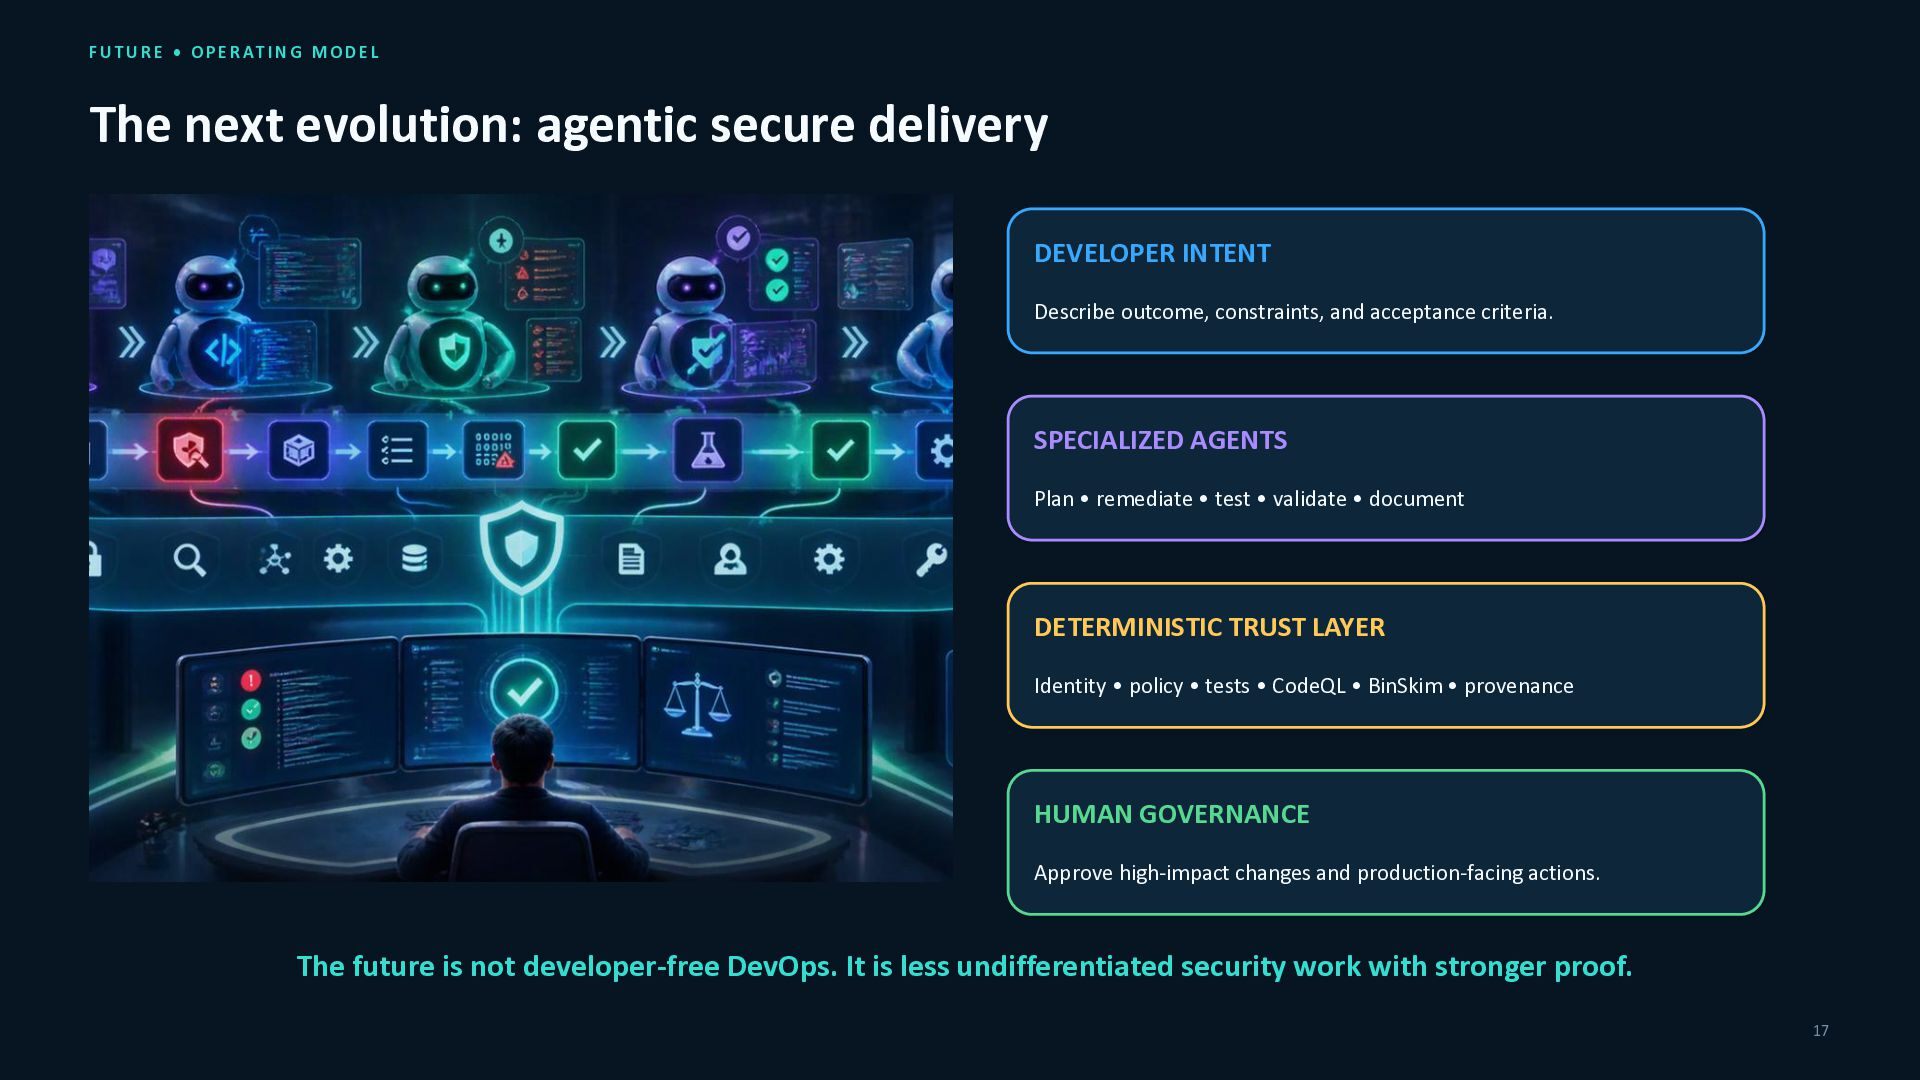
  17. FUTURE • OPERATING MODEL The next evolution: agentic secure delivery

    DEVELOPER INTENT Describe outcome, constraints, and acceptance criteria. SPECIALIZED AGENTS Plan • remediate • test • validate • document DETERMINISTIC TRUST LAYER Identity • policy • tests • CodeQL • BinSkim • provenance HUMAN GOVERNANCE Approve high-impact changes and production-facing actions. The future is not developer-free DevOps. It is less undifferentiated security work with stronger proof. 17
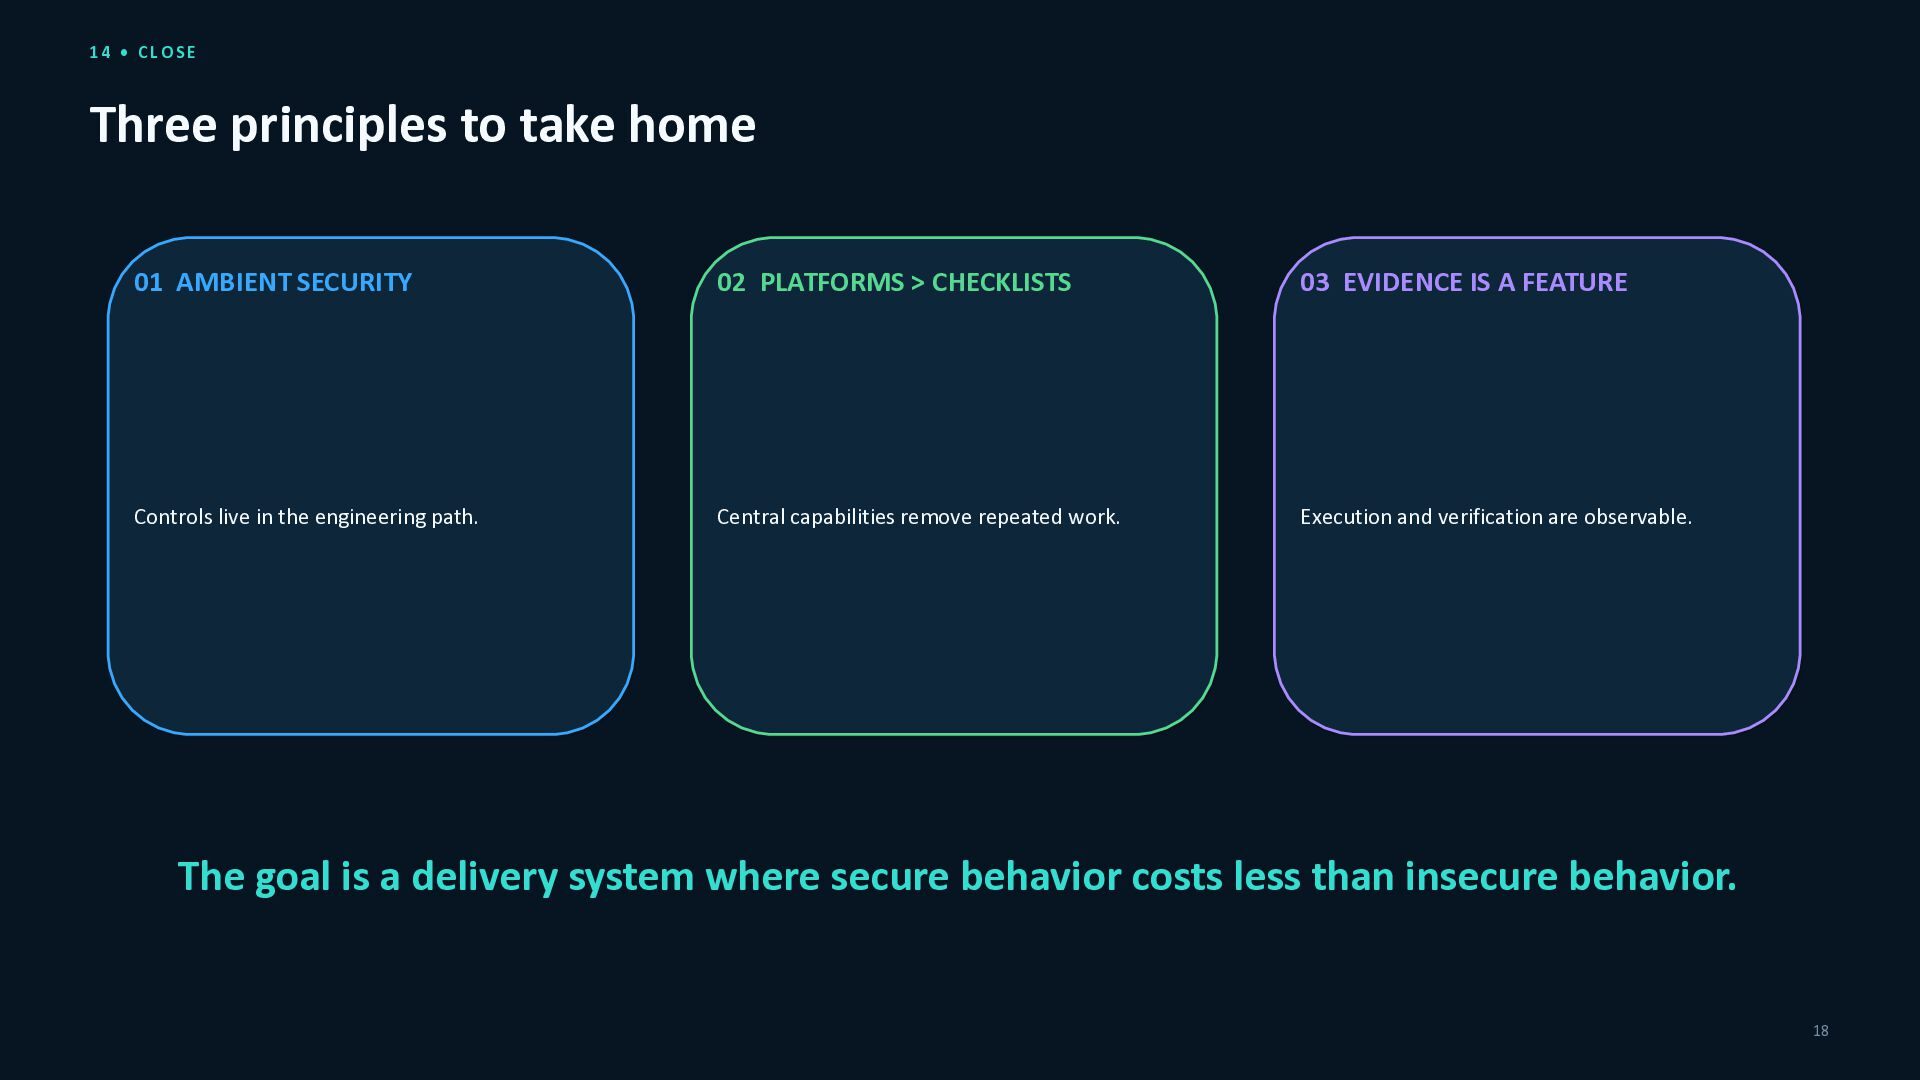
  18. 14 • CLOSE Three principles to take home 01 AMBIENT

    SECURITY 02 PLATFORMS > CHECKLISTS 03 EVIDENCE IS A FEATURE Controls live in the engineering path. Central capabilities remove repeated work. Execution and verification are observable. The goal is a delivery system where secure behavior costs less than insecure behavior. 18
  19. 17 • Q&A Q&A Questions & discussion Name: Lalith lakshmi

    Chaitanya kumar Mangalagiri LinkedIn: linkedin.com/in/lalith-chaitanya-mangalagiri-b31445170 21