Share
Embed
Transcript
127 slides
-
“Treat your password like your toothbrush. Don't let anybody else
use it, and get a new one every six months.” Clifford Stoll -
PASSWORD SECURITY IS NOT UNDER YOUR DIRECT CONTROL (CAN’T ASSUME
YOUR PASSWORD IS STORED IN A SECURE WAY) -
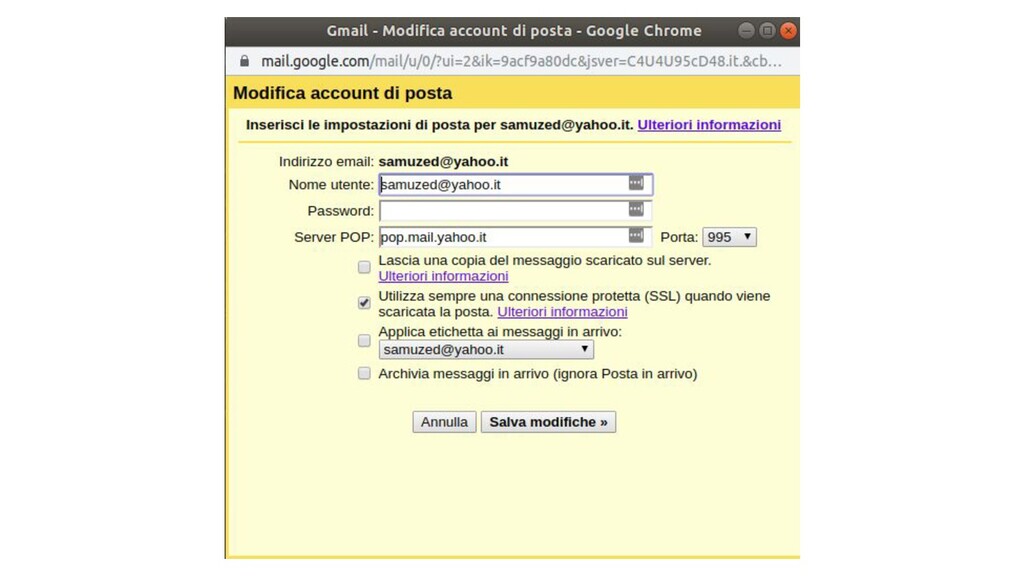
THE ISSUE (OF GIVING TO 3rd PARTY YOUR PASSWORD) •
Password stored in clear-text. • Servers are required to support password authentication, despite the security weaknesses inherent in passwords. • Third-party applications gain overly broad access to the resource owner's protected resources, leaving resource owners without any ability to restrict duration or access to a limited subset of resources. • Resource owners cannot revoke access to an individual third party without revoking access to all third parties, and must do so by changing the third party's password. • Compromise of any third-party application results in compromise of the end-user's password and all of the data protected by that password. -
“The OAuth 2.0 authorization framework enables a third-party application to
obtain limited access to an HTTP service, either on behalf of a resource owner by orchestrating an approval interaction between the resource owner and the HTTP service, or by allowing the third-party application to obtain access on its own behalf.” https://tools.ietf.org/html/rfc6749 -
“The OAuth 2.0 authorization framework enables a third-party application to
obtain limited access to an HTTP service, either on behalf of a resource owner by orchestrating an approval interaction between the resource owner and the HTTP service, or by allowing the third-party application to obtain access on its own behalf.” https://tools.ietf.org/html/rfc6749 -
“The OAuth 2.0 authorization framework enables a third-party application to
obtain limited access to an HTTP service, either on behalf of a resource owner by orchestrating an approval interaction between the resource owner and the HTTP service, or by allowing the third-party application to obtain access on its own behalf.” https://tools.ietf.org/html/rfc6749 -
“The OAuth 2.0 authorization framework enables a third-party application to
obtain limited access to an HTTP service, either on behalf of a resource owner by orchestrating an approval interaction between the resource owner and the HTTP service, or by allowing the third-party application to obtain access on its own behalf.” https://tools.ietf.org/html/rfc6749 -
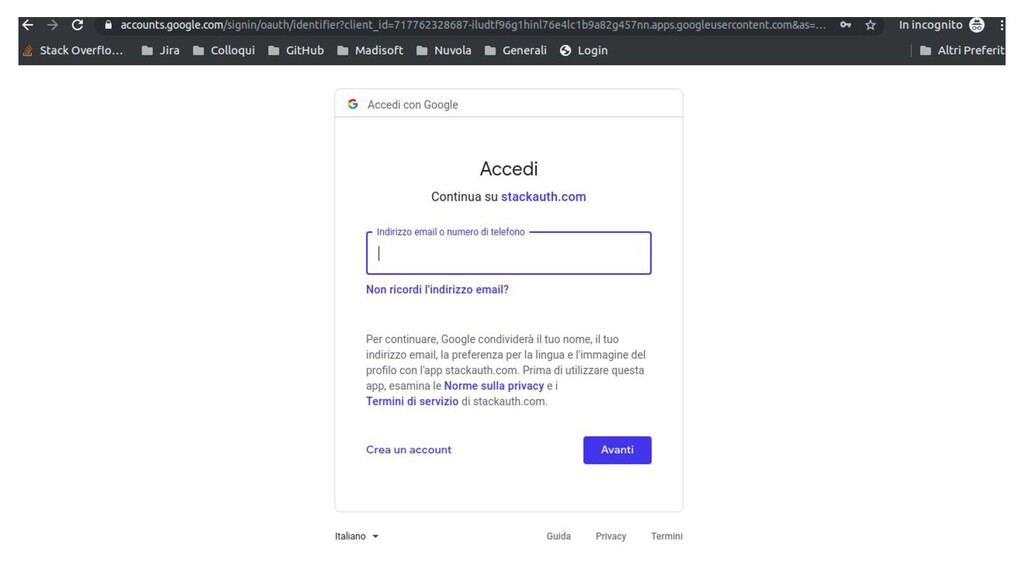
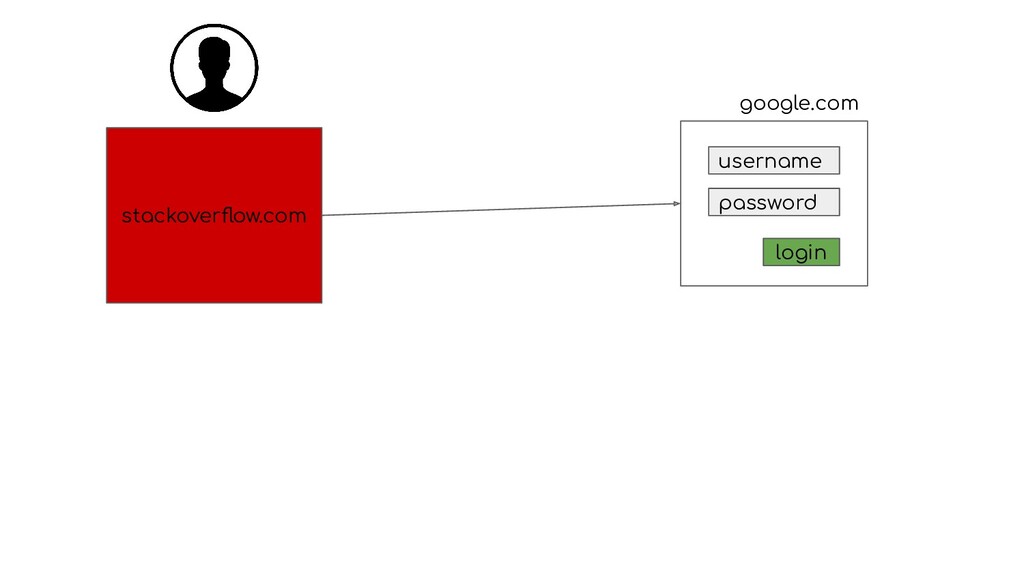
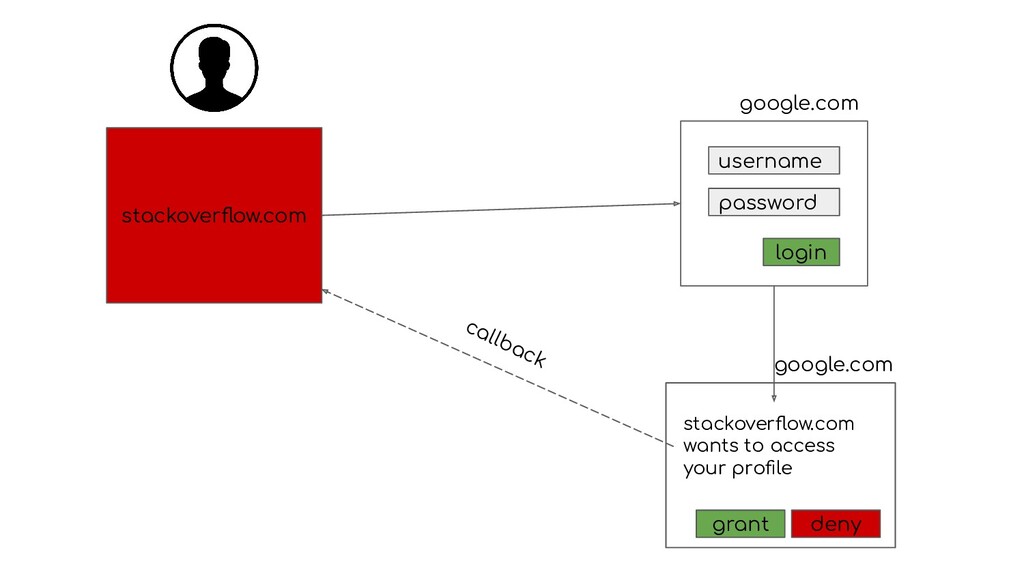
stackoverflow.com username password login google.com google.com stackoverflow.com wants to access
your profile grant deny callback -
stackoverflow.com username password login google.com google.com stackoverflow.com wants to access
your profile grant deny callback -
“The OAuth 2.0 authorization framework enables a third-party application to
obtain limited access to an HTTP service, either on behalf of a resource owner by orchestrating an approval interaction between the resource owner and the HTTP service, or by allowing the third-party application to obtain access on its own behalf.” https://tools.ietf.org/html/rfc6749 -
OpenID CONNECT “OpenID Connect 1.0 is a simple identity layer
on top of the OAuth 2.0 [RFC6749] protocol. It enables Clients to verify the identity of the End-User based on the authentication performed by an Authorization Server, as well as to obtain basic profile information about the End-User in an interoperable and REST-like manner.” https://openid.net/specs/openid-connect-core-1_0.html -
OpenID CONNECT “OpenID Connect 1.0 is a simple identity layer
on top of the OAuth 2.0 [RFC6749] protocol. It enables Clients to verify the identity of the End-User based on the authentication performed by an Authorization Server, as well as to obtain basic profile information about the End-User in an interoperable and REST-like manner.” https://openid.net/specs/openid-connect-core-1_0.html -
OpenID CONNECT “OpenID Connect 1.0 is a simple identity layer
on top of the OAuth 2.0 [RFC6749] protocol. It enables Clients to verify the identity of the End-User based on the authentication performed by an Authorization Server, as well as to obtain basic profile information about the End-User in an interoperable and REST-like manner.” https://openid.net/specs/openid-connect-core-1_0.html -
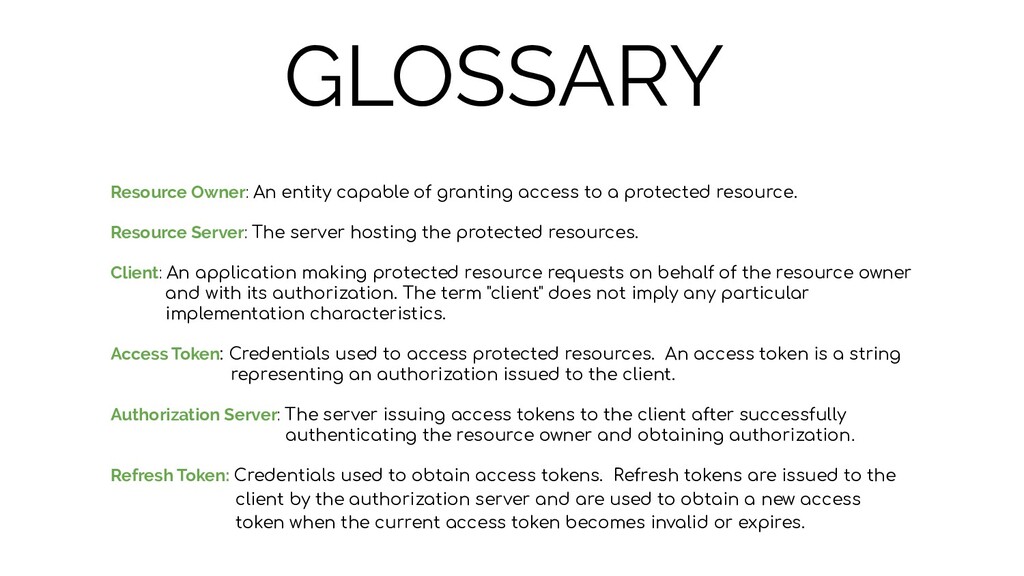
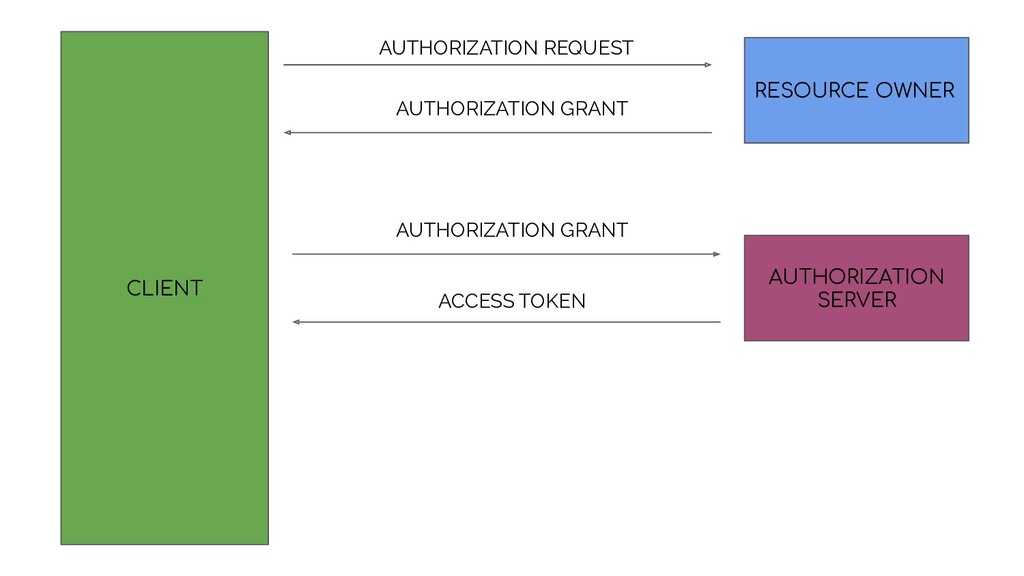
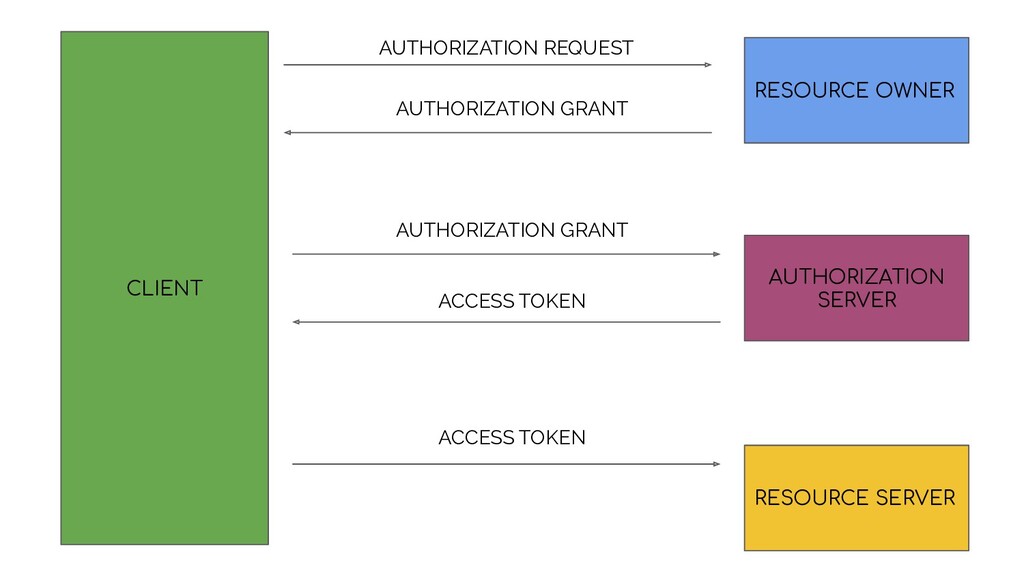
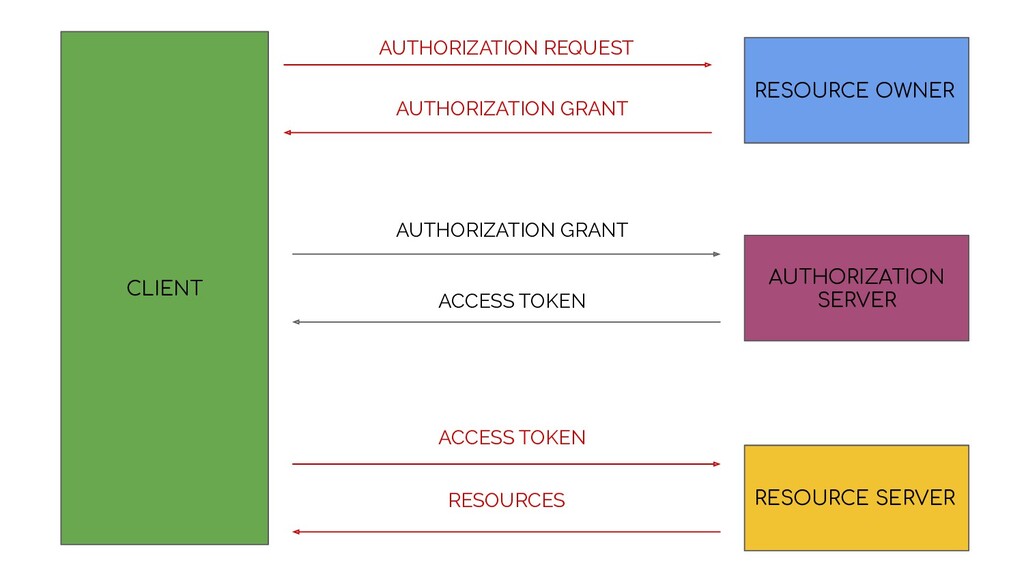
GLOSSARY Resource Owner: An entity capable of granting access to
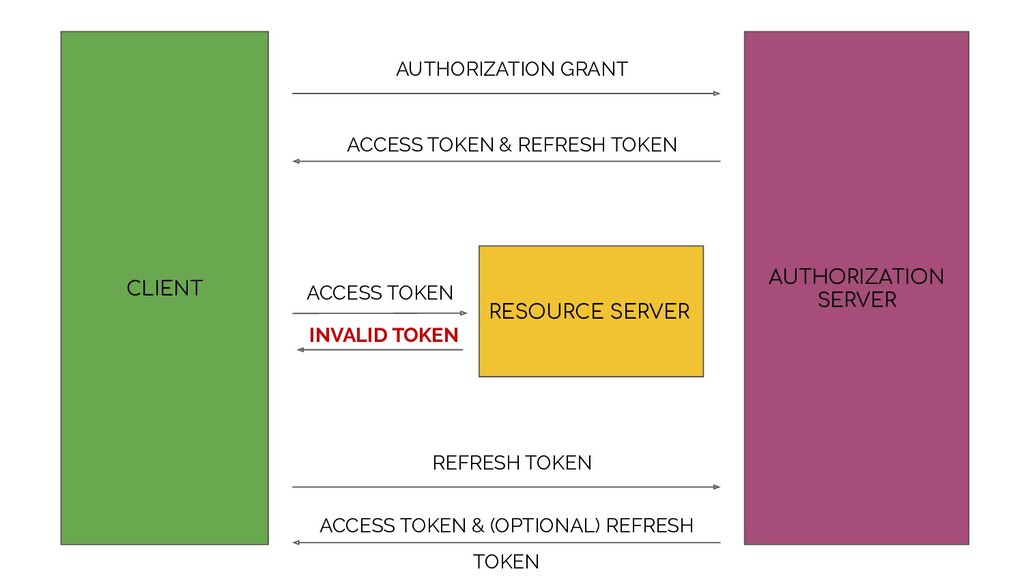
a protected resource. Resource Server: The server hosting the protected resources. Client: An application making protected resource requests on behalf of the resource owner and with its authorization. The term "client" does not imply any particular implementation characteristics. Access Token: Credentials used to access protected resources. An access token is a string representing an authorization issued to the client. Authorization Server: The server issuing access tokens to the client after successfully authenticating the resource owner and obtaining authorization. Refresh Token: Credentials used to obtain access tokens. Refresh tokens are issued to the client by the authorization server and are used to obtain a new access token when the current access token becomes invalid or expires. -
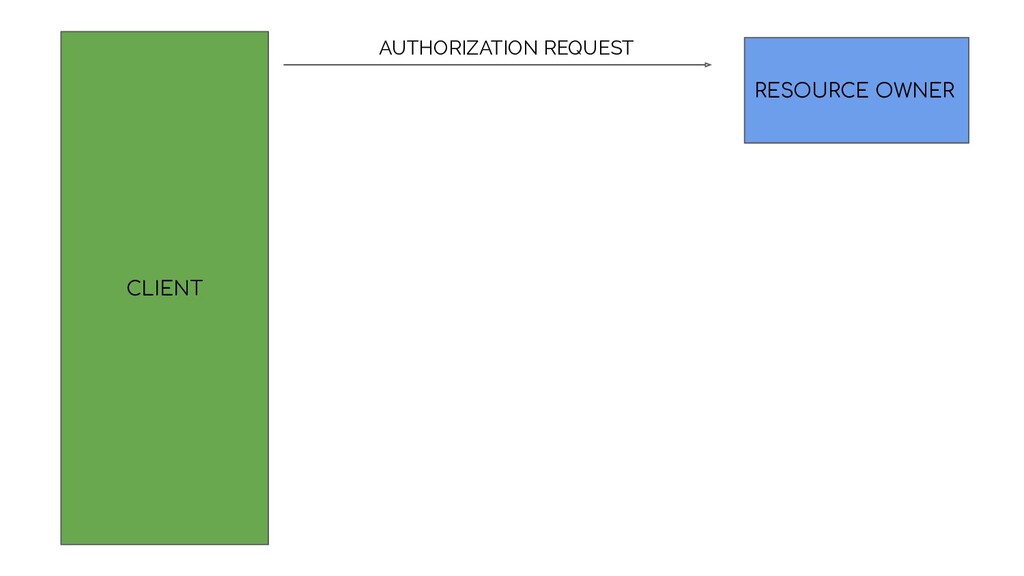
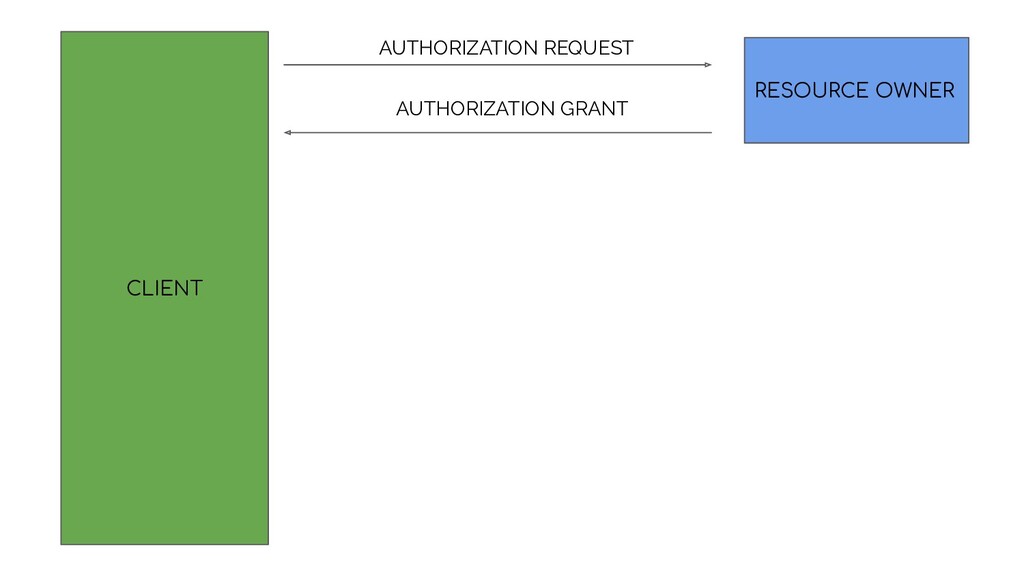
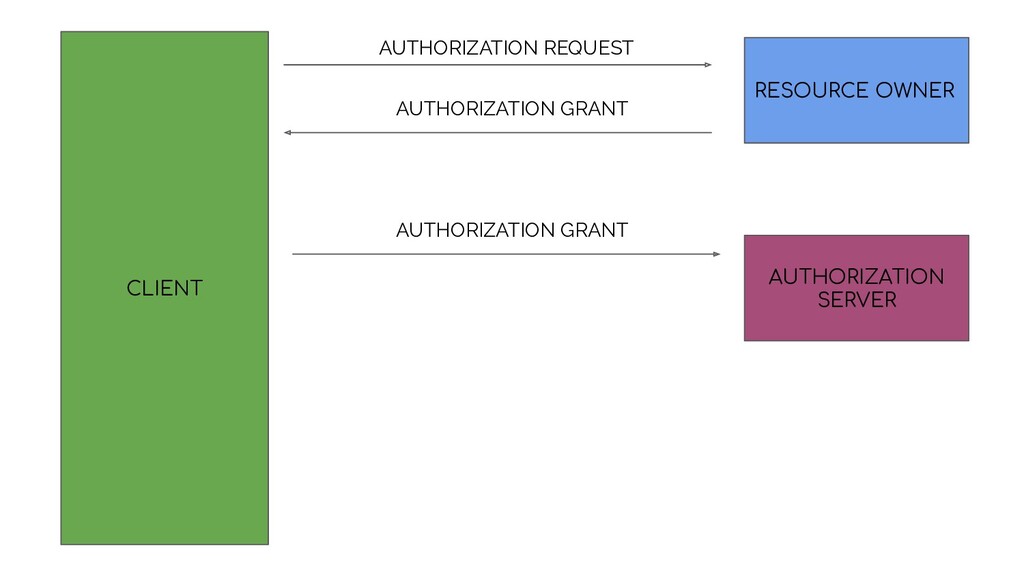
CLIENT RESOURCE OWNER AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION REQUEST AUTHORIZATION
GRANT AUTHORIZATION GRANT ACCESS TOKEN ACCESS TOKEN -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION REQUEST AUTHORIZATION
GRANT AUTHORIZATION GRANT ACCESS TOKEN ACCESS TOKEN RESOURCES -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION REQUEST AUTHORIZATION
GRANT AUTHORIZATION GRANT ACCESS TOKEN ACCESS TOKEN RESOURCES -
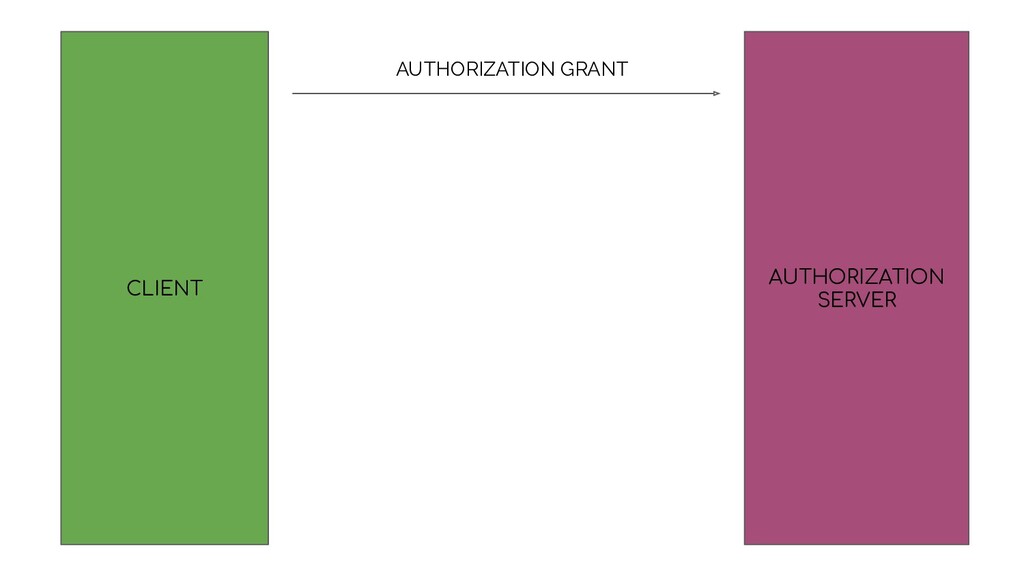
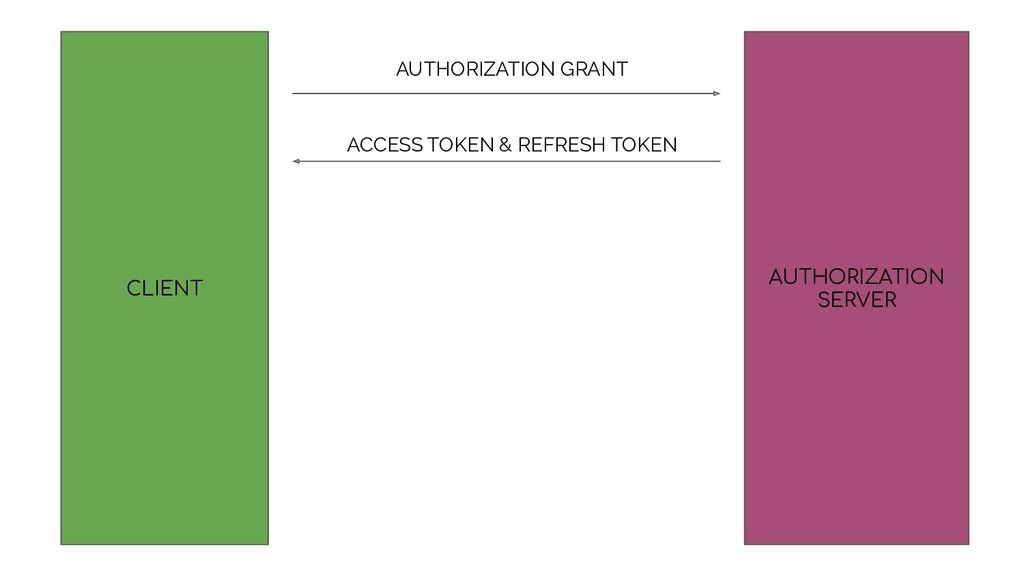
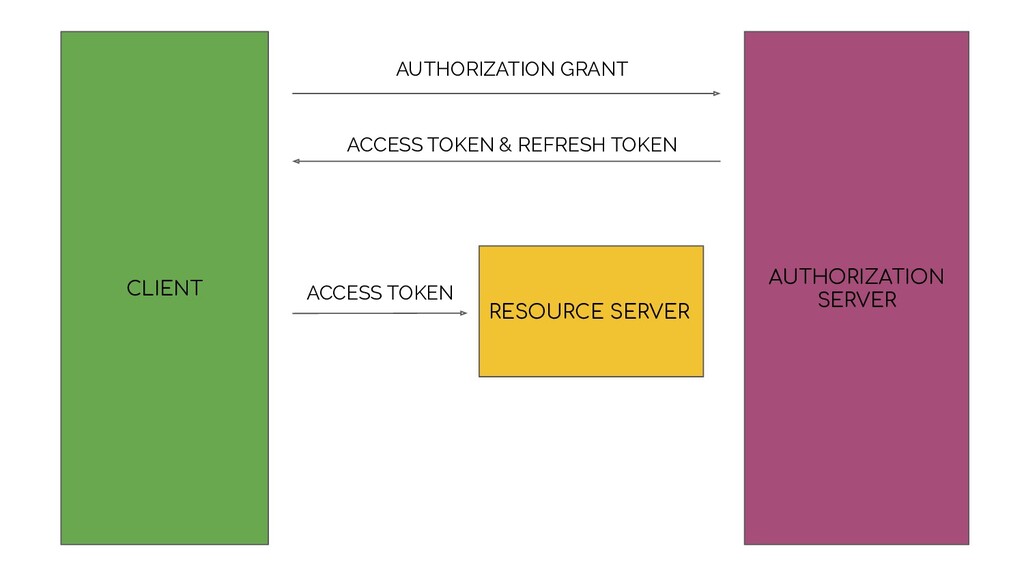
CLIENT AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION GRANT ACCESS TOKEN &
REFRESH TOKEN ACCESS TOKEN -
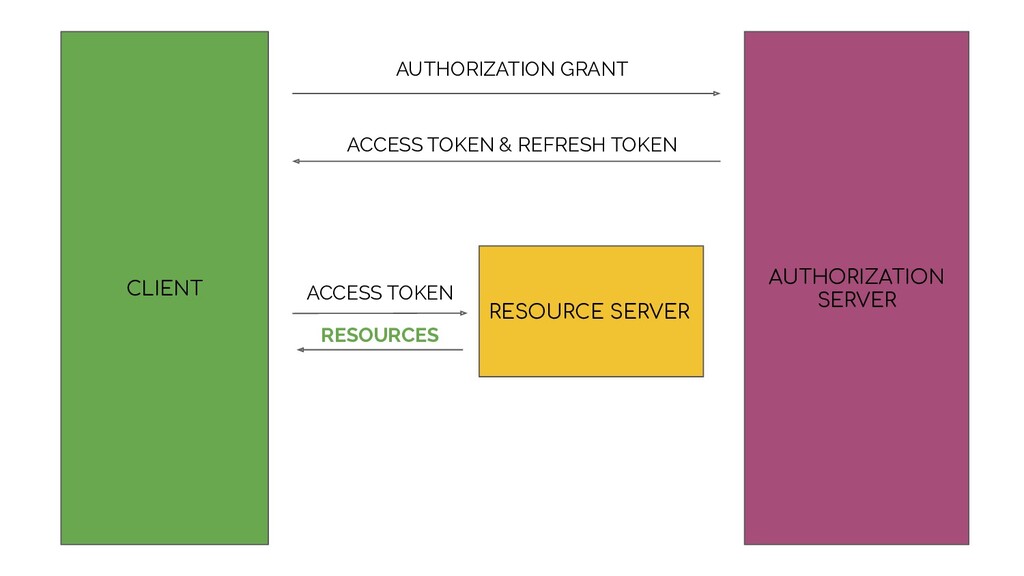
CLIENT AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION GRANT ACCESS TOKEN &
REFRESH TOKEN ACCESS TOKEN RESOURCES -
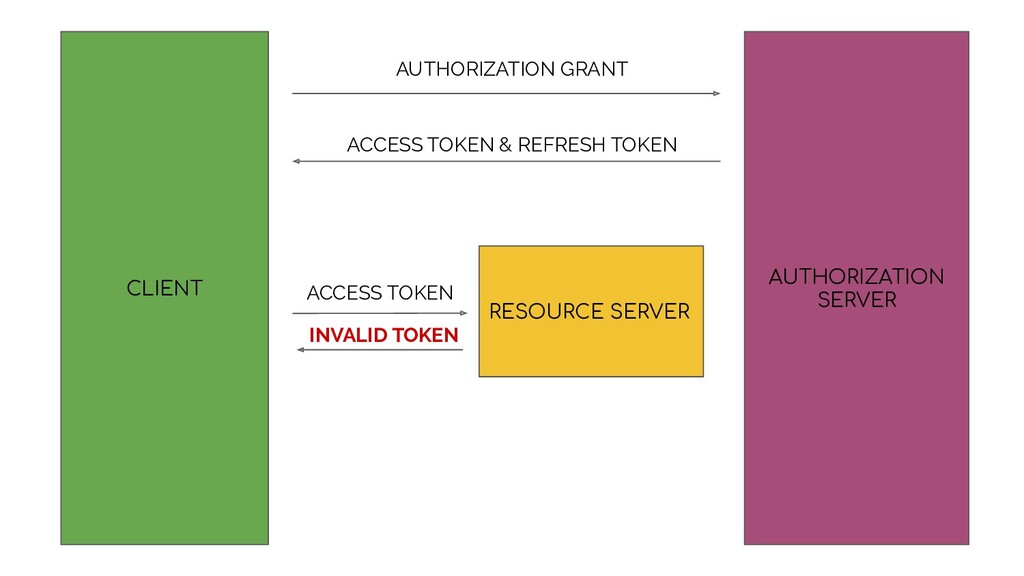
CLIENT AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION GRANT ACCESS TOKEN &
REFRESH TOKEN ACCESS TOKEN INVALID TOKEN -
CLIENT AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION GRANT ACCESS TOKEN &
REFRESH TOKEN ACCESS TOKEN INVALID TOKEN REFRESH TOKEN -
CLIENT AUTHORIZATION SERVER RESOURCE SERVER AUTHORIZATION GRANT ACCESS TOKEN &
REFRESH TOKEN ACCESS TOKEN INVALID TOKEN REFRESH TOKEN ACCESS TOKEN & (OPTIONAL) REFRESH TOKEN -
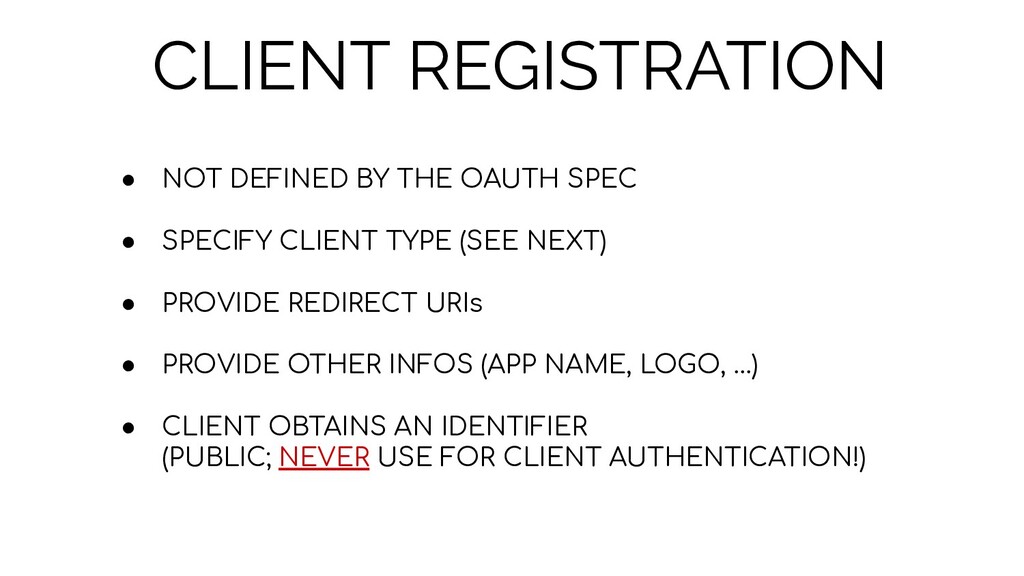
CLIENT REGISTRATION • NOT DEFINED BY THE OAUTH SPEC •
SPECIFY CLIENT TYPE (SEE NEXT) • PROVIDE REDIRECT URIs • PROVIDE OTHER INFOS (APP NAME, LOGO, …) • CLIENT OBTAINS AN IDENTIFIER (PUBLIC; NEVER USE FOR CLIENT AUTHENTICATION!) -
CLIENT TYPES • BASED ON ABILITY TO MAINTAIN THE CONFIDENTIALITY
OF THEIR CREDENTIALS • CONFIDENTIAL (Backend web app) • PUBLIC (SPA, native app, …) -
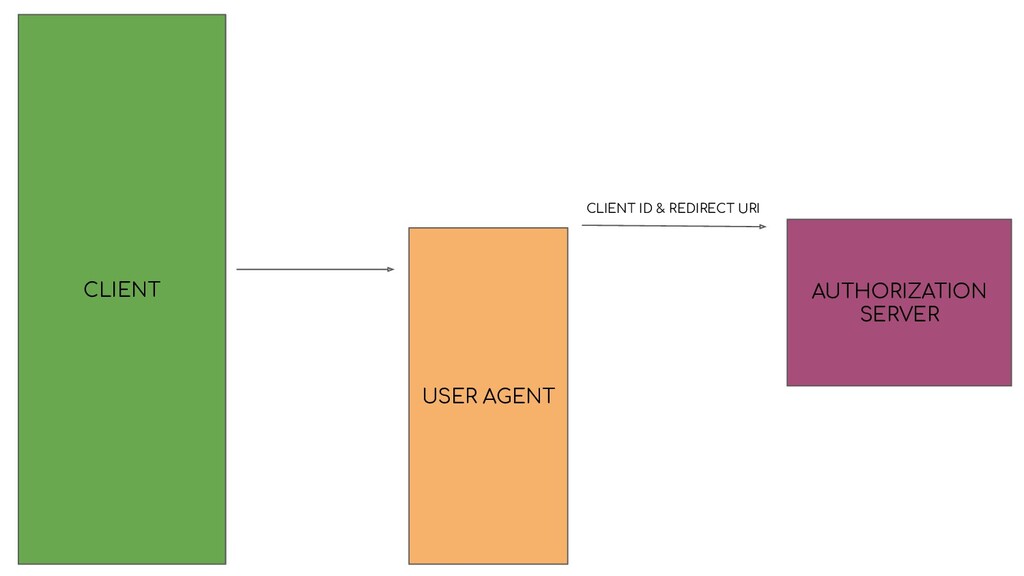
OBTAINING AUTHORIZATION • AUTHORIZATION CODE GRANT • IMPLICIT GRANT •
RESOURCE OWNER PASSWORD CREDENTIAL • CLIENT CREDENTIALS -
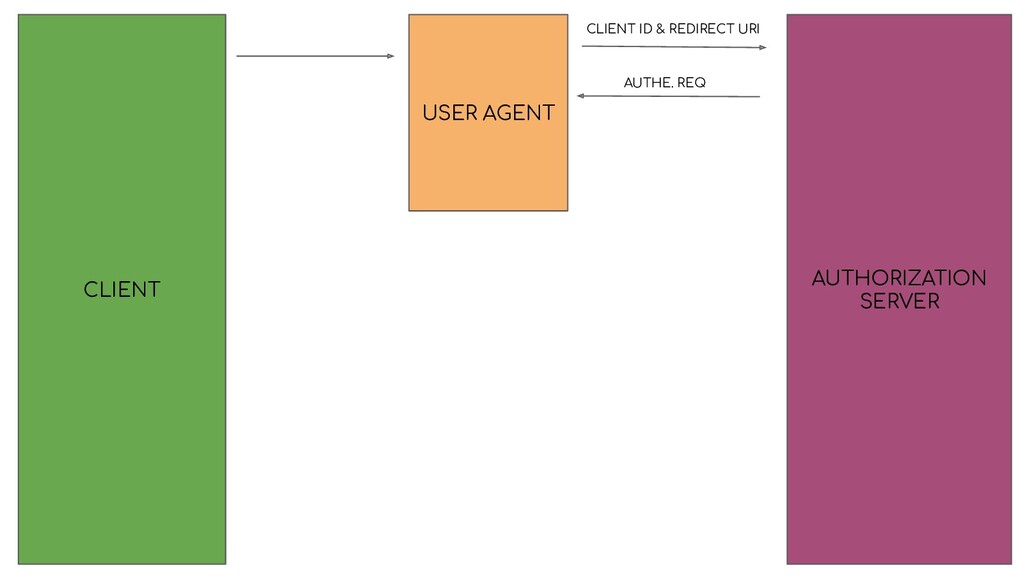
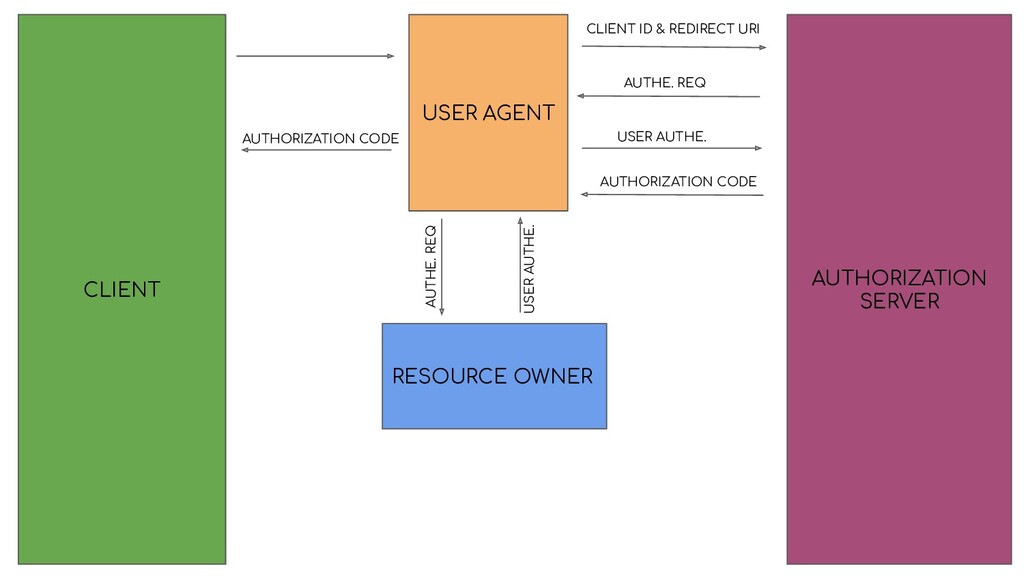
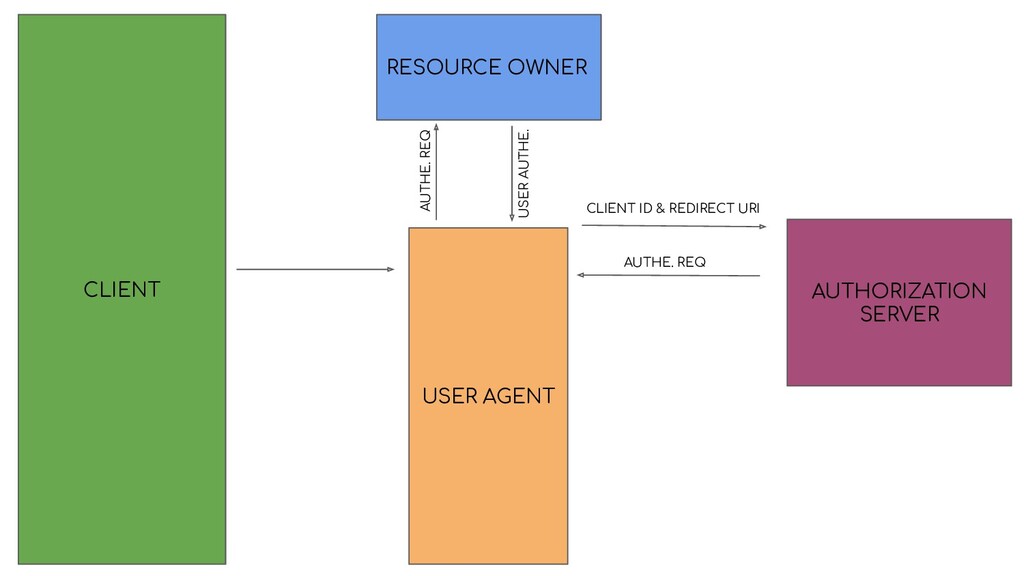
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ -
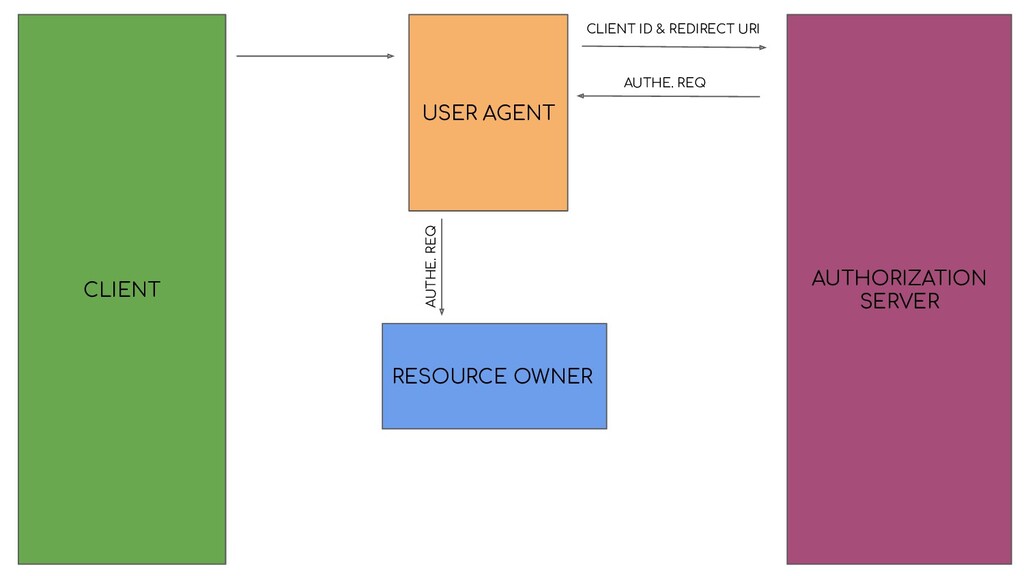
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. -
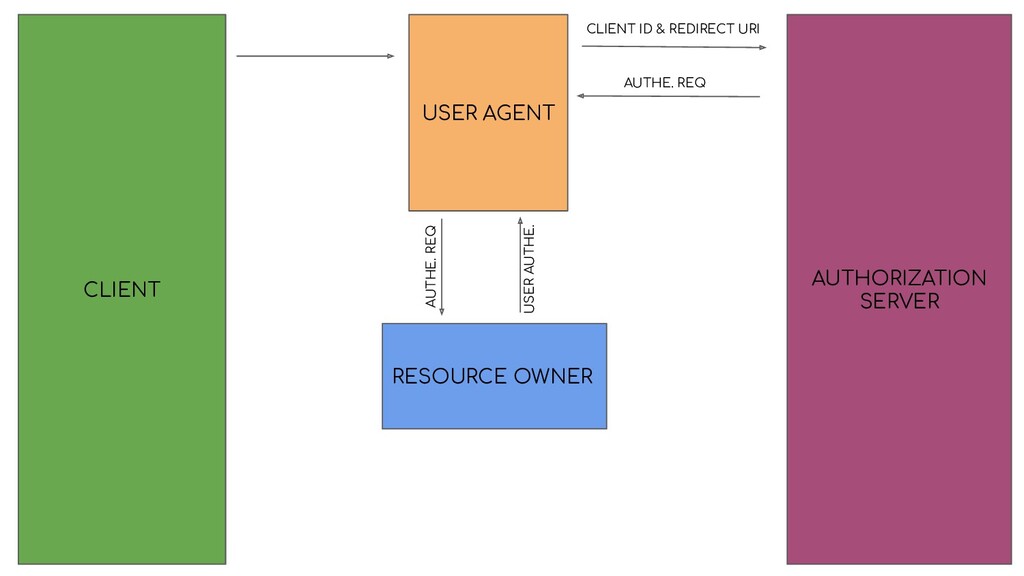
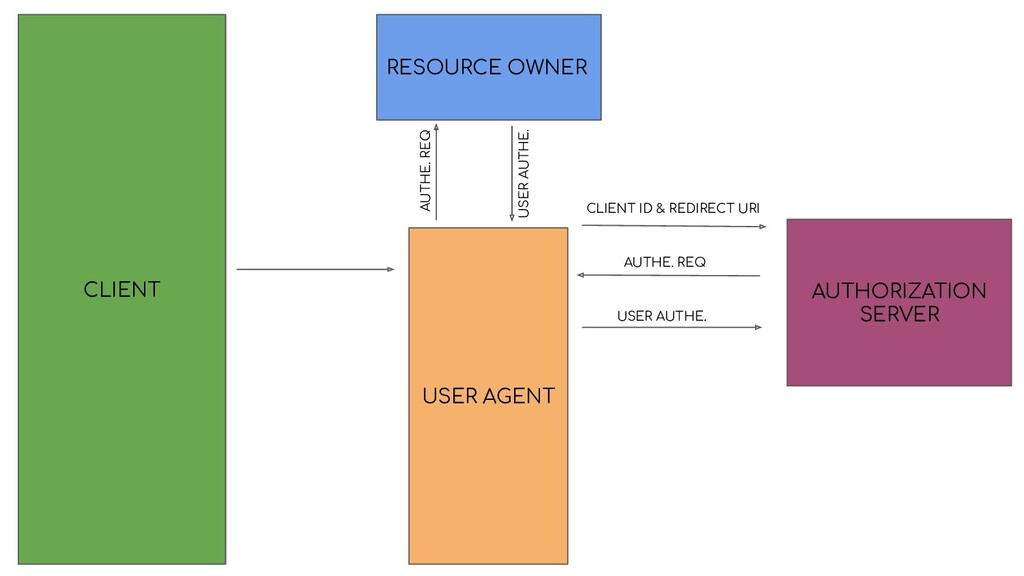
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. -
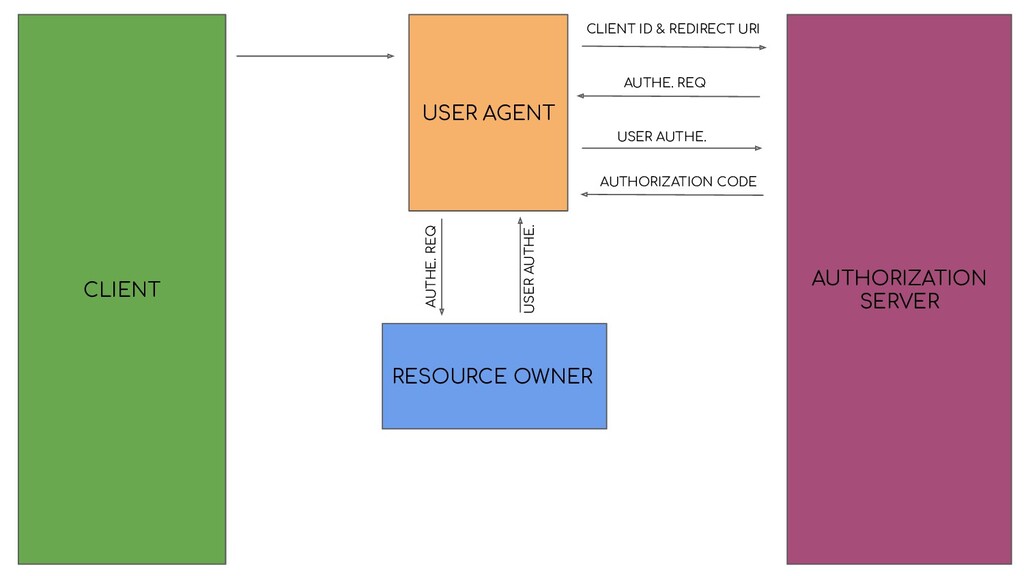
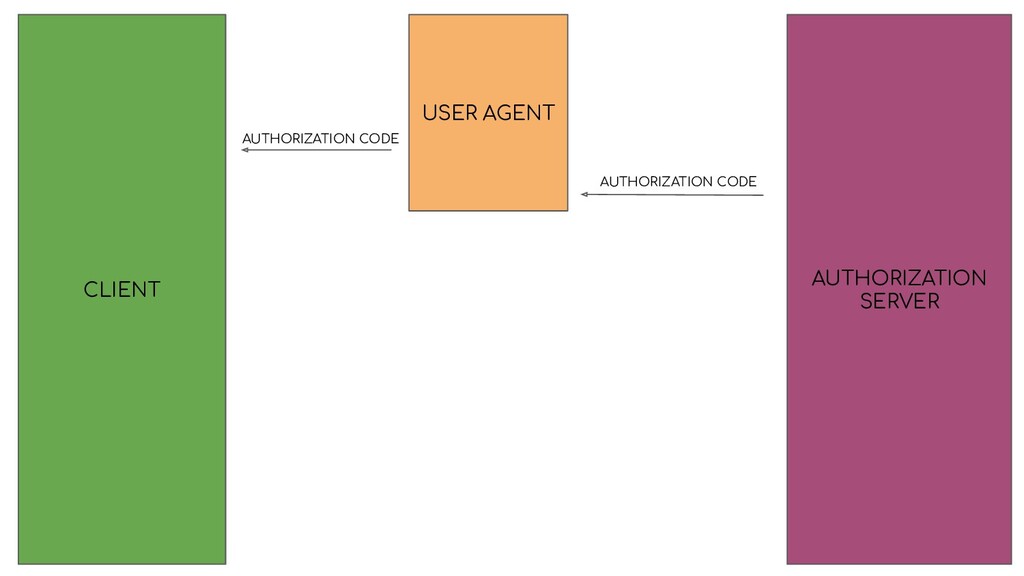
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
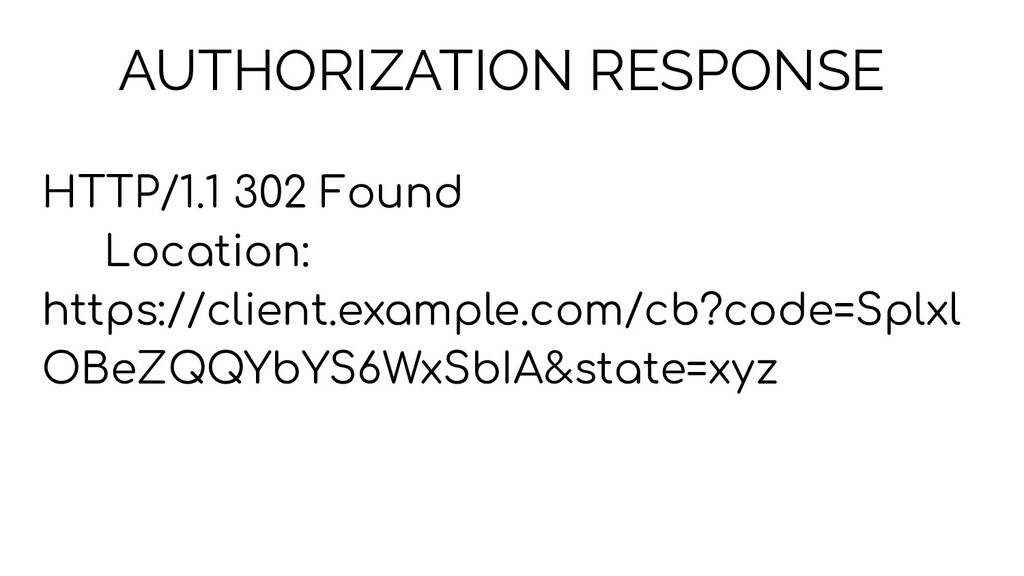
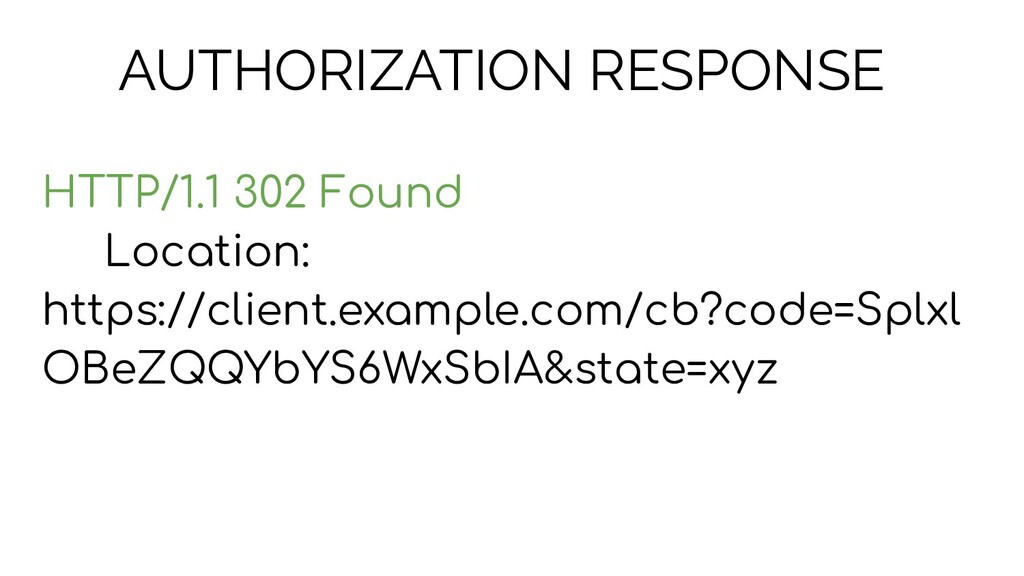
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. AUTHORIZATION CODE -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. AUTHORIZATION CODE AUTHORIZATION CODE -
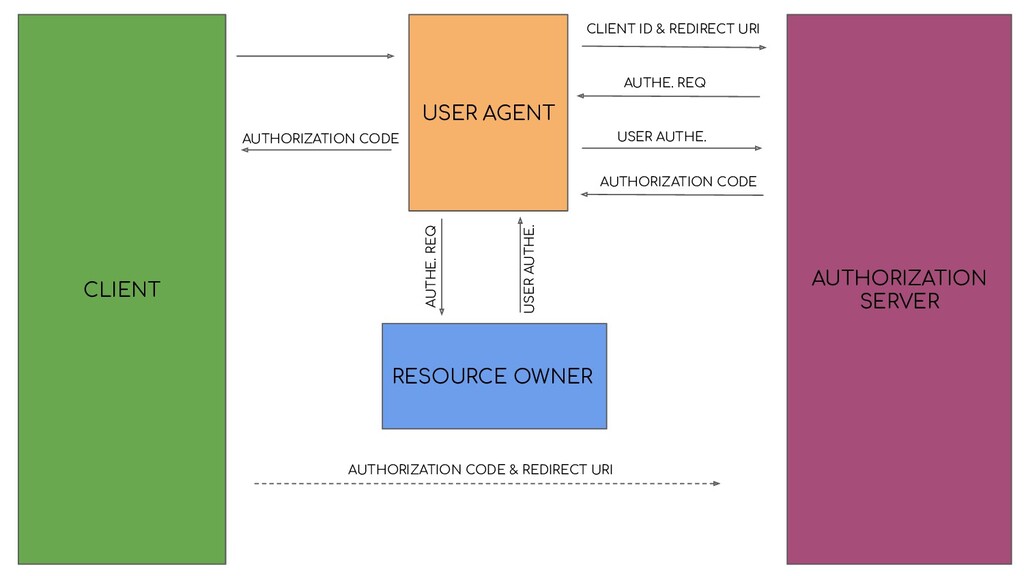
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
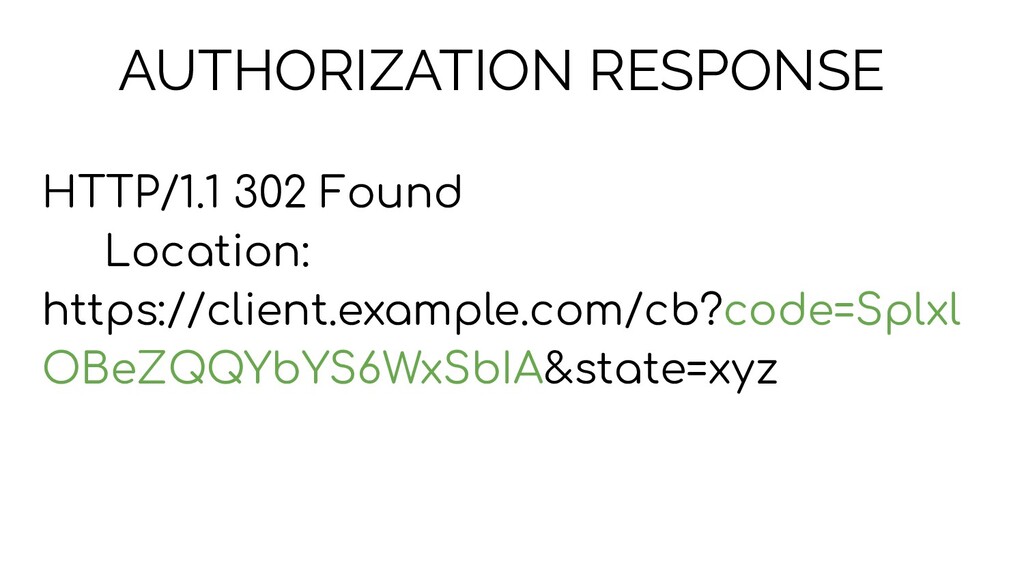
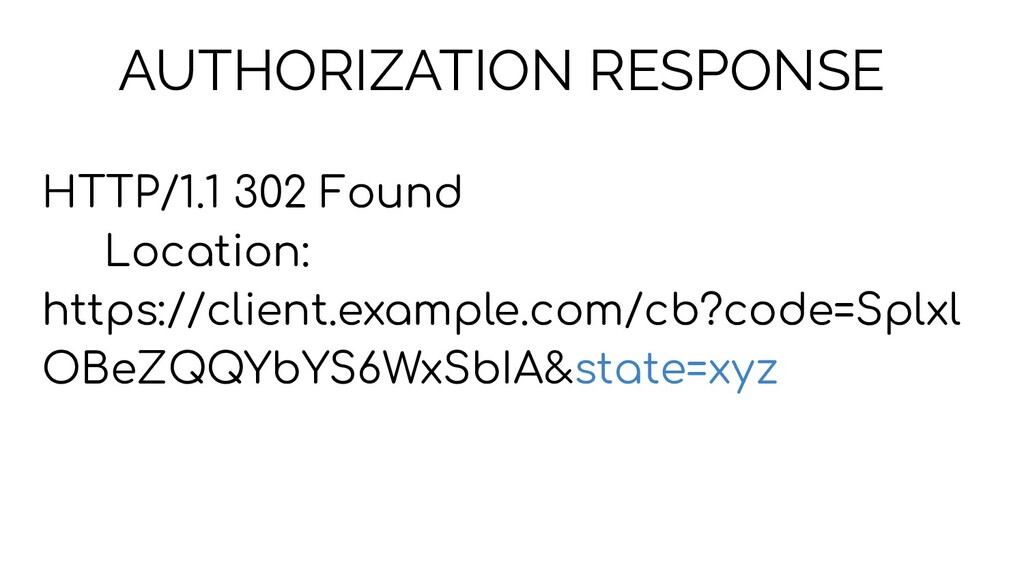
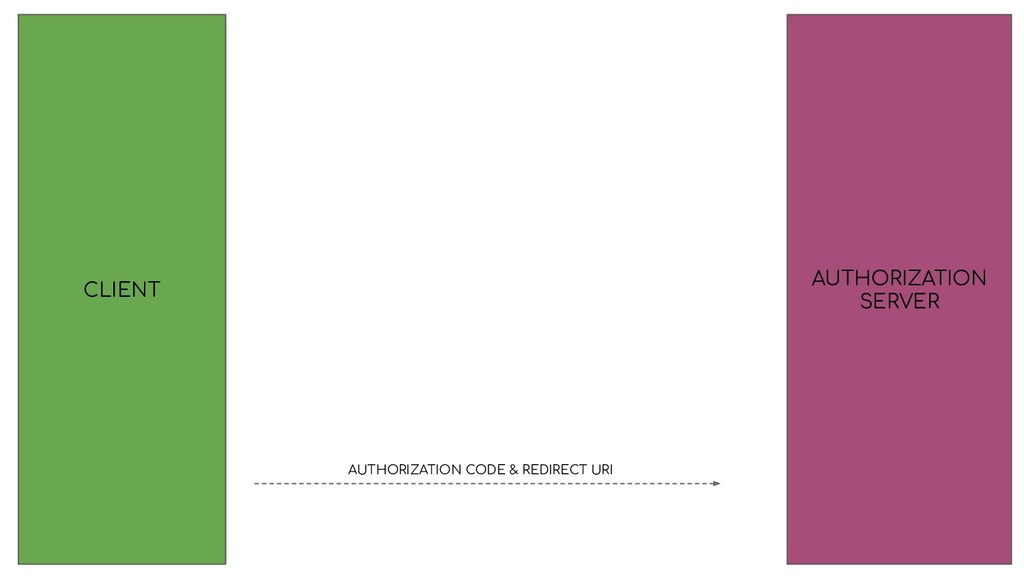
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. AUTHORIZATION CODE AUTHORIZATION CODE AUTHORIZATION CODE & REDIRECT URI -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
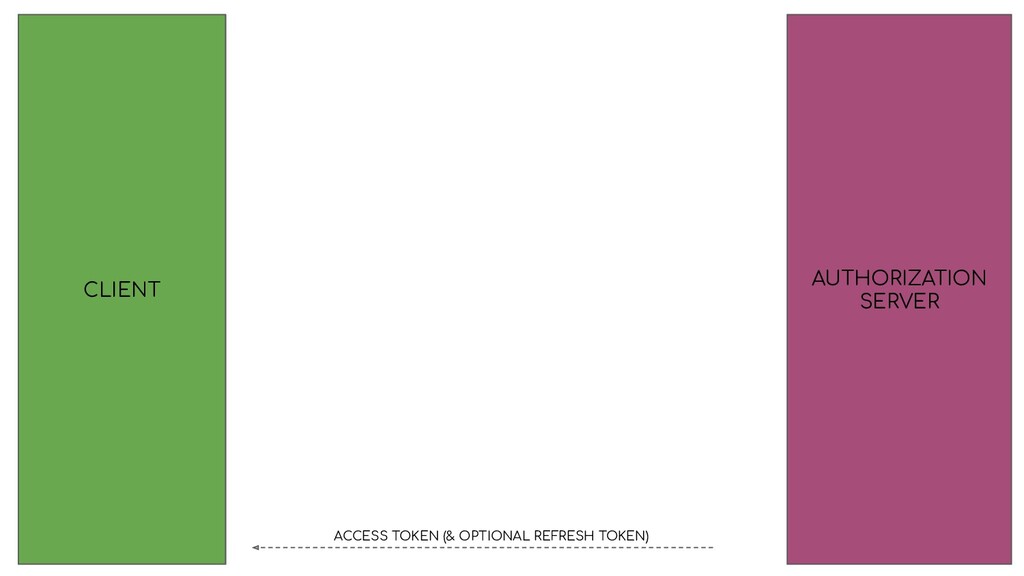
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. AUTHORIZATION CODE AUTHORIZATION CODE AUTHORIZATION CODE & REDIRECT URI ACCESS TOKEN (& OPTIONAL REFRESH TOKEN) -
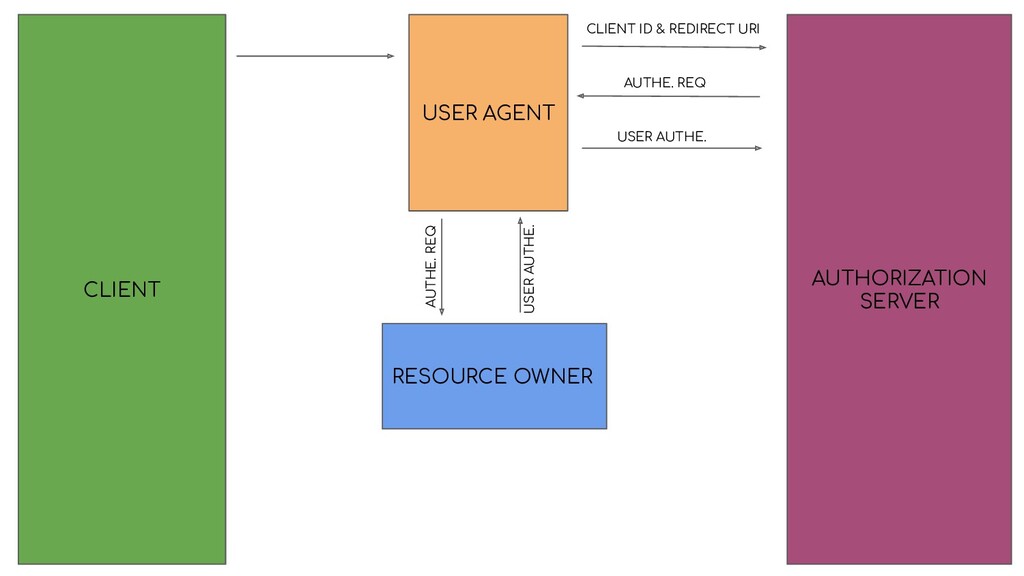
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. -
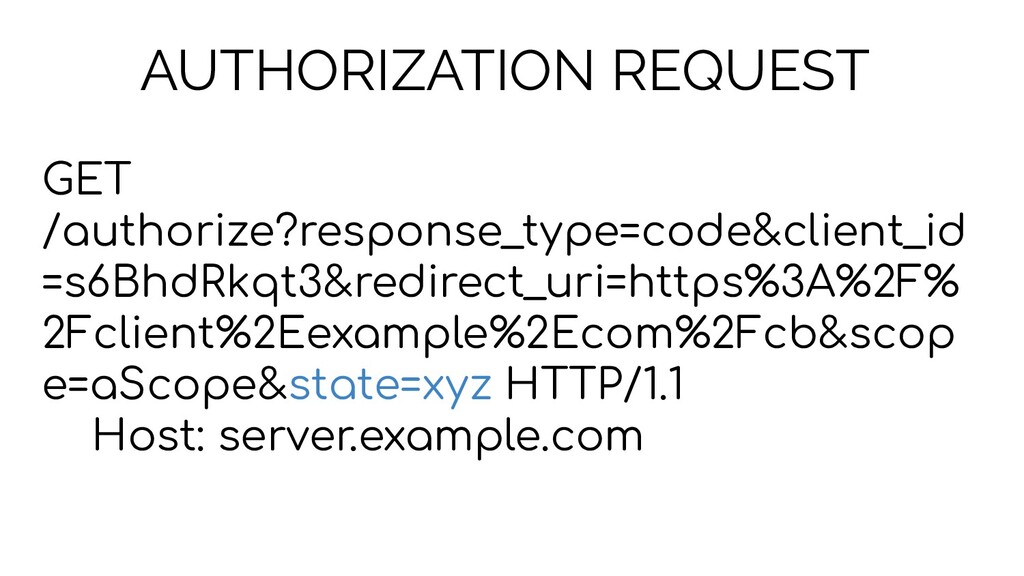
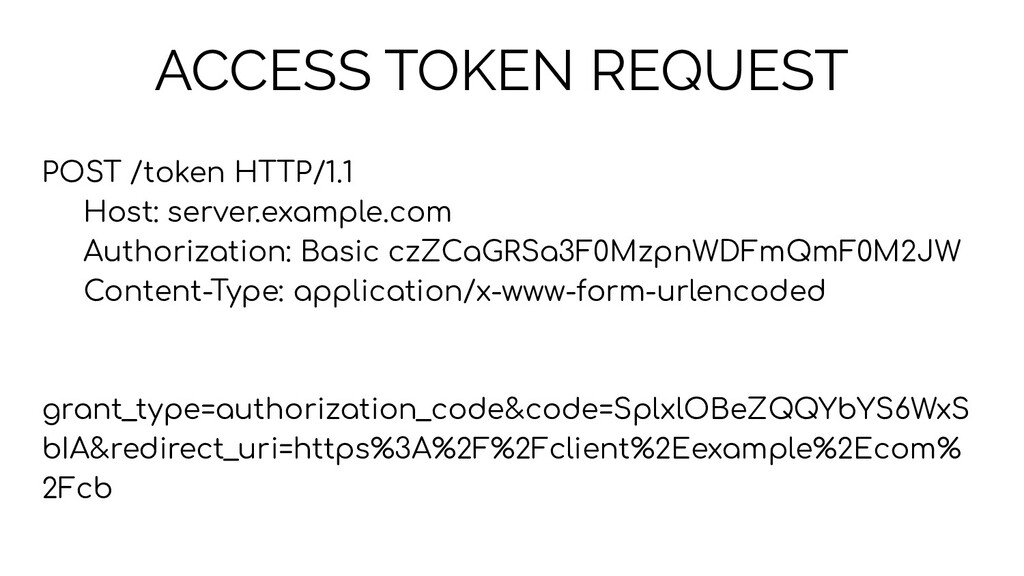
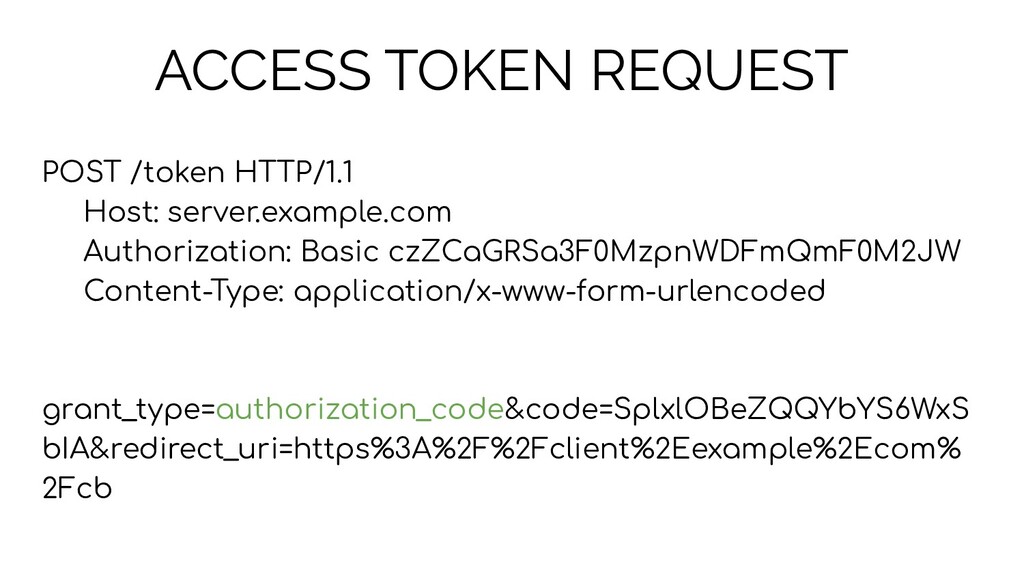
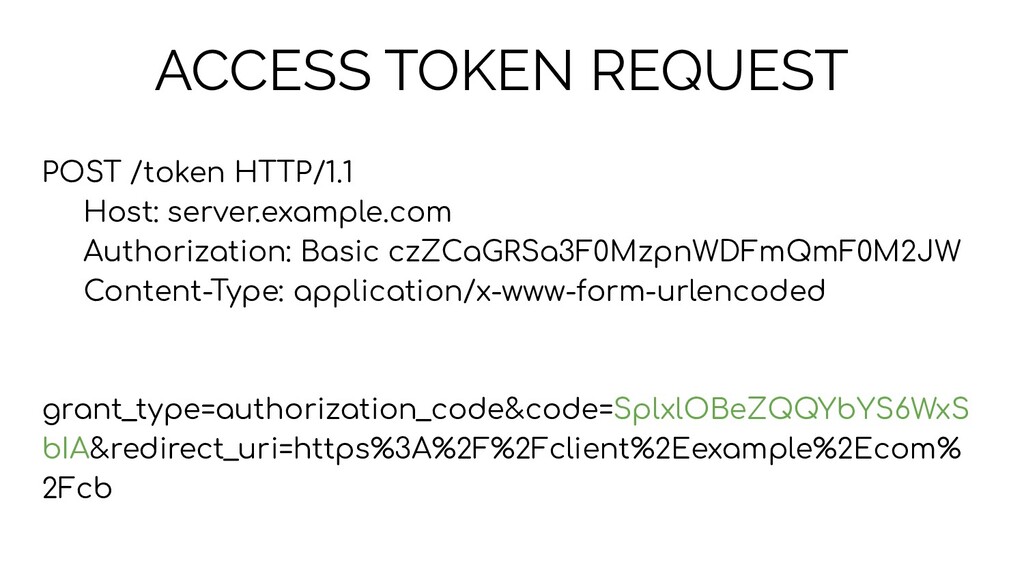
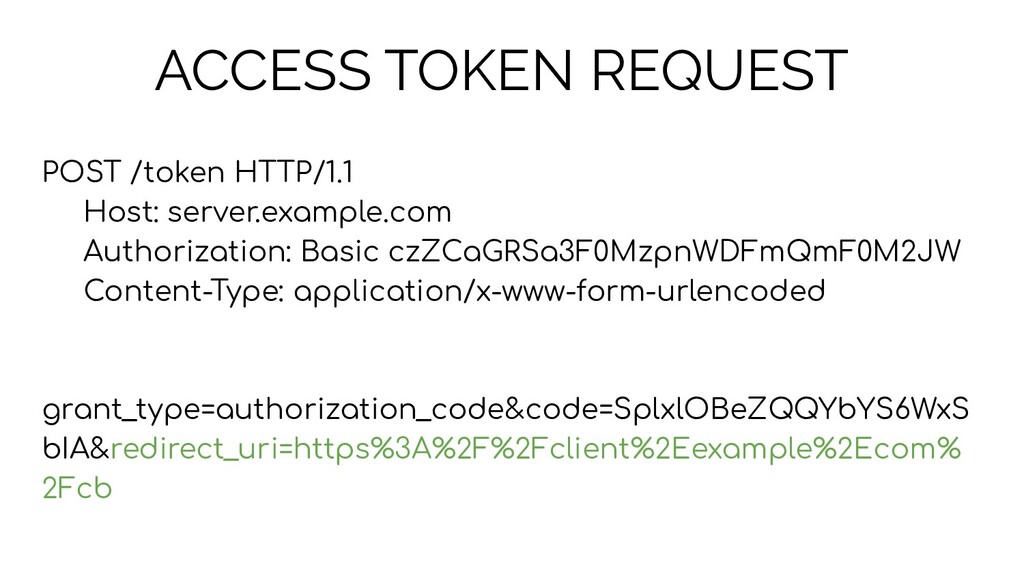
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb -
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb -
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb -
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb -
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb -
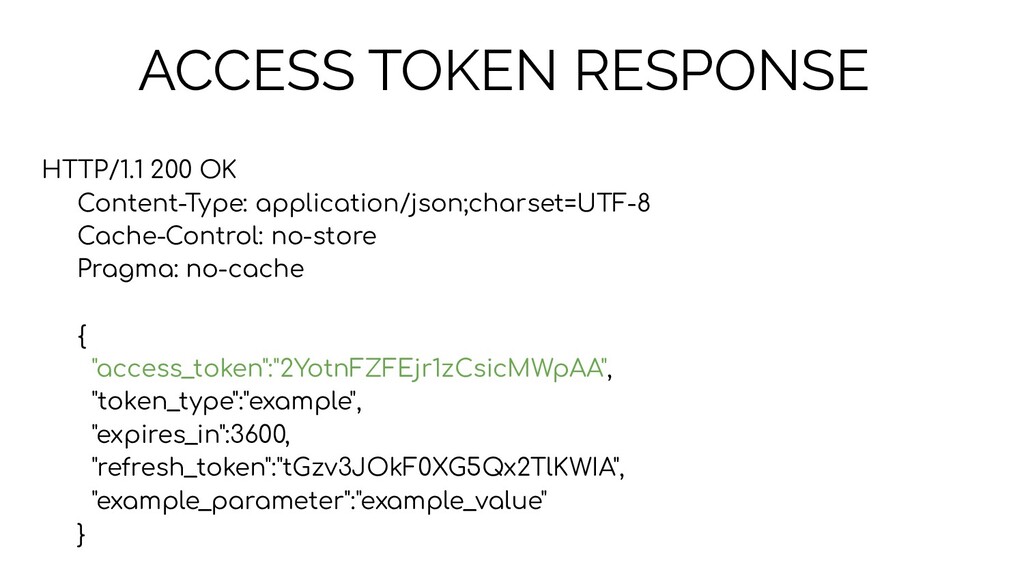
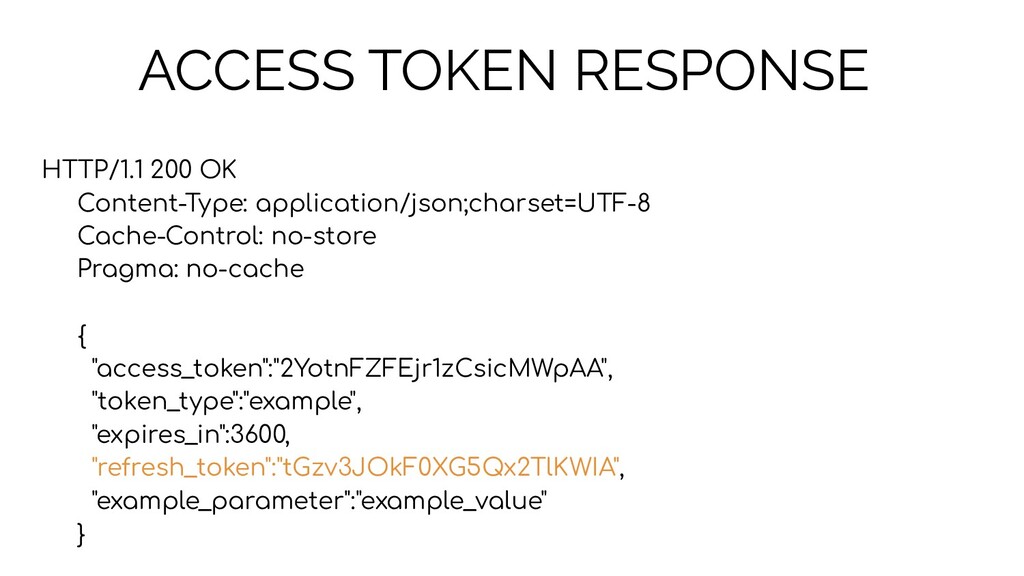
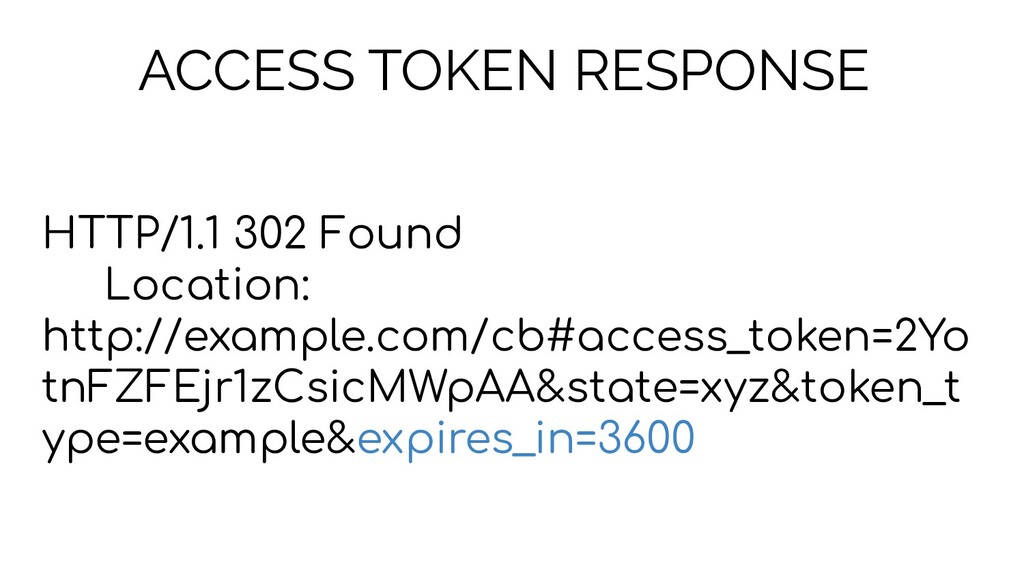
ACCESS TOKEN RESPONSE HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 Cache-Control: no-store
Pragma: no-cache { "access_token":"2YotnFZFEjr1zCsicMWpAA", "token_type":"example", "expires_in":3600, "refresh_token":"tGzv3JOkF0XG5Qx2TlKWIA", "example_parameter":"example_value" } -
ACCESS TOKEN RESPONSE HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 Cache-Control: no-store
Pragma: no-cache { "access_token":"2YotnFZFEjr1zCsicMWpAA", "token_type":"example", "expires_in":3600, "refresh_token":"tGzv3JOkF0XG5Qx2TlKWIA", "example_parameter":"example_value" } -
ACCESS TOKEN RESPONSE HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 Cache-Control: no-store
Pragma: no-cache { "access_token":"2YotnFZFEjr1zCsicMWpAA", "token_type":"example", "expires_in":3600, "refresh_token":"tGzv3JOkF0XG5Qx2TlKWIA", "example_parameter":"example_value" } -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. -
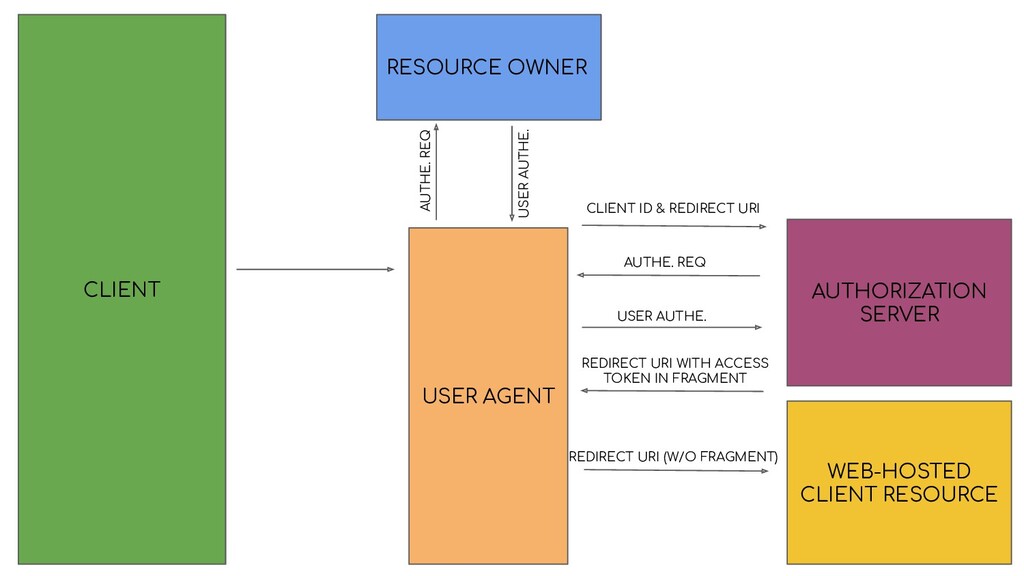
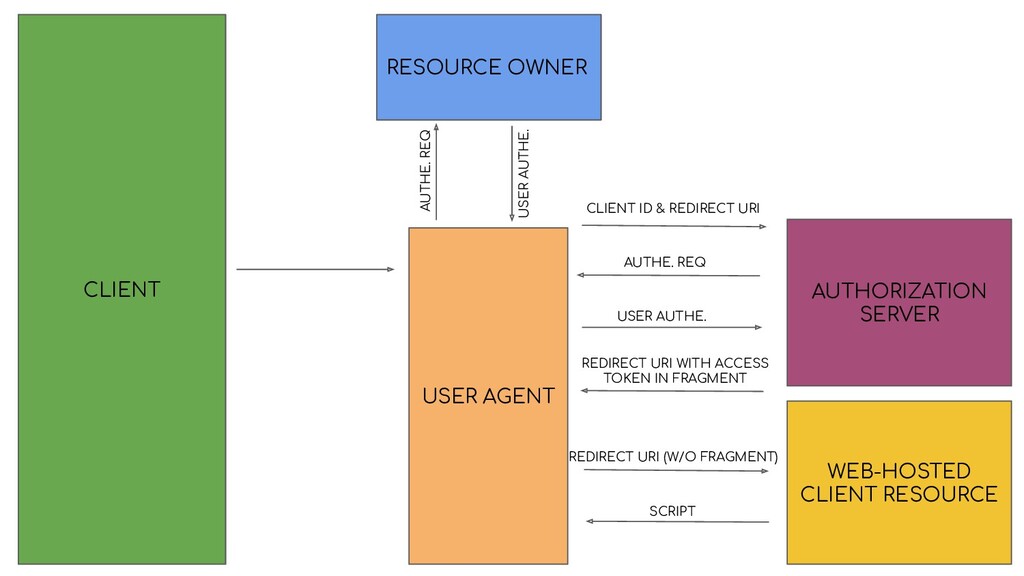
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. REDIRECT URI WITH ACCESS TOKEN IN FRAGMENT -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. REDIRECT URI WITH ACCESS TOKEN IN FRAGMENT WEB-HOSTED CLIENT RESOURCE REDIRECT URI (W/O FRAGMENT) -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. REDIRECT URI WITH ACCESS TOKEN IN FRAGMENT WEB-HOSTED CLIENT RESOURCE REDIRECT URI (W/O FRAGMENT) SCRIPT -
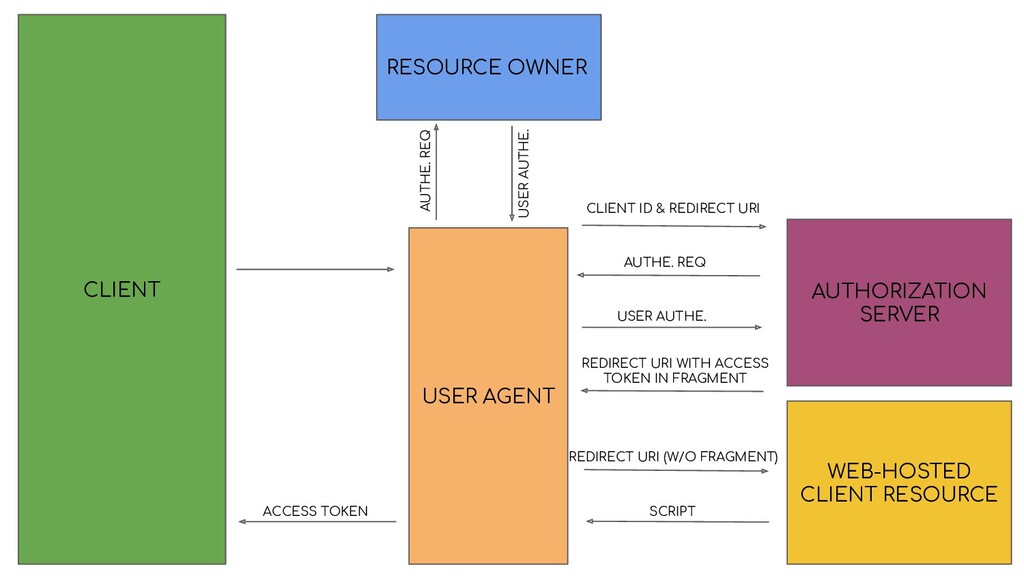
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. REDIRECT URI WITH ACCESS TOKEN IN FRAGMENT WEB-HOSTED CLIENT RESOURCE REDIRECT URI (W/O FRAGMENT) SCRIPT ACCESS TOKEN -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. -
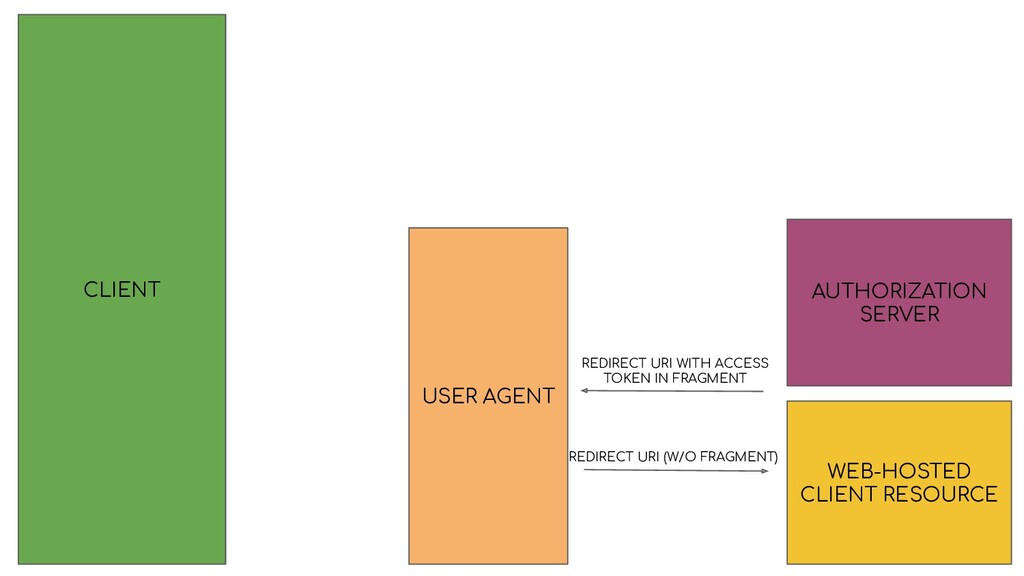
CLIENT AUTHORIZATION SERVER USER AGENT REDIRECT URI WITH ACCESS TOKEN
IN FRAGMENT WEB-HOSTED CLIENT RESOURCE REDIRECT URI (W/O FRAGMENT) -
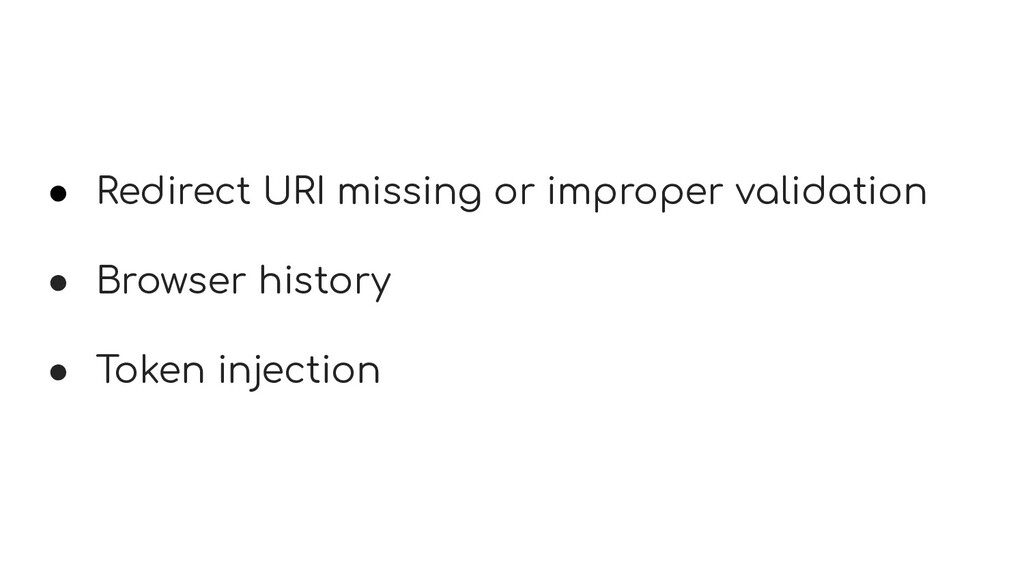
• Redirect URI missing or improper validation • Browser history
• Token injection -
HISTORICAL REASONS FOR IMPLICIT GRANT • Browsers can manipulate only
url fragment without causing a page reload (not true anymore since HistoryAPI) • CORS (Authorization Code Flow requires a POST at some point) -
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb -
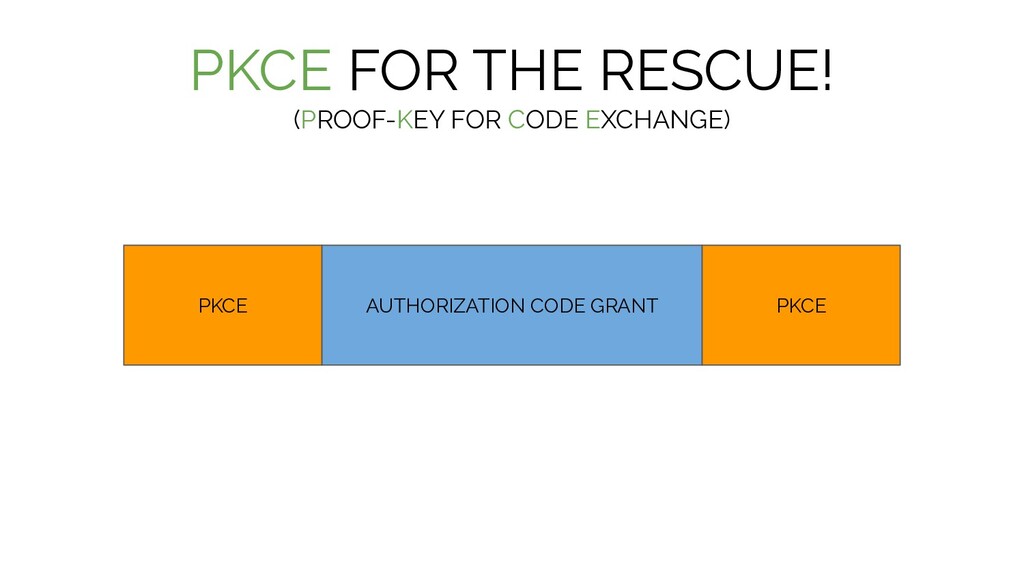
PKCE FOR THE RESCUE! (PROOF-KEY FOR CODE EXCHANGE) PKCE PKCE
AUTHORIZATION CODE GRANT -
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID &
REDIRECT URI AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. AUTHORIZATION CODE AUTHORIZATION CODE AUTHORIZATION CODE & REDIRECT URI ACCESS TOKEN (& OPTIONAL REFRESH TOKEN) -
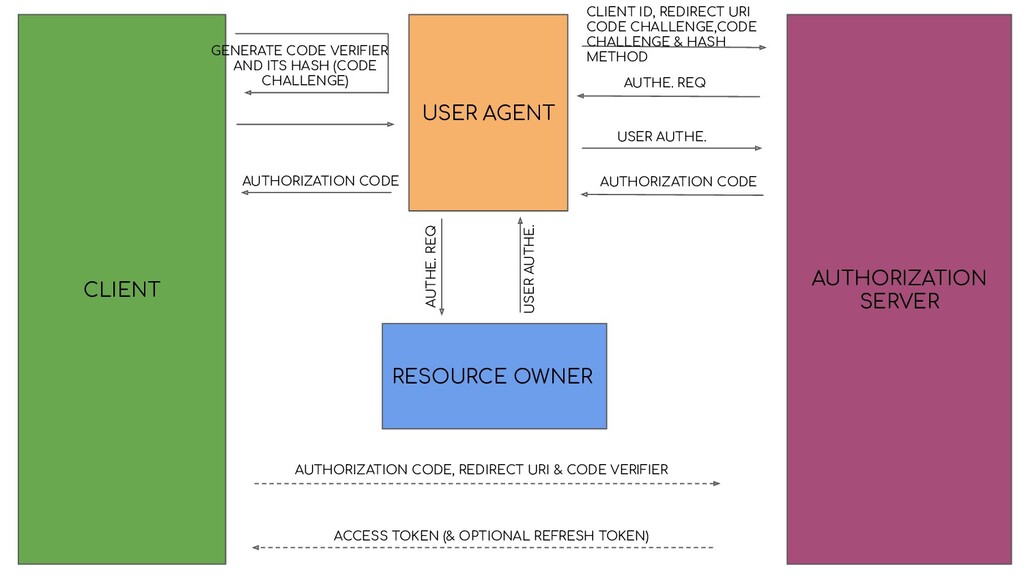
CLIENT RESOURCE OWNER AUTHORIZATION SERVER USER AGENT CLIENT ID, REDIRECT
URI CODE CHALLENGE,CODE CHALLENGE & HASH METHOD AUTHE. REQ AUTHE. REQ USER AUTHE. USER AUTHE. AUTHORIZATION CODE AUTHORIZATION CODE AUTHORIZATION CODE, REDIRECT URI & CODE VERIFIER ACCESS TOKEN (& OPTIONAL REFRESH TOKEN) GENERATE CODE VERIFIER AND ITS HASH (CODE CHALLENGE) -
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb -
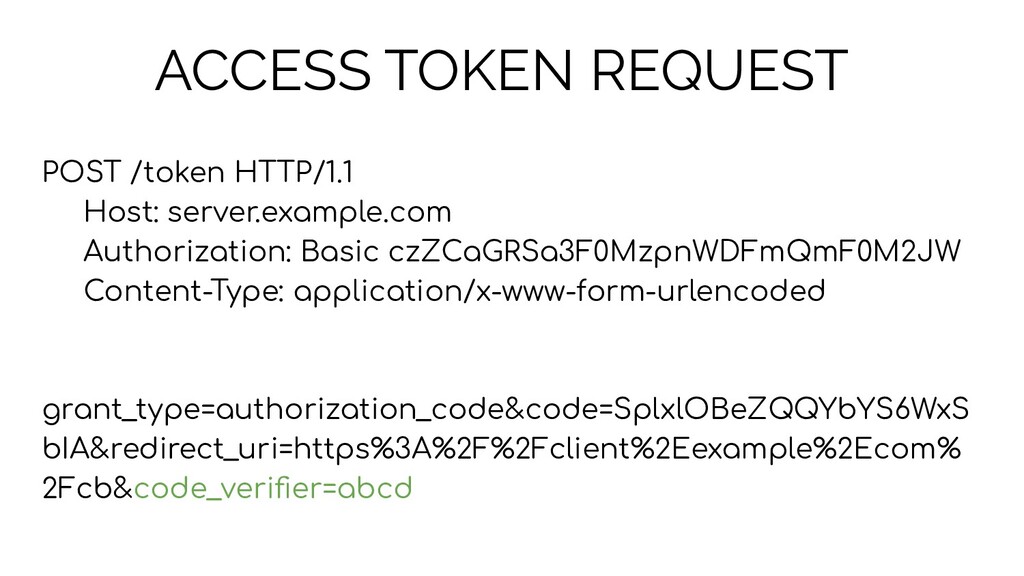
ACCESS TOKEN REQUEST POST /token HTTP/1.1 Host: server.example.com Authorization: Basic
czZCaGRSa3F0MzpnWDFmQmF0M2JW Content-Type: application/x-www-form-urlencoded grant_type=authorization_code&code=SplxlOBeZQQYbYS6WxS bIA&redirect_uri=https%3A%2F%2Fclient%2Eexample%2Ecom% 2Fcb&code_verifier=abcd -
OBTAINING AUTHORIZATION • AUTHORIZATION CODE GRANT • IMPLICIT GRANT •
RESOURCE OWNER PASSWORD CREDENTIAL • CLIENT CREDENTIALS -
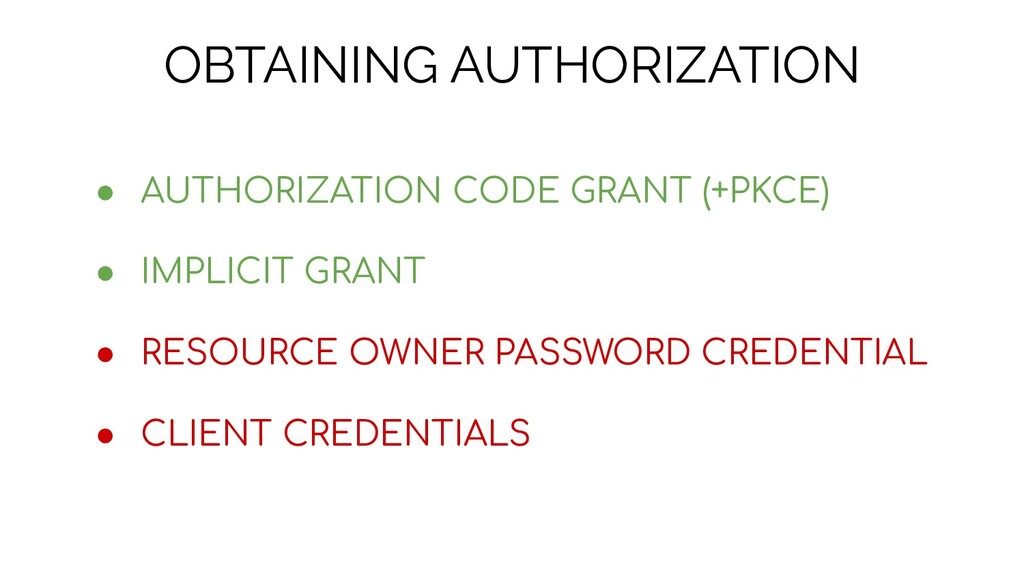
OBTAINING AUTHORIZATION • AUTHORIZATION CODE GRANT (+PKCE) • IMPLICIT GRANT
• RESOURCE OWNER PASSWORD CREDENTIAL • CLIENT CREDENTIALS -
WORTH OF A LOOK... • AMAZON COGNITO • OKTA •
AUTH0 • ORY HYDRA -
CREDITS - https://stocksnap.io/photo/SZE0NDYC0F (George Becker) - https://stocksnap.io/photo/KV6IATK4SM (Emily Morter) -
https://www.iconfinder.com/icons/172626/male_user_icon