Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Extensiegebruik op Byte's Magento platformen

Avatar for Byte Byte
August 27, 2015

Extensiegebruik op Byte's Magento platformen

Een korte analyse over de meest gebruikte extensions in Magento webshops op Byte's hosting platformen en security.

Byte
https://www.byte.nl/

Speakers:
Nick Groenen
https://github.com/zoni

Rick van de Loo
https://github.com/vdloo

Avatar for Byte

Byte

August 27, 2015

Other Decks in Programming

Transcript

  1. Programma - 27 augustus 15:00 Welkom 15:10 Presentatie extensies 15:30

    Brainstorm 16:00 Extensies bespreken 16:30 PAUZE 16:45 Extensies bespreken 18:00 BORREL
  2. Extensiegebruik Bij Byte draaien heel veel shops, dus daar kunnen

    we allemaal mooie dingetjes over uitzoeken!
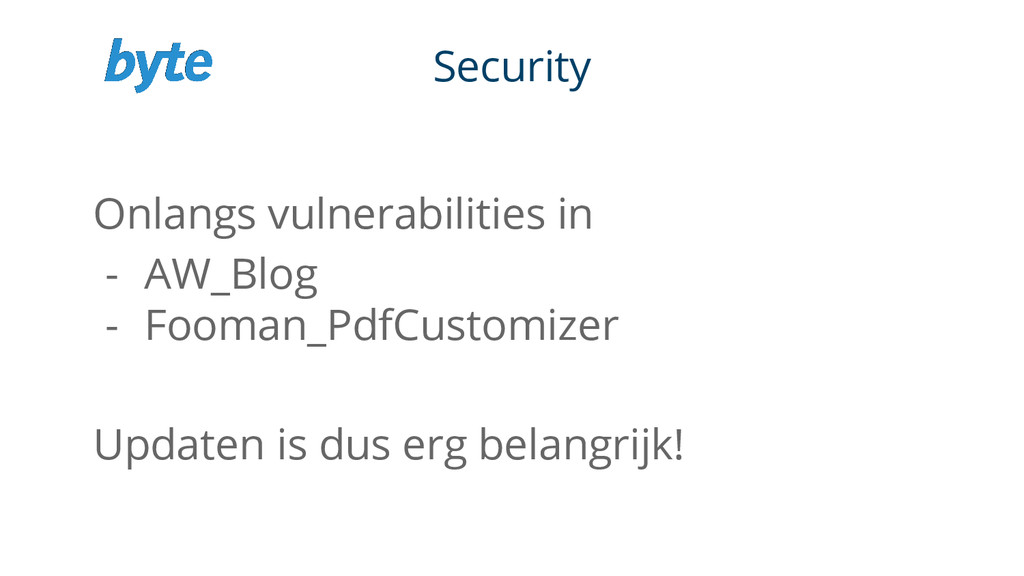
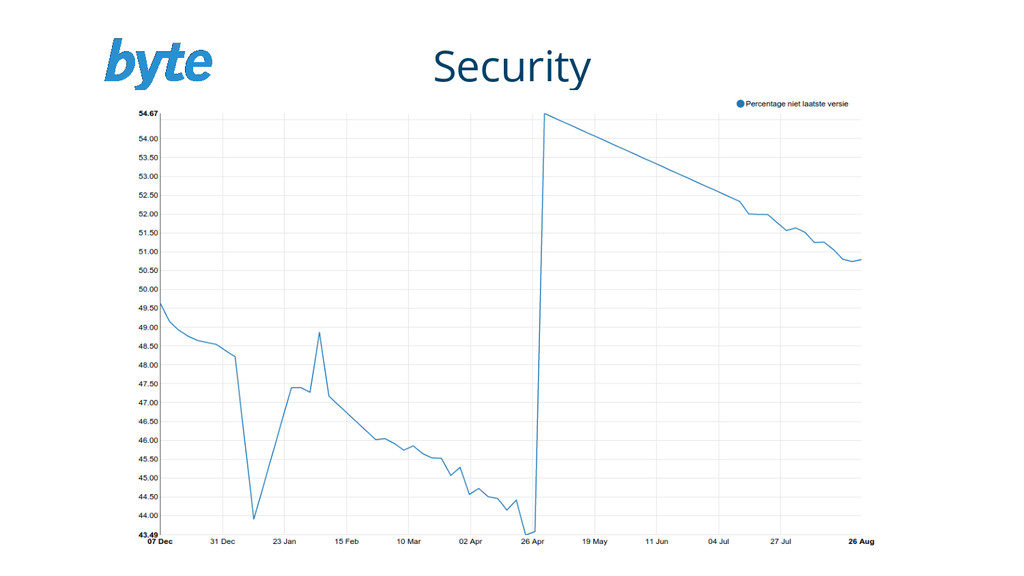
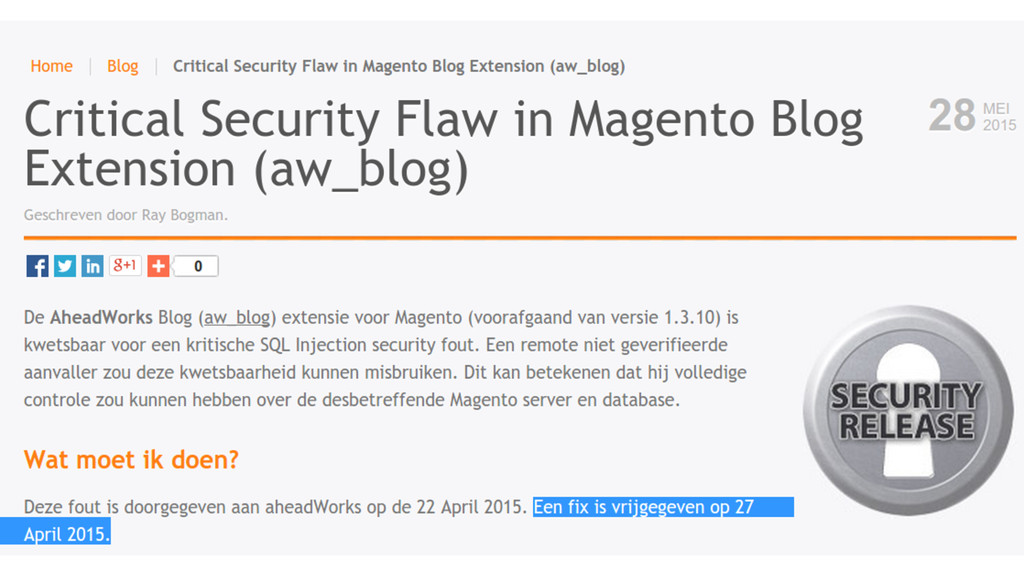
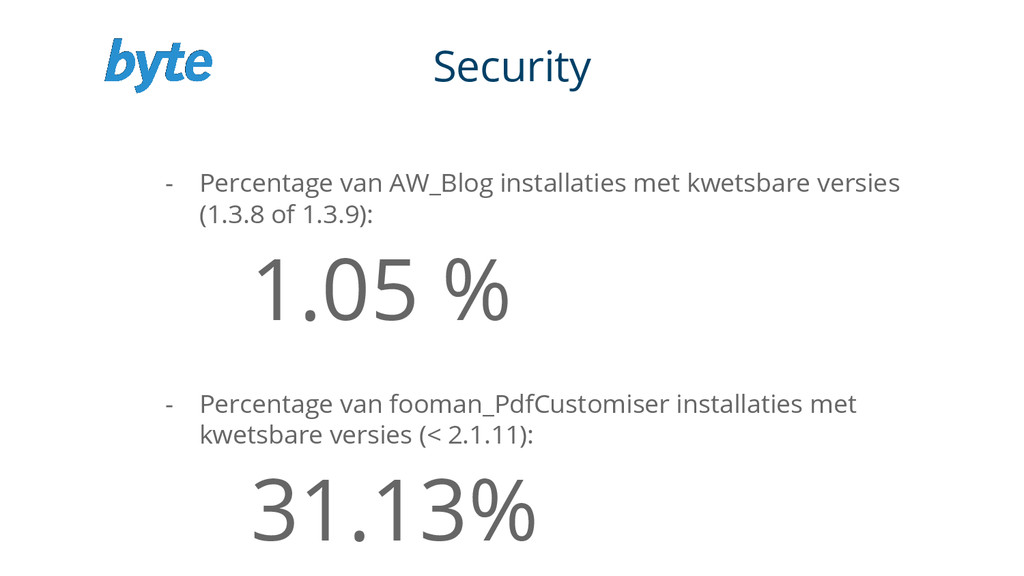
  3. Security - Percentage van AW_Blog installaties met kwetsbare versies (1.3.8

    of 1.3.9): 1.05 % - Percentage van fooman_PdfCustomiser installaties met kwetsbare versies (< 2.1.11): 31.13%
  4. Security • Versturen van spam • Hosten van phishing pagina's

    • Verspreiden van malware • Aanvallen uitvoeren op andere sites • Lekken van gevoelige informatie (Klant informatie, e-mail adressen, creditcard gegevens, etc)
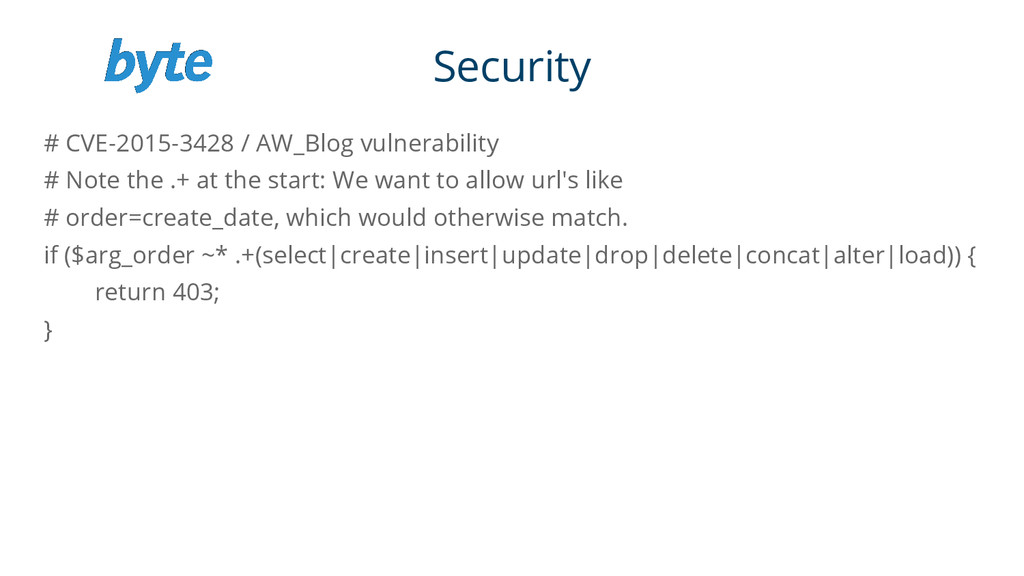
  5. Security # CVE-2015-3428 / AW_Blog vulnerability # Note the .+

    at the start: We want to allow url's like # order=create_date, which would otherwise match. if ($arg_order ~* .+(select|create|insert|update|drop|delete|concat|alter|load)) { return 403; }
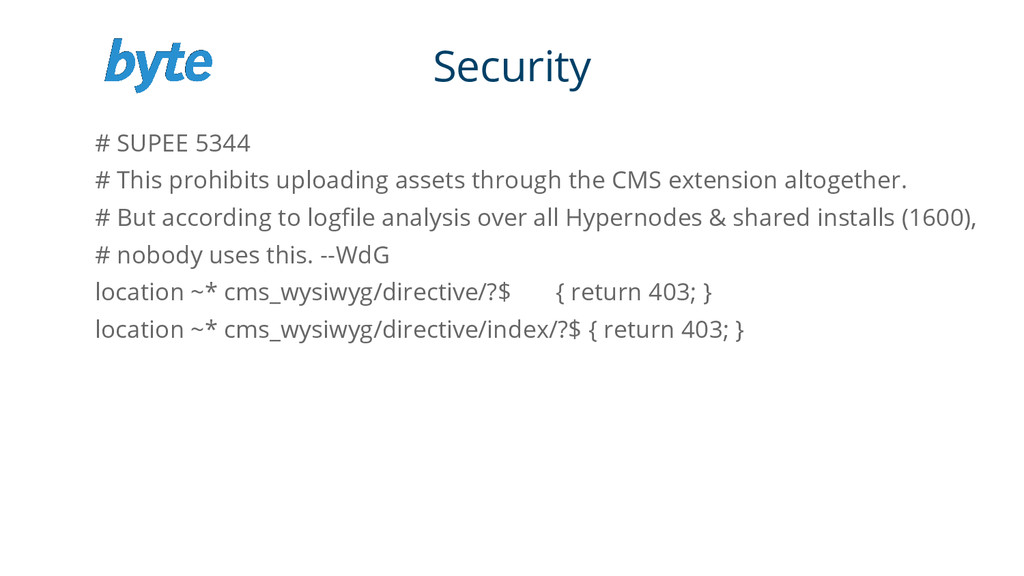
  6. Security # SUPEE 5344 # This prohibits uploading assets through

    the CMS extension altogether. # But according to logfile analysis over all Hypernodes & shared installs (1600), # nobody uses this. --WdG location ~* cms_wysiwyg/directive/?$ { return 403; } location ~* cms_wysiwyg/directive/index/?$ { return 403; }