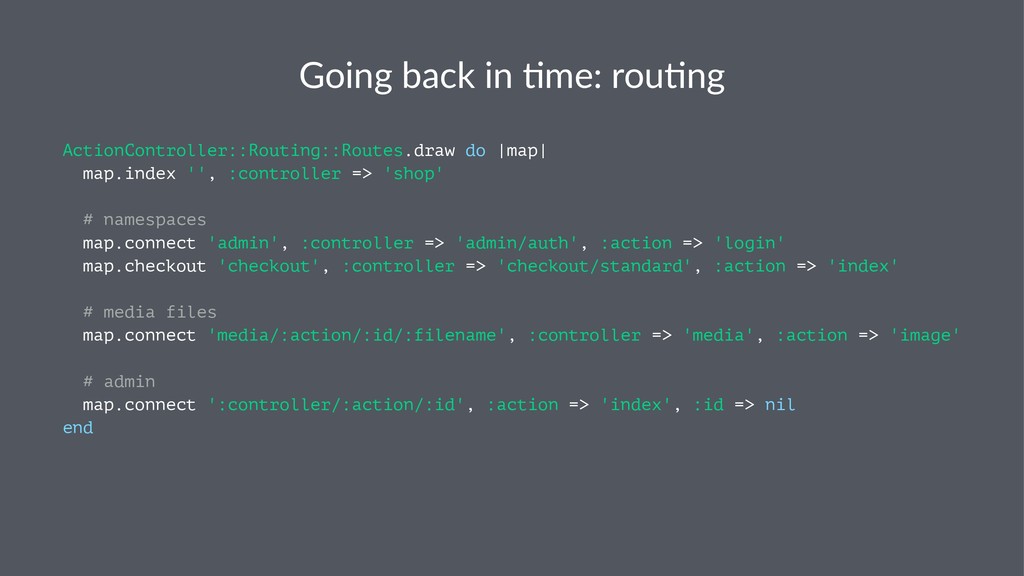
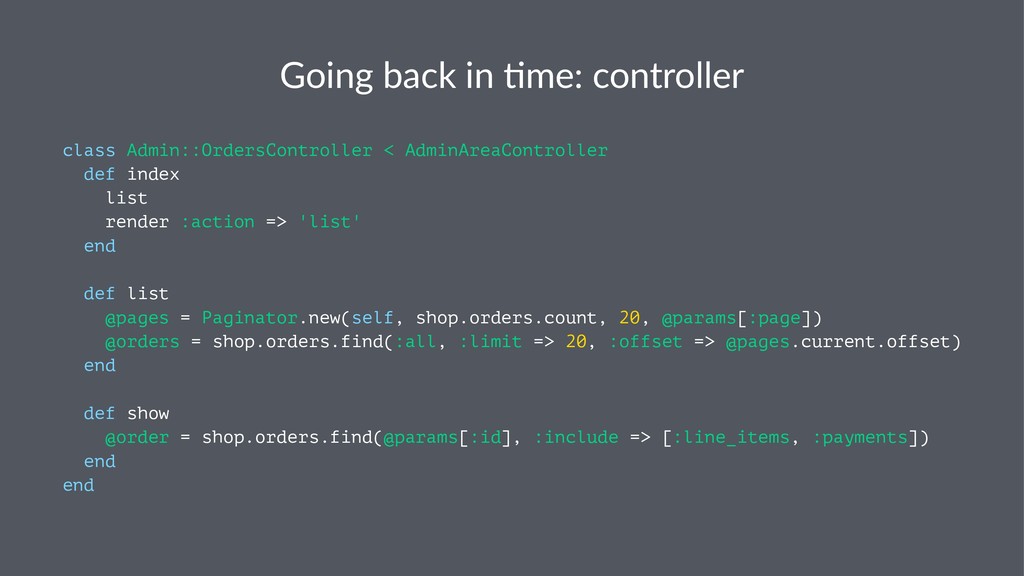
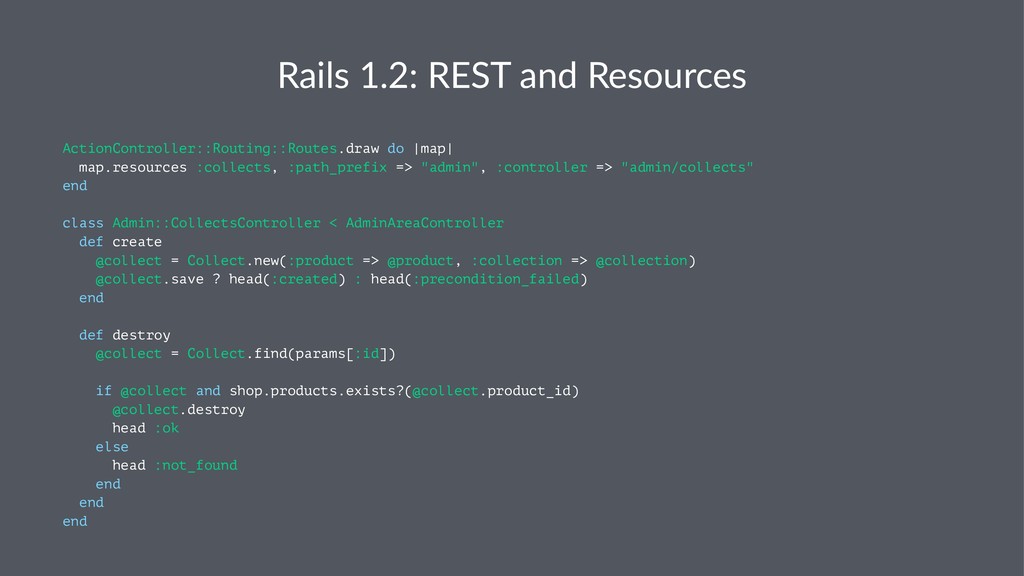
=> "admin/collects" end class Admin::CollectsController < AdminAreaController def create @collect = Collect.new(:product => @product, :collection => @collection) @collect.save ? head(:created) : head(:precondition_failed) end def destroy @collect = Collect.find(params[:id]) if @collect and shop.products.exists?(@collect.product_id) @collect.destroy head :ok else head :not_found end end end
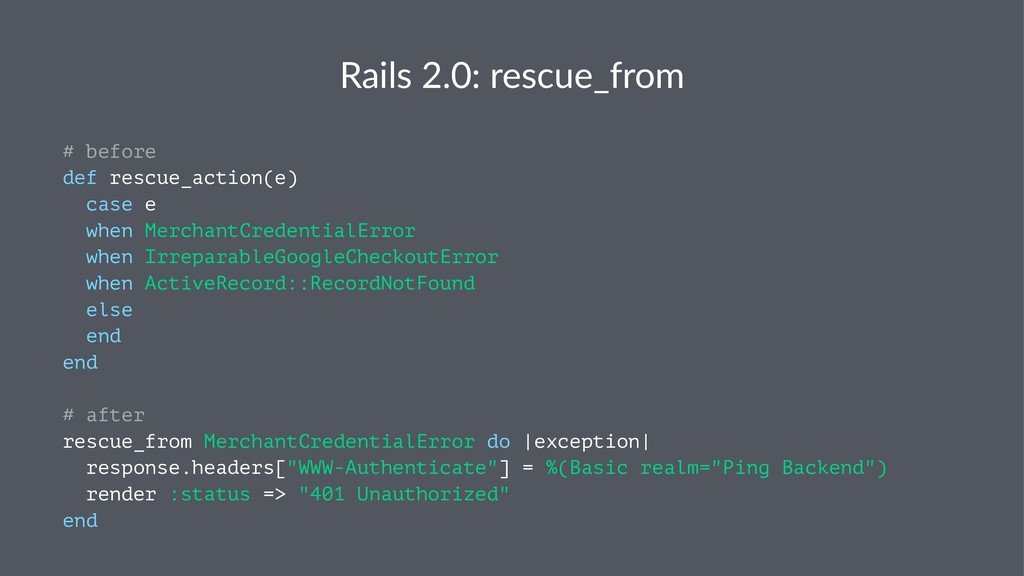
IrreparableGoogleCheckoutError when ActiveRecord::RecordNotFound else end end # after rescue_from MerchantCredentialError do |exception| response.headers["WWW-Authenticate"] = %(Basic realm="Ping Backend") render :status => "401 Unauthorized" end
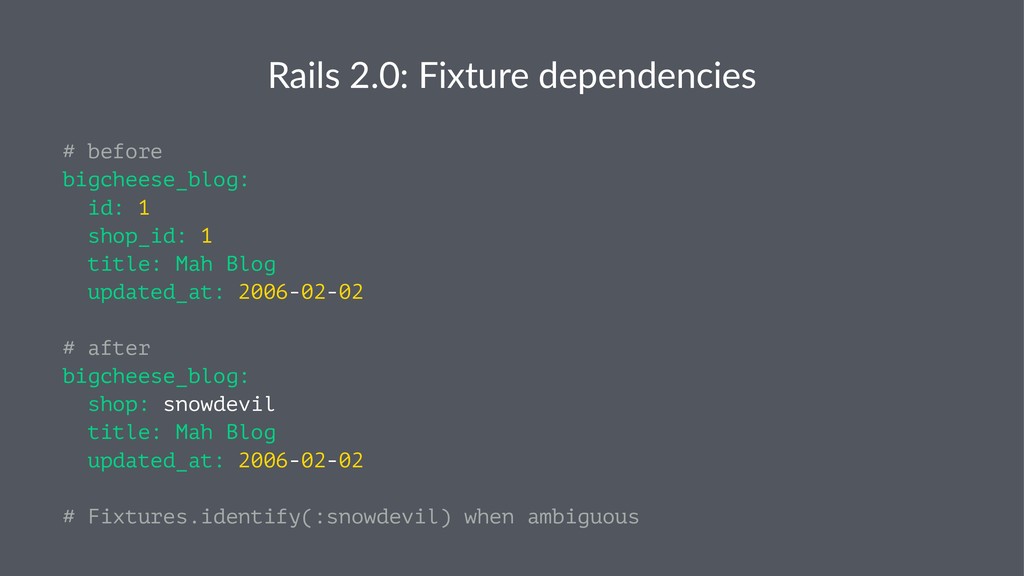
Blog updated_at: 2006-02-02 # after bigcheese_blog: shop: snowdevil title: Mah Blog updated_at: 2006-02-02 # Fixtures.identify(:snowdevil) when ambiguous
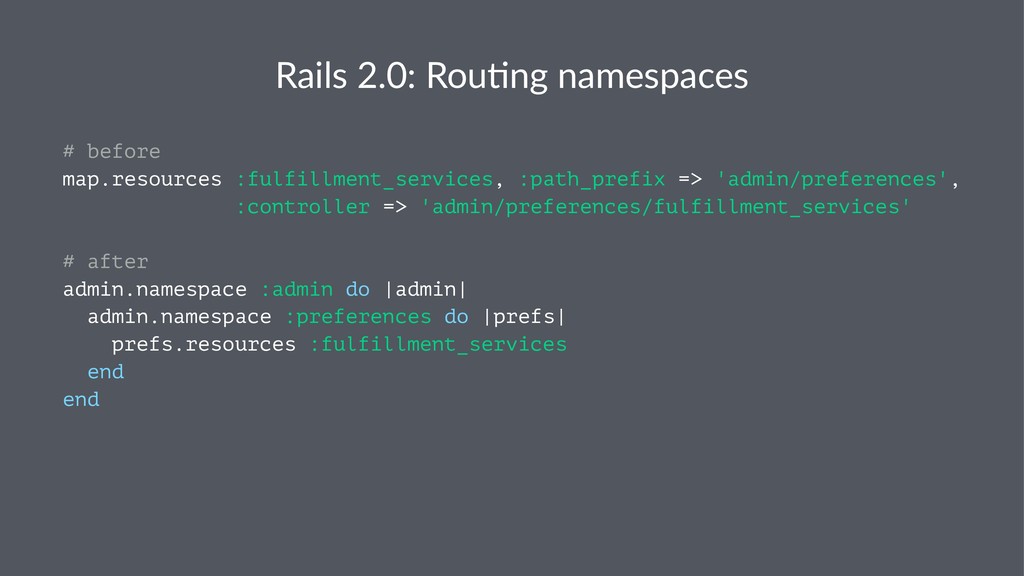
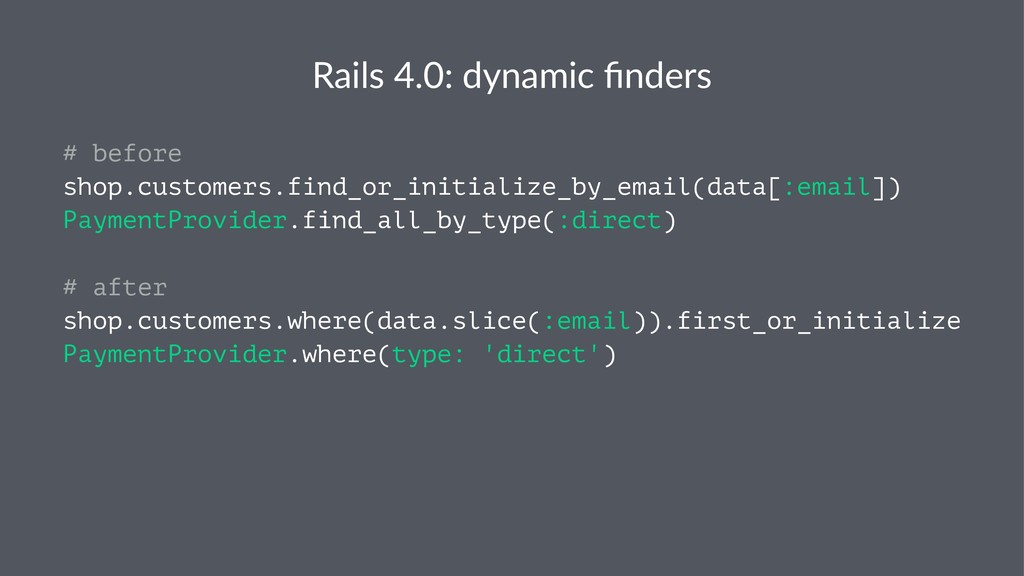
'admin/preferences/fulfillment_services' # after admin.namespace :admin do |admin| admin.namespace :preferences do |prefs| prefs.resources :fulfillment_services end end
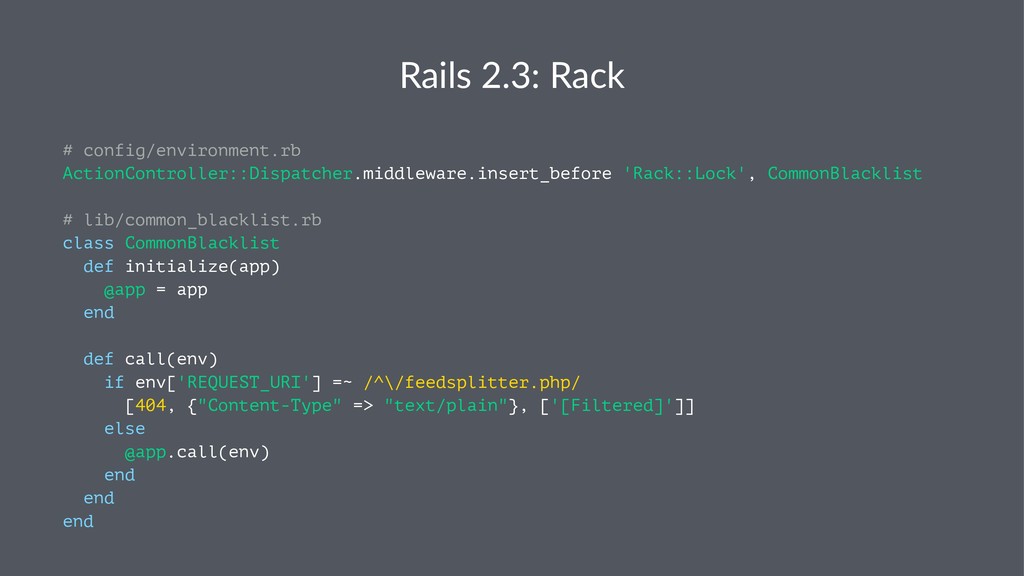
def initialize(app) @app = app end def call(env) if env['REQUEST_URI'] =~ /^\/feedsplitter.php/ [404, {"Content-Type" => "text/plain"}, ['[Filtered]']] else @app.call(env) end end end
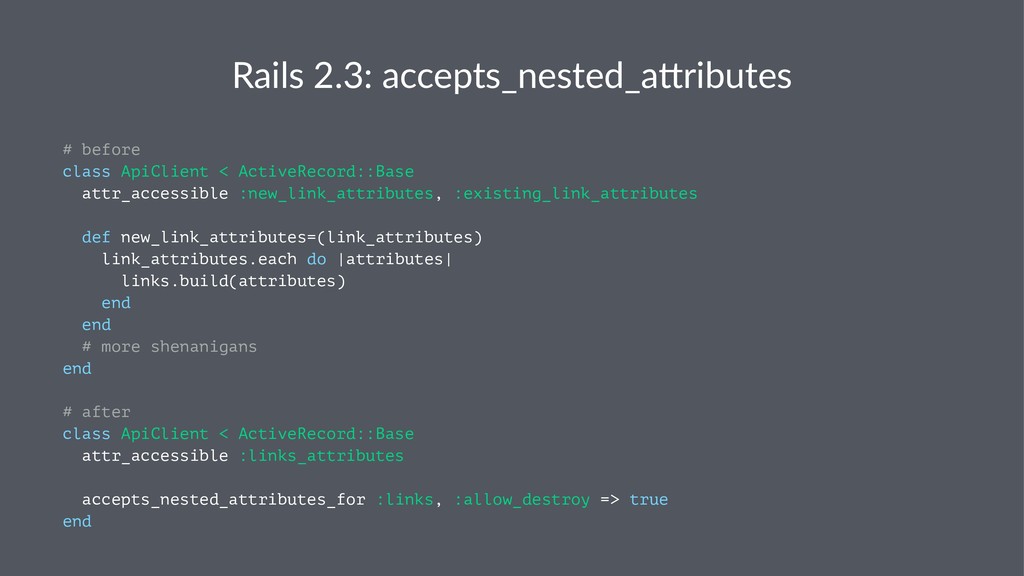
def new_link_attributes=(link_attributes) link_attributes.each do |attributes| links.build(attributes) end end # more shenanigans end # after class ApiClient < ActiveRecord::Base attr_accessible :links_attributes accepts_nested_attributes_for :links, :allow_destroy => true end
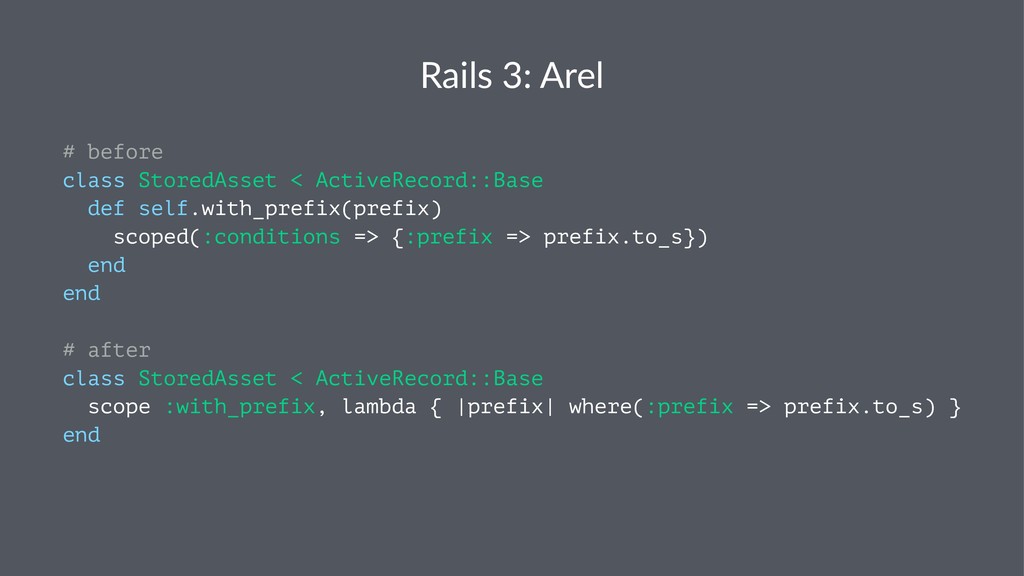
=> {:prefix => prefix.to_s}) end end # after class StoredAsset < ActiveRecord::Base scope :with_prefix, lambda { |prefix| where(:prefix => prefix.to_s) } end


 jduff
 greenmidori
 usanchuu
 keeg
 genda
 codatum
 glaforge
 sh_fk2
 gionn
 pfn
 teamlab
 takahashim
 yahonda
 helenjbeal
 samanthasiow
 csswizardry
 orderedlist
 marketingsoph
 addyosmani
 letsgokoyo
 jnunemaker
 wayneb77
 jlugia
 trishagee
 leimatthew05