paint Pros: mistakes allowed Cons: expensive, not trendy Imagine you are an artist. You want to gift your friend a painting: a portrait. You know your friend is somewhat picky.
paint Pros: mistakes allowed Cons: expensive, not trendy Gouache water-based as watercolor but not that opaque, not expensive, allows minor mistakes Imagine you are an artist. You want to gift your friend a painting: a portrait. You know your friend is somewhat picky.
to share or loose as a user? What sensitive data or PII can be there? Do I need to be compliant to any regulations? Why may the company loose a lot of many? How much do I care about reputation damage? Risk assessment for beginners
don’t want to share or loose as a user? - Credit card What sensitive data or PII can be there? - Name, address, phone Do I need to be compliant to any regulations? - GDPR, CCPA Why may the company loose a lot of many? - Availability issues How much do I care about reputation damage? - I care a lot Food delivery service example
What is our attack surface? How often this or that attack may appear? How probable it is? How interesting (profitable) it may be for an attacker? What skill level is required for it? Do we have (plan) other security controls covering it? What is the cost of implementing the security control? What is the cost of attack mitigation? See also: FAIR, NIST RMF Measure and prioritize
imagination or original ideas to create something; inventiveness Synonyms: imagination, vision, inventiveness Industry Guidelines Technology expertise Tools
based on risks and business goals - is an abstraction Secure Coding - is about writing code - is based on industry guidelines - is platform-specific Why engineers can’t make it secure?
You operate tools, you don’t make business decisions Secure Architecture - is about decision making process - is based on risks and business goals - is an abstraction Secure Coding - is about writing code - is based on industry guidelines - is platform-specific Why engineers can’t make it secure?
You operate tools, you don’t make business decisions Creating structure Adding details Secure Architecture - is about decision making process - is based on risks and business goals - is an abstraction Secure Coding - is about writing code - is based on industry guidelines - is platform-specific Why engineers can’t make it secure?
can pay with the app! No need to interact with people!” “The fraud level is way too high. Let’s ask engineers to investigate and fix the issue” Why engineers can’t make it secure?
can pay with the app! No need to interact with people!” “The fraud level is way too high. Let’s ask engineers to investigate and fix the issue” After a couple of month engineering team arrived with nothing. One of them asked: “What is the actual percentage of fraudulent transactions?” Why engineers can’t make it secure?
can pay with the app! No need to interact with people!” “The fraud level is way too high. Let’s ask engineers to investigate and fix the issue” After a couple of month engineering team arrived with nothing. One of them asked: “What is the actual percentage of fraudulent transactions?” The actual percentage was actually better the industry statistics. Why engineers can’t make it secure?
not for backend, web) But its logic includes both app and backend side. If the app is already released, it take more time to implement it (existing error handling logic created limitations). Why engineers can’t make it secure?
devs discover the risk 3. App devs communicate with architect and manager 4. App devs communicate with backend 5. Updating error handling 6. Adding force upgrade Why engineers can’t make it secure?
devs discover the risk 3. App devs communicate with architect and manager 4. App devs communicate with backend 5. Updating error handling 6. Adding force upgrade Security right from the start: 1. Architect communicates with devs 2. Architect discovers the risk 3. Error handling implemented 4. Adding force upgrade Why engineers can’t make it secure?
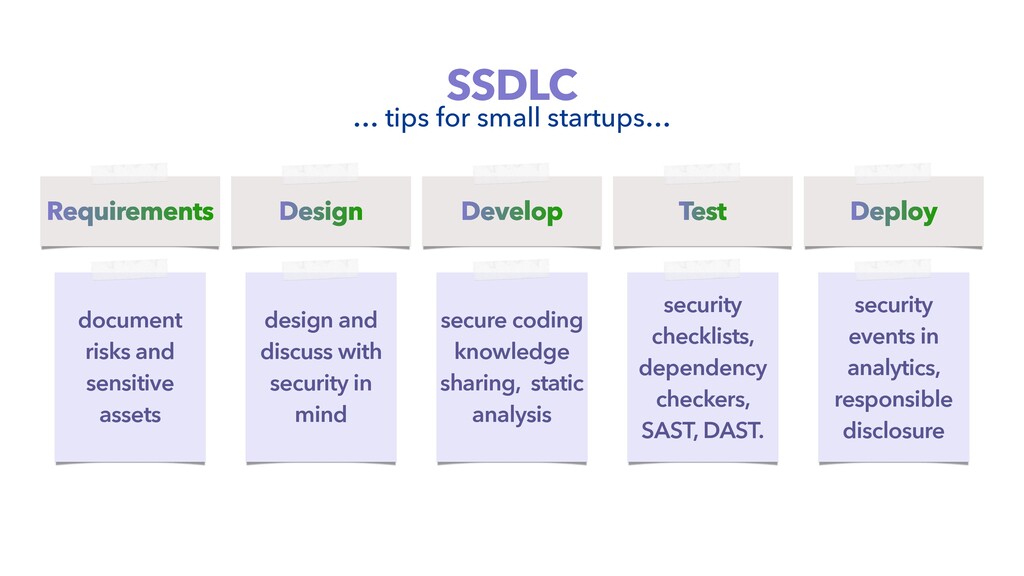
design and discuss with security in mind Secure coding, static analisys Security code review, pentesting Security monitoring, security assessment … tips for small startups… See also: OWASP RAF SSDLC
design and discuss with security in mind secure coding knowledge sharing, static analysis Security code review, pentesting Security monitoring, security assessment … tips for small startups… SSDLC
design and discuss with security in mind secure coding knowledge sharing, static analysis security checklists, dependency checkers, SAST, DAST. Security monitoring, security assessment … tips for small startups… SSDLC
design and discuss with security in mind secure coding knowledge sharing, static analysis security checklists, dependency checkers, SAST, DAST. security events in analytics, responsible disclosure … tips for small startups… SSDLC
design and discuss with security in mind secure coding knowledge sharing, static analysis security checklists, dependency checkers, SAST, DAST. security events in analytics, responsible disclosure … tips for small startups… SSDLC
when the very first app release is coming, but it lacks security completely? Requirements Design Develop Test Deploy What are the most critical events that may happen to your business? Prioritise!
when the very first app release is coming, but it lacks security completely? Requirements Design Develop Test Deploy What are the most critical events that may happen to your business? Prioritise! Communicate. Assess what you already have. Book time.
when the very first app release is coming, but it lacks security completely? Requirements Design Develop Test Deploy Build step by step. Make sure basic security functionality is working. Then, improve. What are the most critical events that may happen to your business? Prioritise! Communicate. Assess what you already have. Book time.
when the very first app release is coming, but it lacks security completely? Requirements Design Develop Test Deploy Build step by step. Make sure basic security functionality is working. Then, improve. Create a checklist with all the security controls. What are the most critical events that may happen to your business? Prioritise! Communicate. Assess what you already have. Book time.
when the very first app release is coming, but it lacks security completely? Requirements Design Develop Test Deploy Build step by step. Make sure basic security functionality is working. Then, improve. Create a checklist with all the security controls. Set up alerting What are the most critical events that may happen to your business? Prioritise! Communicate. Assess what you already have. Book time.
when the very first app release is coming, but it lacks security completely? Requirements Design Develop Test Deploy Build step by step. Make sure basic security functionality is working. Then, improve. Create a checklist with all the security controls. Set up alerting Prepare Plan B What are the most critical events that may happen to your business? Prioritise! Communicate. Assess what you already have. Book time.


 julep
 shihochan
 iwiwi
 sodainc
 kasacchiful
 jame2408
 akihisaikeda
 kosukesaigusa
 ktombow
 hasutosasaki
 steliosf
 koukimiura
 vivion
 mlcsv
 erikaheidi
 palkan
 szymonslowik
 keithpitt
 mongodb
 marktimemedia
 cassininazir
 kneath
 tammyeverts
 tammielis
 honnibal