Share
Embed
Transcript
44 slides
-
Security Software Engineer Julia Potapenko @julepka We help companies to
protect their sensitive and valuable data. -
• Tight deadlines • Feature priorities If you ask developers
what is the problem… -
• Tight deadlines • Feature priorities • Lack of security
expertise • Security controls con f lict with other features If you ask developers what is the problem… -
• Tight deadlines • Feature priorities • Lack of security
expertise • Security controls con f lict with other features • Lack of secure architecture If you ask developers what is the problem… -
https://www.guardsquare.com/state-of-mobile-application-security-report Security controls con f lict with other features Necessity
of communication https://www.ptsecurity.com/ww-en/analytics/web-vulnerabilities-2020/ -
https://www.microfocus.com/en-us/assets/security/application-security-risk-report Lack of security expertise No secure coding skills https://www.ptsecurity.com/ww-en/analytics/web-vulnerabilities-2020/
https://www.ptsecurity.com/ww-en/analytics/web-vulnerabilities-2020/ https://www.veracode.com/state-of-software-security-report -
Secure coding is a separate skill Developers can learn general
best practices and platform speci f ic recommendations. • Security trainings • Online education materials • Conferences -
Secure coding is a separate skill Examples: • Data minimisation
principle (do not store what you don’t really need) • Validate any input from external sources (user input, network requests, etc) • Deny access by default -
Security is invisible - No direct business value. - You
can’t see if it’s working, you can see when it fails. -
The more we delay security – the more effort it
takes to be added – the more chances it has to be ignored -
The longer it takes to f ix an issue, the
less chances it has to be f ixed https://www.veracode.com/state-of-software-security-report -
Secure SDLC Requirements Design Develop Test Deploy Risk assessment Threat
modelling & design review Secure coding & static analysis Code review & security testing Security assessment & secure con f iguration -
Secure SDLC Requirements Design Develop Test Deploy Risk assessment Threat
modelling & design review Secure coding & static analysis Code review & security testing Security assessment & secure con f iguration Software developers -
Secure SDLC Requirements Design Develop Test Deploy Risk assessment Threat
modelling & design review Secure coding & static analysis Code review & security testing Security assessment & secure con f iguration Software developers Architectural decision -
In a fast-pacing environment… People make poor decisions under the
pressure. Secure architecture is about decision making. People mess up the processes under the pressure. Secure architecture is about following the process. -
Secure architecture – is a combination of structural security decisions
that ef f iciently addresses risks considering business goals. -
Secure architecture – is a combination of structural security decisions…
that ef f iciently addresses risks considering -
Secure architecture – is a combination of structural security decisions
that ef f iciently addresses risks… considering business g -
Secure architecture – is a combination of structural security decisions
that ef f iciently addresses risks considering business goals. -
Secure Architecture - is about decision making process - is
based on risks and business goals - is an abstraction Secure Coding - is about writing code - is based on industry guidelines - is platform-speci f ic -
You operate risks and business goals, abstracting from the tools
You operate tools, you don’t make business decisions Secure Architecture - is about decision making process - is based on risks and business goals - is an abstraction Secure Coding - is about writing code - is based on industry guidelines - is platform-speci f ic -
You operate risks and business goals, abstracting from the tools
You operate tools, you don’t make business decisions Creating structure Adding details Secure Architecture - is about decision making process - is based on risks and business goals - is an abstraction Secure Coding - is about writing code - is based on industry guidelines - is platform-speci f ic -
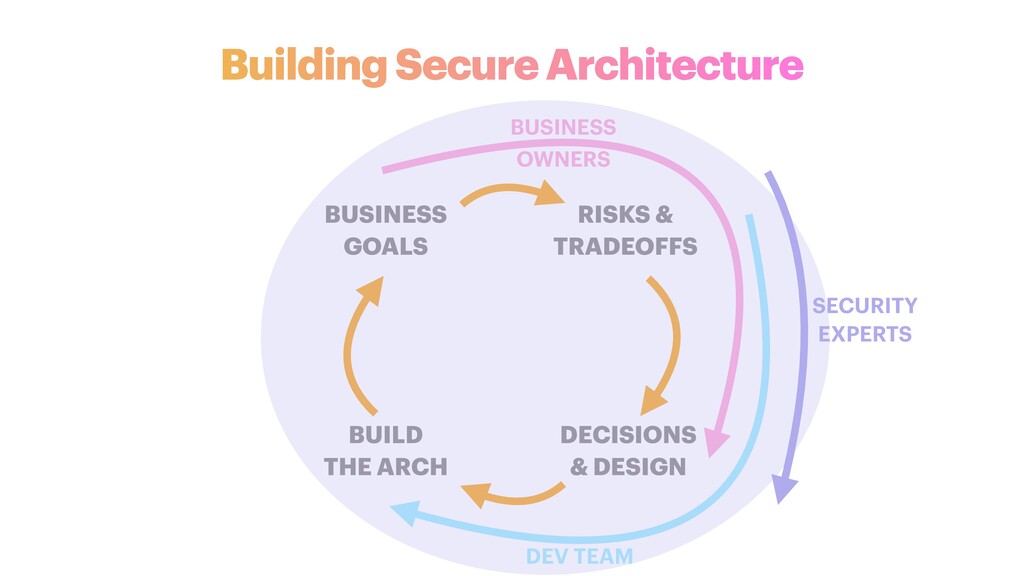
BUSINESS GOALS BUILD THE ARCH DECISIONS & DESIGN RISKS &
TRADEOFFS Building Secure Architecture -
Building Secure Architecture BUSINESS GOALS BUILD THE ARCH DECISIONS &
DESIGN RISKS & TRADEOFFS BUSINESS OWNERS DEV TEAM -
Building Secure Architecture BUSINESS GOALS BUILD THE ARCH DECISIONS &
DESIGN RISKS & TRADEOFFS BUSINESS OWNERS DEV TEAM SECURITY EXPERTS -
Building Secure Architecture BUSINESS GOALS BUILD THE ARCH DECISIONS &
DESIGN RISKS & TRADEOFFS BUSINESS OWNERS DEV TEAM SECURITY EXPERTS -
Shared Responsibility No one can know everything Who makes decisions?
Who plans the work and sets priorities? Who will address security? -
• Business owners • Product and project managers • Software
developers • UI/UX Designers • DevOps team • QA engineers • … Shared Responsibility No one can know everything Who makes decisions? Who plans the work and sets priorities? Who will address security? -
Shared Responsibility No one can know everything Each platform is
different. Secure architecture requires security expertise in each of them. Example: Force upgrade Unlike web, you can’t control when the user updates desktop or mobile app, unless you have implemented additional feature for that. It requires changes from both client and backend. -
Shared Responsibility No one can know everything Each platform is
different. Secure architecture requires security expertise in each of them. Example: Screenshot prevention You can’t prevent screenshots for web apps. Why would you want it for Android app? Because users usually automatically sync photos with Google Photos, iCloud, etc. -
Ownership • Understand your role • Know what you are
doing are what for • Communicate The goal: each team member knows who to ask questions. If you own, you care -
Ownership Example: Owning the features • Understand its value •
Closer look at related PRs • Keep an eye on updates • Be ready to speak up If you own, you care -
Ownership Example: Reading security docs “Have you read security policy
of your compony?” “Have you read risk assessment and threat modelling docs of your project?” If you own, you care -
Want to learn more? “Designing stack agnostic, modern, secure architectures”
by Eugene Pilyankevich https://www.infoq.com/presentations/design-secure-architectures/ “Secure Development Lifecycle” by Jim Manico https://youtu.be/M7qMP3C5bkU https://owasp.org/www-pdf-archive/Jim_Manico_(Hamburg)_-_Securiing_the_SDLC.pdf Collections of security stats reports https://techbeacon.com/security/27-data-security-stats-matter https://techbeacon.com/security/30-app-sec-stats-matter