Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Lockdown my sassy AI agent

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →

Lockdown my sassy AI agent

A session at LINE THAILAND DEVELOPER CONFERENCE 2026

LINE Developers Thailand

October 17, 2026

Transcript

26 slides
  1. About Me Senior Site Reliability Engineer • LINE Company (Thailand)

    • Season 8 Debian Developer • Debian Community • Season 11 Linux Network • Experience ~ 3 decades
  2. Agenda • AI Evolution • Story: The OpenAI - Hugging

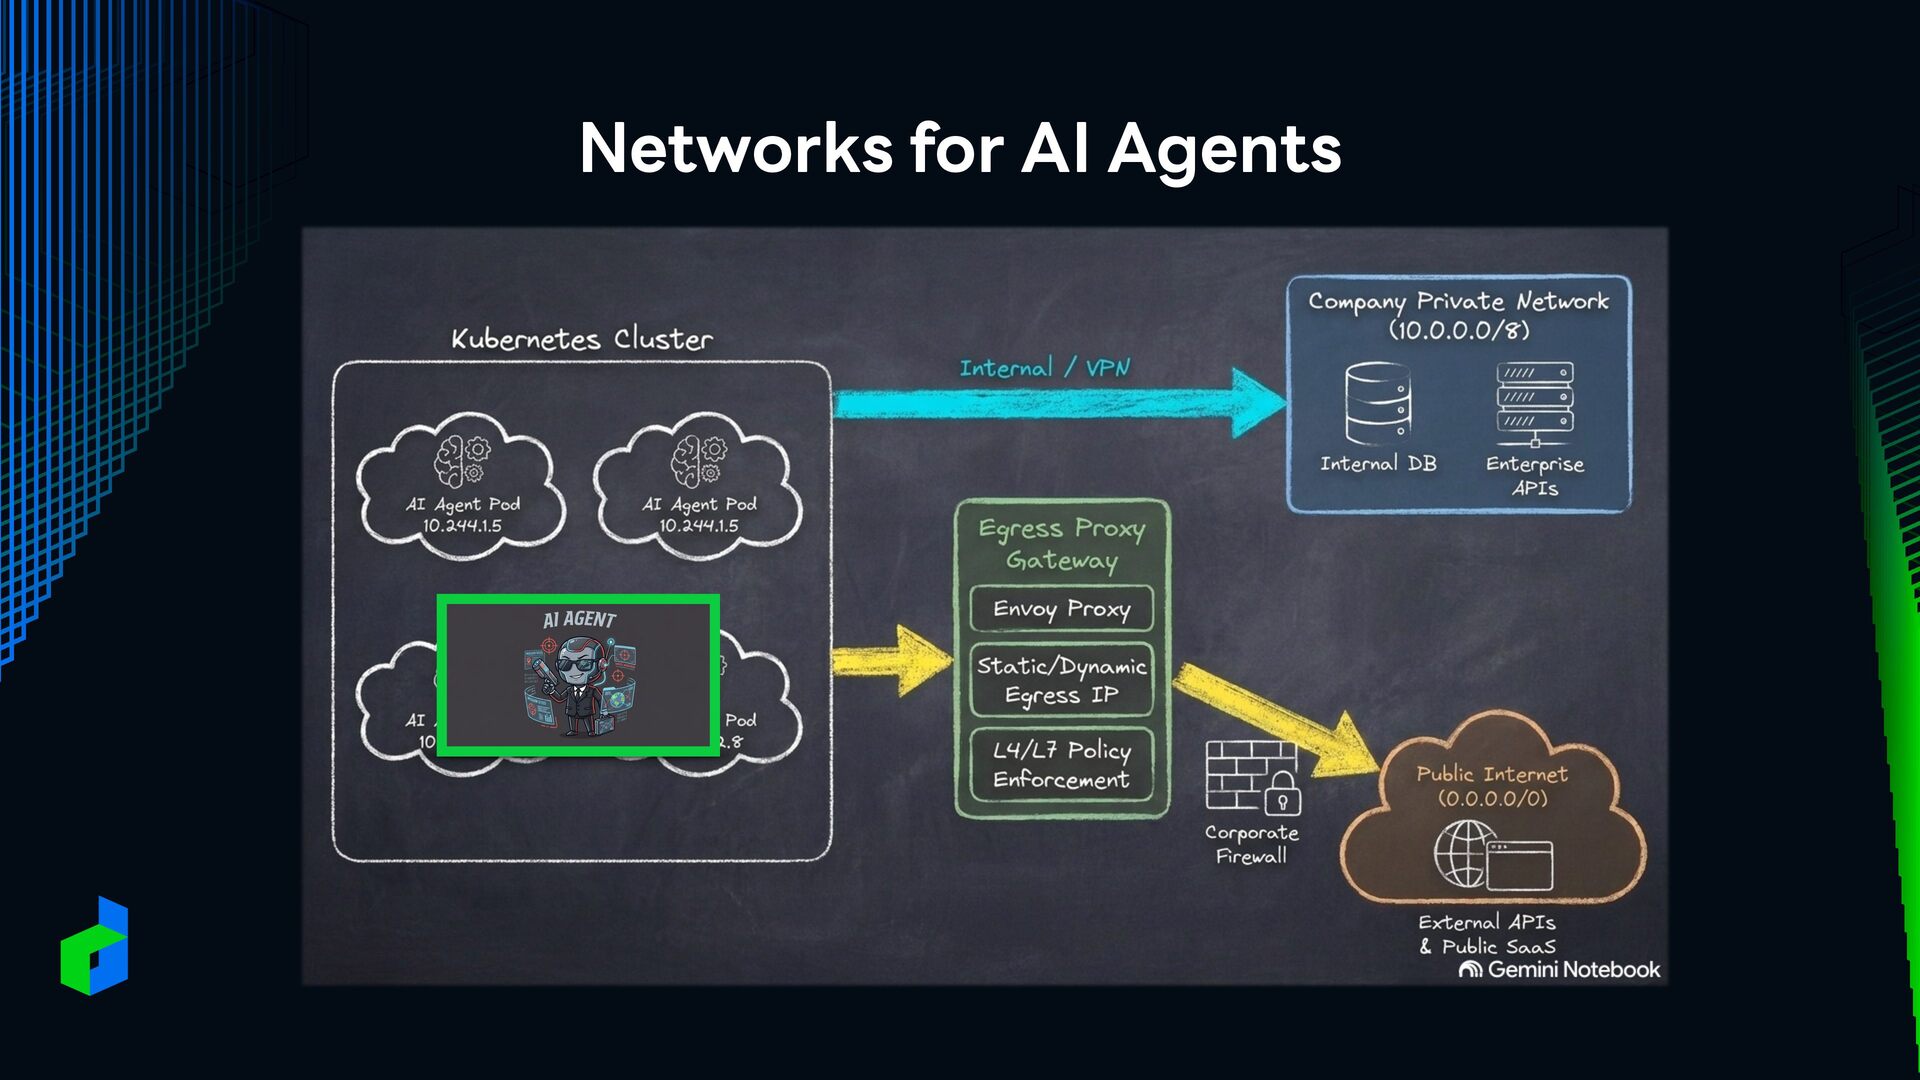
    Face Incident • AI Agent network lockdown • Flex Security Network
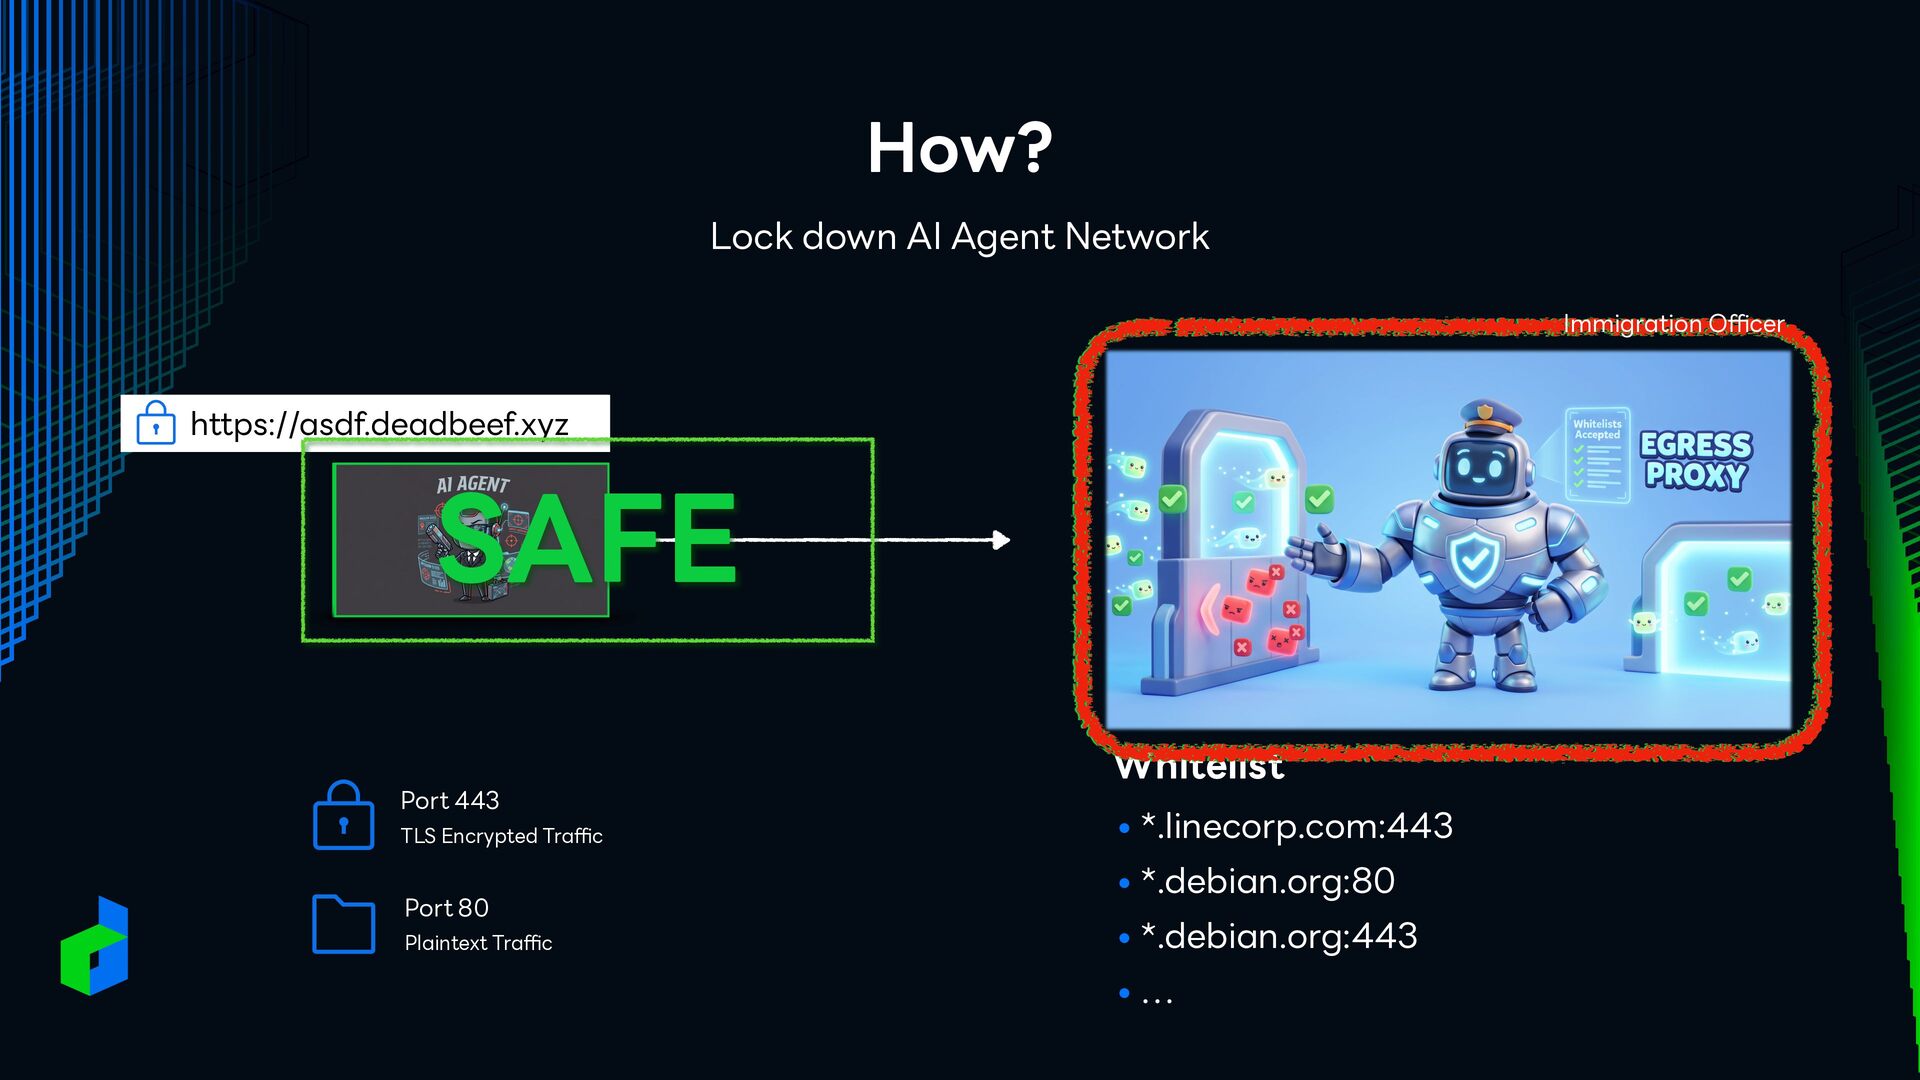
  3. How? Lock down AI Agent Network Immigration O cer http://deb.debian.org

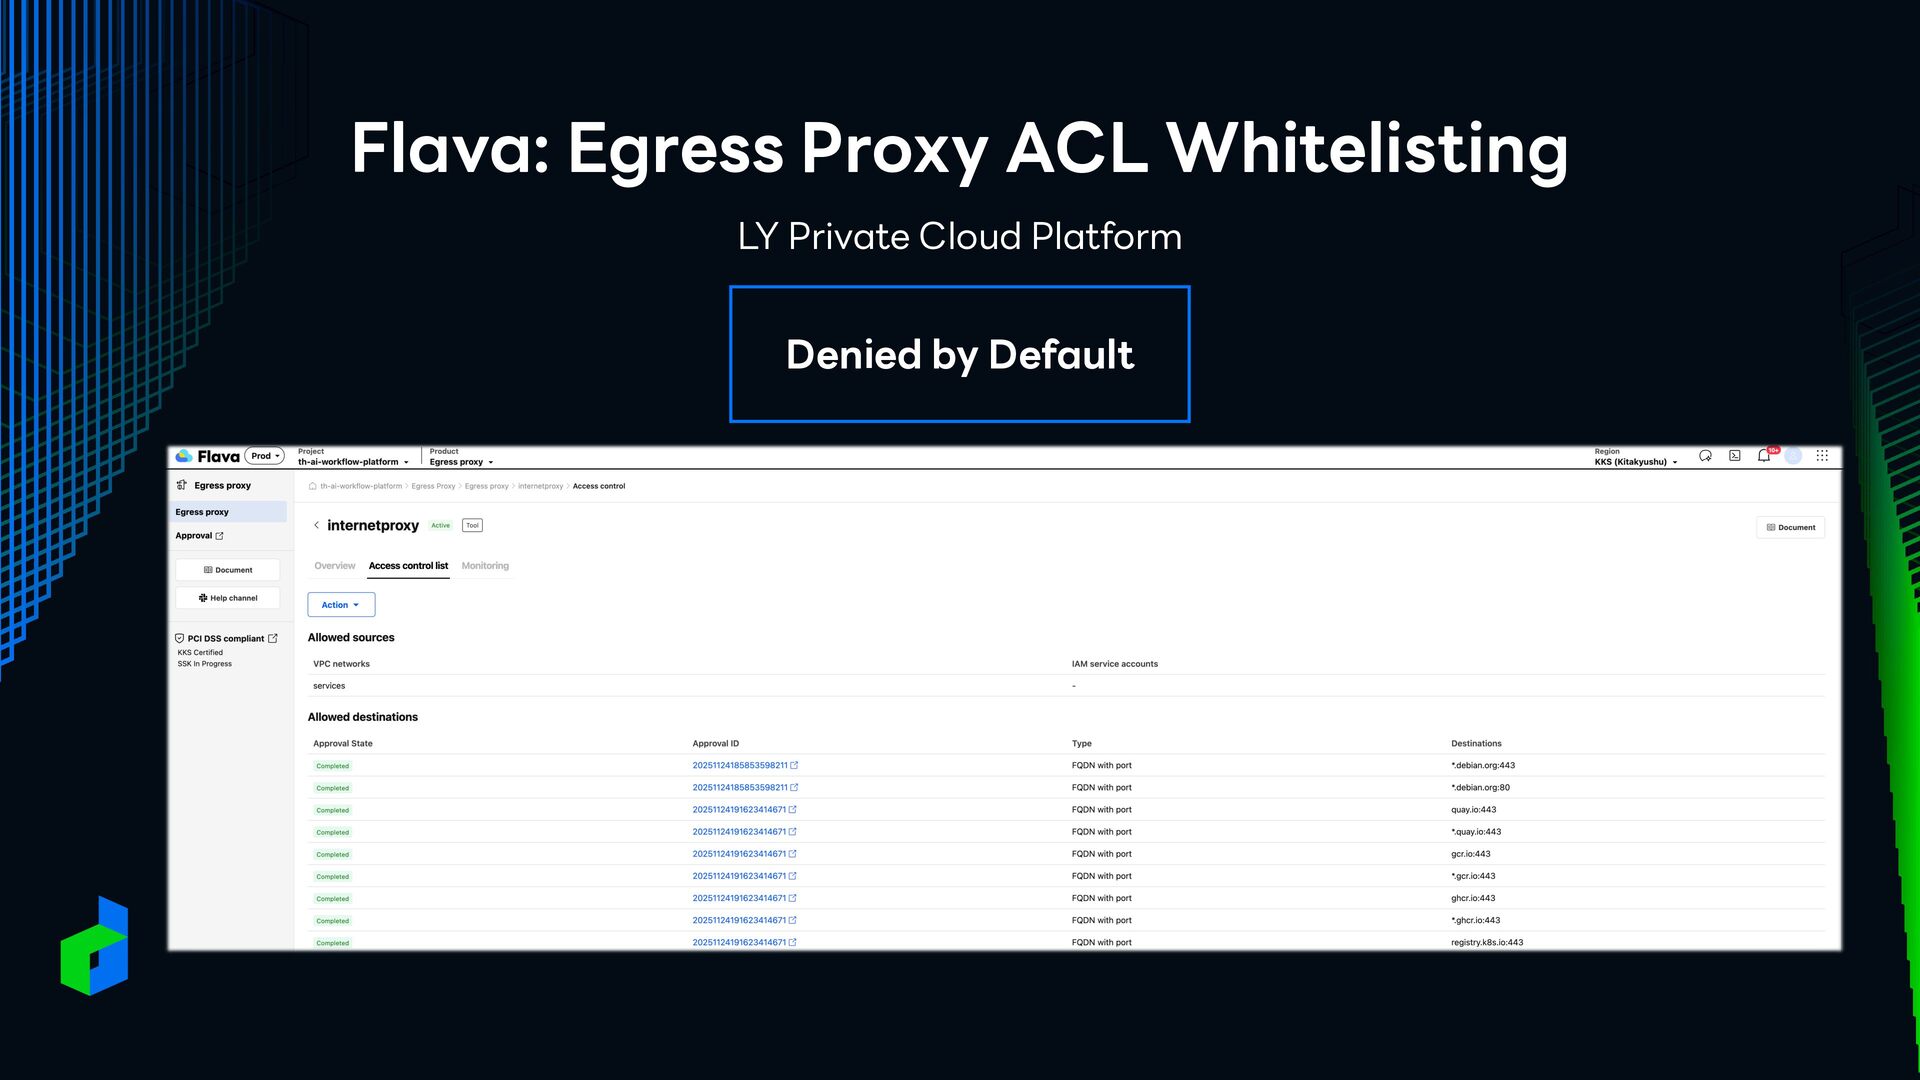
    https://www.linecorp.com https://asdf.deadbeef.xyz SAFE Port 443 TLS Encrypted Tra c Port 80 Plaintext Tra c Whitelist • *.linecorp.com:443 • *.debian.org:80 • *.debian.org:443 ffi ffi ffi •…
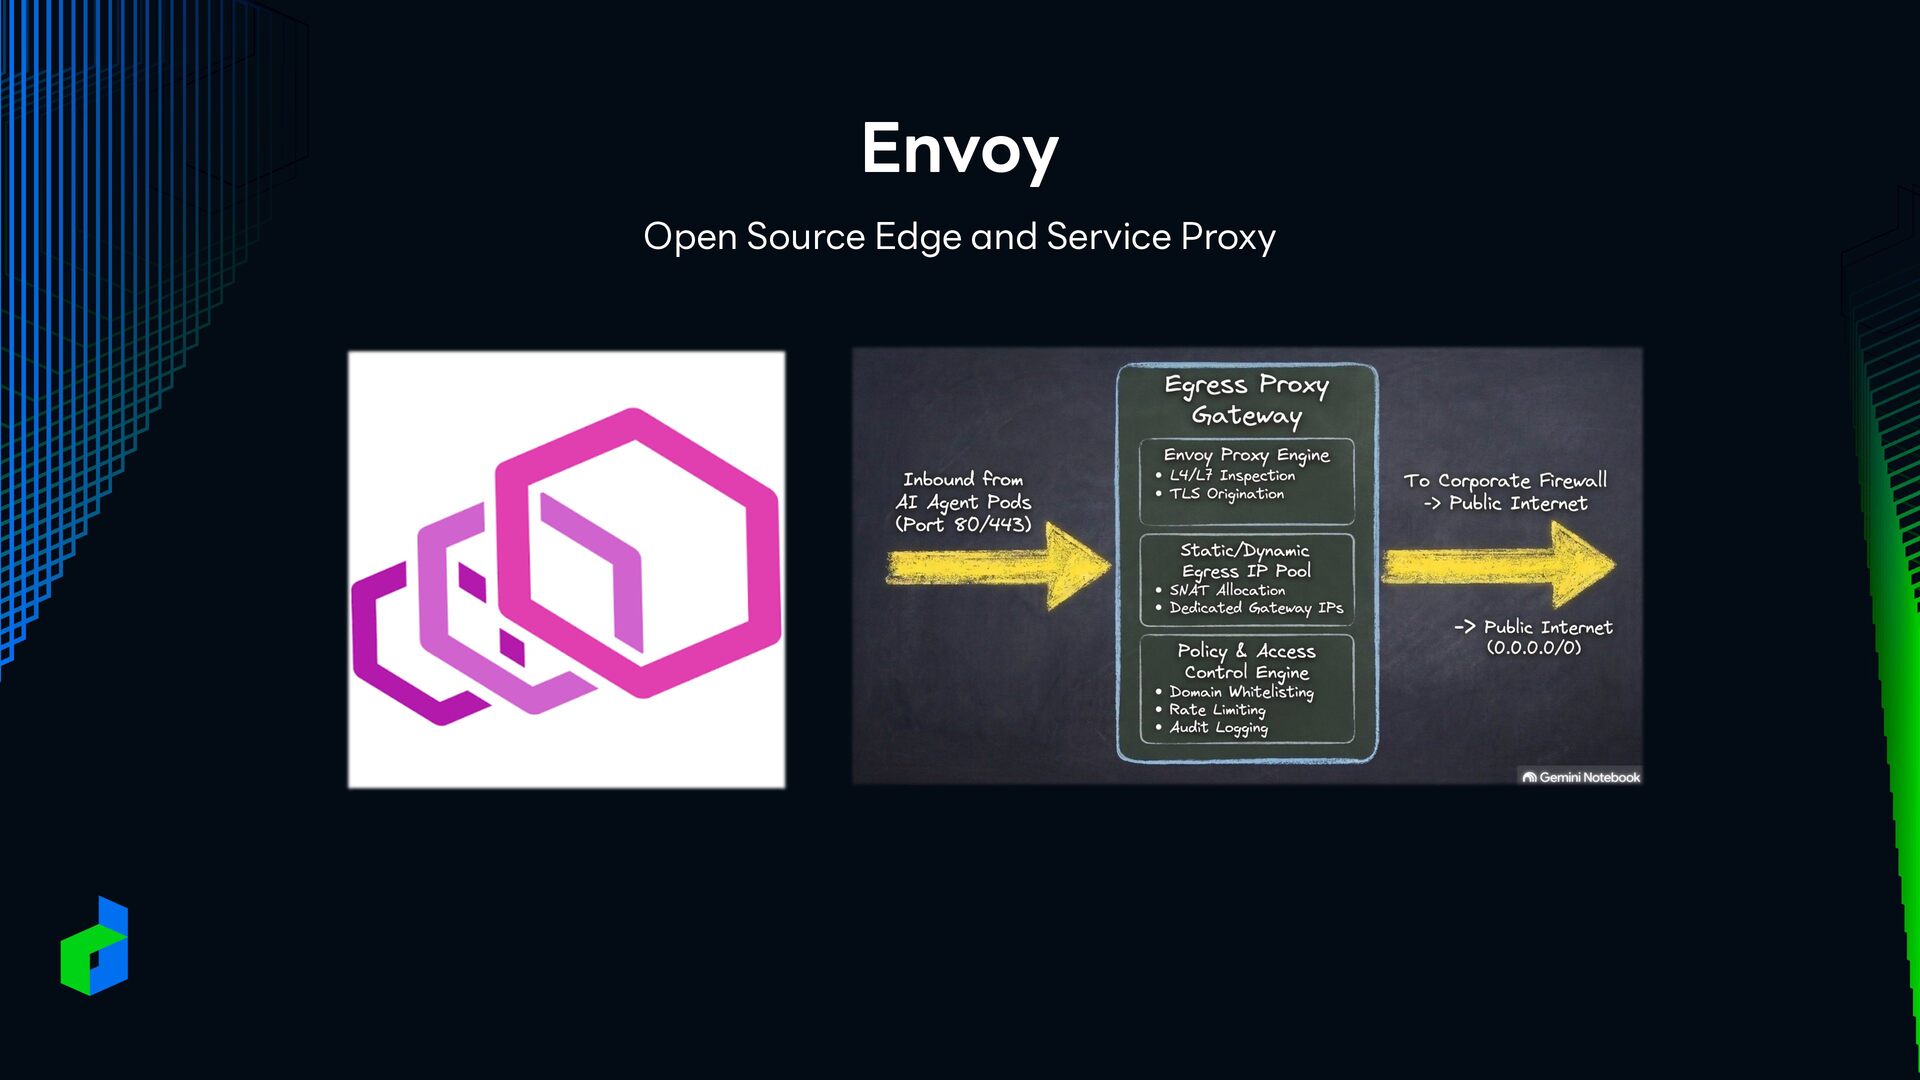
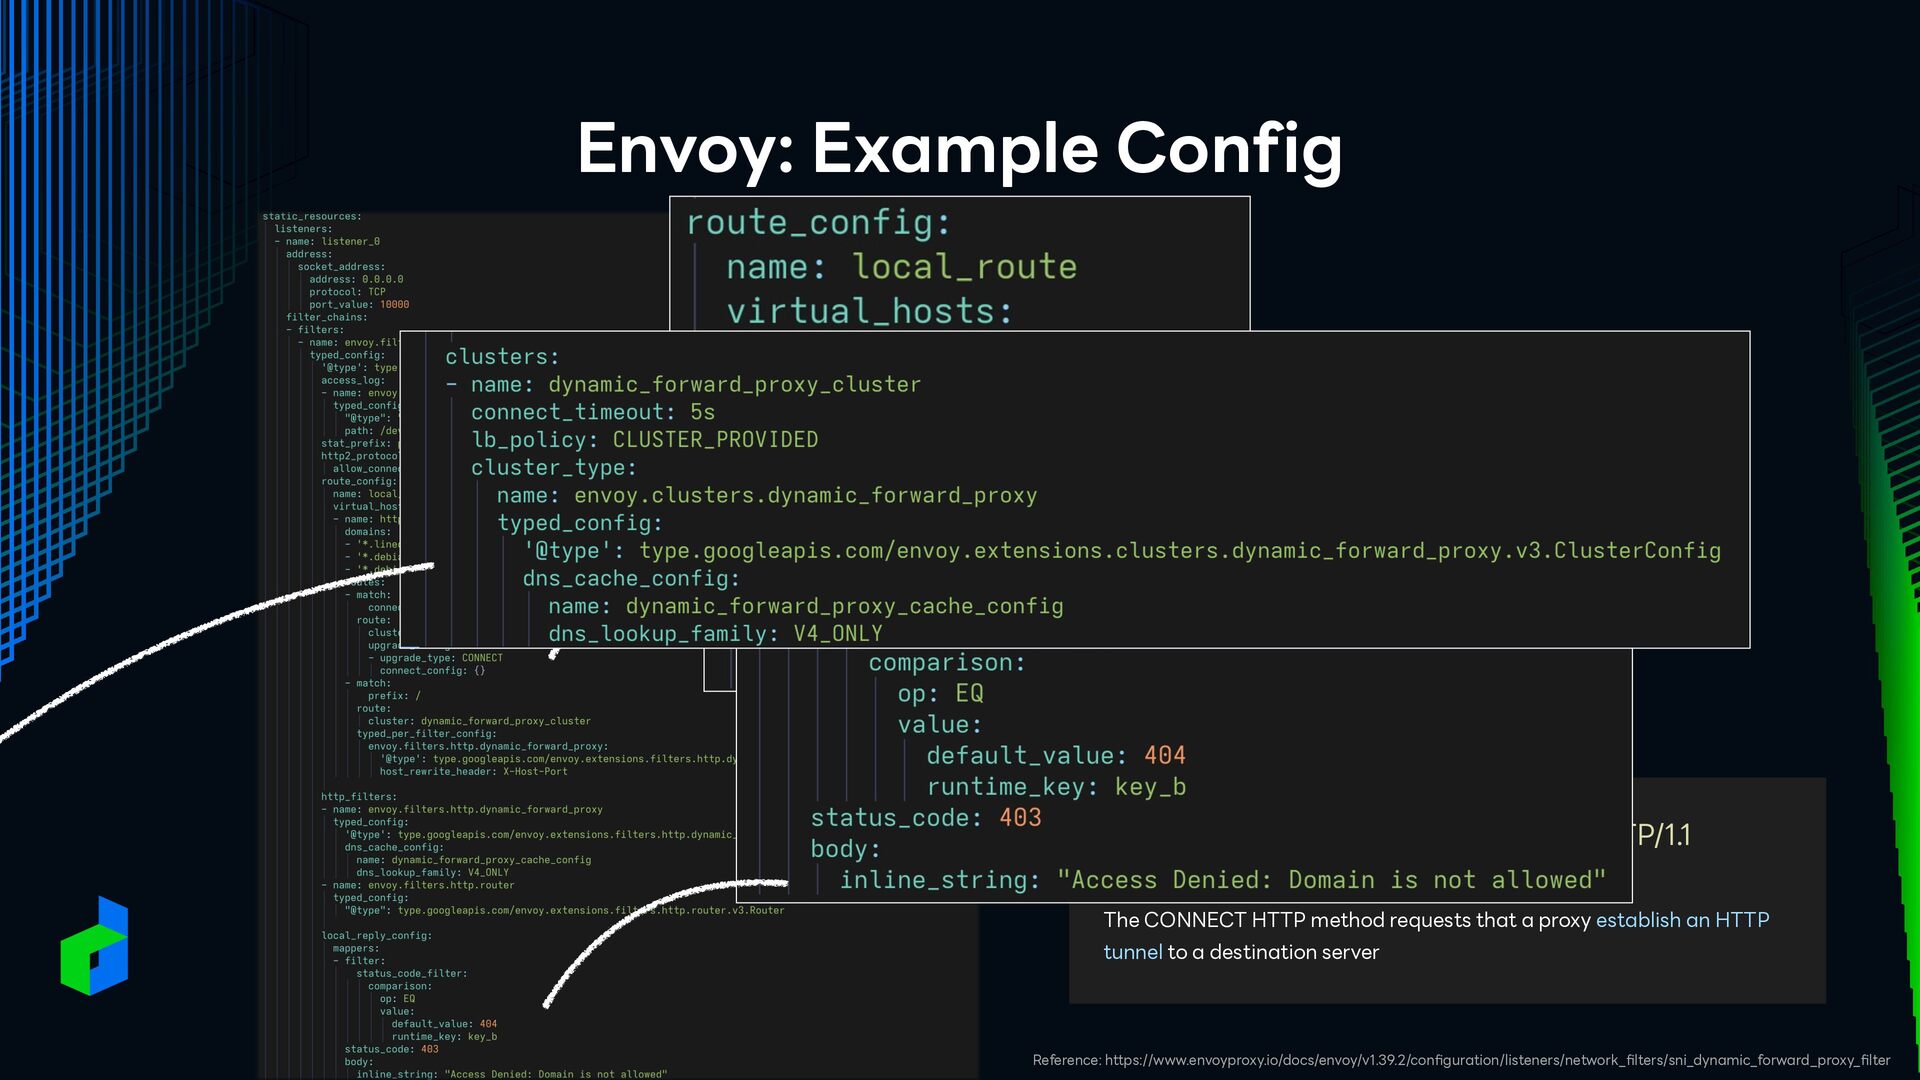
  4. Envoy: Example Config KEYWORD: Dynamic Forward Proxy CONNECT www.linecorp.com:443 HTTP/1.1

    The CONNECT HTTP method requests that a proxy establish an HTTP tunnel to a destination server fi fi fi Reference: https://www.envoyproxy.io/docs/envoy/v1.39.2/con guration/listeners/network_ lters/sni_dynamic_forward_proxy_ lter
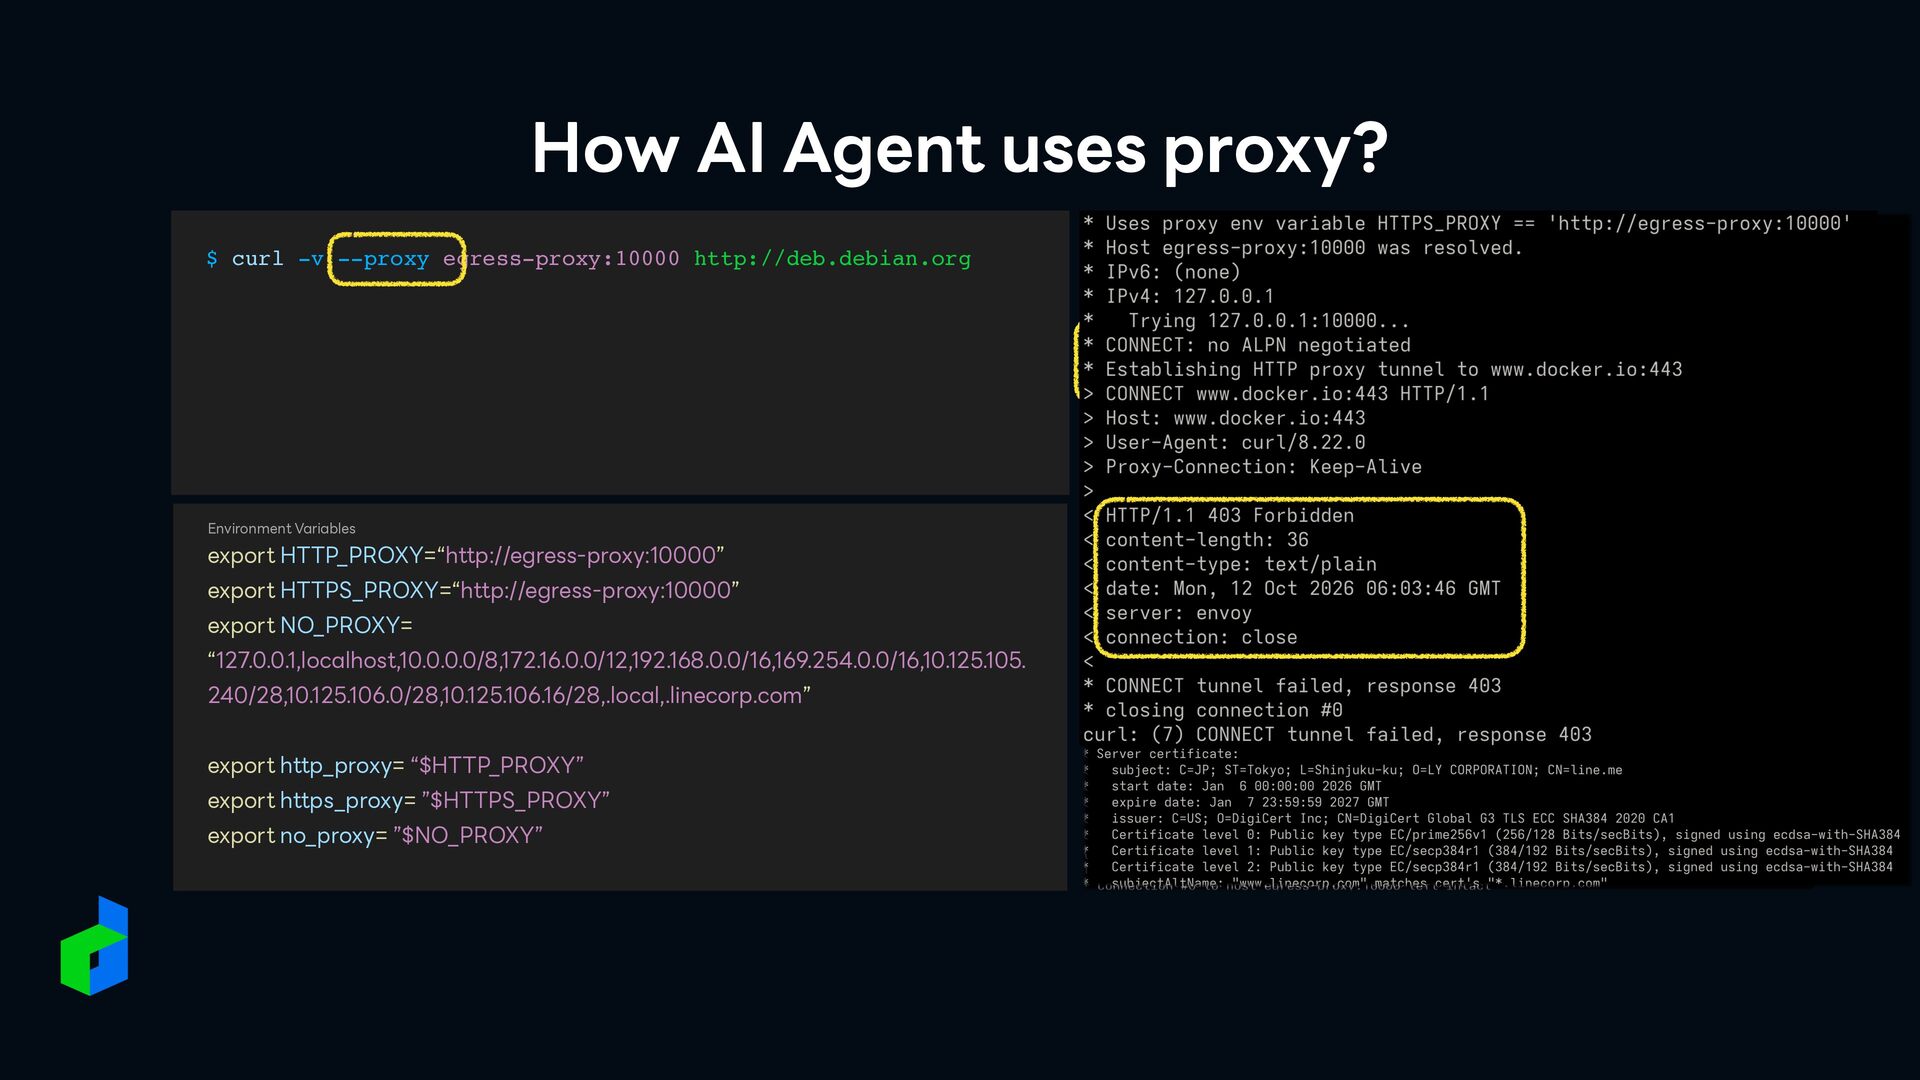
  5. How AI Agent uses proxy? -X GET https://www.linecorp.com $ curl

    -v --proxy https://www.docker.io egress-proxy:10000 http://deb.debian.org Environment Variables export HTTP_PROXY=“http://egress-proxy:10000” export HTTPS_PROXY=“http://egress-proxy:10000” export NO_PROXY= “127.0.0.1,localhost,10.0.0.0/8,172.16.0.0/12,192.168.0.0/16,169.254.0.0/16,10.125.105. 240/28,10.125.106.0/28,10.125.106.16/28,.local,.linecorp.com” export http_proxy= “$HTTP_PROXY” export https_proxy= ”$HTTPS_PROXY” export no_proxy= ”$NO_PROXY”
  6. Proxy Pain Not all applications support Not easy to make

    it right Not easy to maintain at scale
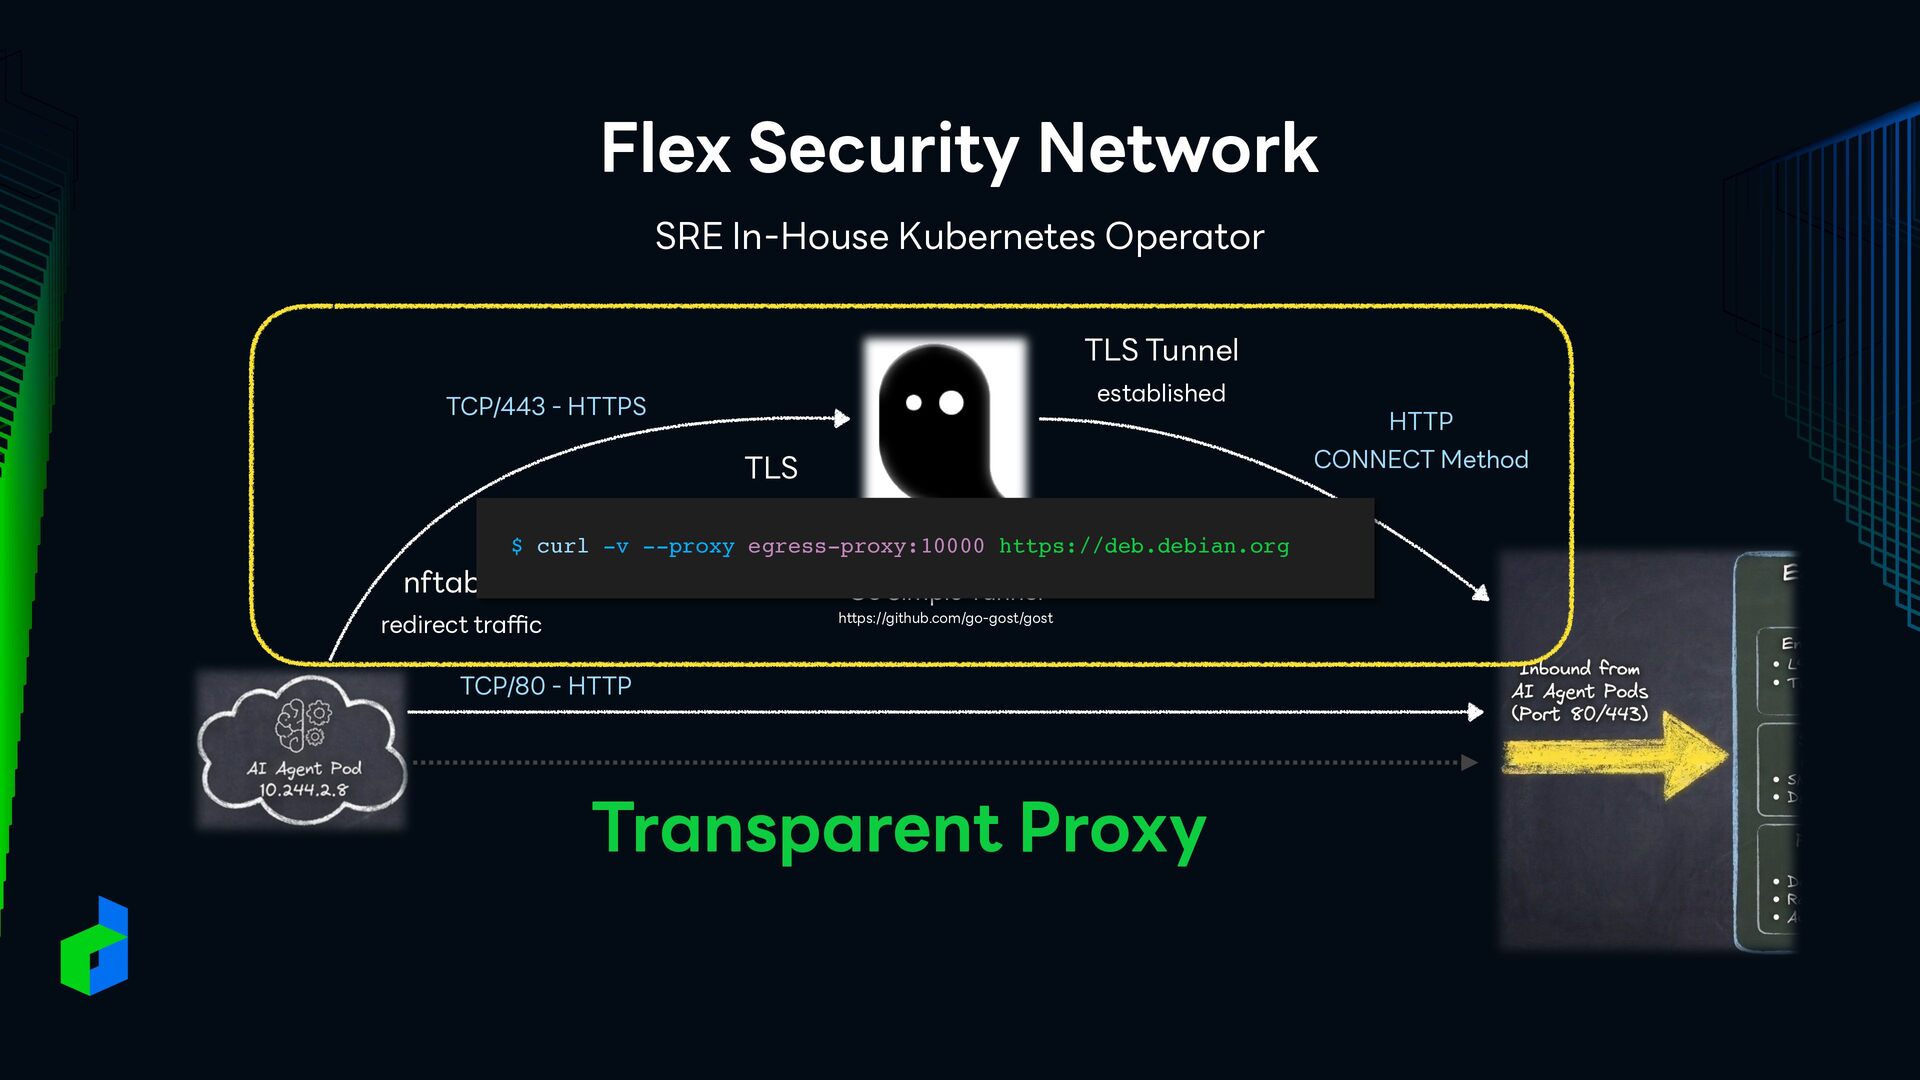
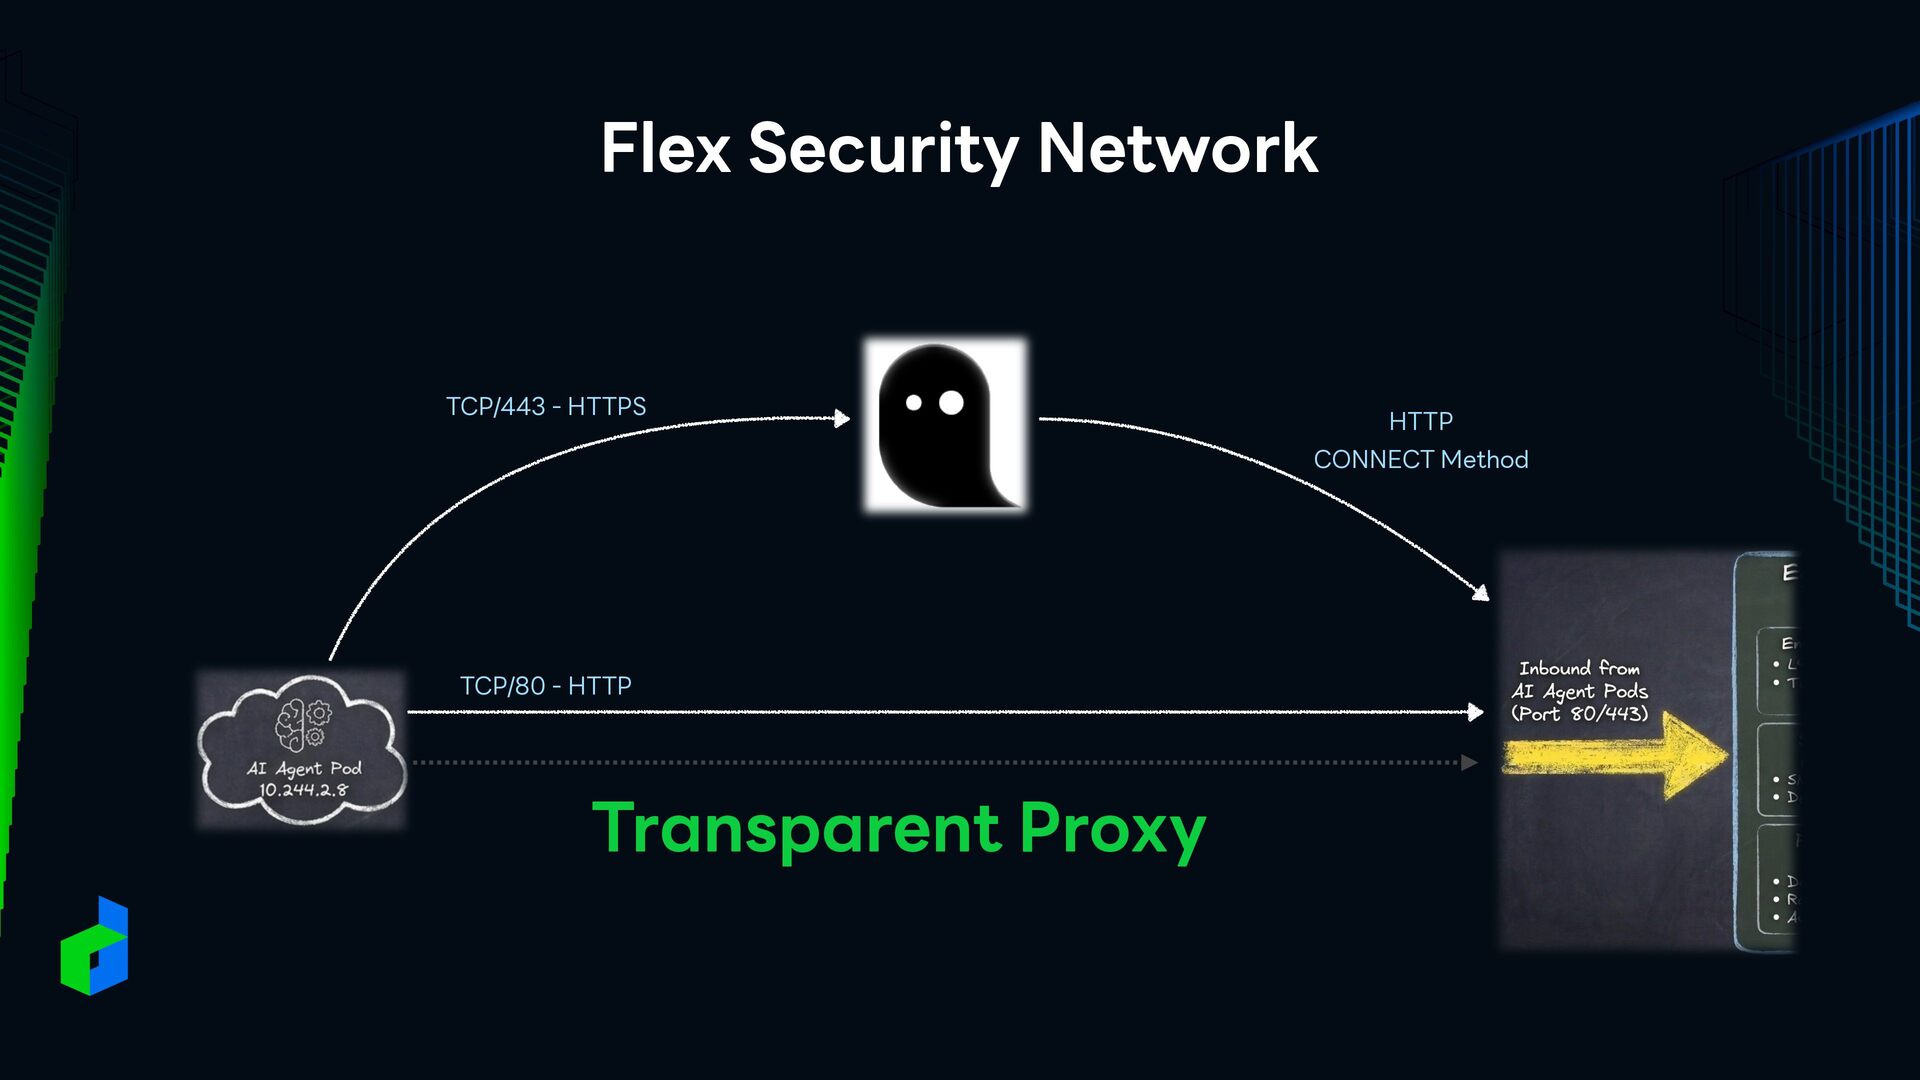
  7. Flex Security Network SRE In-House Kubernetes Operator TLS Tunnel established

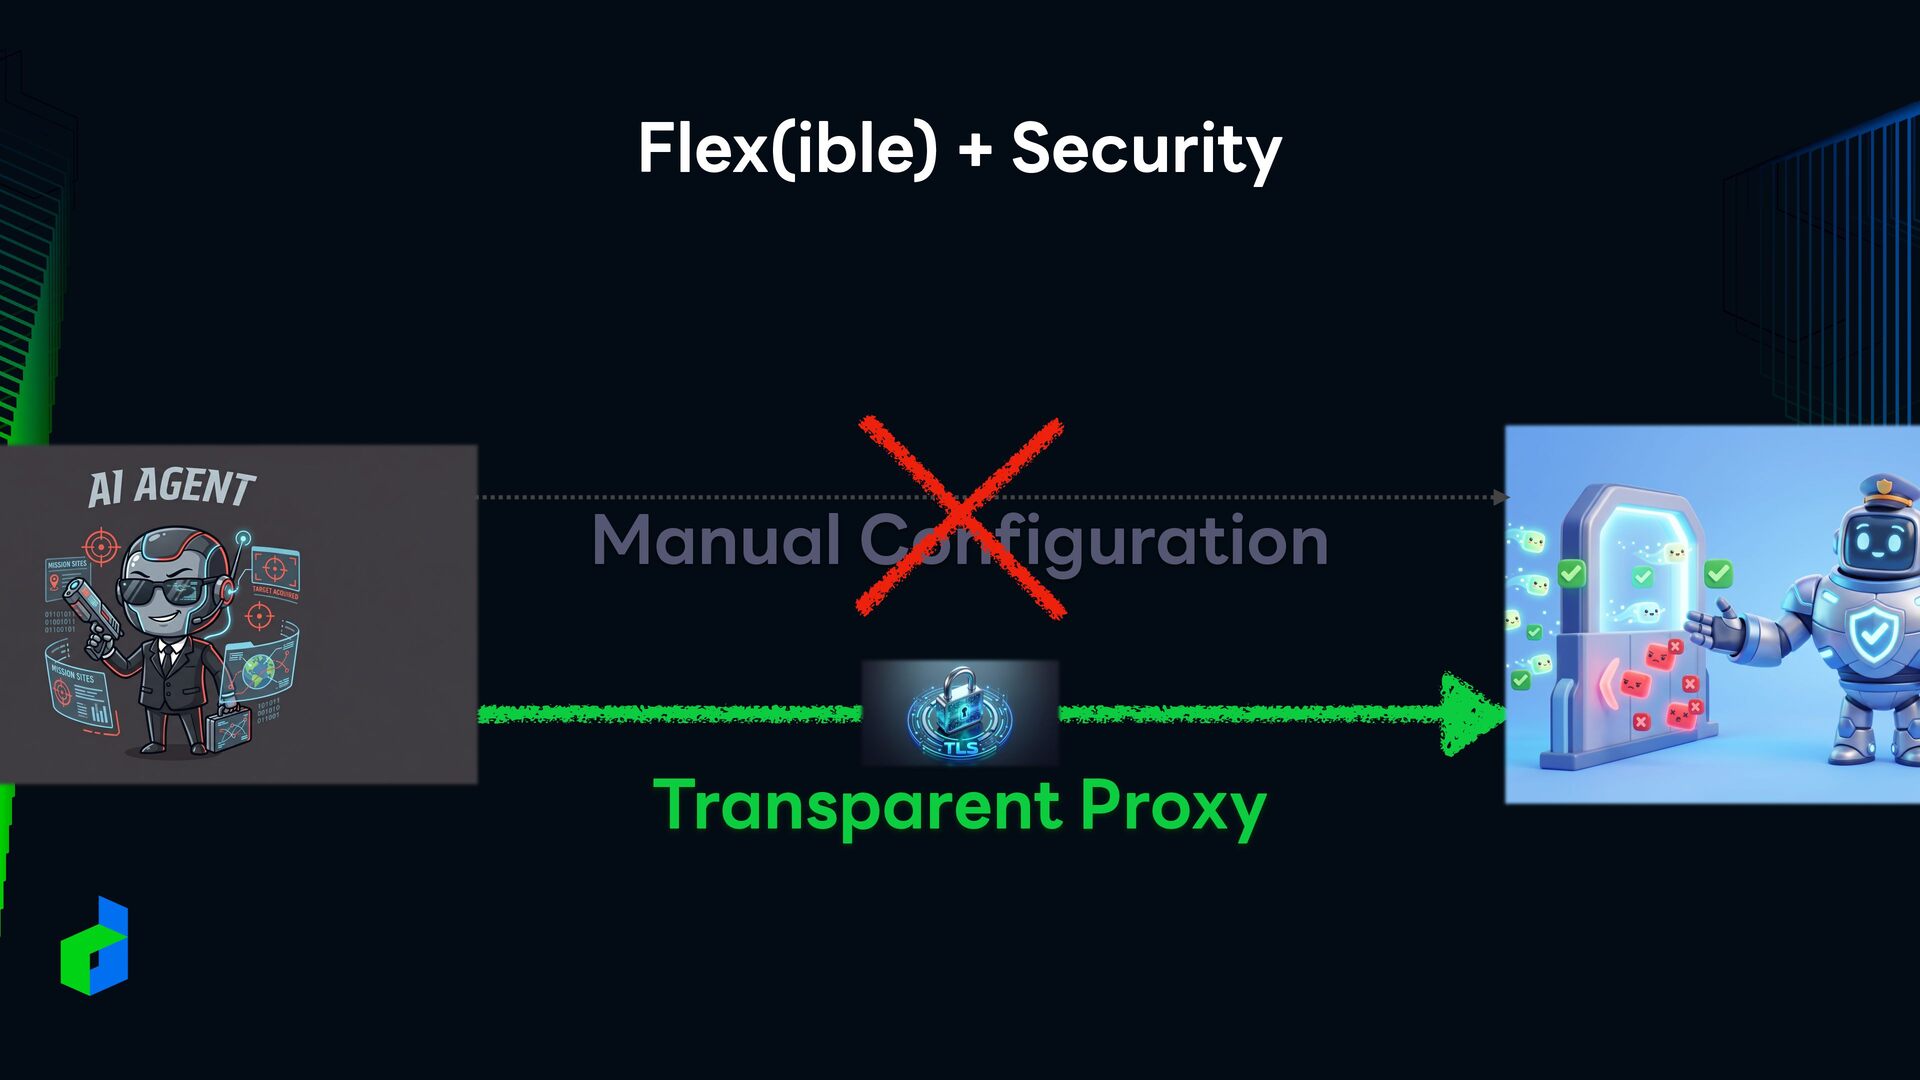
    TCP/443 - HTTPS CONNECT Method TLS inspection $ curl -v --proxy egress-proxy:10000 GOST https://deb.debian.org nftables Go Simple Tunnel redirect tra c https://github.com/go-gost/gost TCP/80 - HTTP Transparent Proxy ffi HTTP
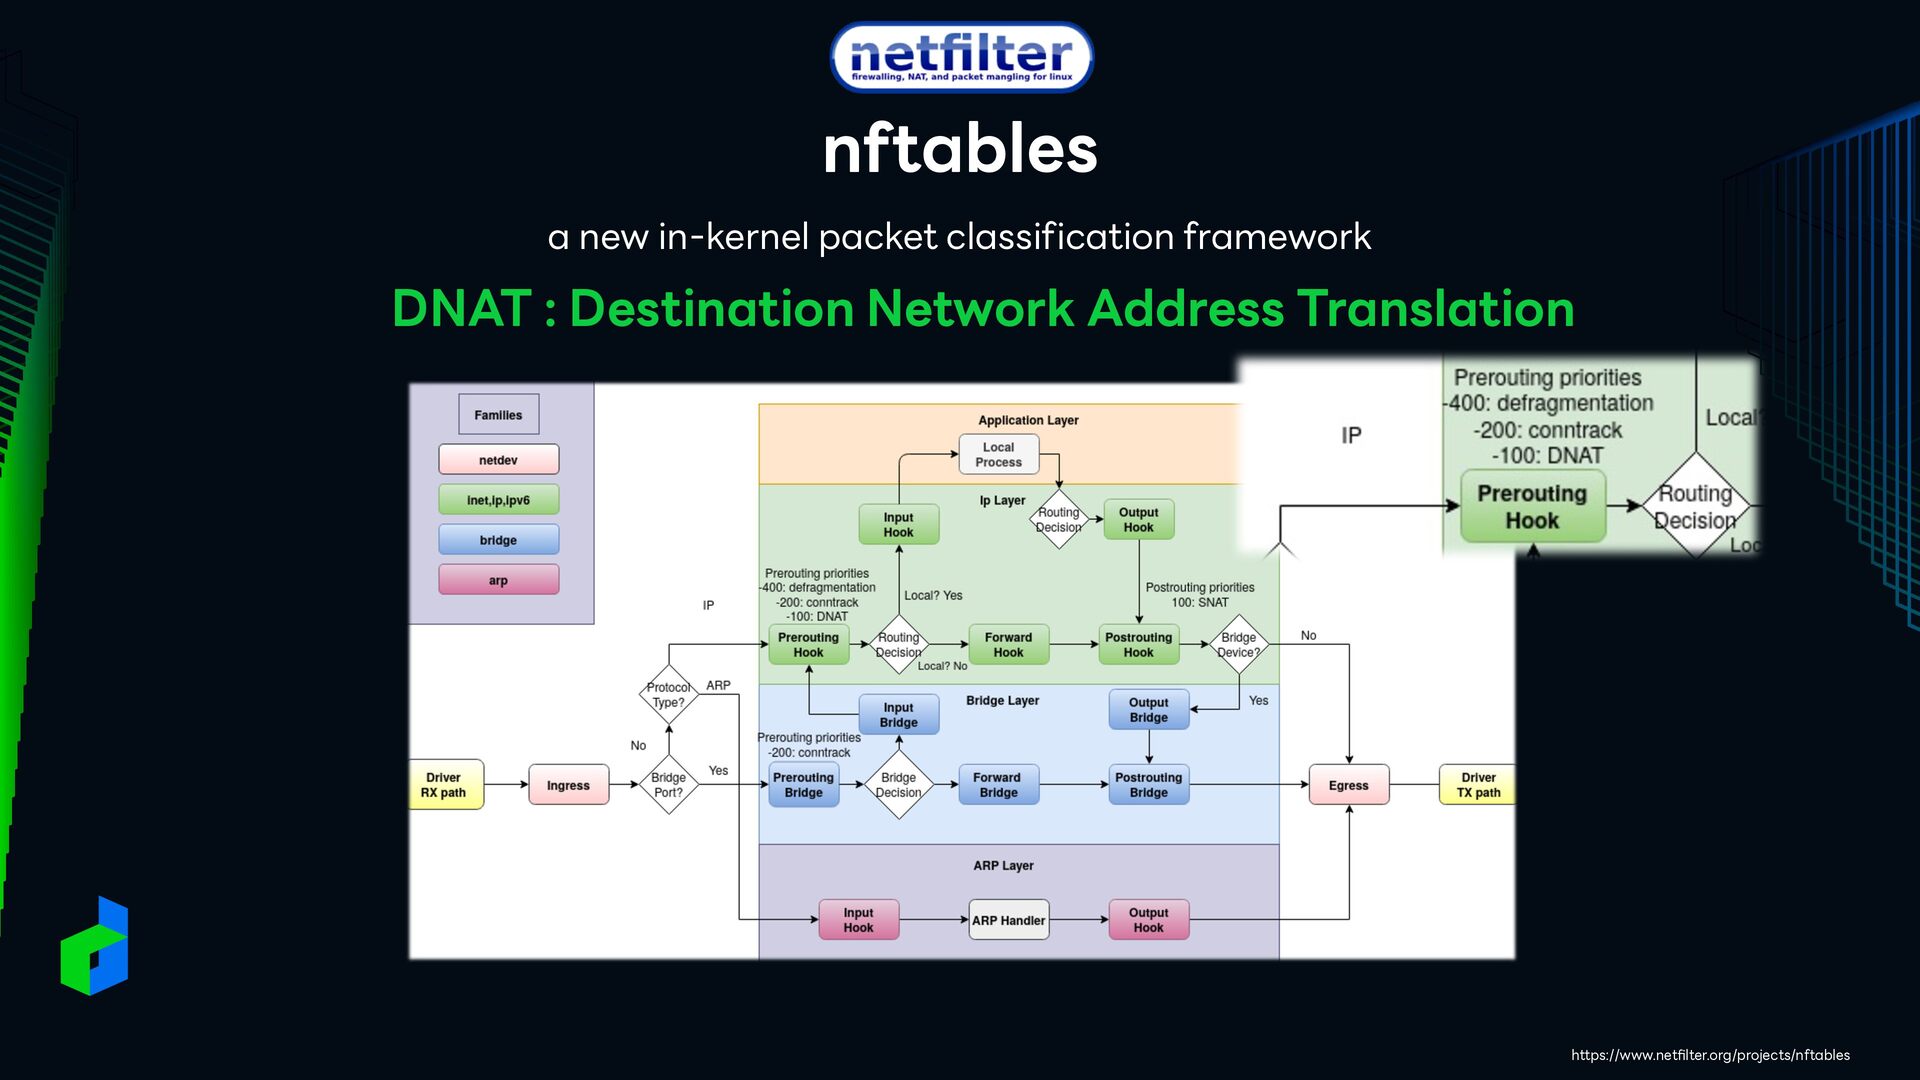
  8. nftables a new in-kernel packet classification framework DNAT : Destination

    Network Address Translation fi https://www.net lter.org/projects/nftables
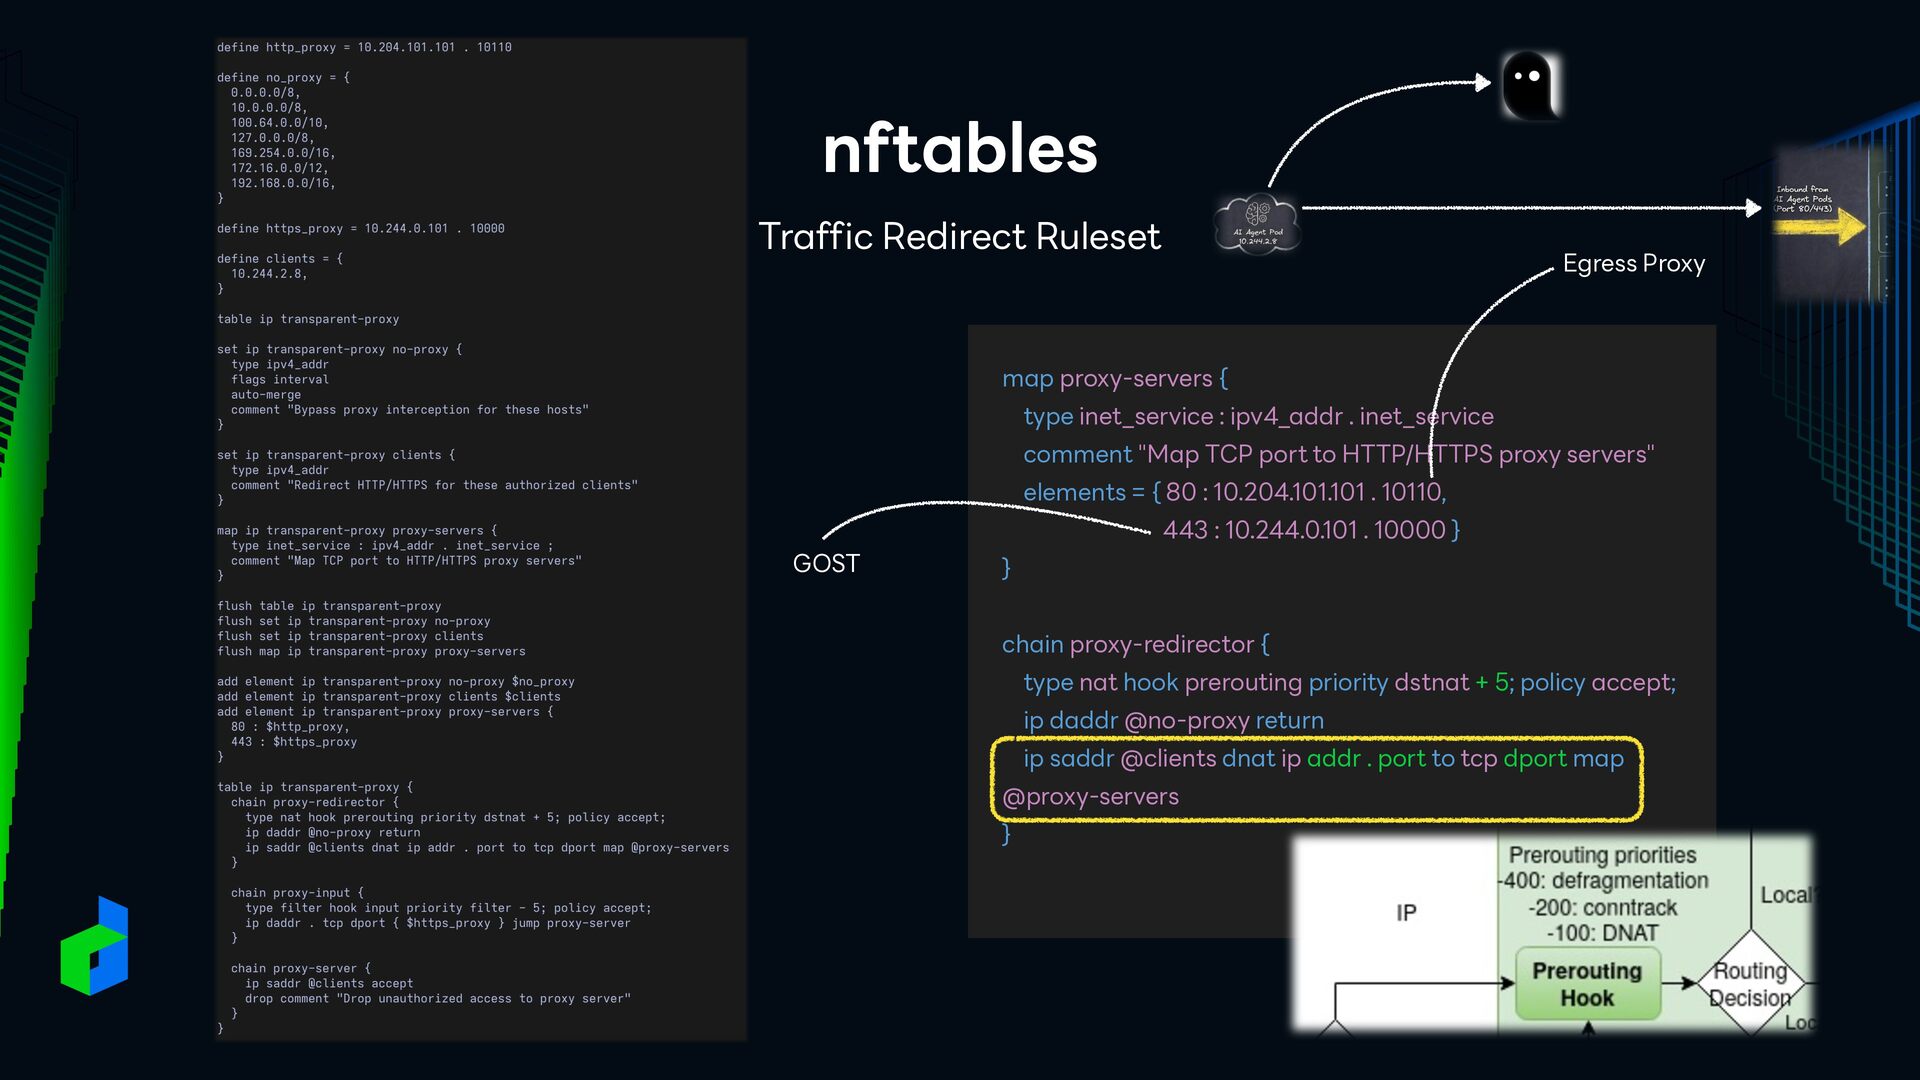
  9. nftables Traffic Redirect Ruleset Egress Proxy map proxy-servers { type

    inet_service : ipv4_addr . inet_service comment "Map TCP port to HTTP/HTTPS proxy servers" elements = { 80 : 10.204.101.101 . 10110, GOST } 443 : 10.244.0.101 . 10000 } chain proxy-redirector { type nat hook prerouting priority dstnat + 5; policy accept; ip daddr @no-proxy return ip saddr @clients dnat ip addr . port to tcp dport map @proxy-servers }
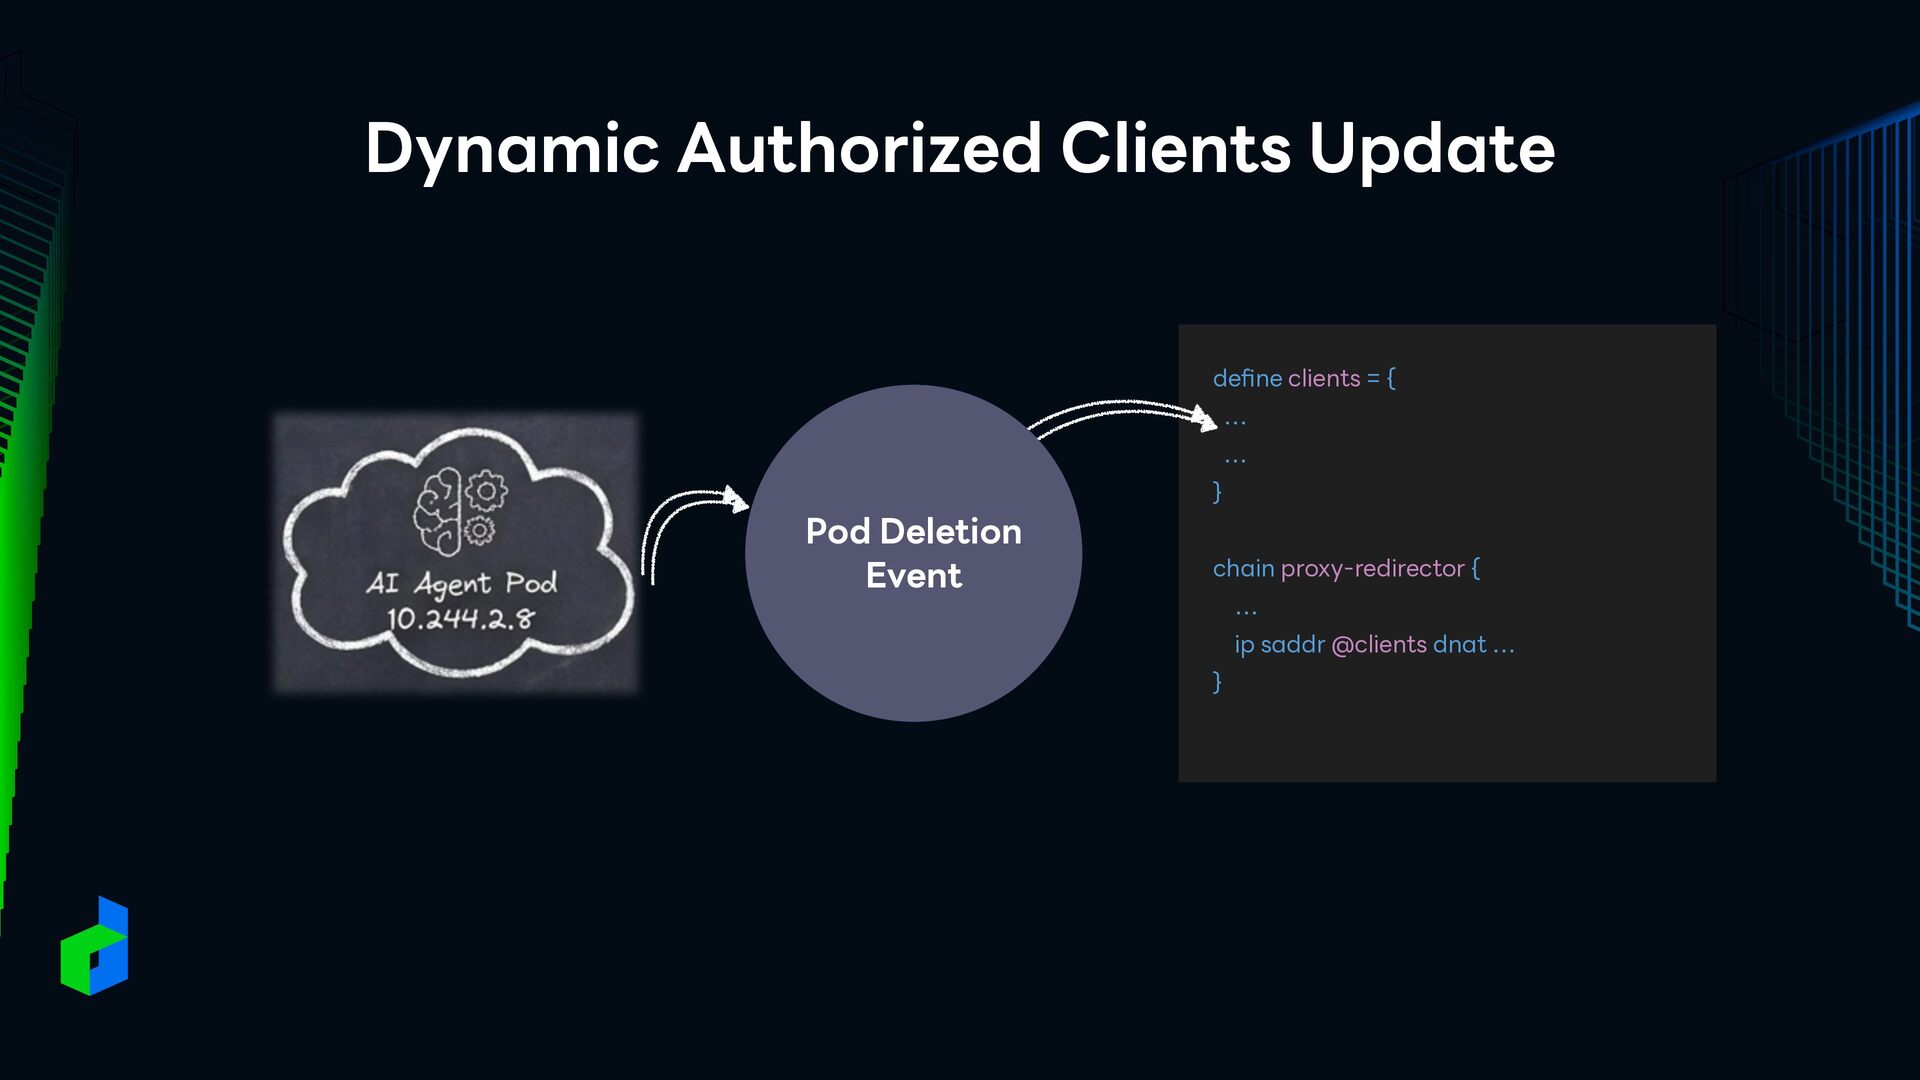
  10. Dynamic Authorized Clients Update de ne clients = { 10.244.2.8,

    … … Pod Pod Creation Deletion Event }… } chain proxy-redirector { chain … proxy-redirector { … saddr @clients dnat … ip } ip saddr @clients dnat … fi fi fi }
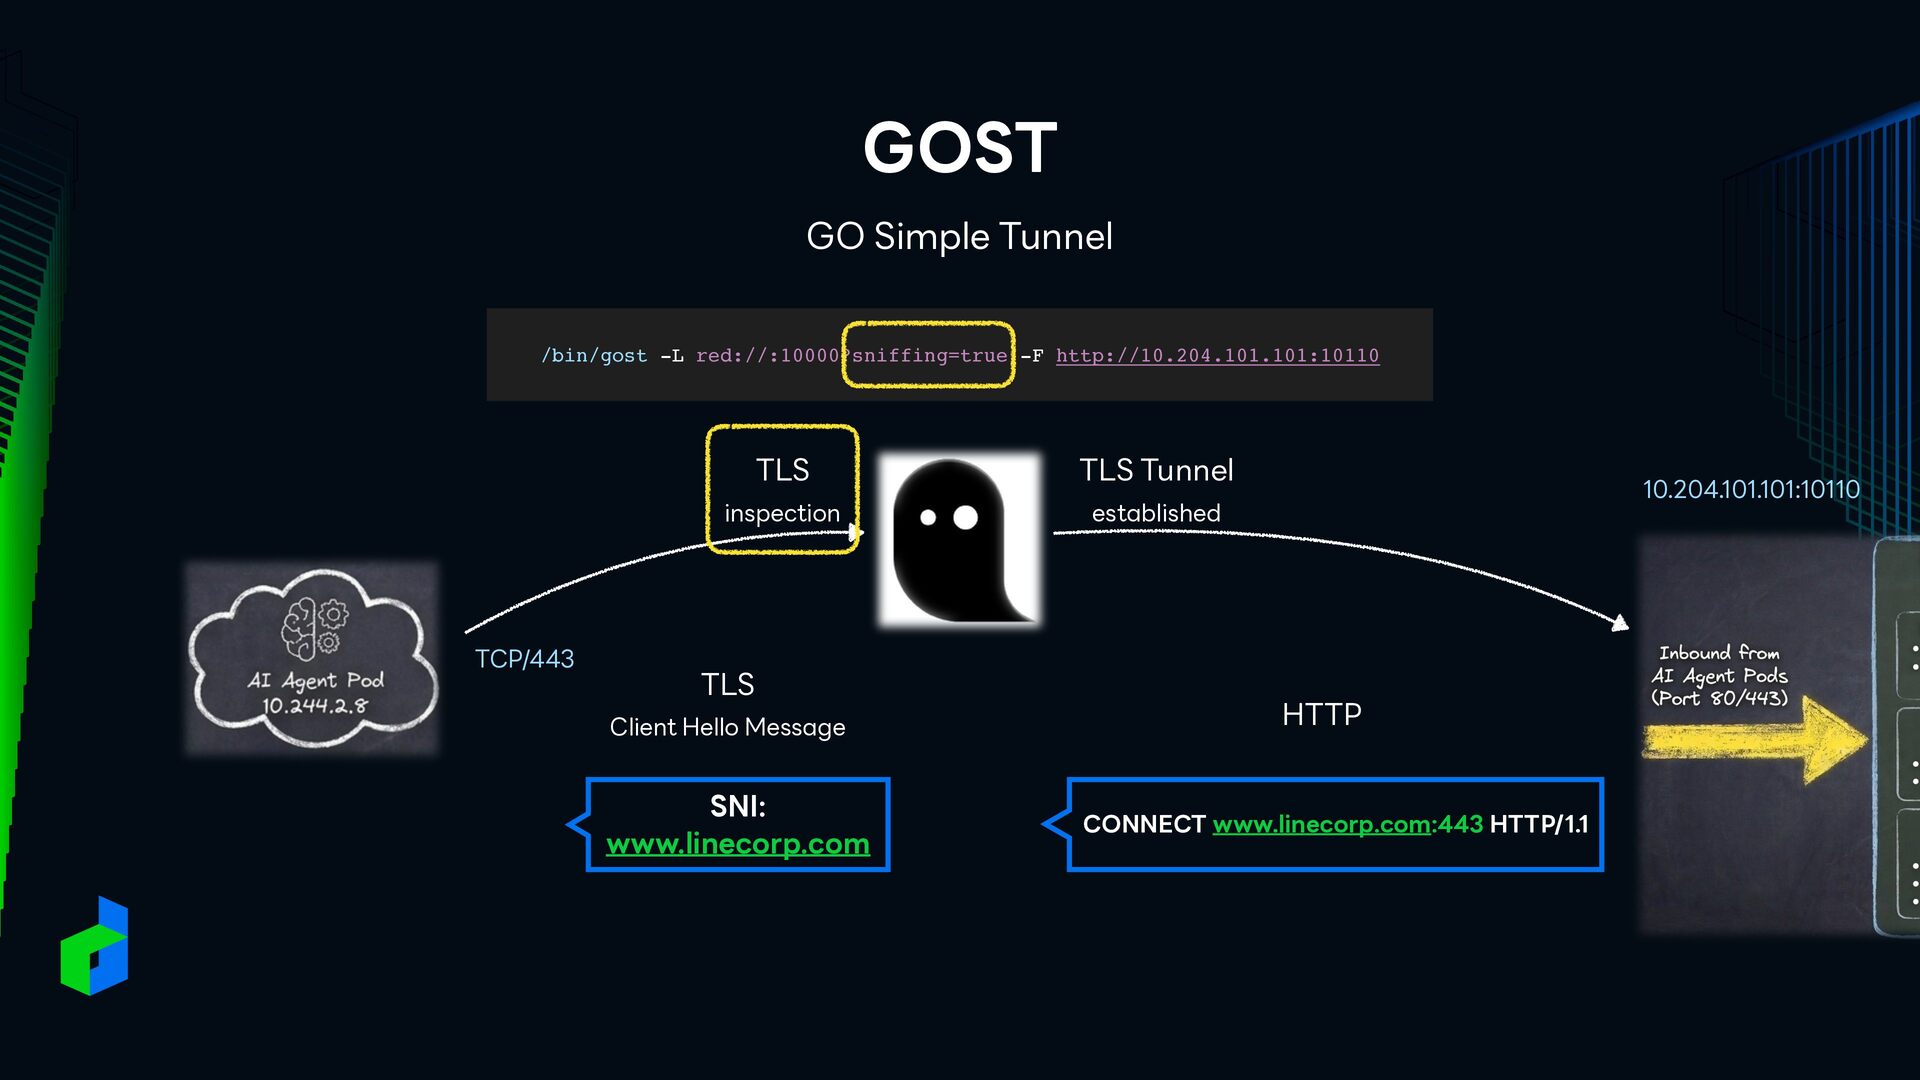
  11. GOST GO Simple Tunnel /bin/gost -L red://:10000?sniffing=true -F http://10.204.101.101:10110 TLS

    inspection TCP/443 TLS Client Hello Message SNI: www.linecorp.com TLS Tunnel 10.204.101.101:10110 established HTTP CONNECT www.linecorp.com:443 HTTP/1.1
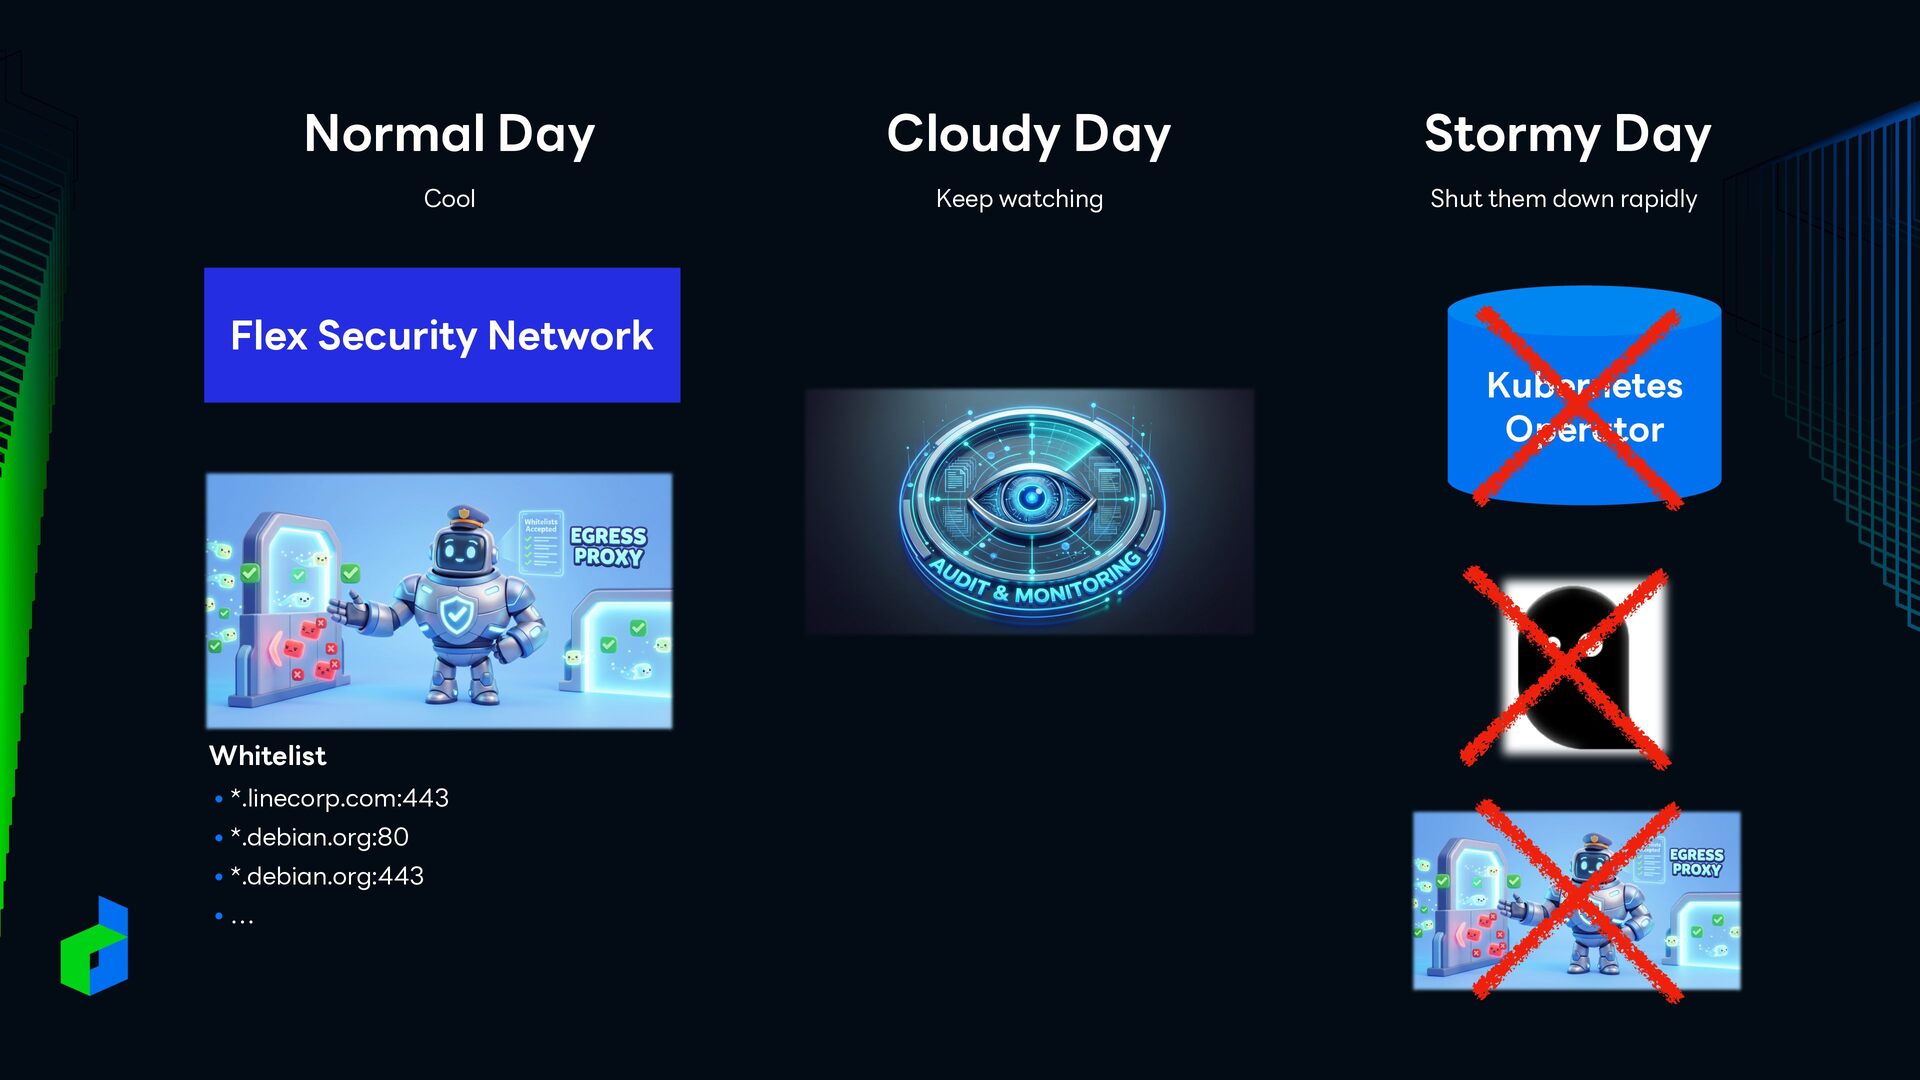
  12. Normal Day Cloudy Day Stormy Day Cool Keep watching Shut

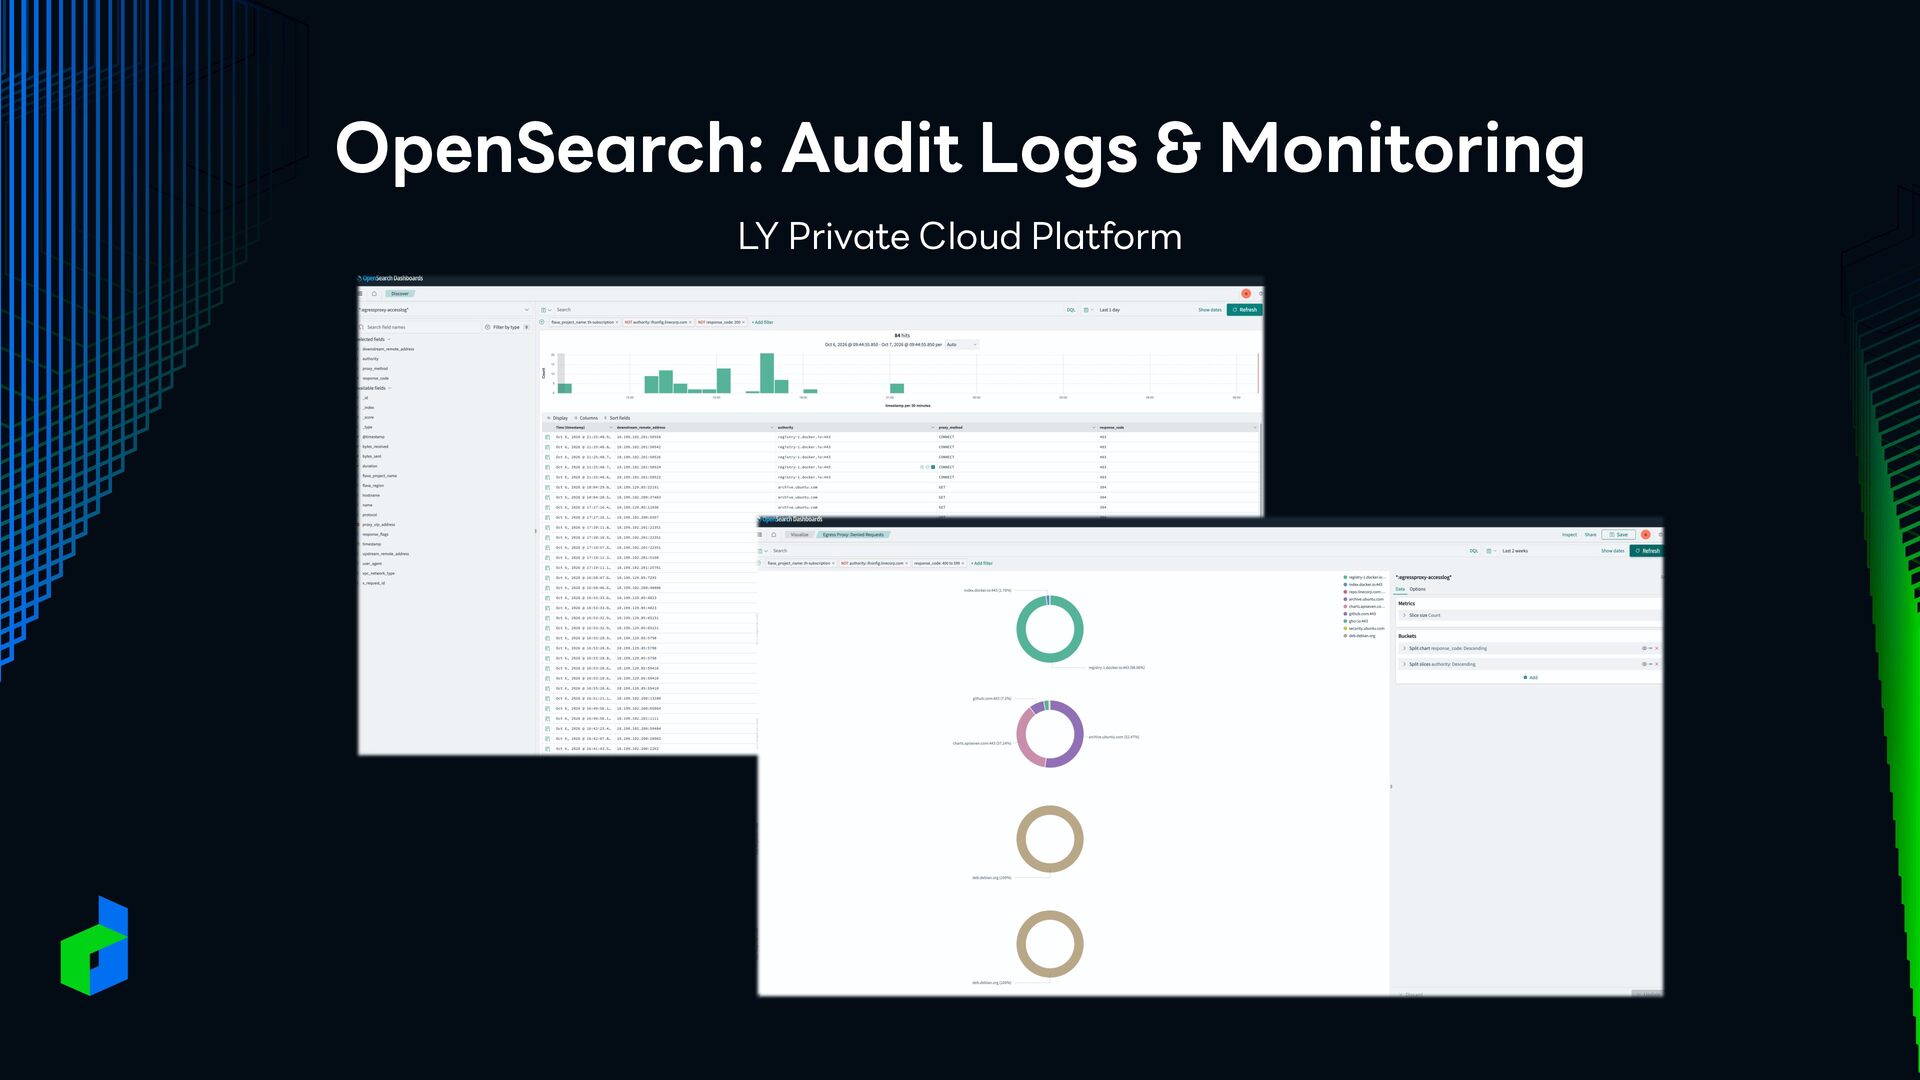
    them down rapidly Flex Security Network Whitelist • *.linecorp.com:443 • *.debian.org:80 • *.debian.org:443 •… Kubernetes Operator

More Decks by LINE Developers Thailand

Other Decks in Technology