Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Threat Intel 101 - Thotcon 0x8

Threat Intel 101 - Thotcon 0x8

Threat Intel is the new magic buzzword for what separates one vendor's product from another. However, Threat Intel is as nebulous and mysterious as ever, because vendors hide what it is behind claims it is their Secret Sauce. Threat Intel is a valuable part of any Incident Reponder's arsenal, though the bad actors are making better use of it that we are. This talk is designed to discuss what the world believes Threat Intel means, what it should mean to you, where to get it, and how to find value in it.

Avatar for M4n_in_Bl4ck

M4n_in_Bl4ck

May 22, 2017

Other Decks in Technology

Transcript

  1. M4N_IN_BL4CK • Ten years in InfoSec • Worked with/for companies

    with 3 to 10,000+ employees • Experience in hospitality, manufacturing, retail, technology and financial industries • Current focus: Incident response and threat intelligence
  2. WHAT IS THE CLOUD? 1. A network of storage and

    services designed to minimize cost and maximize... 2. Someone else’s servers
  3. WHAT IS INTELLIGENCE? 1. Nefarious plans of evil; the plans,

    intentions or actions of a nation state; The Colonel’s 11 herbs and spices... 2. Someone else’s comms
  4. WHAT IS THREAT INTELLIGENCE? 1. A compilation of crowd-sourced and

    critically-analyzed info in near real time 2. Some System’s Logs
  5. WHERE CAN I GET THREAT INTEL? GOVERNMENTS Specific Partners and

    General Releases VENDORS Some sell feeds and some bake it in SHARING LISTS ISACS, STIX and TAXII Groups
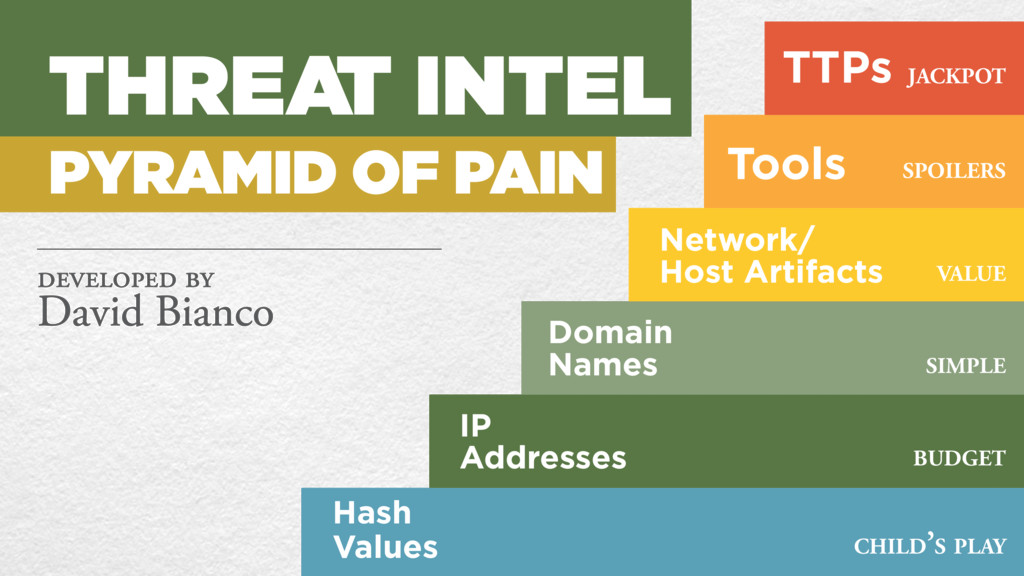
  6. THREAT INTEL PYRAMID OF PAIN developed by David Bianco TTPs

    Tools Network/ Host Artifacts Domain Names IP Addresses Hash Values jackpot spoilers value simple budget child’s play
  7. WHAT ARE VENDORS SELLING? THE GOOD Autoupdating, crowdsourced and contextualized

    information THE BAD Indicators of compromise—plain THE UGLY Out-of-context IOC Data
  8. THE GOOD NETWORK / HOST ARTIFACTS • Patterns in URL

    and URI • Host File changes TOOLS Compression Tools, Exploit Kits and Shells TTP How they pull it all together
  9. DOMAINS • CYBERCROOK.RU • TOTALLYSAFE.TK • CYPHERC0N.COM IP ADDRESSES •

    4.2.2.2 • 147.237.0.71 • 127.0.0.1 HASH VALUES • MD5 • SHA-1 • Malware changes? Never. THE BAD
  10. LACK OF CONTEXT MALICIOUS IP • Vendor included IOC showing

    127.0.0.1 malicious WHAT’S A SUBDOMAIN? • S.YIMG.com Hacked • Vendor blocked YIMG.com THE UGLY
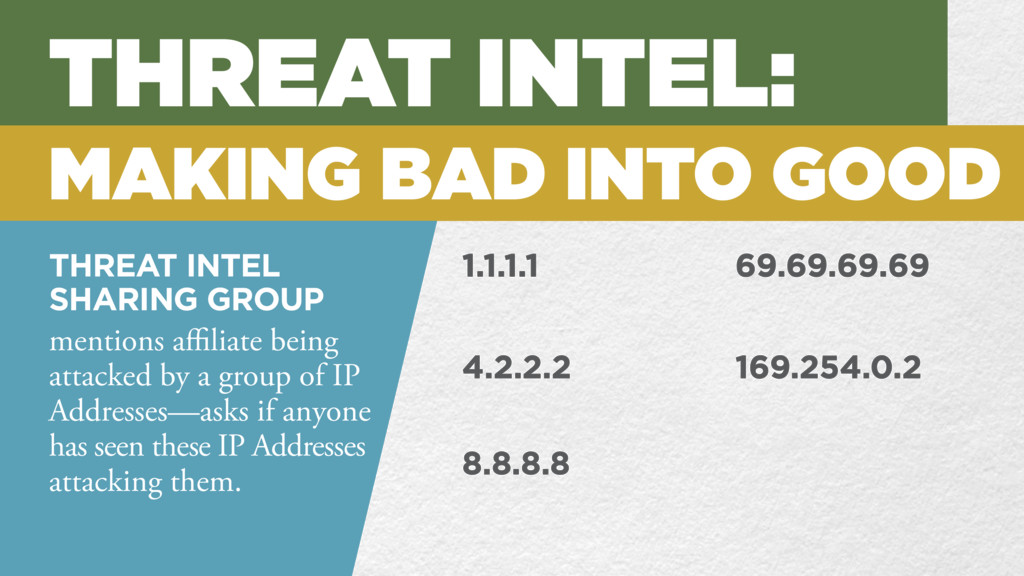
  11. 1.1.1.1 4.2.2.2 8.8.8.8 69.69.69.69 169.254.0.2 THREAT INTEL: MAKING BAD INTO

    GOOD THREAT INTEL SHARING GROUP mentions affiliate being attacked by a group of IP Addresses—asks if anyone has seen these IP Addresses attacking them.
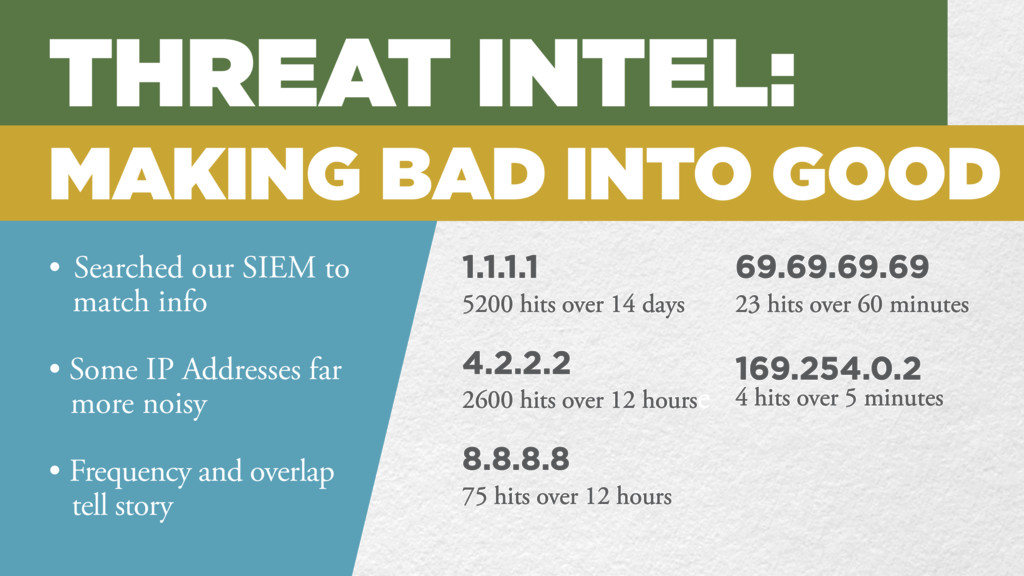
  12. THREAT INTEL: MAKING BAD INTO GOOD • Searched our SIEM

    to match info • Some IP Addresses far more noisy • Frequency and overlap tell story 1.1.1.1 5200 hits over 14 days 4.2.2.2 2600 hits over 12 hourse 8.8.8.8 75 hits over 12 hours 69.69.69.69 23 hits over 60 minutes 169.254.0.2 4 hits over 5 minutes
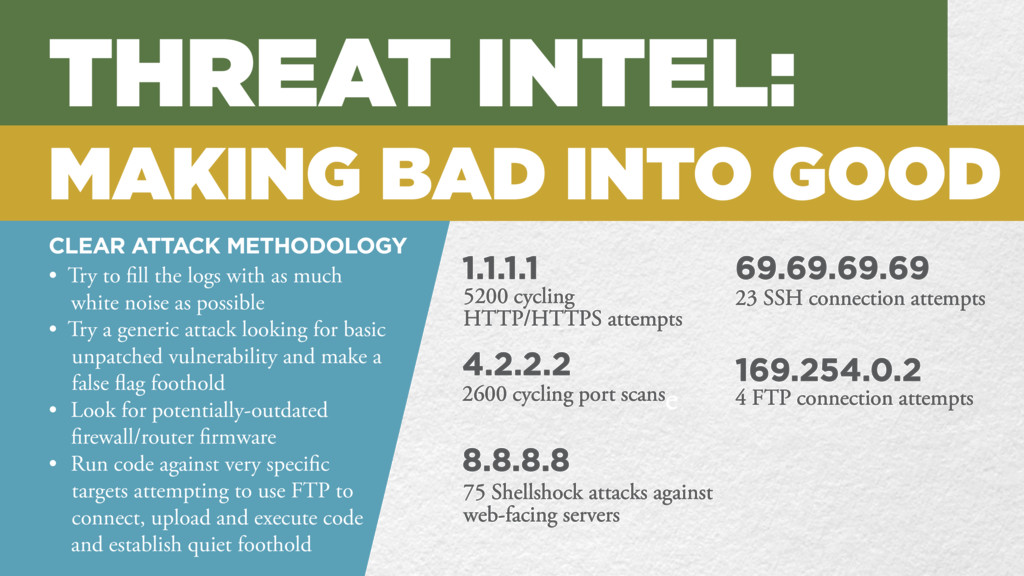
  13. 75 Shellshock attacks against web-facing servers 5200 cycling HTTP/HTTPS attempts

    CLEAR ATTACK METHODOLOGY • Try to fill the logs with as much white noise as possible • Try a generic attack looking for basic unpatched vulnerability and make a false flag foothold • Look for potentially-outdated firewall/router firmware • Run code against very specific targets attempting to use FTP to connect, upload and execute code and establish quiet foothold THREAT INTEL: MAKING BAD INTO GOOD 1.1.1.1 4.2.2.2 2600 cycling port scanse 8.8.8.8 69.69.69.69 23 SSH connection attempts 169.254.0.2 4 FTP connection attempts
  14. 1. Look for an ISAC List in your industry 2.

    Look at vendor offerings 3. Review Basic Hunting Ideology - SANS Threat Hunting Summits WHERE DO I GET MORE?
  15. “Before I refuse to take your questions, I have an

    opening statement.” –Ronald Reagan A CLOSING WORD