Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Hacking OAuth 2.0
Search
Marcin Hoppe
October 13, 2019
Programming
63
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Hacking OAuth 2.0
Marcin Hoppe
October 13, 2019
More Decks by Marcin Hoppe
See All by Marcin Hoppe
Przepraszam, czy można?
marcinhoppe
0
37
Problemy z JSON Web Tokens ... i garść rozwiązań
marcinhoppe
0
71
JSON Web Tokens. Problemy i rozwiązania
marcinhoppe
0
150
Other Decks in Programming
See All in Programming
[2026-09-26]空論ジェネリックプロセス~テスト資産とAIで紡ぐ、再現可能なパフォーマンスチューニングの話~
tosite
0
270
なぜCTOを降りてFDEを選んだのか?〜なぜプロダクト企業がFDEで顧客の現場に踏み込むのか〜
gonta
1
210
Atomic Design, Enforced: Scaling Mobile Design Systems (next.app devCon / droidCon Berlin 2026)
steliosf
PRO
0
170
Domain-Driven Transformation
hschwentner
2
2.3k
sbt 2.0: takeoff
eed3si9n
0
160
Agentic Software Factoryに、すごく賢いIF文を。 / super smart IF statement into the Agentic Software Factory.
rkaga
8
2.2k
AWSに止められる覚悟してますか?
morizo_1984
2
530
AIに “答え“を書かせるのを やめてみた
___akari11
0
120
動作中のプログラムの中身をリアルタイムに覗く / Realtime Debugger for CSharp with Roslyn
prota
1
1.9k
KiroのSpecで「五目並べ」を作ってみる
satoshi256kbyte
1
380
【加筆修正版】Laravel のアプリケーションをどこにデプロイするか #phpcon_ehime
akase244
0
150
自サークルのIdPからログアウトできるようになるまで
taiseiue
1
140
Featured
See All Featured
SEO Brein meetup: CTRL+C is not how to scale international SEO
lindahogenes
2
2.9k
Digital Projects Gone Horribly Wrong (And the UX Pros Who Still Save the Day) - Dean Schuster
uxyall
1
3.4k
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Lightning talk: Run Django tests with GitHub Actions
sabderemane
0
300
BBQ
matthewcrist
90
10k
B2B Lead Gen: Tactics, Traps & Triumph
marketingsoph
1
280
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
2
360
Improving Core Web Vitals using Speculation Rules API
sergeychernyshev
21
1.7k
Sharpening the Axe: The Primacy of Toolmaking
bcantrill
46
3k
How to Get Subject Matter Experts Bought In and Actively Contributing to SEO & PR Initiatives.
livdayseo
0
220
4 Signs Your Business is Dying
shpigford
187
23k
Reflections from 52 weeks, 52 projects
jeffersonlam
356
22k
Transcript
Hacking OAuth 2.0 @marcin_hoppe
Past, present, and future @marcin_hoppe ... told by one security
team
IDaaS Identity protocols Product security team @marcin_hoppe
Protocols and standards @marcin_hoppe PKCE OIDC OAuth 2.0 SAML JWT
WS-Federation
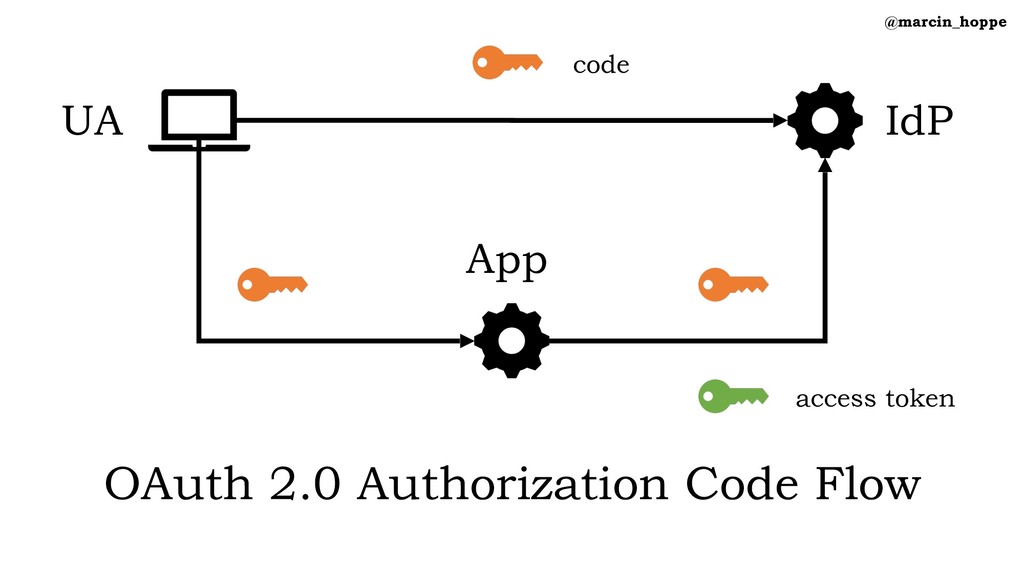
@marcin_hoppe OAuth 2.0 Authorization Code Flow IdP App UA code
access token
How to test for security flaws? @marcin_hoppe
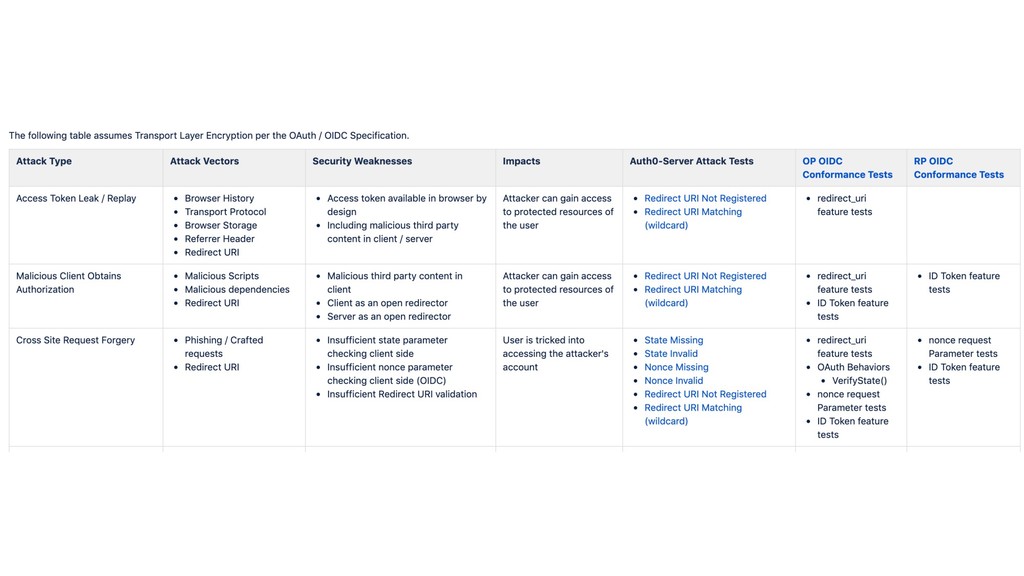
Existing resources Security considerations in RFCs Threat model RFC and
security BCP Formal security model @marcin_hoppe
Good enough? @marcin_hoppe
No, but a great start! @marcin_hoppe
OAuth attack library Structured attack documentation Useful for offensive security
crowd Automation! @marcin_hoppe
None
Meanwhile in the real world... @marcin_hoppe
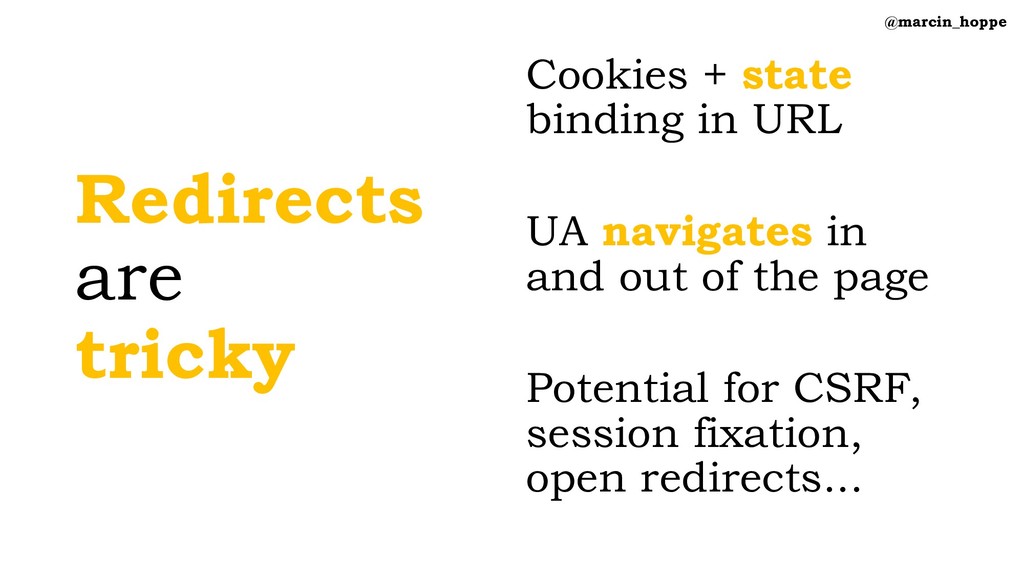
Redirects are tricky Cookies + state binding in URL UA
navigates in and out of the page Potential for CSRF, session fixation, open redirects... @marcin_hoppe
Existing resources are generic! @marcin_hoppe
None
None
None
None
None
None
None
None
Generic threat models do not cover this complexity! @marcin_hoppe
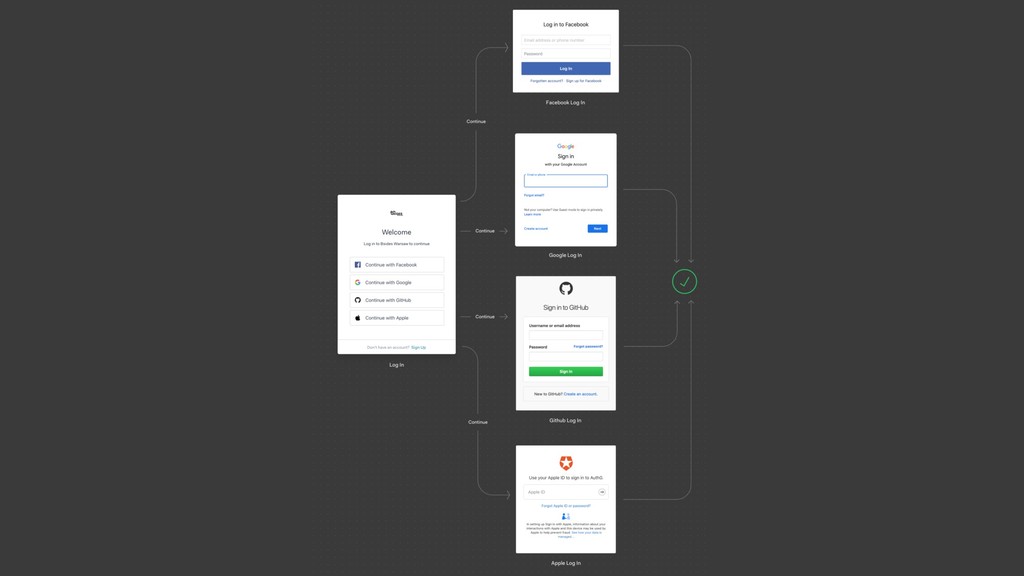
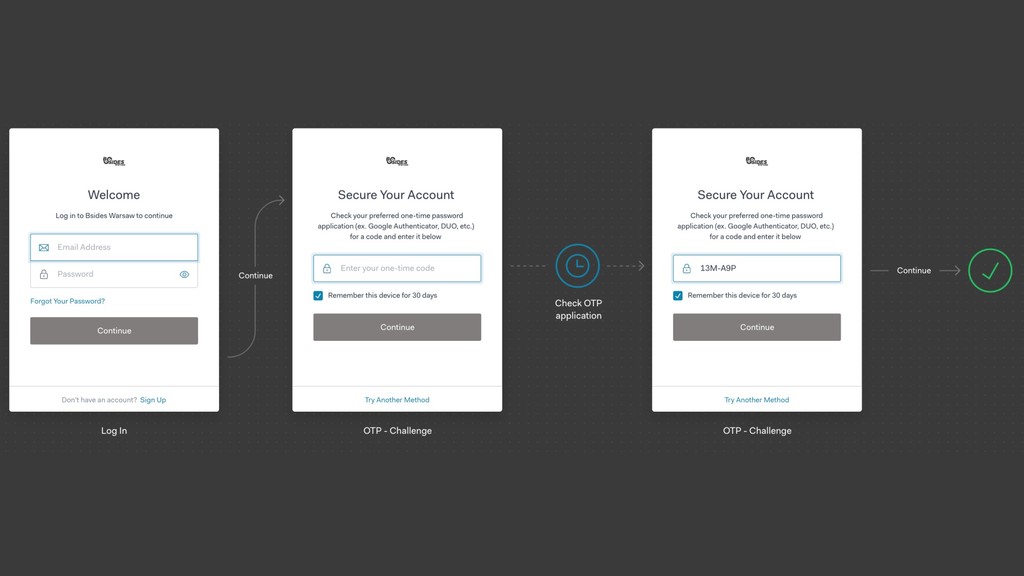
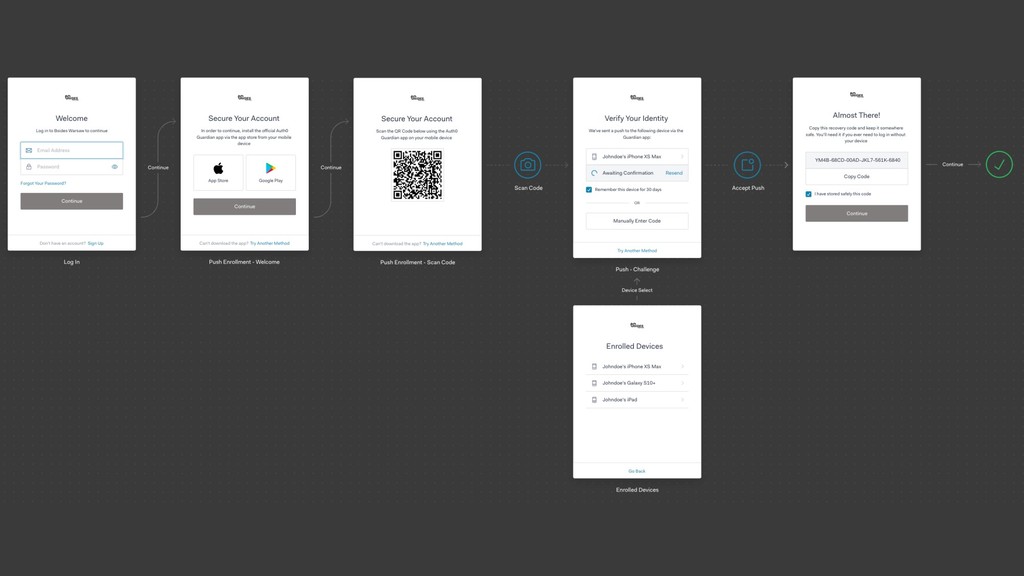
Protocols as FSMs Each prompt is a state Only some
state transitions allowed Security properties for states and transitions @marcin_hoppe
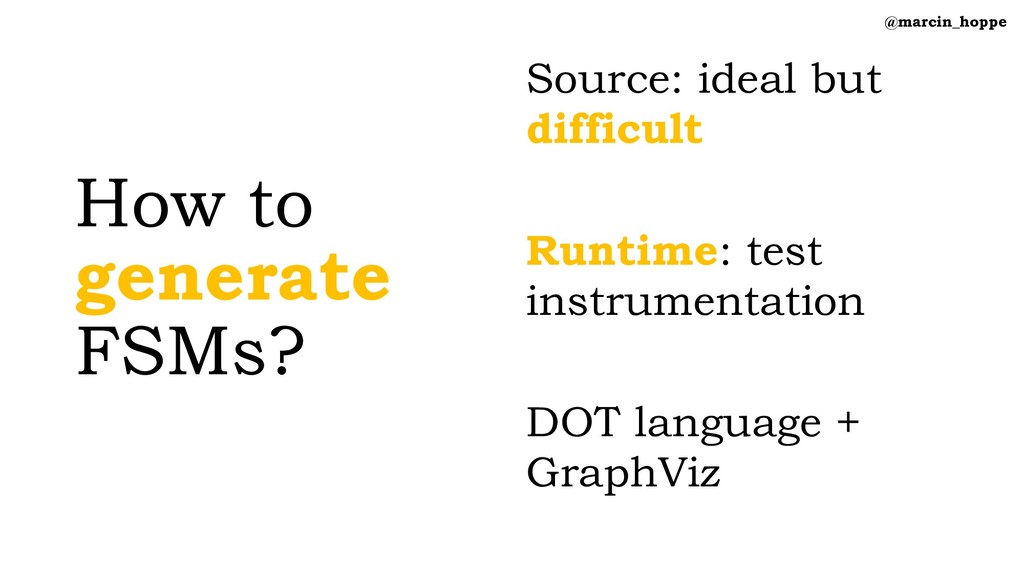
How to generate FSMs? Source: ideal but difficult Runtime: test
instrumentation DOT language + GraphViz @marcin_hoppe
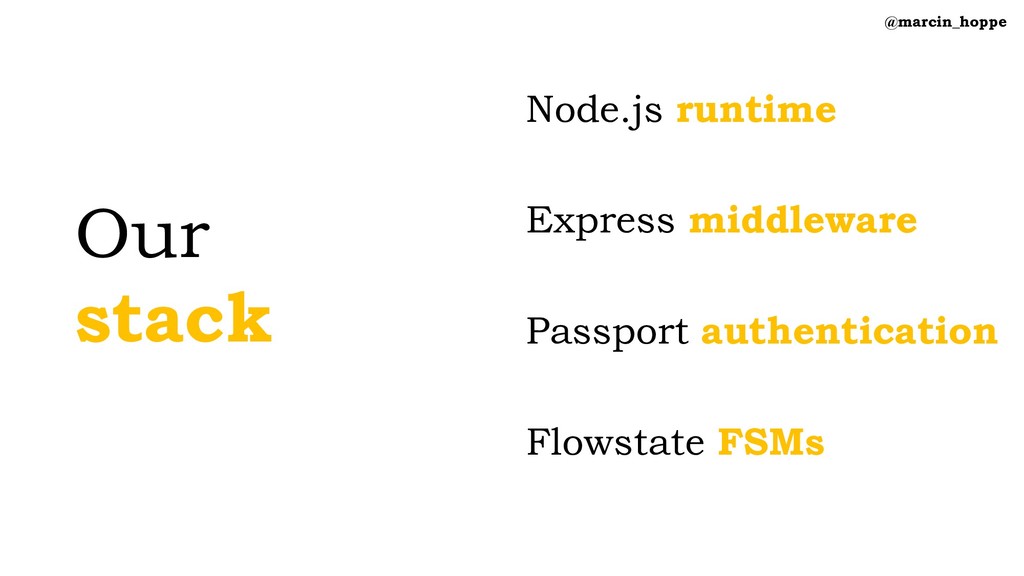
Our stack Node.js runtime Express middleware Passport authentication Flowstate FSMs
@marcin_hoppe
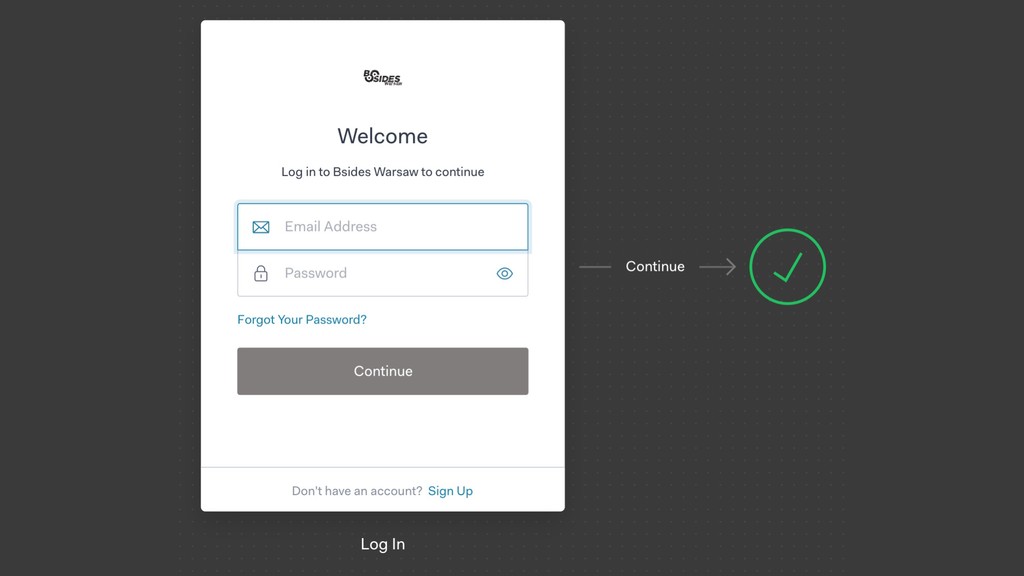
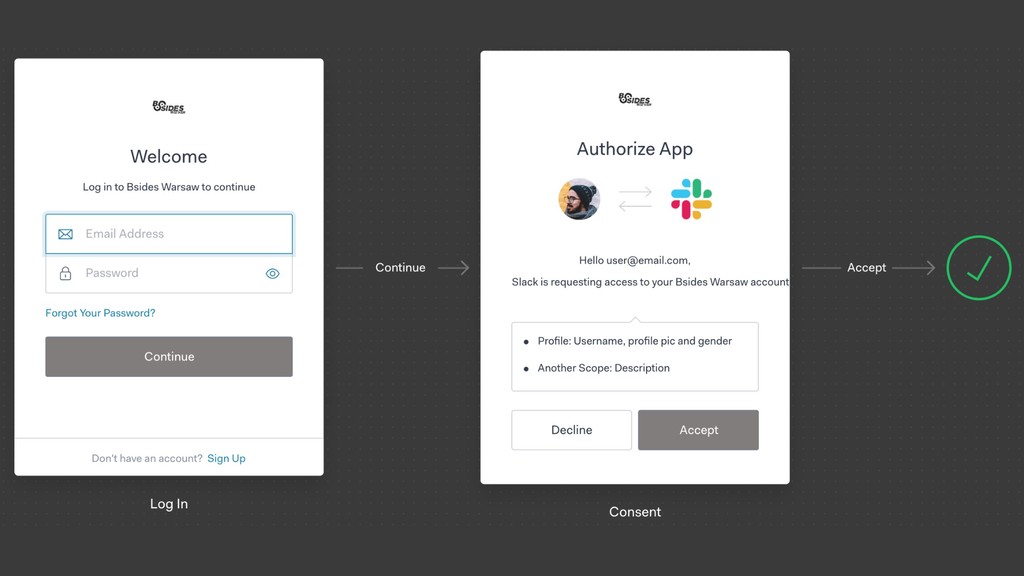
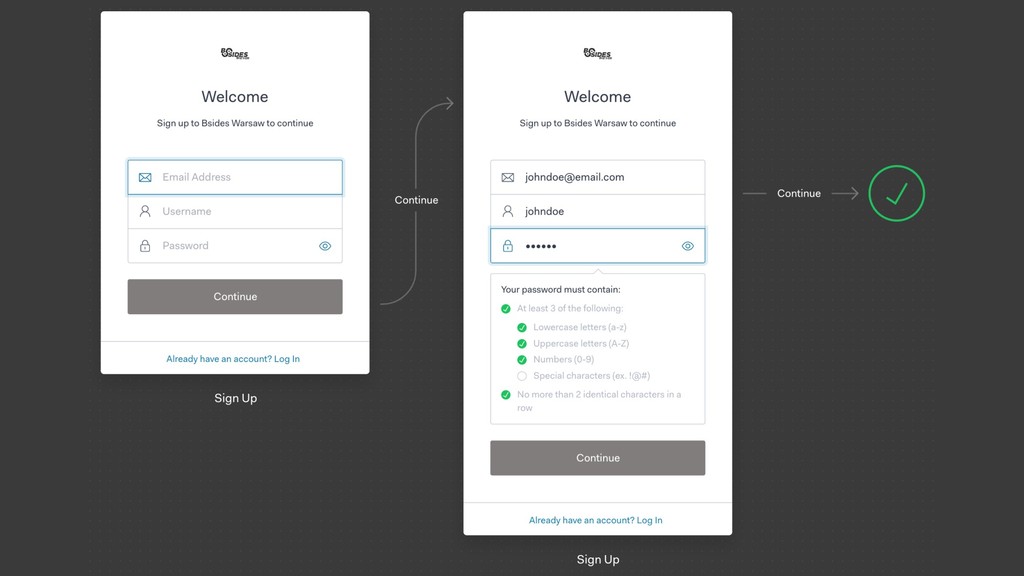
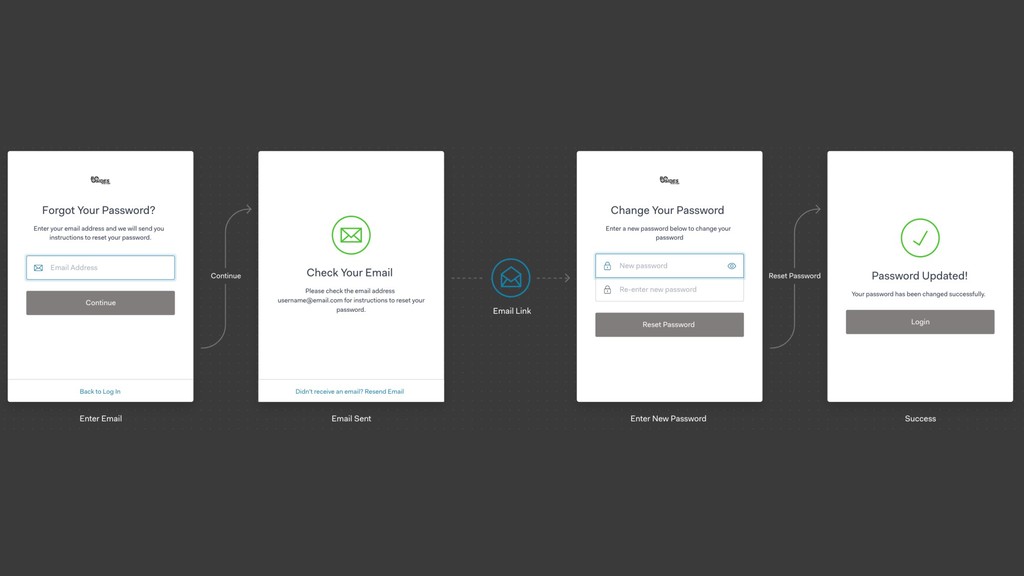
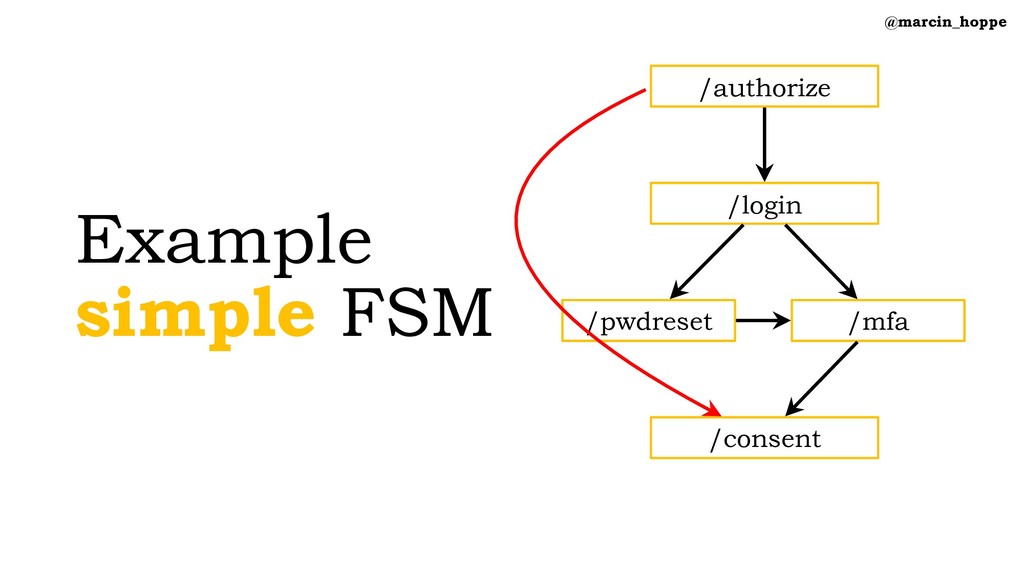
Example simple FSM @marcin_hoppe /authorize /login /mfa /pwdreset /consent
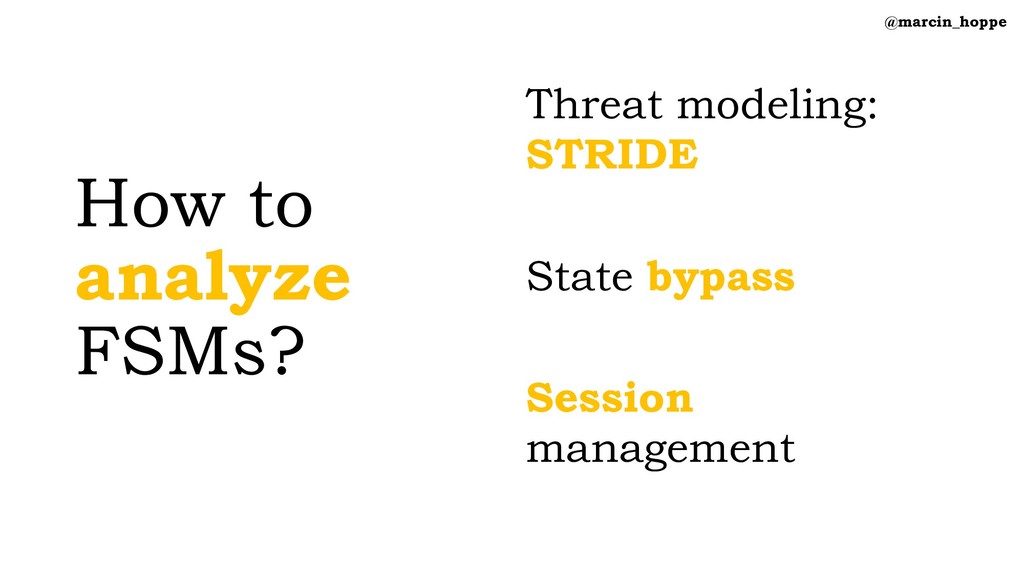
How to analyze FSMs? Threat modeling: STRIDE State bypass Session
management @marcin_hoppe
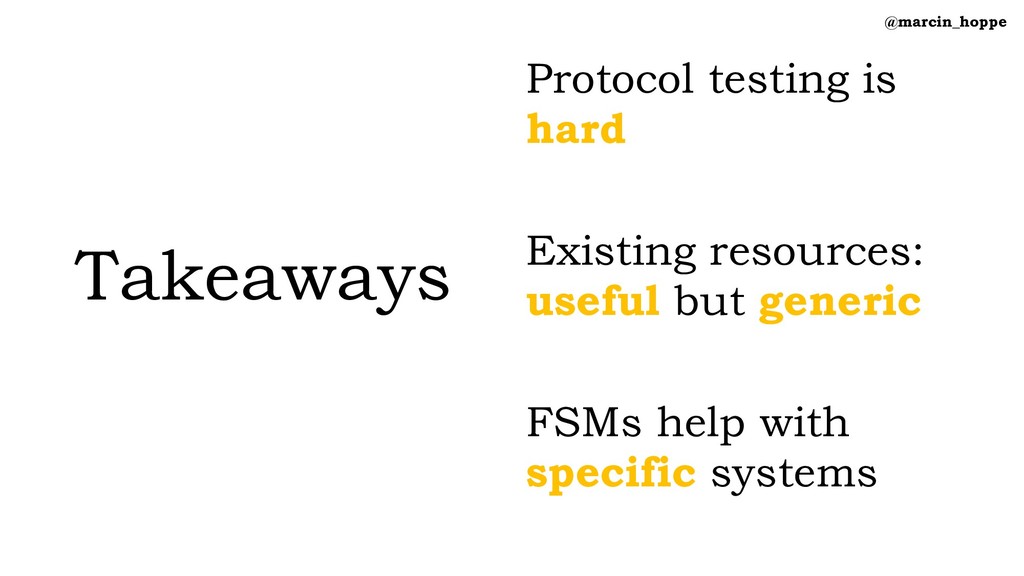
Takeaways Protocol testing is hard Existing resources: useful but generic
FSMs help with specific systems @marcin_hoppe
Marcin Hoppe Senior Manager Product Security Auth0 Security Working Group
Node.js Foundation Project Leader OWASP Serverless Top 10 marcin.hoppe @ auth0.com twitter.com/Marcin_Hoppe
Ask me anything! @marcin_hoppe


 marcinhoppe
 tosite
 gonta
 steliosf
 hschwentner
 eed3si9n
 rkaga
 morizo_1984
 ___akari11
 prota
 satoshi256kbyte
 akase244
 taiseiue
 lindahogenes
 uxyall
 eileencodes
 sabderemane
 matthewcrist
 marketingsoph
 helenjbeal
 sergeychernyshev
 bcantrill
 livdayseo
 shpigford
 jeffersonlam