and scale of AI. Govern Author policies once, enforce everywhere. Provision Handle data access requests automatically. Comply Monitor everything, all in one place.
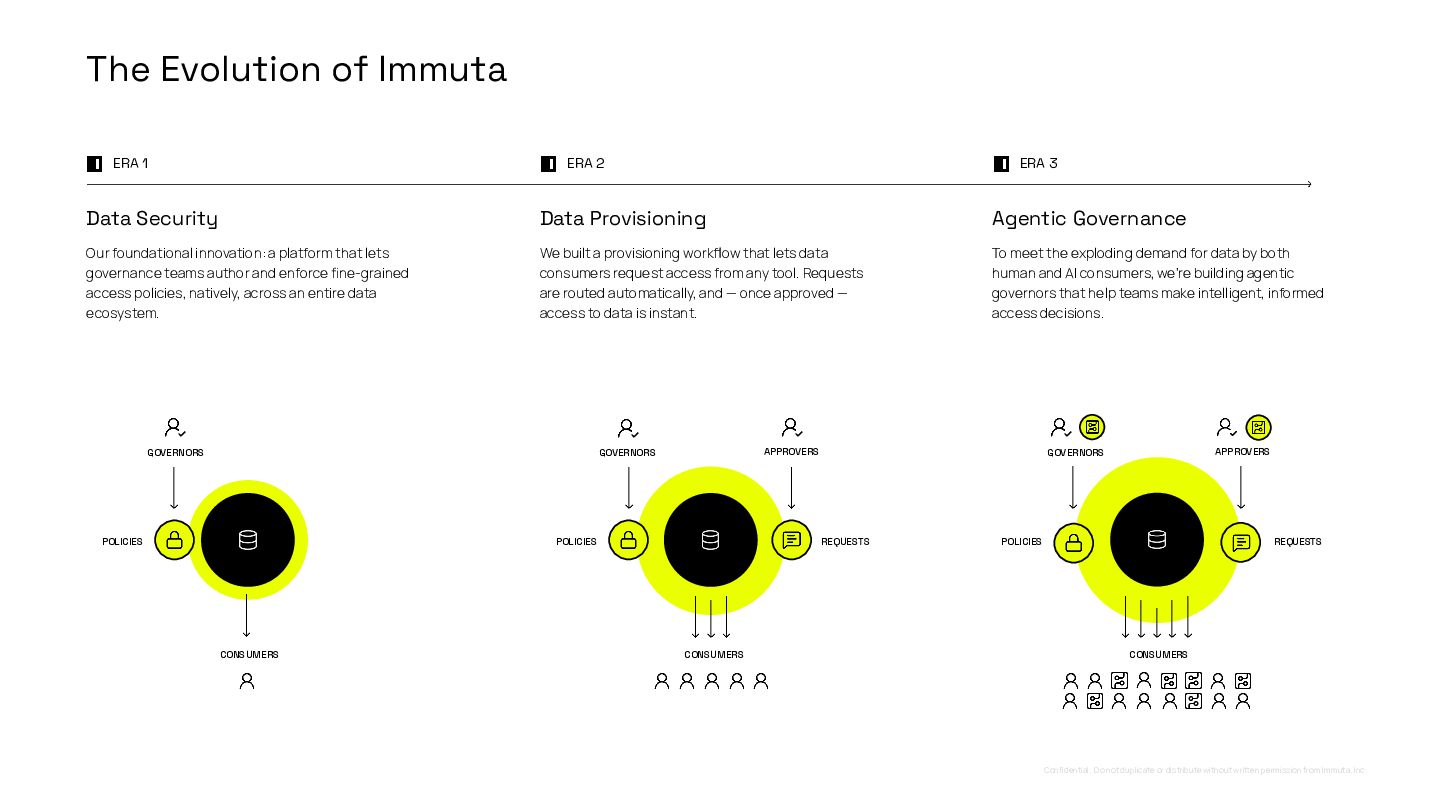
Data Security Data Provisioning Agentic Governance Our foundational innovation: a platform that lets governance teams author and enforce fine-grained access policies, natively, across an entire data ecosystem. We built a provisioning workflow that lets data consumers request access from any tool. Requests are routed automatically, and — once approved — access to data is instant. To meet the exploding demand for data by both human and AI consumers, we’re building agentic governors that help teams make intelligent, informed access decisions. APPROVERS GOVERNORS GOVERNORS POLICIES POLICIES CONSUMERS REQUESTS CONSUMERS APPROVERS GOVERNORS POLICIES REQUESTS CONSUMERS Confidential. Do not duplicate or distribute without wrien permission from Immuta, Inc.
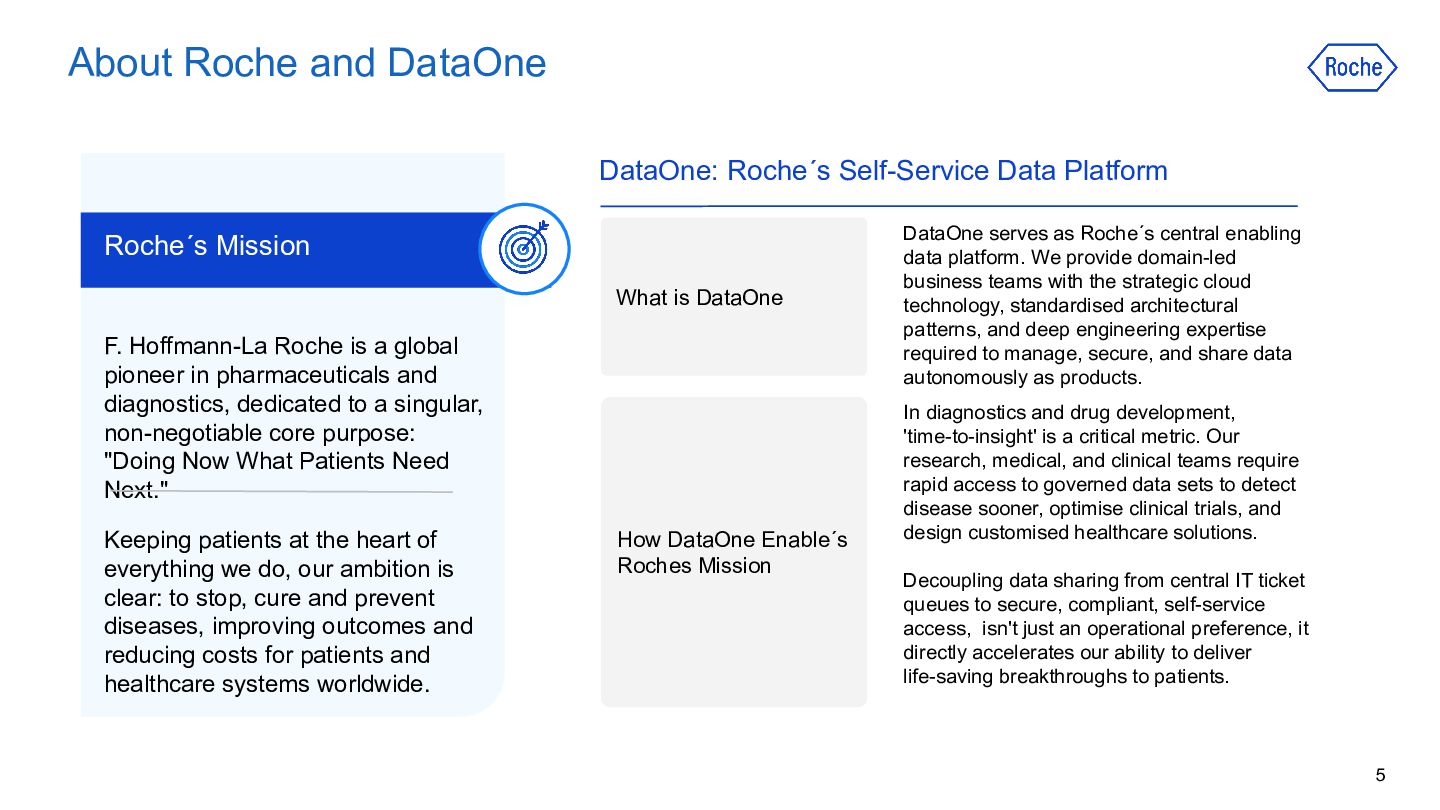
Mission What is DataOne F. Hoffmann-La Roche is a global pioneer in pharmaceuticals and diagnostics, dedicated to a singular, non-negotiable core purpose: "Doing Now What Patients Need Next." Keeping patients at the heart of everything we do, our ambition is clear: to stop, cure and prevent diseases, improving outcomes and reducing costs for patients and healthcare systems worldwide. How DataOne Enable´s Roches Mission DataOne serves as Roche´s central enabling data platform. We provide domain-led business teams with the strategic cloud technology, standardised architectural patterns, and deep engineering expertise required to manage, secure, and share data autonomously as products. In diagnostics and drug development, 'time-to-insight' is a critical metric. Our research, medical, and clinical teams require rapid access to governed data sets to detect disease sooner, optimise clinical trials, and design customised healthcare solutions. Decoupling data sharing from central IT ticket queues to secure, compliant, self-service access, isn't just an operational preference, it directly accelerates our ability to deliver life-saving breakthroughs to patients. 5
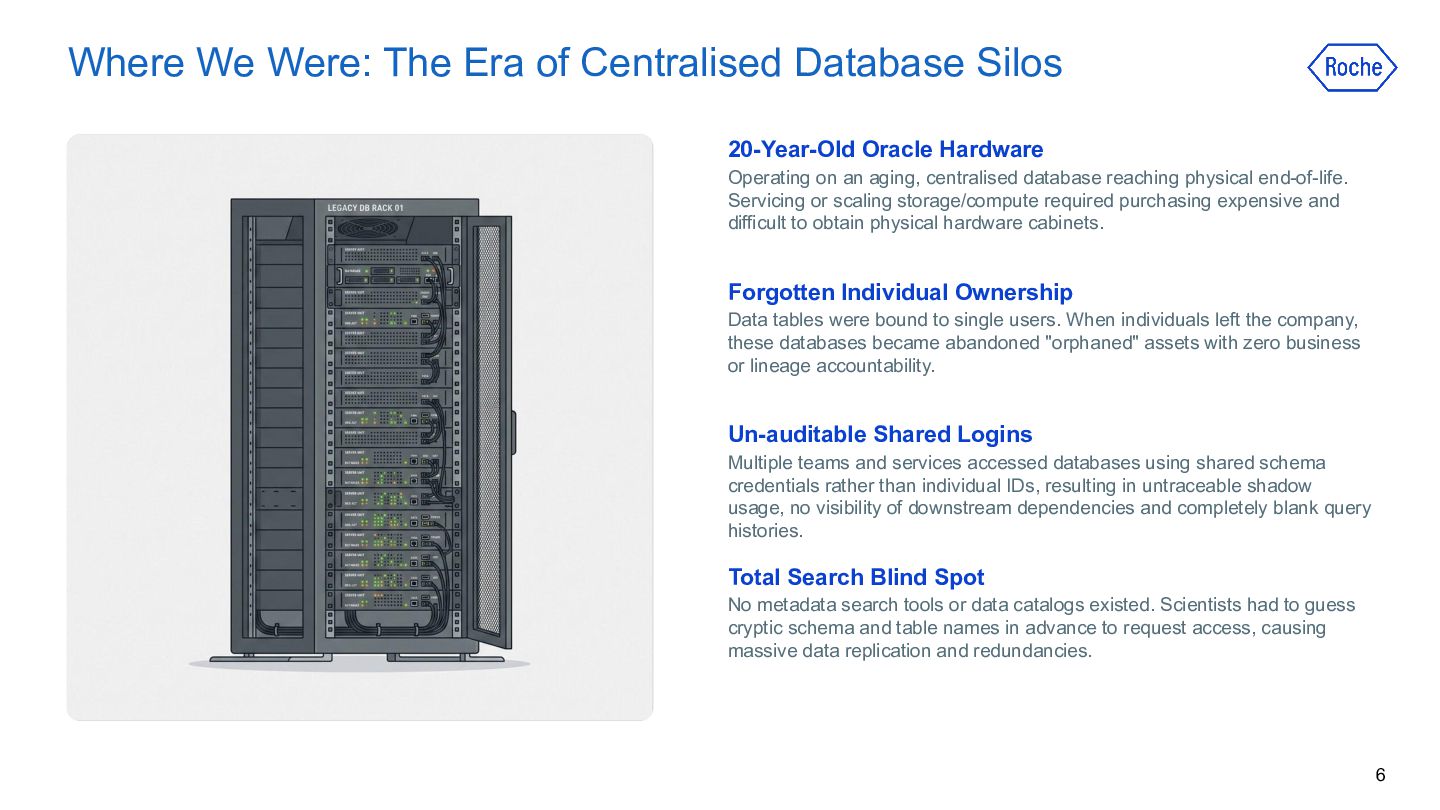
Oracle Hardware Operating on an aging, centralised database reaching physical end-of-life. Servicing or scaling storage/compute required purchasing expensive and difficult to obtain physical hardware cabinets. Forgotten Individual Ownership Data tables were bound to single users. When individuals left the company, these databases became abandoned "orphaned" assets with zero business or lineage accountability. Un-auditable Shared Logins Multiple teams and services accessed databases using shared schema credentials rather than individual IDs, resulting in untraceable shadow usage, no visibility of downstream dependencies and completely blank query histories. Total Search Blind Spot No metadata search tools or data catalogs existed. Scientists had to guess cryptic schema and table names in advance to request access, causing massive data replication and redundancies. 6
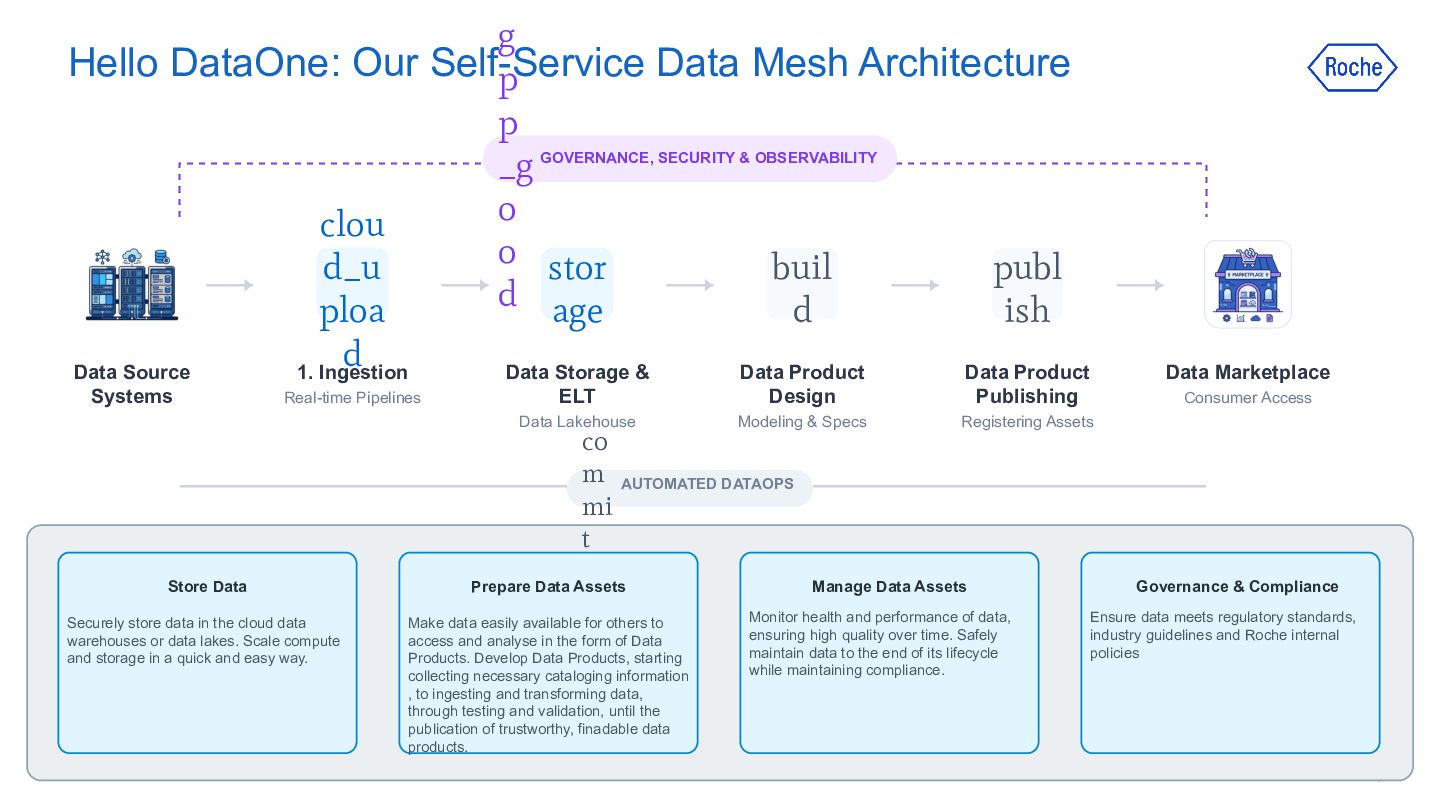
_g GOVERNANCE, SECURITY & OBSERVABILITY o clou o stor d_u buil publ d age ploa d ish Data Source Systems d 1. Ingestion Real-time Pipelines Data Storage & ELT Data Product Design Data Product Publishing Data Lakehouse Modeling & Specs Registering Assets co m AUTOMATED DATAOPS mi t Store Data Prepare Data Assets Manage Data Assets Securely store data in the cloud data warehouses or data lakes. Scale compute and storage in a quick and easy way. Make data easily available for others to access and analyse in the form of Data Products. Develop Data Products, starting collecting necessary cataloging information , to ingesting and transforming data, through testing and validation, until the publication of trustworthy, finadable data products. Monitor health and performance of data, ensuring high quality over time. Safely maintain data to the end of its lifecycle while maintaining compliance. Data Marketplace Consumer Access Governance & Compliance Ensure data meets regulatory standards, industry guidelines and Roche internal policies 7
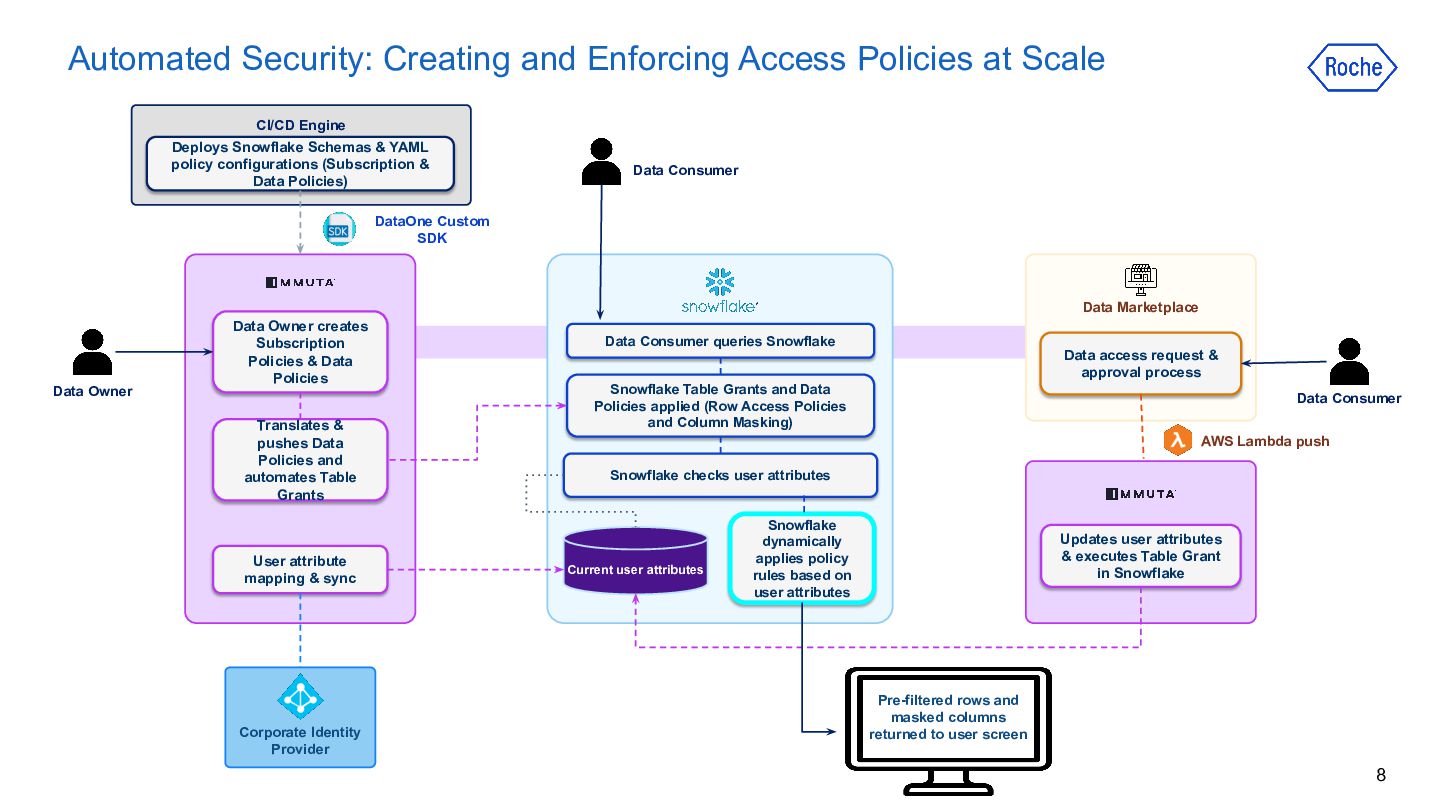
Engine Deploys Snowflake Schemas & YAML policy configurations (Subscription & Data Policies) Data Consumer DataOne Custom SDK Shortening Time-to-Insight Data Owner Data Owner creates Subscription Policies & Data Policies Translates & pushes Data Policies and automates Table Grants User attribute mapping & sync Corporate Identity Provider Data Marketplace Data Consumer queries Snowflake Data access request & approval process Snowflake Table Grants and Data Policies applied (Row Access Policies and Column Masking) Data Consumer AWS Lambda push Snowflake checks user attributes Current user attributes Snowflake dynamically applies policy rules based on user attributes Updates user attributes & executes Table Grant in Snowflake Pre-filtered rows and masked columns returned to user screen 8
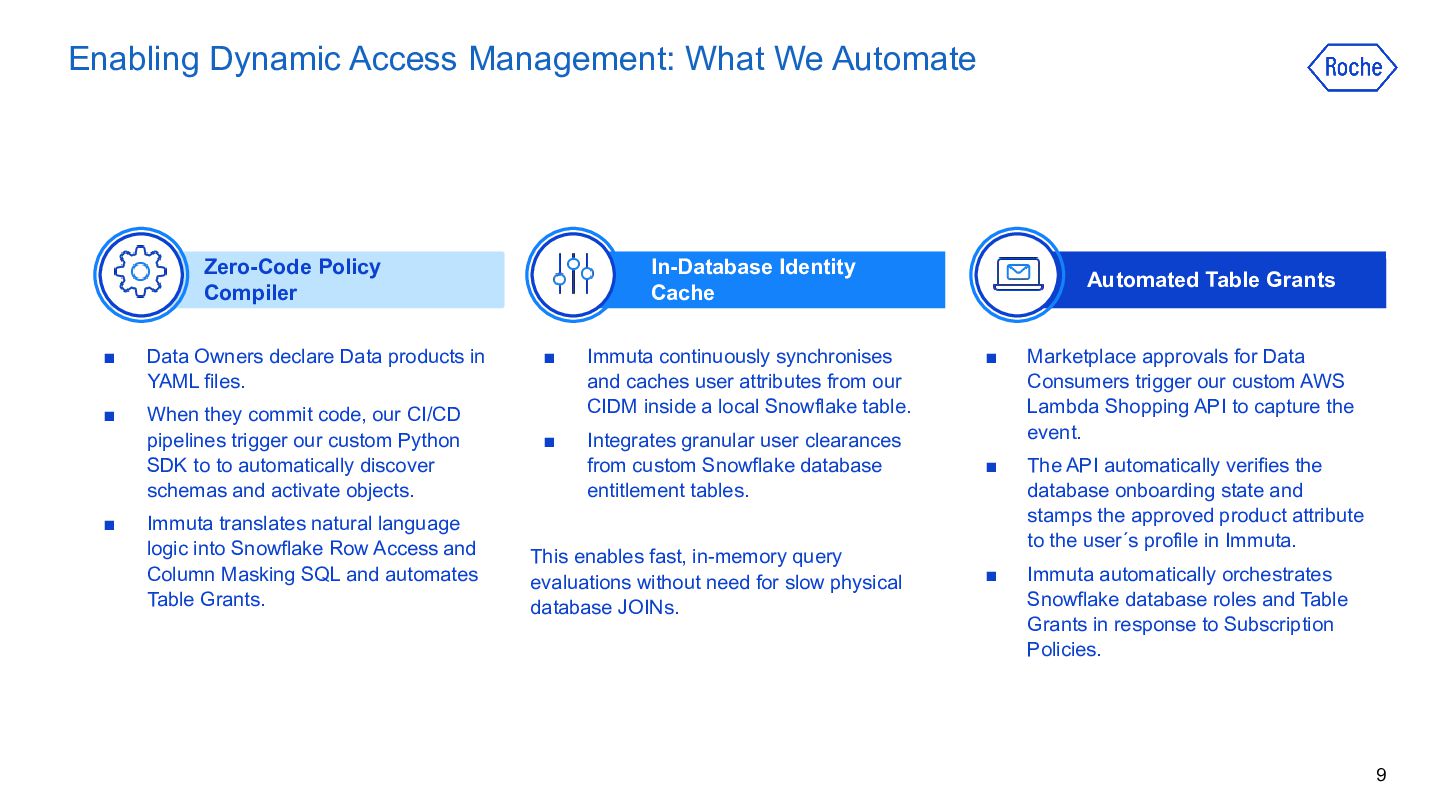
▪ Data Owners declare Data products in YAML files. ▪ When they commit code, our CI/CD pipelines trigger our custom Python SDK to to automatically discover schemas and activate objects. ▪ Immuta translates natural language logic into Snowflake Row Access and Column Masking SQL and automates Table Grants. In-Database Identity Cache ▪ Immuta continuously synchronises and caches user attributes from our CIDM inside a local Snowflake table. ▪ Automated Table Grants ▪ Integrates granular user clearances from custom Snowflake database entitlement tables. Marketplace approvals for Data Consumers trigger our custom AWS Lambda Shopping API to capture the event. ▪ This enables fast, in-memory query evaluations without need for slow physical database JOINs. The API automatically verifies the database onboarding state and stamps the approved product attribute to the user´s profile in Immuta. ▪ Immuta automatically orchestrates Snowflake database roles and Table Grants in response to Subscription Policies. 9 9
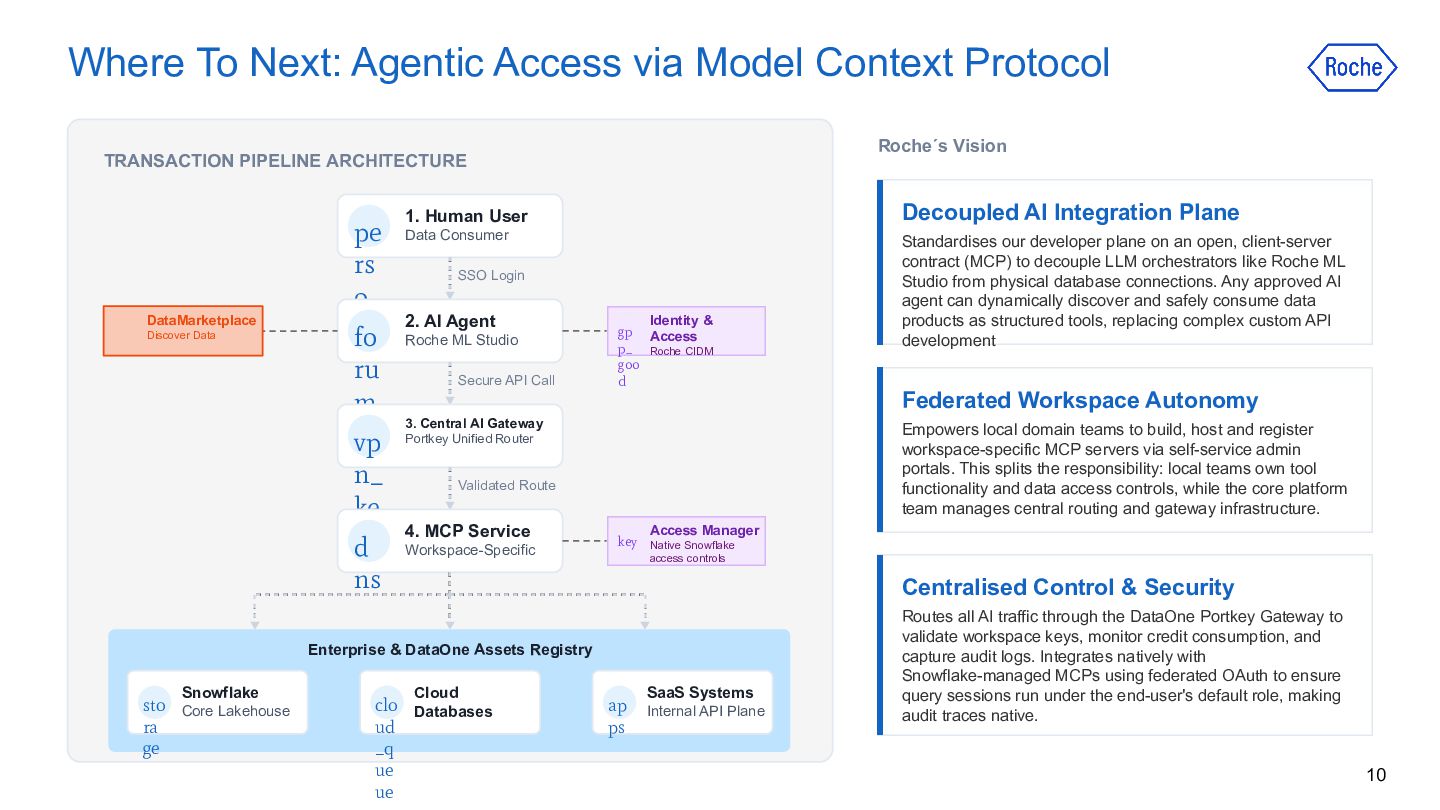
Vision TRANSACTION PIPELINE ARCHITECTURE DataMarketplace Discover Data pe rs o n fo ru m vp n_ ke yd ns 1. Human User Decoupled AI Integration Plane Data Consumer Standardises our developer plane on an open, client-server contract (MCP) to decouple LLM orchestrators like Roche ML Studio from physical database connections. Any approved AI agent can dynamically discover and safely consume data products as structured tools, replacing complex custom API development SSO Login 2. AI Agent Roche ML Studio Secure API Call Identity & gp Access p_ Roche CIDM goo d Federated Workspace Autonomy 3. Central AI Gateway Empowers local domain teams to build, host and register workspace-specific MCP servers via self-service admin portals. This splits the responsibility: local teams own tool functionality and data access controls, while the core platform team manages central routing and gateway infrastructure. Portkey Unified Router Validated Route 4. MCP Service Workspace-Specific Access Manager key Native Snowflake access controls Centralised Control & Security Enterprise & DataOne Assets Registry Snowflake sto Core Lakehouse ra ge Cloud clo Databases ud _q ue ue ap ps SaaS Systems Internal API Plane Routes all AI traffic through the DataOne Portkey Gateway to validate workspace keys, monitor credit consumption, and capture audit logs. Integrates natively with Snowflake-managed MCPs using federated OAuth to ensure query sessions run under the end-user's default role, making audit traces native. 10
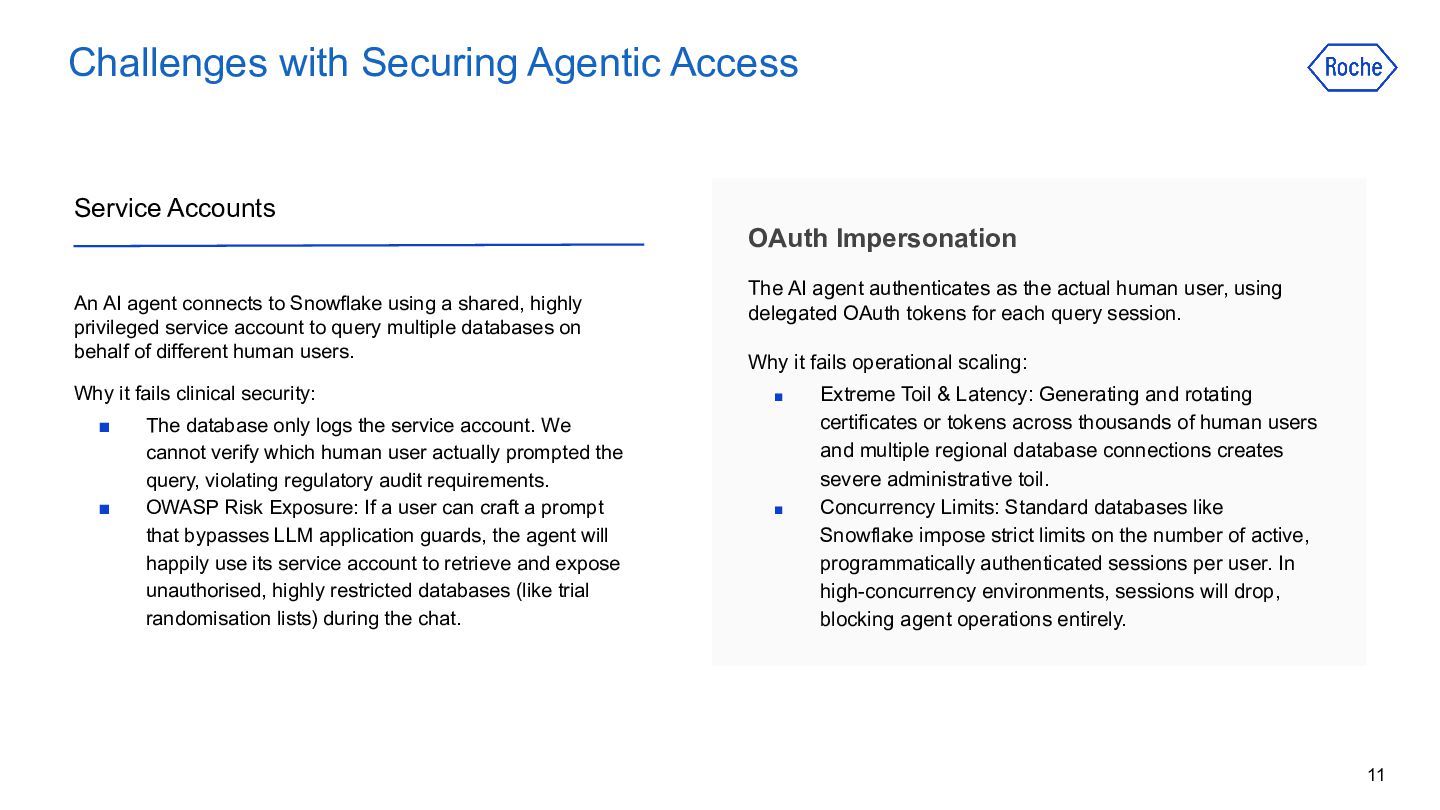
AI agent connects to Snowflake using a shared, highly privileged service account to query multiple databases on behalf of different human users. Why it fails clinical security: ▪ ▪ The database only logs the service account. We cannot verify which human user actually prompted the query, violating regulatory audit requirements. OWASP Risk Exposure: If a user can craft a prompt that bypasses LLM application guards, the agent will happily use its service account to retrieve and expose unauthorised, highly restricted databases (like trial randomisation lists) during the chat. The AI agent authenticates as the actual human user, using delegated OAuth tokens for each query session. Why it fails operational scaling: ▪ ▪ Extreme Toil & Latency: Generating and rotating certificates or tokens across thousands of human users and multiple regional database connections creates severe administrative toil. Concurrency Limits: Standard databases like Snowflake impose strict limits on the number of active, programmatically authenticated sessions per user. In high-concurrency environments, sessions will drop, blocking agent operations entirely. 11
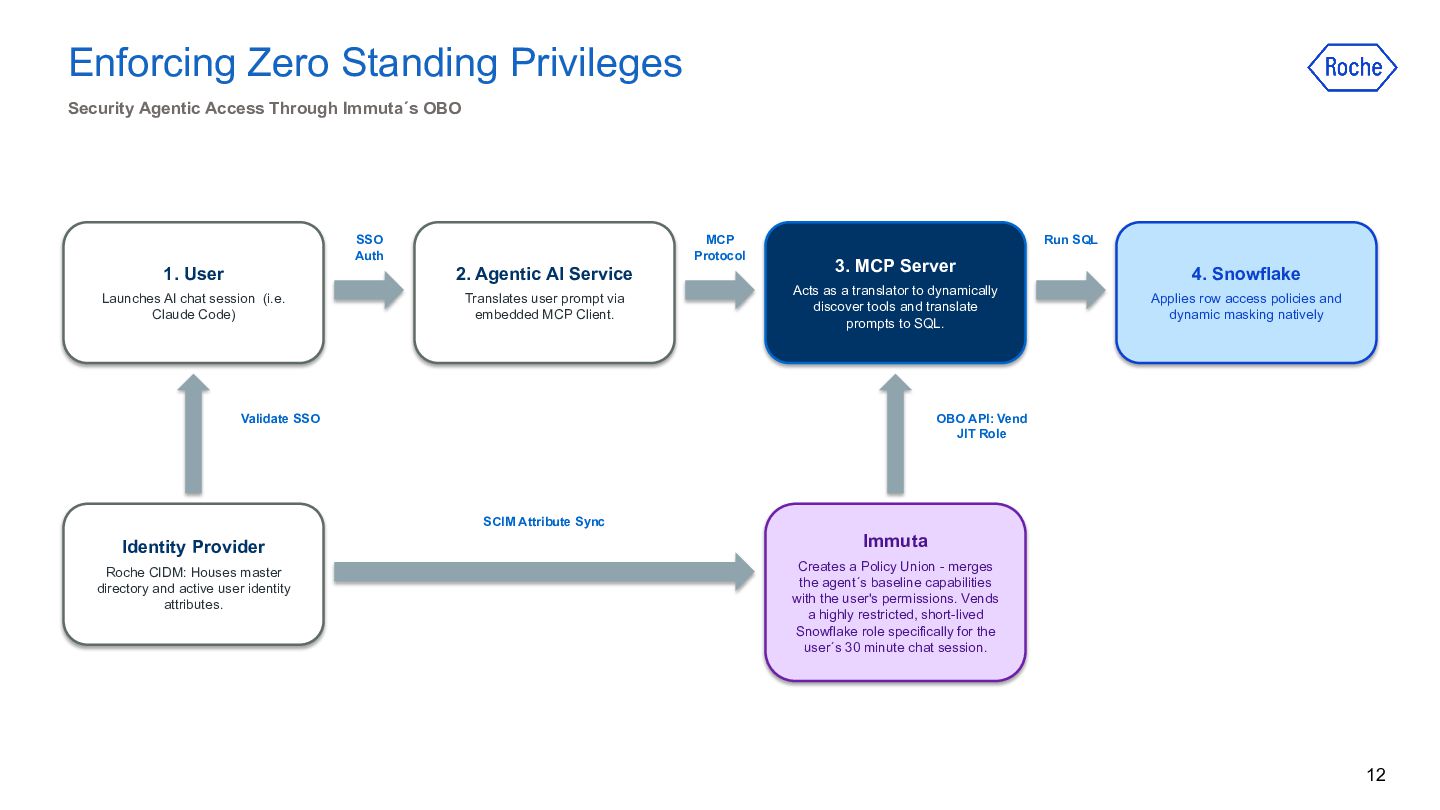
SSO Auth MCP Protocol 1. User 2. Agentic AI Service Launches AI chat session (i.e. Claude Code) Translates user prompt via embedded MCP Client. Run SQL 3. MCP Server Acts as a translator to dynamically discover tools and translate prompts to SQL. Validate SSO 4. Snowflake Applies row access policies and dynamic masking natively OBO API: Vend JIT Role SCIM Attribute Sync Identity Provider Immuta Roche CIDM: Houses master directory and active user identity attributes. Creates a Policy Union - merges the agent´s baseline capabilities with the user's permissions. Vends a highly restricted, short-lived Snowflake role specifically for the user´s 30 minute chat session. 12


 mark3t1ng
 addyosmani
 tamaranovitovic
 axbom
 katarinadahlin
 michaelherold
 tammielis
 aemeredith
 marcduiker
 davidcarrasco
 reverentgeek
 apolaine
 skipperchong