of experience in mobile application development. She is a regular Android/Kotlin speaker at mobile development conferences/meetups. Last, but not the least, she shares her birthday with Java :) Twitter handle: @monika_jethani
• To protect sensitive data like personally identifiable information (PII), personal health information(PHI), financial details, enterprise data, etc. • To protect data on a rooted device, even with full-disk encryption. • To prevent the users from accessing tokens and keys used in your app.
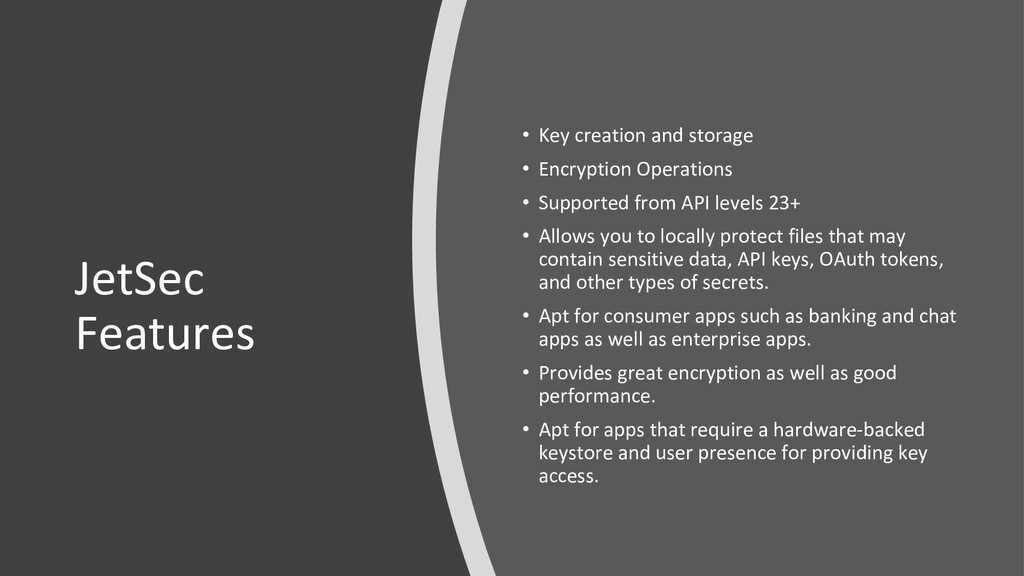
• Supported from API levels 23+ • Allows you to locally protect files that may contain sensitive data, API keys, OAuth tokens, and other types of secrets. • Apt for consumer apps such as banking and chat apps as well as enterprise apps. • Provides great encryption as well as good performance. • Apt for apps that require a hardware-backed keystore and user presence for providing key access.
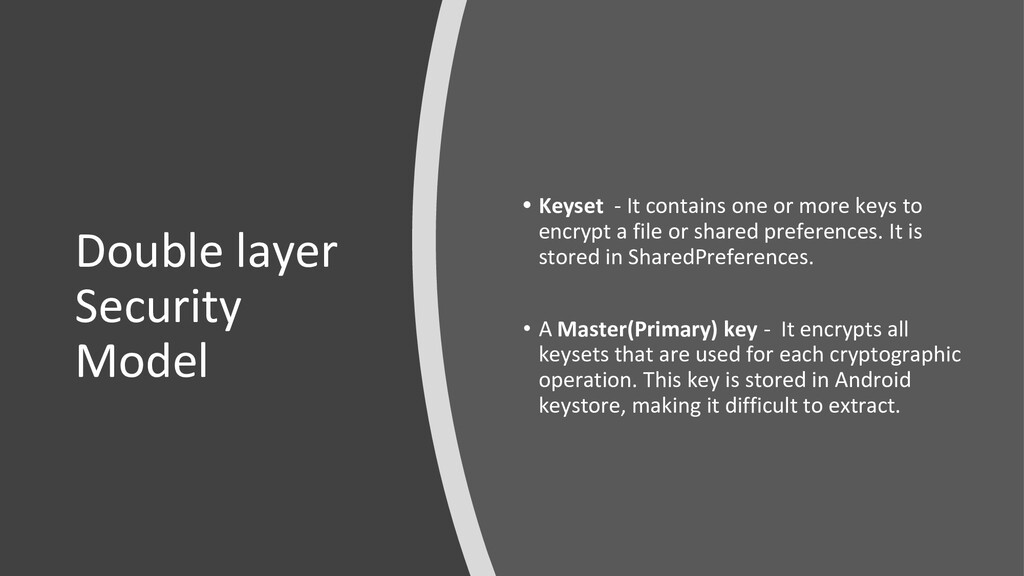
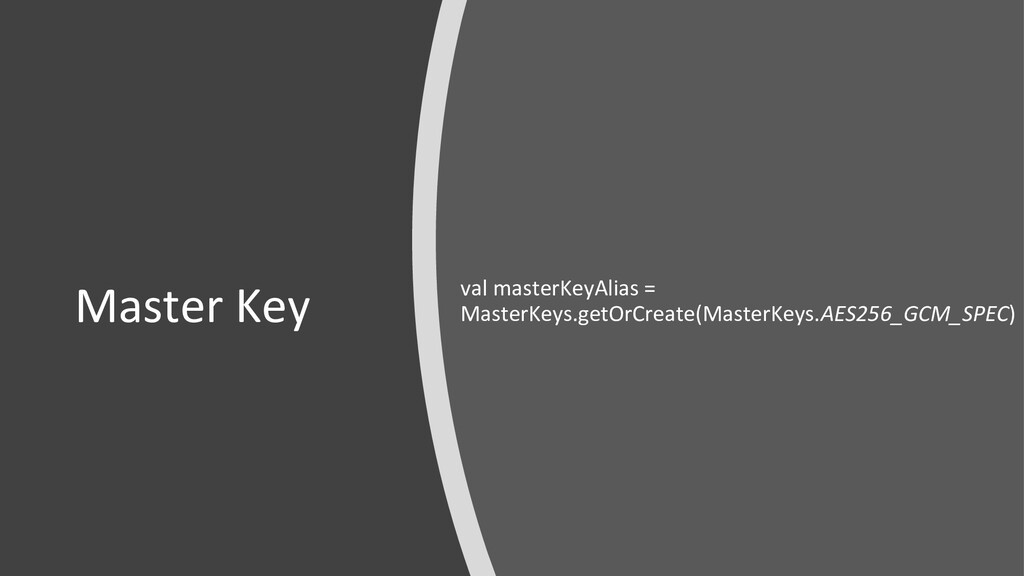
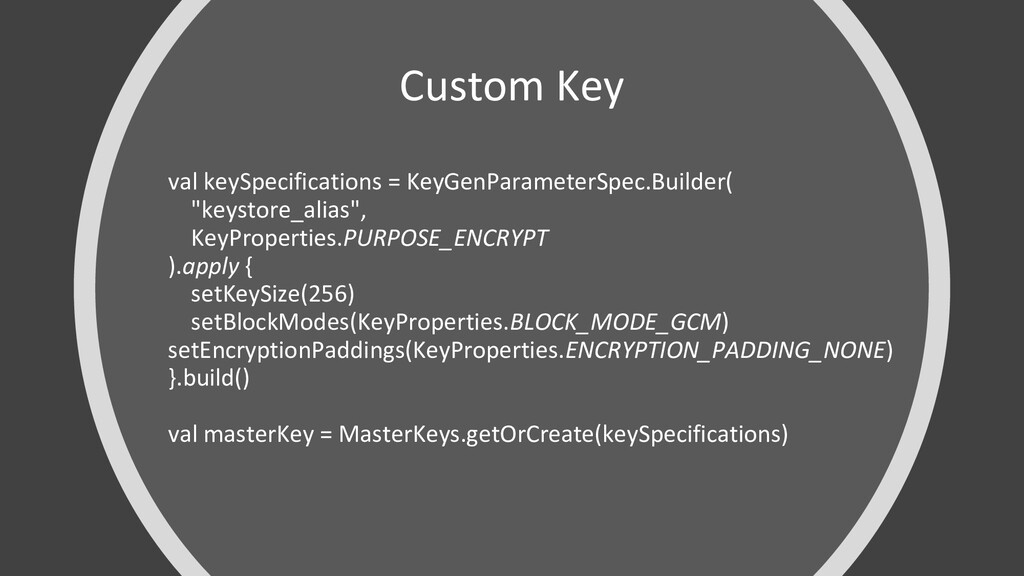
or more keys to encrypt a file or shared preferences. It is stored in SharedPreferences. • A Master(Primary) key - It encrypts all keysets that are used for each cryptographic operation. This key is stored in Android keystore, making it difficult to extract.
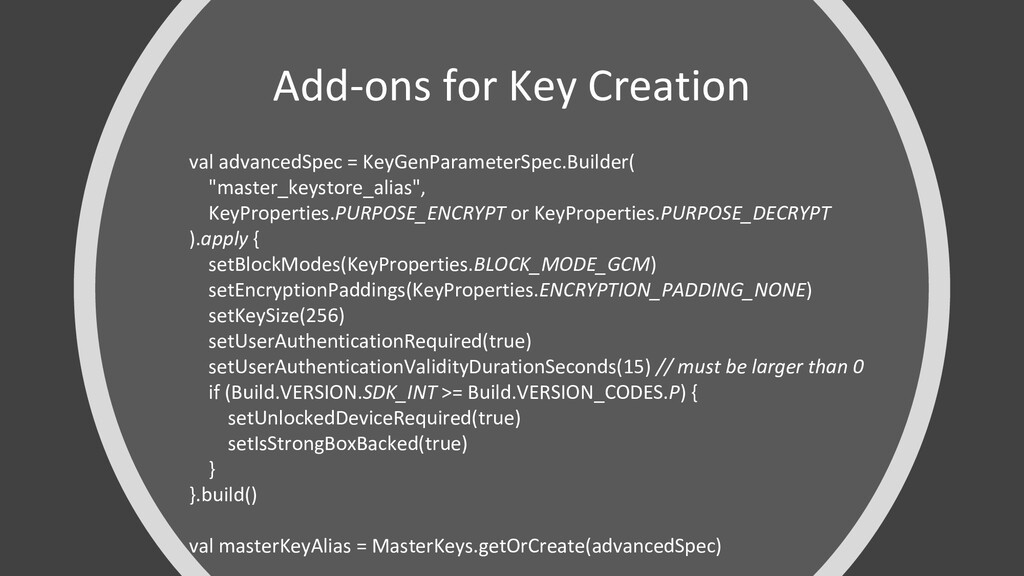
hard to extract. • Stores keys in a trusted execution environment or StrongBox. • To allow JetSec to store keys in StrongBox, we need to enable a flag.
or KeyProperties.PURPOSE_DECRYPT ).apply { setBlockModes(KeyProperties.BLOCK_MODE_GCM) setEncryptionPaddings(KeyProperties.ENCRYPTION_PADDING_NONE) setKeySize(256) setUserAuthenticationRequired(true) setUserAuthenticationValidityDurationSeconds(15) // must be larger than 0 if (Build.VERSION.SDK_INT >= Build.VERSION_CODES.P) { setUnlockedDeviceRequired(true) setIsStrongBoxBacked(true) } }.build() val masterKeyAlias = MasterKeys.getOrCreate(advancedSpec)
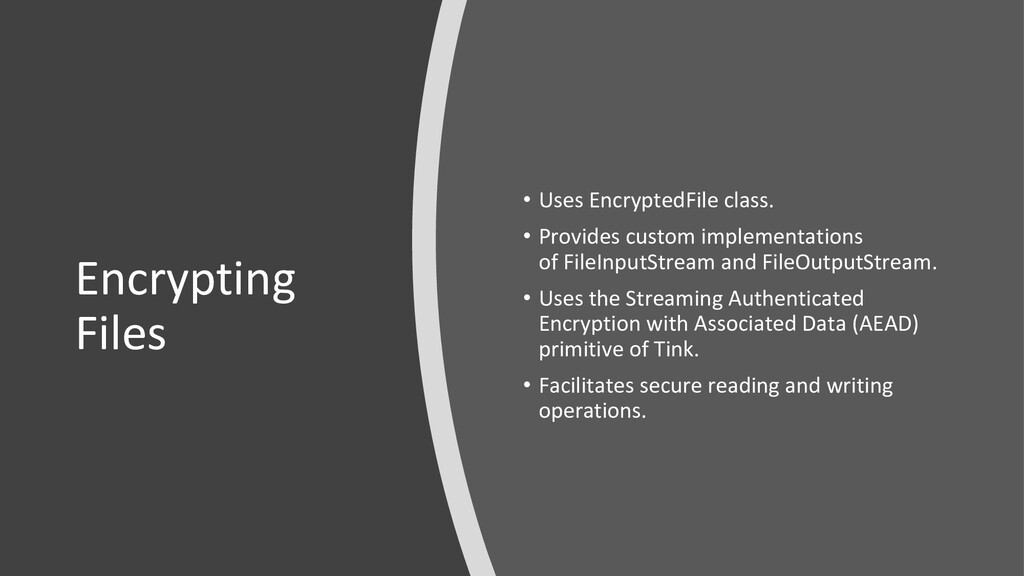
of FileInputStream and FileOutputStream. • Uses the Streaming Authenticated Encryption with Associated Data (AEAD) primitive of Tink. • Facilitates secure reading and writing operations.
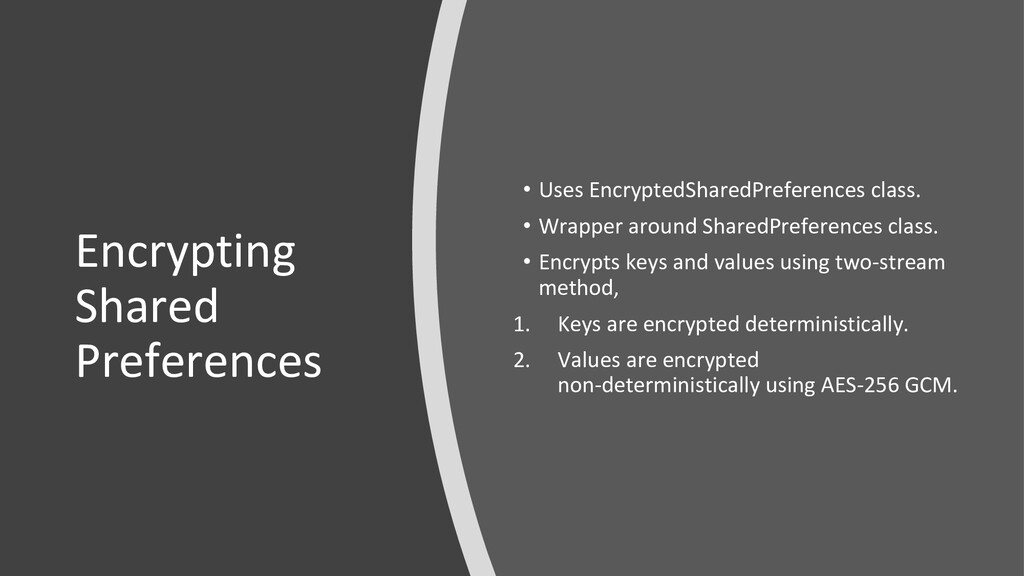
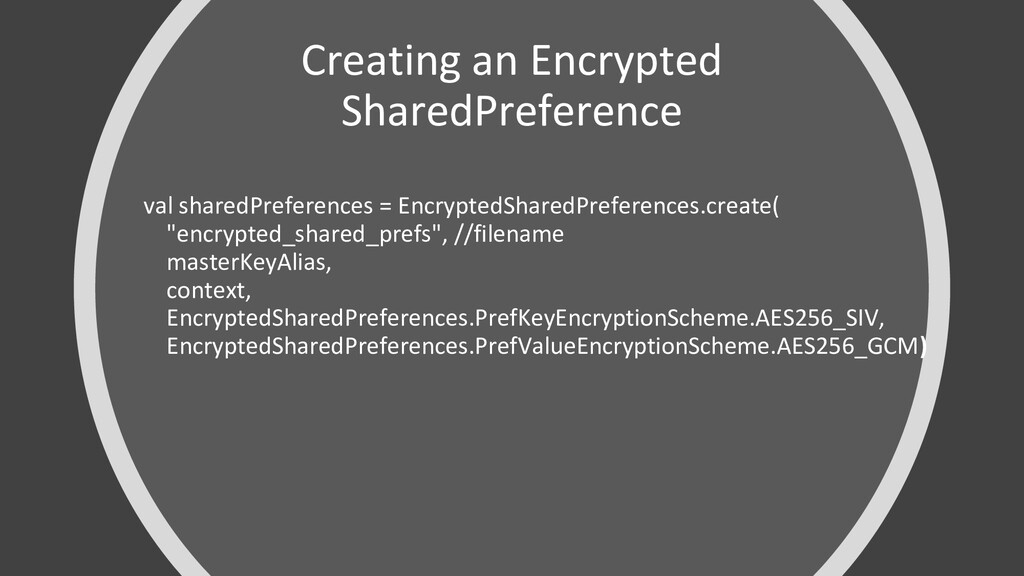
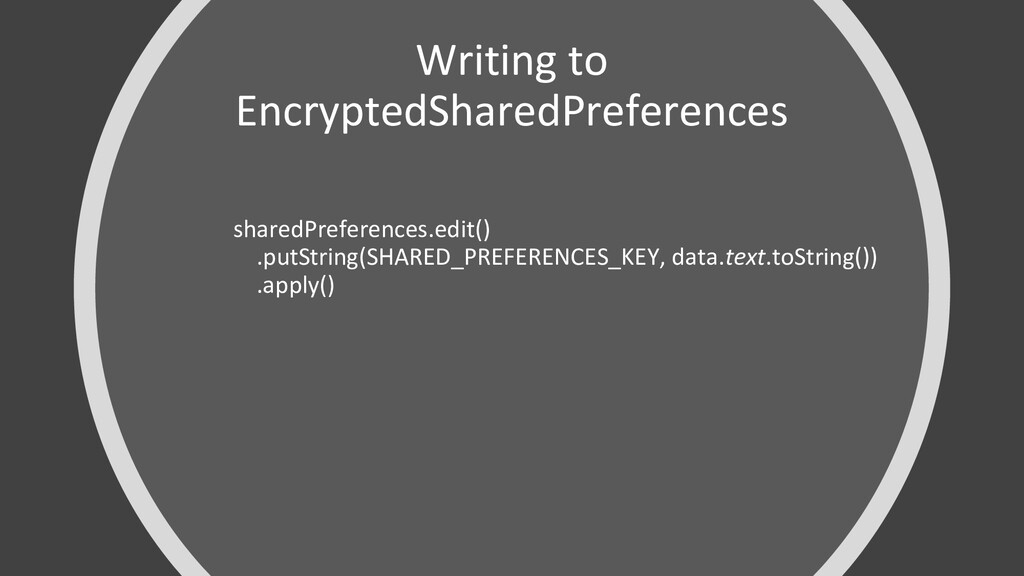
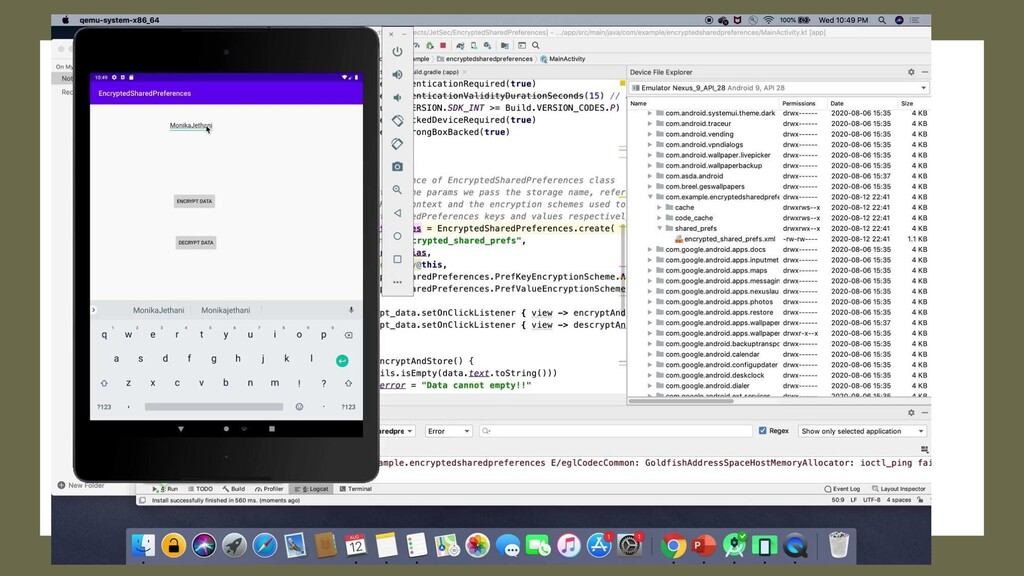
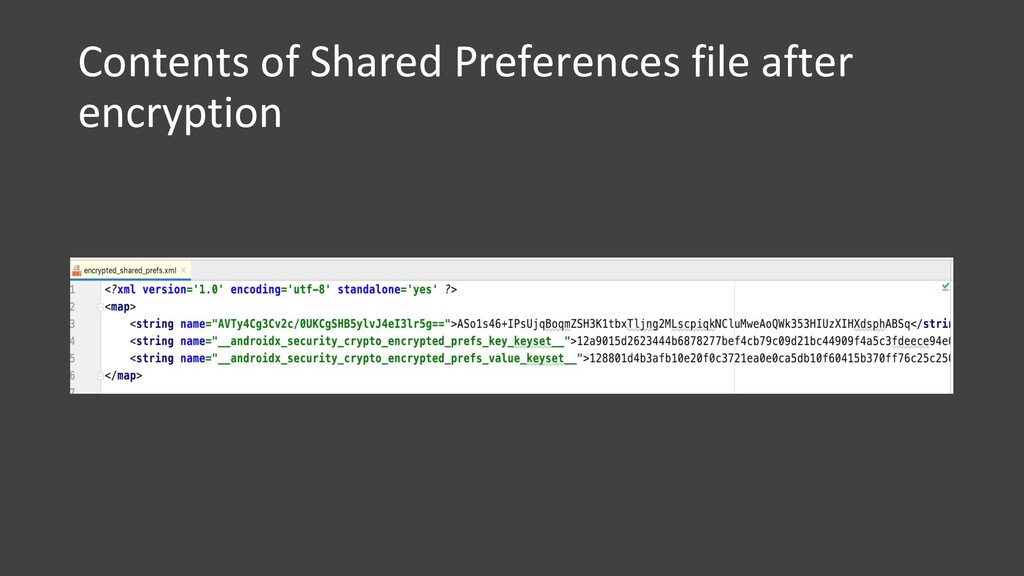
SharedPreferences class. • Encrypts keys and values using two-stream method, 1. Keys are encrypted deterministically. 2. Values are encrypted non-deterministically using AES-256 GCM.
Tink under the hood. • Tink is an open-source, cross-platform security project from Google. • https://github.com/google/tink • Provides cryptographic APIs that are secure, easy to use, harder to misuse.
• MasterKeys class has become deprecated and a new MasterKey class has come into picture to support new features and new versions of Android that don’t have KeyGenParameterSpec.


 monikakumarjethani
 carta_engineering
 sue445
 fj_yoshimura_kosuke
 nsatoh
 swdtkuy
 pipepasta
 sat
 yuutosi
 tsukuboshi
 sansantech
 oracle4engineer
 a_suenami
 joshbly
 apolaine
 jnunemaker
 honzajavorek
 denniskardys
 skoyamalab
 seathinner
 akademiya2063
 tammyeverts
 tanoku
 kimpetersen
 aleyda