Ecosystem of Malware 4. Technical detail and how to reveal it's functionality 5. Case studies a. Bby Stealer b. 1337 stealer c. Pulse(not a Node.js malware!) 6. Dual Hook 7. Conclusion 3
crypto currency community, gamers ◦ AVTOKYO also use DIscord • Nowadays, New Gen Malware is spreading and steal important information from PC with Phishing and it was not detected by AVs 4
written in JavaScript ◦ and also called as a token grabber • It uses Node.js to run their scripts • Most of them uses Discord’s Webhook to send stolen data to threat actors • Malware injects malicous JavaScript code into Discord itself ◦ Discord has Credit Card Number, Tokens, Email, Password, etc… • Right now, infection vector is only phishing. ◦ No ExploitKit or Loaders. 6
uses Electron ◦ Easy to analyze, just unpack ASAR file and you can see source code ◦ Source code is obfuscated tho • Second generation of malware uses Vercel pkg ◦ Hard to analyze ◦ Malware, binary itself contains various GZipped binary ◦ Static analysis is very hard • For anti-analysis and scams, JavaScript based Malware evolved like this! • I forget when it did, Novel JavaScript based Malware, BbyStealer and others banned debuggers and capture tool same time 7
and Telegram • Build, Lure, Infection, Steal, Manage stolen data • Malicious Discord server is suddenly banned by Discord Abuse Response Team • Telegram is used in a way to notify new Discord server • Details are on section of “Case study2 - 1337 stealer” 😉 8
generation is easy as I told ◦ Electron based malware ◦ Unpack(asar command) and you can get source code ◦ Source code is obfuscated but you can defeat it! • Second generation is hard ◦ Vercel pkg based malware ◦ Static analysis is impossible! ◦ Dynamic analysis works ◦ Run malware and dump memory and analyze it and you can find IoCs! • We take a look into Second generation of malware! 9
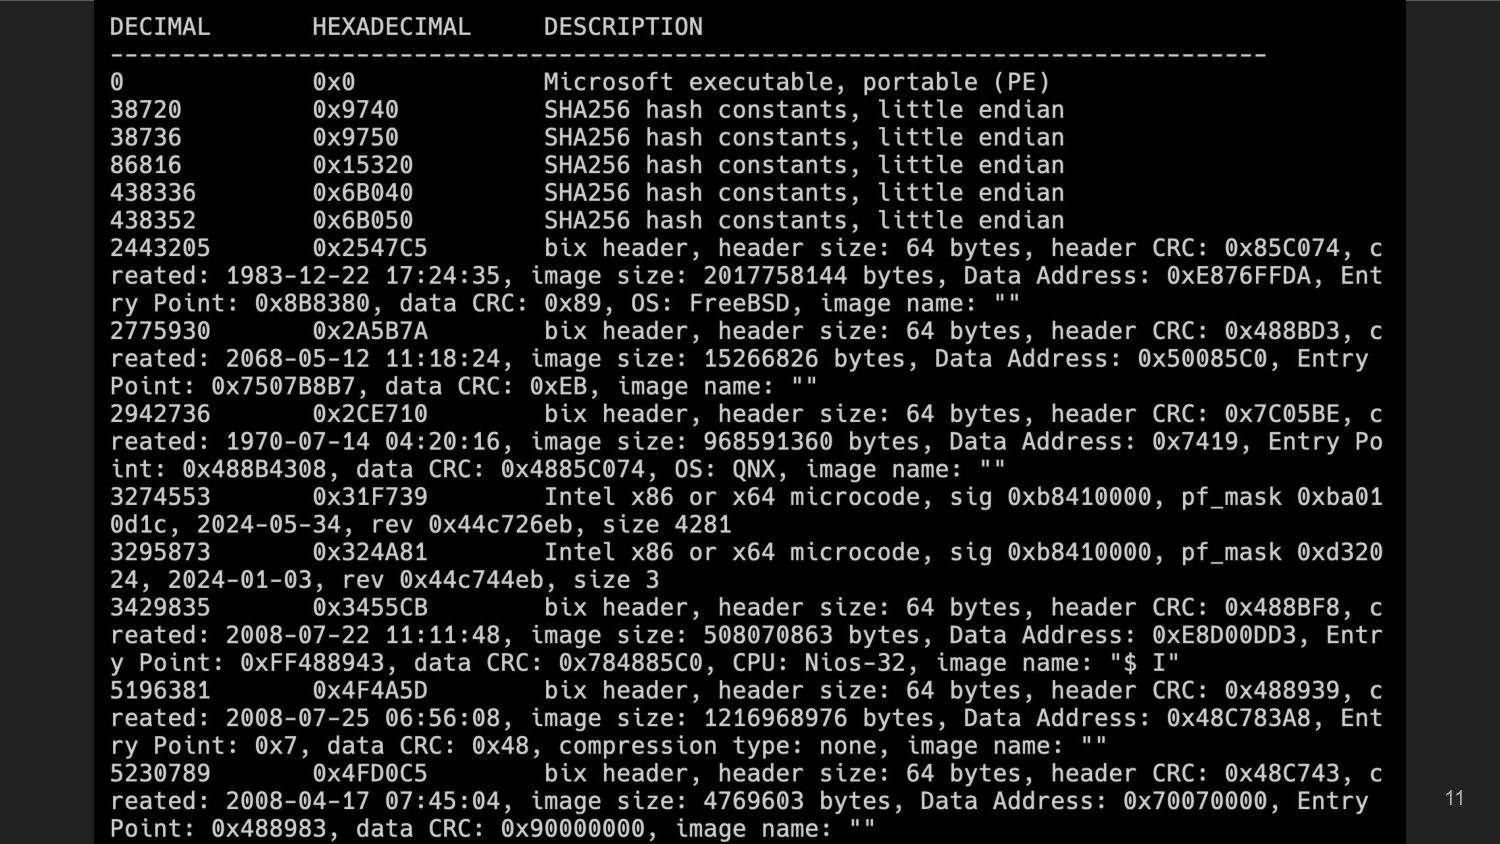
pkg is https://github.com/vercel/pkg • Source code is completely disappeared • When you binwalk malware, you can see lots of junk files is contained!!!! ◦ You can not ungzip it also • This is totally brainfucked 10
does not work ◦ We can not get IoCs • Online Free Sandbox is not working because file size is larger than 2MB and it needs Discord app to kick in • I used dynamic analysis ◦ Run malware and terminate and dump memory ◦ This memory image contains IoCs and important string ◦ And also part of source code • After I get part of source code, I deobfuscate source code and analyzed it ◦ also dynamic deobfuscation is useful in this stage! • I used Process Hacker, x64dbg and some forensics tool 12
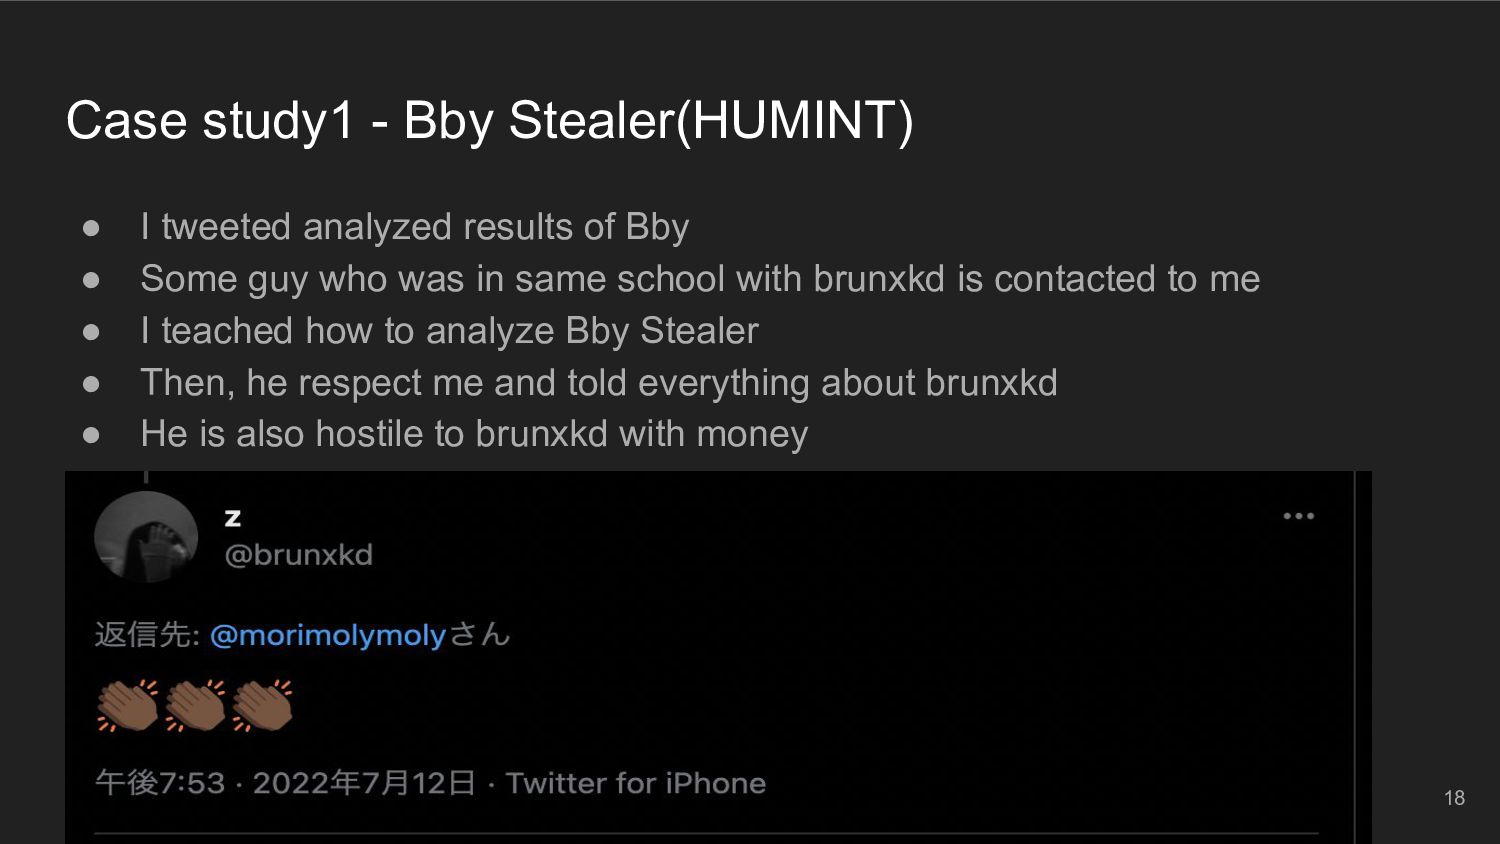
of Bby • Some guy who was in same school with brunxkd is contacted to me • I teached how to analyze Bby Stealer • Then, he respect me and told everything about brunxkd • He is also hostile to brunxkd with money 18
of Bby. • wearenotbbystealer[.]nl(C2) and superfurrycdn[.]nl and rustlercoppy[.]nl are owned by same actor • wearenotbbystealer[.]nl has link to hxxps[:]//superfurrycdn/[.]nl/assets/favicon.png • superfurrycdn is a distributer of malware • superfurrycdn is also linked to rustlercoppy[.]com 20
1337 stealer and RedFinger stealer and 1337 Network • First generation of 1337 stealer is sooooo shit • This has a vulnerability • I reported this vuln and got reputation and admin loves me ◦ It is time to HUMINT!!!!!!!!!!!!!!!!!! 22
itself contains a Discord tokens and MongoDB Username/Password as a plain text • My friend researcher from US dumped Mongo and wiped out and used Discord token and nuked their server 23
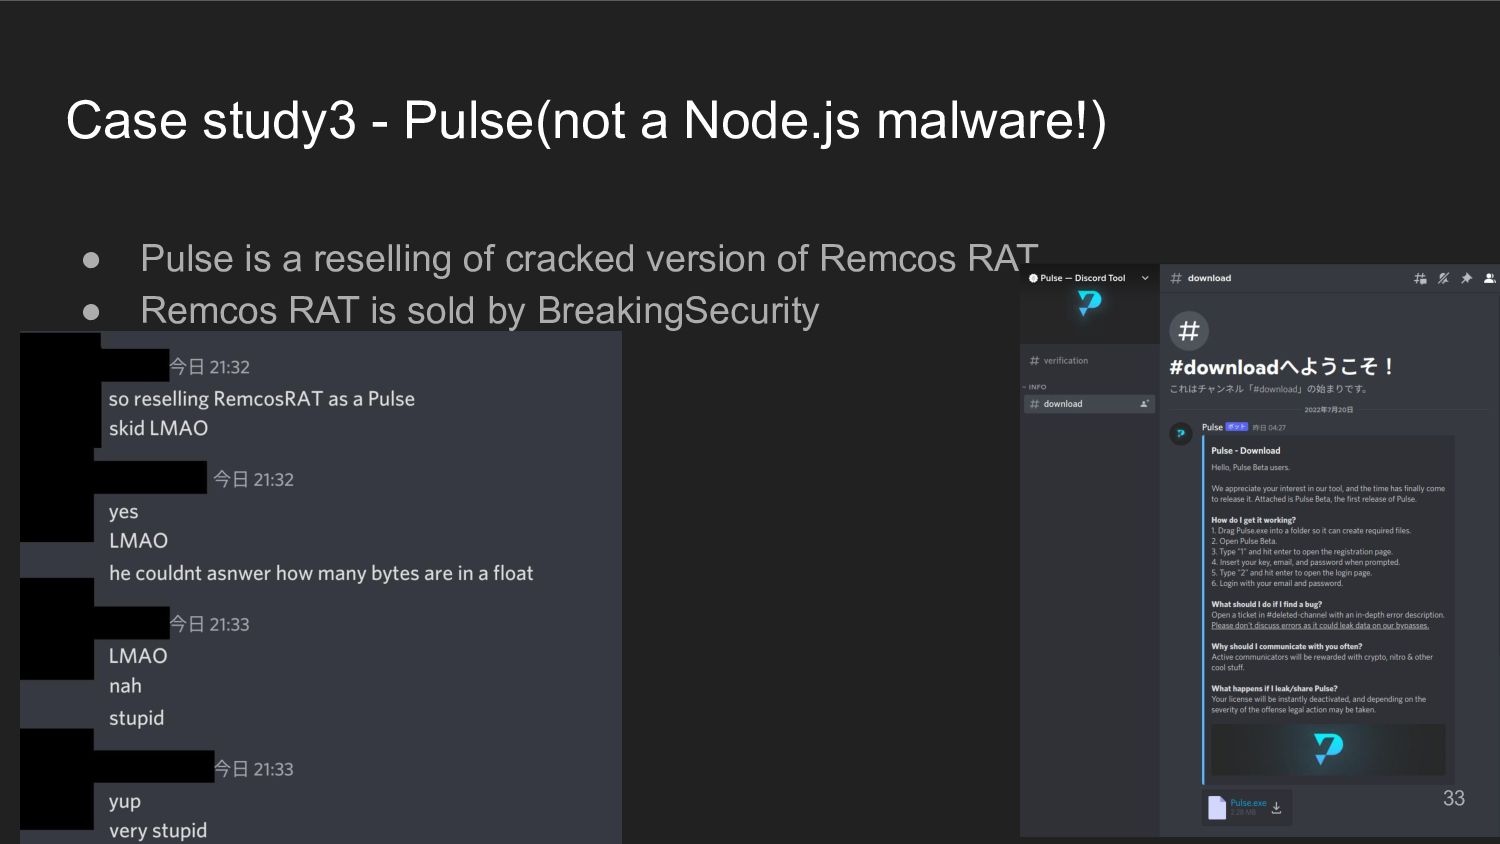
is reselling cracked version of another malware • Size is so big but Pulse is not detected by AV • There is some actor which sell malware packed with cryptor as a new malware 35
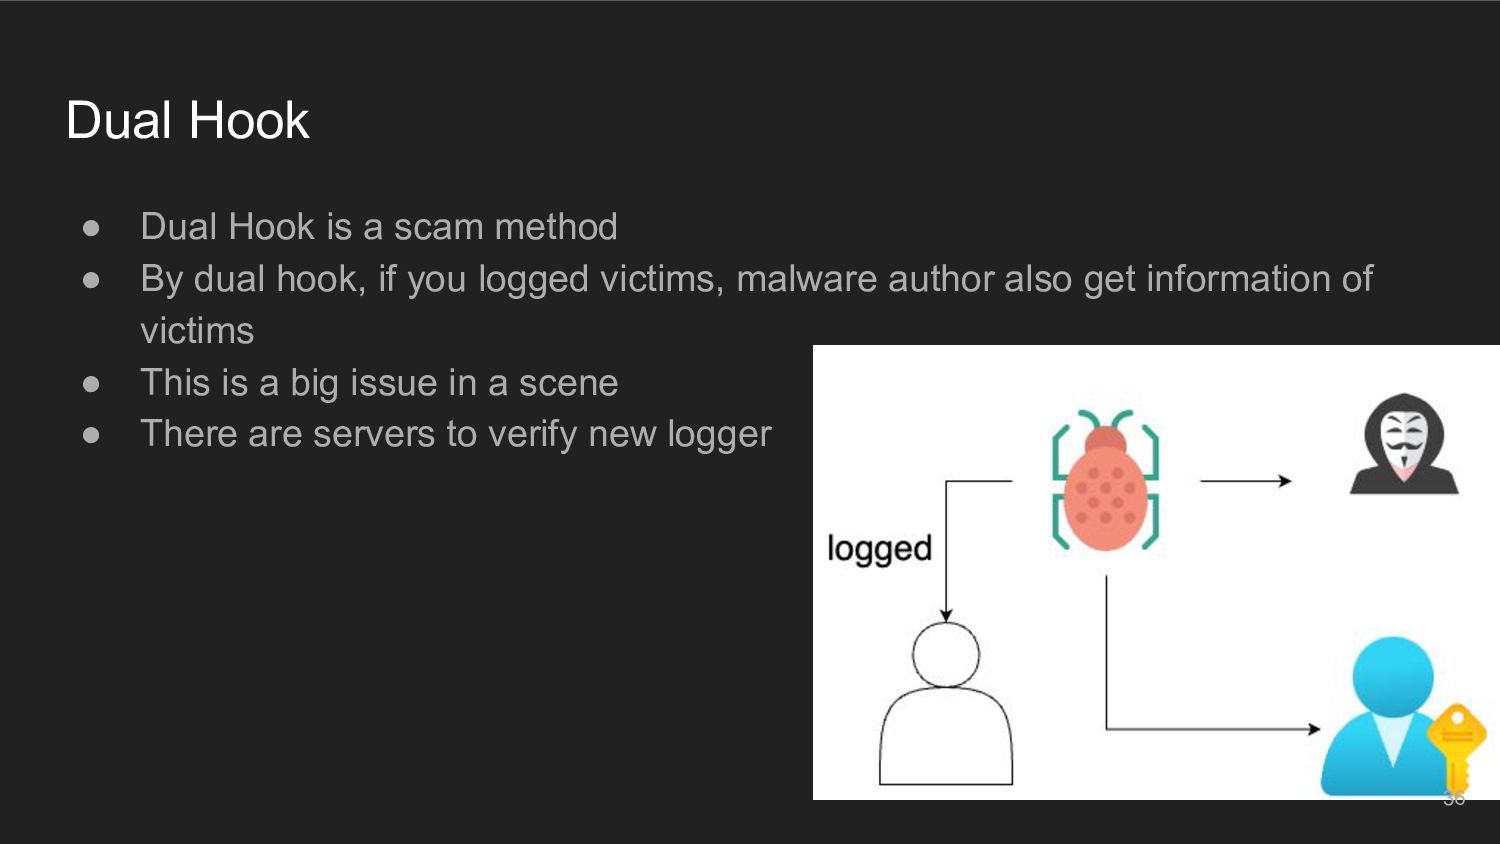
By dual hook, if you logged victims, malware author also get information of victims • This is a big issue in a scene • There are servers to verify new logger 36
and not detected by most of AVs • Most of actors are kids • They does not have loaders or EK to spread ◦ No injection, no hollowing, no nothing ◦ So, AVs can not detect it as suspicious • They are immature cybercriminals • If we carefully observe them, we can get some information of future of cybercrime 37


 morimolymoly
 jcabot
 nealle
 everpeace
 knwoop
 dkduppf
 hagino3000
 fj_yoshimura_kosuke
 ota1022
 endonanana
 comi190327
 silmin_
 ren8k
 pwiseman
 hannesfritz
 jonoalderson
 akademiya2063
 ryanjones
 stuffmc
 samtorres
 cassininazir
 watany
 inesmontani
 davidcarrasco
 codingconduct