Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Taming secrets with Vault
Search
Jérémy Courtial
June 13, 2017
Programming
110
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Taming secrets with Vault
Video:
https://www.youtube.com/watch?v=fZDd4-McNSU
Jérémy Courtial
June 13, 2017
More Decks by Jérémy Courtial
See All by Jérémy Courtial
sudo give the cloud
mrartichaut
0
36
An introduction to AppSec?
mrartichaut
0
57
Secure by design: introduction to threat modeling
mrartichaut
0
67
Lead Tech: Empowering the team
mrartichaut
0
56
Web Platform Security
mrartichaut
0
62
go doSomeThing()
mrartichaut
0
63
Practical Cryptography : Data Encryption
mrartichaut
0
76
Practical Cryptography : Password Hashing
mrartichaut
1
84
HTTP/2 : One connection to rule them all
mrartichaut
1
77
Other Decks in Programming
See All in Programming
ハーネス設計入門 〜 基礎知識の整理から実務へのステップアップ 〜
kinopeee
22
22k
UPDATE をやめる — EF Core でマスタをバージョン管理する
panda728
PRO
0
1.2k
パーソナライズPodcastを作った話
repunit11
0
140
contenteditable と日本語入力に向き合う
colorful12
0
190
ジョジョの世界をXRで再現する
mofurune
0
160
個人開発者よ、Honoを使え(おじさんver)
tanahiro2010
2
250
月間100万人のサービス刷新で、 技術選定をHonoに振り切った話
yutobara
8
6.4k
re:Inventに行く前に知っておきたい現地参加のノウハウ
nokomoro3
0
410
Kubernetes祭り #2 OP/ED
bells17
0
110
Rでドレミ/Do-Re-Mi_with_R
florets1
0
130
なぜCTOを降りてFDEを選んだのか?〜なぜプロダクト企業がFDEで顧客の現場に踏み込むのか〜
gonta
1
200
IBM Bob でAI駆動開発『QC-Playbook』
ichirokano2
0
110
Featured
See All Featured
エンジニアに許された特別な時間の終わり
watany
109
250k
4 Signs Your Business is Dying
shpigford
187
23k
Making the Leap to Tech Lead
cromwellryan
135
10k
The untapped power of vector embeddings
frankvandijk
2
1.9k
The World Runs on Bad Software
bkeepers
PRO
72
12k
AI Search: Where Are We & What Can We Do About It?
aleyda
0
8.1k
We Have a Design System, Now What?
morganepeng
55
8.4k
How to Ace a Technical Interview
jacobian
280
24k
Principles of Awesome APIs and How to Build Them.
keavy
128
18k
Mobile First: as difficult as doing things right
swwweet
225
10k
Designing for humans not robots
tammielis
254
26k
Sharpening the Axe: The Primacy of Toolmaking
bcantrill
46
3k
Transcript
Taming secrets with Vault Jérémy Courtial - Software Security Architect
Oodrive
Secrets & Sensitive data
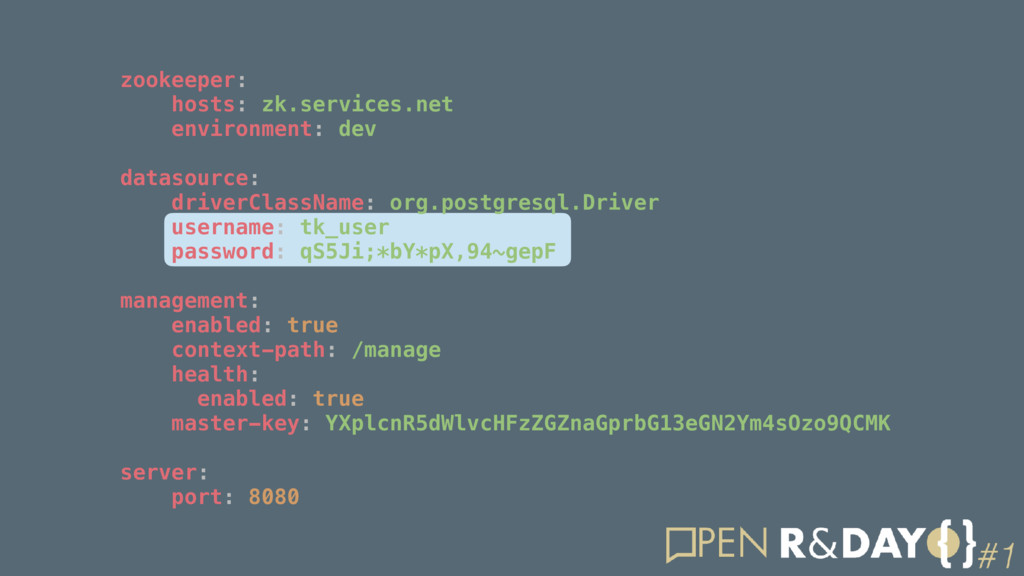
zookeeper: hosts: zk.services.net environment: dev datasource: driverClassName: org.postgresql.Driver username: tk_user
password: qS5Ji;*bY*pX,94~gepF management: enabled: true context-path: /manage health: enabled: true master-key: YXplcnR5dWlvcHFzZGZnaGprbG13eGN2Ym4sOzo9QCMK server: port: 8080
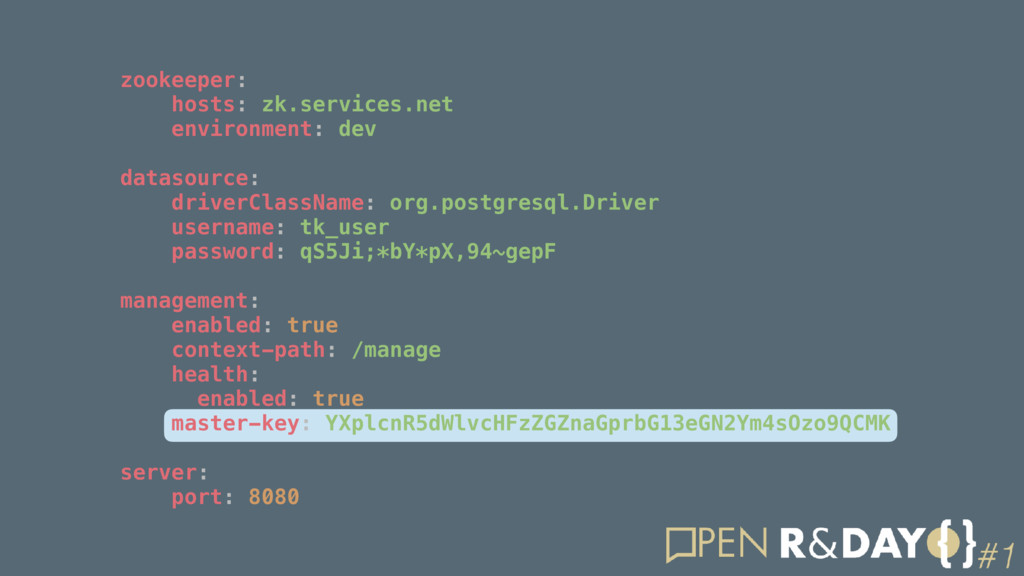
zookeeper: hosts: zk.services.net environment: dev datasource: driverClassName: org.postgresql.Driver username: tk_user
password: qS5Ji;*bY*pX,94~gepF management: enabled: true context-path: /manage health: enabled: true master-key: YXplcnR5dWlvcHFzZGZnaGprbG13eGN2Ym4sOzo9QCMK server: port: 8080
Why bother?
Traditional security
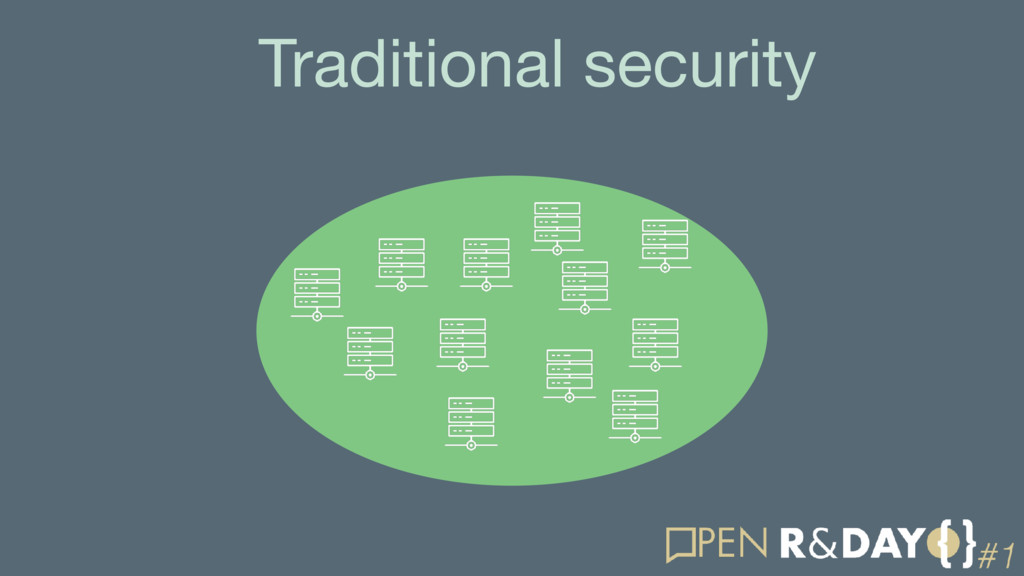
Traditional security
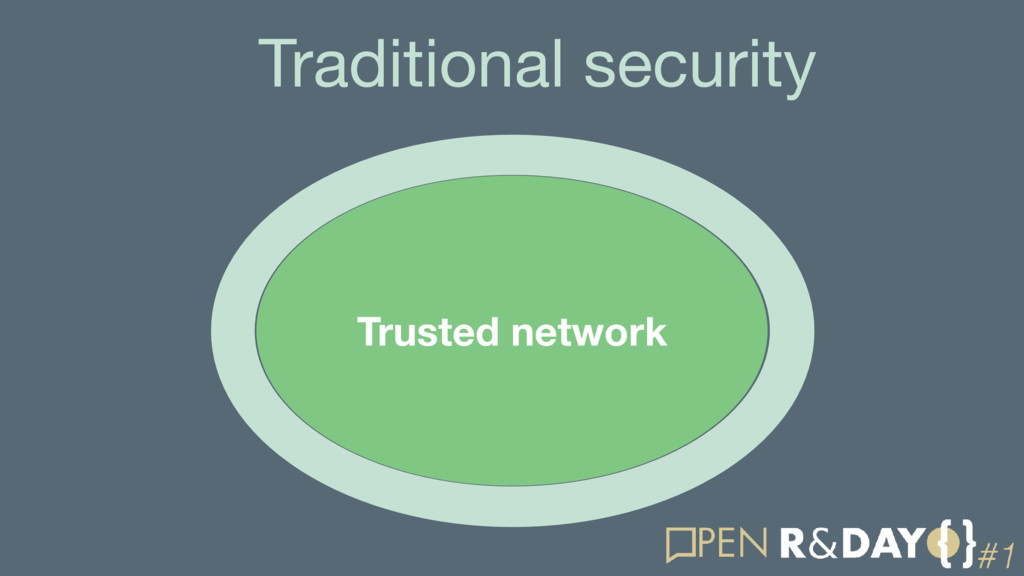
Trusted network Traditional security
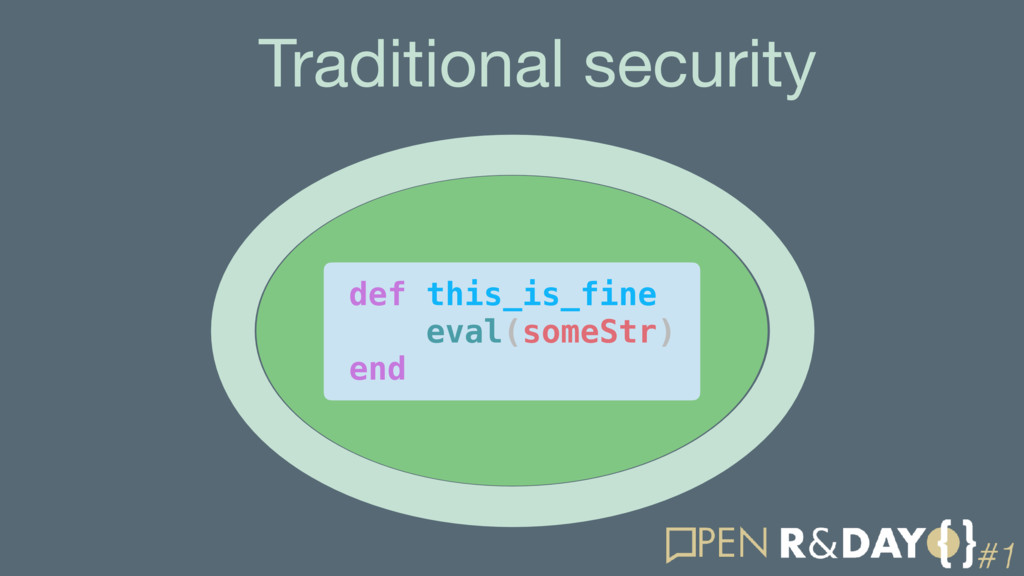
Trusted network def this_is_fine eval(someStr) end Traditional security
Traditional security
"I’m simply saying that hackers, uh… finds a way." Dr.
Ian Malcolm
Defense in depth Don't rely on a single line of
defense
Defense in depth Don't assume threats stop at the gateway
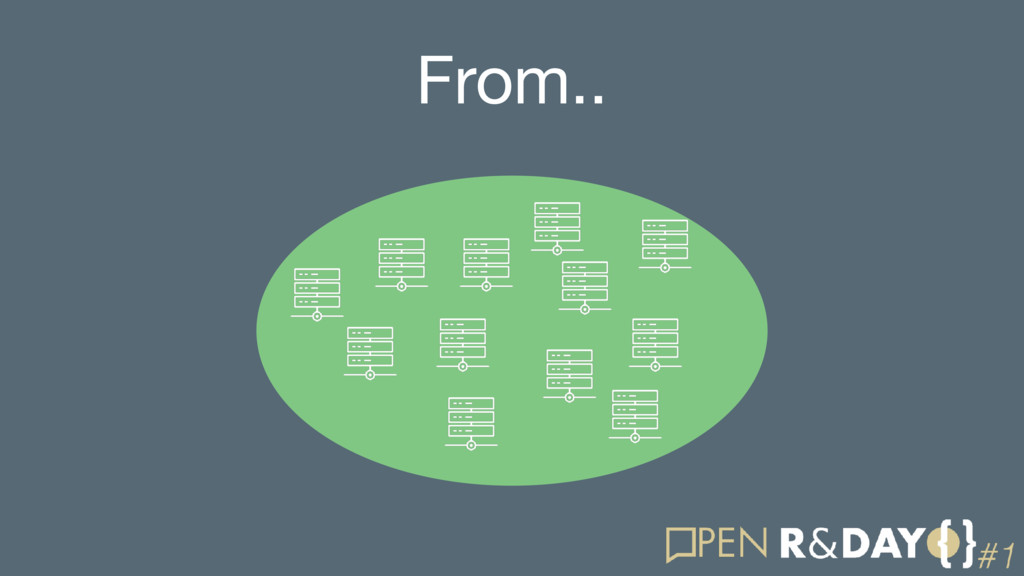
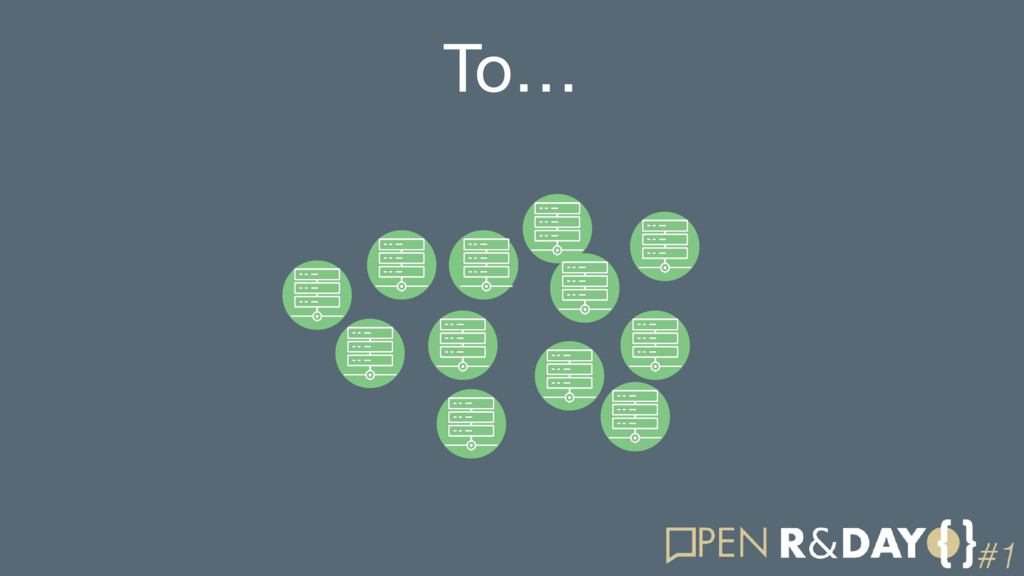
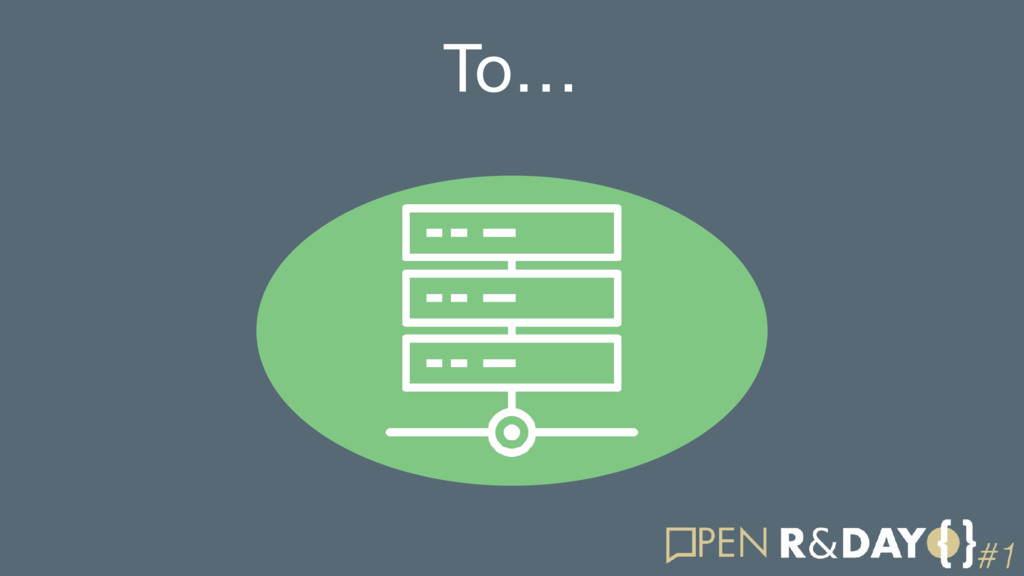
Defense in depth Try smaller trust boundaries
From..
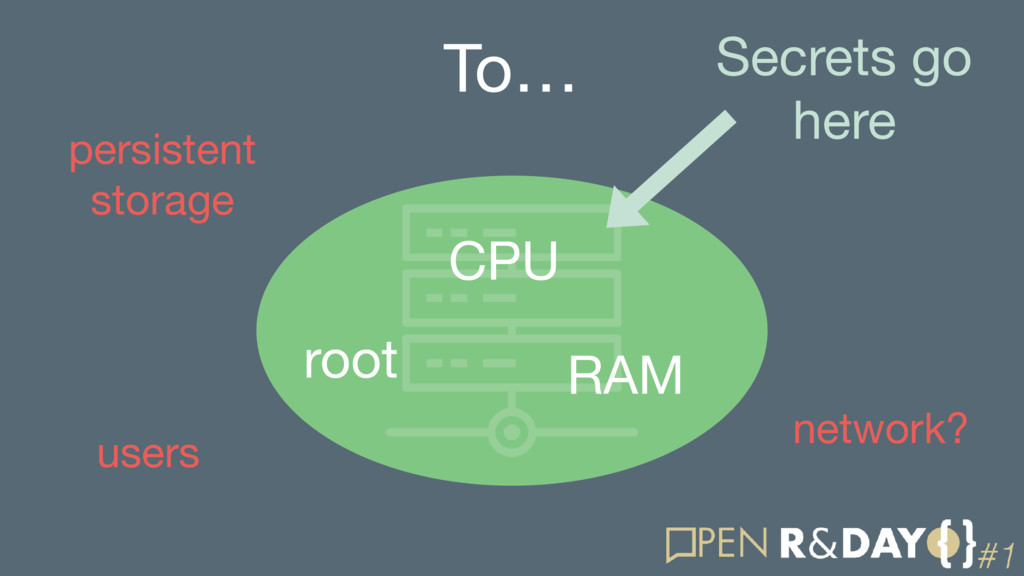
To…
To…
CPU RAM root To… Secrets go here persistent storage users
network?
Traceability & Management
Where are our secrets?
Who can access them?
When are they accessed?
How do we rotate them?
We want those answers BEFORE we need them
The right tool SCM? Configuration management? Secrets management tool
Lots of secrets management tools nowadays Keywhiz (Square) Confidant (Lyft)
KMS (Amazon) Docker Secret
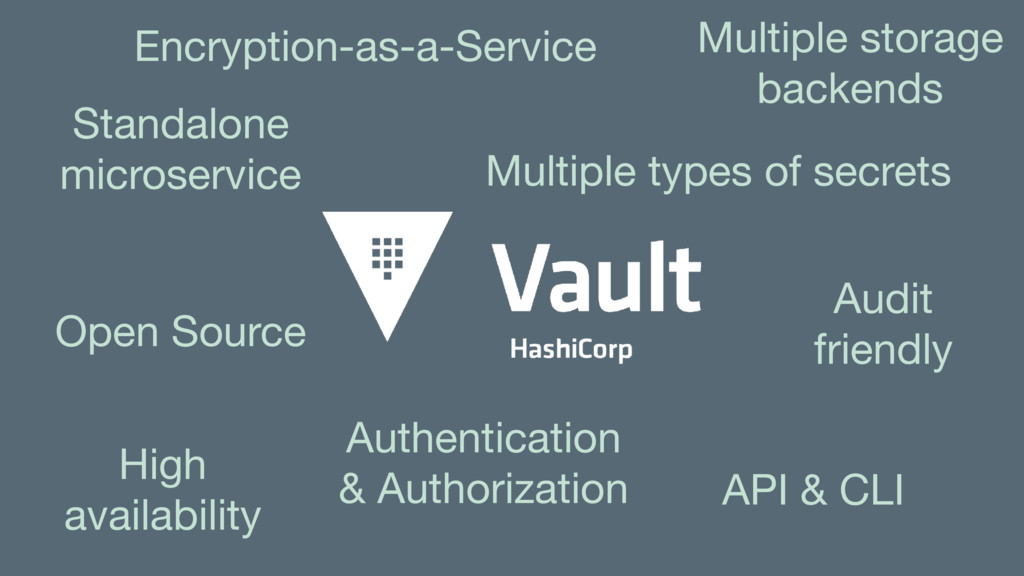
Open Source Multiple storage backends Standalone microservice API & CLI
High availability Encryption-as-a-Service Multiple types of secrets Audit friendly Authentication & Authorization
Demo
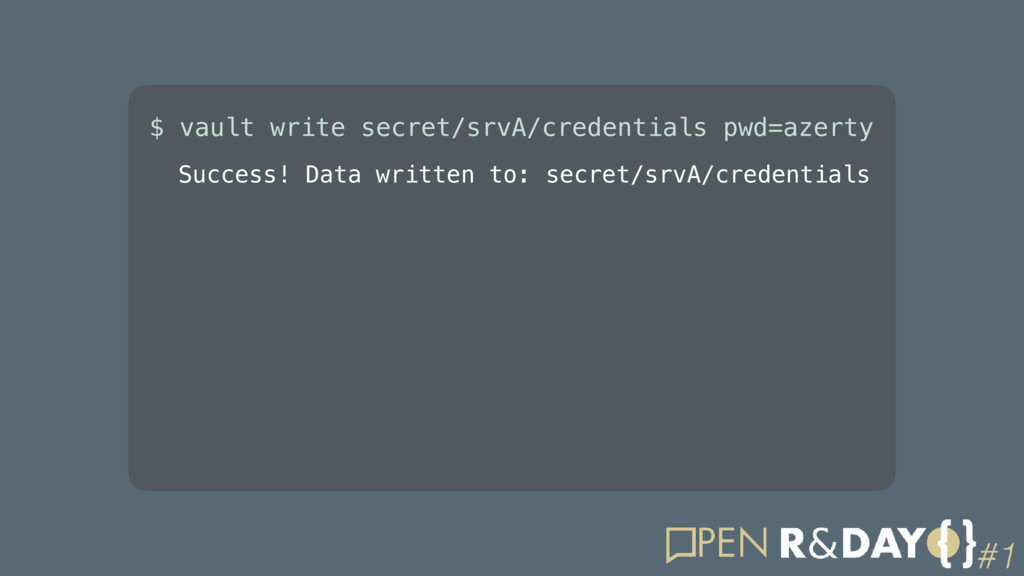
$ vault write secret/srvA/credentials pwd=azerty Success! Data written to: secret/srvA/credentials
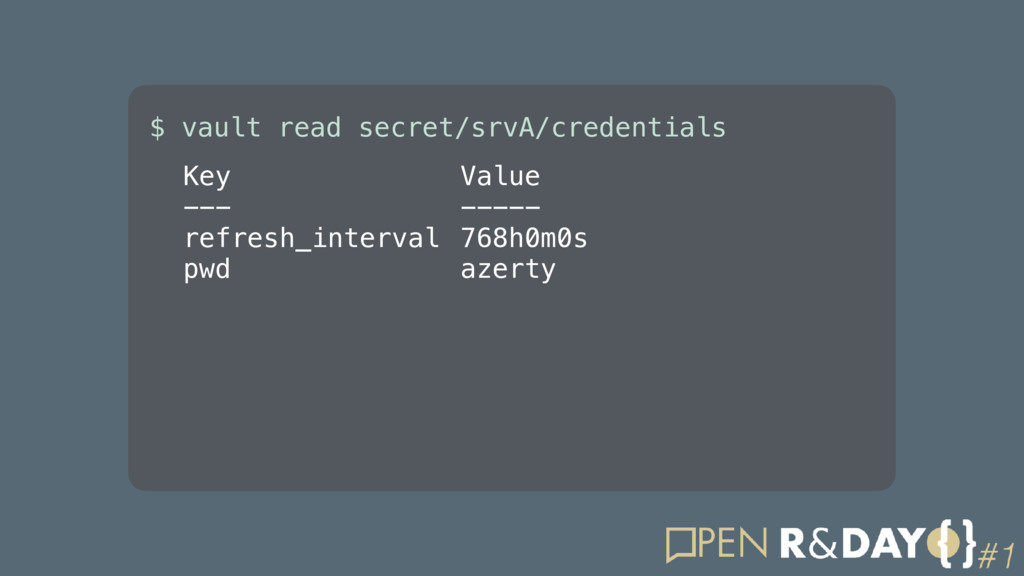
$ vault read secret/srvA/credentials Key Value --- ----- refresh_interval 768h0m0s
pwd azerty
$ vault read /sys/policy/my-service-A path "secret/srvA/*" { capabilities = ["read"]
}
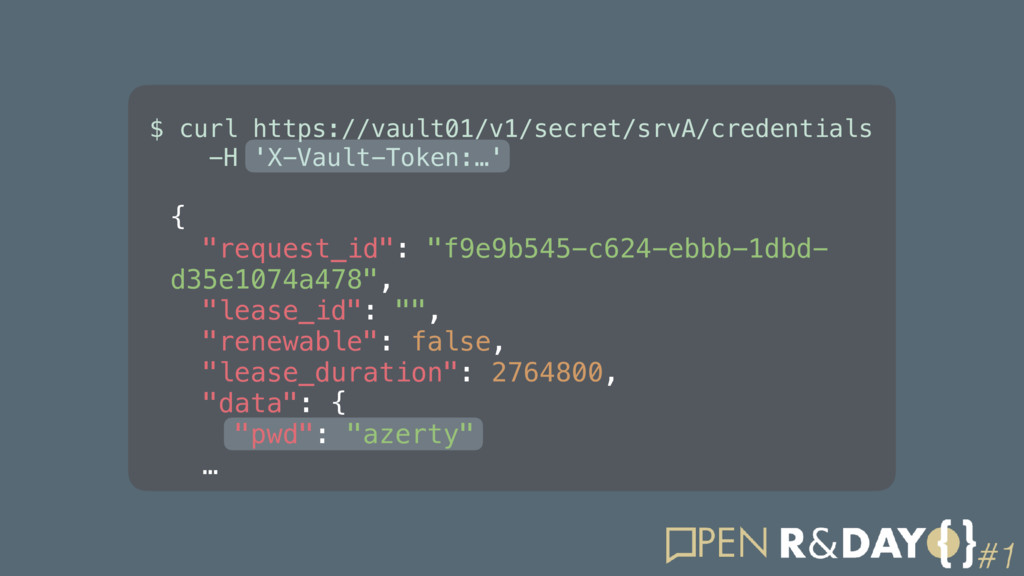
$ curl https://vault01/v1/secret/srvA/credentials -H 'X-Vault-Token:…' { "request_id": "f9e9b545-c624-ebbb-1dbd- d35e1074a478",
"lease_id": "", "renewable": false, "lease_duration": 2764800, "data": { "pwd": "azerty" …
Protecting secrets Turtles all the way down
Secrets are encrypted at rest How does Vault protect secrets?
Encryption keys only live in memory How does Vault protect
secrets?
How to obtain the Master Key? How does Vault protect
secrets?
Master key split in N shards K shards required Vault
sealed until a quorum is reached Shamir secret sharing
How do apps access secrets? Ask Vault at runtime Need
an authentication token How to pass the token to the app?
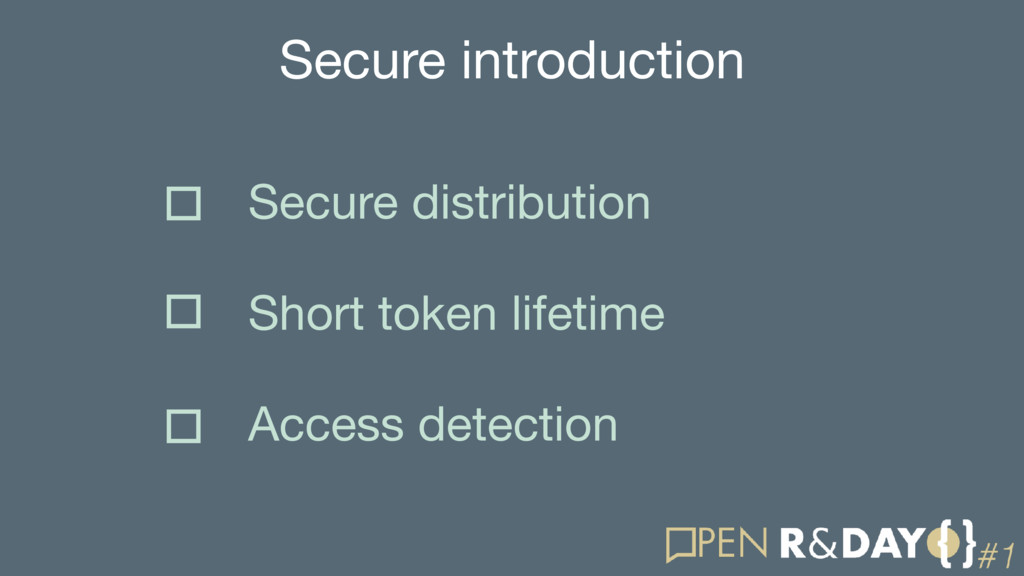
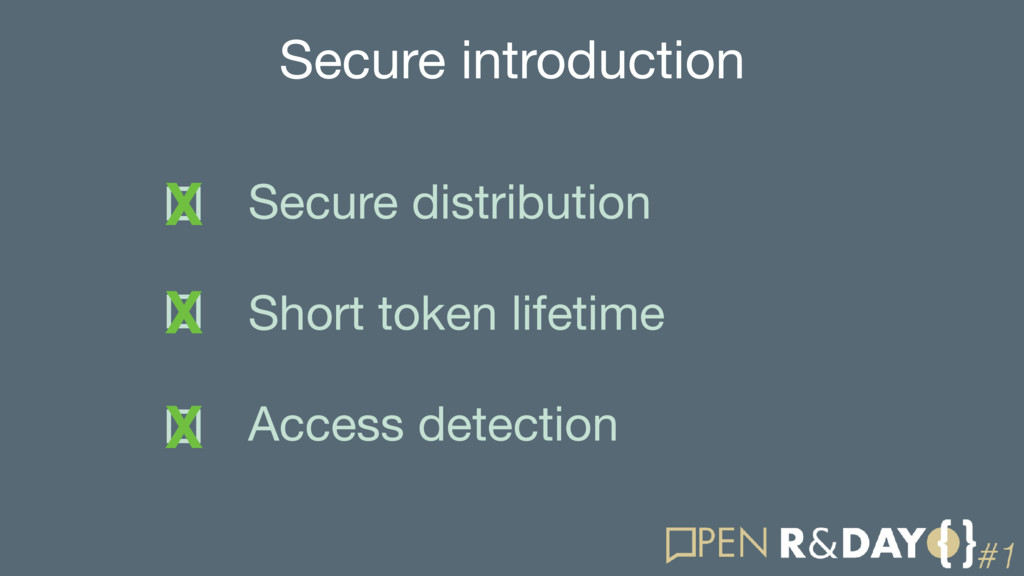
Secure introduction Secure distribution Short token lifetime Access detection
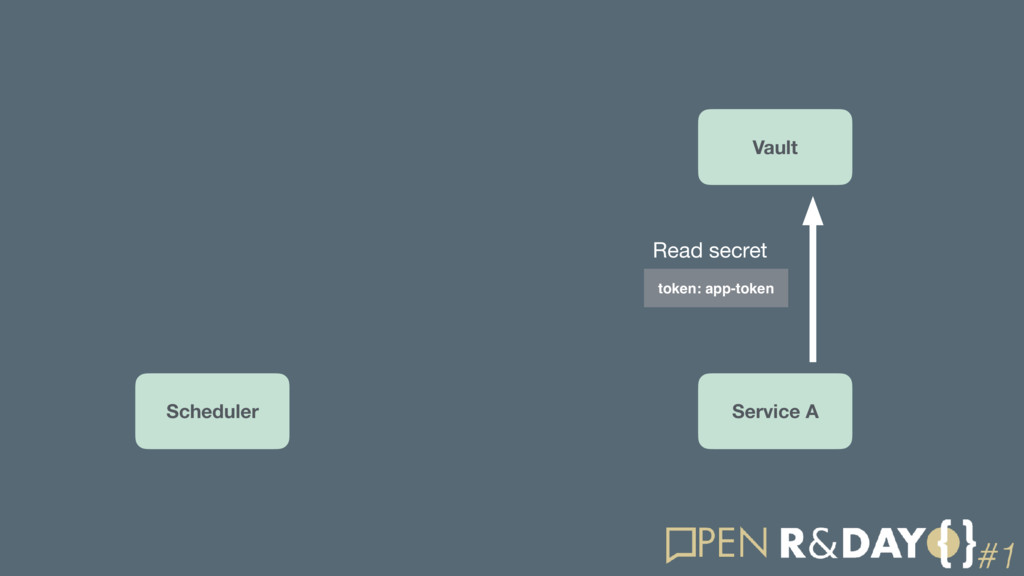
Scheduler Vault Service A
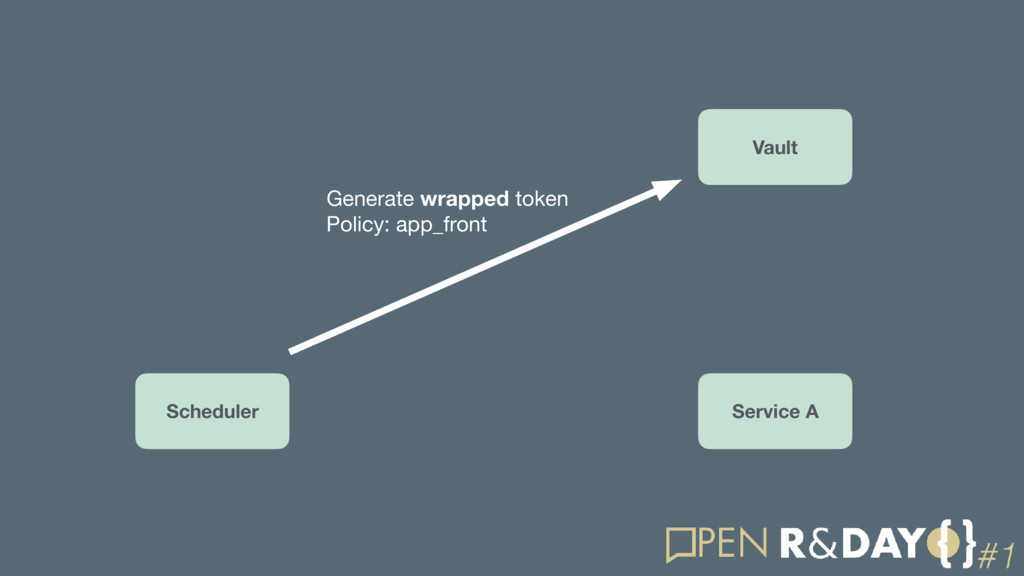
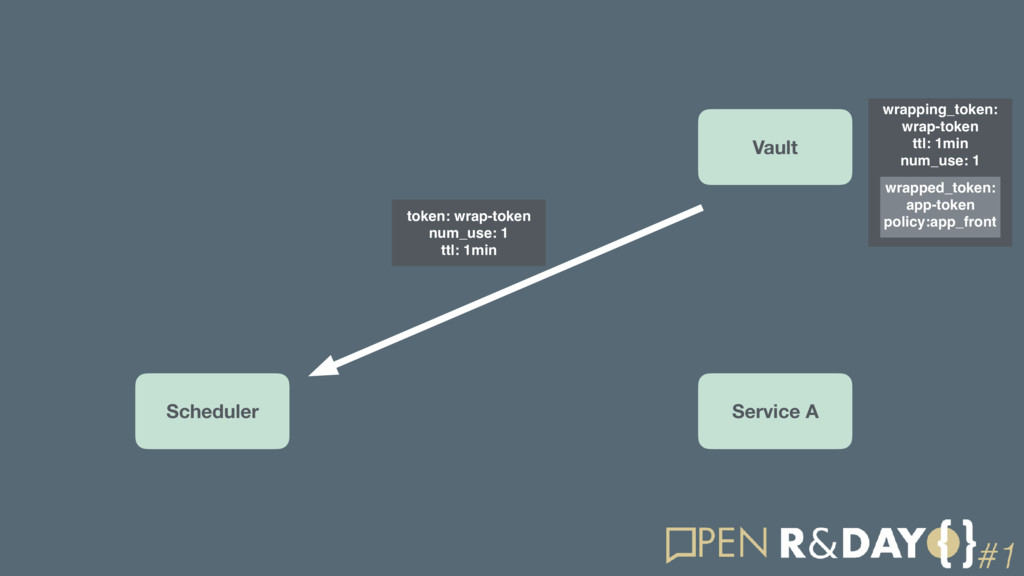
Generate wrapped token Policy: app_front Scheduler Vault Service A
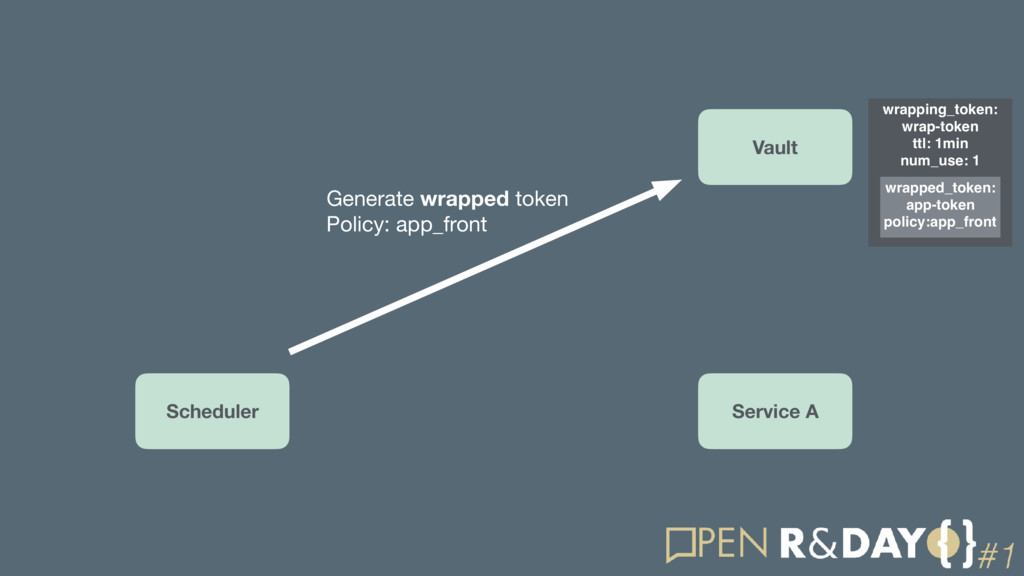
Generate wrapped token Policy: app_front Scheduler Vault Service A wrapping_token:
wrap-token ttl: 1min num_use: 1 wrapped_token: app-token policy:app_front
wrapping_token: wrap-token ttl: 1min num_use: 1 wrapped_token: app-token policy:app_front token:
wrap-token num_use: 1 ttl: 1min Scheduler Vault Service A
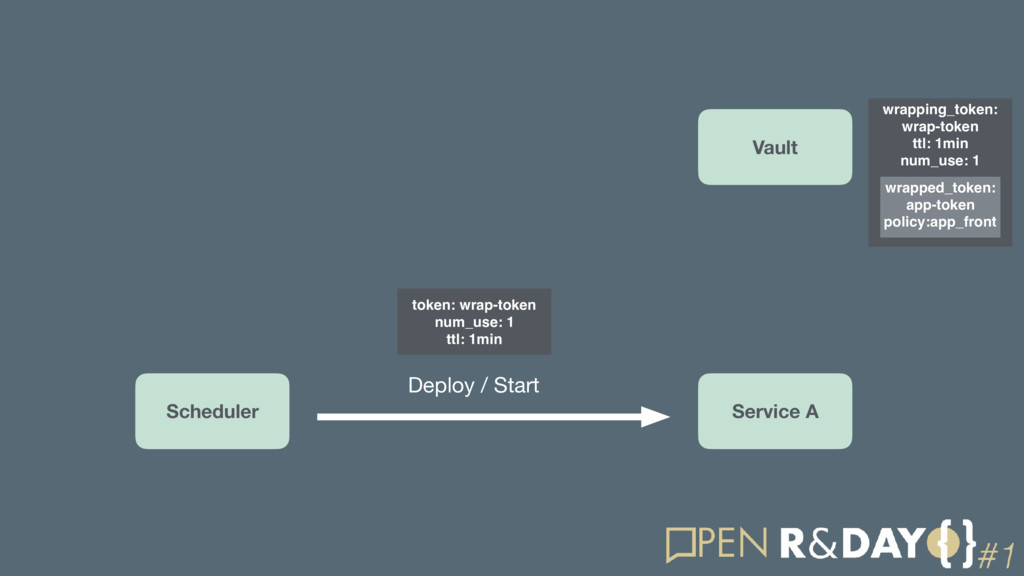
Deploy / Start token: wrap-token num_use: 1 ttl: 1min wrapping_token:
wrap-token ttl: 1min num_use: 1 wrapped_token: app-token policy:app_front Scheduler Vault Service A
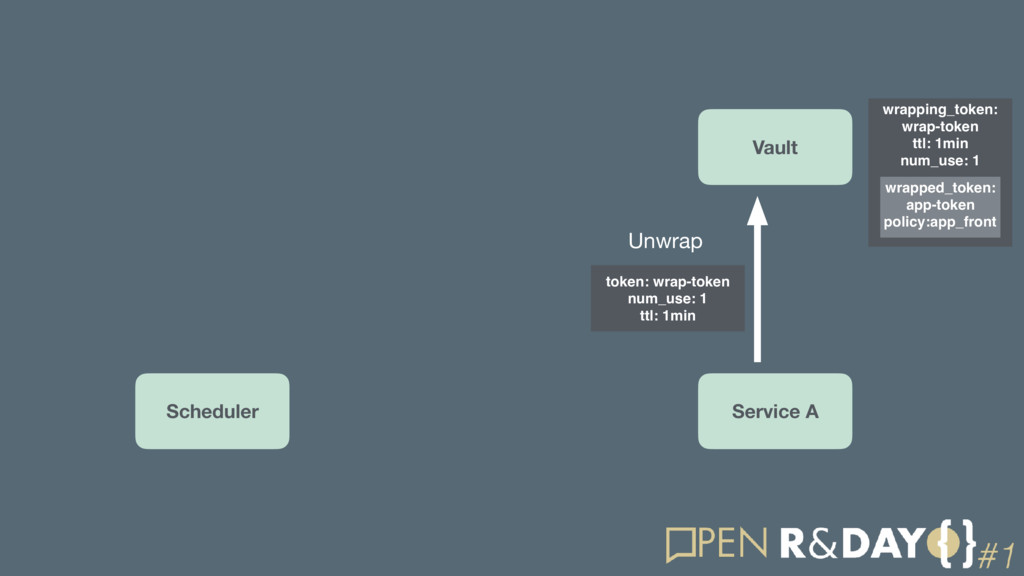
token: wrap-token num_use: 1 ttl: 1min Unwrap wrapping_token: wrap-token ttl:
1min num_use: 1 wrapped_token: app-token policy:app_front Scheduler Vault Service A
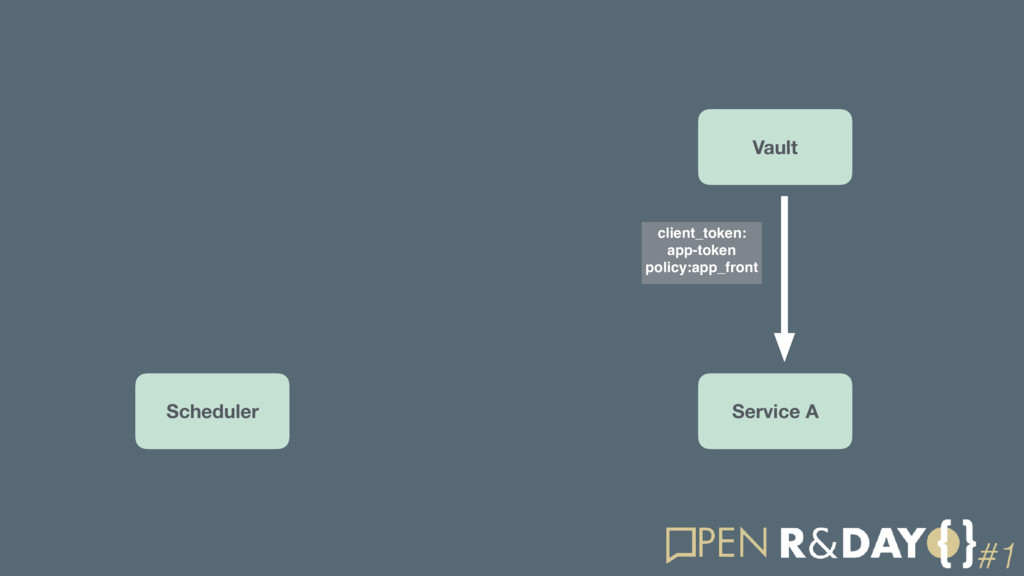
client_token: app-token policy:app_front Scheduler Vault Service A
token: app-token Read secret Scheduler Vault Service A
Secure introduction X X X Secure distribution Short token lifetime
Access detection
Vault @ Oodrive
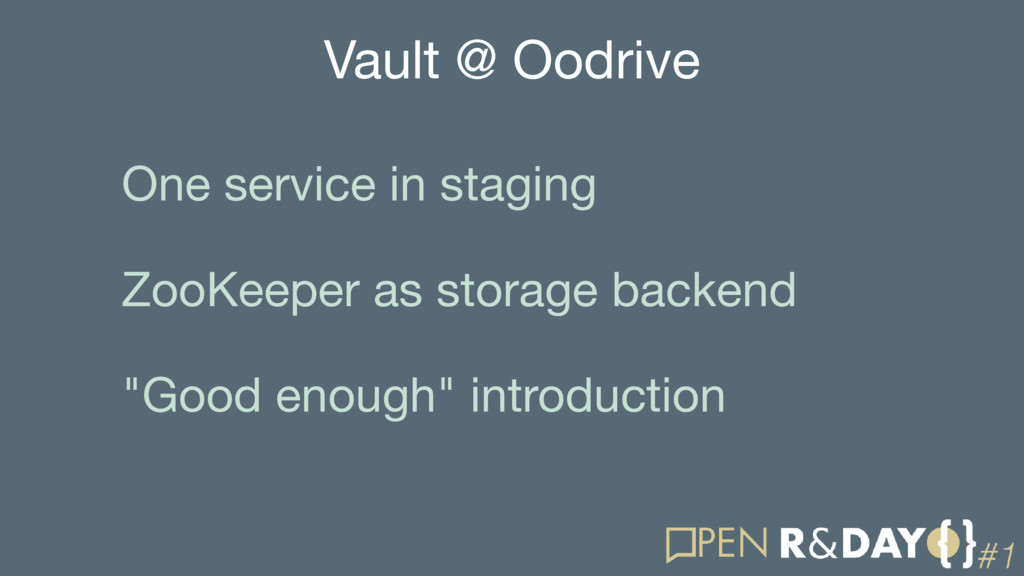
Vault @ Oodrive One service in staging ZooKeeper as storage
backend "Good enough" introduction
Challenges @ Oodrive Ongoing transition to an orchestrated architecture
Challenges @ Oodrive For now: Puppet. No scheduler.
Challenges @ Oodrive Don't want to break everything twice
Challenges @ Oodrive Puppet Server and init script as "scheduler"
Challenges @ Oodrive Leverage existing Puppet authentication
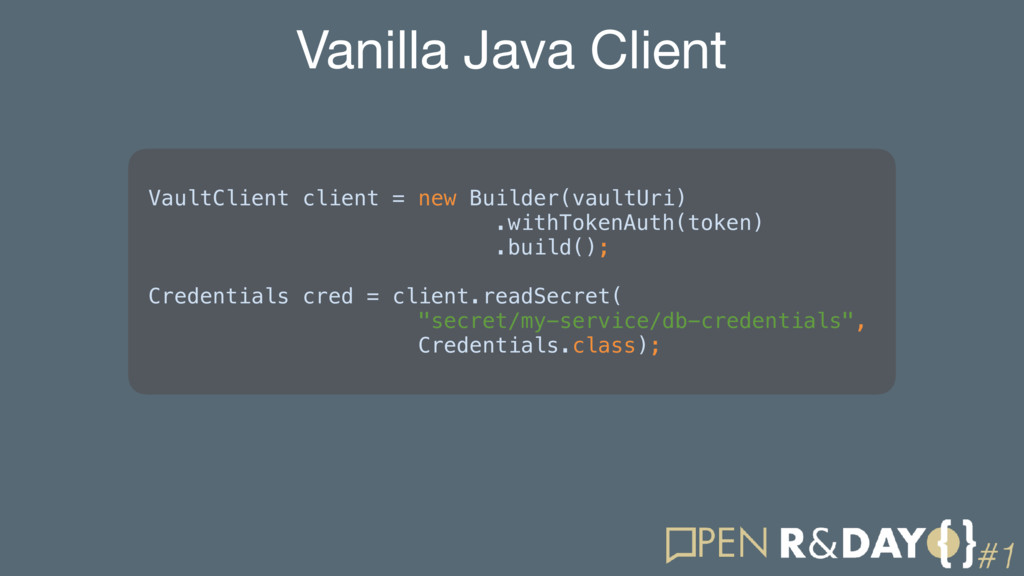
VaultClient client = new Builder(vaultUri) .withTokenAuth(token) .build(); Credentials cred =
client.readSecret( "secret/my-service/db-credentials", Credentials.class); Vanilla Java Client
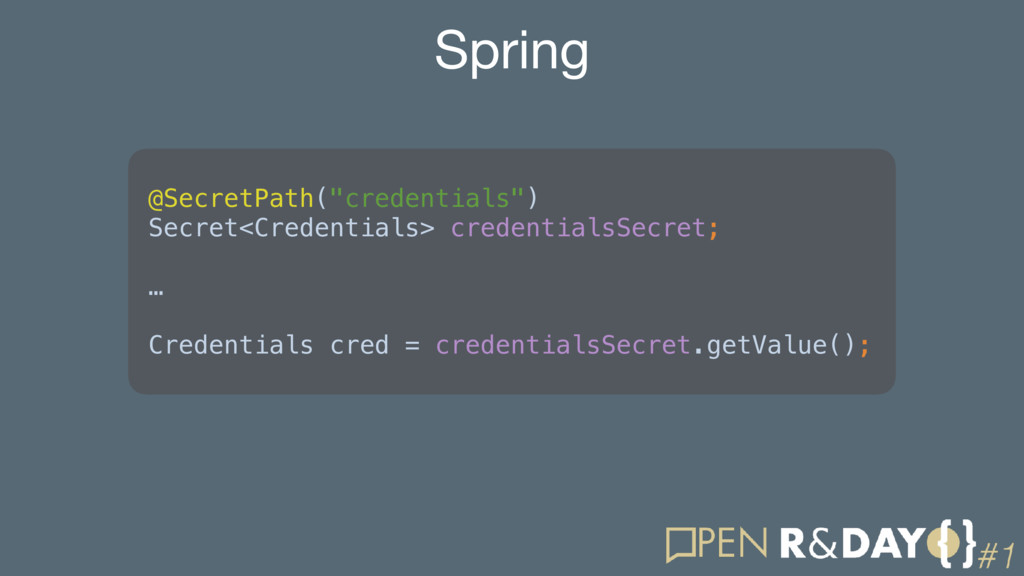
@SecretPath("credentials") Secret<Credentials> credentialsSecret; … Credentials cred = credentialsSecret.getValue(); Spring
Hopefully to be open sourced
Best practices
Least Privilege all the way!
Vault as single secrets repository
Secrets grouped under service name
Use roles for easier management
Enable ACL on ZooKeeper
Next steps Fully secure introduction Dynamic secrets (db credentials) Vault
as internal PKI
Thanks Questions? To win!


 mrartichaut
 kinopeee
 panda728
 repunit11
 colorful12
 mofurune
 tanahiro2010
 yutobara
 nokomoro3
 bells17
 florets1
 gonta
 ichirokano2
 watany
 shpigford
 cromwellryan
 frankvandijk
 bkeepers
 aleyda
 morganepeng
 jacobian
 keavy
 swwweet
 tammielis
 bcantrill