Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
An introduction to AppSec?
Search
Jérémy Courtial
October 23, 2018
Programming
57
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
An introduction to AppSec?
What is Application Security? Why it's important and how it can be implemented in tech teams?
Jérémy Courtial
October 23, 2018
More Decks by Jérémy Courtial
See All by Jérémy Courtial
sudo give the cloud
mrartichaut
0
36
Secure by design: introduction to threat modeling
mrartichaut
0
67
Taming secrets with Vault
mrartichaut
0
110
Lead Tech: Empowering the team
mrartichaut
0
56
Web Platform Security
mrartichaut
0
62
go doSomeThing()
mrartichaut
0
63
Practical Cryptography : Data Encryption
mrartichaut
0
76
Practical Cryptography : Password Hashing
mrartichaut
1
84
HTTP/2 : One connection to rule them all
mrartichaut
1
77
Other Decks in Programming
See All in Programming
sbt 2.0: takeoff
eed3si9n
0
150
Rでドレミ/Do-Re-Mi_with_R
florets1
0
130
AI時代のコードレビューは人に向けるな、仕組みに向けろ
texmeijin
5
3.6k
Agentic Software Factoryに、すごく賢いIF文を。 / super smart IF statement into the Agentic Software Factory.
rkaga
8
2.1k
AI主導のプログラミング学習アプリを作ってみた
econanringo
0
160
IBM Bob Dojo #1 仕様駆動開発入門
oniak3ibm
PRO
0
380
Turning Architecture into Unit Tests in the AI Era (NSSpain XIV)
steliosf
PRO
1
140
Augmenting AI with the Power of Jakarta EE
ivargrimstad
0
650
Event is what happens
moro
1
340
Jetpack Compose Mechanisms
skydoves
2
730
[2026-09-26]空論ジェネリックプロセス~テスト資産とAIで紡ぐ、再現可能なパフォーマンスチューニングの話~
tosite
0
270
C#の現在地 進化の歴史と、AI時代の.NET Everywhere
neuecc
5
5.1k
Featured
See All Featured
Navigating the moral maze — ethical principles for Al-driven product design
skipperchong
2
630
Joys of Absence: A Defence of Solitary Play
codingconduct
1
550
"I'm Feeling Lucky" - Building Great Search Experiences for Today's Users (#IAC19)
danielanewman
230
23k
Build your cross-platform service in a week with App Engine
jlugia
234
19k
Refactoring Trust on Your Teams (GOTO; Chicago 2020)
rmw
35
3.8k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
Practical Orchestrator
shlominoach
192
12k
Ecommerce SEO: The Keys for Success Now & Beyond - #SERPConf2024
aleyda
1
2.2k
Facilitating Awesome Meetings
lara
57
7.2k
B2B Lead Gen: Tactics, Traps & Triumph
marketingsoph
1
280
Introduction to Domain-Driven Design and Collaborative software design
baasie
1
1k
Information Architects: The Missing Link in Design Systems
soysaucechin
1
1.2k
Transcript
An introduction to AppSec Jérémy Courtial Software Security Architect @JeremyCourtial
AppSec?
Application Secucirty?
It’s not just about firewall
Combination of 3 bugs leading to privilege escalation https://newsroom.fb.com/news/2018/09/security-update/
Unpatched Apache Struts with critical Remote Execution vulnerability. (Plus lake
of defence in depth?)
« Application security encompasses measures taken to improve the security
of an application often by finding, fixing and preventing security vulnerabilities. » Wikipedia
It not just about finding & fixing It’s how applications
are made
Security is not a feature It’s a property like performance
and reliability
Security should be addressed at each step of the development
lifecycle
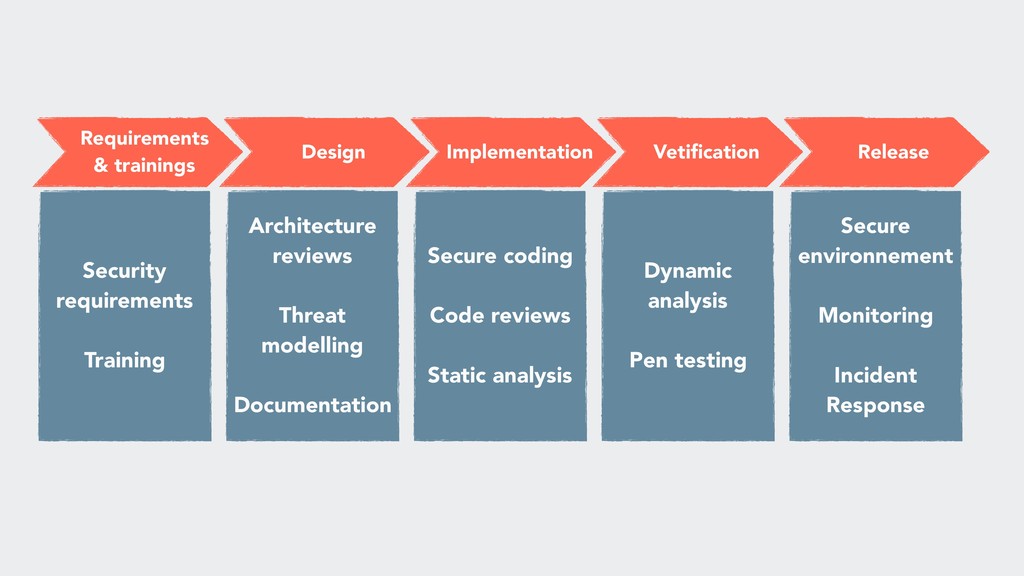
Design Implementation Vetification Release Security requirements Training Architecture reviews Threat
modelling Documentation Secure coding Code reviews Static analysis Dynamic analysis Pen testing Secure environnement Monitoring Incident Response Requirements & trainings
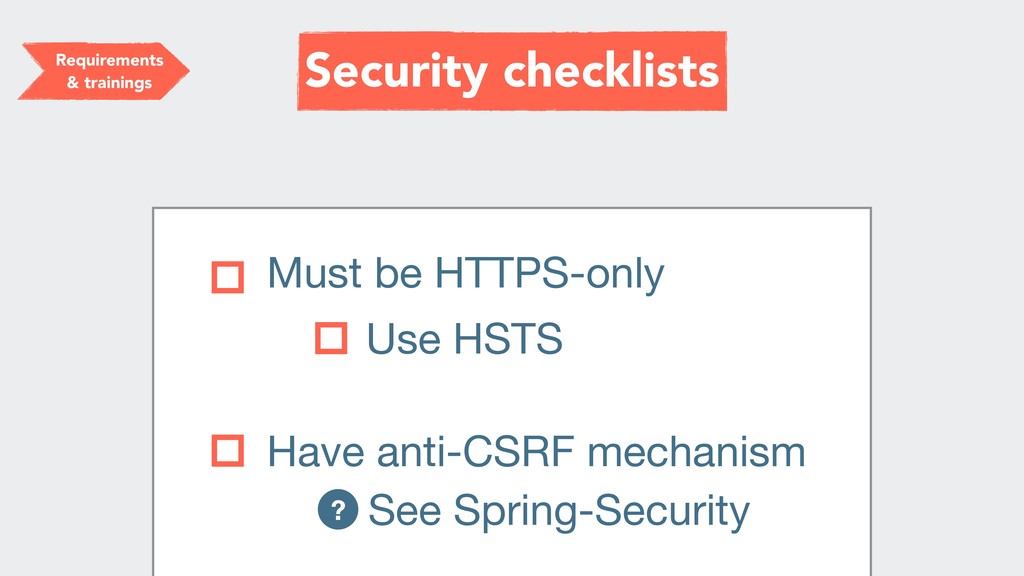
Requirements & trainings Use HSTS Must be HTTPS-only Have anti-CSRF
mechanism See Spring-Security ? Security checklists
Design Feedbacks-oriented meeting before any major changes enters development. Identifying
subjects that need closer follow-ups. Ensuring best practices. Architecture reviews
Impl. Static analysis Code analysis: Looks for common vulnerabilities pattern
in code. Composition analysis: Looks for vulnerable dependencies.
Impl. Static analysis Code analysis Composition analysis
Verification Dynamic analysis Looks for common vulnerabilities in live applications.
OWASP ZAP
Release Secure environment Up-to-date infrastructure (« patch, patch, patch… »)
Host hardening: system, Docker, k8s, etc. Protected and segmented networks
Who ?
None
Security champions One per team/platform Infuses security in daily activities
Security owner Owns the threat model Leads structural projects Harmonises
practices Leans on champions
Security team Varies skills: - DevSec - Pen testing -
Network & system - Compliance - …
How ?
Don’t be a faceless gate
Support Help Devs to produce more secure apps! Tools, guidance,
feedback, even code!
Partnership Communicate goals, roadmaps, challenges, etc. We all want to
ship ours (secure) products Shared responsibility
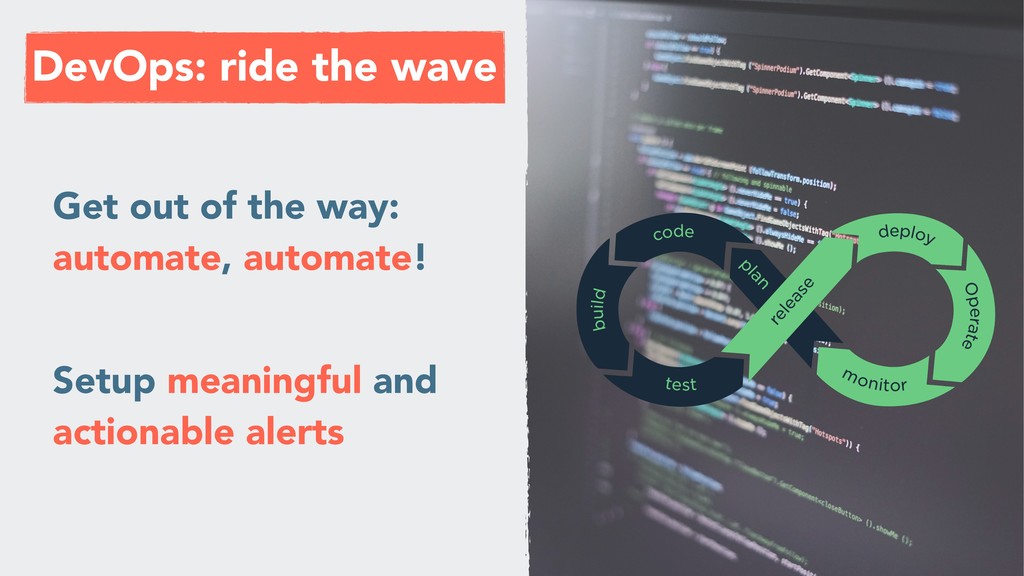
Get out of the way: automate, automate! Setup meaningful and
actionable alerts DevOps: ride the wave
Security is impor Last challenge: awareness
openrday.oodrive.fr Come talk about dev, security, etc.
Thank you!


 mrartichaut
 eed3si9n
 florets1
 texmeijin
 rkaga
 econanringo
 oniak3ibm
 steliosf
 ivargrimstad
 moro
 skydoves
 tosite
 neuecc
 skipperchong
 codingconduct
 danielanewman
 jlugia
 rmw
 destraynor
 shlominoach
 aleyda
 lara
 marketingsoph
 baasie
 soysaucechin