Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Practical Cryptography : Data Encryption
Search
Jérémy Courtial
October 22, 2015
Programming
76
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Practical Cryptography : Data Encryption
Jérémy Courtial
October 22, 2015
More Decks by Jérémy Courtial
See All by Jérémy Courtial
sudo give the cloud
mrartichaut
0
36
An introduction to AppSec?
mrartichaut
0
57
Secure by design: introduction to threat modeling
mrartichaut
0
67
Taming secrets with Vault
mrartichaut
0
110
Lead Tech: Empowering the team
mrartichaut
0
56
Web Platform Security
mrartichaut
0
62
go doSomeThing()
mrartichaut
0
63
Practical Cryptography : Password Hashing
mrartichaut
1
84
HTTP/2 : One connection to rule them all
mrartichaut
1
77
Other Decks in Programming
See All in Programming
速習iPhone Duo対応
yuukiw00w
2
980
AI が書く Go コードの品質を劇的に向上させる Linter: “declscope”
mpyw
0
490
Kotlinの15年とServer-Side Kotlin
n_takehata
1
140
Optunaを作ったときにやりたかったこと、その後 (2026/10/16, Optuna Meetup #3)
iwiwi
0
100
Unity6 URPによる海底をテーマにしたVJシステムの解説 | Unity Shader 完全に理解した 勉強会
gam0022
0
360
AI時代のコードレビューは人に向けるな、仕組みに向けろ
texmeijin
5
3.6k
Atomic Design, Enforced: Scaling Mobile Design Systems (next.app devCon / droidCon Berlin 2026)
steliosf
PRO
0
170
Apple Intelligence を用いた個人情報誤送信防止、及びユーザーリクエスト体験の改善について
yukiny
0
330
re:Inventに行く前に知っておきたい現地参加のノウハウ
nokomoro3
0
410
Kubernetes祭り #2 OP/ED
bells17
0
110
Verilogで学ぶCPU自作入門
uyuki234
8
4.1k
気持ちぃ〜角丸 Squircle
ryu1013
0
290
Featured
See All Featured
The Director’s Chair: Orchestrating AI for Truly Effective Learning
tmiket
1
330
Context Engineering - Making Every Token Count
addyosmani
9
1.2k
Art, The Web, and Tiny UX
lynnandtonic
304
22k
From Legacy to Launchpad: Building Startup-Ready Communities
dugsong
0
350
Making the Leap to Tech Lead
cromwellryan
135
10k
Automating Front-end Workflow
addyosmani
1369
210k
Building an army of robots
kneath
307
47k
Intergalactic Javascript Robots from Outer Space
tanoku
273
27k
How to make the Groovebox
asonas
2
2.5k
SERP Conf. Vienna - Web Accessibility: Optimizing for Inclusivity and SEO
sarafernandez
2
1.6k
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
2
6.3k
Transcript
Jérémy Courtial Data encryption Practical cryptography
Password hashing breaking news
Final impl. on the way Winner : Argon2 Goal: find
a new password hashing algorithm Password Hashing Competition
Now back to the subject
Confidentiality Hide things
Authentication Ensure thing’s owner
Integrity Check things
The Cryptography Club’s Rules
Rule #1 Don’t reinvent crypto
Rule #2 Don’t reinvent crypto
Be aware of the Kerckhoffs Principle Rule #3
« The enemy knowns the system »
Forget about « security through obscurity »
The key is the secret
Data Encryption
Not messing up Cipher stuff Keys management Challenges
Key Management
Should be easy to retrieve Must be kept secret (from
Rule #3) Maximum entropy Key Properties
Con: must be shared between actors Pro: shorter keys, ie.
better performances Opposed to asymmetric keys (obviously…) Symmetric Key
Network services (ex: Vault) OS level container (ex: Keychain) Specialised
hardware (ex: HSM) Key Storage
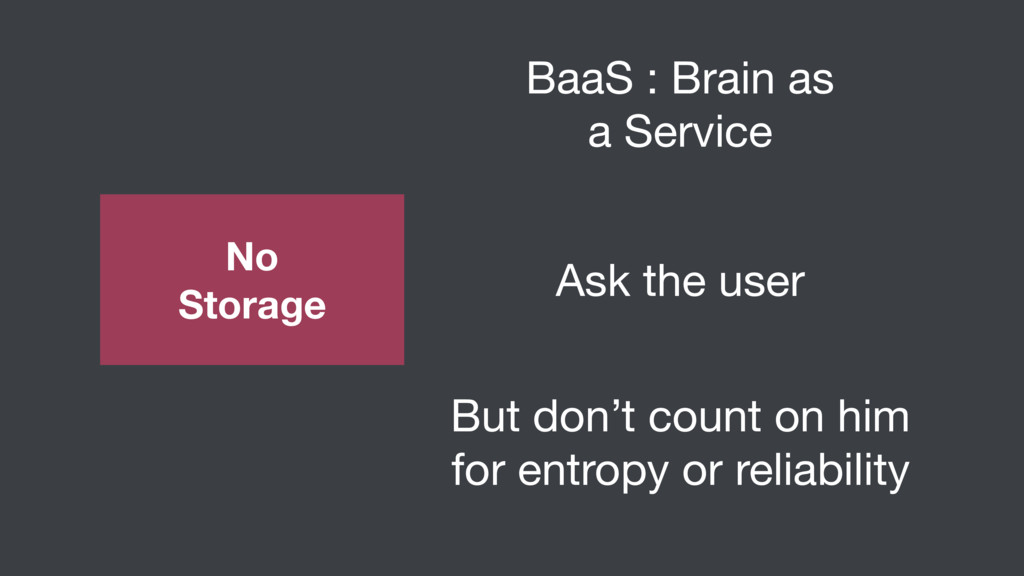
Better : no storage
But don’t count on him for entropy or reliability Ask
the user BaaS : Brain as a Service No Storage
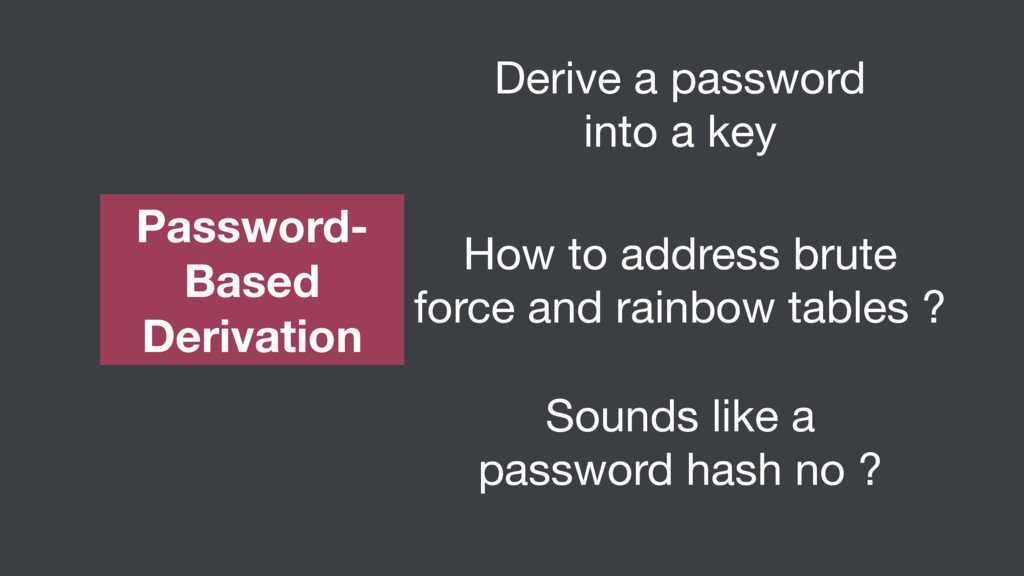
Sounds like a password hash no ? How to address
brute force and rainbow tables ? Derive a password into a key Password- Based Derivation
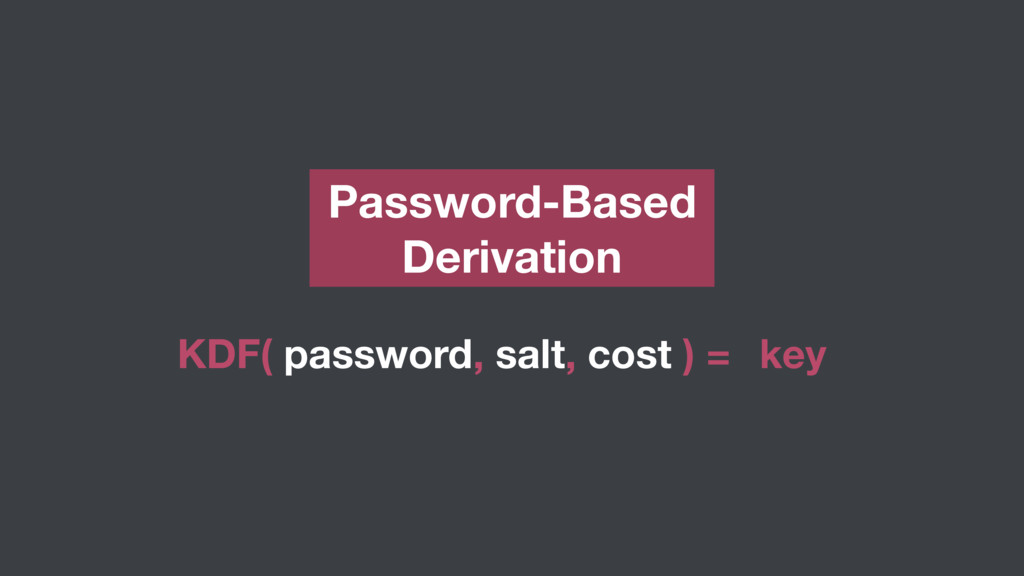
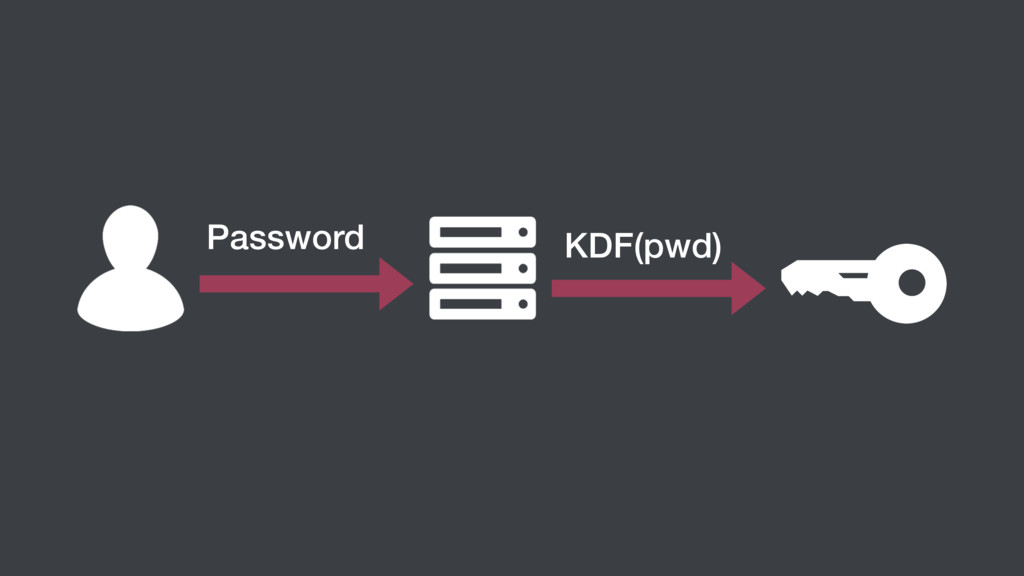
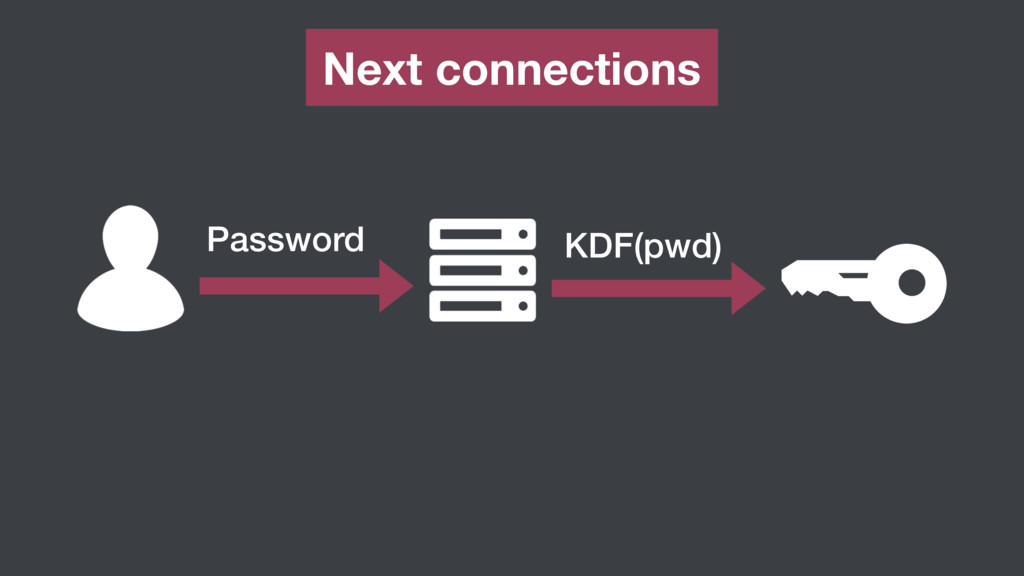
Password-Based Derivation KDF( password, salt, cost ) = key
Do not store the result ! The key only live
in memory Derived when need Key Derivation
Password KDF(pwd)
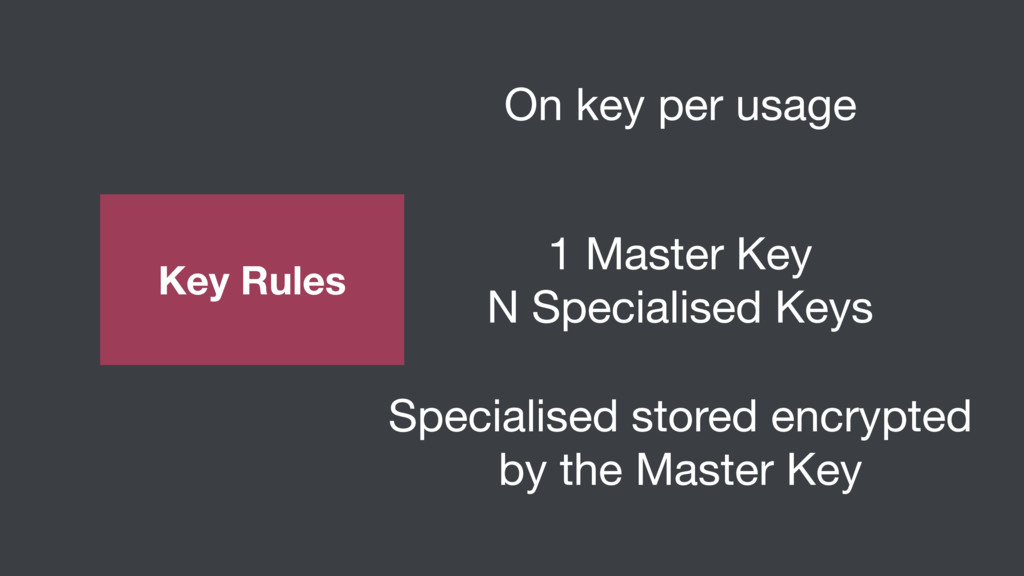
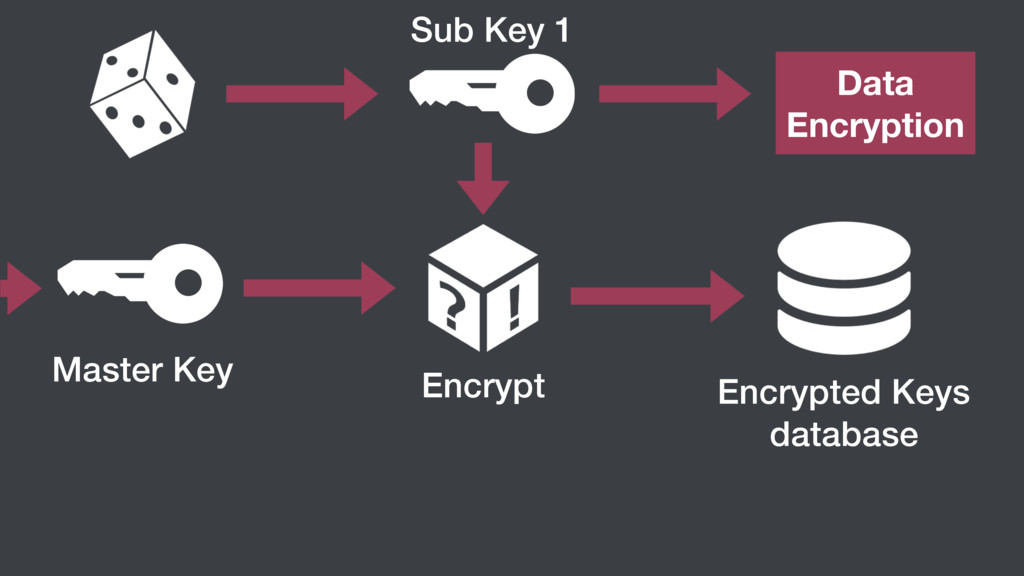
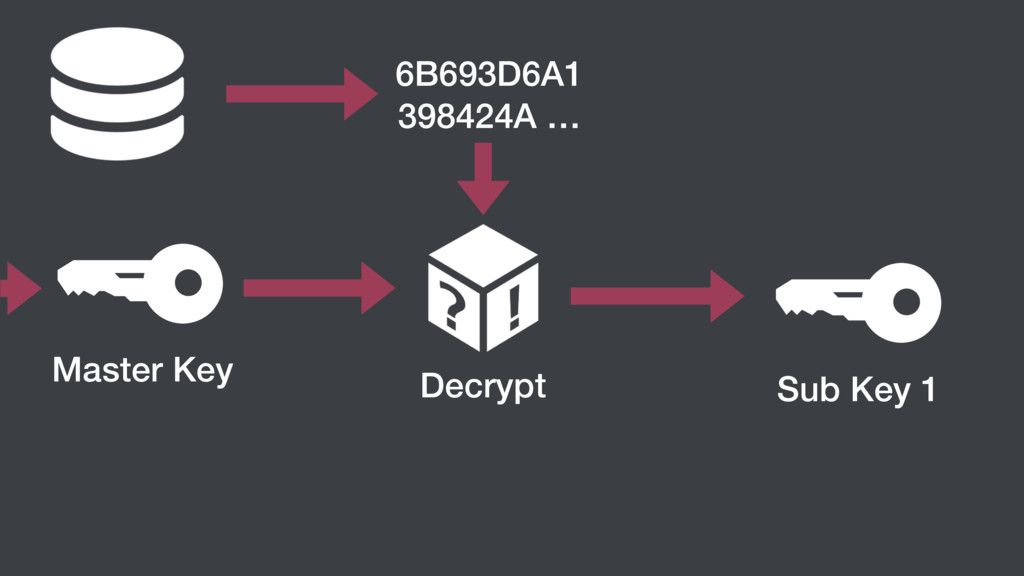
Specialised stored encrypted by the Master Key 1 Master Key
N Specialised Keys On key per usage Key Rules
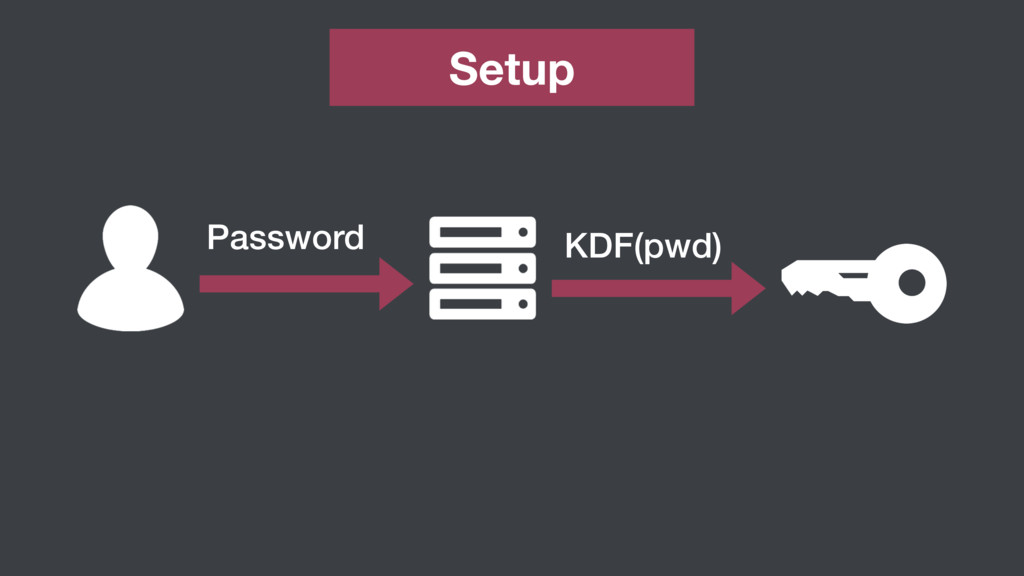
Password KDF(pwd) Setup
Encrypt Sub Key 1 Master Key Data Encryption Encrypted Keys
database
Password KDF(pwd) Next connections
Decrypt Master Key 6B693D6A1 398424A … Sub Key 1
Data Encryption
data encryption
None
None
What’s just happen ??
Know what you’re doing APIs are usually terrible and don’t
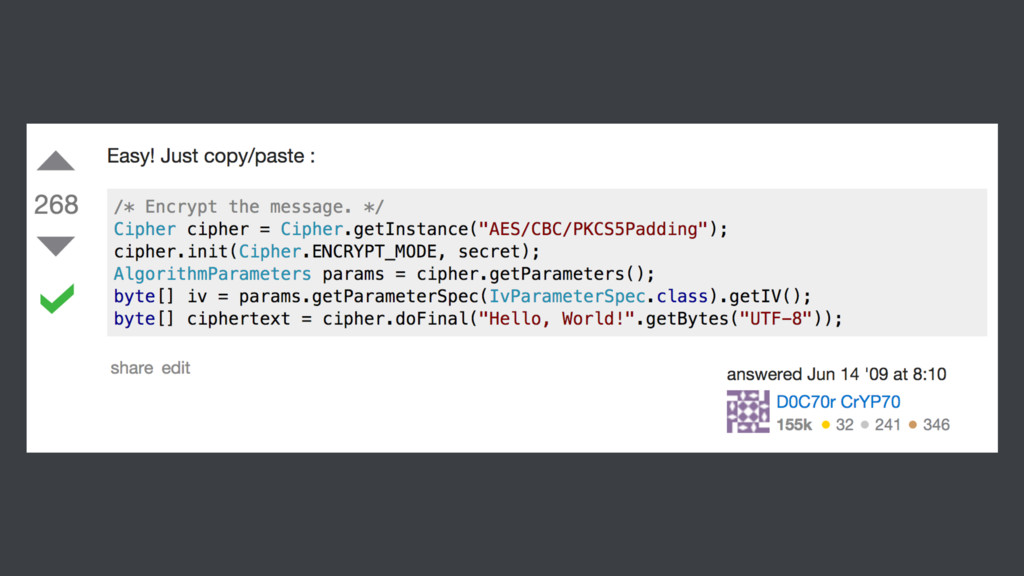
help Stack Overflow is not a way to learn crypto Data Encryption
The harder part : use it correctly Choose a mode
(if relevant) Choose an algorithm Encryption : How to ?
What about certifications ? Good cryptanalysis, well implemented Symmetric encryption
algorithm Which algorithm ?
Won’t save you RGS (ANSSI) in France FIPS for US
& international Certifications See keylength.com
Have a doubt ? A E S dvance crypton tandard
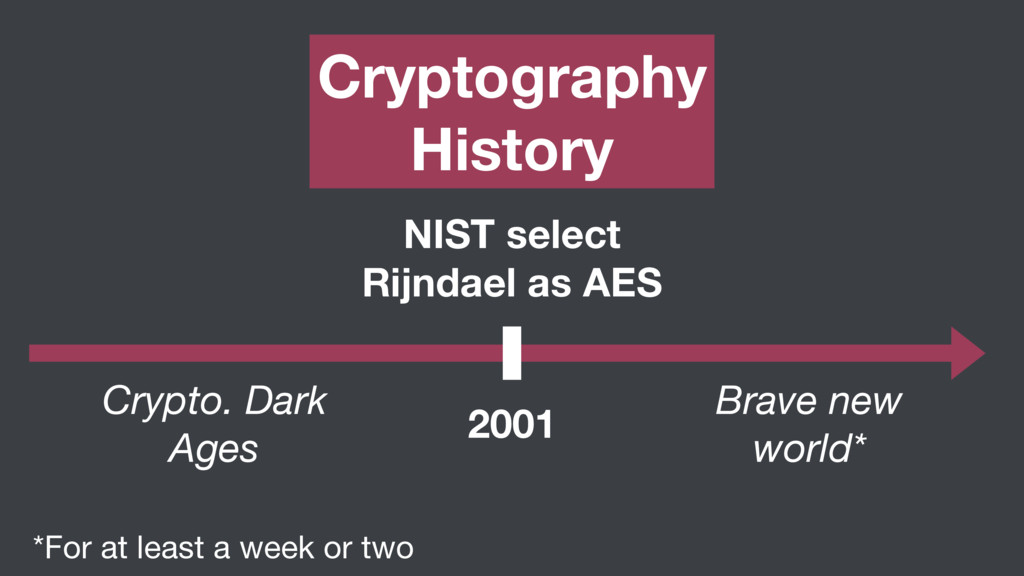
Cryptography History 2001 NIST select Rijndael as AES Crypto. Dark
Ages Brave new world* *For at least a week or two
Most studied algorithm, no realistic attack Universally supported « Nobody
ever get fired for choosing AES » AES
Choose your AES mode (You thought it was that simple
?)
None
blabla blabla blabla blabla not ECB blabla blabla blabla blabla
blabla blabla blabla blabla not OCB blabla blabla block cipher blabla blabla blabla blabla blabla blabla blabla blabla blabla blabla blabla CBC blabla blabla blabla blabla blabla blabla blabla padding blabla blabla blabla CTR blabla blabla blabla blabla blabla blabla blabla blabla stream cipher blabla blabla counter blabla blabla blabla blabla blabla blabla Please stop It’s already 18h no ? I want to die… I will never do crypto…
Just tell me what to choose…
What do we need ? Confidentiality
What do we need ? Confidentiality Not just
How to detect tampering ? Some modes are very malleable
Attacks are rarely read-only Cipher text tampering
What do we need ? Confidentiality
What do we need ? Confidentiality, Authentication, Integrity
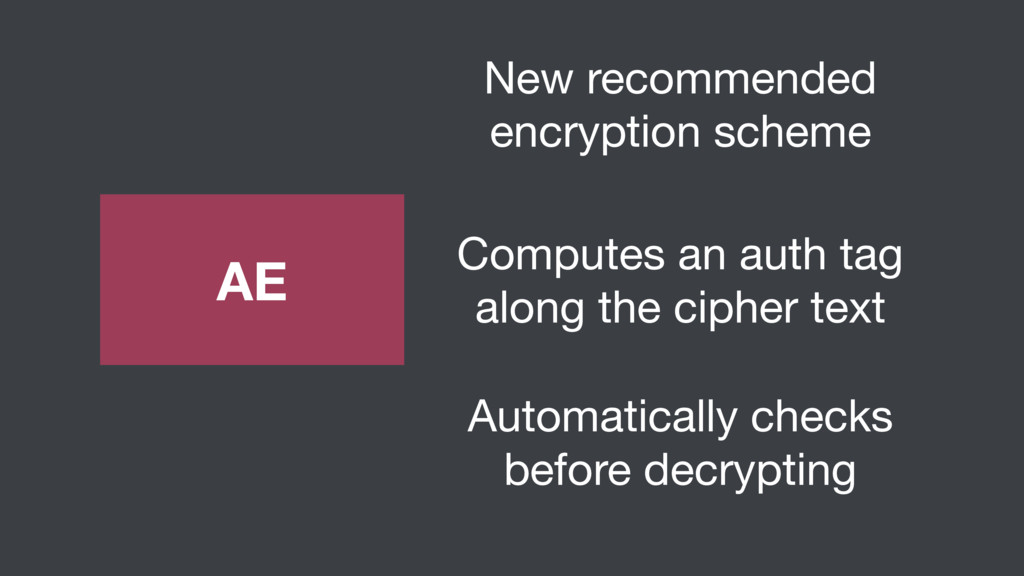
What do we need ? Authenticated Encryption
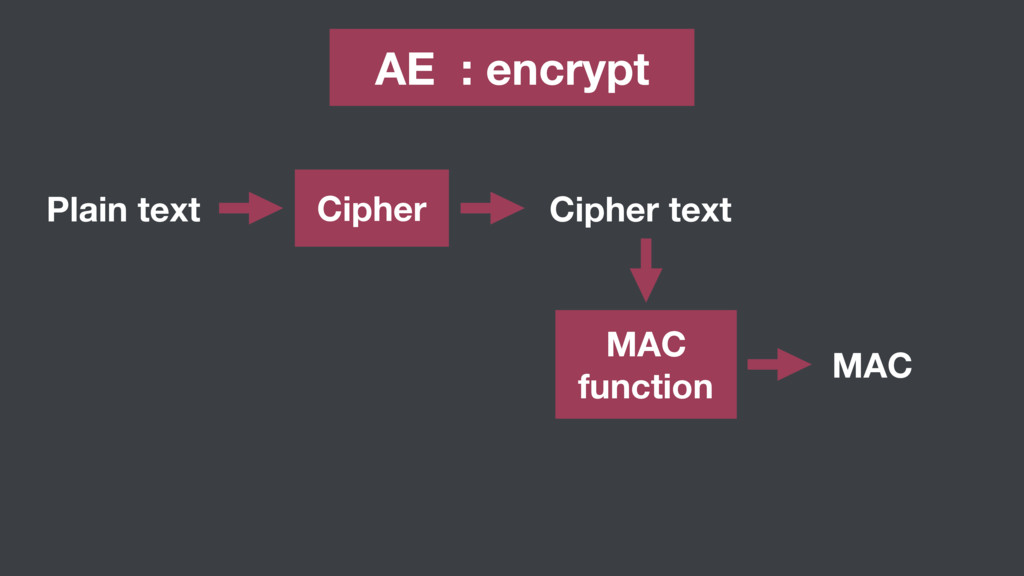
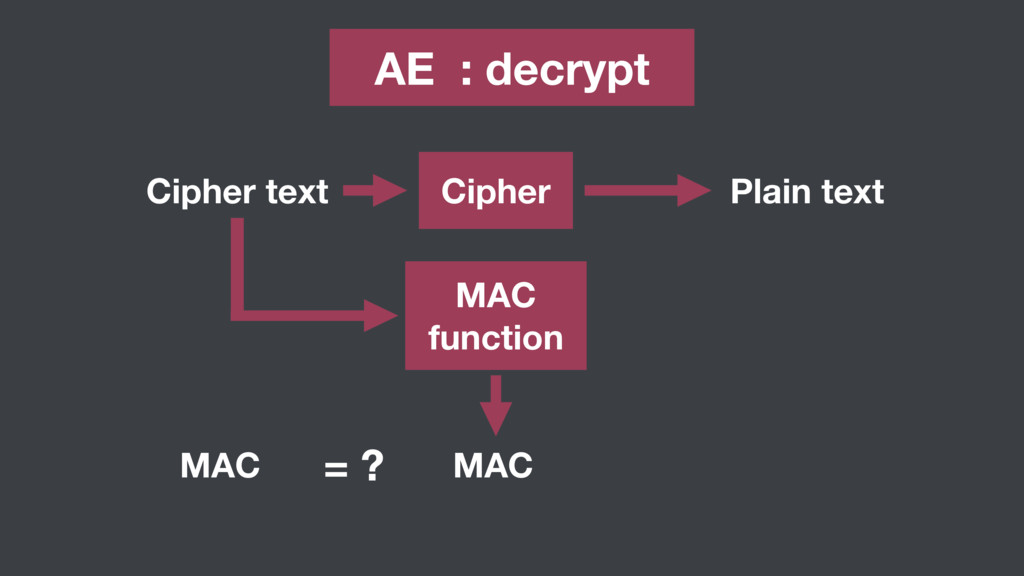
Automatically checks before decrypting Computes an auth tag along the
cipher text New recommended encryption scheme AE
Plain text Cipher Cipher text MAC MAC function AE :
encrypt
Cipher text Cipher Plain text MAC MAC MAC function =
? AE : decrypt
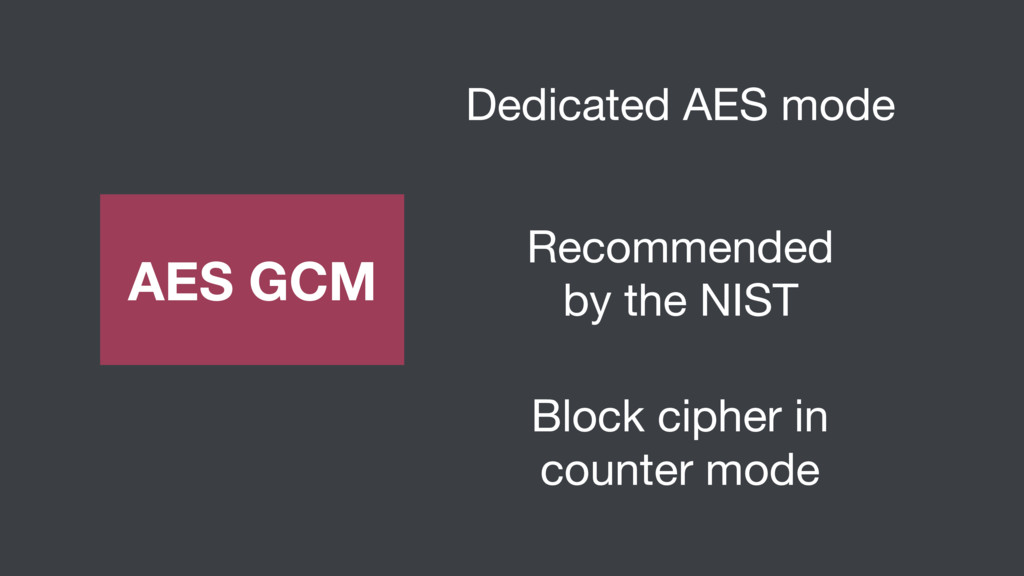
Block cipher in counter mode Recommended by the NIST Dedicated
AES mode AES GCM
What if I don’t have GCM ? Do It Yourself
style* *Not recommended
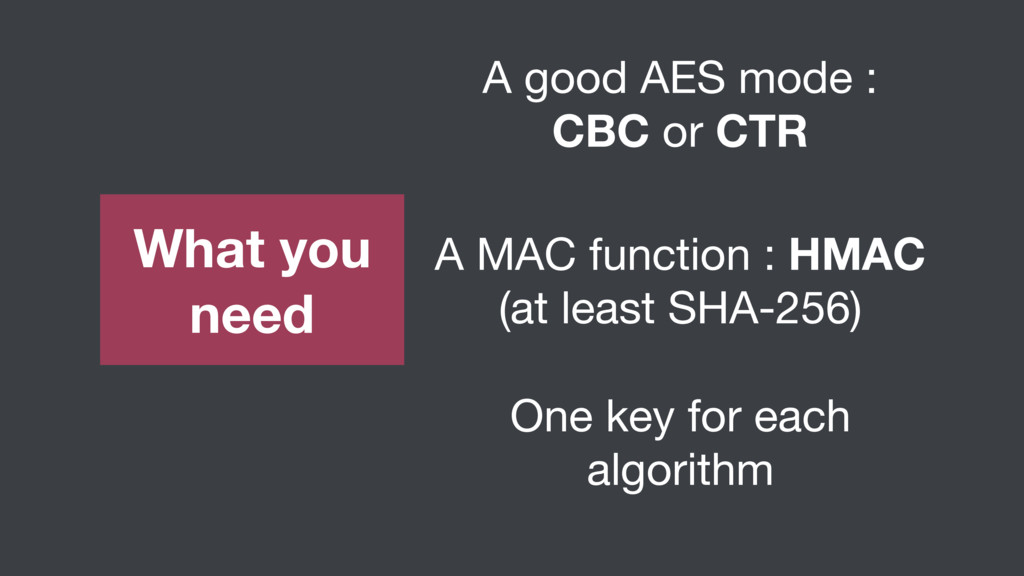
One key for each algorithm A MAC function : HMAC
(at least SHA-256) A good AES mode : CBC or CTR What you need
One rule Encrypt-Then-Mac
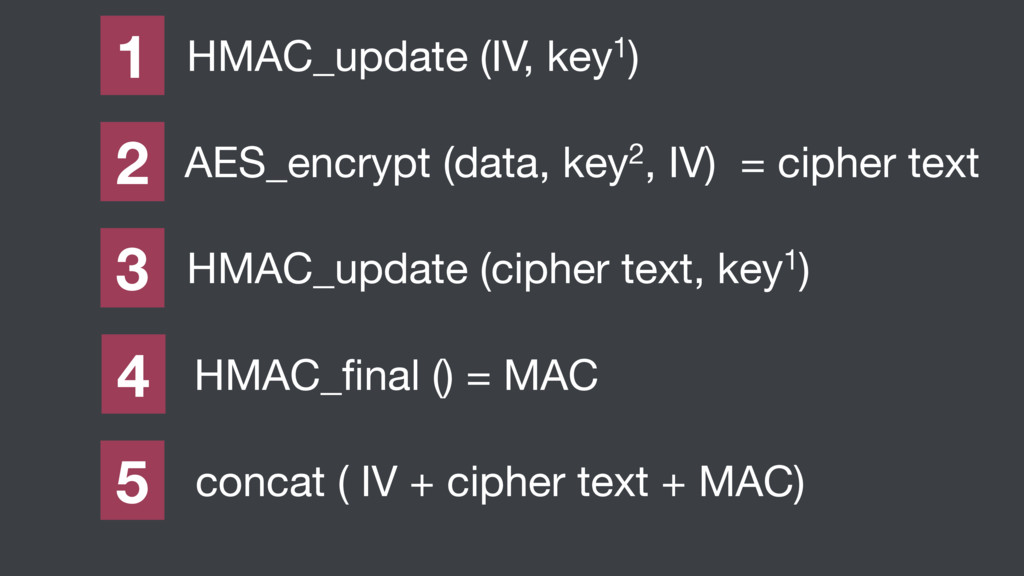
HMAC_update (IV, key1) 1 AES_encrypt (data, key2, IV) = cipher
text 2 HMAC_update (cipher text, key1) 3 concat ( IV + cipher text + MAC) 5 HMAC_final () = MAC 4
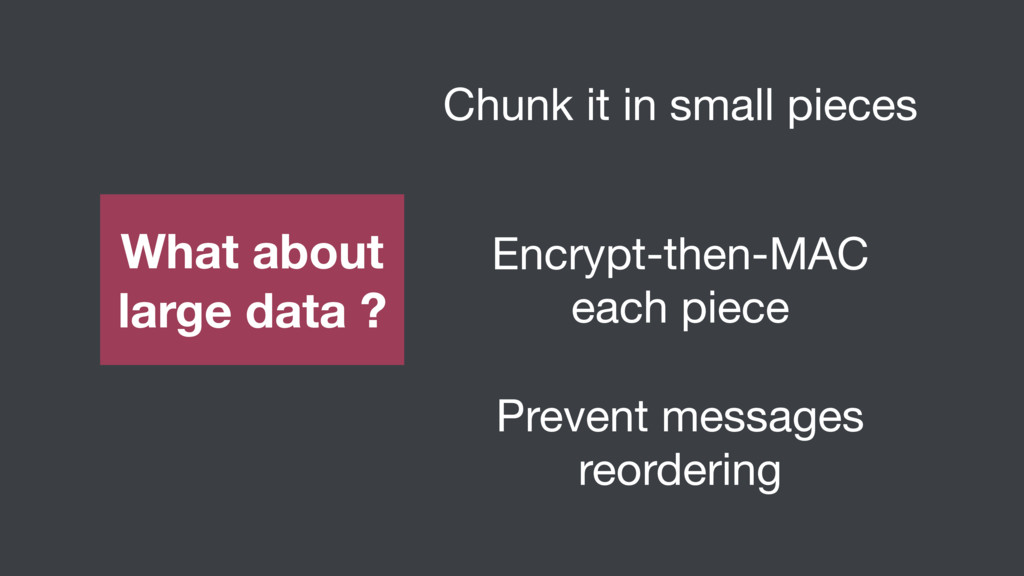
Prevent messages reordering Encrypt-then-MAC each piece Chunk it in small
pieces What about large data ?
A word about IVs Depends of your AES mode …
None
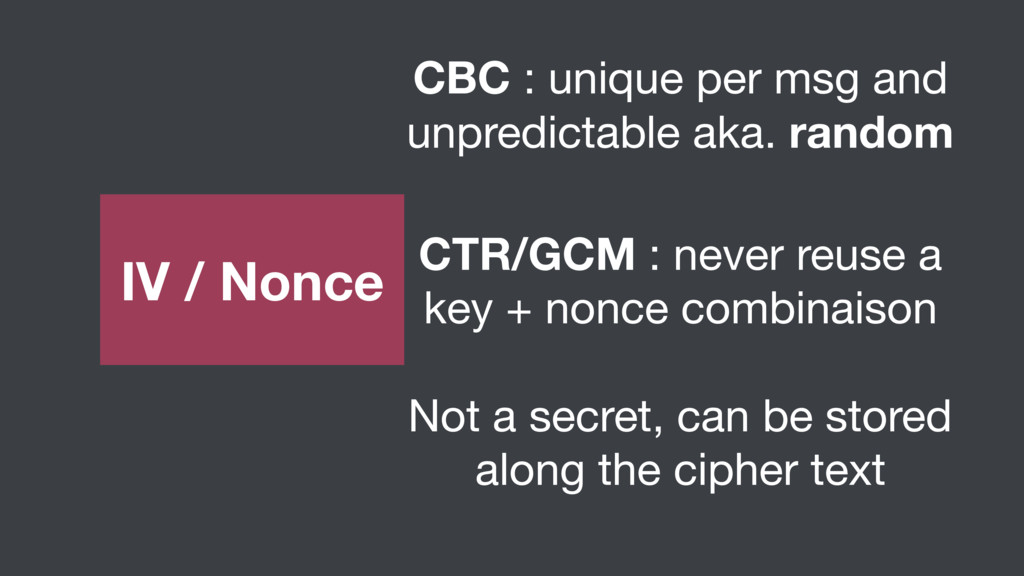
Not a secret, can be stored along the cipher text
CTR/GCM : never reuse a key + nonce combinaison CBC : unique per msg and unpredictable aka. random IV / Nonce
Done ?
Nope
Forget all of this
In fact, if you type the letters « A-E-S »
you’ve already lost
Treat crypto primitives like plutonium not AAA batteries
Attackers have a lot of imagination One error can invalidate
your whole system Using crypto primitives is incredibly tricky Why ?
Attacks Timing attacks Extension length Padding oracle Preimage attacks Cache
timing
None
Avoid OpenSSL Choose mature OSS lib, carefully audited Only use
high-level crypto library The right tools
Don’t write a line before extensive learning Errors messages are
information Be careful not leaking information The right use
Bindings exist in multiple languages Carefully designed to be safe
and easy to use Currently the most lib recommended by experts NaCl/ LibSodium
New kid in the block, so no certification Stream cipher,
good perf. even in software NaCl’s underlying primitives Chacha20/ Salsa20
Perish in flames Huuu… Keyczar in Java, Python, C++ Alternatives
It will hurt By crypto experts Every line of crypto
should be audited Audit
Be prepared for JS WebCryptocalypse Watch out for CAESAR competition
All I’ve said will probably be wrong in some months Stay tuned
Bibliography Cryptography Engineering by N. Ferguson & B. Schneier Some
cryptographers to follow - Adam Langley (imperialviolet.org) - Matthew Green (blog.cryptographyengineering.com) - Thomas Ptacek (@tqbf & tptacek on Hacker News) - JP Aumasson (@veorq) http://www.cryptofails.com https://cryptocoding.net/
Thank you Questions ? To be continued…


 mrartichaut
 yuukiw00w
 mpyw
 n_takehata
 iwiwi
 gam0022
 texmeijin
 steliosf
 yukiny
 nokomoro3
 bells17
 uyuki234
 ryu1013
 tmiket
 addyosmani
 lynnandtonic
 dugsong
 cromwellryan
 kneath
 tanoku
 asonas
 sarafernandez
 garrettdimon
 aleyda