Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Secure by design: introduction to threat modeling
Search
Jérémy Courtial
June 20, 2018
Technology
67
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Secure by design: introduction to threat modeling
An introduction to threat modeling and some ideas on how to integrate it in yours teams.
Jérémy Courtial
June 20, 2018
More Decks by Jérémy Courtial
See All by Jérémy Courtial
sudo give the cloud
mrartichaut
0
36
An introduction to AppSec?
mrartichaut
0
57
Taming secrets with Vault
mrartichaut
0
110
Lead Tech: Empowering the team
mrartichaut
0
56
Web Platform Security
mrartichaut
0
62
go doSomeThing()
mrartichaut
0
63
Practical Cryptography : Data Encryption
mrartichaut
0
76
Practical Cryptography : Password Hashing
mrartichaut
1
84
HTTP/2 : One connection to rule them all
mrartichaut
1
77
Other Decks in Technology
See All in Technology
メルペイ 会計システム概要と歴史
mewuto
1
220
実体験から学ぶ分析エージェントの開発と運⽤
recruitengineers
PRO
8
2.3k
ゲームのリアルタイム通信から見た QUIC と MoQ
segadevtech
0
110
パッチ更新でterraform initが落ちた日
grimoh
1
120
AI時代だからこそ推したい!Gitコマンド再入門
munakata
0
180
組み立てて楽しむ AWS Blocks 入門
kmiya84377
0
230
AI駆動開発の時代になったのでトヨタ生産方式から見直す
terurou
7
5.9k
Kiro Crewをはじめよう
kizawa2020
1
150
転んだ話が背中を預ける理由になる / A_story_about_falling_down_gives_you_a_reason_to_watch_each_other_s_backs.pdf
pauli
3
360
AI時代に必要な脅威モデリング― 変化の速度に負けない理解とリスク判断
masakane55
5
1.3k
UniFi(ユニファイ)AIカメラの現場活用
ludicmind
1
420
LocalStack を使ったサーバーレスアプリケーション開発 / Serverless Development with LocalStack
kakakakakku
1
420
Featured
See All Featured
Six Lessons from altMBA
skipperchong
29
4.5k
Chasing Engaging Ingredients in Design
codingconduct
0
360
ReactJS: Keep Simple. Everything can be a component!
pedronauck
666
130k
How to Grow Your eCommerce with AI & Automation
katarinadahlin
PRO
2
320
What the history of the web can teach us about the future of AI
inesmontani
PRO
2
740
Practical Orchestrator
shlominoach
192
12k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Game over? The fight for quality and originality in the time of robots
wayneb77
1
300
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.3k
Become a Pro
speakerdeck
PRO
31
6.3k
Navigating Weather and Climate Data
rabernat
0
550
The World Runs on Bad Software
bkeepers
PRO
72
12k
Transcript
Secure by design Threat modeling Jérémy Courtial - Software Security
Architect
How to ship secure applications?
Vulnerability: a very nasty kind of bug Oxford dictionary
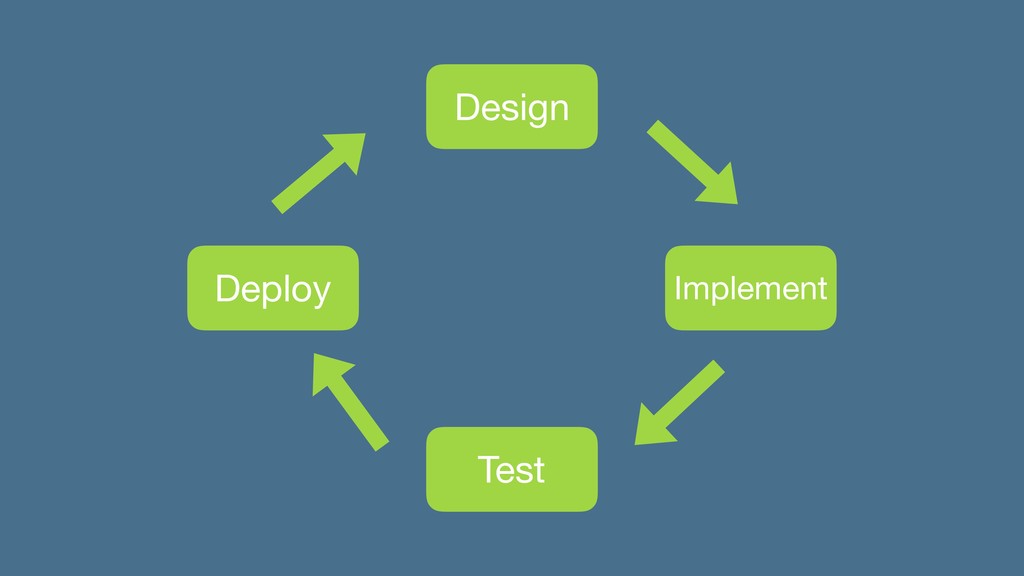
Good news! We know how to handle bugs!
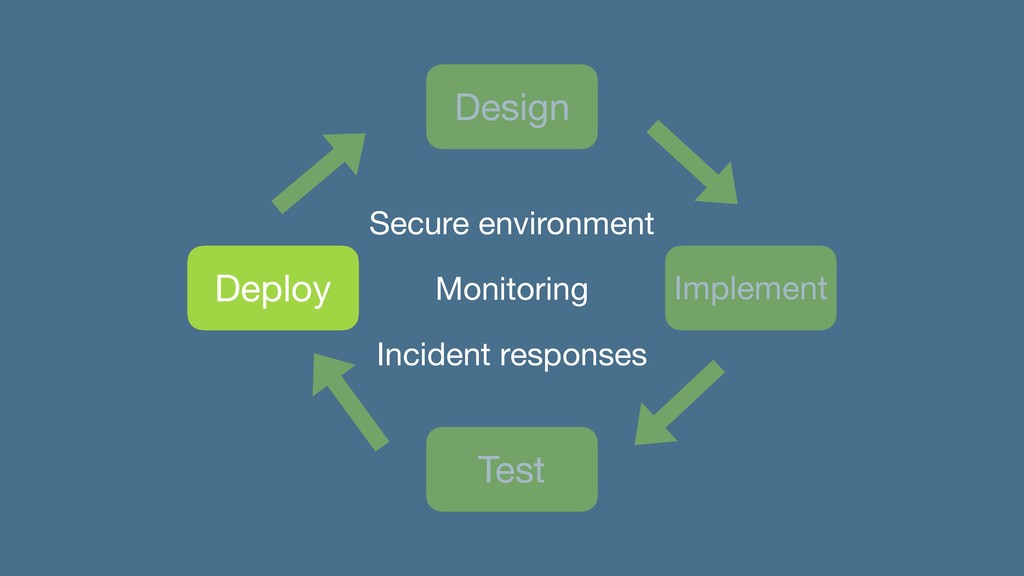
Design Test Implement Deploy
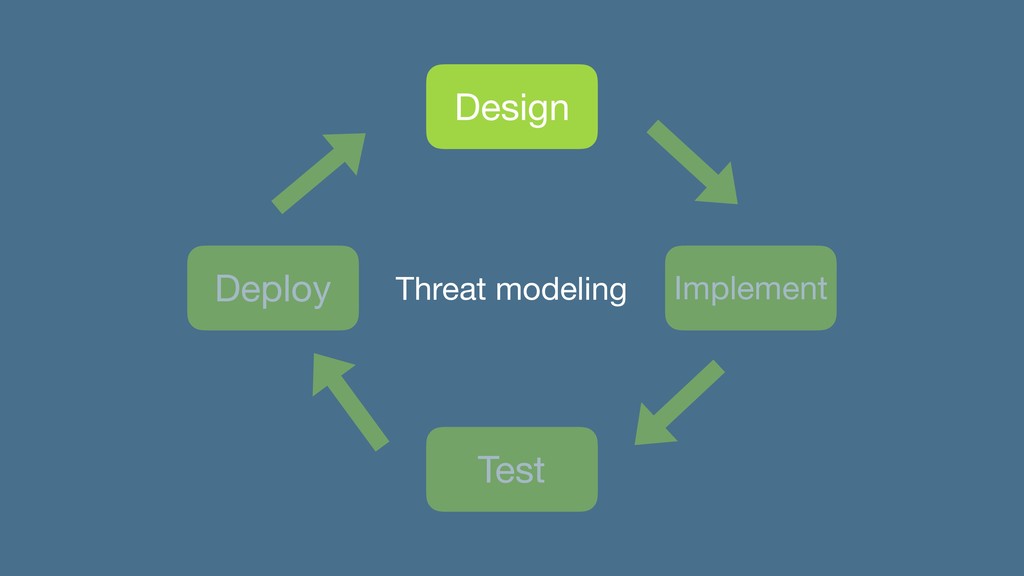
Design Test Implement Deploy Threat modeling
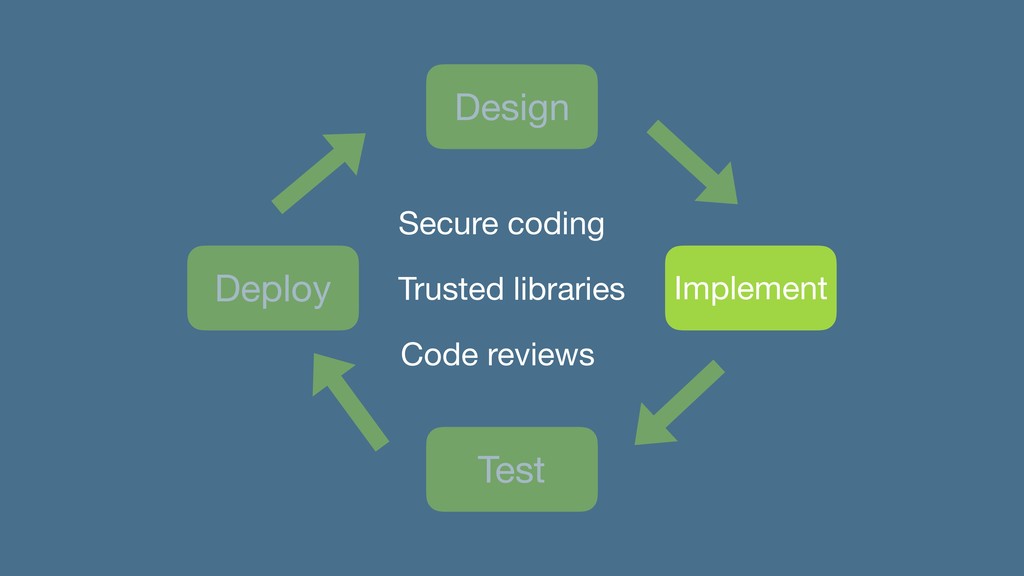
Design Test Implement Deploy Secure coding Trusted libraries Code reviews
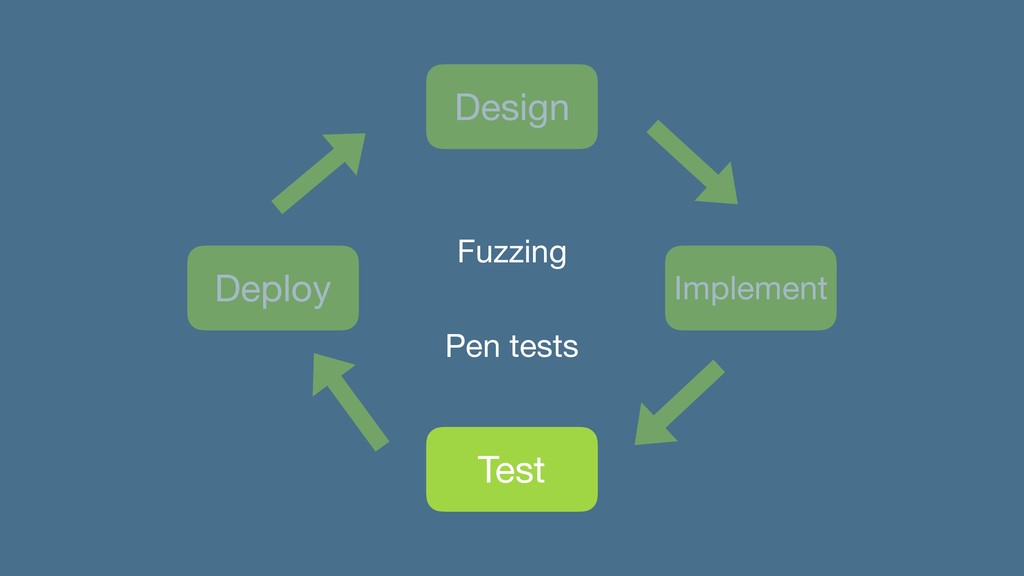
Design Test Implement Deploy Fuzzing Pen tests
Design Test Implement Deploy Secure environment Monitoring Incident responses
Threat modeling?
What you all want… $ ./threat_model app.jar Analyzing… Done. You’re
fine! Good job!
Sorry
Threat modeling: A process to identify and prioritize structural threats
in applications
How to? - decompose your app - find threats -
decide what to do
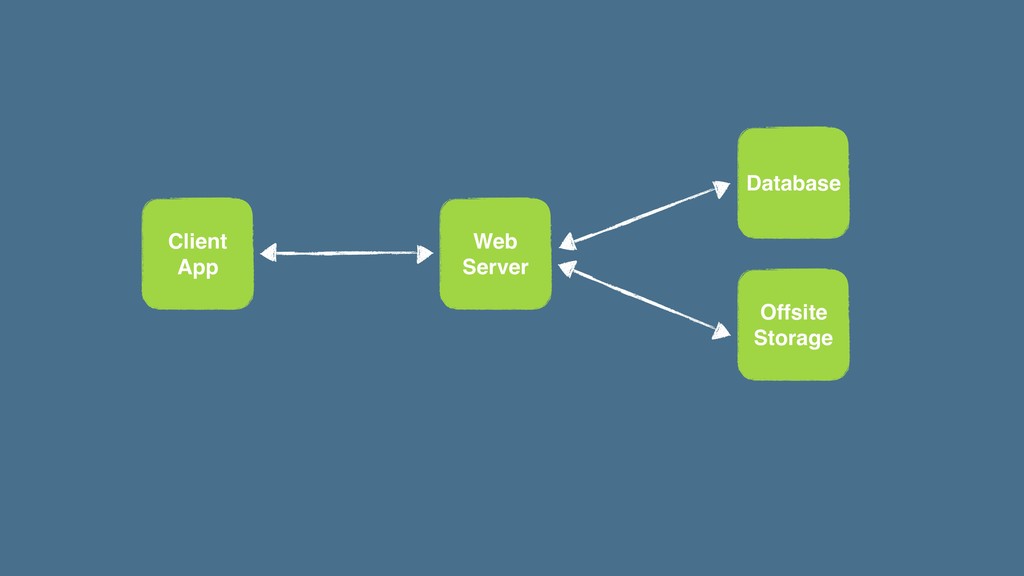
1. What are you building?
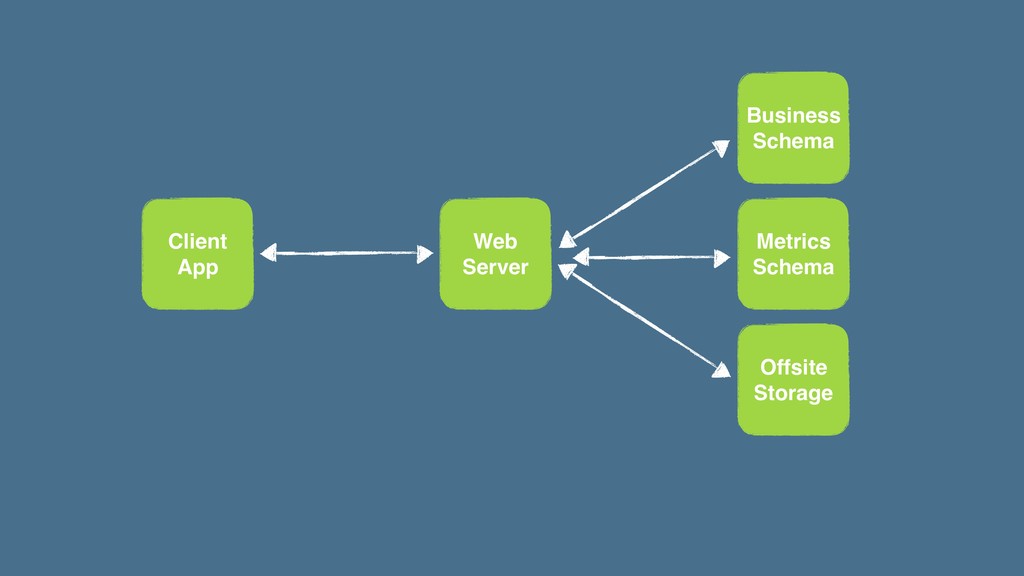
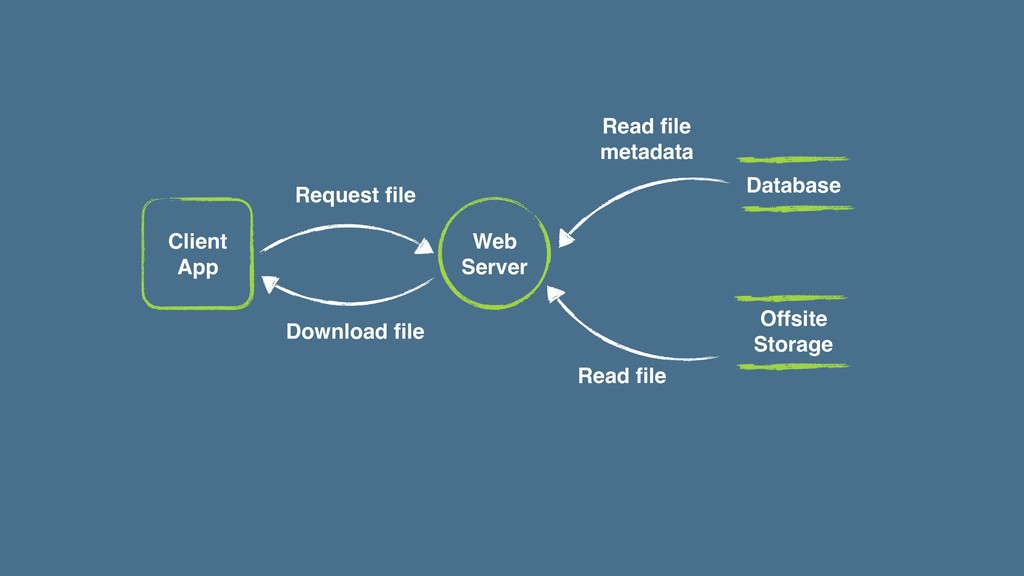
List entities, processes, data stores and data flows
Architecture and communication diagrams are good starting points
Otherwise, use a whiteboard!
Client App Web Server Database Offsite Storage
Client App Web Server Business Schema Offsite Storage Metrics Schema
Client App Web Server Database Offsite Storage Request file Read
file metadata Read file Download file
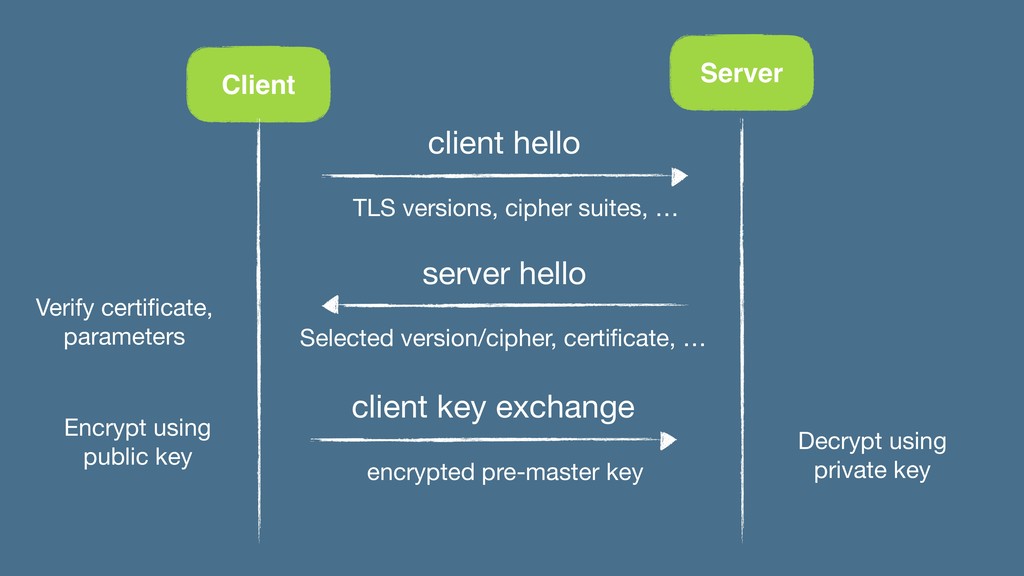
Client client hello TLS versions, cipher suites, … server hello
Selected version/cipher, certificate, … client key exchange encrypted pre-master key Verify certificate, parameters Decrypt using private key Server Encrypt using public key
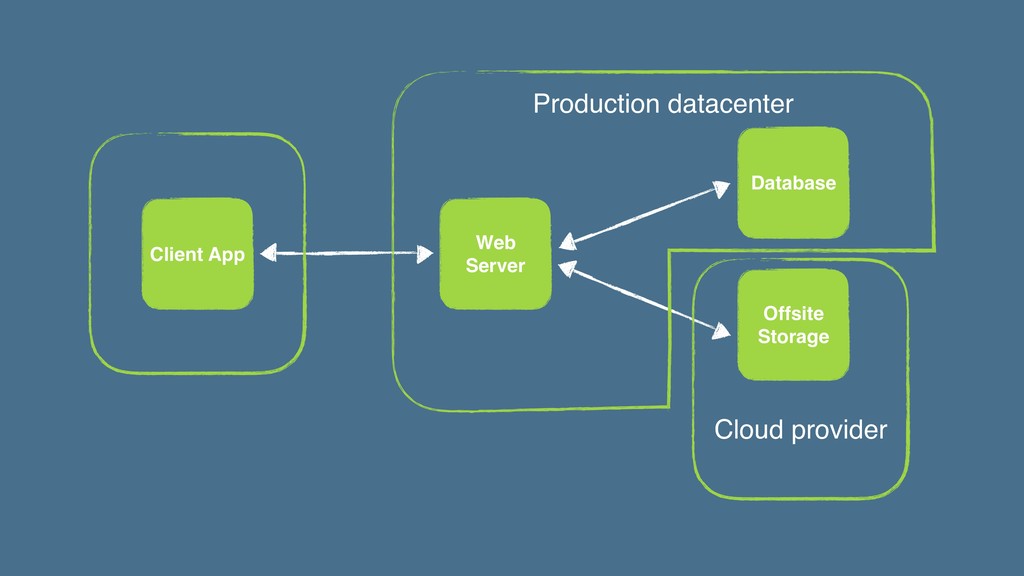
Now the most important part: add trust boundaries
Trust boundaries make explicit different levels of privilege
Client App Web Server Database Offsite Storage Production datacenter Cloud
provider
Trust boundaries help you focus your efforts where they matter
2. Find threats
Threats tend to appear around trust boundaries.
But how to find them?
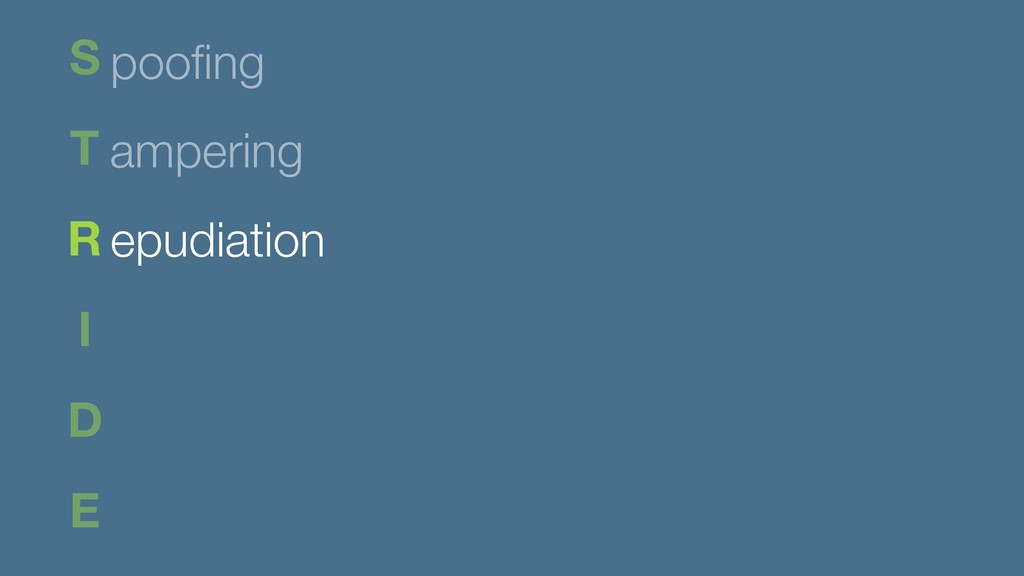
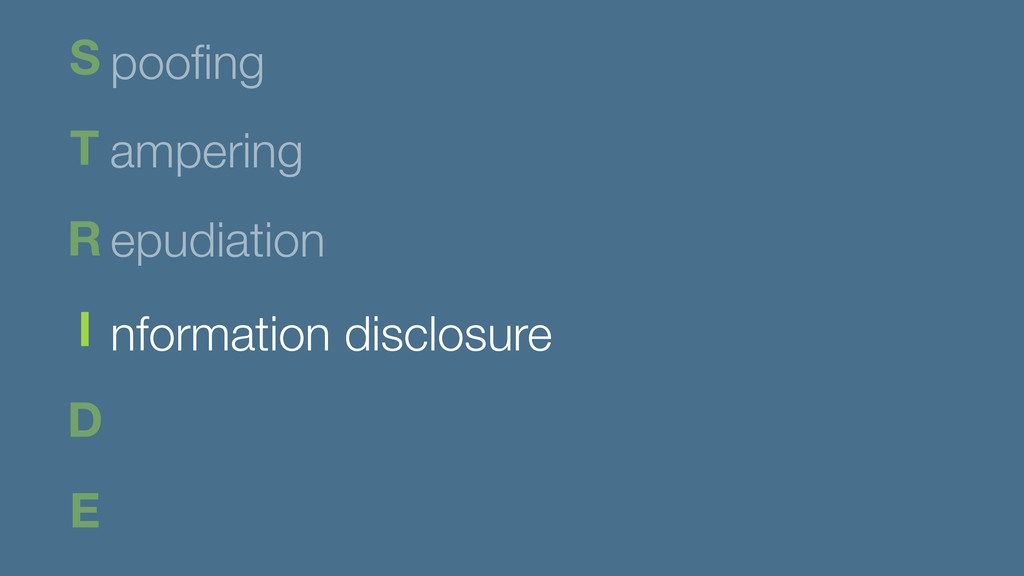
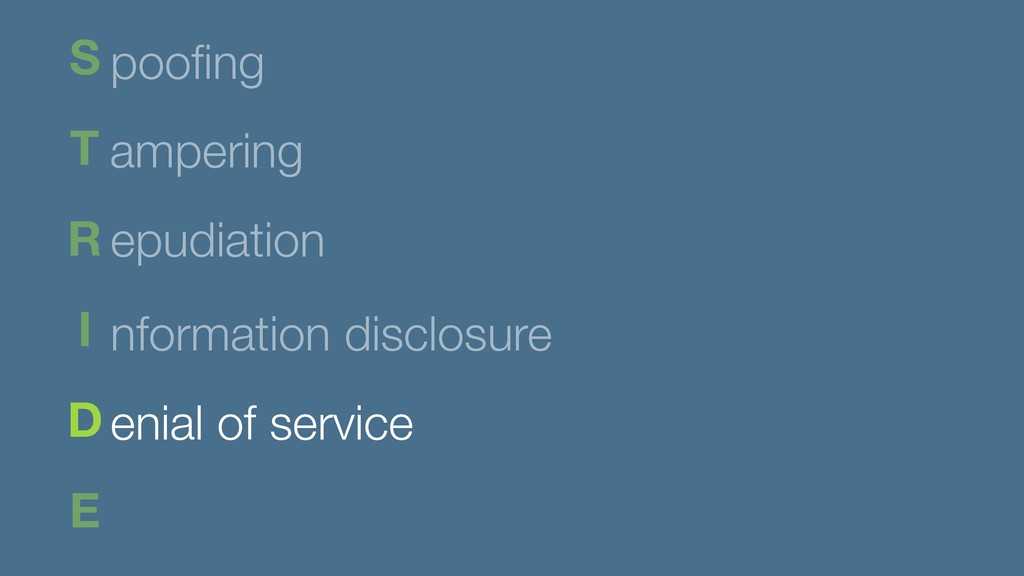
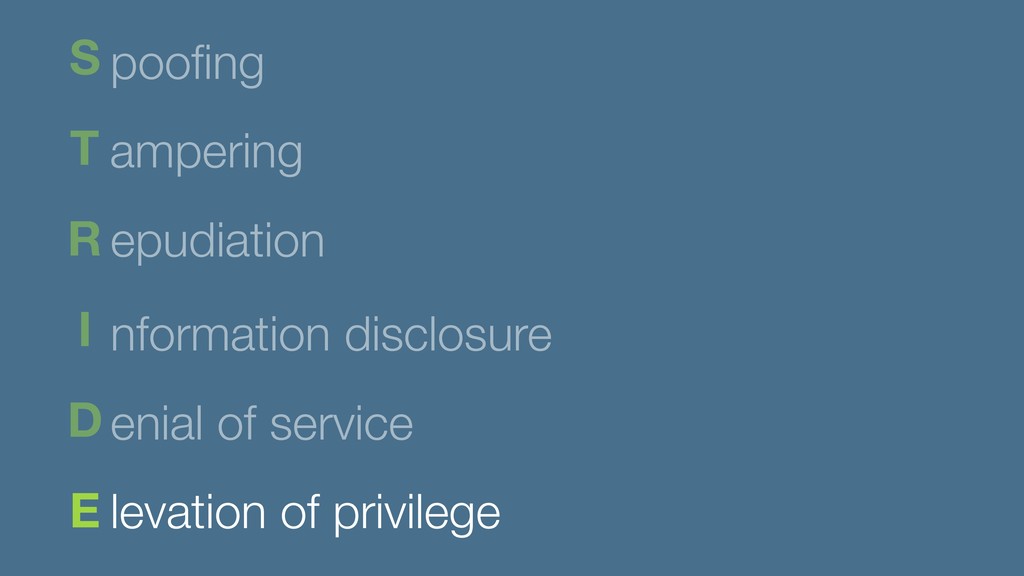
R S E D I T Useful mnemonic/framework:
R S E D I T
R S E D I T poofing
R S E D I T poofing ampering
R S E D I T poofing ampering epudiation
R S E D I T poofing epudiation nformation disclosure
ampering
R S E D I T poofing epudiation nformation disclosure
enial of service ampering
R S E D I T poofing epudiation nformation disclosure
enial of service levation of privilege ampering
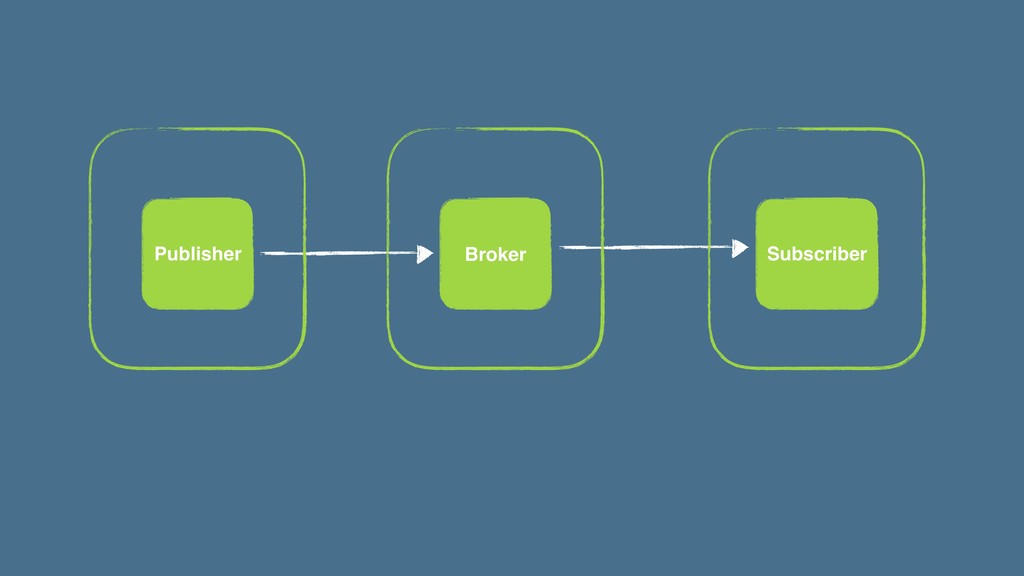
Publisher Broker Subscriber
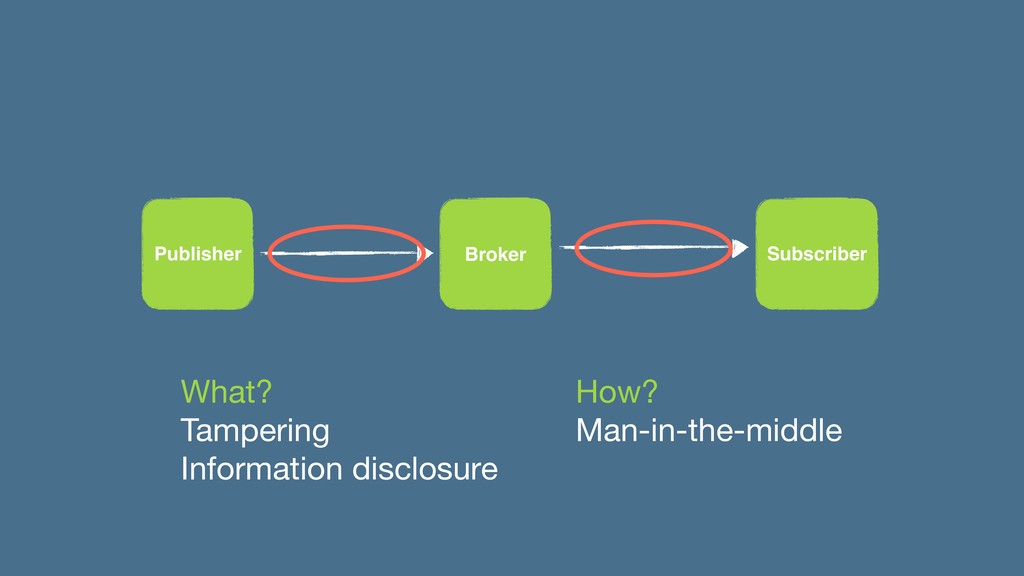
Publisher Broker Subscriber What? Tampering Information disclosure How? Man-in-the-middle
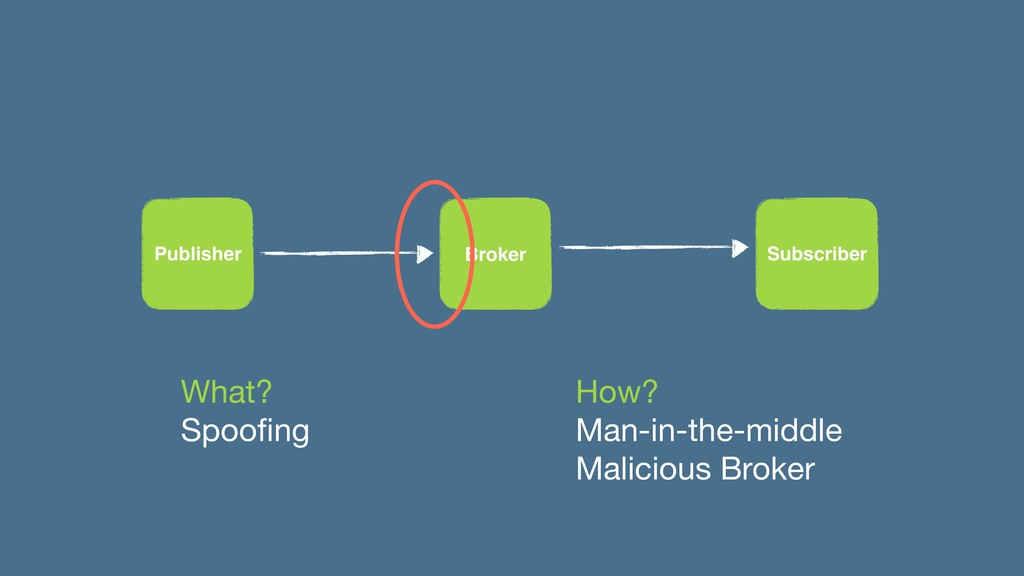
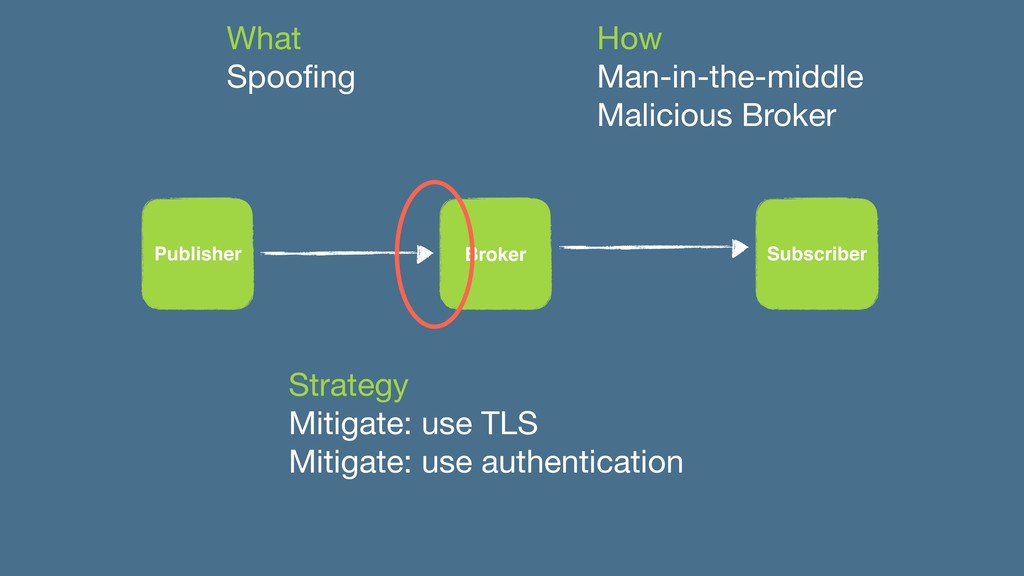
Publisher Broker Subscriber What? Spoofing How? Man-in-the-middle Malicious Broker
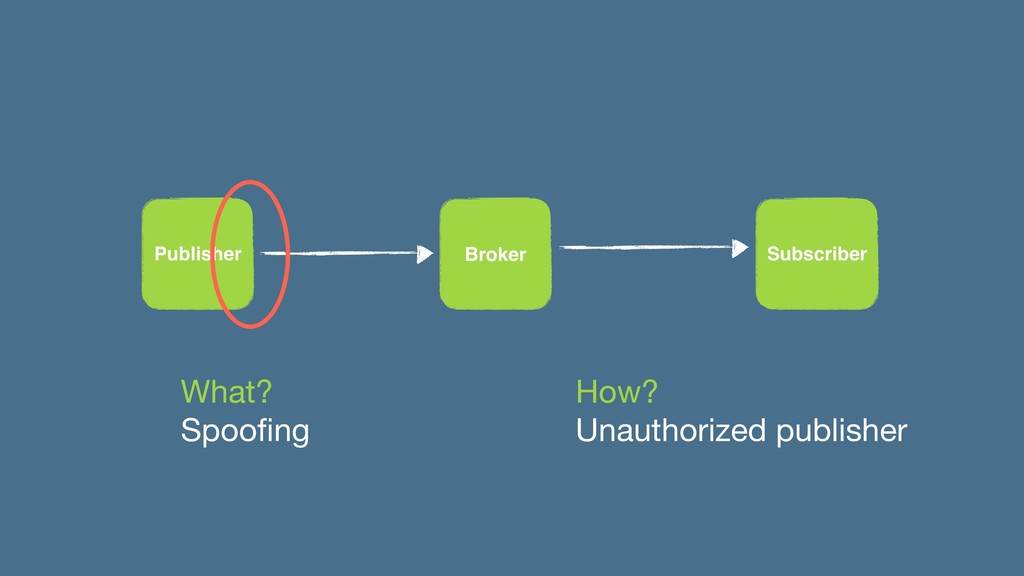
Publisher Broker Subscriber What? Spoofing How? Unauthorized publisher
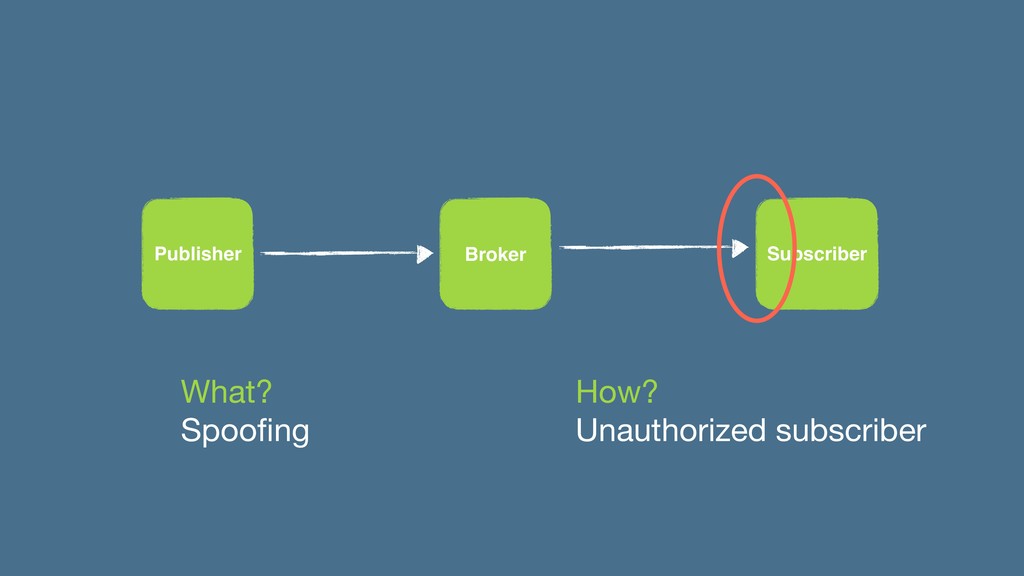
Publisher Broker Subscriber What? Spoofing How? Unauthorized subscriber
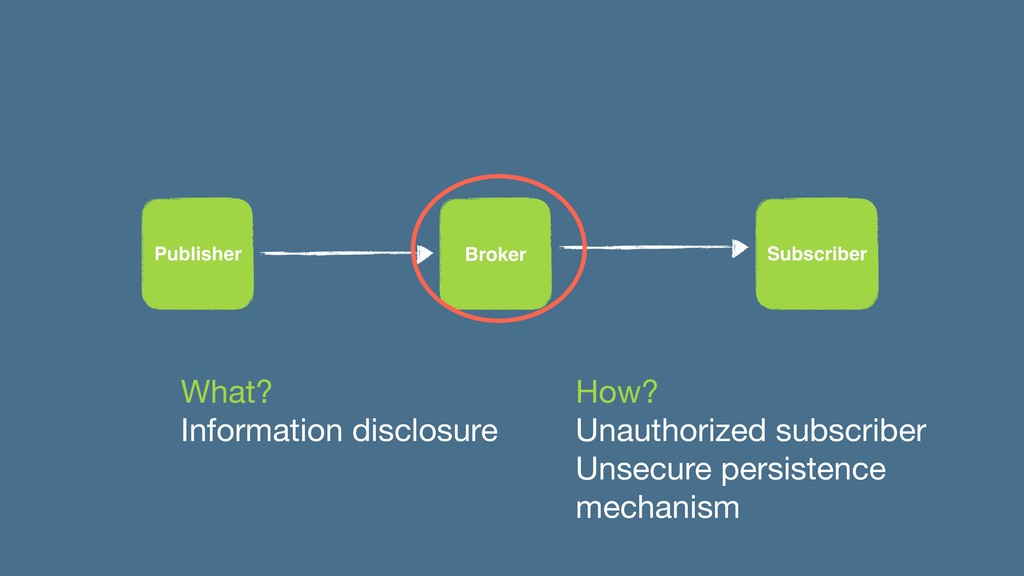
Publisher Broker Subscriber What? Information disclosure How? Unauthorized subscriber Unsecure
persistence mechanism
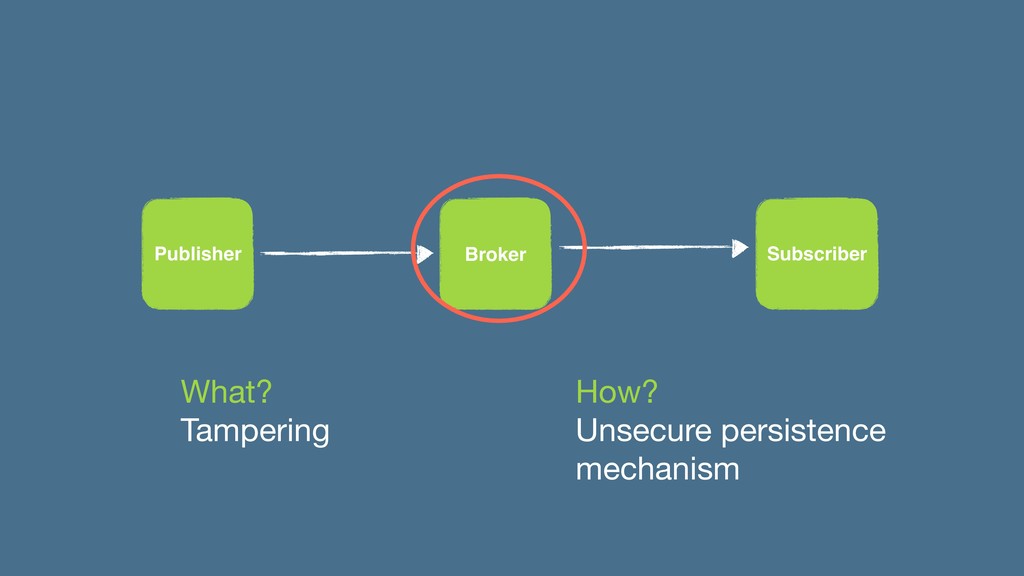
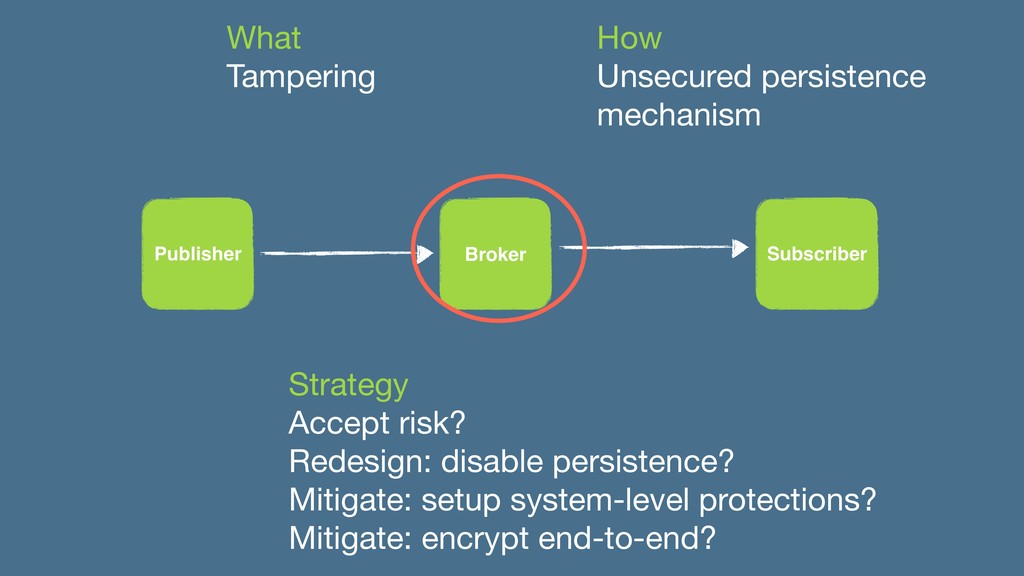
Publisher Broker Subscriber What? Tampering How? Unsecure persistence mechanism
3. Decide what to do
None
Nope (except if you’re the NSA)
For each threat: First, evaluate the risk (impact, probability, exploitation,
etc.) Then, choose a strategy
Redesign to eliminate Remove vulnerable features Add features reducing the
risk
Mitigate Apply standard mitigations Design new ones (riskier)
Accept the risk Make the risk explicit You could also
transfer it
Never ignore threats (one word: GDRP)
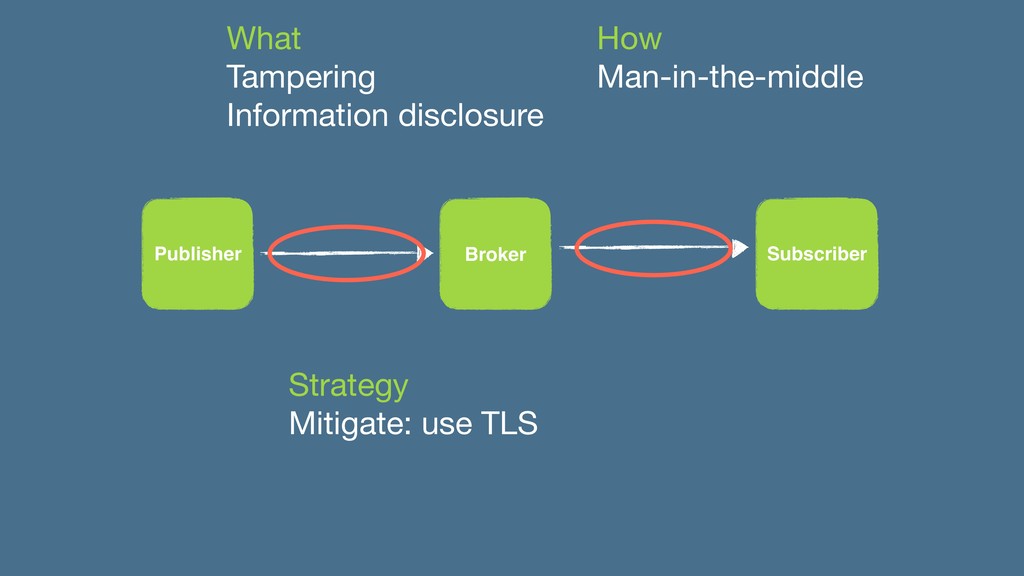
Publisher Broker Subscriber What Tampering Information disclosure How Man-in-the-middle Strategy
Mitigate: use TLS
Publisher Broker Subscriber What Spoofing How Man-in-the-middle Malicious Broker Strategy
Mitigate: use TLS Mitigate: use authentication
Publisher Broker Subscriber What Tampering How Unsecured persistence mechanism Strategy
Accept risk? Redesign: disable persistence? Mitigate: setup system-level protections? Mitigate: encrypt end-to-end?
You don’t have one threat model Final note
How to integrate threat modeling in your R&D?
Schedule a 4 hours meeting Invite half the devs, half
the ops and some people with long titles Have them produce a 20-pages long threat model
Do what fits your culture
Dedicated meetings/projects Back-to-the-envelope Opportunistic meetings How?
Whiteboard picture Meetings notes Full documentation Delivery?
Don’t care. Just do it.
Architecture reviews Threat modeling @ Oodrive
Feedbacks-oriented meeting before any major changes enter development Eg. new
service, major refactoring
Ensuring best practices Identifying subjects that need closer follow-ups Providing
feedbacks and challenging architectural choices
Not a threat modeling meeting per-se… … more like «
Hey! While we’re all here … » Parasite-security
Security checklists Threat modeling @ Oodrive
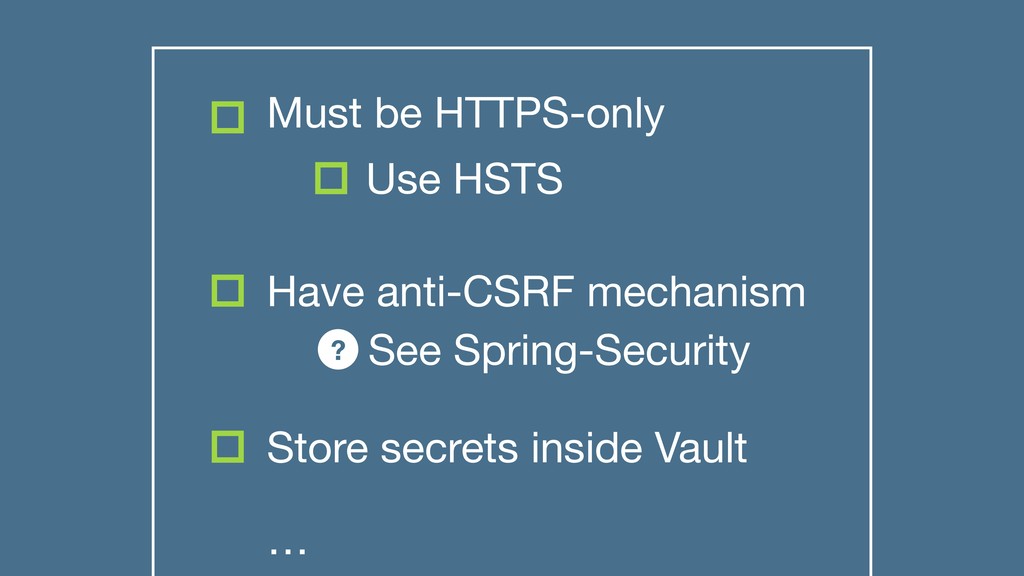
Use HSTS Must be HTTPS-only Store secrets inside Vault Have
anti-CSRF mechanism … See Spring-Security ?
Ready-to-use (implicit) threat models Focus on mitigations Validated during security
reviews
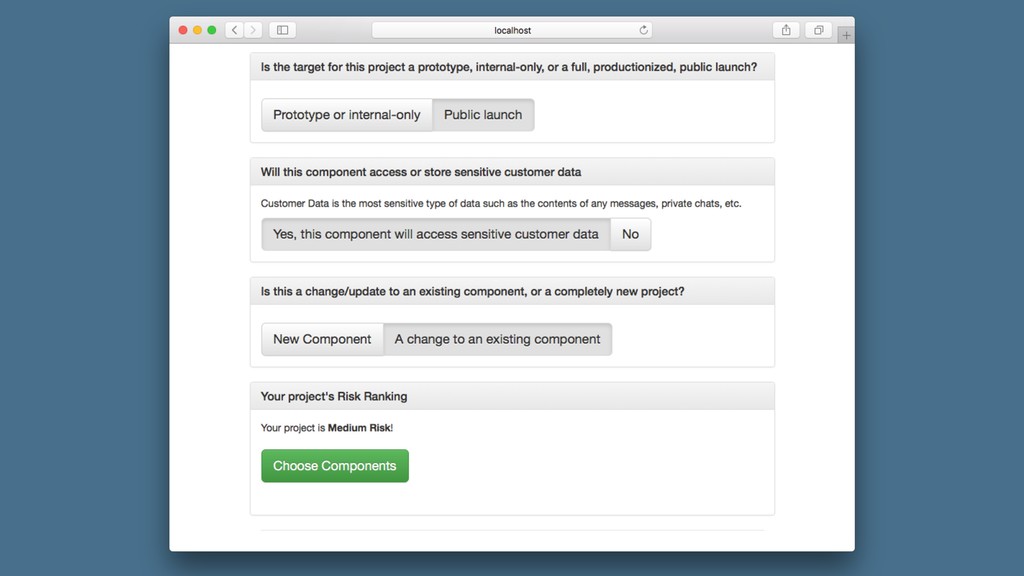
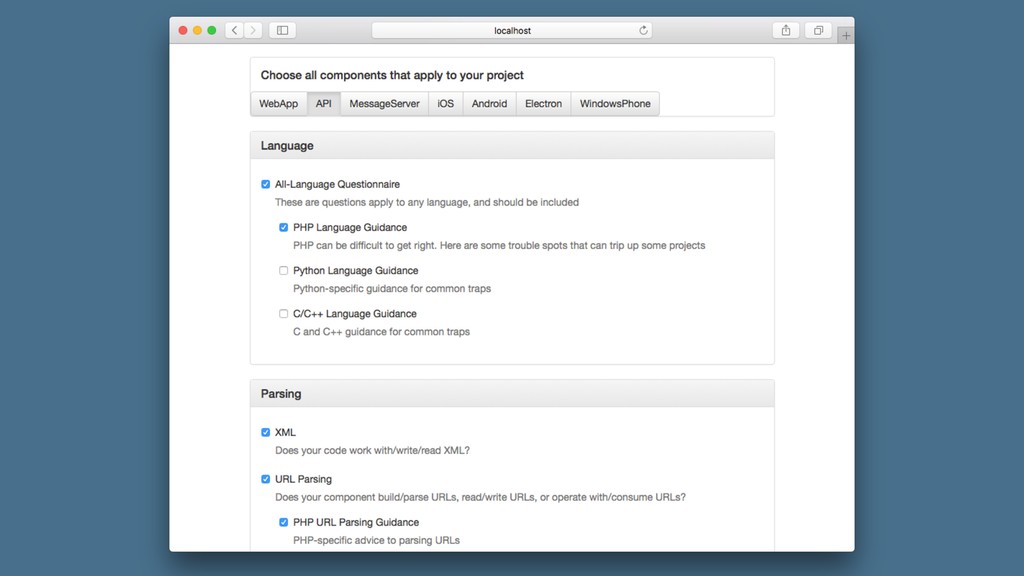
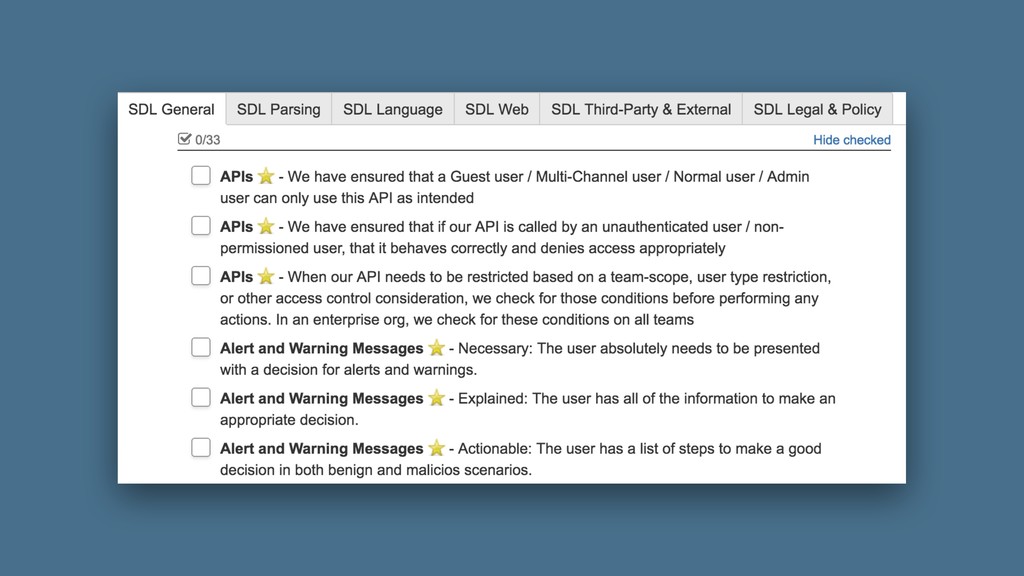
Slack’s goSDL Threat modeling elsewhere https://github.com/slackhq/goSDL https://slack.engineering/moving-fast-and-securing- things-540e6c5ae58a
None
None
None
Should you threat model?
Yes! (obviously)
At least once
Know your(s) threat model(s)!
Questions? Thank you To win! Icons created by Tomas Knopp,
Edwin Prayogi M and Dima Lagunov from the thenounproject.com


 mrartichaut
 mewuto
 recruitengineers
 segadevtech
 grimoh
 munakata
 kmiya84377
 terurou
 kizawa2020
 pauli
 masakane55
 ludicmind
 kakakakakku
 skipperchong
 codingconduct
 pedronauck
 katarinadahlin
 inesmontani
 shlominoach
 aki_iinuma
 wayneb77
 tomoyanonymous
 speakerdeck
 rabernat
 bkeepers