Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
讀書會-CVE-2025-59489.pdf
Search
Fox
July 25, 2026
0
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
讀書會-CVE-2025-59489.pdf
Fox
July 25, 2026
More Decks by Fox
See All by Fox
社課-組合語言.pdf
nyanfox87
0
0
讀書會-CatInTheMiddle.pdf
nyanfox87
0
0
讀書會-Unicorn.pdf
nyanfox87
0
0
讀書會-UnityReverse.pdf
nyanfox87
0
0
2026沙崙競賽決賽-1.pdf
nyanfox87
0
0
社課-HowToHackAGame_final.pdf
nyanfox87
0
6
Featured
See All Featured
Building Experiences: Design Systems, User Experience, and Full Site Editing
marktimemedia
1
630
A Soul's Torment
seathinner
8
3.8k
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
2
360
How to train your dragon (web standard)
notwaldorf
96
6.9k
From Legacy to Launchpad: Building Startup-Ready Communities
dugsong
0
360
Fireside Chat
paigeccino
43
4.1k
YesSQL, Process and Tooling at Scale
rocio
174
15k
Exploring anti-patterns in Rails
aemeredith
4
540
Done Done
chrislema
187
17k
Reflections from 52 weeks, 52 projects
jeffersonlam
356
22k
What's in a price? How to price your products and services
michaelherold
247
13k
What the history of the web can teach us about the future of AI
inesmontani
PRO
2
740
Transcript
CVE-2025-59489 Arbitrary Code Execution in Unity Runtime Presenter: Fox, Date:
10/31
Outline • Overview of Vuln. • Explain Unity Runtime •
Cause of Vulnerabilities • Vulnerability impact • Conclusion
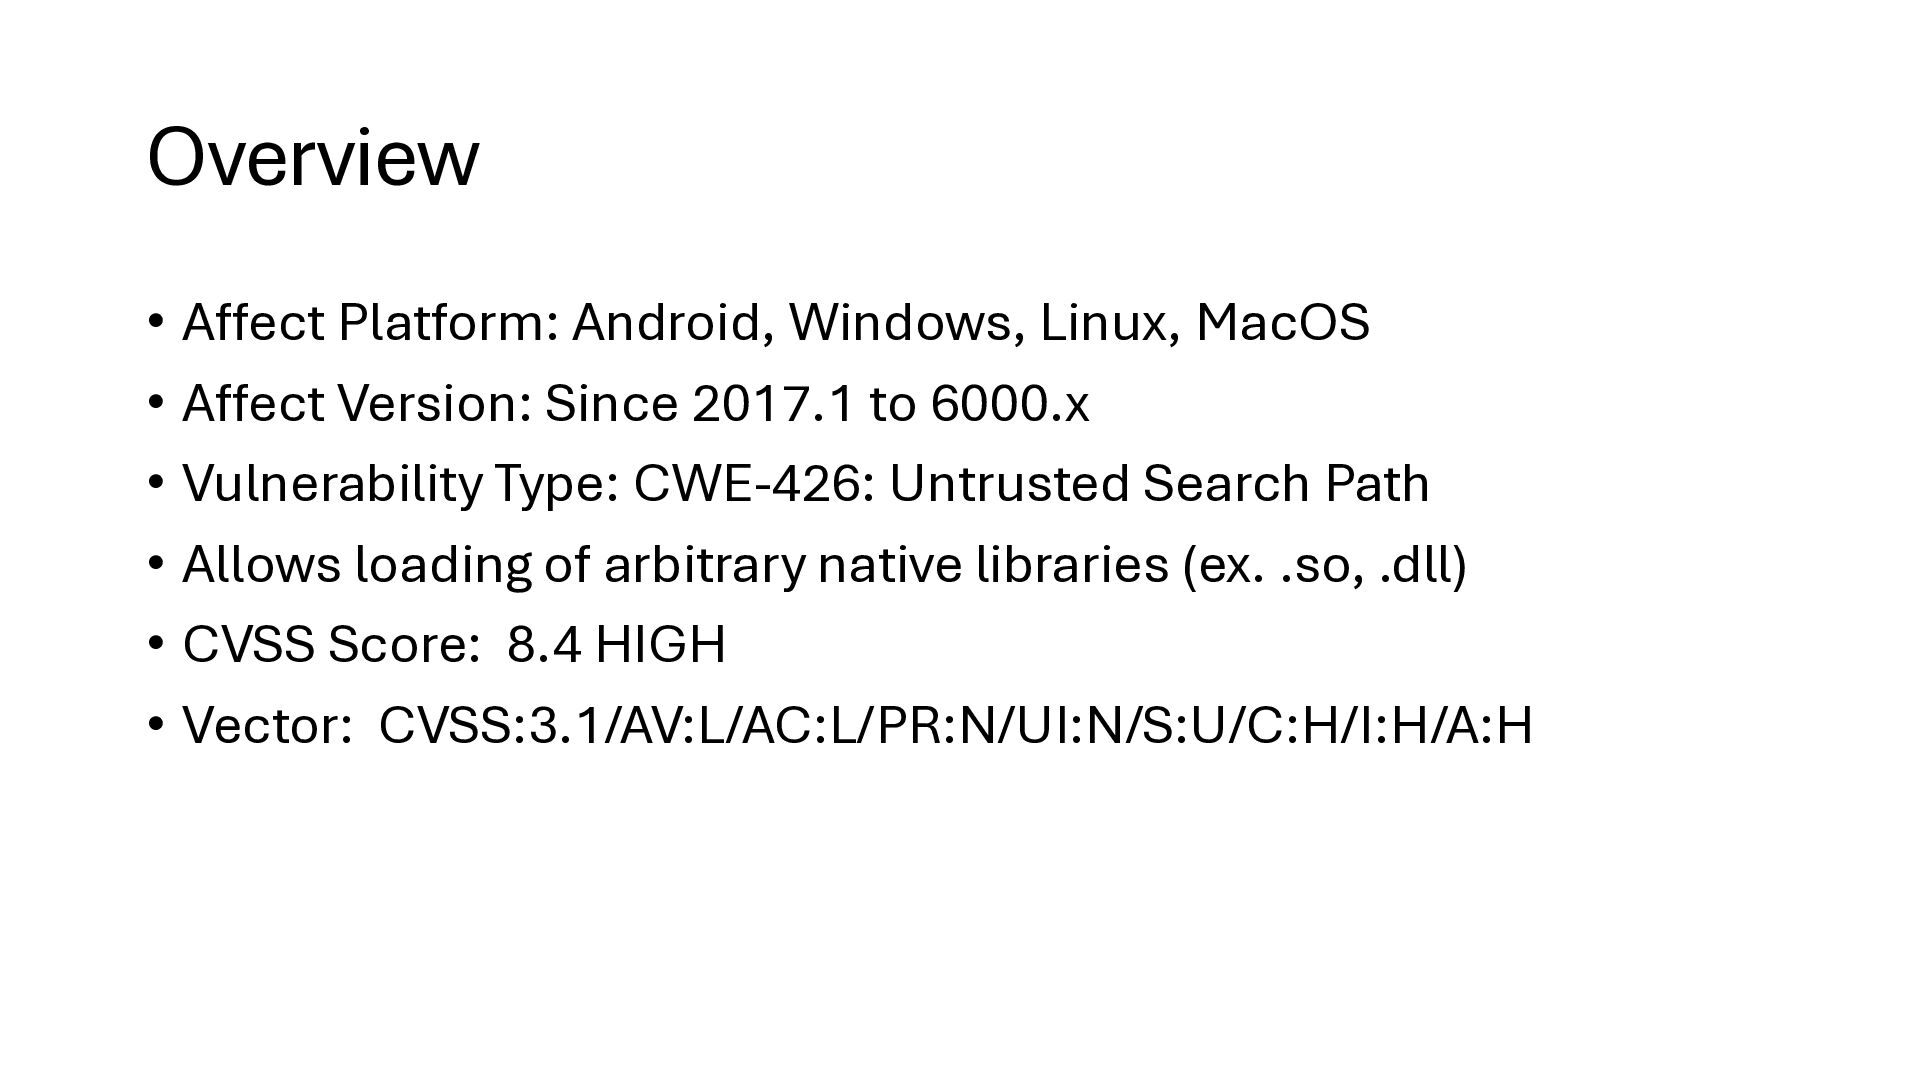
Overview • Affect Platform: Android, Windows, Linux, MacOS • Affect
Version: Since 2017.1 to 6000.x • Vulnerability Type: CWE-426: Untrusted Search Path • Allows loading of arbitrary native libraries (ex. .so, .dll) • CVSS Score: 8.4 HIGH • Vector: CVSS:3.1/AV:L/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
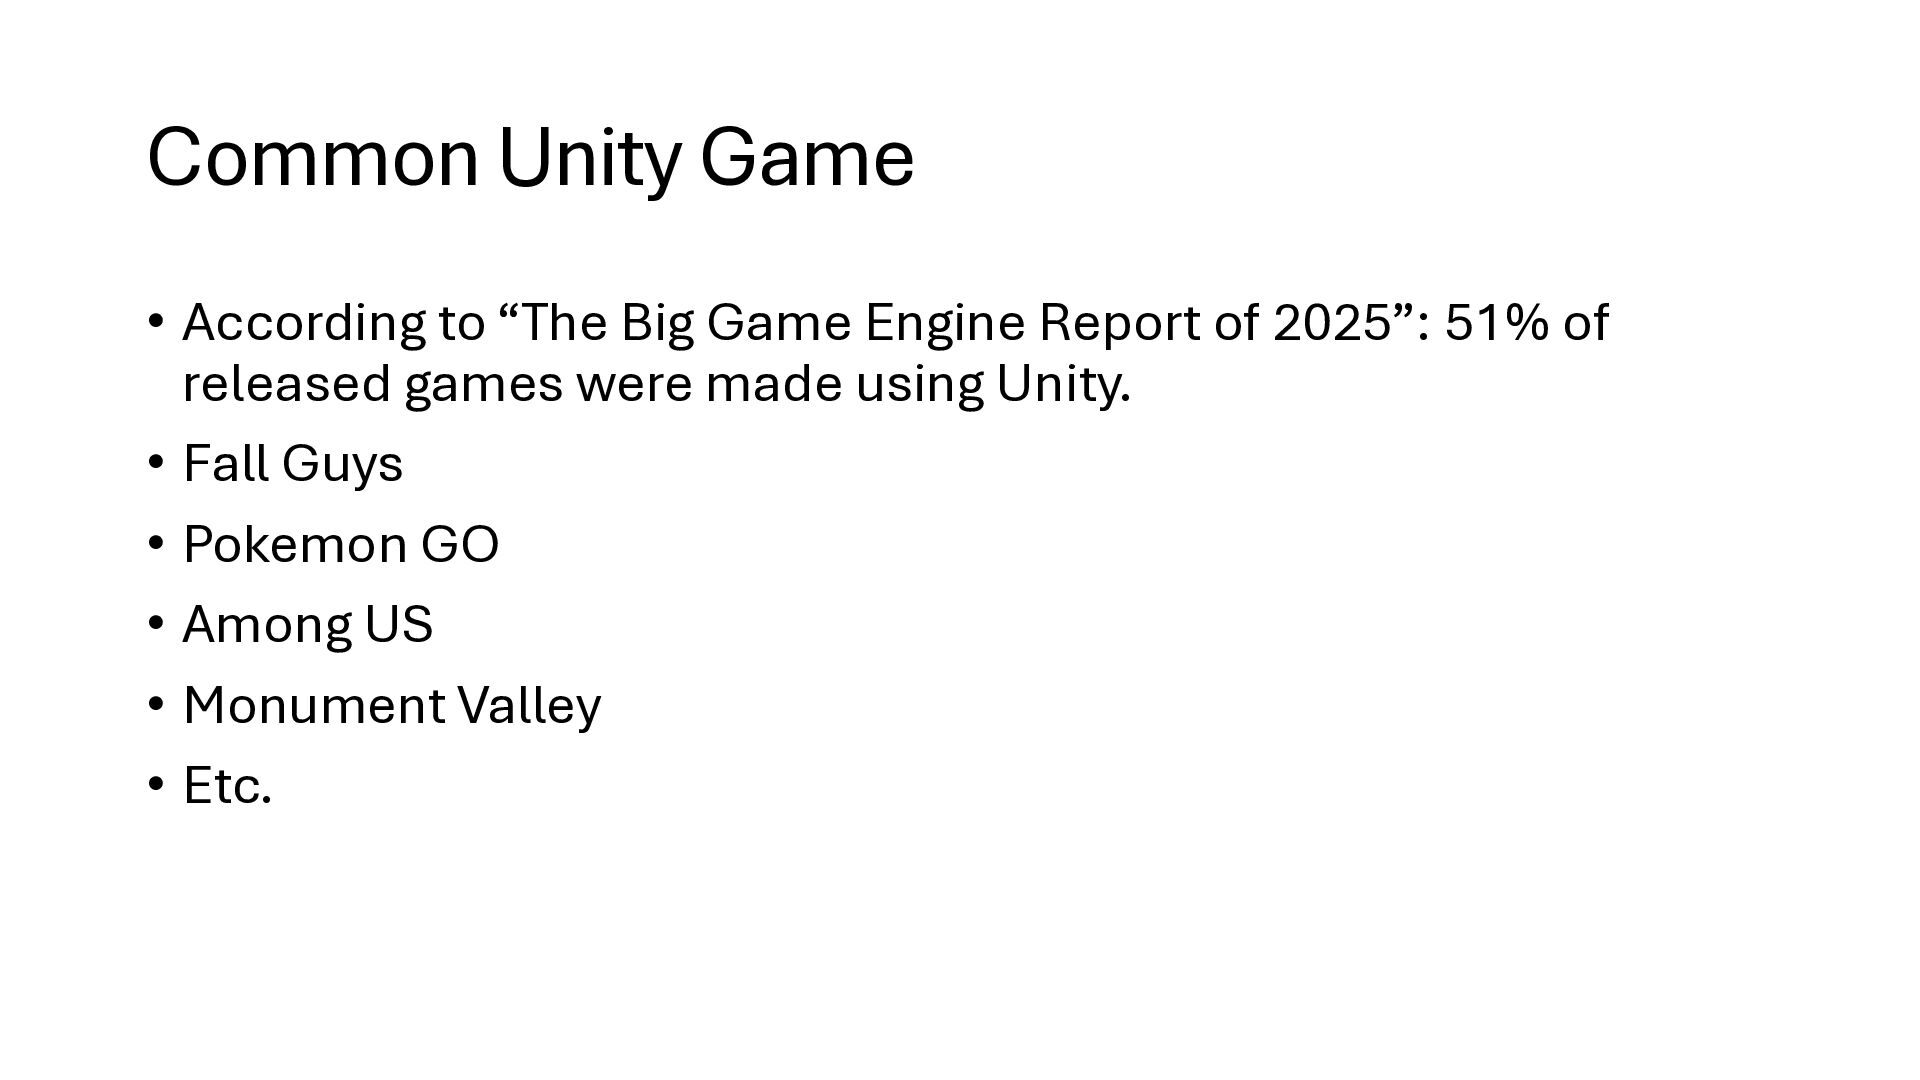
Common Unity Game • According to “The Big Game Engine
Report of 2025”: 51% of released games were made using Unity. • Fall Guys • Pokemon GO • Among US • Monument Valley • Etc.
Unity Runtime Binary • Windows: UnityPlayer.dll • Android: libunity.so
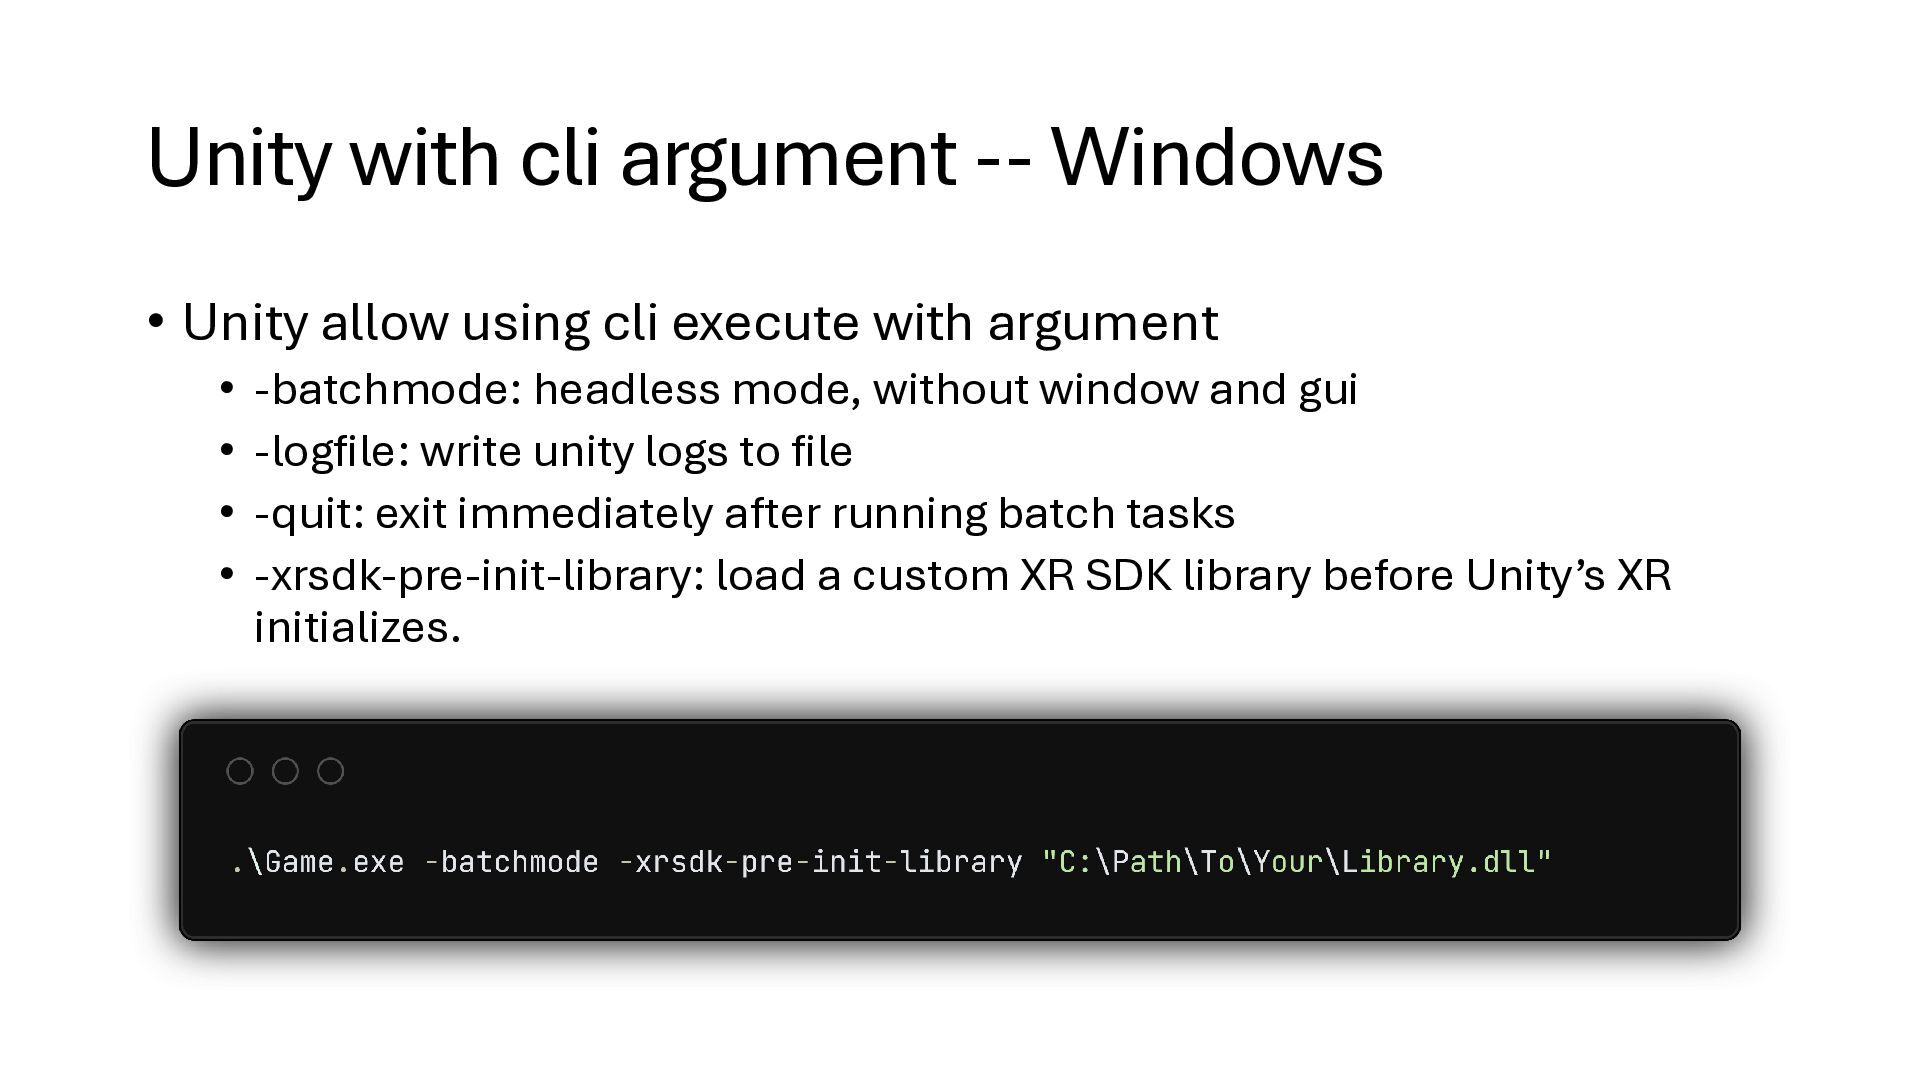
Unity with cli argument -- Windows • Unity allow using
cli execute with argument • -batchmode: headless mode, without window and gui • -logfile: write unity logs to file • -quit: exit immediately after running batch tasks • -xrsdk-pre-init-library: load a custom XR SDK library before Unity’s XR initializes.
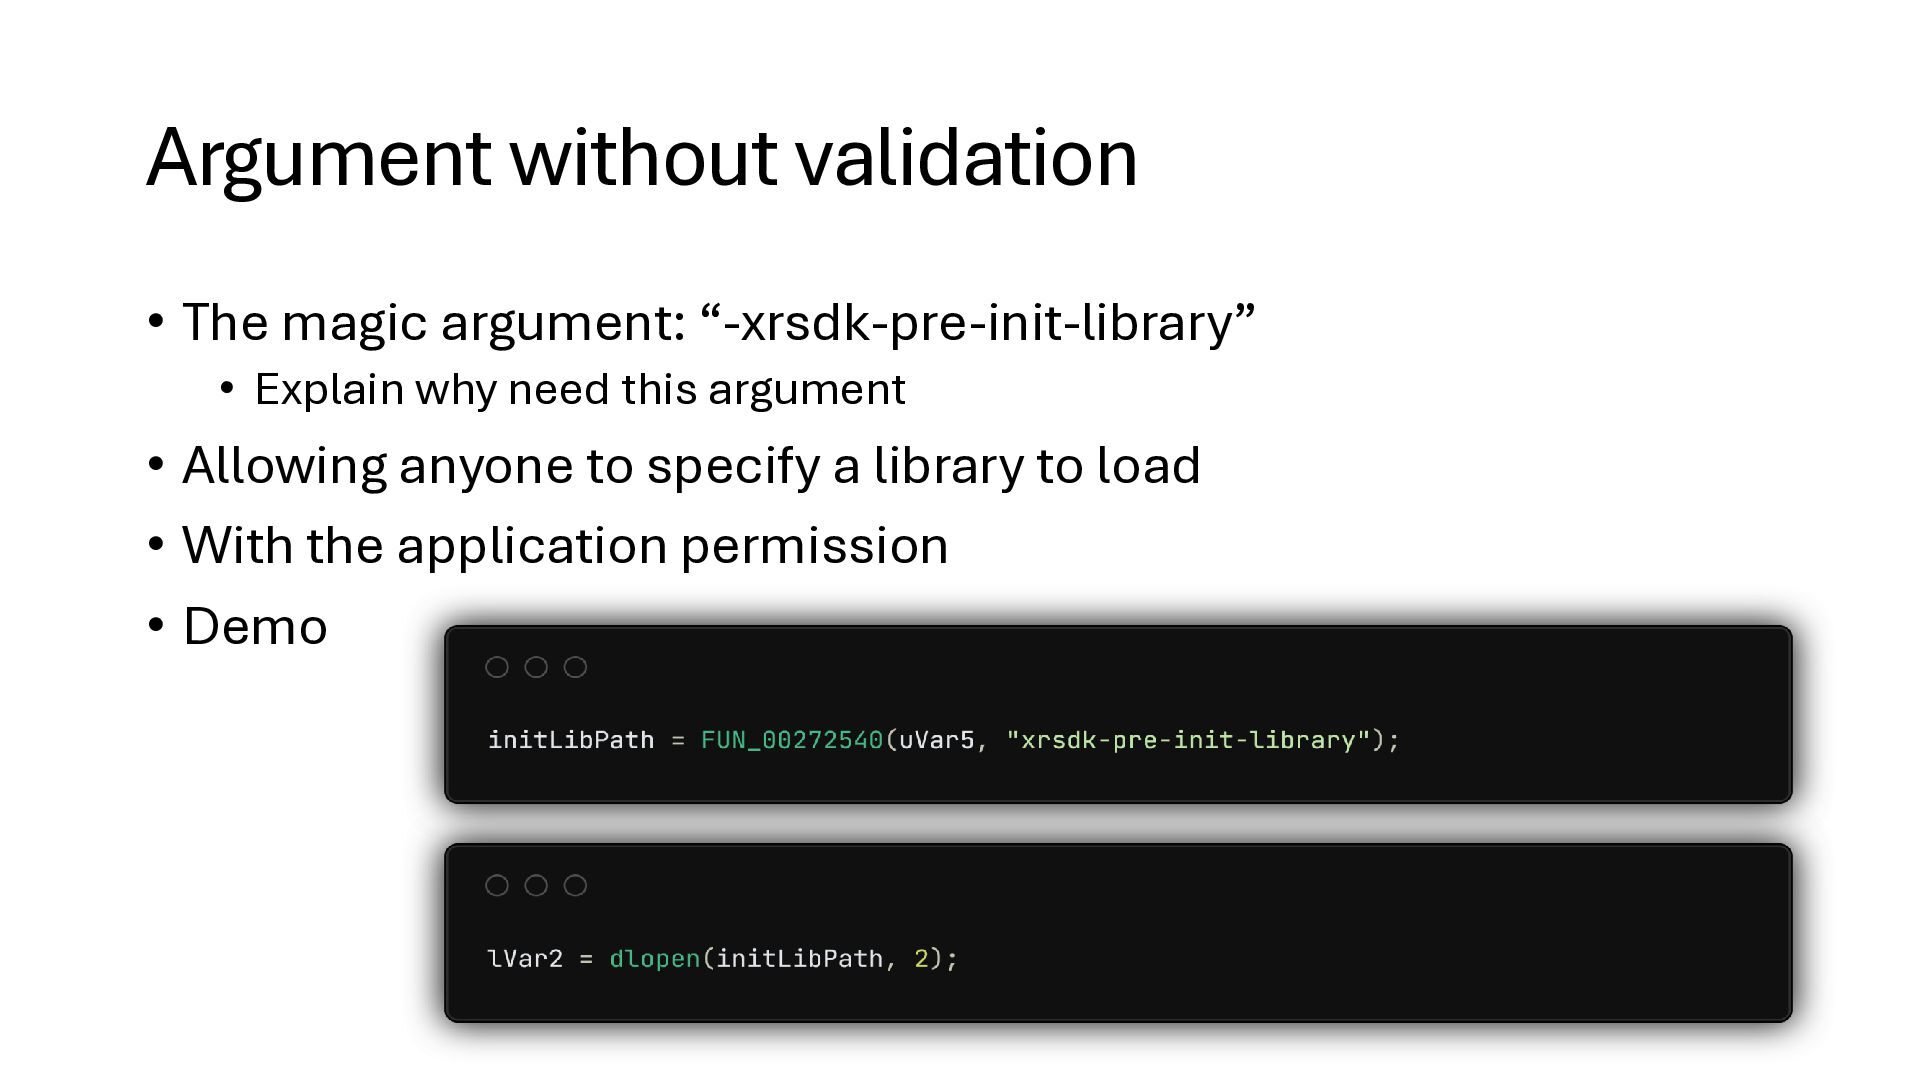
Argument without validation • The magic argument: “-xrsdk-pre-init-library” • Explain
why need this argument • Allowing anyone to specify a library to load • With the application permission • Demo
Conclusion • There are no known public attacks exploiting this
vulnerability. • After public disclosure, its real-world impact will likely be much lower. • The Steam launcher will automatically filter out malicious parameters.
Ref • CVE-2025-59489: Arbitrary Code Execution in Unity Runtime https://flatt.tech/research/posts/arbitrary-code-execution-inunity-runtime/
• Unity Security Update Advisory https://unity.com/security/sept-2025-01


 nyanfox87
 marktimemedia
 seathinner
 helenjbeal
 notwaldorf
 dugsong
 paigeccino
 rocio
 aemeredith
 chrislema
 jeffersonlam
 michaelherold
 inesmontani