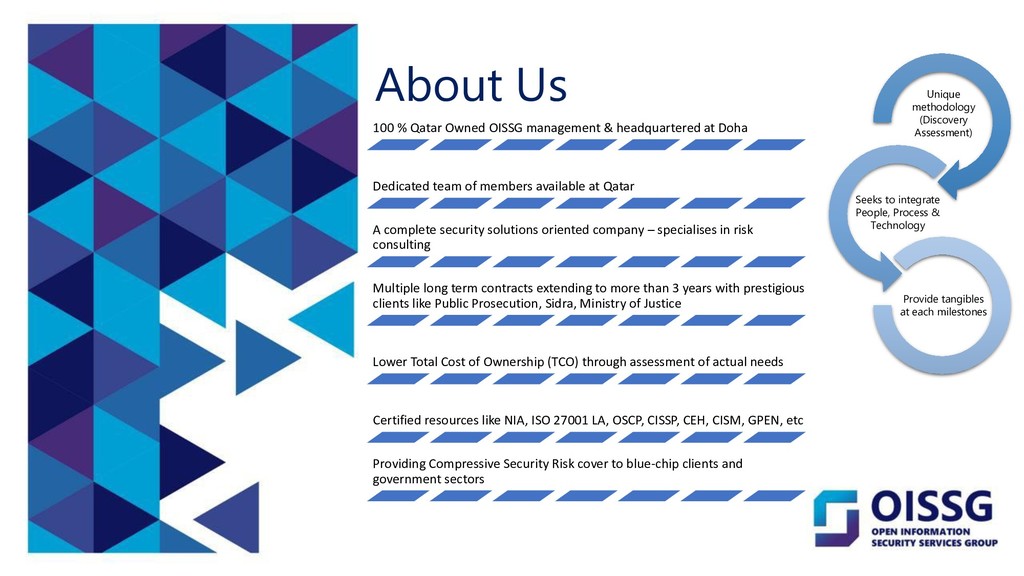
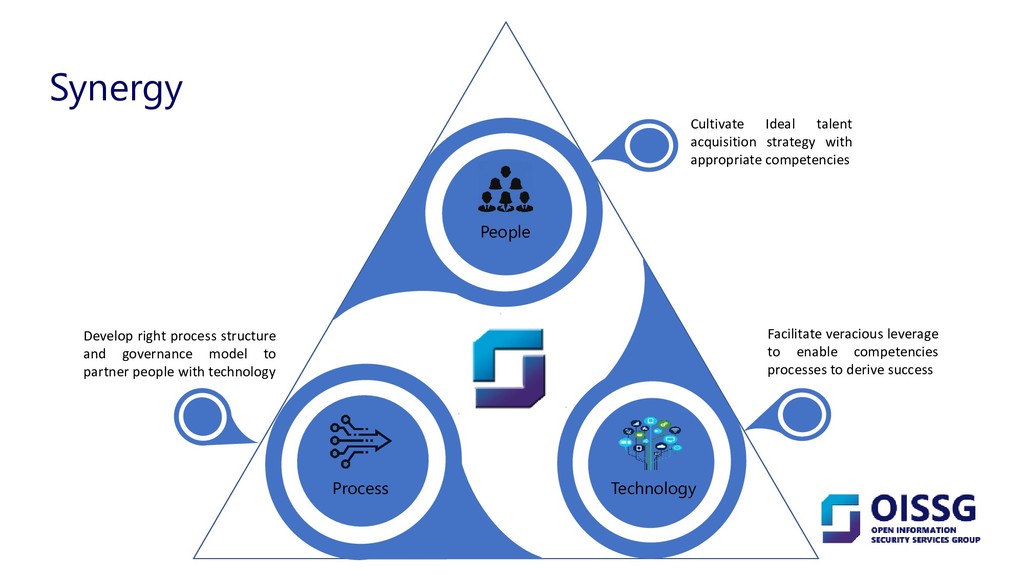
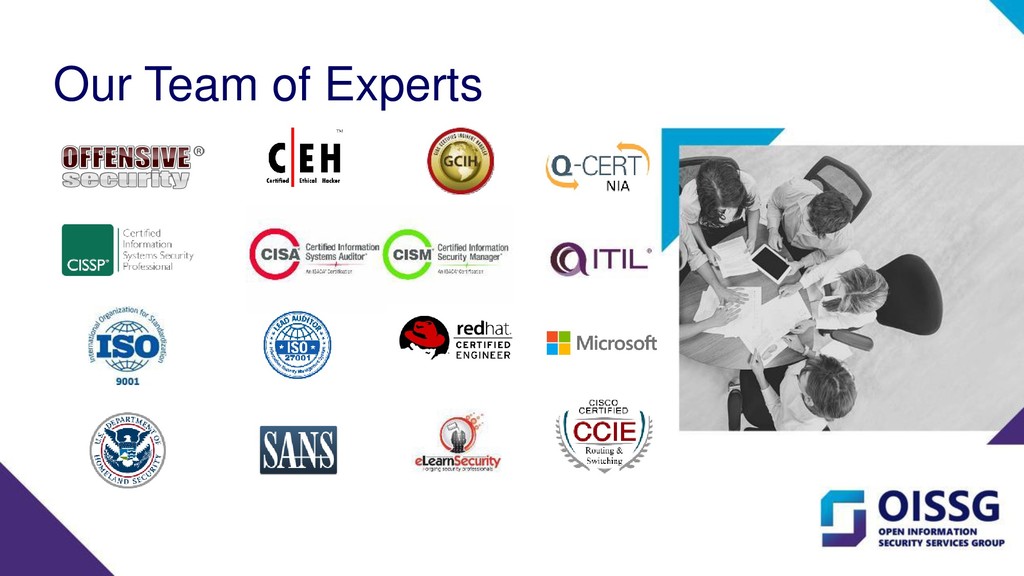
Dedicated team of members available at Qatar A complete security solutions oriented company – specialises in risk consulting Multiple long term contracts extending to more than 3 years with prestigious clients like Public Prosecution, Sidra, Ministry of Justice Lower Total Cost of Ownership (TCO) through assessment of actual needs Certified resources like NIA, ISO 27001 LA, OSCP, CISSP, CEH, CISM, GPEN, etc Providing Compressive Security Risk cover to blue-chip clients and government sectors Unique methodology (Discovery Assessment) Seeks to integrate People, Process & Technology Provide tangibles at each milestones About Us
appropriate competencies Facilitate veracious leverage to enable competencies processes to derive success Develop right process structure and governance model to partner people with technology
ISO 27001, 22000, 22301, 31000 and other ISO Certification training • LMS based Security Awareness Programs • Posters for User Awareness • Software for User Awareness • Awareness SMS - EMAIL
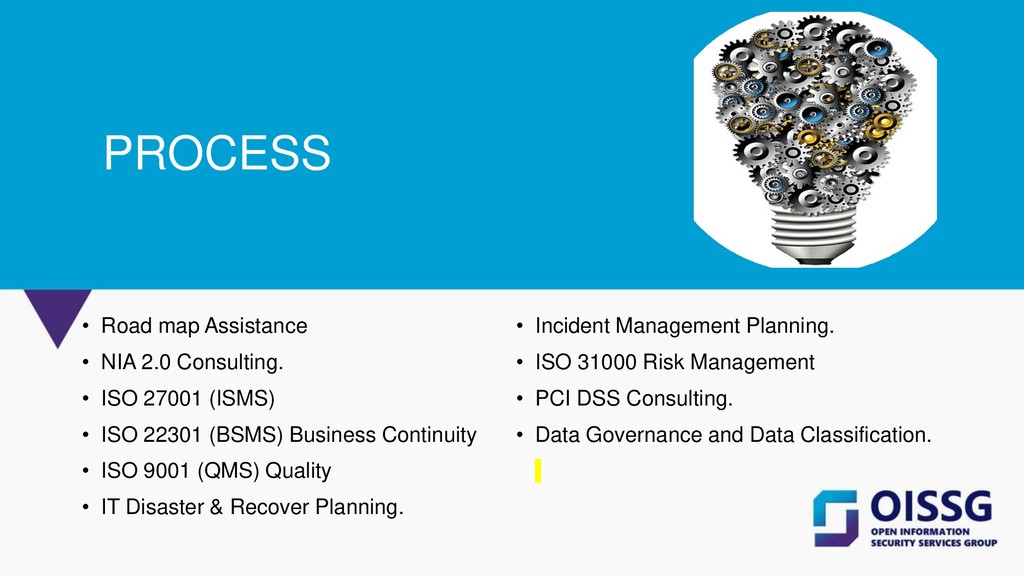
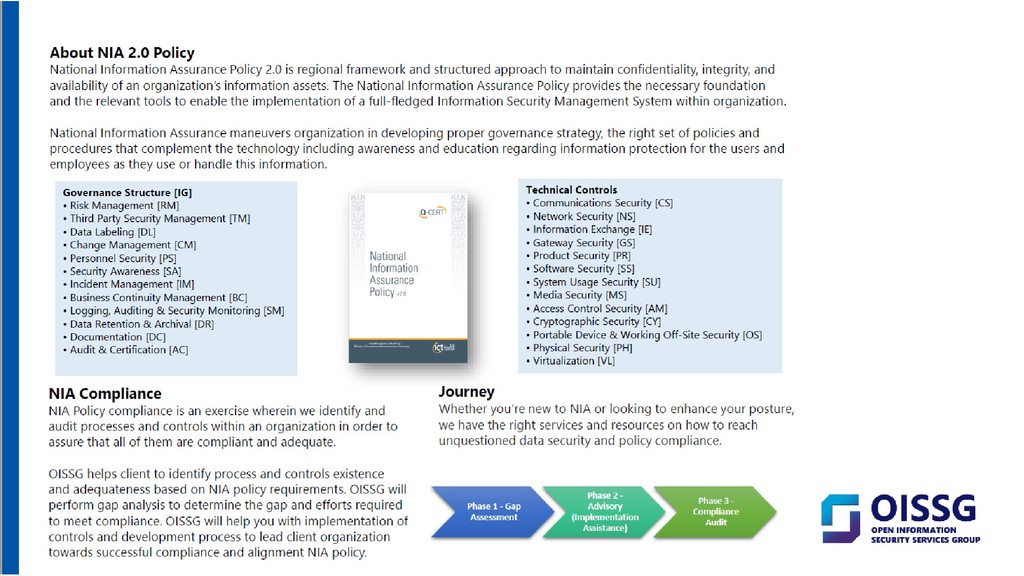
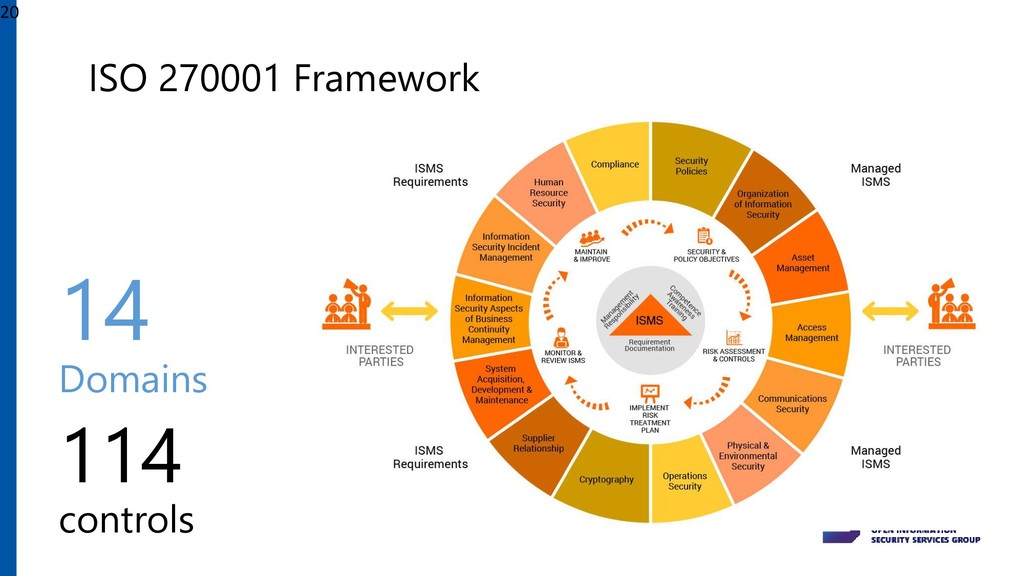
27001 (ISMS) • ISO 22301 (BSMS) Business Continuity • ISO 9001 (QMS) Quality • IT Disaster & Recover Planning. • Incident Management Planning. • ISO 31000 Risk Management • PCI DSS Consulting. • Data Governance and Data Classification. PROCESS
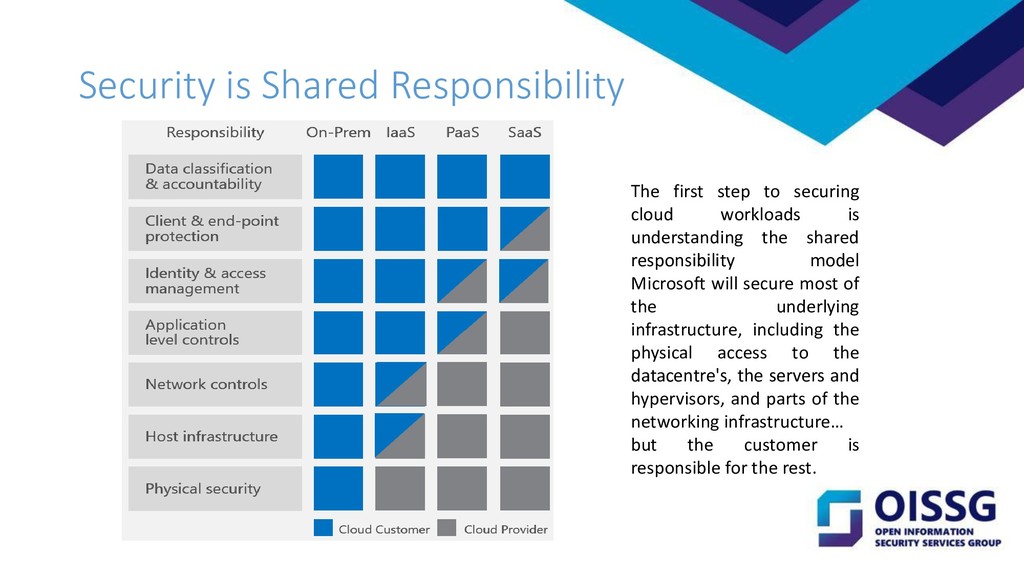
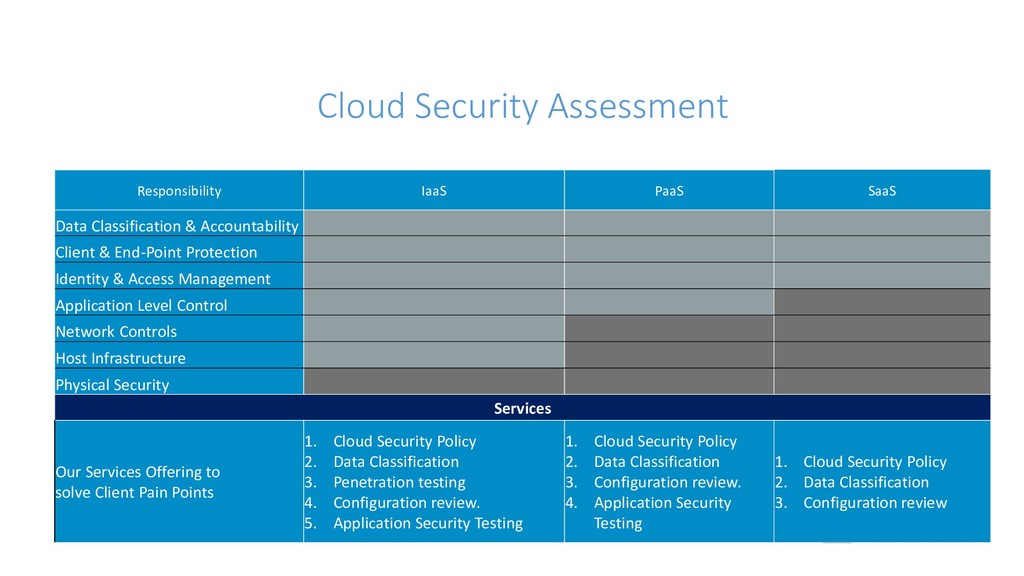
workloads is understanding the shared responsibility model Microsoft will secure most of the underlying infrastructure, including the physical access to the datacentre's, the servers and hypervisors, and parts of the networking infrastructure… but the customer is responsible for the rest.
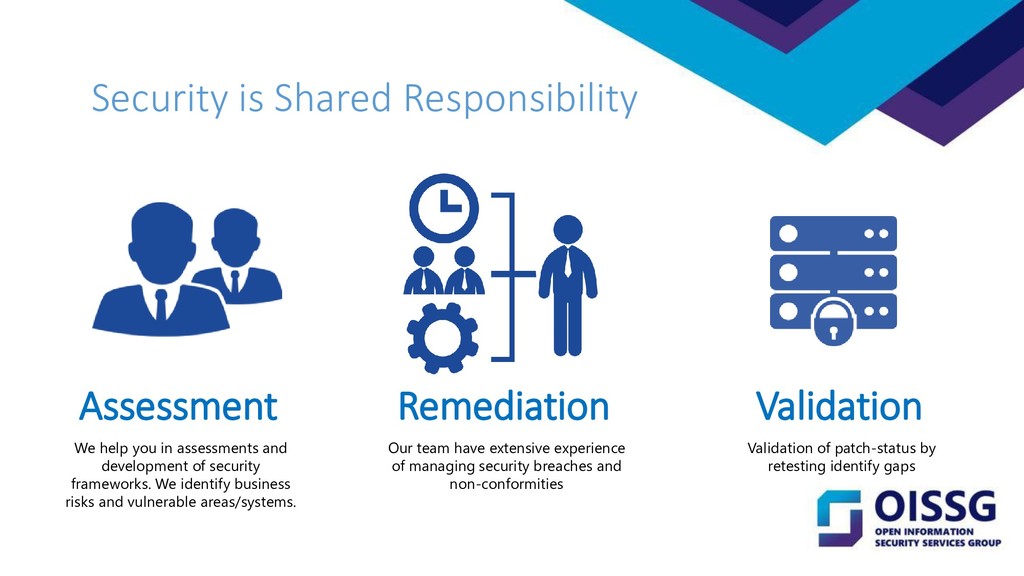
of security frameworks. We identify business risks and vulnerable areas/systems. Our team have extensive experience of managing security breaches and non-conformities Validation of patch-status by retesting identify gaps Security is Shared Responsibility
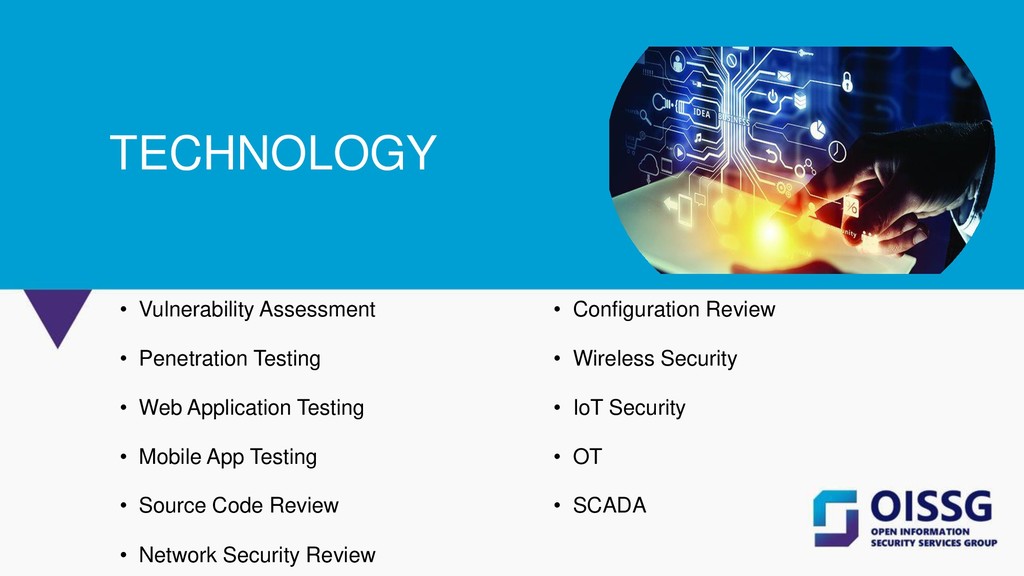
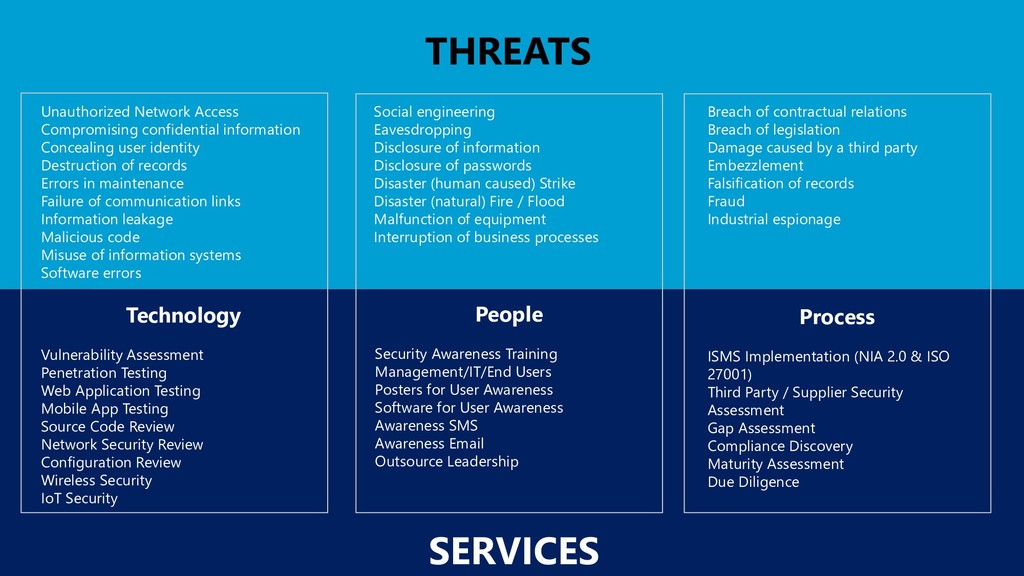
Testing Source Code Review Network Security Review Configuration Review Wireless Security IoT Security People Security Awareness Training Management/IT/End Users Posters for User Awareness Software for User Awareness Awareness SMS Awareness Email Outsource Leadership Process ISMS Implementation (NIA 2.0 & ISO 27001) Third Party / Supplier Security Assessment Gap Assessment Compliance Discovery Maturity Assessment Due Diligence Unauthorized Network Access Compromising confidential information Concealing user identity Destruction of records Errors in maintenance Failure of communication links Information leakage Malicious code Misuse of information systems Software errors Social engineering Eavesdropping Disclosure of information Disclosure of passwords Disaster (human caused) Strike Disaster (natural) Fire / Flood Malfunction of equipment Interruption of business processes Breach of contractual relations Breach of legislation Damage caused by a third party Embezzlement Falsification of records Fraud Industrial espionage THREATS SERVICES


 inesmontani
 nwiizo
 skipperchong
 rasmusluckow
 mlcsv
 rkendrick25
 techseoconnect
 skoyamalab
 orderedlist
 andyhume
 shlominoach
 jct