Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Go Fuzz
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
Oleg Kovalov
January 15, 2019
Programming
100
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Go Fuzz
Oleg Kovalov
January 15, 2019
More Decks by Oleg Kovalov
See All by Oleg Kovalov
Embedded Postgres in Go
olegkovalov
0
100
Hedged requests in Go
olegkovalov
0
450
Writing faster Redis client
olegkovalov
0
240
Moments before main()
olegkovalov
0
120
За пару мгновений до main() [RUS]
olegkovalov
1
660
Bencode - serializer and deserializer in Go
olegkovalov
0
690
impguard - protect your project structure
olegkovalov
0
790
Versioning
olegkovalov
0
150
Modifiability
olegkovalov
0
150
Other Decks in Programming
See All in Programming
Compiling a real-world CLI tool to native with Static Hermes
tmikov2023
0
140
dotNET_vulnclicker_intro.pdf
deka_morita
0
160
最近”作らせてる” ローカルAIアプリの話
akit37
0
520
プロジェクトコードをキレイキレイしよう!暗黙的な参照を読み解く静的解析
ostk0069
0
190
続・コーディングルールの鮮度を保ちたい / keep-fresh-go-internal-conventions-again
handlename
0
150
Seven New Principles of Software Engineering
yegor256
0
380
S3 TablesのIcebergデータに、AIエージェントからアクセスしてみた / 20261016developersio2026joetsu-accessing-iceberg-in-s3tables-via-agent
kasacchiful
PRO
0
240
SODA - FACT BOOK(EN)
sodainc
1
190
Performance Optimization With LLMs
xleitix
0
230
3回つくってわかった、 定期実行ジョブ基盤の本質情報
takai
4
3.4k
コードで差別化できない時代の ソフトウェアエンジニアリング / Software Engineering in an Era Where Code Doesn’t Differentiate
kishida
2
220
Materialが消えた日 〜真っ白なFlutterキャンバスにRenderObjectで絵を描く〜
umigishiaoi
0
120
Featured
See All Featured
Done Done
chrislema
187
17k
DBのスキルで生き残る技術 - AI時代におけるテーブル設計の勘所
soudai
PRO
68
59k
Building a A Zero-Code AI SEO Workflow
portentint
PRO
0
800
Become a Pro
speakerdeck
PRO
31
6.3k
SERP Conf. Vienna - Web Accessibility: Optimizing for Inclusivity and SEO
sarafernandez
2
1.6k
The agentic SEO stack - context over prompts
schlessera
0
990
Jess Joyce - The Pitfalls of Following Frameworks
techseoconnect
PRO
1
460
The Spectacular Lies of Maps
axbom
PRO
1
1.1k
AI Search: Implications for SEO and How to Move Forward - #ShenzhenSEOConference
aleyda
1
1.4k
エンジニアに許された特別な時間の終わり
watany
109
250k
4 Signs Your Business is Dying
shpigford
187
23k
For a Future-Friendly Web
brad_frost
184
11k
Transcript
go-fuzz or new unit testing WARSAW, JAN 15 2019 Oleg
Kovalov Allegro Twitter: oleg_kovalov Github: cristaloleg
Me - Gopher for ~3 years - Open-source contributor -
Engineer at Allegro.pl core team Twitter: @oleg_kovalov Github: @cristaloleg
Everything start from the Wikipedia Fuzzing is a software testing
technique, often automated or semi-automated, that involves providing invalid, unexpected, or random data to the inputs of a computer program.
go-fuzz - Made by The Dmitry Vyukov aka Bug Slaughterer
at Google - 300+ fixes in Go compiler and stdlib - +inf in the wild, or more - See AFL and syzkaller
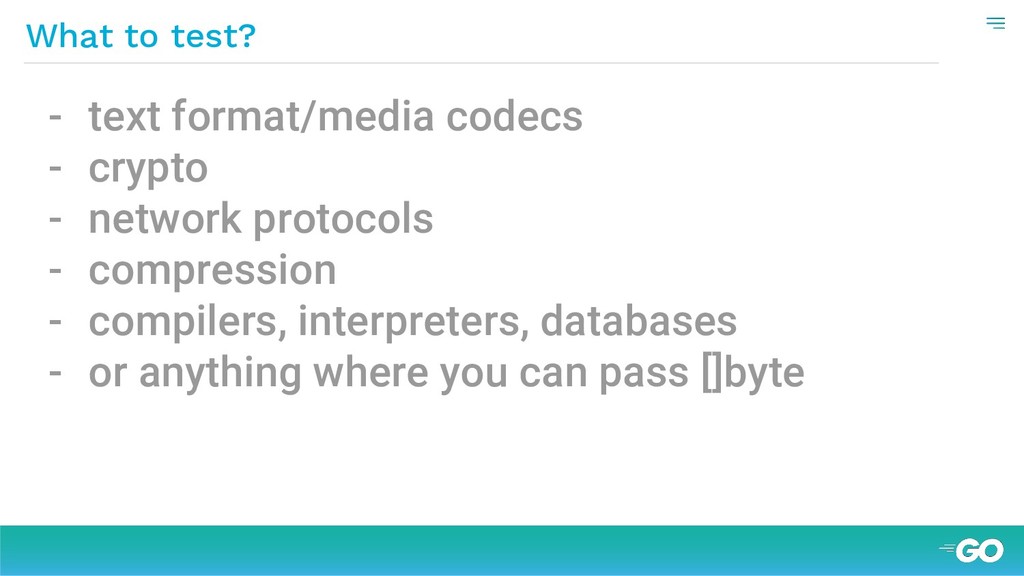
What to test? - text format/media codecs - crypto -
network protocols - compression - compilers, interpreters, databases - or anything where you can pass []byte
- horribly easy to use - no human interaction -
designed for computers But why fuzzing?
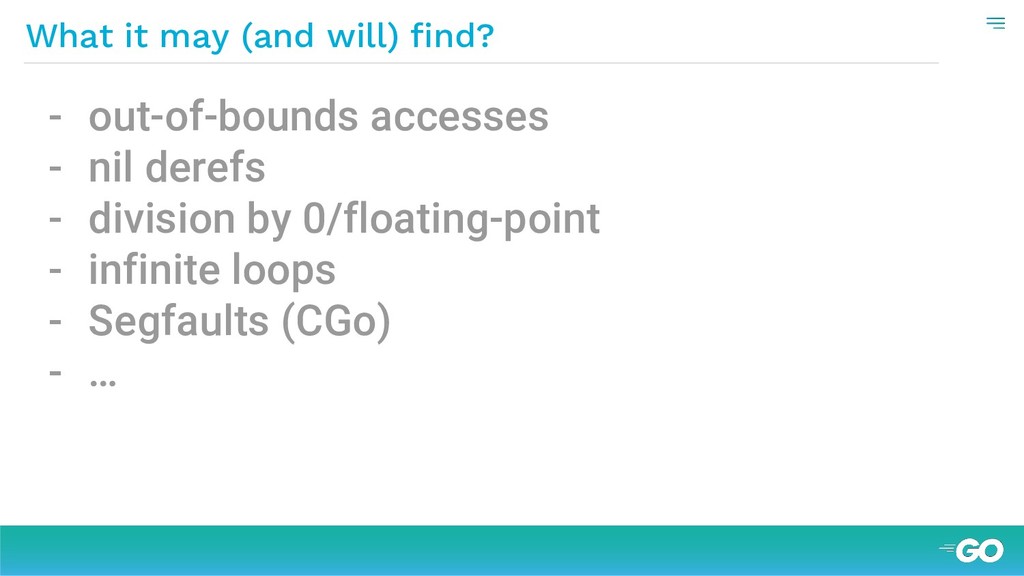
- out-of-bounds accesses - nil derefs - division by 0/floating-point
- infinite loops - Segfaults (CGo) - … What it may (and will) find?
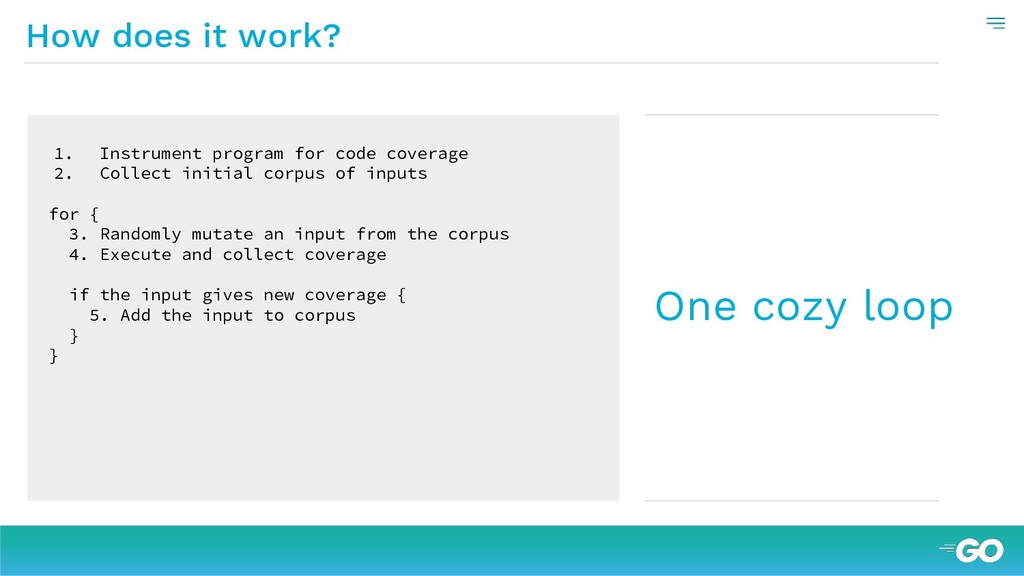
How does it work? 1. Instrument program for code coverage
2. Collect initial corpus of inputs for { 3. Randomly mutate an input from the corpus 4. Execute and collect coverage if the input gives new coverage { 5. Add the input to corpus } } One cozy loop
func SafeFunc(input string) { if input[0] == 'A' { if
input[1] == 'B' { if input[2] == 'C' { if input[3] == 'D' { print(input[4]) // }}}}} Brute force generation O(2^8^4) = O(2^32) tries. Bruteforce “SafeFunc”
func SafeFunc(input string) { if input[0] == 'A' { if
input[1] == 'B' { if input[2] == 'C' { if input[3] == 'D' { print(input[4]) // }}}}} Brute force generation O(2^8^4) = O(2^32) tries. 0. {} 1. {"A"} 2. {"A", "AB"} 3. {"A", "AB", "ABC"} 4. {"A", "AB", "ABC", "ABCD"} Coverage-guided fuzzer needs O(4 * 2^8) = O(2^10) tries. Smartforce “SafeFunc”
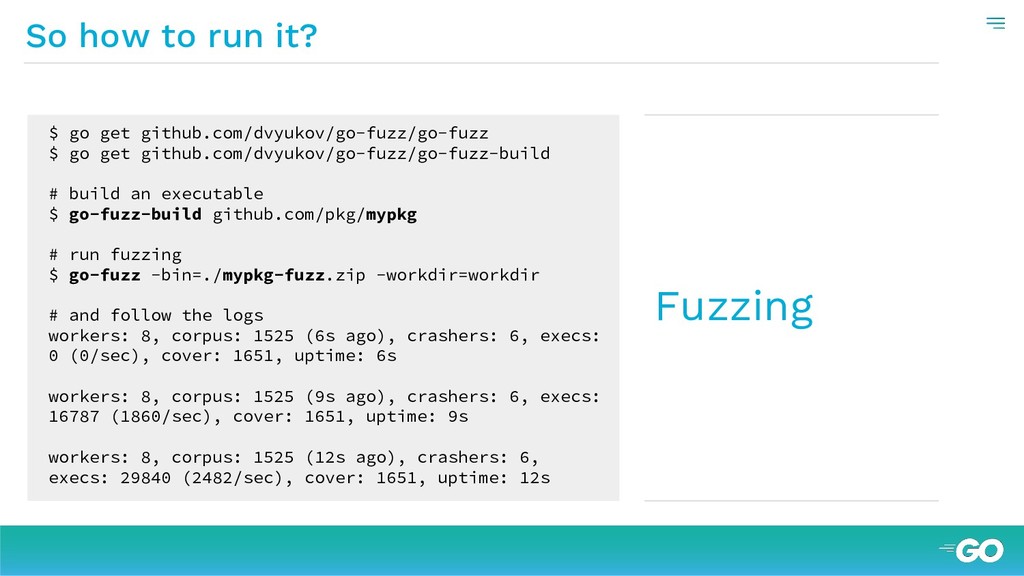
So how to run it? $ go get github.com/dvyukov/go-fuzz/go-fuzz $
go get github.com/dvyukov/go-fuzz/go-fuzz-build # build an executable $ go-fuzz-build github.com/pkg/mypkg # run fuzzing $ go-fuzz -bin=./mypkg-fuzz.zip -workdir=workdir # and follow the logs workers: 8, corpus: 1525 (6s ago), crashers: 6, execs: 0 (0/sec), cover: 1651, uptime: 6s workers: 8, corpus: 1525 (9s ago), crashers: 6, execs: 16787 (1860/sec), cover: 1651, uptime: 9s workers: 8, corpus: 1525 (12s ago), crashers: 6, execs: 29840 (2482/sec), cover: 1651, uptime: 12s Fuzzing
func Fuzz([]byte) int // +build gofuzz package mypkg func Fuzz(data
[]byte) int { _, err := WellTestedFunc(string(data)) if err != nil { return 0 } return 1 } 95% fuzz funcs
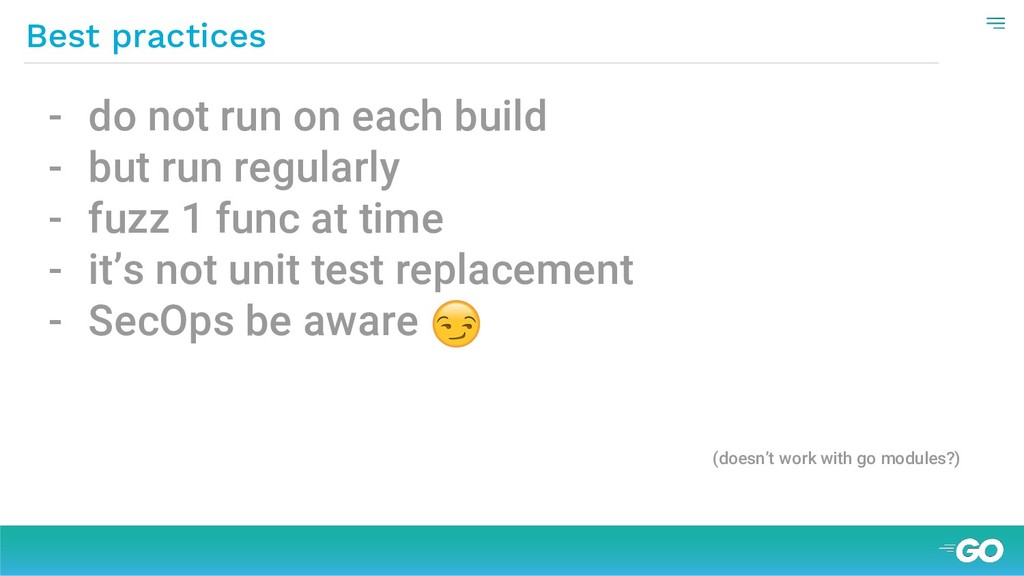
- do not run on each build - but run
regularly - fuzz 1 func at time - it’s not unit test replacement - SecOps be aware (doesn’t work with go modules?) Best practices
That’s all folks Thank you Questions? Twitter: @oleg_kovalov Github: @cristaloleg


 olegkovalov
 tmikov2023
 deka_morita
 akit37
 ostk0069
 handlename
 yegor256
 kasacchiful
 sodainc
 xleitix
 takai
 kishida
 umigishiaoi
 chrislema
 soudai
 portentint
 speakerdeck
 sarafernandez
 schlessera
 techseoconnect
 axbom
 aleyda
 watany
 shpigford
 brad_frost