Share
Embed
Single sign-on for mobile native applications
Slides for the NDC Oslo 2014 session on mobile authentication and authorization.
Video available at https://vimeo.com/97349269. Demos available at https://github.com/pmhsfelix/ndc-oslo-14-mobile-auth.
Pedro Felix
June 04, 2014
Transcript
89 slides
-
Outline • Token based access control circa 2014 • Mobile
clients • Single sign-on for mobile clients • Hybrid clients 2 -
• Teacher at the Lisbon Polytechnic Institute • Independent Consultant
• Web APIs, Identity and Access Control • Co-author of Designing Evolvable Web APIs with ASP.NET, O’Reilly, 2014 whoami 3 -
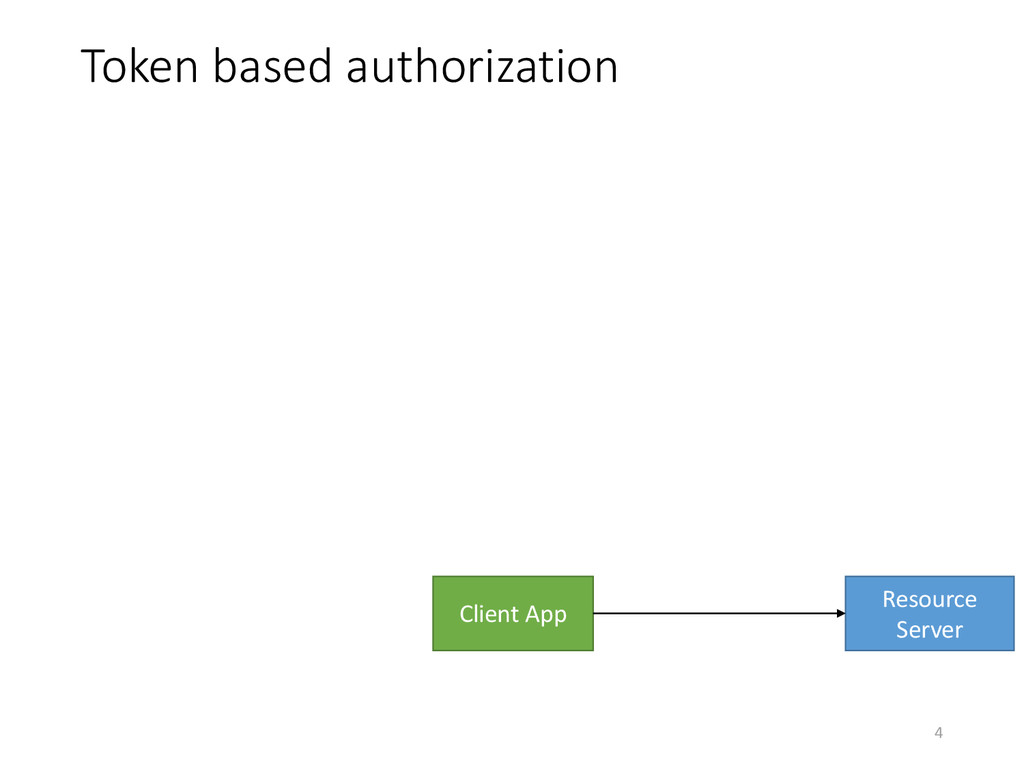
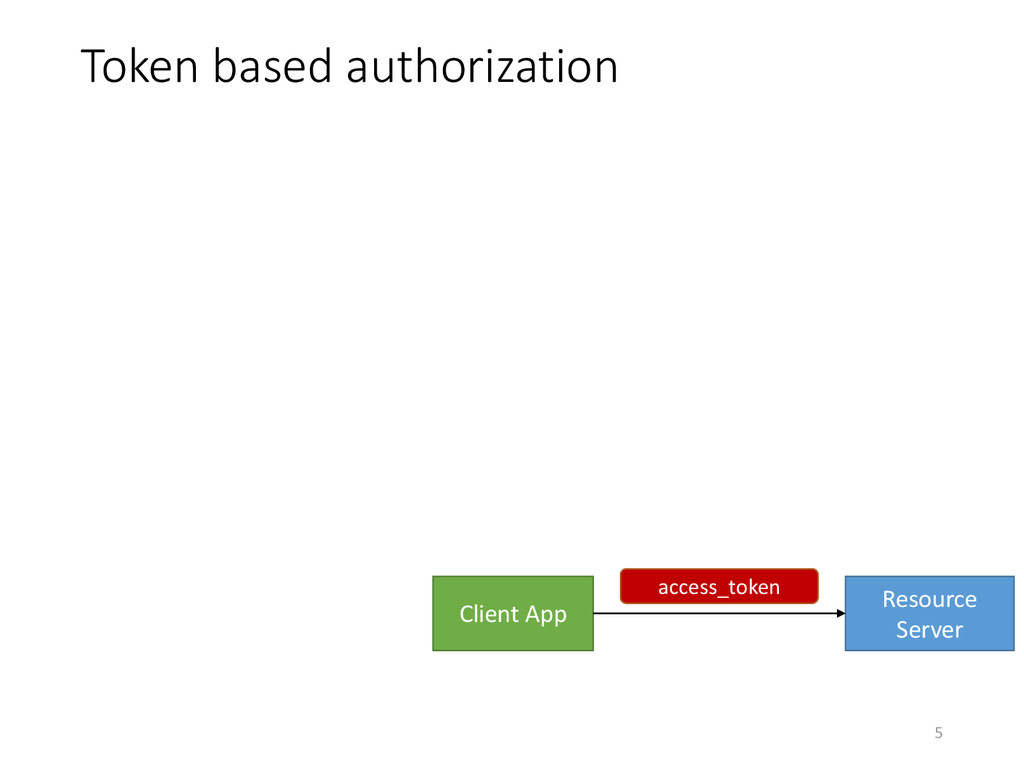
Token based authorization 6 Client App Resource Server access_token GET
/resource HTTP/1.1 Authorization: Bearer the.access.token -
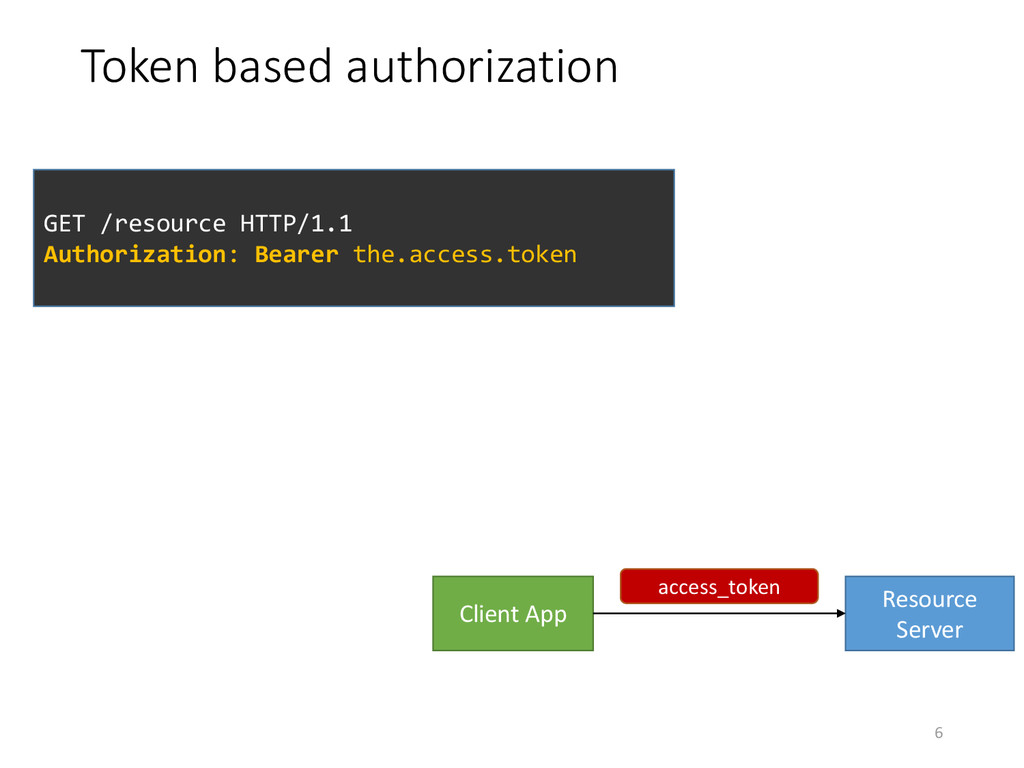
Token based authorization 7 Client App Resource Server access_token GET
/resource HTTP/1.1 Authorization: Bearer the.access.token POST /resource HTTP/1.1 Content-Type: application/x-www-form-urlencoded access_token=the.access.token -
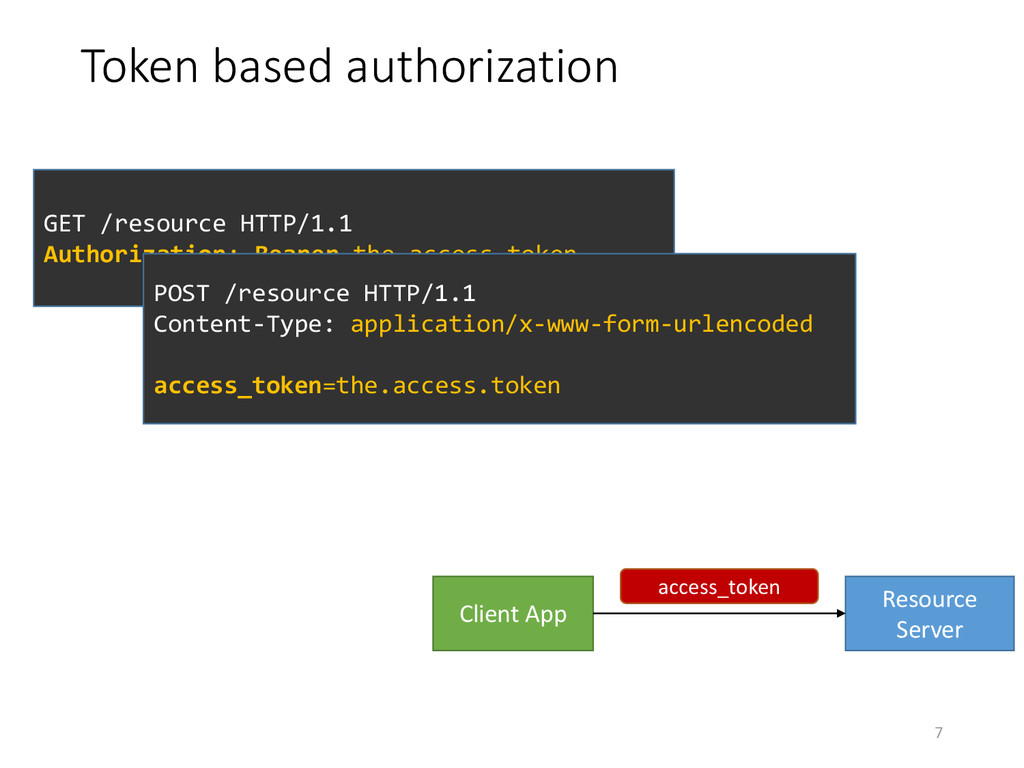
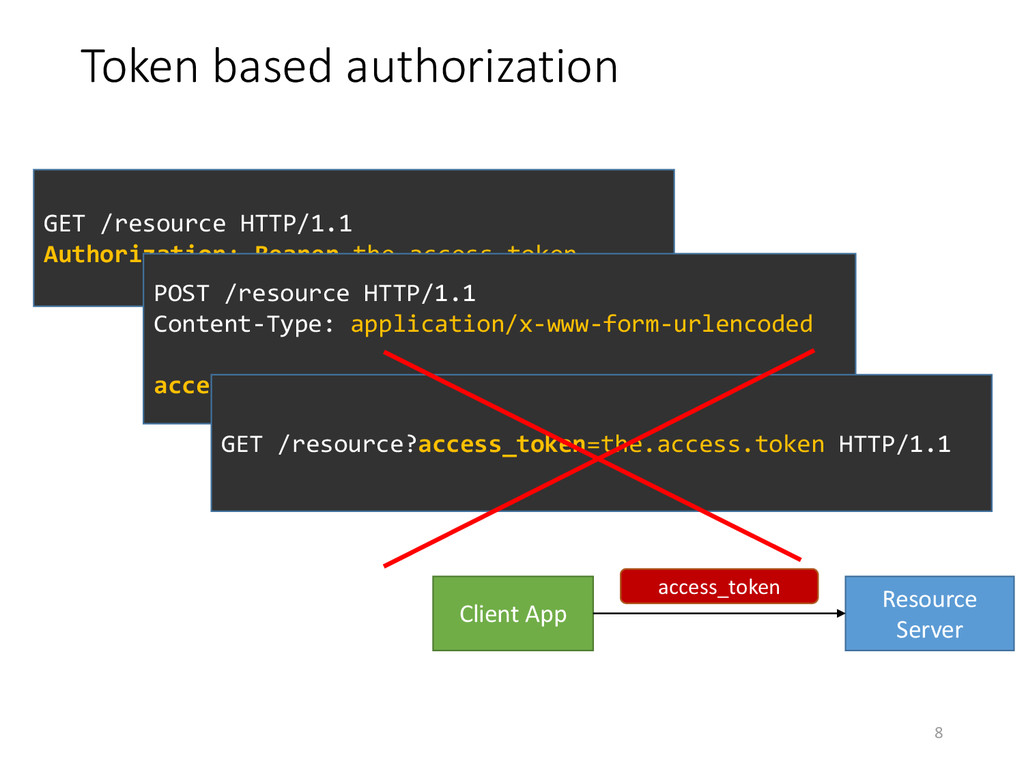
Token based authorization 8 Client App Resource Server access_token GET
/resource HTTP/1.1 Authorization: Bearer the.access.token POST /resource HTTP/1.1 Content-Type: application/x-www-form-urlencoded access_token=the.access.token GET /resource?access_token=the.access.token HTTP/1.1 -
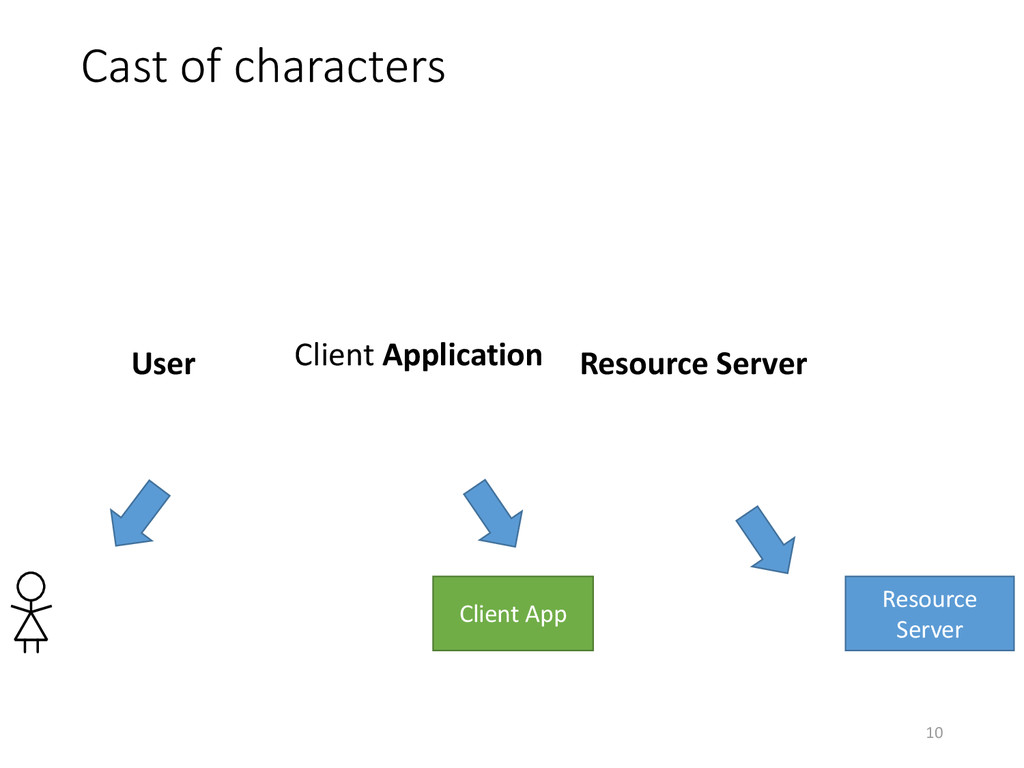
Cast of characters 10 Client App Resource Server Client Application
User Resource Server -
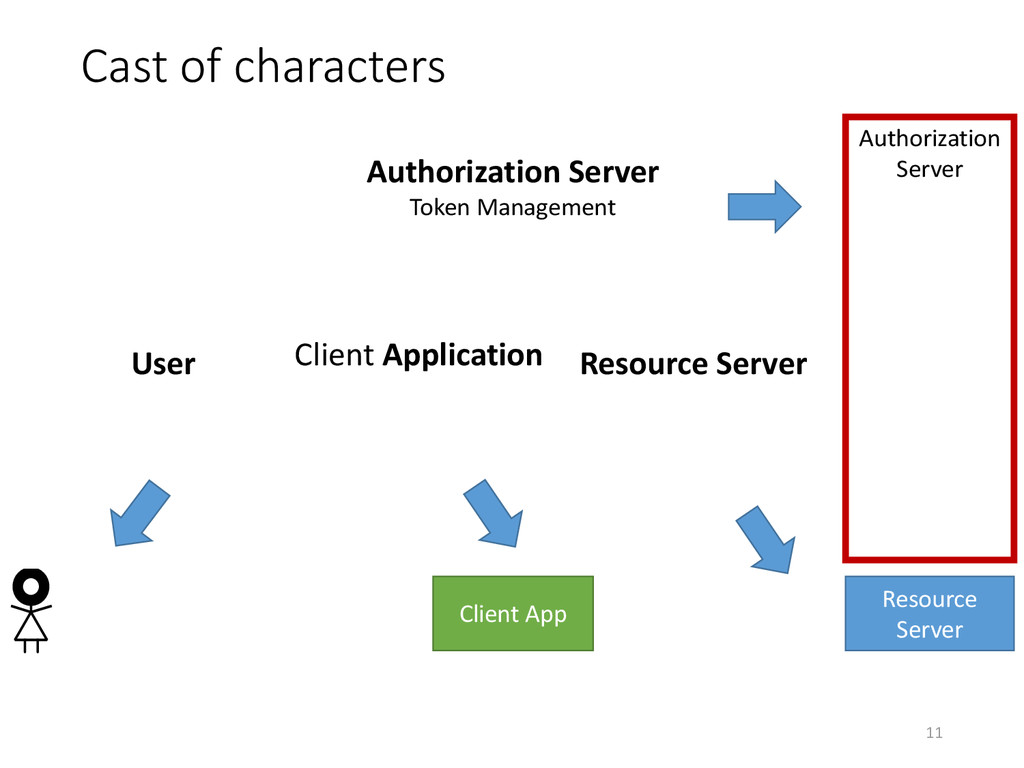
Cast of characters 11 Client App Resource Server Authorization Server
Client Application User Authorization Server Token Management Resource Server -
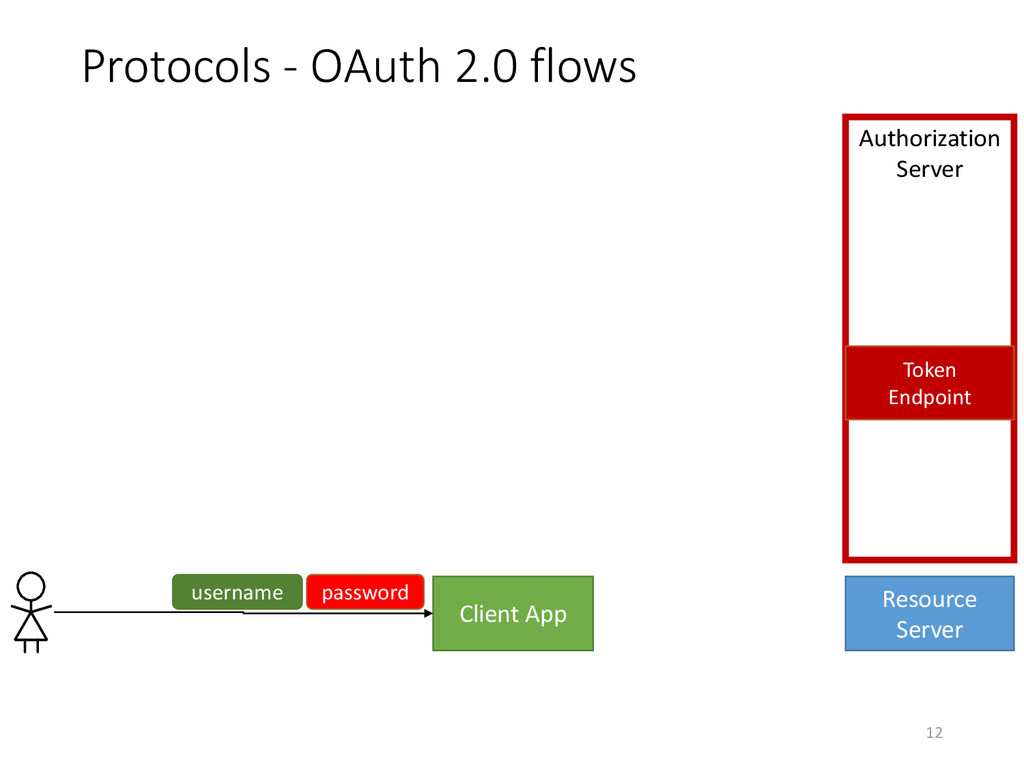
Protocols - OAuth 2.0 flows 12 Client App Resource Server
Authorization Server Token Endpoint password username -
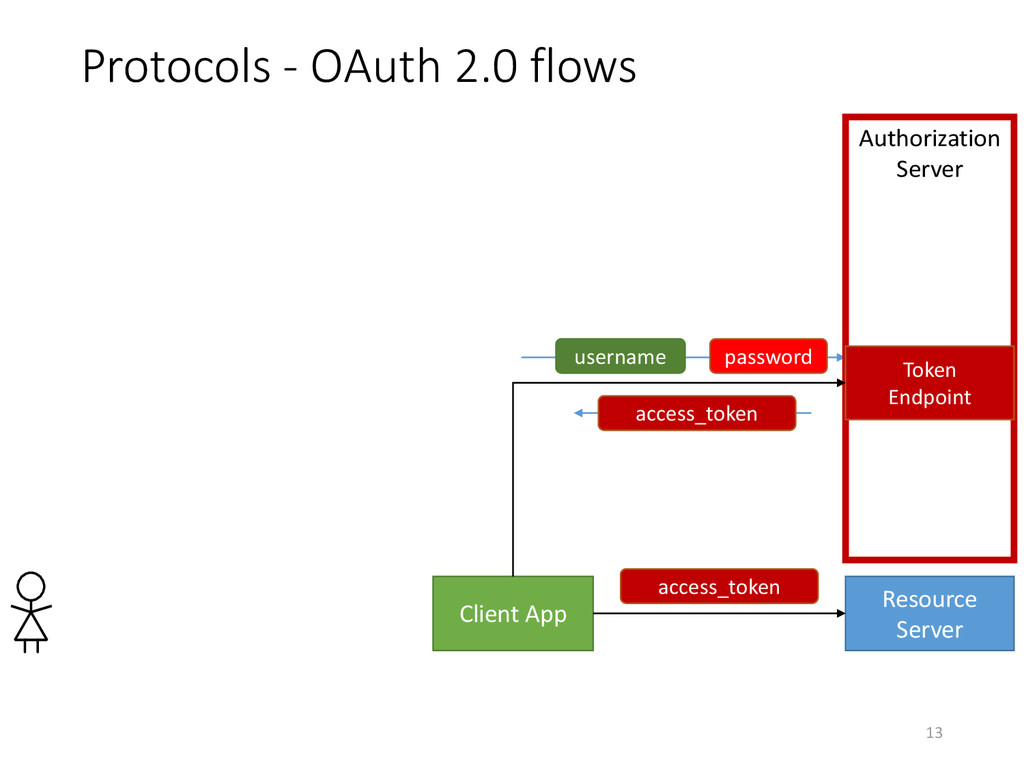
Protocols - OAuth 2.0 flows 13 Client App Resource Server
Authorization Server Token Endpoint access_token password username access_token -
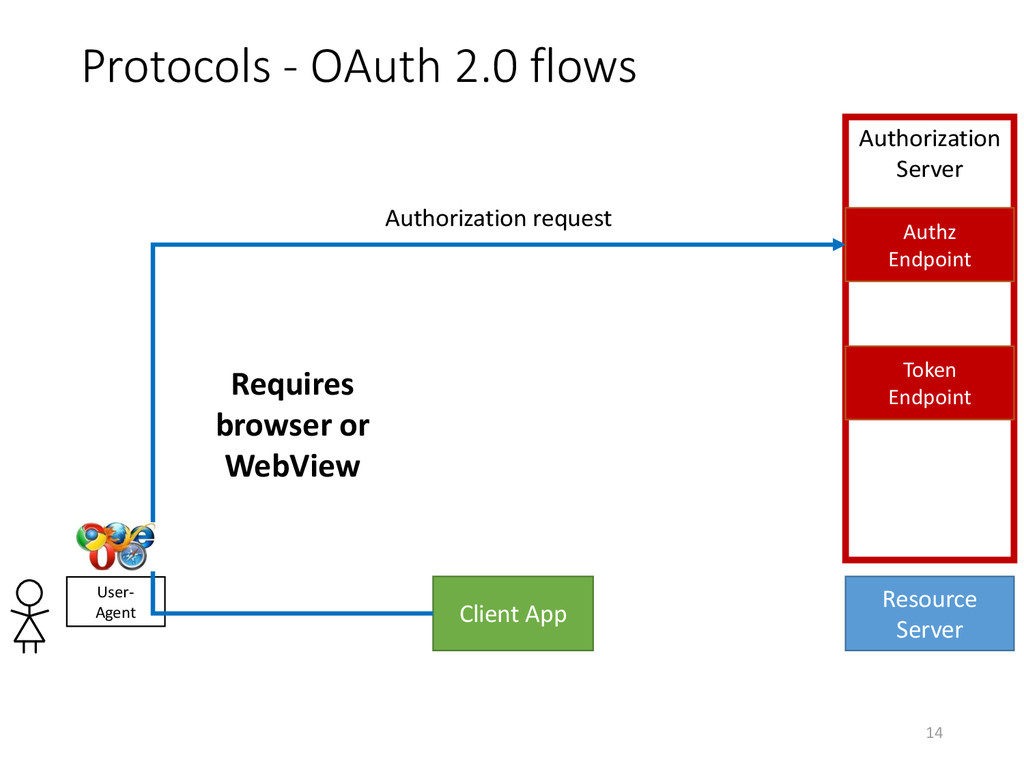
Protocols - OAuth 2.0 flows 14 Client App Resource Server
Authorization Server Token Endpoint User- Agent Authorization request Authz Endpoint Requires browser or WebView -
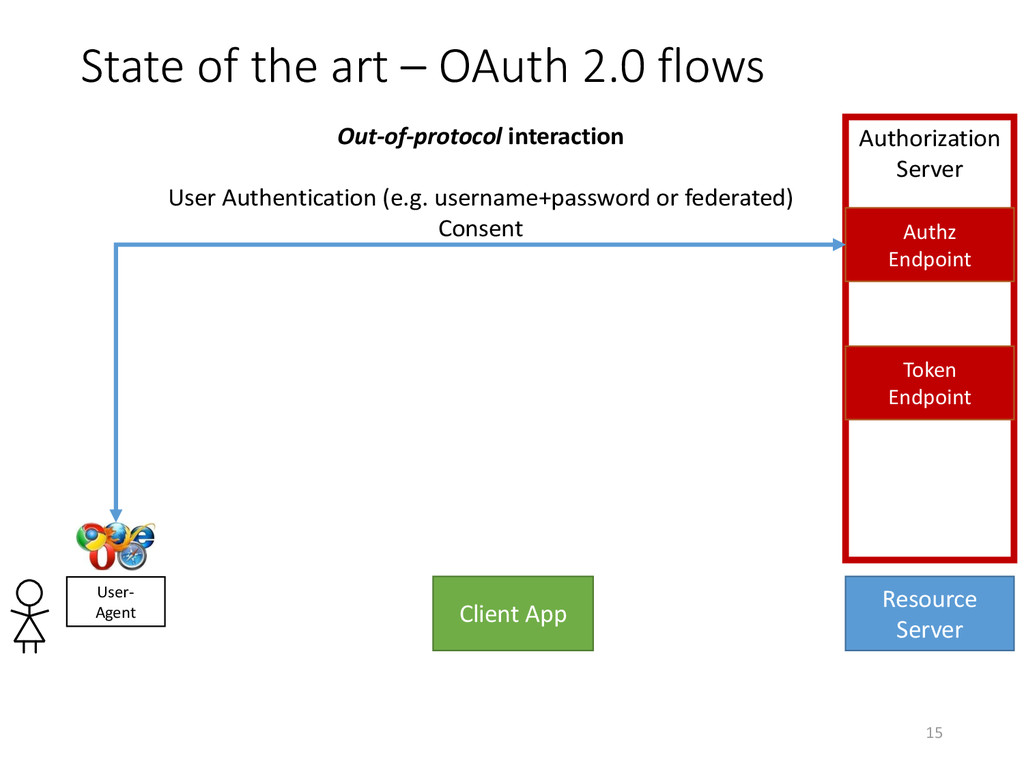
State of the art – OAuth 2.0 flows 15 Client
App Resource Server Authorization Server Token Endpoint User- Agent Authz Endpoint Out-of-protocol interaction User Authentication (e.g. username+password or federated) Consent -
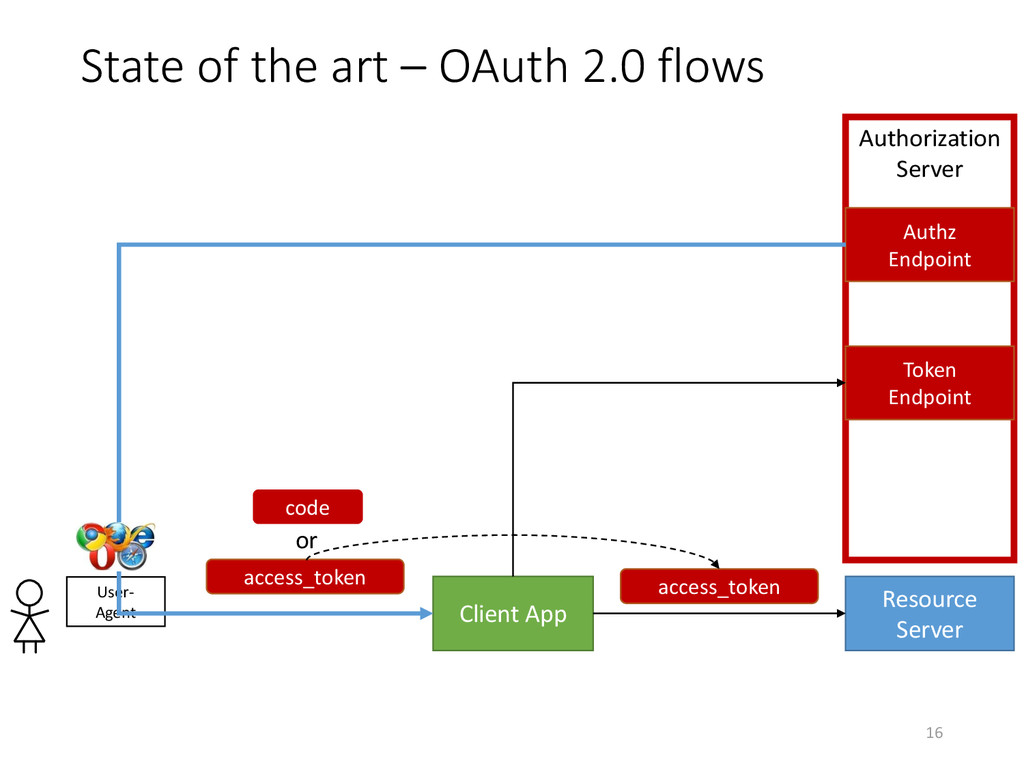
State of the art – OAuth 2.0 flows 16 Client
App Resource Server Authorization Server Token Endpoint User- Agent Authz Endpoint code access_token or access_token -
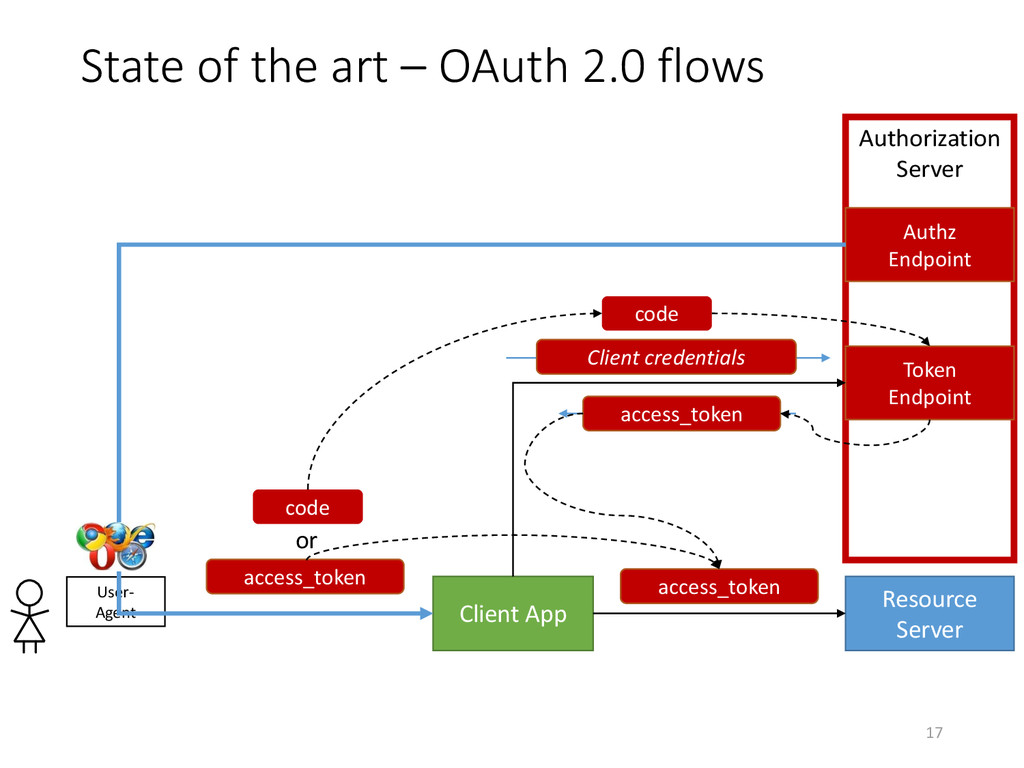
State of the art – OAuth 2.0 flows 17 Client
App Resource Server Authorization Server Token Endpoint User- Agent Authz Endpoint access_token Client credentials code code access_token or access_token -
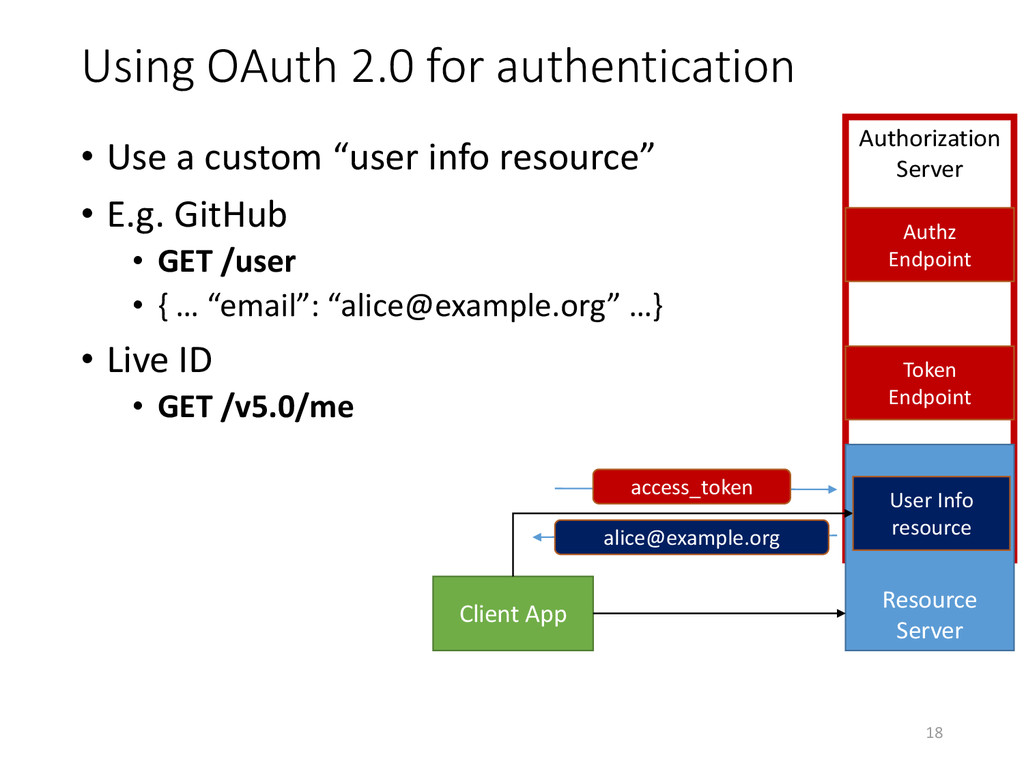
Authorization Server Using OAuth 2.0 for authentication • Use a
custom “user info resource” • E.g. GitHub • GET /user • { … “email”: “[email protected]” …} • Live ID • GET /v5.0/me 18 Client App Resource Server Token Endpoint Authz Endpoint access_token User Info resource [email protected] -
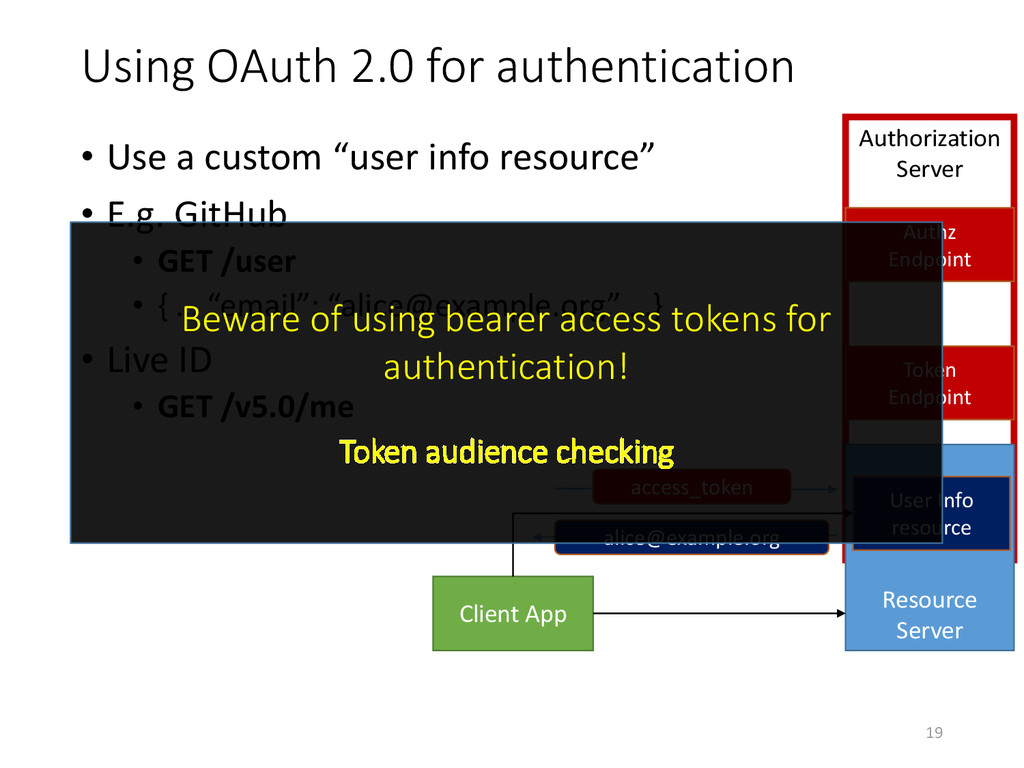
Authorization Server Using OAuth 2.0 for authentication • Use a
custom “user info resource” • E.g. GitHub • GET /user • { … “email”: “[email protected]” …} • Live ID • GET /v5.0/me 19 Client App Resource Server Token Endpoint Authz Endpoint access_token User Info resource [email protected] Beware of using bearer access tokens for authentication! Token audience checking -
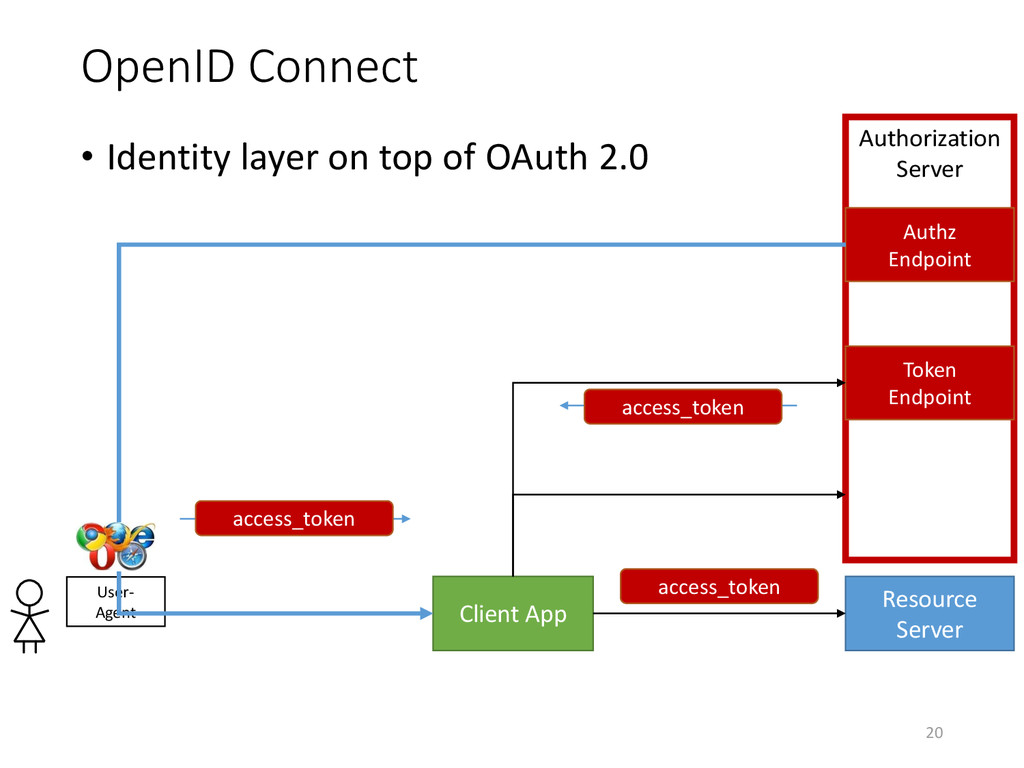
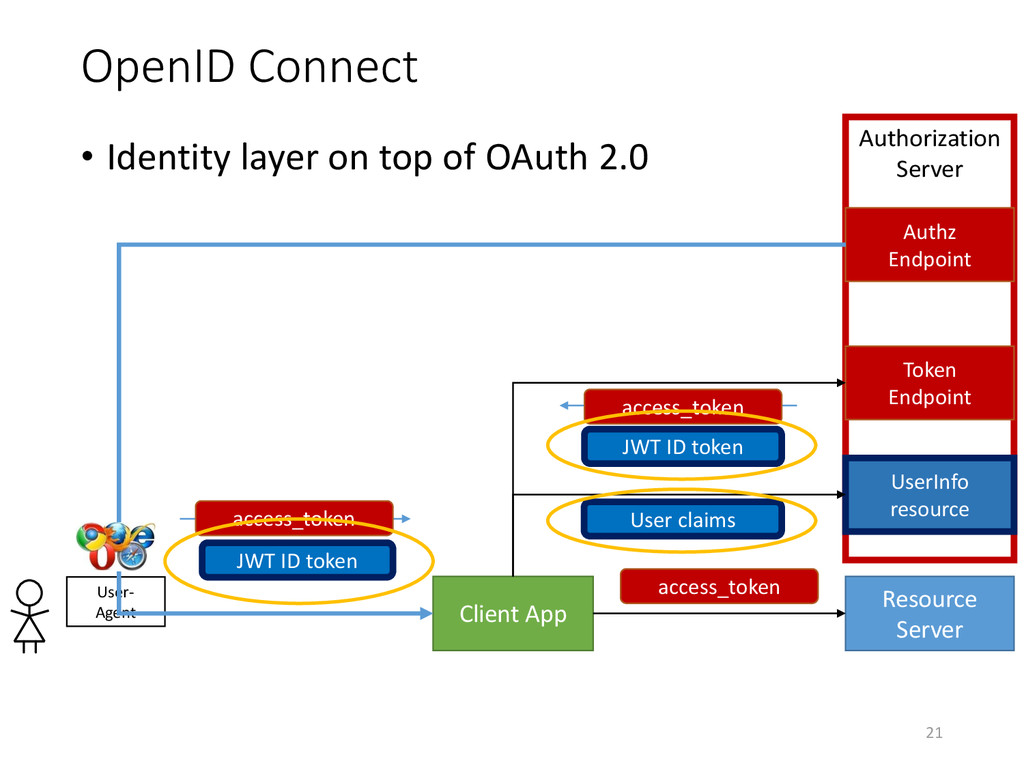
OpenID Connect • Identity layer on top of OAuth 2.0
20 Client App Resource Server Authorization Server Token Endpoint User- Agent Authz Endpoint access_token access_token access_token -
OpenID Connect 21 Client App Resource Server Authorization Server Token
Endpoint User- Agent Authz Endpoint access_token access_token access_token JWT ID token JWT ID token UserInfo resource User claims • Identity layer on top of OAuth 2.0 -
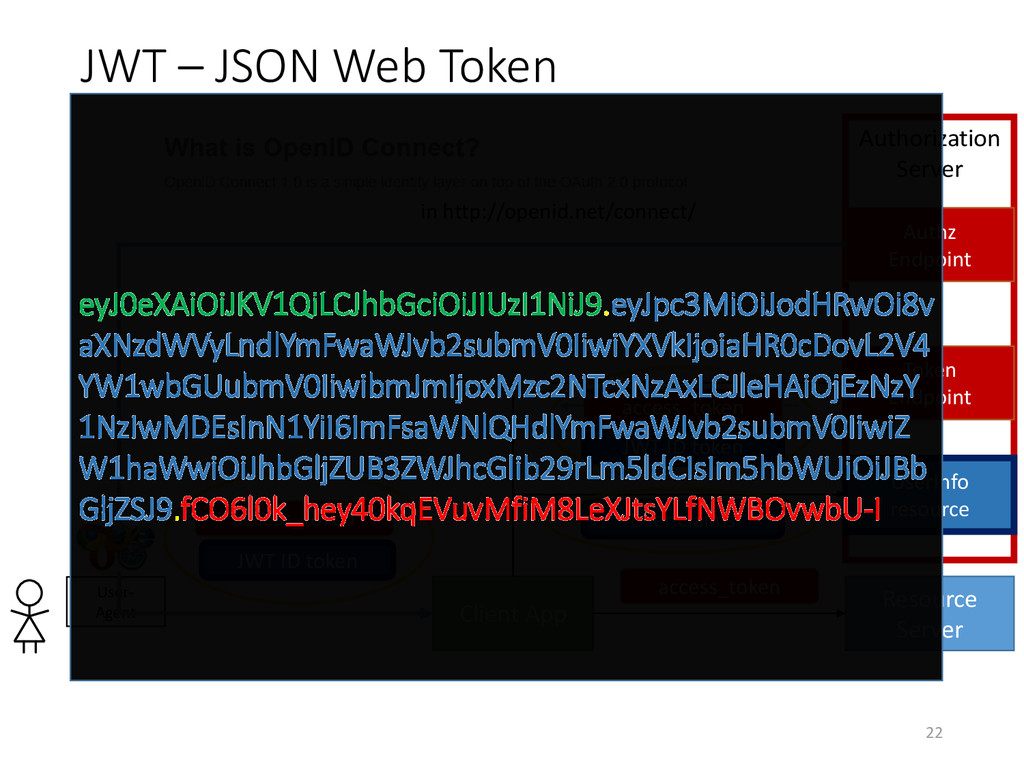
JWT – JSON Web Token 22 Client App Resource Server
Authorization Server Token Endpoint User- Agent Authz Endpoint access_token access_token access_token JWT ID token JWT ID token UserInfo resource User claims in http://openid.net/connect/ eyJ0eXAiOiJKV1QiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiJodHRwOi8v aXNzdWVyLndlYmFwaWJvb2submV0IiwiYXVkIjoiaHR0cDovL2V4 YW1wbGUubmV0IiwibmJmIjoxMzc2NTcxNzAxLCJleHAiOjEzNzY 1NzIwMDEsInN1YiI6ImFsaWNlQHdlYmFwaWJvb2submV0IiwiZ W1haWwiOiJhbGljZUB3ZWJhcGlib29rLm5ldCIsIm5hbWUiOiJBb GljZSJ9.fCO6l0k_hey40kqEVuvMfiM8LeXJtsYLfNWBOvwbU-I -
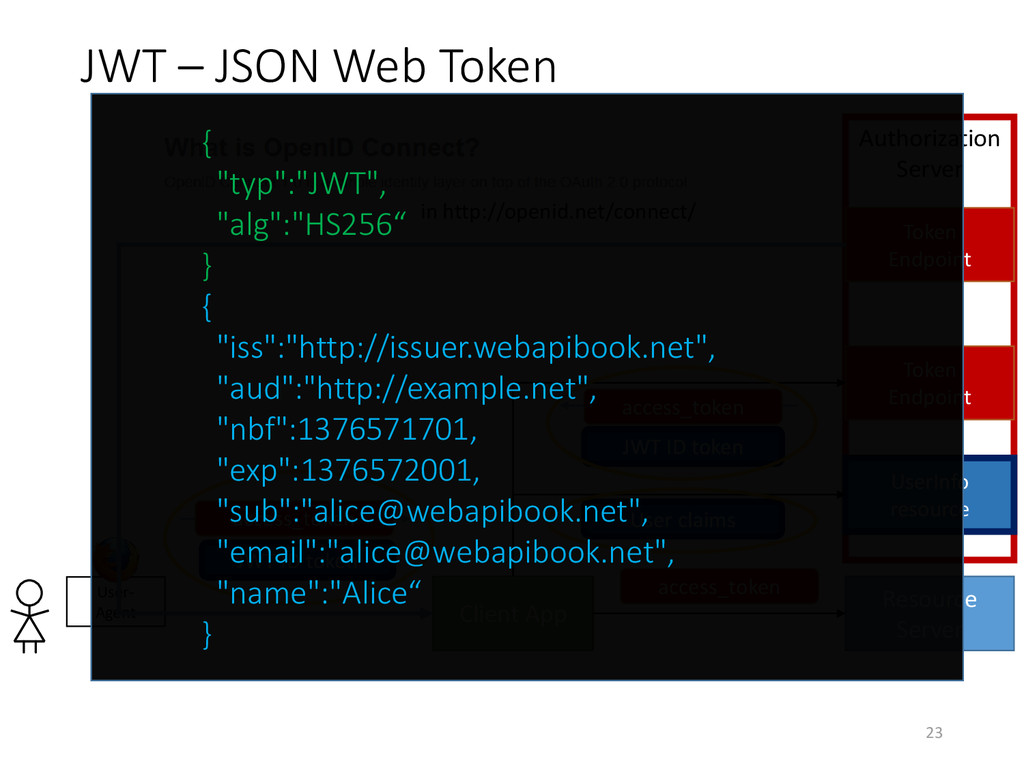
JWT – JSON Web Token 23 Client App Resource Server
Authorization Server Token Endpoint User- Agent Token Endpoint access_token access_token access_token JWT ID token JWT ID token UserInfo resource User claims in http://openid.net/connect/ { "typ":"JWT", "alg":"HS256“ } { "iss":"http://issuer.webapibook.net", "aud":"http://example.net", "nbf":1376571701, "exp":1376572001, "sub":"[email protected]", "email":"[email protected]", "name":"Alice“ } -
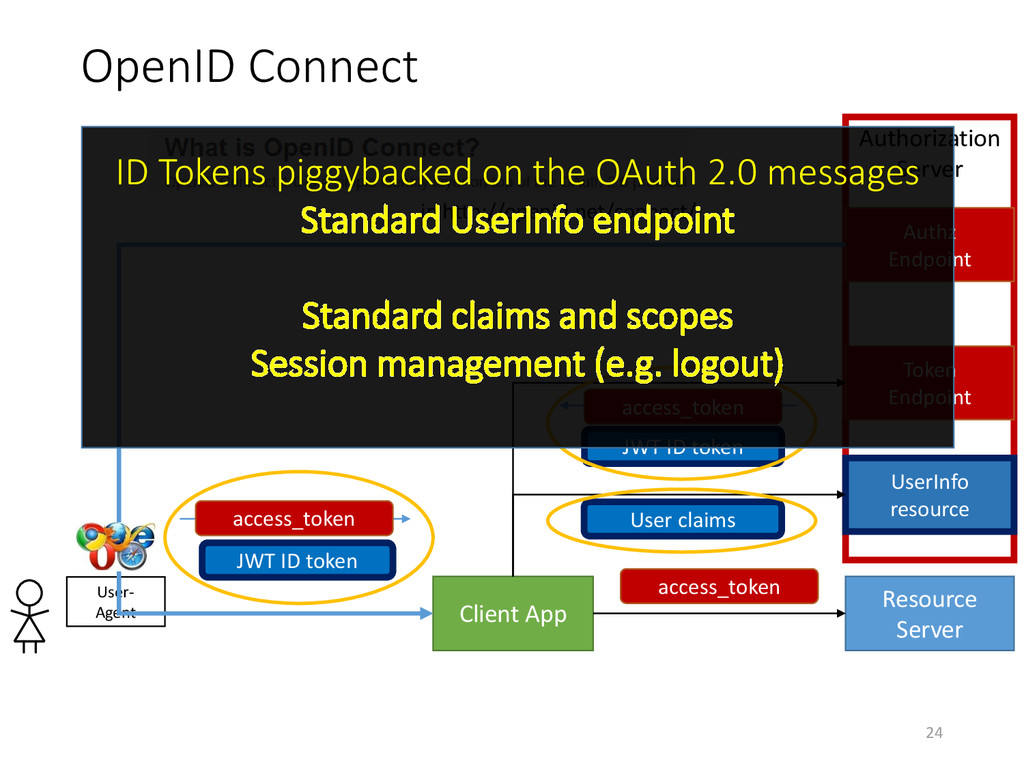
OpenID Connect 24 Client App Resource Server Authorization Server Token
Endpoint User- Agent Authz Endpoint access_token access_token access_token JWT ID token JWT ID token UserInfo resource User claims in http://openid.net/connect/ ID Tokens piggybacked on the OAuth 2.0 messages Standard UserInfo endpoint Standard claims and scopes Session management (e.g. logout) -
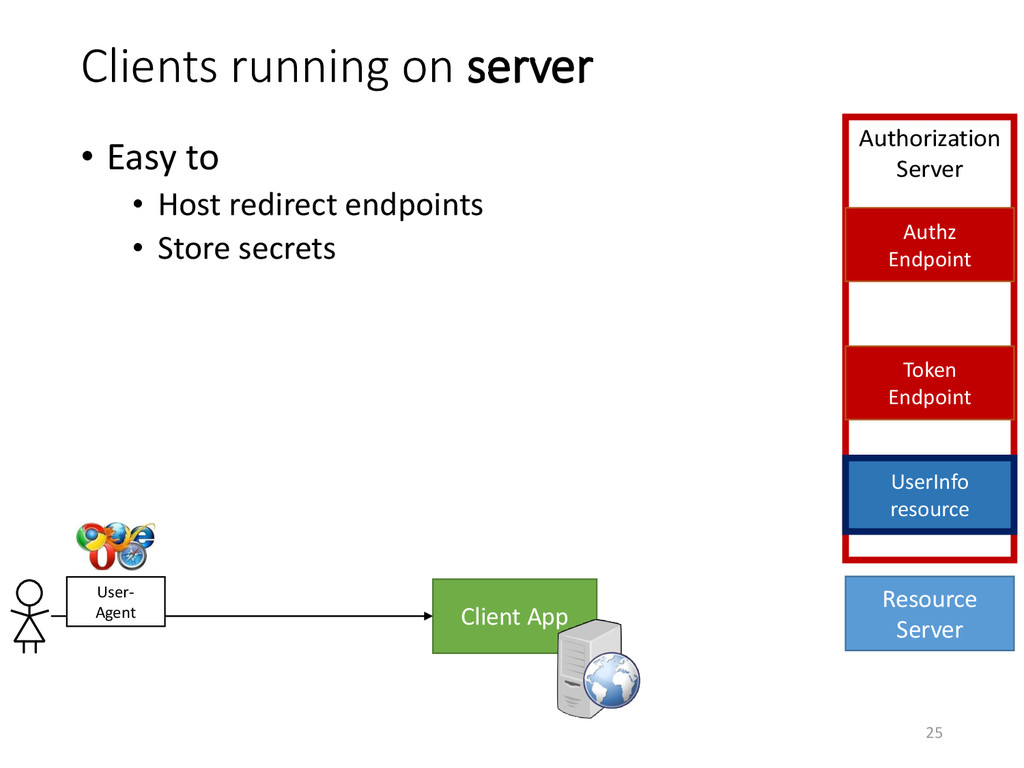
Clients running on server • Easy to • Host redirect
endpoints • Store secrets 25 Client App Resource Server Authorization Server Token Endpoint Authz Endpoint UserInfo resource User- Agent -
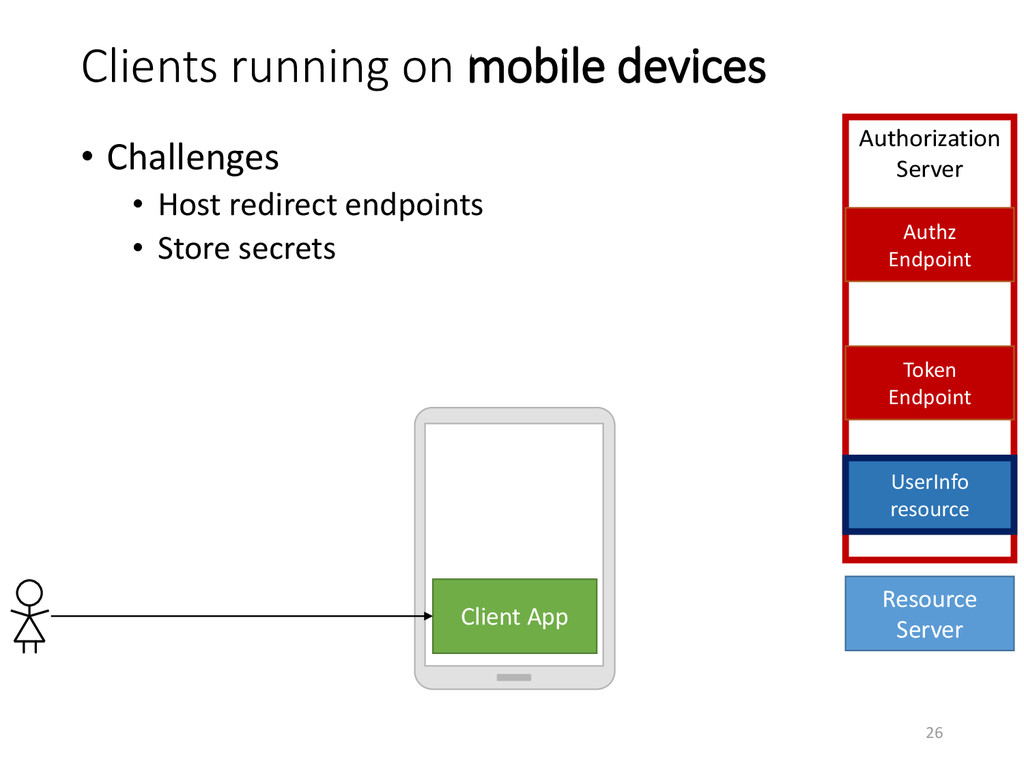
Clients running on mobile devices 26 Client App Resource Server
Authorization Server Token Endpoint Authz Endpoint UserInfo resource • Challenges • Host redirect endpoints • Store secrets -
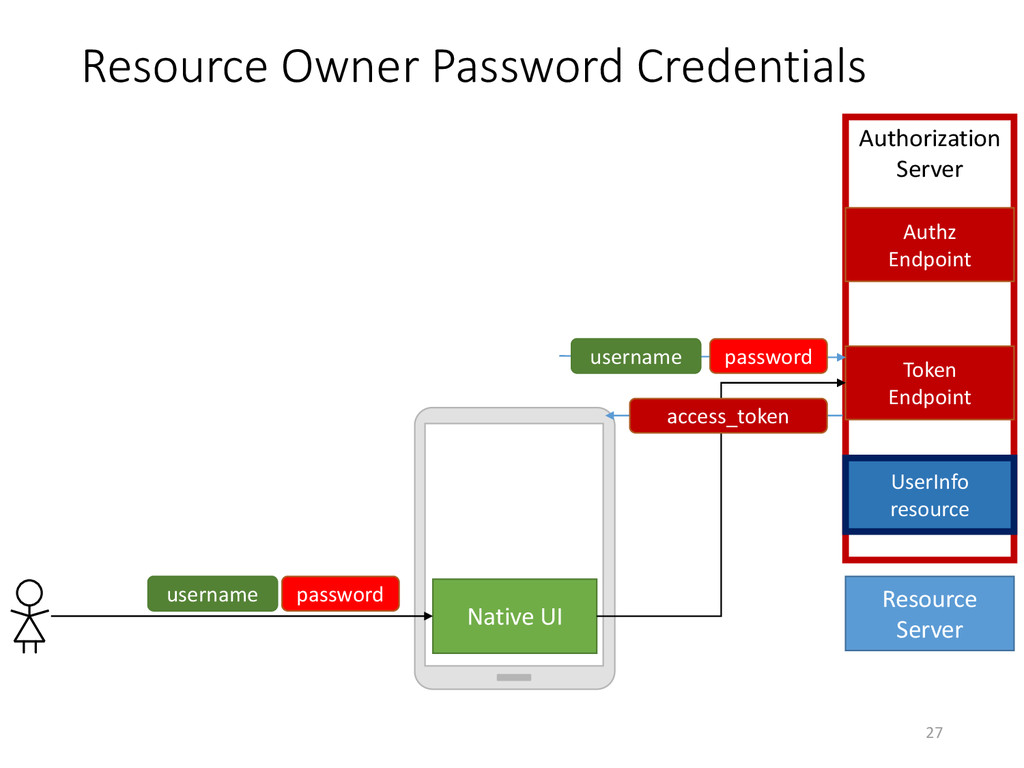
Resource Owner Password Credentials 27 Native UI Resource Server Authorization
Server Token Endpoint Authz Endpoint UserInfo resource password username access_token password username -
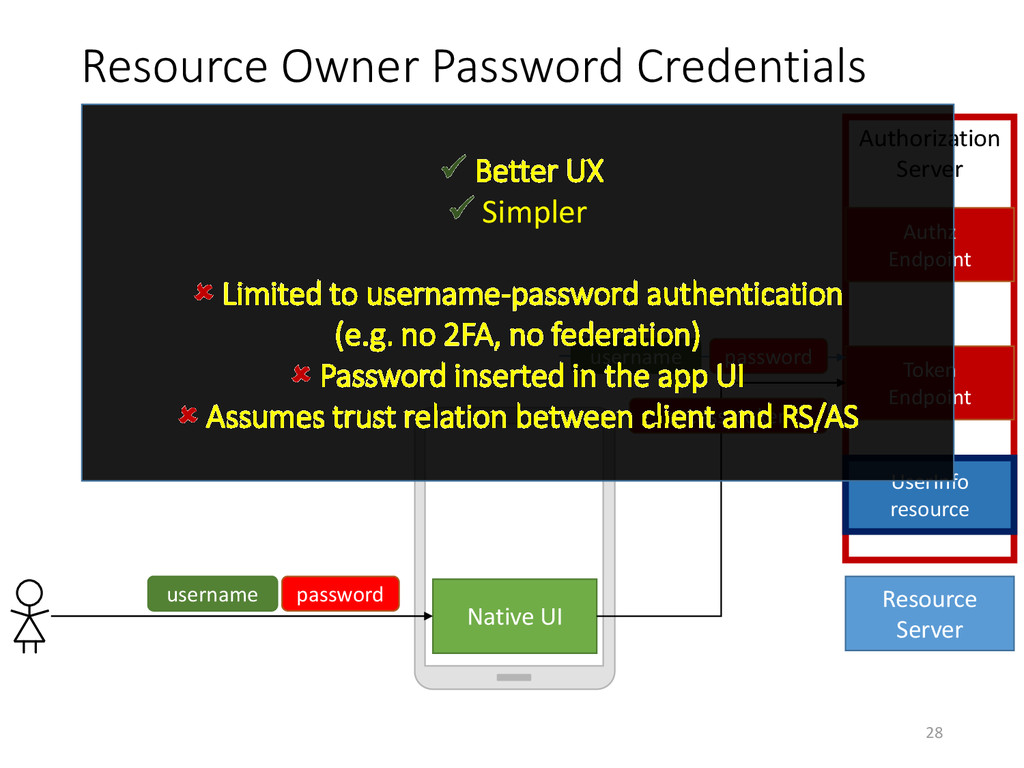
Resource Owner Password Credentials 28 Native UI Resource Server Authorization
Server Token Endpoint Authz Endpoint UserInfo resource password username access_token password username Better UX Simpler Limited to username-password authentication (e.g. no 2FA, no federation) Password inserted in the app UI Assumes trust relation between client and RS/AS -
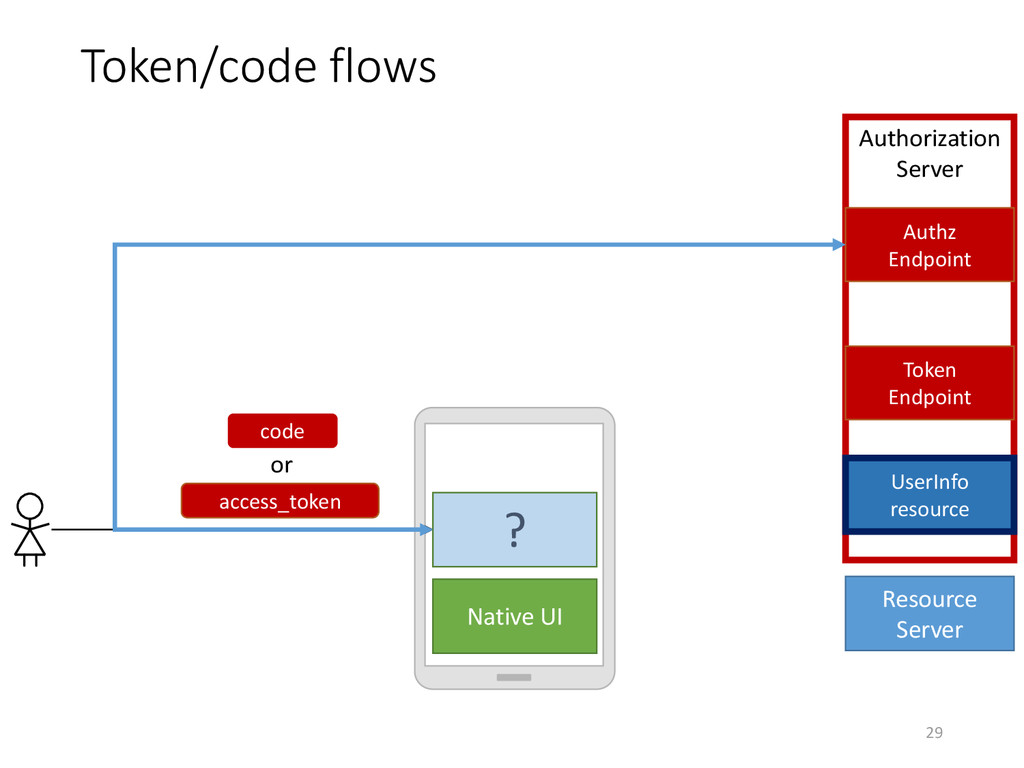
Token/code flows 29 Native UI Resource Server Authorization Server Token
Endpoint Authz Endpoint UserInfo resource ? code access_token or -
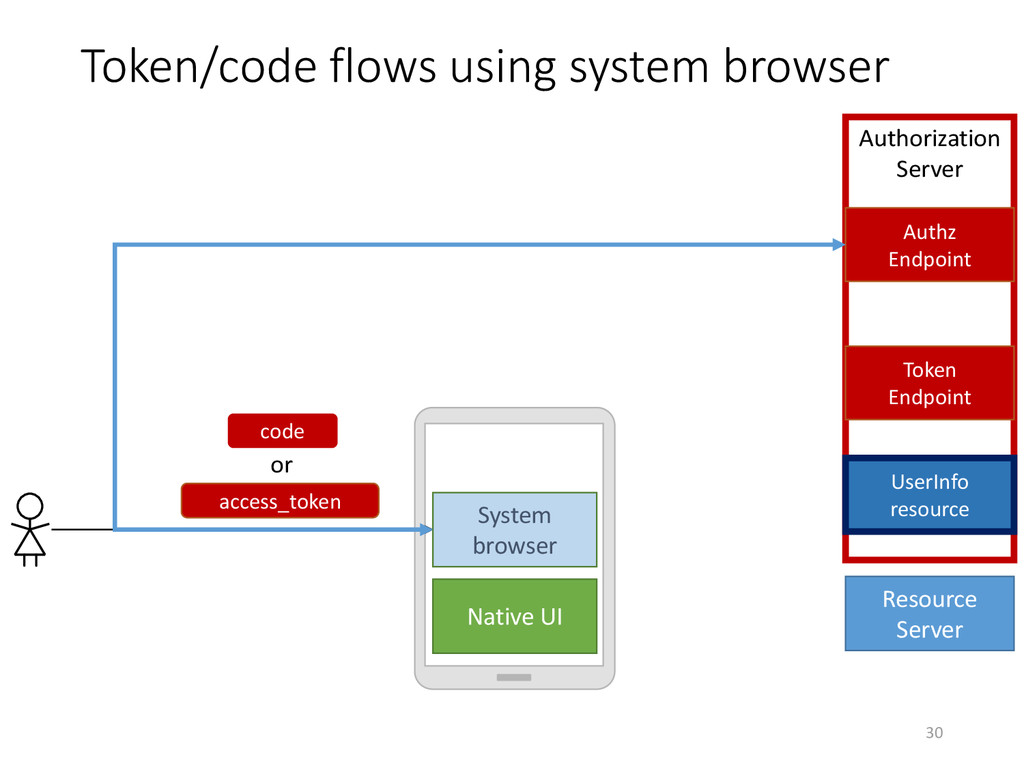
Token/code flows using system browser 30 Native UI Resource Server
Authorization Server Token Endpoint Authz Endpoint UserInfo resource System browser code access_token or -
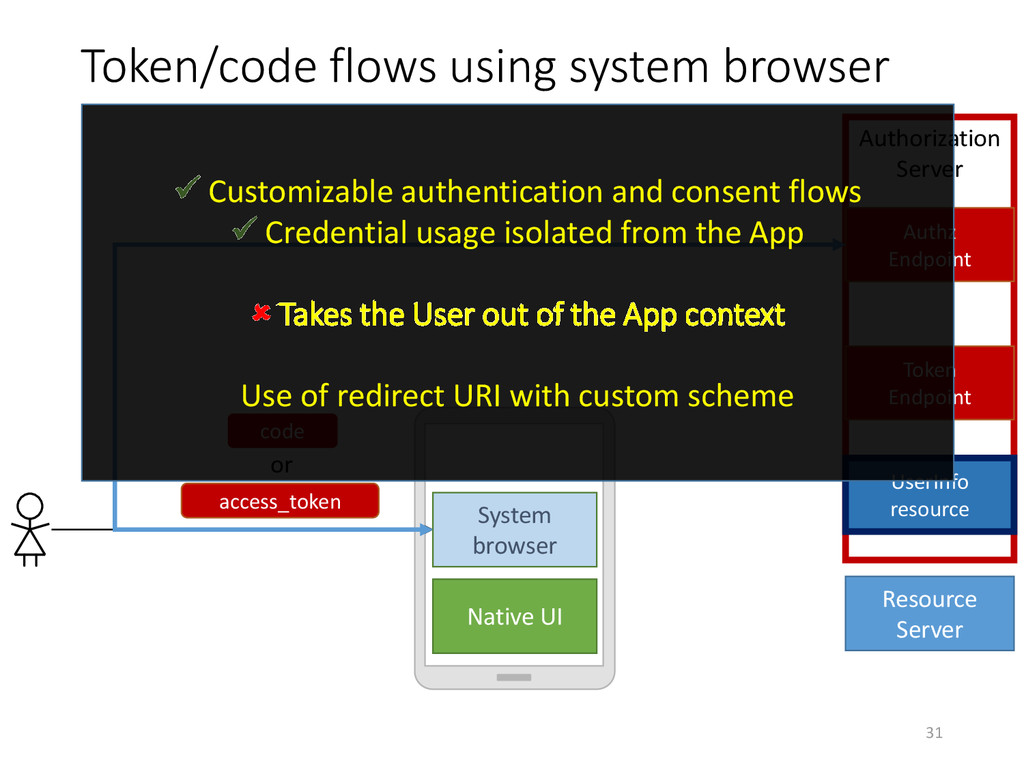
Token/code flows using system browser 31 Native UI Resource Server
Authorization Server Token Endpoint Authz Endpoint UserInfo resource System browser code access_token or Customizable authentication and consent flows Credential usage isolated from the App Takes the User out of the App context Use of redirect URI with custom scheme -
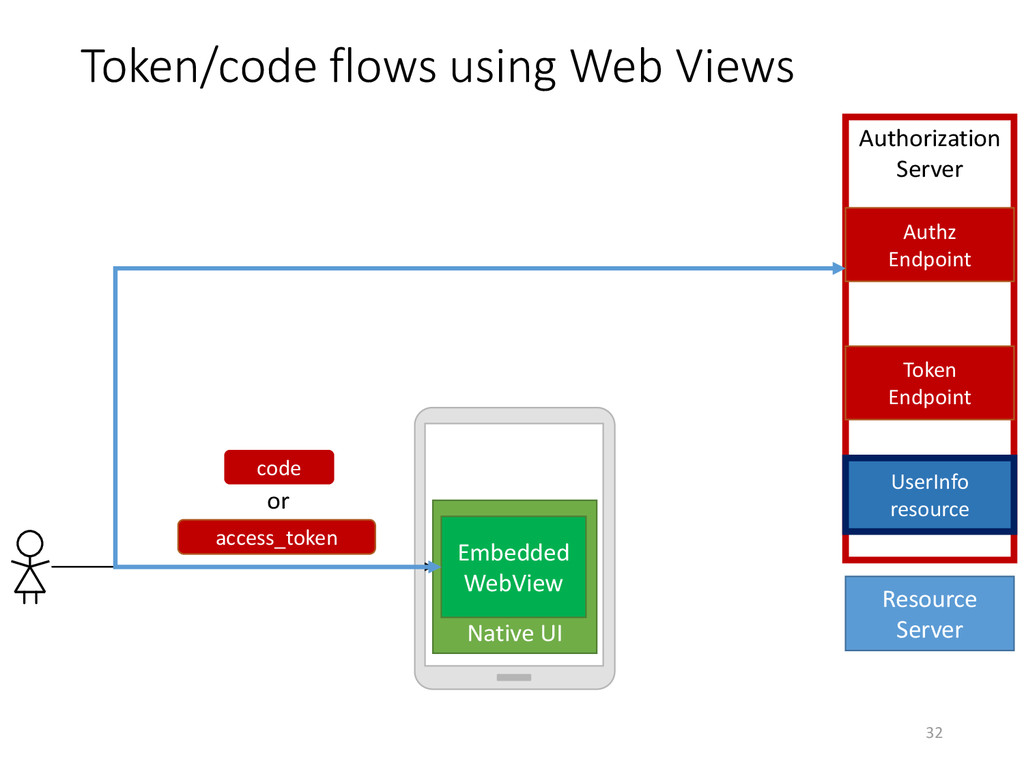
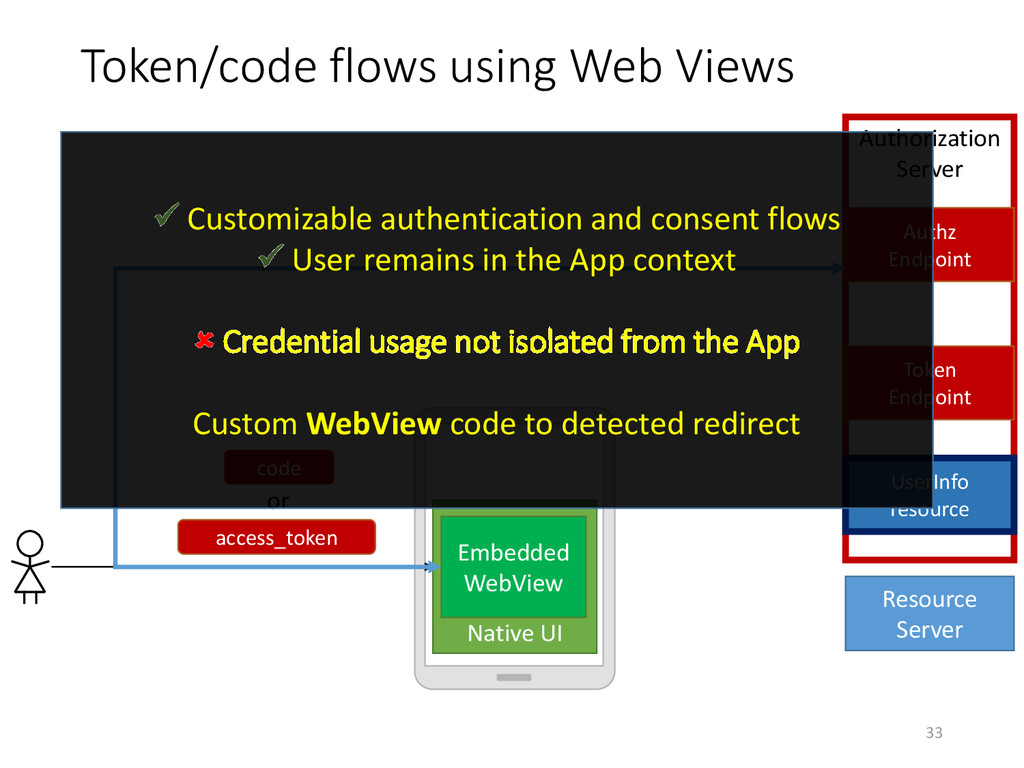
Token/code flows using Web Views 32 Native UI Resource Server
Authorization Server Token Endpoint Authz Endpoint UserInfo resource Embedded WebView code access_token or -
Token/code flows using Web Views 33 Native UI Resource Server
Authorization Server Token Endpoint Authz Endpoint UserInfo resource Embedded WebView code access_token or Customizable authentication and consent flows User remains in the App context Credential usage not isolated from the App Custom WebView code to detected redirect -
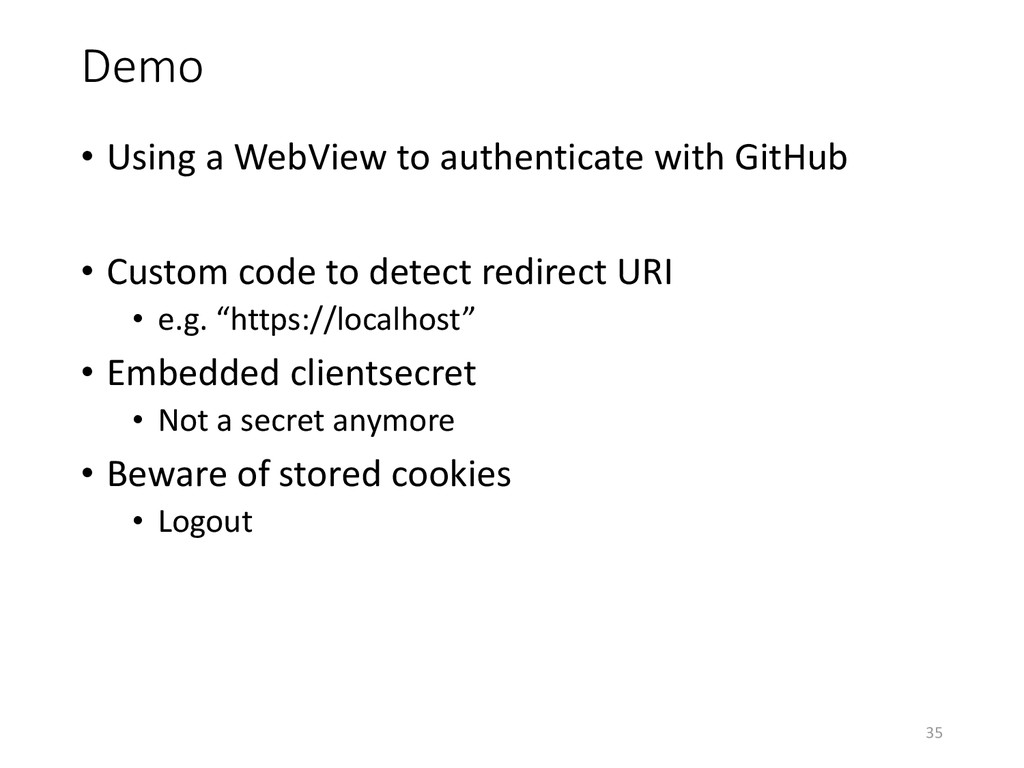
Demo • Using a WebView to authenticate with GitHub •
Custom code to detect redirect URI • e.g. “https://localhost” • Embedded clientsecret • Not a secret anymore • Beware of stored cookies • Logout 35 -
Multiple authentications • Multiple apps that require authentication • Imply
multiple authentication ceremonies • Can it be better? Can we have SSO for mobile apps? 36 -
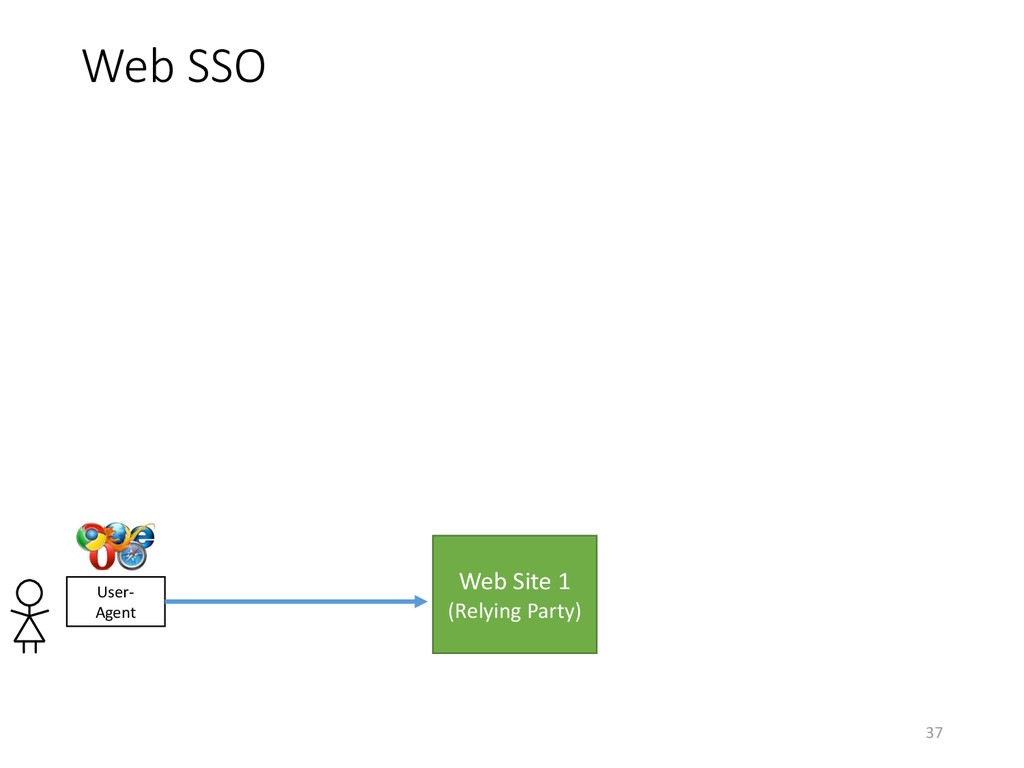
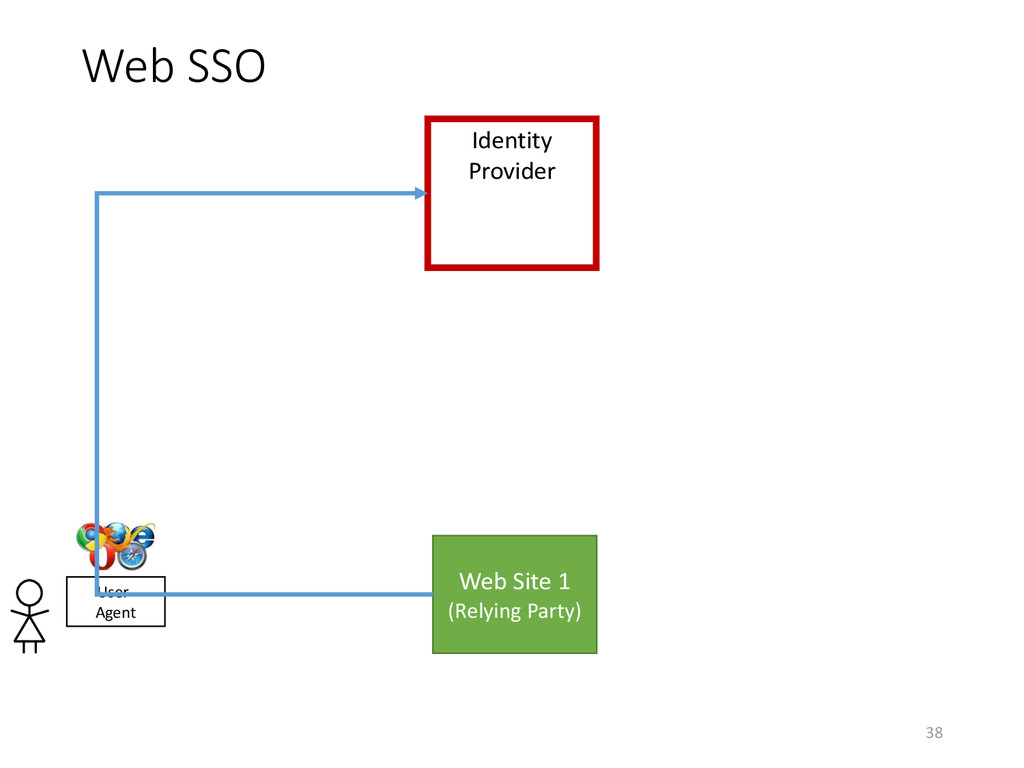
Web SSO 38 User- Agent Identity Provider Web Site 1
(Relying Party) -
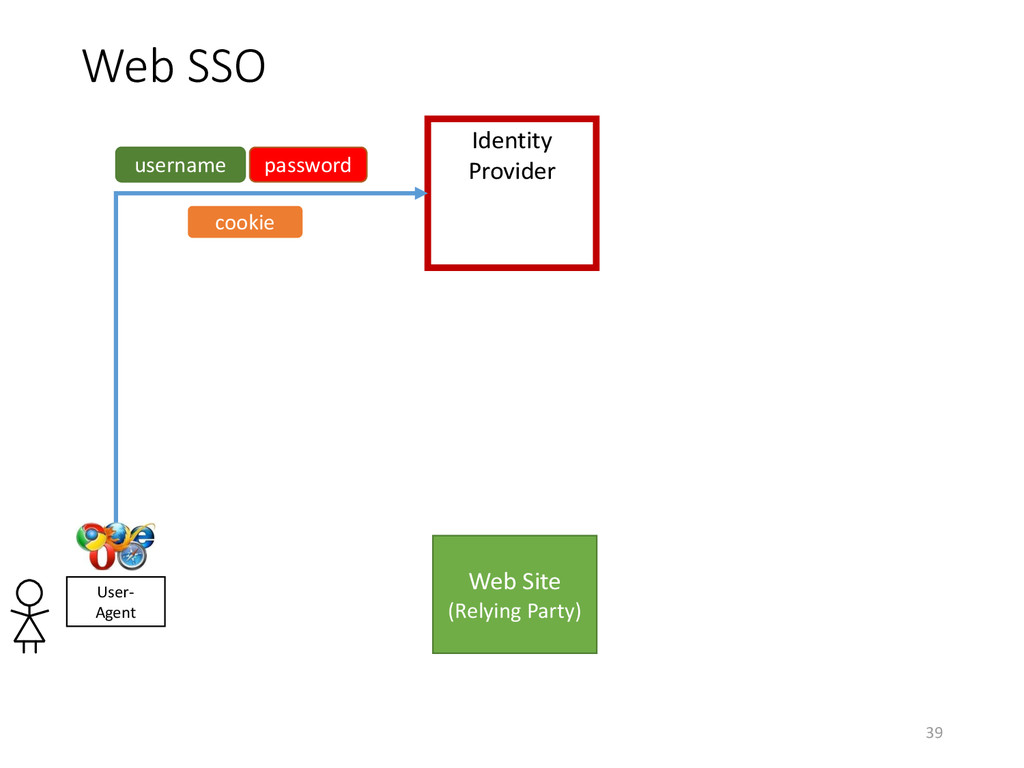
Web SSO 39 User- Agent Identity Provider Web Site (Relying
Party) password username cookie -
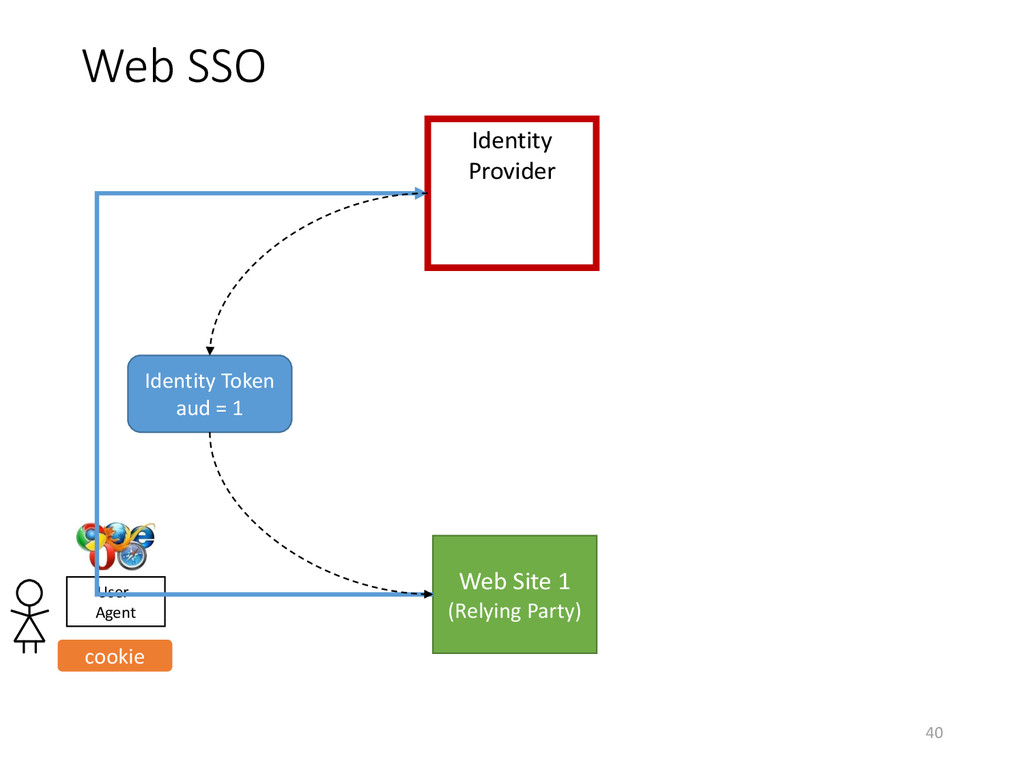
Web SSO 40 User- Agent Identity Provider Web Site 1
(Relying Party) Identity Token aud = 1 cookie -
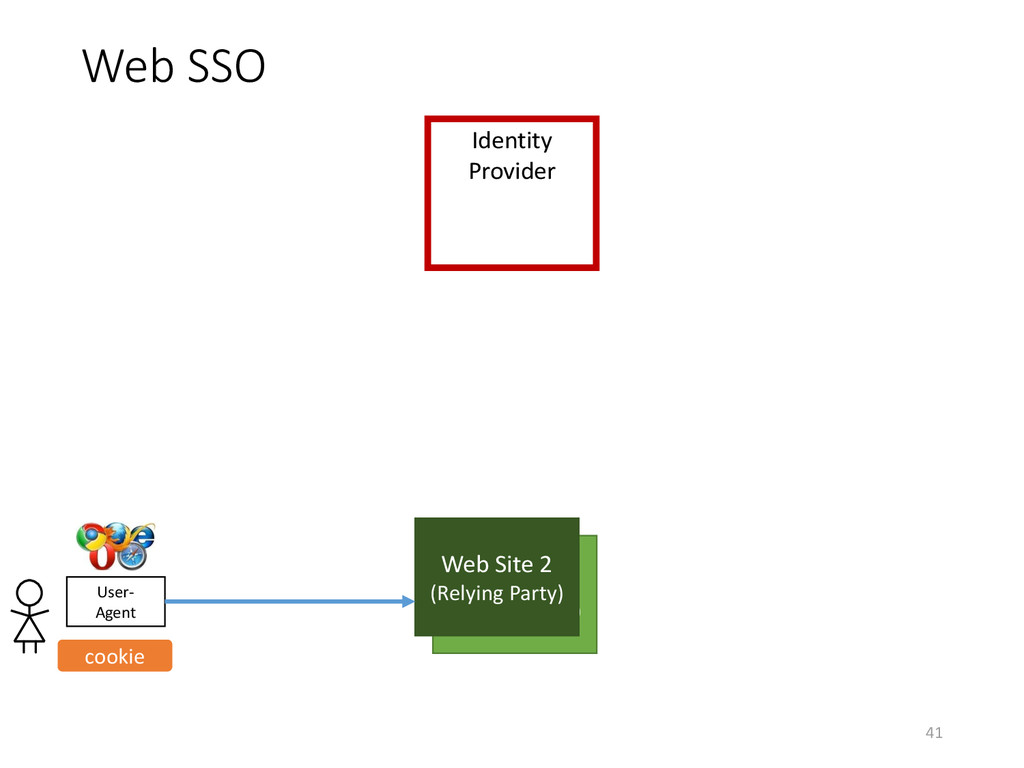
Web SSO 41 User- Agent Identity Provider Web Site (Relying
Party) cookie Web Site 2 (Relying Party) -
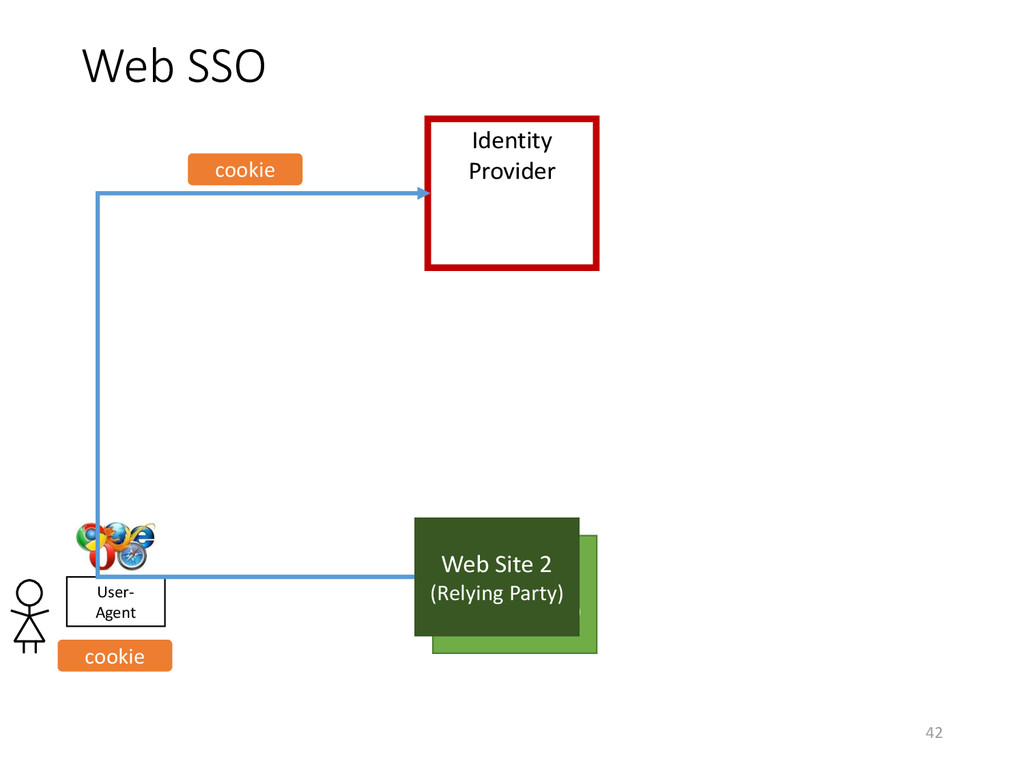
Web SSO 42 User- Agent Identity Provider Web Site (Relying
Party) cookie cookie Web Site 2 (Relying Party) -
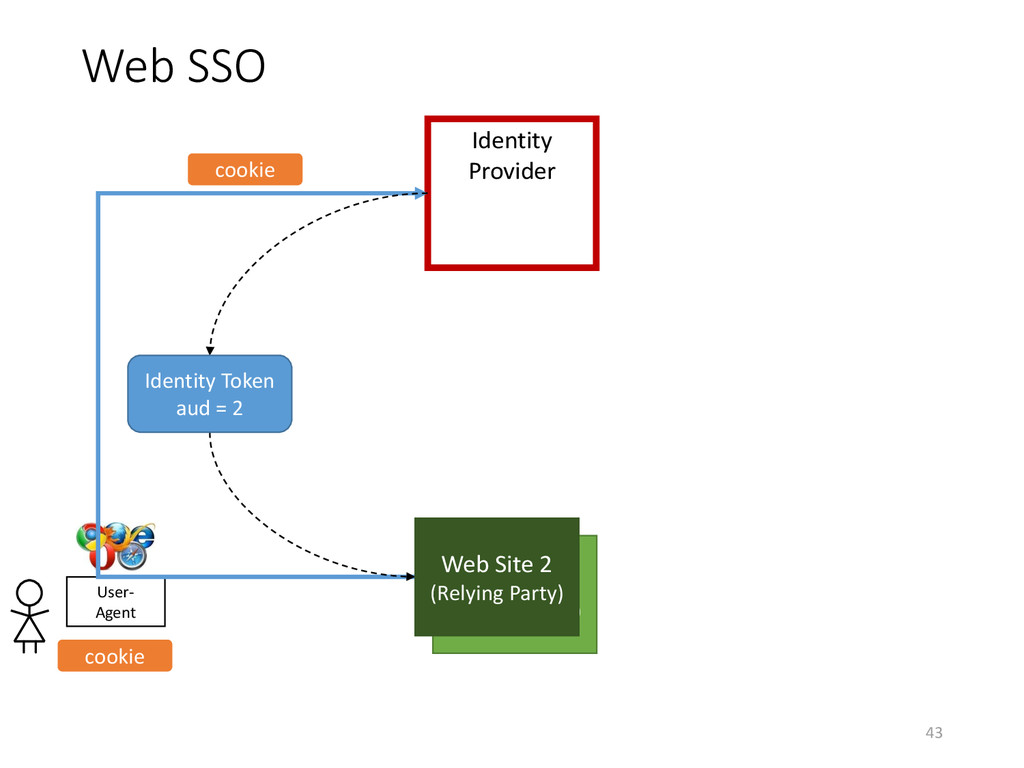
Web SSO 43 User- Agent Identity Provider Web Site (Relying
Party) cookie cookie Web Site 2 (Relying Party) Identity Token aud = 2 -
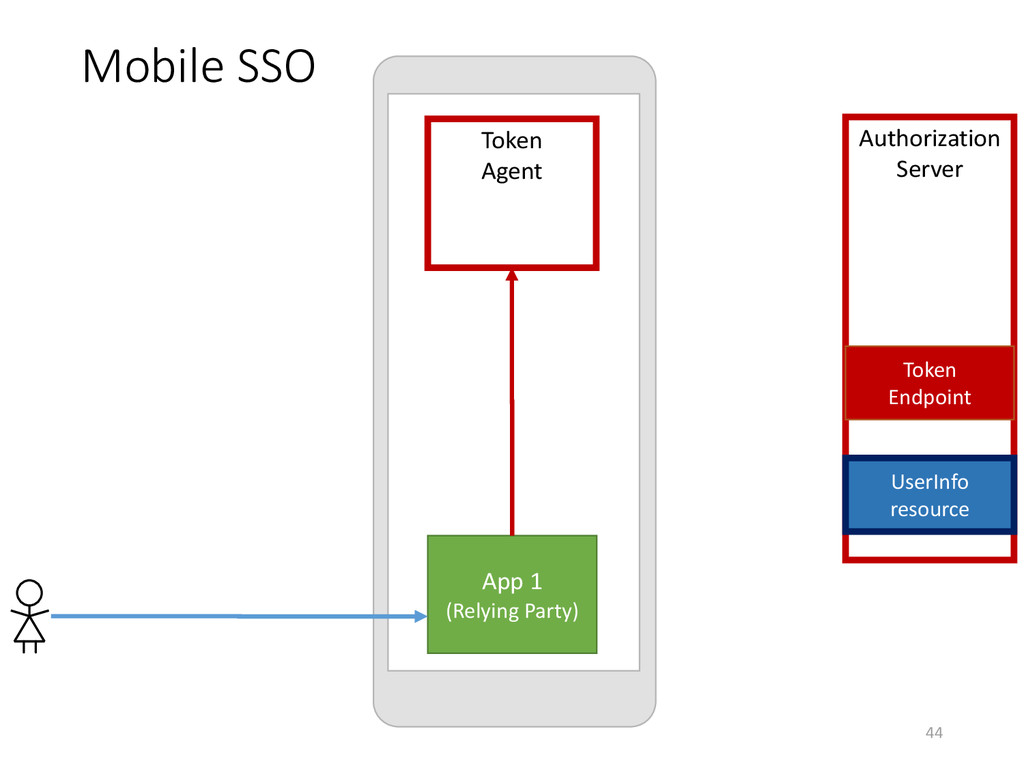
Mobile SSO 44 Token Agent App 1 (Relying Party) Authorization
Server Token Endpoint UserInfo resource -
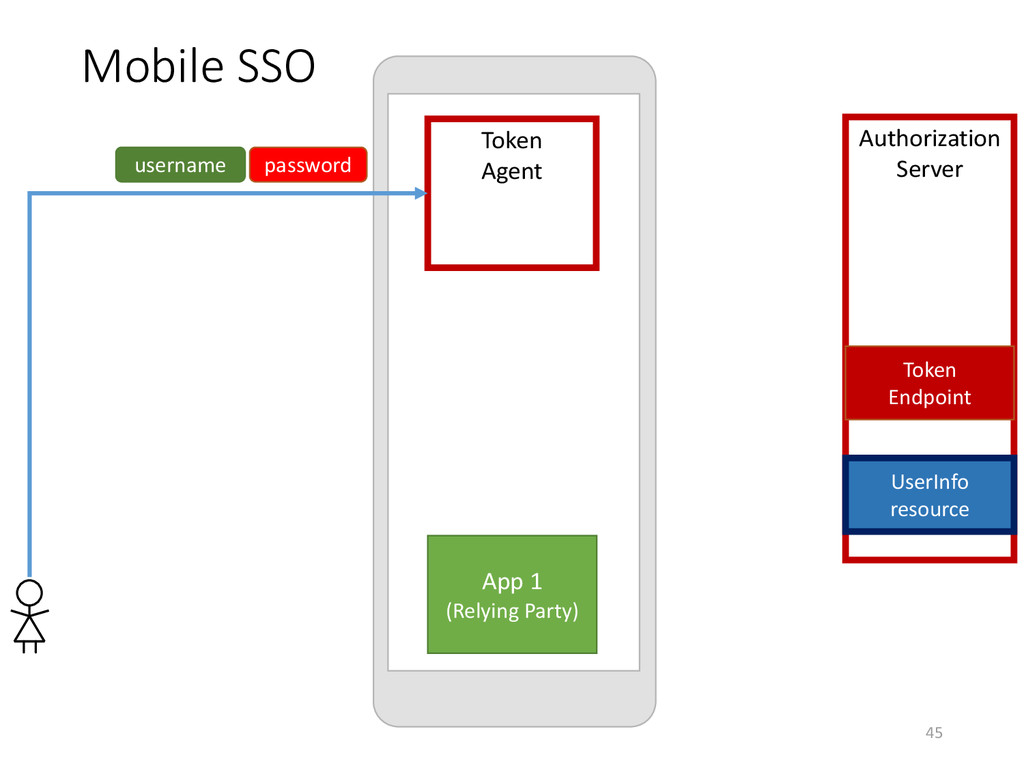
Mobile SSO 45 Token Agent App 1 (Relying Party) password
username Authorization Server Token Endpoint UserInfo resource -
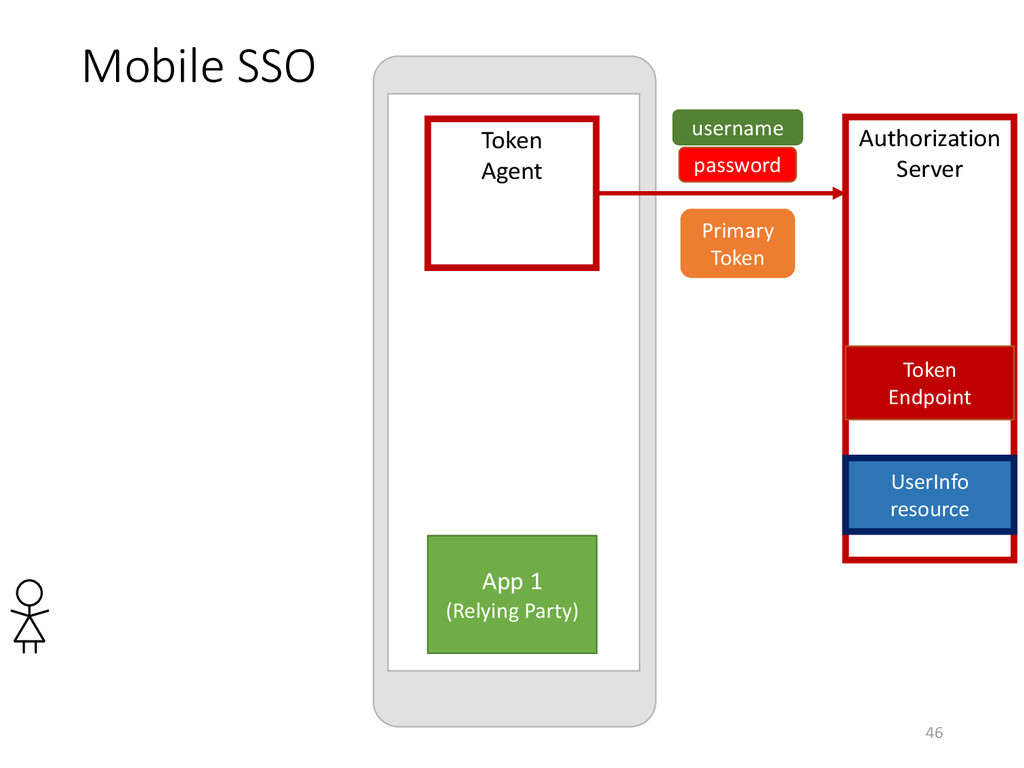
Mobile SSO 46 Token Agent App 1 (Relying Party) Authorization
Server Token Endpoint UserInfo resource password username Primary Token -
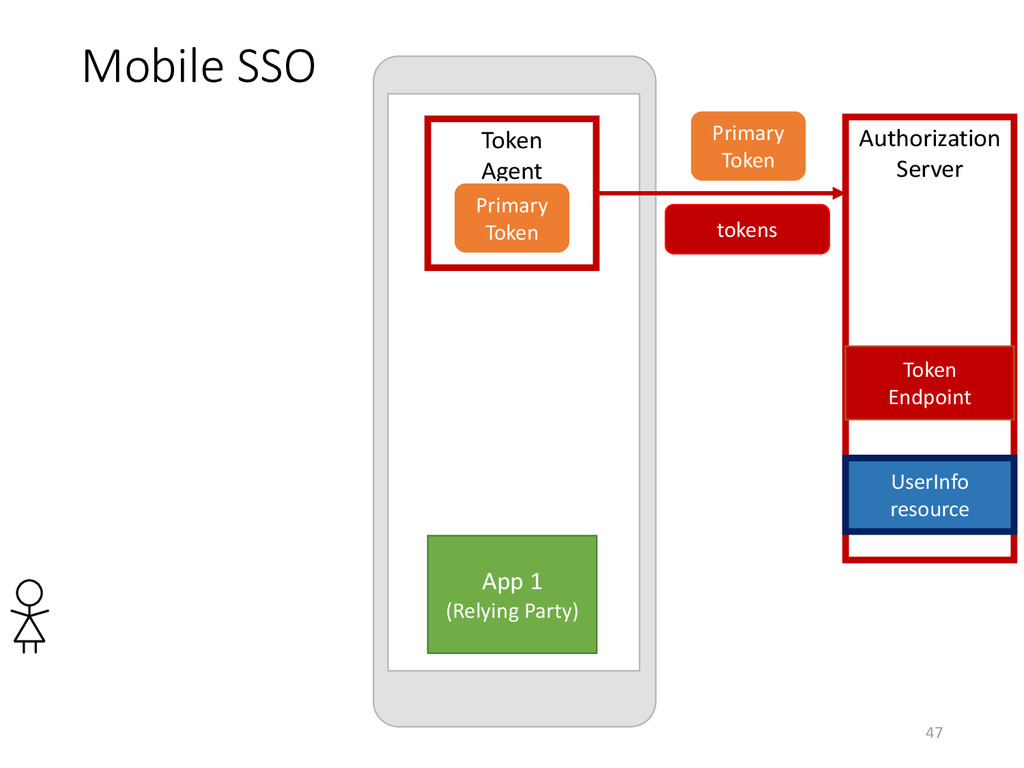
Mobile SSO 47 Token Agent App 1 (Relying Party) Authorization
Server Token Endpoint UserInfo resource Primary Token tokens Primary Token -
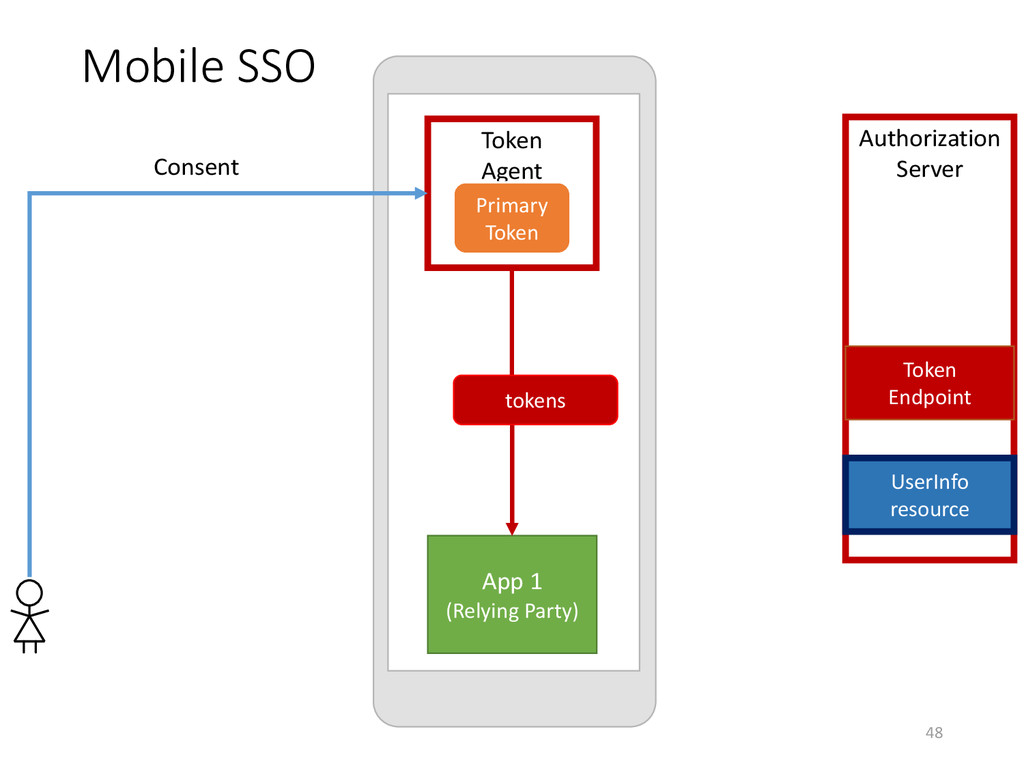
Mobile SSO 48 Token Agent App 1 (Relying Party) Authorization
Server Token Endpoint UserInfo resource Primary Token Consent tokens -
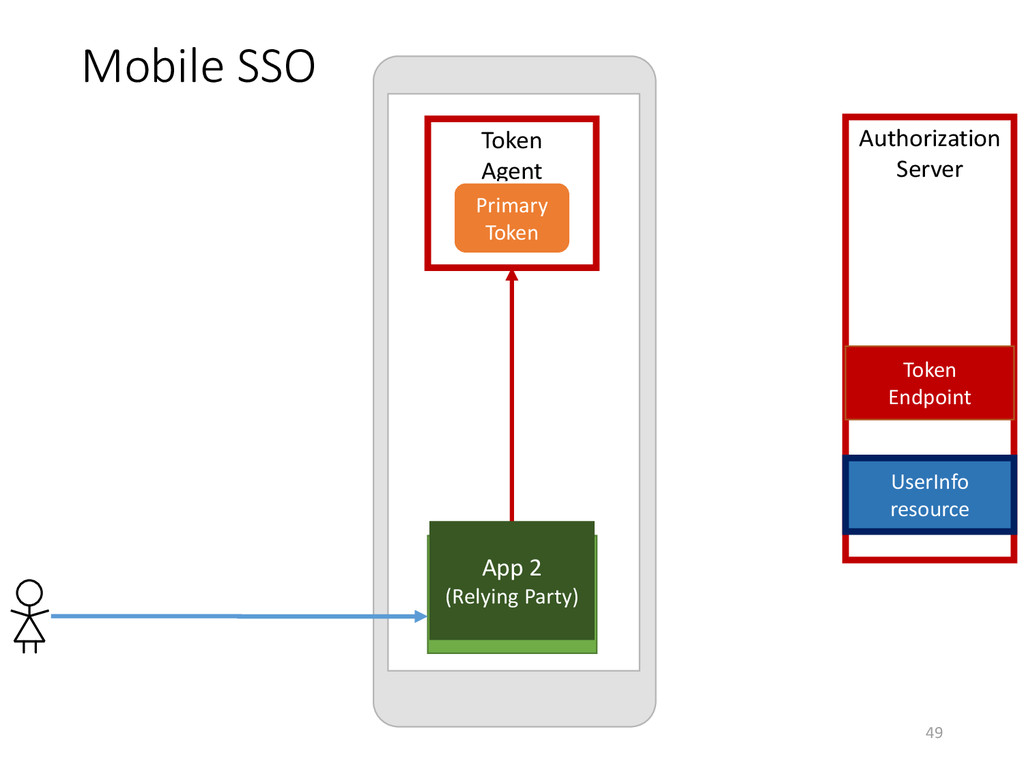
Mobile SSO 49 Token Agent Web Site (Relying Party) Authorization
Server Token Endpoint UserInfo resource Primary Token App 2 (Relying Party) -
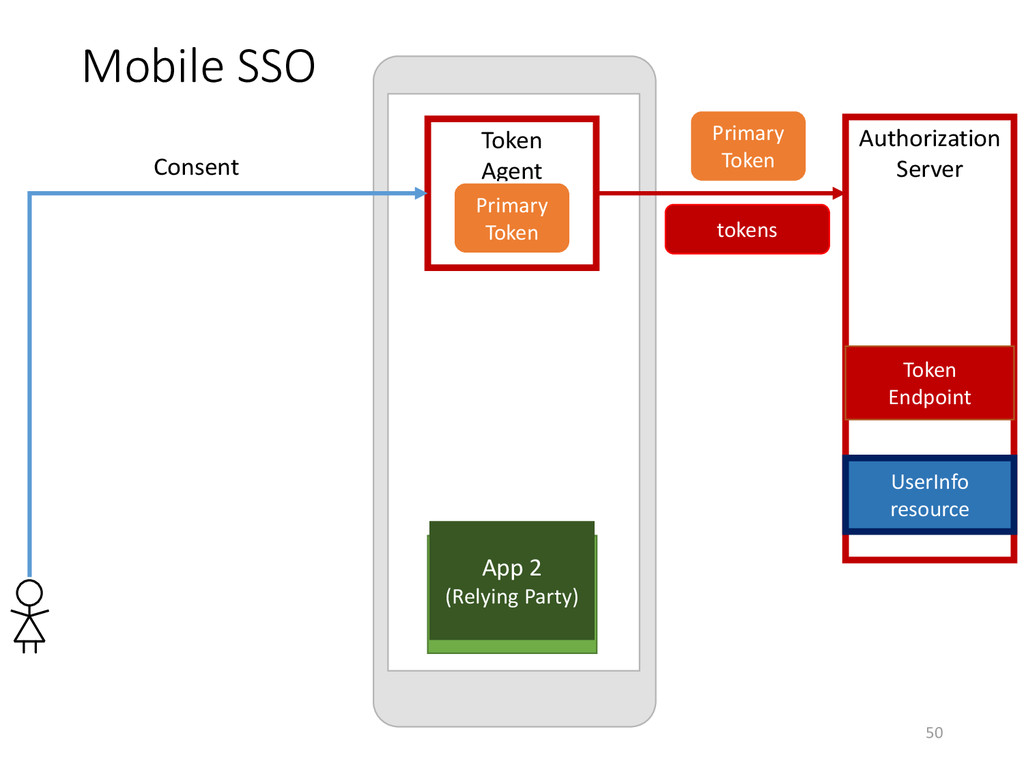
Mobile SSO 50 Token Agent Web Site (Relying Party) Authorization
Server Token Endpoint UserInfo resource Primary Token Primary Token App 2 (Relying Party) tokens Consent -
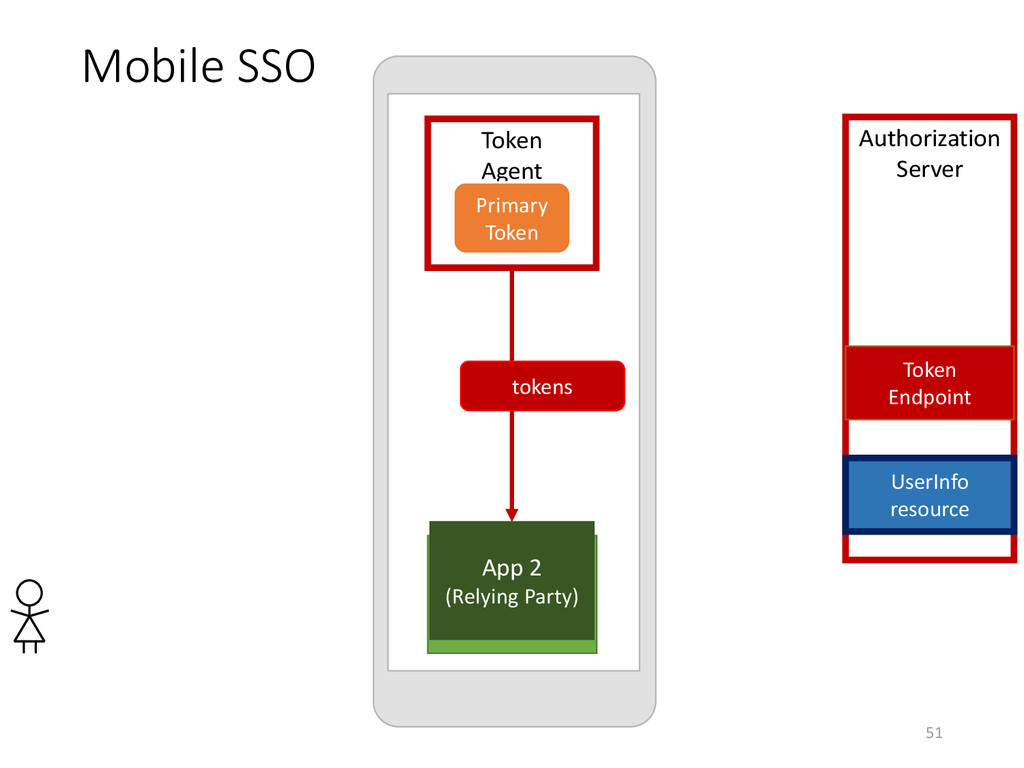
Mobile SSO 51 Token Agent App 1 (Relying Party) Authorization
Server Token Endpoint UserInfo resource Primary Token App 2 (Relying Party) tokens -
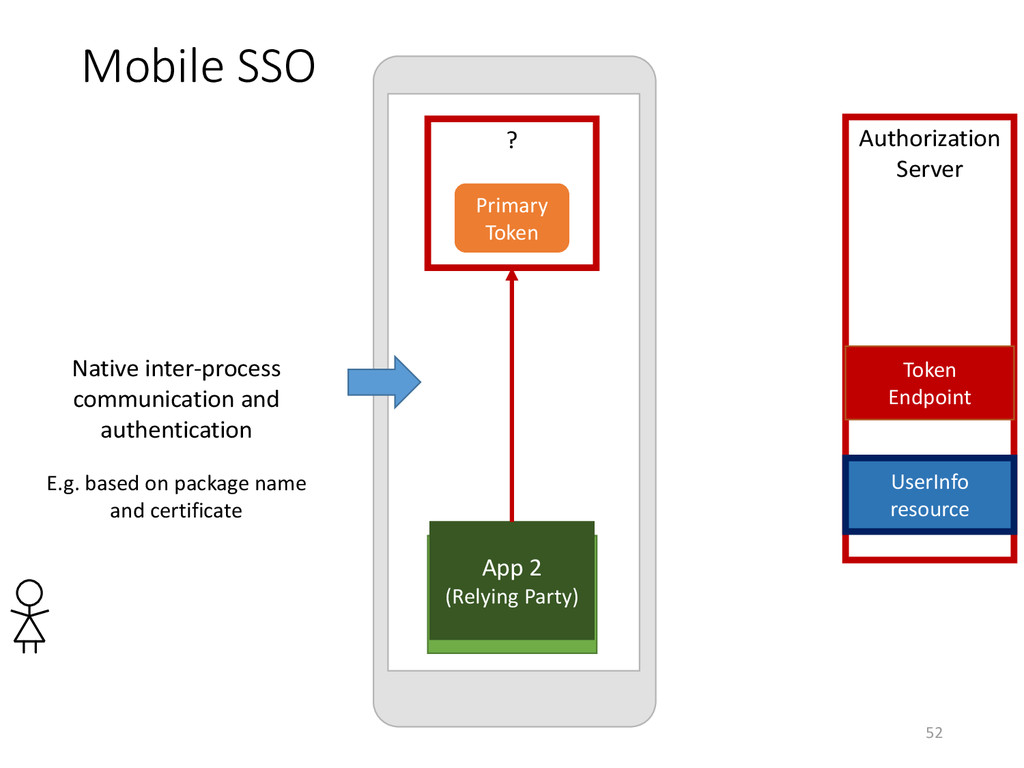
Mobile SSO 52 ? App 1 (Relying Party) Authorization Server
Token Endpoint UserInfo resource Primary Token App 2 (Relying Party) Native inter-process communication and authentication E.g. based on package name and certificate -
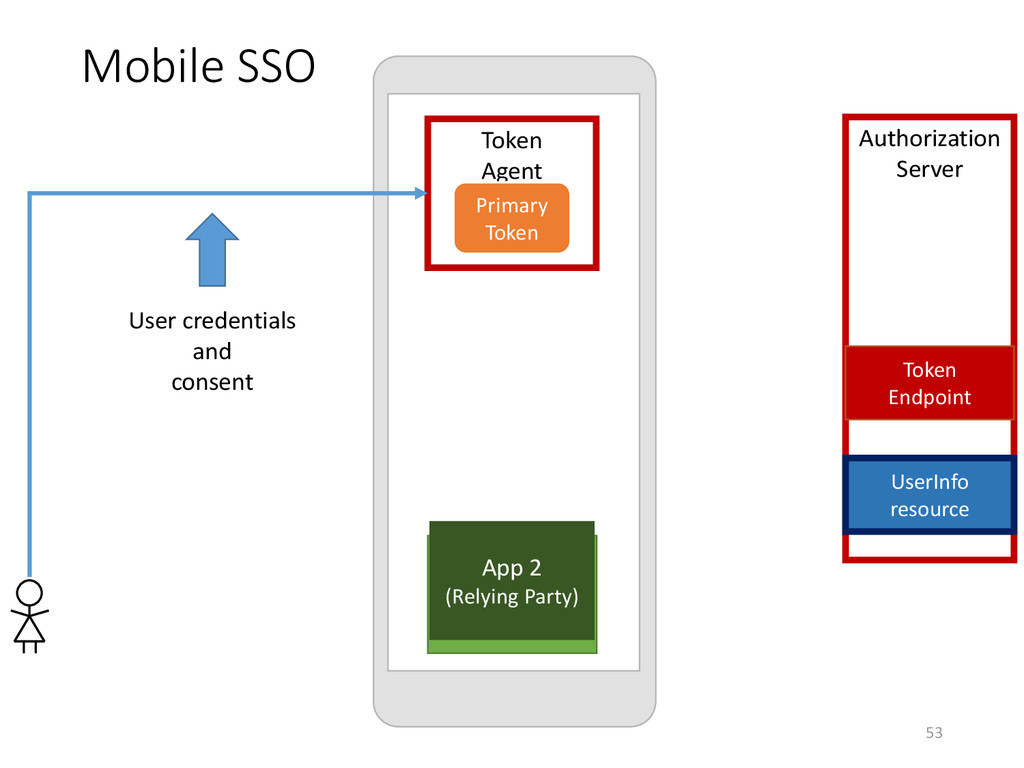
Mobile SSO 53 Token Agent App 1 (Relying Party) Authorization
Server Token Endpoint UserInfo resource Primary Token App 2 (Relying Party) User credentials and consent -
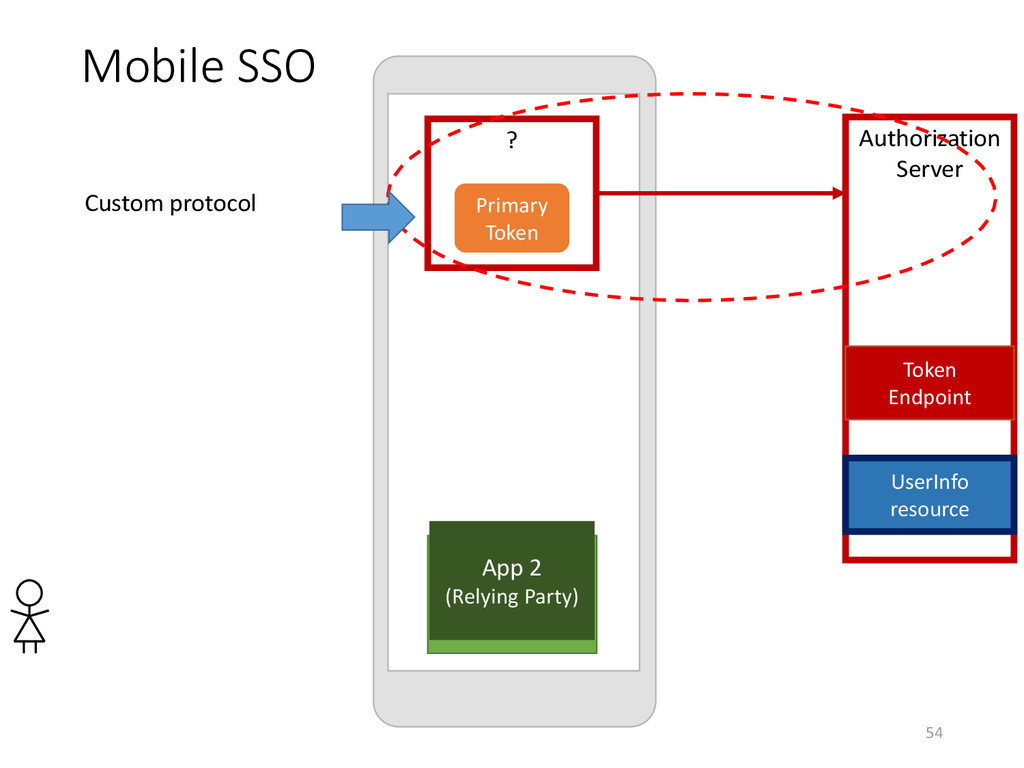
Mobile SSO 54 ? App 1 (Relying Party) Authorization Server
Token Endpoint UserInfo resource Primary Token App 2 (Relying Party) Custom protocol -
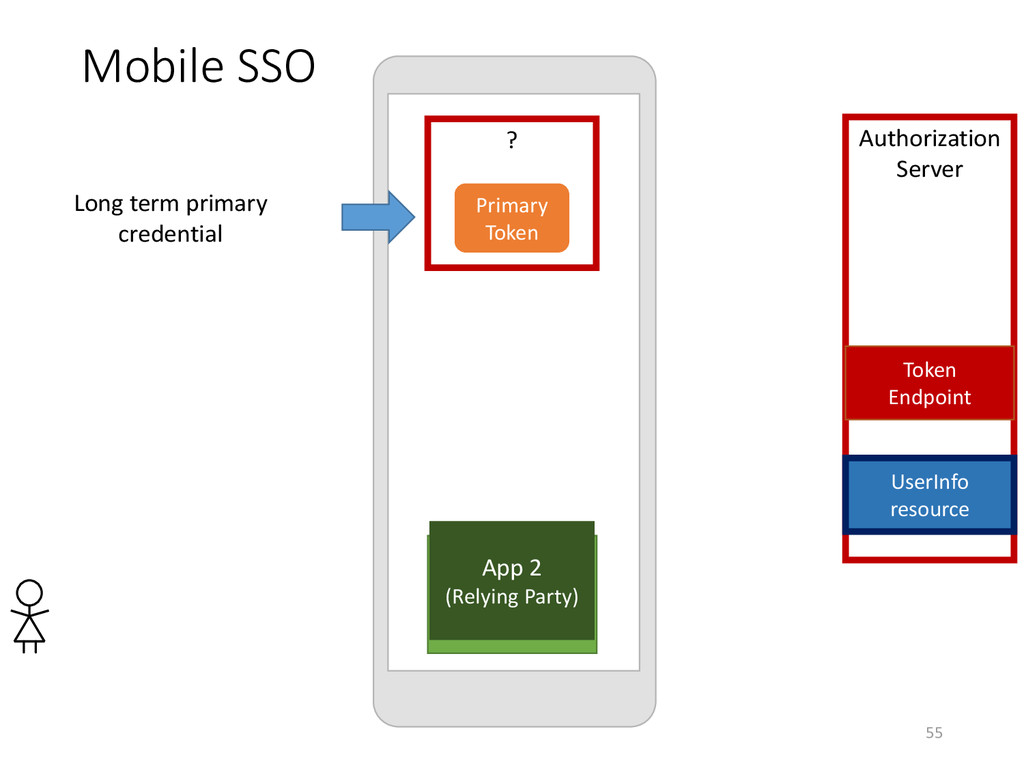
Mobile SSO 55 ? App 1 (Relying Party) Authorization Server
Token Endpoint UserInfo resource Primary Token App 2 (Relying Party) Long term primary credential -
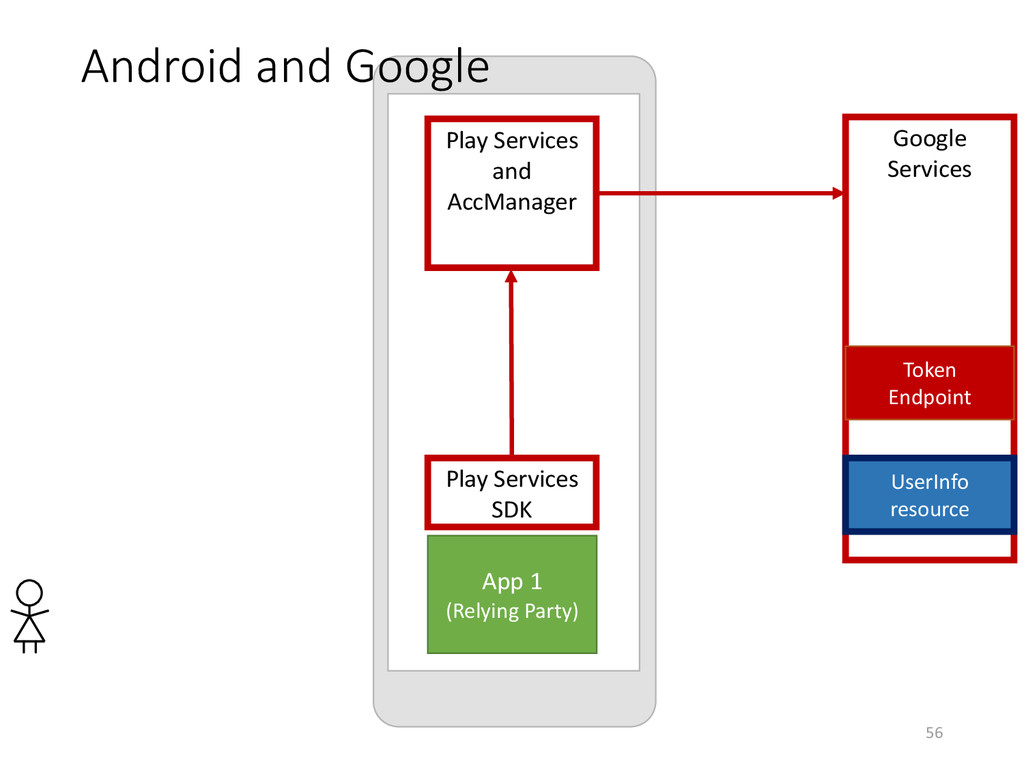
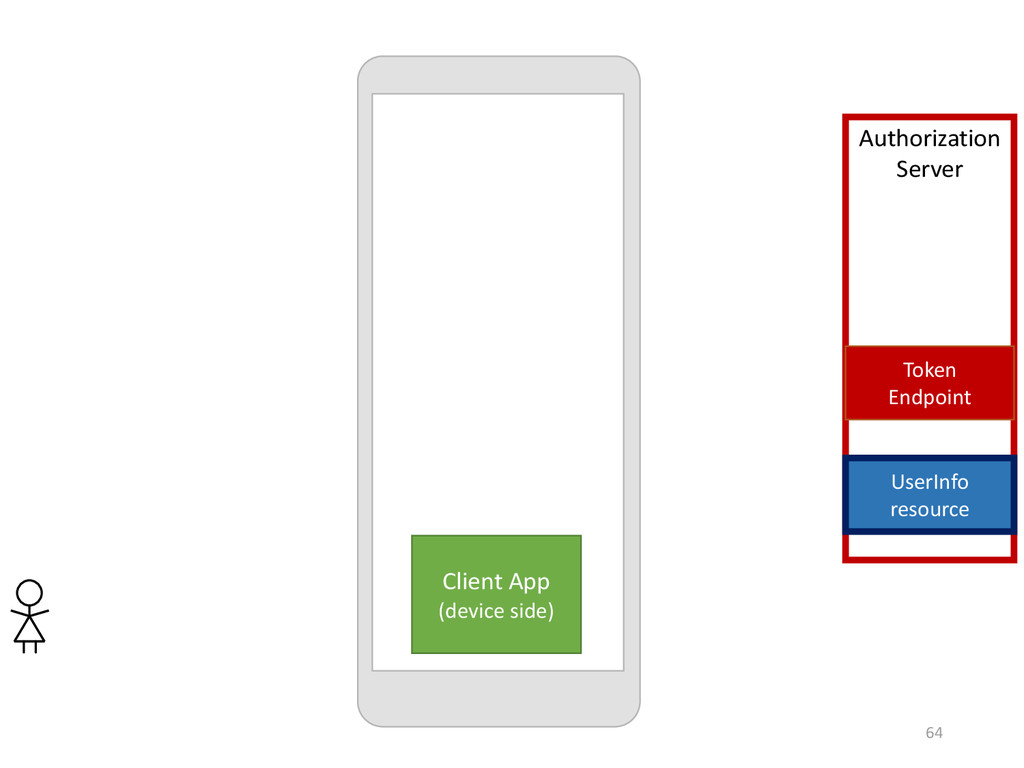
56 Play Services and AccManager App 1 (Relying Party) Google
Services Token Endpoint UserInfo resource Android and Google Play Services SDK -
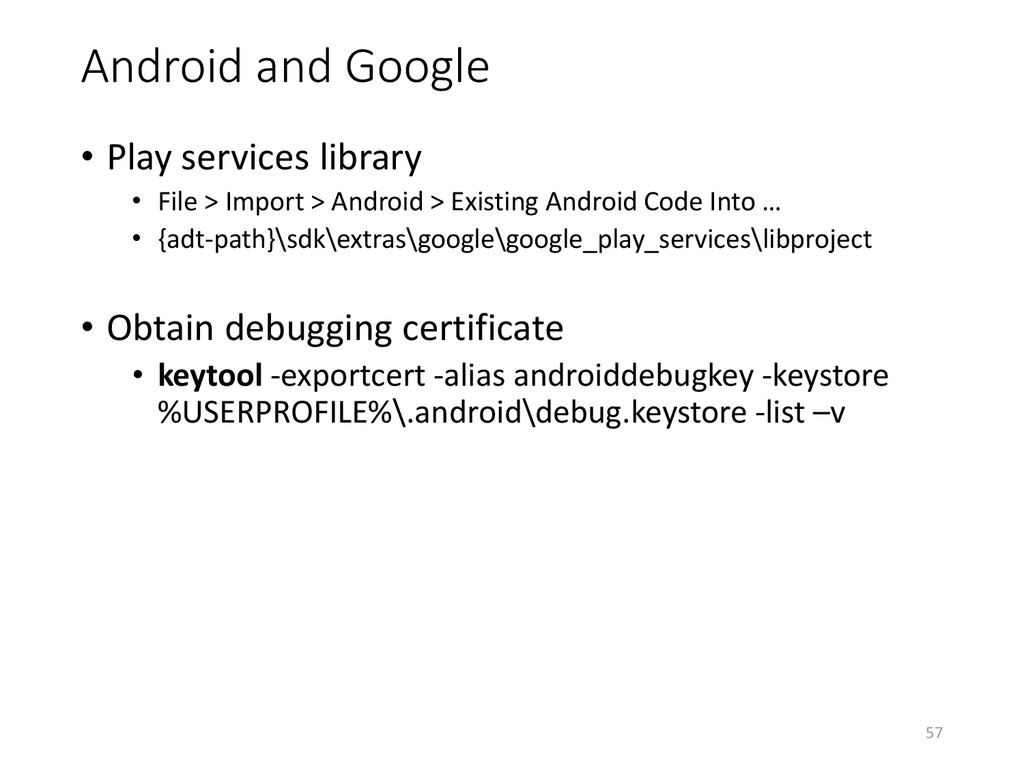
Android and Google • Play services library • File >
Import > Android > Existing Android Code Into … • {adt-path}\sdk\extras\google\google_play_services\libproject • Obtain debugging certificate • keytool -exportcert -alias androiddebugkey -keystore %USERPROFILE%\.android\debug.keystore -list –v 57 -
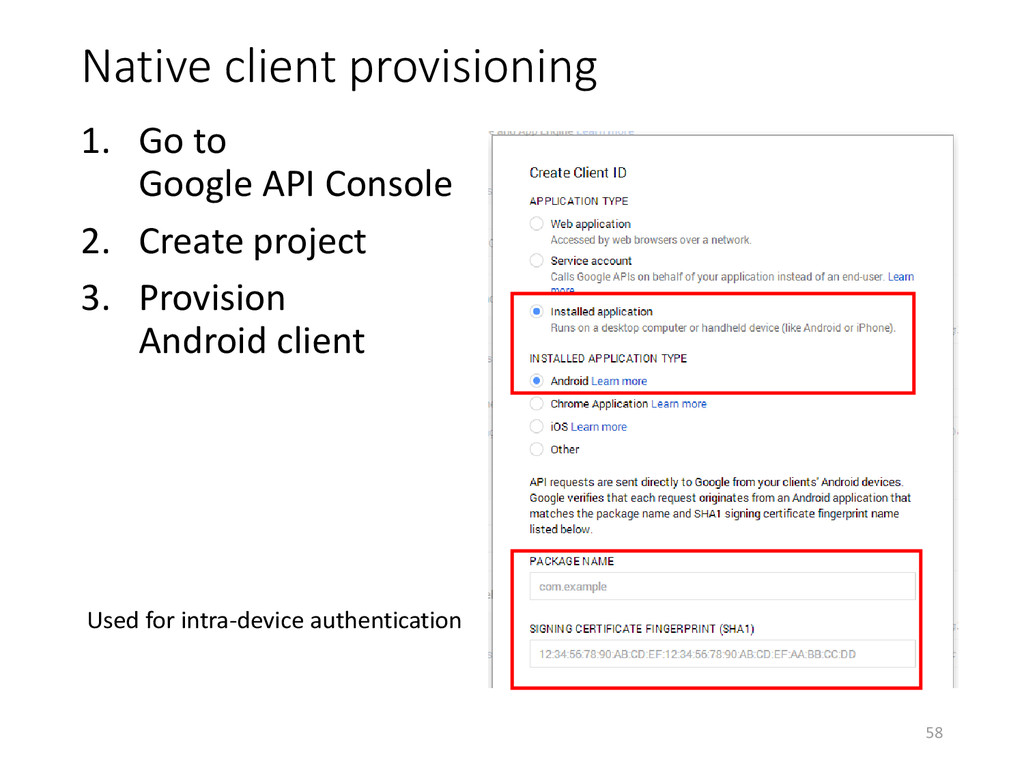
Native client provisioning 1. Go to Google API Console 2.
Create project 3. Provision Android client 58 Used for intra-device authentication -
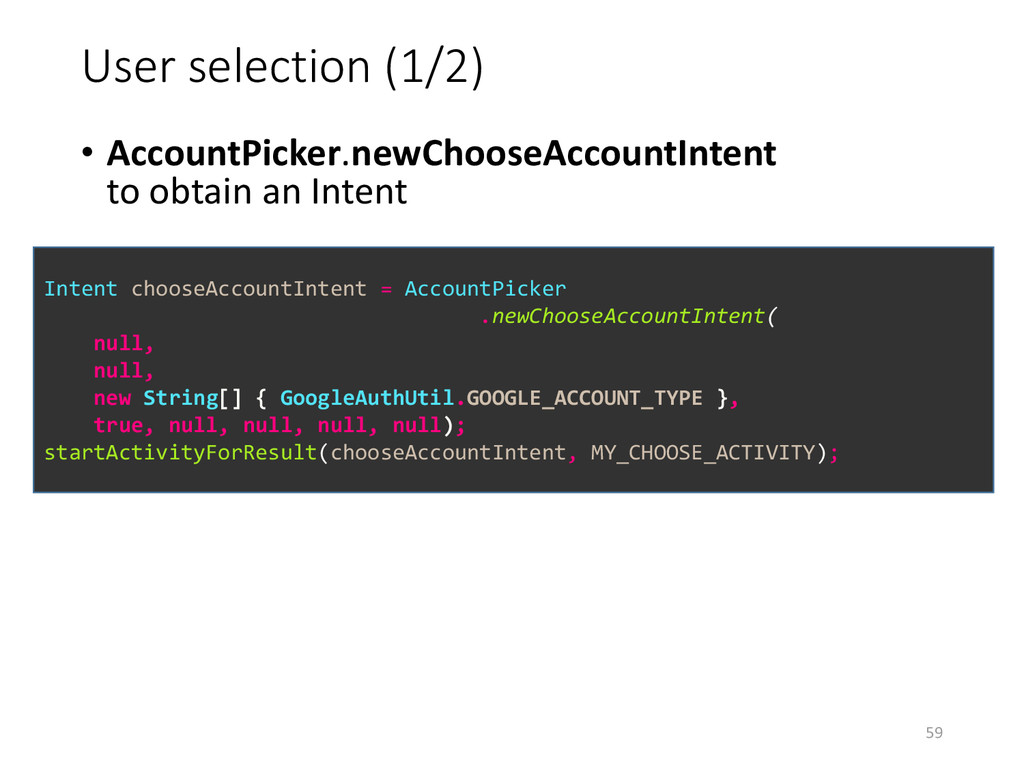
User selection (1/2) • AccountPicker.newChooseAccountIntent to obtain an Intent 59
Intent chooseAccountIntent = AccountPicker .newChooseAccountIntent( null, null, new String[] { GoogleAuthUtil.GOOGLE_ACCOUNT_TYPE }, true, null, null, null, null); startActivityForResult(chooseAccountIntent, MY_CHOOSE_ACTIVITY); -
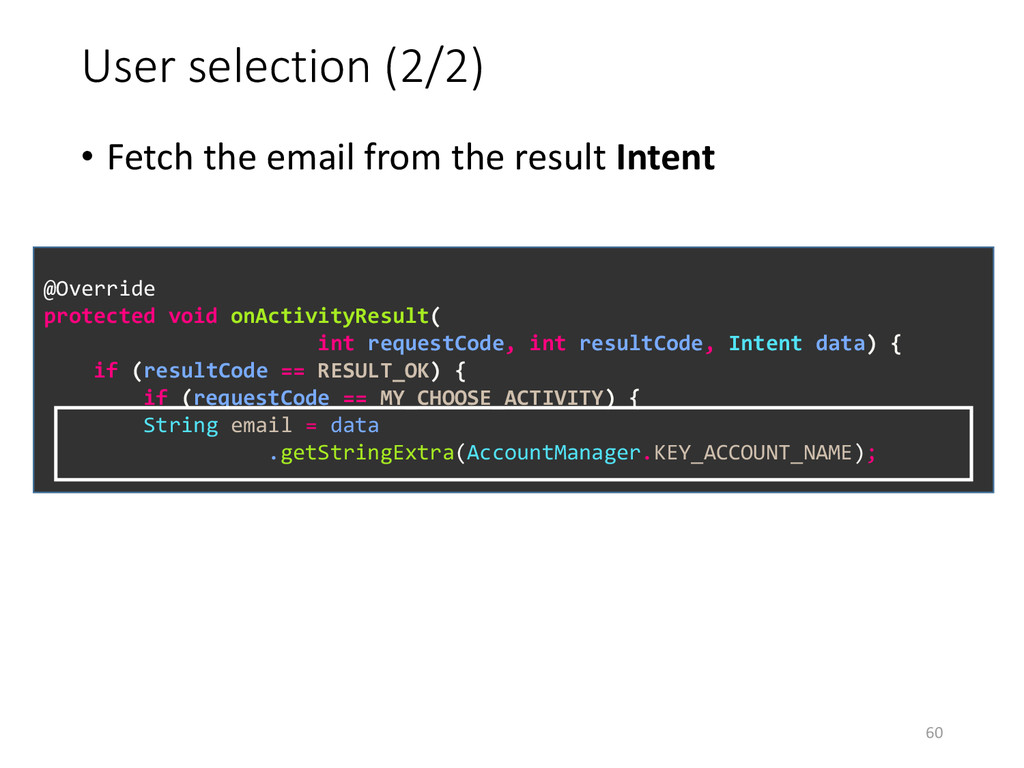
User selection (2/2) • Fetch the email from the result
Intent 60 @Override protected void onActivityResult( int requestCode, int resultCode, Intent data) { if (resultCode == RESULT_OK) { if (requestCode == MY_CHOOSE_ACTIVITY) { String email = data .getStringExtra(AccountManager.KEY_ACCOUNT_NAME); -
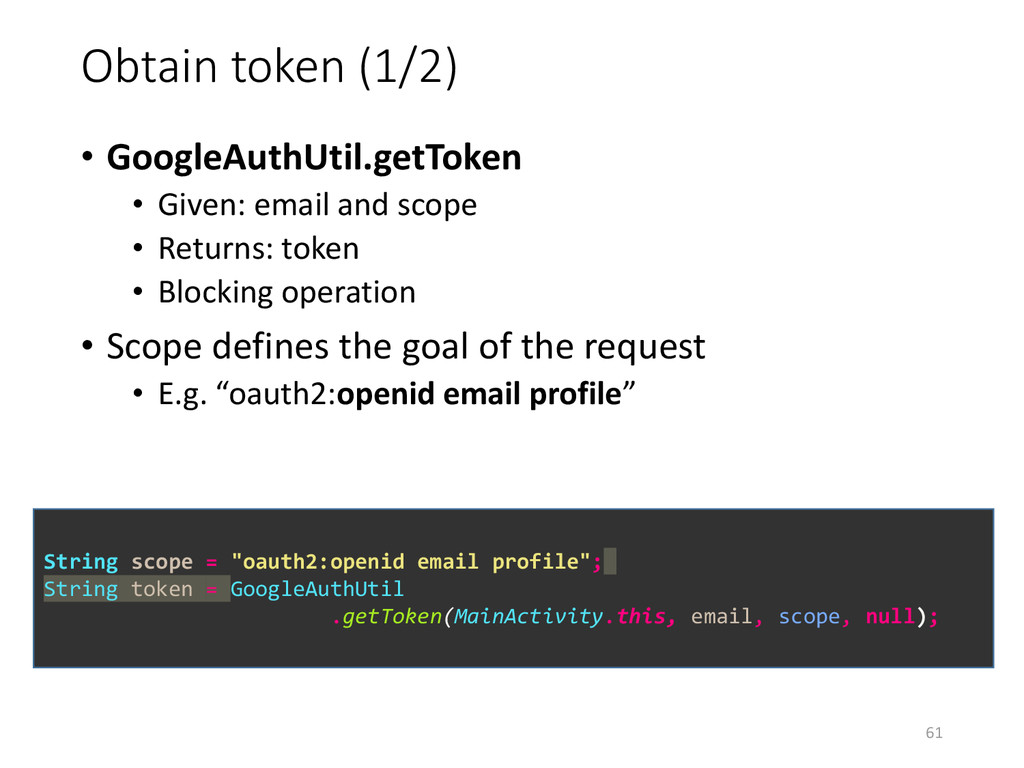
Obtain token (1/2) • GoogleAuthUtil.getToken • Given: email and scope
• Returns: token • Blocking operation • Scope defines the goal of the request • E.g. “oauth2:openid email profile” 61 String scope = "oauth2:openid email profile"; String token = GoogleAuthUtil .getToken(MainActivity.this, email, scope, null); -
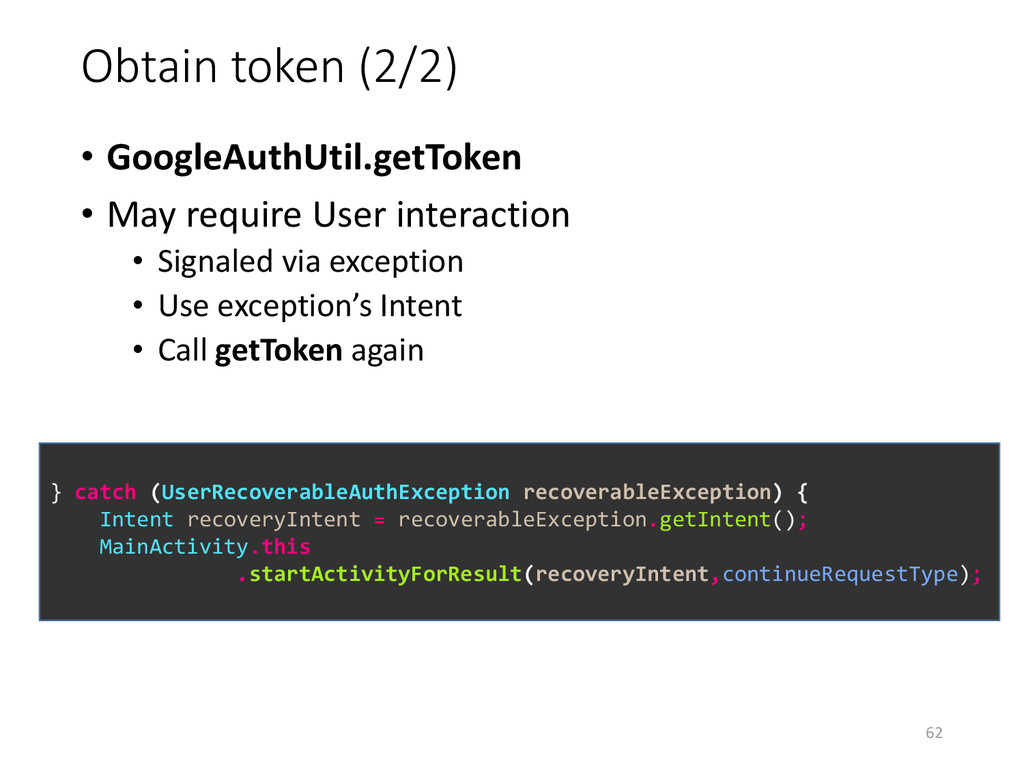
Obtain token (2/2) • GoogleAuthUtil.getToken • May require User interaction
• Signaled via exception • Use exception’s Intent • Call getToken again 62 } catch (UserRecoverableAuthException recoverableException) { Intent recoveryIntent = recoverableException.getIntent(); MainActivity.this .startActivityForResult(recoveryIntent,continueRequestType); -
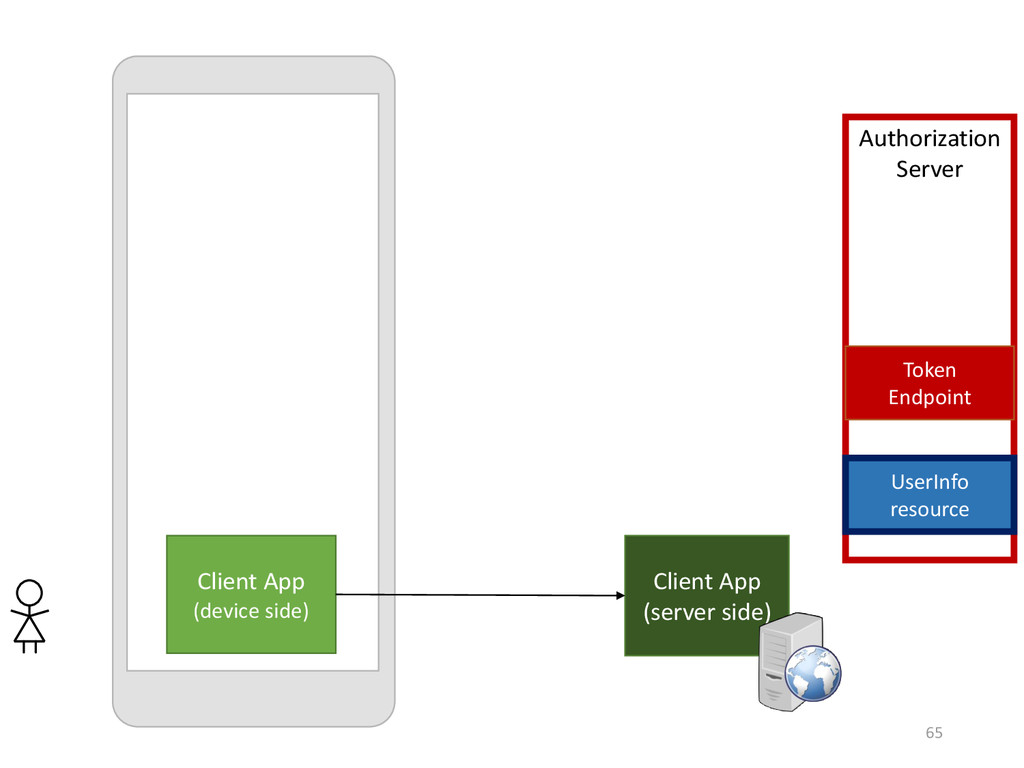
65 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) -
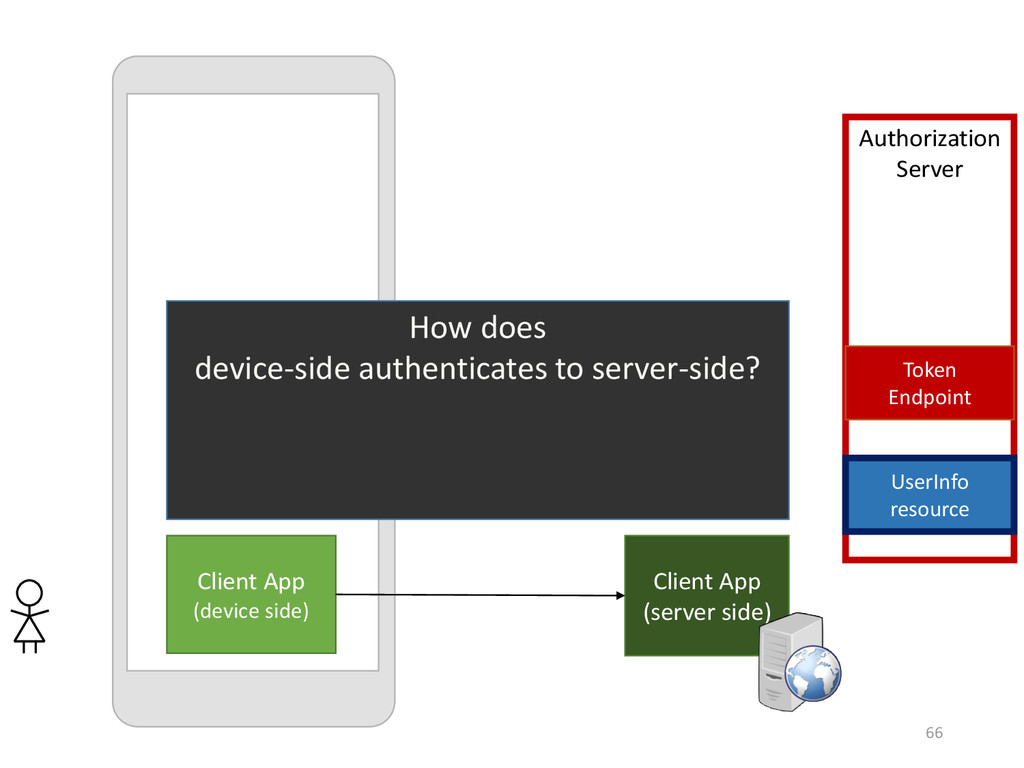
66 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) How does device-side authenticates to server-side? -
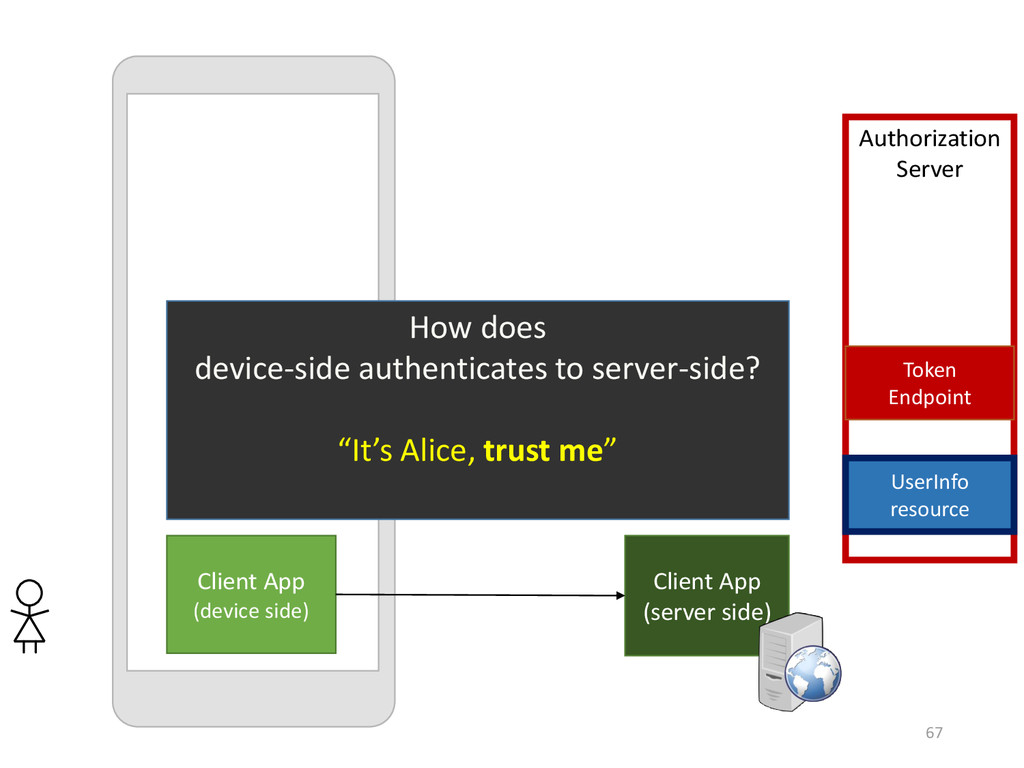
67 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) How does device-side authenticates to server-side? “It’s Alice, trust me” -
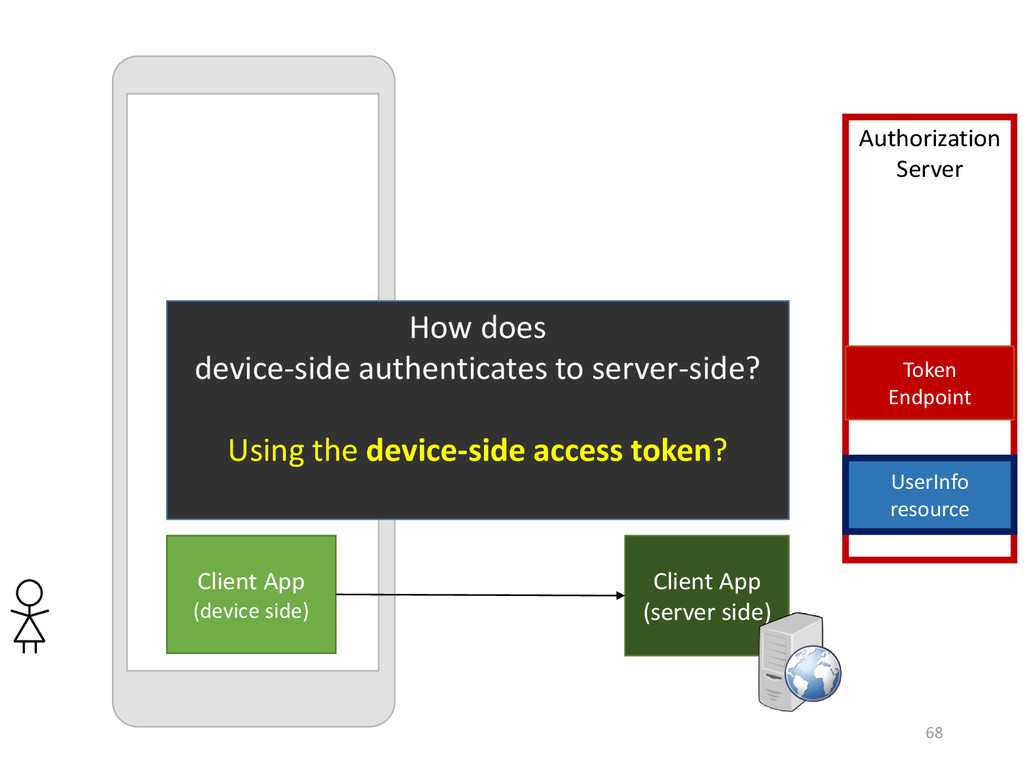
68 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) How does device-side authenticates to server-side? Using the device-side access token? -
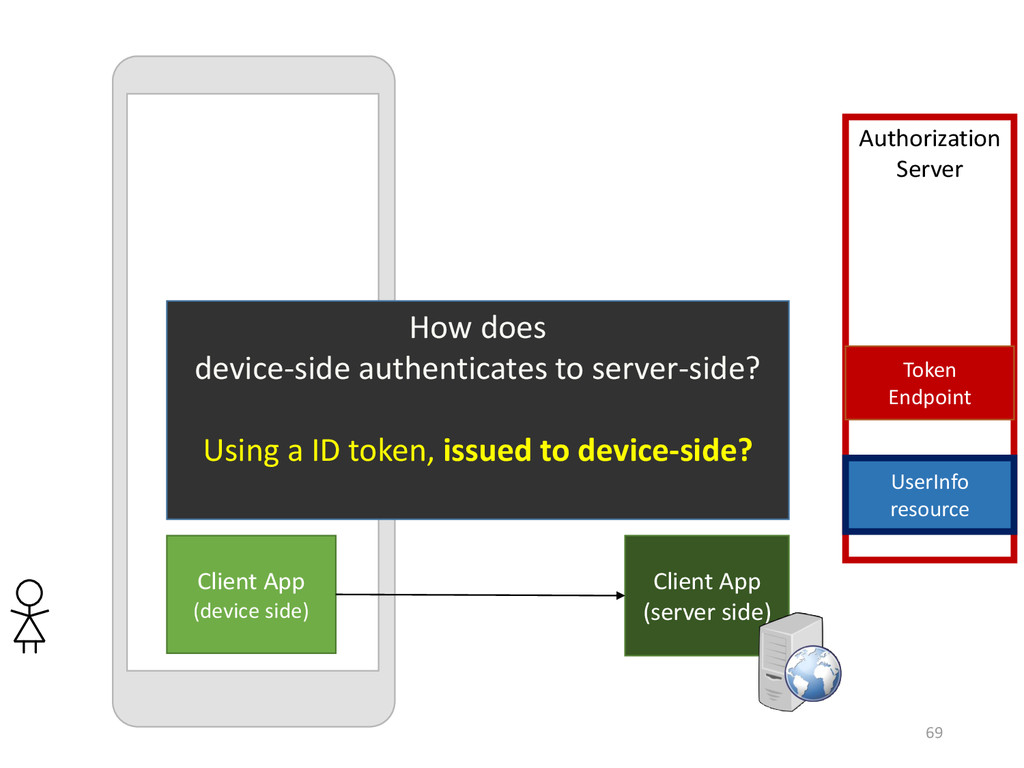
69 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) How does device-side authenticates to server-side? Using a ID token, issued to device-side? -
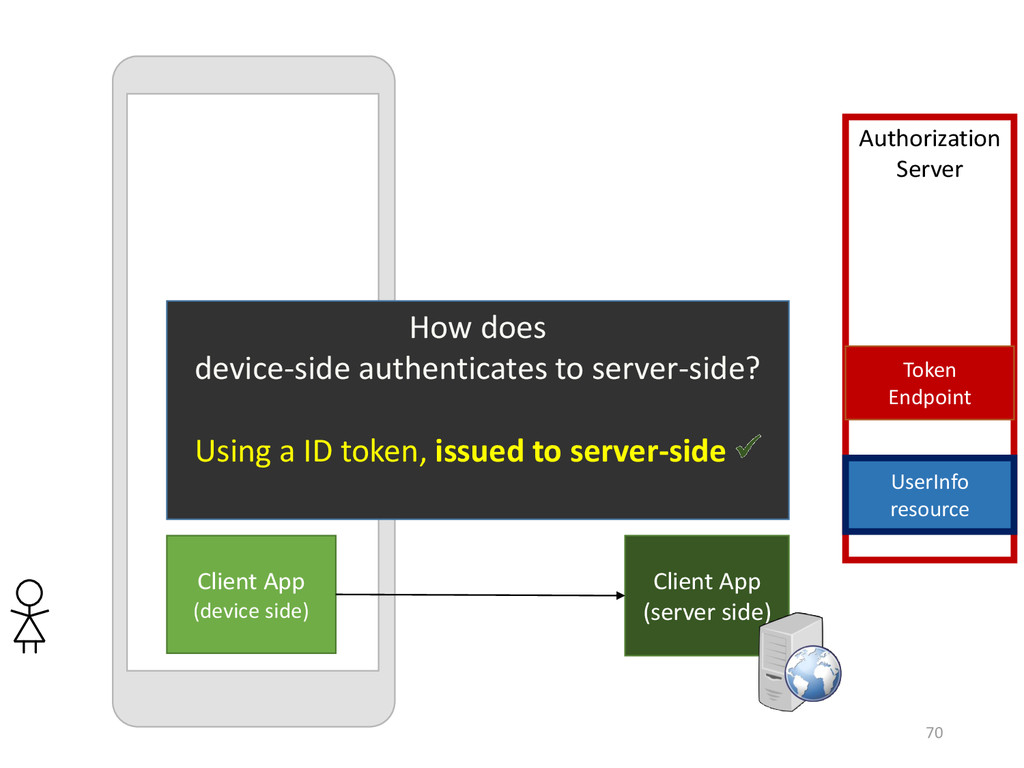
70 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) How does device-side authenticates to server-side? Using a ID token, issued to server-side -
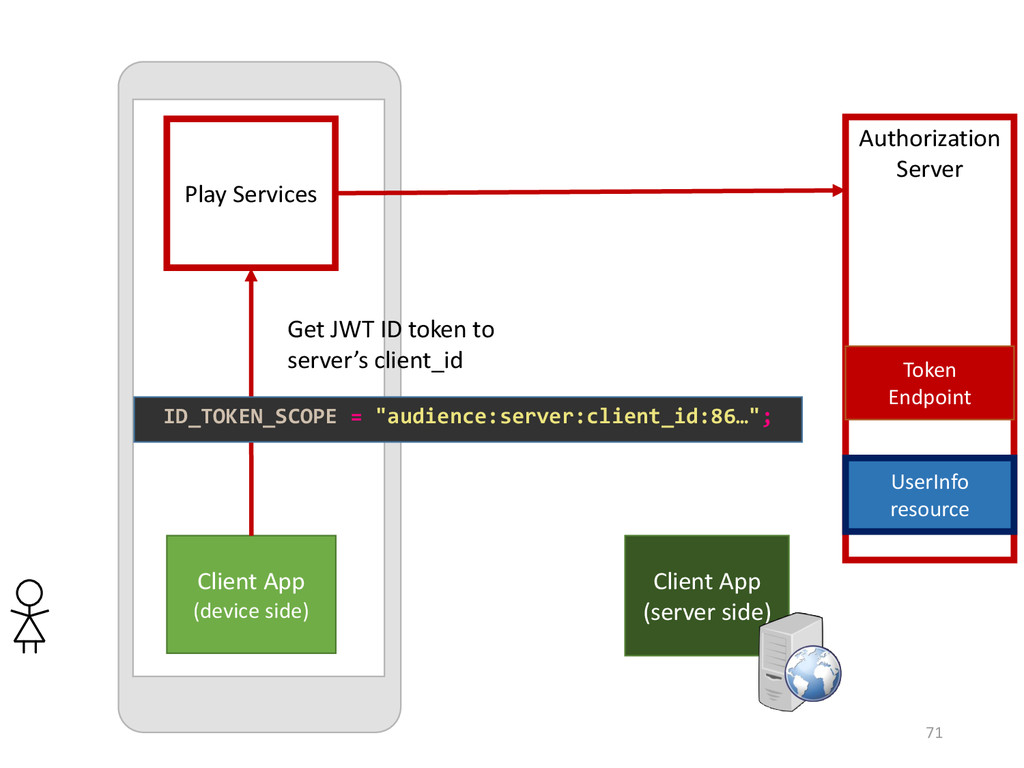
71 Play Services Client App (device side) Authorization Server Token
Endpoint UserInfo resource Client App (server side) Get JWT ID token to server’s client_id ID_TOKEN_SCOPE = "audience:server:client_id:86…"; -
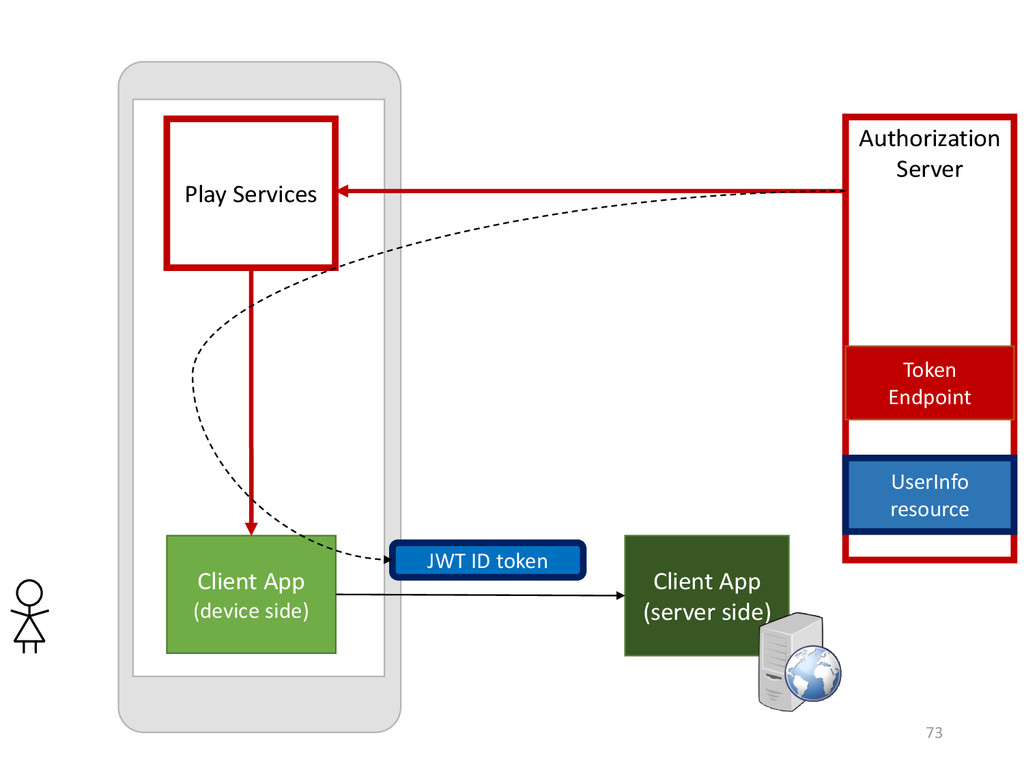
73 Play Services Client App (device side) Authorization Server Token
Endpoint UserInfo resource Client App (server side) JWT ID token -
Demo • Using a Google to obtain an ID token
for the server 74 -
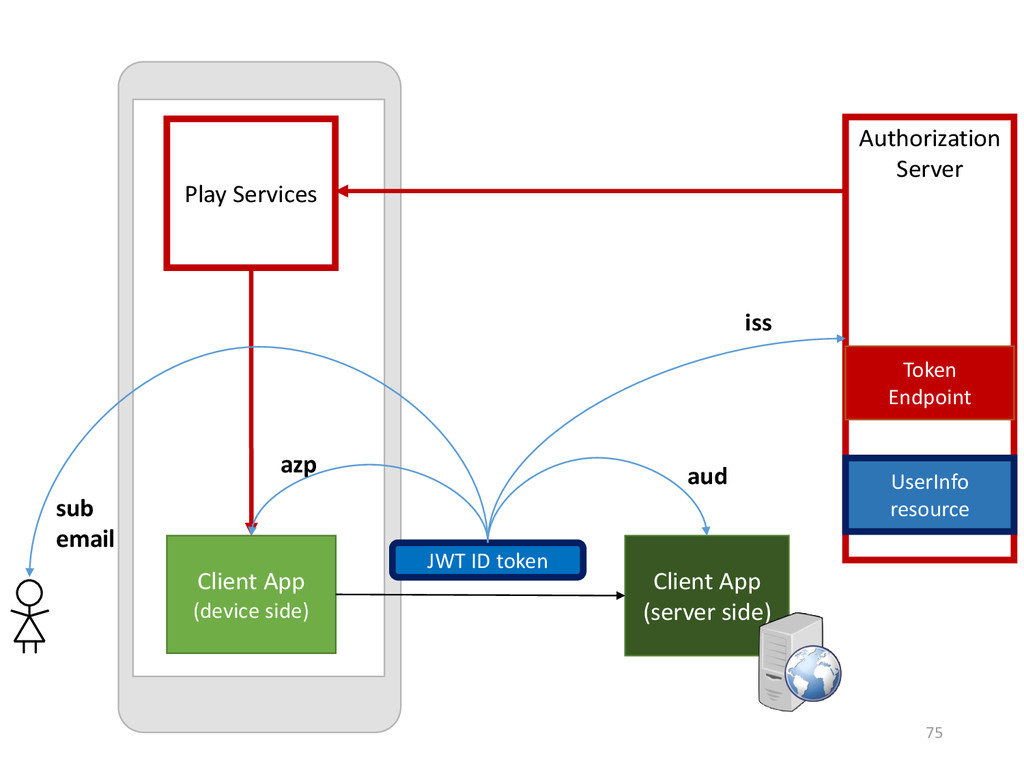
75 Play Services Client App (device side) Authorization Server Token
Endpoint UserInfo resource Client App (server side) JWT ID token aud azp iss sub email -
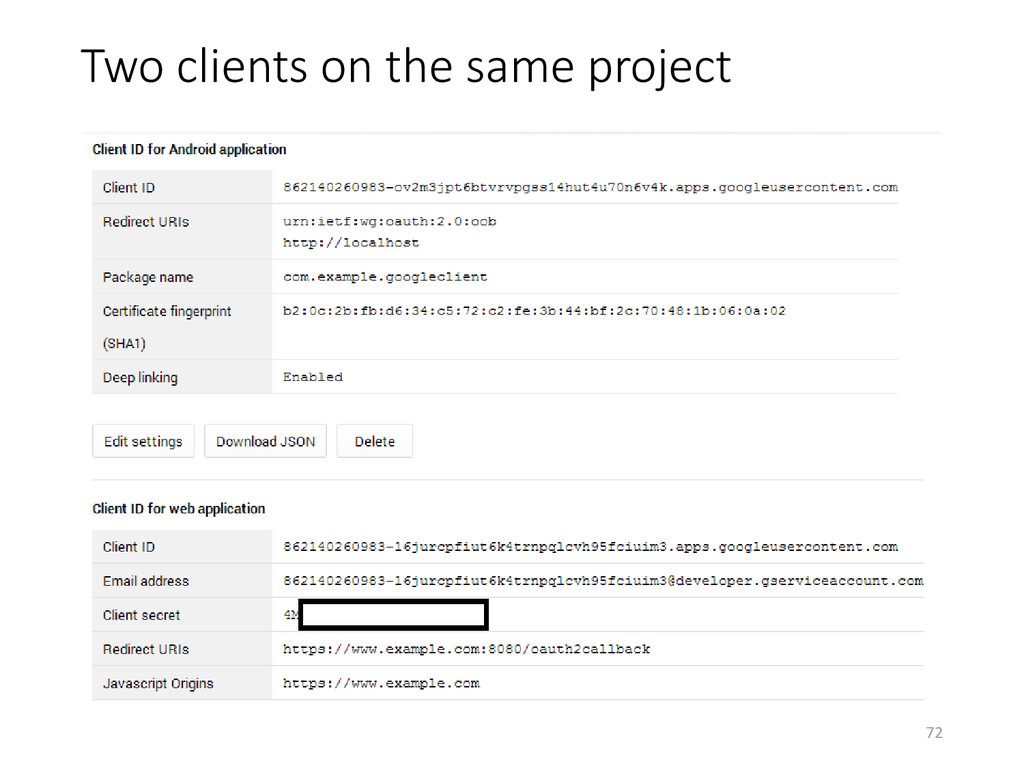
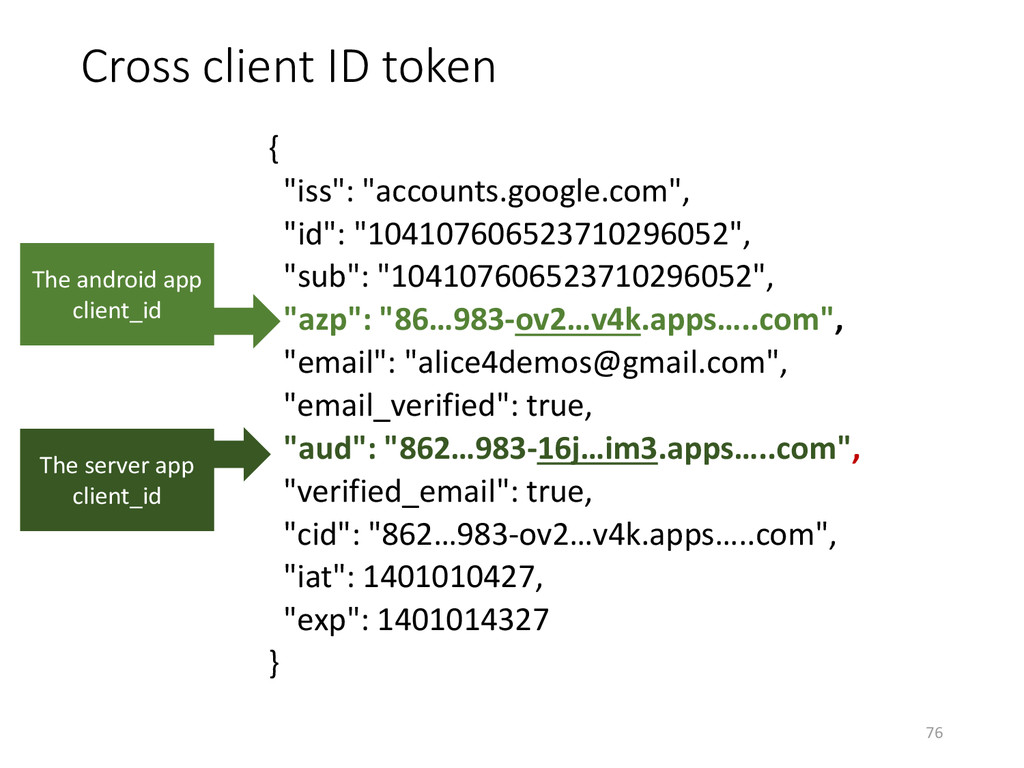
Cross client ID token { "iss": "accounts.google.com", "id": "104107606523710296052", "sub":
"104107606523710296052", "azp": "86…983-ov2…v4k.apps…..com", "email": "[email protected]", "email_verified": true, "aud": "862…983-16j…im3.apps…..com", "verified_email": true, "cid": "862…983-ov2…v4k.apps…..com", "iat": 1401010427, "exp": 1401014327 } 76 The android app client_id The server app client_id -
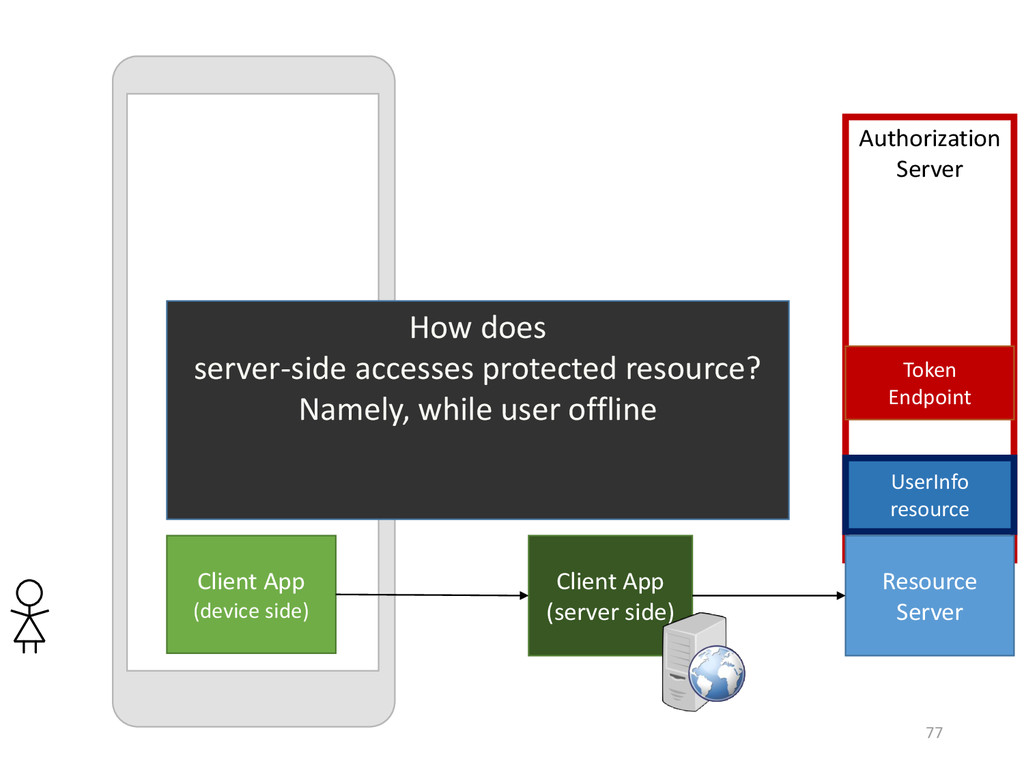
77 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) How does server-side accesses protected resource? Namely, while user offline Resource Server -
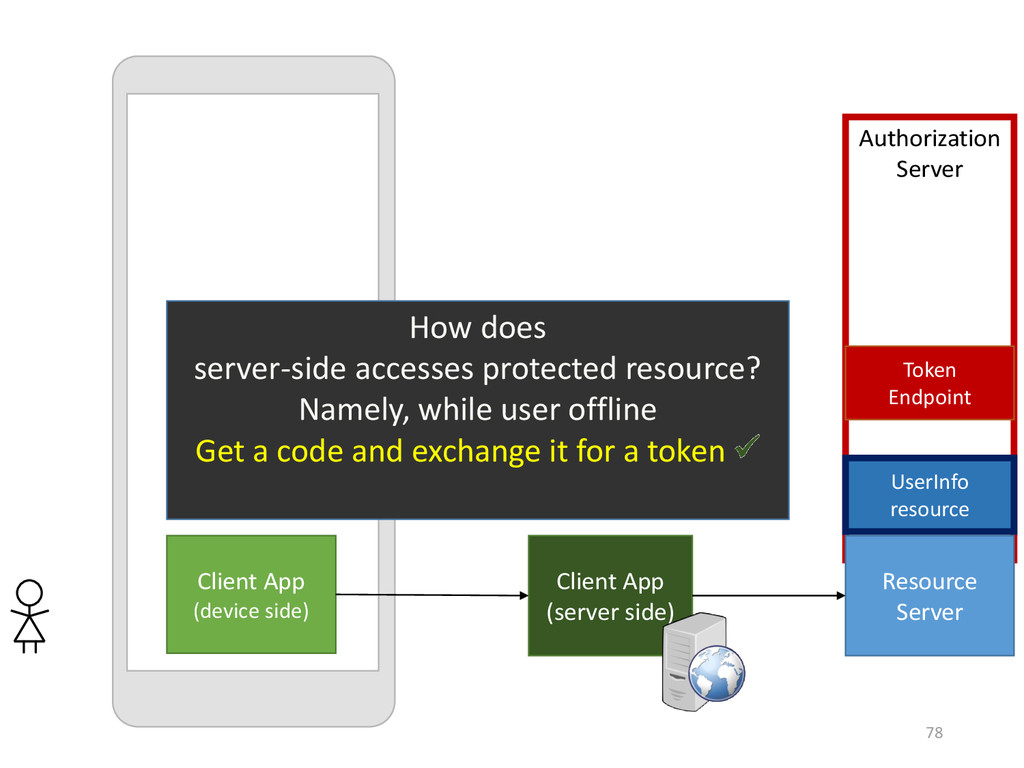
78 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) How does server-side accesses protected resource? Namely, while user offline Get a code and exchange it for a token Resource Server -
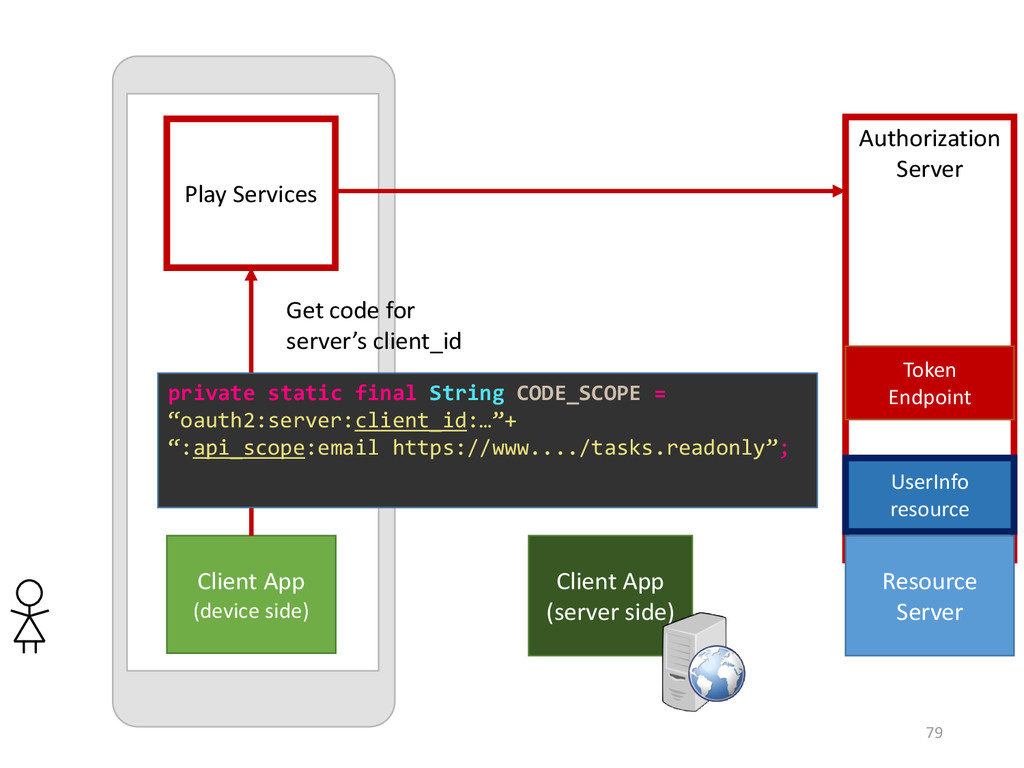
79 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) Resource Server Play Services Get code for server’s client_id private static final String CODE_SCOPE = “oauth2:server:client_id:…”+ “:api_scope:email https://www..../tasks.readonly”; -
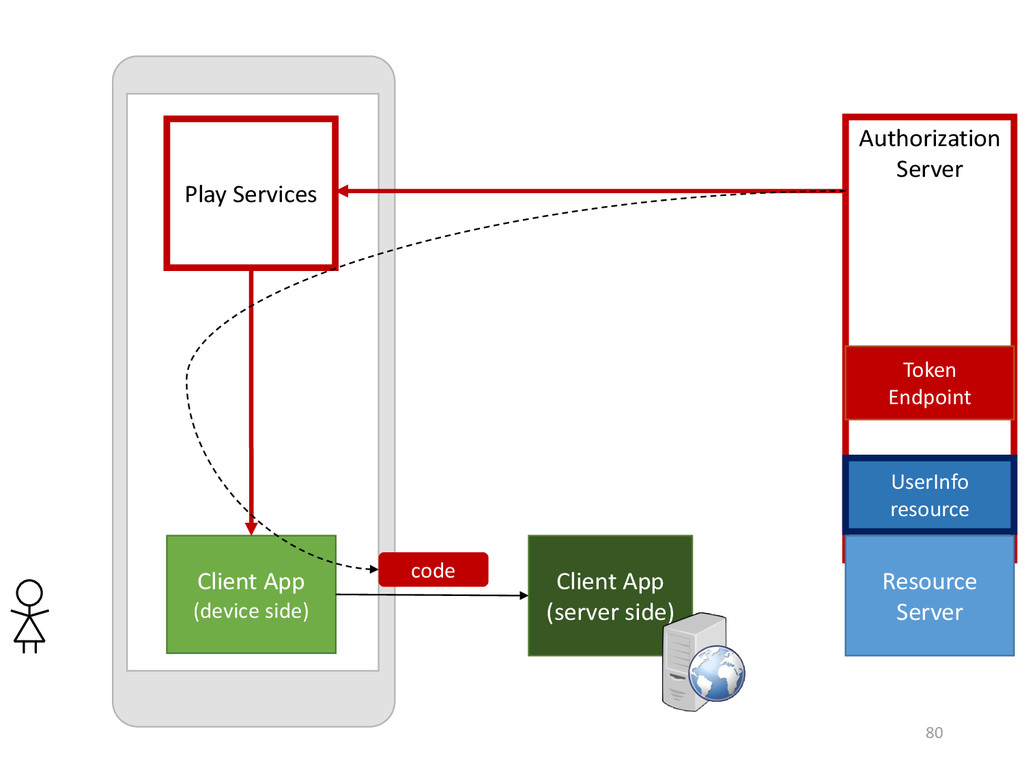
80 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) Resource Server Play Services code -
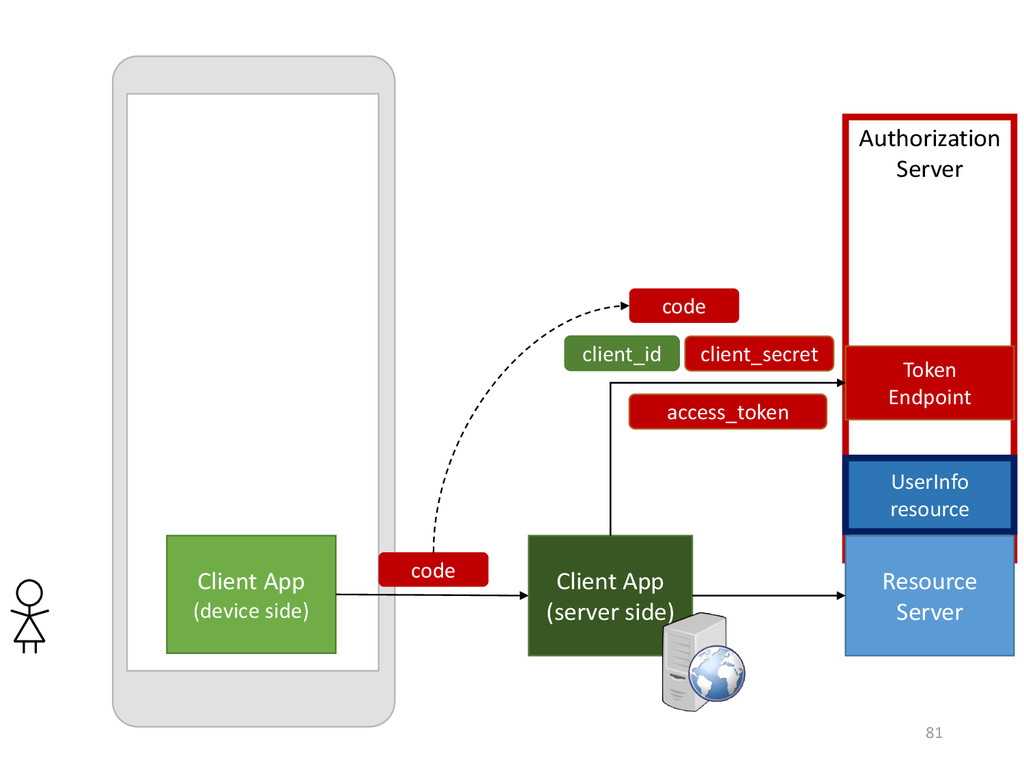
81 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) Resource Server client_secret client_id code code access_token -
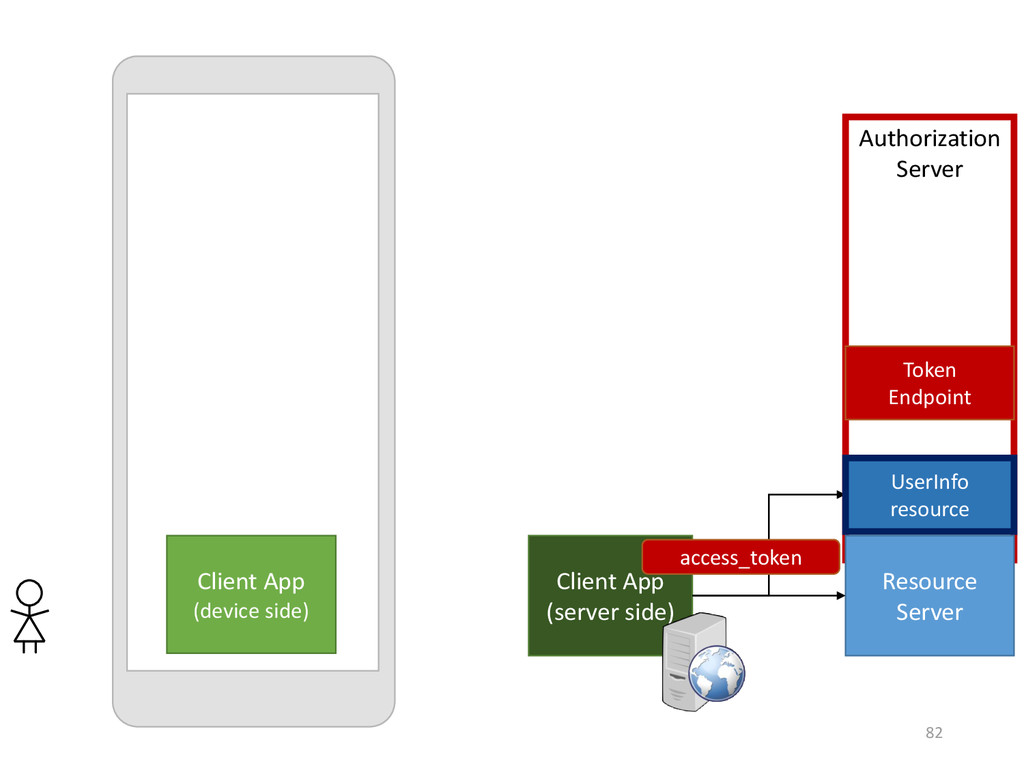
82 Client App (device side) Authorization Server Token Endpoint UserInfo
resource Client App (server side) Resource Server access_token -
Custom solution • Scopes prefixes • SDK to interact with
token agent • Protocol between Token Agent and Authz Server • There are other custom solutions • E.g. Facebook 84 -
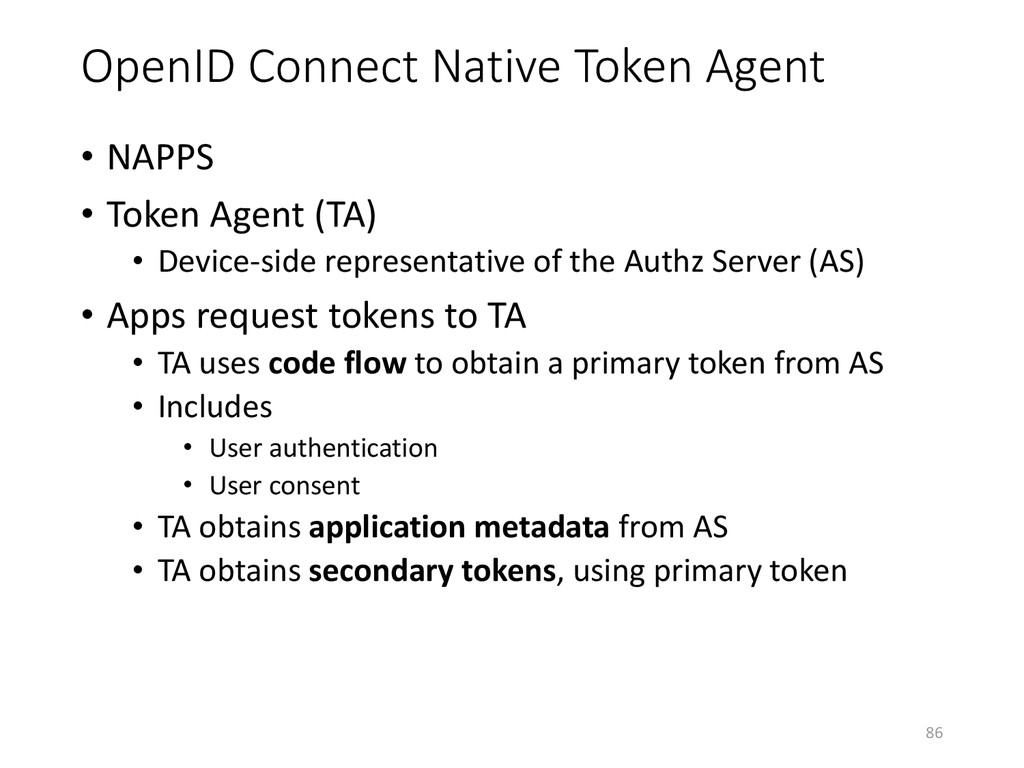
OpenID Connect Native Token Agent • NAPPS • Token Agent
(TA) • Device-side representative of the Authz Server (AS) • Apps request tokens to TA • TA uses code flow to obtain a primary token from AS • Includes • User authentication • User consent • TA obtains application metadata from AS • TA obtains secondary tokens, using primary token 86 -
OpenID Connect Native Token Agent • Communication between apps and
TA • On Android, using Intents and Activities • Delegation to server side? • Device identity? 87 -
Resources • RFCs 6749 and 6750 • Google https://developers.google.com/+/mobile/android/sign-in •
NAPPS http://hg.openid.net/napps/wiki/Home • Designing Evolvable Web APIs with ASP.NET One chapter on OAuth 2.0 and OpenID Connect • https://github.com/pmhsfelix • Thank you! 88