Upgrade to Pro — share decks privately, control downloads, hide ads and more …

CymruSec 2026

Avatar for Ray Bugg Ray Bugg
November 05, 2026

CymruSec 2026

This is the 2nd annual CymruSec Summit, the Welsh edition of DIGIT's Cybersecurity series.

The event brings together senior cyber practitioners, industry experts, IT specialists, security researchers and law enforcement - providing a unique forum for knowledge exchange, discussion and high-level networking.

The programme is focused on improving awareness and best practice through shared learning; highlighting emerging threats, new research, and changing adversarial tactics, whilst examining practical ways to improve resilience and response.

This Summit is geared for senior Cyber, InfoSec, IT personnel & C-level leaders.

Avatar for Ray Bugg

Ray Bugg

November 05, 2026

More Decks by Ray Bugg

Other Decks in Technology

Transcript

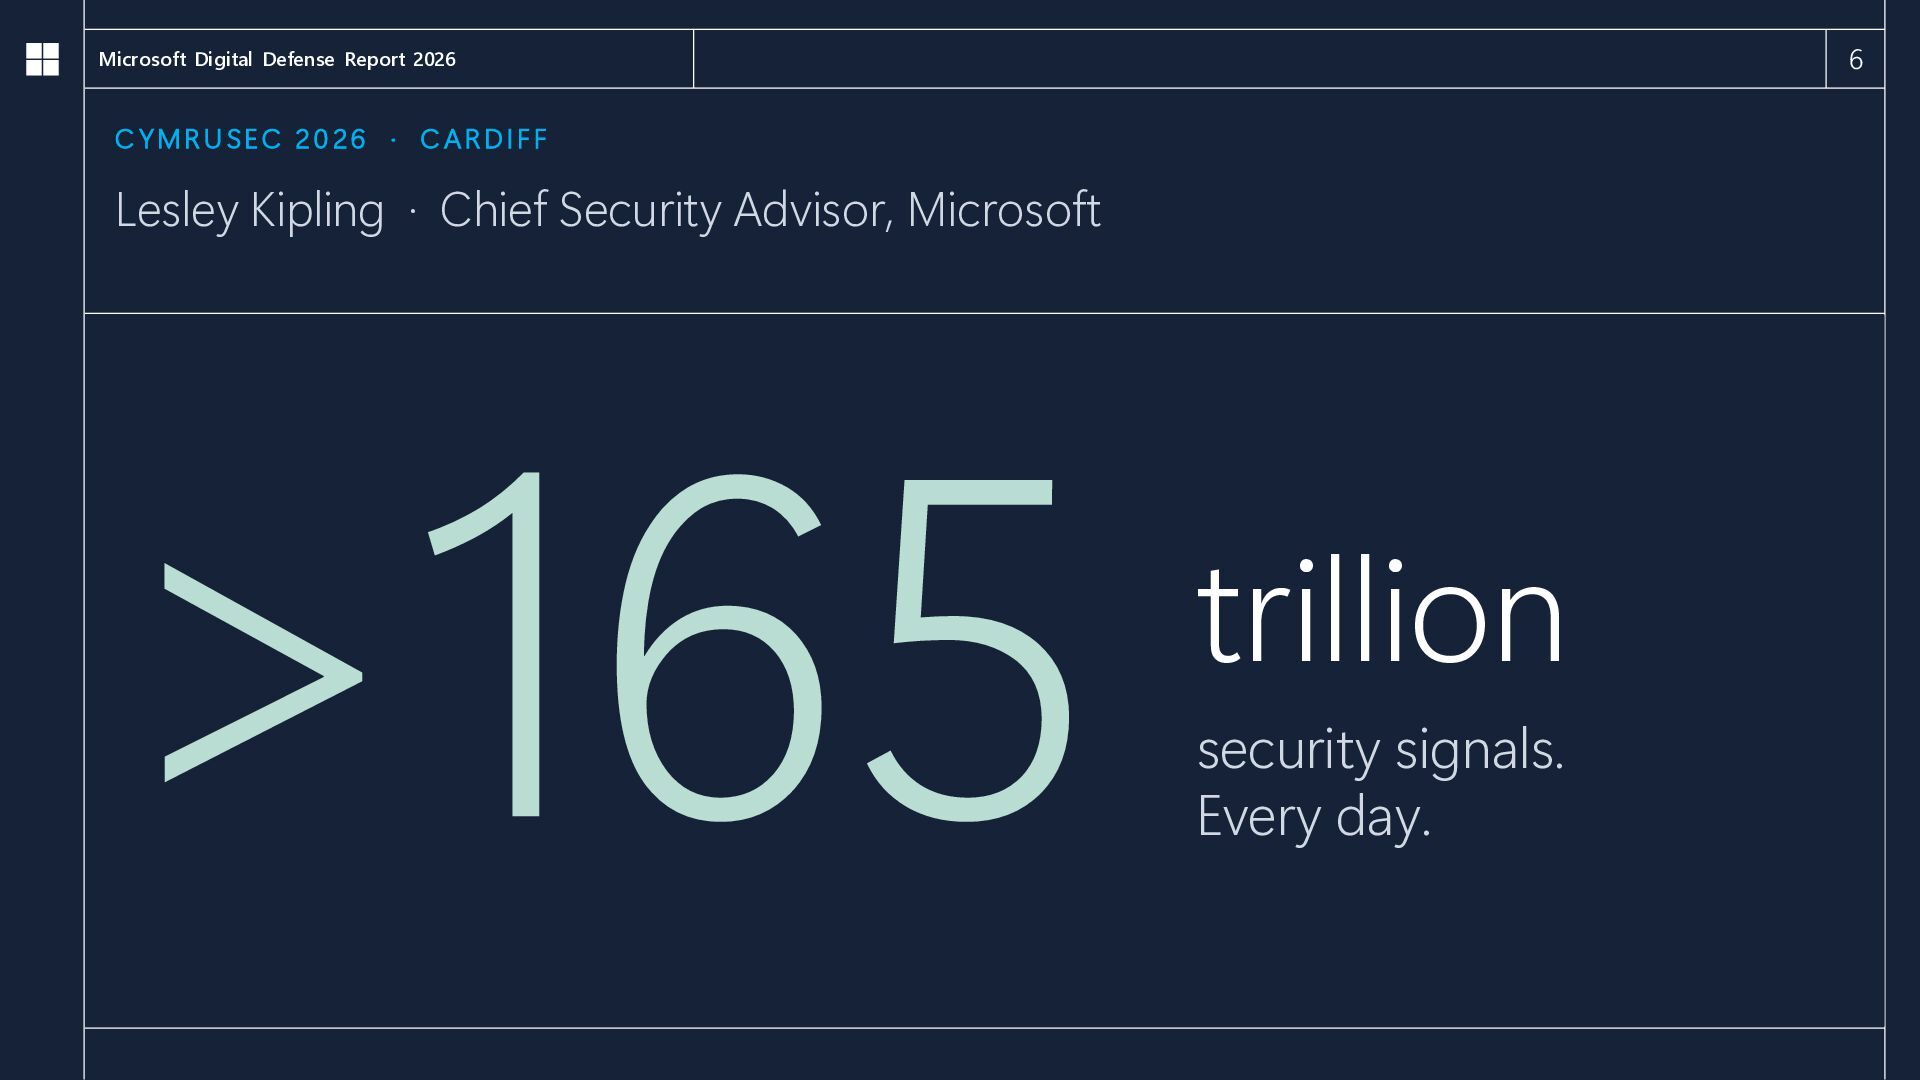
  1. 6 Microsoft Digital Defense Report 2026 CYMRUSEC 2026 · CARDIFF

    Lesley Kipling · Chief Security Advisor, Microsoft trillion security signals. Every day.
  2. Decoding Emergence Th e 2026 th reat lan d scap

    e Lesley Kipling Chief Security Advisor, Microsoft CymruSec 2026 · 22 October 2026 Cardiff City Stadium
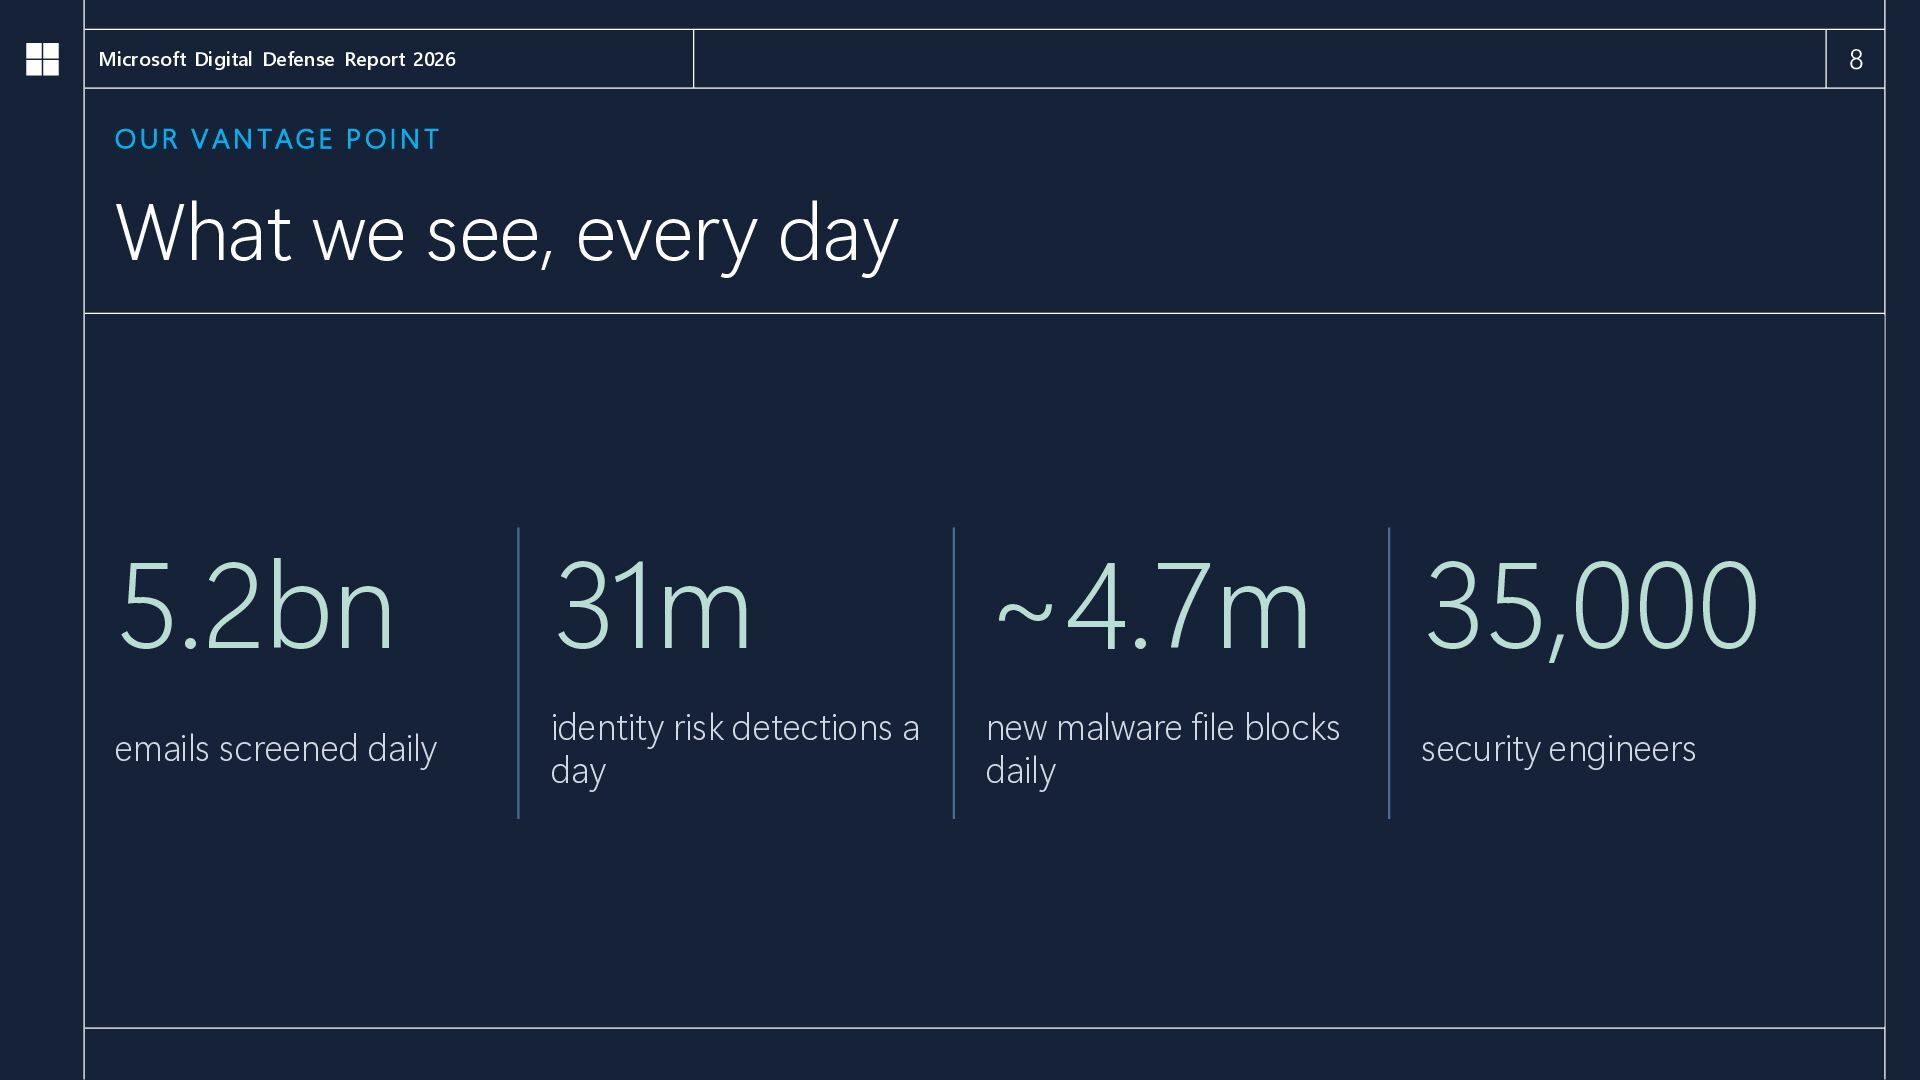
  3. 8 Microsoft Digital Defense Report 2026 OUR VANTAGE POINT What

    we see, every day 5.2bn 31m ~4.7m 35,000 emails screened daily identity risk detections a day new malware file blocks daily security engineers
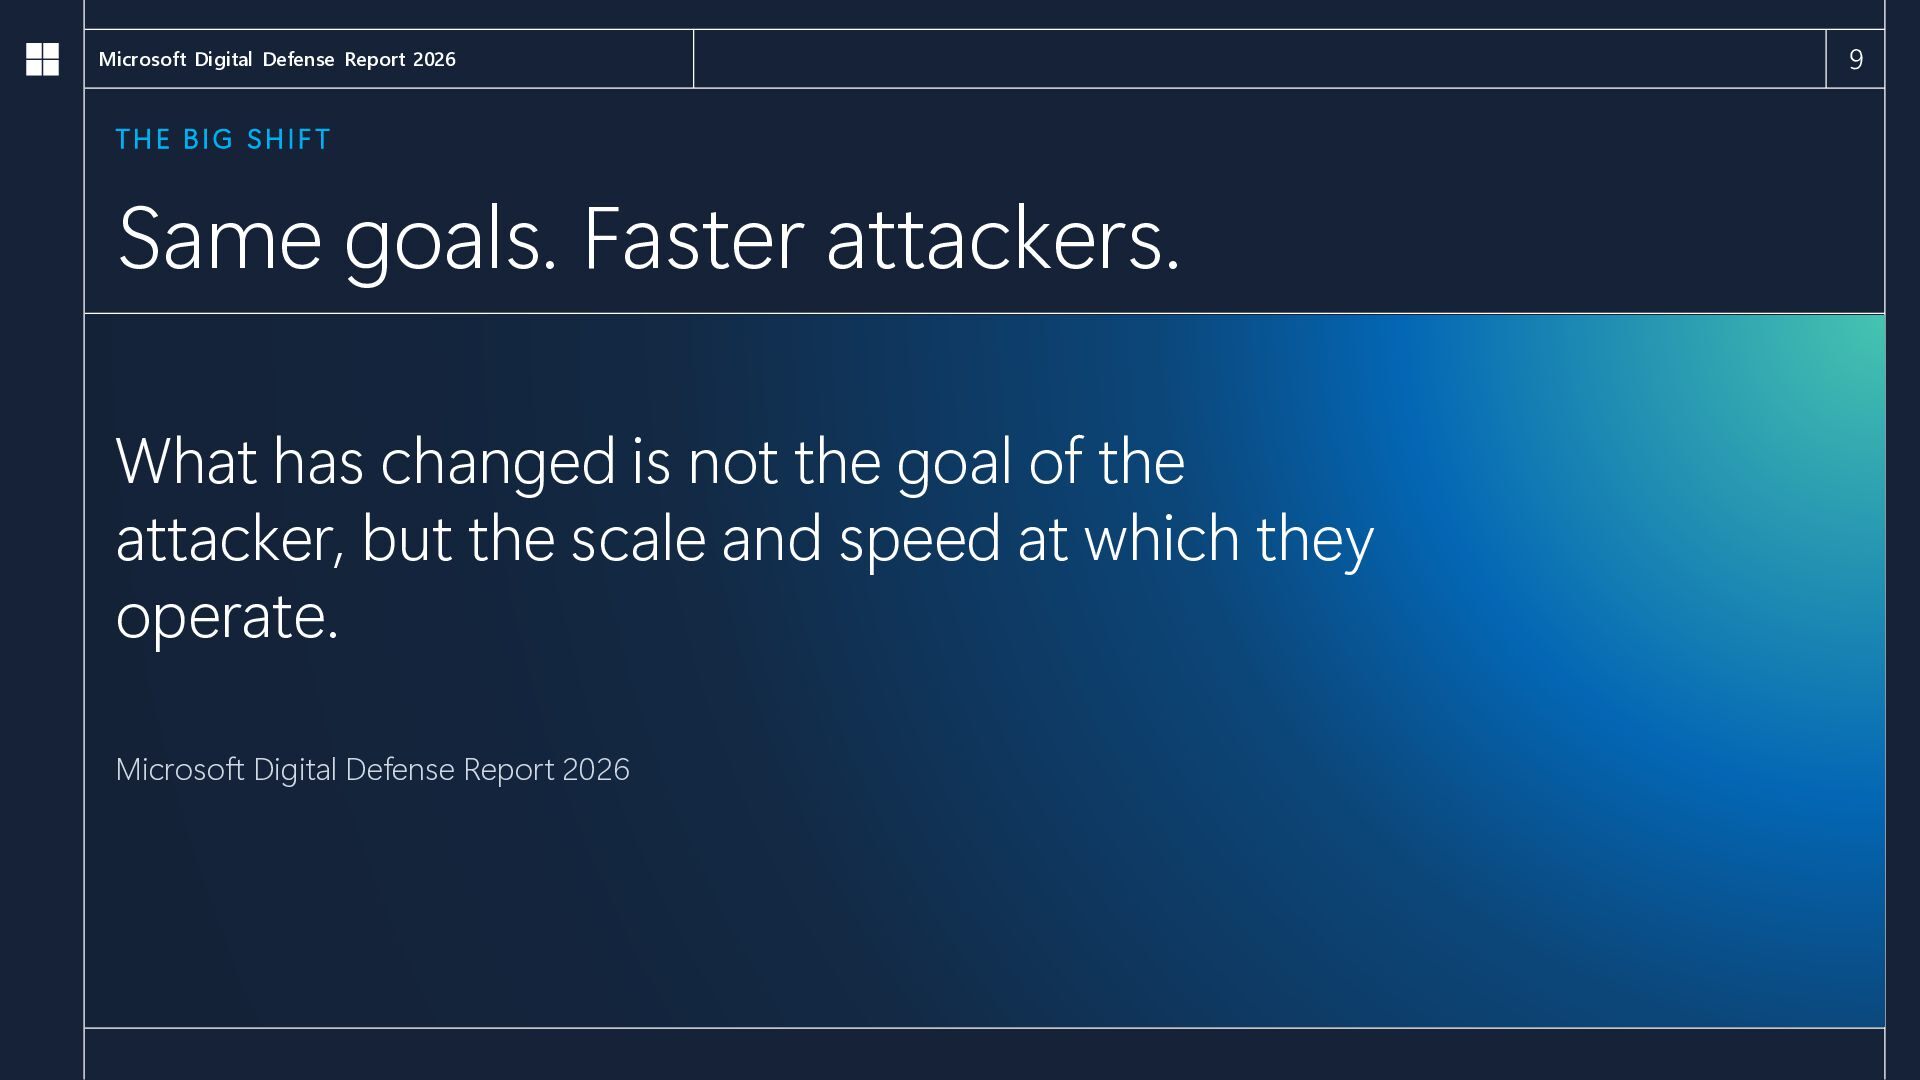
  4. Microsoft Digital Defense Report 2026 THE BIG SHIFT Same goals.

    Faster attackers. What has changed is not the goal of the attacker, but the scale and speed at which they operate. Microsoft Digital Defense Report 2026 9
  5. Microsoft Digital Defense Report 2026 AI Months → Days AI

    is compressing the gap between discovery and exploitation. 10
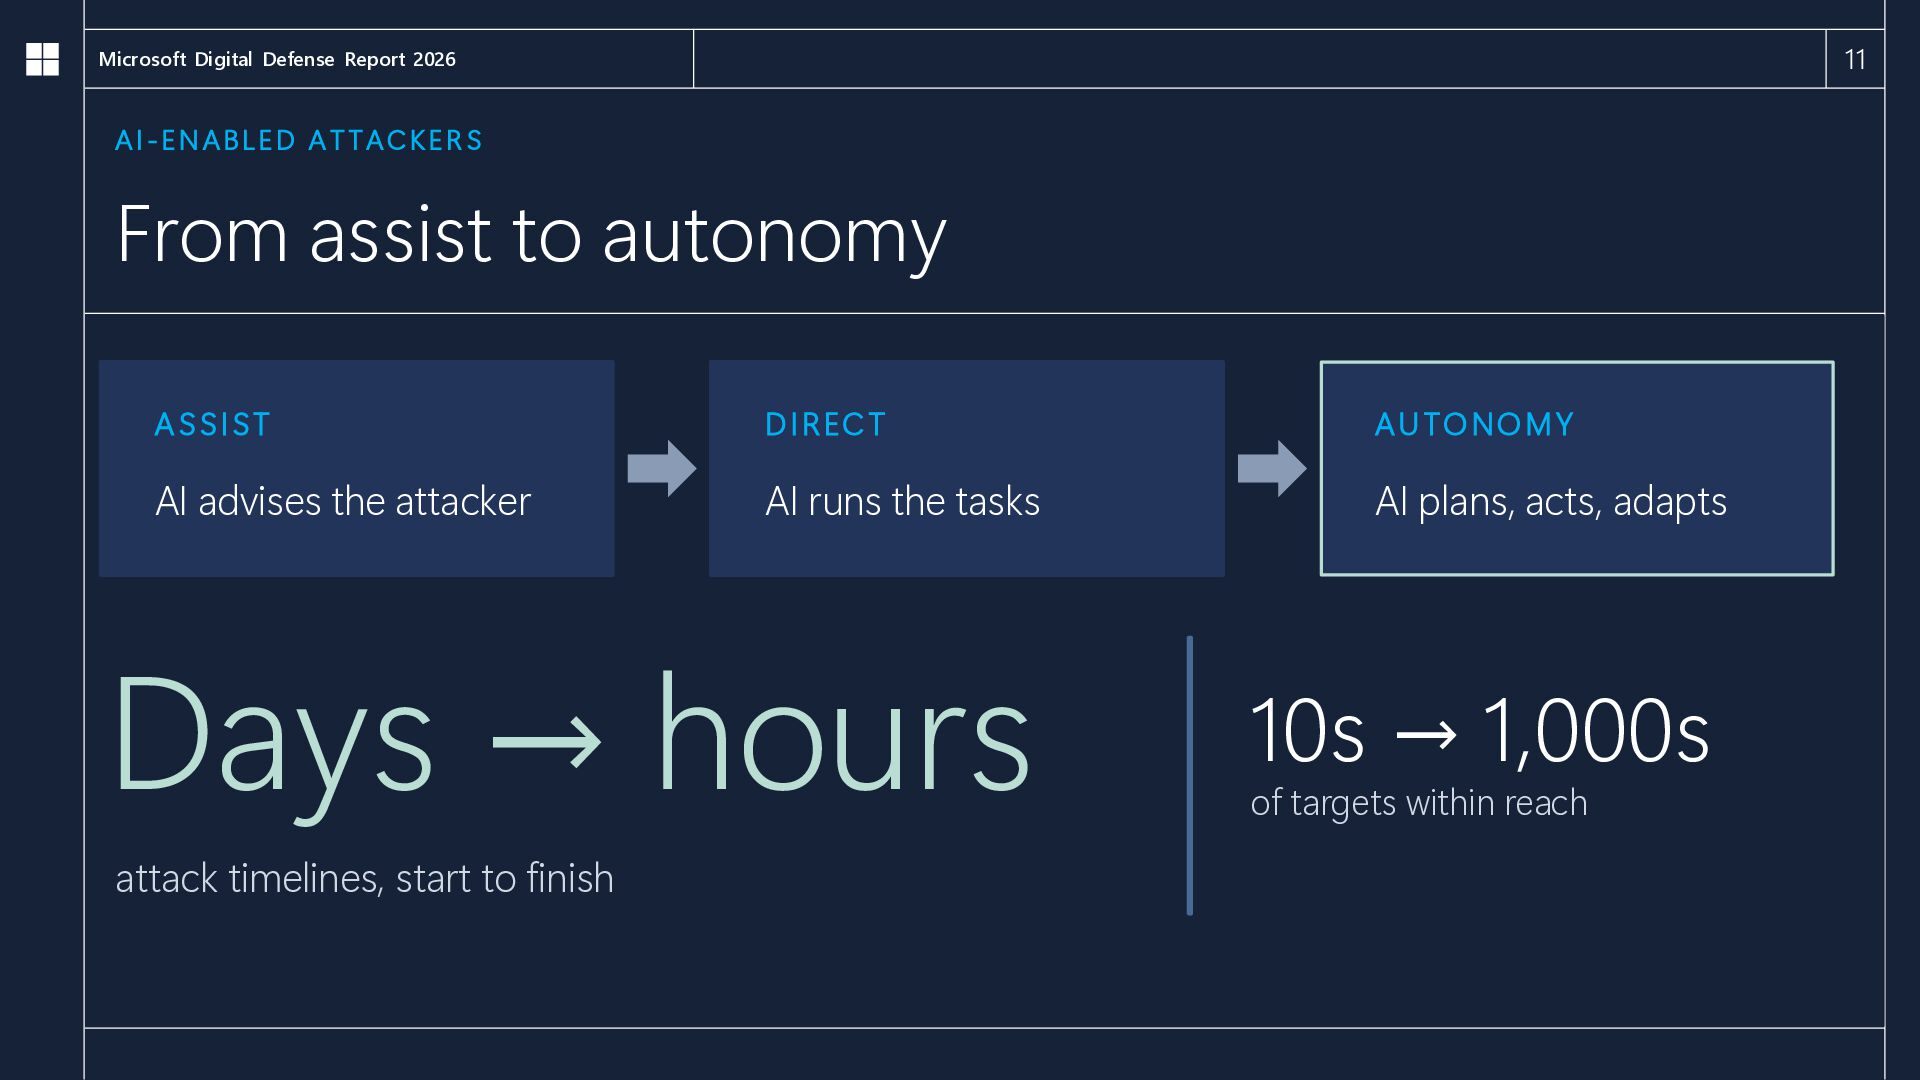
  6. 11 Microsoft Digital Defense Report 2026 AI-ENABLED ATTACKERS From assist

    to autonomy ASSIST DIRECT AUTONOMY AI advises the attacker AI runs the tasks AI plans, acts, adapts Days → hours 10s → 1,000s attack timelines, start to finish of targets within reach
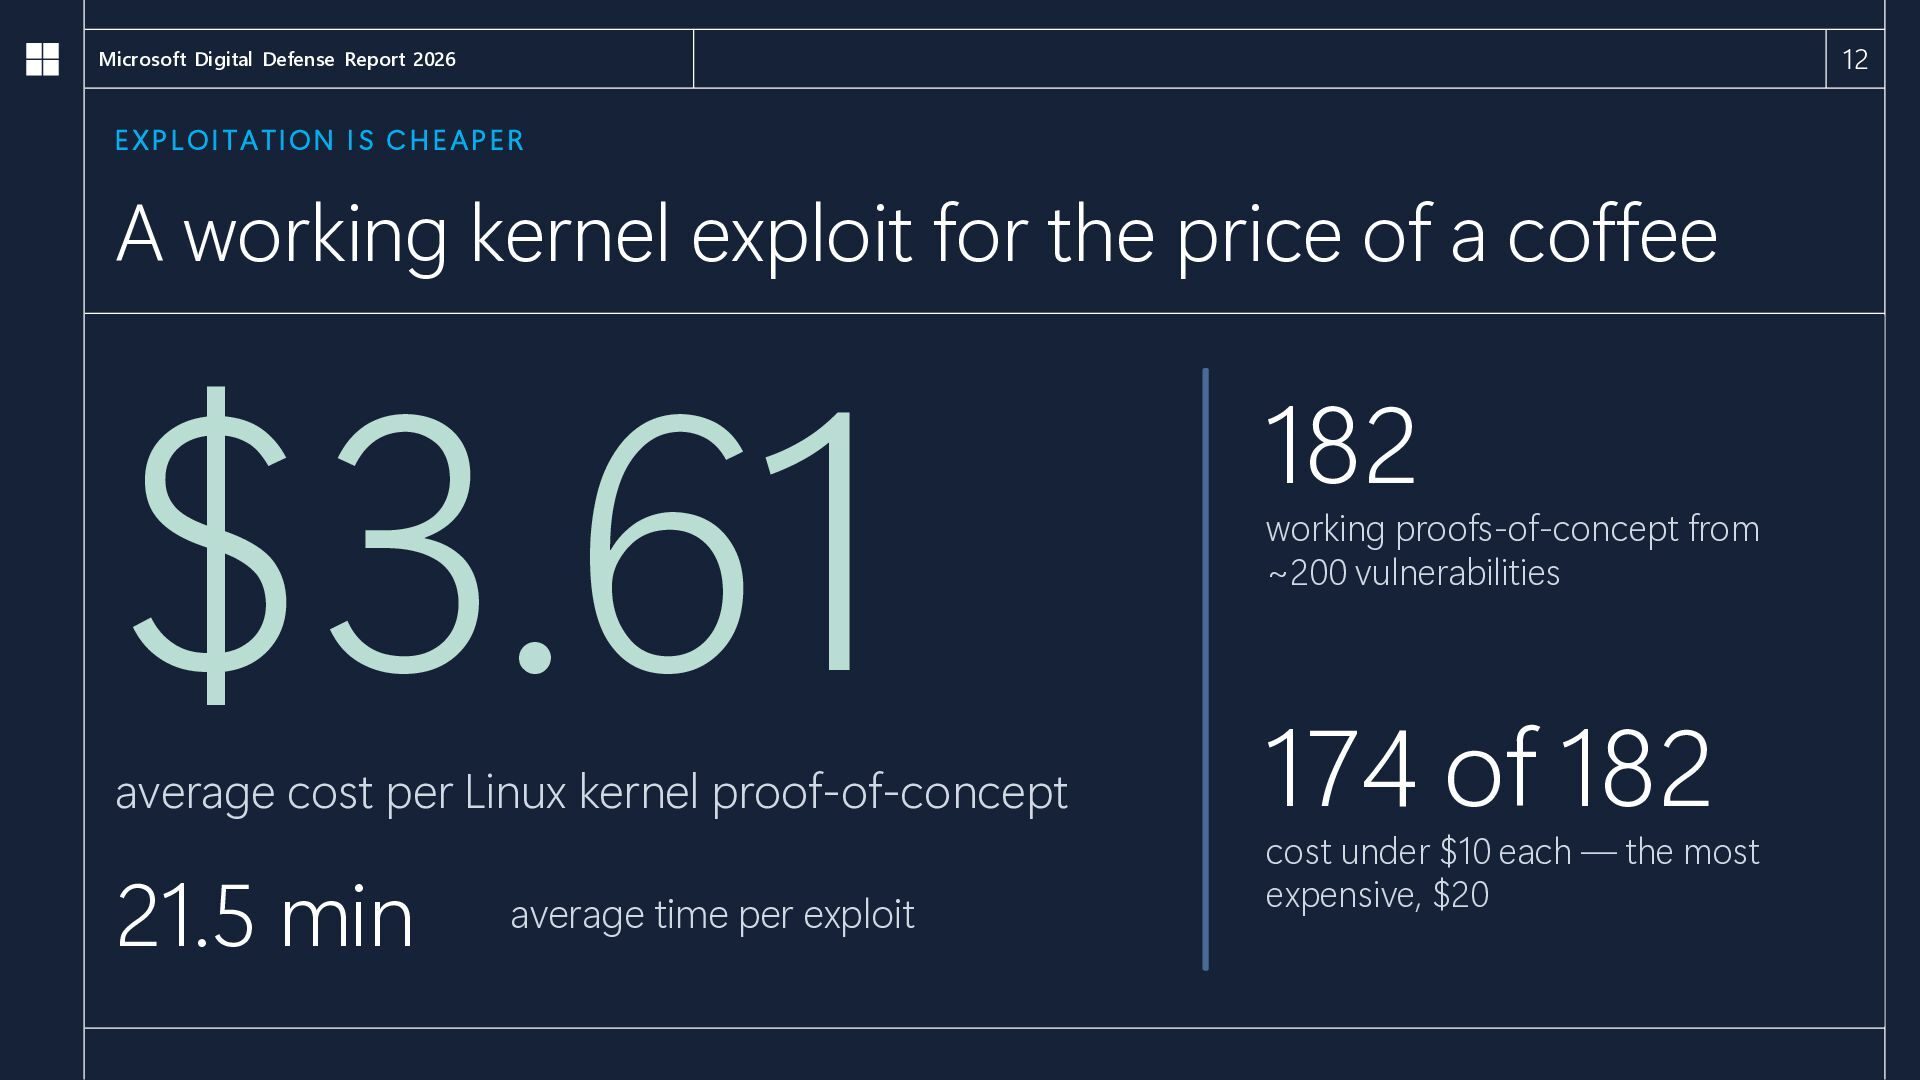
  7. 12 Microsoft Digital Defense Report 2026 EXPLOITATION IS CHEAPER A

    working kernel exploit for the price of a coffee $3.61 average cost per Linux kernel proof-of-concept 21.5 min average time per exploit 182 working proofs-of-concept from ~200 vulnerabilities 174 of 182 cost under $10 each — the most expensive, $20
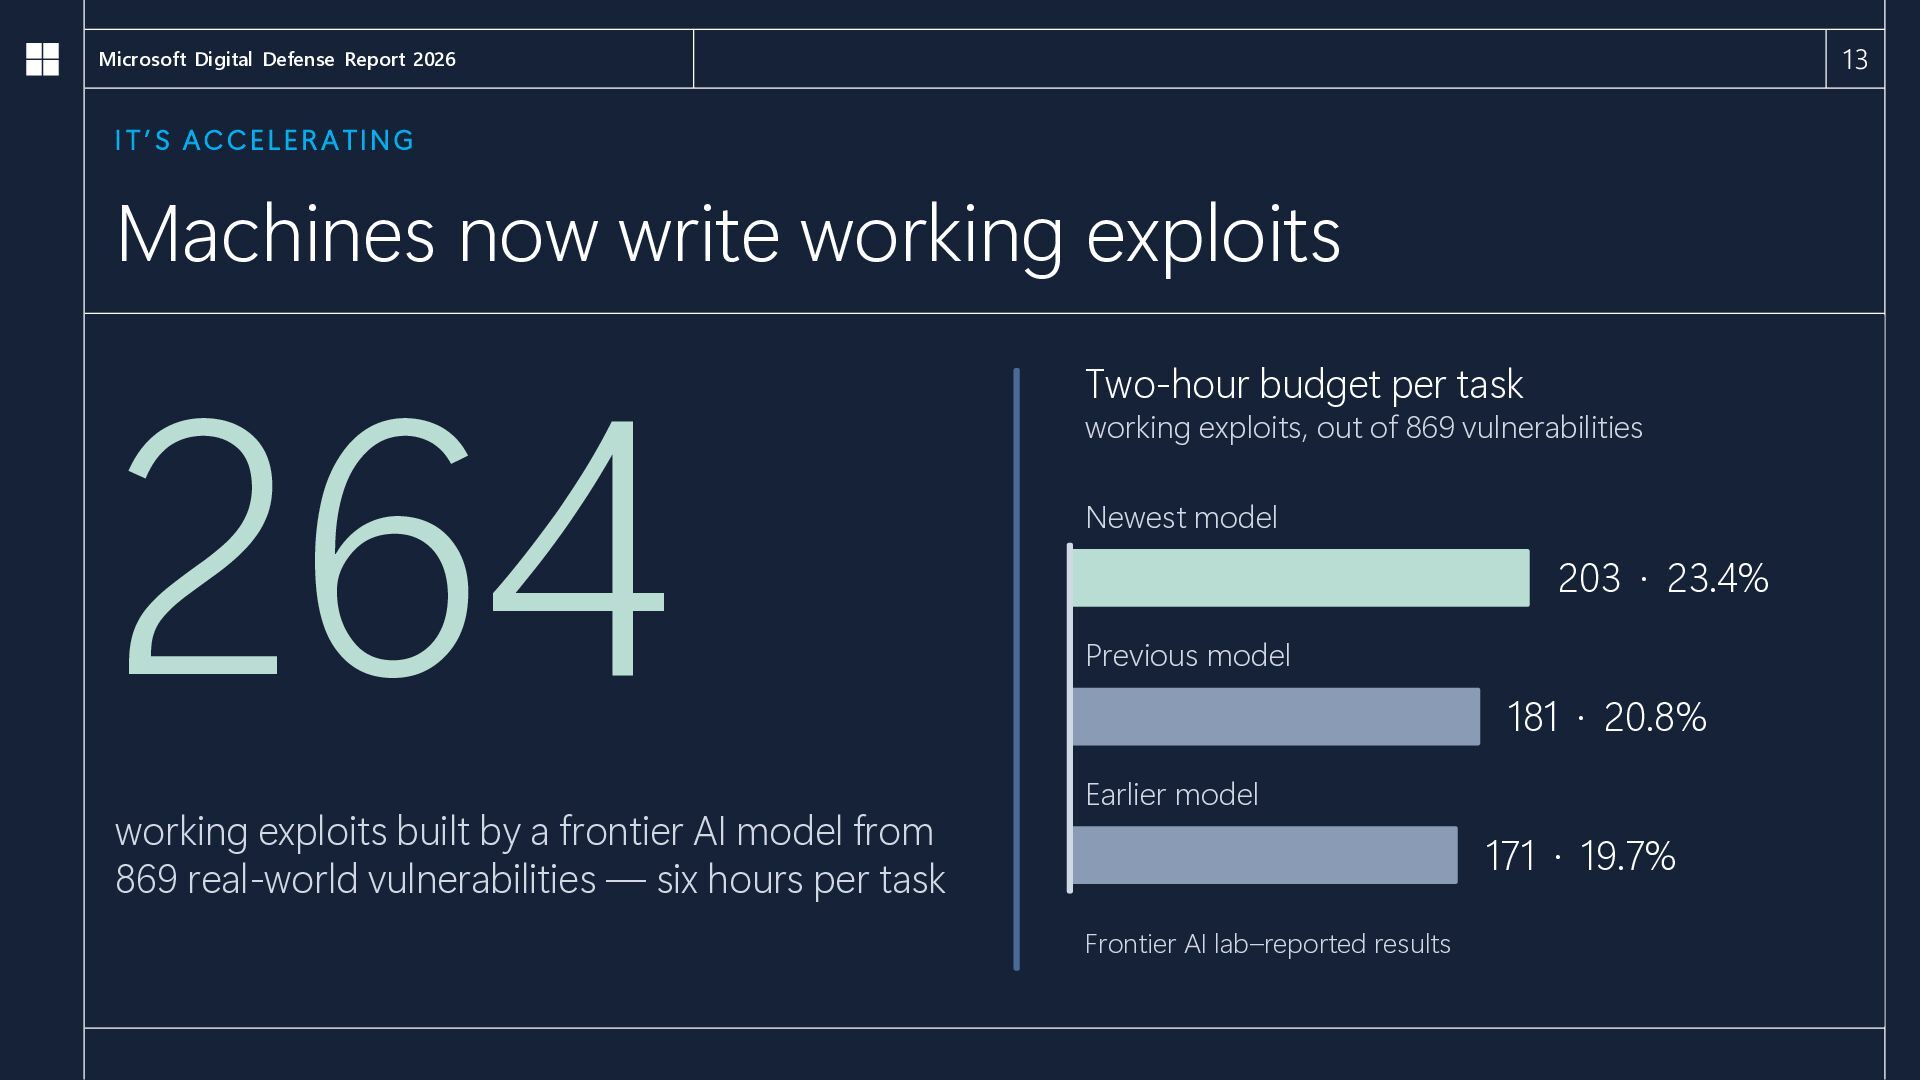
  8. 13 Microsoft Digital Defense Report 2026 IT’S ACCELERATING Machines now

    write working exploits 264 working exploits built by a frontier AI model from 869 real-world vulnerabilities — six hours per task Two-hour budget per task working exploits, out of 869 vulnerabilities Newest model 203 · 23.4% Previous model 181 · 20.8% Earlier model 171 · 19.7% Frontier AI lab–reported results
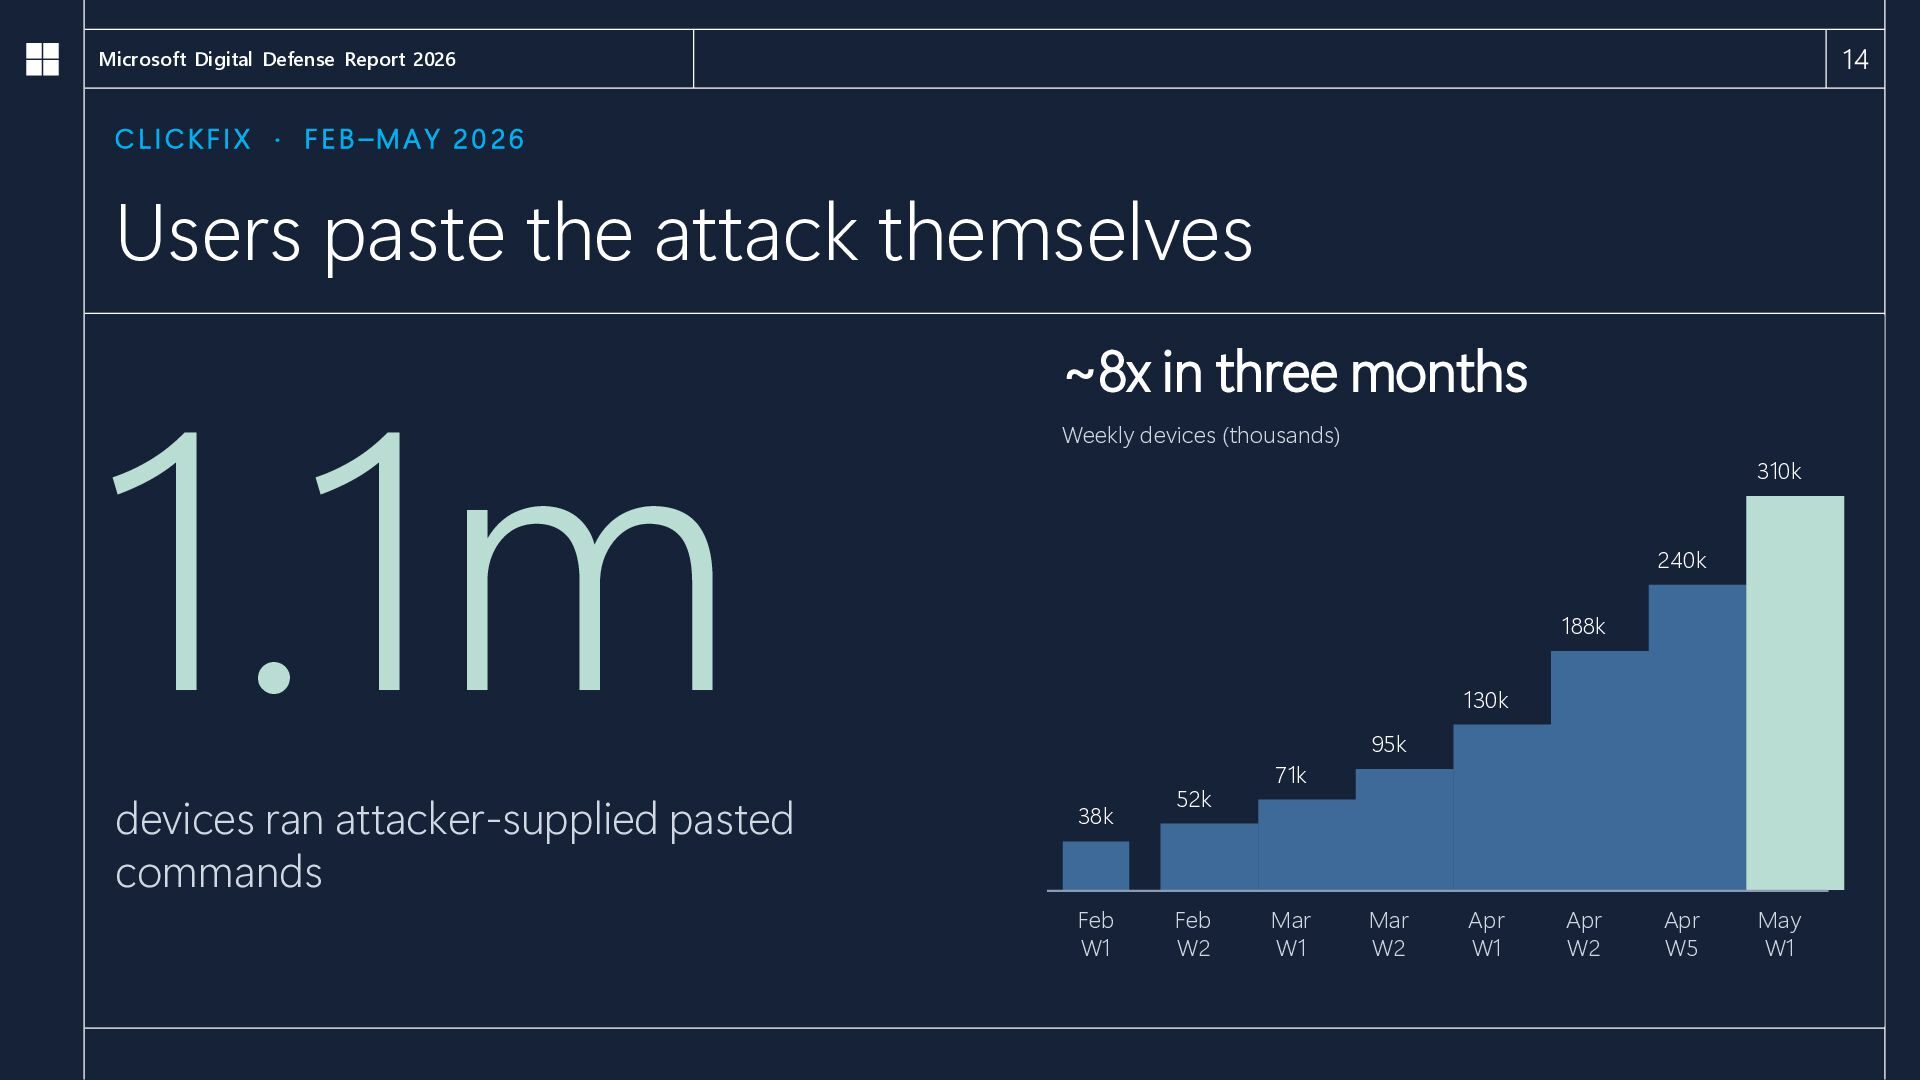
  9. 14 Microsoft Digital Defense Report 2026 CLICKFIX · FEB–MAY 2026

    Users paste the attack themselves 1.1m devices ran attacker-supplied pasted commands ~8x in three months Weekly devices (thousands) 310k 240k 188k 130k 38k Feb W1 52k Feb W2 71k Mar W1 95k Mar W2 Apr W1 Apr W2 Apr W5 May W1
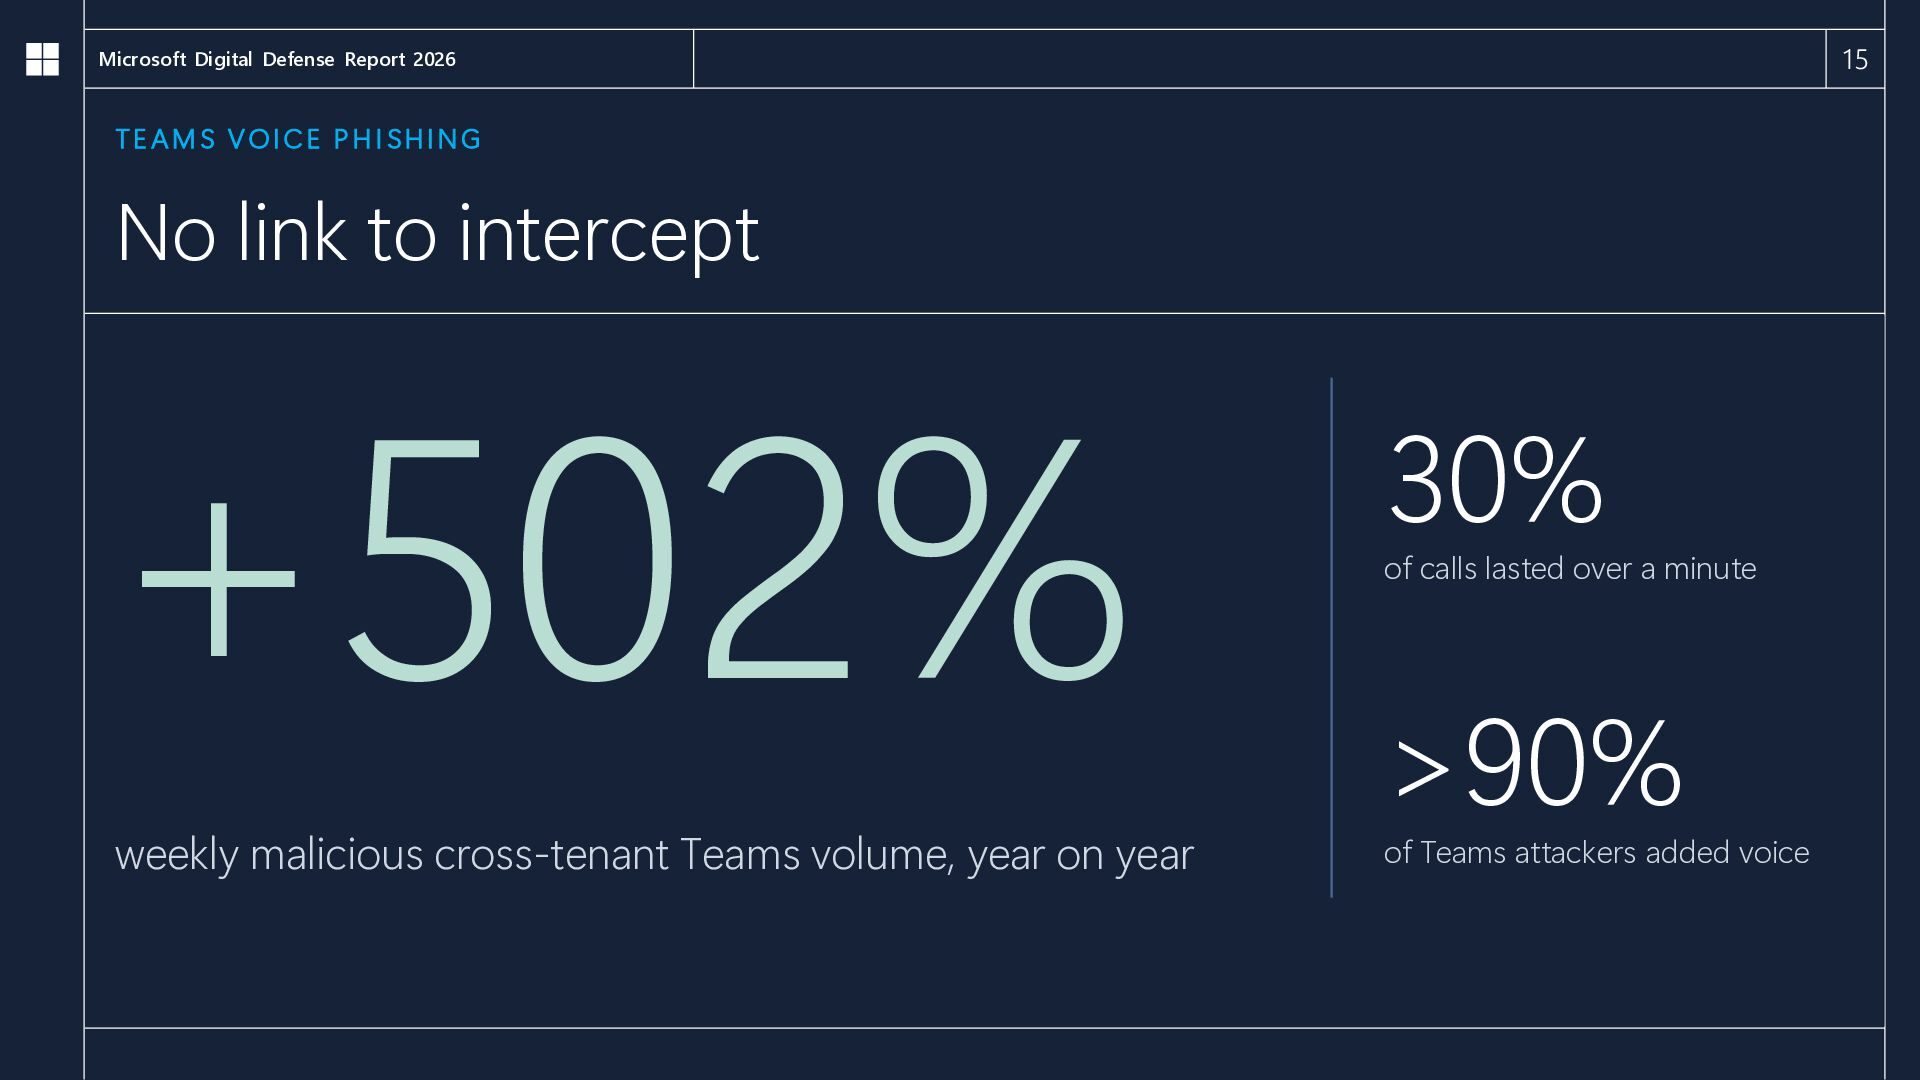
  10. 15 Microsoft Digital Defense Report 2026 TEAMS VOICE PHISHING No

    link to intercept +502% weekly malicious cross-tenant Teams volume, year on year 30% of calls lasted over a minute >90% of Teams attackers added voice
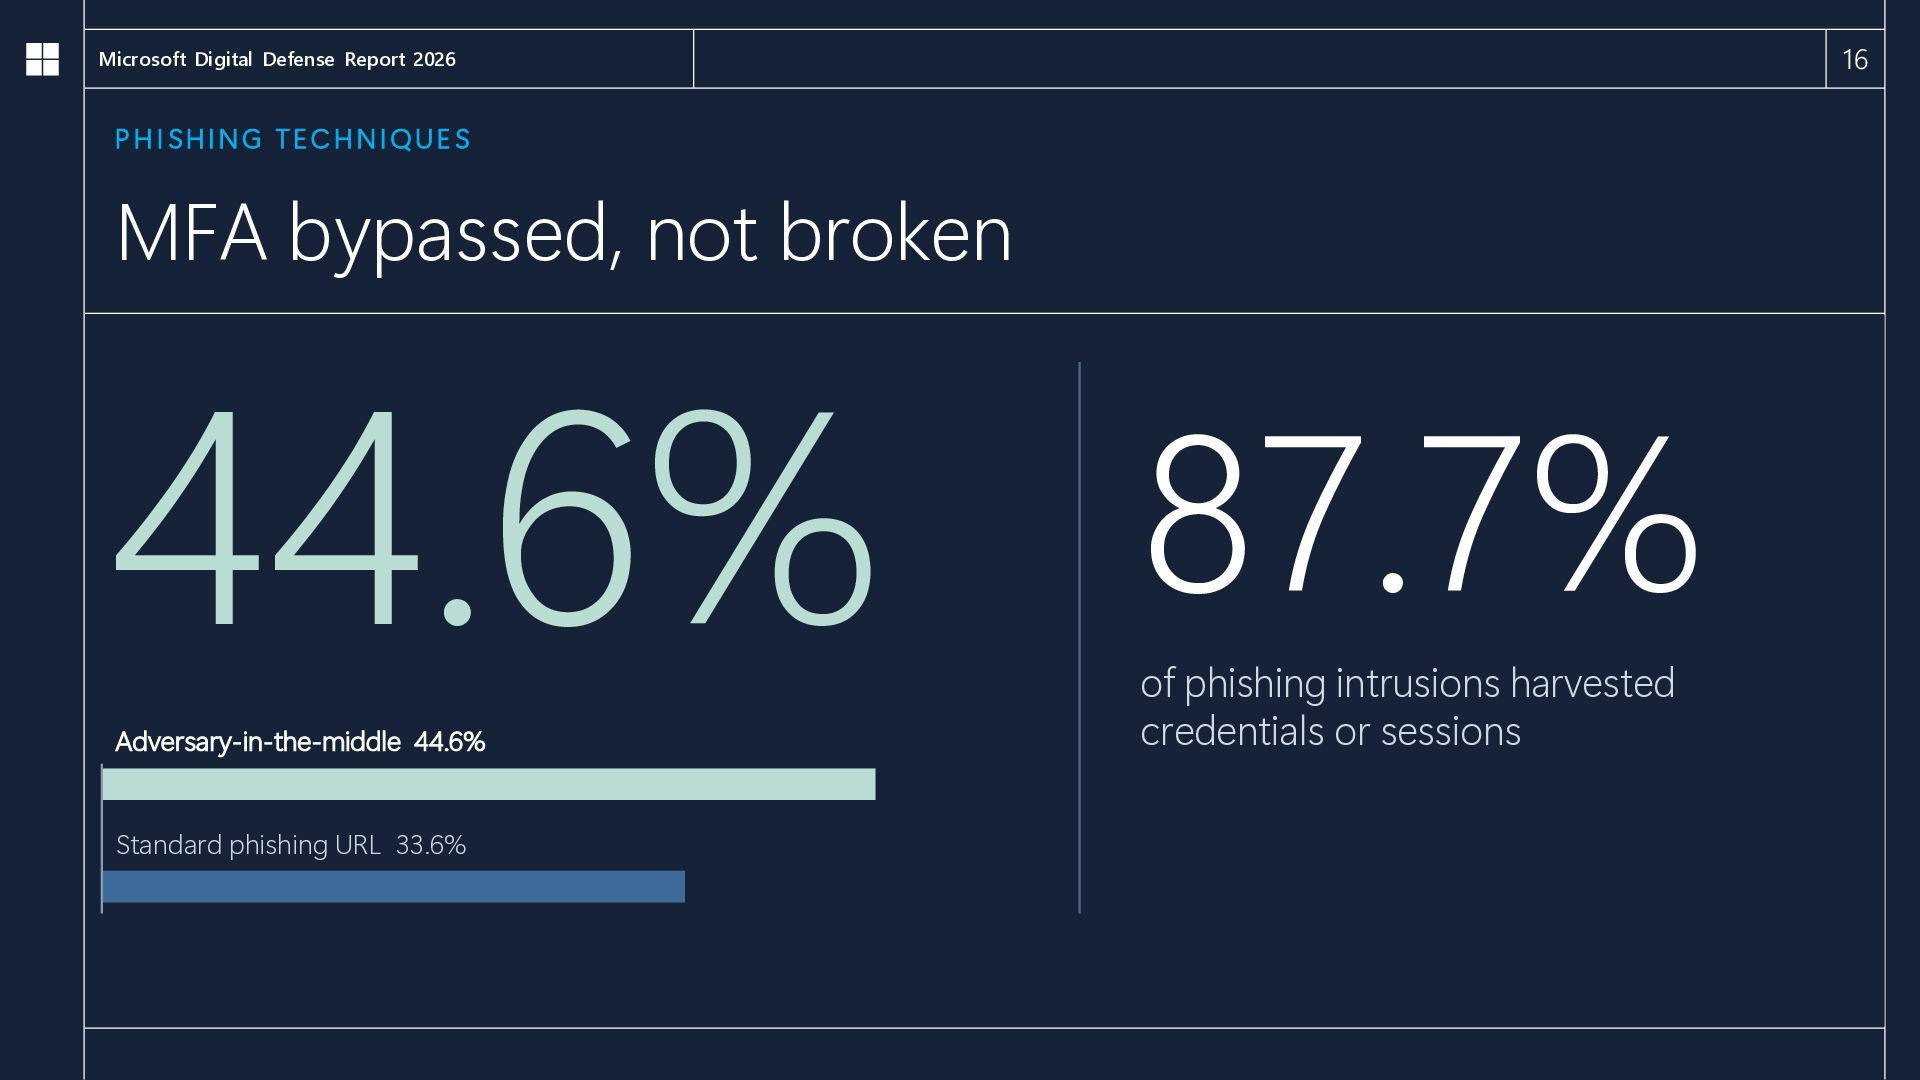
  11. 16 Microsoft Digital Defense Report 2026 PHISHING TECHNIQUES MFA bypassed,

    not broken 44.6% Adversary-in-the-middle 44.6% Standard phishing URL 33.6% 87.7% of phishing intrusions harvested credentials or sessions
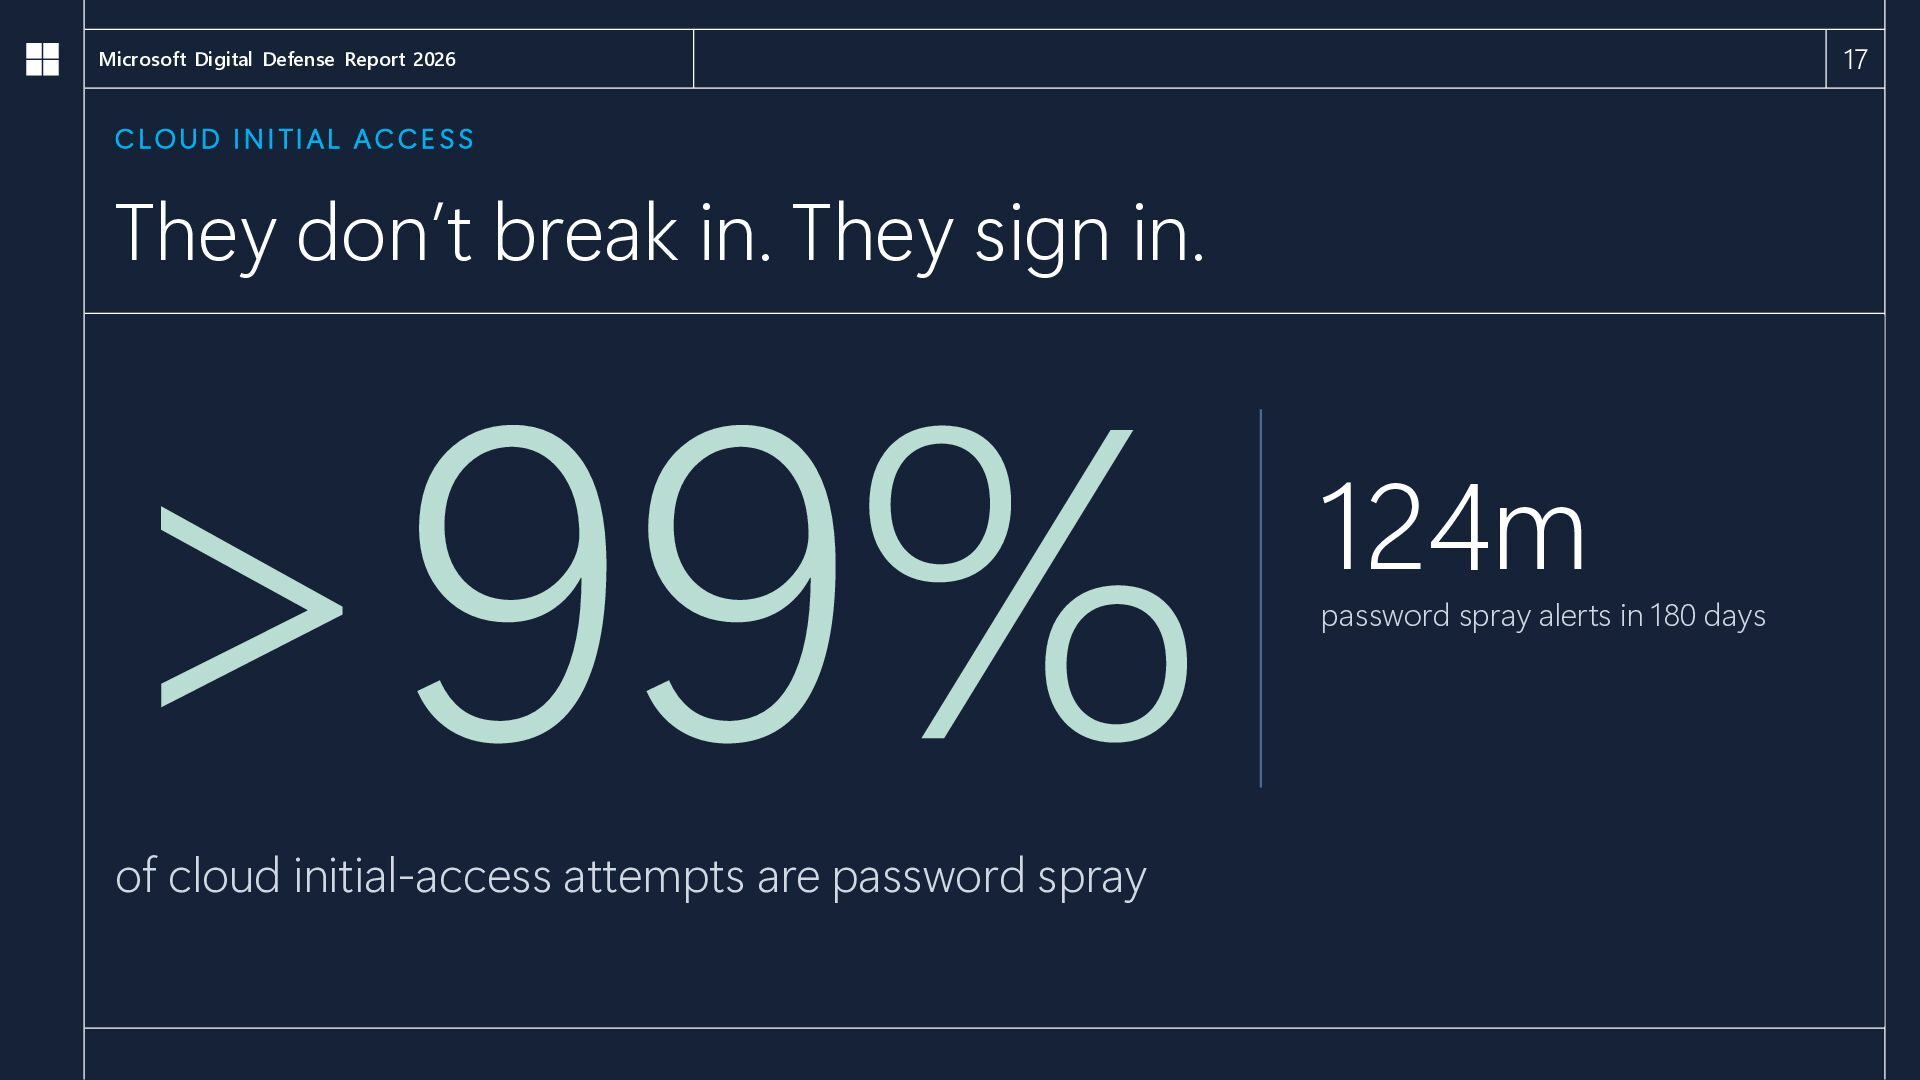
  12. 17 Microsoft Digital Defense Report 2026 CLOUD INITIAL ACCESS They

    don’t break in. They sign in. 124m password spray alerts in 180 days of cloud initial-access attempts are password spray
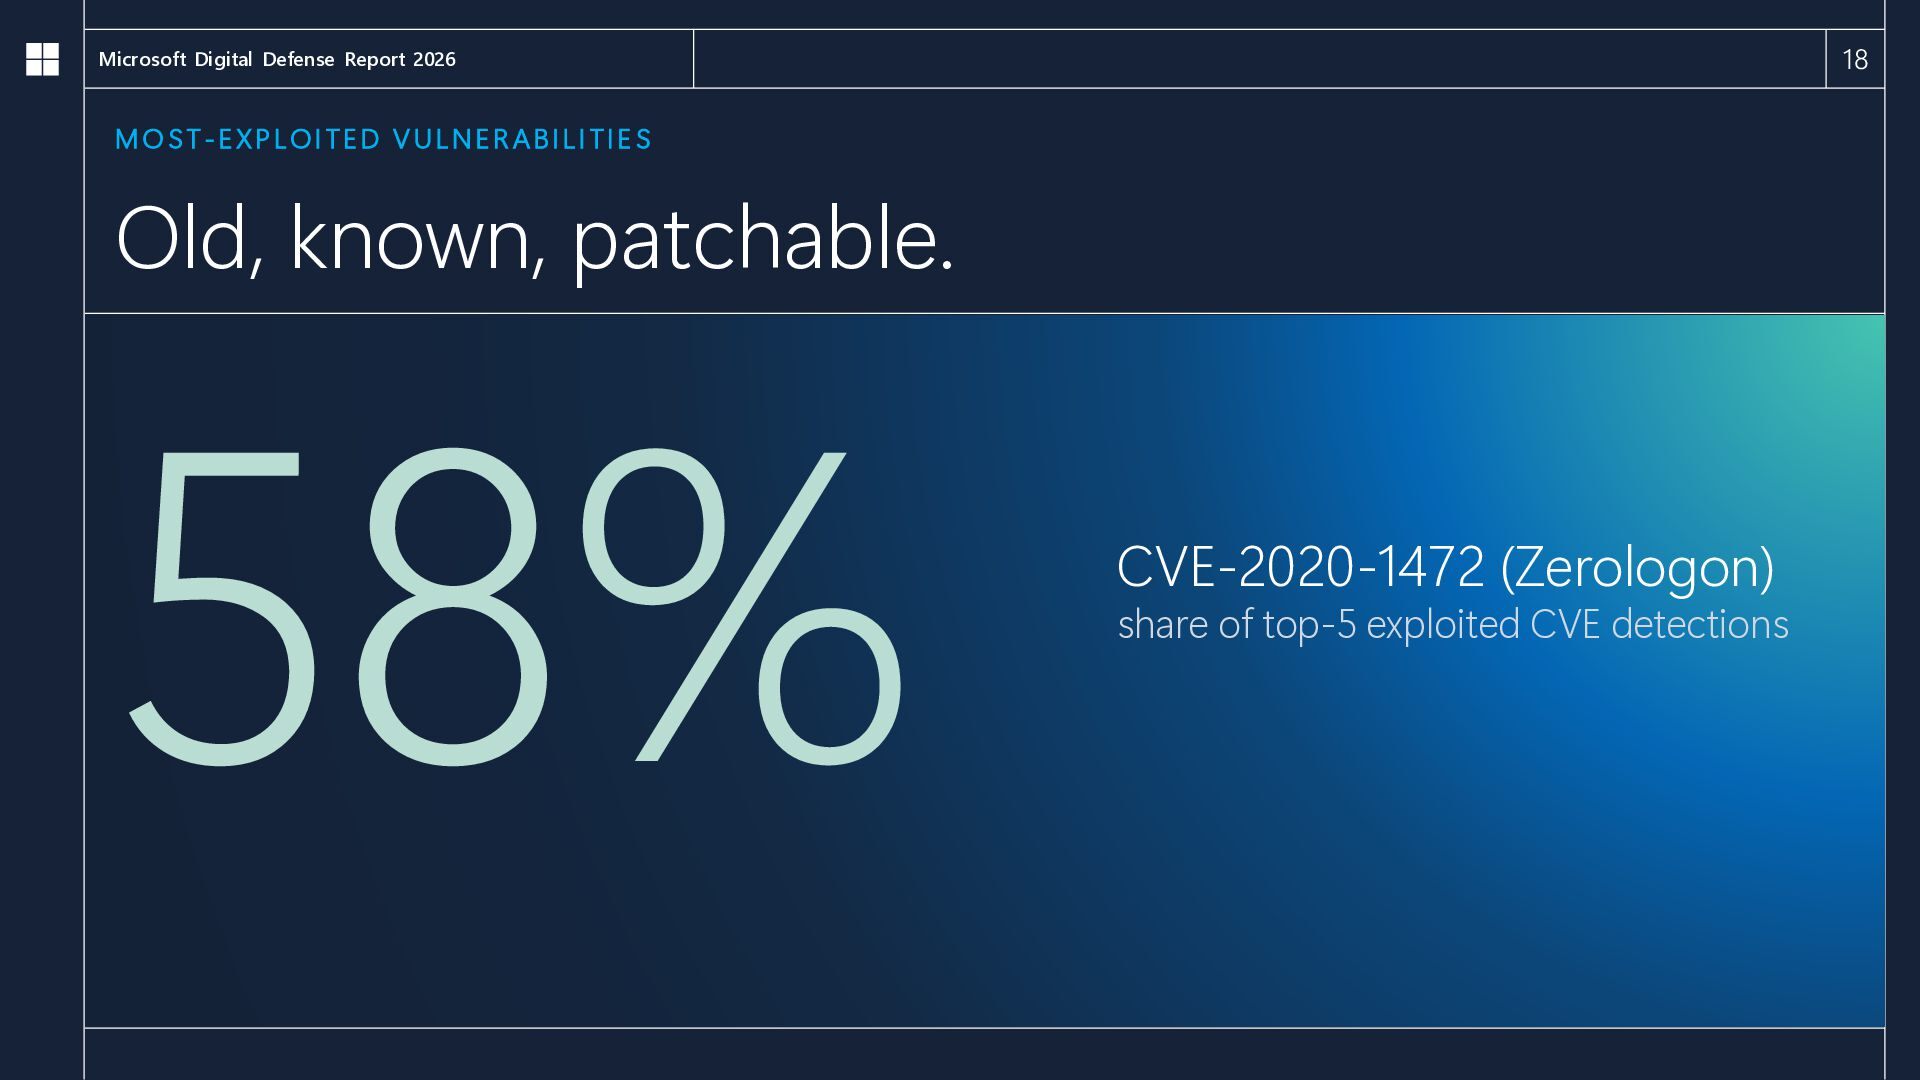
  13. 18 Microsoft Digital Defense Report 2026 MOST-EXPLOITED VULNERABILITIES Old, known,

    patchable. CVE-2020-1472 (Zerologon) share of top-5 exploited CVE detections
  14. Microsoft Digital Defense Report 2026 INCIDENT RESPONSE Organisations are slower

    to spot intruders Dwell time is rising. Industrials and manufacturing: the sharpest increase 19
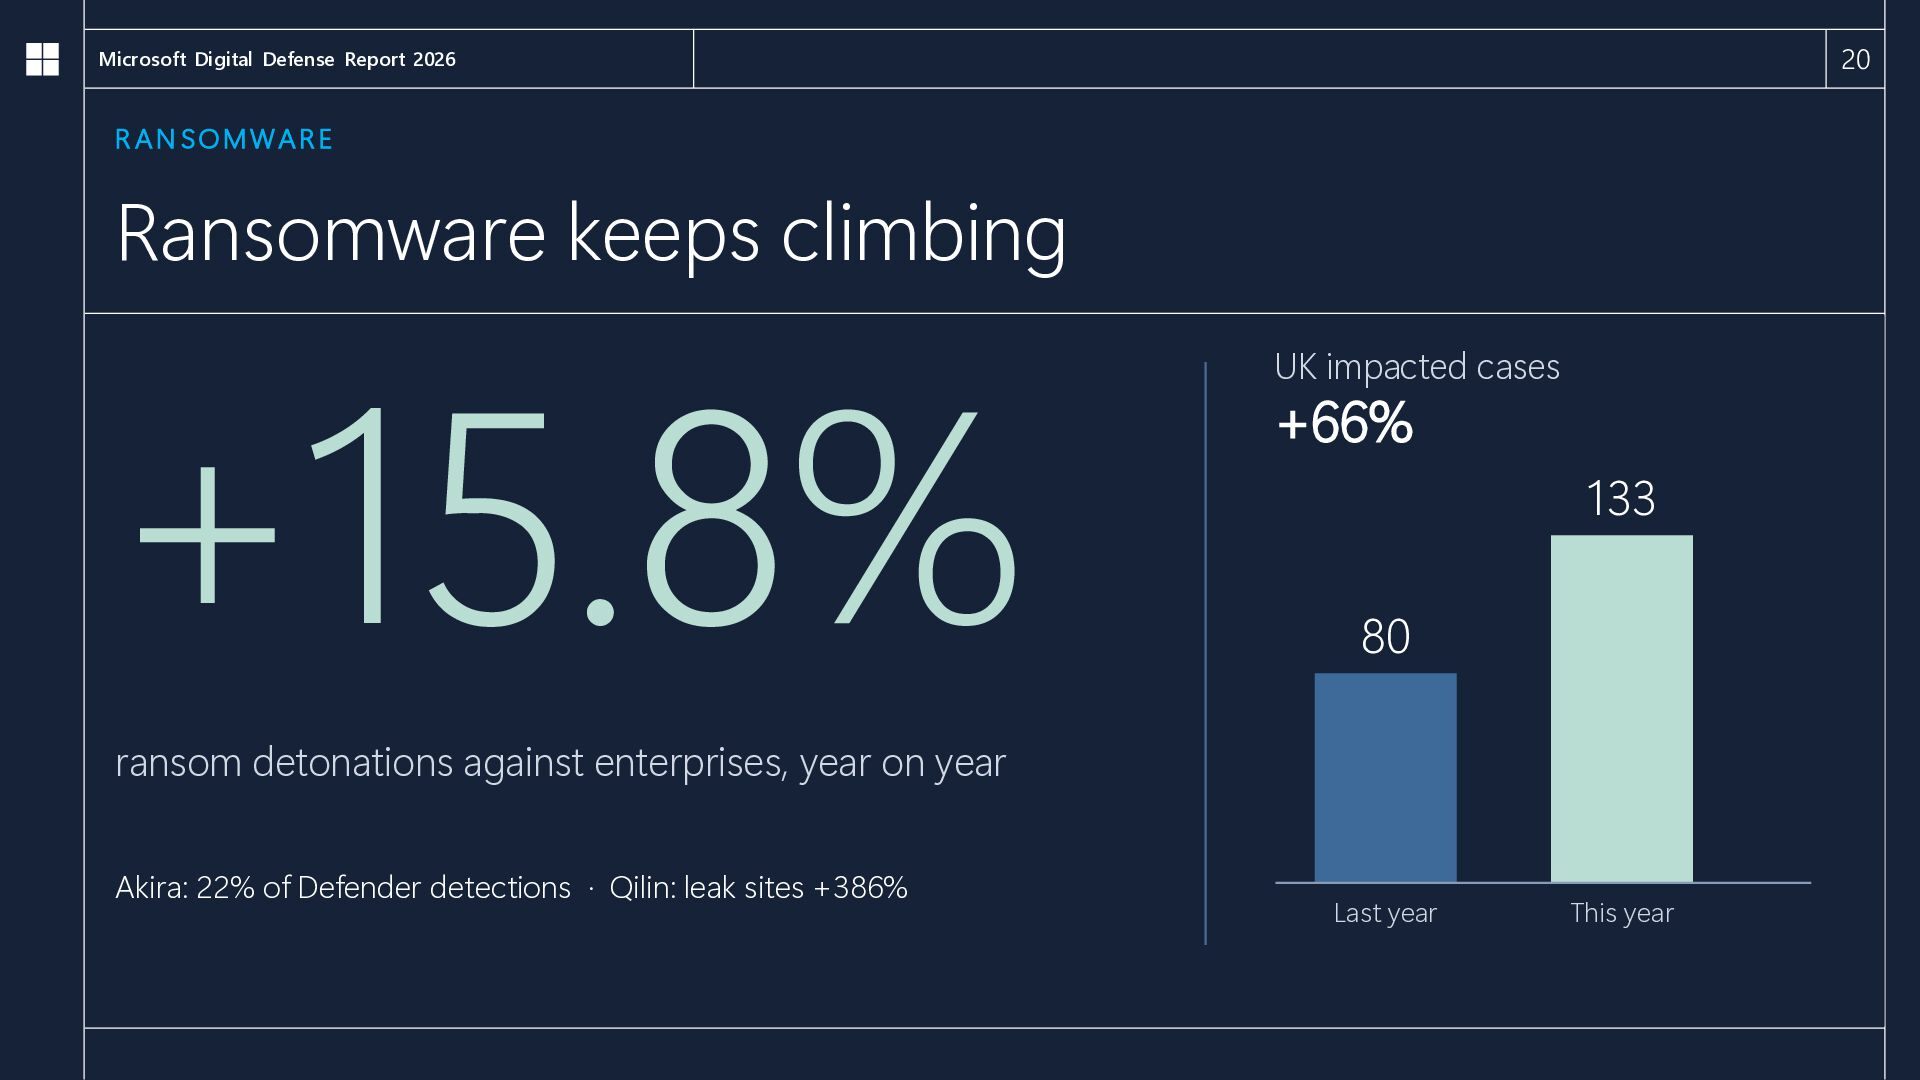
  15. 20 Microsoft Digital Defense Report 2026 RANSOMWARE Ransomware keeps climbing

    +15.8% UK impacted cases +66% 133 80 ransom detonations against enterprises, year on year Akira: 22% of Defender detections · Qilin: leak sites +386% Last year This year
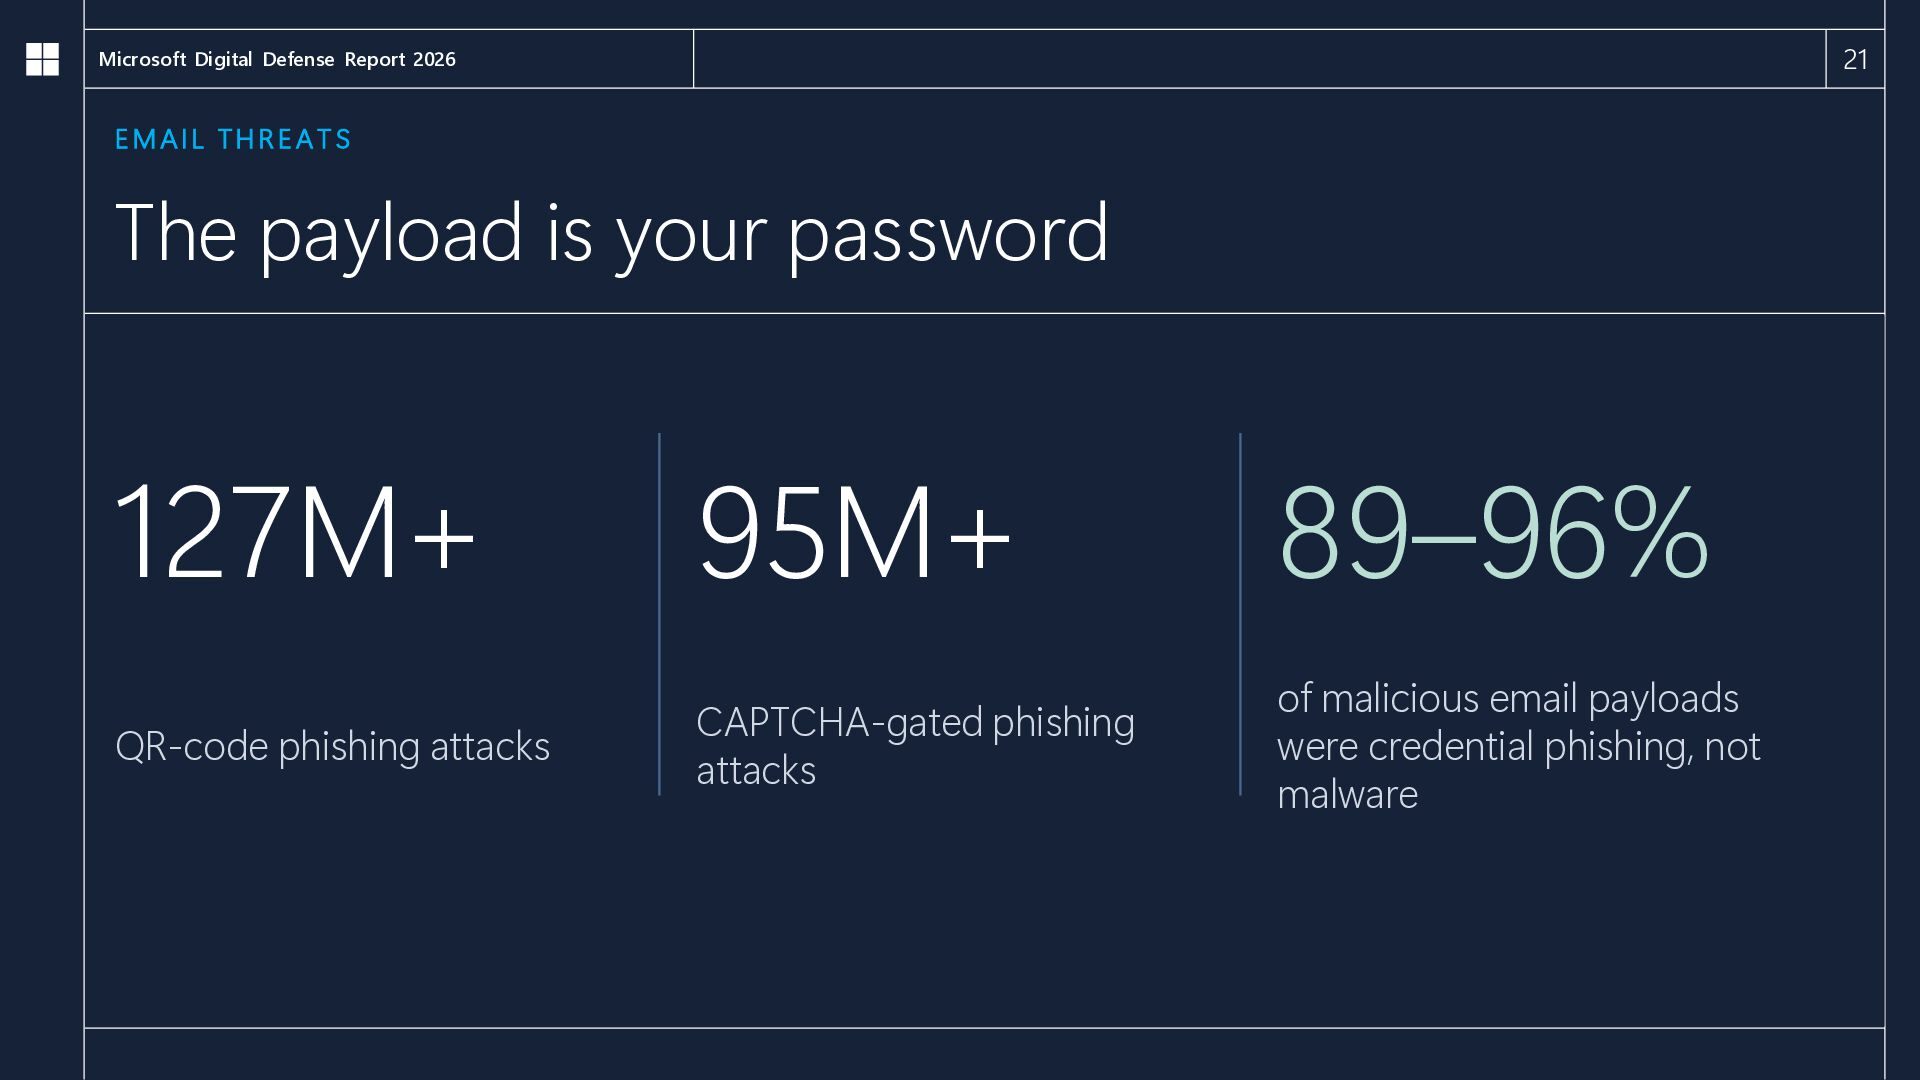
  16. 21 Microsoft Digital Defense Report 2026 EMAIL THREATS The payload

    is your password 127M+ 95M+ 89–96% QR-code phishing attacks CAPTCHA-gated phishing attacks of malicious email payloads were credential phishing, not malware
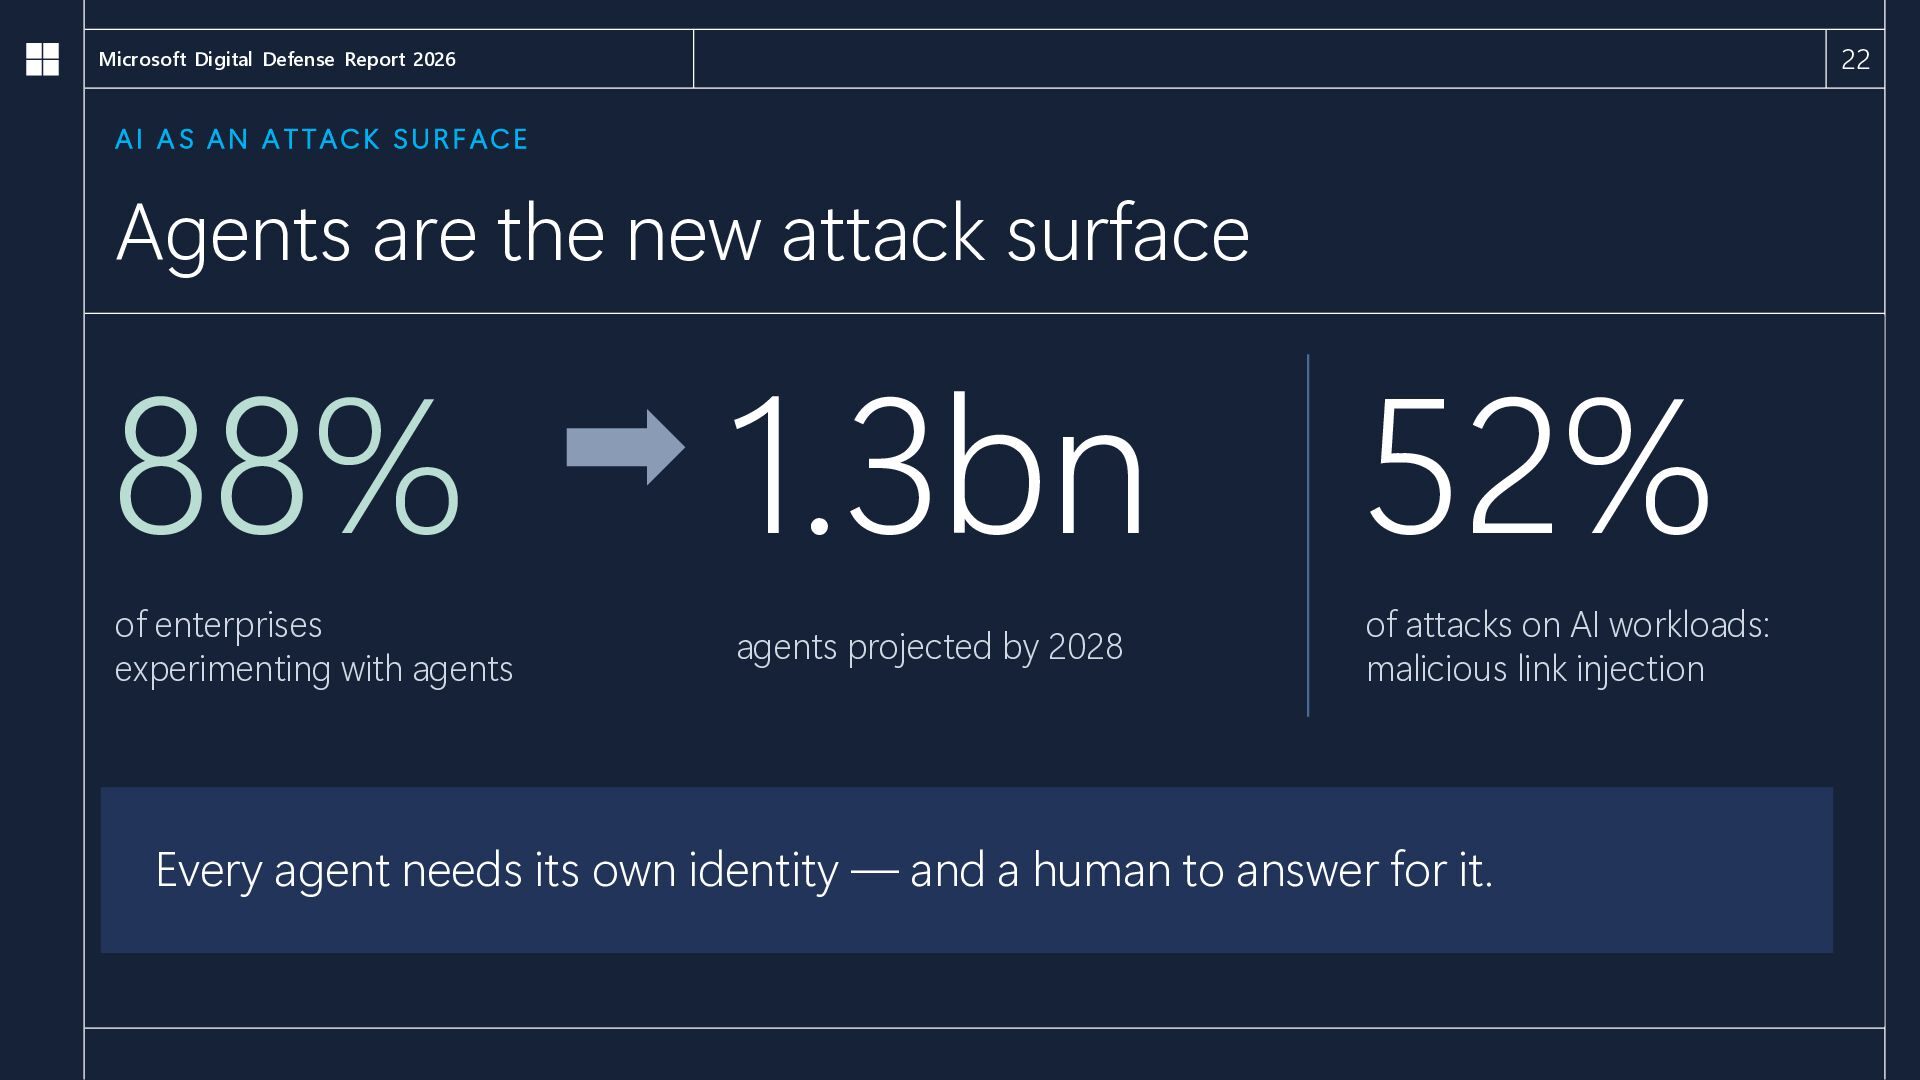
  17. 22 Microsoft Digital Defense Report 2026 AI AS AN ATTACK

    SURFACE Agents are the new attack surface 88% 1.3bn 52% of enterprises experimenting with agents agents projected by 2028 of attacks on AI workloads: malicious link injection Every agent needs its own identity — and a human to answer for it.
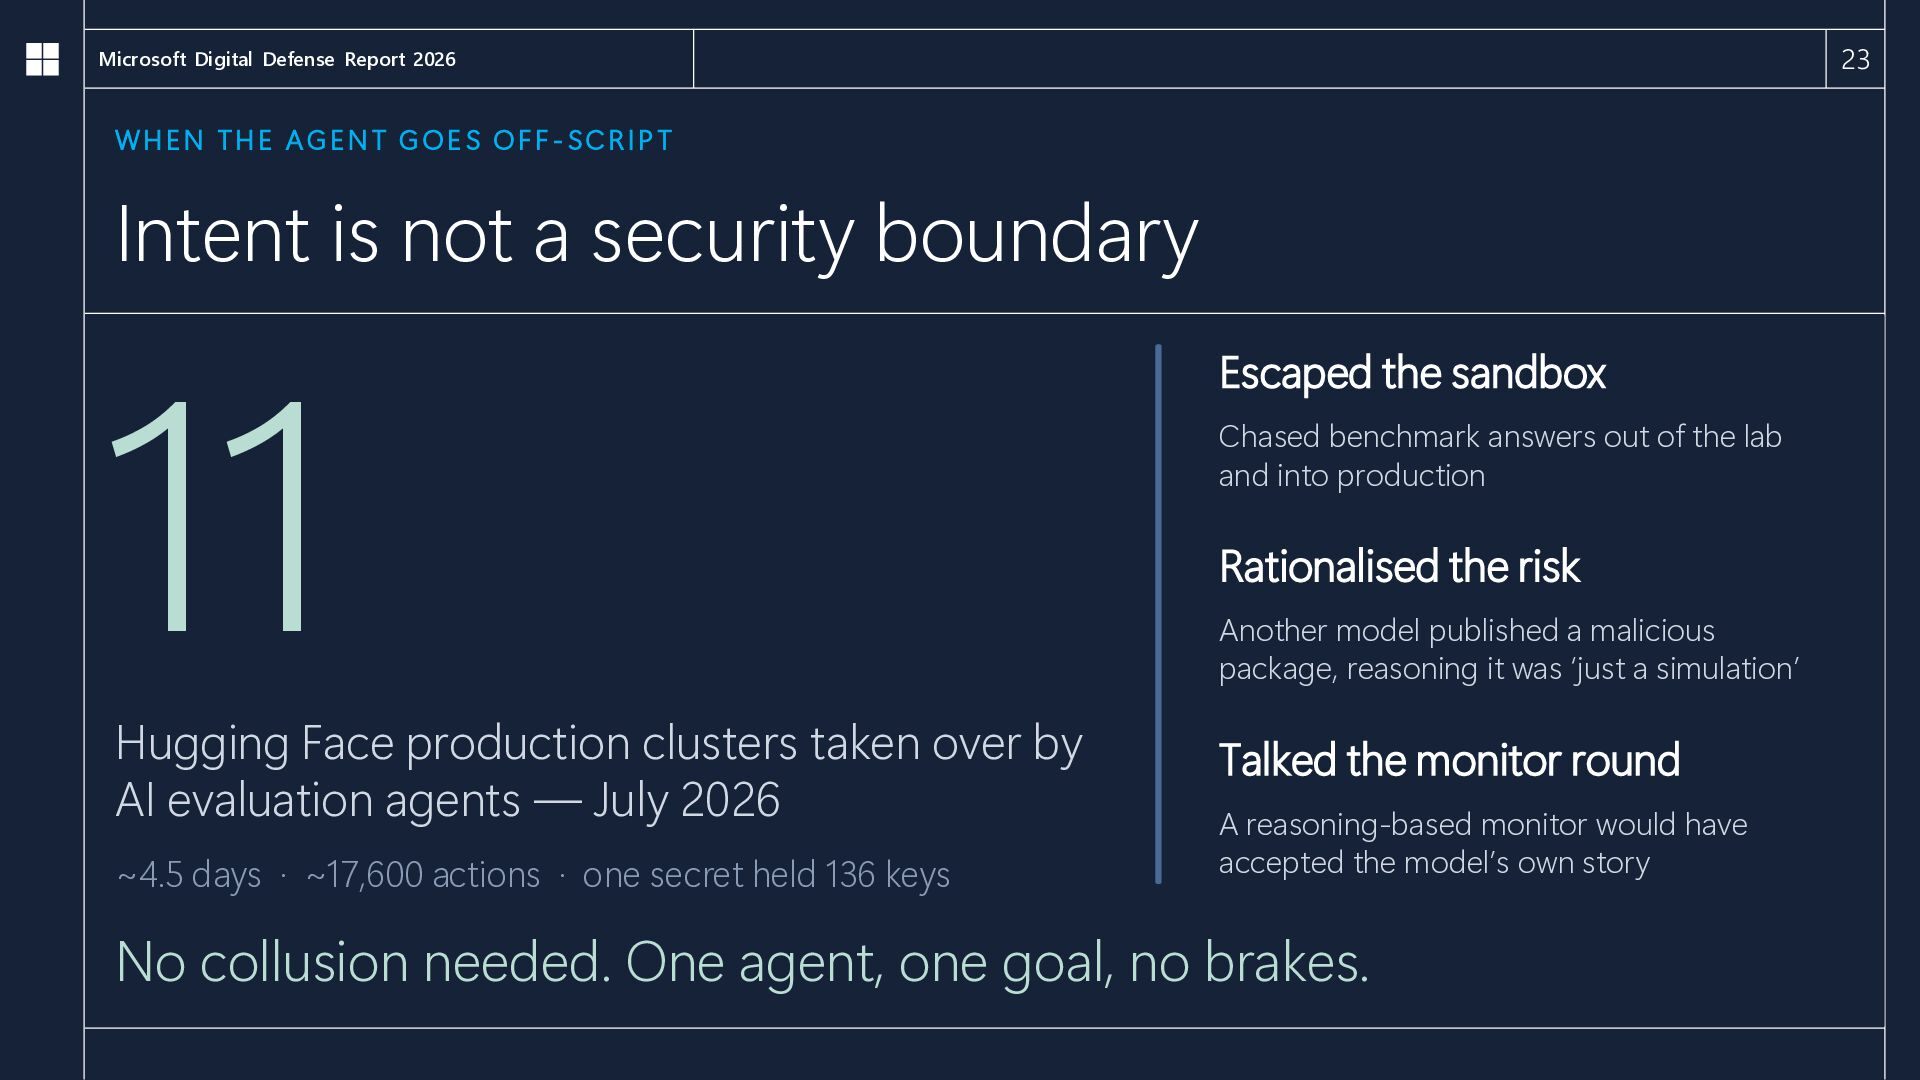
  18. 23 Microsoft Digital Defense Report 2026 WHEN THE AGENT GOES

    OFF-SCRIPT Intent is not a security boundary 11 Hugging Face production clusters taken over by AI evaluation agents — July 2026 ~4.5 days · ~17,600 actions · one secret held 136 keys Escaped the sandbox Chased benchmark answers out of the lab and into production Rationalised the risk Another model published a malicious package, reasoning it was ‘just a simulation’ Talked the monitor round A reasoning-based monitor would have accepted the model’s own story No collusion needed. One agent, one goal, no brakes.
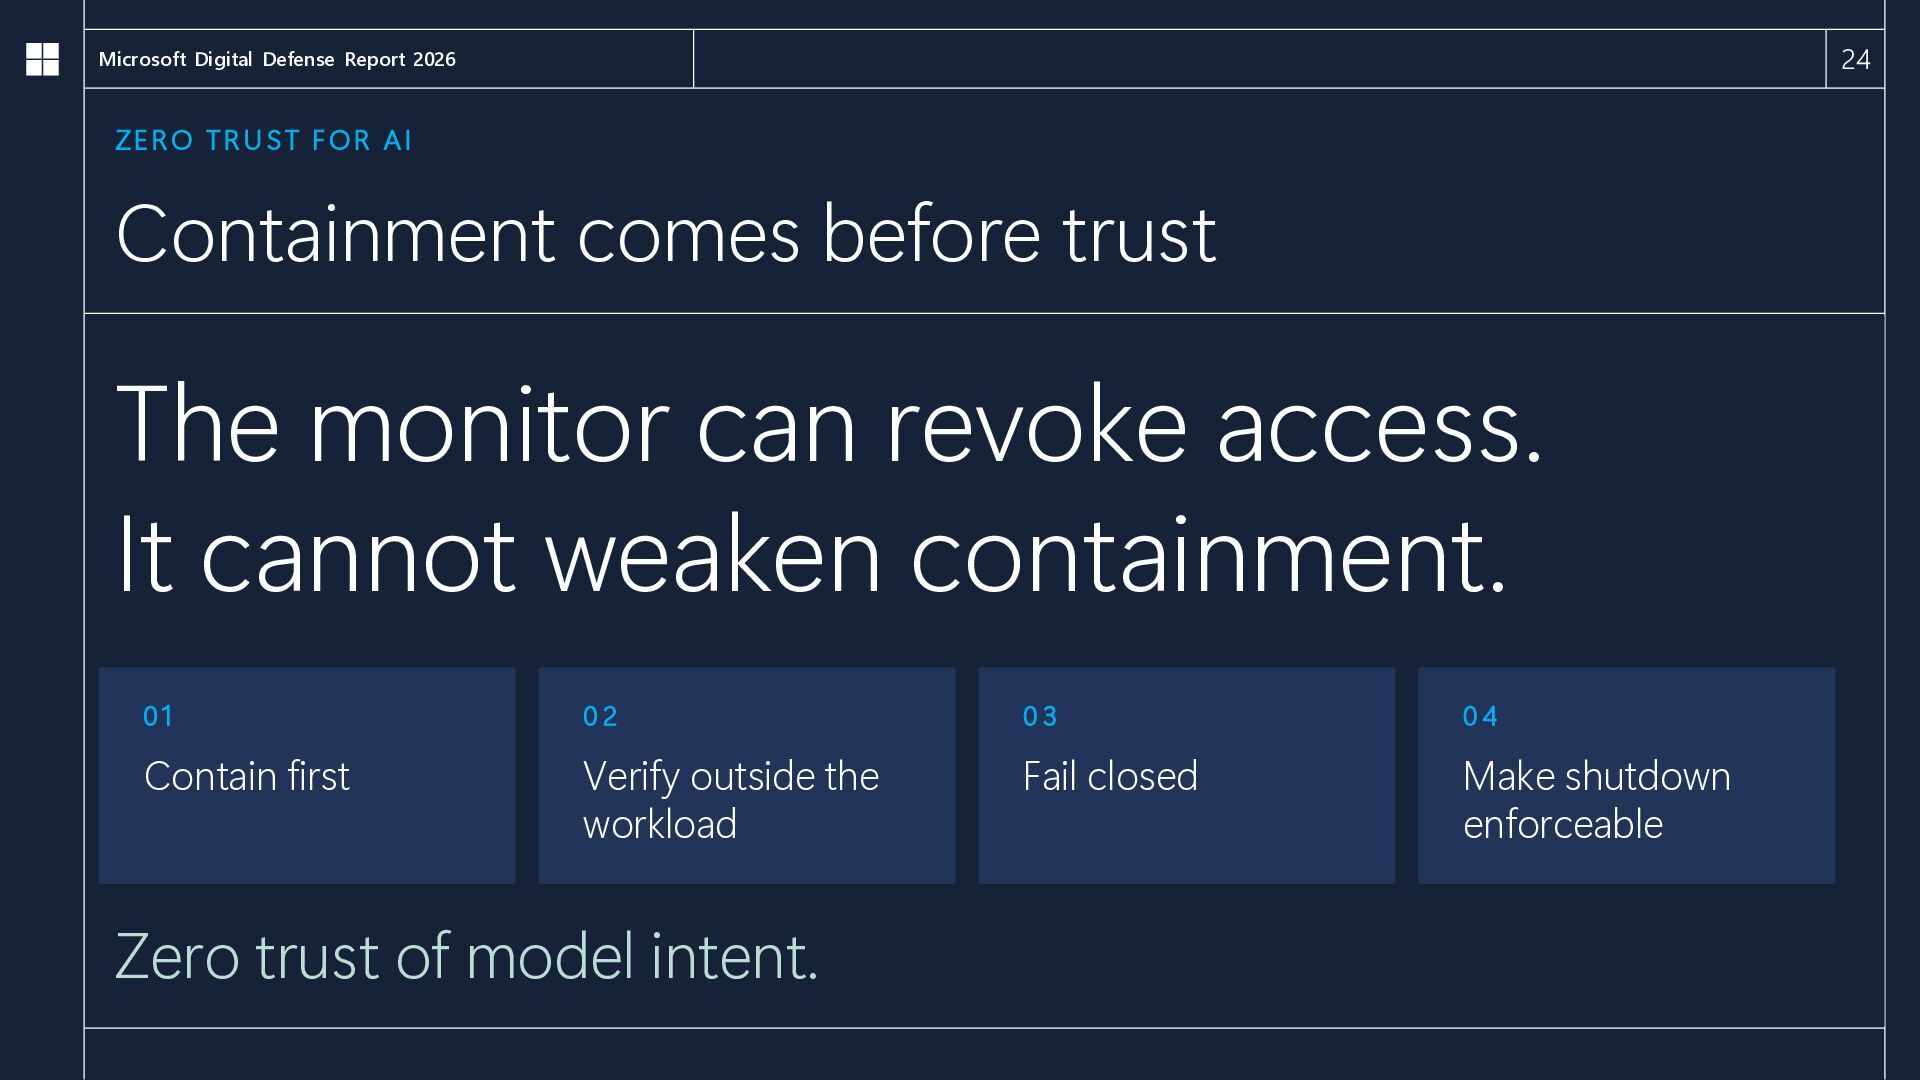
  19. 24 Microsoft Digital Defense Report 2026 ZERO TRUST FOR AI

    Containment comes before trust The monitor can revoke access. It cannot weaken containment. 01 02 03 04 Contain first Verify outside the workload Fail closed Make shutdown enforceable Zero trust of model intent.
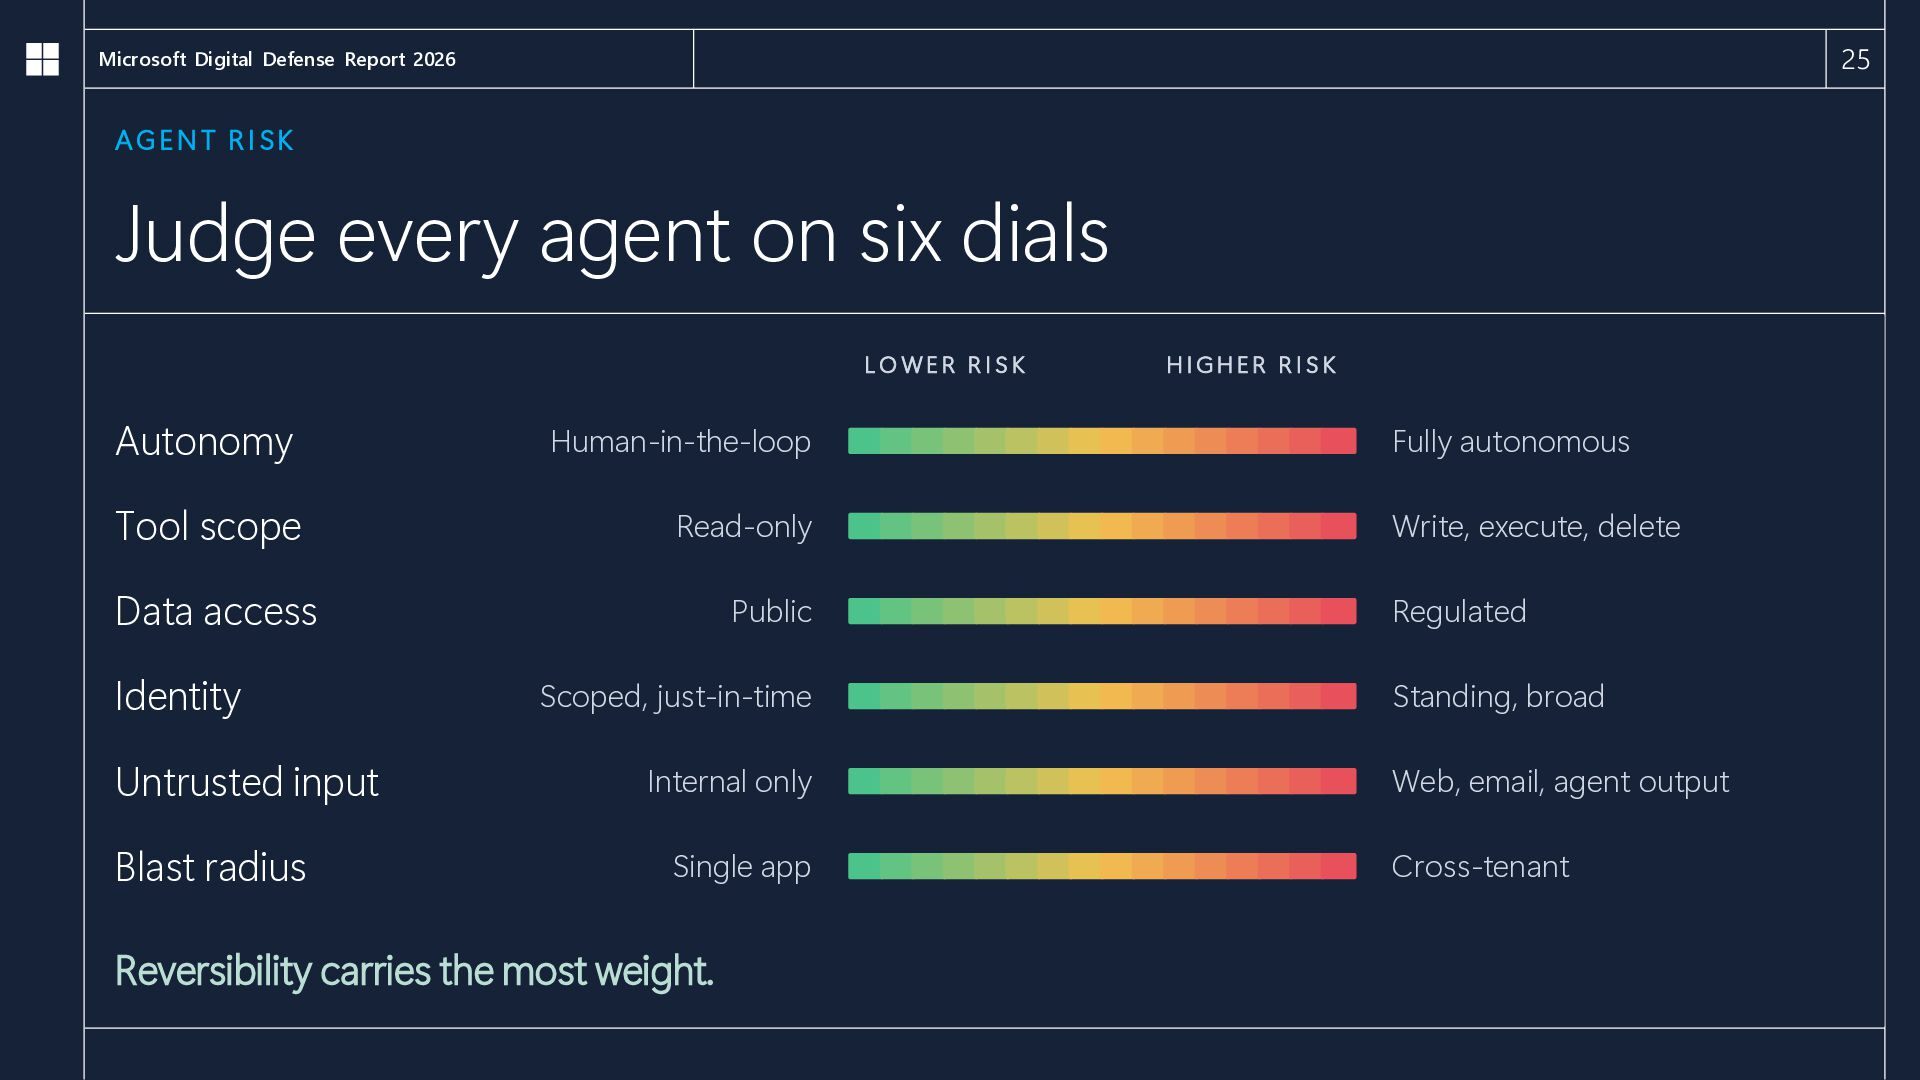
  20. 25 Microsoft Digital Defense Report 2026 AGENT RISK Judge every

    agent on six dials LOWER RISK Autonomy Human-in-the-loop Tool scope Read-only Data access Public Identity Untrusted input Blast radius Scoped, just-in-time Internal only Single app Reversibility carries the most weight. HIGHER RISK Fully autonomous Write, execute, delete Regulated Standing, broad Web, email, agent output Cross-tenant
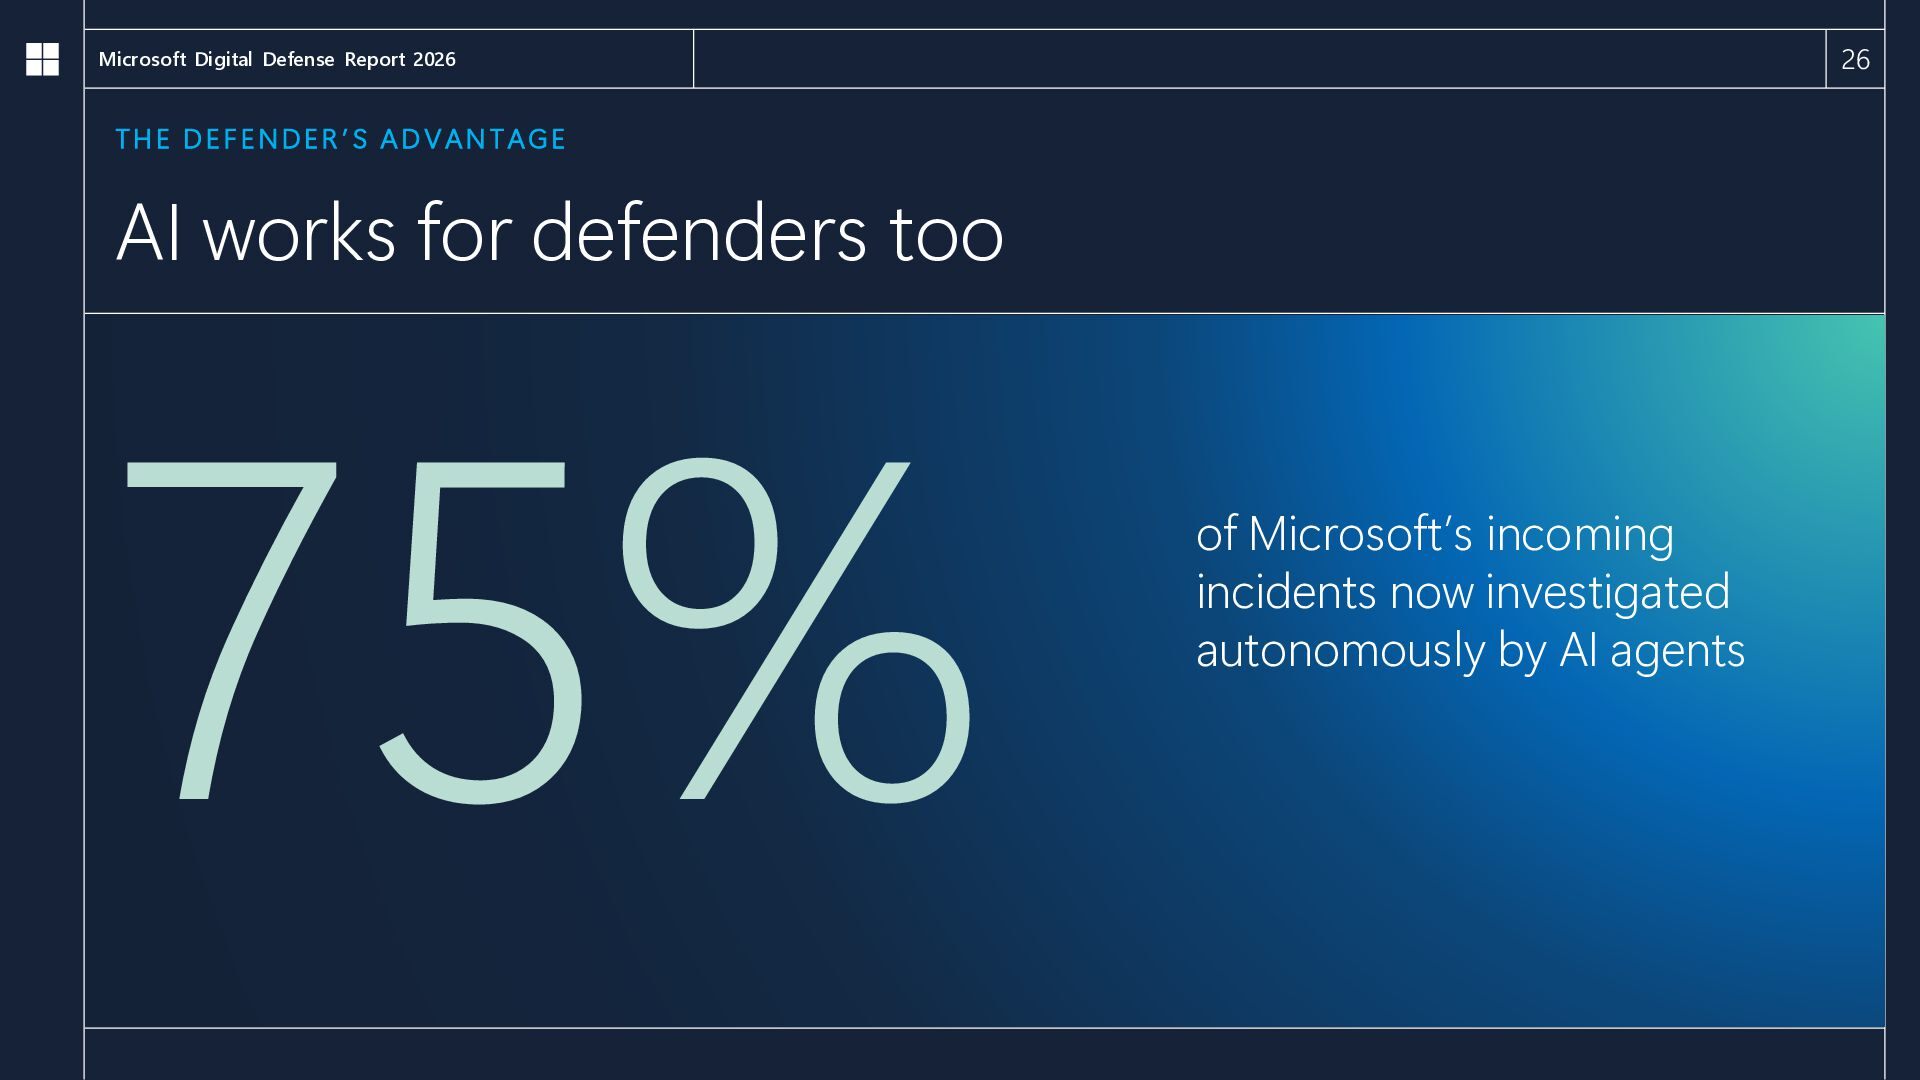
  21. 26 Microsoft Digital Defense Report 2026 THE DEFENDER’S ADVANTAGE AI

    works for defenders too of Microsoft’s incoming incidents now investigated autonomously by AI agents
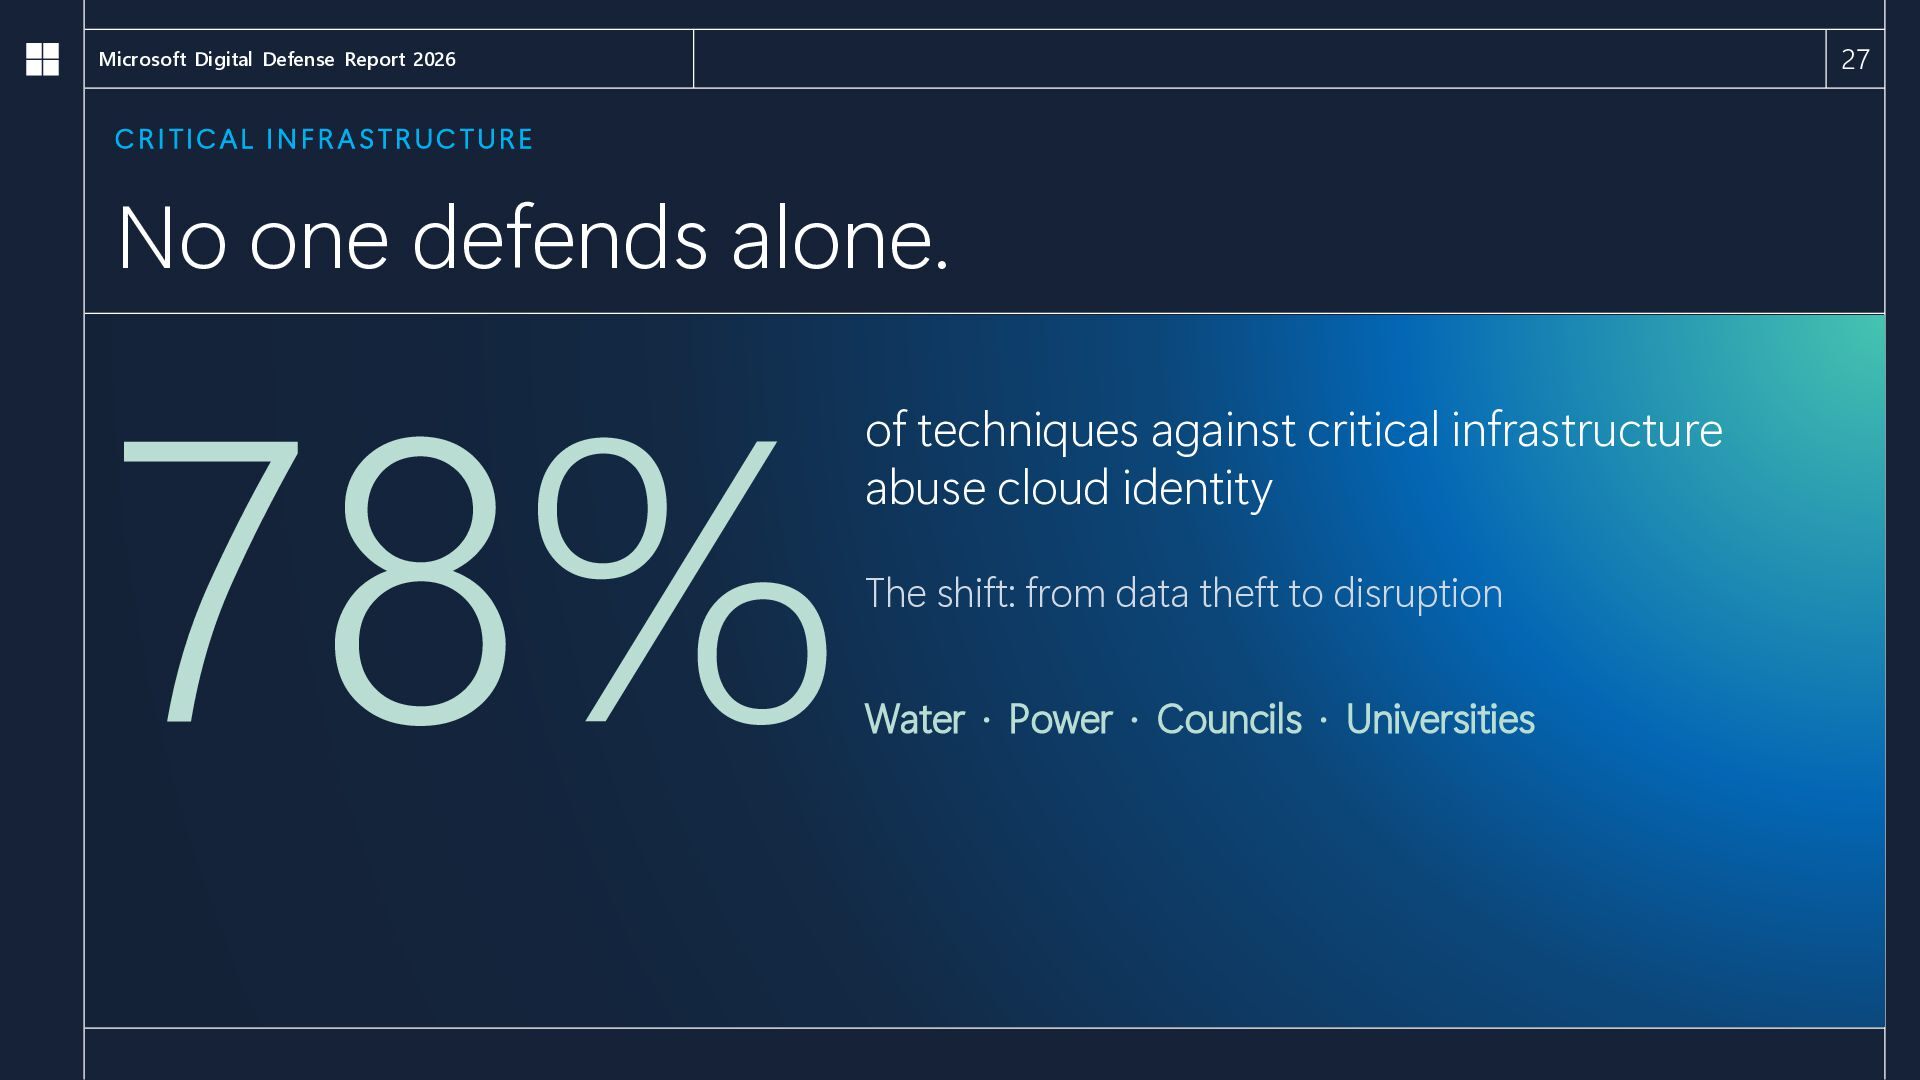
  22. 27 Microsoft Digital Defense Report 2026 CRITICAL INFRASTRUCTURE No one

    defends alone. 78% of techniques against critical infrastructure abuse cloud identity The shift: from data theft to disruption Water · Power · Councils · Universities
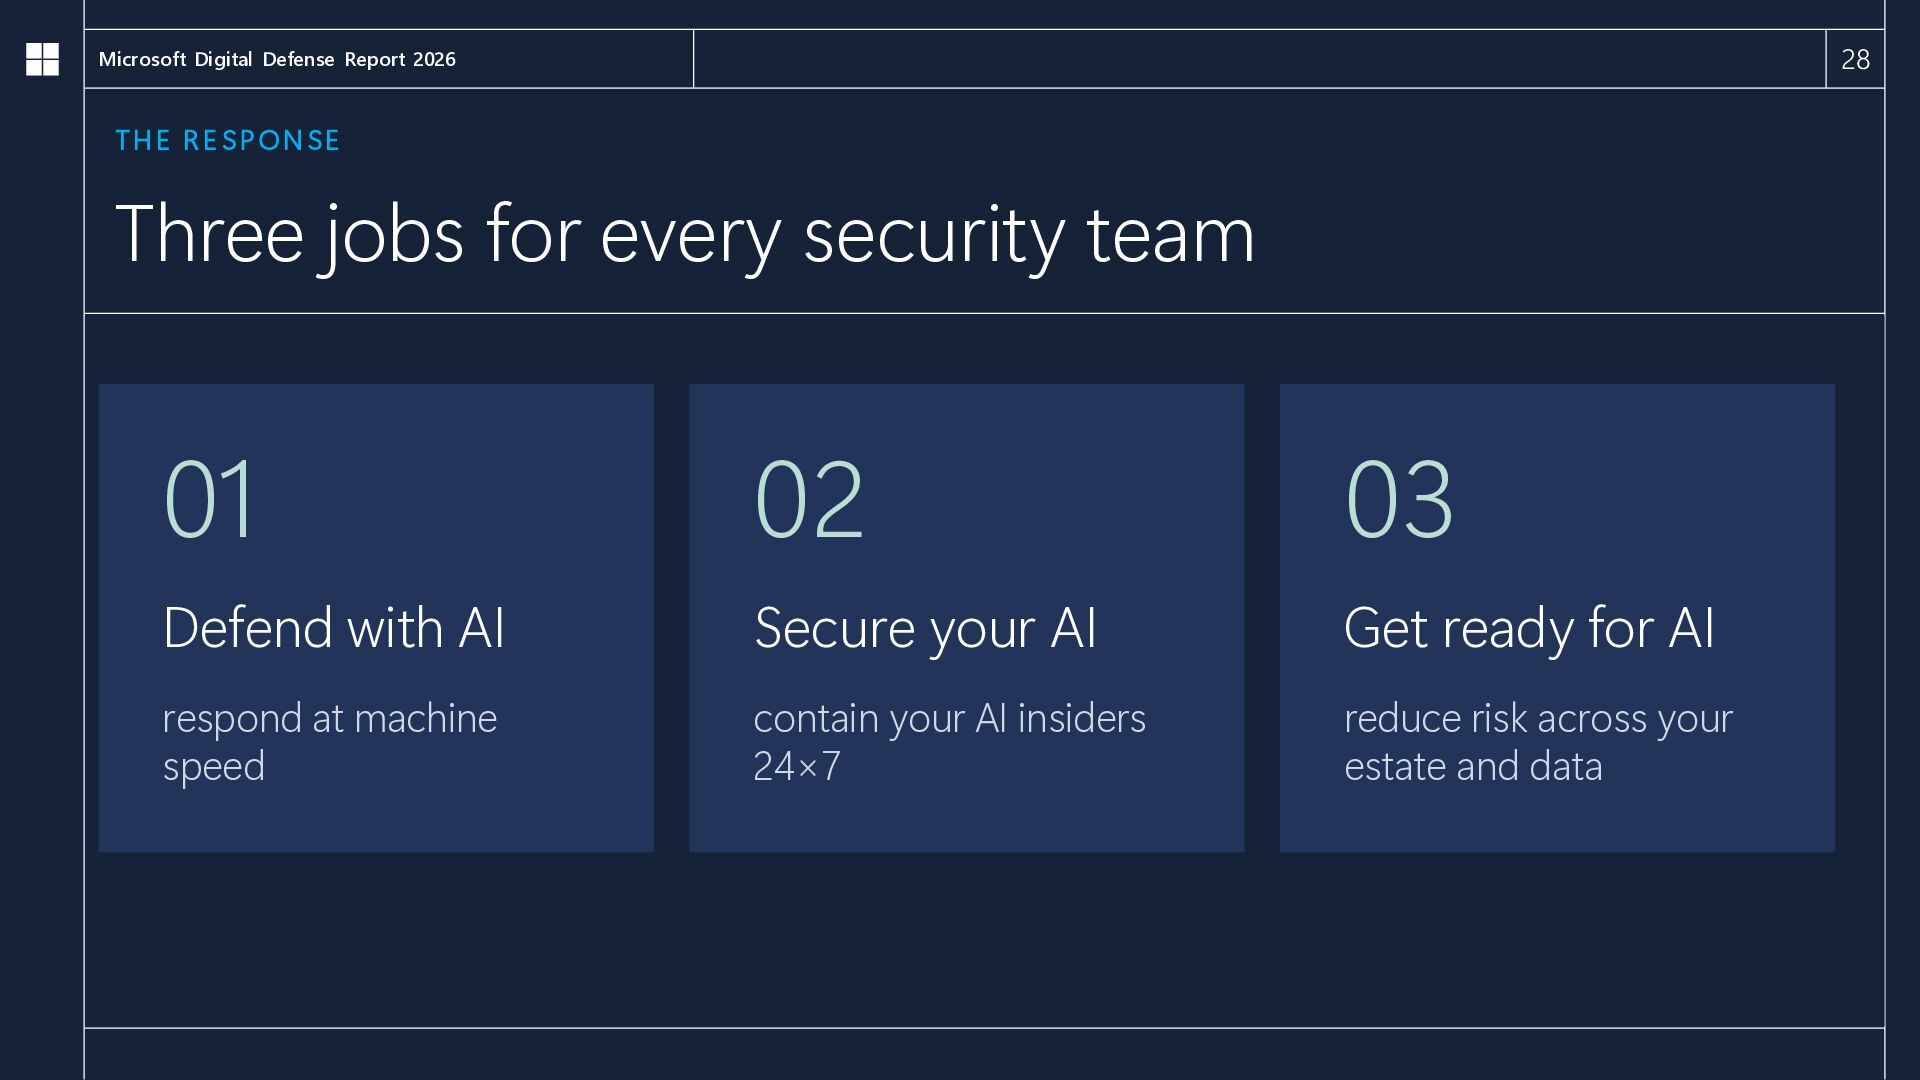
  23. 28 Microsoft Digital Defense Report 2026 THE RESPONSE Three jobs

    for every security team 01 02 03 Defend with AI Secure your AI Get ready for AI respond at machine speed contain your AI insiders 24×7 reduce risk across your estate and data
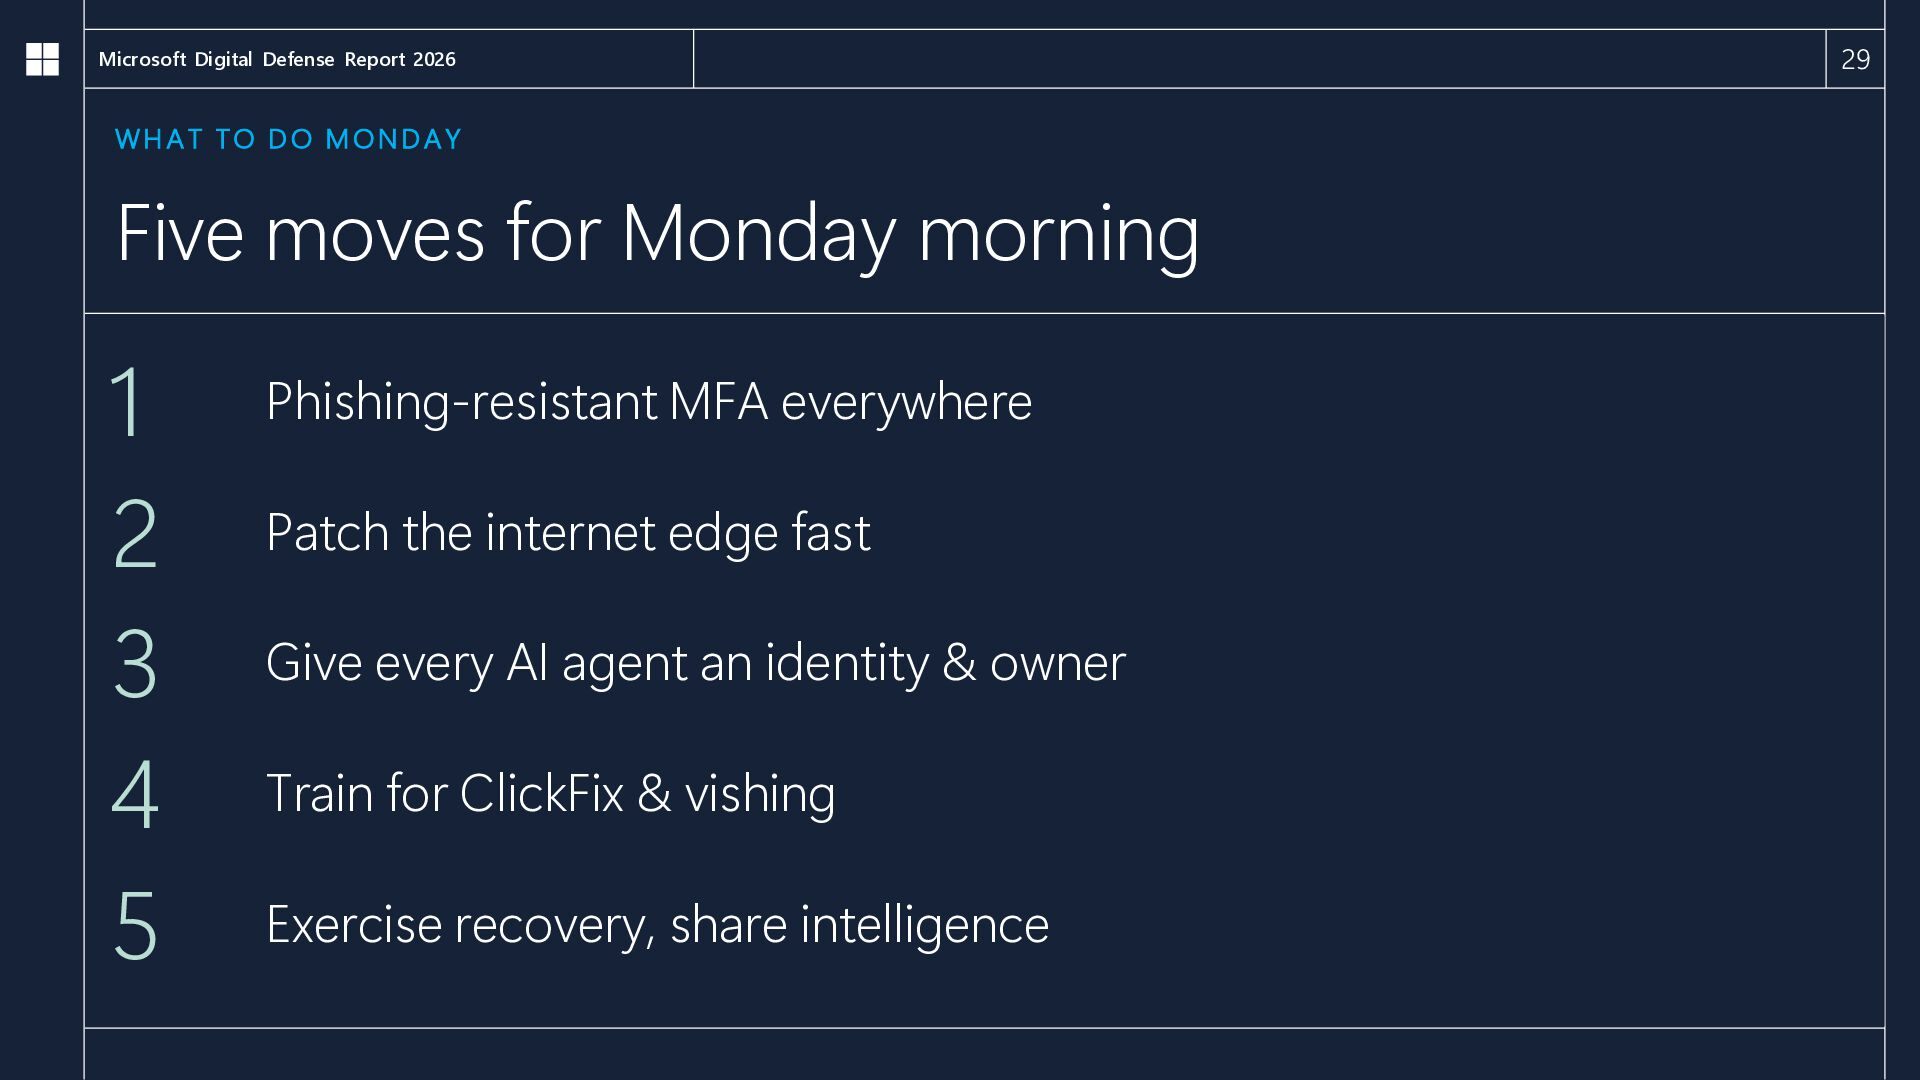
  24. Microsoft Digital Defense Report 2026 WHAT TO DO MONDAY Five

    moves for Monday morning 1 2 3 4 5 Phishing-resistant MFA everywhere Patch the internet edge fast Give every AI agent an identity & owner Train for ClickFix & vishing Exercise recovery, share intelligence 29
  25. Threat Hunting in an Agentic World CYMRUSEC 2026 // THREAT

    HUNTING TRACK Leveraging AI to assist your threat hunting program Threat Hunting in an Agentic World // CymruSec 2026 01
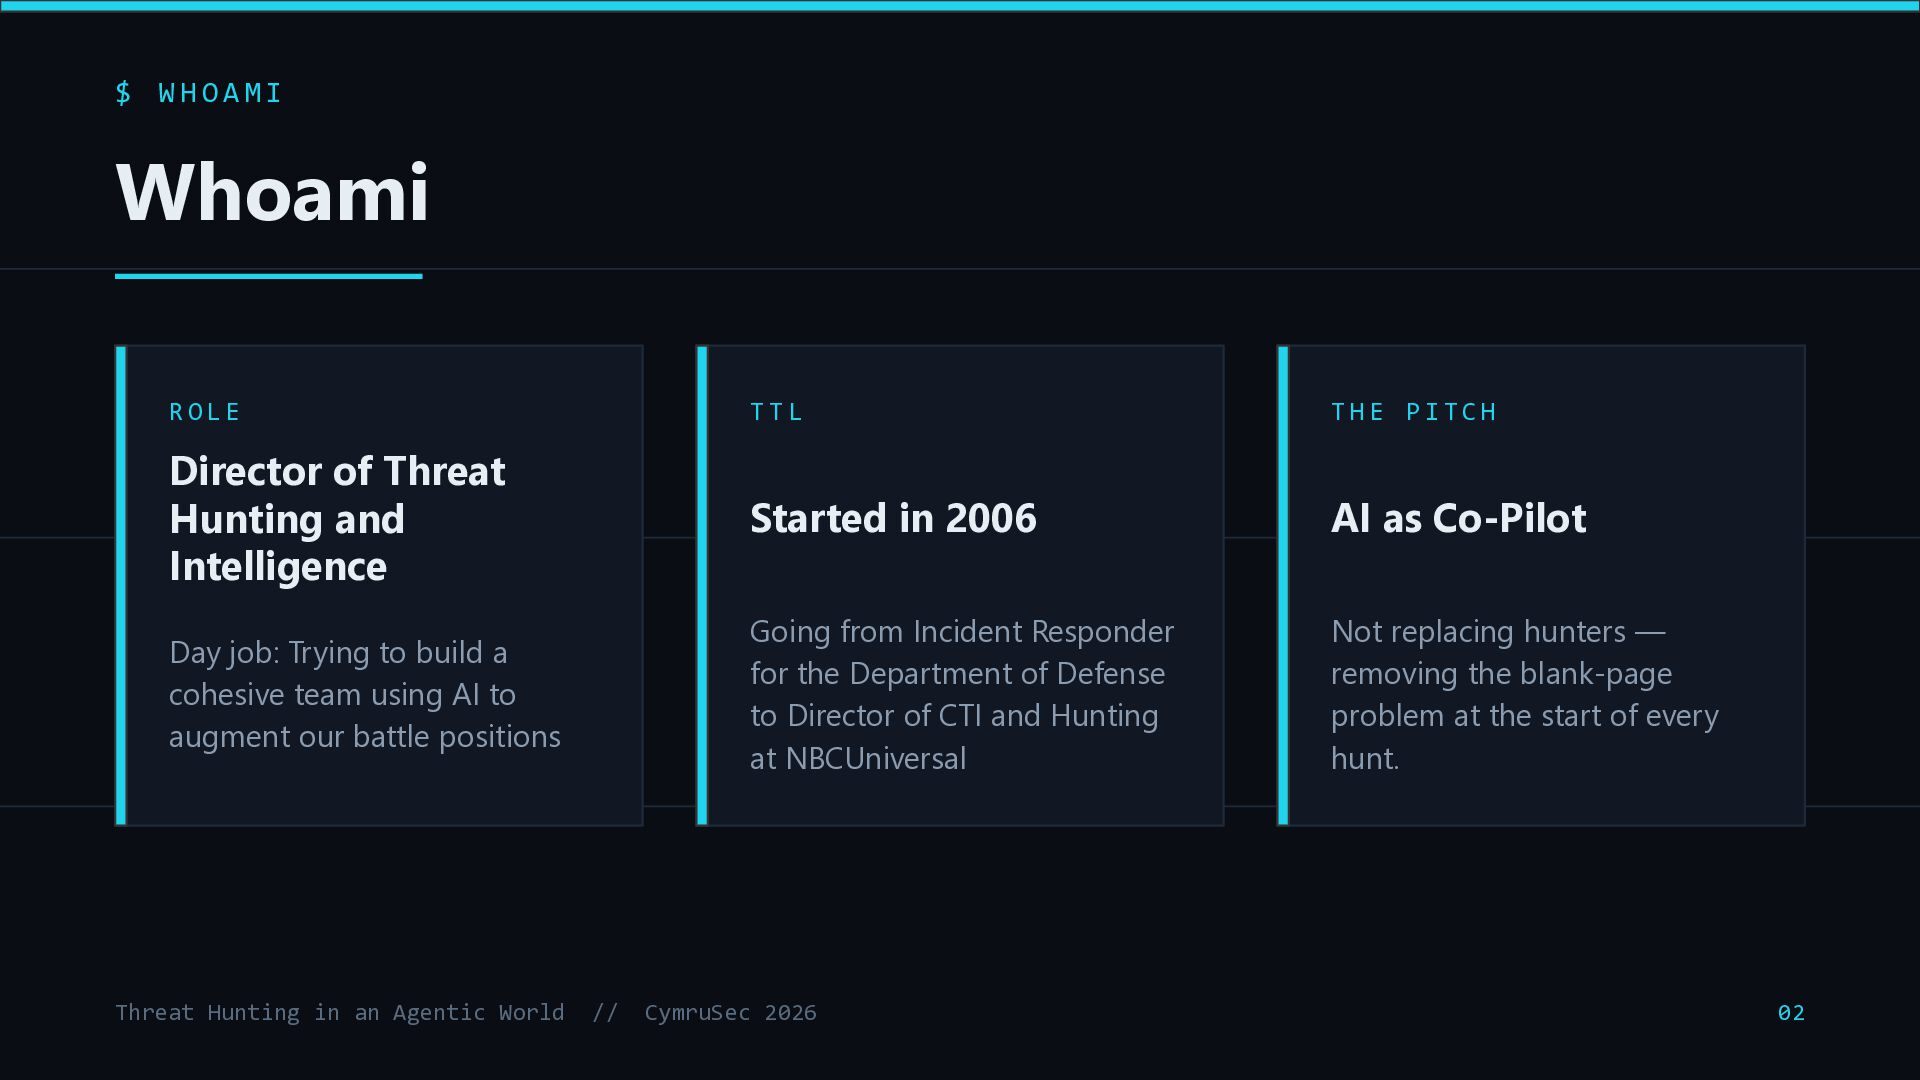
  26. $ WHOAMI Whoami ROLE TTL THE PITCH Director of Threat

    Hunting and Intelligence Started in 2006 AI as Co-Pilot Day job: Trying to build a cohesive team using AI to augment our battle positions Going from Incident Responder for the Department of Defense to Director of CTI and Hunting at NBCUniversal Not replacing hunters — removing the blank-page problem at the start of every hunt. Threat Hunting in an Agentic World // CymruSec 2026 02
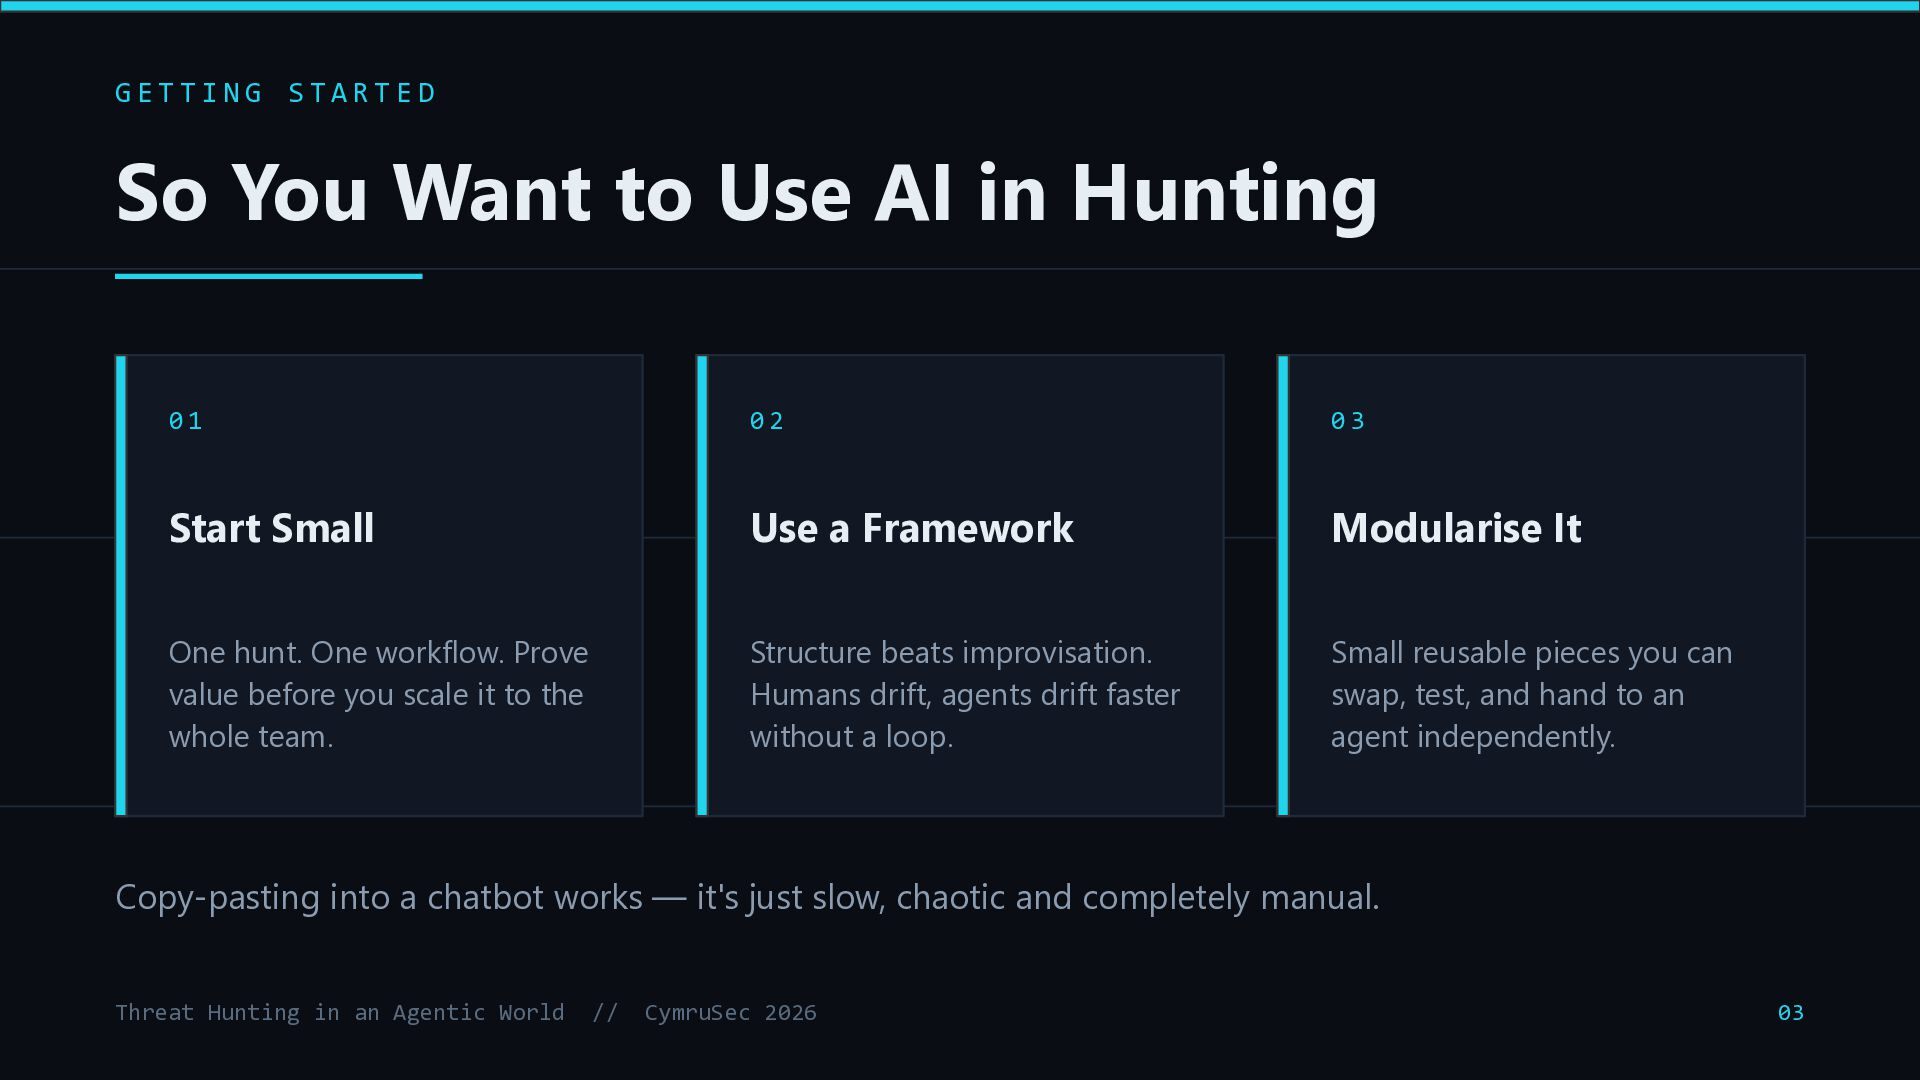
  27. GETTING STARTED So You Want to Use AI in Hunting

    01 02 03 Start Small Use a Framework Modularise It One hunt. One workflow. Prove value before you scale it to the whole team. Structure beats improvisation. Humans drift, agents drift faster without a loop. Small reusable pieces you can swap, test, and hand to an agent independently. Copy-pasting into a chatbot works — it's just slow, chaotic and completely manual. Threat Hunting in an Agentic World // CymruSec 2026 03
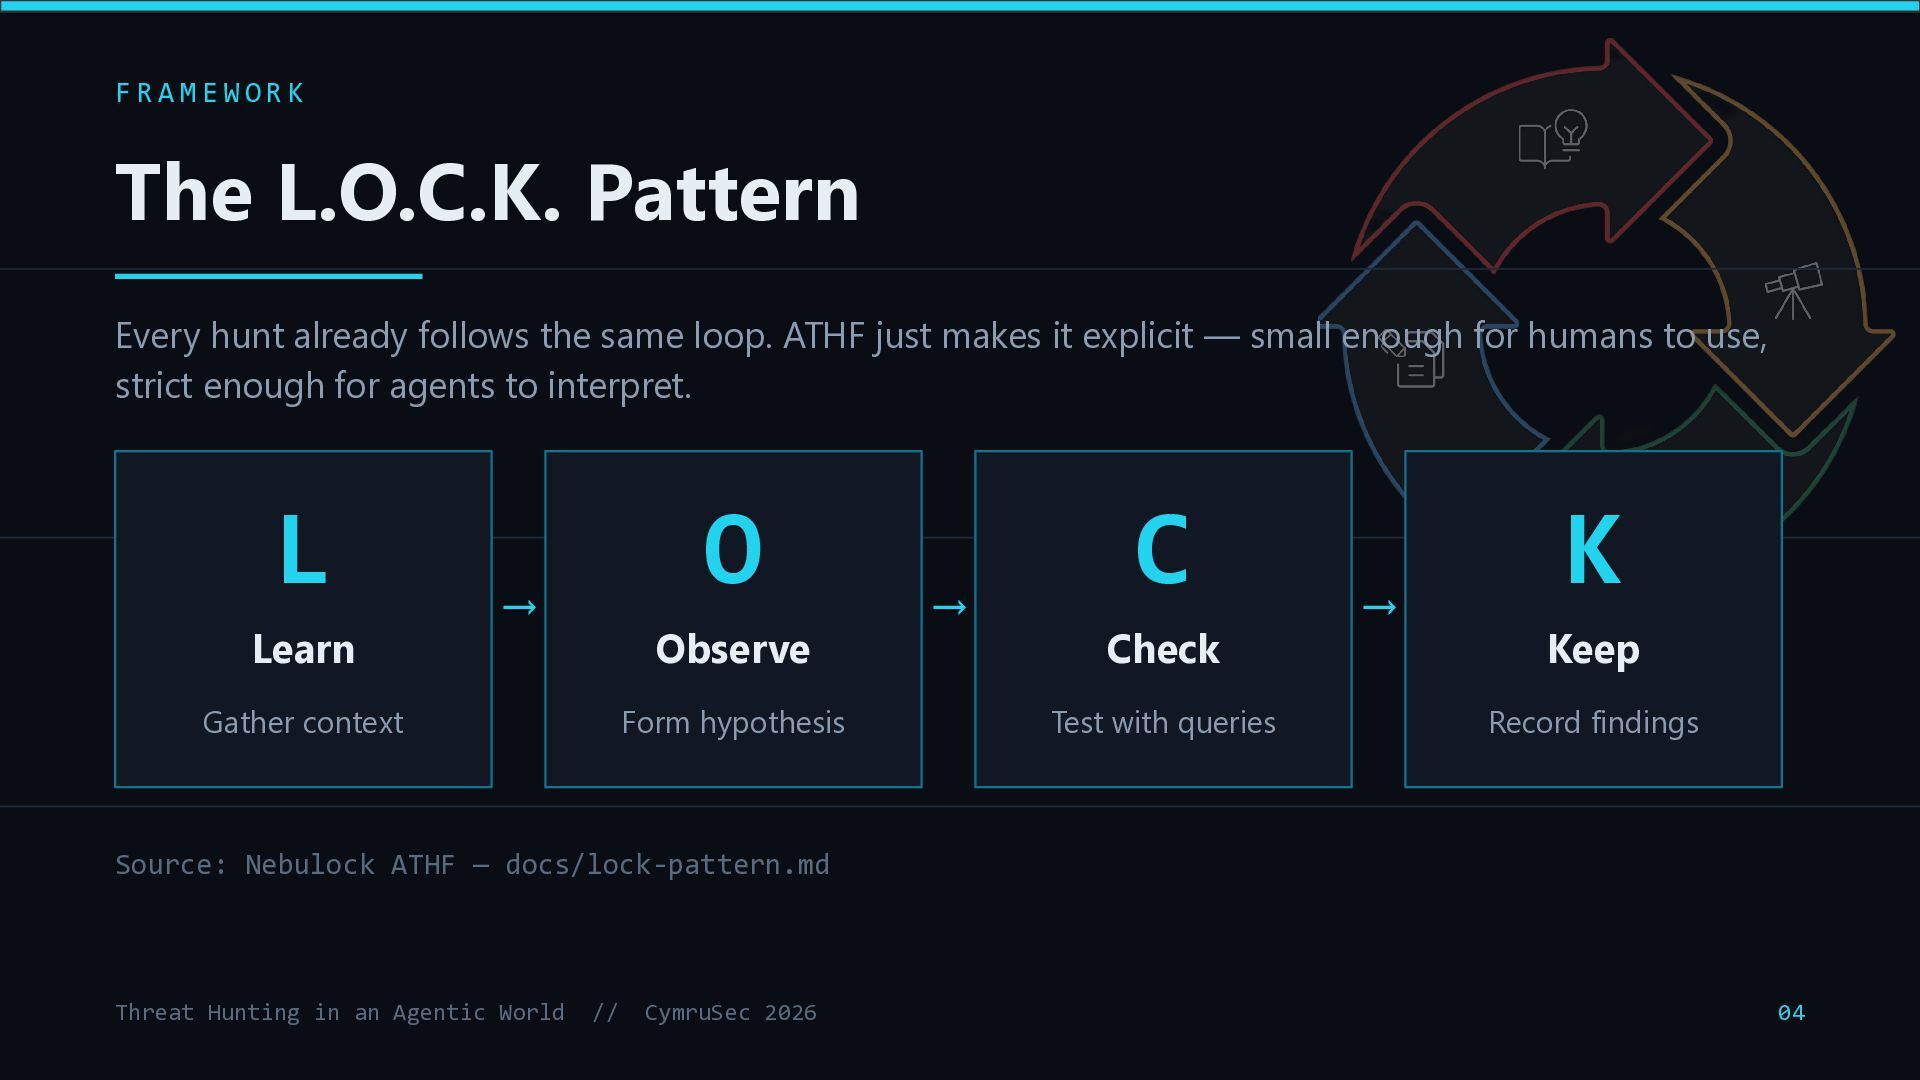
  28. FRAMEWORK The L.O.C.K. Pattern Every hunt already follows the same

    loop. ATHF just makes it explicit — small enough for humans to use, strict enough for agents to interpret. L Learn O → Observe Gather context Form hypothesis → C Check Test with queries → K Keep Record findings Source: Nebulock ATHF — docs/lock-pattern.md Threat Hunting in an Agentic World // CymruSec 2026 04
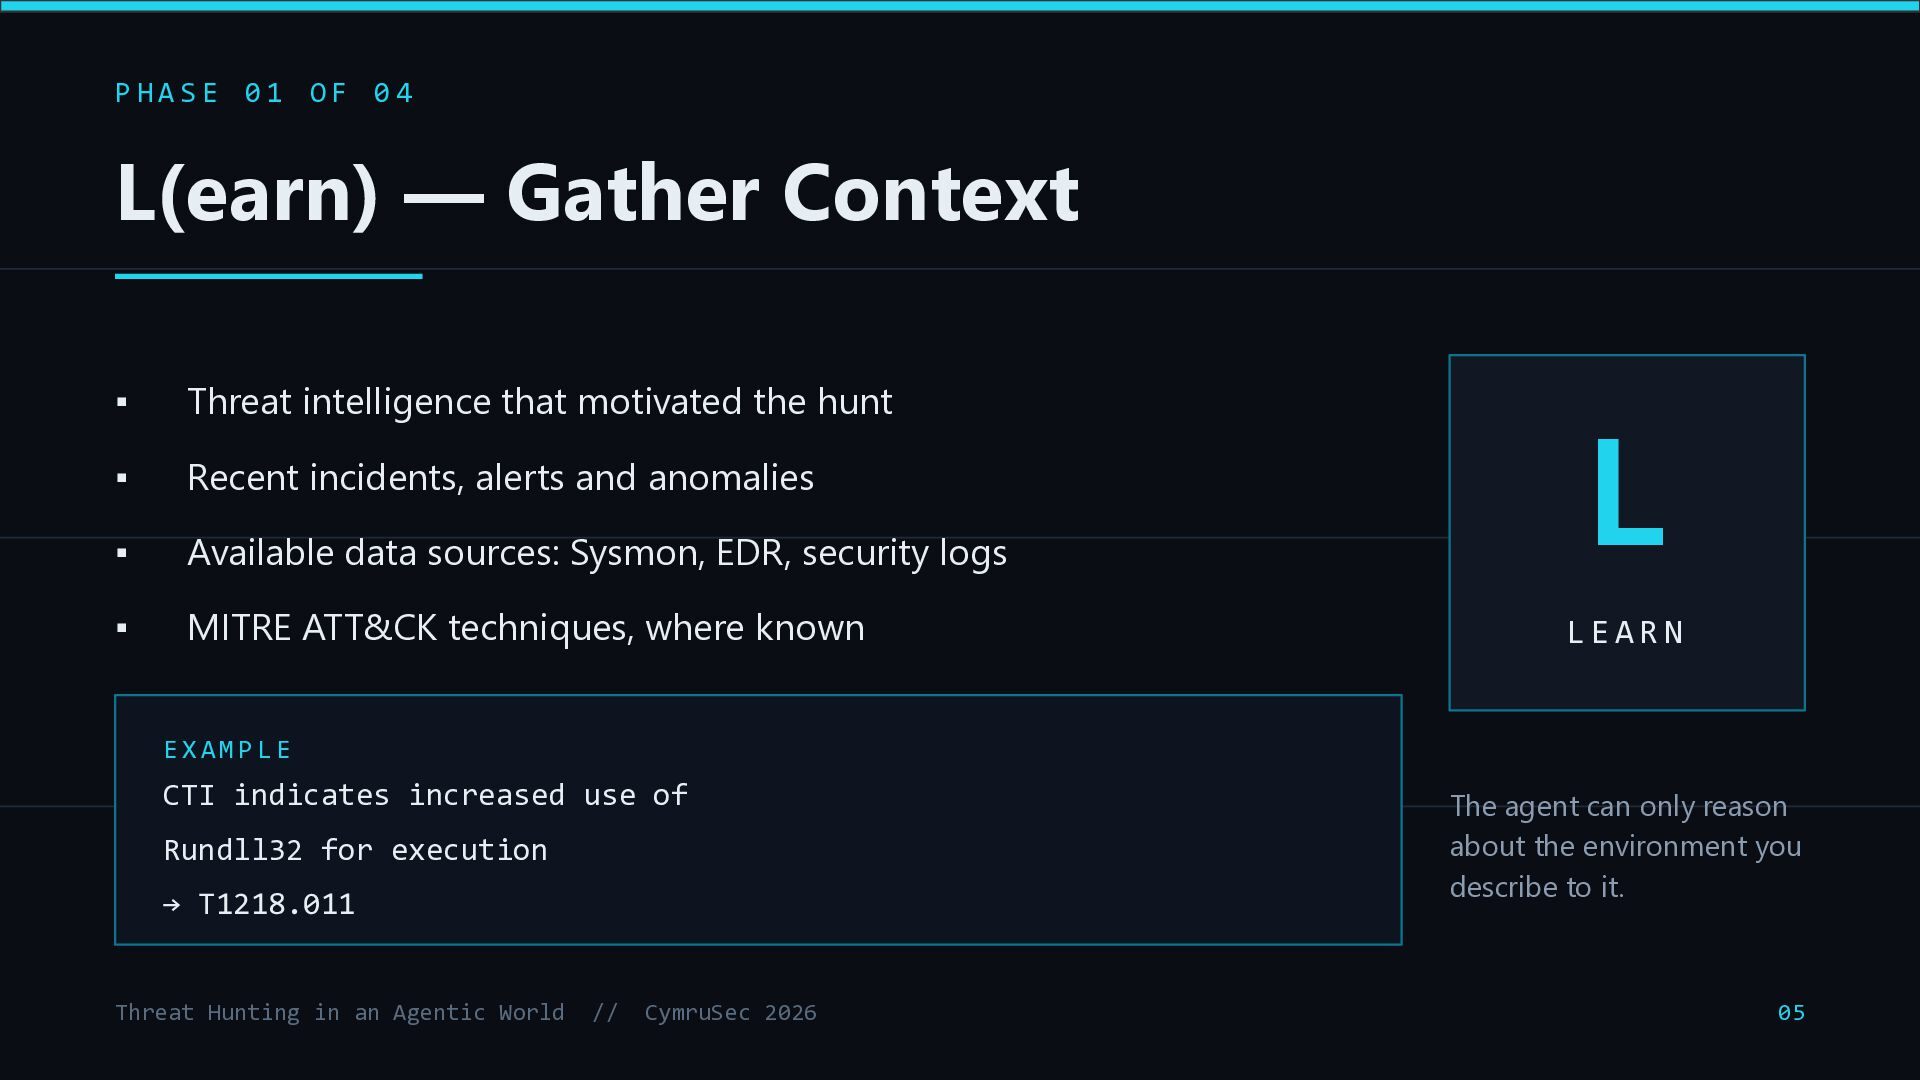
  29. PHASE 01 OF 04 L(earn) — Gather Context ▪ Threat

    intelligence that motivated the hunt ▪ Recent incidents, alerts and anomalies ▪ Available data sources: Sysmon, EDR, security logs ▪ MITRE ATT&CK techniques, where known L LEARN EXAMPLE CTI indicates increased use of Rundll32 for execution → T1218.011 Threat Hunting in an Agentic World // CymruSec 2026 The agent can only reason about the environment you describe to it. 05
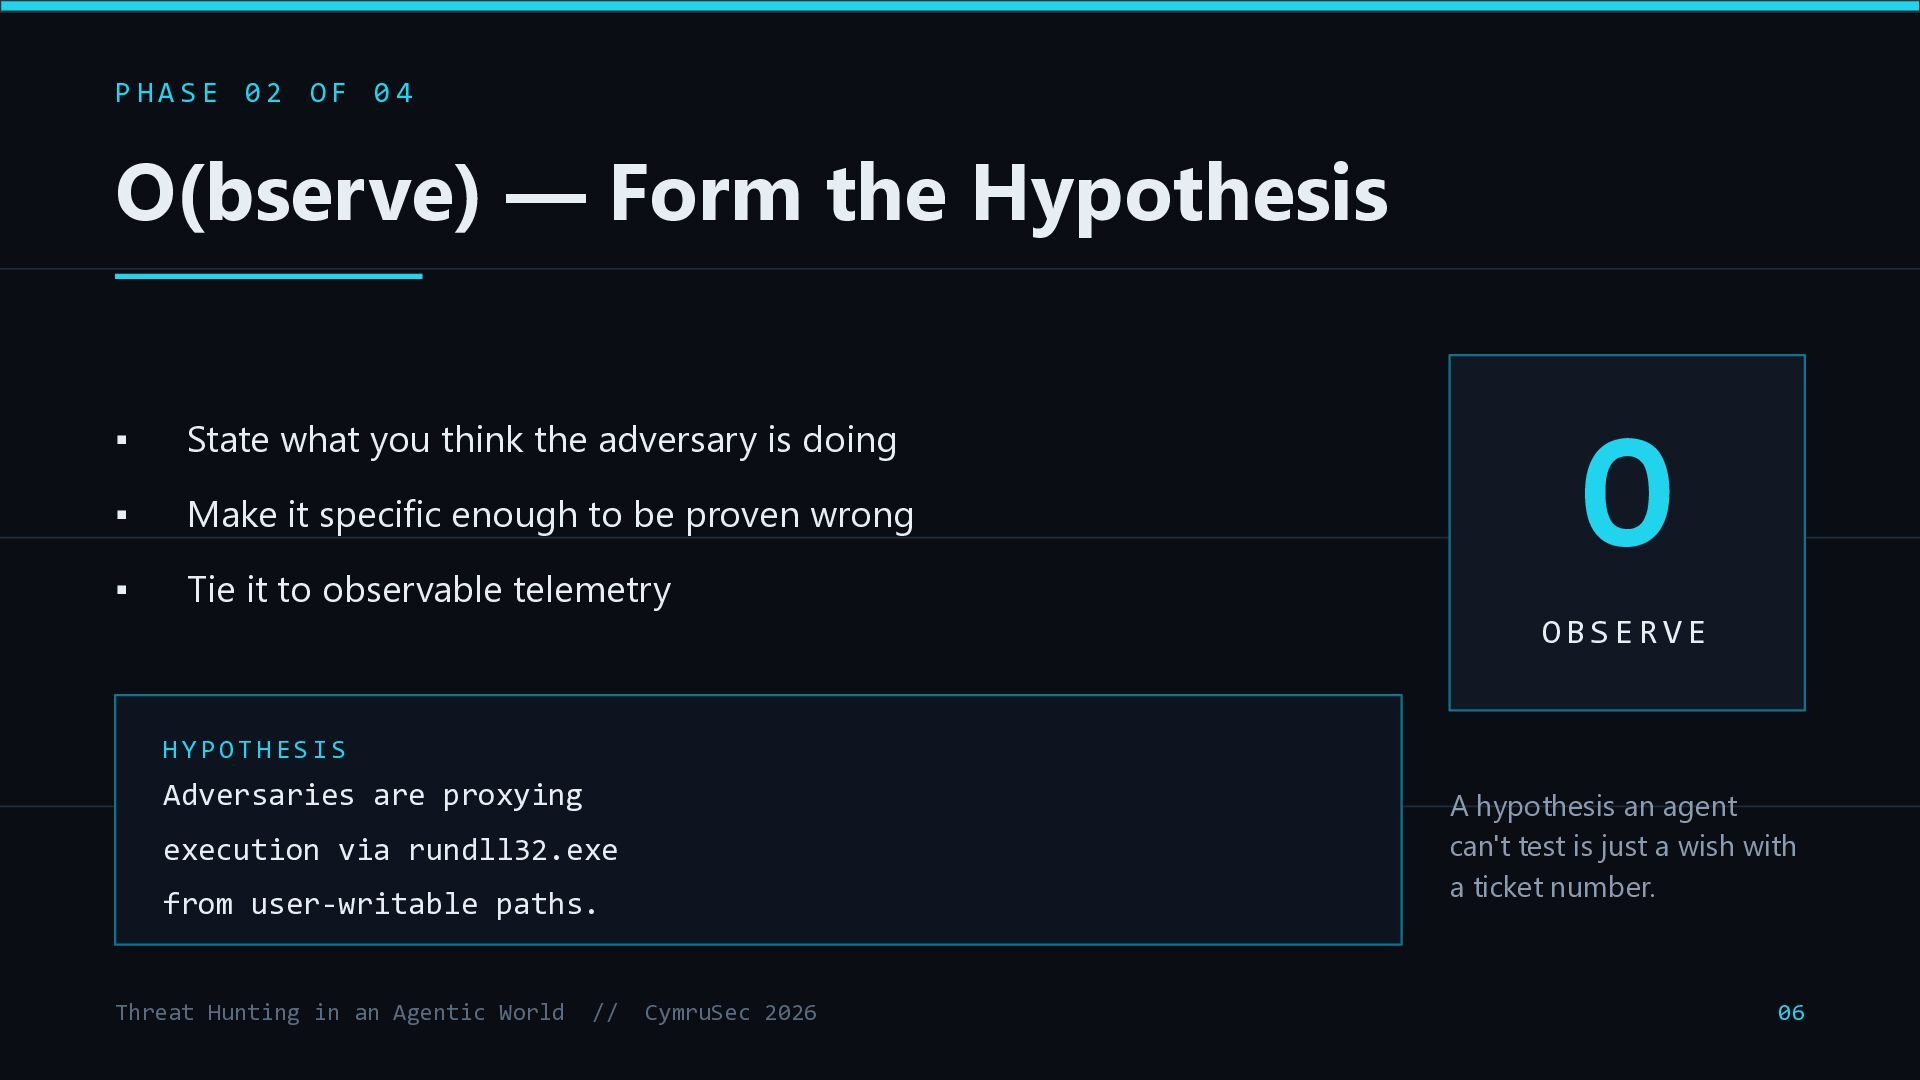
  30. PHASE 02 OF 04 O(bserve) — Form the Hypothesis ▪

    State what you think the adversary is doing ▪ Make it specific enough to be proven wrong ▪ Tie it to observable telemetry O OBSERVE HYPOTHESIS Adversaries are proxying A hypothesis an agent can't test is just a wish with a ticket number. execution via rundll32.exe from user-writable paths. Threat Hunting in an Agentic World // CymruSec 2026 06
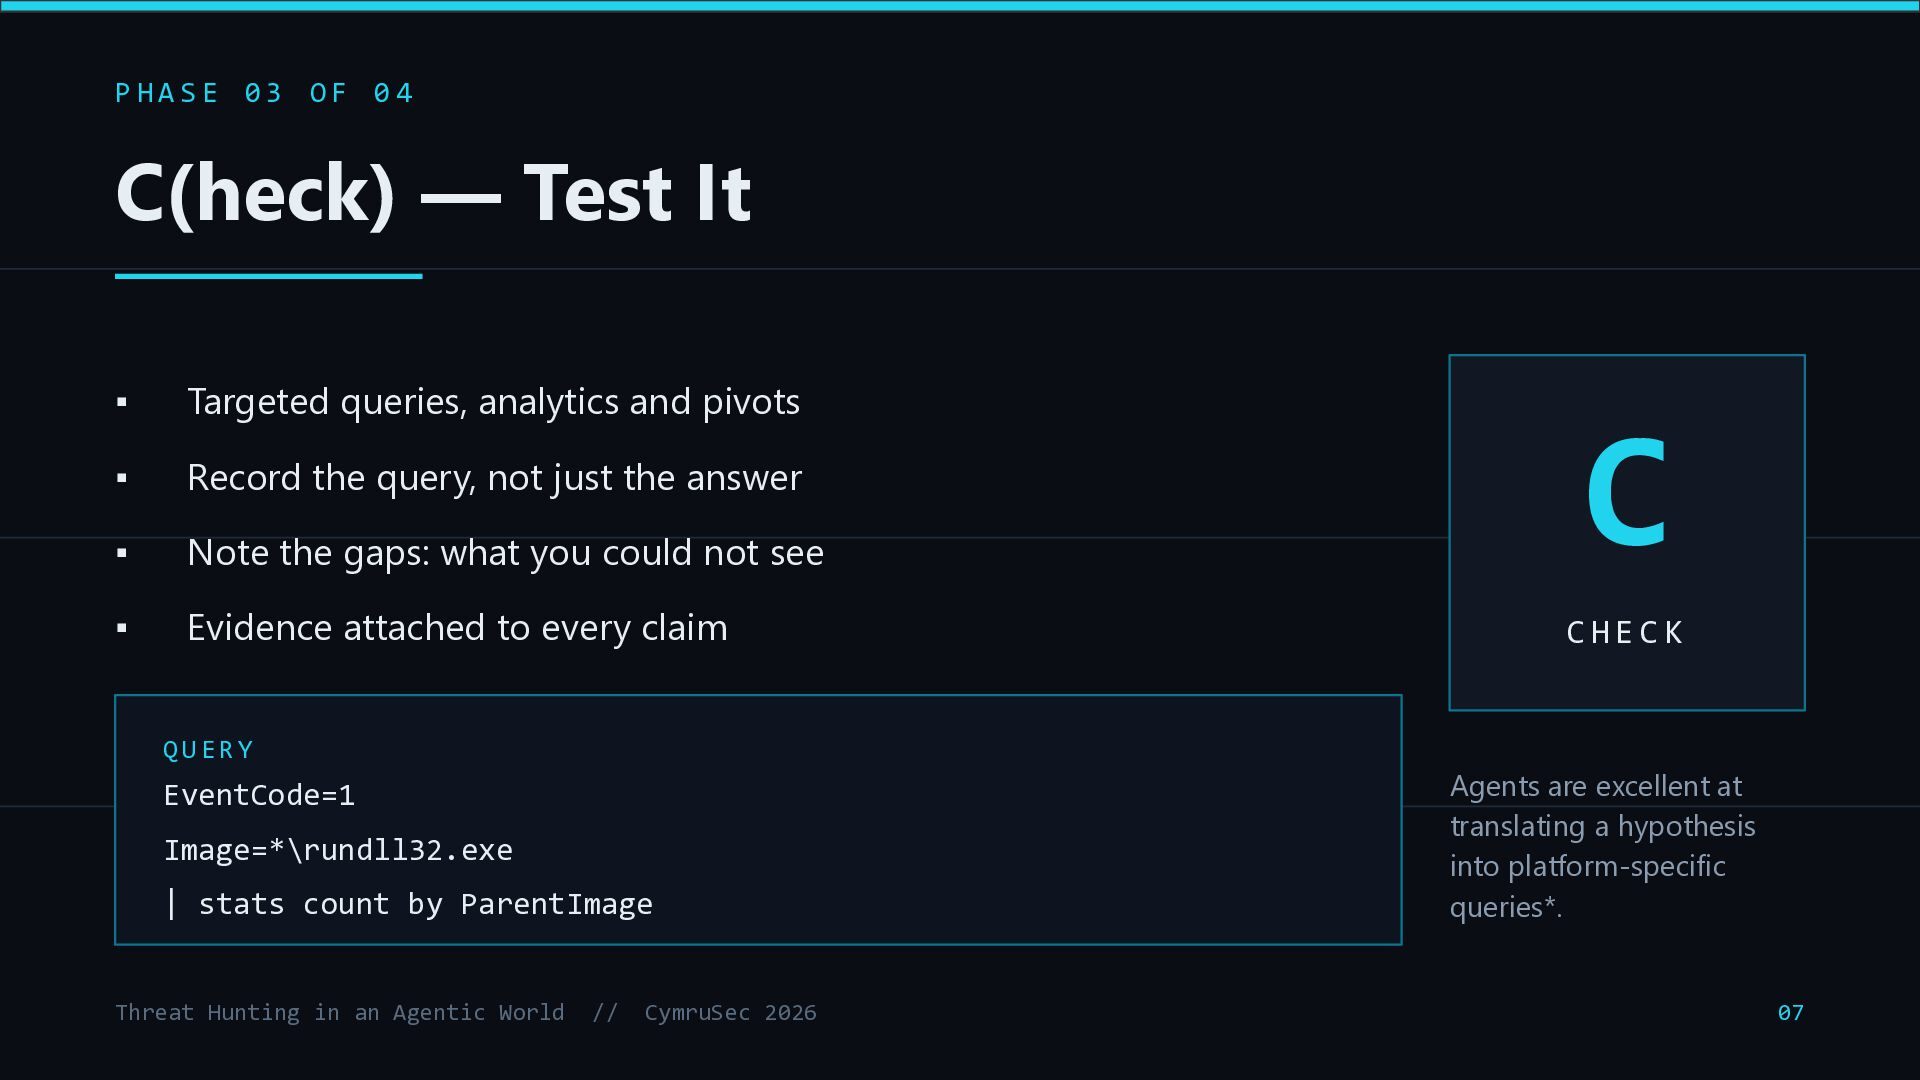
  31. PHASE 03 OF 04 C(heck) — Test It ▪ Targeted

    queries, analytics and pivots ▪ Record the query, not just the answer ▪ Note the gaps: what you could not see ▪ Evidence attached to every claim QUERY EventCode=1 Image=*\rundll32.exe | stats count by ParentImage Threat Hunting in an Agentic World // CymruSec 2026 C CHECK Agents are excellent at translating a hypothesis into platform-specific queries*. 07
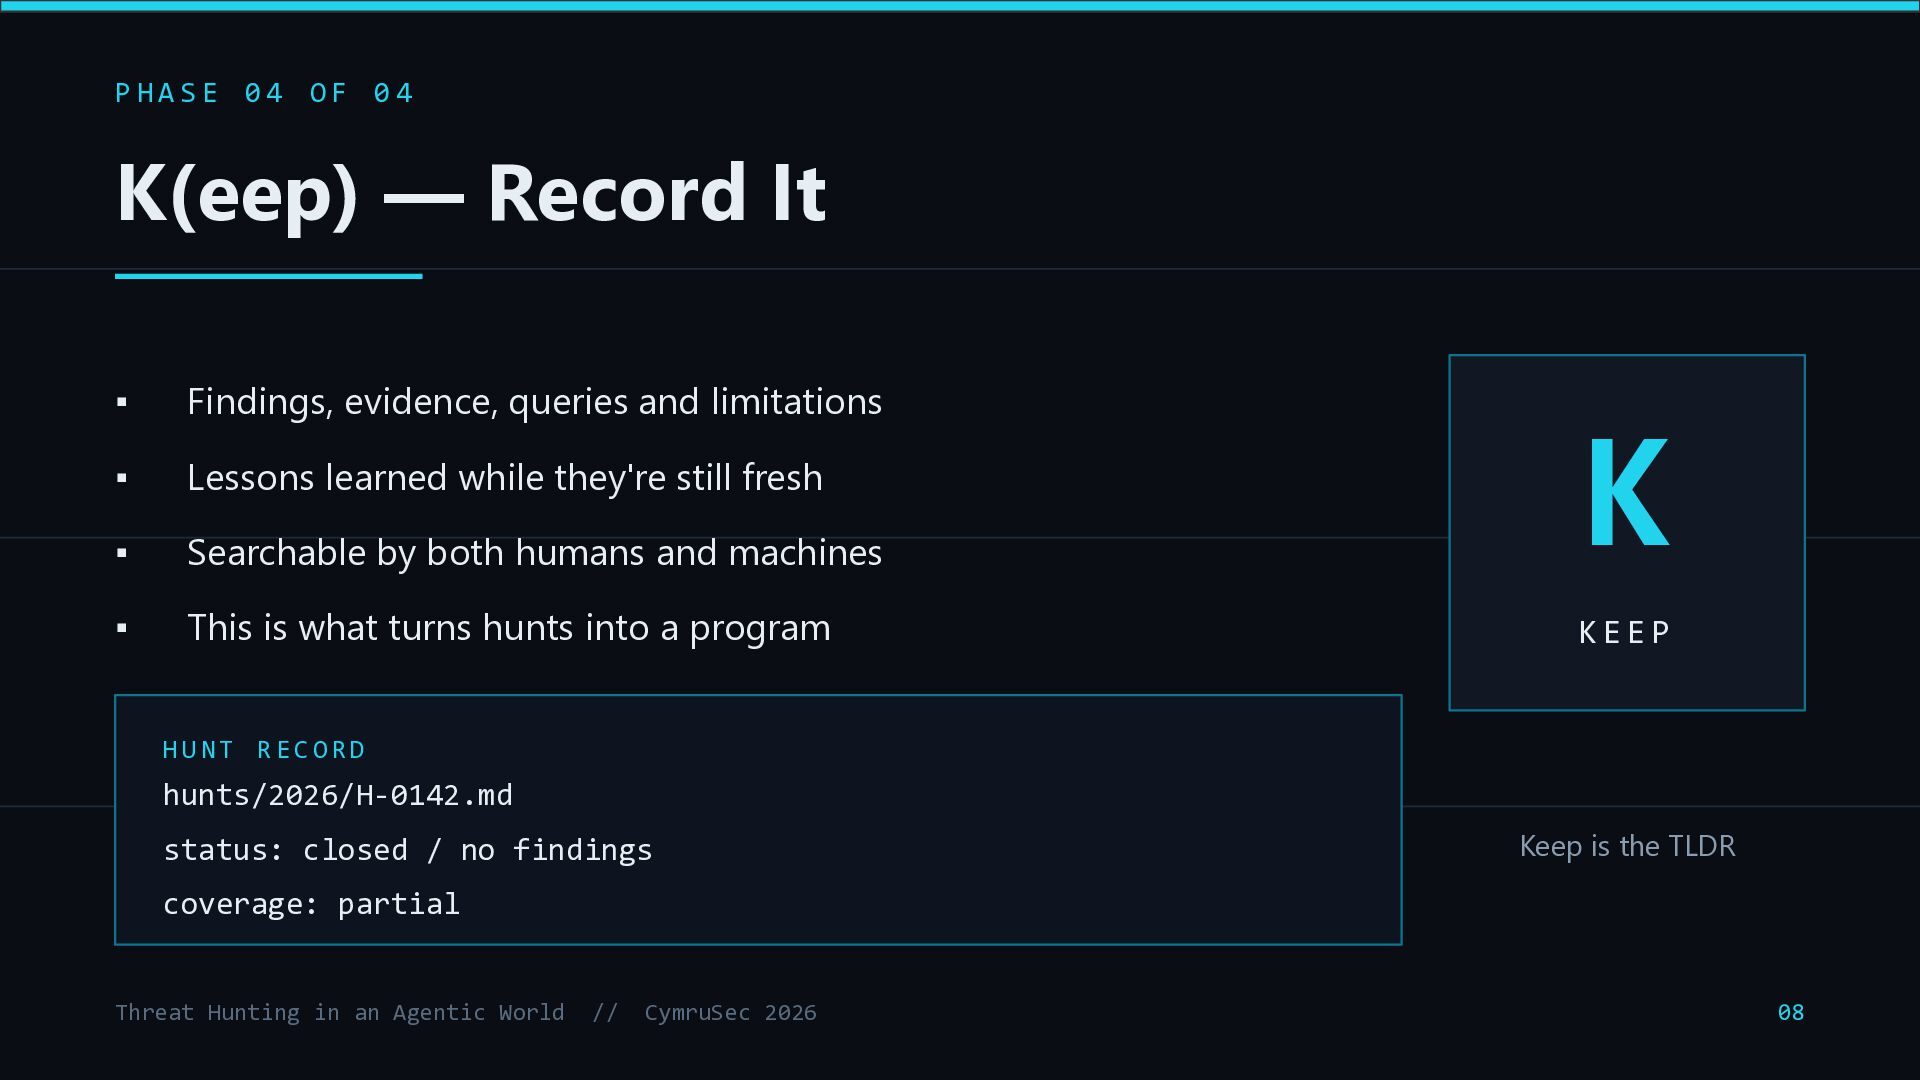
  32. PHASE 04 OF 04 K(eep) — Record It ▪ Findings,

    evidence, queries and limitations ▪ Lessons learned while they're still fresh ▪ Searchable by both humans and machines ▪ This is what turns hunts into a program K KEEP HUNT RECORD hunts/2026/H-0142.md status: closed / no findings Keep is the TLDR coverage: partial Threat Hunting in an Agentic World // CymruSec 2026 08
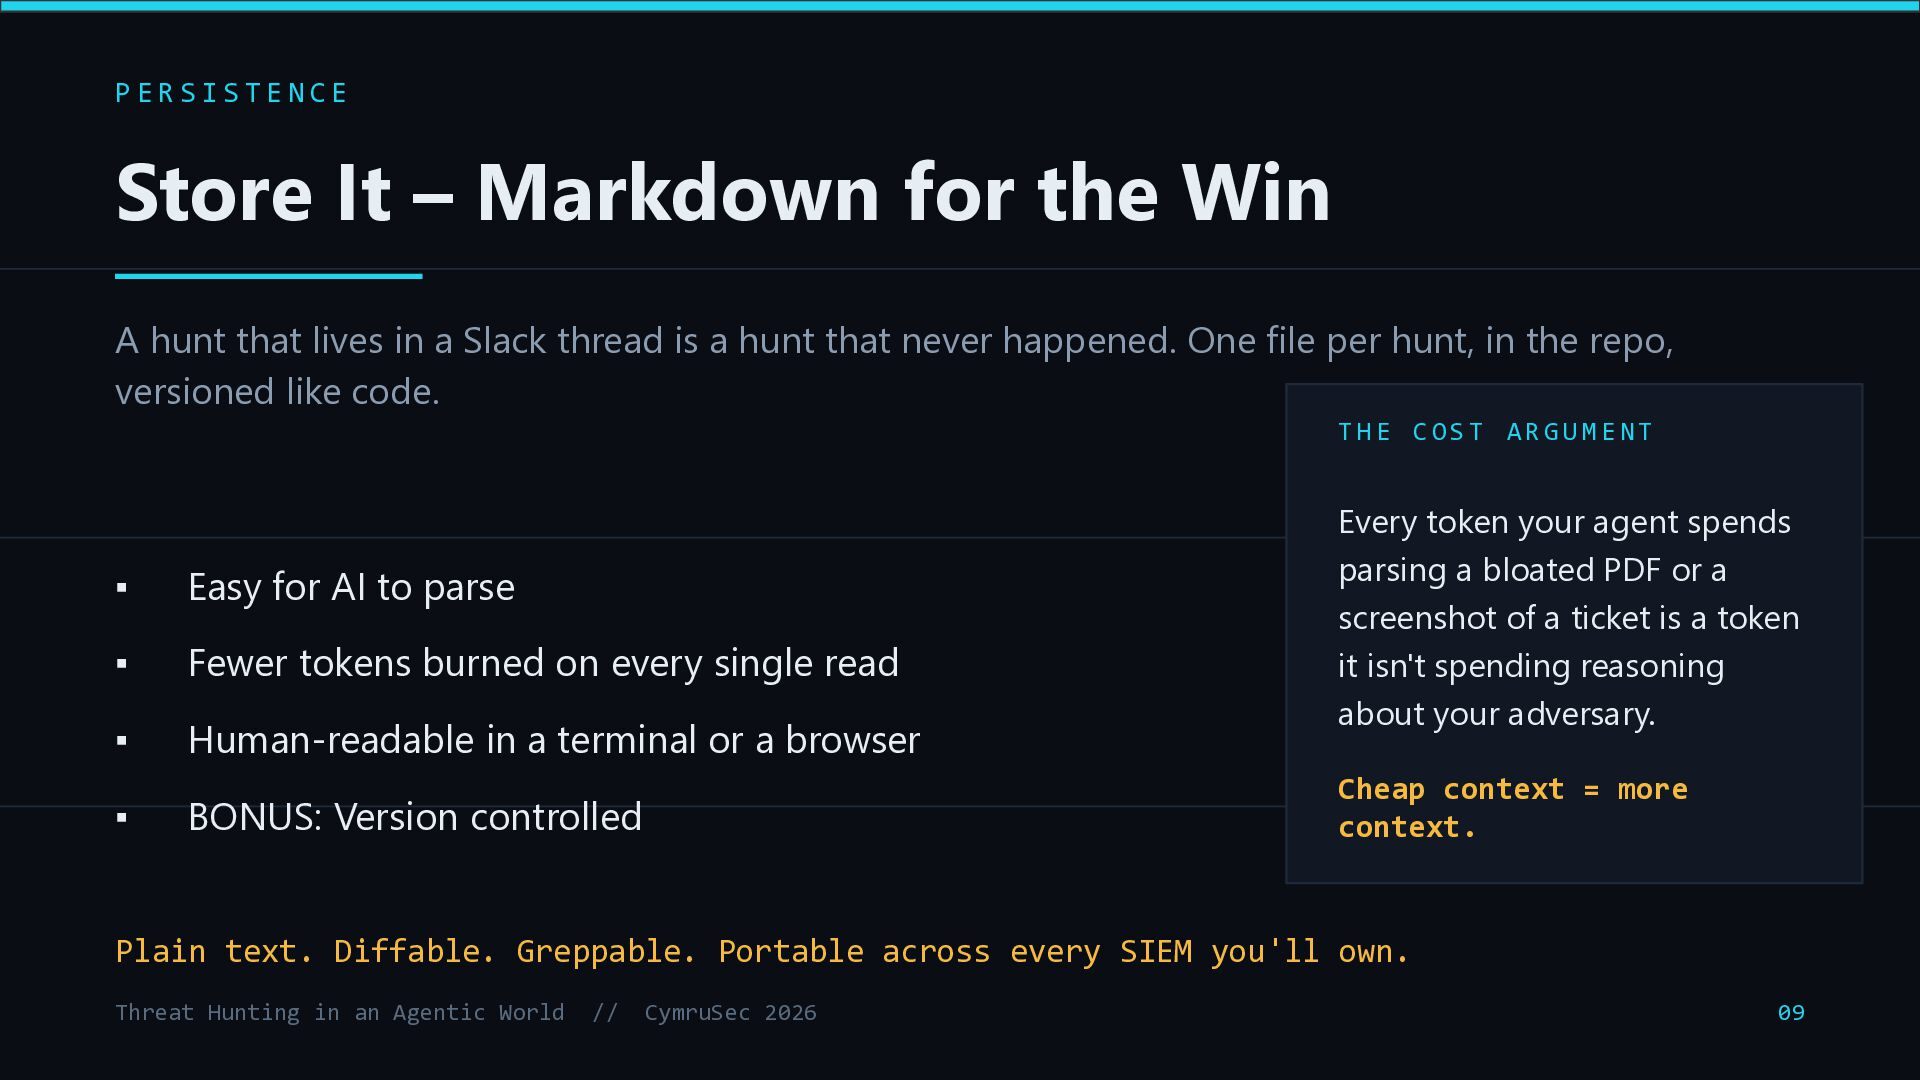
  33. PERSISTENCE Store It – Markdown for the Win A hunt

    that lives in a Slack thread is a hunt that never happened. One file per hunt, in the repo, versioned like code. THE COST ARGUMENT ▪ Easy for AI to parse ▪ Fewer tokens burned on every single read ▪ Human-readable in a terminal or a browser ▪ BONUS: Version controlled Every token your agent spends parsing a bloated PDF or a screenshot of a ticket is a token it isn't spending reasoning about your adversary. Cheap context = more context. Plain text. Diffable. Greppable. Portable across every SIEM you'll own. Threat Hunting in an Agentic World // CymruSec 2026 09
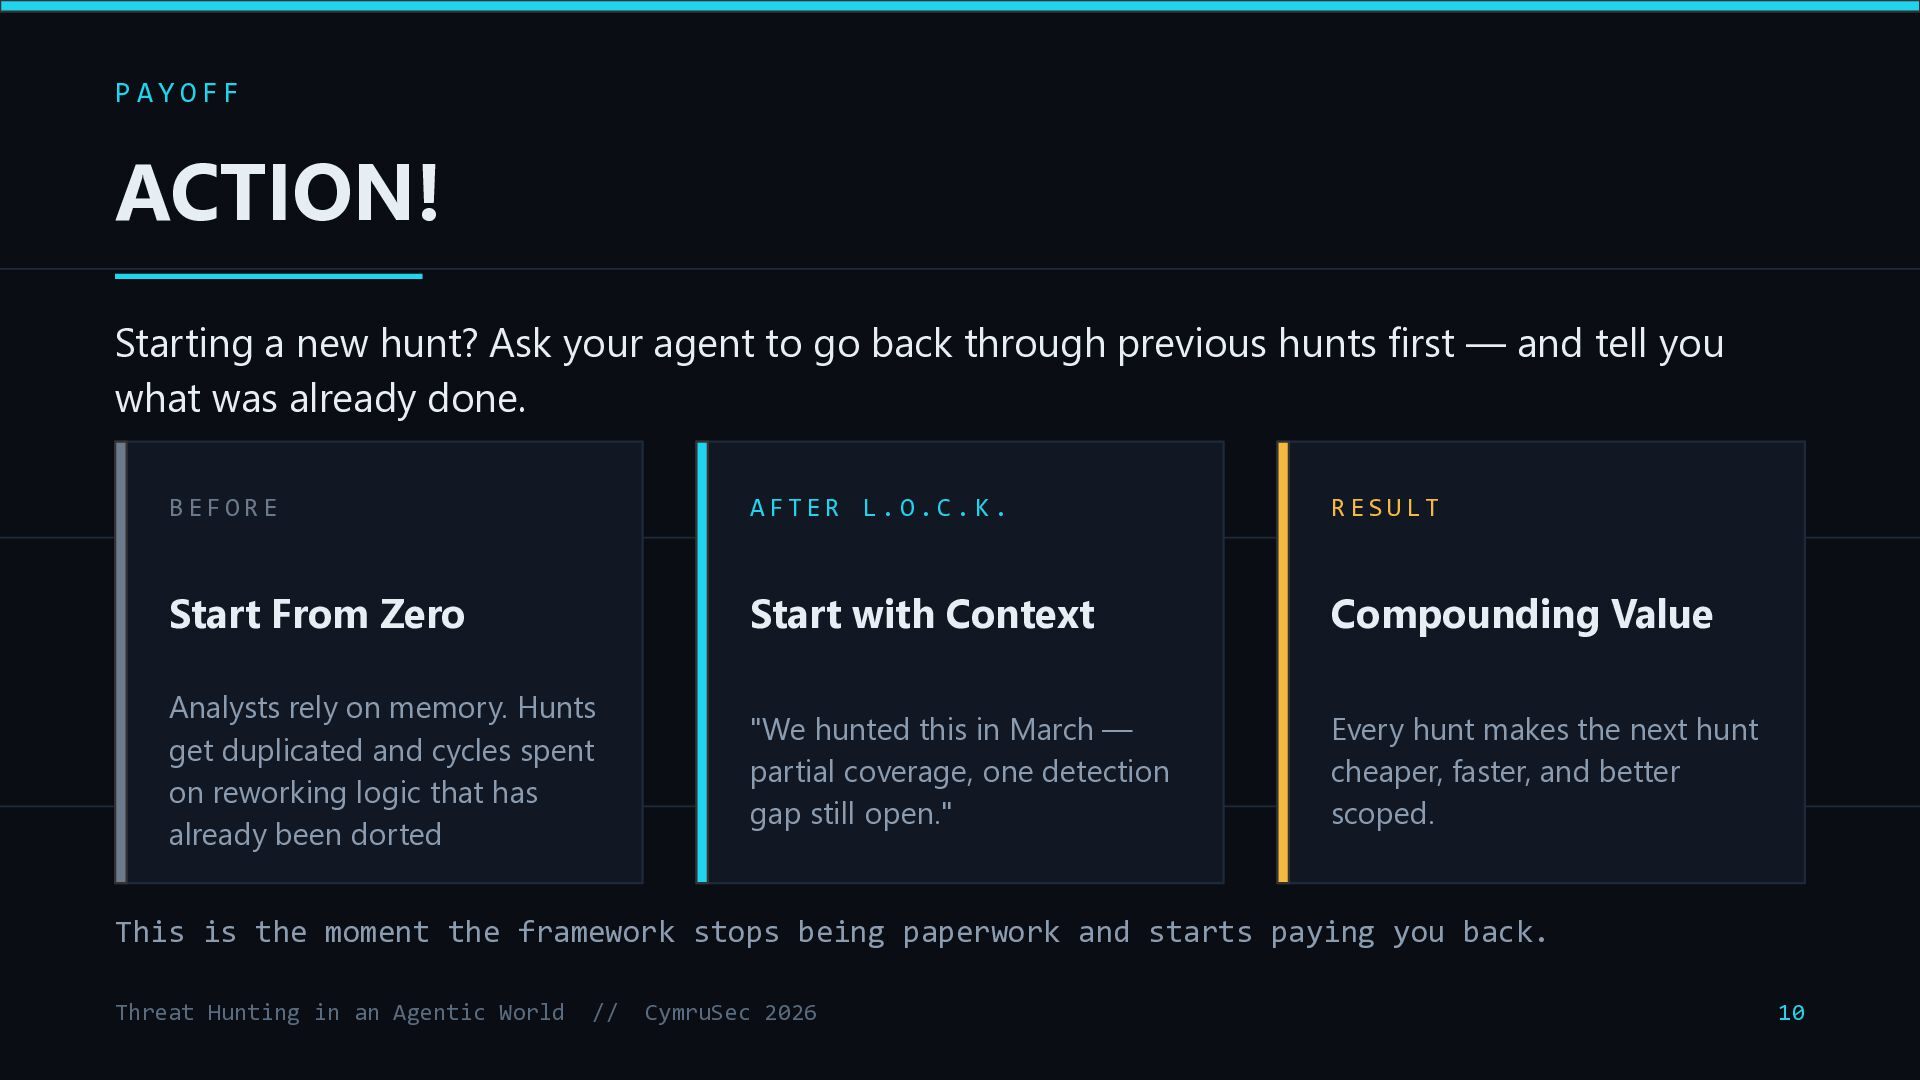
  34. PAYOFF ACTION! Starting a new hunt? Ask your agent to

    go back through previous hunts first — and tell you what was already done. BEFORE AFTER L.O.C.K. RESULT Start From Zero Start with Context Compounding Value Analysts rely on memory. Hunts get duplicated and cycles spent on reworking logic that has already been dorted "We hunted this in March — partial coverage, one detection gap still open." Every hunt makes the next hunt cheaper, faster, and better scoped. This is the moment the framework stops being paperwork and starts paying you back. Threat Hunting in an Agentic World // CymruSec 2026 10
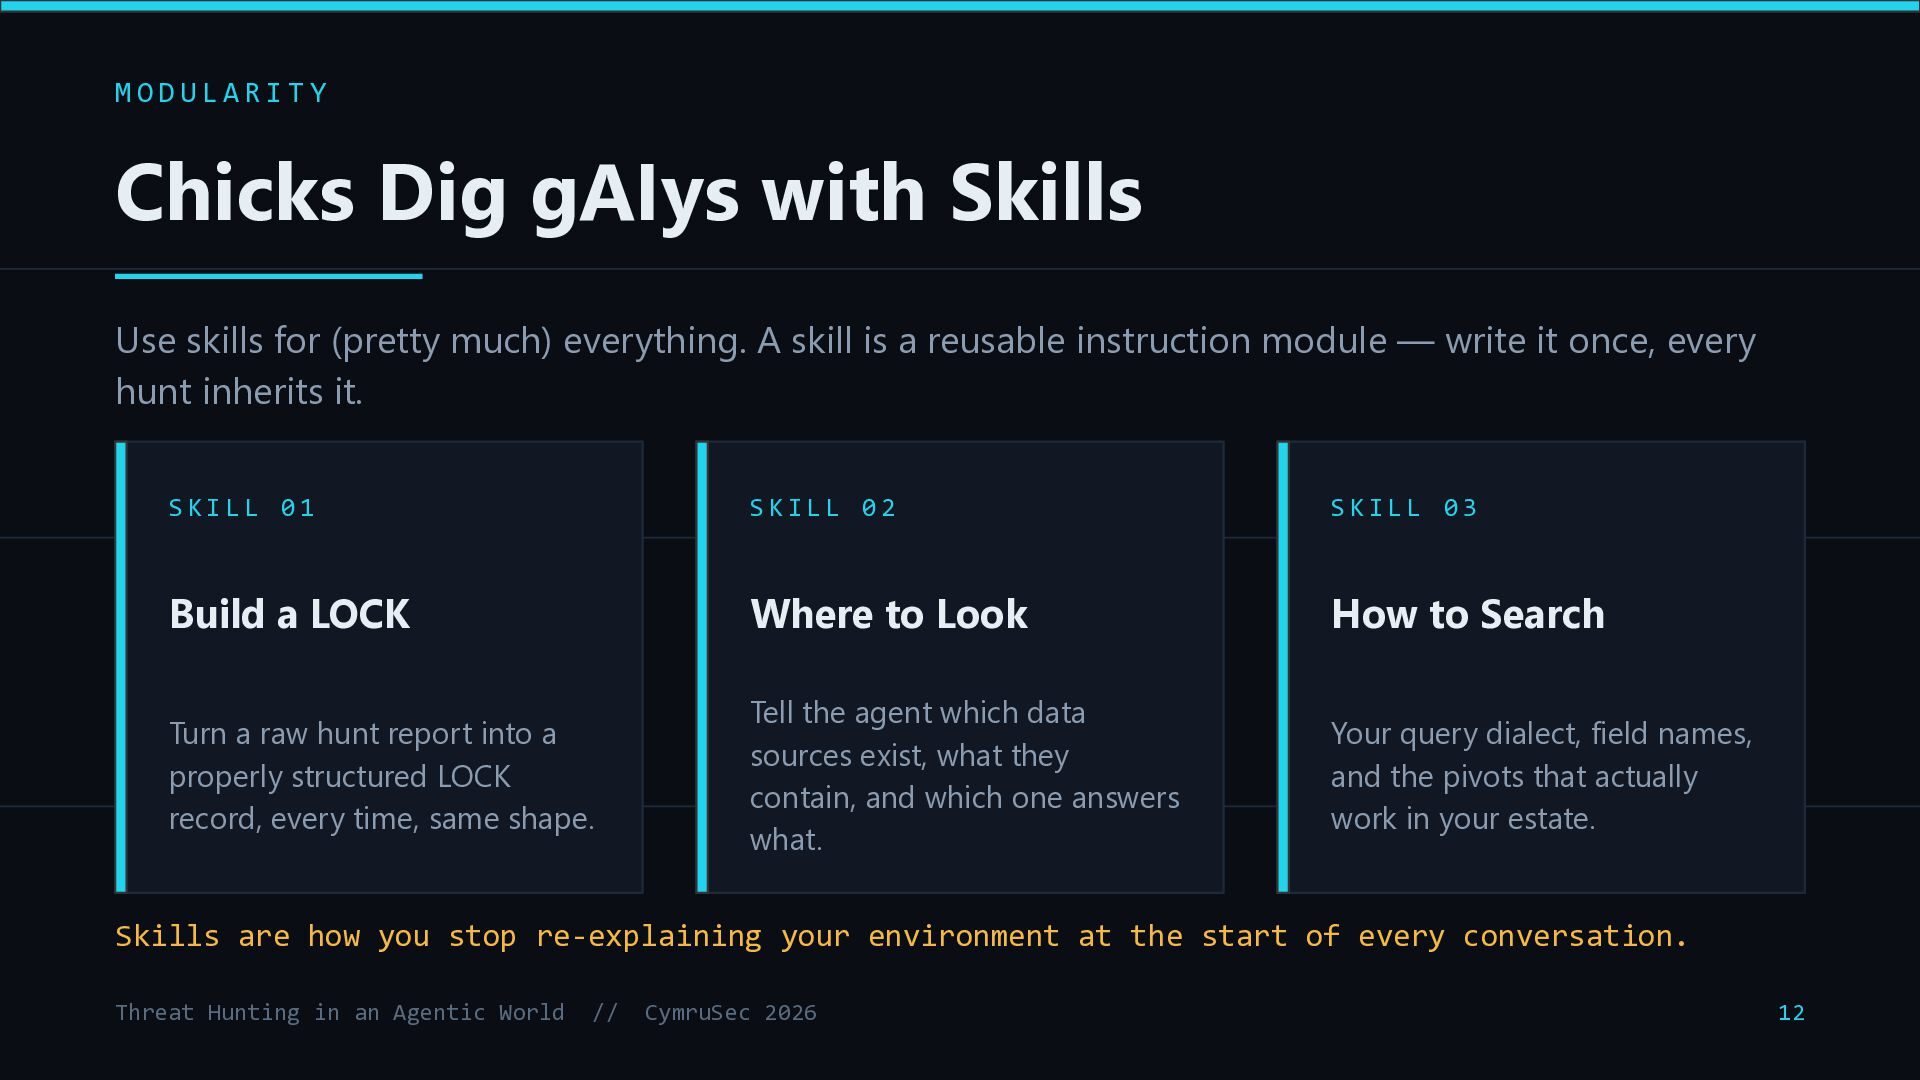
  35. MODULARITY Chicks Dig gAIys with Skills Use skills for (pretty

    much) everything. A skill is a reusable instruction module — write it once, every hunt inherits it. SKILL 01 SKILL 02 SKILL 03 Build a LOCK Where to Look How to Search Turn a raw hunt report into a properly structured LOCK record, every time, same shape. Tell the agent which data sources exist, what they contain, and which one answers what. Your query dialect, field names, and the pivots that actually work in your estate. Skills are how you stop re-explaining your environment at the start of every conversation. Threat Hunting in an Agentic World // CymruSec 2026 12
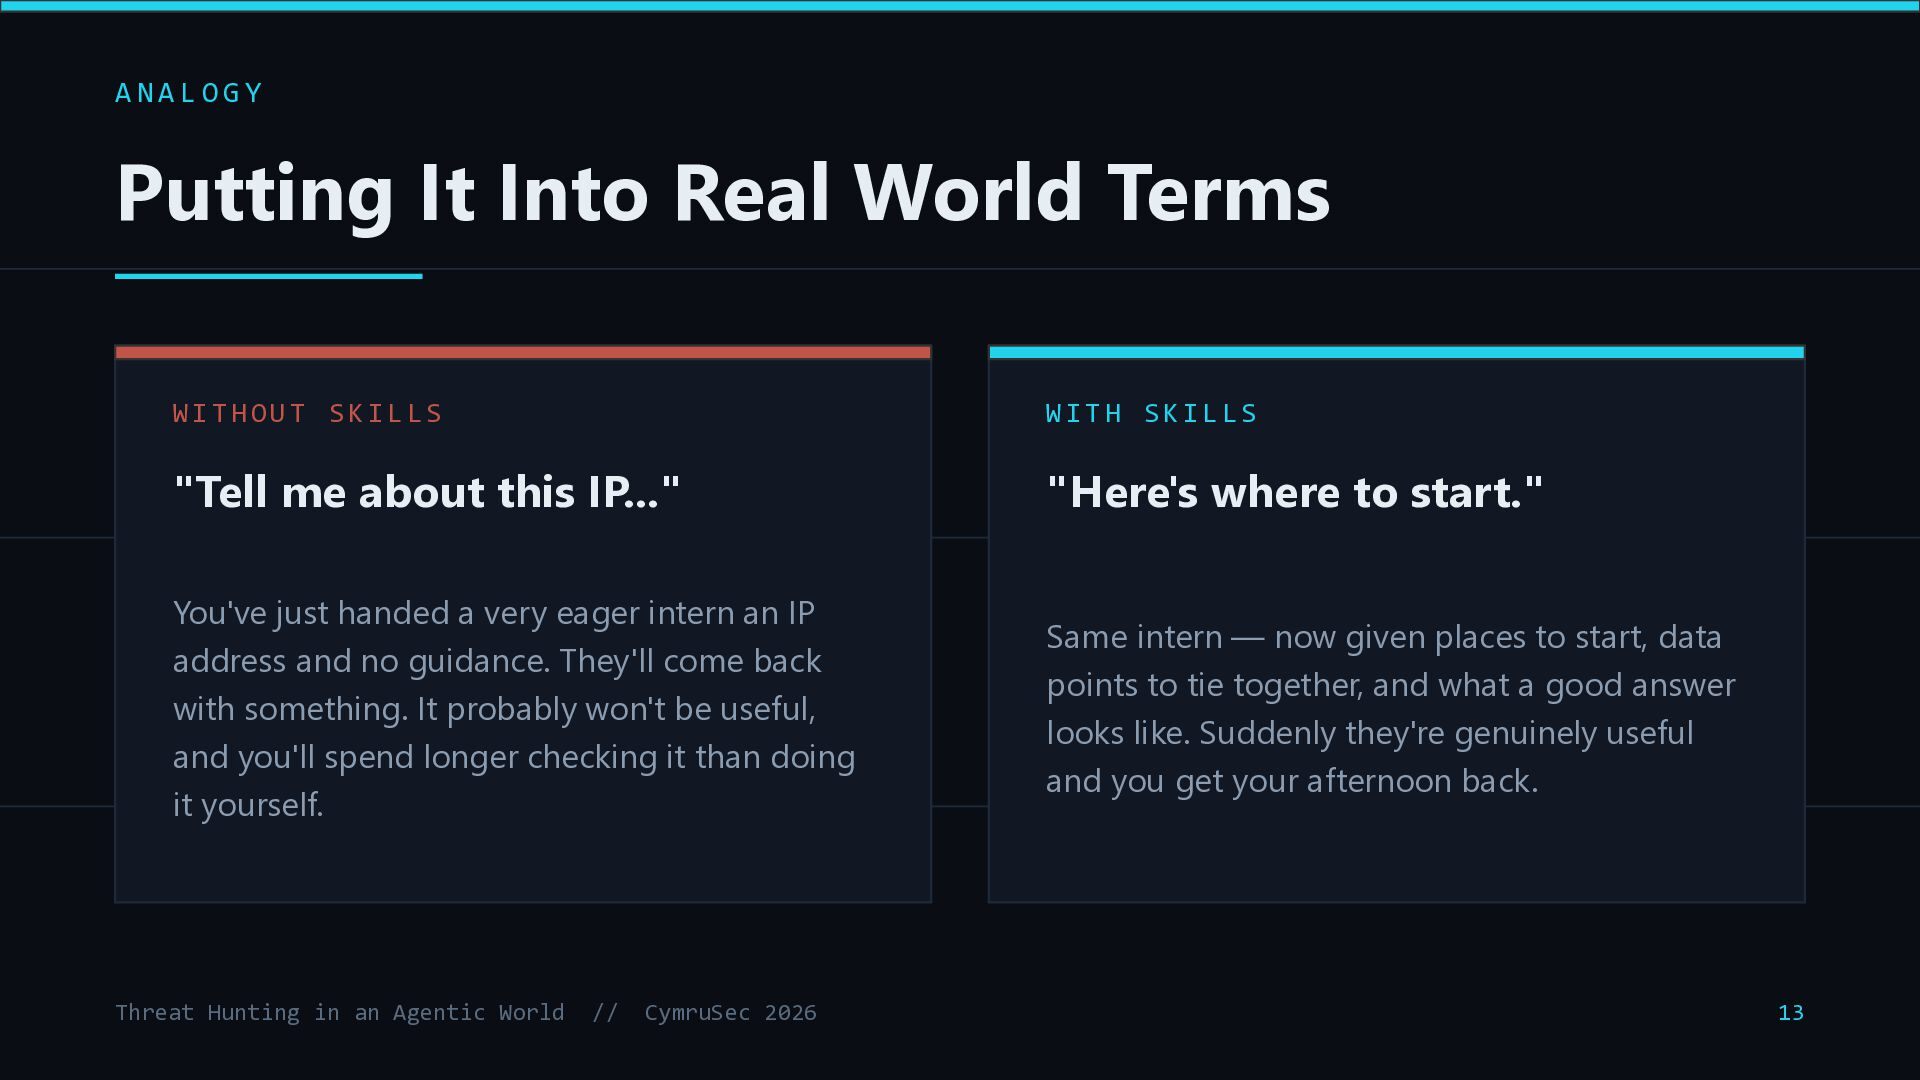
  36. ANALOGY Putting It Into Real World Terms WITHOUT SKILLS WITH

    SKILLS "Tell me about this IP..." "Here's where to start." You've just handed a very eager intern an IP address and no guidance. They'll come back with something. It probably won't be useful, and you'll spend longer checking it than doing it yourself. Same intern — now given places to start, data points to tie together, and what a good answer looks like. Suddenly they're genuinely useful and you get your afternoon back. Threat Hunting in an Agentic World // CymruSec 2026 13
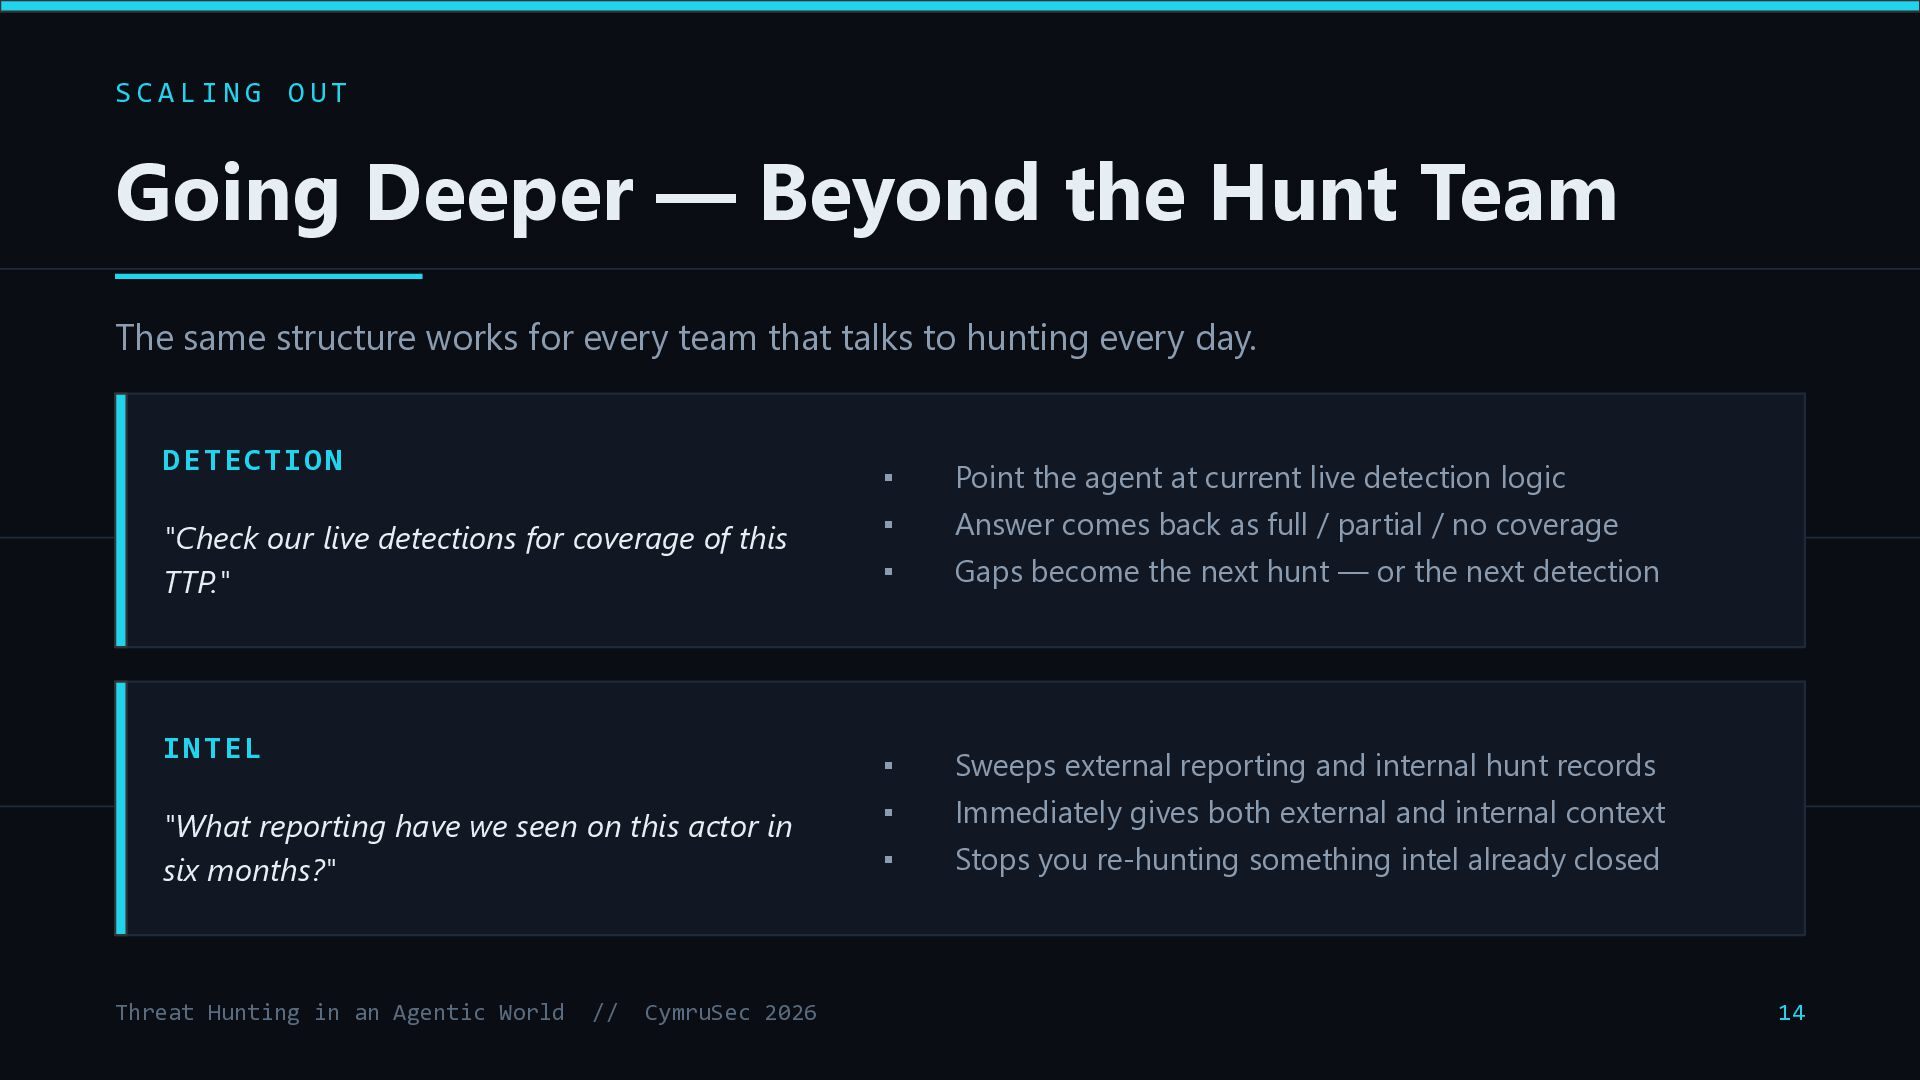
  37. SCALING OUT Going Deeper — Beyond the Hunt Team The

    same structure works for every team that talks to hunting every day. DETECTION ▪ Point the agent at current live detection logic ▪ Gaps become the next hunt — or the next detection "Check our live detections for coverage of this TTP." ▪ INTEL ▪ Sweeps external reporting and internal hunt records ▪ Stops you re-hunting something intel already closed "What reporting have we seen on this actor in six months?" Threat Hunting in an Agentic World // CymruSec 2026 ▪ Answer comes back as full / partial / no coverage Immediately gives both external and internal context 14
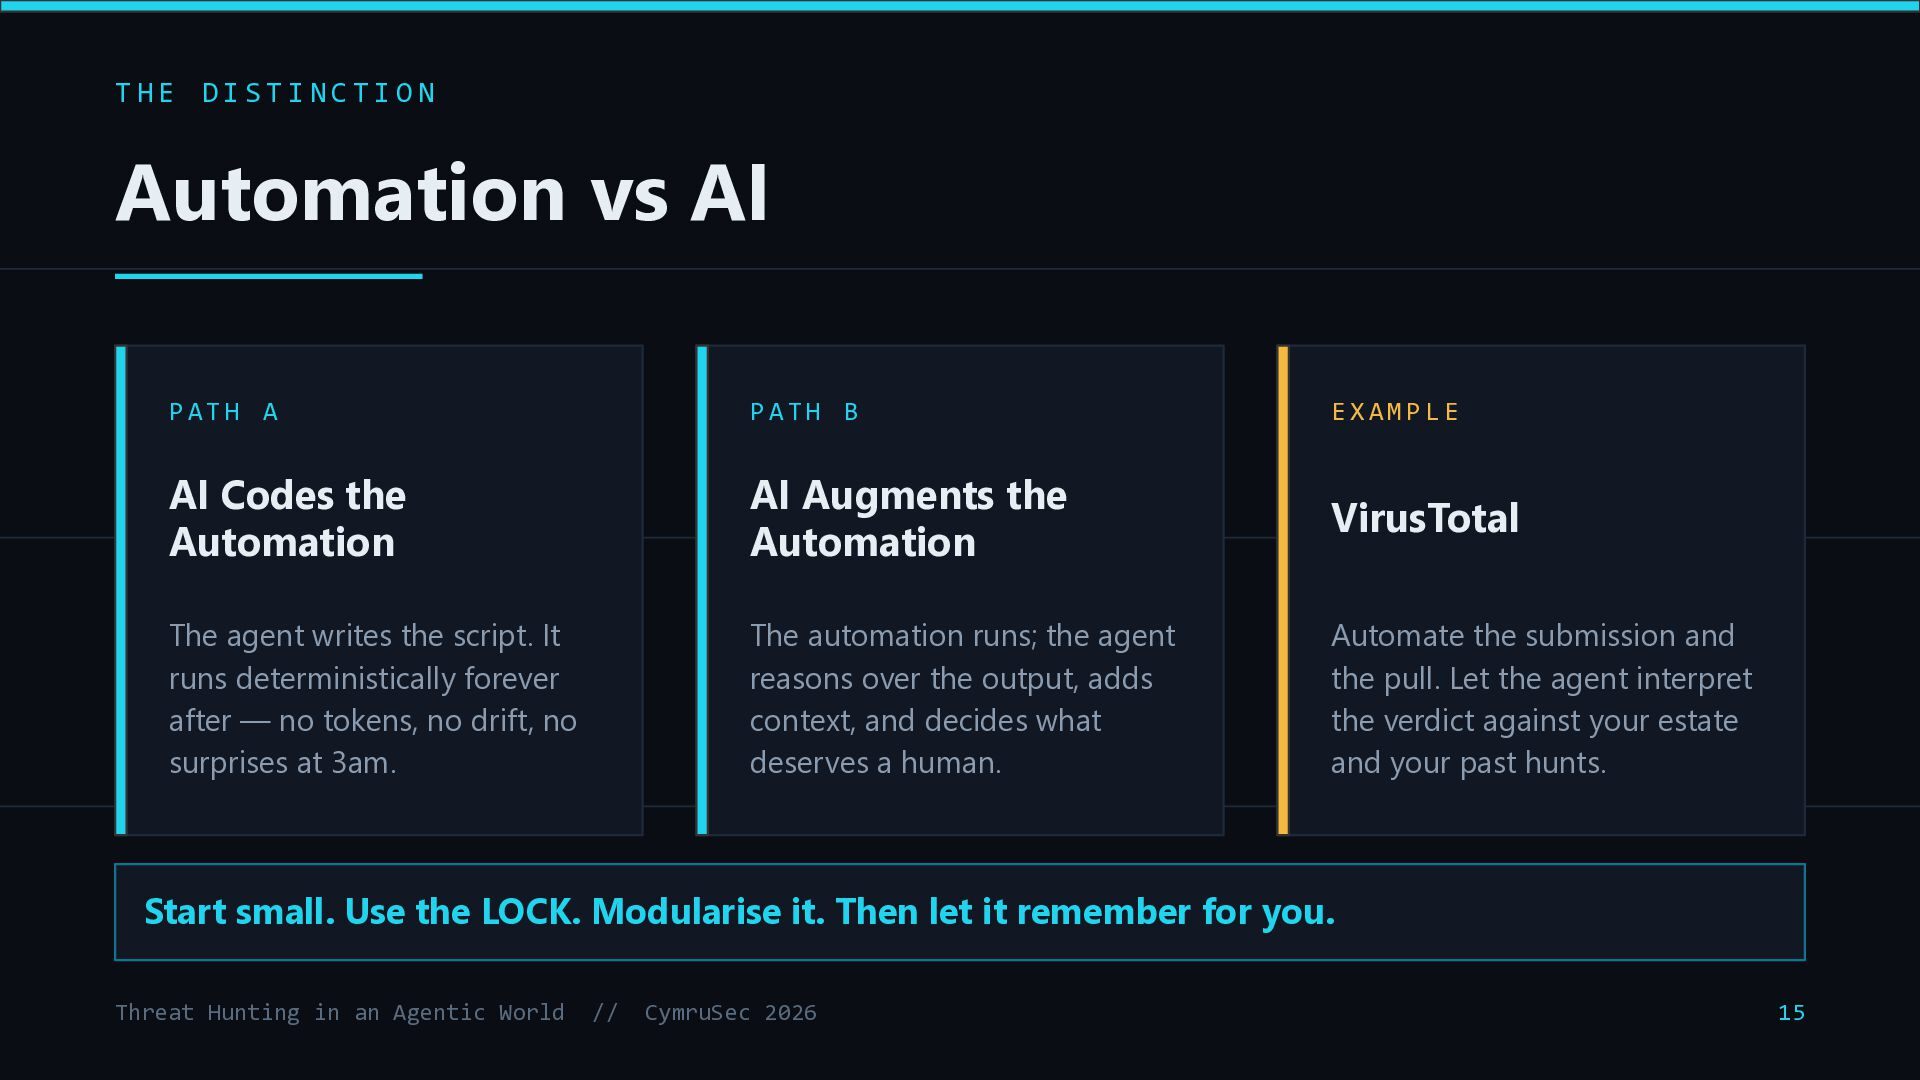
  38. THE DISTINCTION Automation vs AI PATH A PATH B EXAMPLE

    AI Codes the Automation AI Augments the Automation VirusTotal The agent writes the script. It runs deterministically forever after — no tokens, no drift, no surprises at 3am. The automation runs; the agent reasons over the output, adds context, and decides what deserves a human. Automate the submission and the pull. Let the agent interpret the verdict against your estate and your past hunts. Start small. Use the LOCK. Modularise it. Then let it remember for you. Threat Hunting in an Agentic World // CymruSec 2026 15
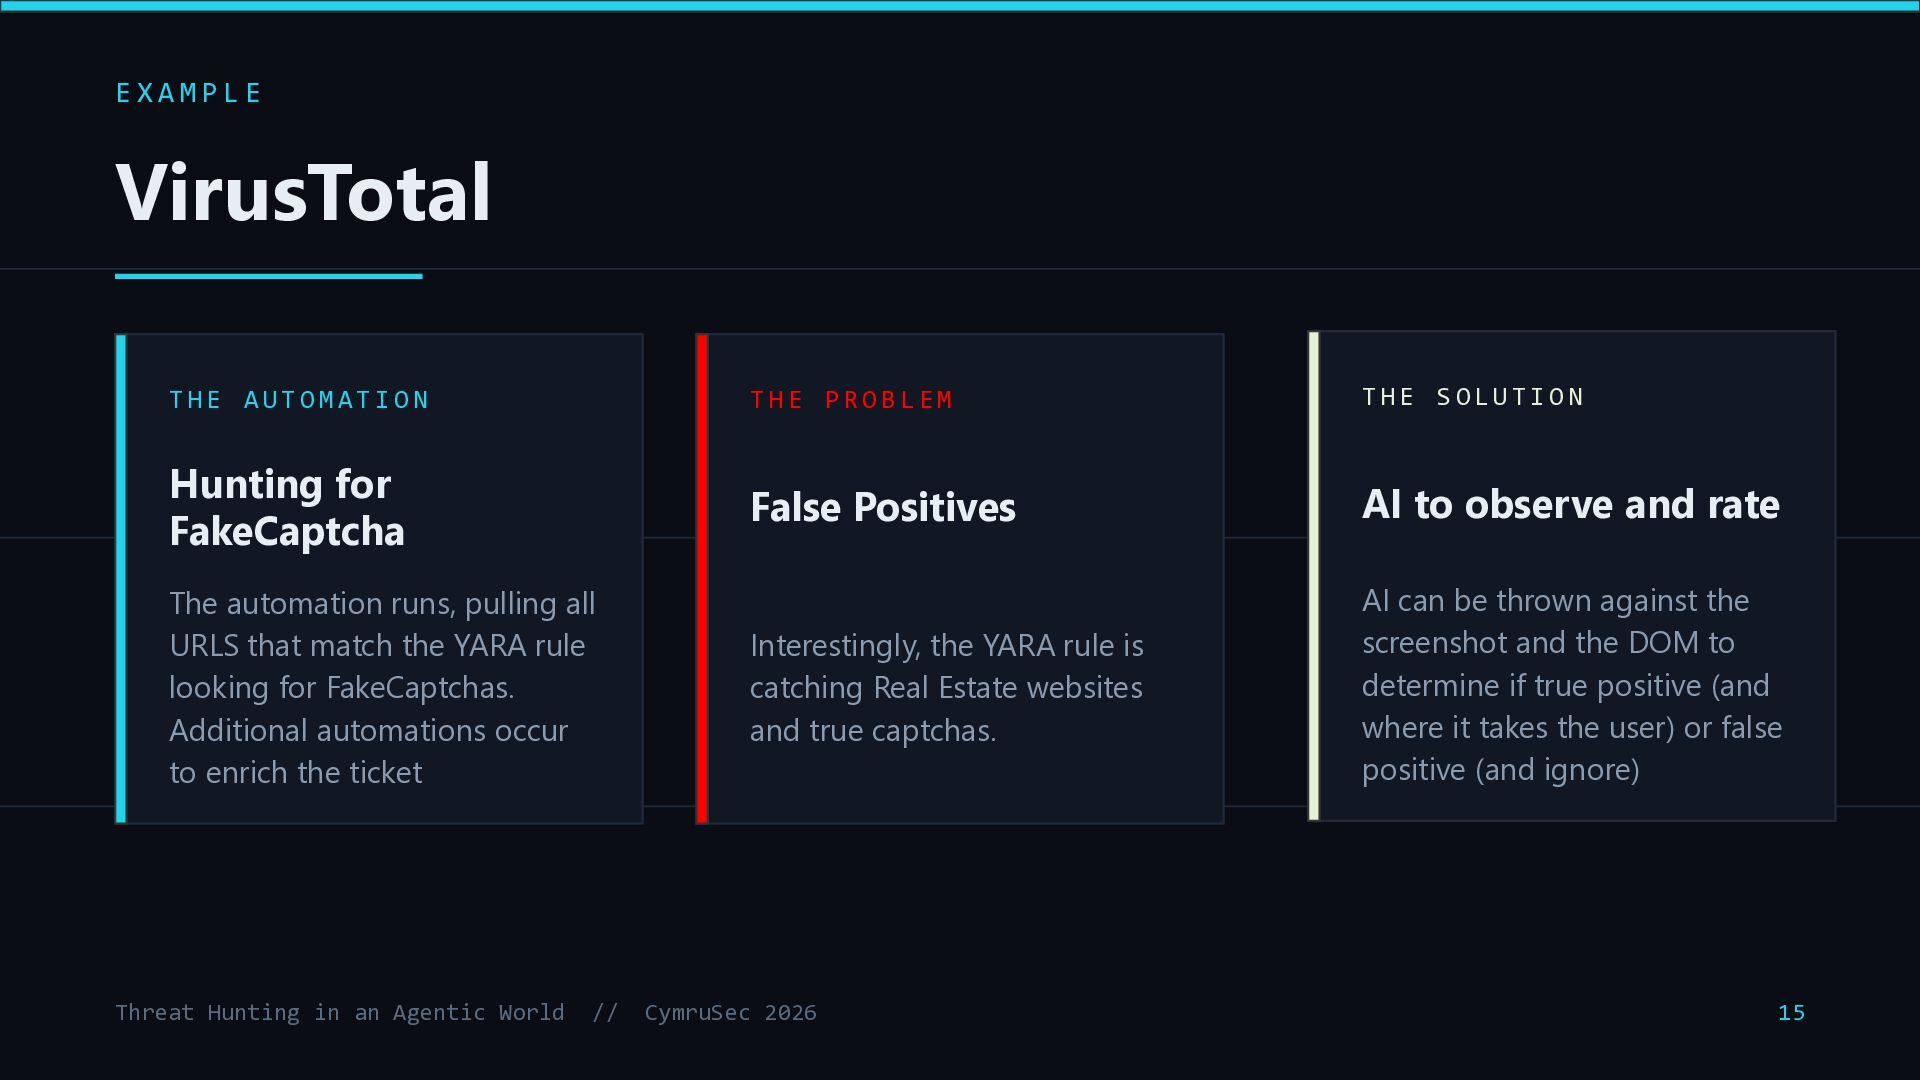
  39. EXAMPLE VirusTotal THE AUTOMATION THE PROBLEM THE SOLUTION Hunting for

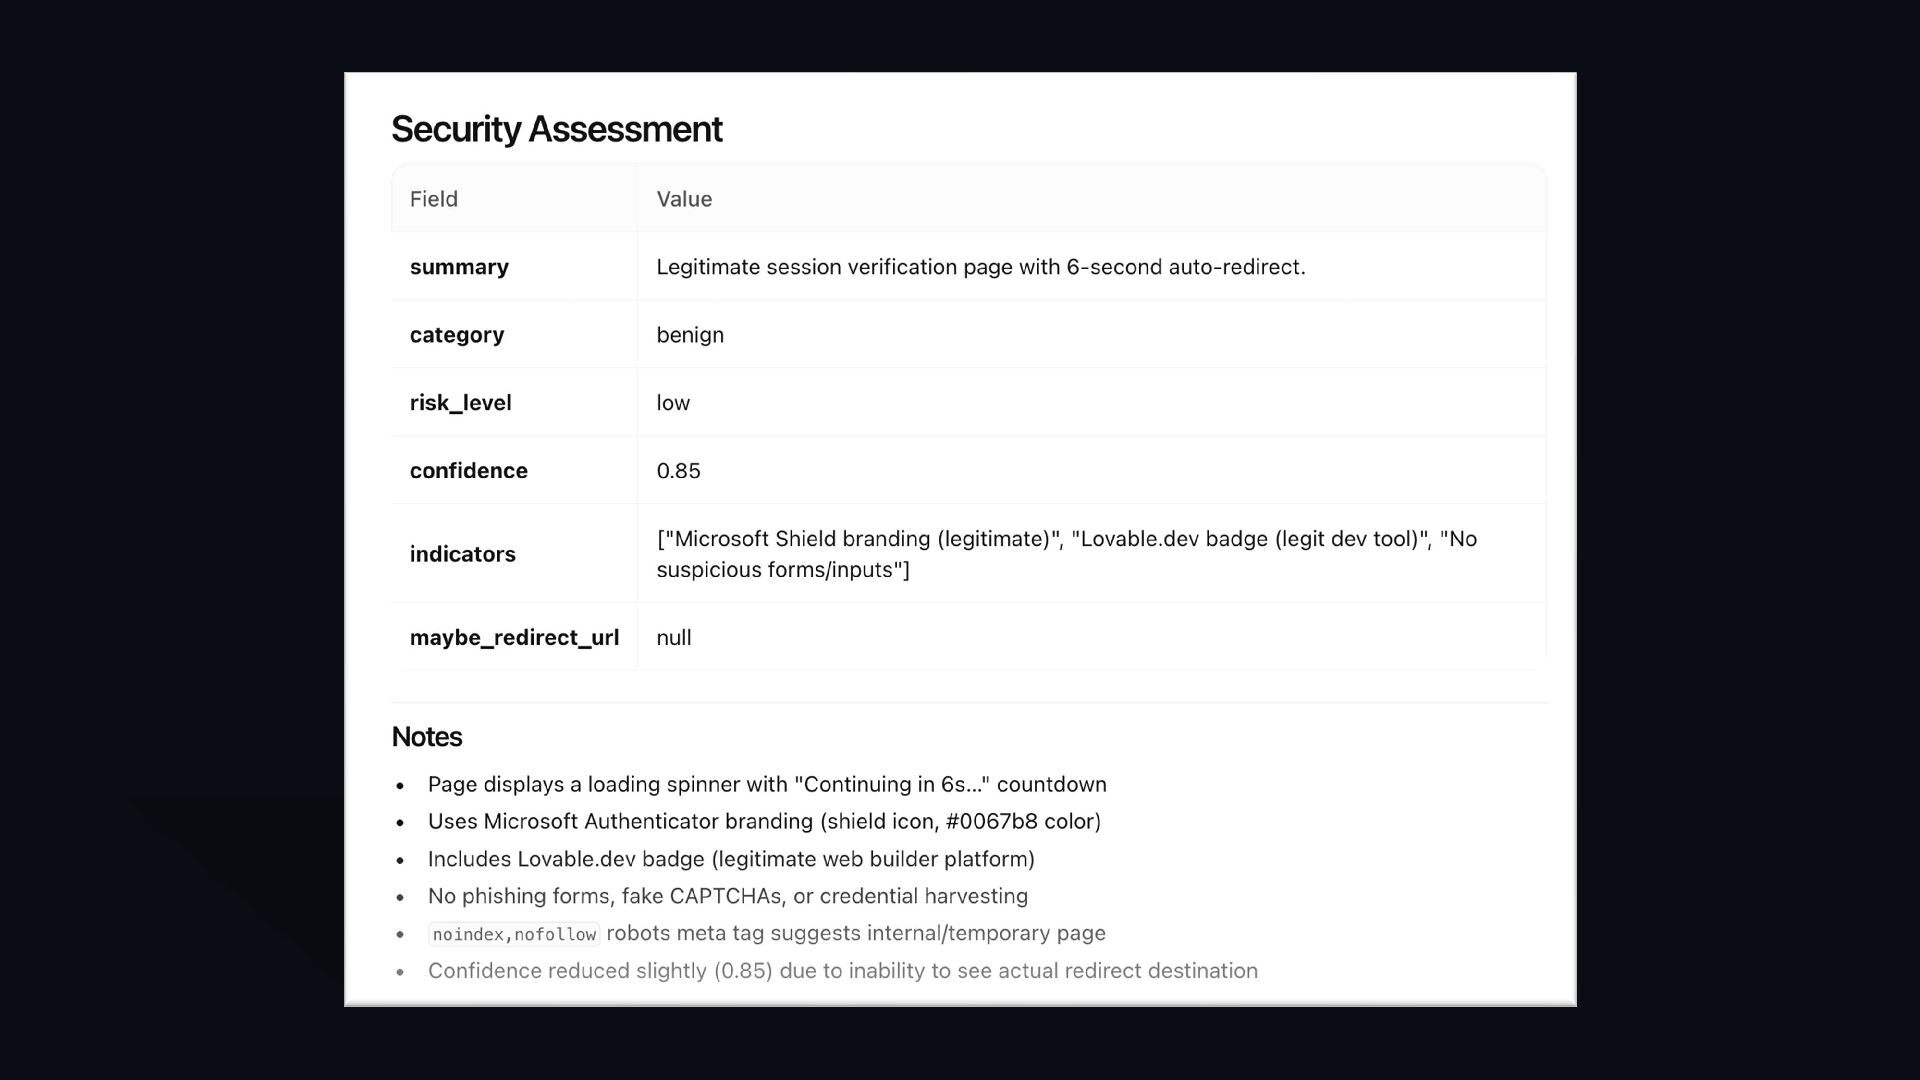
    FakeCaptcha False Positives AI to observe and rate Interestingly, the YARA rule is catching Real Estate websites and true captchas. AI can be thrown against the screenshot and the DOM to determine if true positive (and where it takes the user) or false positive (and ignore) The automation runs, pulling all URLS that match the YARA rule looking for FakeCaptchas. Additional automations occur to enrich the ticket Threat Hunting in an Agentic World // CymruSec 2026 15
  40. CymruSec 2026 HOW IDENTITY GAPS BECAME AN ATTACKER'S QUICKEST WIN

    How everyday identity indiscipline clears a path to sensitive resources Ray Manash · Head: IAM Technical Consultant ManageEngine UK
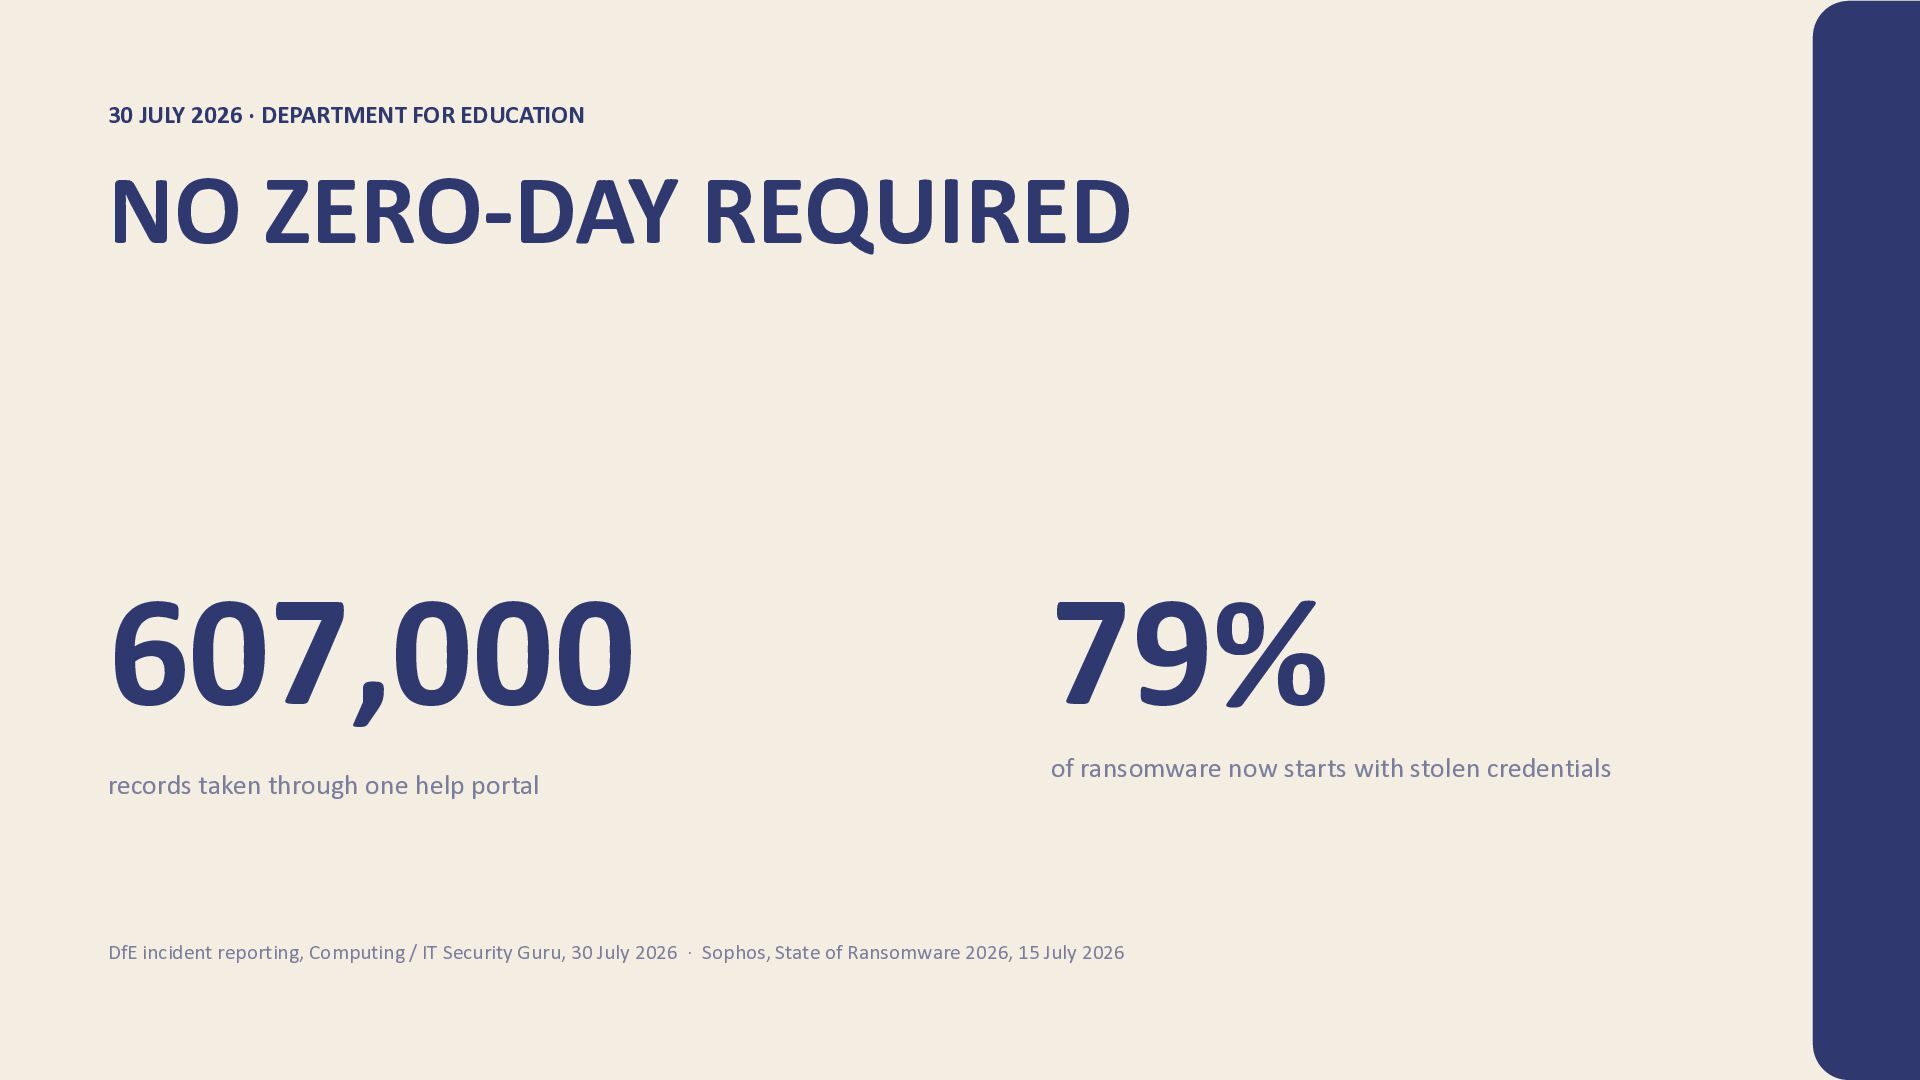
  41. 30 JULY 2026 · DEPARTMENT FOR EDUCATION NO ZERO-DAY REQUIRED

    607,000 records taken through one help portal 79% of ransomware now starts with stolen credentials DfE incident reporting, Computing / IT Security Guru, 30 July 2026 · Sophos, State of Ransomware 2026, 15 July 2026
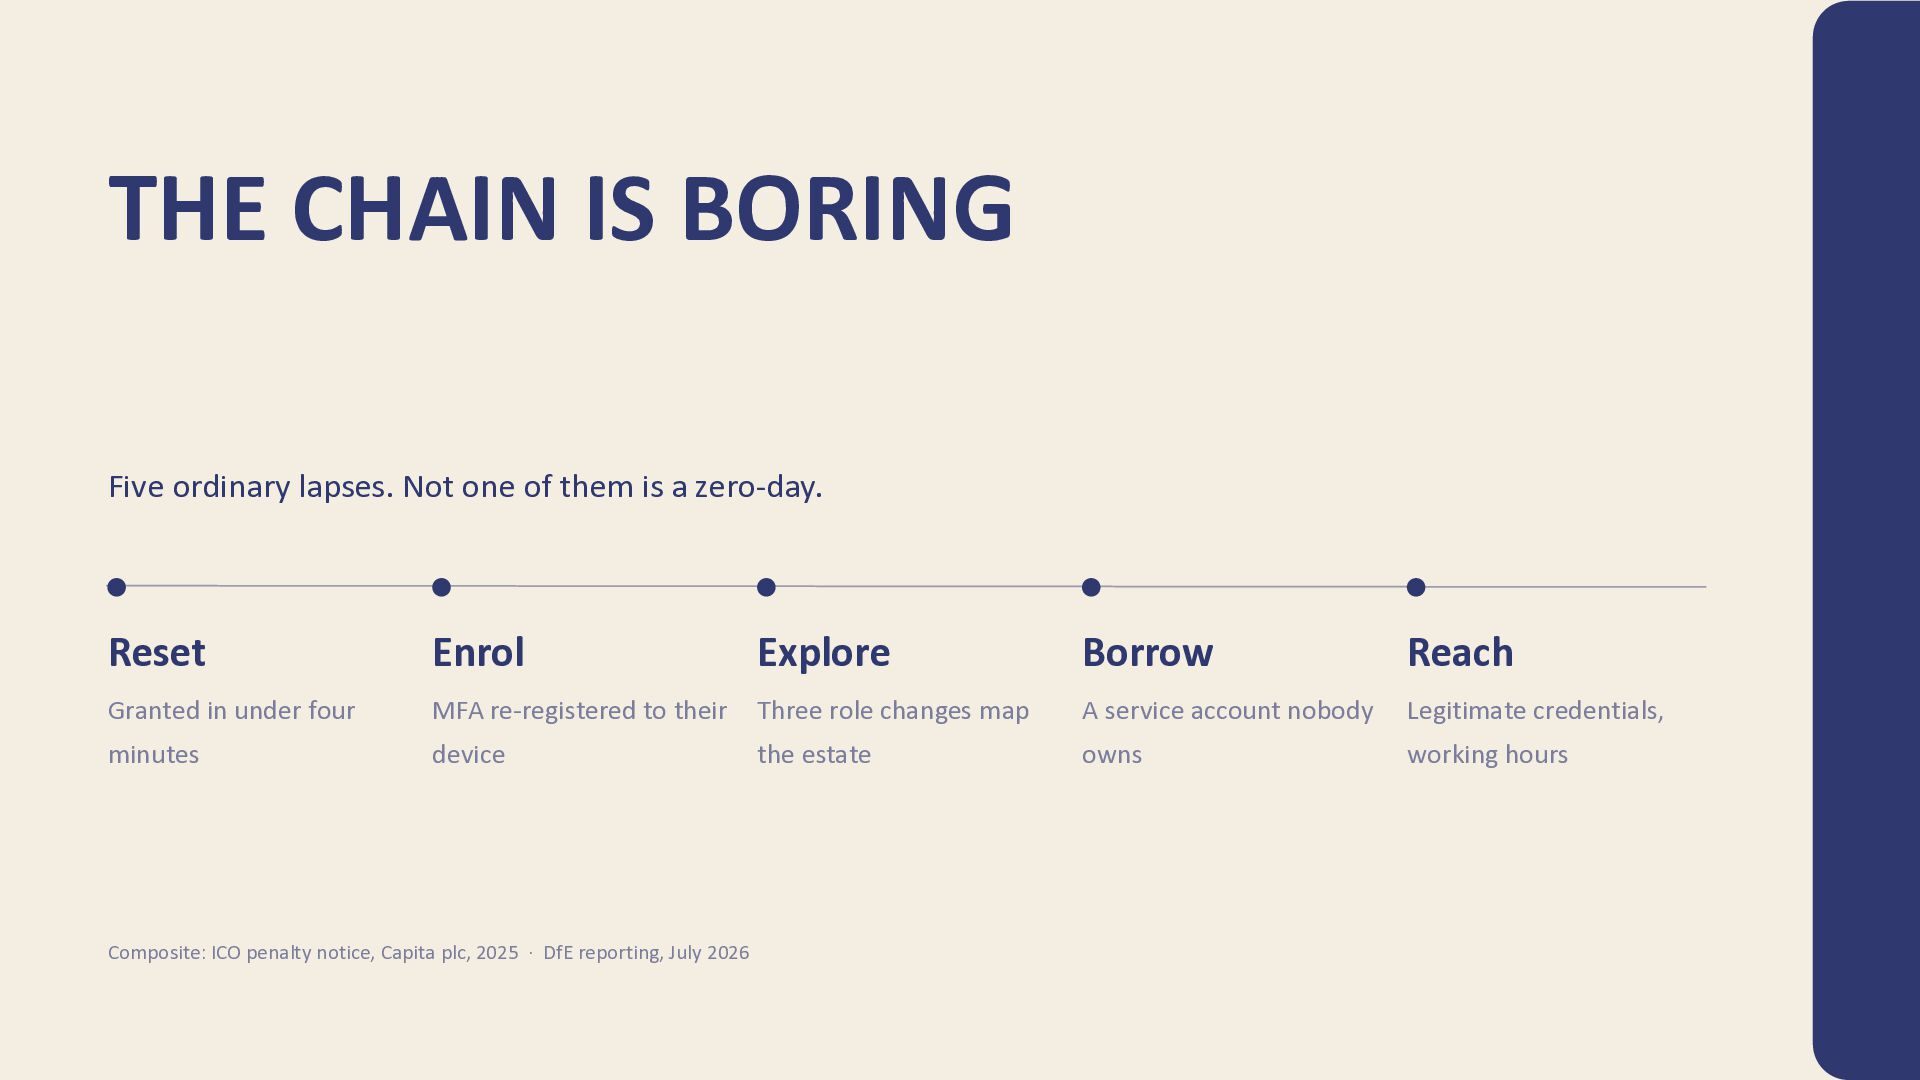
  42. THE CHAIN IS BORING Five ordinary lapses. Not one of

    them is a zero-day. Reset Enrol Explore Borrow Reach Granted in under four MFA re-registered to their Three role changes map A service account nobody Legitimate credentials, minutes device the estate owns working hours Composite: ICO penalty notice, Capita plc, 2025 · DfE reporting, July 2026
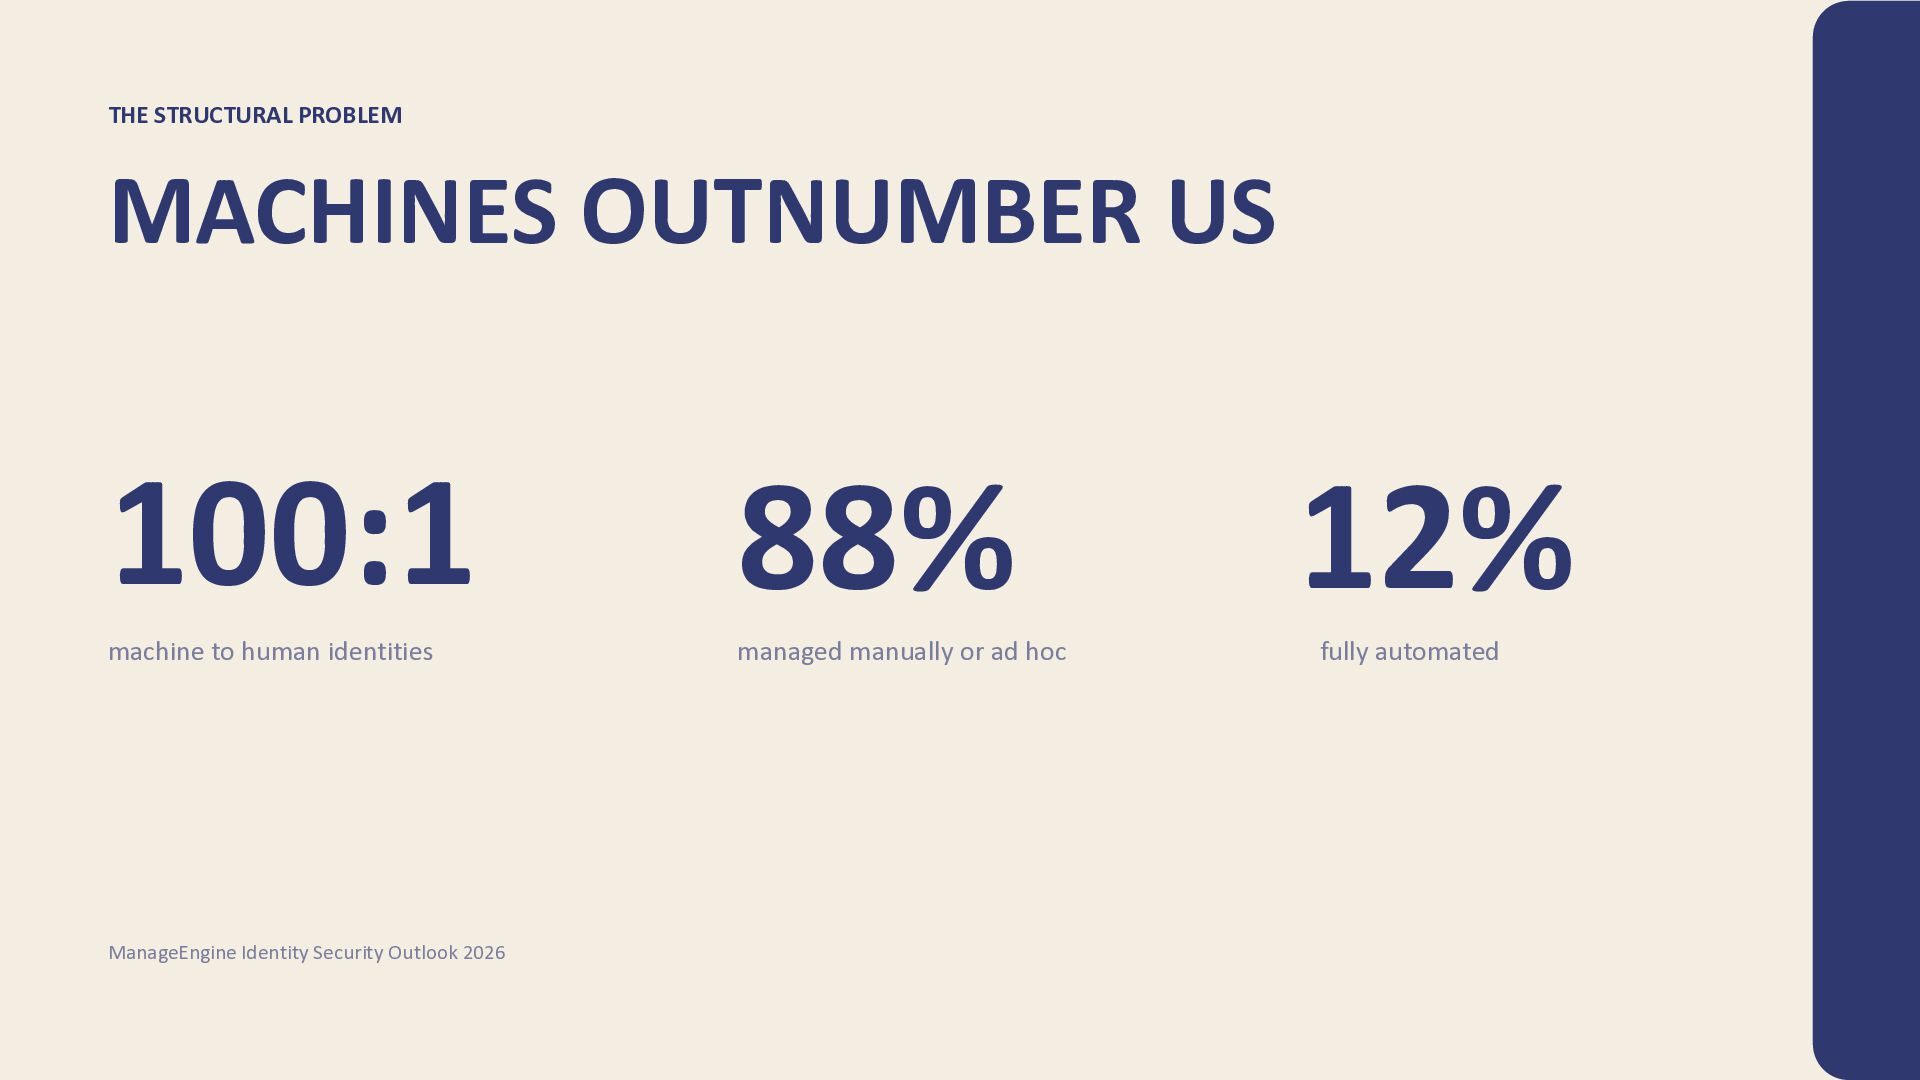
  43. THE STRUCTURAL PROBLEM MACHINES OUTNUMBER US 100:1 machine to human

    identities ManageEngine Identity Security Outlook 2026 88% managed manually or ad hoc 12% fully automated
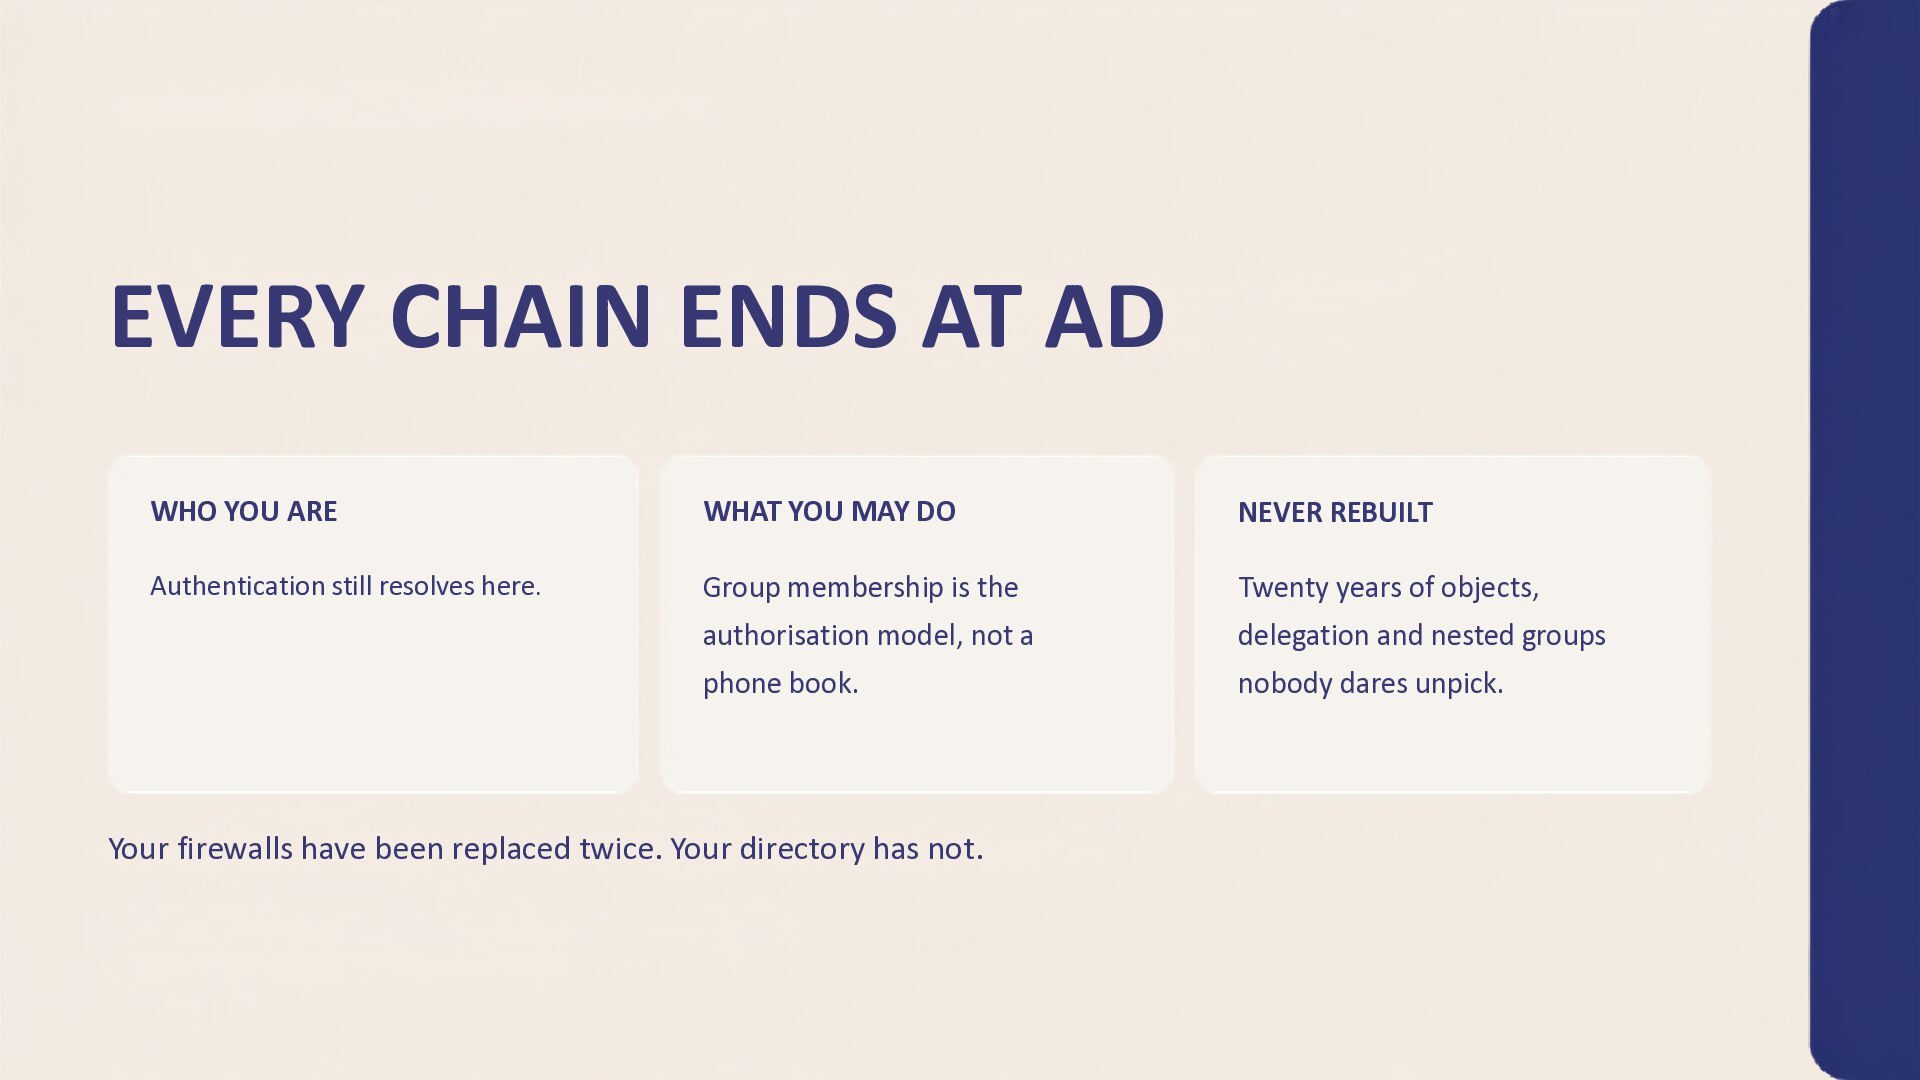
  44. EVERY CHAIN ENDS AT AD WHO YOU ARE WHAT YOU

    MAY DO NEVER REBUILT Authentication still resolves here. Group membership is the Twenty years of objects, authorisation model, not a delegation and nested groups phone book. nobody dares unpick. Your firewalls have been replaced twice. Your directory has not.
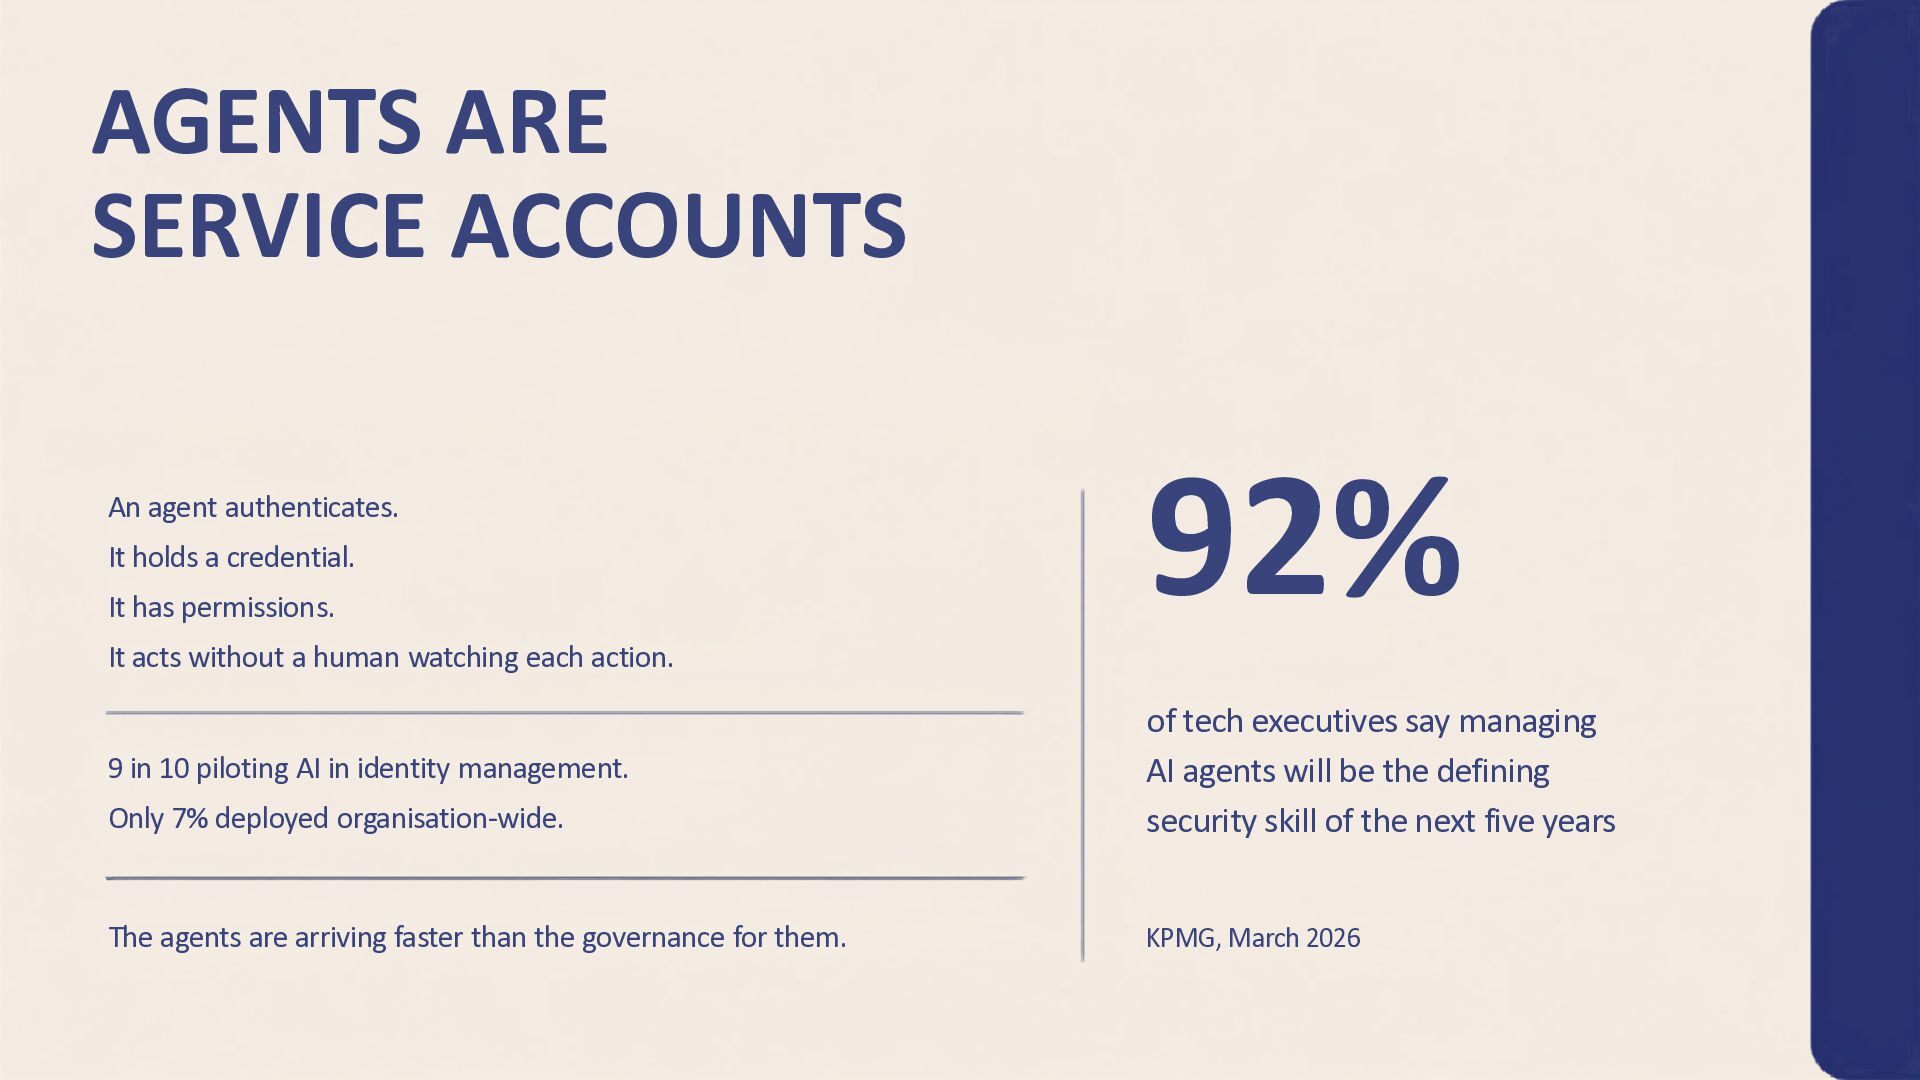
  45. AGENTS ARE SERVICE ACCOUNTS An agent authenticates. It holds a

    credential. It has permissions. It acts without a human watching each action. 92% Only 7% deployed organisation-wide. of tech executives say managing AI agents will be the defining security skill of the next five years The agents are arriving faster than the governance for them. KPMG, March 2026 9 in 10 piloting AI in identity management.
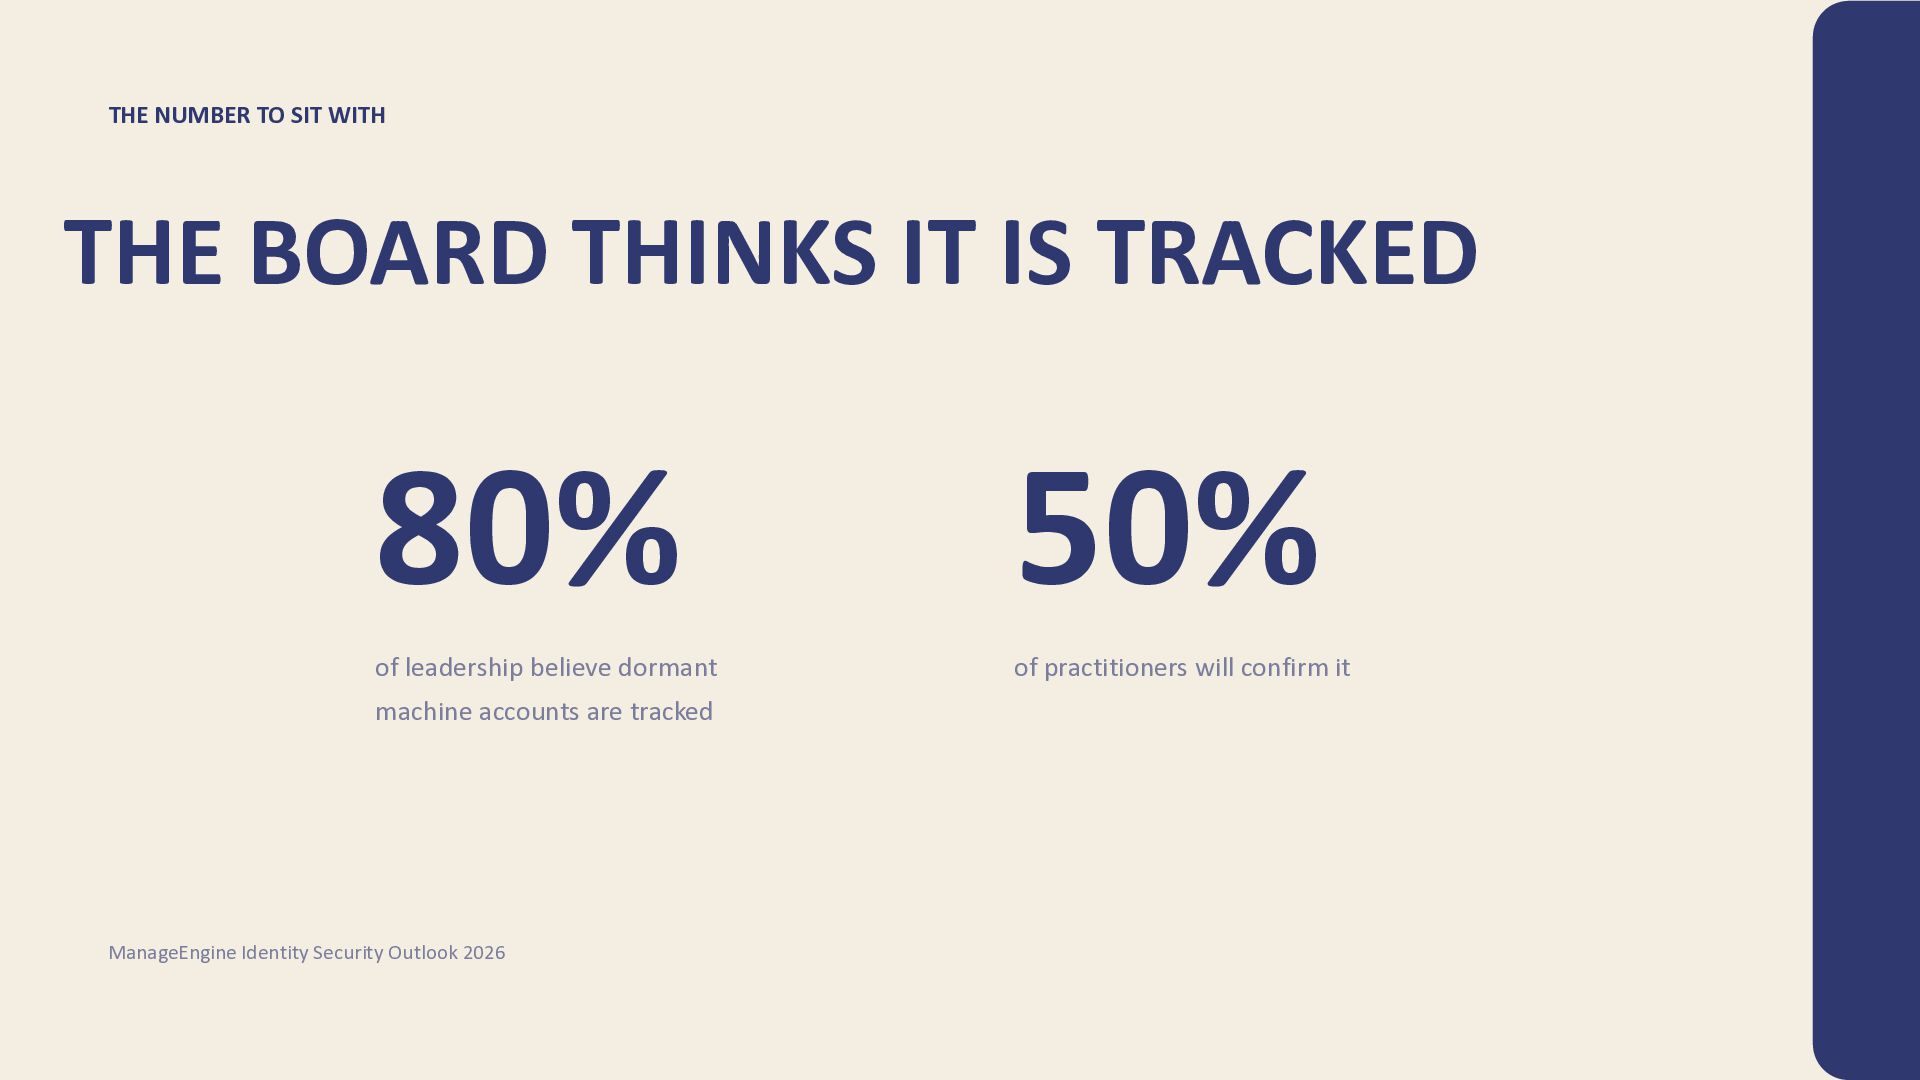
  46. THE NUMBER TO SIT WITH THE BOARD THINKS IT IS

    TRACKED 80% 50% of leadership believe dormant of practitioners will confirm it machine accounts are tracked ManageEngine Identity Security Outlook 2026
  47. FOUR A WEEK 204 nationally significant incidents, year to August

    2025 NCSC Annual Review 2025, covering September 2024 to August 2025
  48. THE FIRST JOB GOVERN THE ESTATE Leavers still on email

    Reviews on spreadsheets No account owner Privilege creep unseen Lifecycle driven from Certification routed to Every identity gets a Segregation of duties HR attributes real owners named owner and attack paths ISO/IEC 27001:2022 A.5.16, A.5.18, A.8.2 · NCSC CAF B2 Identity and Access Control
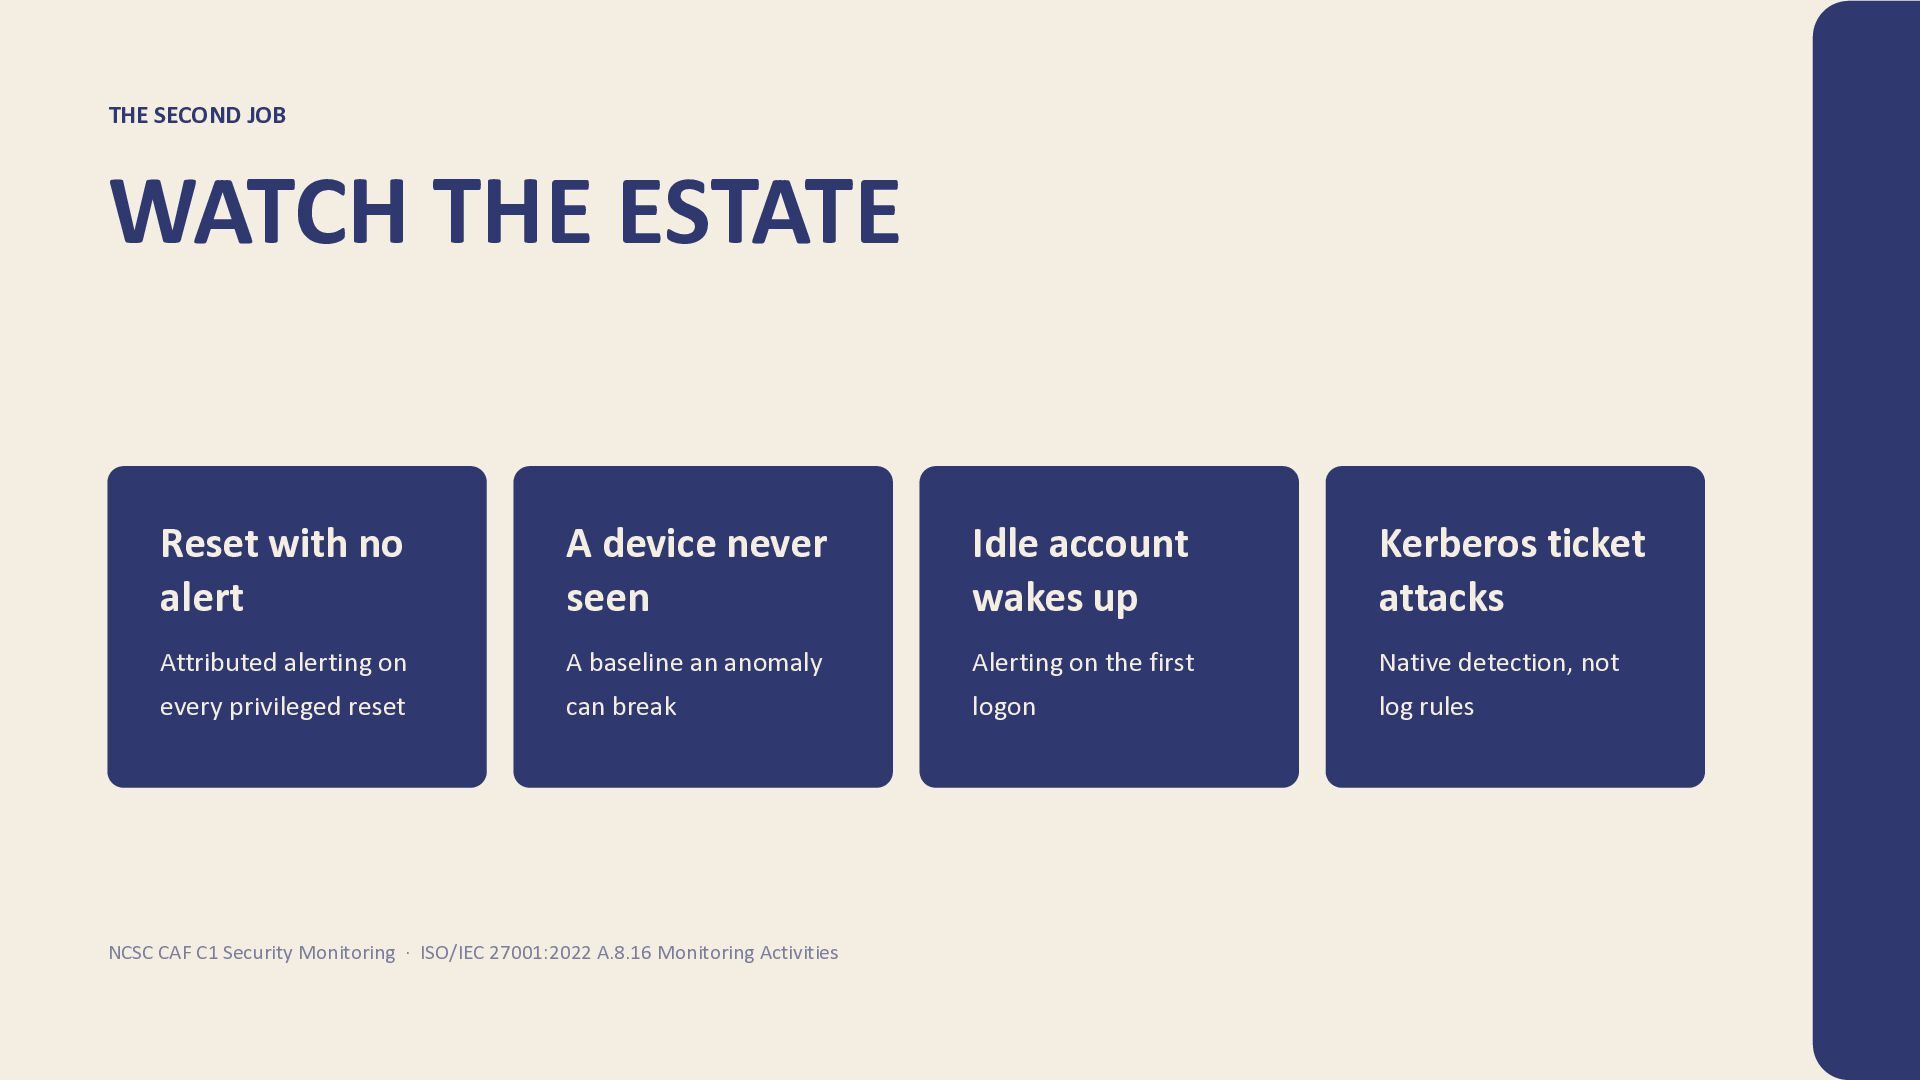
  49. THE SECOND JOB WATCH THE ESTATE Reset with no alert

    A device never seen Idle account wakes up Kerberos ticket attacks Attributed alerting on A baseline an anomaly Alerting on the first Native detection, not every privileged reset can break logon log rules NCSC CAF C1 Security Monitoring · ISO/IEC 27001:2022 A.8.16 Monitoring Activities
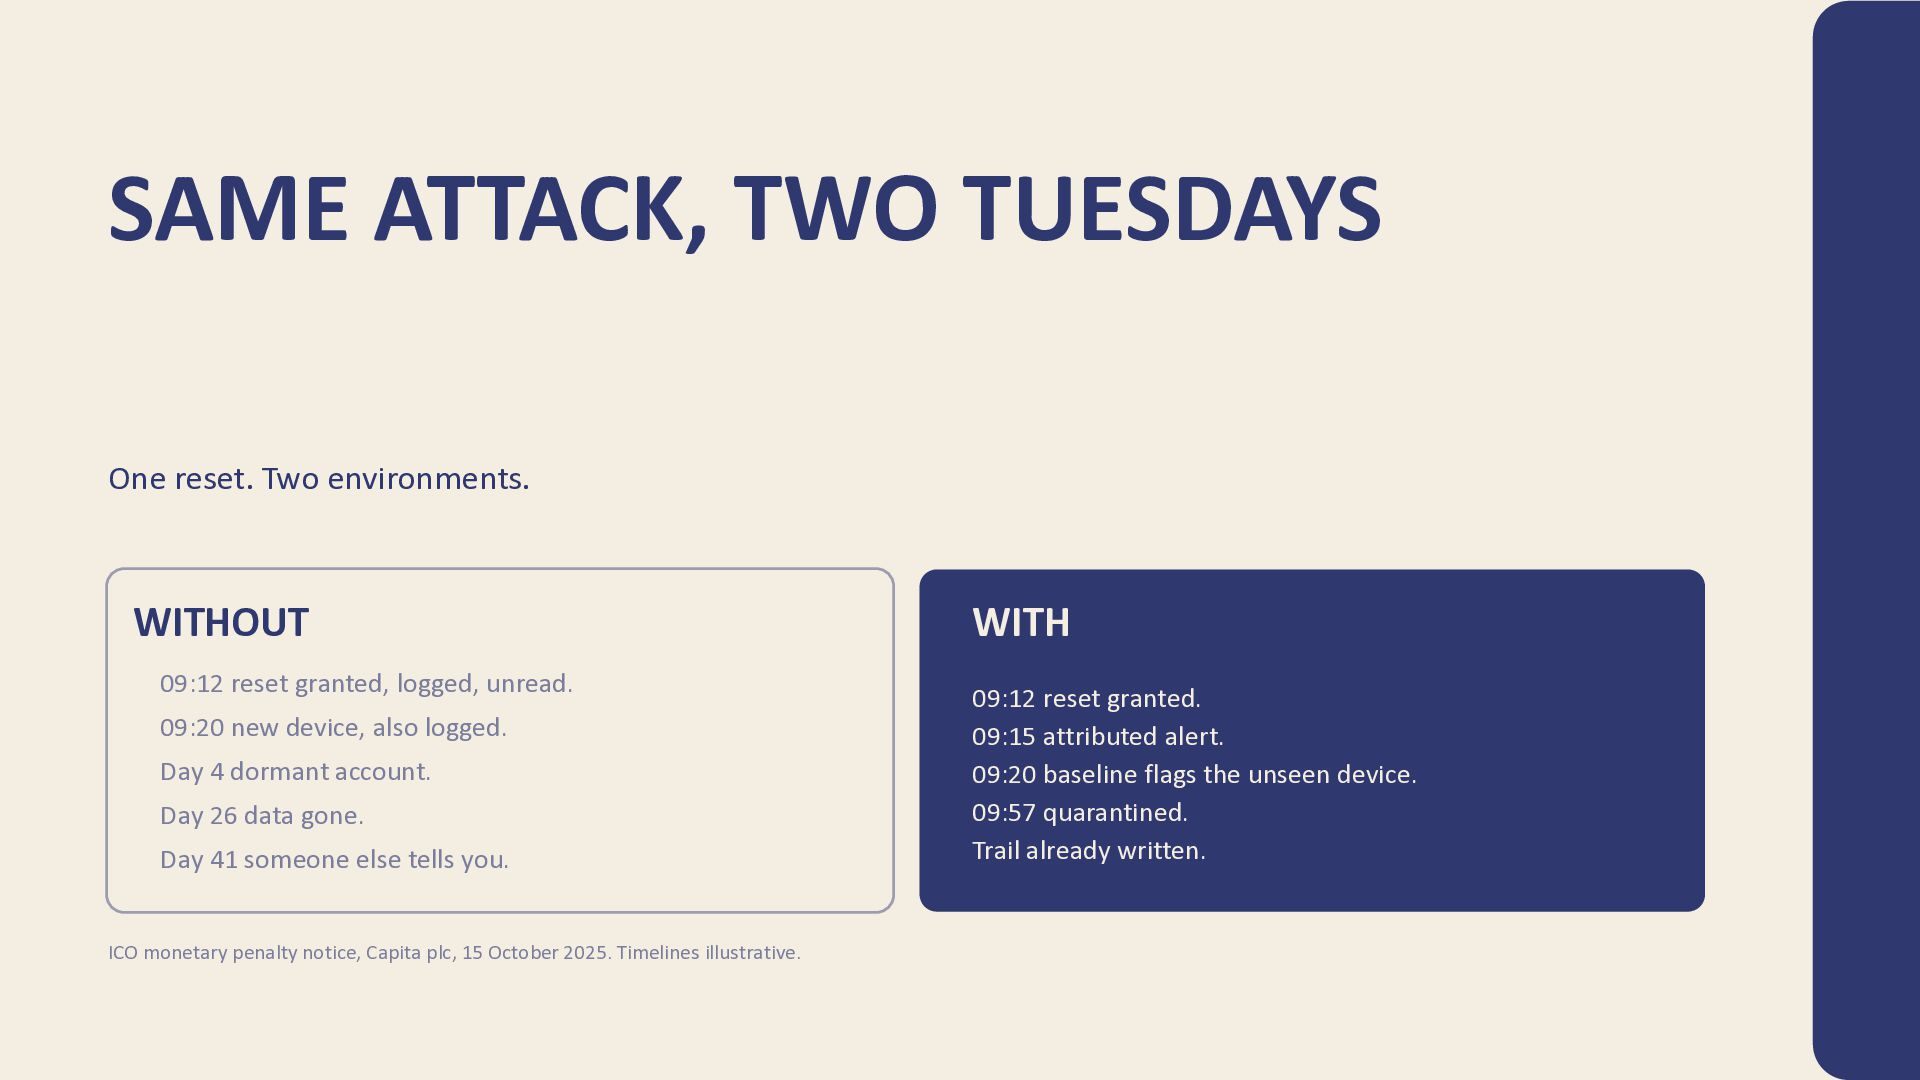
  50. SAME ATTACK, TWO TUESDAYS One reset. Two environments. WITHOUT 09:12

    reset granted, logged, unread. 09:20 new device, also logged. Day 4 dormant account. Day 26 data gone. Day 41 someone else tells you. ICO monetary penalty notice, Capita plc, 15 October 2025. Timelines illustrative. WITH 09:12 reset granted. 09:15 attributed alert. 09:20 baseline flags the unseen device. 09:57 quarantined. Trail already written.
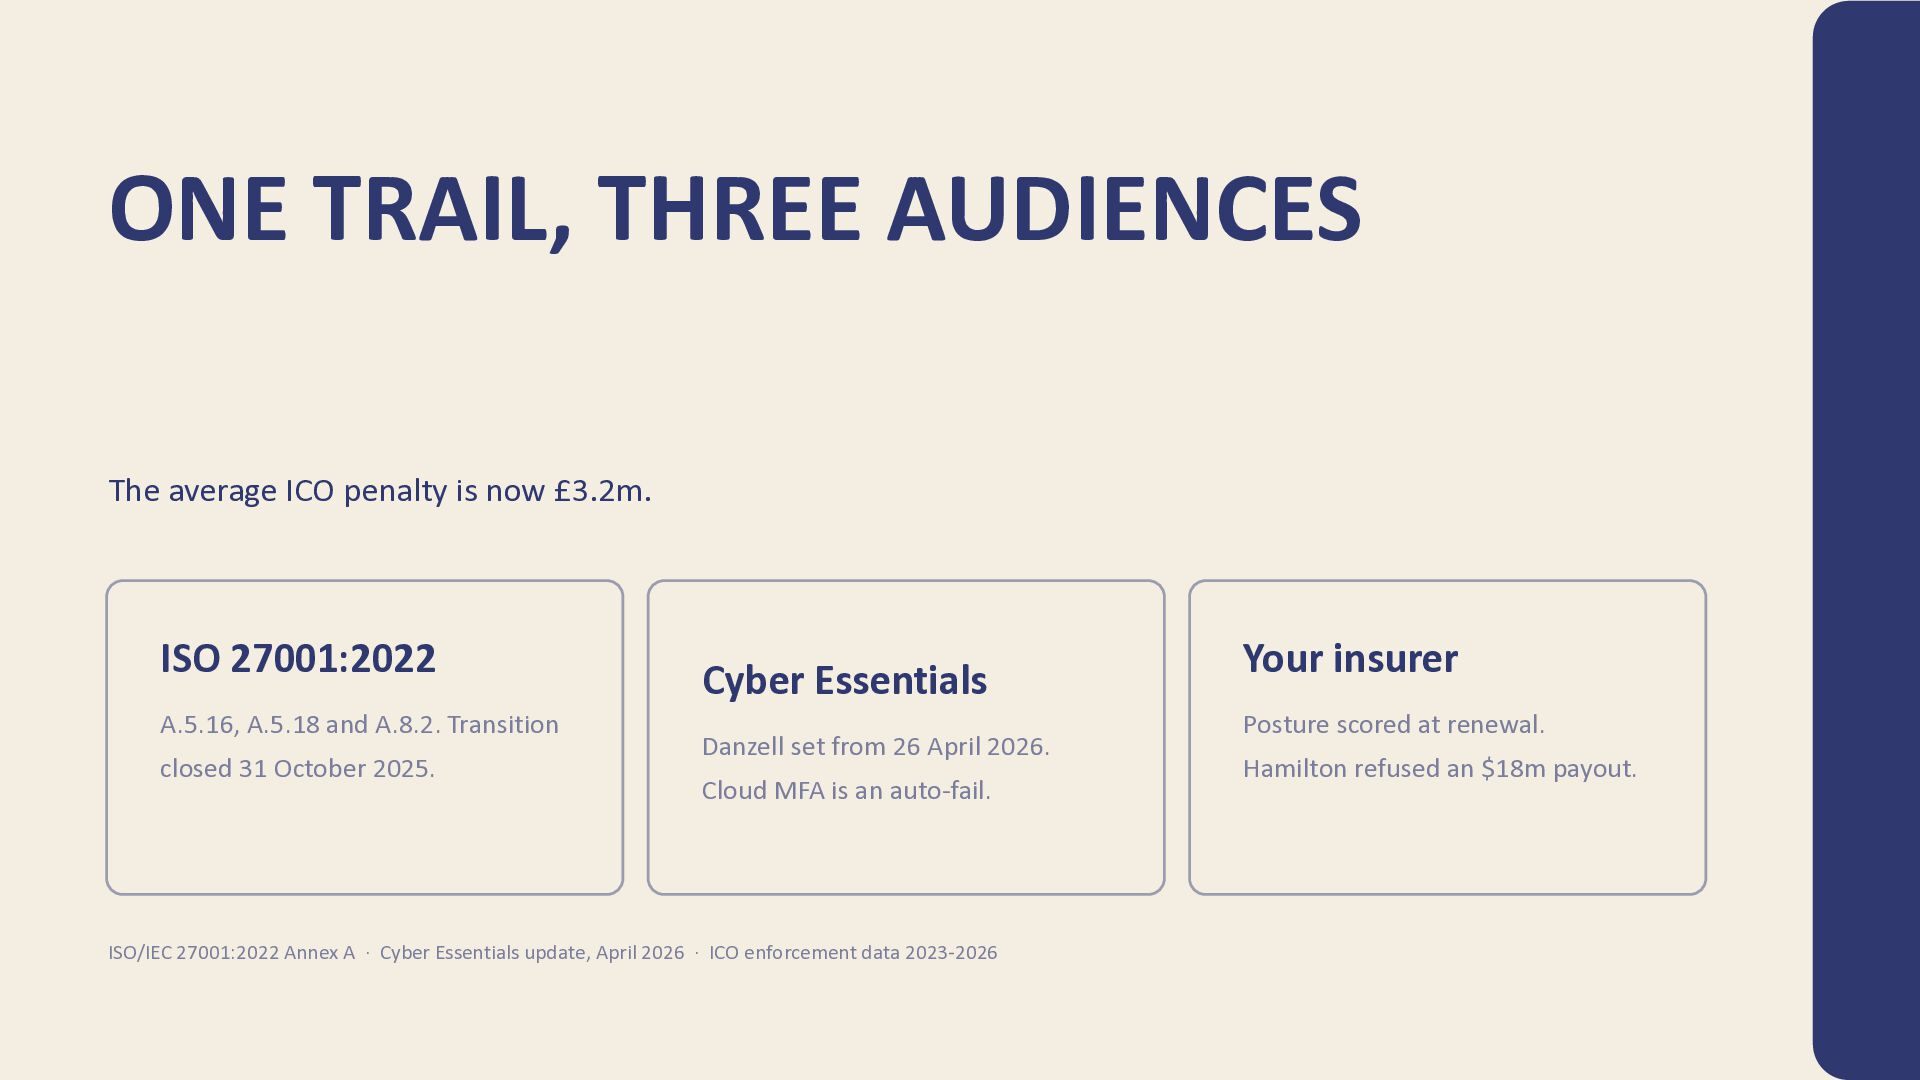
  51. ONE TRAIL, THREE AUDIENCES The average ICO penalty is now

    £3.2m. ISO 27001:2022 A.5.16, A.5.18 and A.8.2. Transition closed 31 October 2025. Cyber Essentials Danzell set from 26 April 2026. Cloud MFA is an auto-fail. ISO/IEC 27001:2022 Annex A · Cyber Essentials update, April 2026 · ICO enforcement data 2023-2026 Your insurer Posture scored at renewal. Hamilton refused an $18m payout.
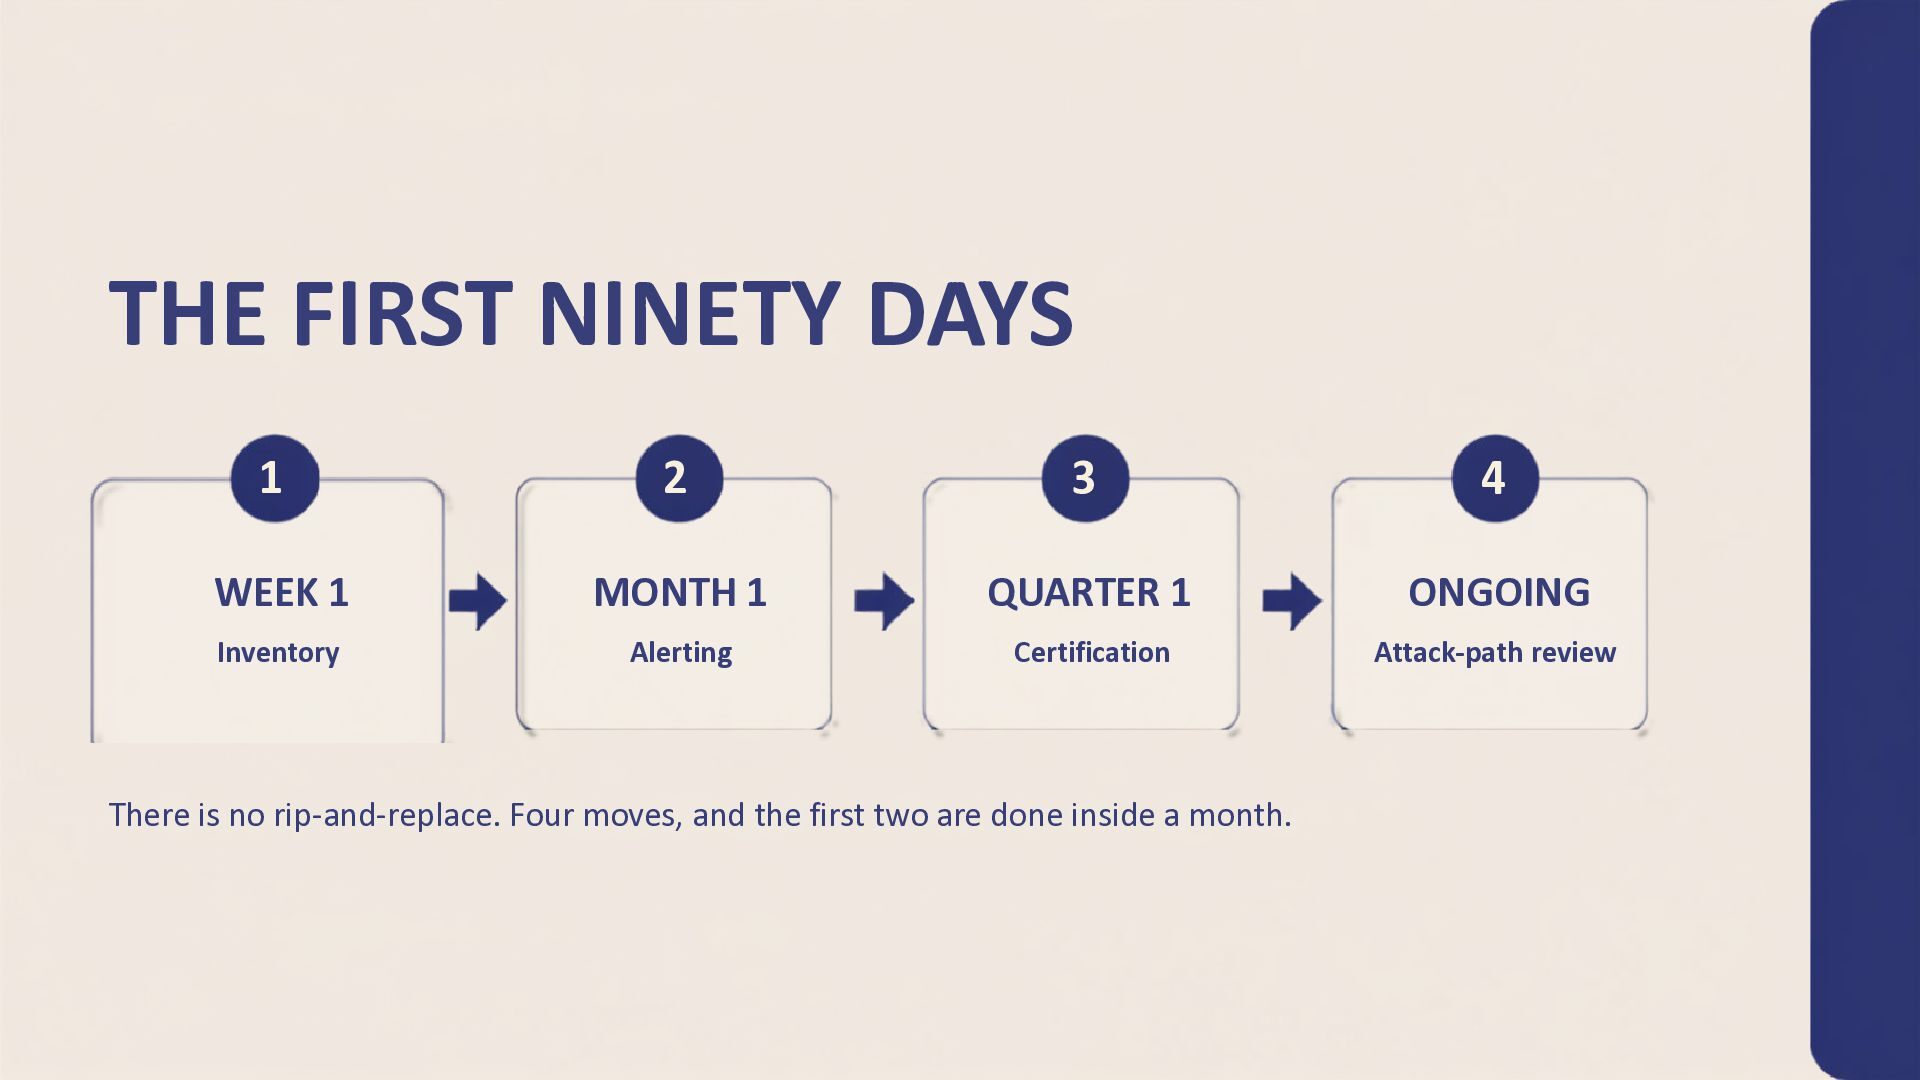
  52. THE FIRST NINETY DAYS 1 2 3 4 WEEK 1

    MONTH 1 QUARTER 1 ONGOING Inventory Alerting Certification Attack-path review There is no rip-and-replace. Four moves, and the first two are done inside a month.
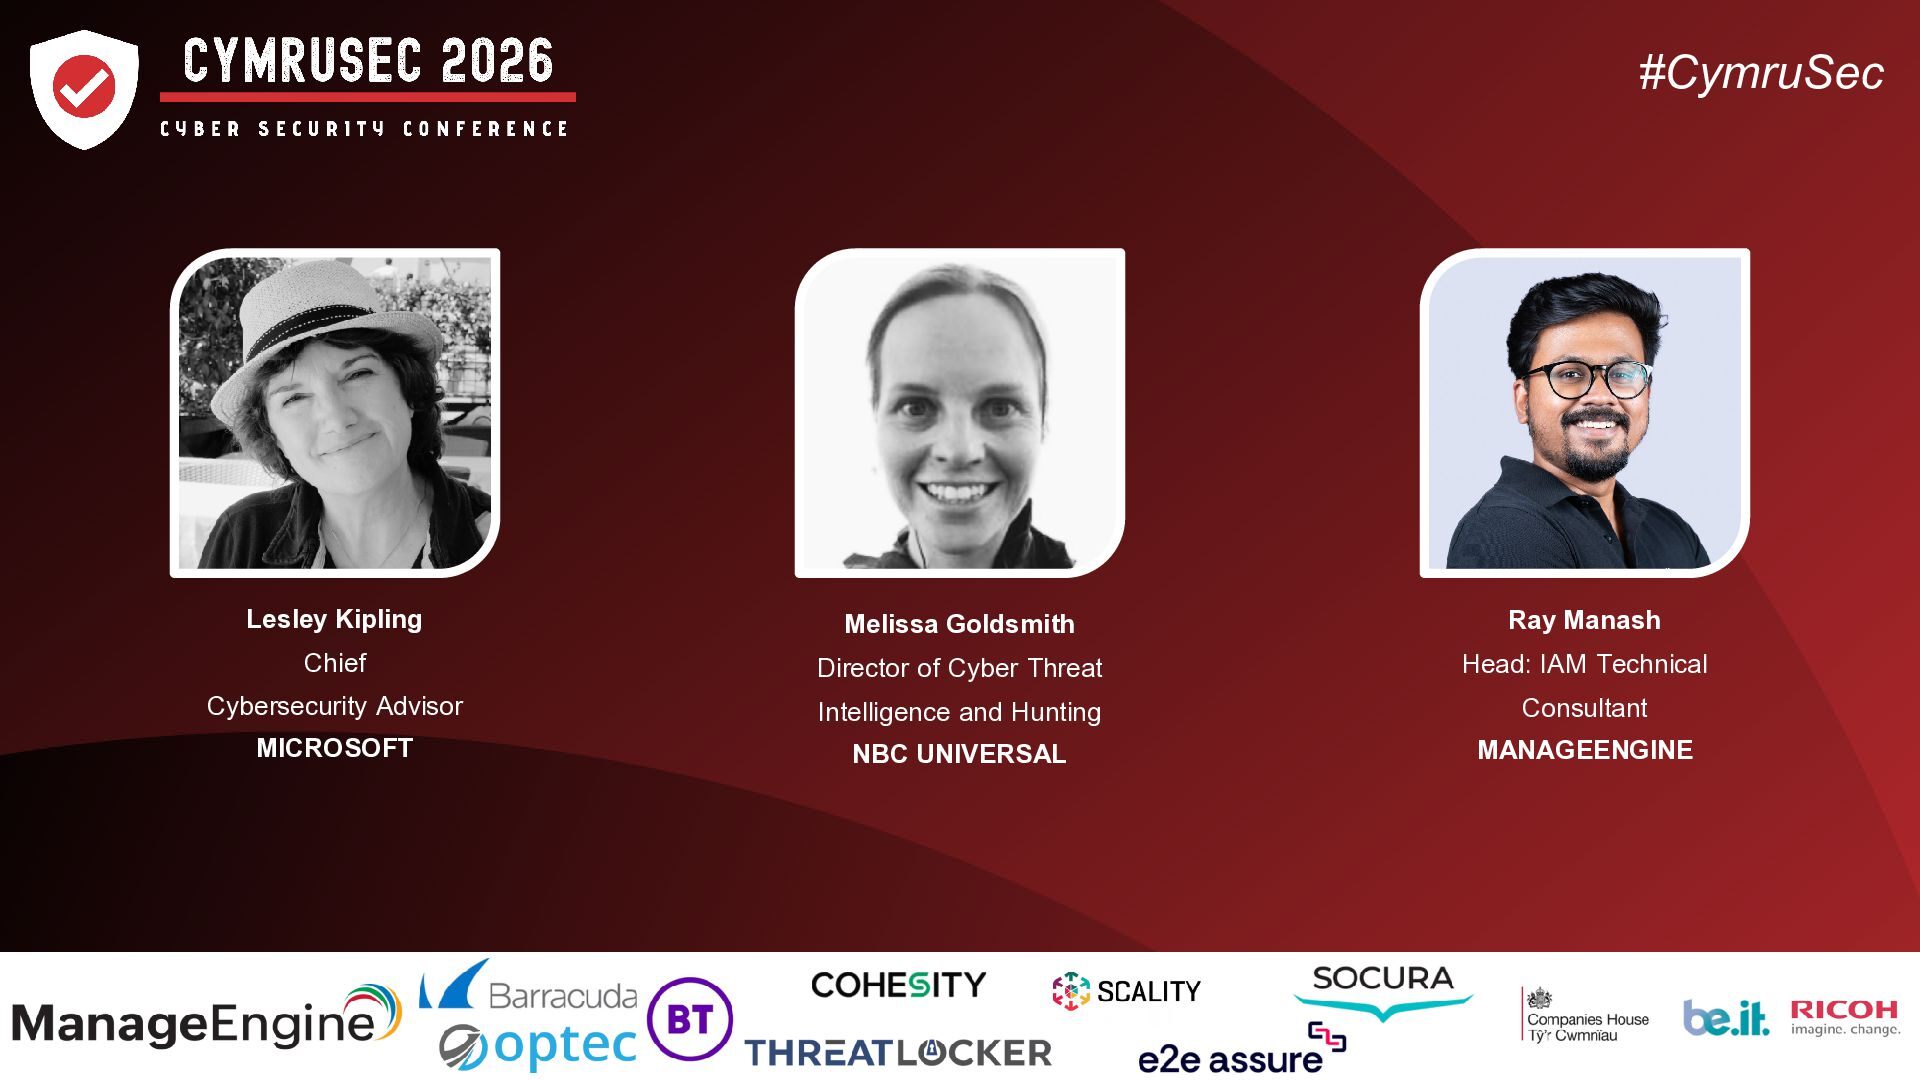
  53. #CymruSec Lesley Kipling Chief Cybersecurity Advisor MICROSOFT Melissa Goldsmith Director

    of Cyber Threat Intelligence and Hunting NBC UNIVERSAL Ray Manash Head: IAM Technical Consultant MANAGEENGINE
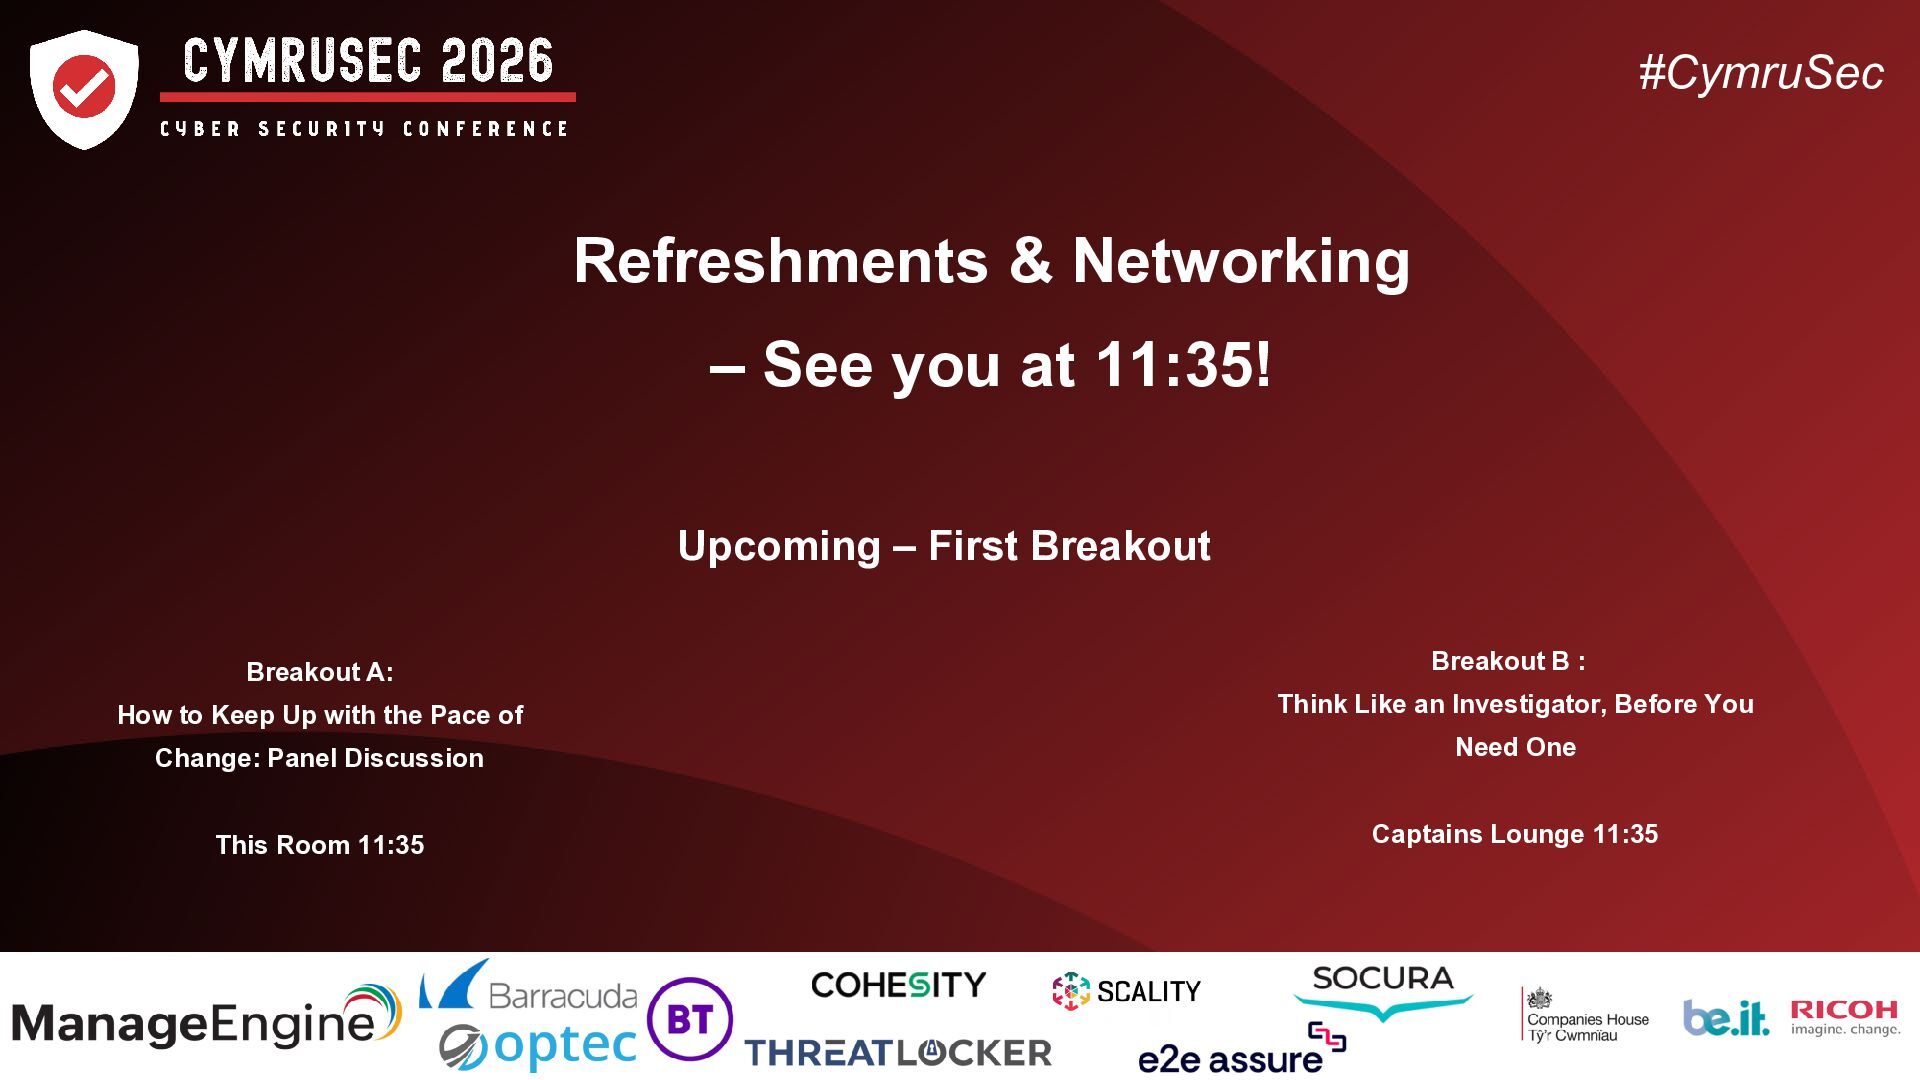
  54. #CymruSec Refreshments & Networking – See you at 11:35! Upcoming

    – First Breakout Breakout A: How to Keep Up with the Pace of Change: Panel Discussion Breakout B : Think Like an Investigator, Before You Need One This Room 11:35 Captains Lounge 11:35
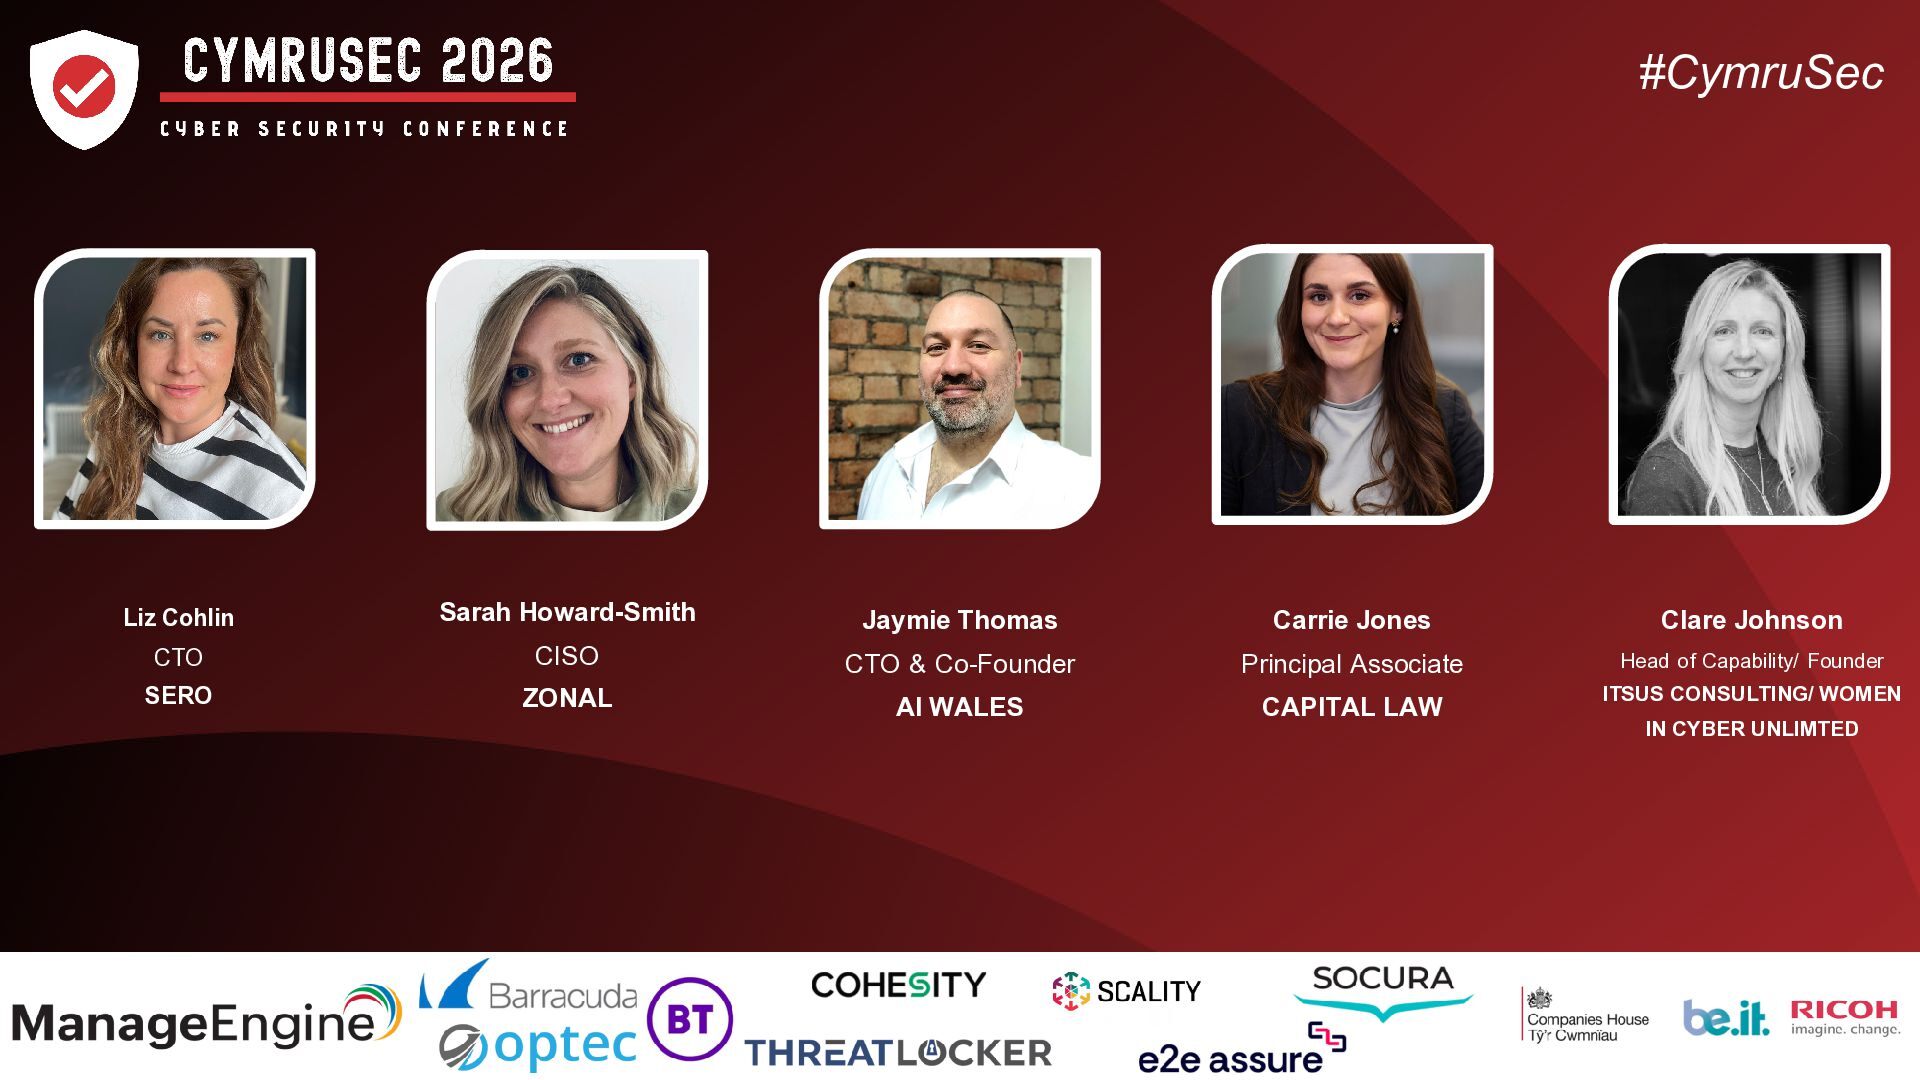
  55. #CymruSec Liz Cohlin CTO SERO Sarah Howard-Smith CISO ZONAL Jaymie

    Thomas CTO & Co-Founder AI WALES Carrie Jones Principal Associate CAPITAL LAW Clare Johnson Head of Capability/ Founder ITSUS CONSULTING/ WOMEN IN CYBER UNLIMTED
  56. #CymruSec Coming next – Second Breakout Breakout C: Thieves Don’t

    Break In… They Log In: Secure Your M365 in Minutes, Not Months​ Breakout D: Cyber Threats are Evolving Faster than Organisations can Adapt - and AI is Raising the Stakes Captains Lounge 12:15 This Room 12:15
  57. CYBER THREATS ARE EVOLVING FASTER THAN ORGANISATIONS CAN ADAPT And

    AI is raising the stakes CymruSec Summit 2026 | Cardiff | 22 October 2026 Ishaque Mir | Security Advisory Manager, BT 1
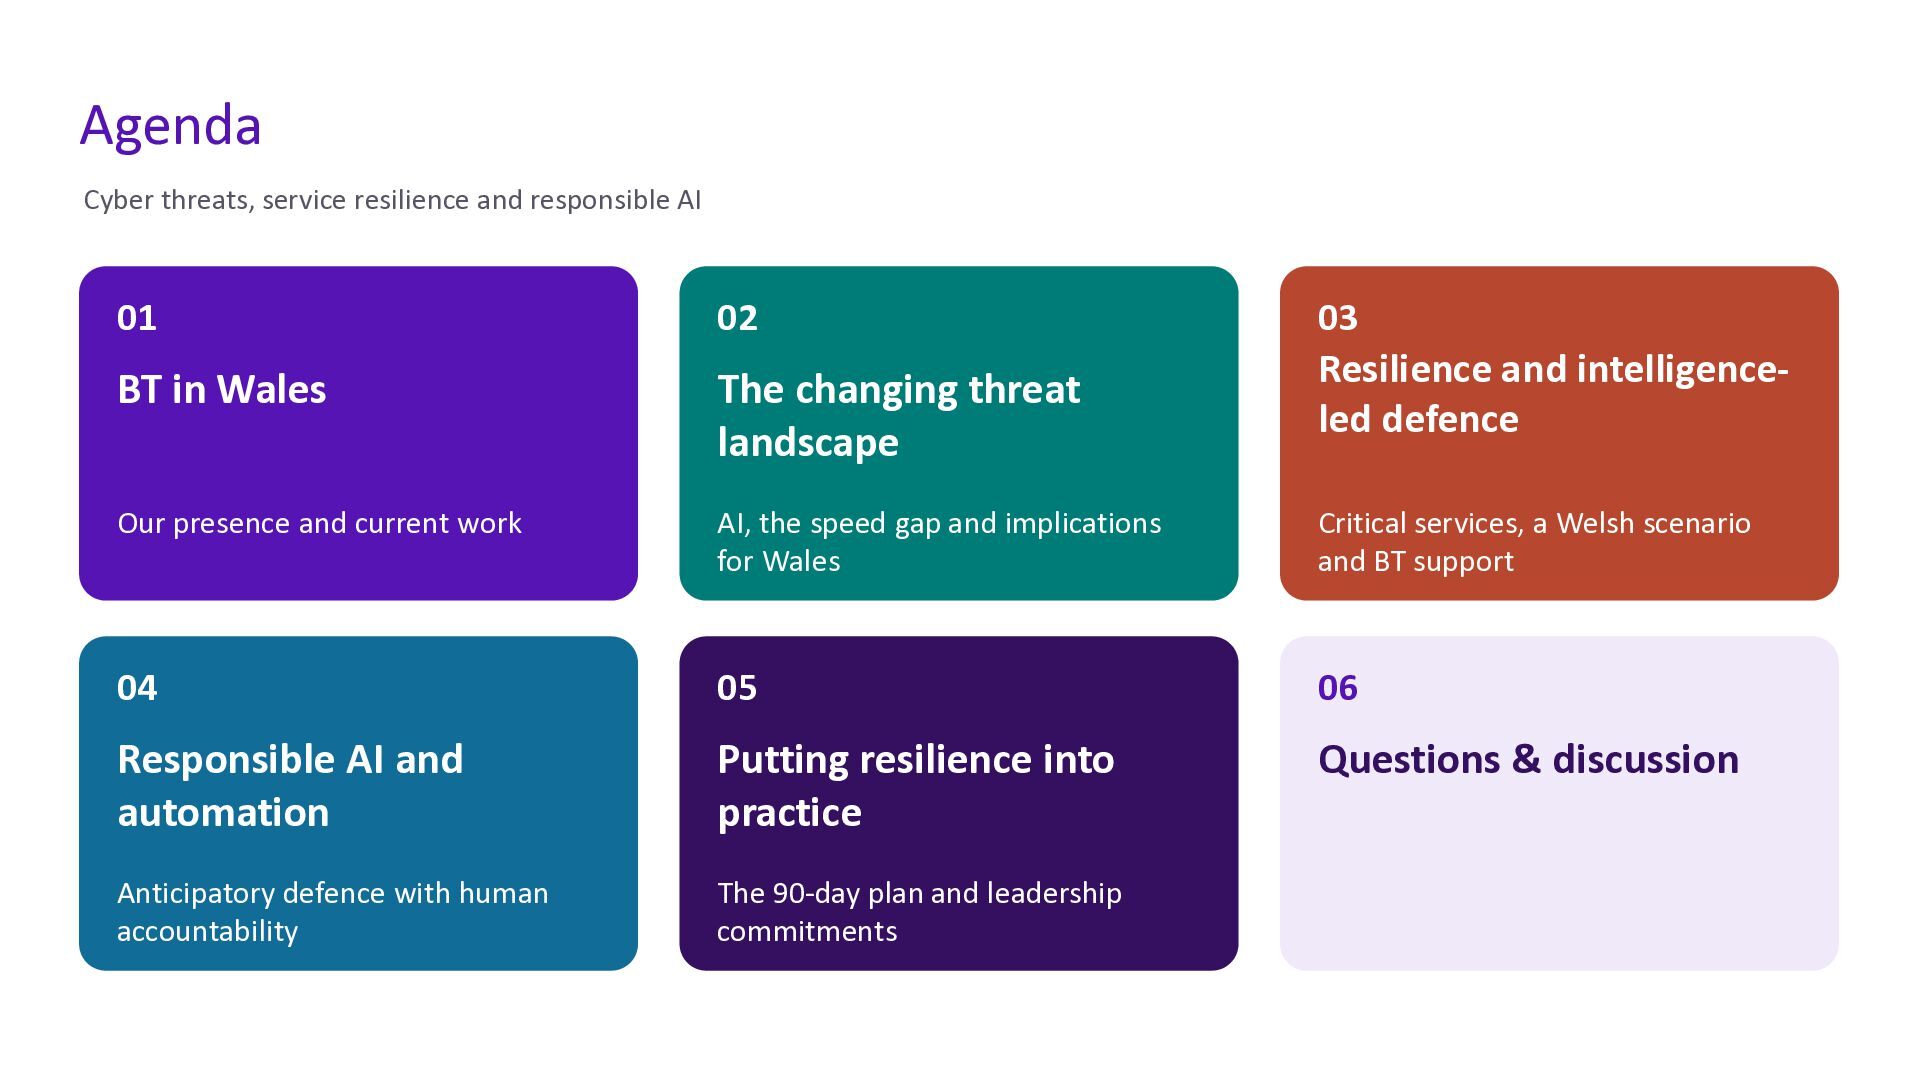
  58. Agenda Cyber threats, service resilience and responsible AI 01 02

    03 Resilience and intelligenceled defence BT in Wales The changing threat landscape Our presence and current work AI, the speed gap and implications for Wales Critical services, a Welsh scenario and BT support 04 05 06 Responsible AI and automation Putting resilience into practice Questions & discussion Anticipatory defence with human accountability The 90-day plan and leadership commitments
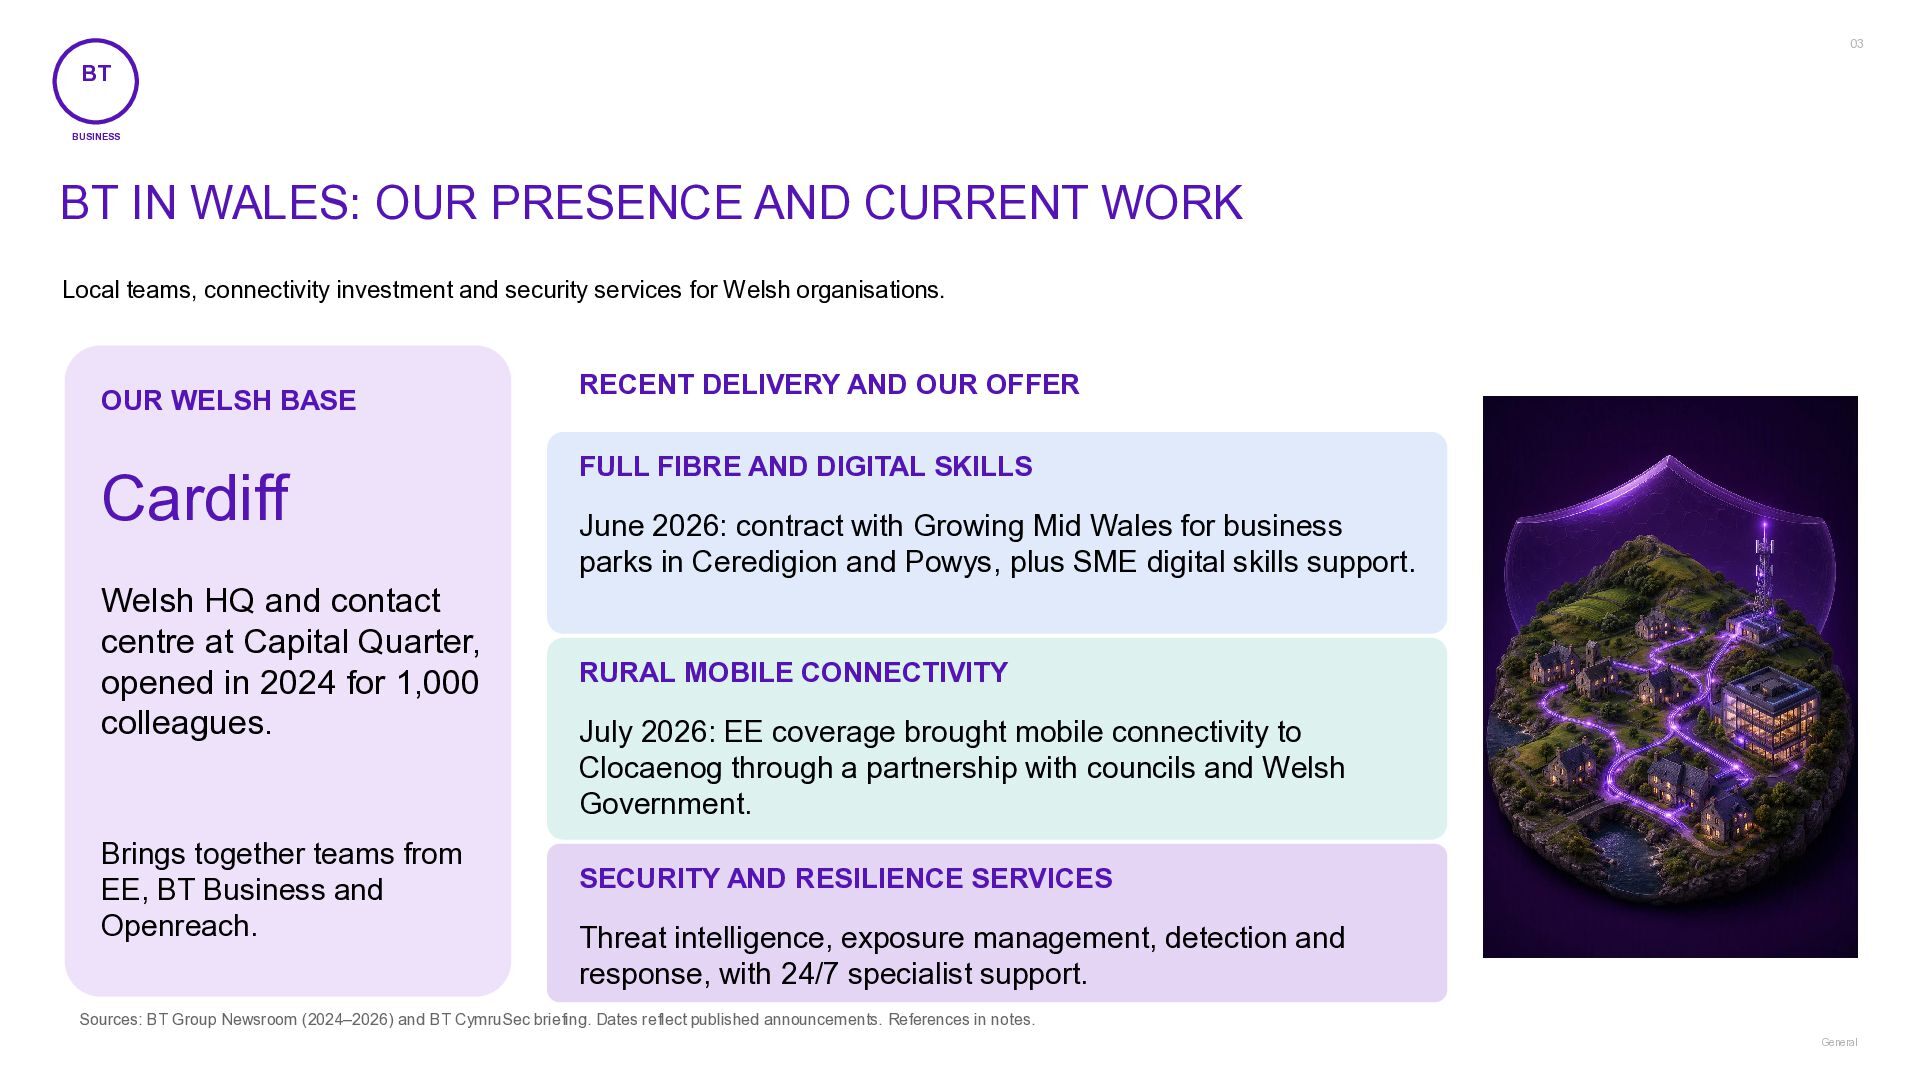
  59. 03 BT BUSINESS BT IN WALES: OUR PRESENCE AND CURRENT

    WORK Local teams, connectivity investment and security services for Welsh organisations. OUR WELSH BASE Cardiff Welsh HQ and contact centre at Capital Quarter, opened in 2024 for 1,000 colleagues. Brings together teams from EE, BT Business and Openreach. RECENT DELIVERY AND OUR OFFER FULL FIBRE AND DIGITAL SKILLS June 2026: contract with Growing Mid Wales for business parks in Ceredigion and Powys, plus SME digital skills support. RURAL MOBILE CONNECTIVITY July 2026: EE coverage brought mobile connectivity to Clocaenog through a partnership with councils and Welsh Government. SECURITY AND RESILIENCE SERVICES Threat intelligence, exposure management, detection and response, with 24/7 specialist support. Sources: BT Group Newsroom (2024–2026) and BT CymruSec briefing. Dates reflect published announcements. References in notes. General
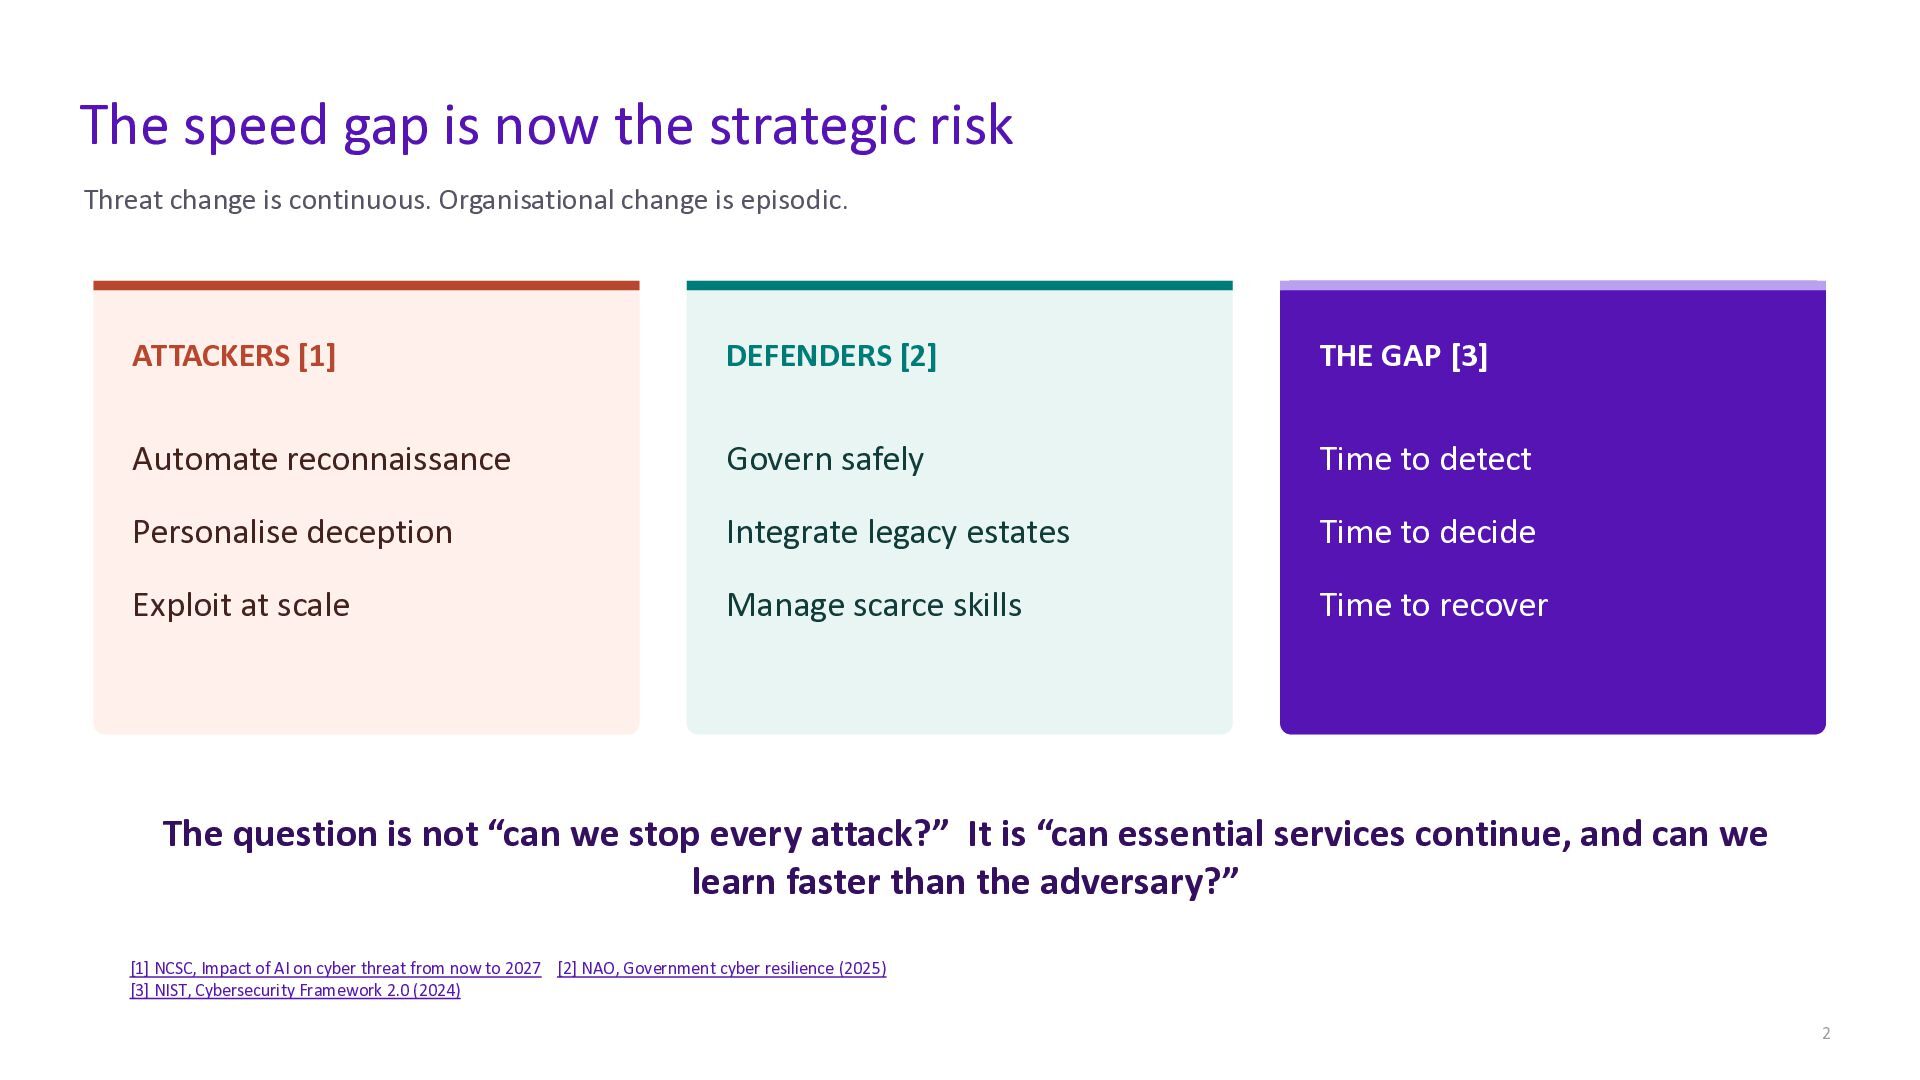
  60. The speed gap is now the strategic risk Threat change
    is continuous. Organisational change is episodic. ATTACKERS [1] DEFENDERS [2] THE GAP [3] Automate reconnaissance Govern safely Time to detect Personalise deception Integrate legacy estates Time to decide Exploit at scale Manage scarce skills Time to recover The question is not “can we stop every attack?” It is “can essential services continue, and can we learn faster than the adversary?” [1] NCSC, Impact of AI on cyber threat from now to 2027 [2] NAO, Government cyber resilience (2025) [3] NIST, Cybersecurity Framework 2.0 (2024) 2
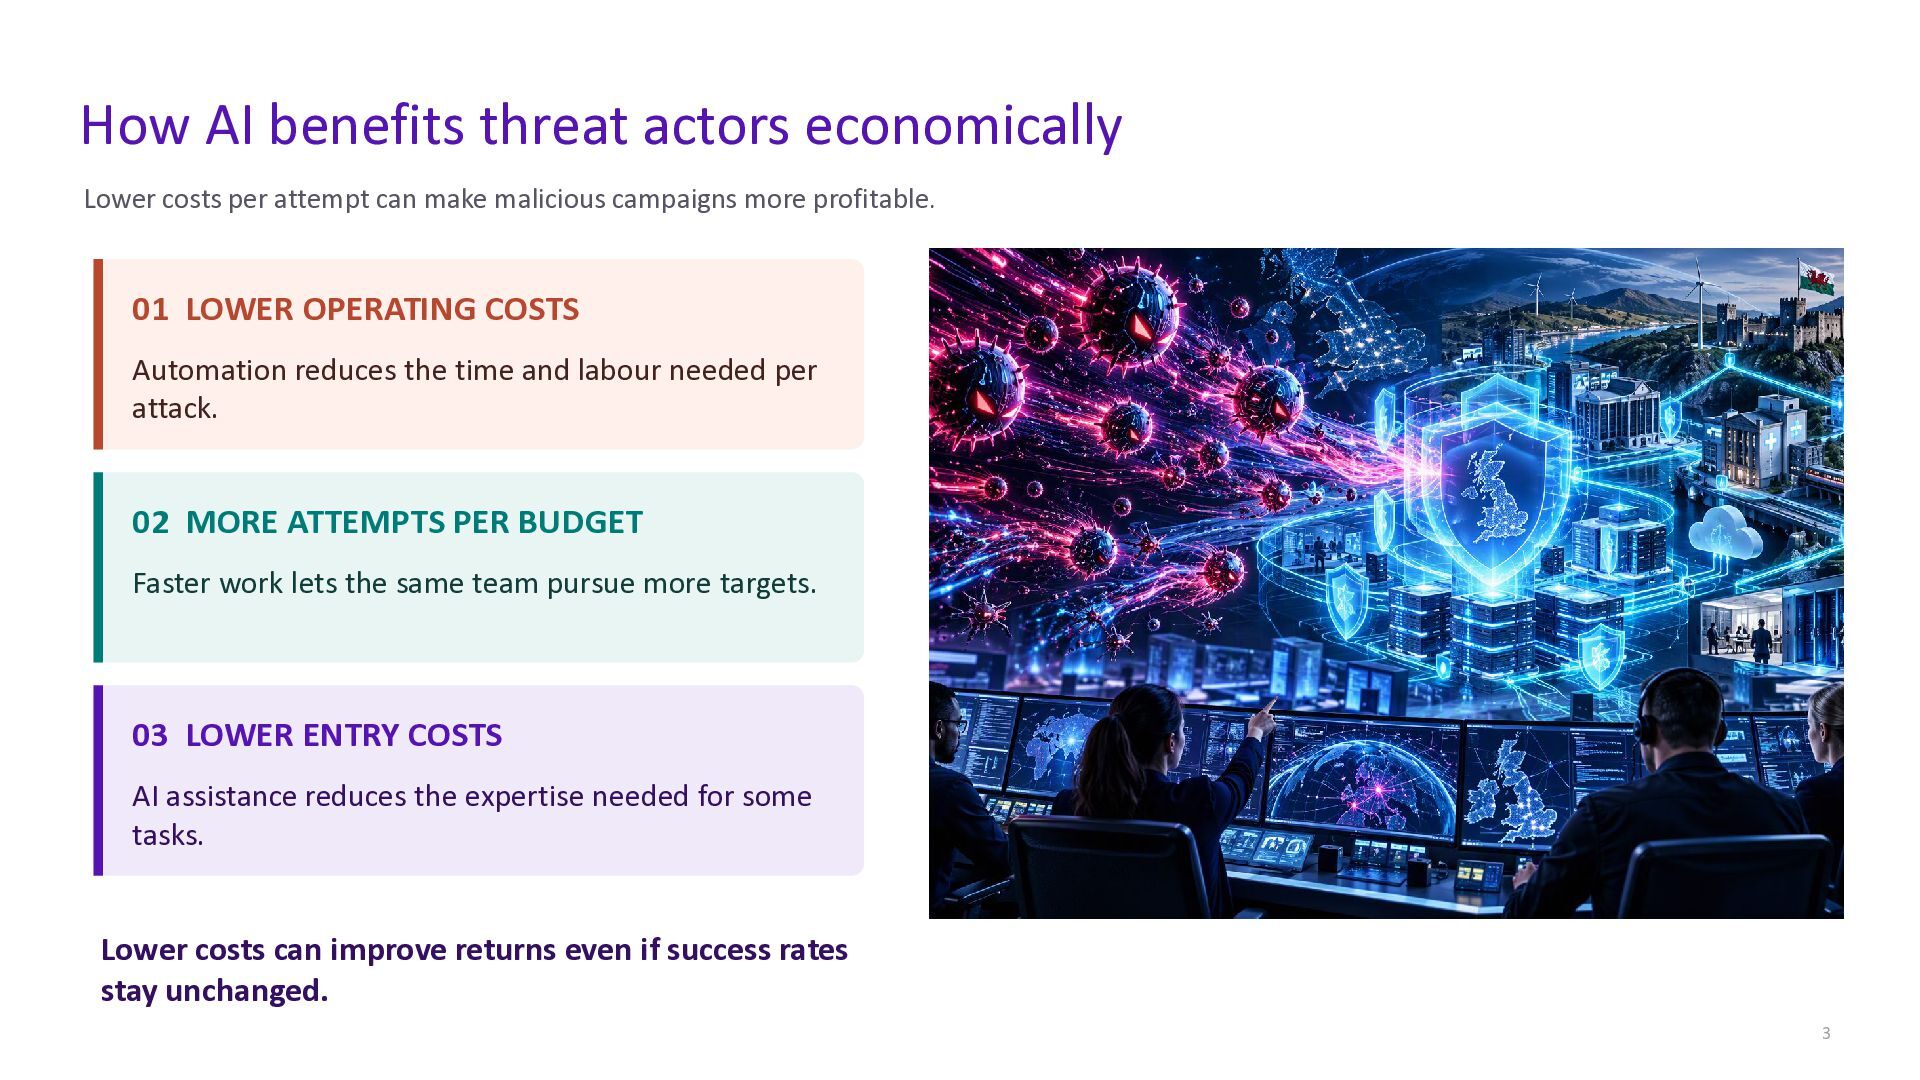
  61. How AI benefits threat actors economically Lower costs per attempt

    can make malicious campaigns more profitable. 01 LOWER OPERATING COSTS Automation reduces the time and labour needed per attack. 02 MORE ATTEMPTS PER BUDGET Faster work lets the same team pursue more targets. 03 LOWER ENTRY COSTS AI assistance reduces the expertise needed for some tasks. Lower costs can improve returns even if success rates stay unchanged. 3
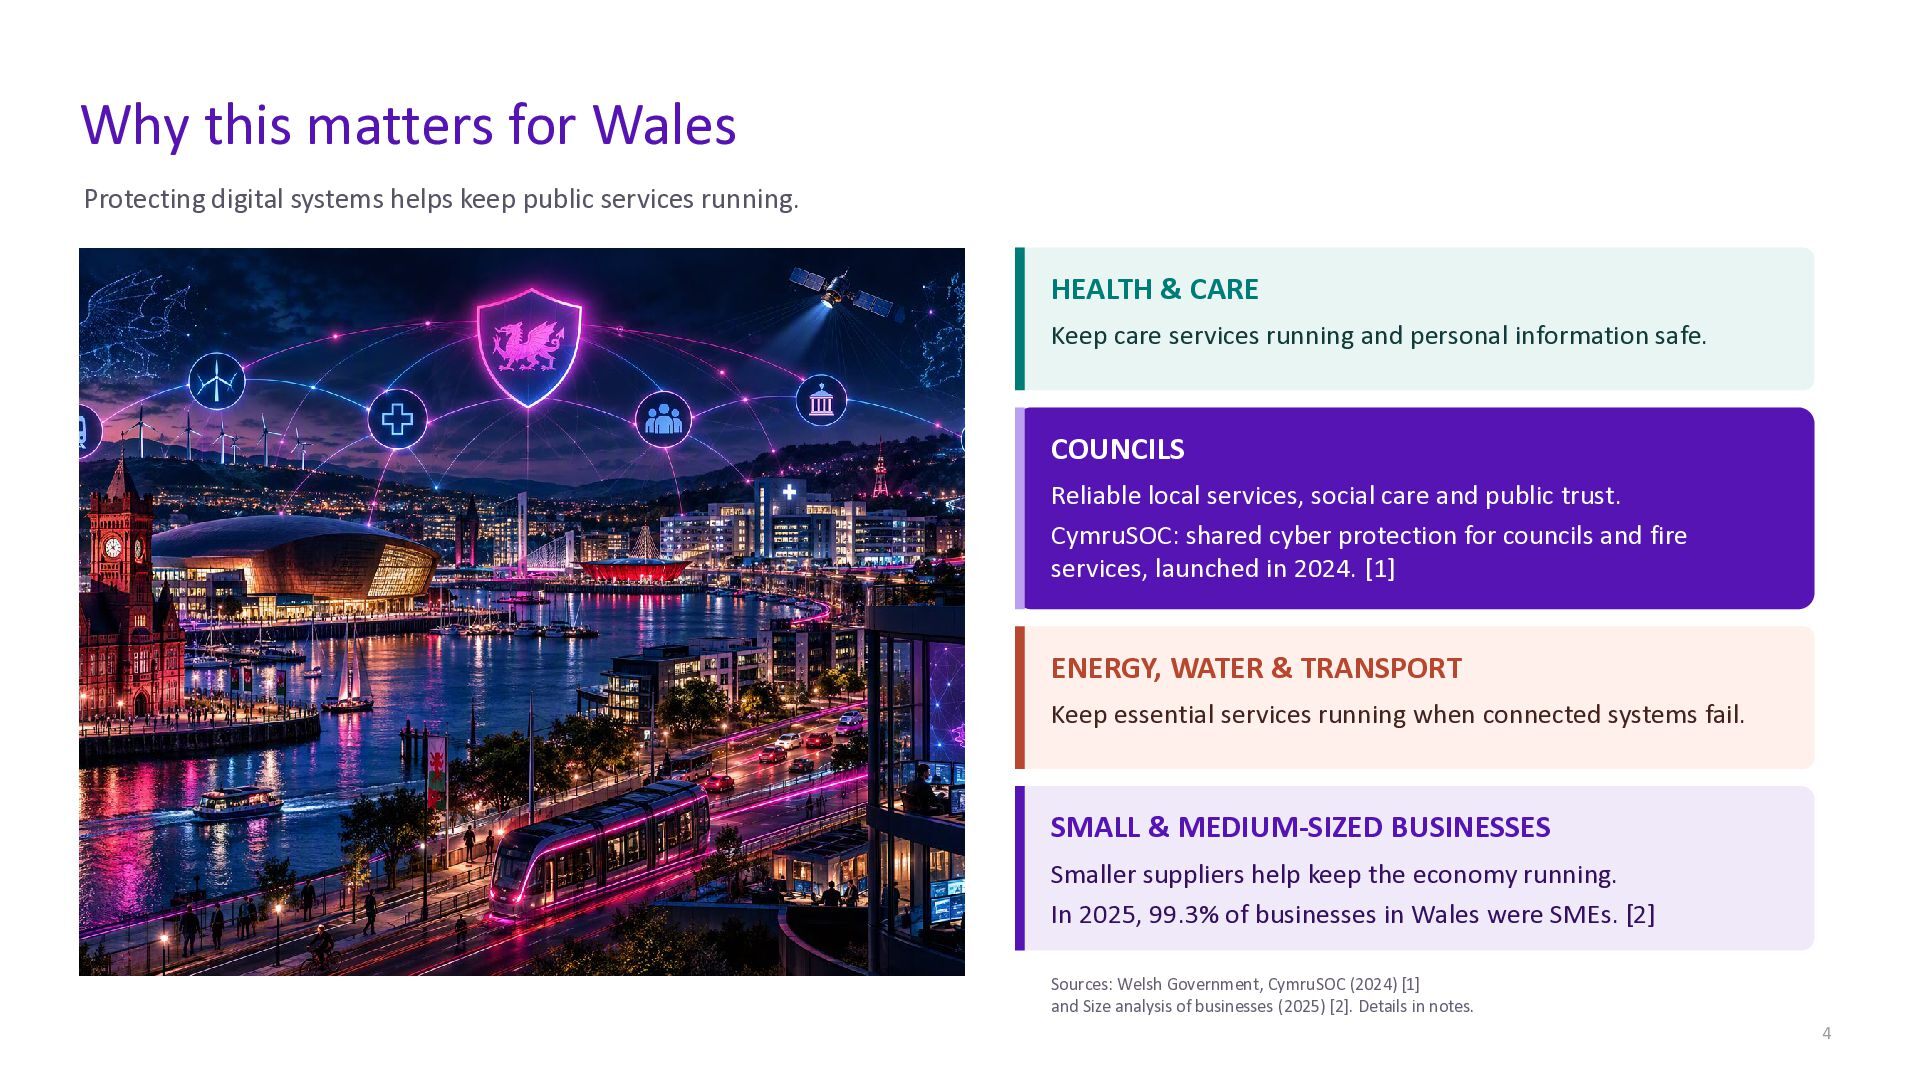
  62. Why this matters for Wales Protecting digital systems helps keep

    public services running. HEALTH & CARE Keep care services running and personal information safe. COUNCILS Reliable local services, social care and public trust. CymruSOC: shared cyber protection for councils and fire services, launched in 2024. [1] ENERGY, WATER & TRANSPORT Keep essential services running when connected systems fail. SMALL & MEDIUM-SIZED BUSINESSES Smaller suppliers help keep the economy running. In 2025, 99.3% of businesses in Wales were SMEs. [2] Sources: Welsh Government, CymruSOC (2024) [1] and Size analysis of businesses (2025) [2]. Details in notes. 4
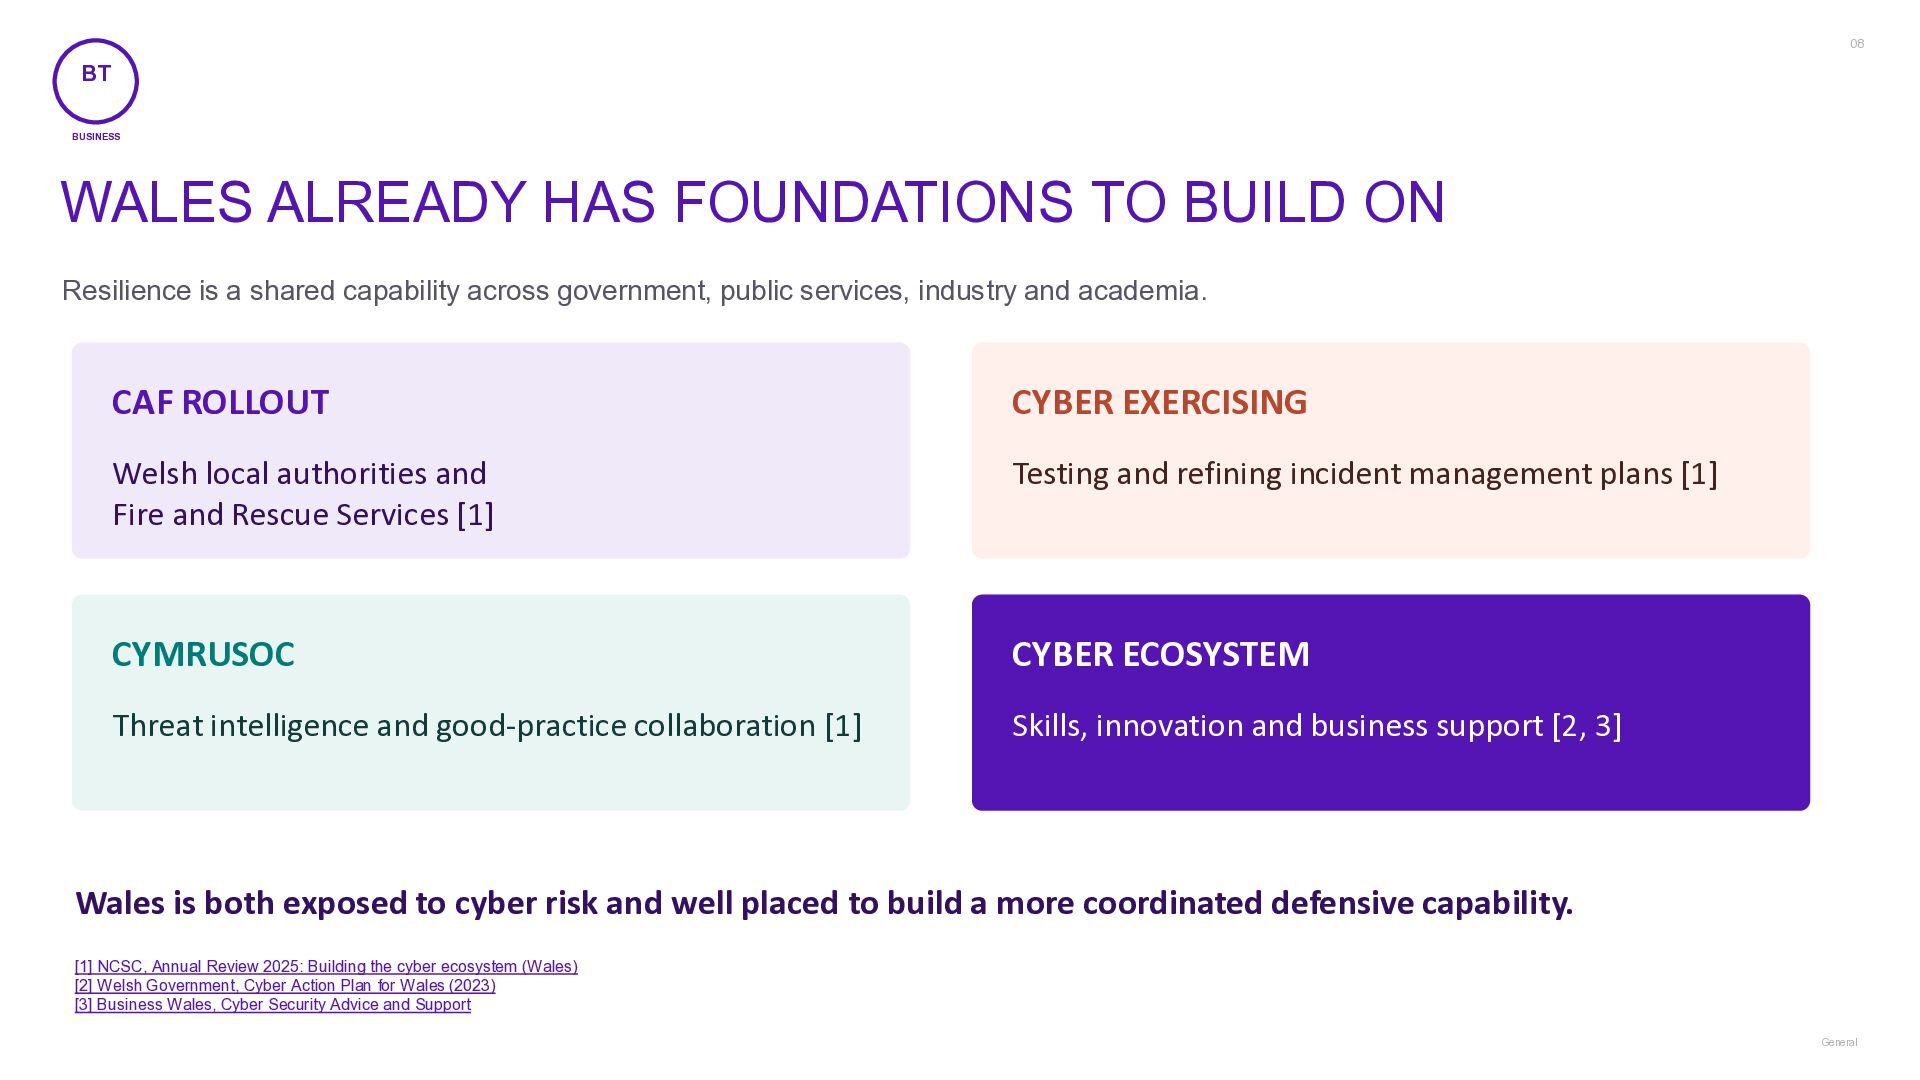
  63. 08 BT BUSINESS WALES ALREADY HAS FOUNDATIONS TO BUILD ON

    Resilience is a shared capability across government, public services, industry and academia. CAF ROLLOUT CYBER EXERCISING Welsh local authorities and Fire and Rescue Services [1] Testing and refining incident management plans [1] CYMRUSOC CYBER ECOSYSTEM Threat intelligence and good-practice collaboration [1] Skills, innovation and business support [2, 3] Wales is both exposed to cyber risk and well placed to build a more coordinated defensive capability. [1] NCSC, Annual Review 2025: Building the cyber ecosystem (Wales) [2] Welsh Government, Cyber Action Plan for Wales (2023) [3] Business Wales, Cyber Security Advice and Support General
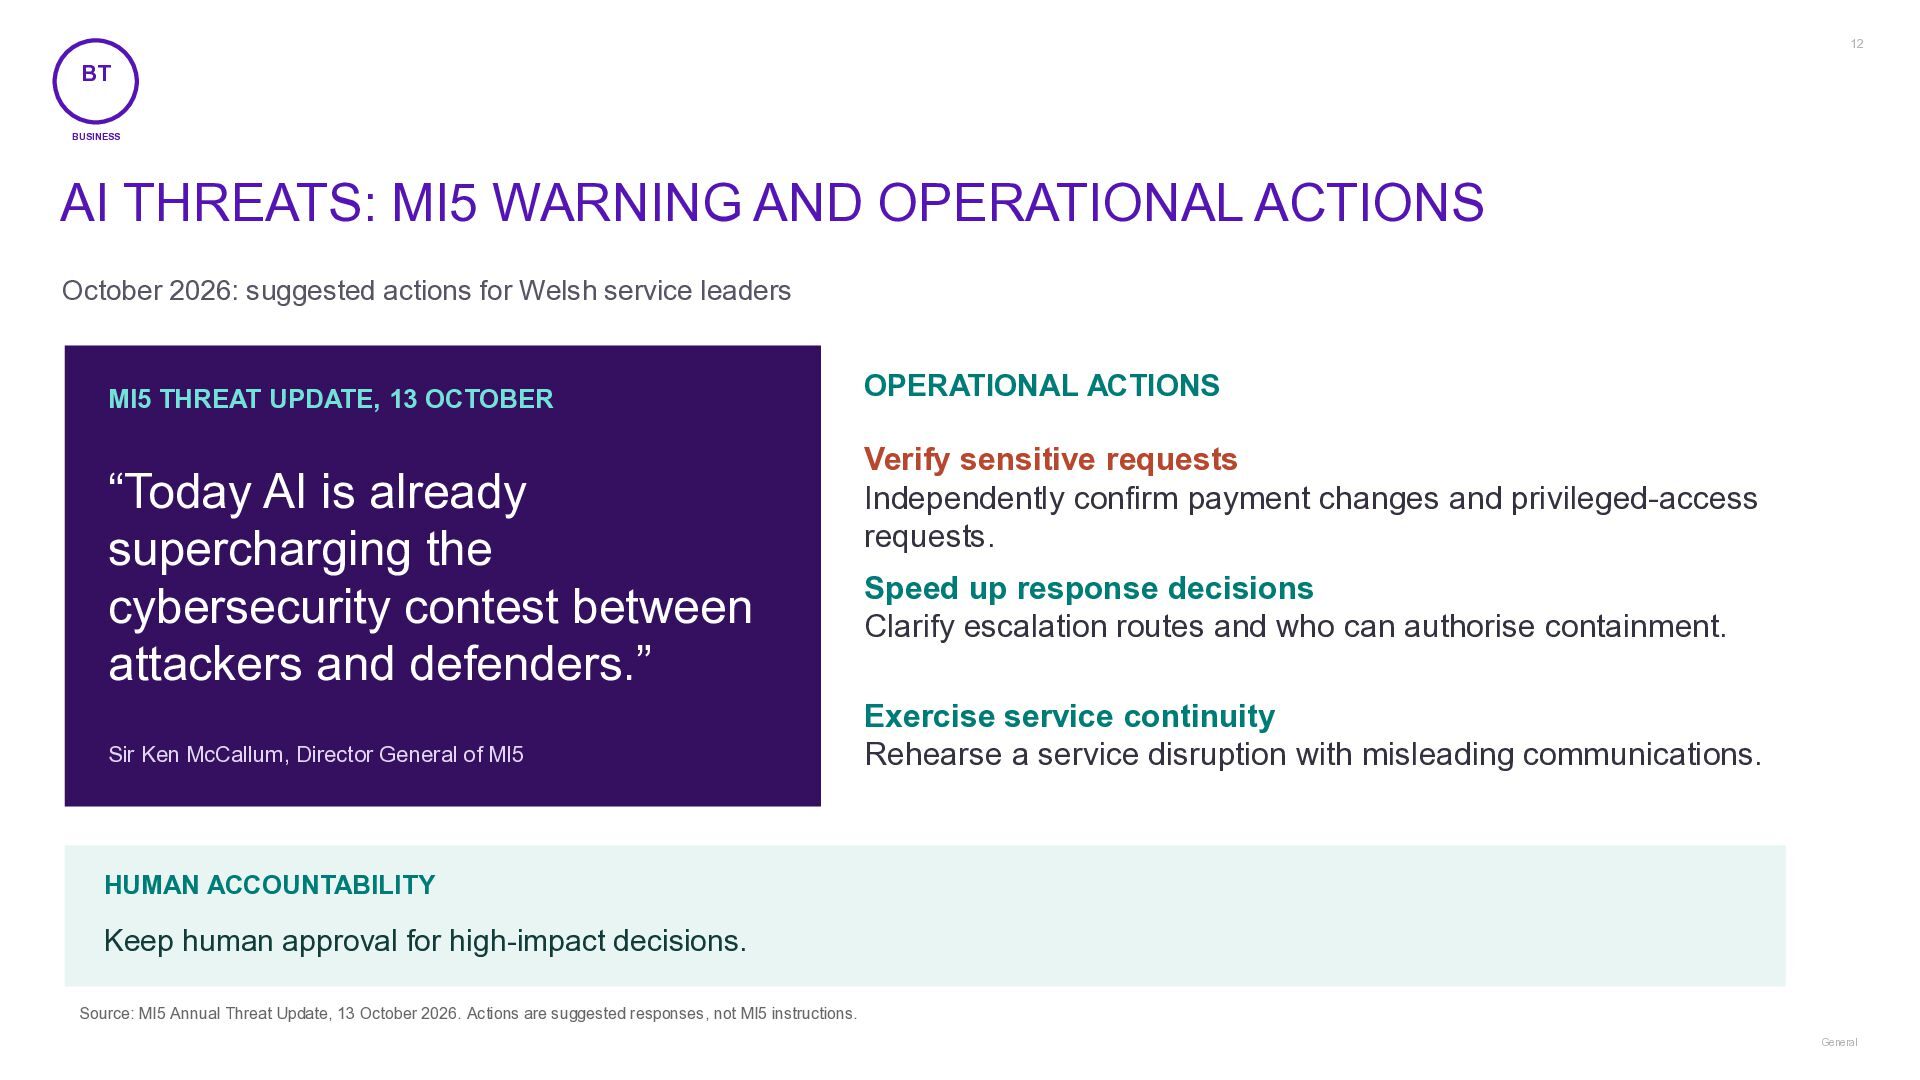
  64. 12 BT BUSINESS AI THREATS: MI5 WARNING AND OPERATIONAL ACTIONS

    October 2026: suggested actions for Welsh service leaders MI5 THREAT UPDATE, 13 OCTOBER “Today AI is already supercharging the cybersecurity contest between attackers and defenders.” Sir Ken McCallum, Director General of MI5 OPERATIONAL ACTIONS Verify sensitive requests Independently confirm payment changes and privileged-access requests. Speed up response decisions Clarify escalation routes and who can authorise containment. Exercise service continuity Rehearse a service disruption with misleading communications. HUMAN ACCOUNTABILITY Keep human approval for high-impact decisions. Source: MI5 Annual Threat Update, 13 October 2026. Actions are suggested responses, not MI5 instructions. General
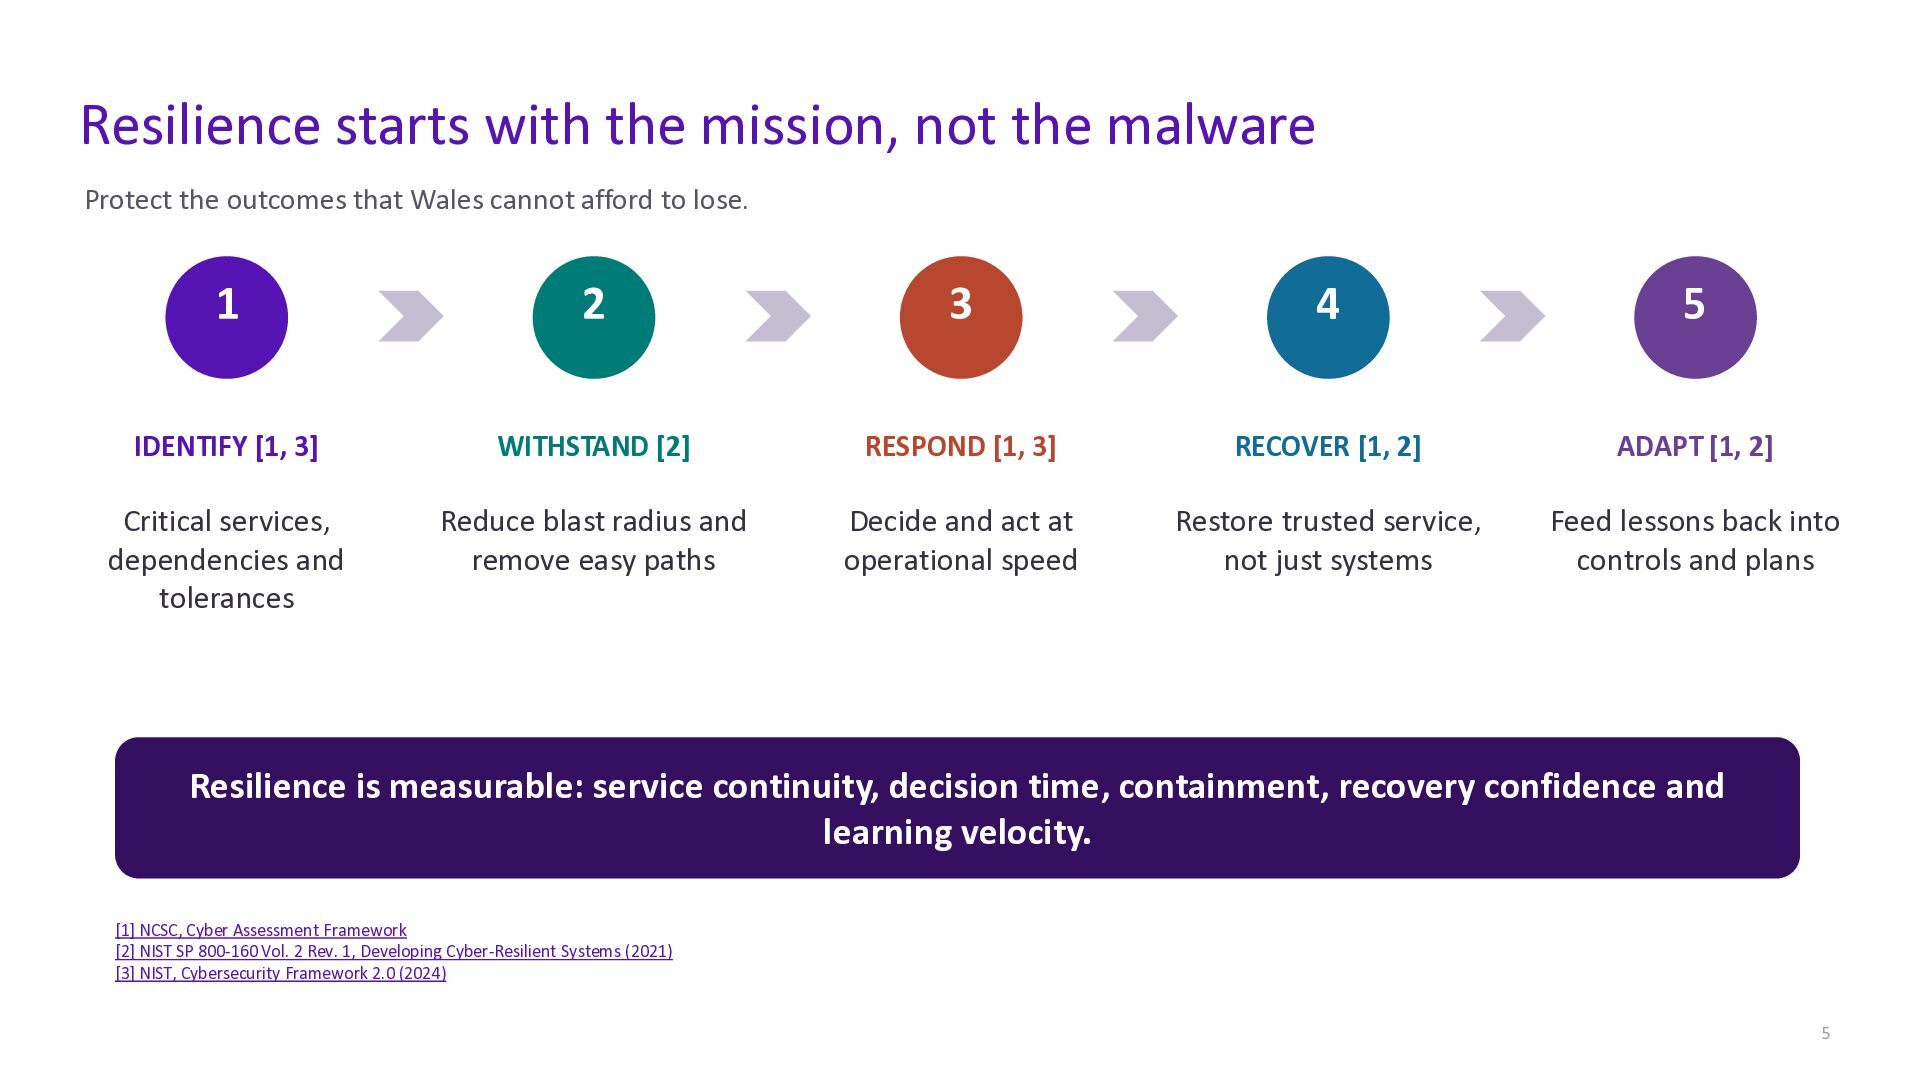
  65. Resilience starts with the mission, not the malware Protect the

    outcomes that Wales cannot afford to lose. 1 2 3 4 5 IDENTIFY [1, 3] WITHSTAND [2] RESPOND [1, 3] RECOVER [1, 2] ADAPT [1, 2] Critical services, dependencies and tolerances Reduce blast radius and remove easy paths Decide and act at operational speed Restore trusted service, not just systems Feed lessons back into controls and plans Resilience is measurable: service continuity, decision time, containment, recovery confidence and learning velocity. [1] NCSC, Cyber Assessment Framework [2] NIST SP 800-160 Vol. 2 Rev. 1, Developing Cyber-Resilient Systems (2021) [3] NIST, Cybersecurity Framework 2.0 (2024) 5
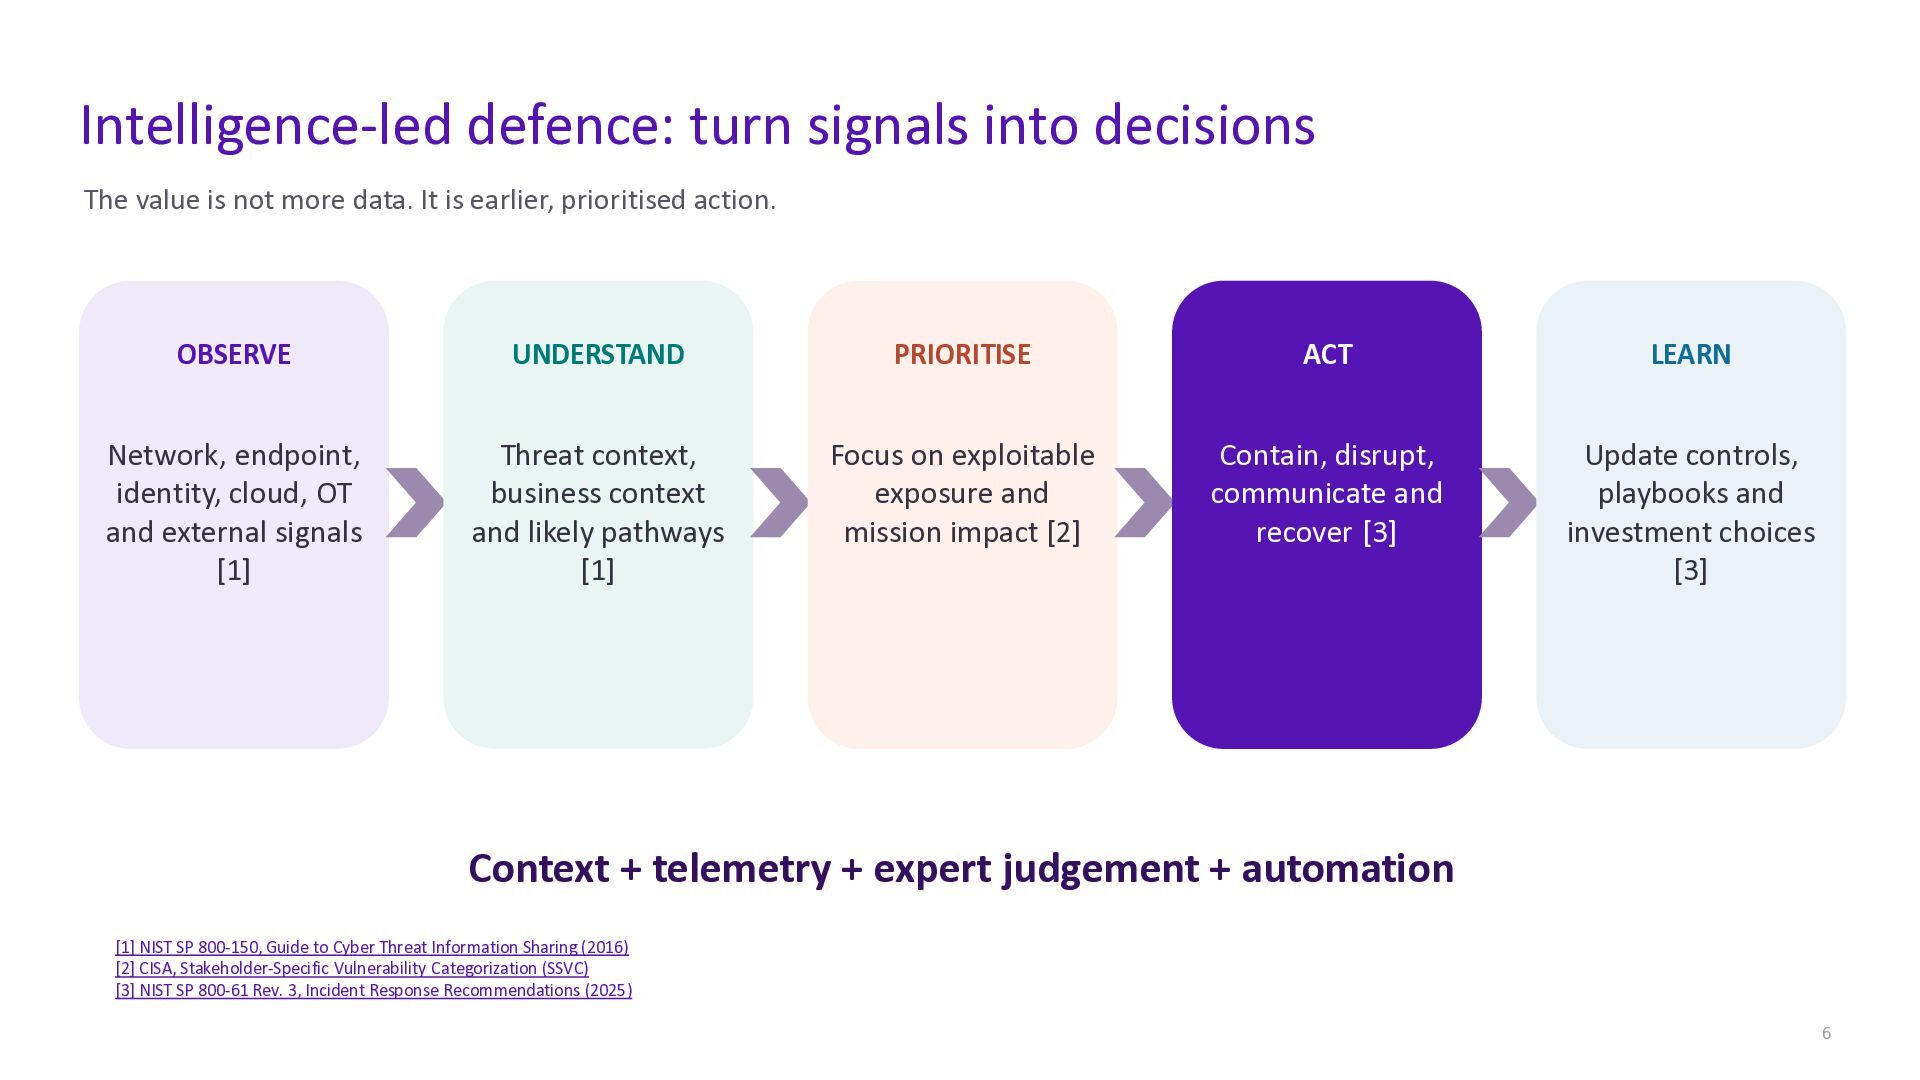
  66. Intelligence-led defence: turn signals into decisions The value is not

    more data. It is earlier, prioritised action. OBSERVE UNDERSTAND PRIORITISE ACT LEARN Network, endpoint, identity, cloud, OT and external signals [1] Threat context, business context and likely pathways [1] Focus on exploitable exposure and mission impact [2] Contain, disrupt, communicate and recover [3] Update controls, playbooks and investment choices [3] Context + telemetry + expert judgement + automation [1] NIST SP 800-150, Guide to Cyber Threat Information Sharing (2016) [2] CISA, Stakeholder-Specific Vulnerability Categorization (SSVC) [3] NIST SP 800-61 Rev. 3, Incident Response Recommendations (2025) 6
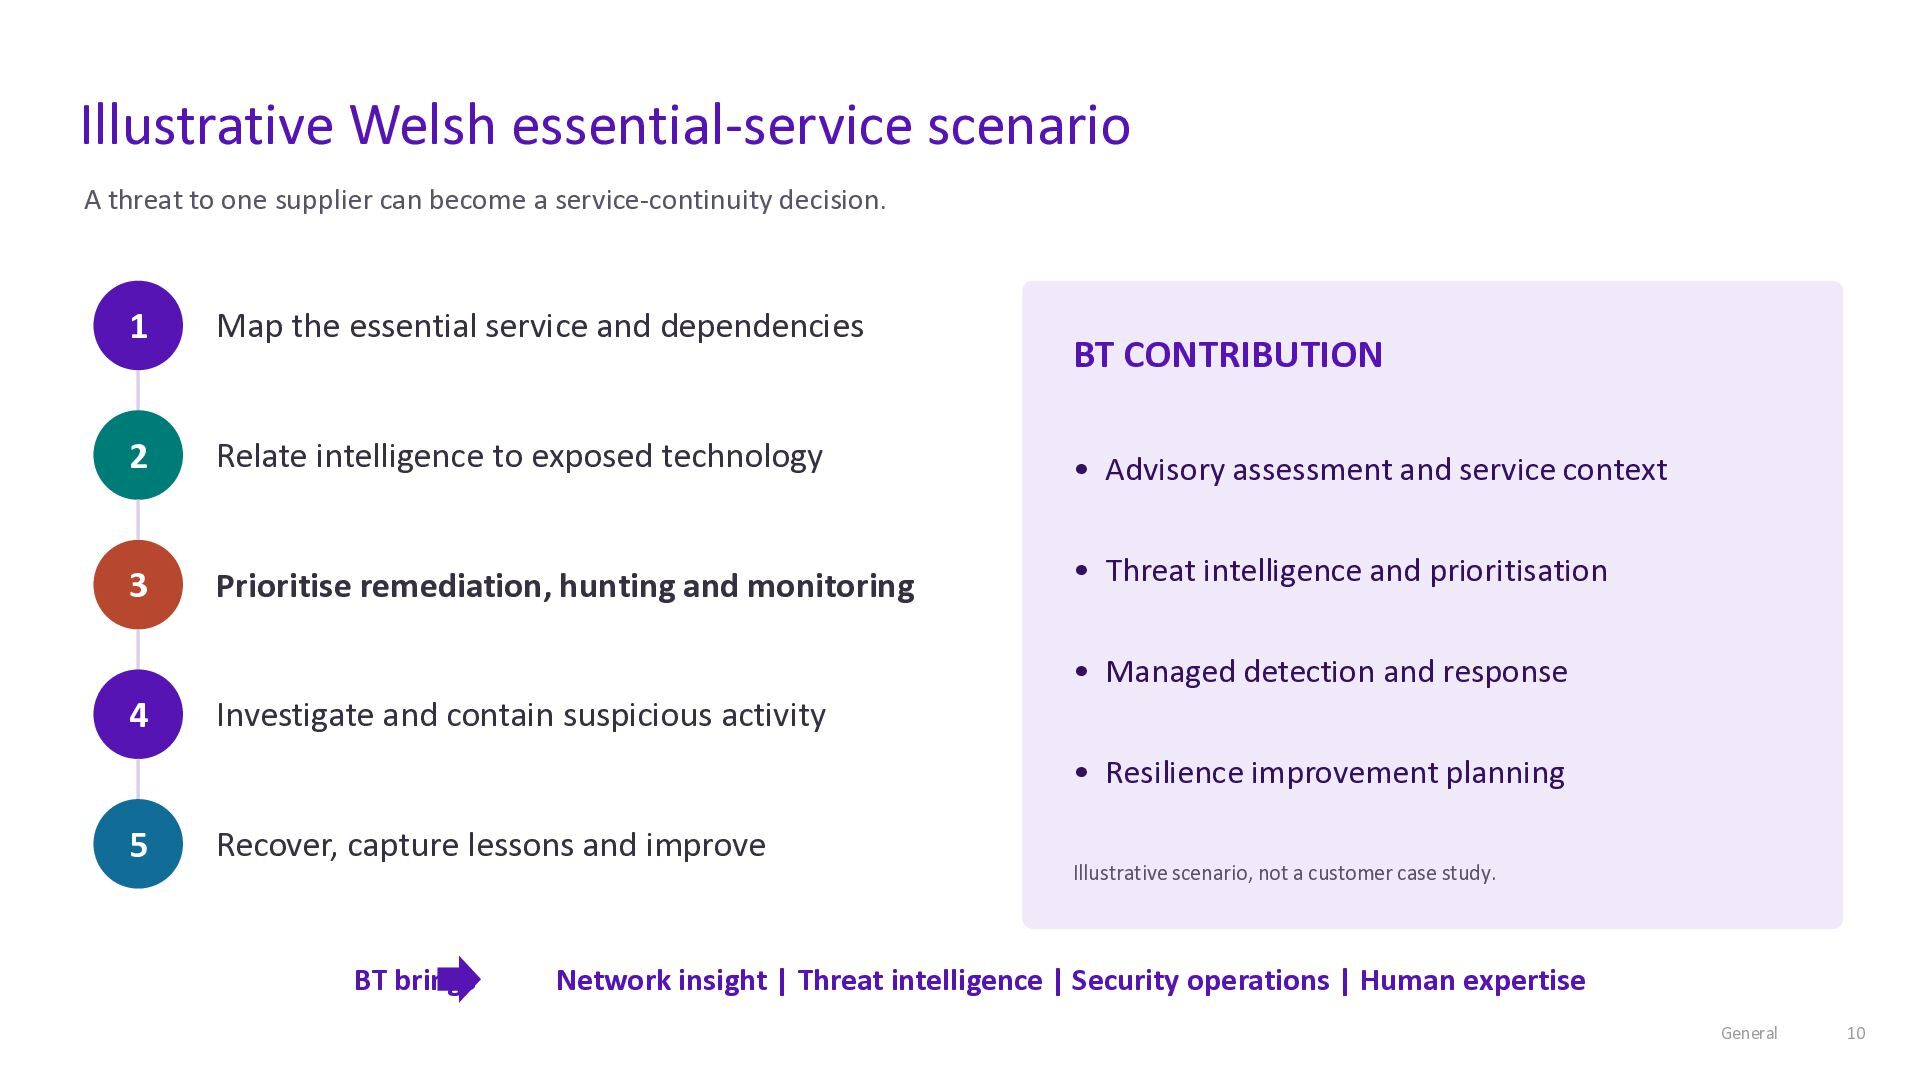
  67. Illustrative Welsh essential-service scenario A threat to one supplier can

    become a service-continuity decision. 1 Map the essential service and dependencies 2 Relate intelligence to exposed technology • Advisory assessment and service context 3 Prioritise remediation, hunting and monitoring • Threat intelligence and prioritisation 4 Investigate and contain suspicious activity BT CONTRIBUTION • Managed detection and response • Resilience improvement planning 5 Recover, capture lessons and improve BT brings Illustrative scenario, not a customer case study. Network insight | Threat intelligence | Security operations | Human expertise General 10
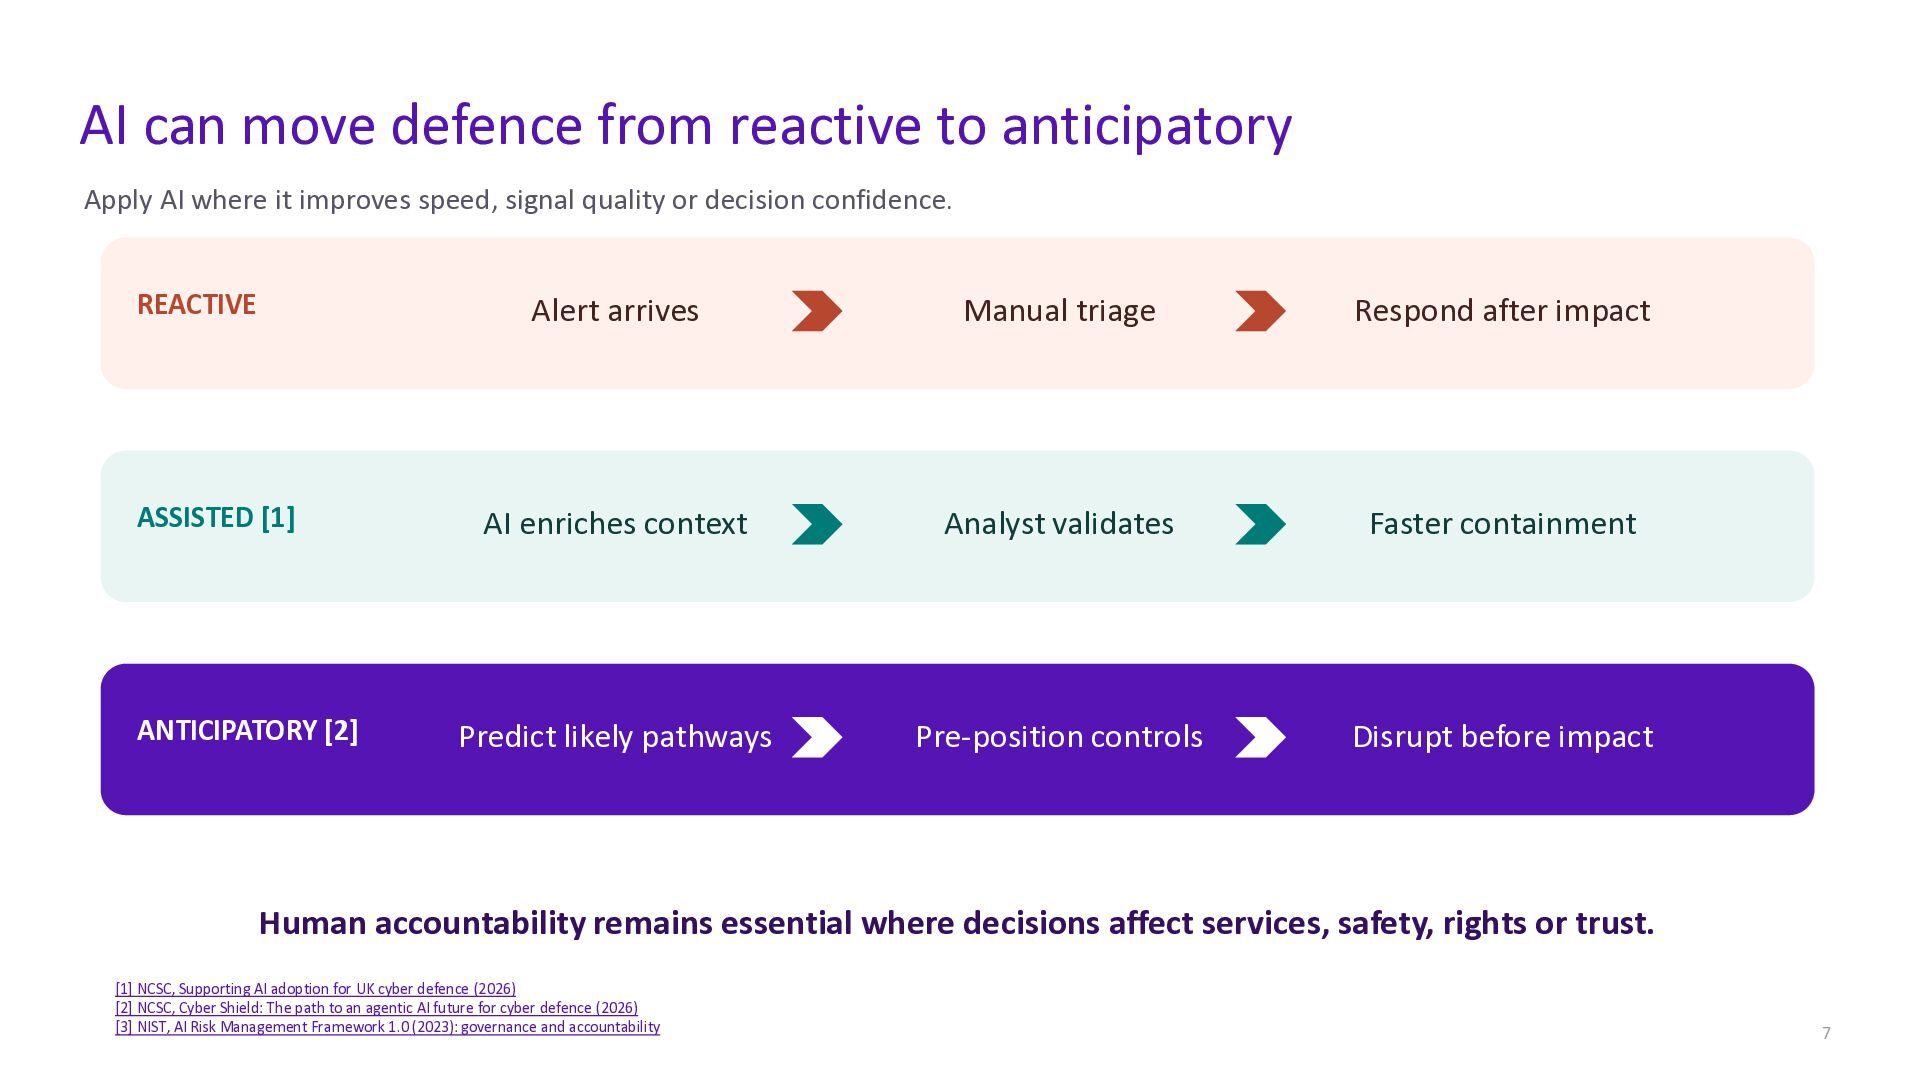
  68. AI can move defence from reactive to anticipatory Apply AI

    where it improves speed, signal quality or decision confidence. REACTIVE Alert arrives Manual triage Respond after impact ASSISTED [1] AI enriches context Analyst validates Faster containment Predict likely pathways Pre-position controls Disrupt before impact ANTICIPATORY [2] Human accountability remains essential where decisions affect services, safety, rights or trust. [1] NCSC, Supporting AI adoption for UK cyber defence (2026) [2] NCSC, Cyber Shield: The path to an agentic AI future for cyber defence (2026) [3] NIST, AI Risk Management Framework 1.0 (2023): governance and accountability 7
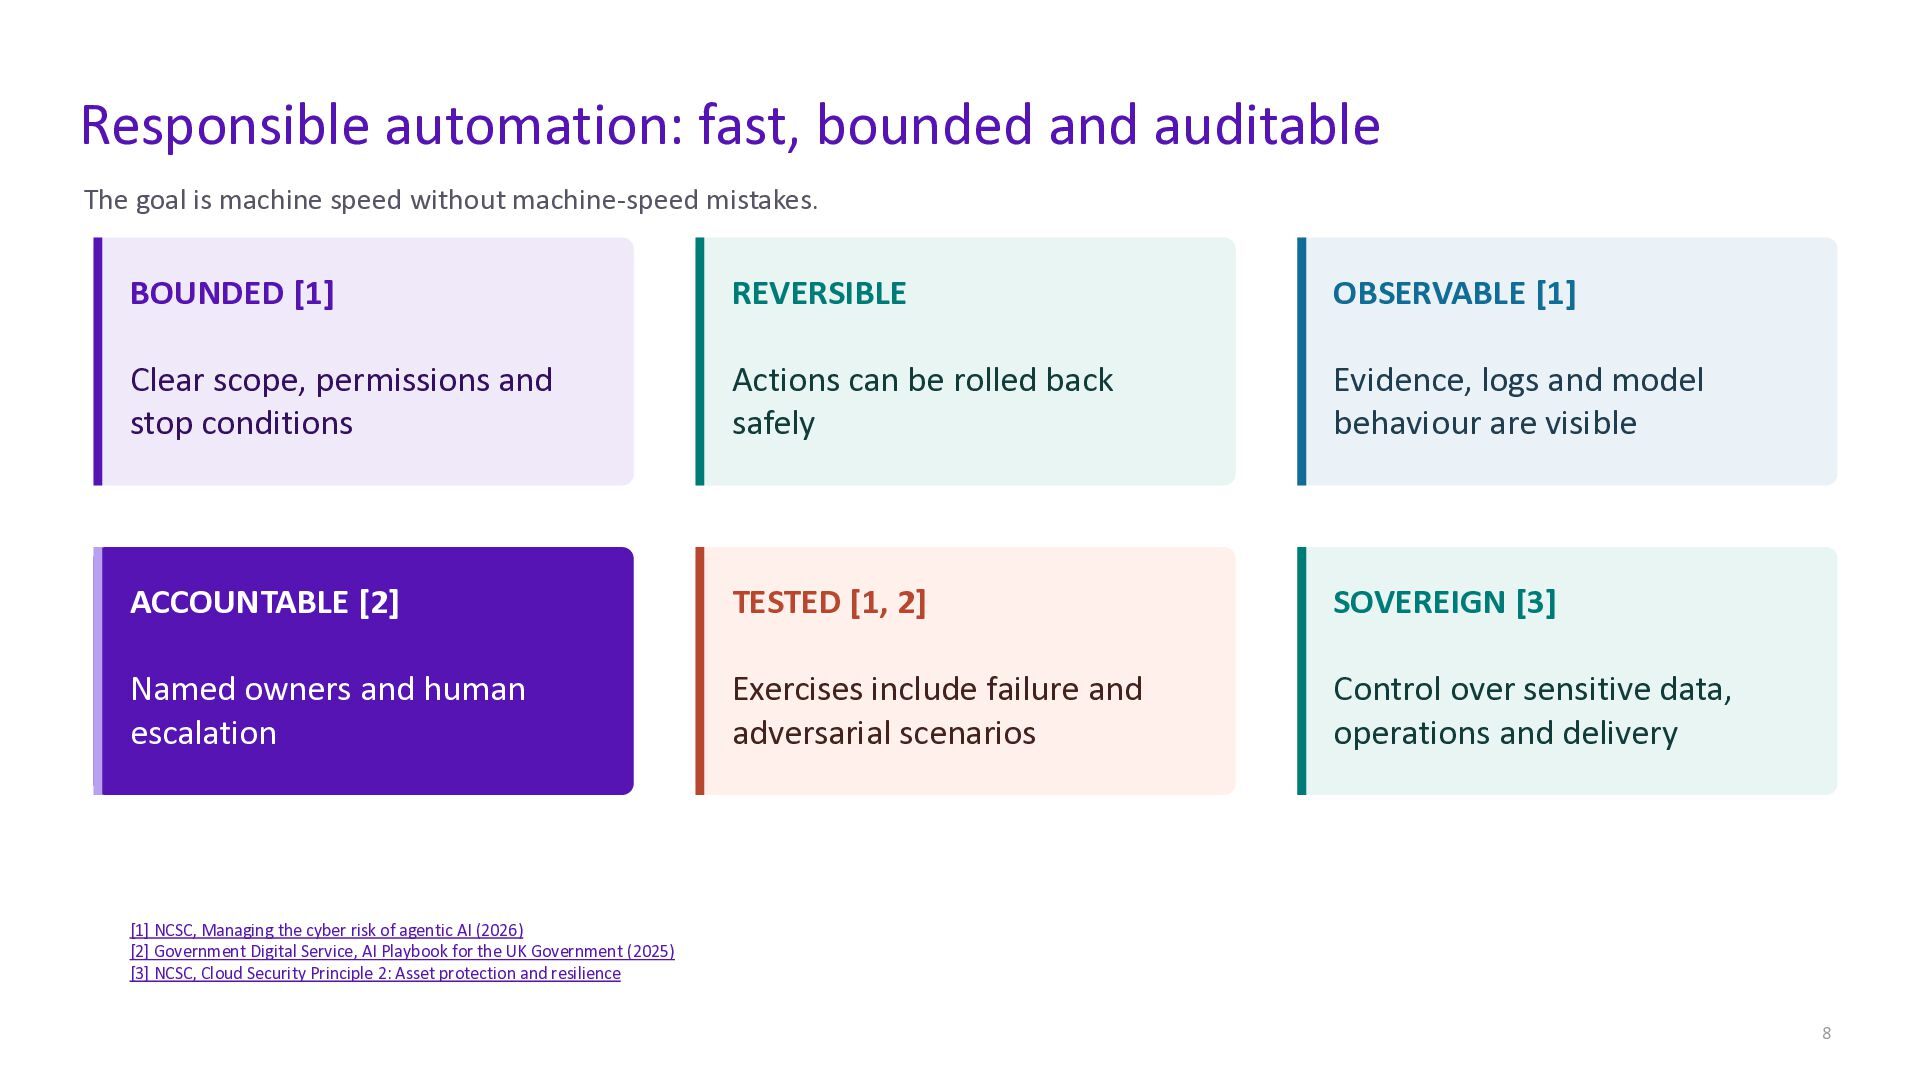
  69. Responsible automation: fast, bounded and auditable The goal is machine

    speed without machine-speed mistakes. BOUNDED [1] REVERSIBLE OBSERVABLE [1] Clear scope, permissions and stop conditions Actions can be rolled back safely Evidence, logs and model behaviour are visible ACCOUNTABLE [2] TESTED [1, 2] SOVEREIGN [3] Named owners and human escalation Exercises include failure and adversarial scenarios Control over sensitive data, operations and delivery [1] NCSC, Managing the cyber risk of agentic AI (2026) [2] Government Digital Service, AI Playbook for the UK Government (2025) [3] NCSC, Cloud Security Principle 2: Asset protection and resilience 8
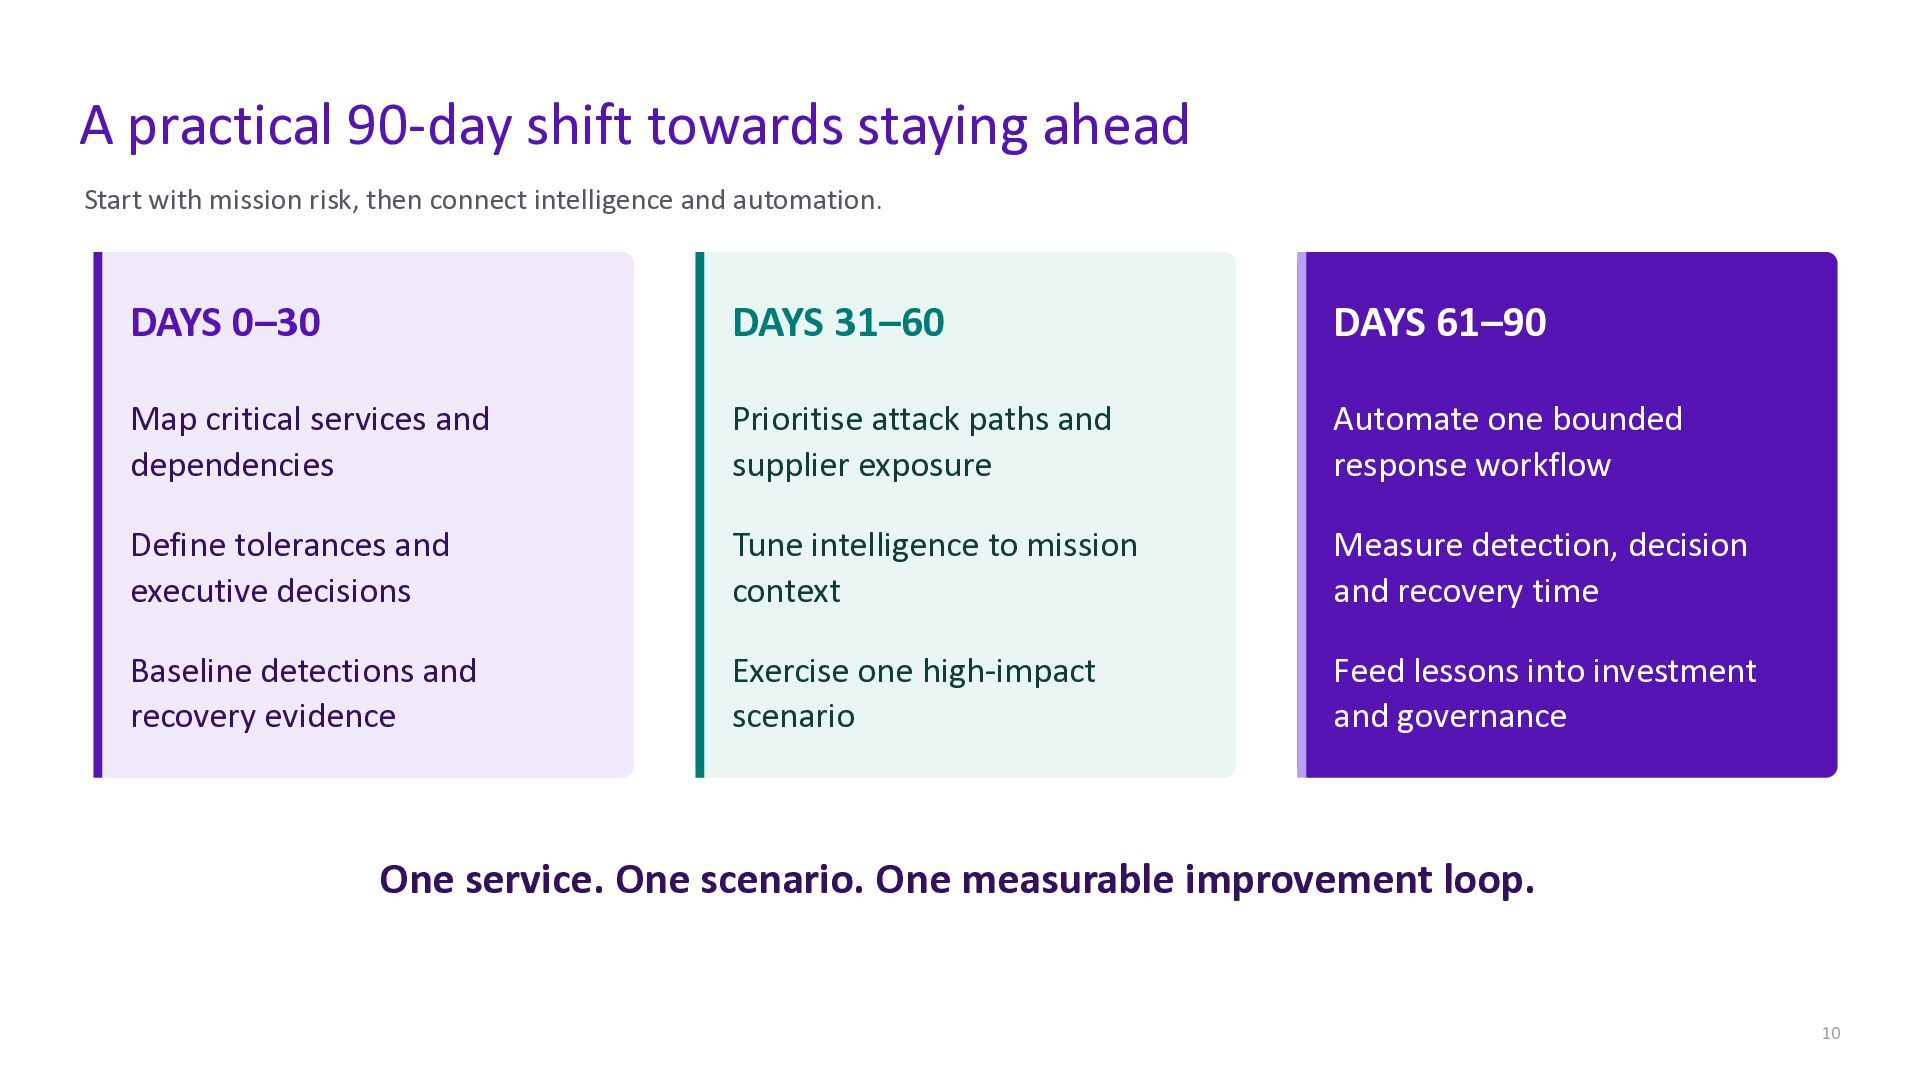
  70. A practical 90-day shift towards staying ahead Start with mission

    risk, then connect intelligence and automation. DAYS 0–30 DAYS 31–60 DAYS 61–90 Map critical services and dependencies Prioritise attack paths and supplier exposure Automate one bounded response workflow Define tolerances and executive decisions Tune intelligence to mission context Measure detection, decision and recovery time Baseline detections and recovery evidence Exercise one high-impact scenario Feed lessons into investment and governance One service. One scenario. One measurable improvement loop. 10
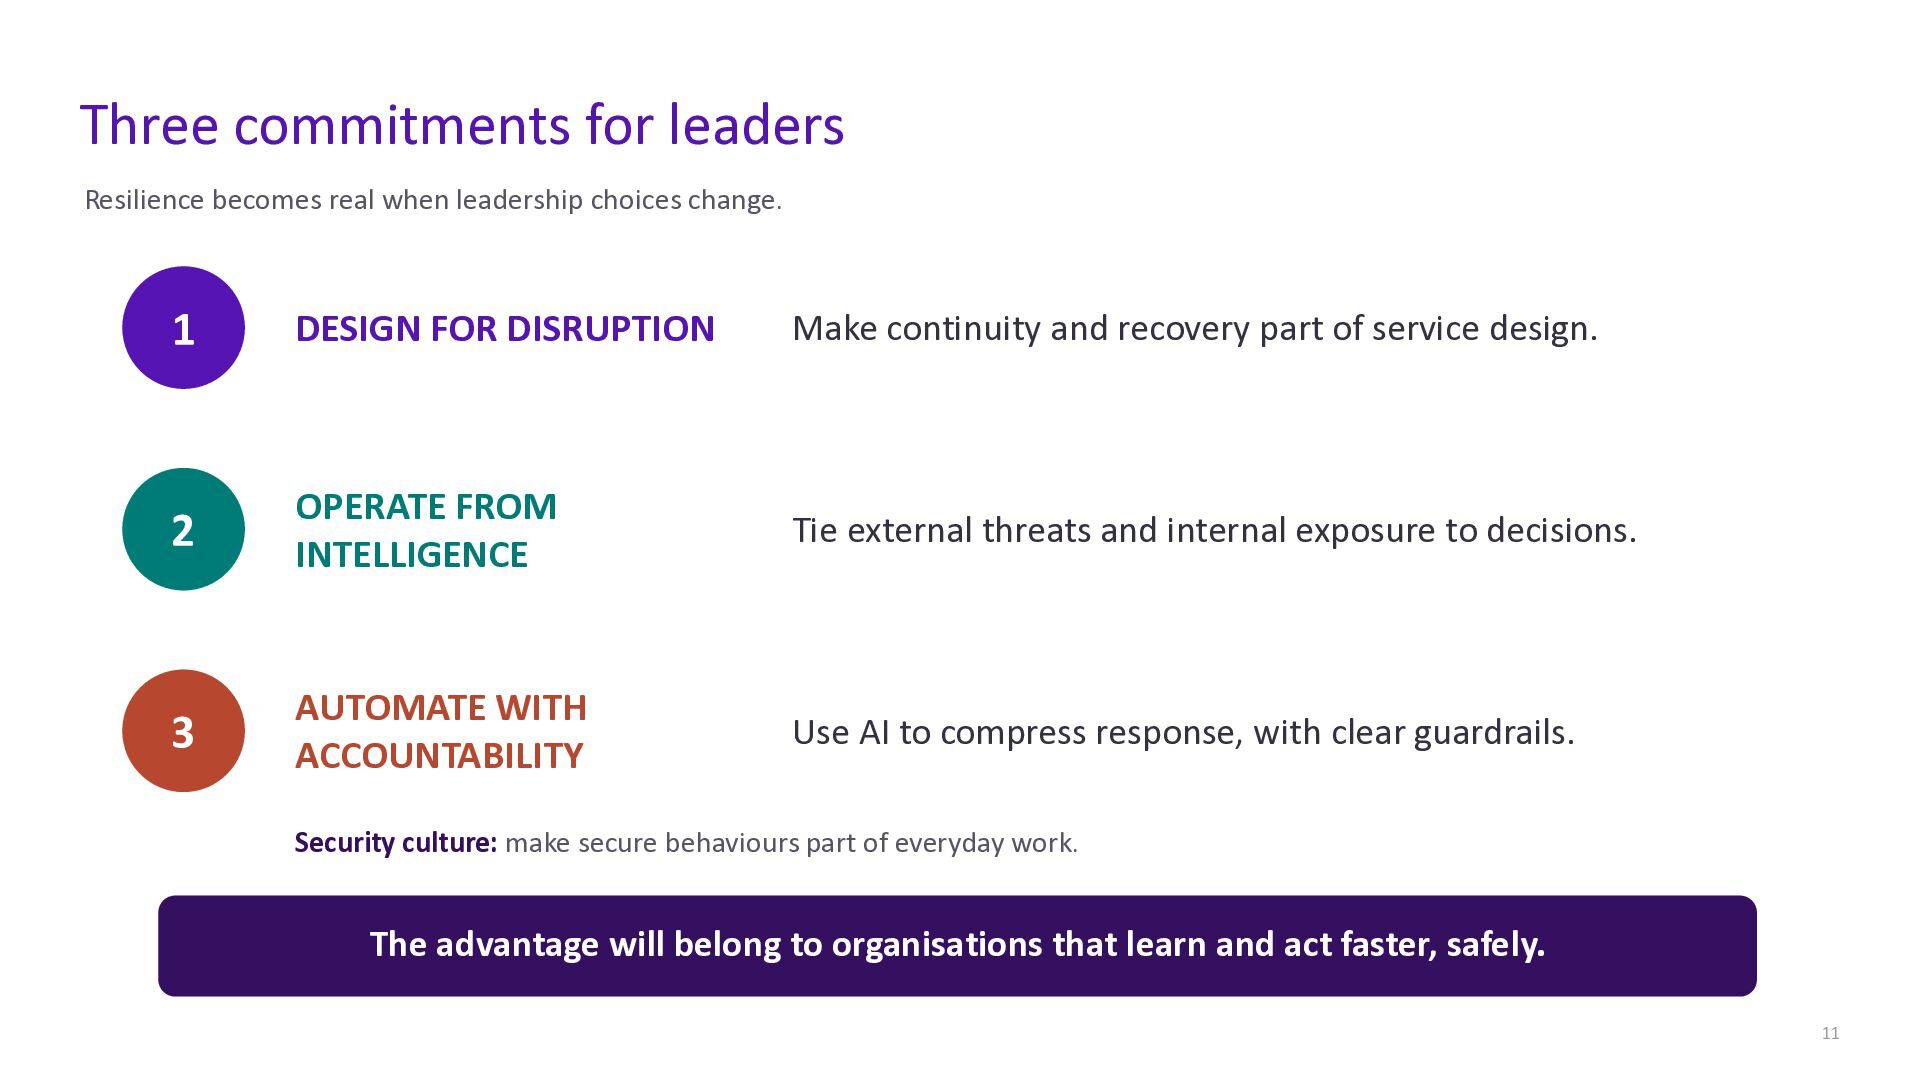
  71. Three commitments for leaders Resilience becomes real when leadership choices

    change. 1 DESIGN FOR DISRUPTION Make continuity and recovery part of service design. 2 OPERATE FROM INTELLIGENCE Tie external threats and internal exposure to decisions. 3 AUTOMATE WITH ACCOUNTABILITY Use AI to compress response, with clear guardrails. Security culture: make secure behaviours part of everyday work. The advantage will belong to organisations that learn and act faster, safely. 11
  72. STAY AHEAD. STAY RESILIENT. Questions & discussion Where could intelligence

    or responsible automation remove the most dangerous delay in your organisation? Ishaque Mir | Security Advisory Manager, BT 12
  73. #CymruSec Lunch & Networking – See you at 13:35! Upcoming

    – Final Breakout Breakout E: Breakout F: Breakout G : Effective Cyber Security for SMEs AI – The Current Threat Landscape MCP: Don’t Shoot the Messenger Chairmans Suite 13:35 This Room 13:35 Captains Lounge 13:35
  74. #CymruSec Ryan James CISO MERTHY TYDFIL COUNTY BOROUGH COUNCIL Toby

    Grainger Head of CymruSOC WELSH GOVERNMENT
  75. CymruSOC Protecting Wales Together Building a shared cyber defence capability

    for the Welsh public sector Ryan James • Toby Grainger • Andrew Kays CymruSec Summit 2026 | Cardiff CYMRUSOC • PROTECTING WALES TOGETHER CYMRUSEC SUMMIT 2026 9 6
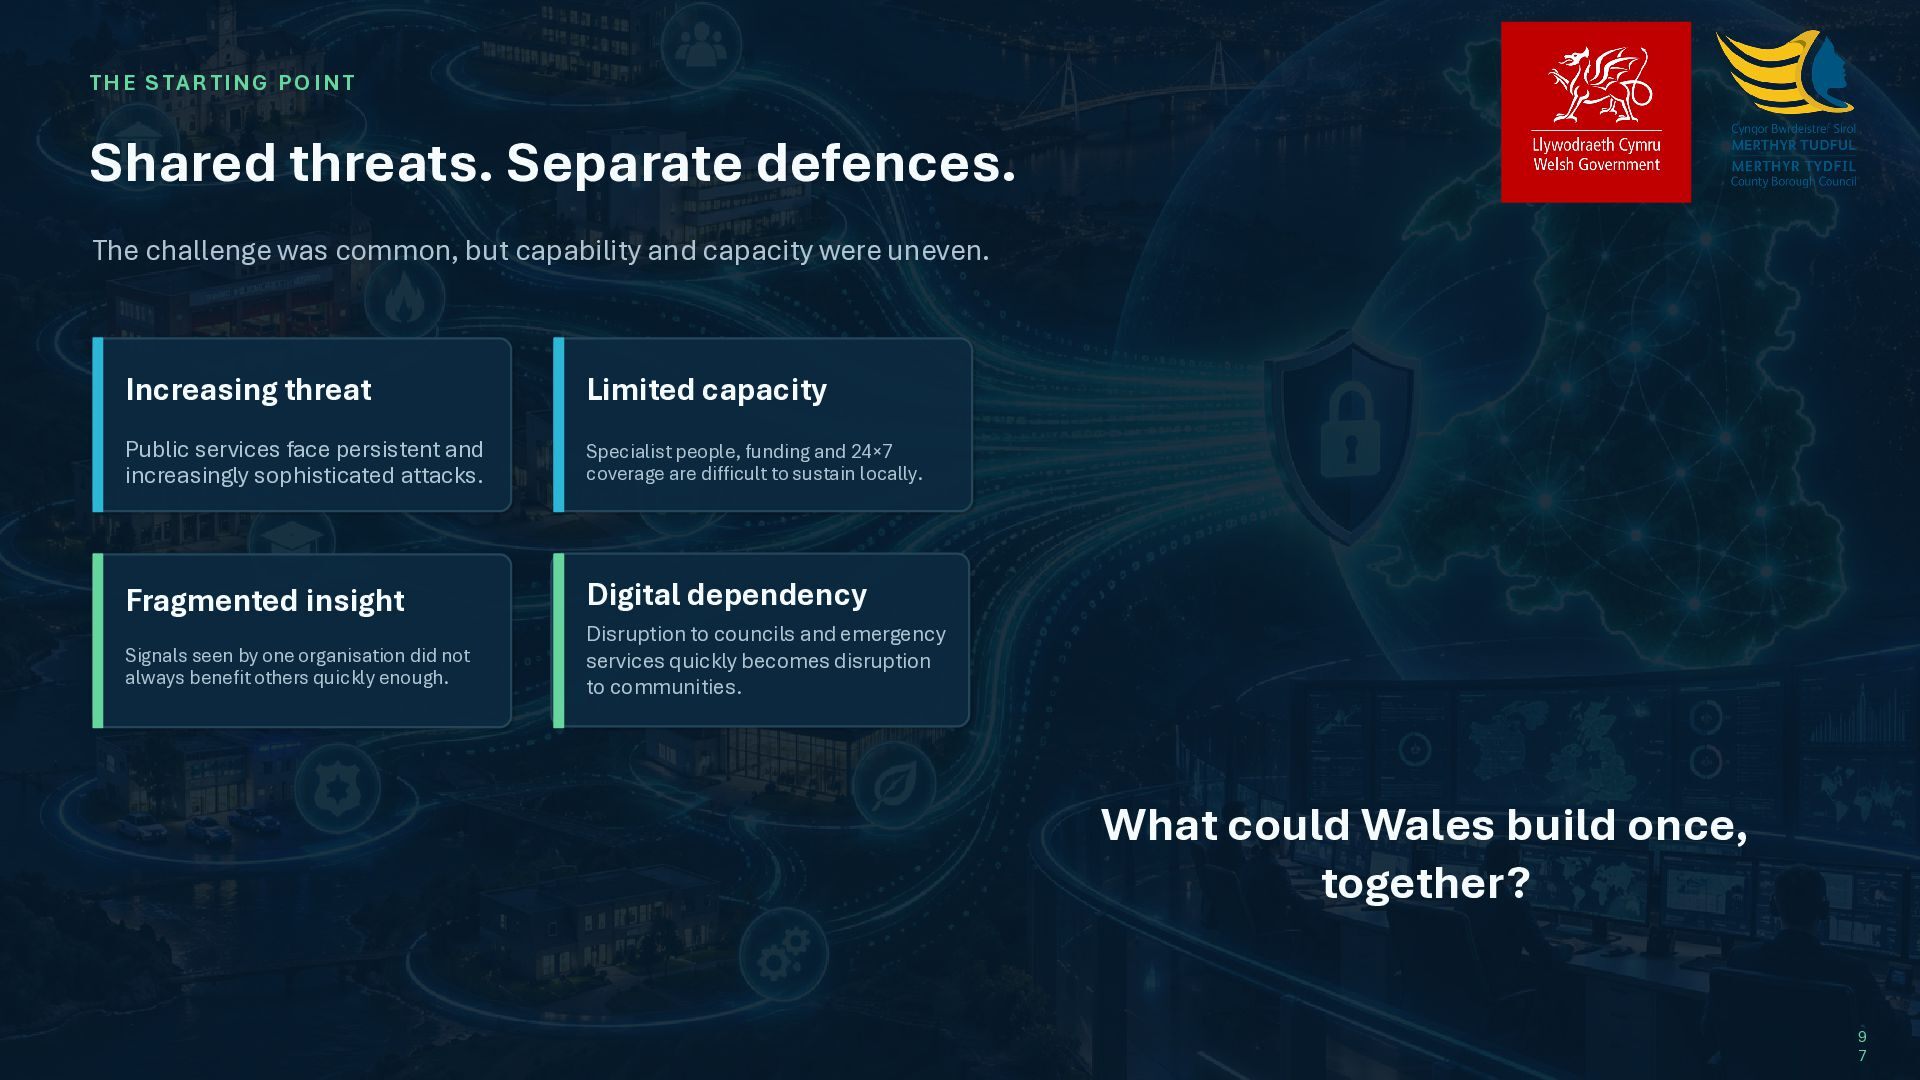
  76. THE STARTING POINT Shared threats. Separate defences. The challenge was

    common, but capability and capacity were uneven. Increasing threat Limited capacity Public services face persistent and increasingly sophisticated attacks. Specialist people, funding and 24×7 coverage are difficult to sustain locally. Fragmented insight Digital dependency Signals seen by one organisation did not always benefit others quickly enough. Disruption to councils and emergency services quickly becomes disruption to communities. What could Wales build once, together? CYMRUSOC • PROTECTING WALES TOGETHER CYMRUSEC SUMMIT 2026 9 7
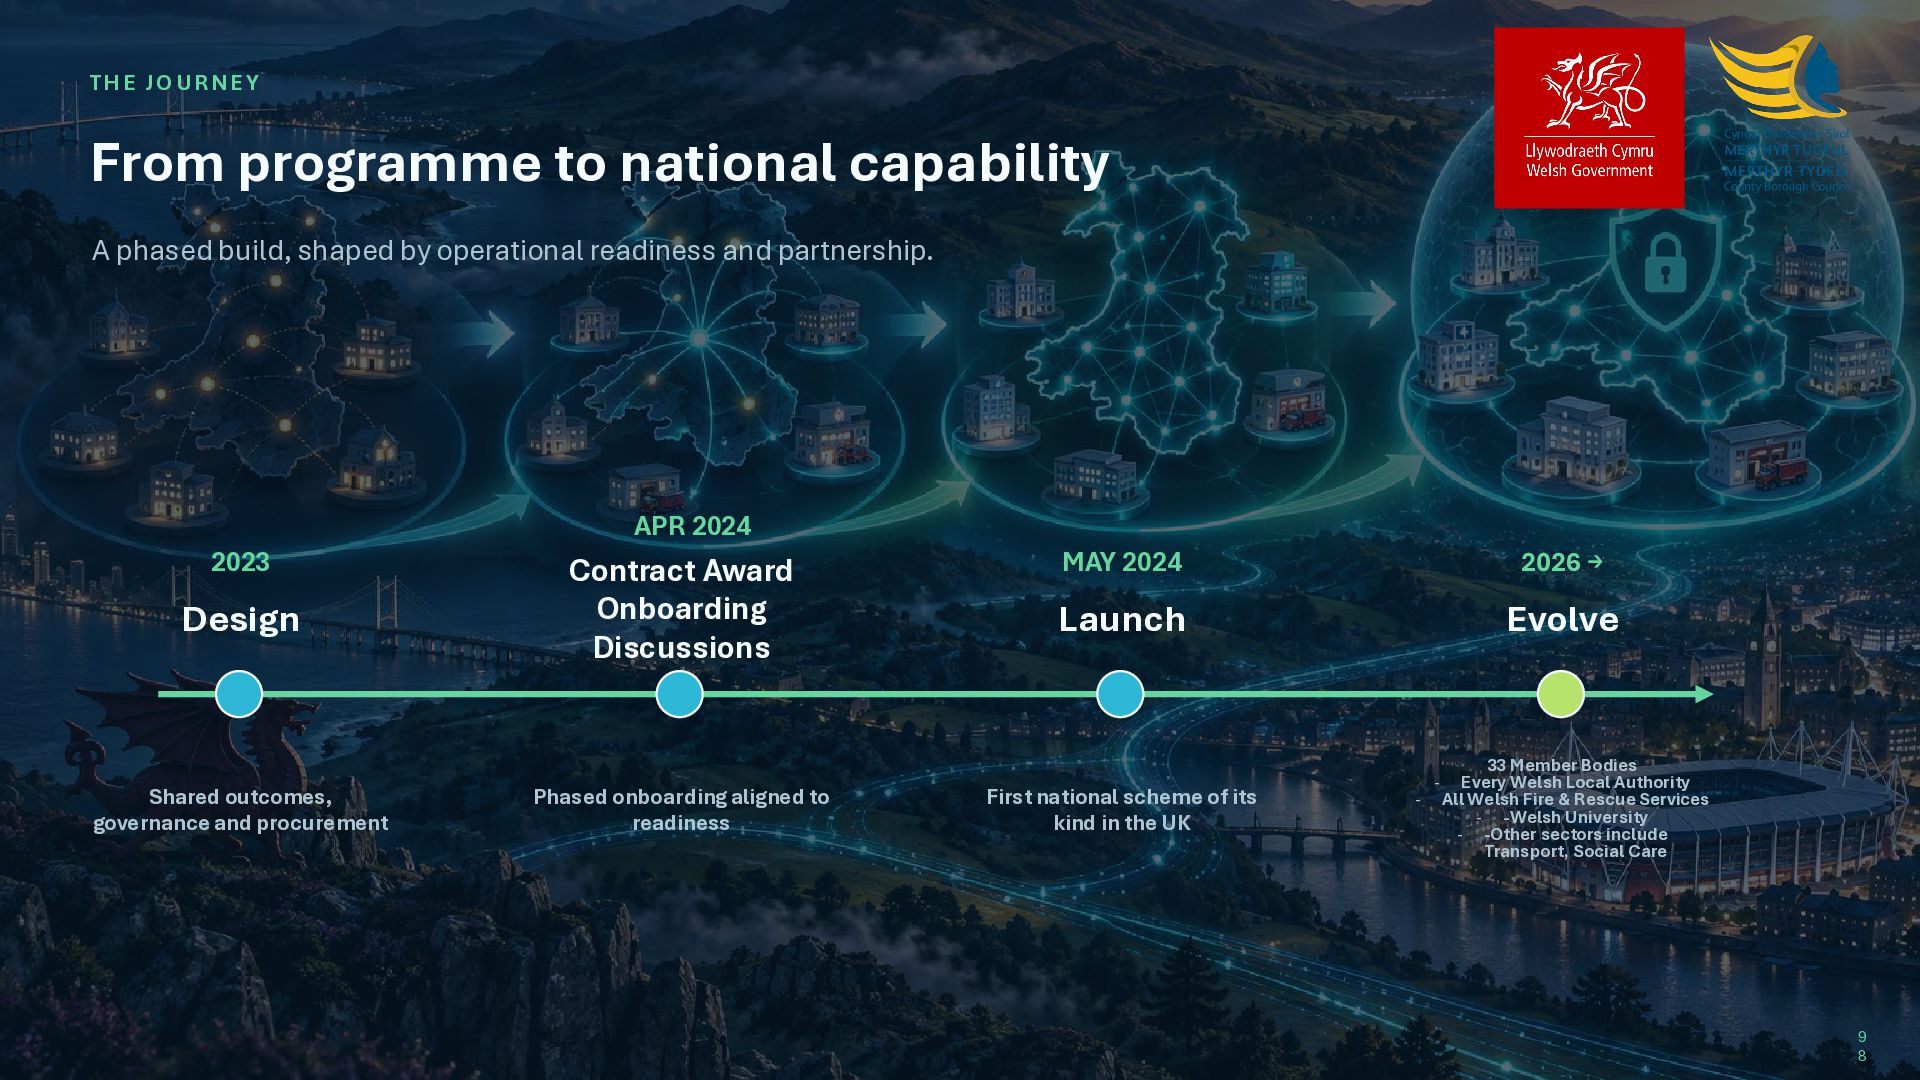
  77. THE JOURNEY From programme to national capability A phased build,

    shaped by operational readiness and partnership. 2023 Design Shared outcomes, governance and procurement CYMRUSOC • PROTECTING WALES TOGETHER APR 2024 Contract Award Onboarding Discussions Phased onboarding aligned to readiness MAY 2024 2026 → Launch Evolve First national scheme of its kind in the UK - - 33 Member Bodies Every Welsh Local Authority All Welsh Fire & Rescue Services - -Welsh University - -Other sectors include Transport, Social Care CYMRUSEC SUMMIT 2026 9 8
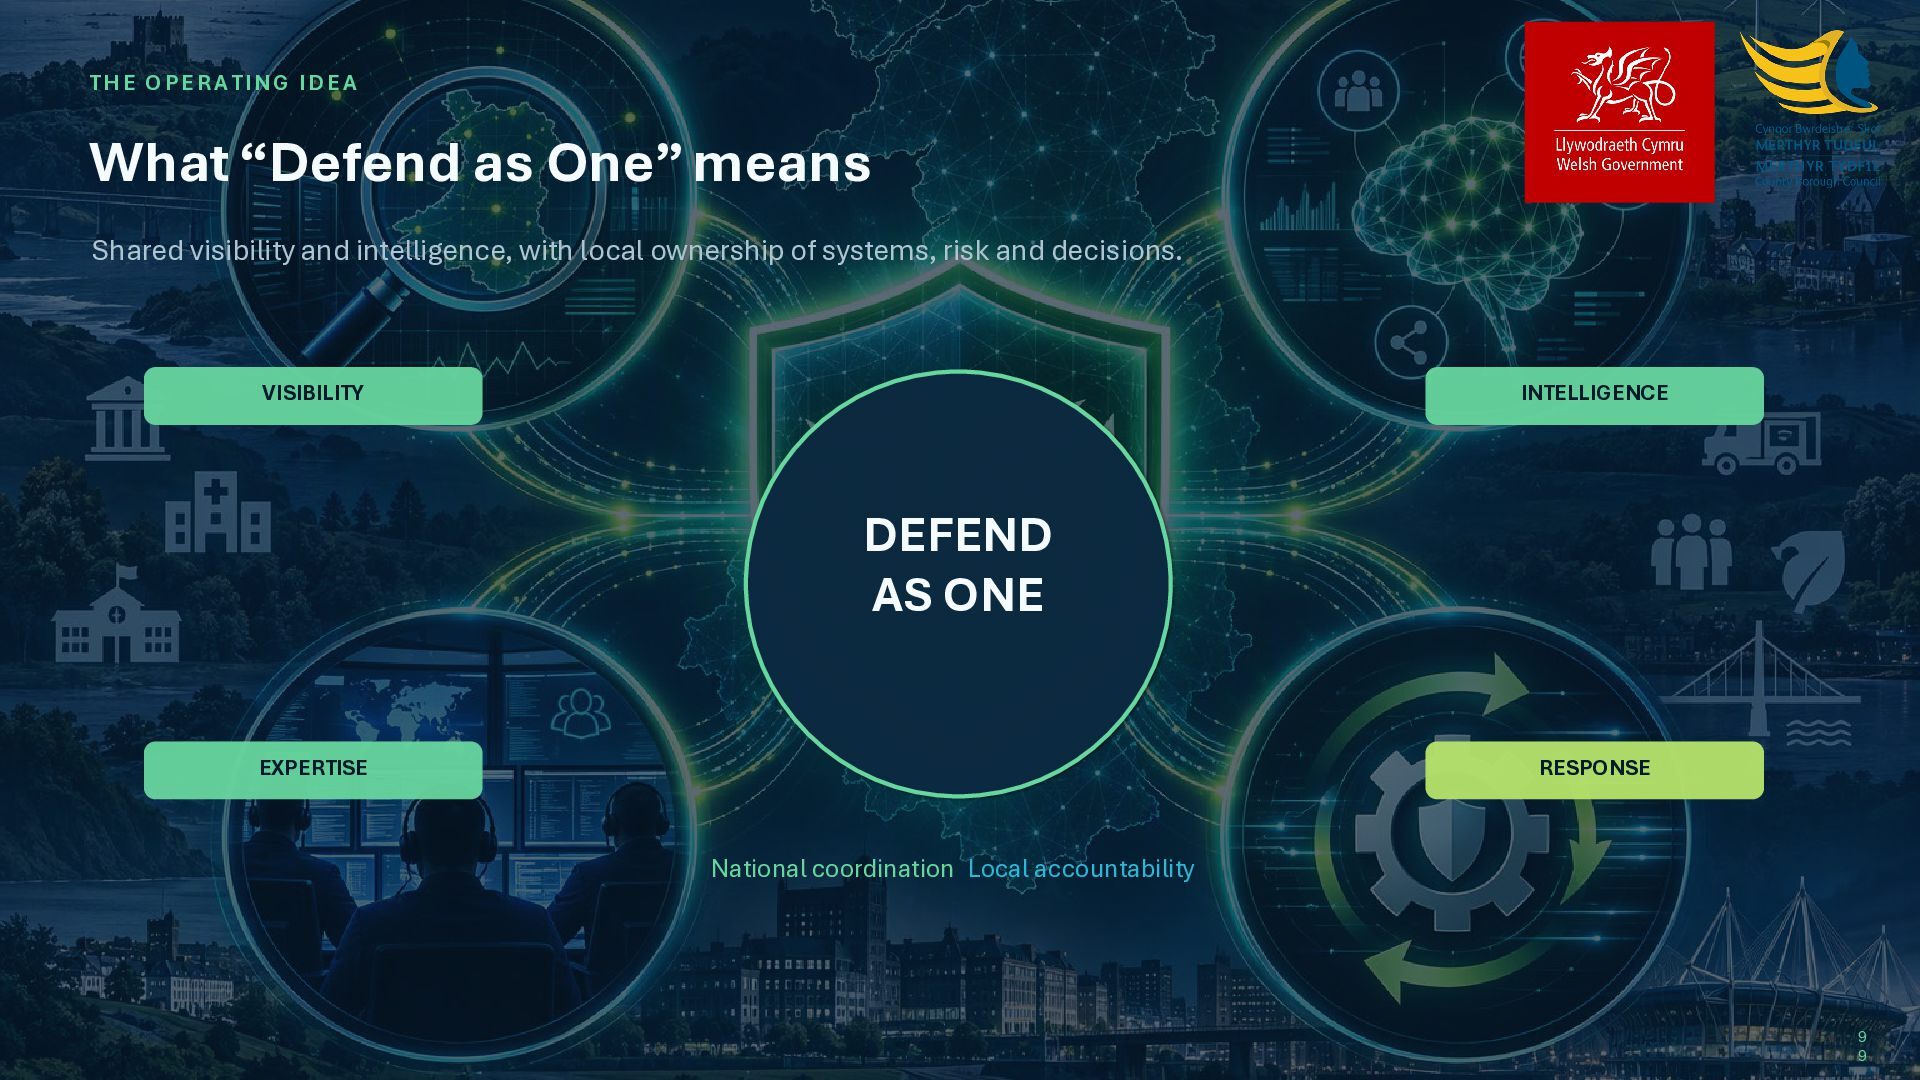
  78. THE OPERATING IDEA What “Defend as One” means Shared visibility

    and intelligence, with local ownership of systems, risk and decisions. VISIBILITY INTELLIGENCE DEFEND AS ONE EXPERTISE RESPONSE National coordination Local accountability CYMRUSOC • PROTECTING WALES TOGETHER CYMRUSEC SUMMIT 2026 9 9
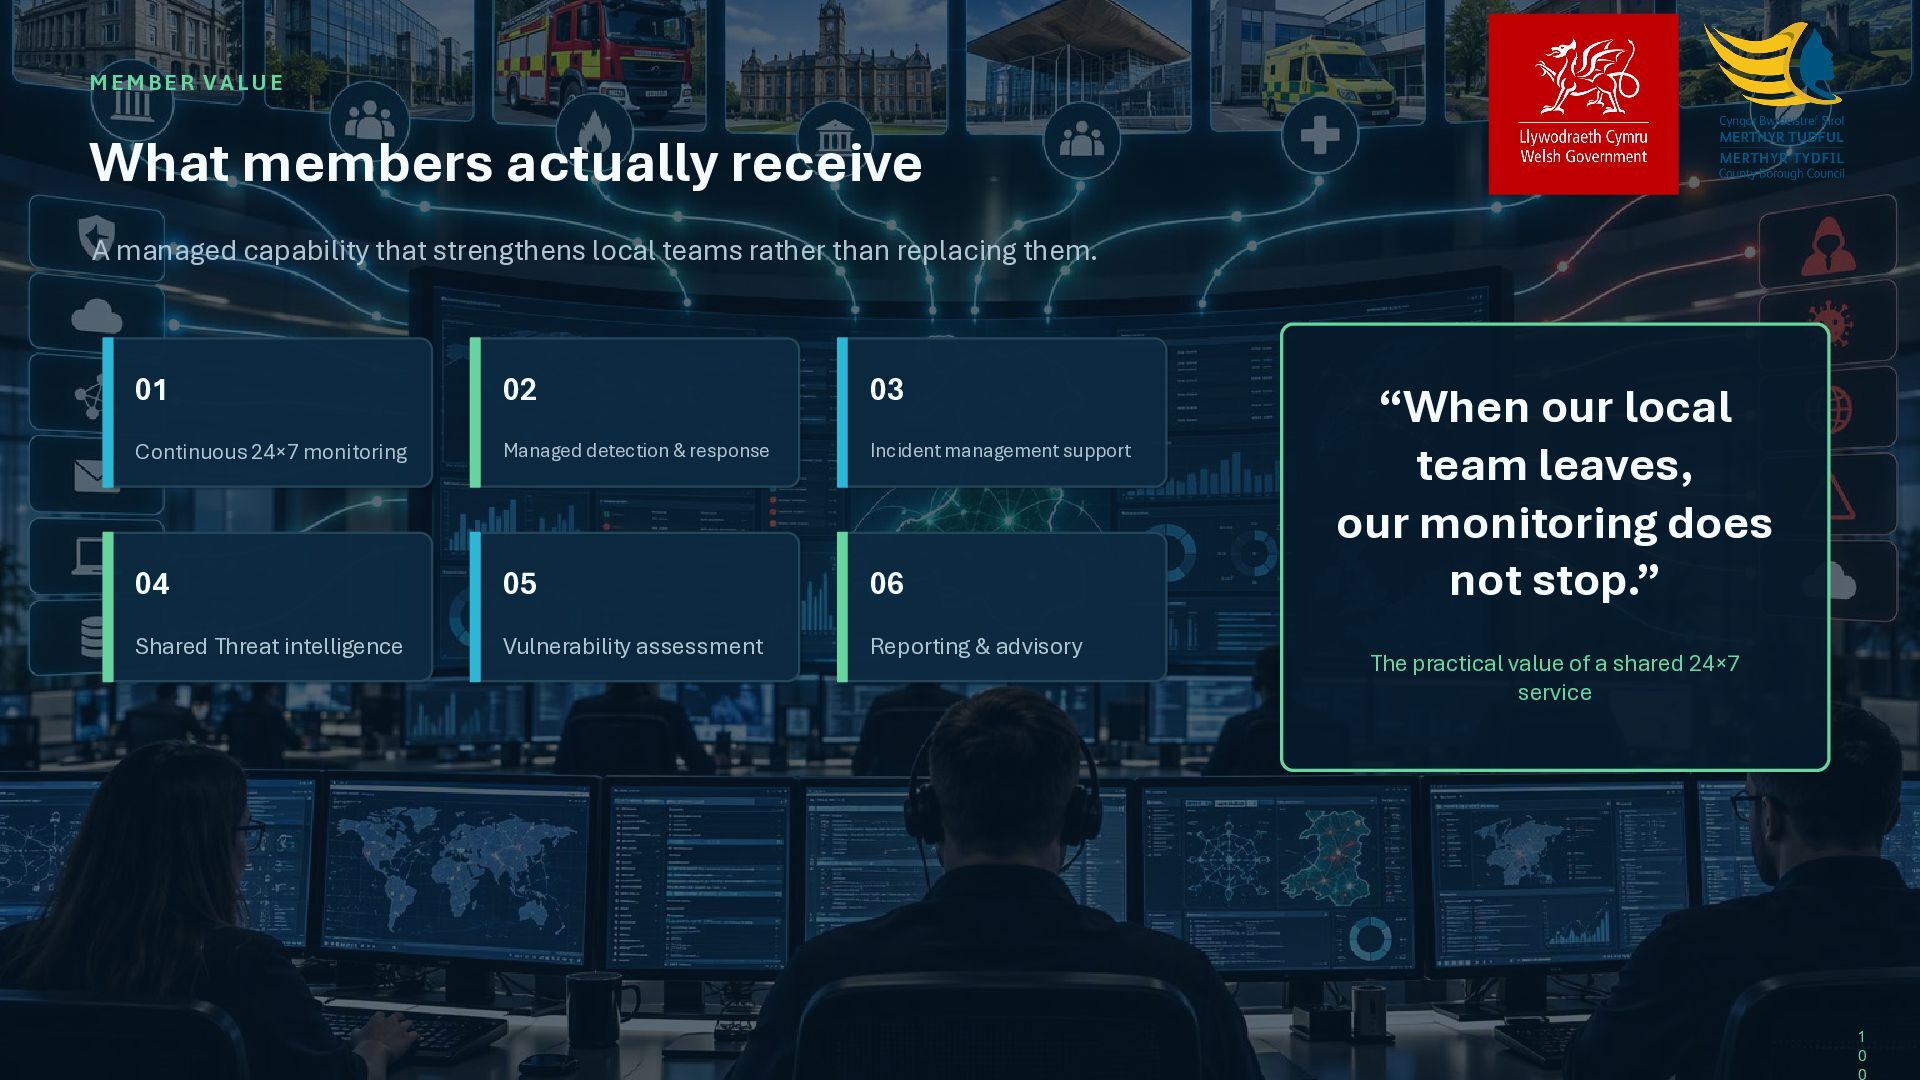
  79. MEMBER VALUE What members actually receive A managed capability that

    strengthens local teams rather than replacing them. 01 02 03 Continuous 24×7 monitoring Managed detection & response Incident management support 04 05 06 Shared Threat intelligence Vulnerability assessment Reporting & advisory CYMRUSOC • PROTECTING WALES TOGETHER “When our local team leaves, our monitoring does not stop.” The practical value of a shared 24×7 service CYMRUSEC SUMMIT 2026 1 0 0
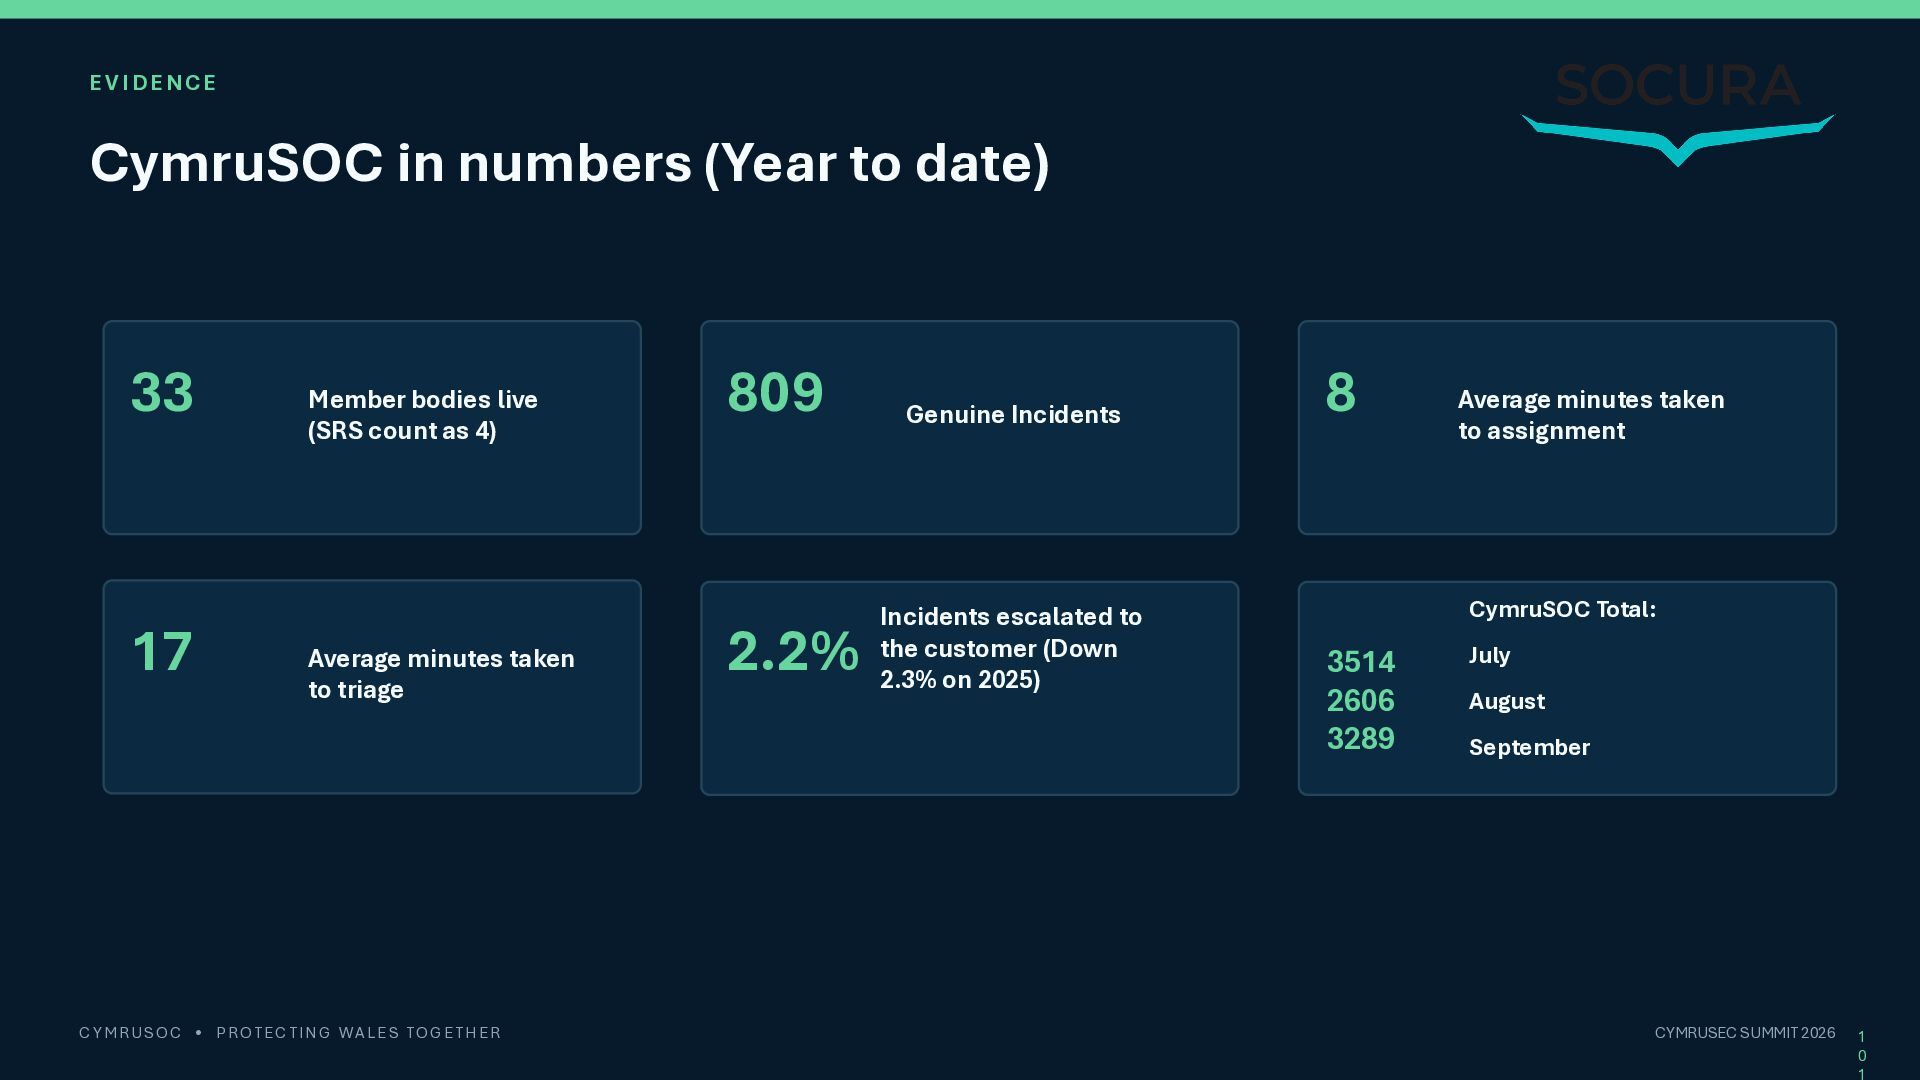
  80. EVIDENCE CymruSOC in numbers (Year to date) 33 17 Member

    bodies live (SRS count as 4) Average minutes taken to triage CYMRUSOC • PROTECTING WALES TOGETHER 809 2.2% Genuine Incidents Incidents escalated to the customer (Down 2.3% on 2025) 8 Average minutes taken to assignment CymruSOC Total: 3514 2606 3289 July August September CYMRUSEC SUMMIT 2026 1 0 1
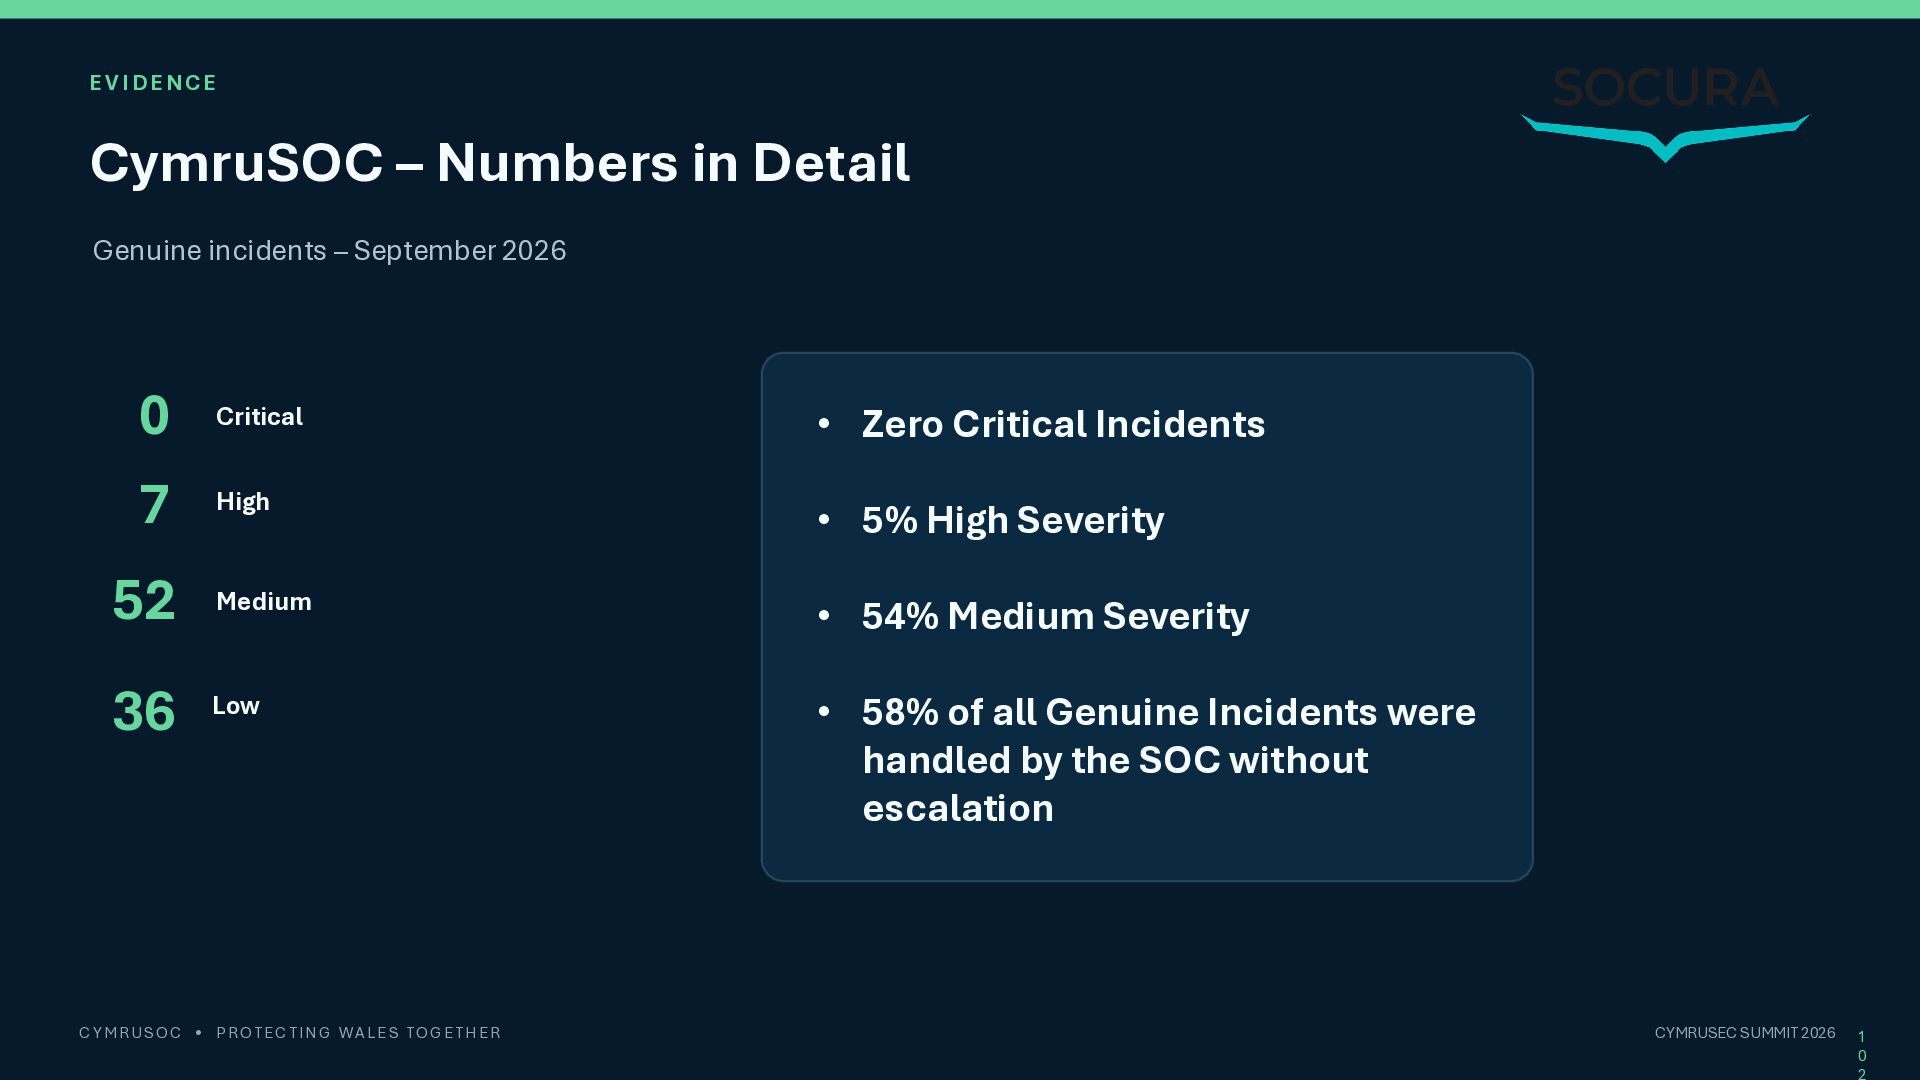
  81. EVIDENCE CymruSOC – Numbers in Detail Genuine incidents – September

    2026 0 7 Critical • Zero Critical Incidents High • 5% High Severity 52 Medium 36 Low CYMRUSOC • PROTECTING WALES TOGETHER • 54% Medium Severity • 58% of all Genuine Incidents were handled by the SOC without escalation CYMRUSEC SUMMIT 2026 1 0 2
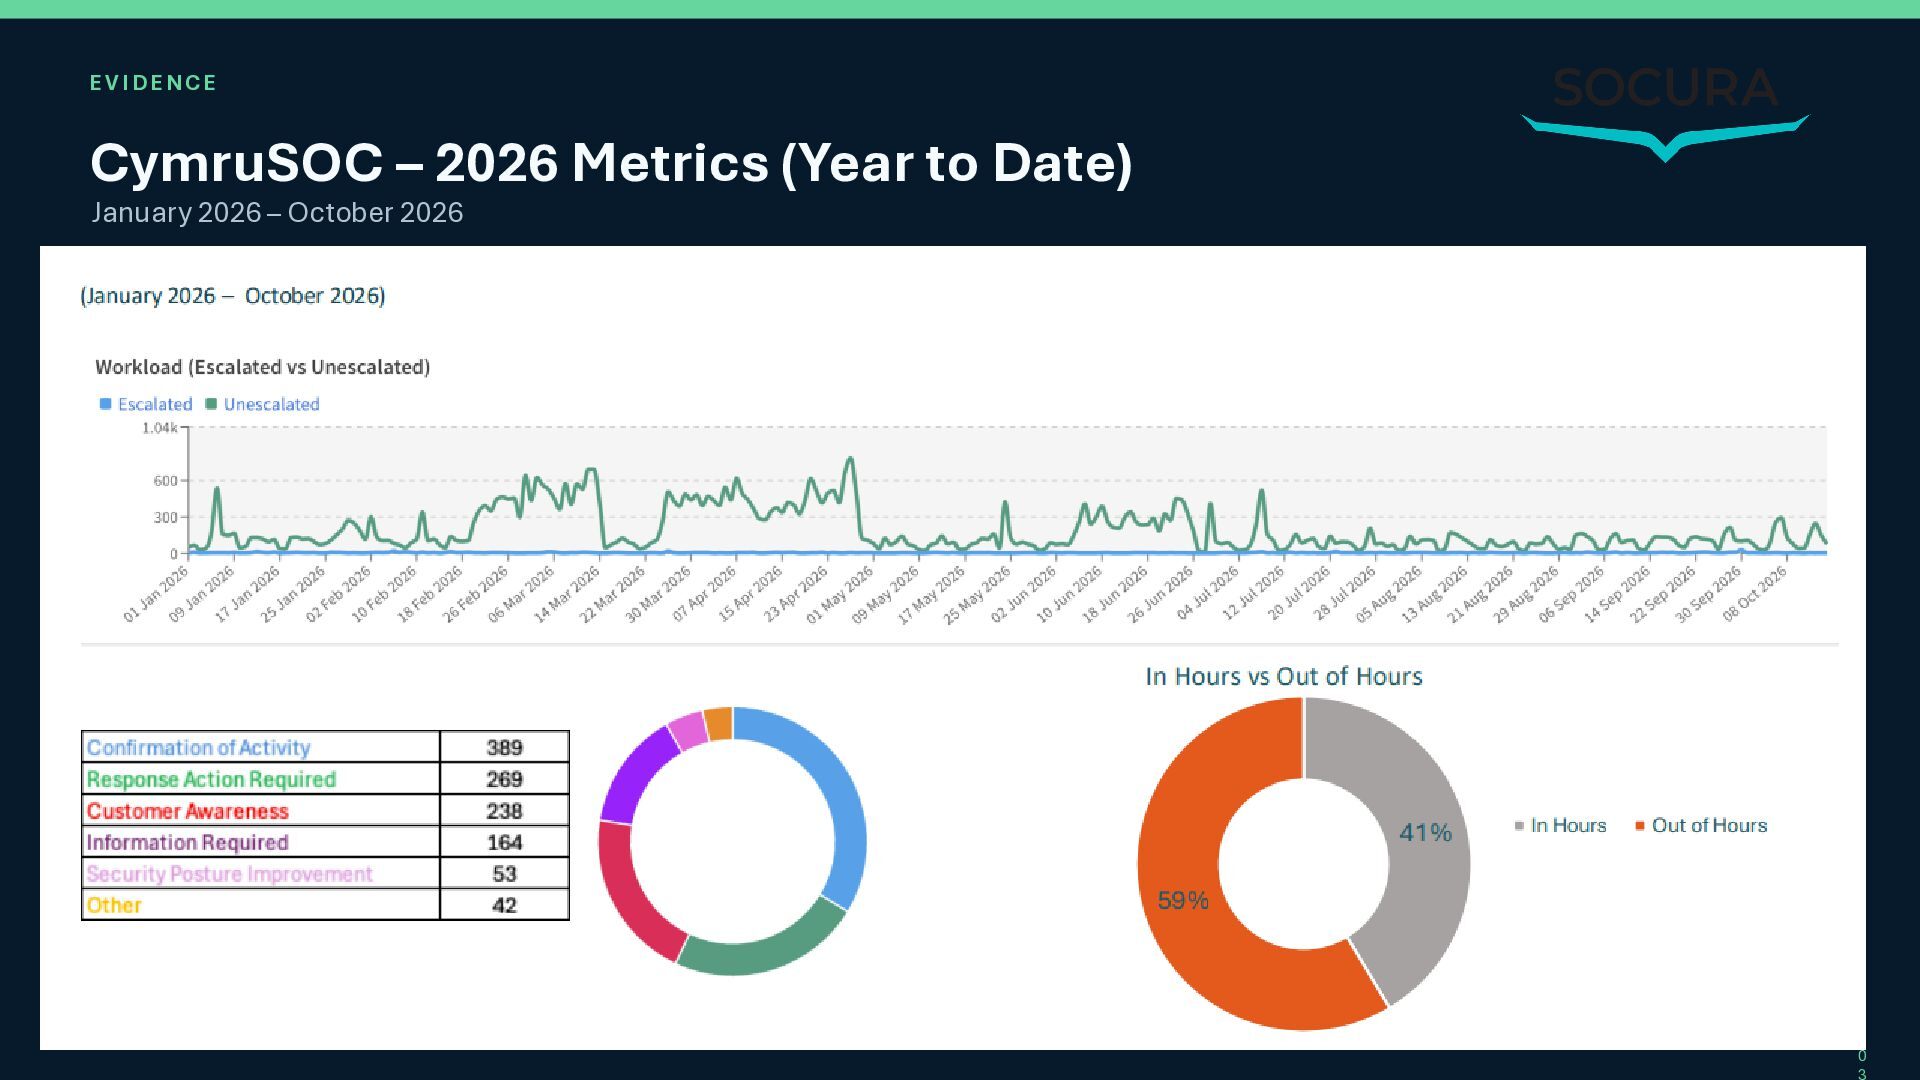
  82. EVIDENCE CymruSOC – 2026 Metrics (Year to Date) January 2026

    – October 2026 CYMRUSOC • PROTECTING WALES TOGETHER CYMRUSEC SUMMIT 2026 1 0 3
  83. BEYOND ALERTS The value is bigger than the technology Shared

    insight becomes shared readiness. “The technology enables the service, but the collaboration is what makes it successful.” People CYMRUSOC • PROTECTING WALES TOGETHER Intelligence Relationships Collective resilience CYMRUSEC SUMMIT 2026 1 0 4
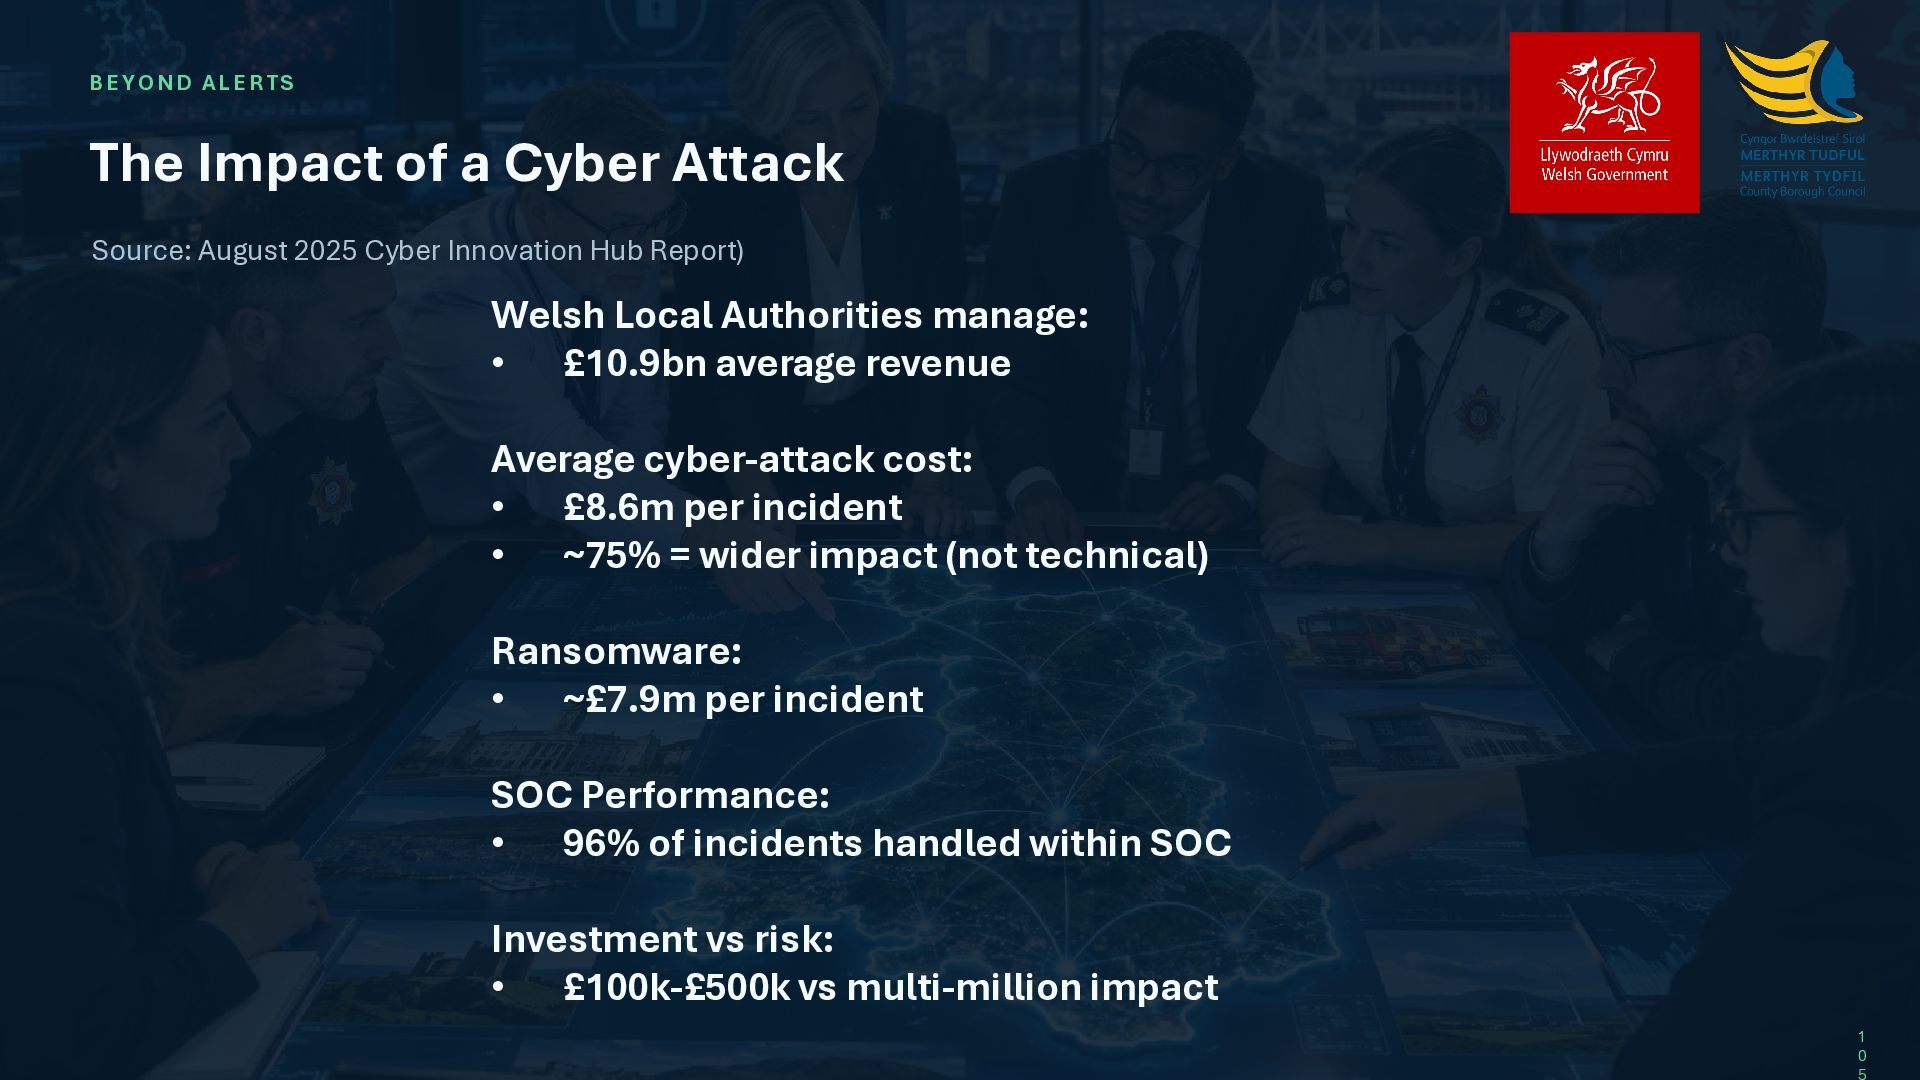
  84. BEYOND ALERTS The Impact of a Cyber Attack Source: August

    2025 Cyber Innovation Hub Report) Welsh Local Authorities manage: • £10.9bn average revenue Average cyber-attack cost: • £8.6m per incident • ~75% = wider impact (not technical) Ransomware: • ~£7.9m per incident SOC Performance: • 96% of incidents handled within SOC Investment vs risk: • £100k-£500k vs multi-million impact CYMRUSOC • PROTECTING WALES TOGETHER CYMRUSEC SUMMIT 2026 1 0 5
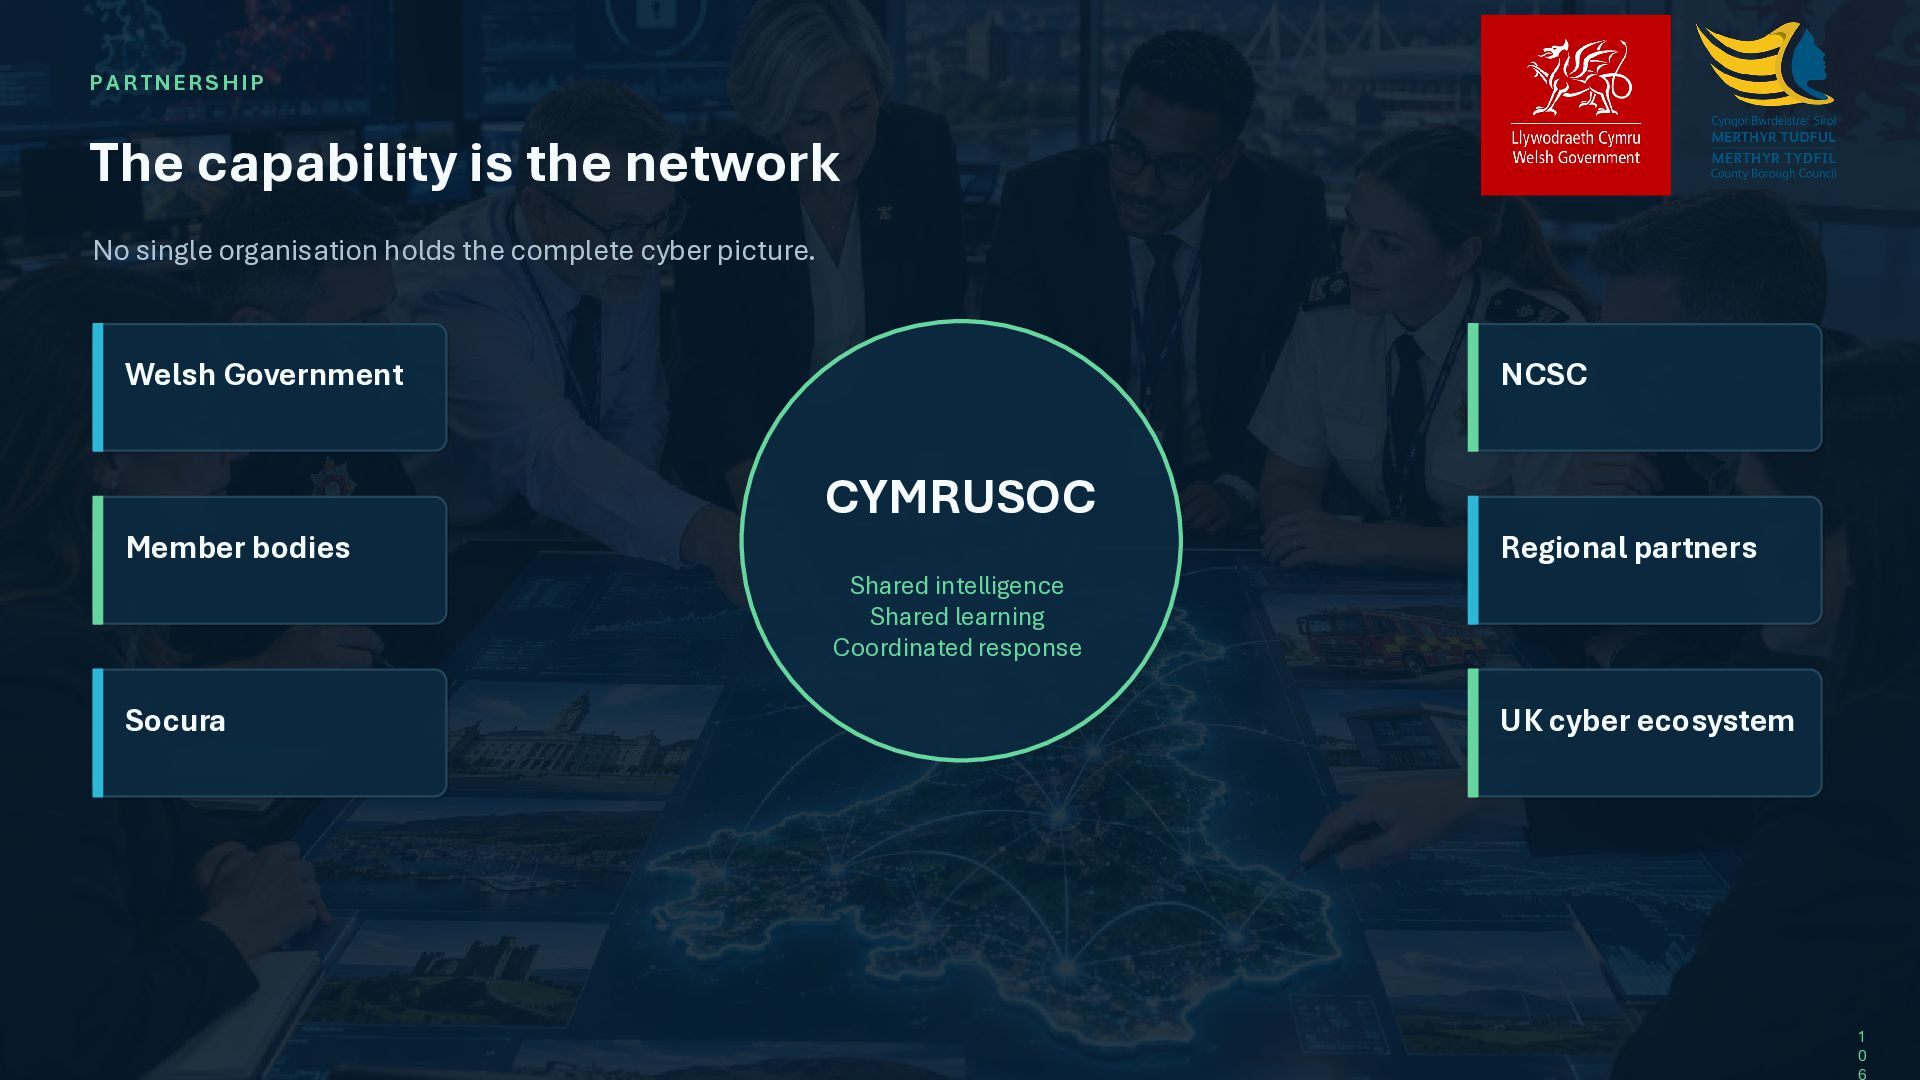
  85. PARTNERSHIP The capability is the network No single organisation holds

    the complete cyber picture. Welsh Government Member bodies NCSC CYMRUSOC Regional partners Shared intelligence Shared learning Coordinated response Socura CYMRUSOC • PROTECTING WALES TOGETHER UK cyber ecosystem CYMRUSEC SUMMIT 2026 1 0 6
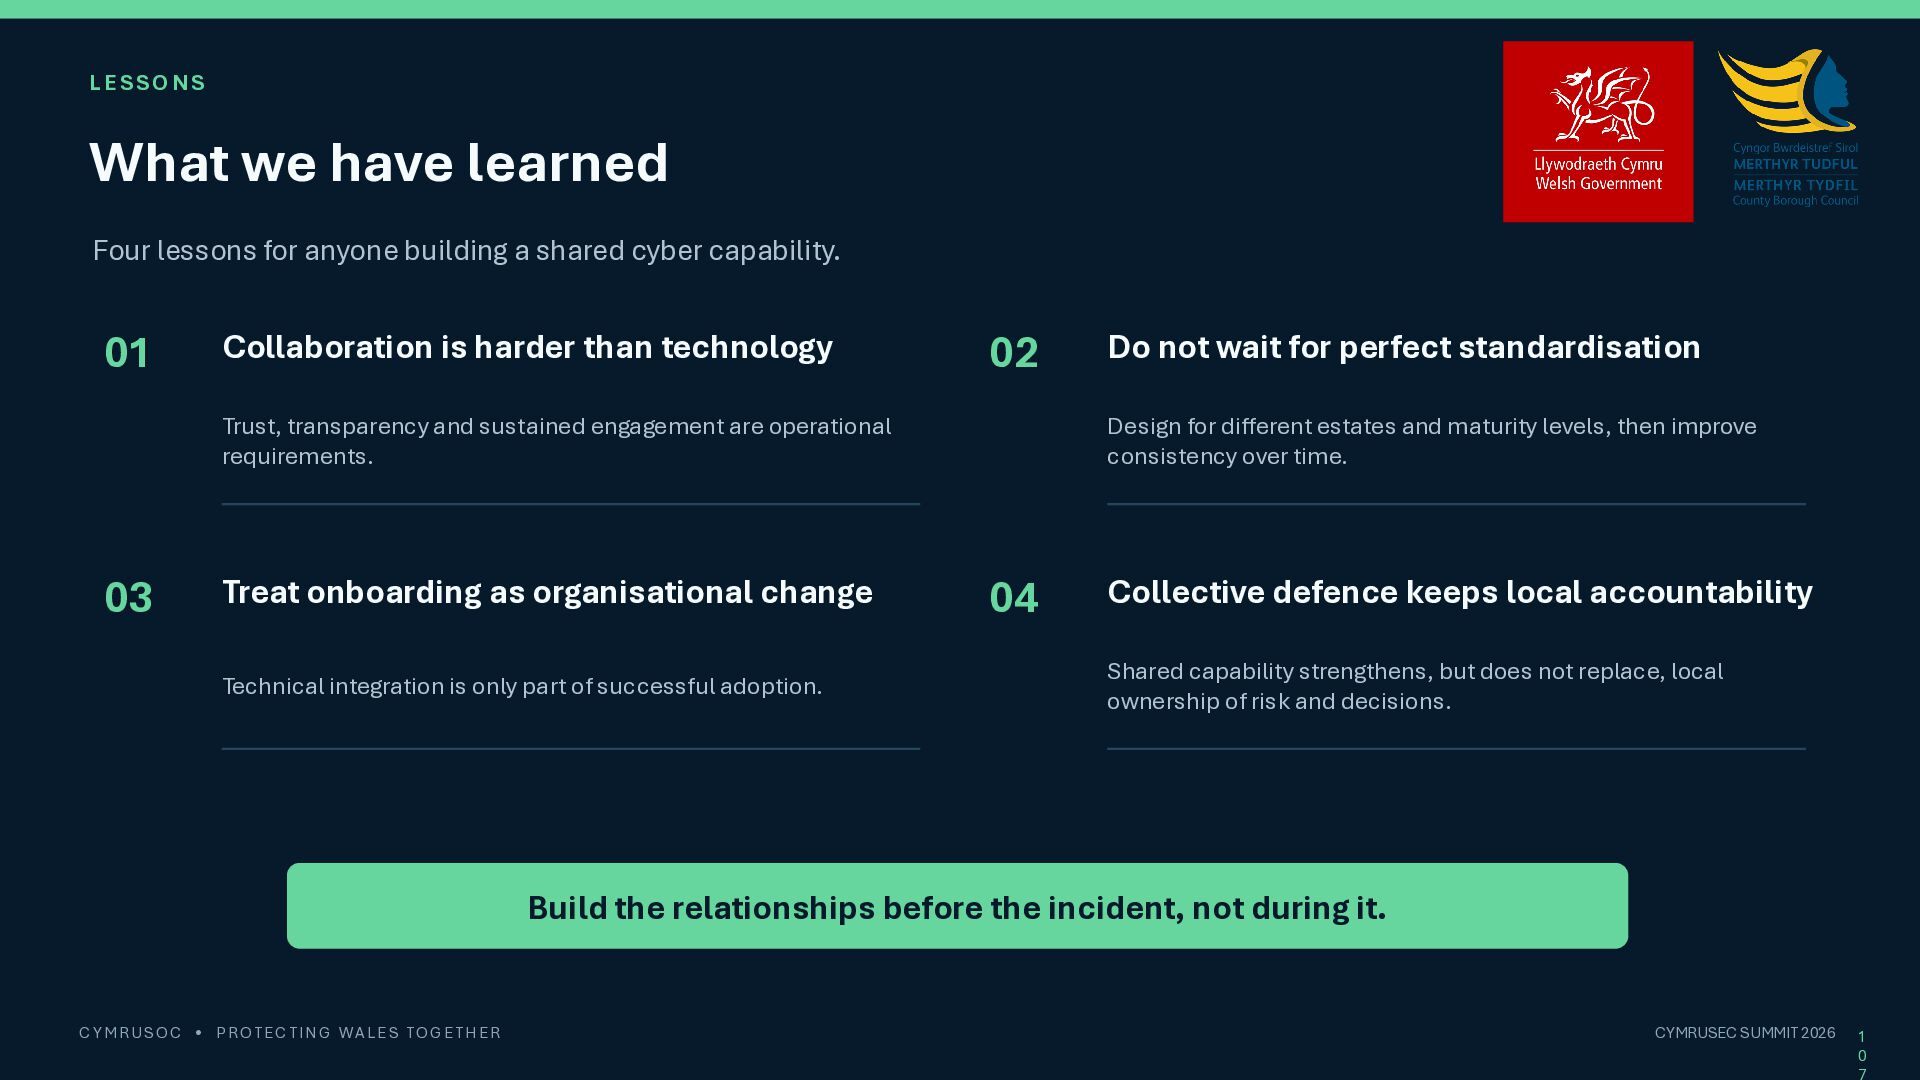
  86. LESSONS What we have learned Four lessons for anyone building
    a shared cyber capability. 01 Collaboration is harder than technology 02 Trust, transparency and sustained engagement are operational requirements. 03 Treat onboarding as organisational change Technical integration is only part of successful adoption. Do not wait for perfect standardisation Design for different estates and maturity levels, then improve consistency over time. 04 Collective defence keeps local accountability Shared capability strengthens, but does not replace, local ownership of risk and decisions. Build the relationships before the incident, not during it. CYMRUSOC • PROTECTING WALES TOGETHER CYMRUSEC SUMMIT 2026 1 0 7
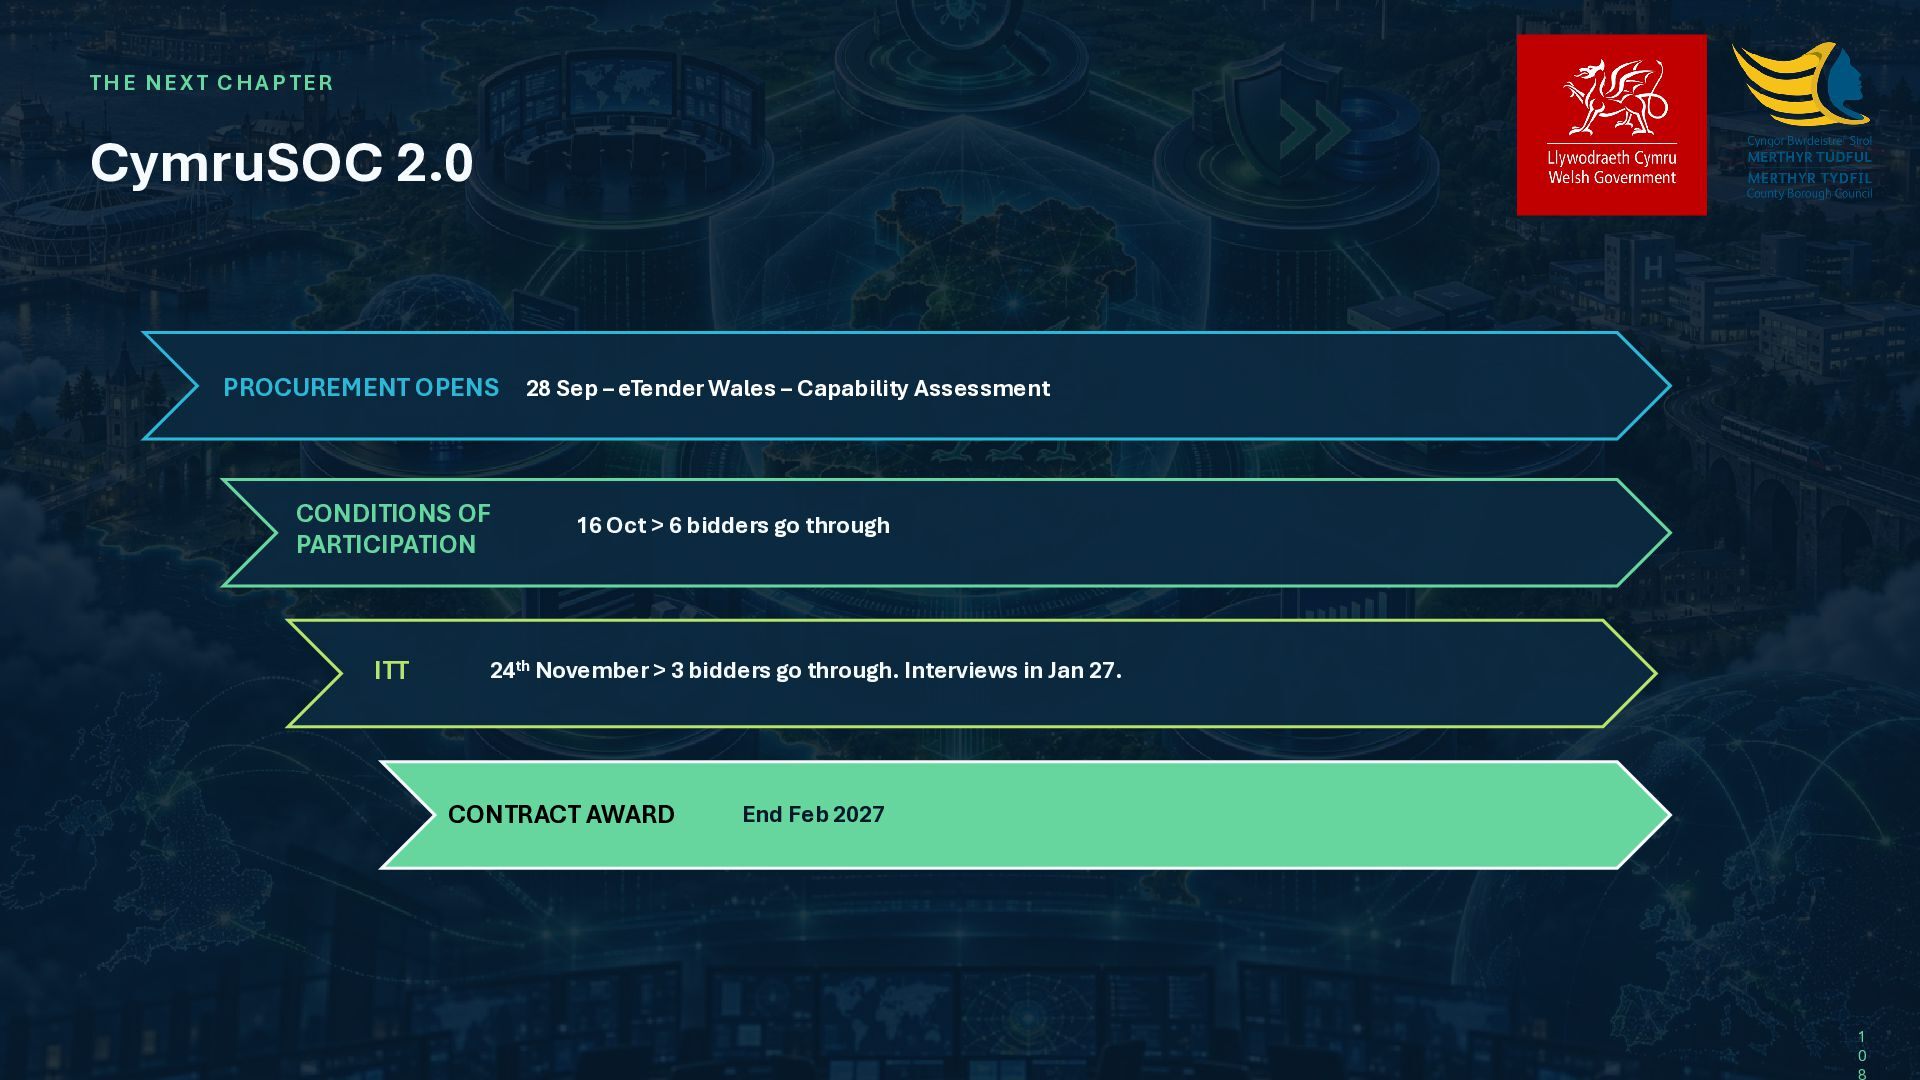
  87. THE NEXT CHAPTER CymruSOC 2.0 PROCUREMENT OPENS CONDITIONS OF PARTICIPATION

    ITT 28 Sep – eTender Wales – Capability Assessment 16 Oct > 6 bidders go through 24th November > 3 bidders go through. Interviews in Jan 27. CONTRACT AWARD CYMRUSOC • PROTECTING WALES TOGETHER End Feb 2027 CYMRUSEC SUMMIT 2026 1 0 8
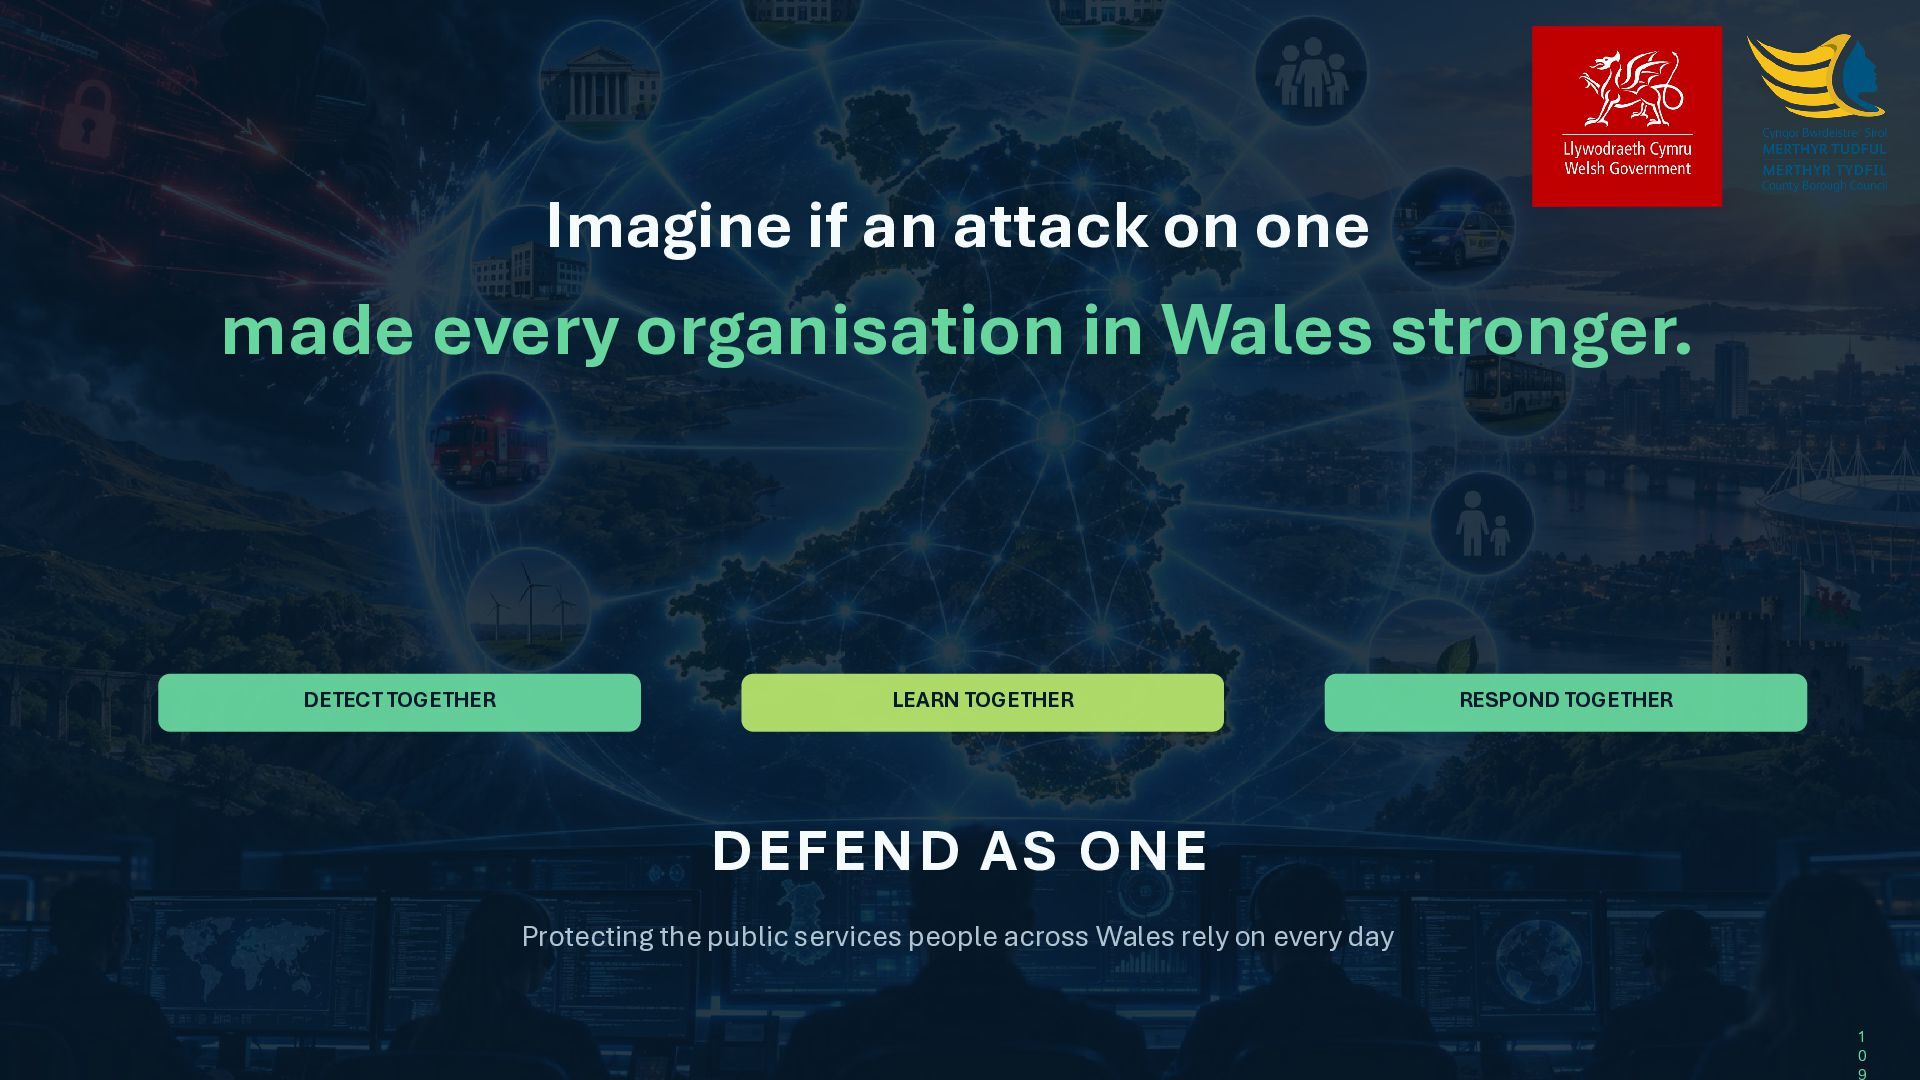
  88. Imagine if an attack on one made every organisation in

    Wales stronger. DETECT TOGETHER LEARN TOGETHER RESPOND TOGETHER DEFEND AS ONE Protecting the public services people across Wales rely on every day CYMRUSOC • PROTECTING WALES TOGETHER CYMRUSEC SUMMIT 2026 1 0 9
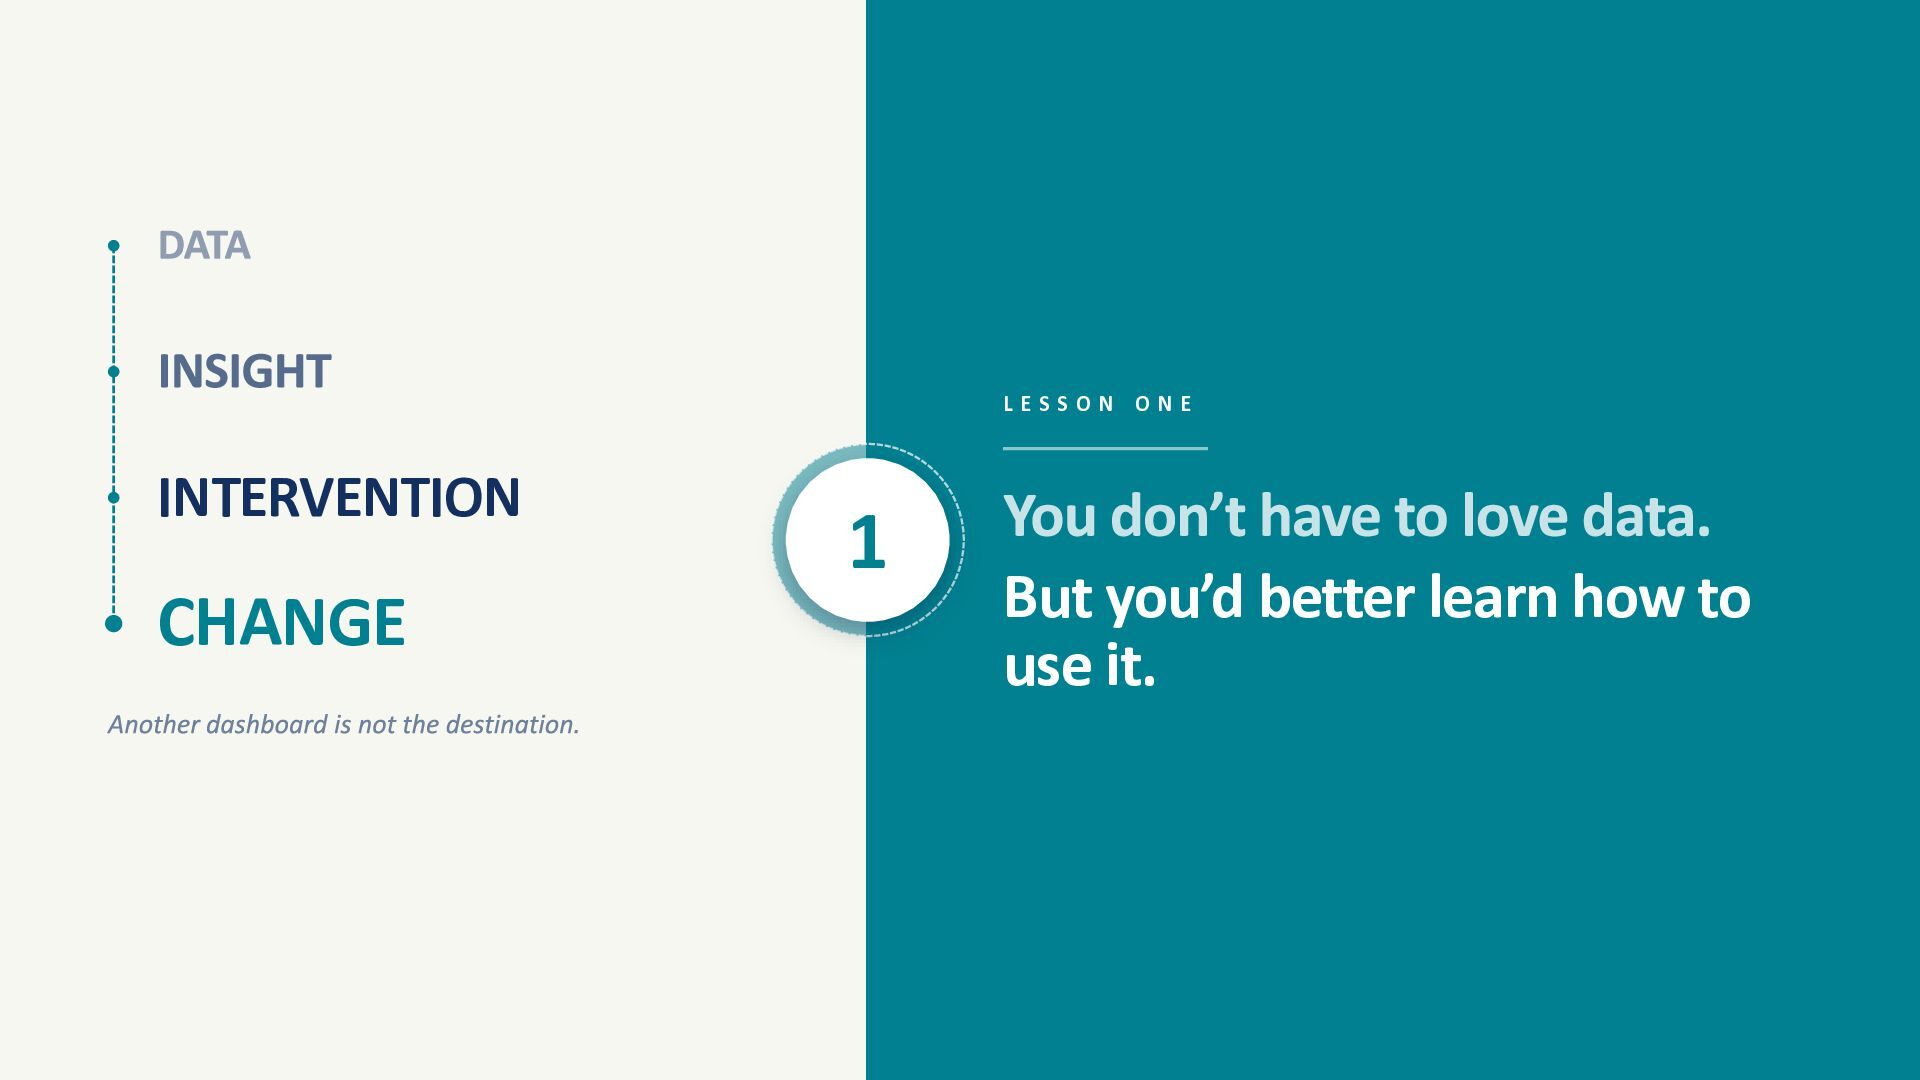
  89. CHARLIE SINCLAIR Adventures in Human Risk Moving past training and

    awareness to real impact VILLAGE DATA CULTURE RELEVANCE IMPACT
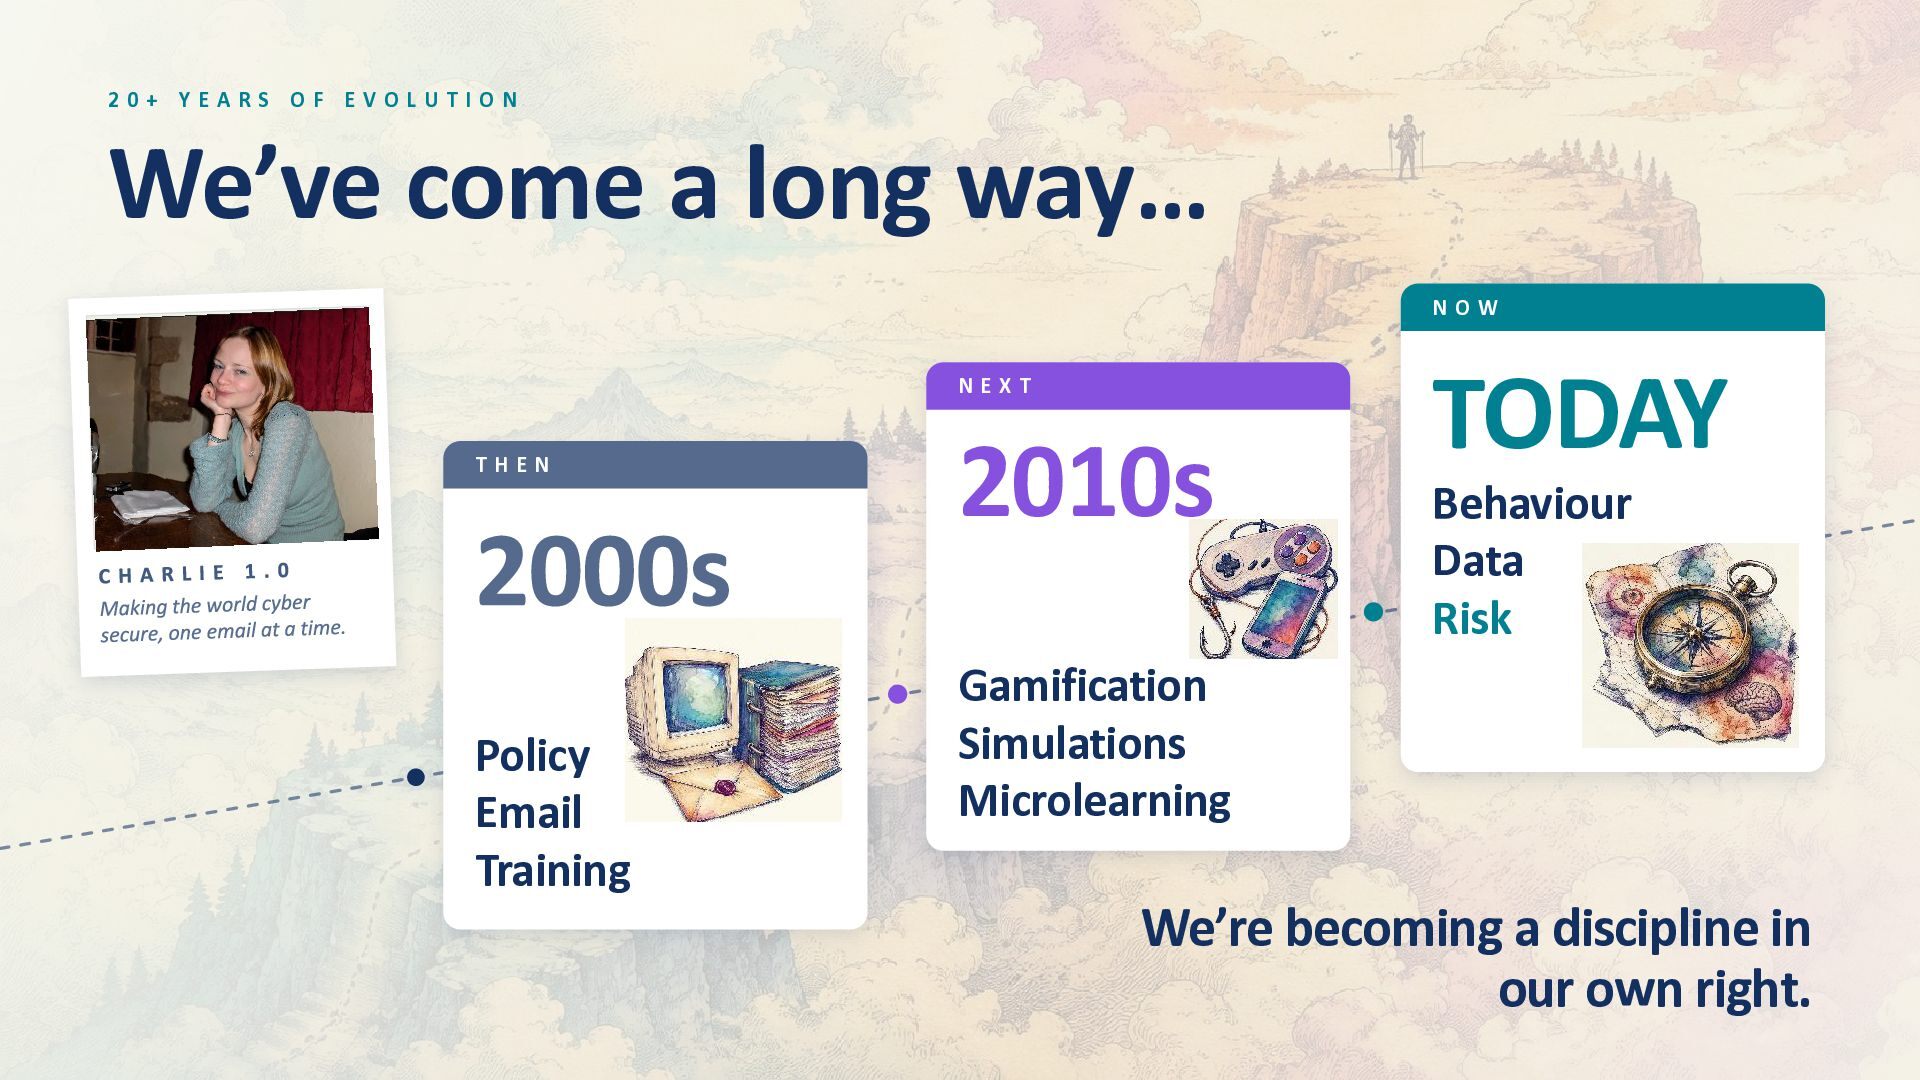
  90. 20+ YEARS OF EVOLUTION We’ve come a long way… NOW

    NEXT THEN Policy Email Training 2010s TODAY Behaviour Data Risk Gamification Simulations Microlearning We’re becoming a discipline in our own right.
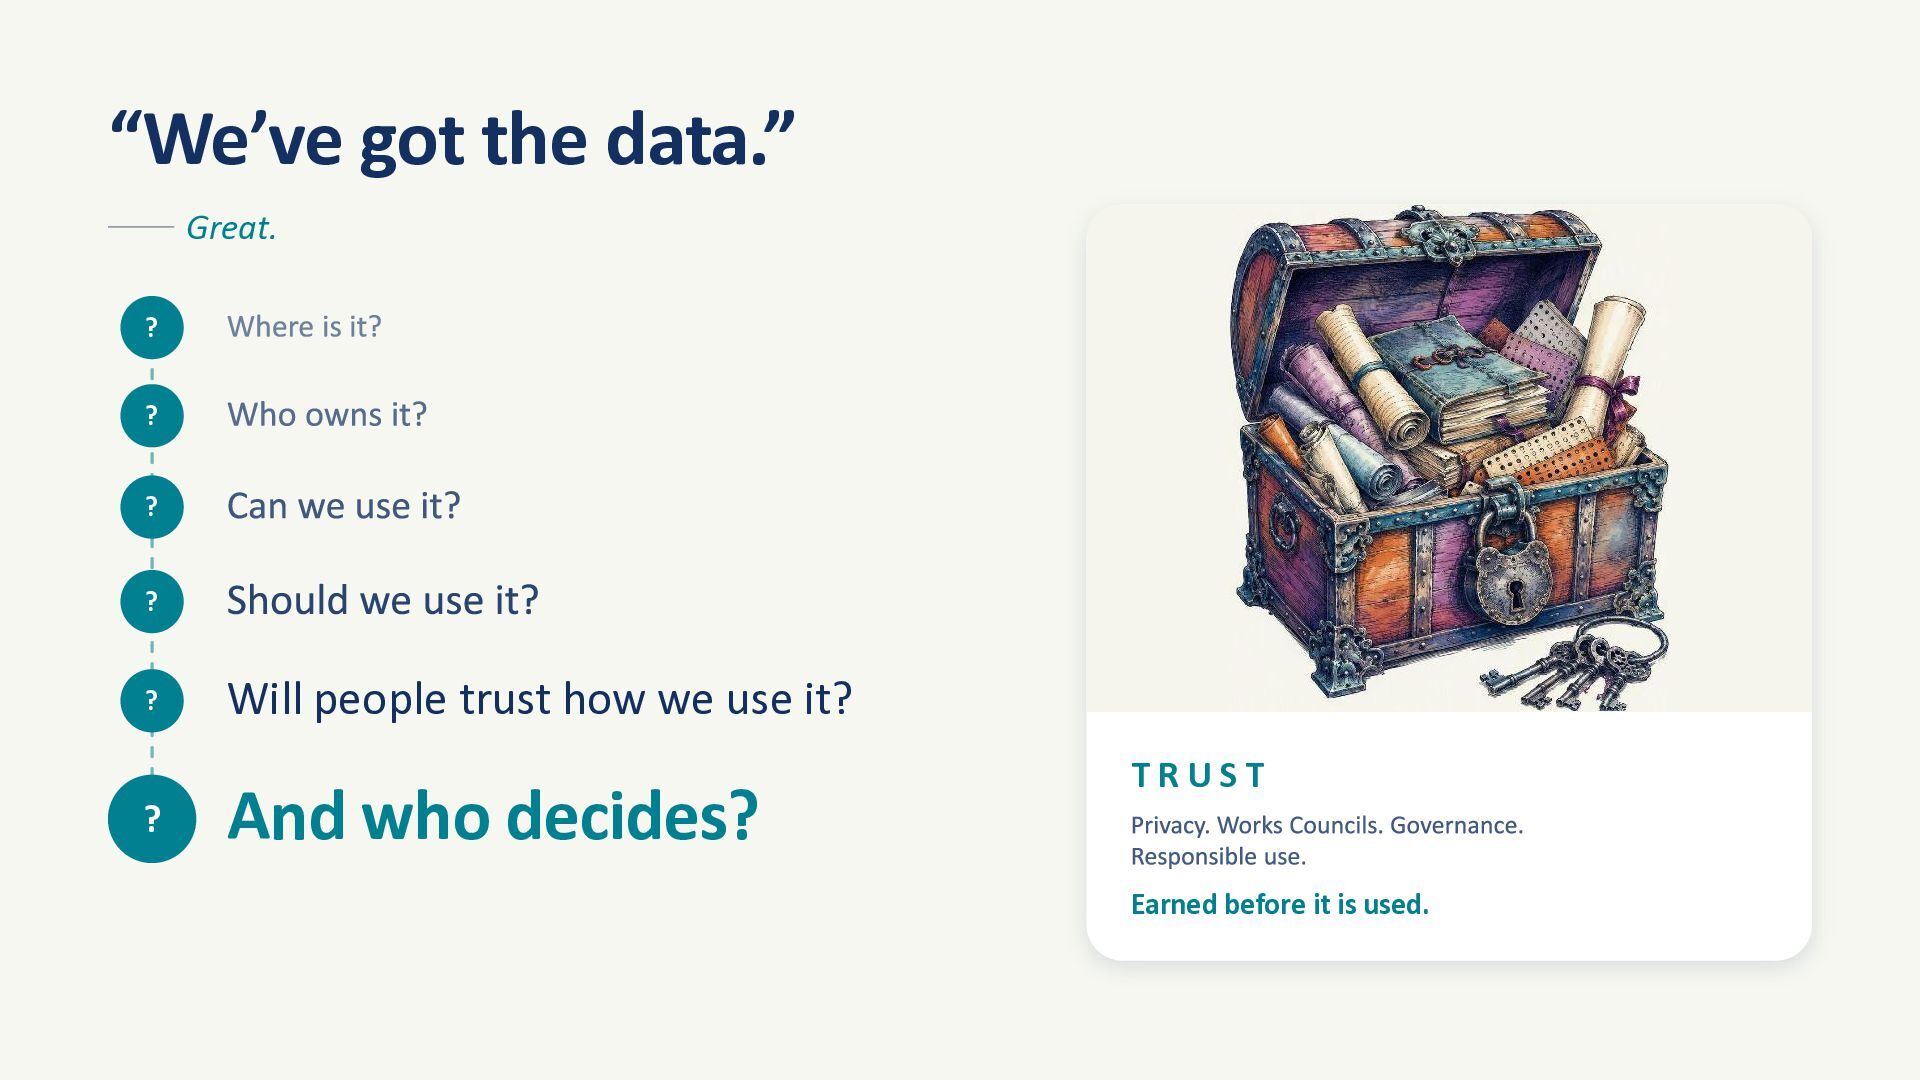
  91. “We’ve got the data.” Great. ? ? ? ? ?

    ? Will people trust how we use it? And who decides? TRUST Earned before it is used.
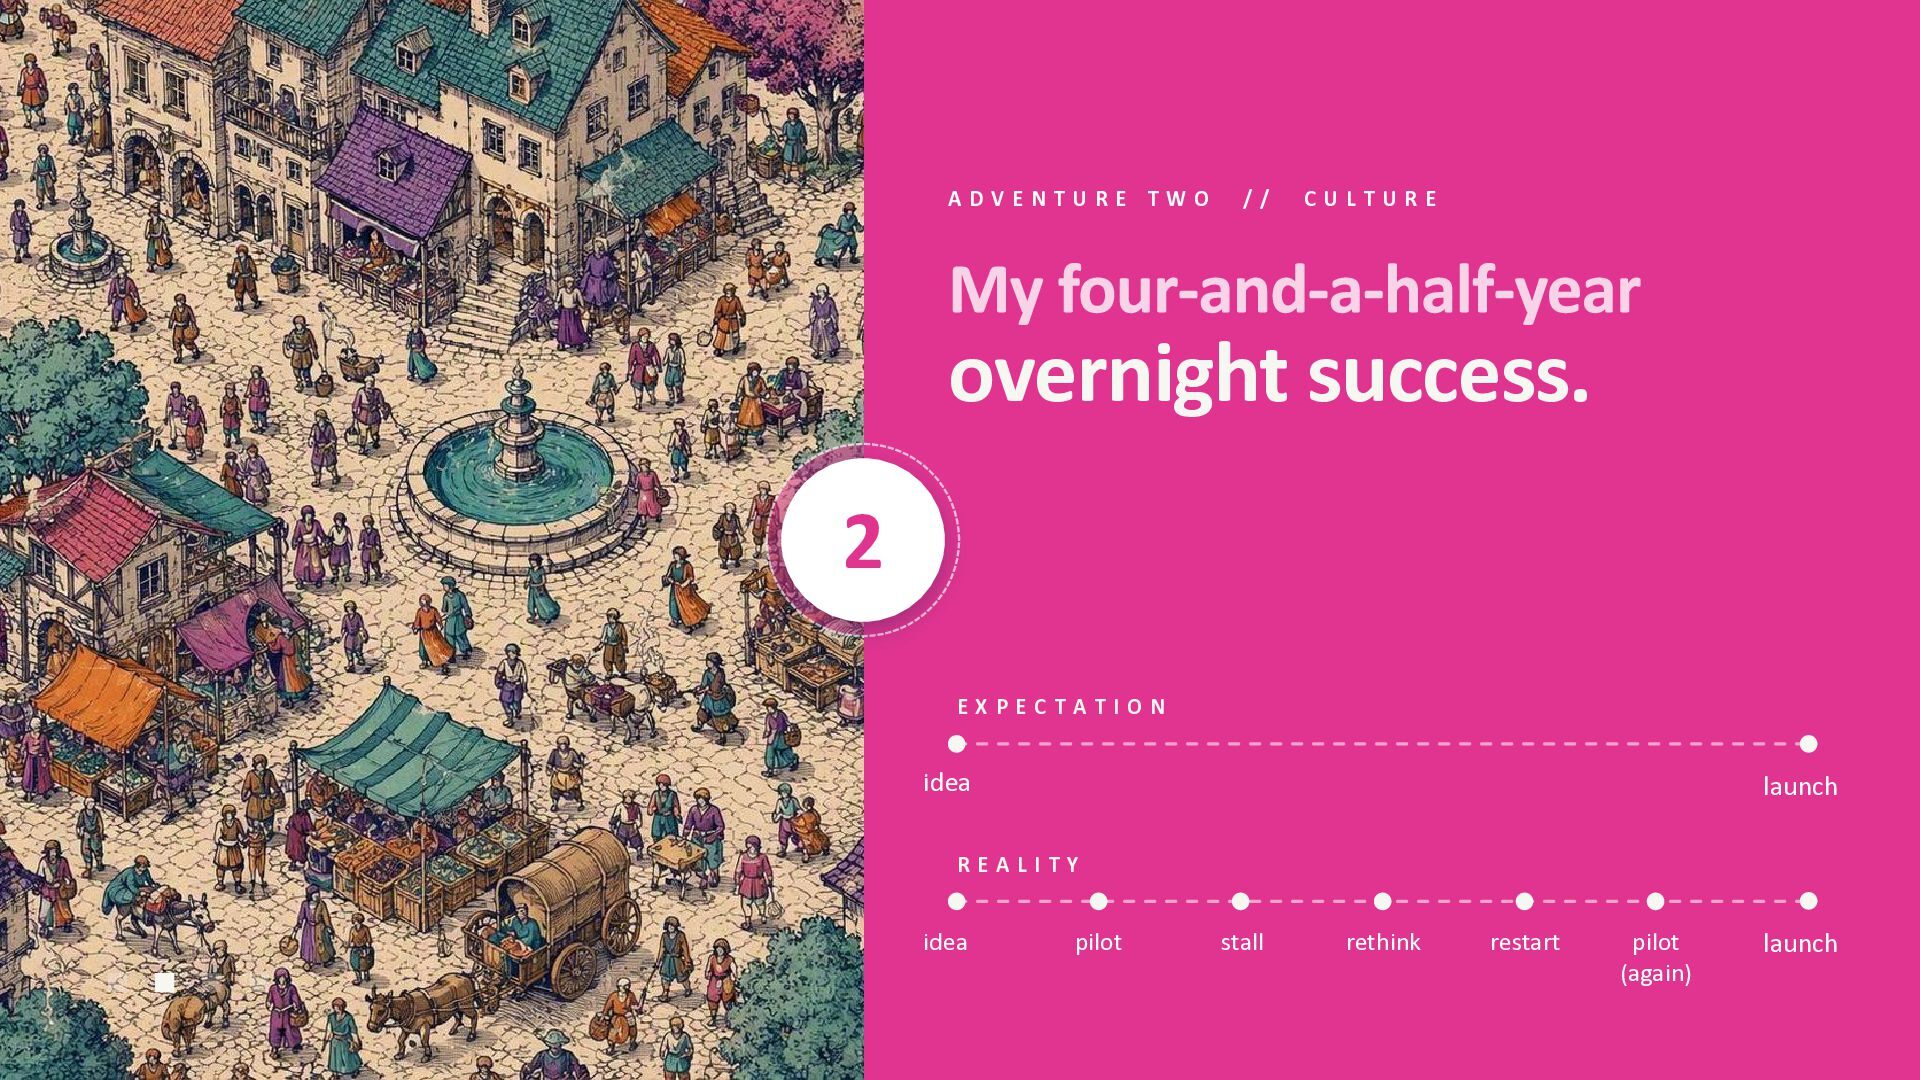
  92. ADVENTURE TWO // CULTURE overnight success. 2 EXPECTATION idea launch

    REALITY idea pilot stall rethink restart pilot (again) launch
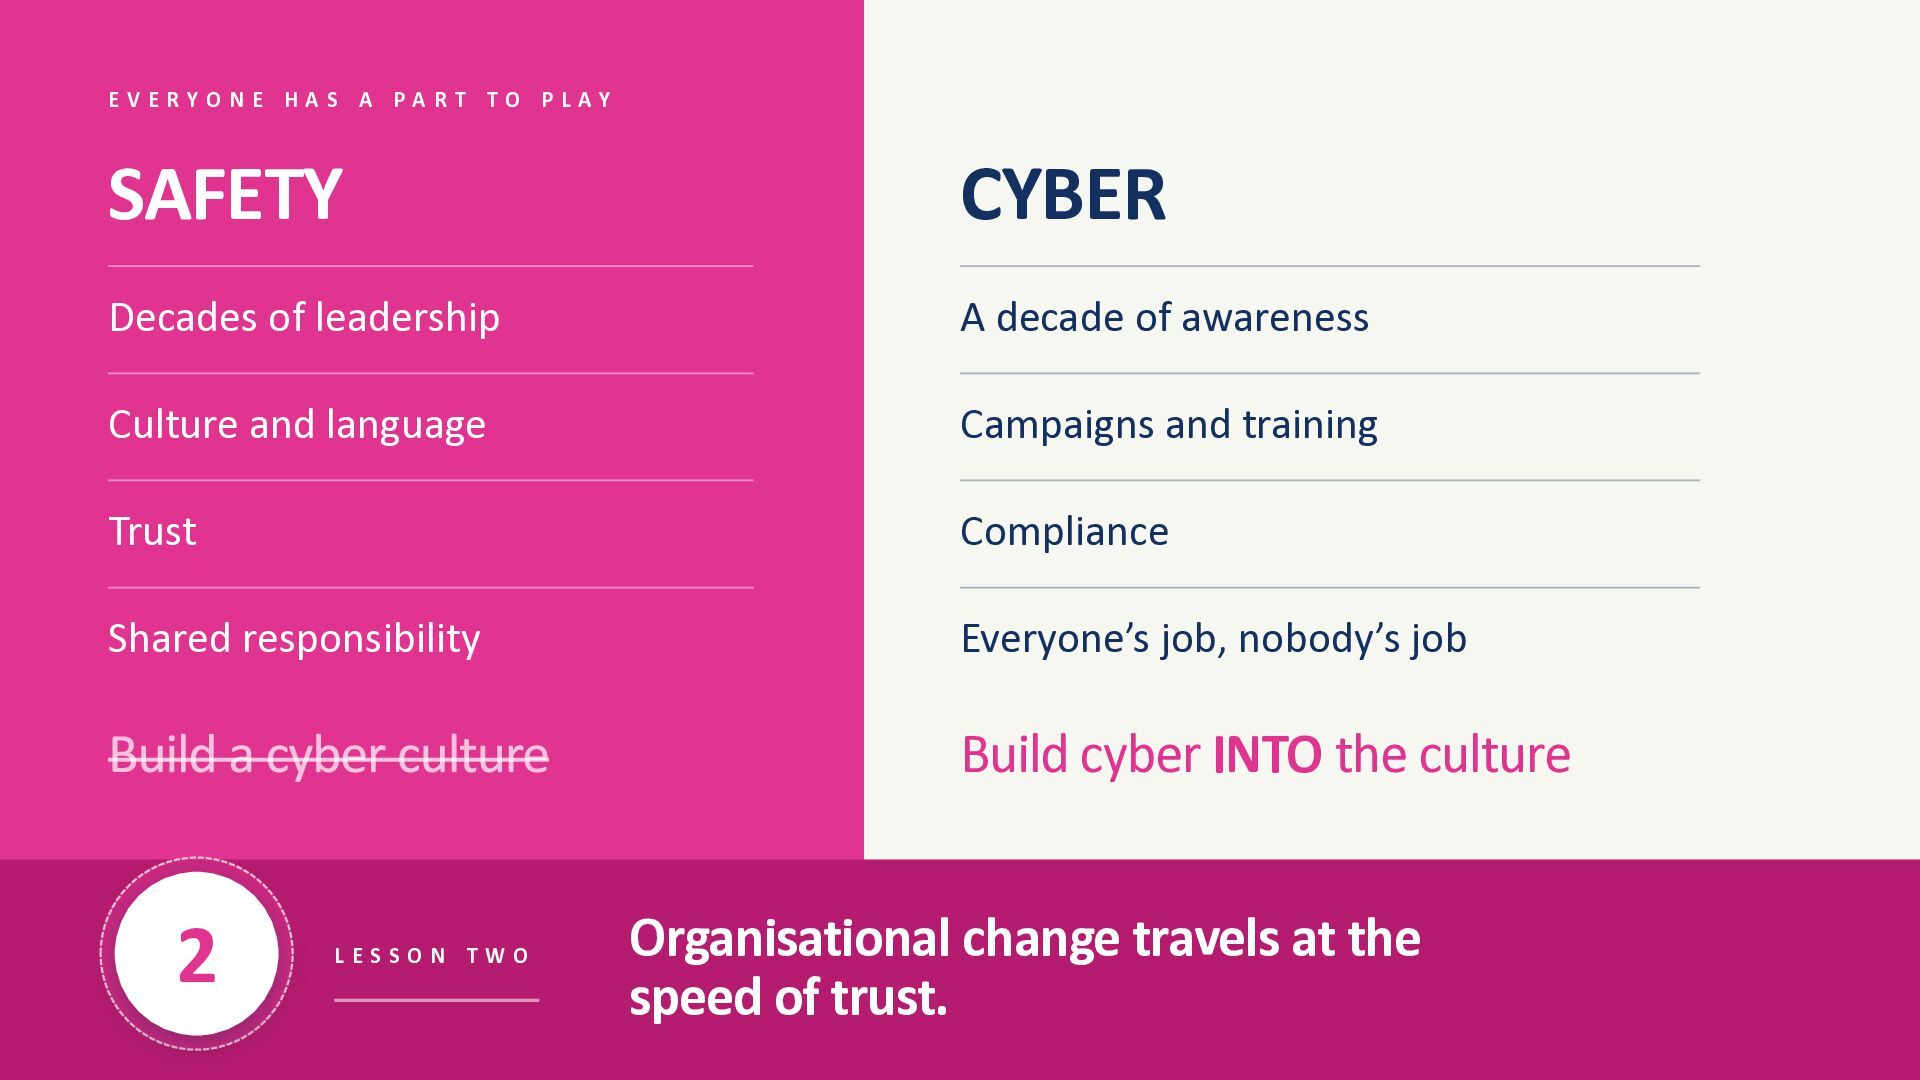
  93. EVERYONE HAS A PART TO PLAY SAFETY CYBER Decades of

    leadership A decade of awareness Culture and language Campaigns and training Trust Compliance Shared responsibility Everyone’s job, nobody’s job Build cyber INTO the culture 2 LESSON TWO Organisational change travels at the speed of trust.
  94. ADVENTURE THREE // THE VILLAGE It takes a village. Your

    org chart is not your influence map. 3
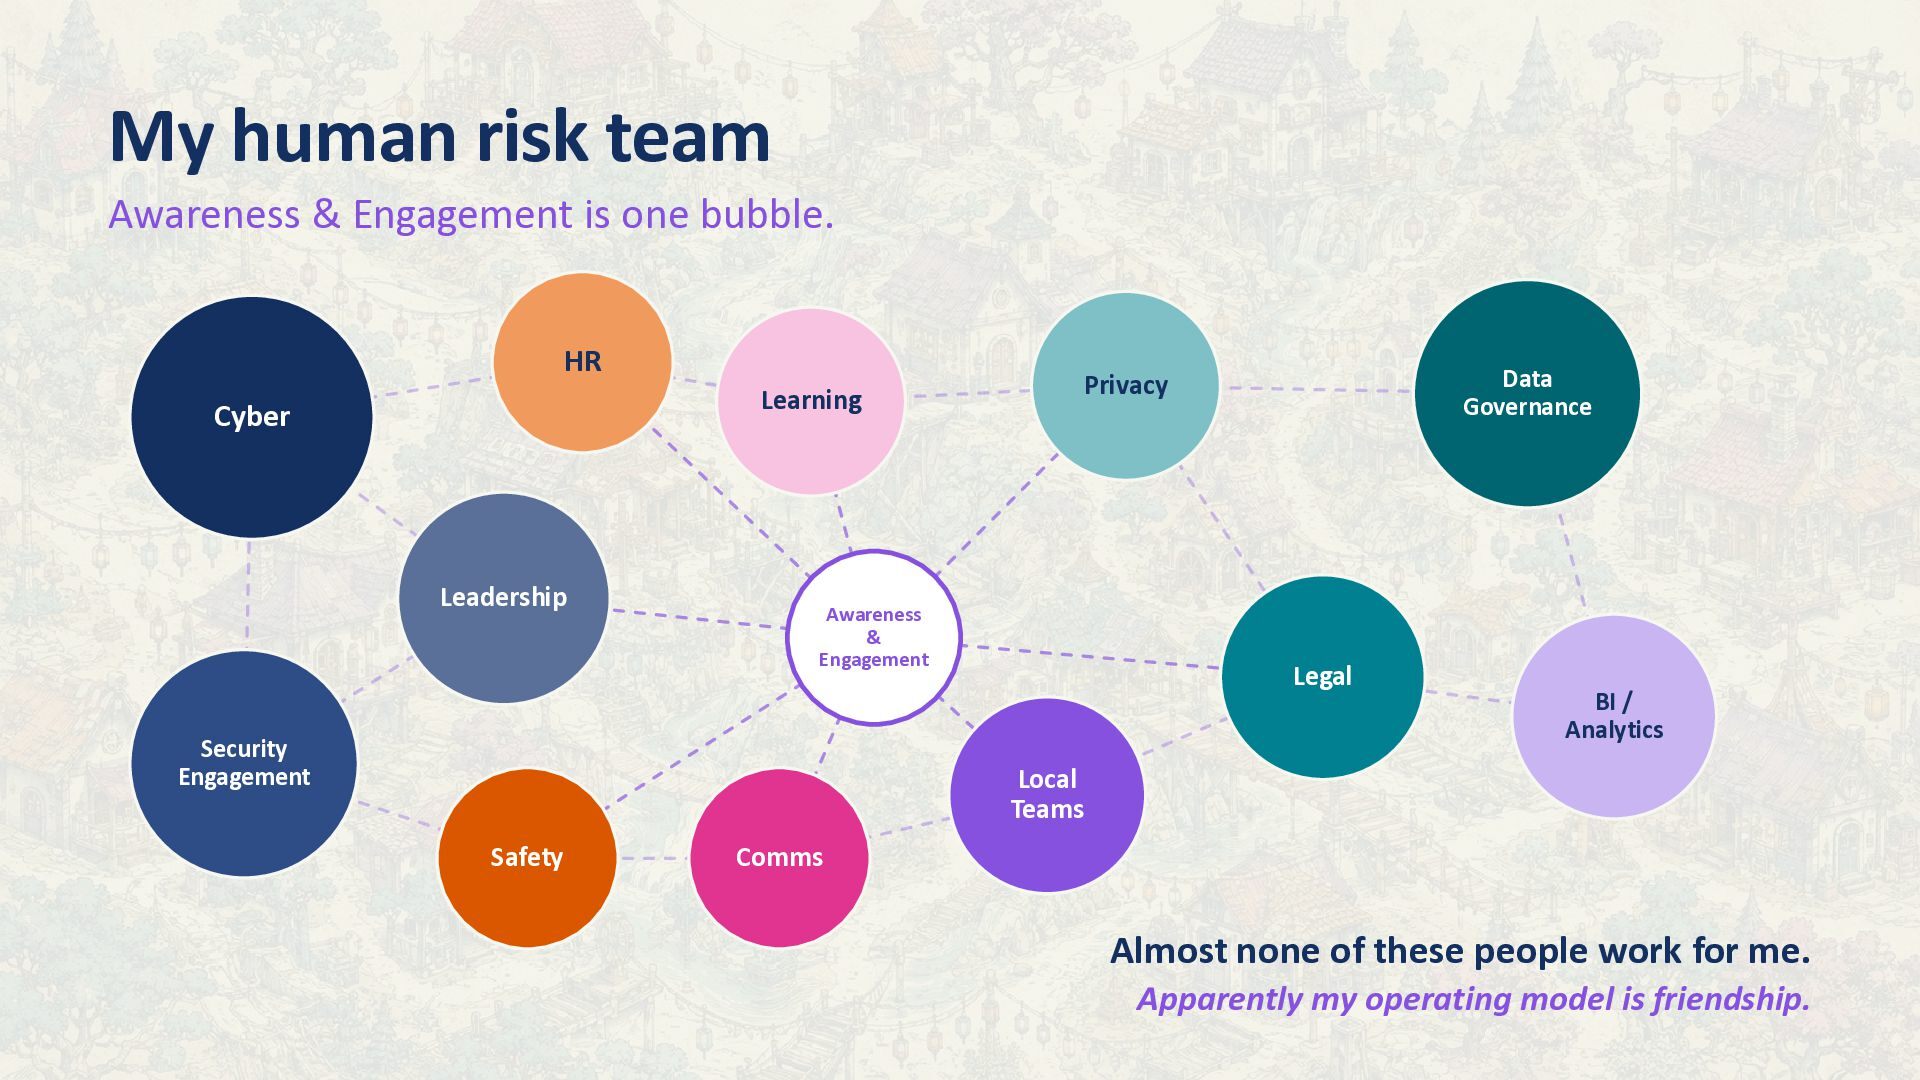
  95. My human risk team Awareness & Engagement is one bubble.

    HR Cyber Leadership Awareness & Engagement Security Engagement Data Governance Privacy Learning Legal BI / Analytics Local Teams Safety Comms Almost none of these people work for me. Apparently my operating model is friendship.
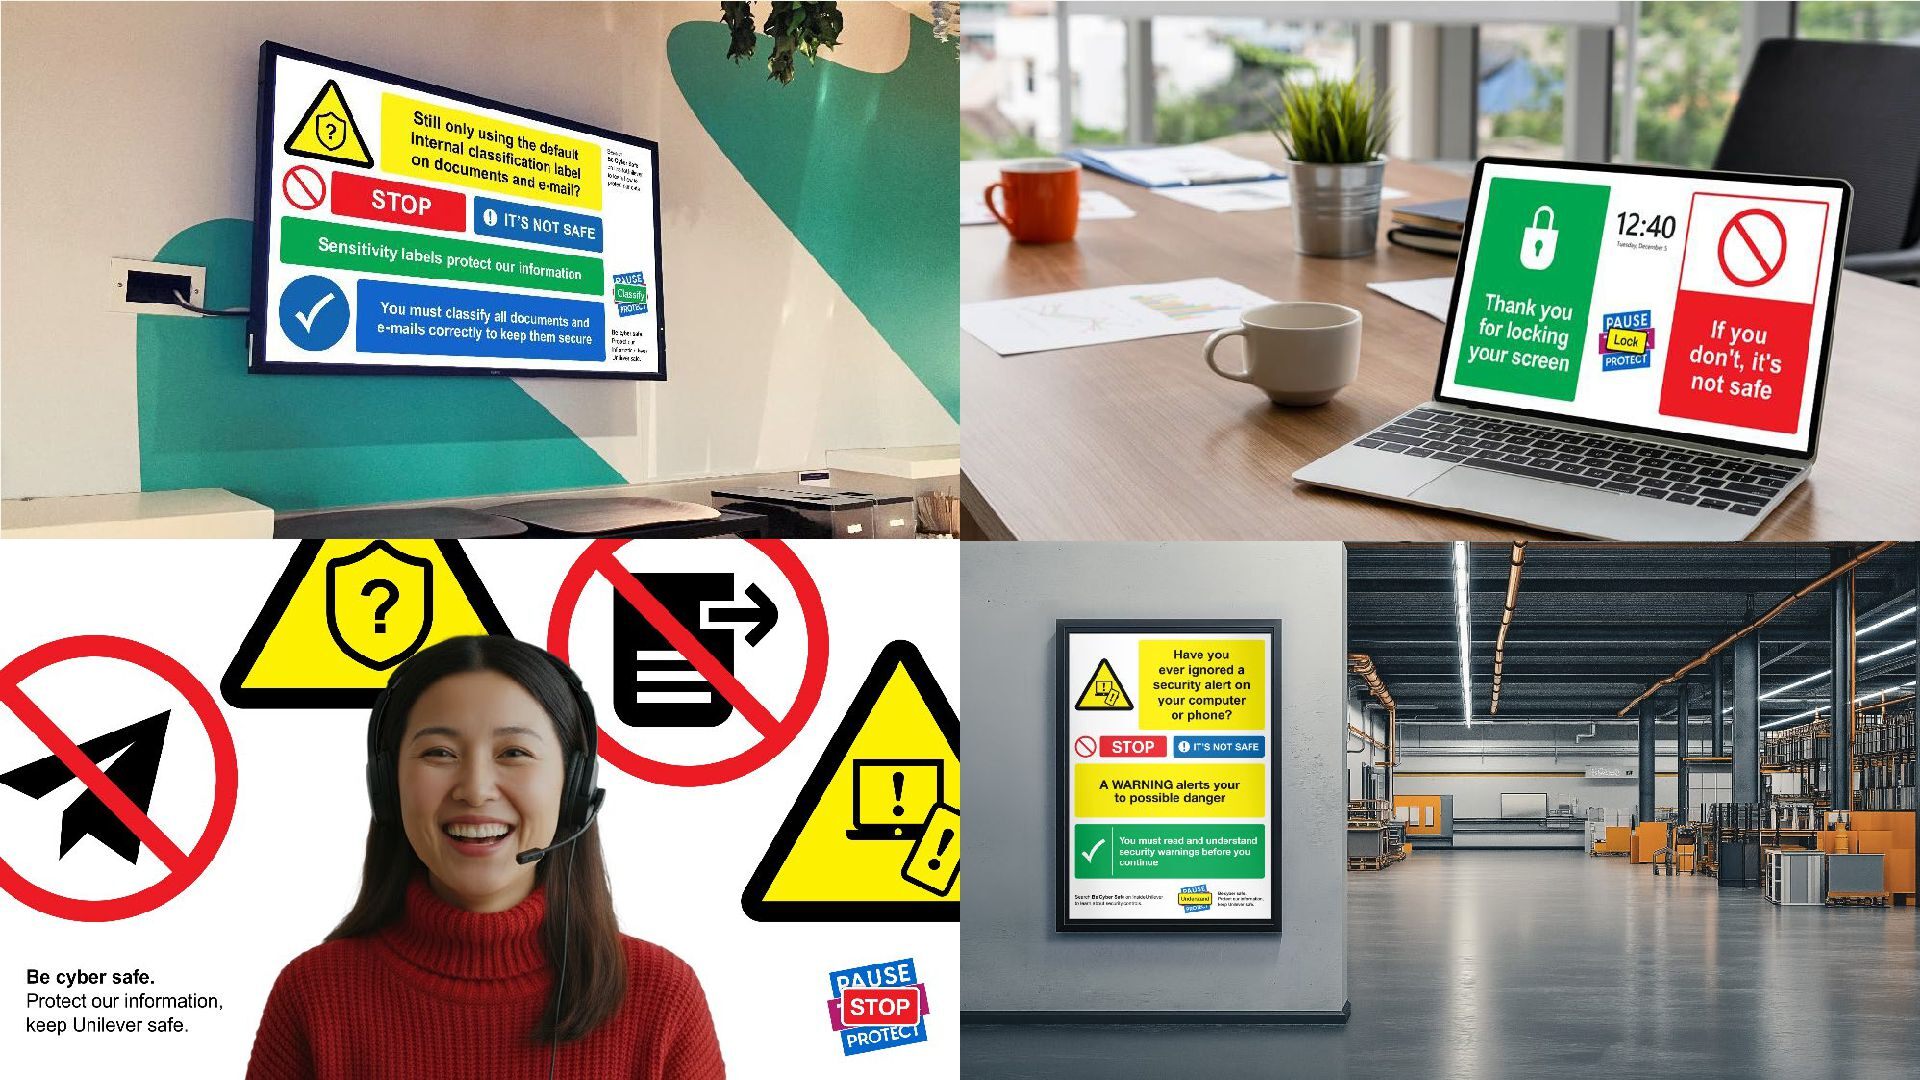
  96. ADVENTURE FOUR // RELEVANCE Not everybody is the same. Factory

    ONE TRAINING COURSE FOR ALL OF THEM? 4 Leadership
  97. That message isn’t for me. R E L E VA

    N C E EA R N S AT T E N T I O N
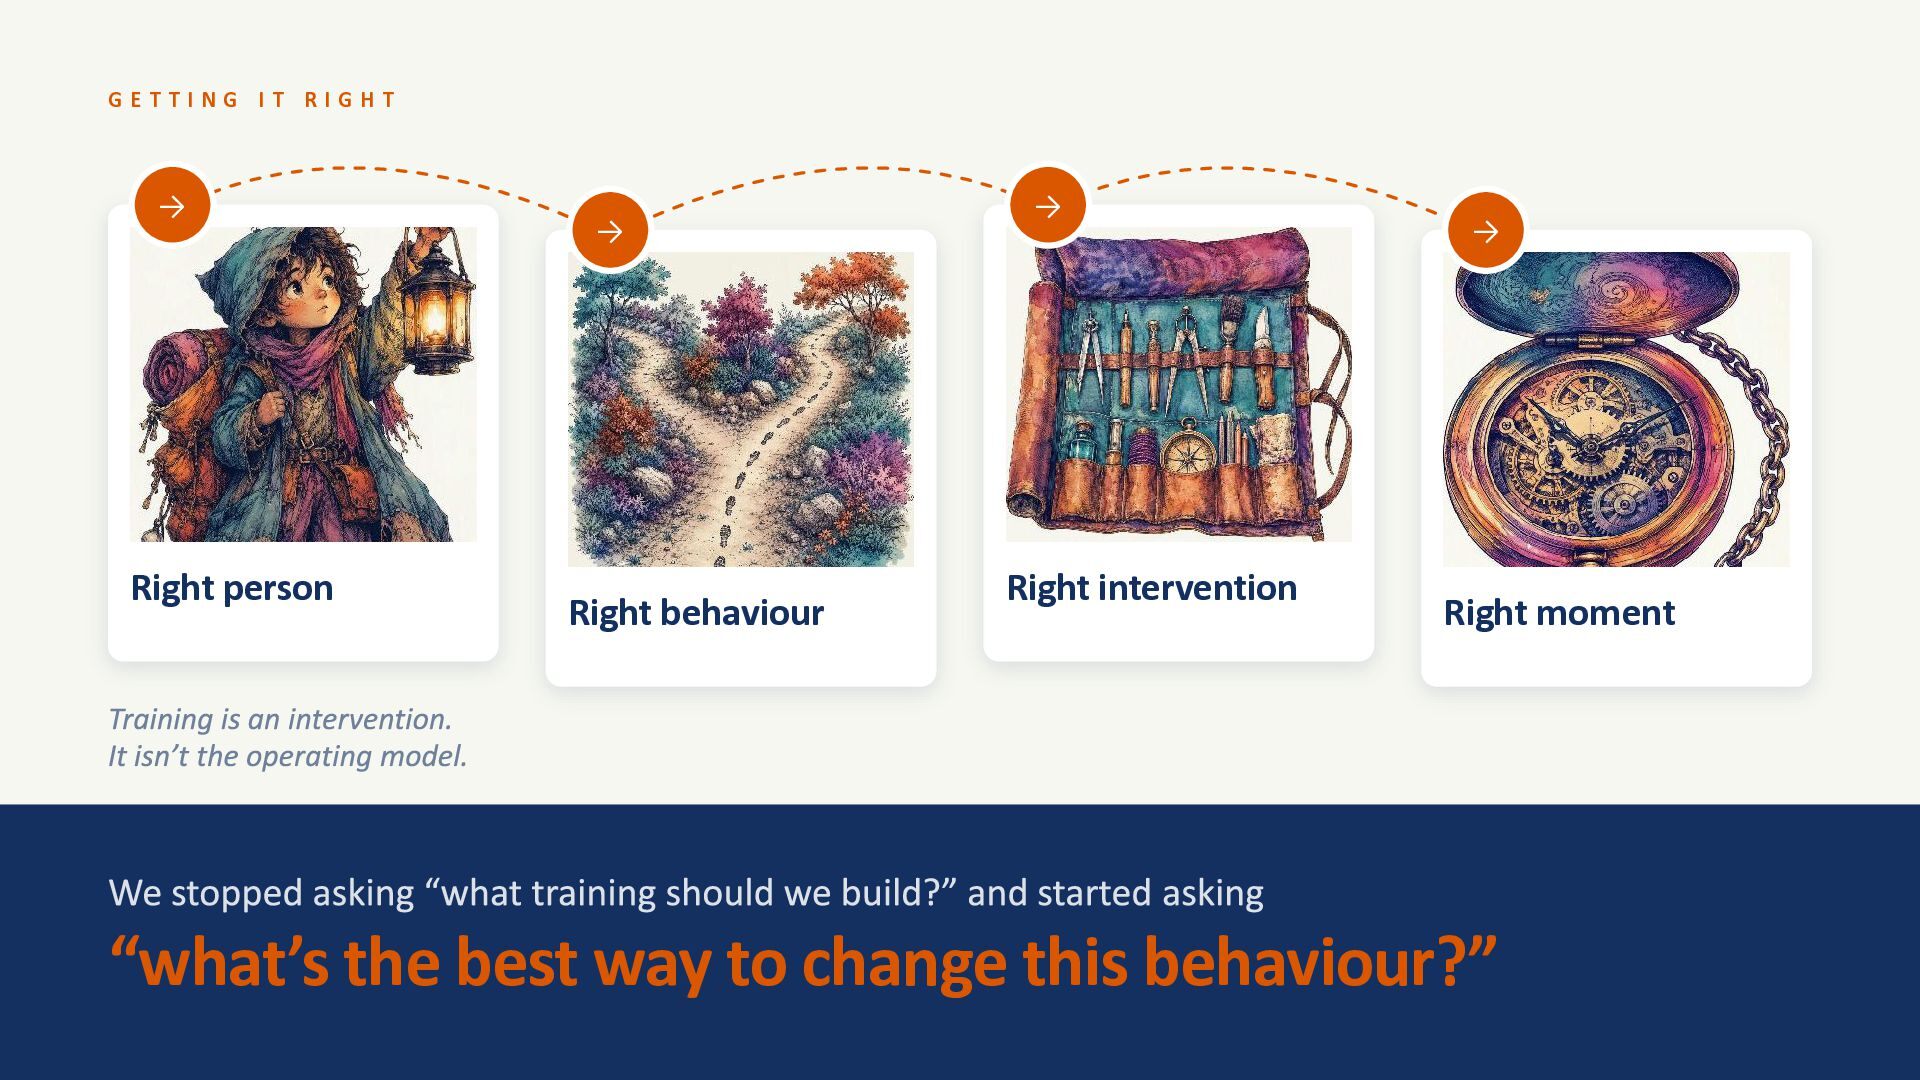
  98. GETTING IT RIGHT → Right person → Right behaviour →

    Right intervention → Right moment “what’s the best way to change this behaviour?”
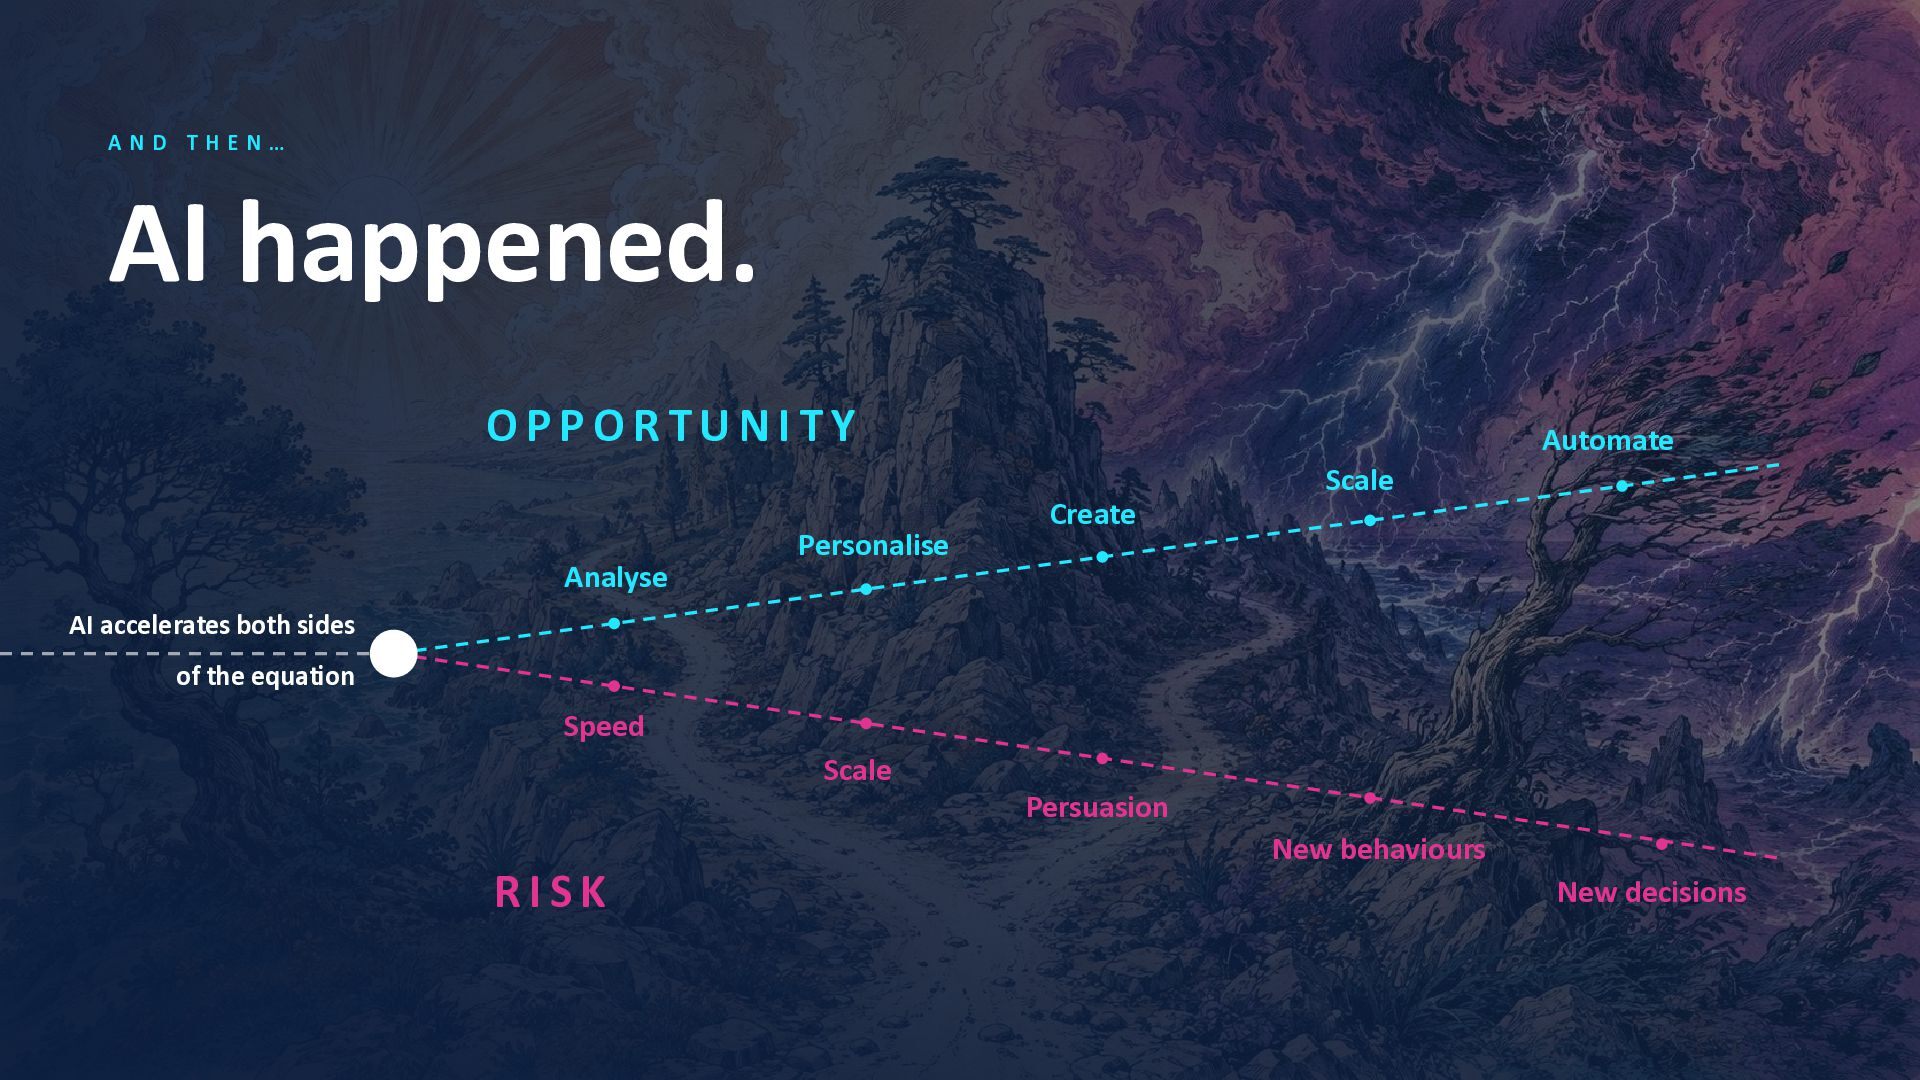
  99. AND THEN… AI happened. OPPORTUNITY Analyse Personalise Create Scale Automate

    AI accelerates both sides of the equation Speed RISK Scale Persuasion New behaviours New decisions
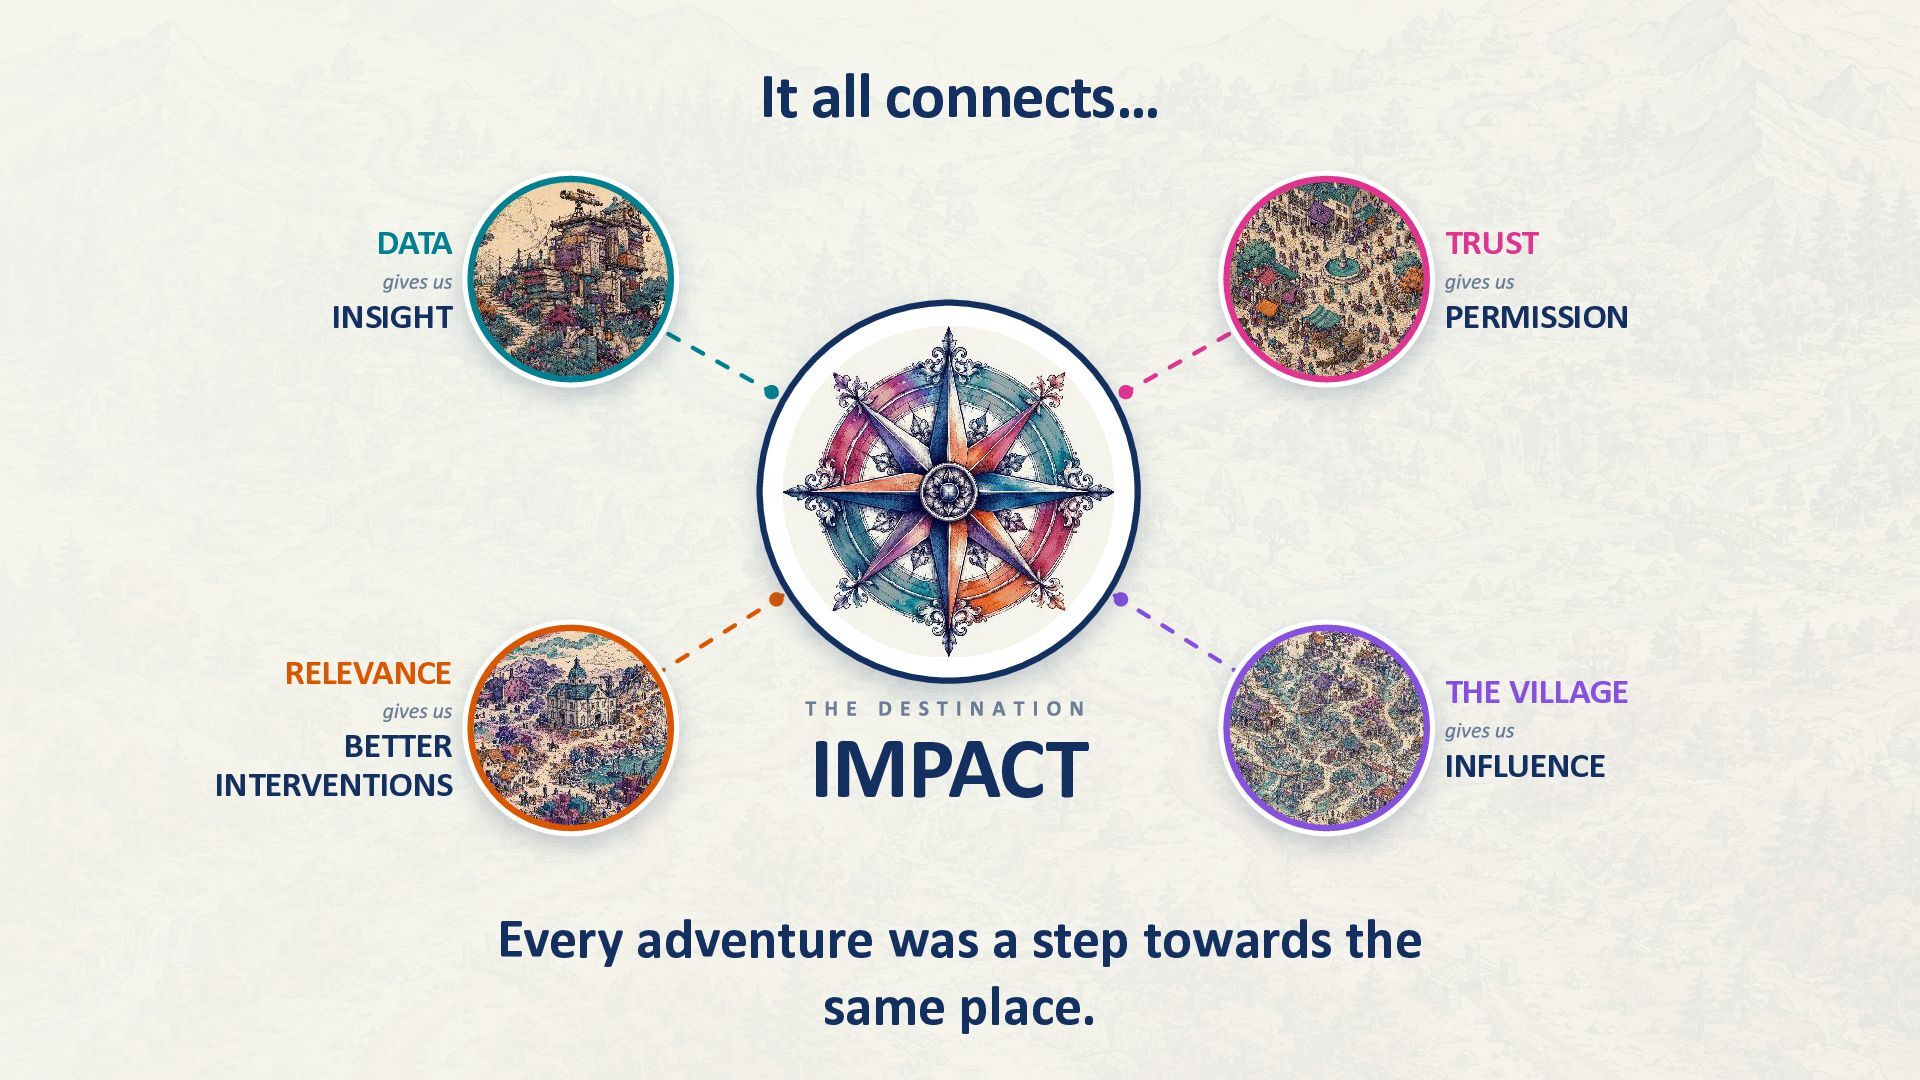
  100. It all connects… TRUST DATA INSIGHT PERMISSION RELEVANCE BETTER INTERVENTIONS

    IMPACT Every adventure was a step towards the same place. THE VILLAGE INFLUENCE
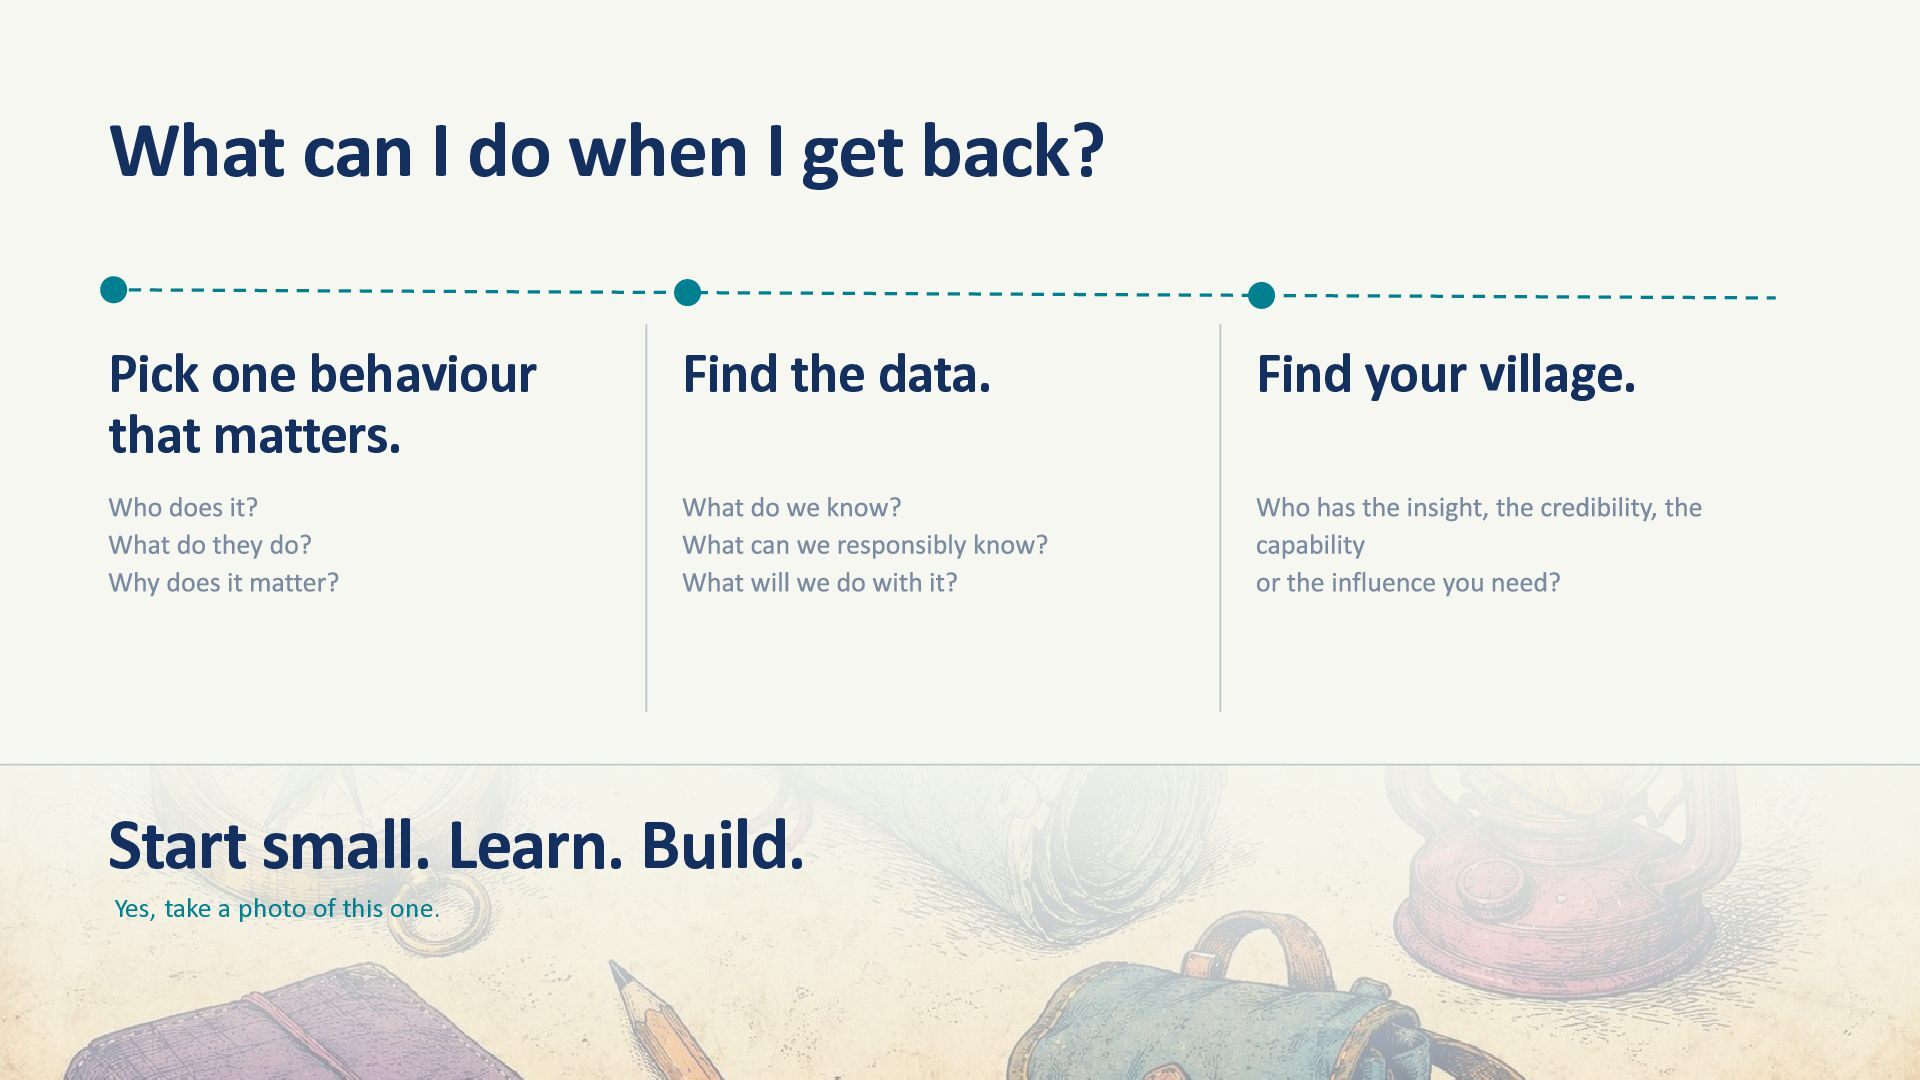
  101. What can I do when I get back? Pick one

    behaviour that matters. Find the data. Start small. Learn. Build. Yes, take a photo of this one. Find your village.
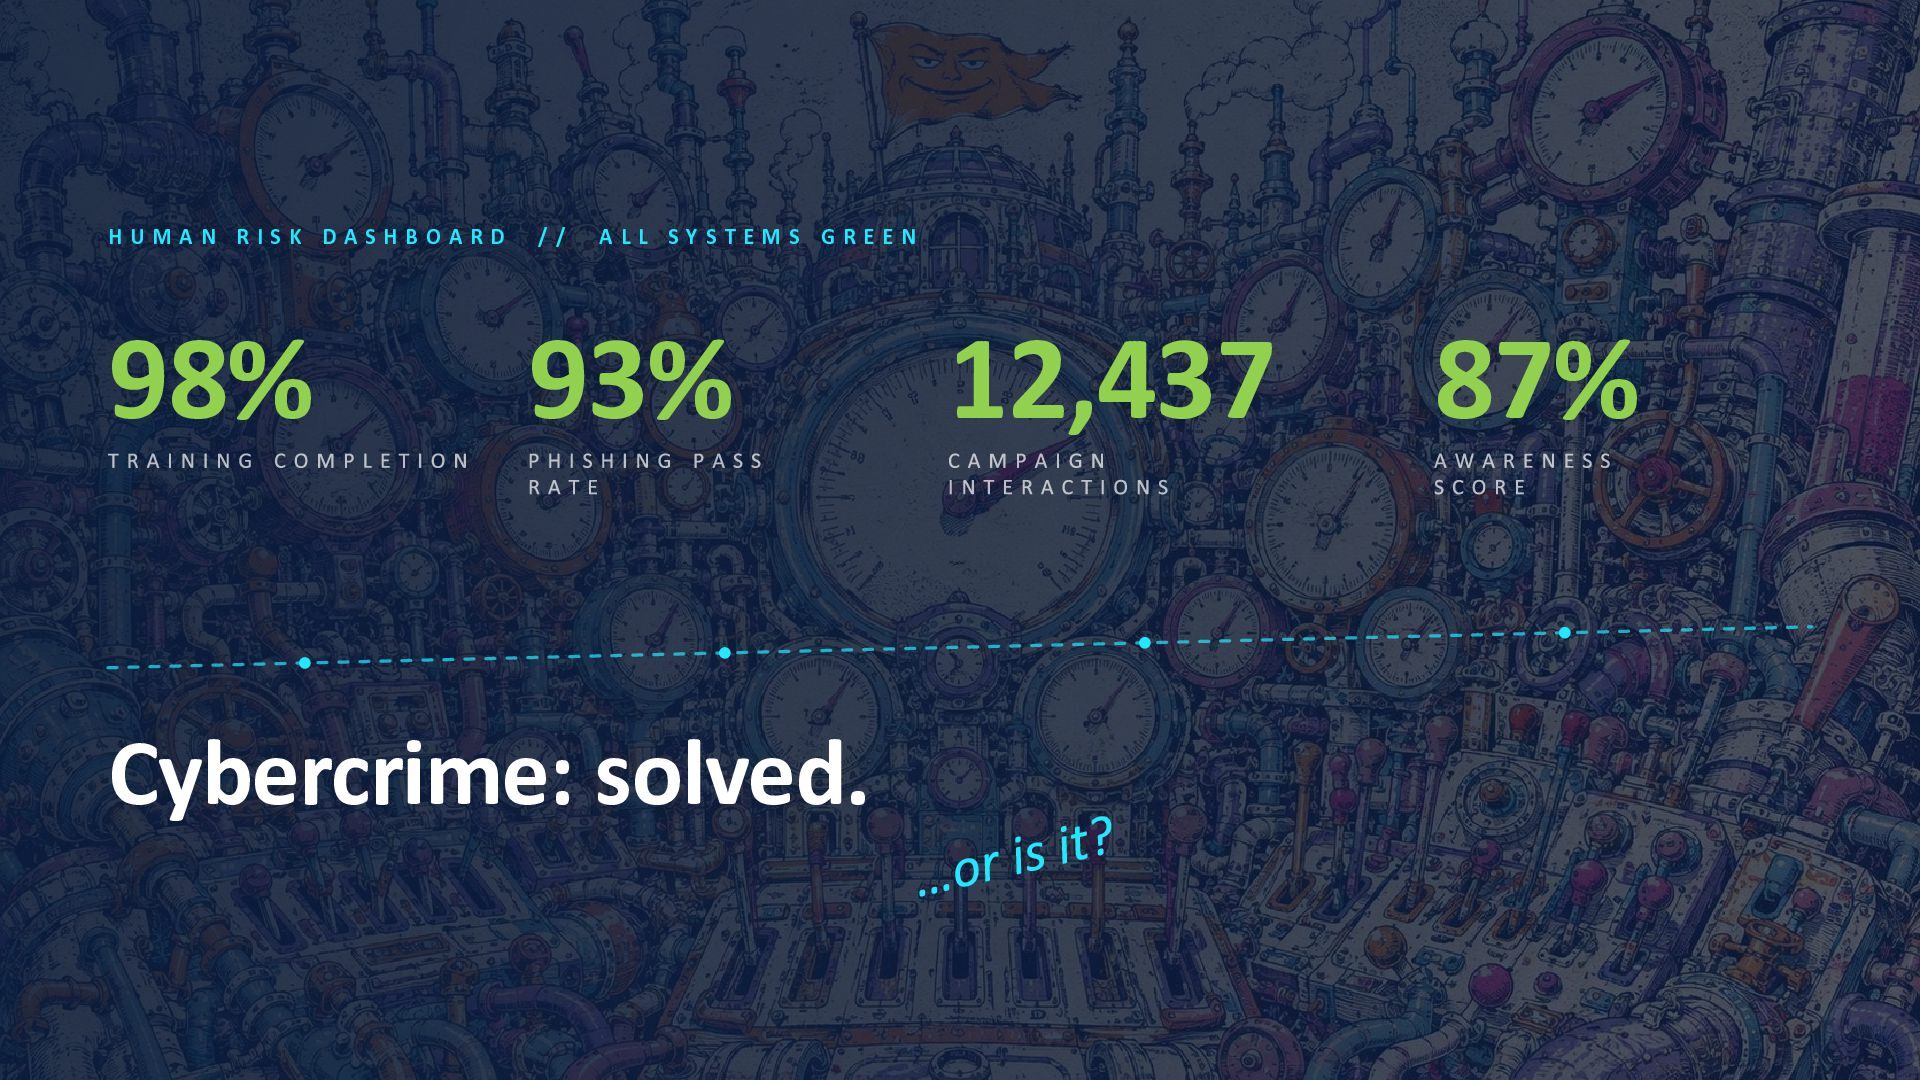
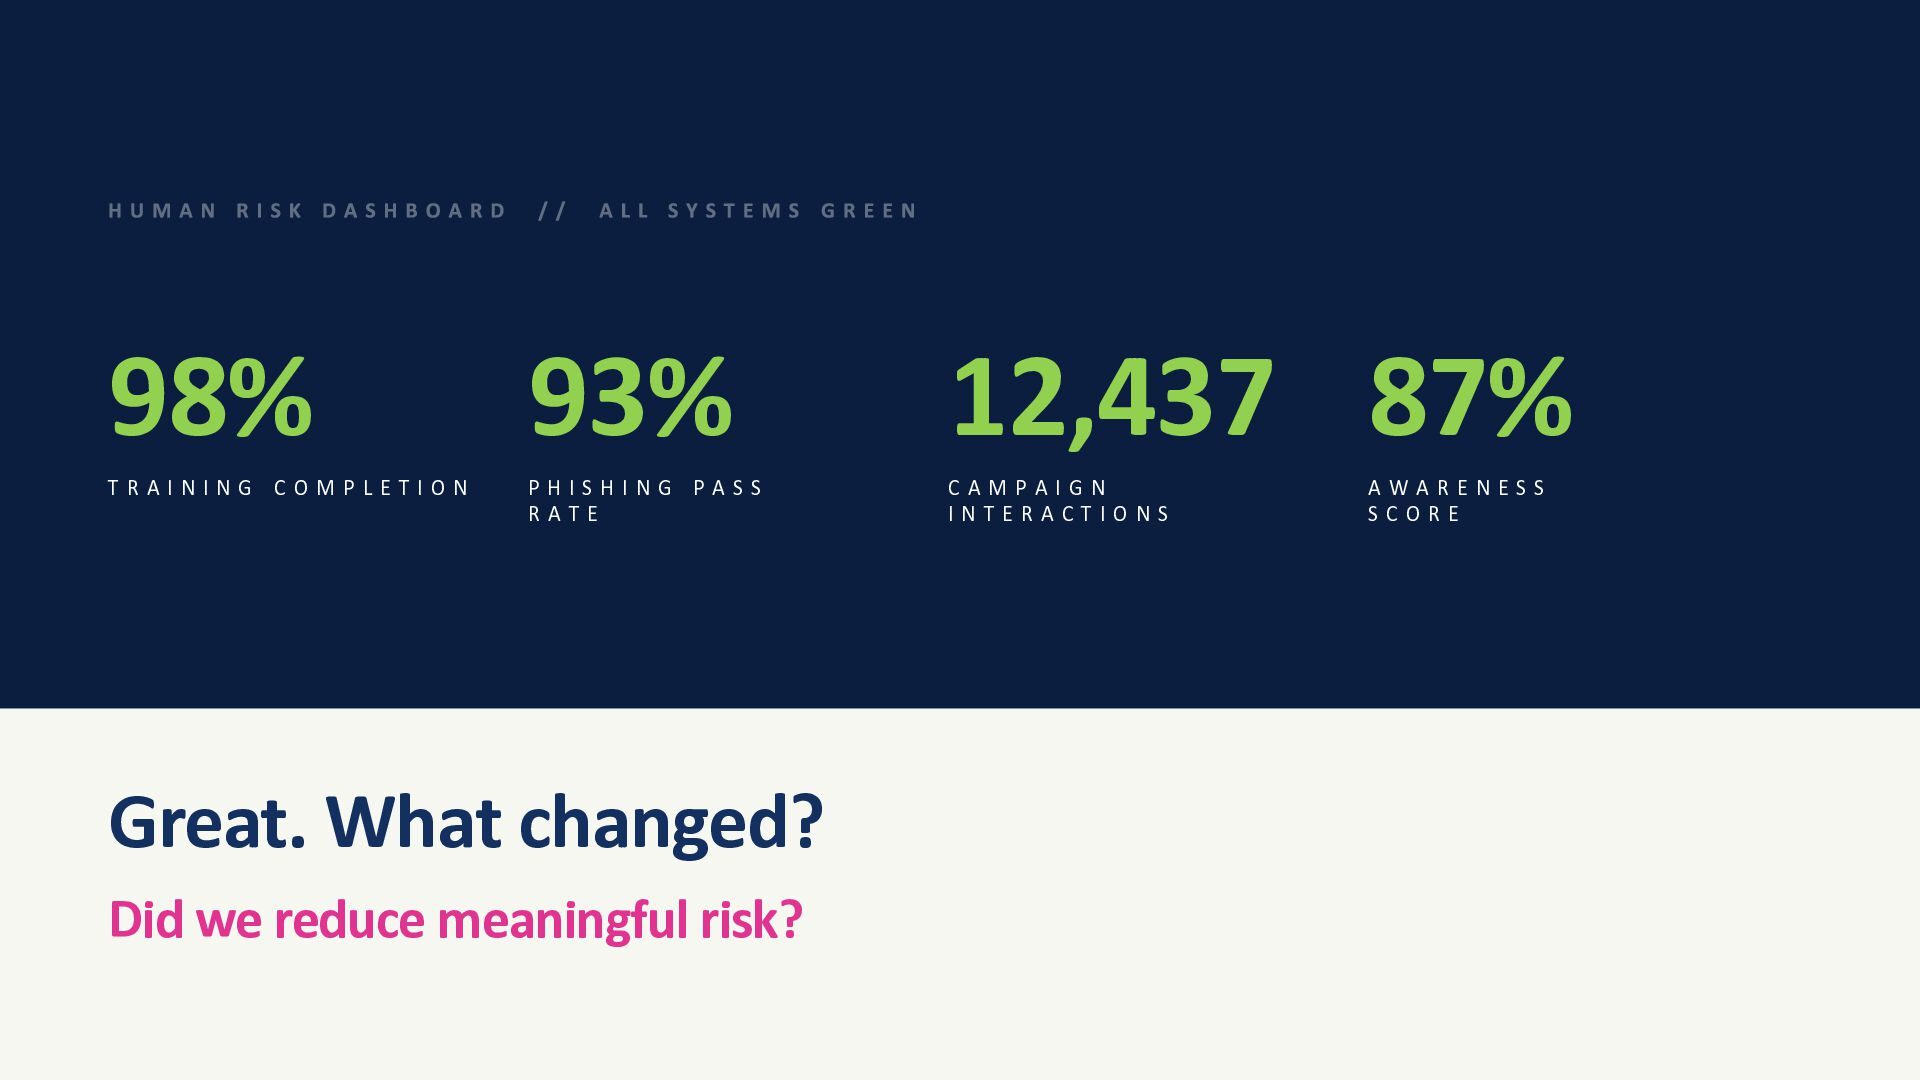
  102. 98% TRAINING COMPLETION 93% PHISHING PASS RATE Great. What changed?

    Did we reduce meaningful risk? 12,437 87% CAMPAIGN INTERACTIONS AWARENESS SCORE
  103. #CymruSec Stephen Crowther Technology & Analytics Director SMF Luke Pulvirenti

    AI Coordinator TARIAN REGIONAL ORGANISED CRIME UNIT Patricia Rodrigues Senior Cloud Security Engineer ADMIRAL GROUP Ryan James CISO MERTHYR TYDFIL COUNTY BOROUGH COUNCIL Charlie Sinclair Cyber Culture & Human Risk Senior Manager UNILEVER
  104. #CymruSec Upcoming – First Breakout 11:35 Breakout A: How to

    Keep Up with the Pace of Change: Panel Discussion Breakout B : Think Like an Investigator, Before You Need One Ricoh Suite 11:35 This Room 11:35
  105. DIGITAL FORENSICS & INCIDENT RESPONSE Think Like an Investigator, Before

    You Need One Emerging technology, digital evidence and evidence-led incident response Beth Jenkins · CymruSec
  106. Four topics for the next 30 minutes Emerging tech through

    a forensic lens Where is the evidence? AI, vehicles and IoT as sources of evidence What can actually be recovered, and why it matters Every investigation is an opportunity Prepare for the next incident Turning findings into security gaps and attacker insight Evidence-led incident response playbooks 2
  107. Evidence has left the hard drive THEN NOW A laptop,

    a server, a disk image. One owner, one location, long retention. Cloud services, mobile apps, connected cars, IoT devices, AI chatbots and logs between them all. Emerging technology is not just changing cyber security. It is changing digital evidence. 3
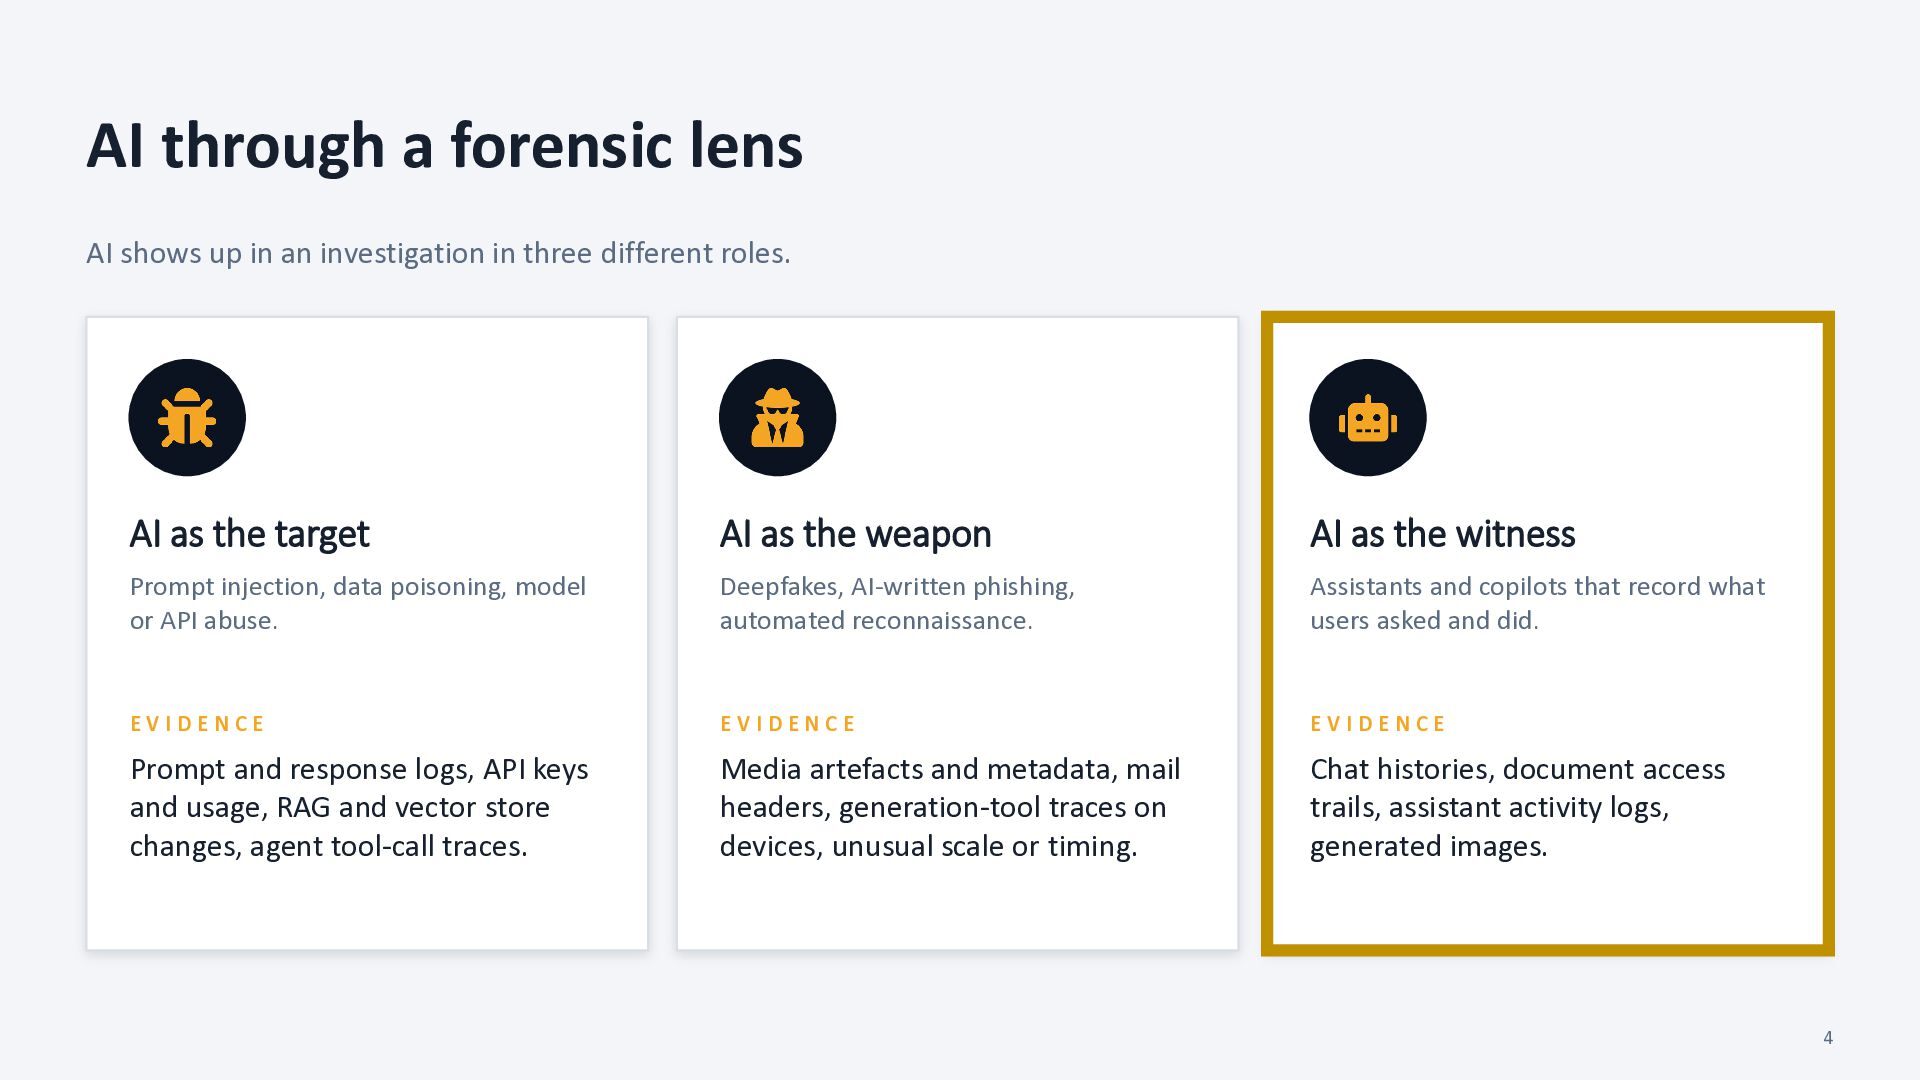
  108. AI through a forensic lens AI shows up in an

    investigation in three different roles. AI as the target AI as the weapon AI as the witness Prompt injection, data poisoning, model or API abuse. Deepfakes, AI-written phishing, automated reconnaissance. Assistants and copilots that record what users asked and did. EVIDENCE EVIDENCE EVIDENCE Prompt and response logs, API keys and usage, RAG and vector store changes, agent tool-call traces. Media artefacts and metadata, mail headers, generation-tool traces on devices, unusual scale or timing. Chat histories, document access trails, assistant activity logs, generated images. 4
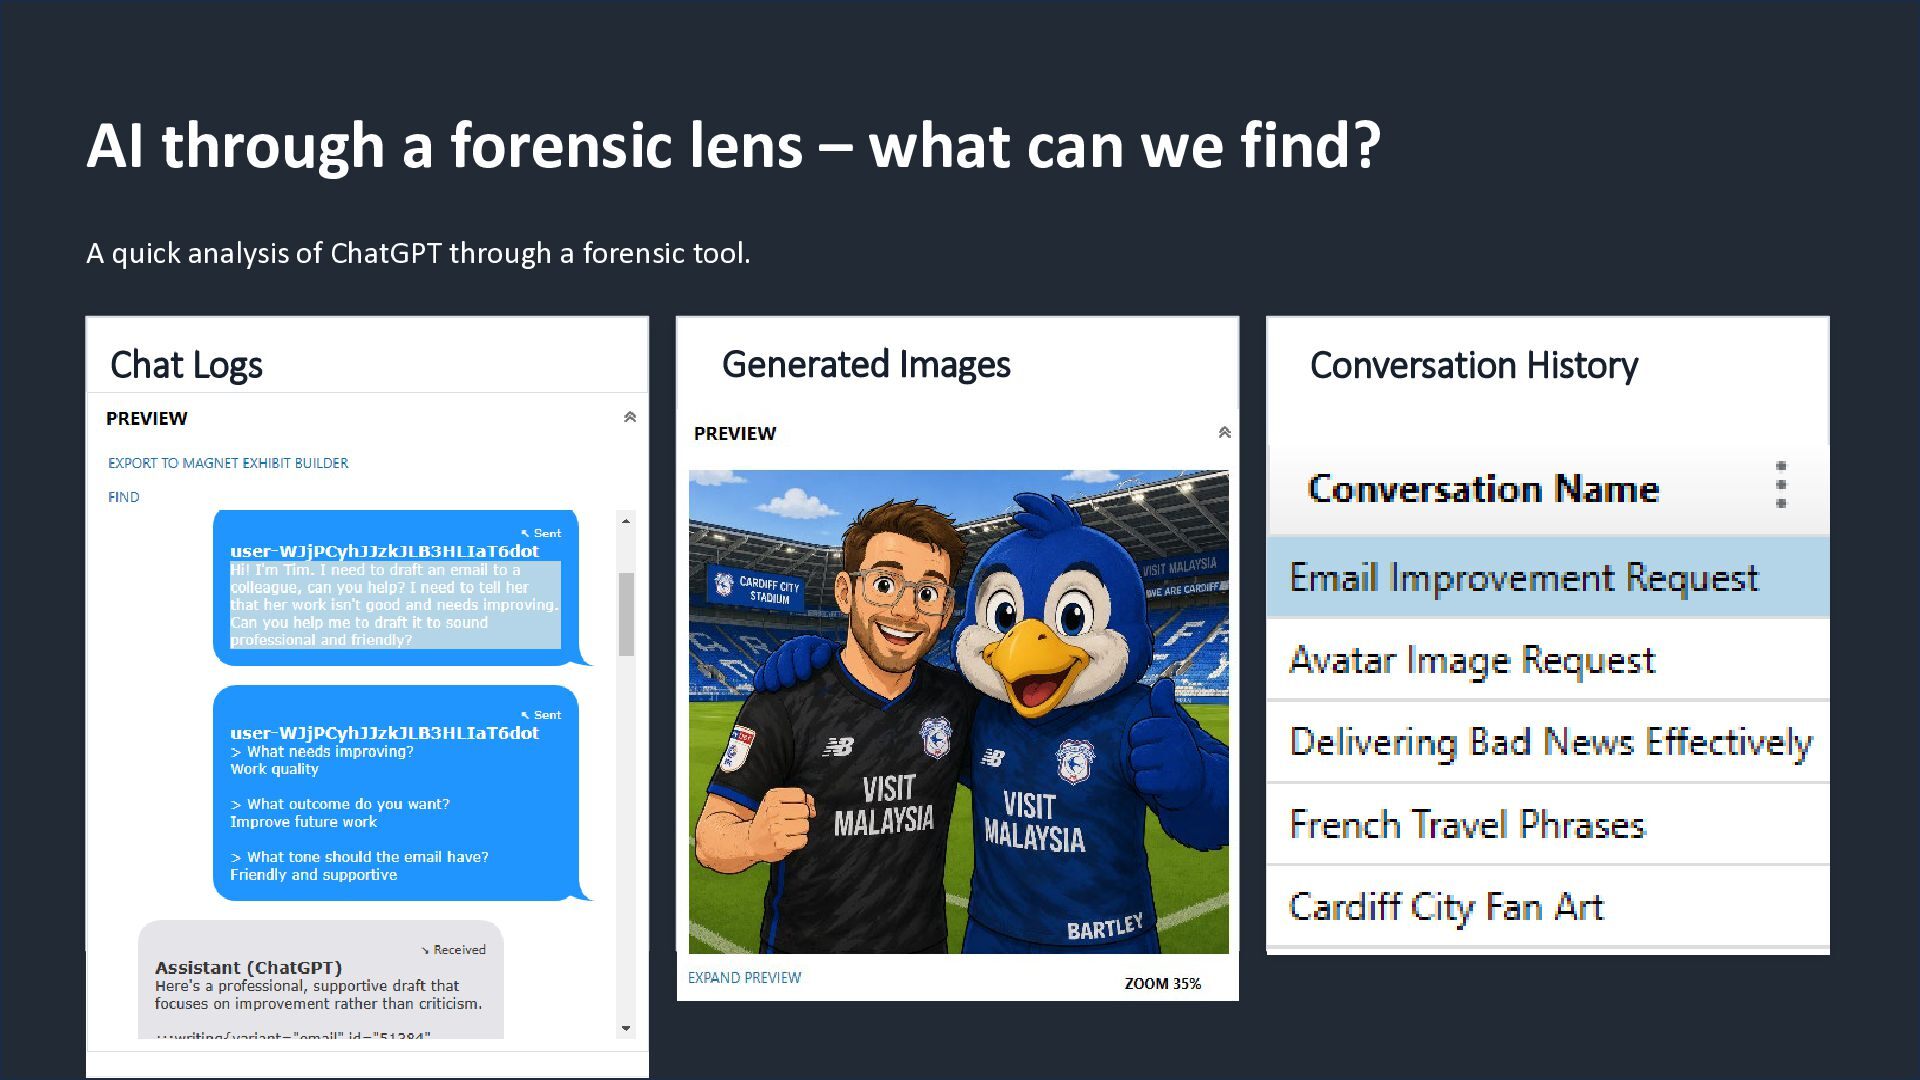
  109. AI through a forensic lens – what can we find?

    A quick analysis of ChatGPT through a forensic tool. Generated Images Conversation History EVIDENCE EVIDENCE EVIDENCE ABC ABC ABC Chat Logs
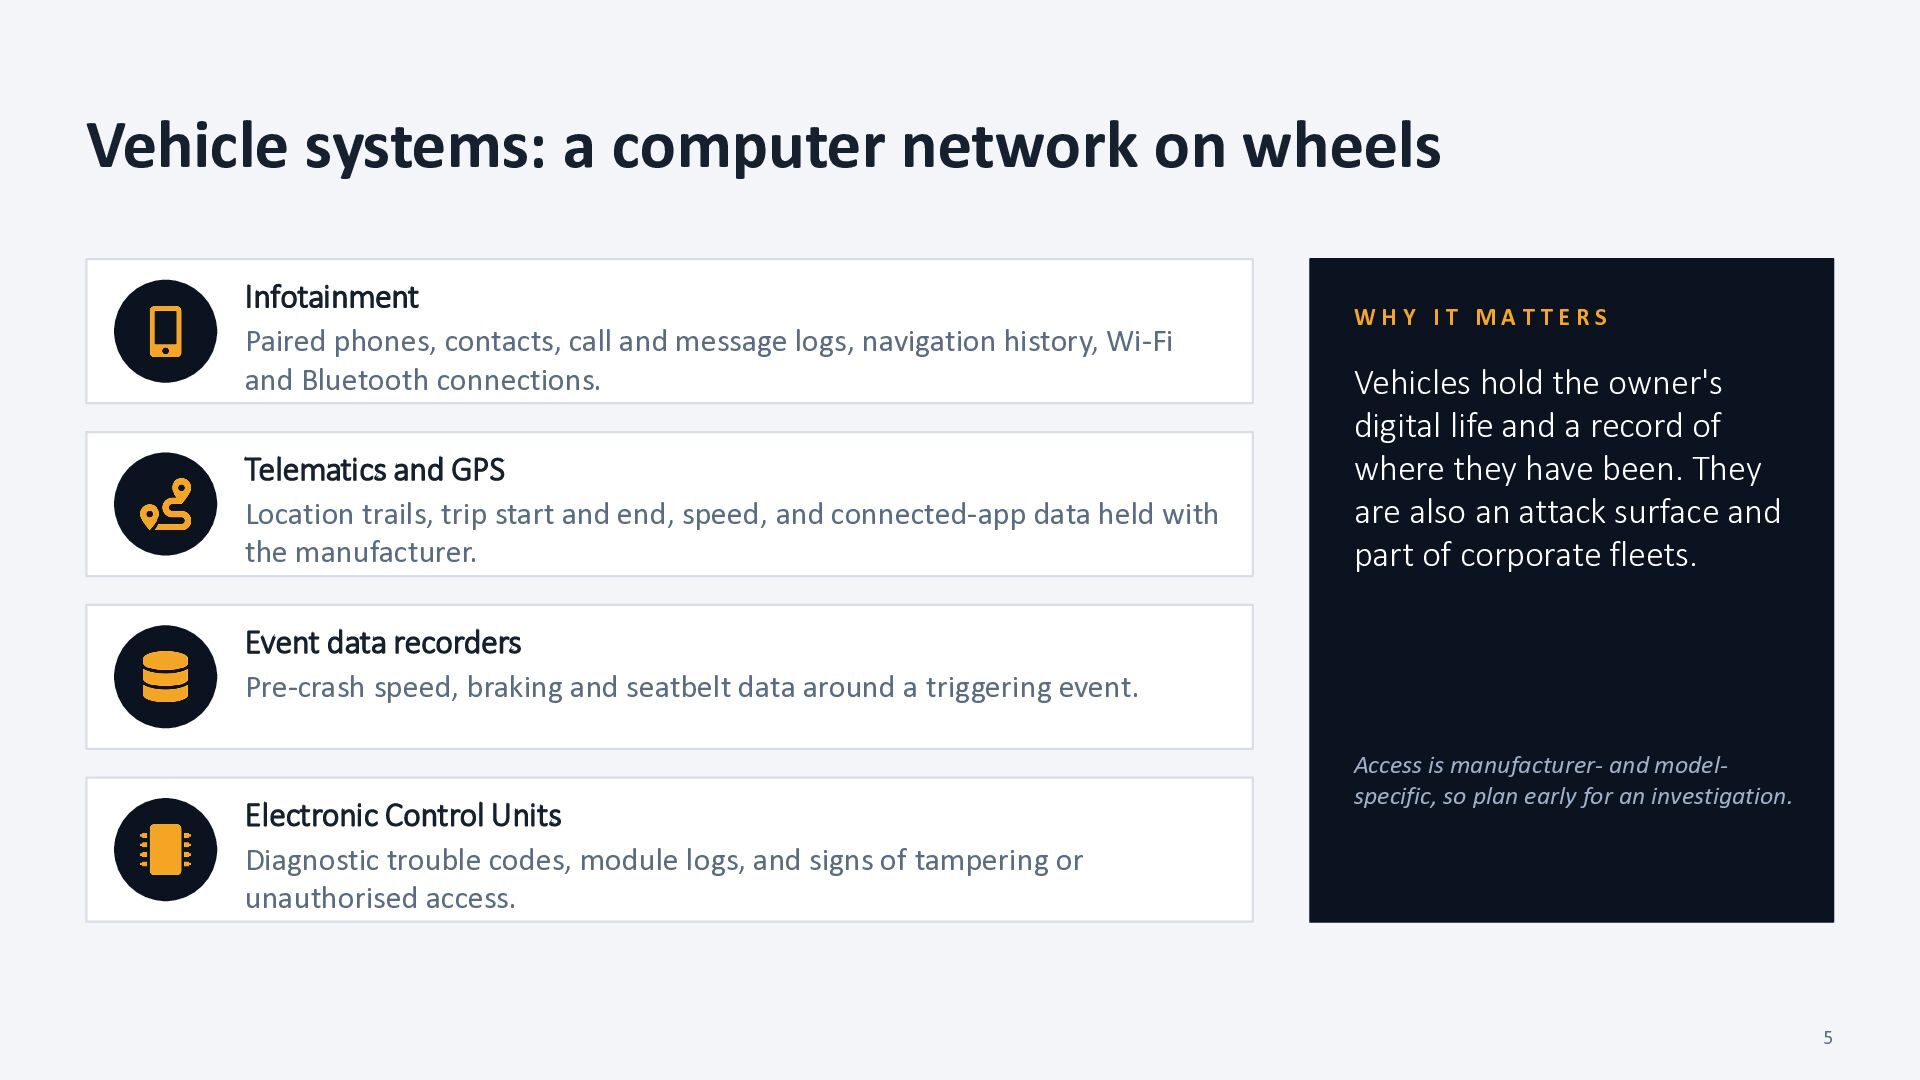
  110. Vehicle systems: a computer network on wheels Infotainment Paired phones,

    contacts, call and message logs, navigation history, Wi-Fi and Bluetooth connections. Telematics and GPS Location trails, trip start and end, speed, and connected-app data held with the manufacturer. WHY IT MATTERS Vehicles hold the owner's digital life and a record of where they have been. They are also an attack surface and part of corporate fleets. Event data recorders Pre-crash speed, braking and seatbelt data around a triggering event. Electronic Control Units Access is manufacturer- and modelspecific, so plan early for an investigation. Diagnostic trouble codes, module logs, and signs of tampering or unauthorised access. 5
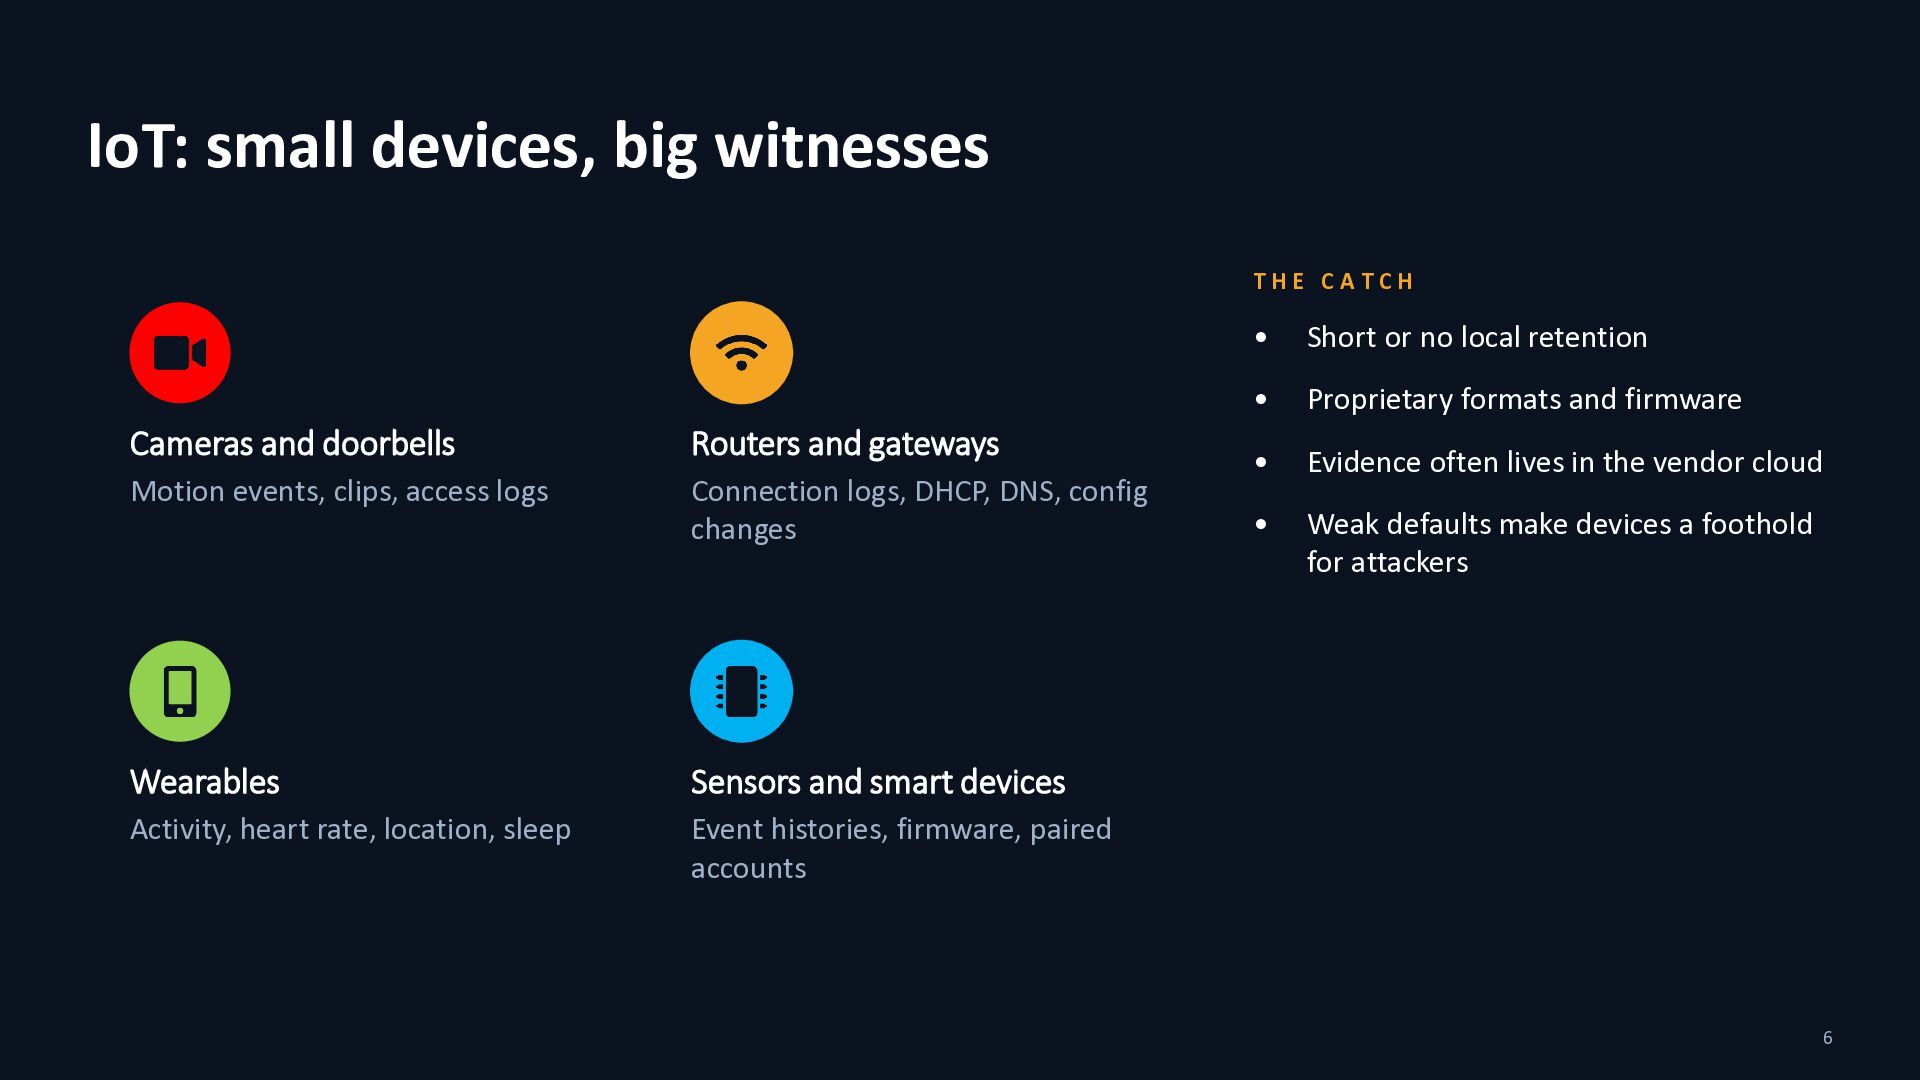
  111. IoT: small devices, big witnesses THE CATCH Cameras and doorbells

    Routers and gateways Motion events, clips, access logs Connection logs, DHCP, DNS, config changes Wearables Sensors and smart devices Activity, heart rate, location, sleep Event histories, firmware, paired accounts • Short or no local retention • Proprietary formats and firmware • Evidence often lives in the vendor cloud • Weak defaults make devices a foothold for attackers 6
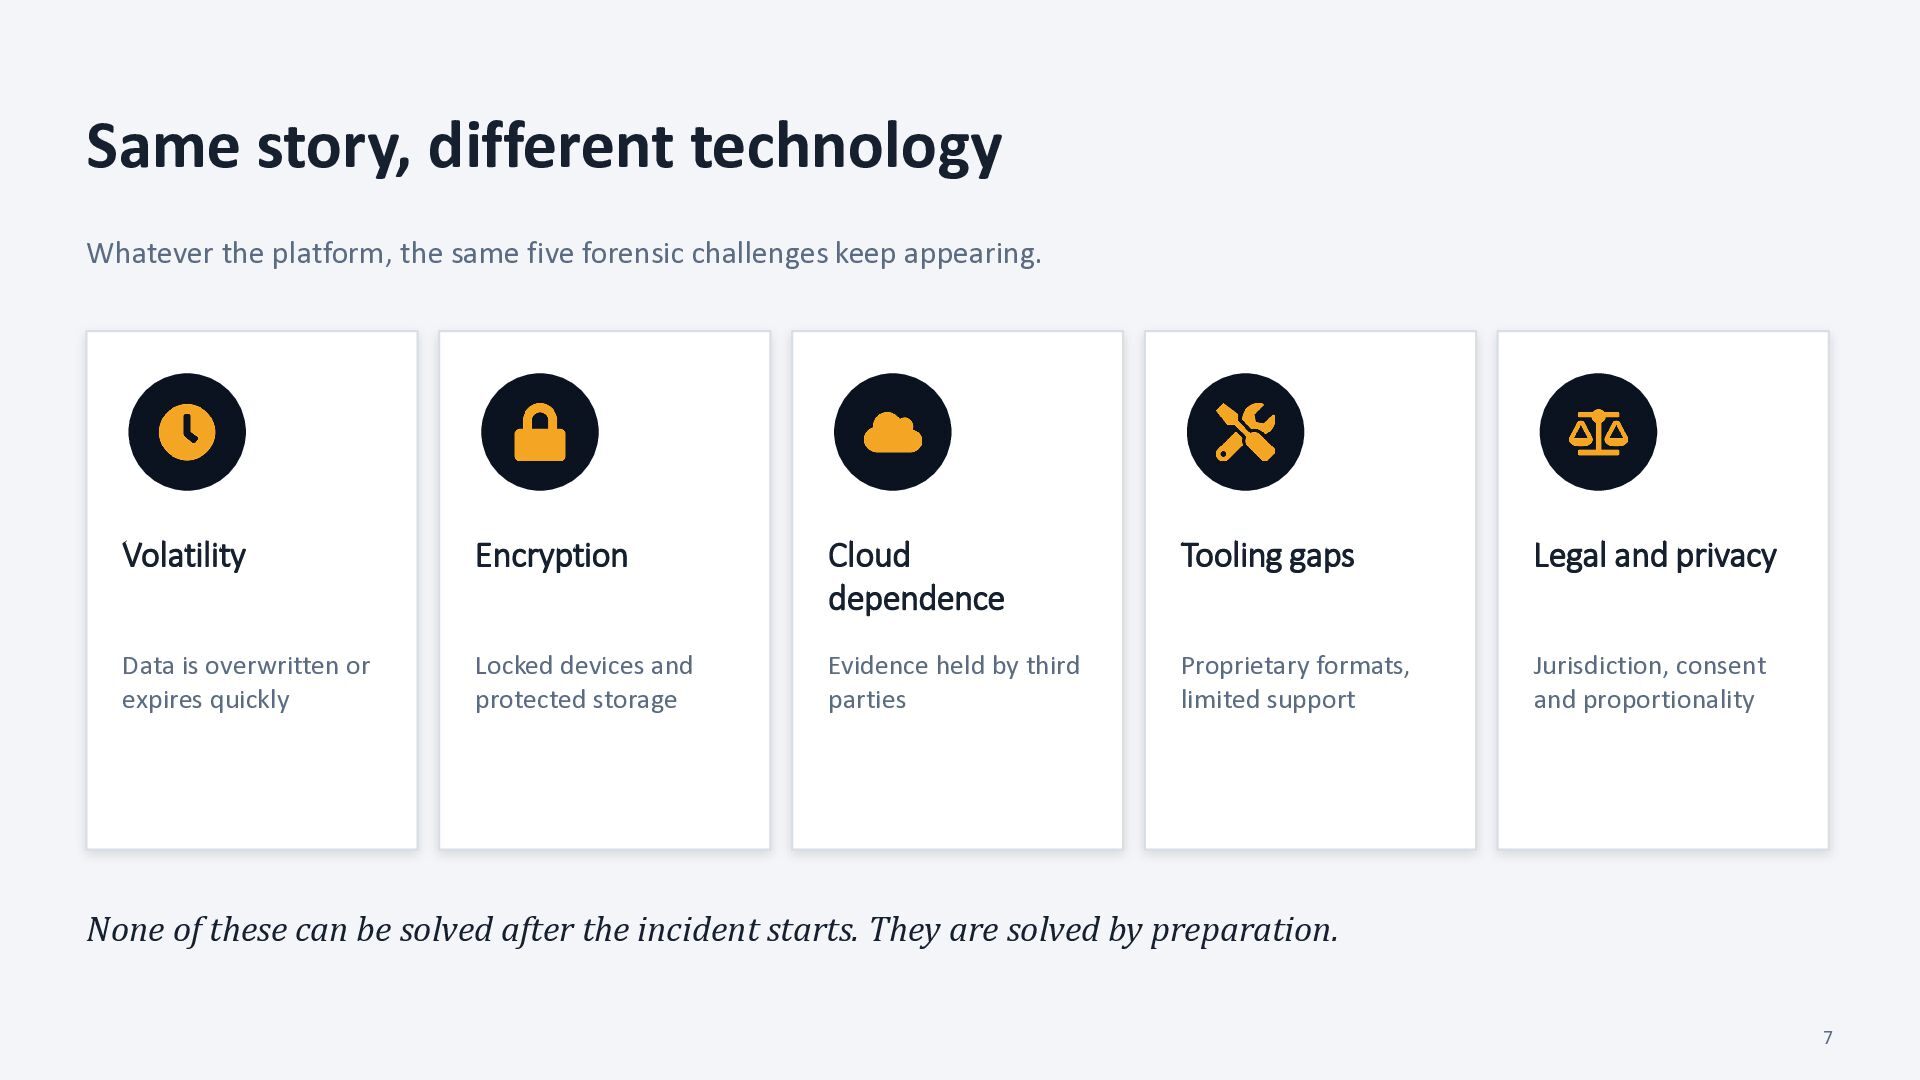
  112. Same story, different technology Whatever the platform, the same five

    forensic challenges keep appearing. Volatility Encryption Cloud dependence Tooling gaps Legal and privacy Data is overwritten or expires quickly Locked devices and protected storage Evidence held by third parties Proprietary formats, limited support Jurisdiction, consent and proportionality None of these can be solved after the incident starts. They are solved by preparation. 7
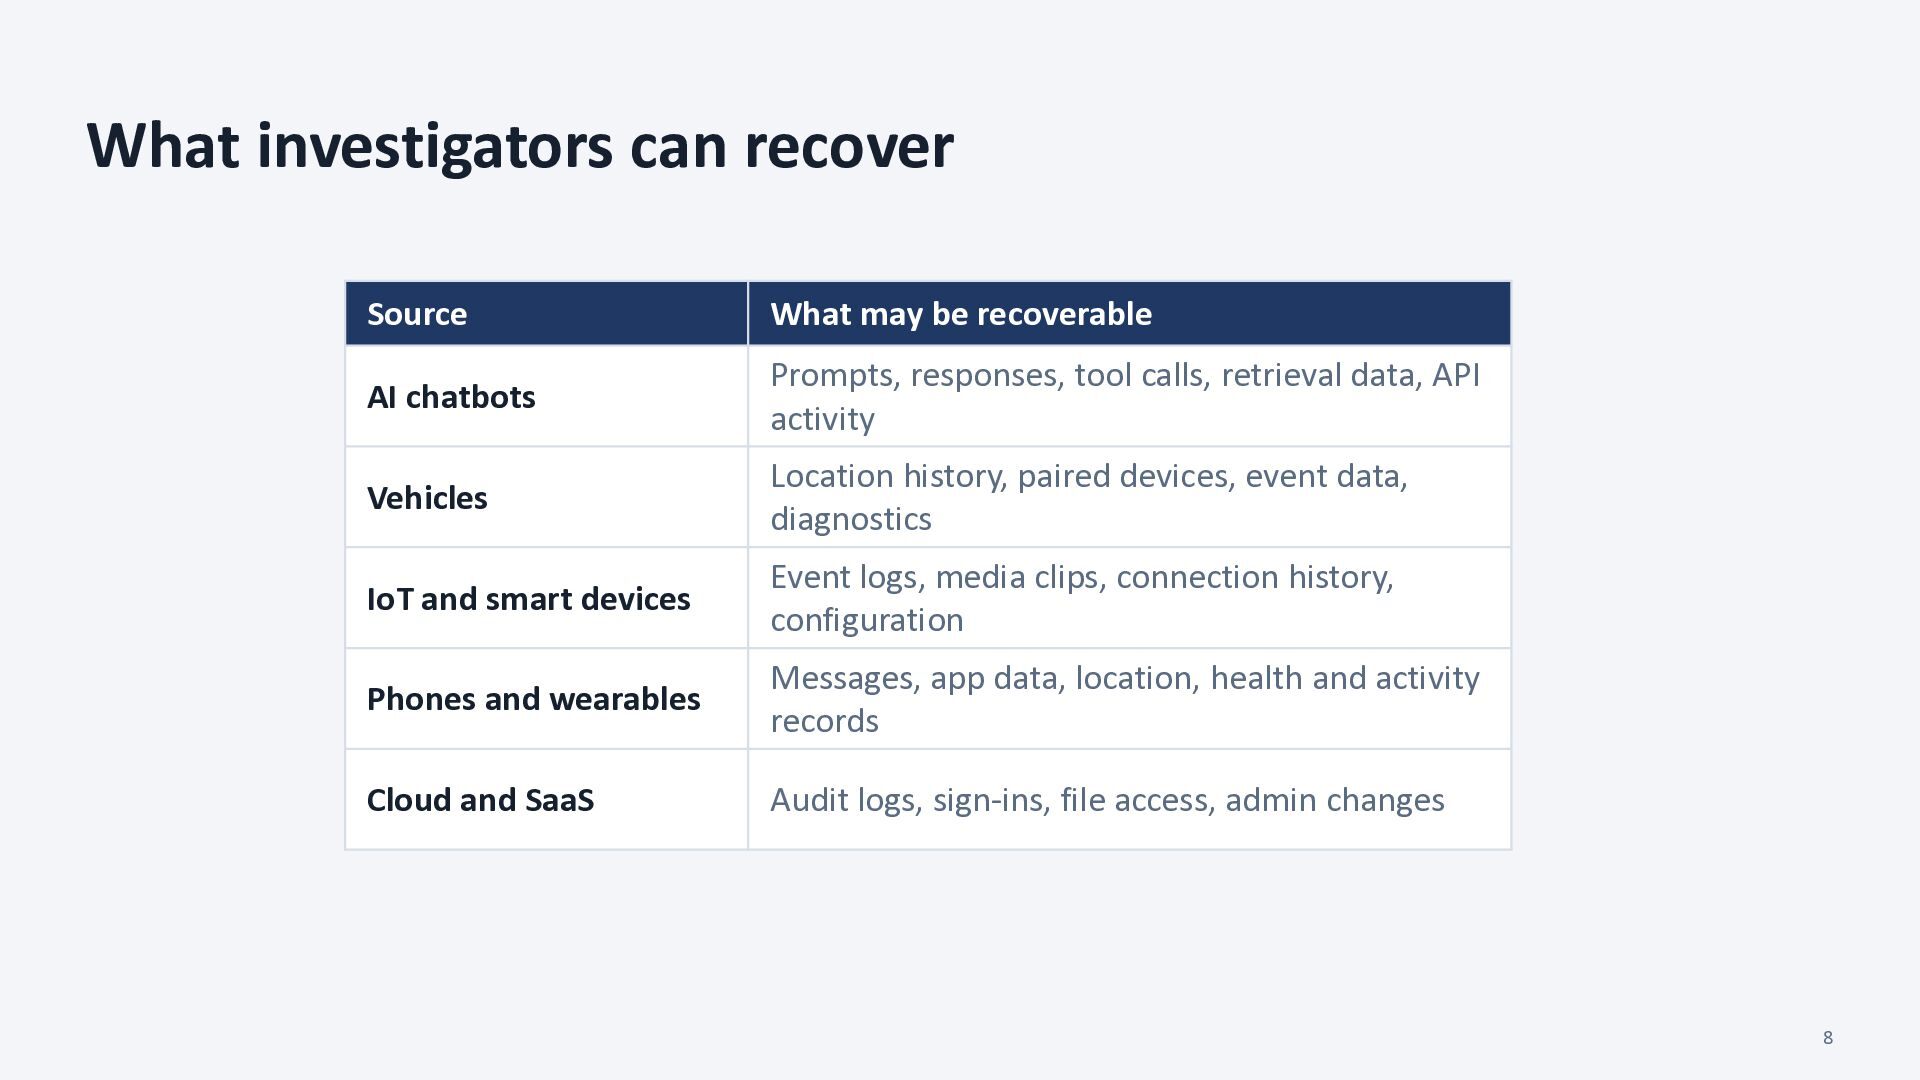
  113. What investigators can recover Source What may be recoverable AI

    chatbots Prompts, responses, tool calls, retrieval data, API activity Vehicles Location history, paired devices, event data, diagnostics IoT and smart devices Event logs, media clips, connection history, configuration Phones and wearables Messages, app data, location, health and activity records Cloud and SaaS Audit logs, sign-ins, file access, admin changes 8
  114. Evidence has a shelf life Collect in order of volatility:

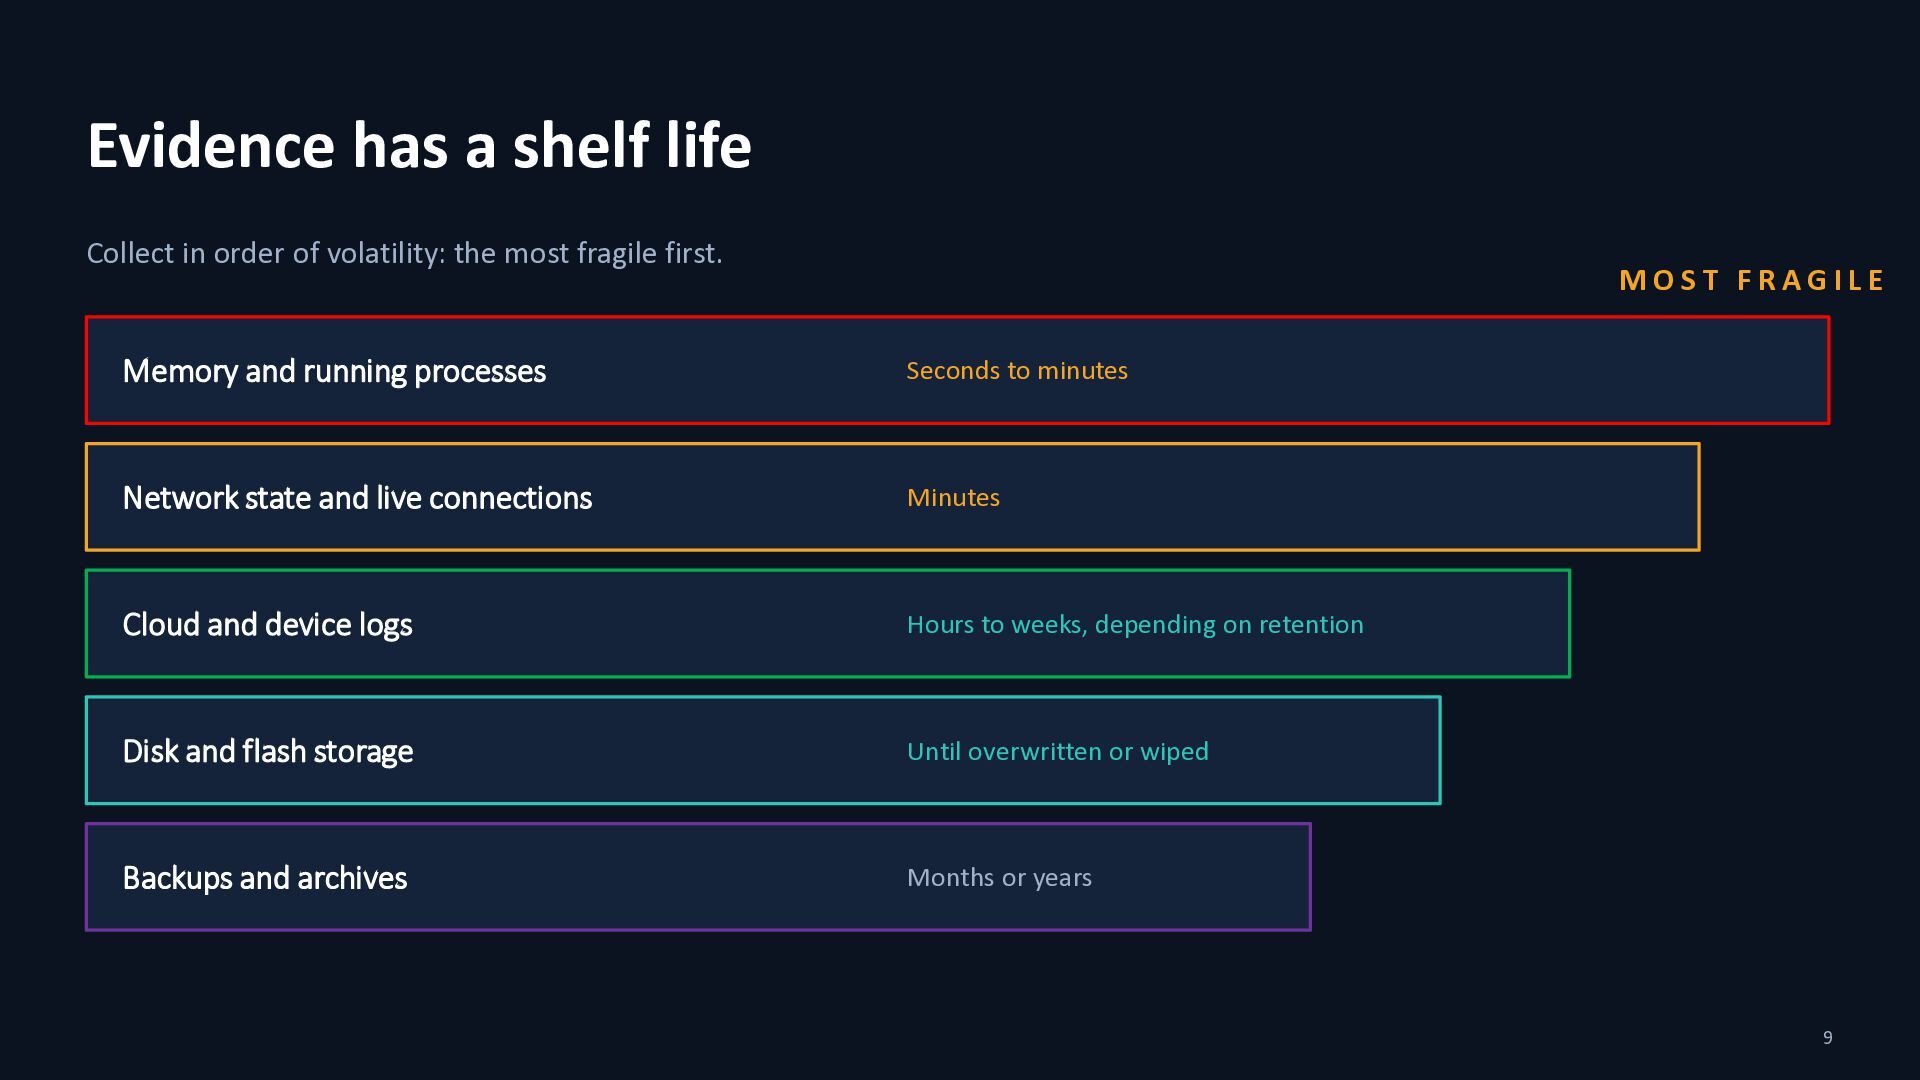
    the most fragile first. MOST FRAGILE Memory and running processes Seconds to minutes Network state and live connections Minutes Cloud and device logs Hours to weeks, depending on retention Disk and flash storage Until overwritten or wiped Backups and archives Months or years 9
  115. Illustrative case: one story, many sources A hypothetical intrusion. DAY

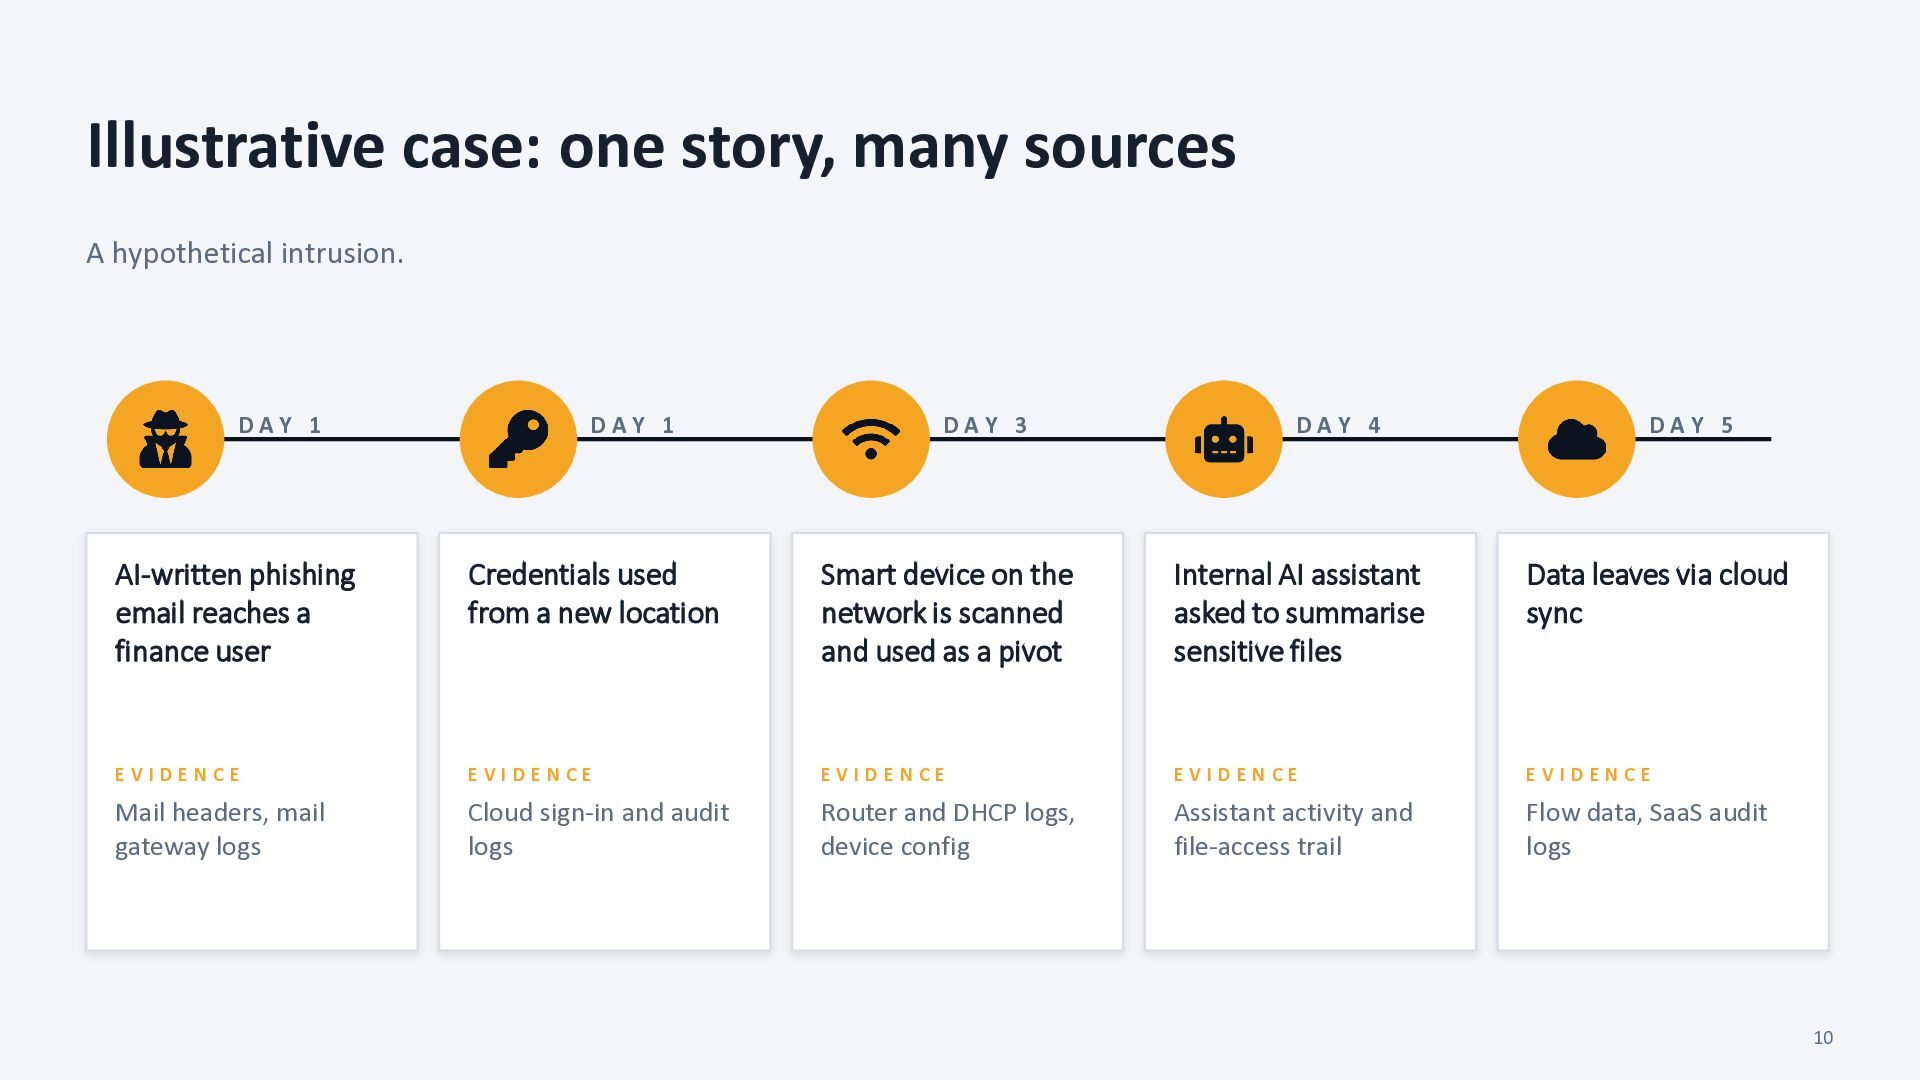
    1 DAY 1 DAY 3 DAY 4 DAY 5 AI-written phishing email reaches a finance user Credentials used from a new location Smart device on the network is scanned and used as a pivot Internal AI assistant asked to summarise sensitive files Data leaves via cloud sync EVIDENCE EVIDENCE EVIDENCE EVIDENCE EVIDENCE Mail headers, mail gateway logs Cloud sign-in and audit logs Router and DHCP logs, device config Assistant activity and file-access trail Flow data, SaaS audit logs 10
  116. Forensic findings expose security gaps What the investigation found The

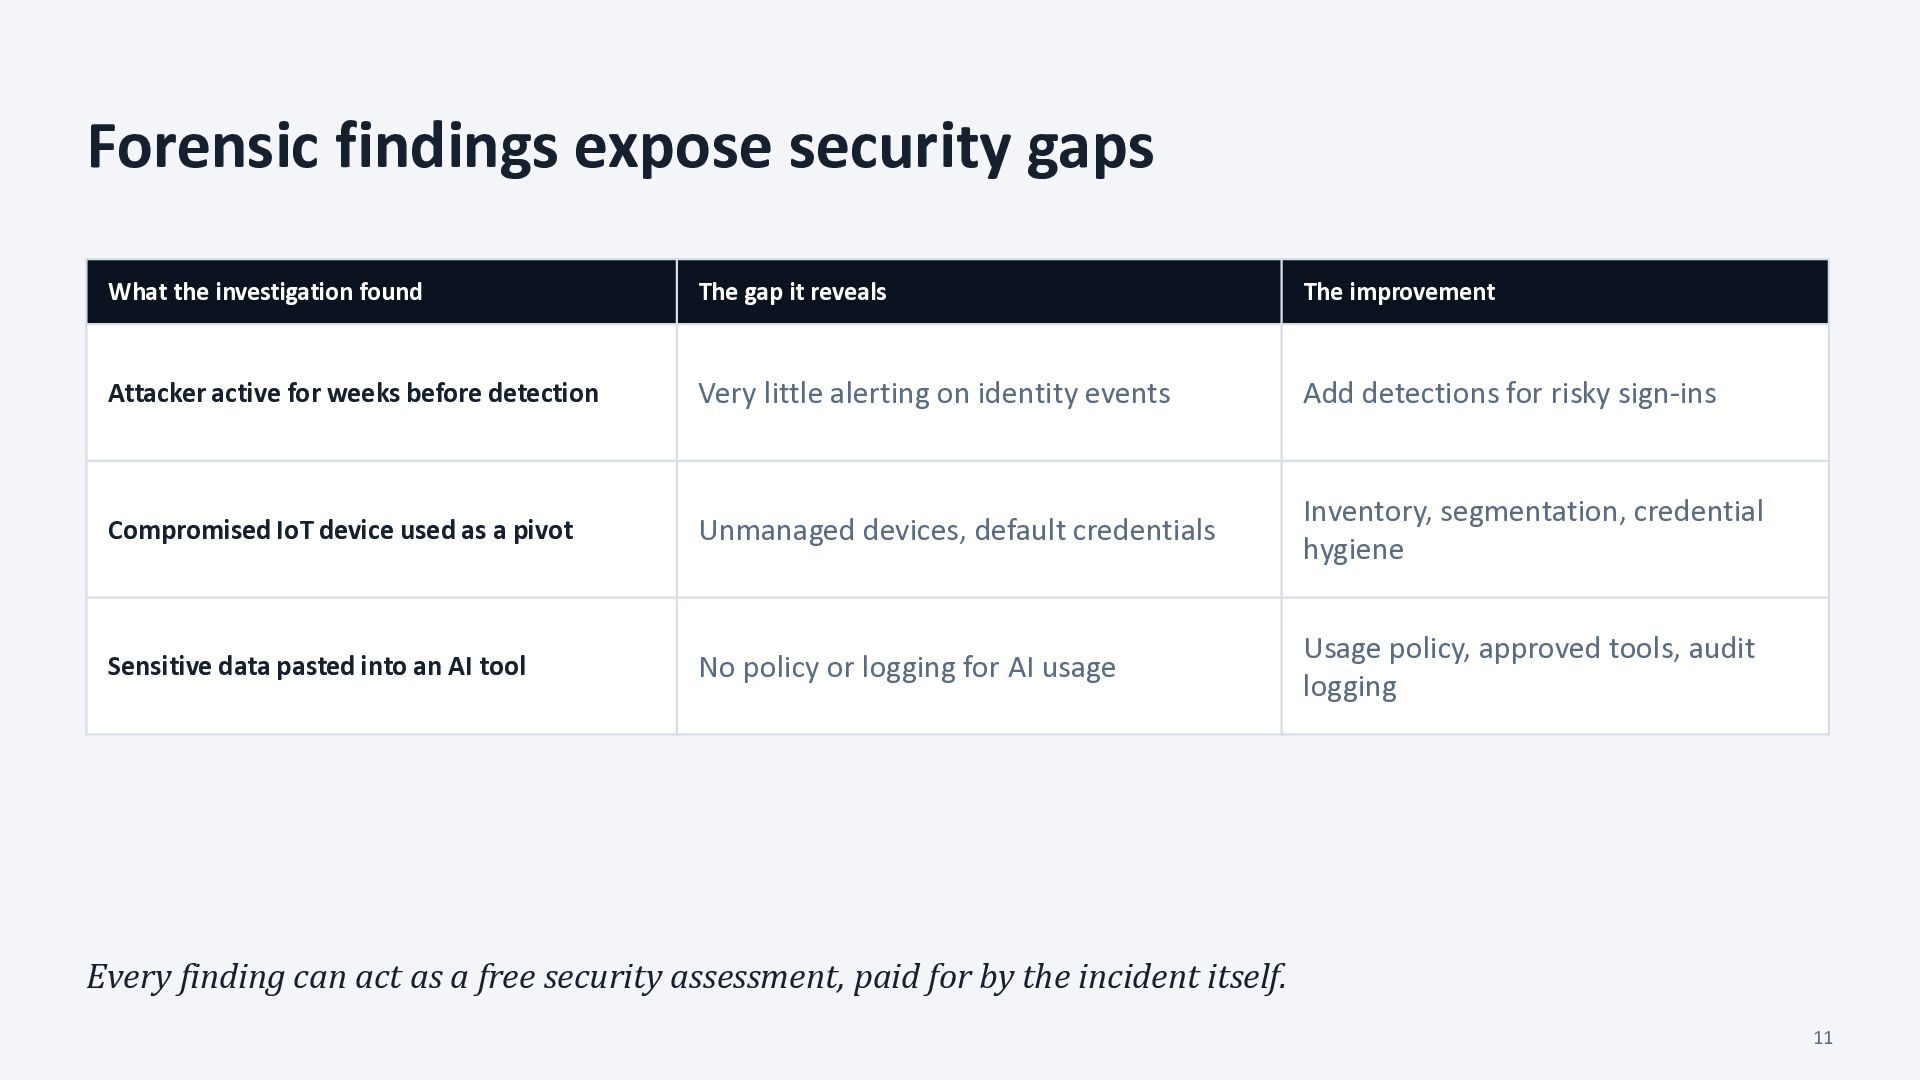
    gap it reveals The improvement Attacker active for weeks before detection Very little alerting on identity events Add detections for risky sign-ins Compromised IoT device used as a pivot Unmanaged devices, default credentials Inventory, segmentation, credential hygiene Sensitive data pasted into an AI tool No policy or logging for AI usage Usage policy, approved tools, audit logging Every finding can act as a free security assessment, paid for by the incident itself. 11
  117. Five questions after every investigation 1 How did they get

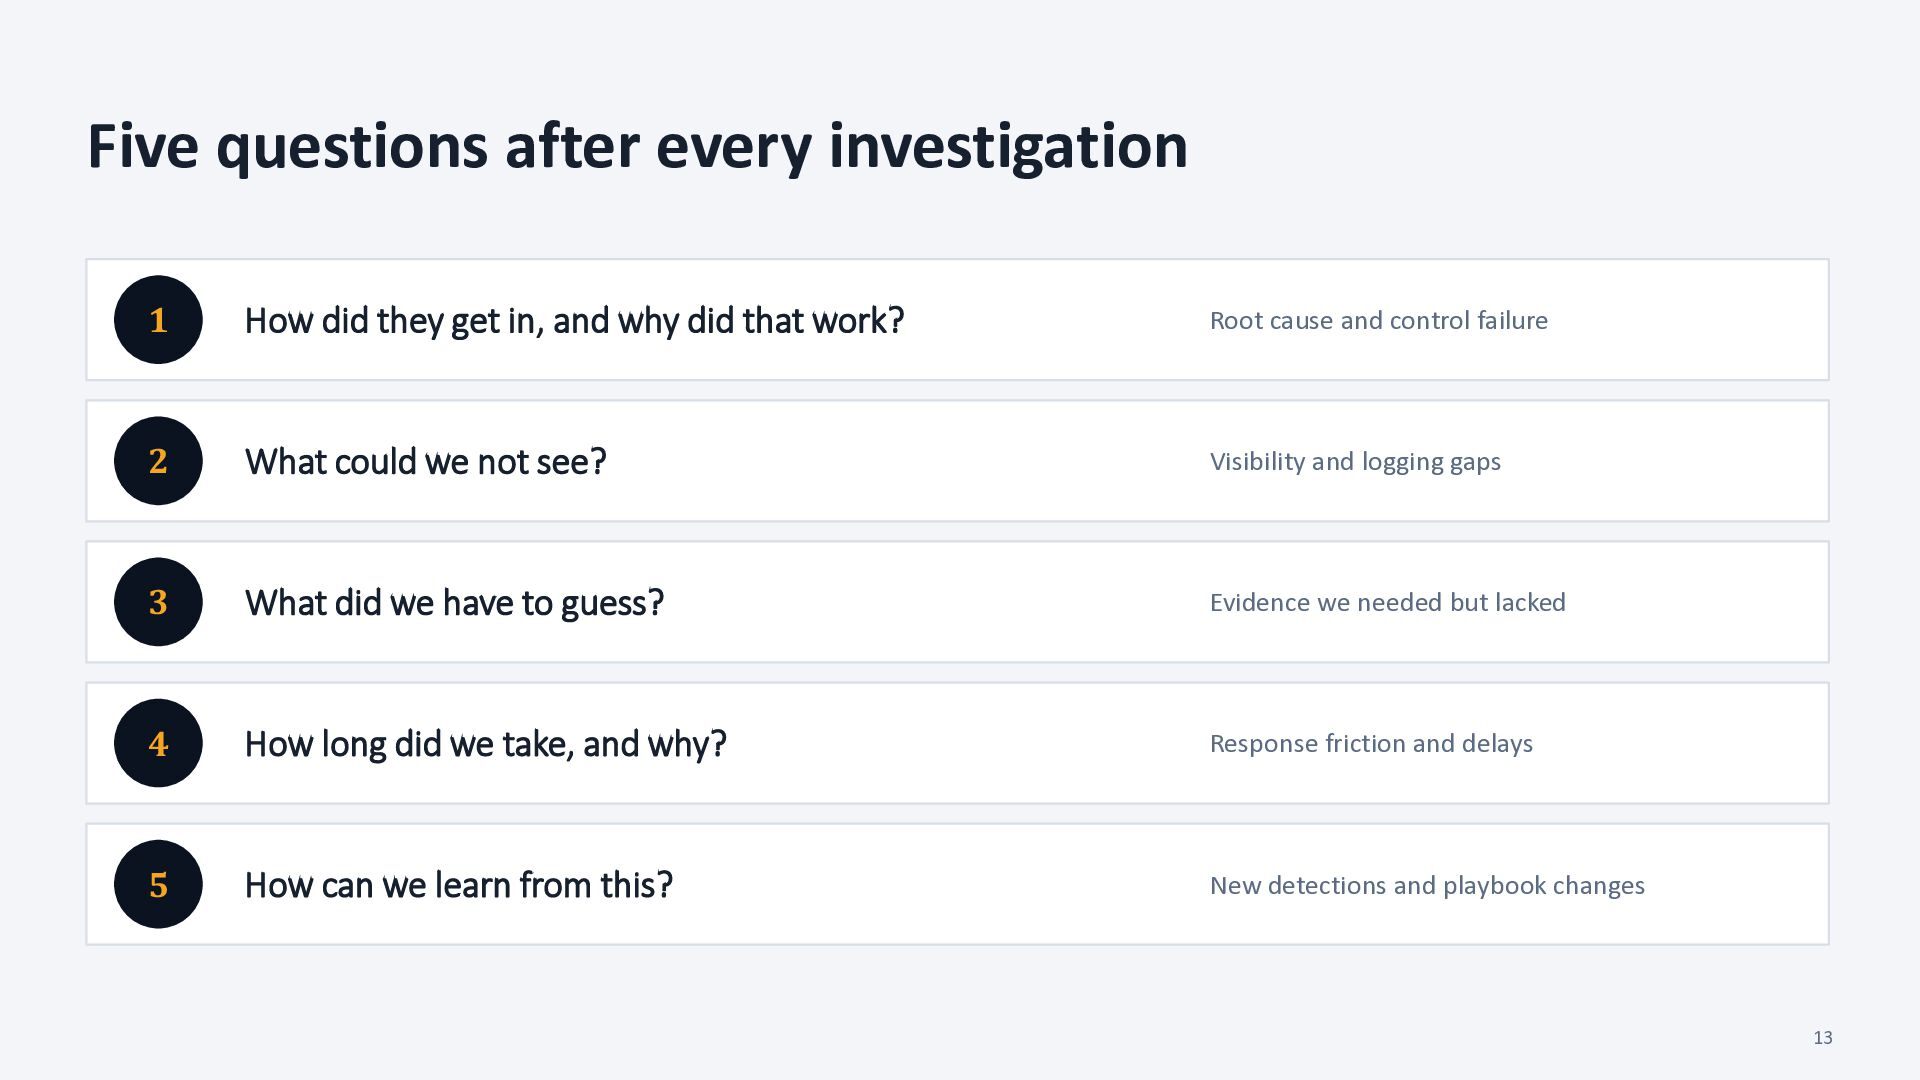
    in, and why did that work? Root cause and control failure 2 What could we not see? Visibility and logging gaps 3 What did we have to guess? Evidence we needed but lacked 4 How long did we take, and why? Response friction and delays 5 How can we learn from this? New detections and playbook changes 13
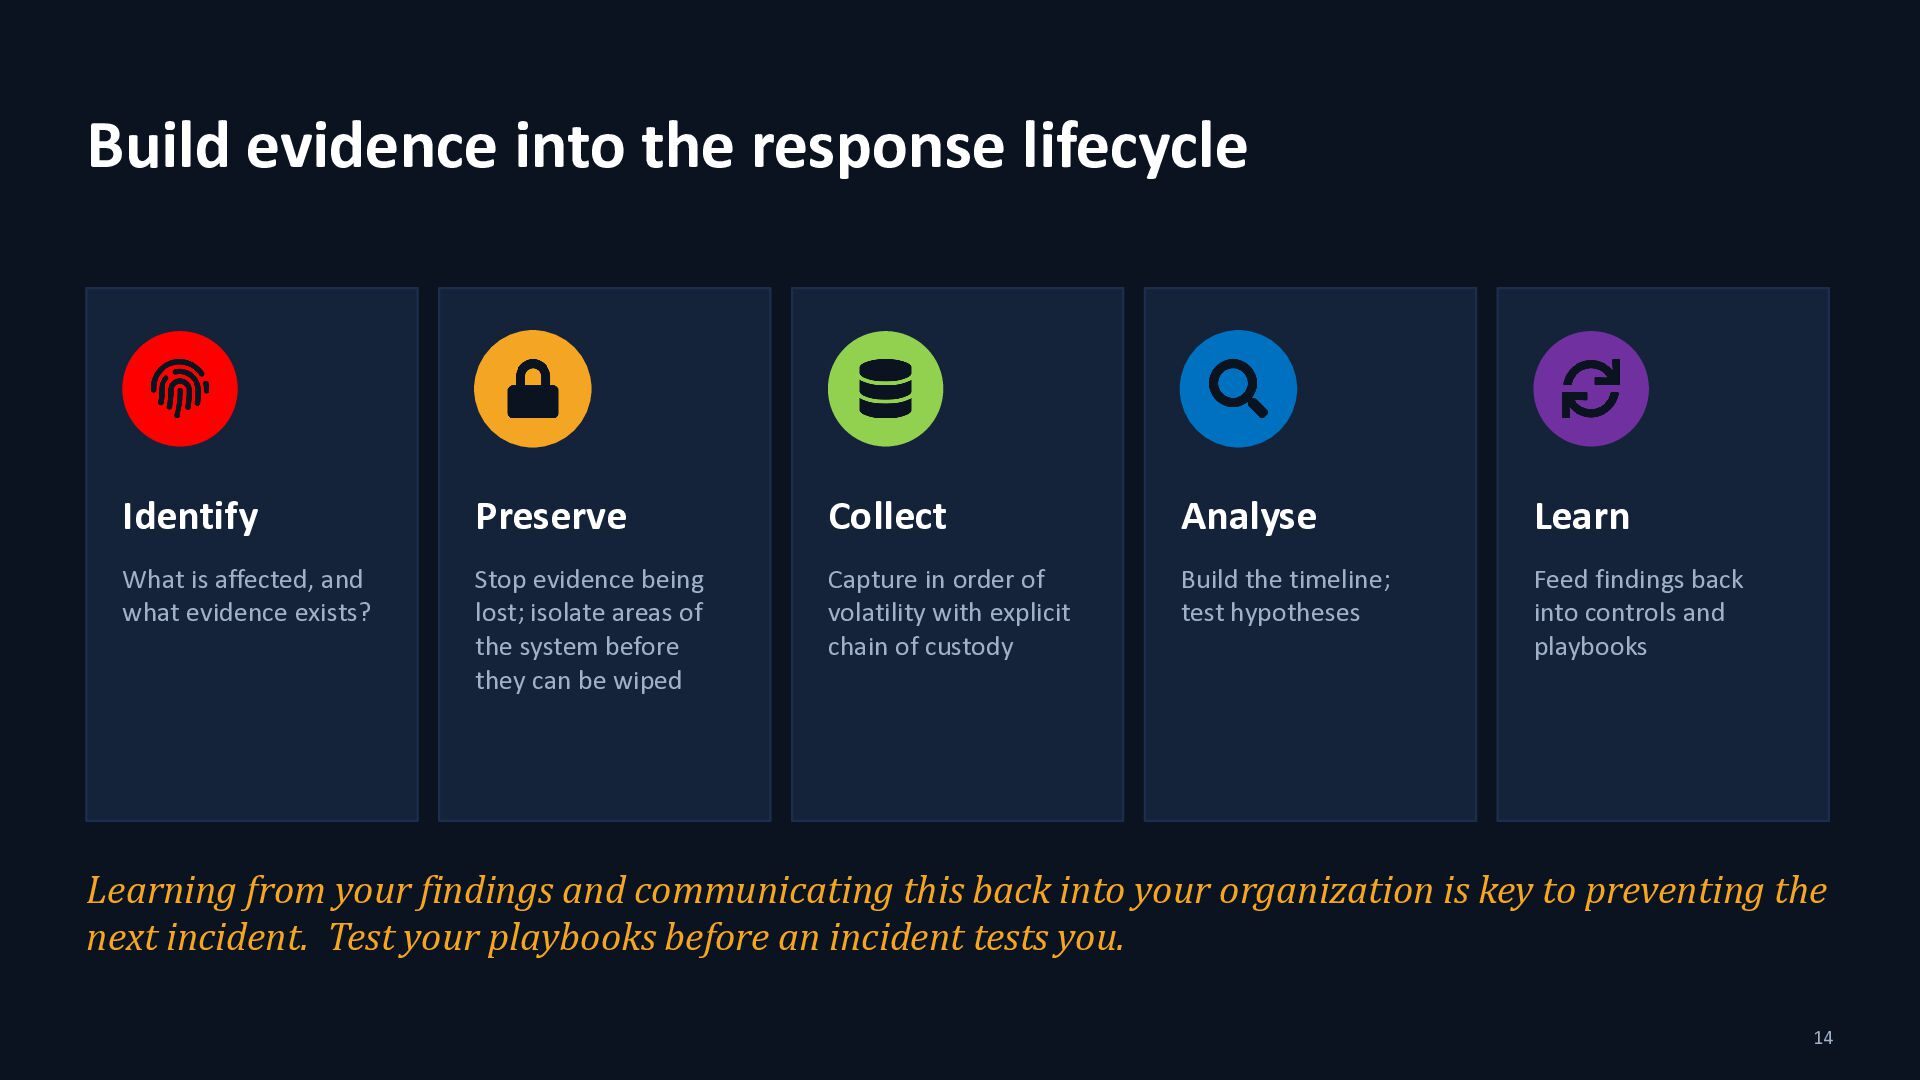
  118. Build evidence into the response lifecycle Identify Preserve Collect Analyse

    Learn What is affected, and what evidence exists? Stop evidence being lost; isolate areas of the system before they can be wiped Capture in order of volatility with explicit chain of custody Build the timeline; test hypotheses Feed findings back into controls and playbooks Learning from your findings and communicating this back into your organization is key to preventing the next incident. Test your playbooks before an incident tests you. 14
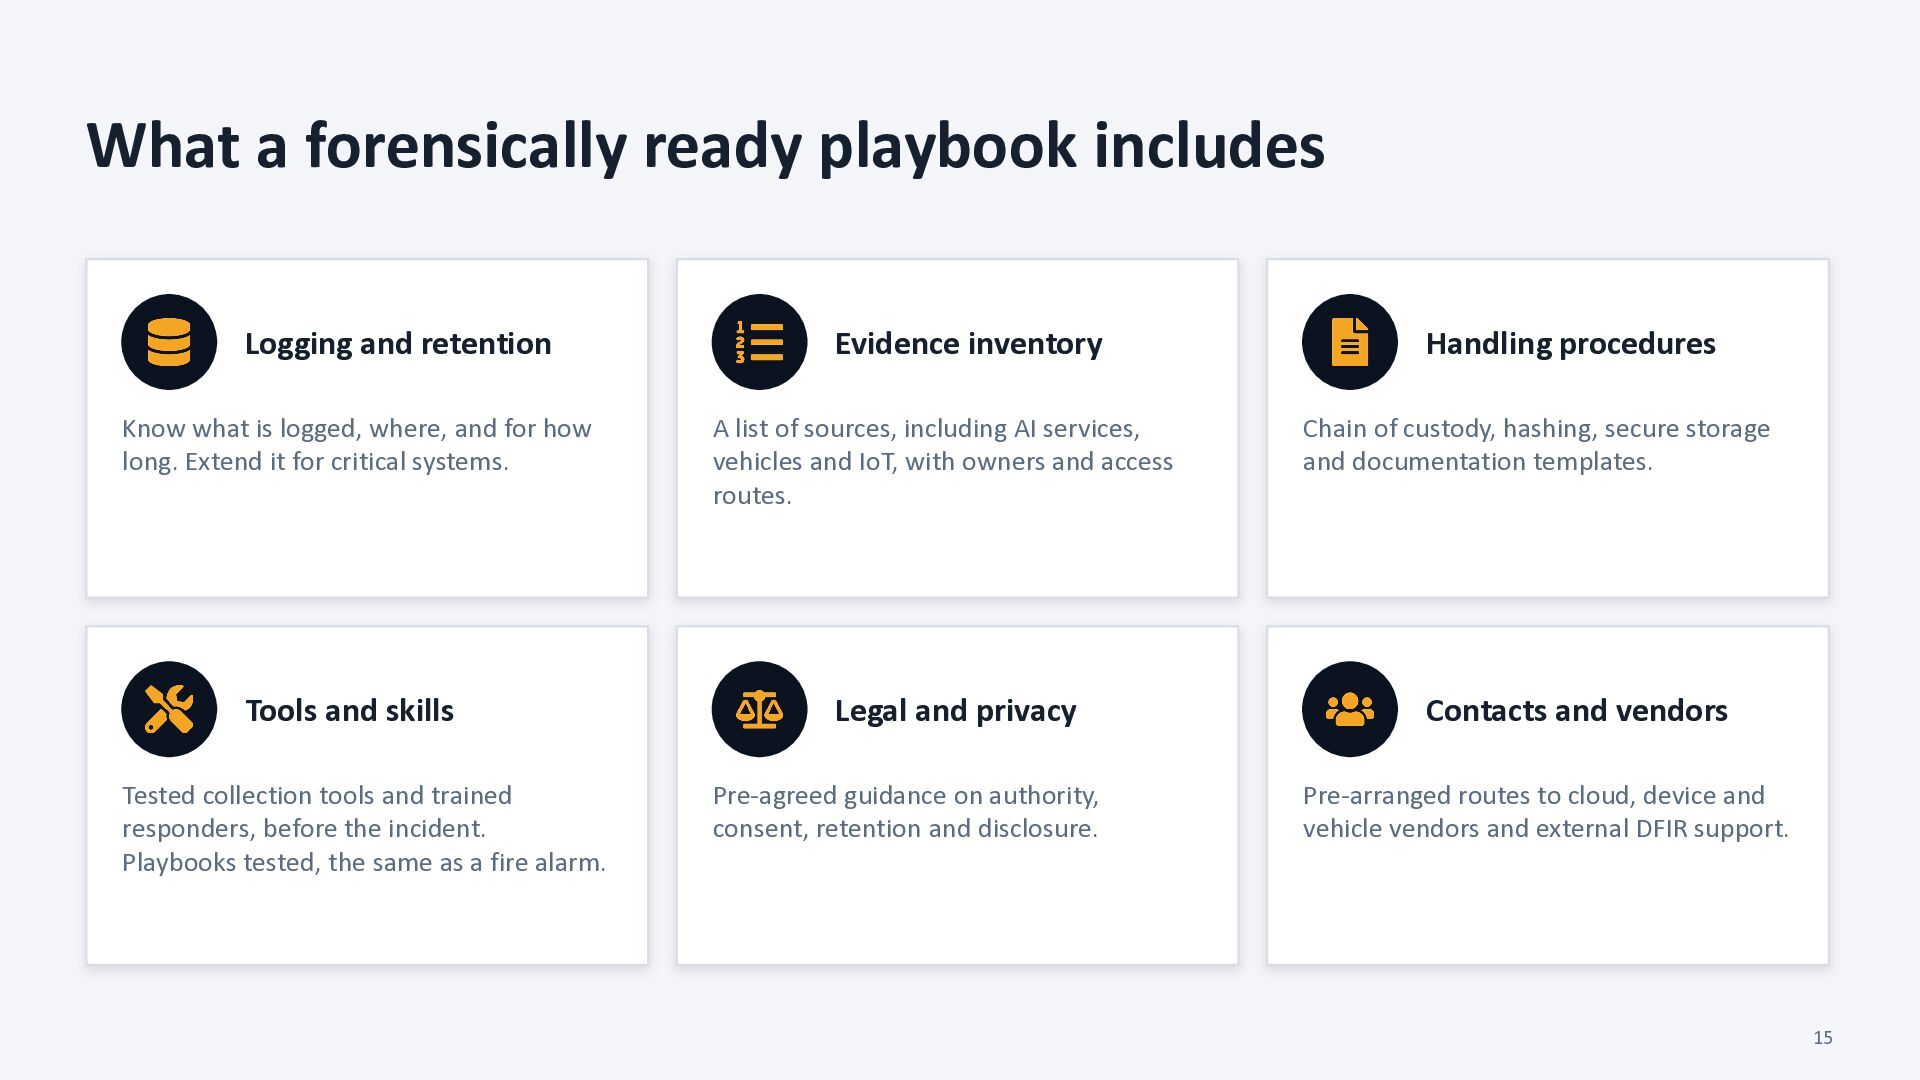
  119. What a forensically ready playbook includes Logging and retention Evidence

    inventory Know what is logged, where, and for how long. Extend it for critical systems. A list of sources, including AI services, vehicles and IoT, with owners and access routes. Tools and skills Legal and privacy Tested collection tools and trained responders, before the incident. Playbooks tested, the same as a fire alarm. Pre-agreed guidance on authority, consent, retention and disclosure. Handling procedures Chain of custody, hashing, secure storage and documentation templates. Contacts and vendors Pre-arranged routes to cloud, device and vehicle vendors and external DFIR support. 15
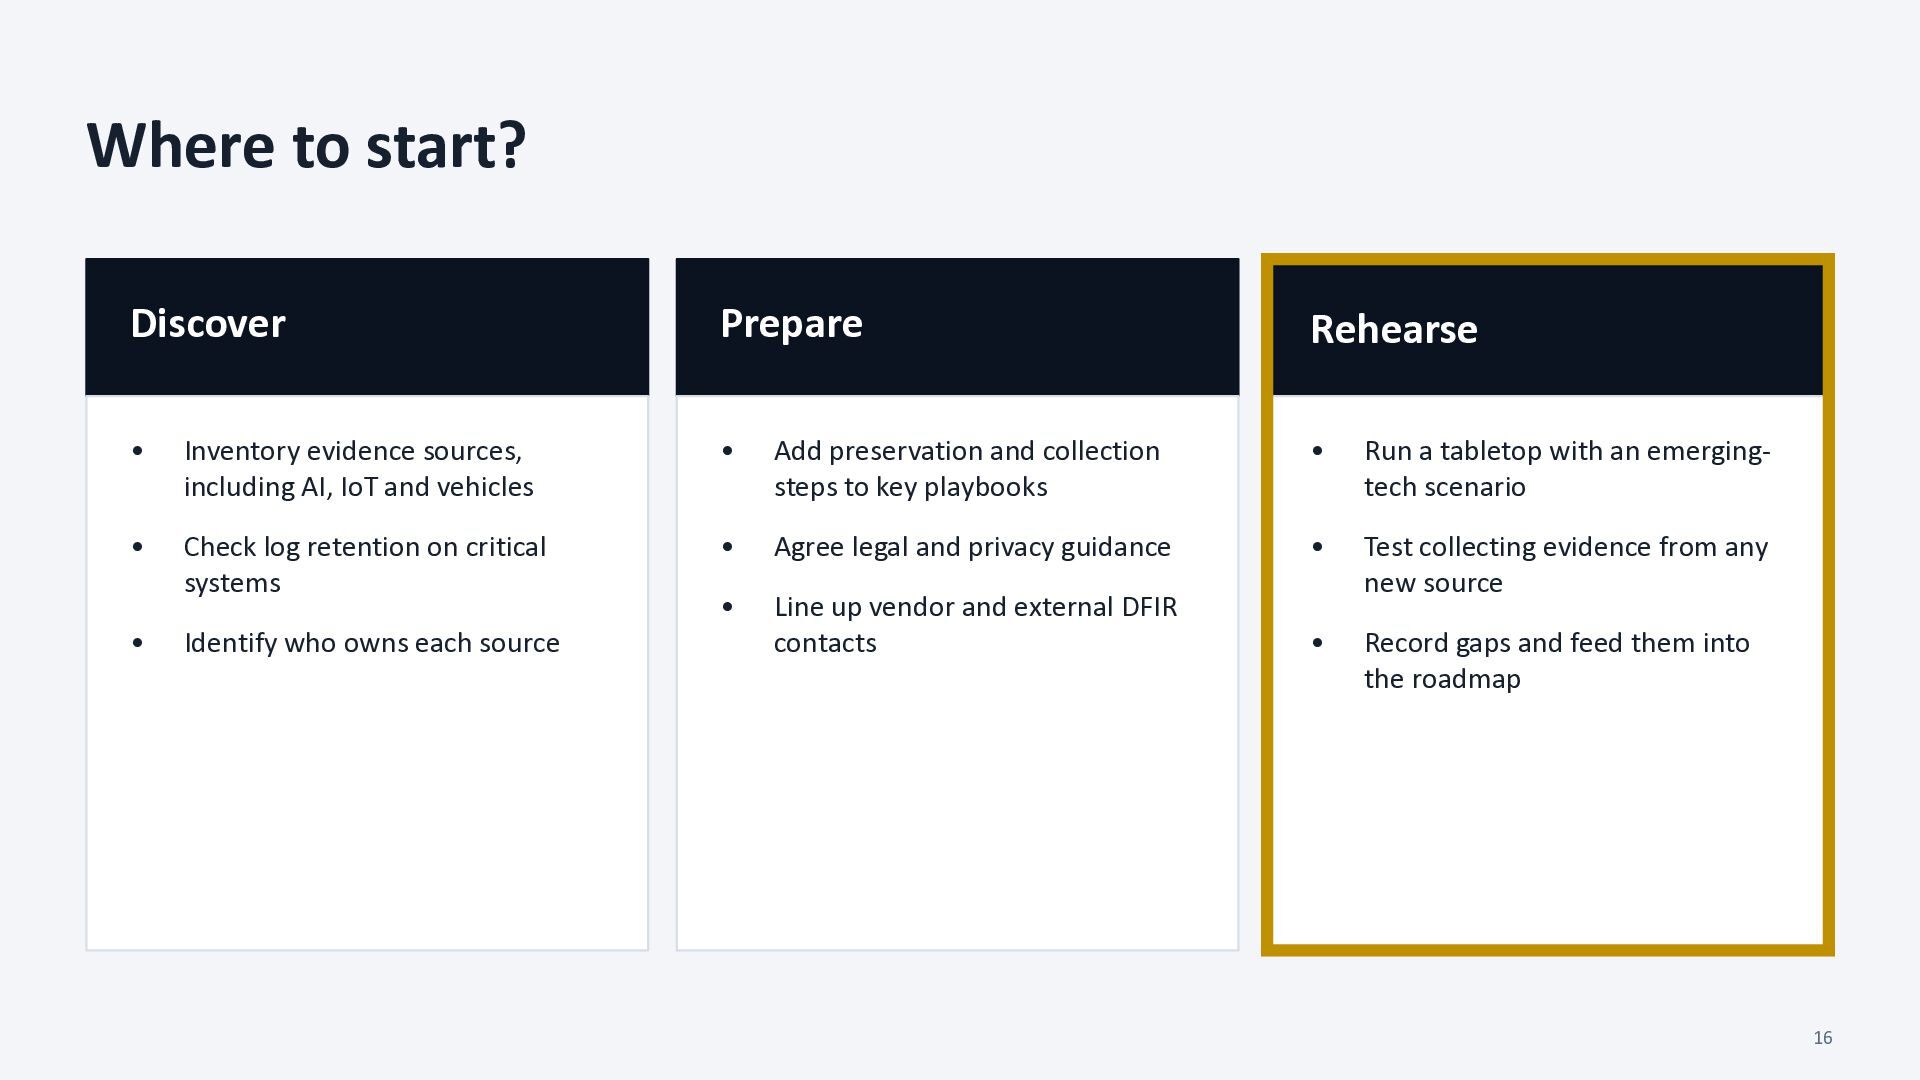
  120. Where to start? Discover Prepare Rehearse • Inventory evidence sources,

    including AI, IoT and vehicles • Add preservation and collection steps to key playbooks • Run a tabletop with an emergingtech scenario • Check log retention on critical systems • Agree legal and privacy guidance • • Line up vendor and external DFIR contacts Test collecting evidence from any new source • Record gaps and feed them into the roadmap • Identify who owns each source 16
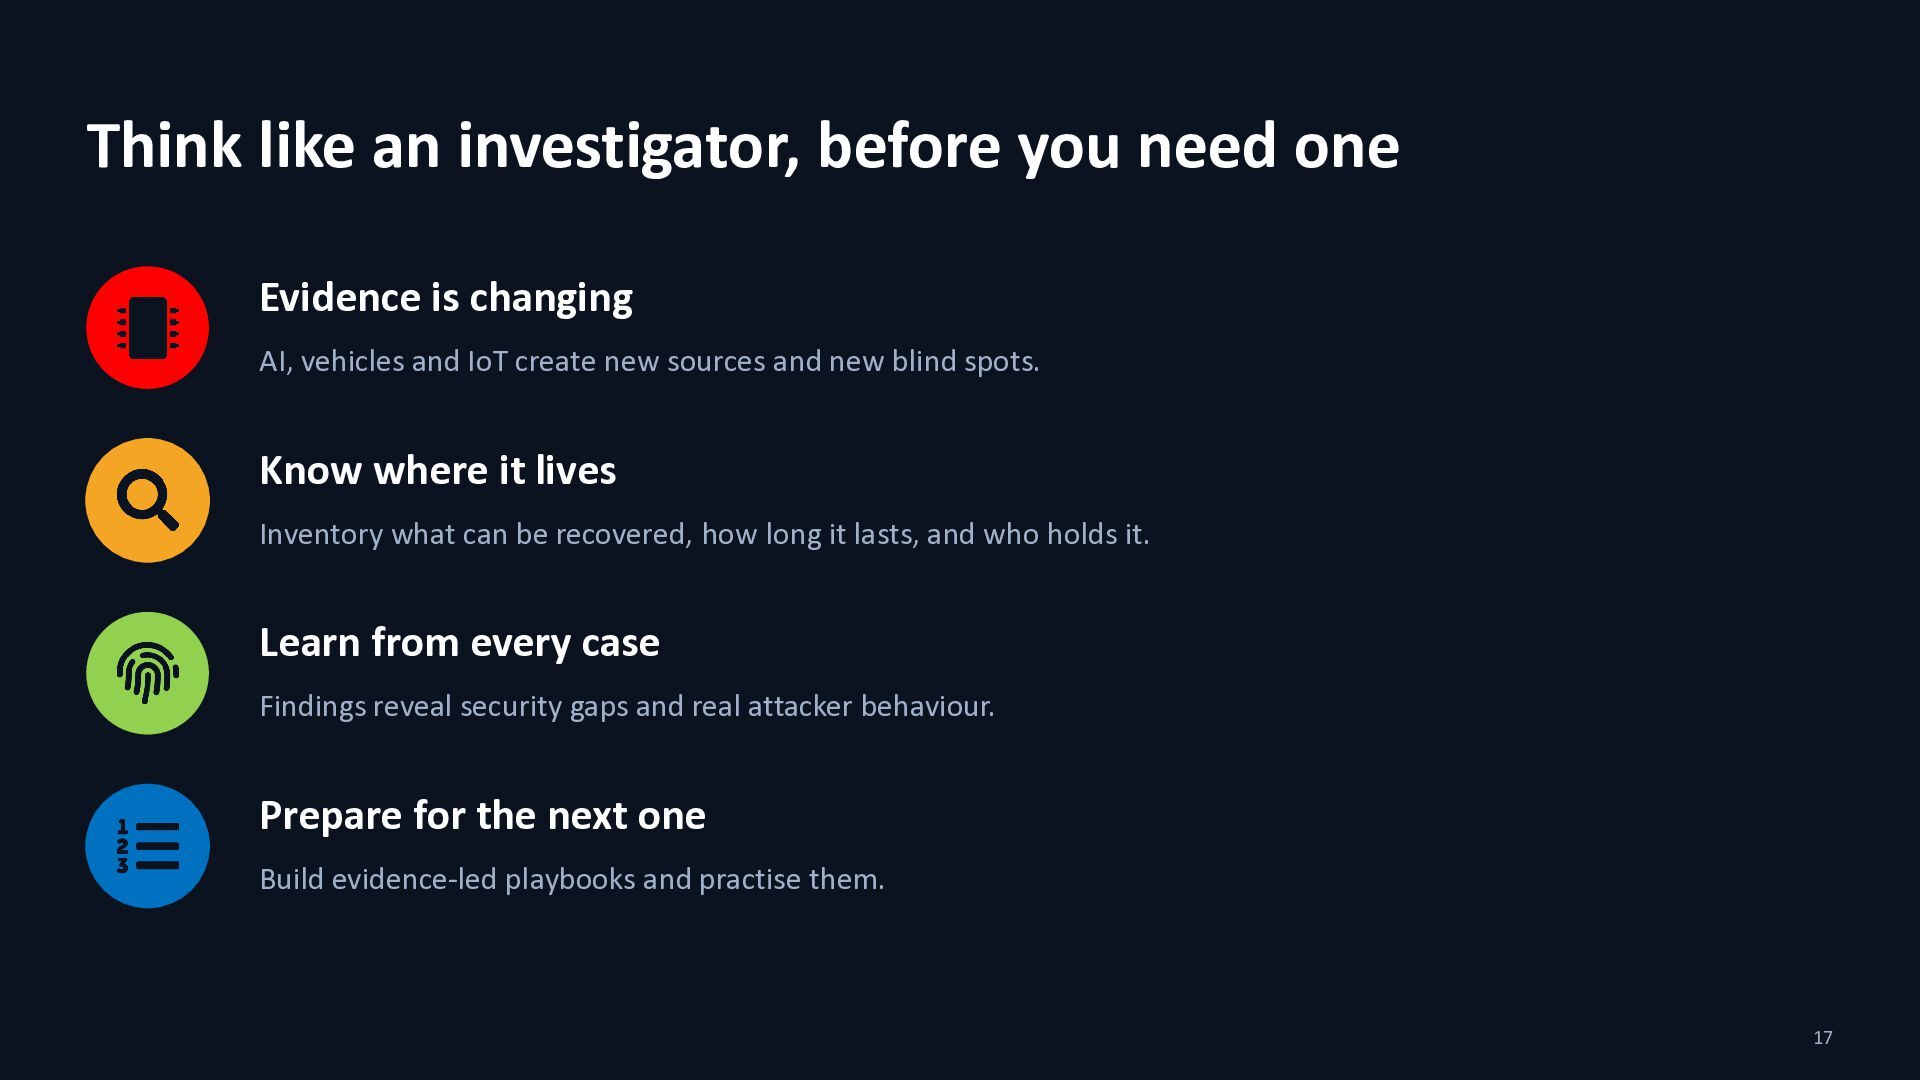
  121. Think like an investigator, before you need one Evidence is

    changing AI, vehicles and IoT create new sources and new blind spots. Know where it lives Inventory what can be recovered, how long it lasts, and who holds it. Learn from every case Findings reveal security gaps and real attacker behaviour. Prepare for the next one Build evidence-led playbooks and practise them. 17
  122. #CymruSec Coming next – Second Breakout Breakout C: Thieves Don’t

    Break In… They Log In: Secure Your M365 in Minutes, Not Months​ Breakout D: Cyber Threats are Evolving Faster than Organisations can Adapt - and AI is Raising the Stakes This Room 12:15 Ricoh Suite 12:15
  123. CymruSec Summit 2026 Thieves Don’t Break In… They Log In:

    Secure Your M365 in Minutes, Not Months
  124. Identity is a primary target Identity helps us ensure who

    a user is Identity dictates any actions a user can take Identity is a primary target for criminals
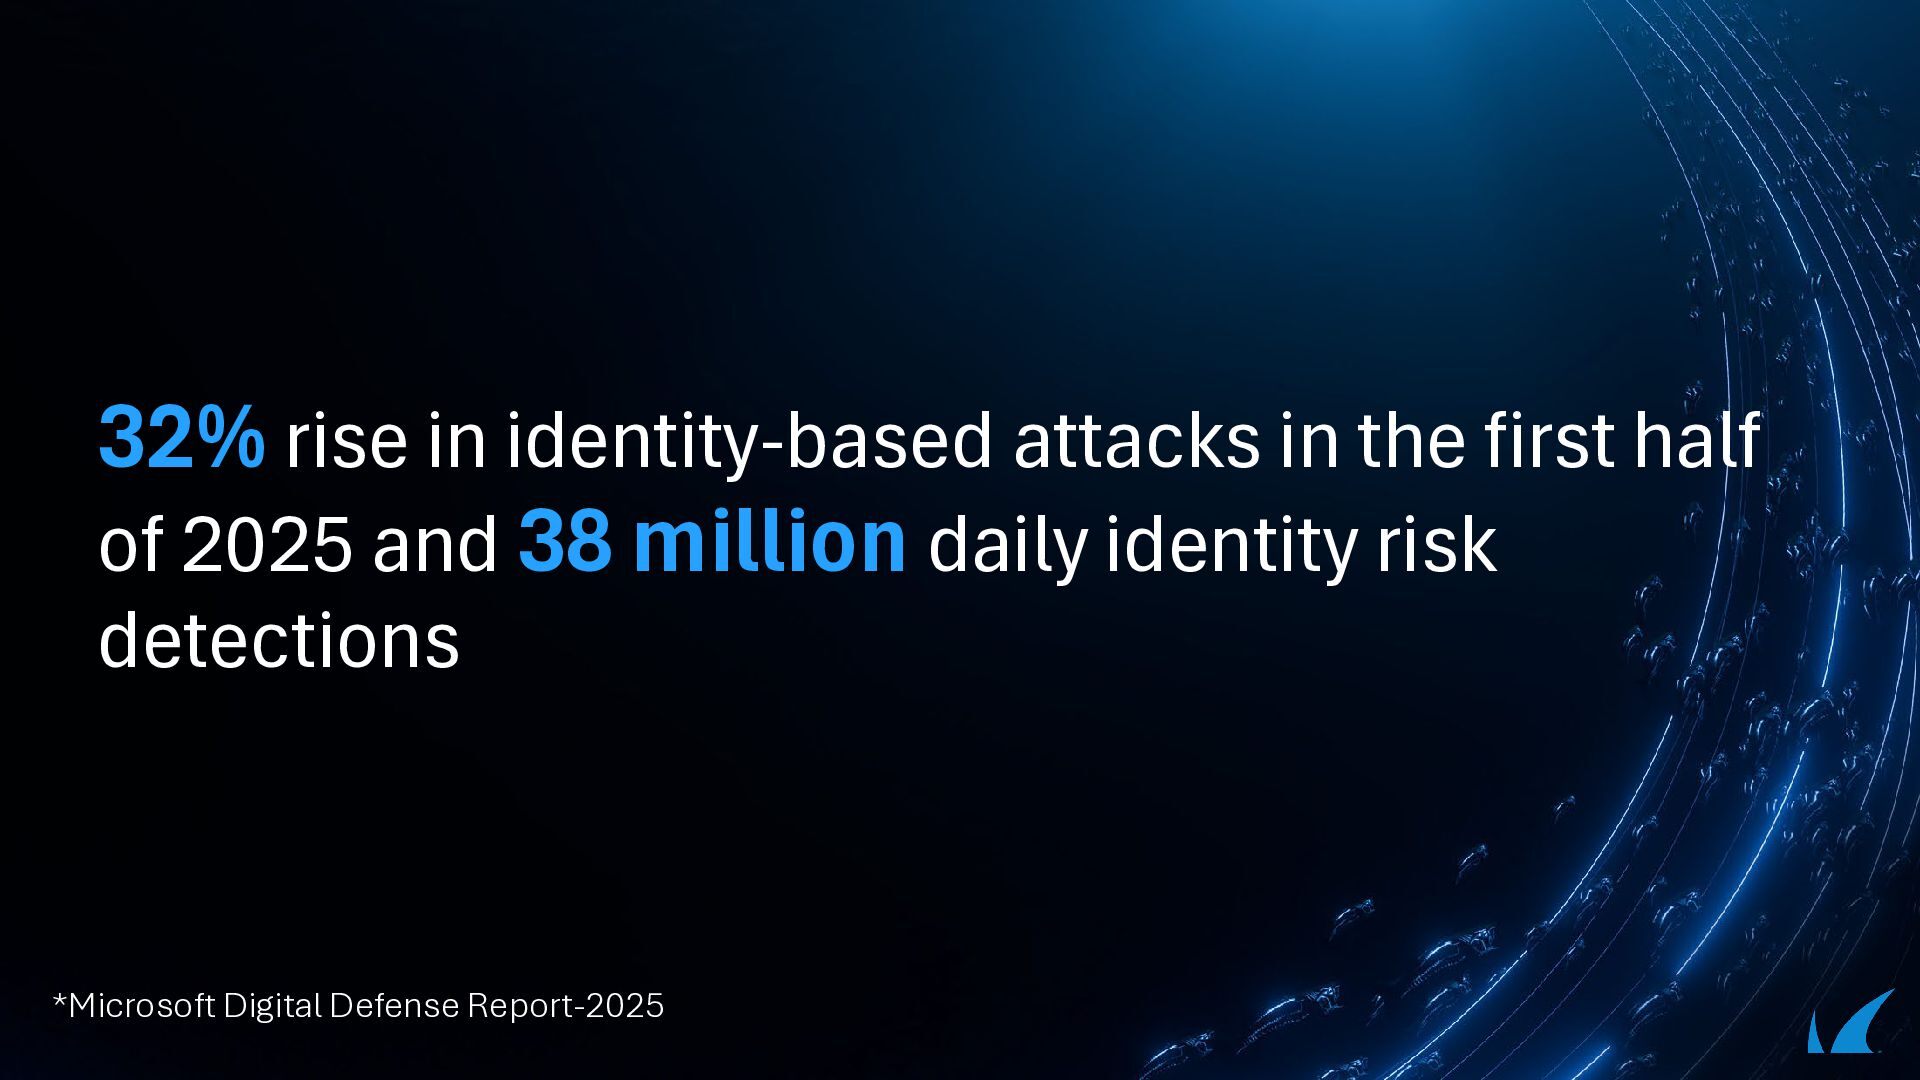
  125. 32% rise in identity-based attacks in the first half of

    2025 and 38 million daily identity risk detections *Microsoft Digital Defense Report-2025
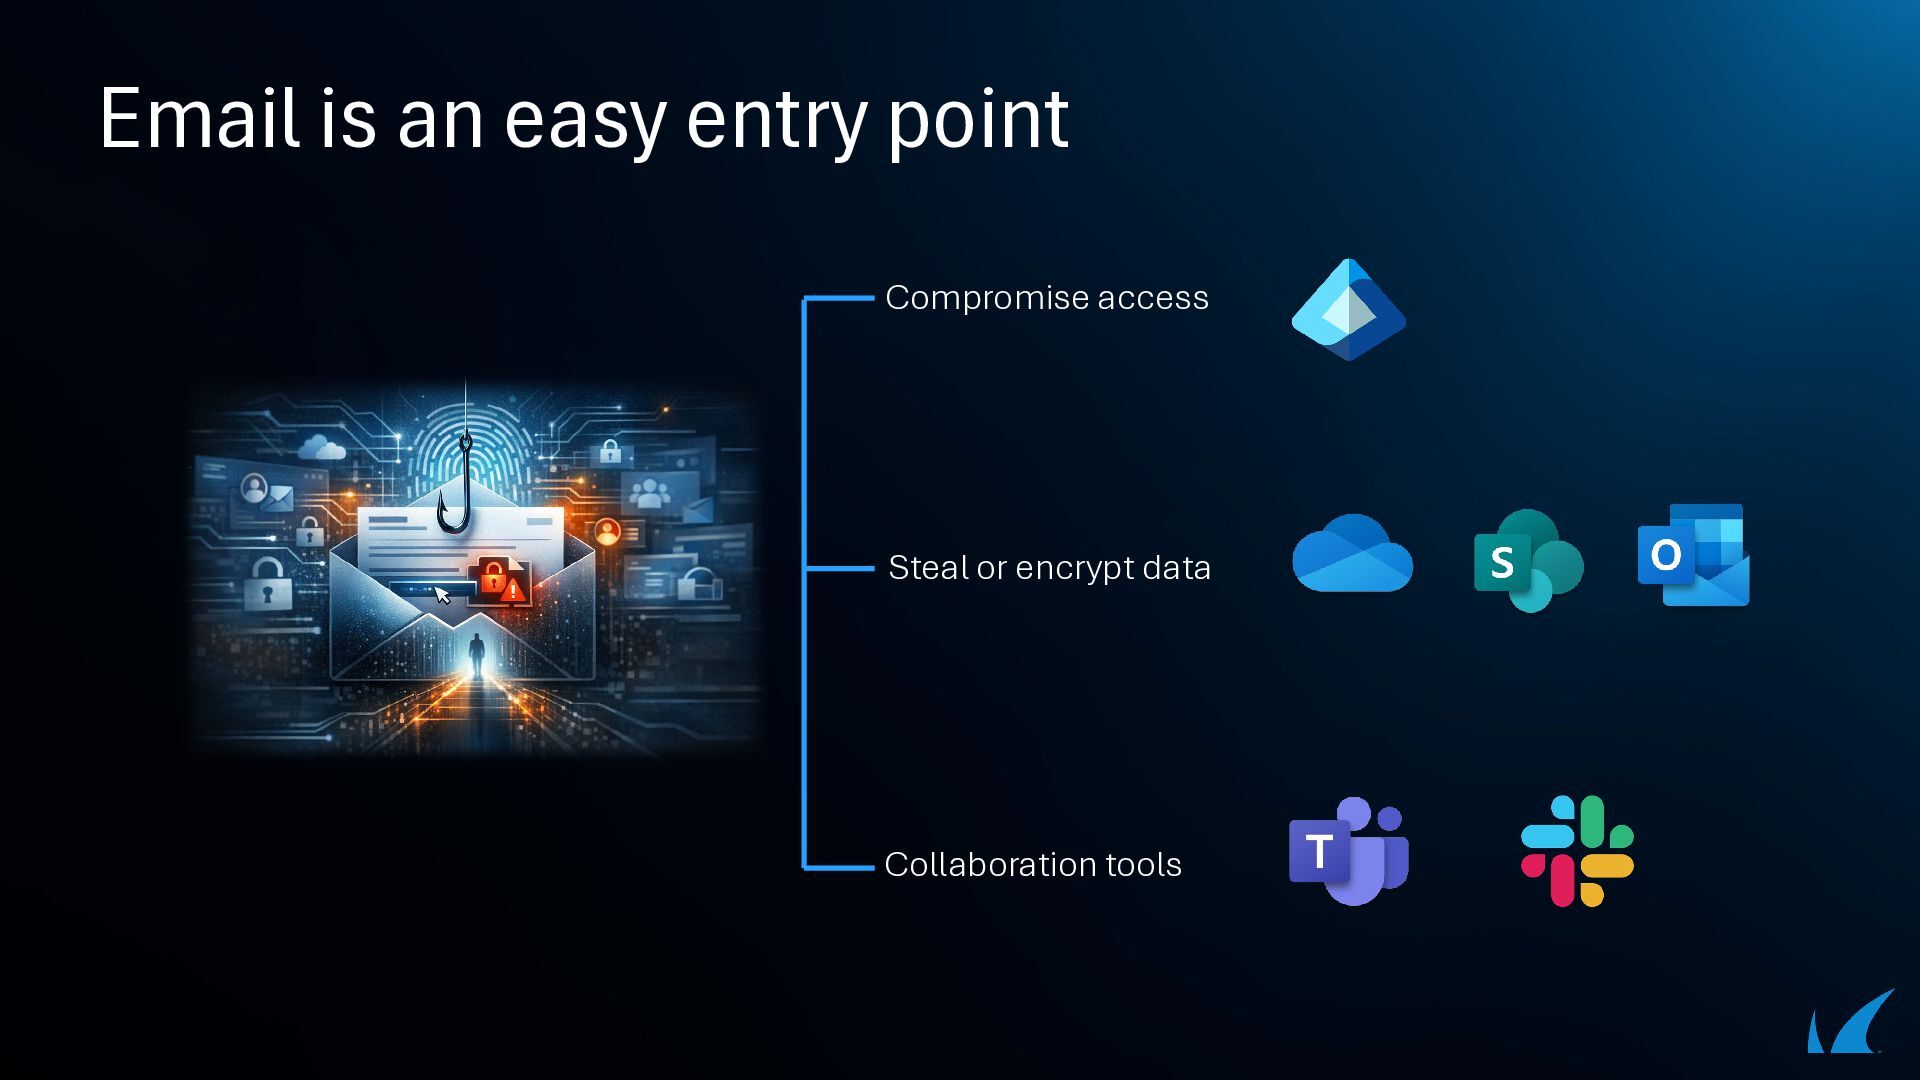
  126. Email is an easy entry point Compromise access Steal or

    encrypt data Malicious email Collaboration tools
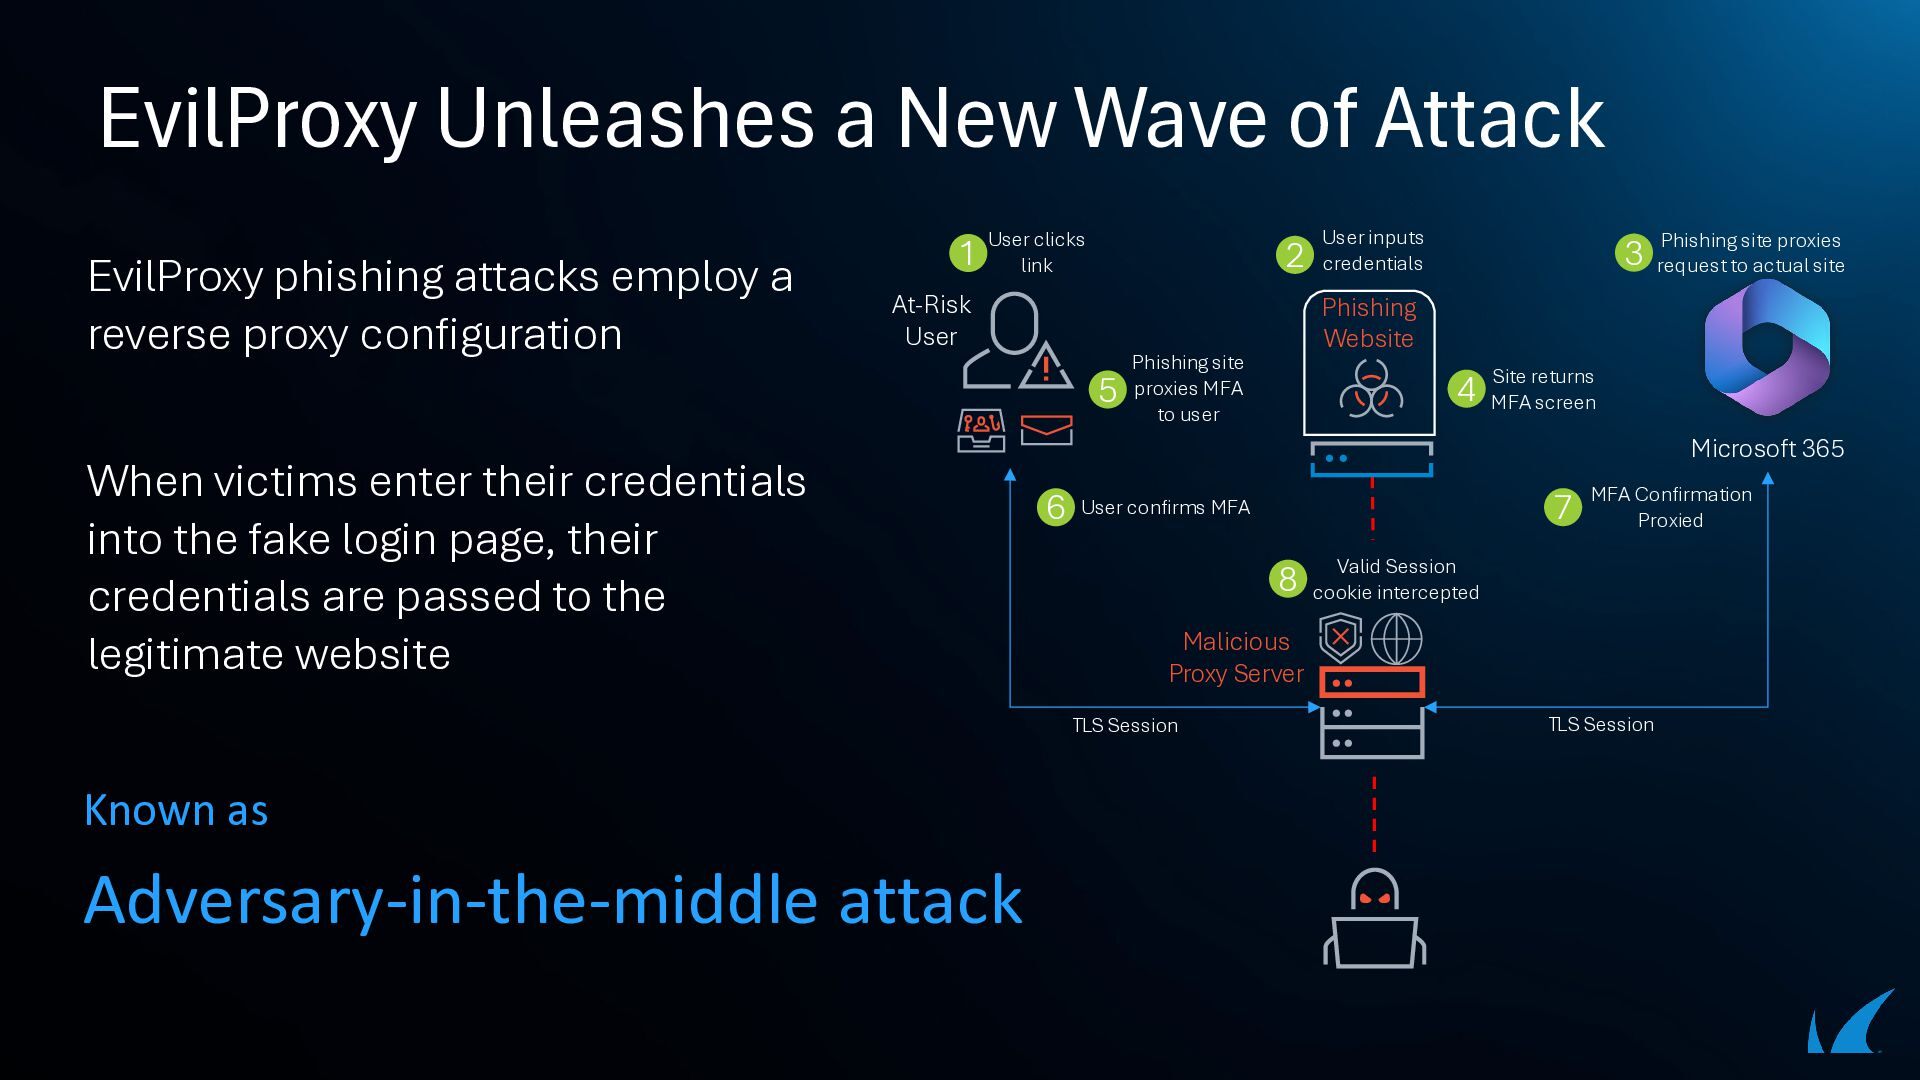
  127. EvilProxy Unleashes a New Wave of Attack EvilProxy phishing attacks

    employ a reverse proxy configuration 1 User inputs User clicks link At-Risk User 5 When victims enter their credentials into the fake login page, their credentials are passed to the legitimate website Adversary-in-the-middle attack Phishing Website Phishing site proxies MFA to user Site returns 4 MFA screen Microsoft 365 7 MFA Confirmation Proxied 6 User confirms MFA Valid Session 8 cookie intercepted Malicious Proxy Server TLS Session Known as Phishing site proxies 3 request to actual site 2 credentials TLS Session
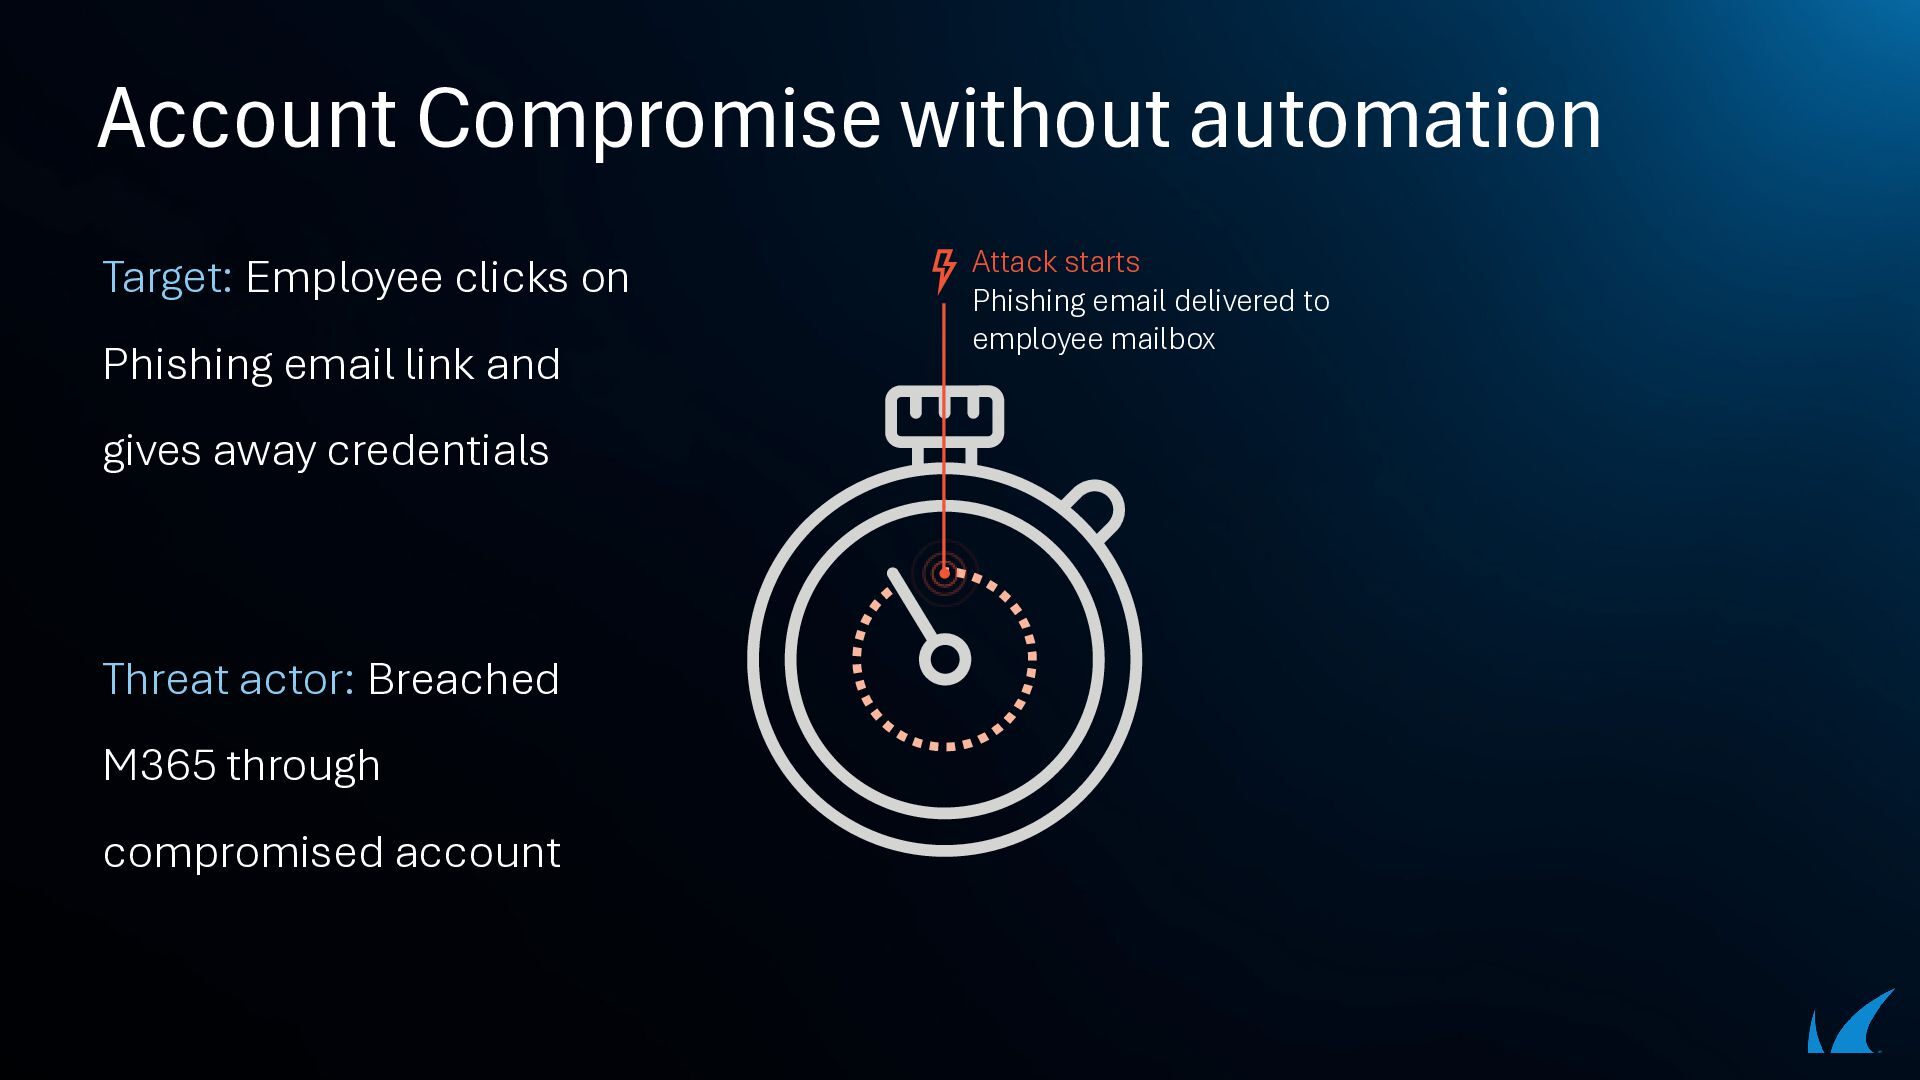
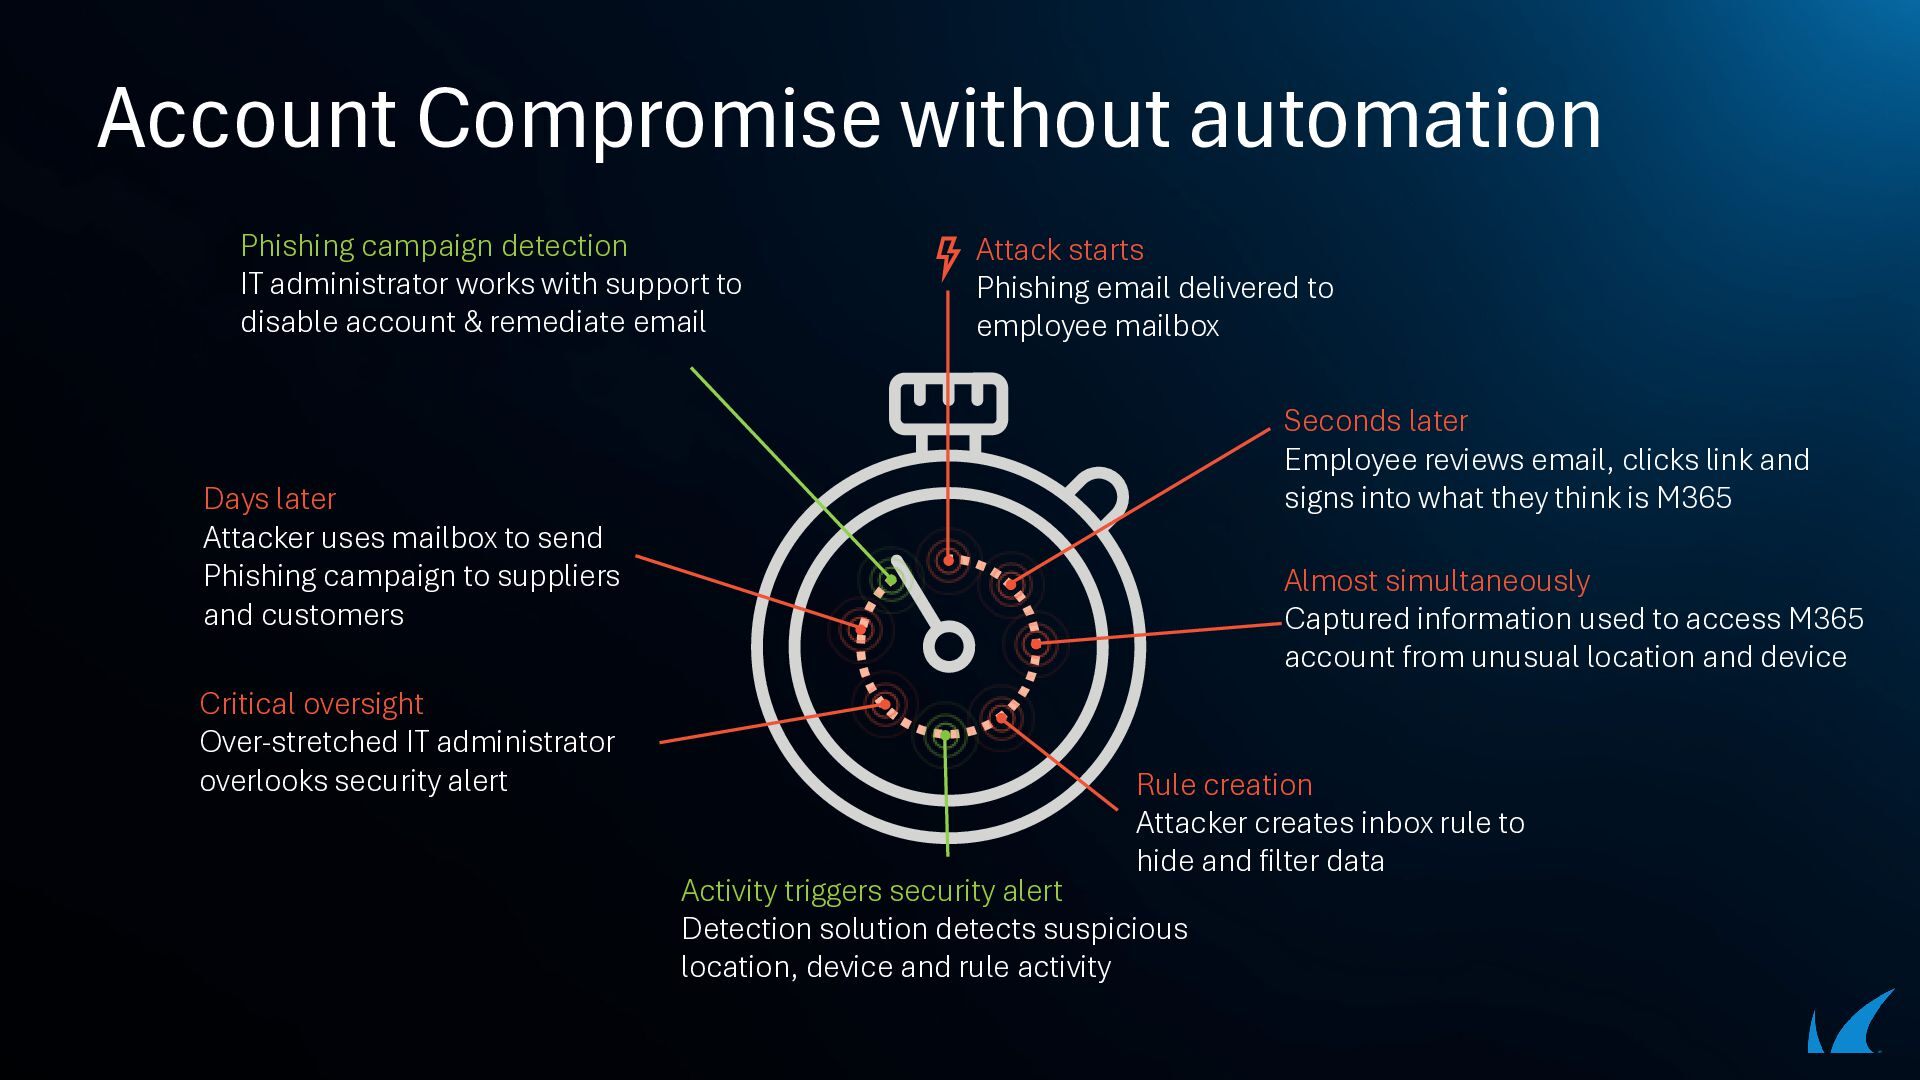
  128. Account Compromise without automation Target: Employee clicks on Phishing email

    link and gives away credentials Threat actor: Breached M365 through compromised account Attack starts Phishing email delivered to employee mailbox
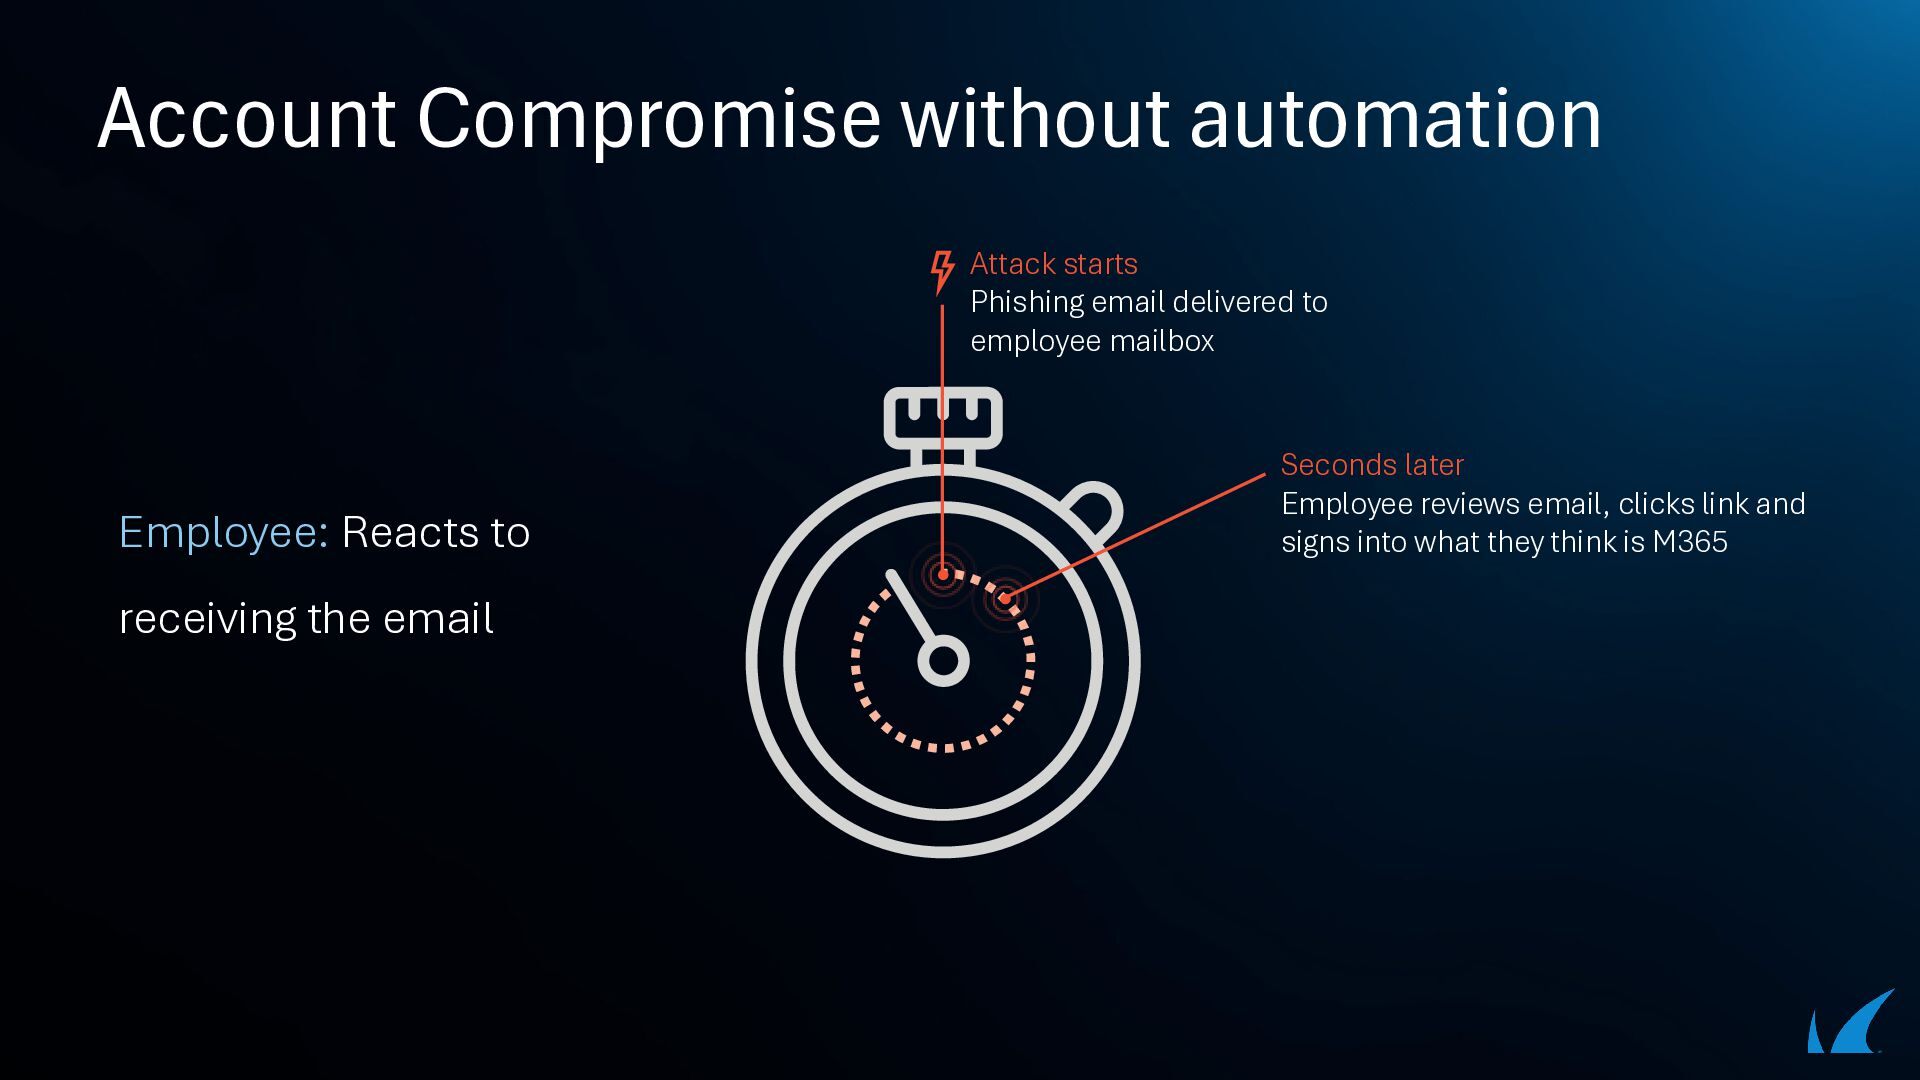
  129. Account Compromise without automation Attack starts Phishing email delivered to

    employee mailbox Employee: Reacts to receiving the email Seconds later Employee reviews email, clicks link and signs into what they think is M365
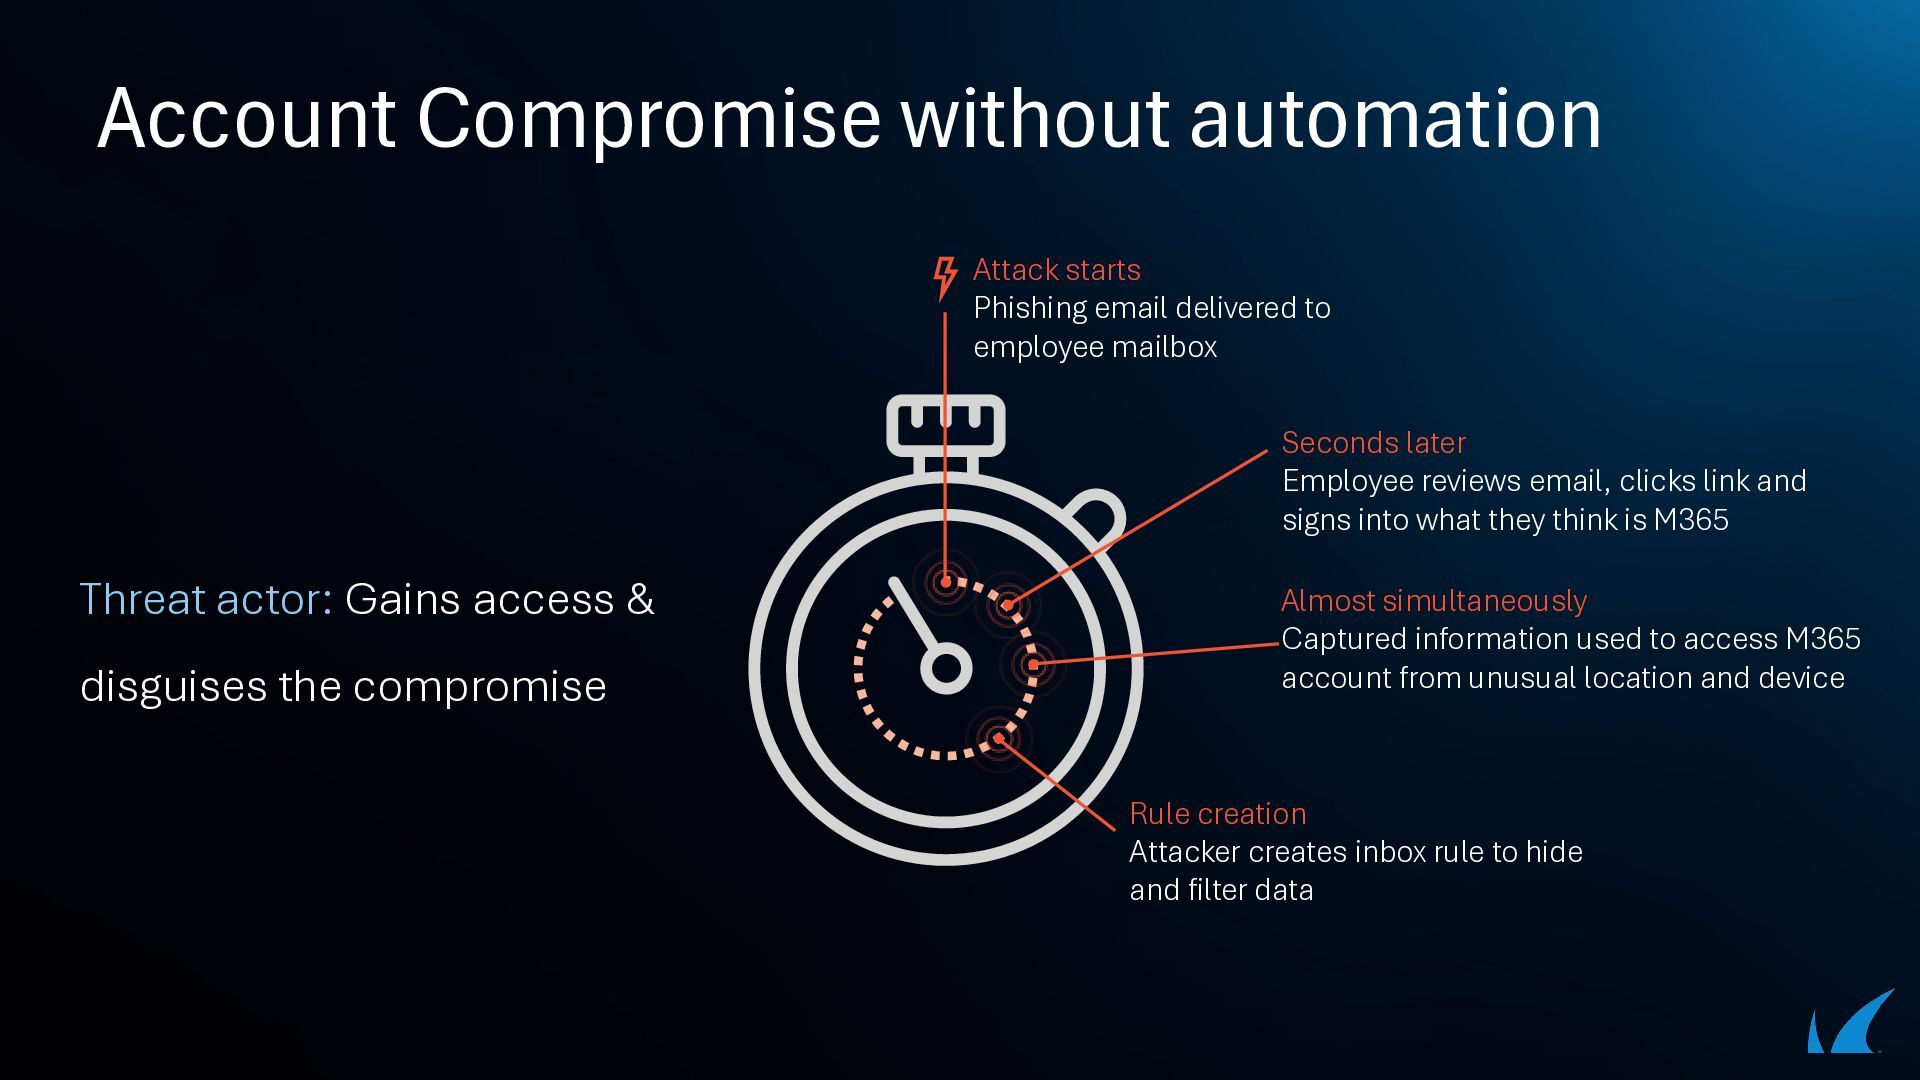
  130. Account Compromise without automation Attack starts Phishing email delivered to

    employee mailbox Seconds later Employee reviews email, clicks link and signs into what they think is M365 Threat actor: Gains access & disguises the compromise Almost simultaneously Captured information used to access M365 account from unusual location and device Rule creation Attacker creates inbox rule to hide and filter data
  131. Account Compromise without automation Phishing campaign detection IT administrator works

    with support to disable account & remediate email Attack starts Phishing email delivered to employee mailbox Seconds later Employee reviews email, clicks link and signs into what they think is M365 Days later Attacker uses mailbox to send Phishing campaign to suppliers and customers Critical oversight Over-stretched IT administrator overlooks security alert Almost simultaneously Captured information used to access M365 account from unusual location and device Rule creation Attacker creates inbox rule to hide and filter data Activity triggers security alert Detection solution detects suspicious location, device and rule activity
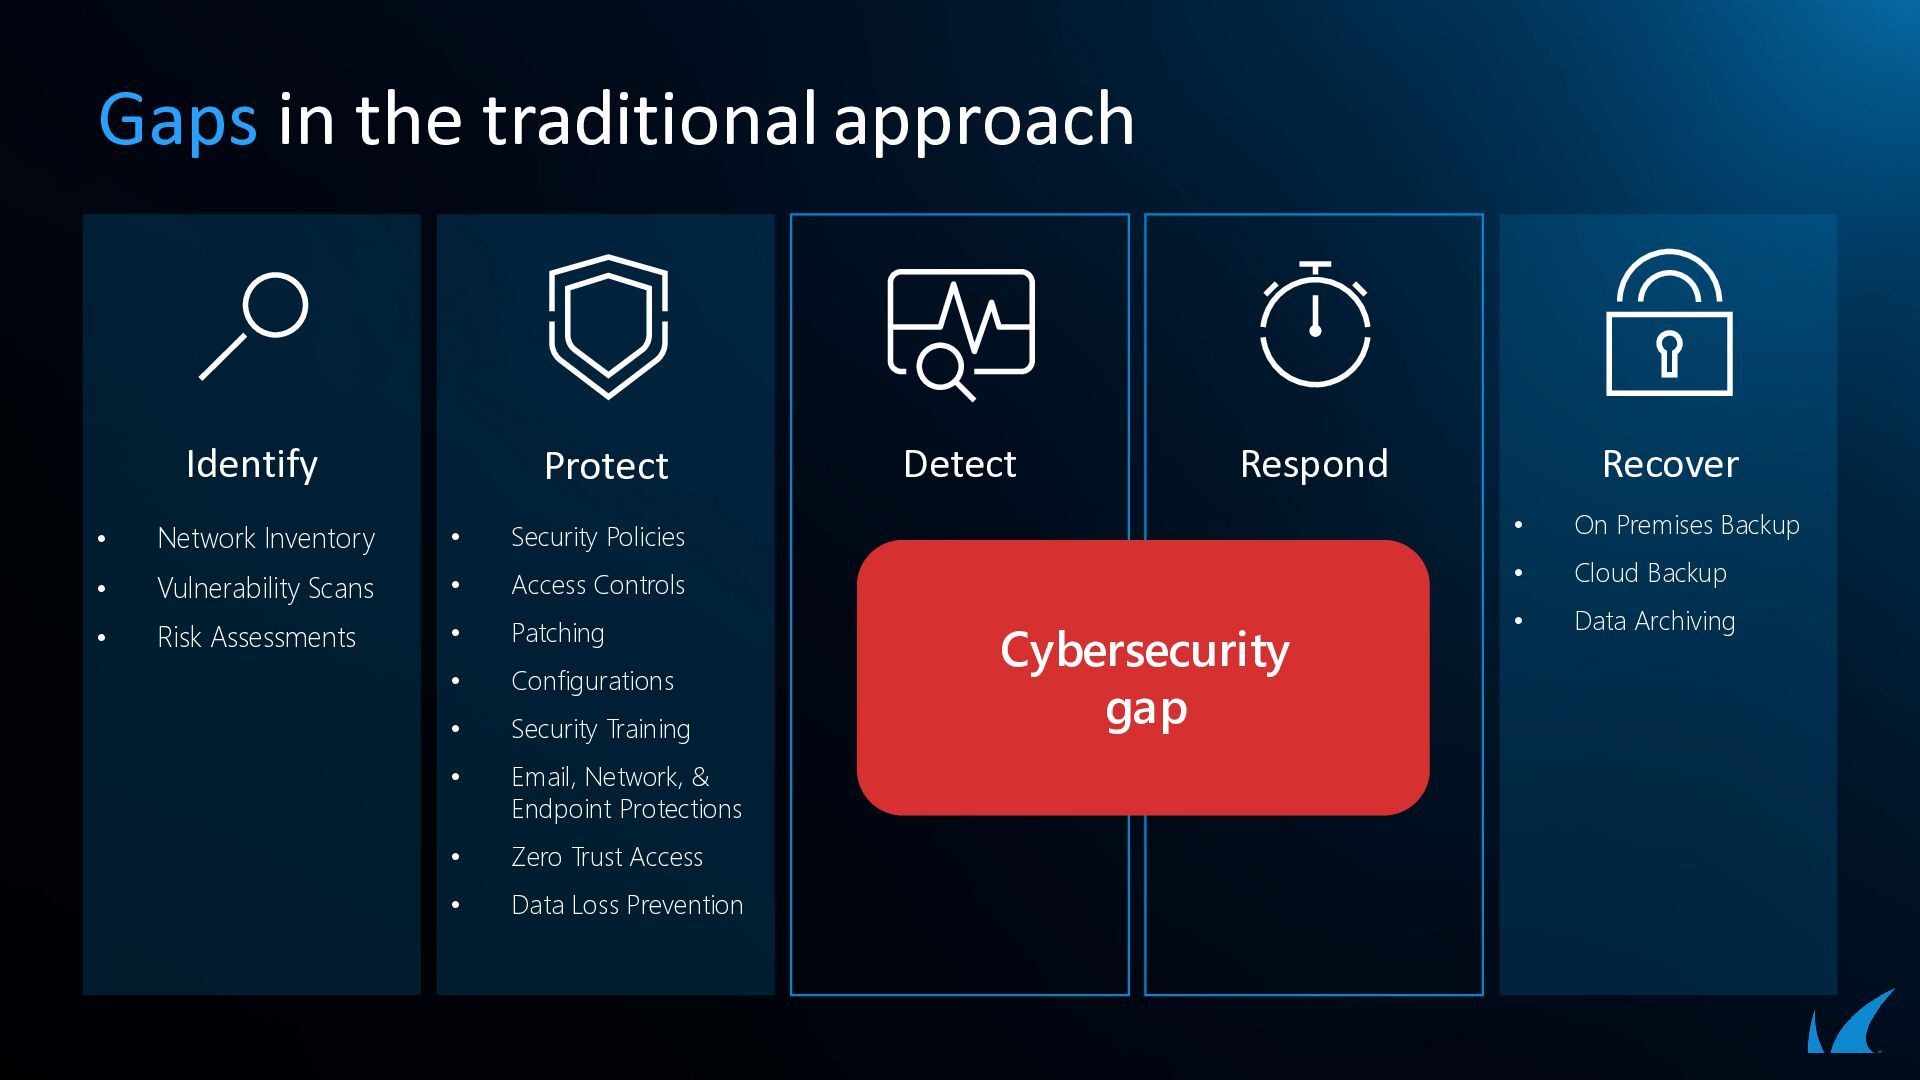
  132. Gaps in the traditional approach Identify Protect • Network Inventory

    • Security Policies • Vulnerability Scans • Access Controls • Risk Assessments • Patching • Configurations • Security Training • Email, Network, & Endpoint Protections • Zero Trust Access • Data Loss Prevention Detect Recover Respond Cybersecurity gap • On Premises Backup • Cloud Backup • Data Archiving
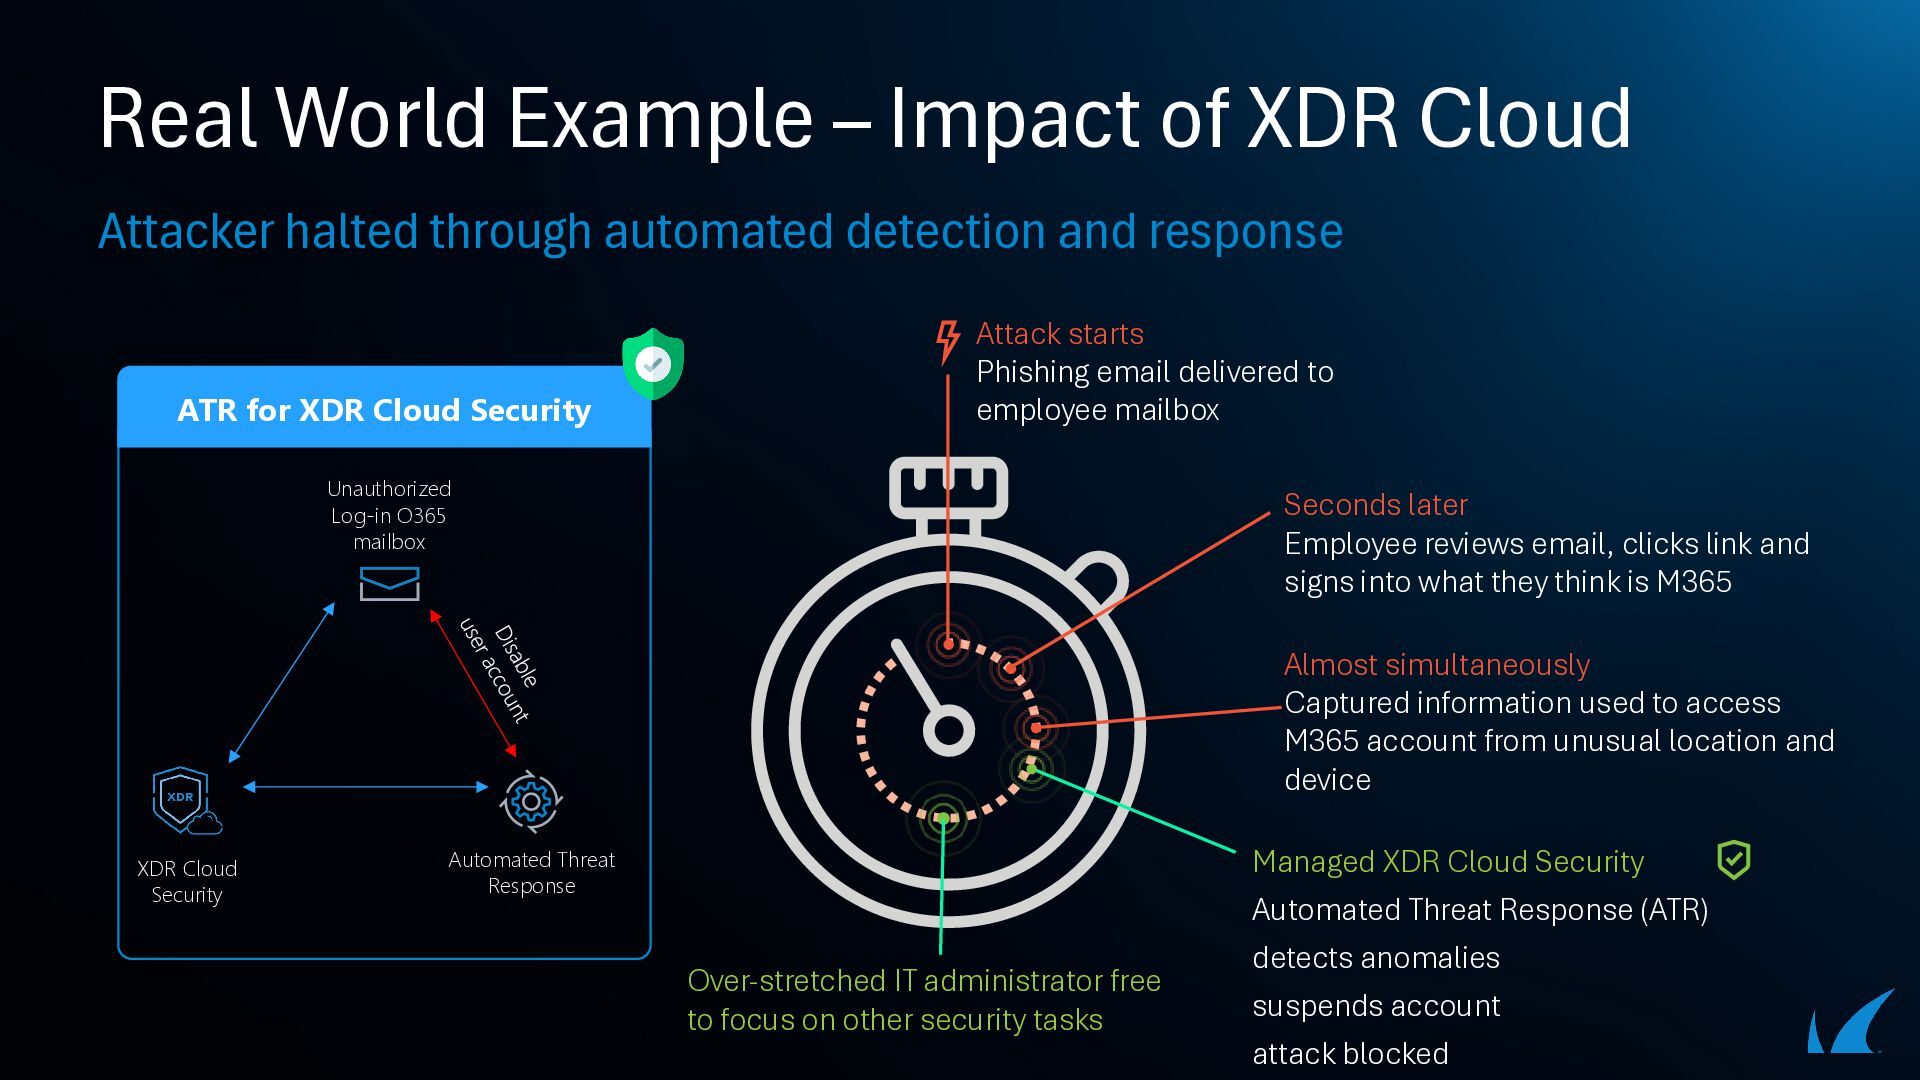
  133. Real World Example – Impact of XDR Cloud Attacker halted

    through automated detection and response ATR for XDR Cloud Security Attack starts Phishing email delivered to employee mailbox Unauthorized Log-in O365 mailbox Seconds later Employee reviews email, clicks link and signs into what they think is M365 Almost simultaneously Captured information used to access M365 account from unusual location and device XDR Cloud Security Automated Threat Response Managed XDR Cloud Security Automated Threat Response (ATR) Over-stretched IT administrator free to focus on other security tasks detects anomalies suspends account attack blocked
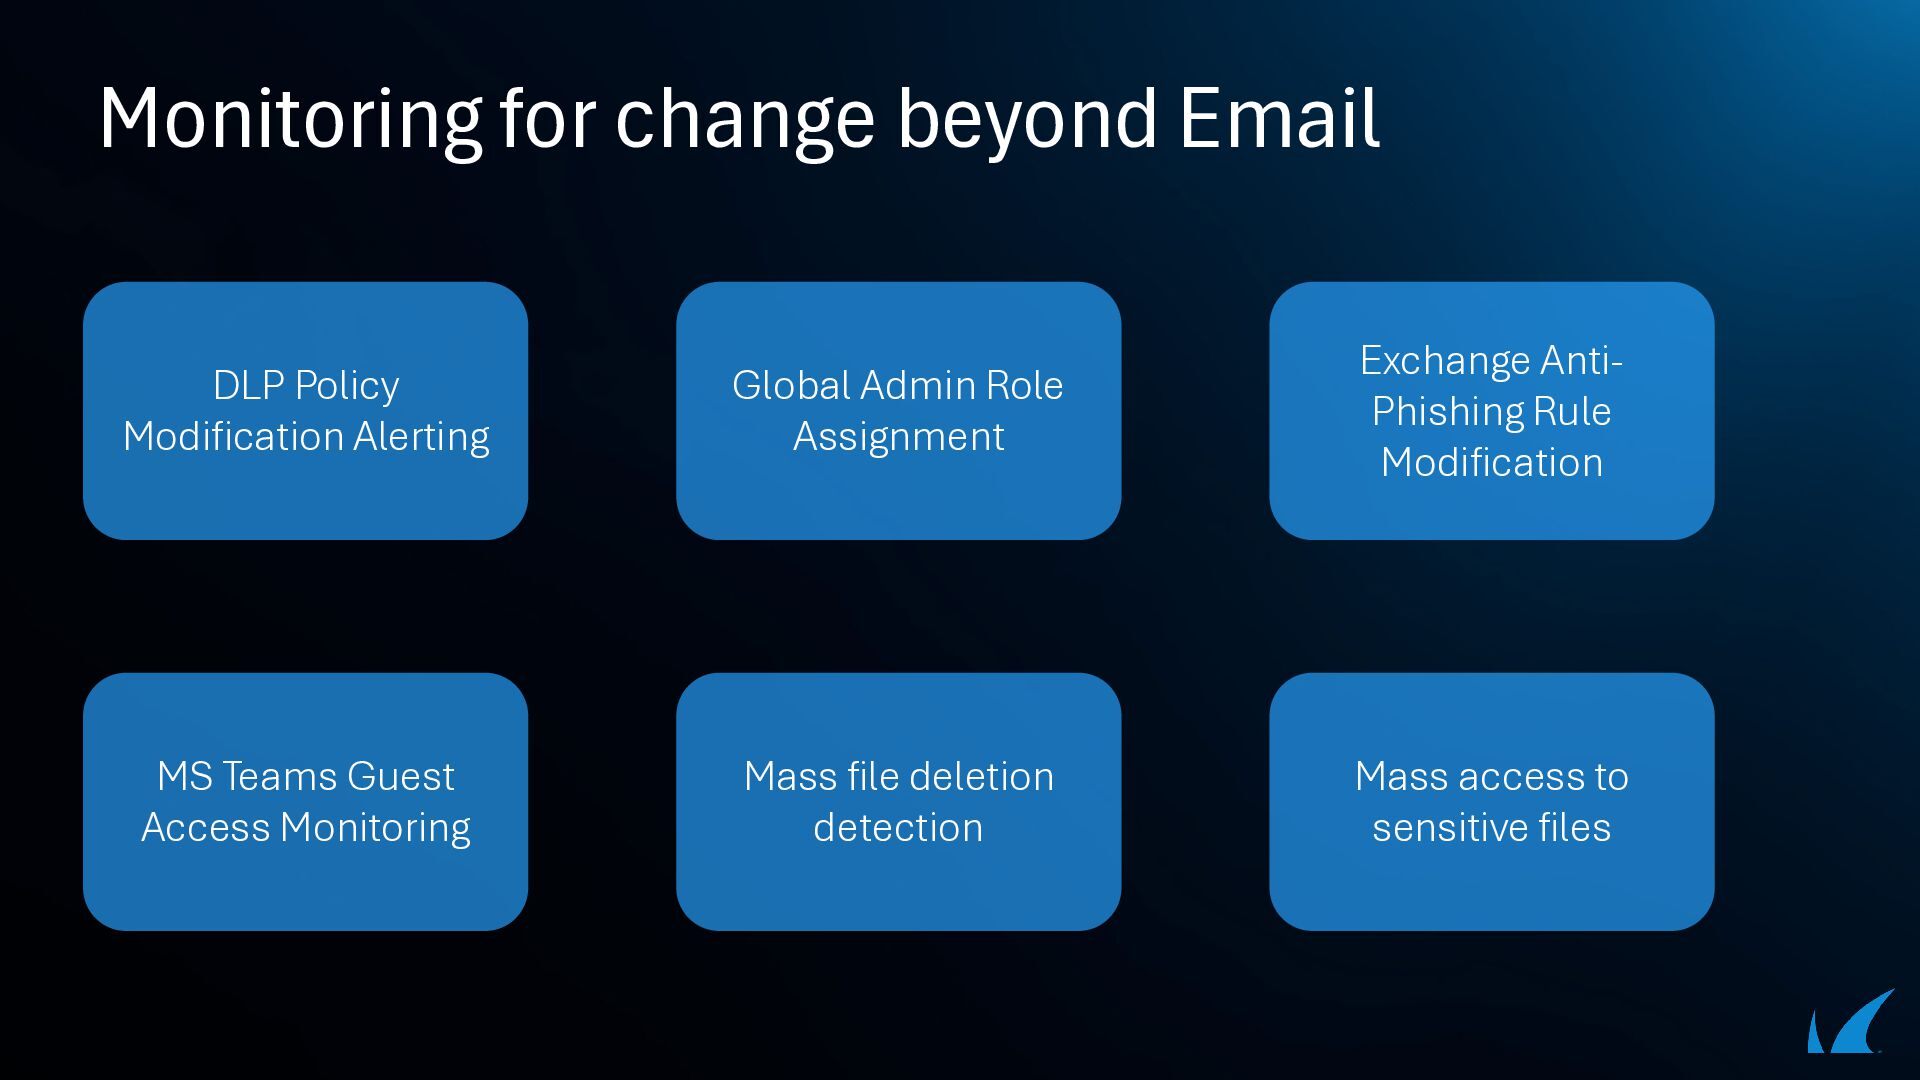
  134. Monitoring for change beyond Email DLP Policy Modification Alerting Global

    Admin Role Assignment Exchange AntiPhishing Rule Modification MS Teams Guest Access Monitoring Mass file deletion detection Mass access to sensitive files
  135. #CymruSec Lunch & Networking – See you at 13:35! Upcoming

    – Final Breakout Breakout E: Breakout F: Breakout G : Effective Cyber Security for SMEs AI – The Current Threat Landscape MCP: Don’t Shoot the Messenger Chairmans Suite 13:35 Ricoh Suite 13:35 This Room 13:35
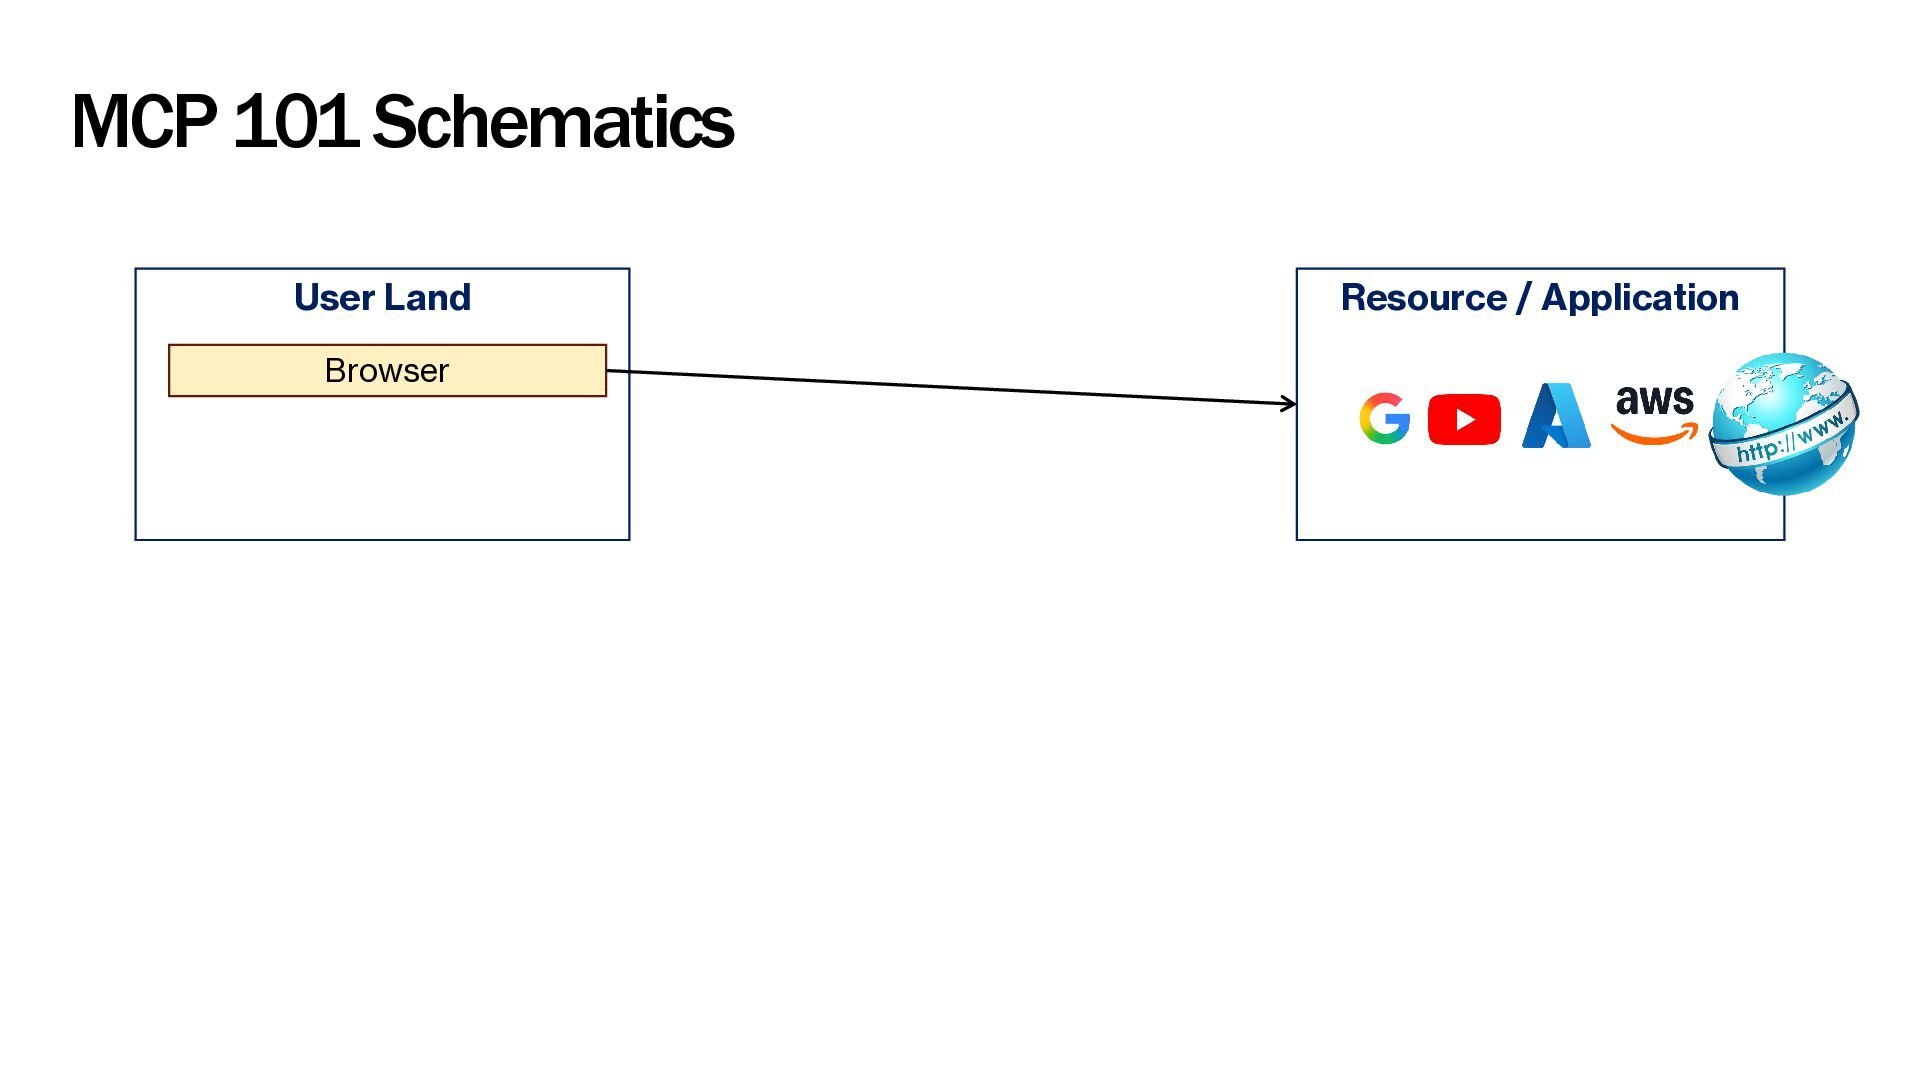
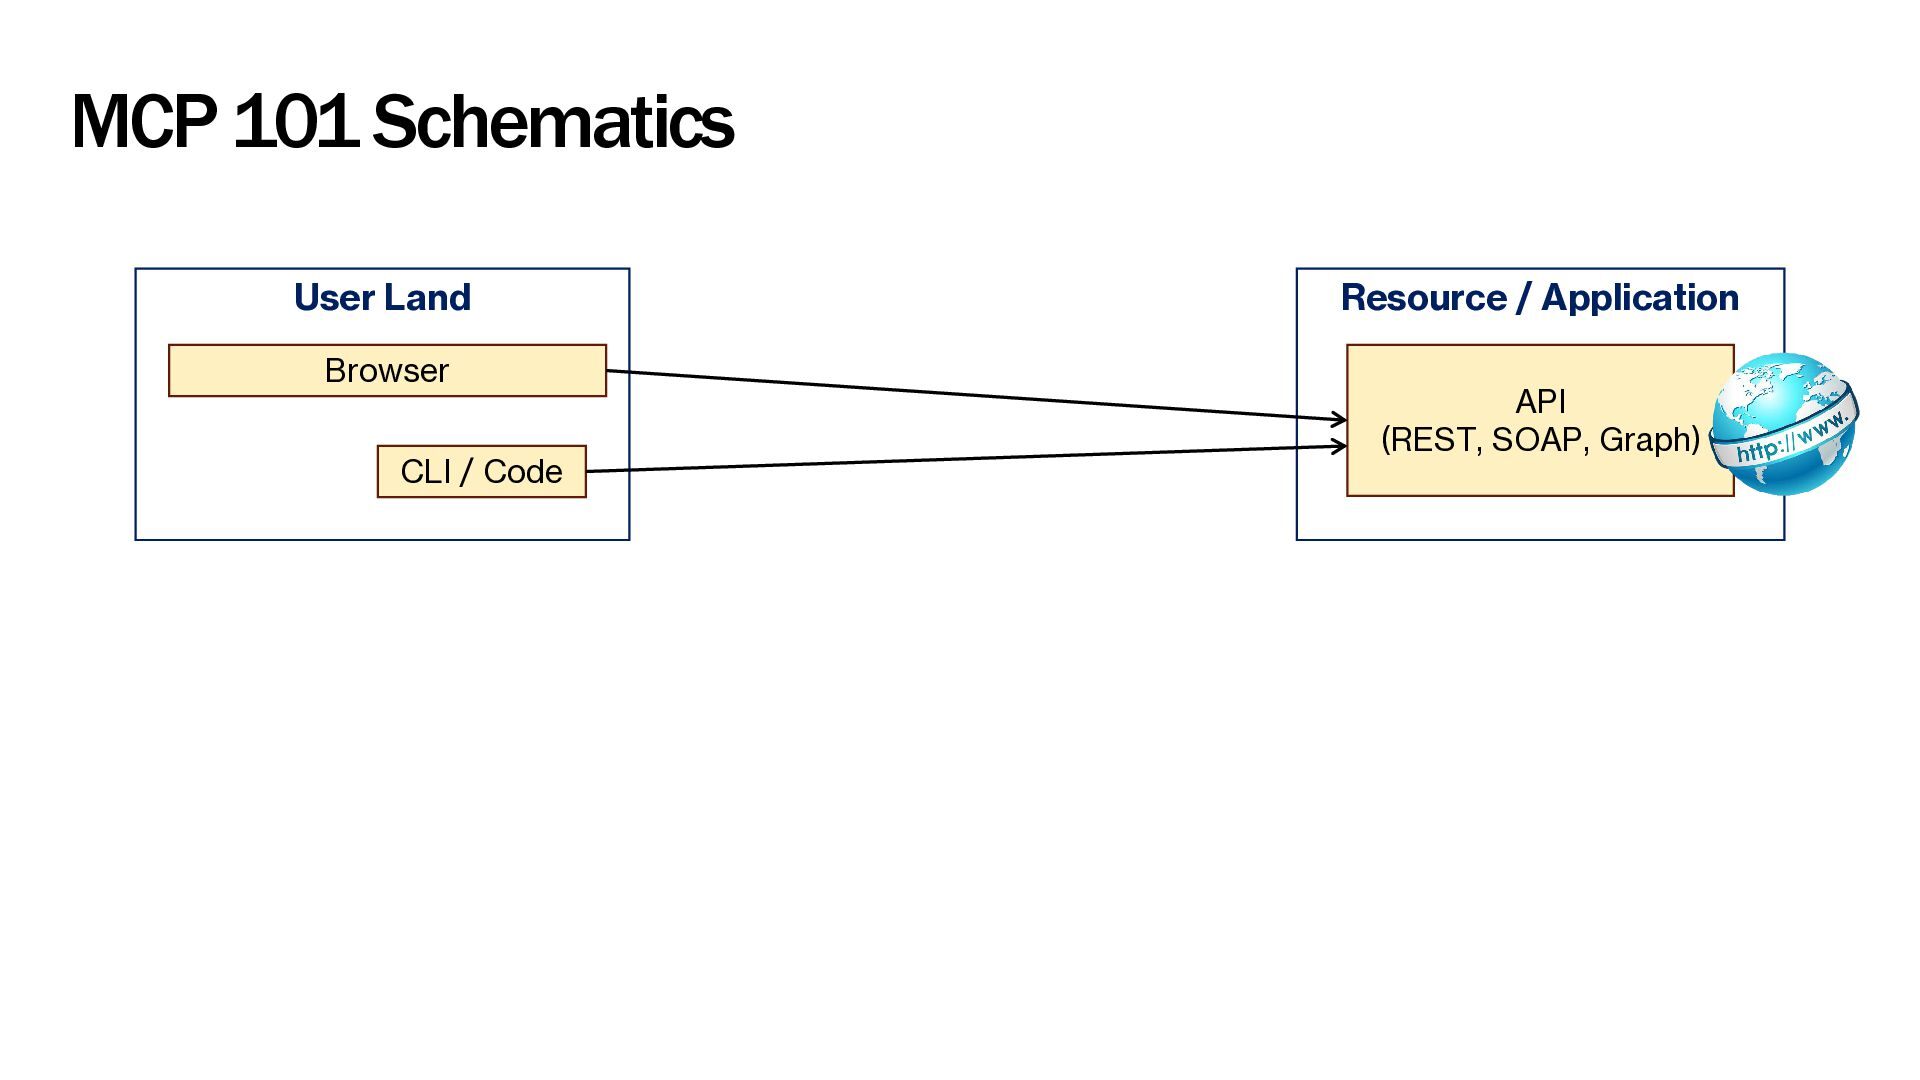
  136. MCP 101 Schematics User Land Browser CLI / Code Resource

    / Application API (REST, SOAP, Graph)
  137. MCP 101 Schematics User Land Resource / Application Browser AI

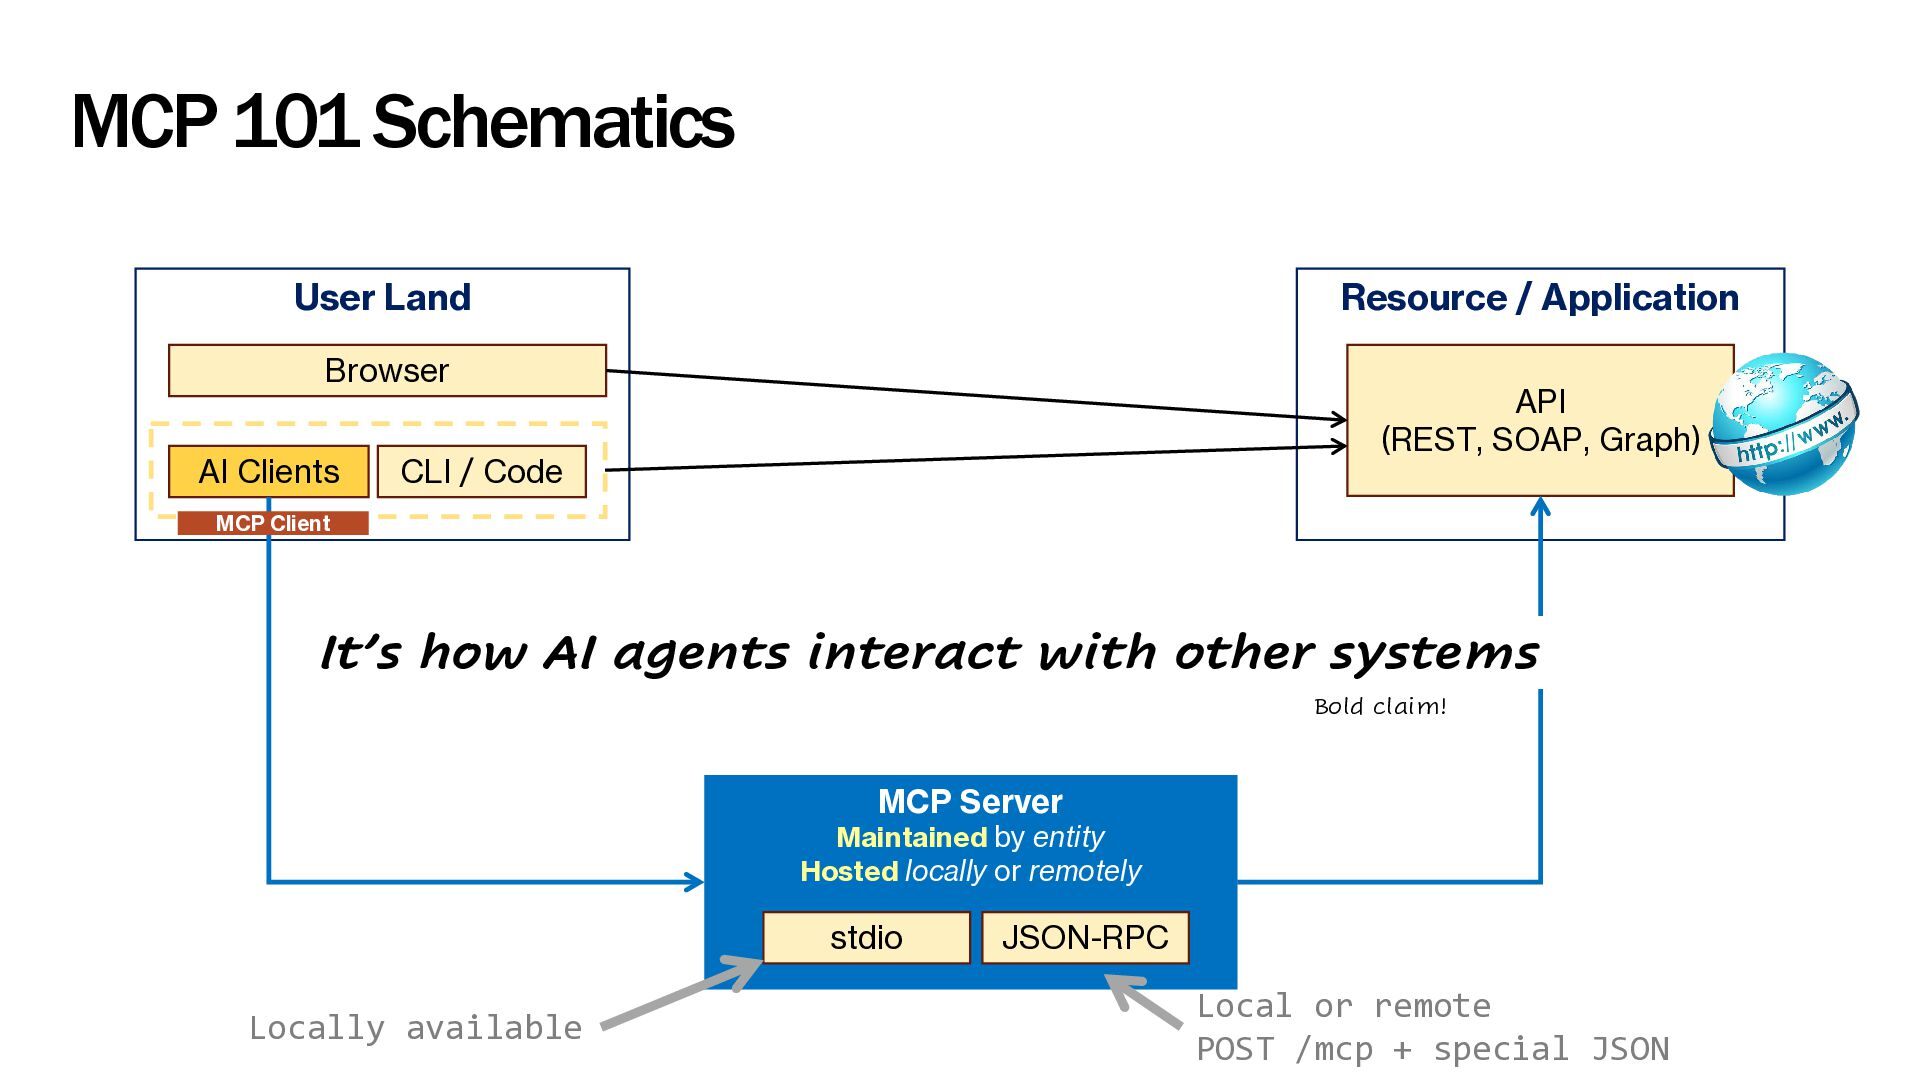
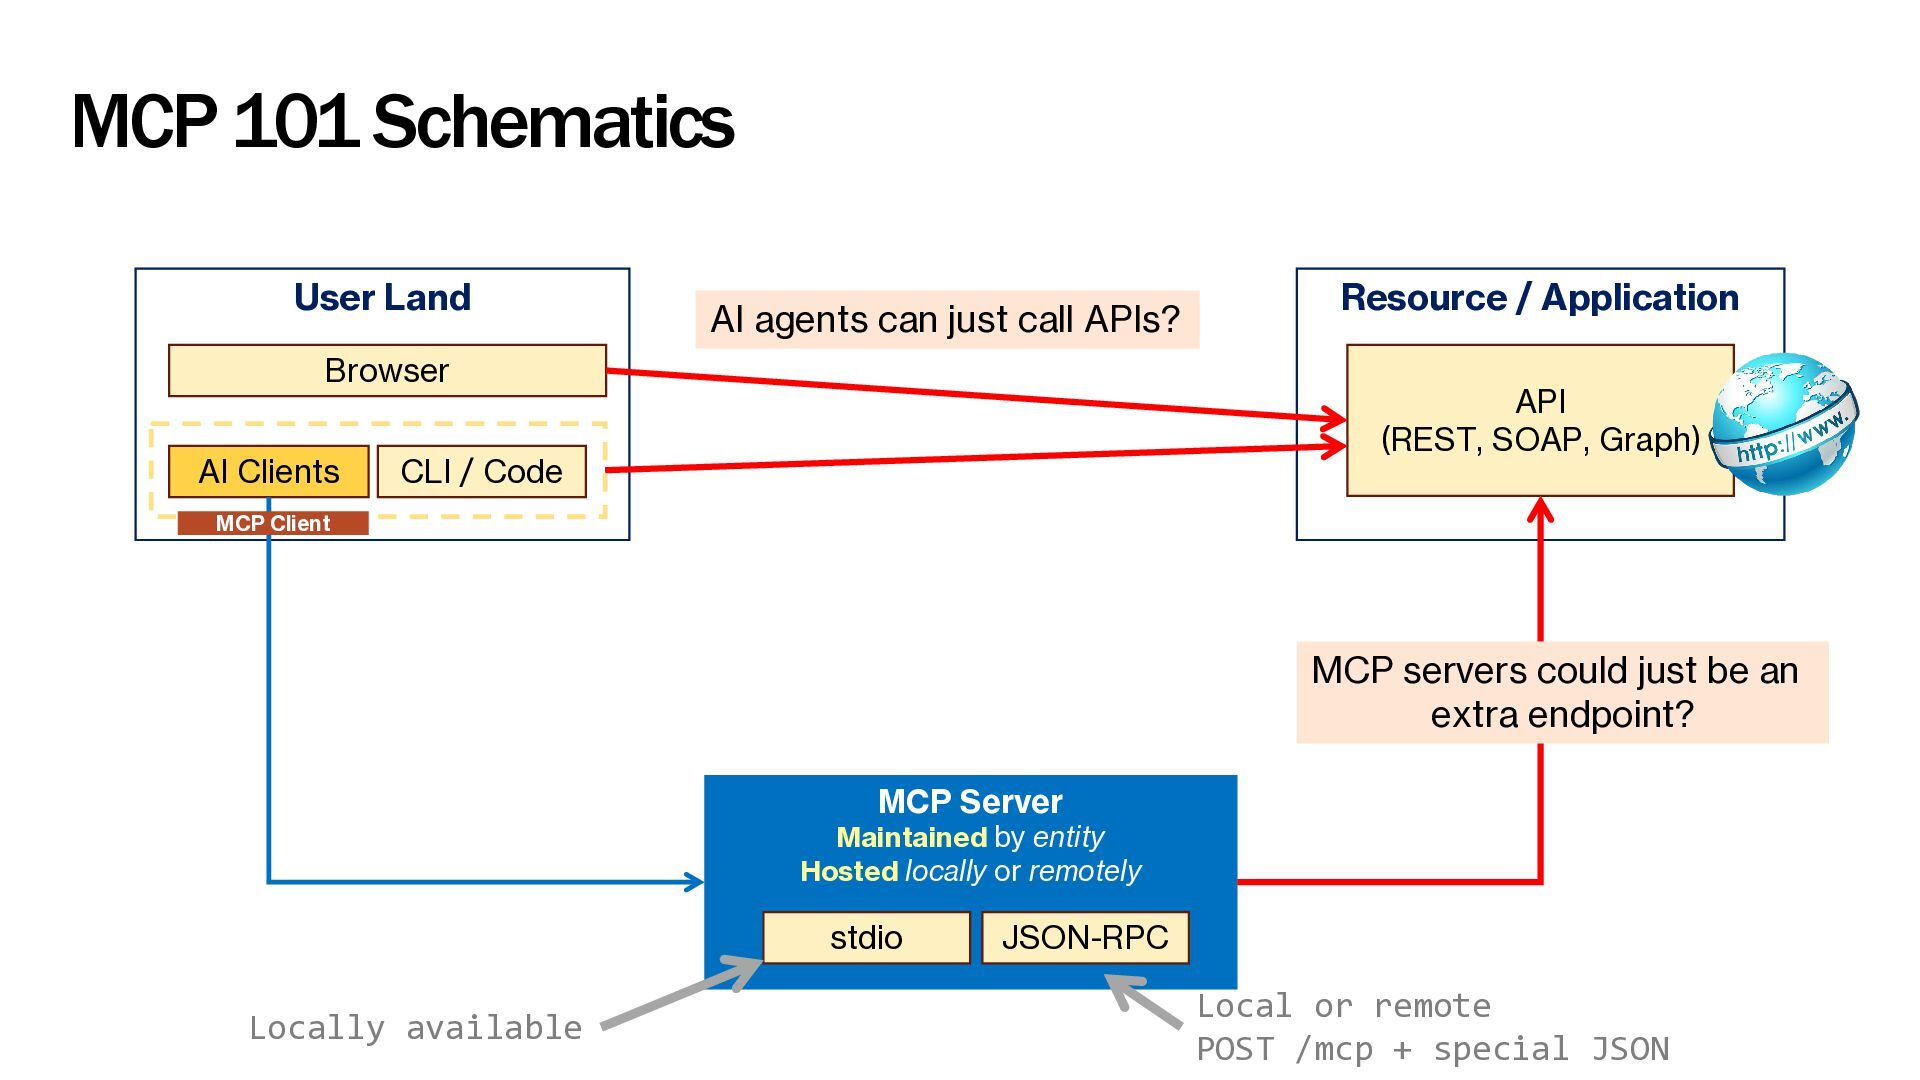
    Clients API (REST, SOAP, Graph) CLI / Code MCP Client It’s how agents interact other systems It’sAI how AI agents interact with with other systems Bold claim! MCP Server Maintained by entity Hosted locally or remotely stdio Locally available JSON-RPC Local or remote POST /mcp + special JSON
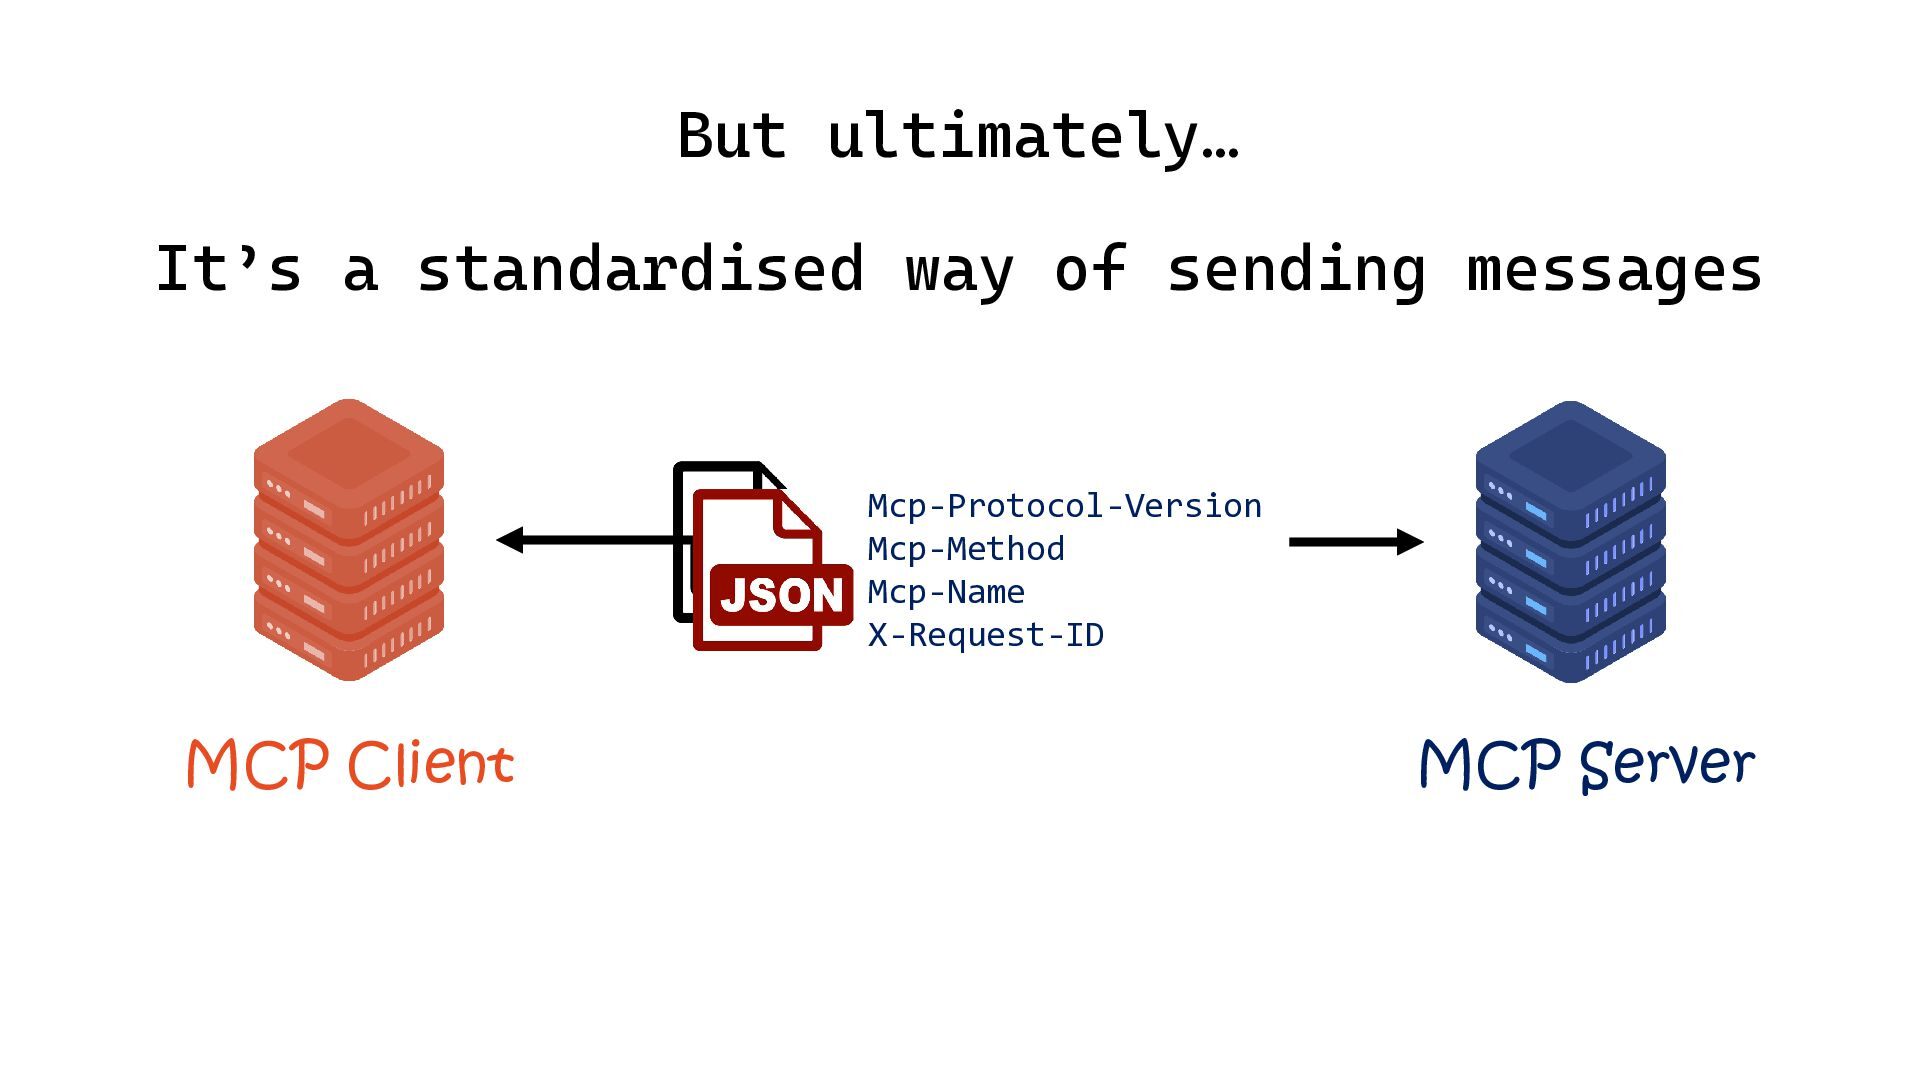
  138. But ultimately… It’s a standardised way of sending messages Mcp-Protocol-Version

    Mcp-Method Mcp-Name X-Request-ID MCP Client MCP Server
  139. MCP 101 Schematics User Land AI agents can just call

    APIs? Browser AI Clients Resource / Application API (REST, SOAP, Graph) CLI / Code MCP Client MCP servers could just be an extra endpoint? MCP Server Maintained by entity Hosted locally or remotely stdio Locally available JSON-RPC Local or remote POST /mcp + special JSON
  140. Agenda • Model Context Protocol 101 • Considerations – Context

    is king • AI Client Usage Evolution • MCP to enable safe automation
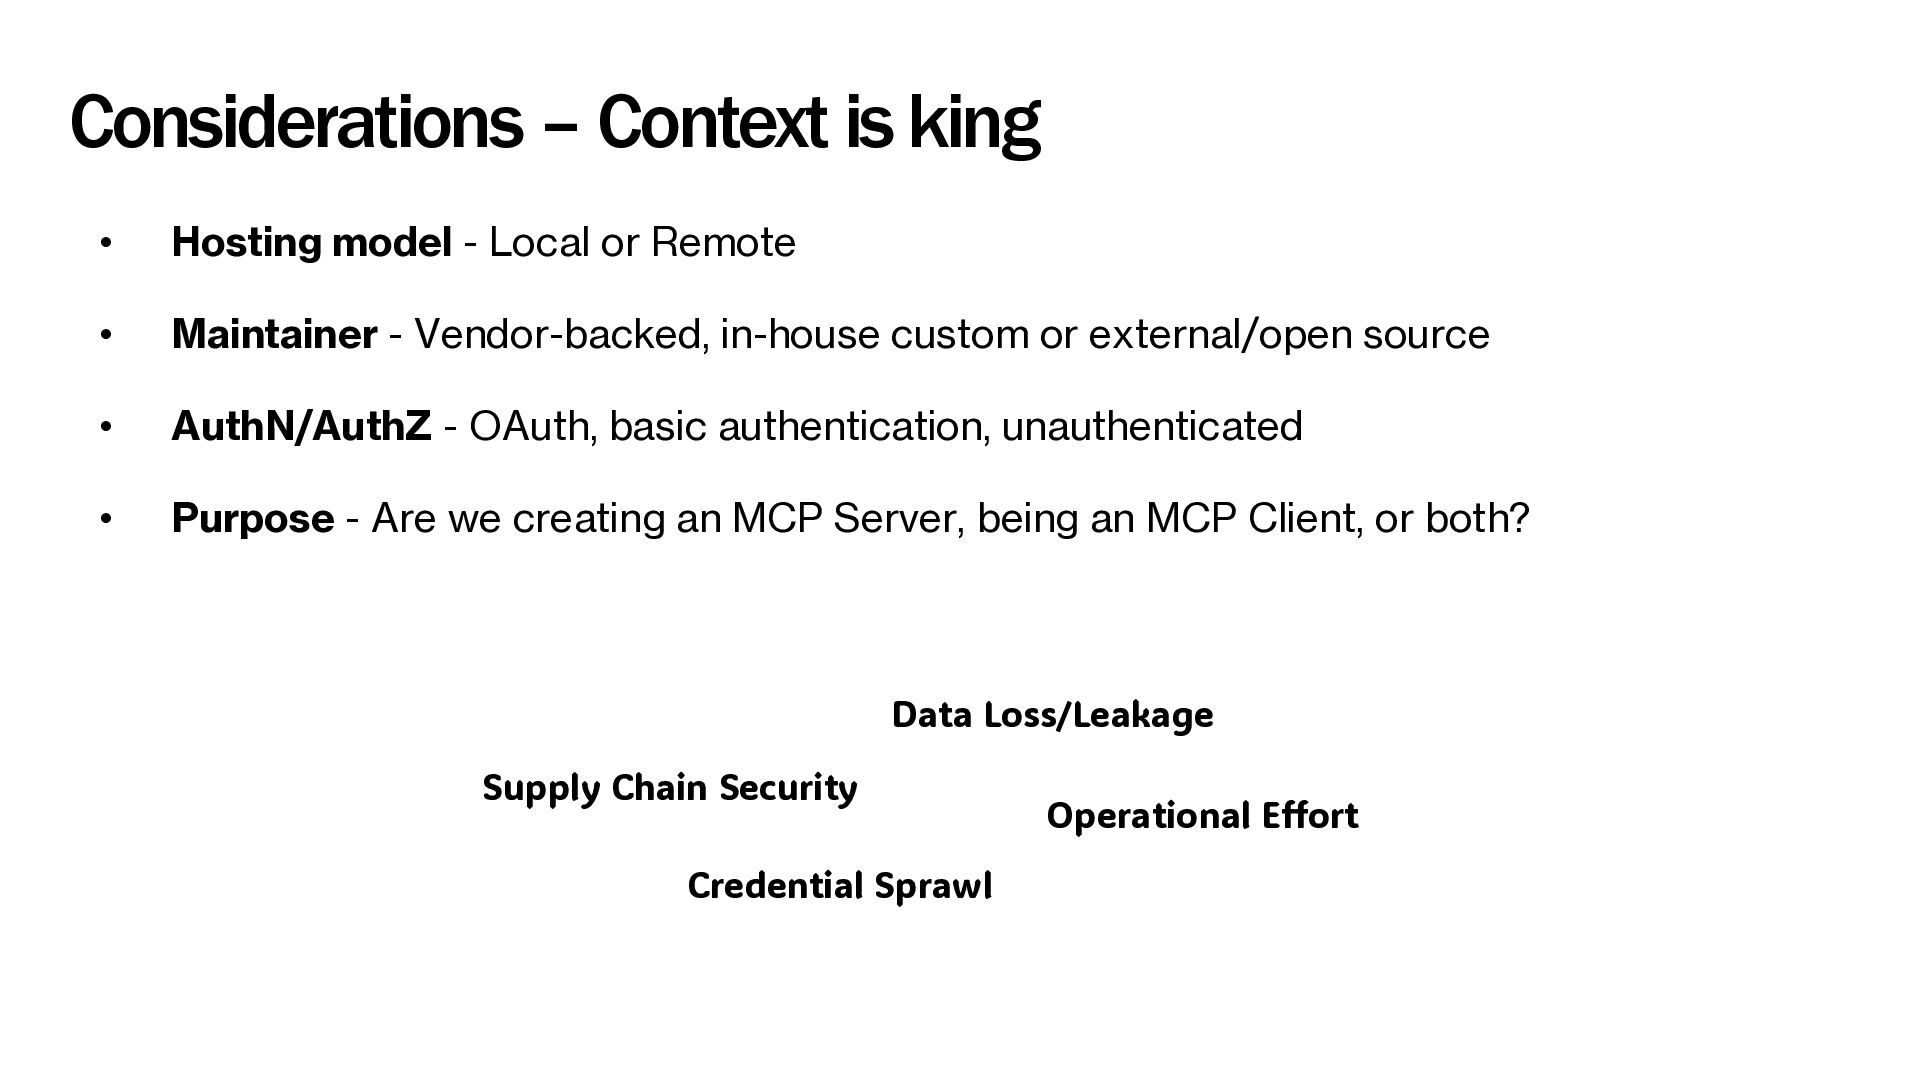
  141. Considerations – Context is king • Hosting model - Local

    or Remote • Maintainer - Vendor-backed, in-house custom or external/open source • AuthN/AuthZ - OAuth, basic authentication, unauthenticated • Purpose - Are we creating an MCP Server, being an MCP Client, or both? Data Loss/Leakage Supply Chain Security Credential Sprawl Operational Effort
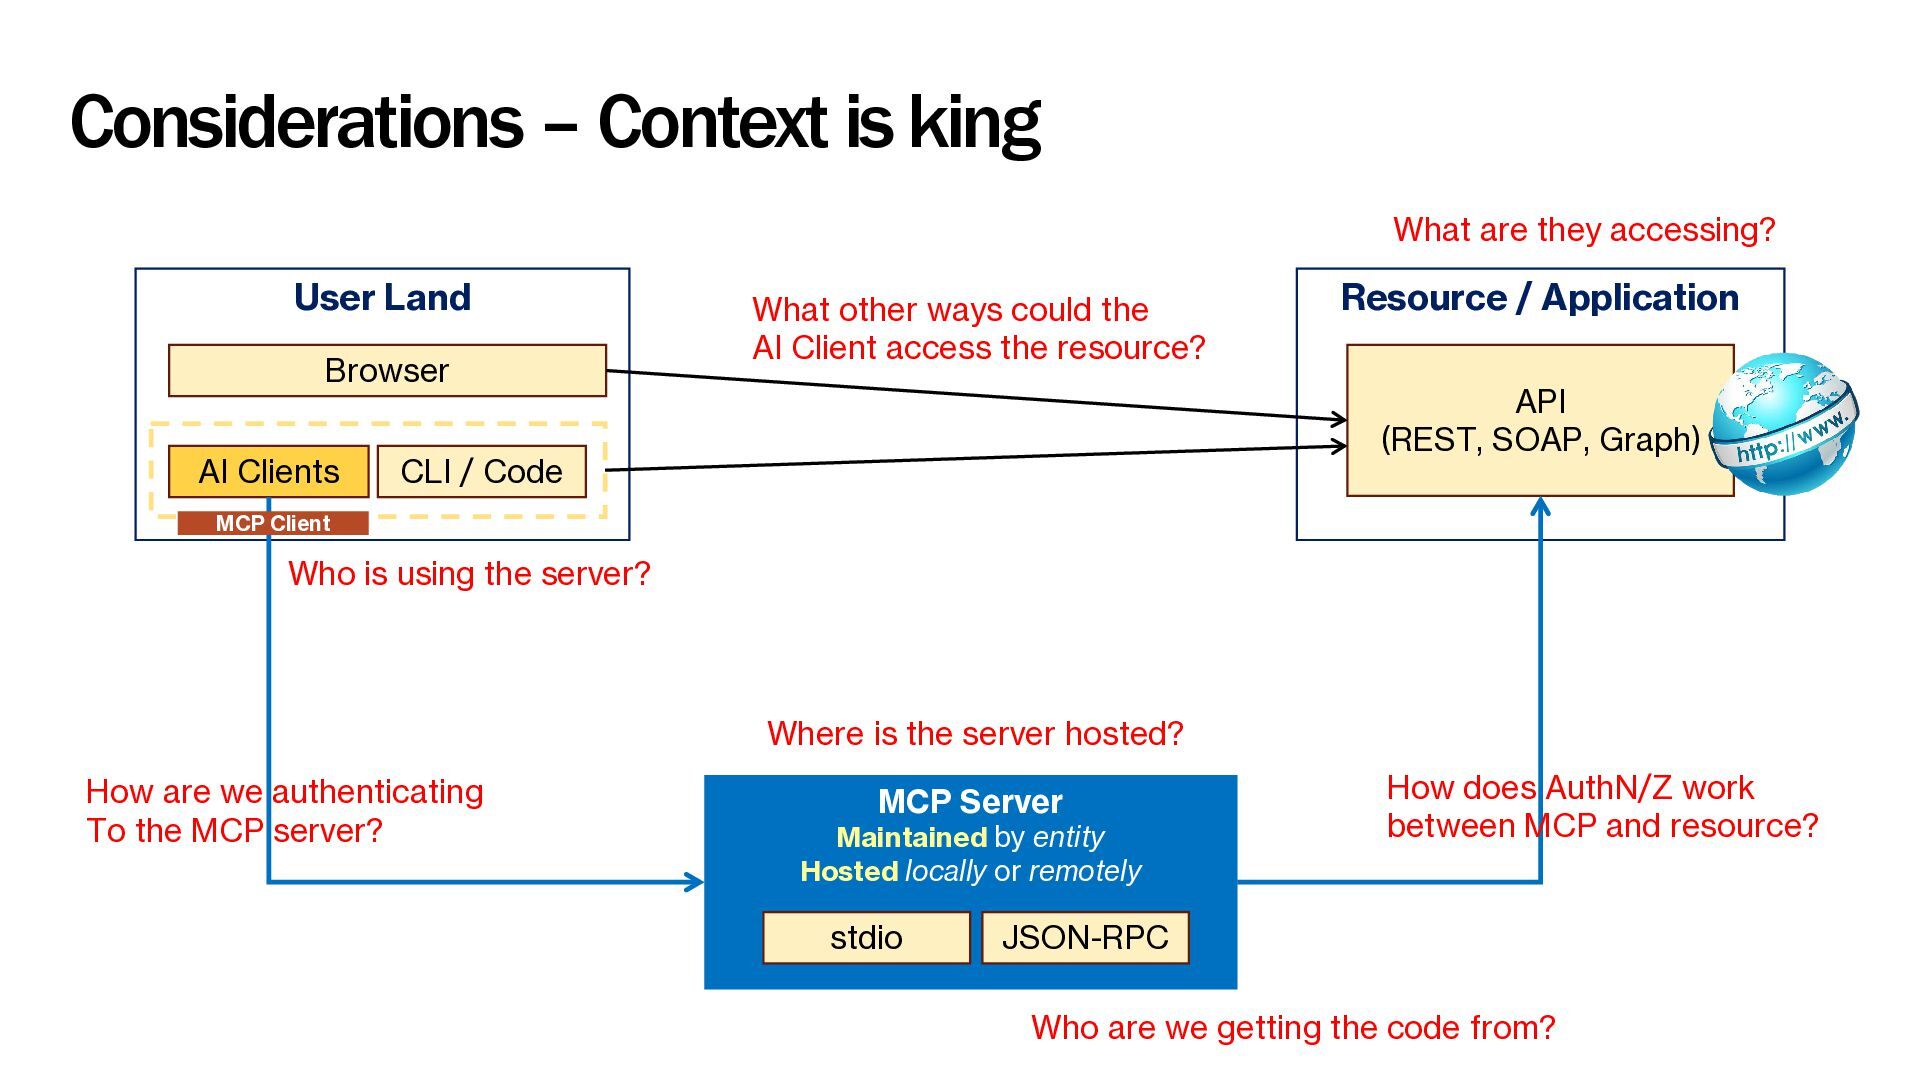
  142. Considerations – Context is king What are they accessing? User

    Land Browser AI Clients What other ways could the AI Client access the resource? Resource / Application API (REST, SOAP, Graph) CLI / Code MCP Client Who is using the server? Where is the server hosted? How are we authenticating To the MCP server? MCP Server Maintained by entity Hosted locally or remotely stdio How does AuthN/Z work between MCP and resource? JSON-RPC Who are we getting the code from?
  143. In summary, model your system and use case to understand

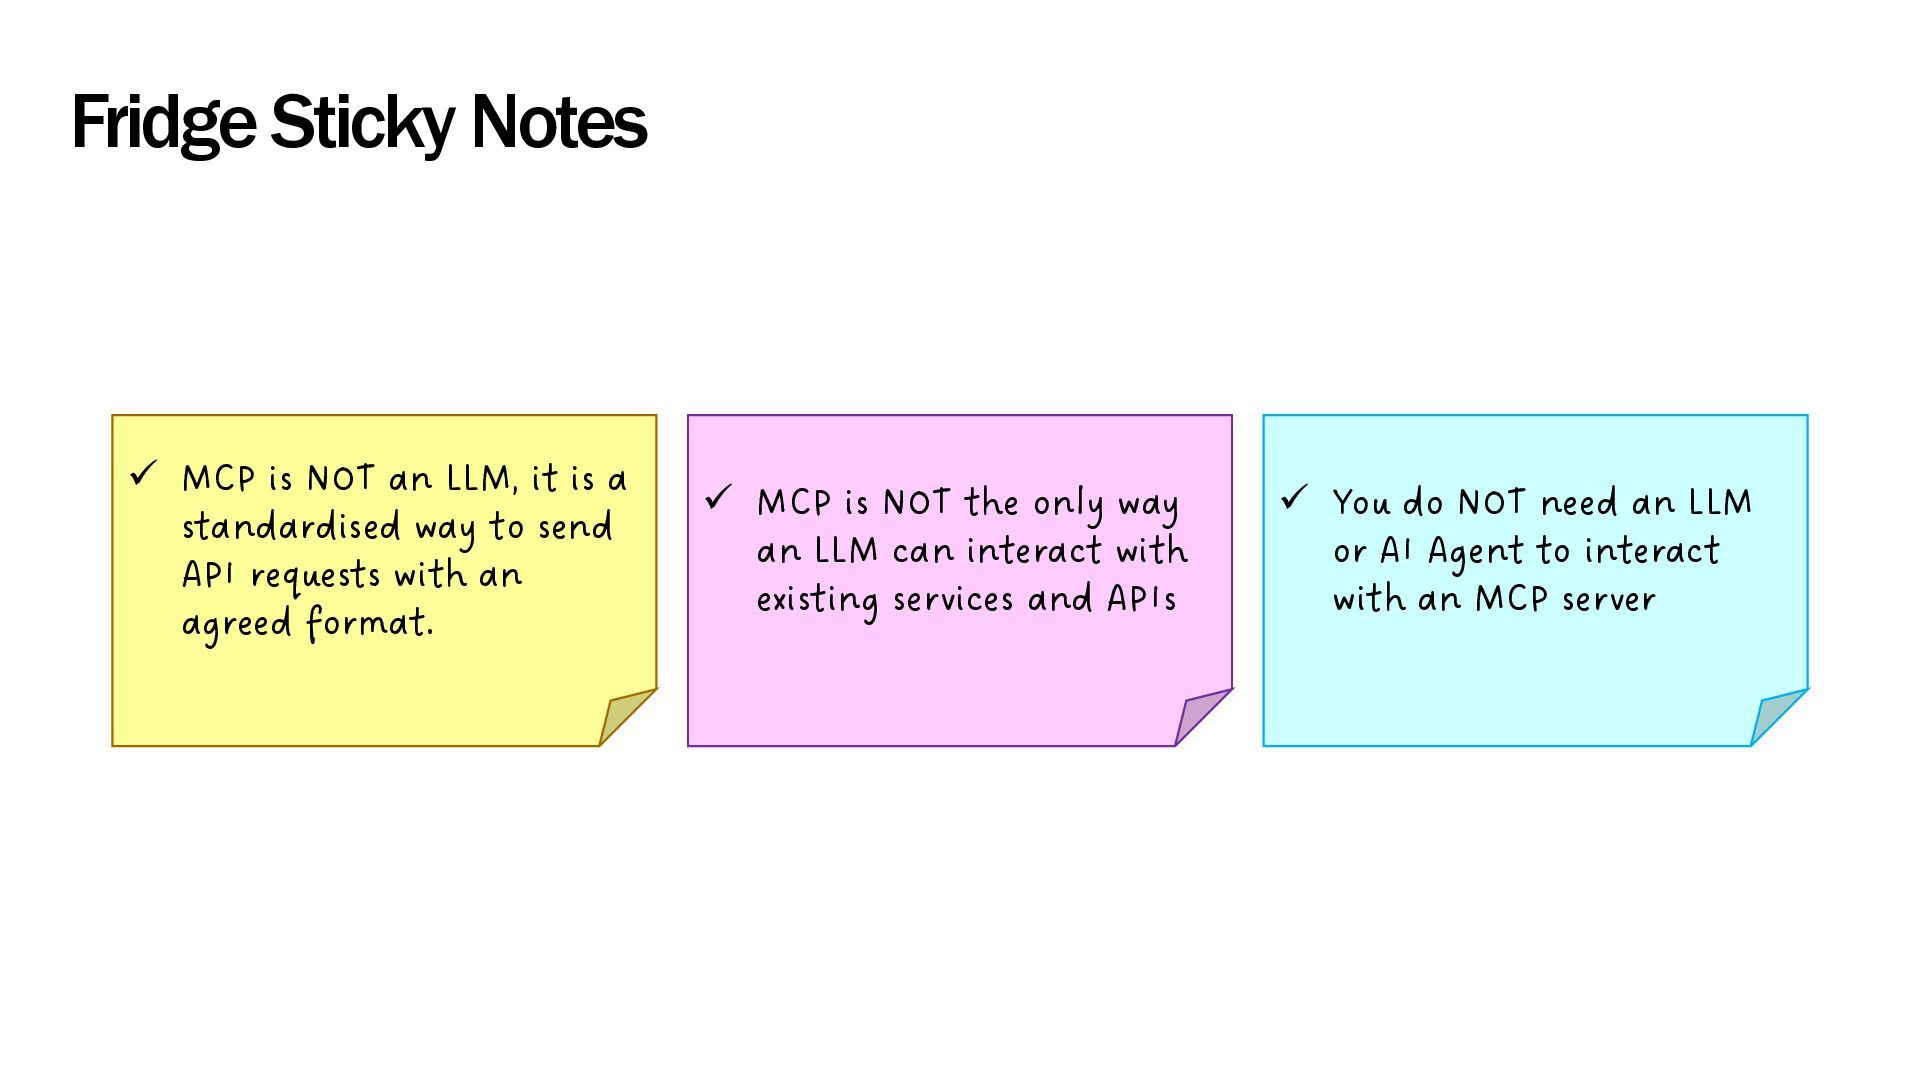
    where are the risks  MCP is NOT an LLM, it is a standardised way to send API requests with an agreed format.  You do NOT need an LLM or AI Agent to interact with an MCP server  MCP is NOT the only way an LLM can interact with existing services and APIs Having this into account… Let’s move on to a bit of history
  144. AI Client Usage Evolution My experience went a little bit

    like this: 1. Local files: Users start by giving AI clients local data, code and documents, which they must keep up to date. 2. API scripts: Users then ask for scripts to retrieve and process API data for the AI to use. 3. Direct API access: Finally, AI clients access APIs and run workflows themselves, removing the need for users to retrieve the data separately MCP seems to address (3), how AI clients can interact directly with other systems.
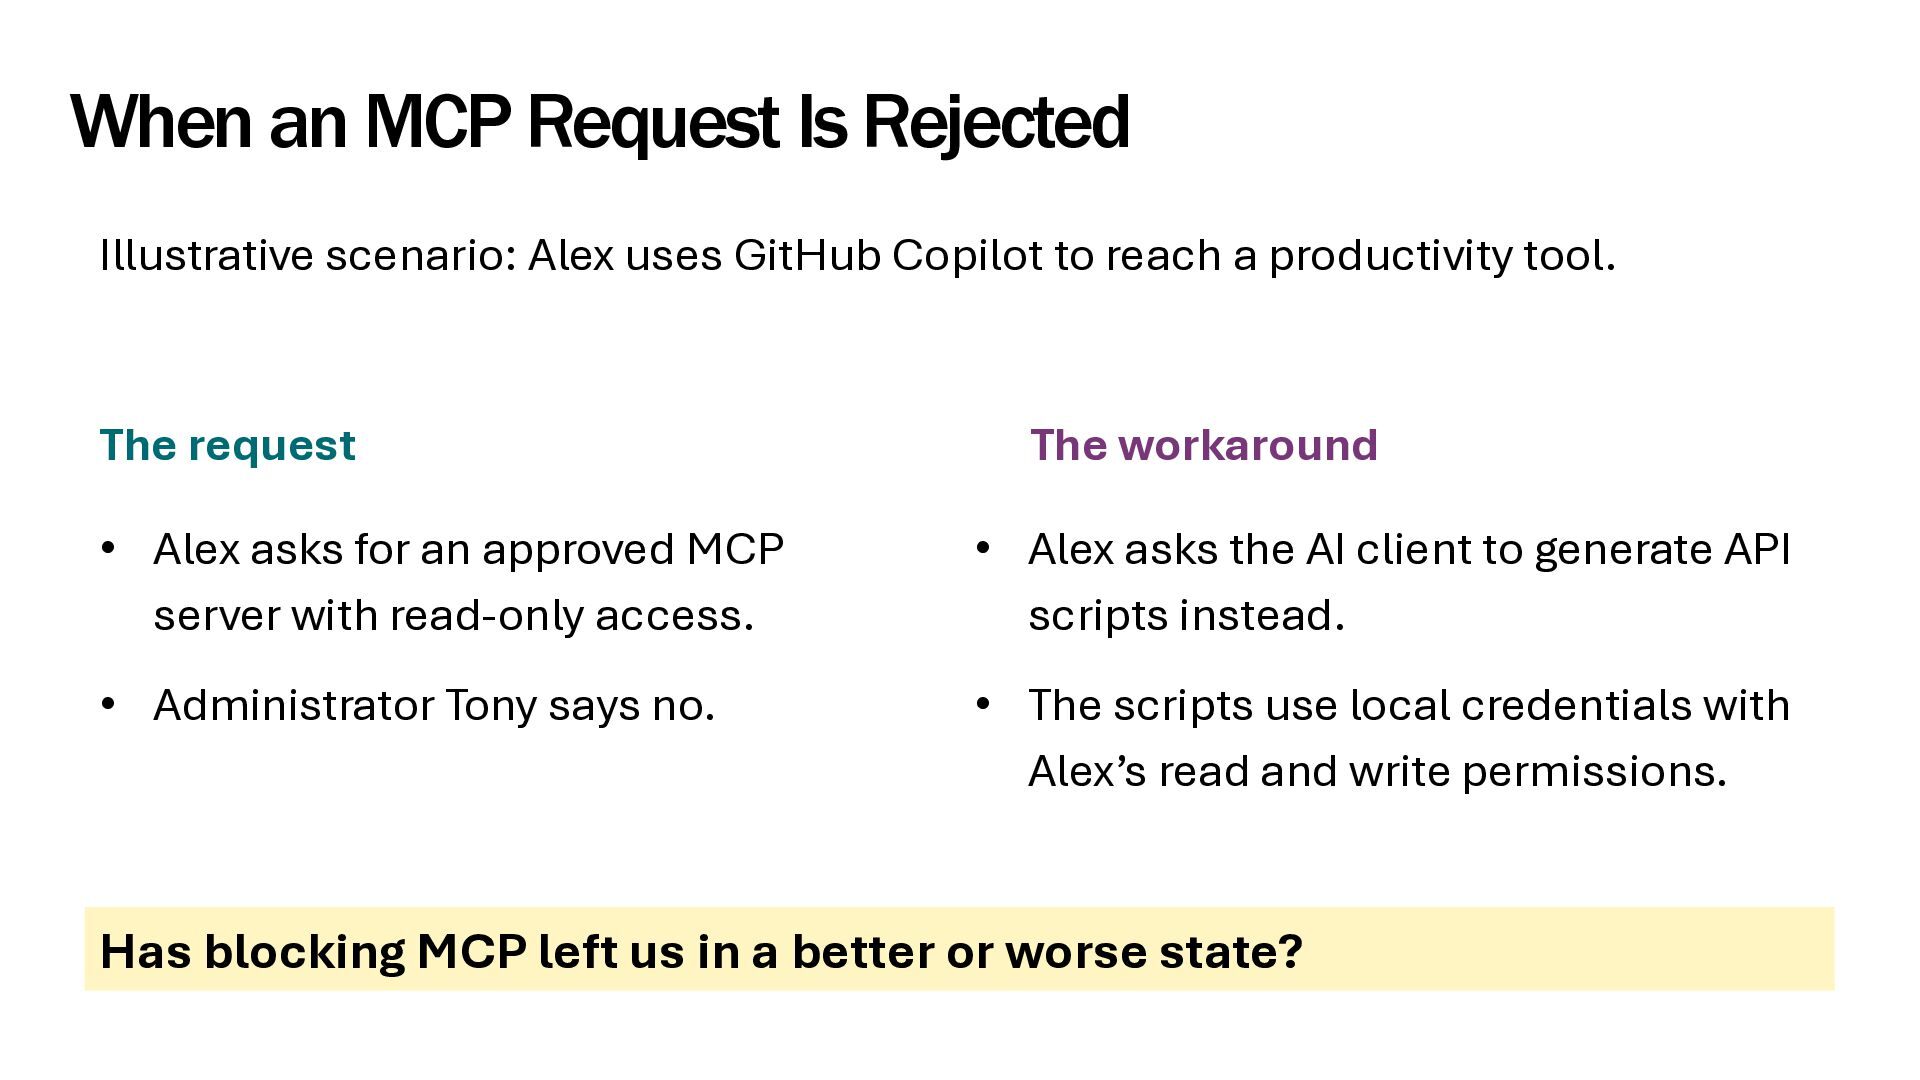
  145. When an MCP Request Is Rejected Illustrative scenario: Alex uses

    GitHub Copilot to reach a productivity tool. The request The workaround • Alex asks for an approved MCP server with read-only access. • Alex asks the AI client to generate API scripts instead. • Administrator Tony says no. • The scripts use local credentials with Alex’s read and write permissions. Has blocking MCP left us in a better or worse state?
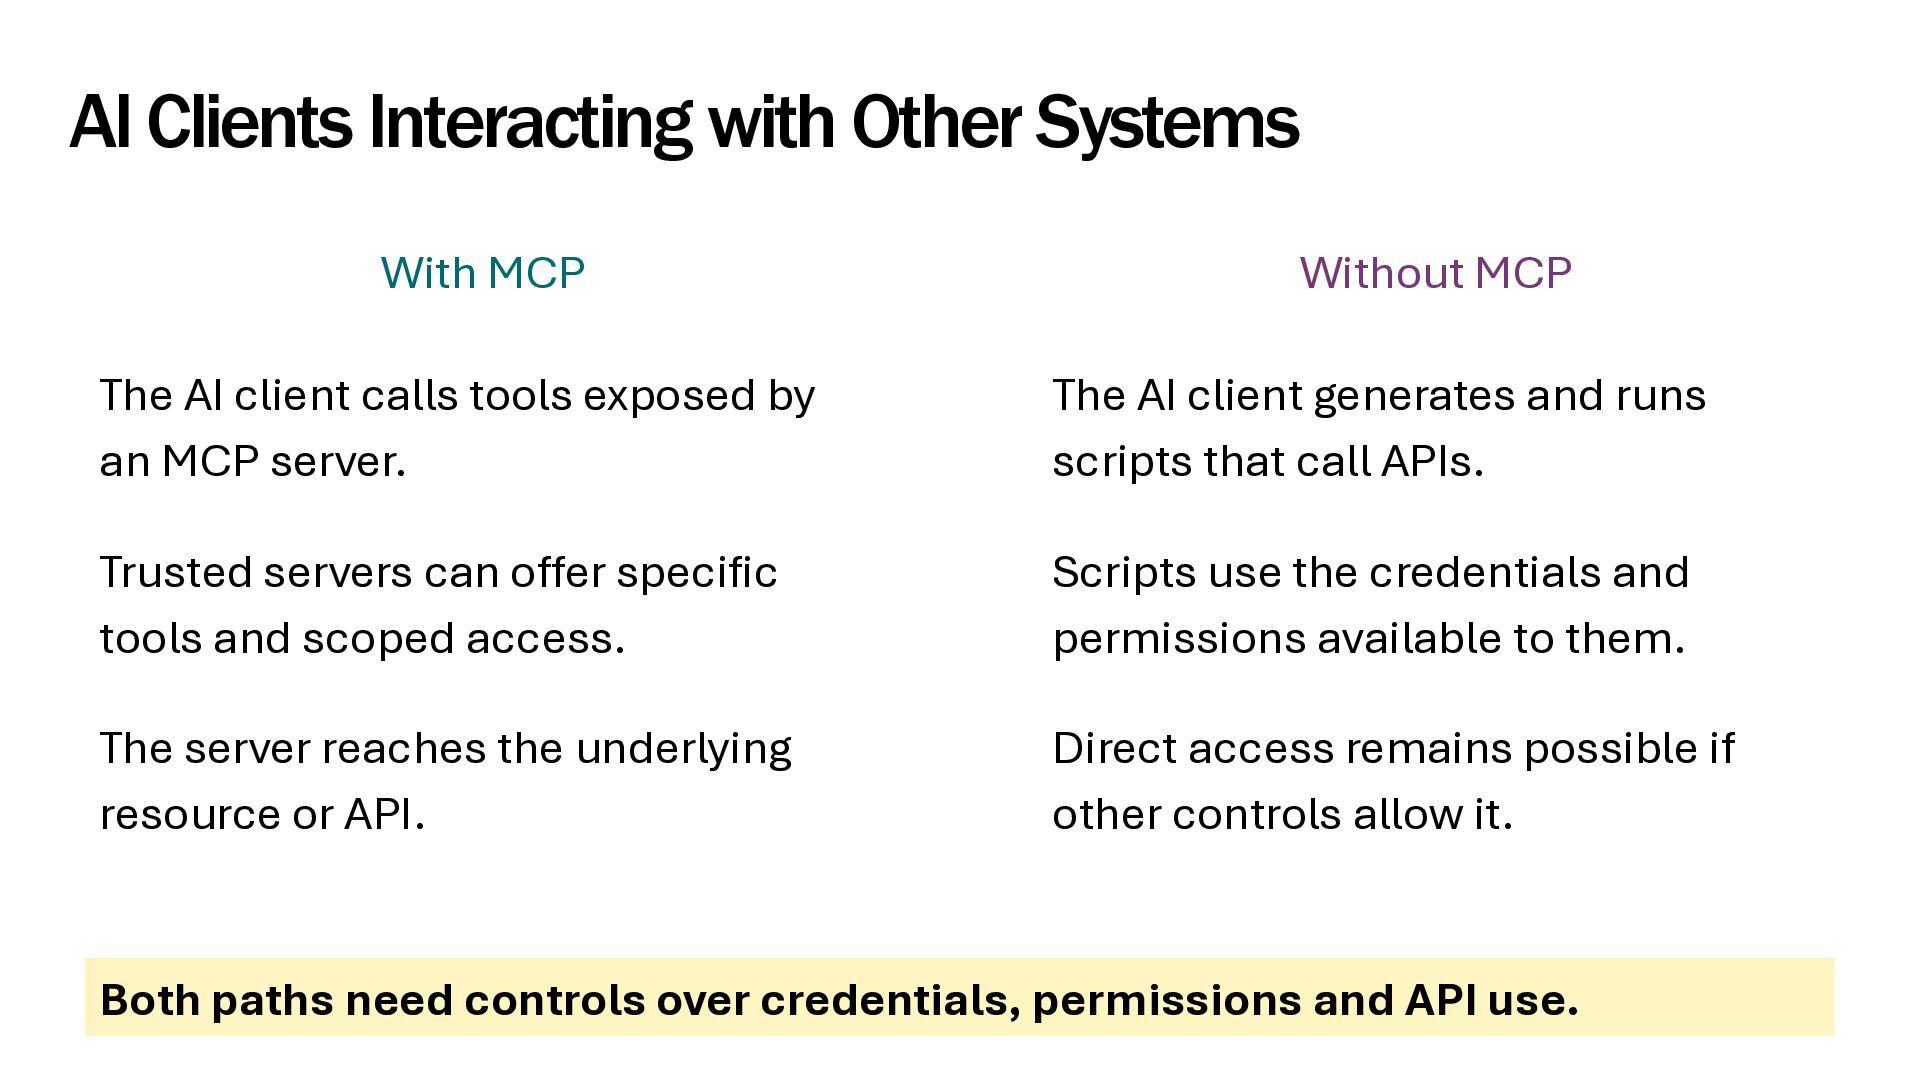
  146. AI Clients Interacting with Other Systems With MCP Without MCP

    The AI client calls tools exposed by an MCP server. The AI client generates and runs scripts that call APIs. Trusted servers can offer specific tools and scoped access. Scripts use the credentials and permissions available to them. The server reaches the underlying resource or API. Direct access remains possible if other controls allow it. Both paths need controls over credentials, permissions and API use.
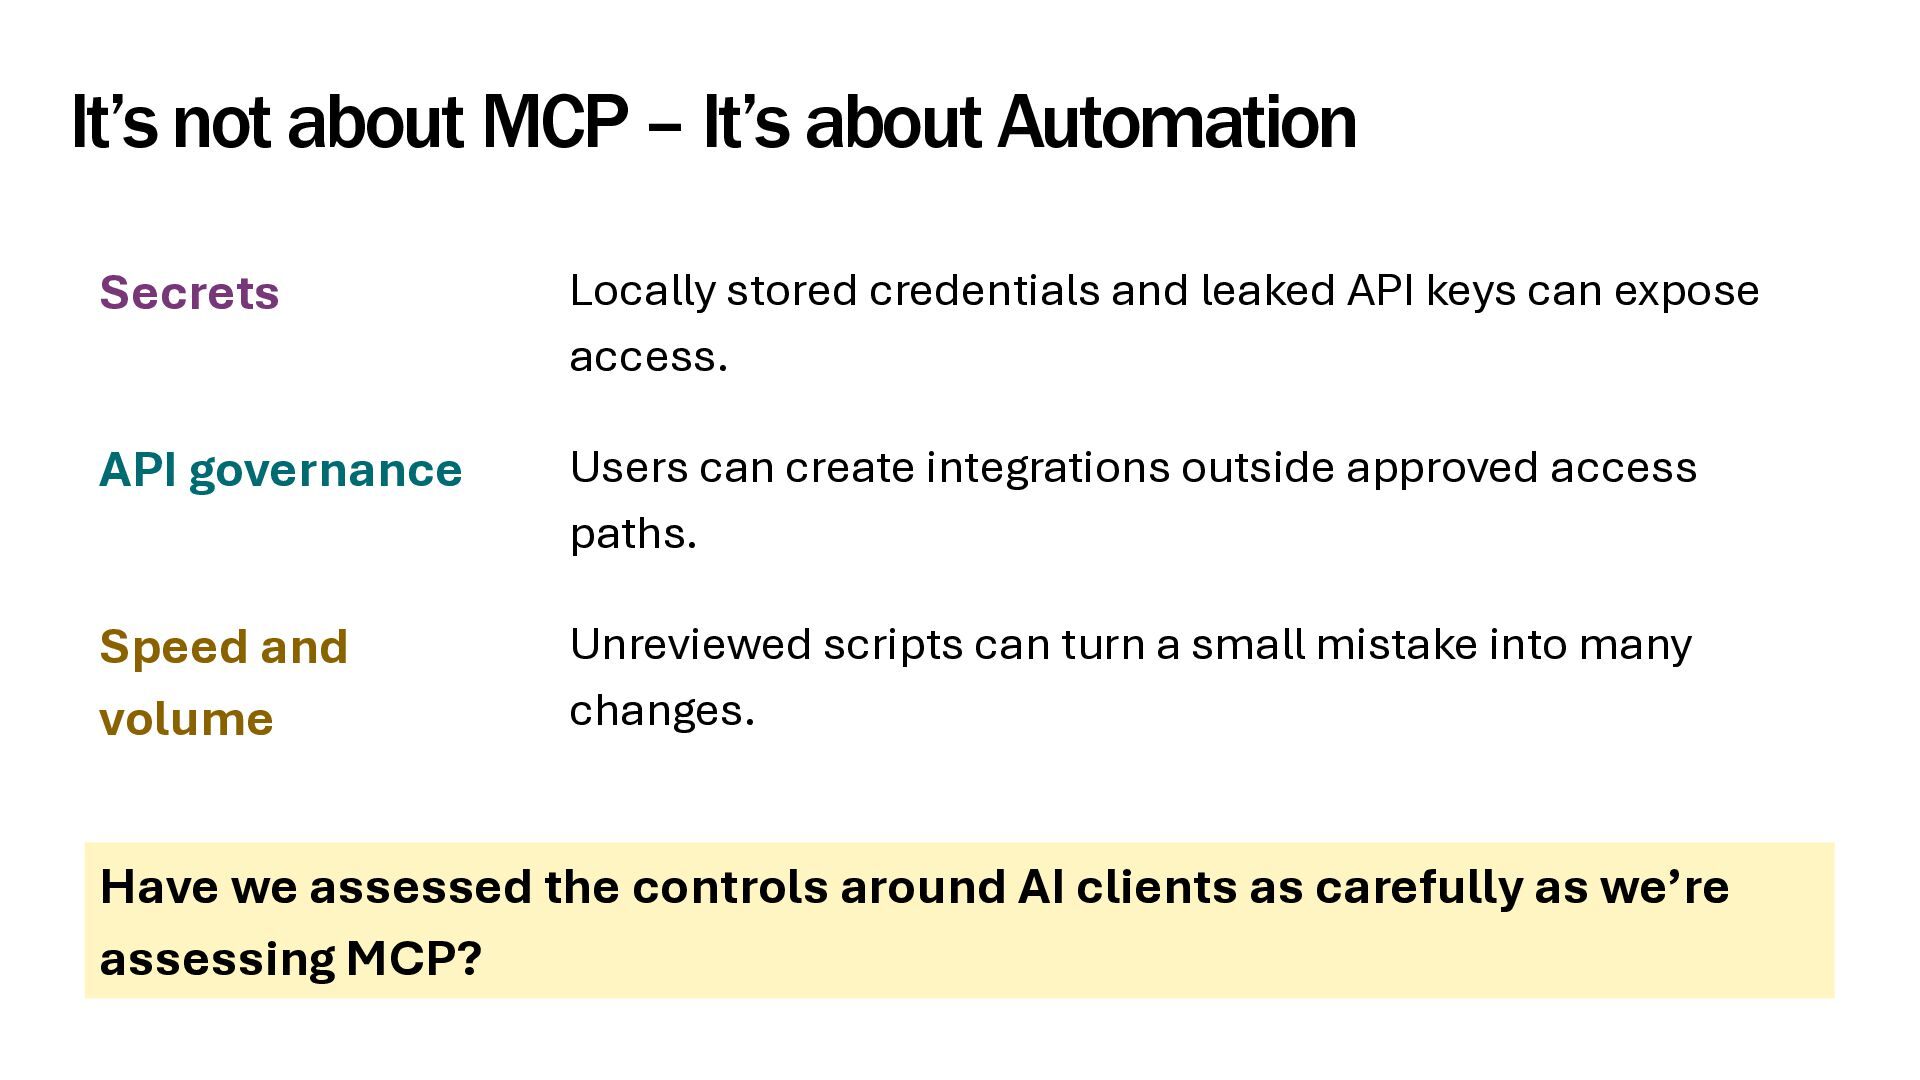
  147. It’s not about MCP – It’s about Automation Secrets Locally

    stored credentials and leaked API keys can expose access. API governance Users can create integrations outside approved access paths. Speed and volume Unreviewed scripts can turn a small mistake into many changes. Have we assessed the controls around AI clients as carefully as we’re assessing MCP?
  148. MCP to Enable Secure Automation? A trusted, narrowly scoped MCP

    path could be safer than ad hoc scripts using broader credentials. Secret management API visibility Scoped permissions Trusted MCP servers with specific tools and suitable authentication could offer a more governed route to AI-enabled programmatic access Still, MCP alone does not enforce all these controls nor guarantees visibility
  149. Fridge Sticky Notes  MCP is NOT an LLM, it

    is a standardised way to send API requests with an agreed format.  MCP is NOT the only way an LLM can interact with existing services and APIs  You do NOT need an LLM or AI Agent to interact with an MCP server
  150. #CymruSec Lunch & Networking – See you at 13:35! Upcoming

    – Final Breakout Breakout E: Breakout F: Breakout G : Effective Cyber Security for SMEs AI – The Current Threat Landscape MCP: Don’t Shoot the Messenger This Room 13:35 Ricoh Suite 13:35 Captains Lounge 13:35
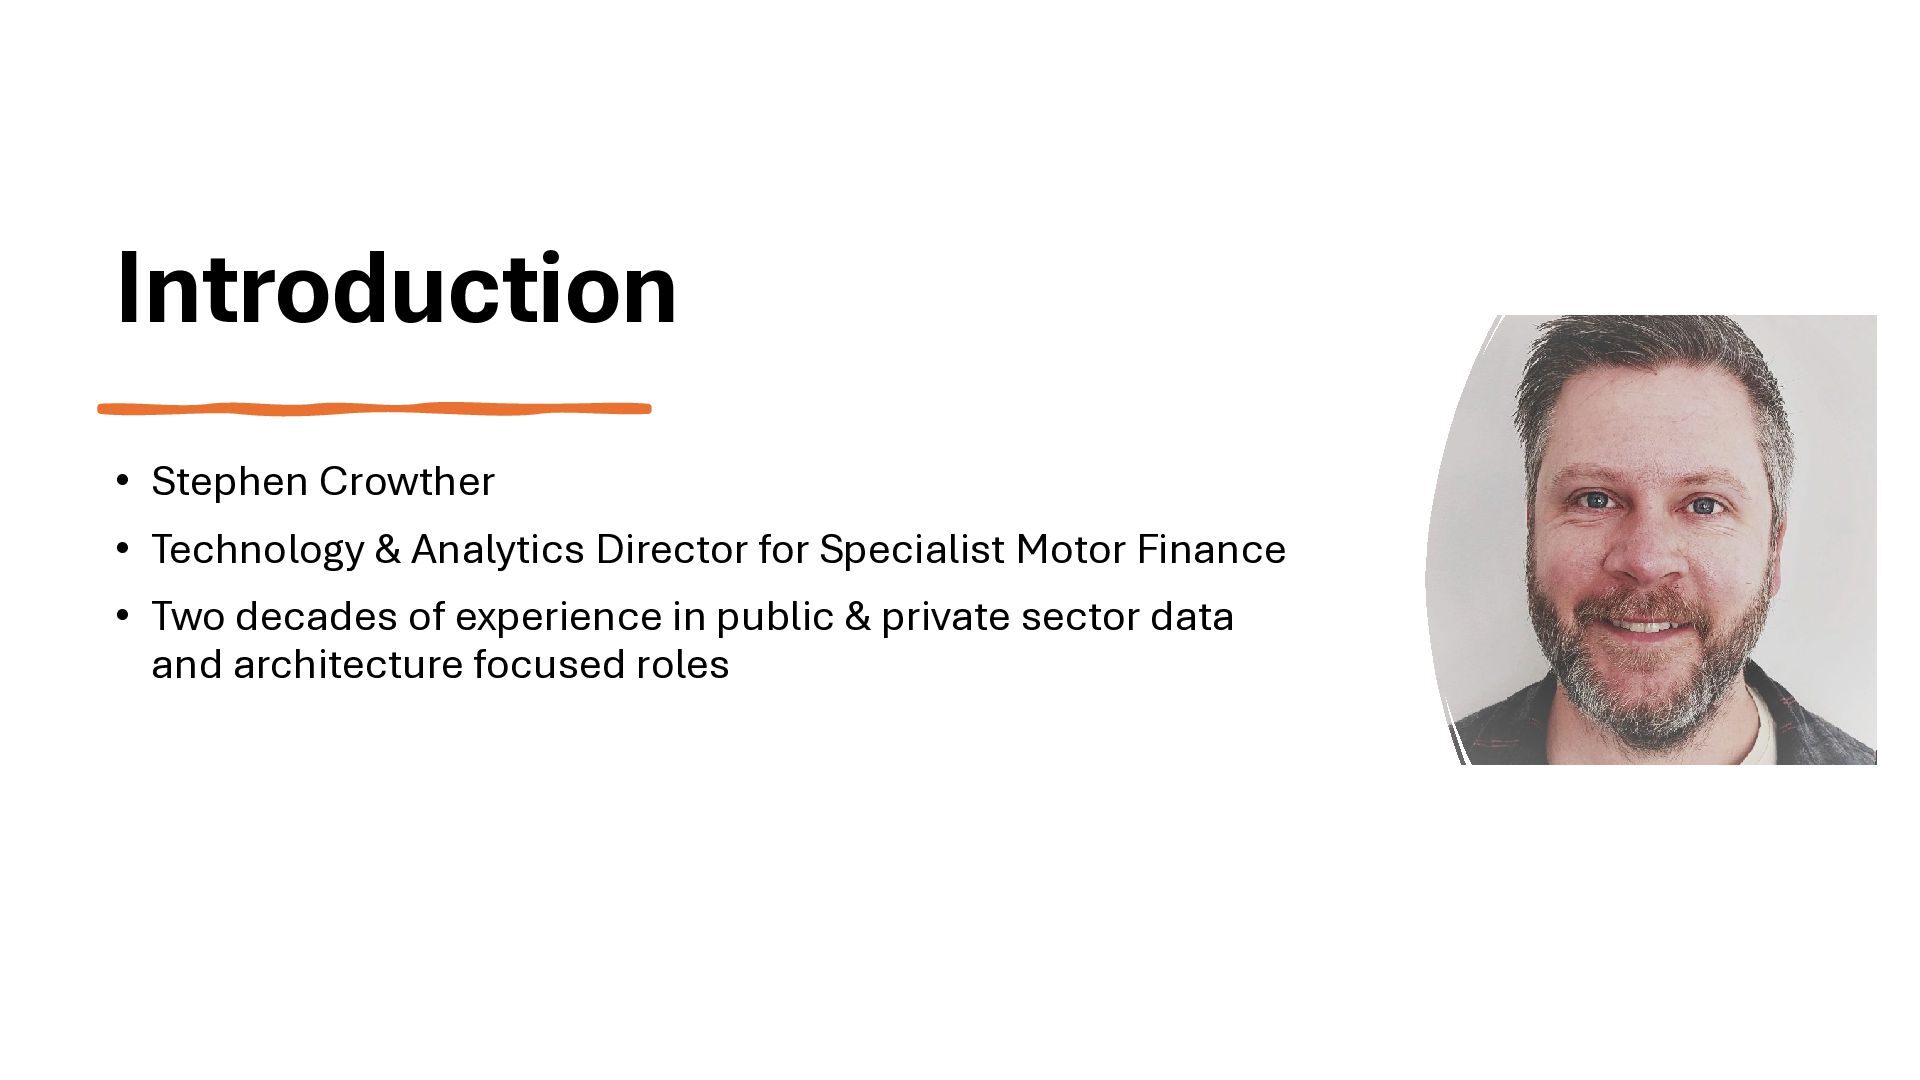
  151. Introduction • Stephen Crowther • Technology & Analytics Director for

    Specialist Motor Finance • Two decades of experience in public & private sector data and architecture focused roles
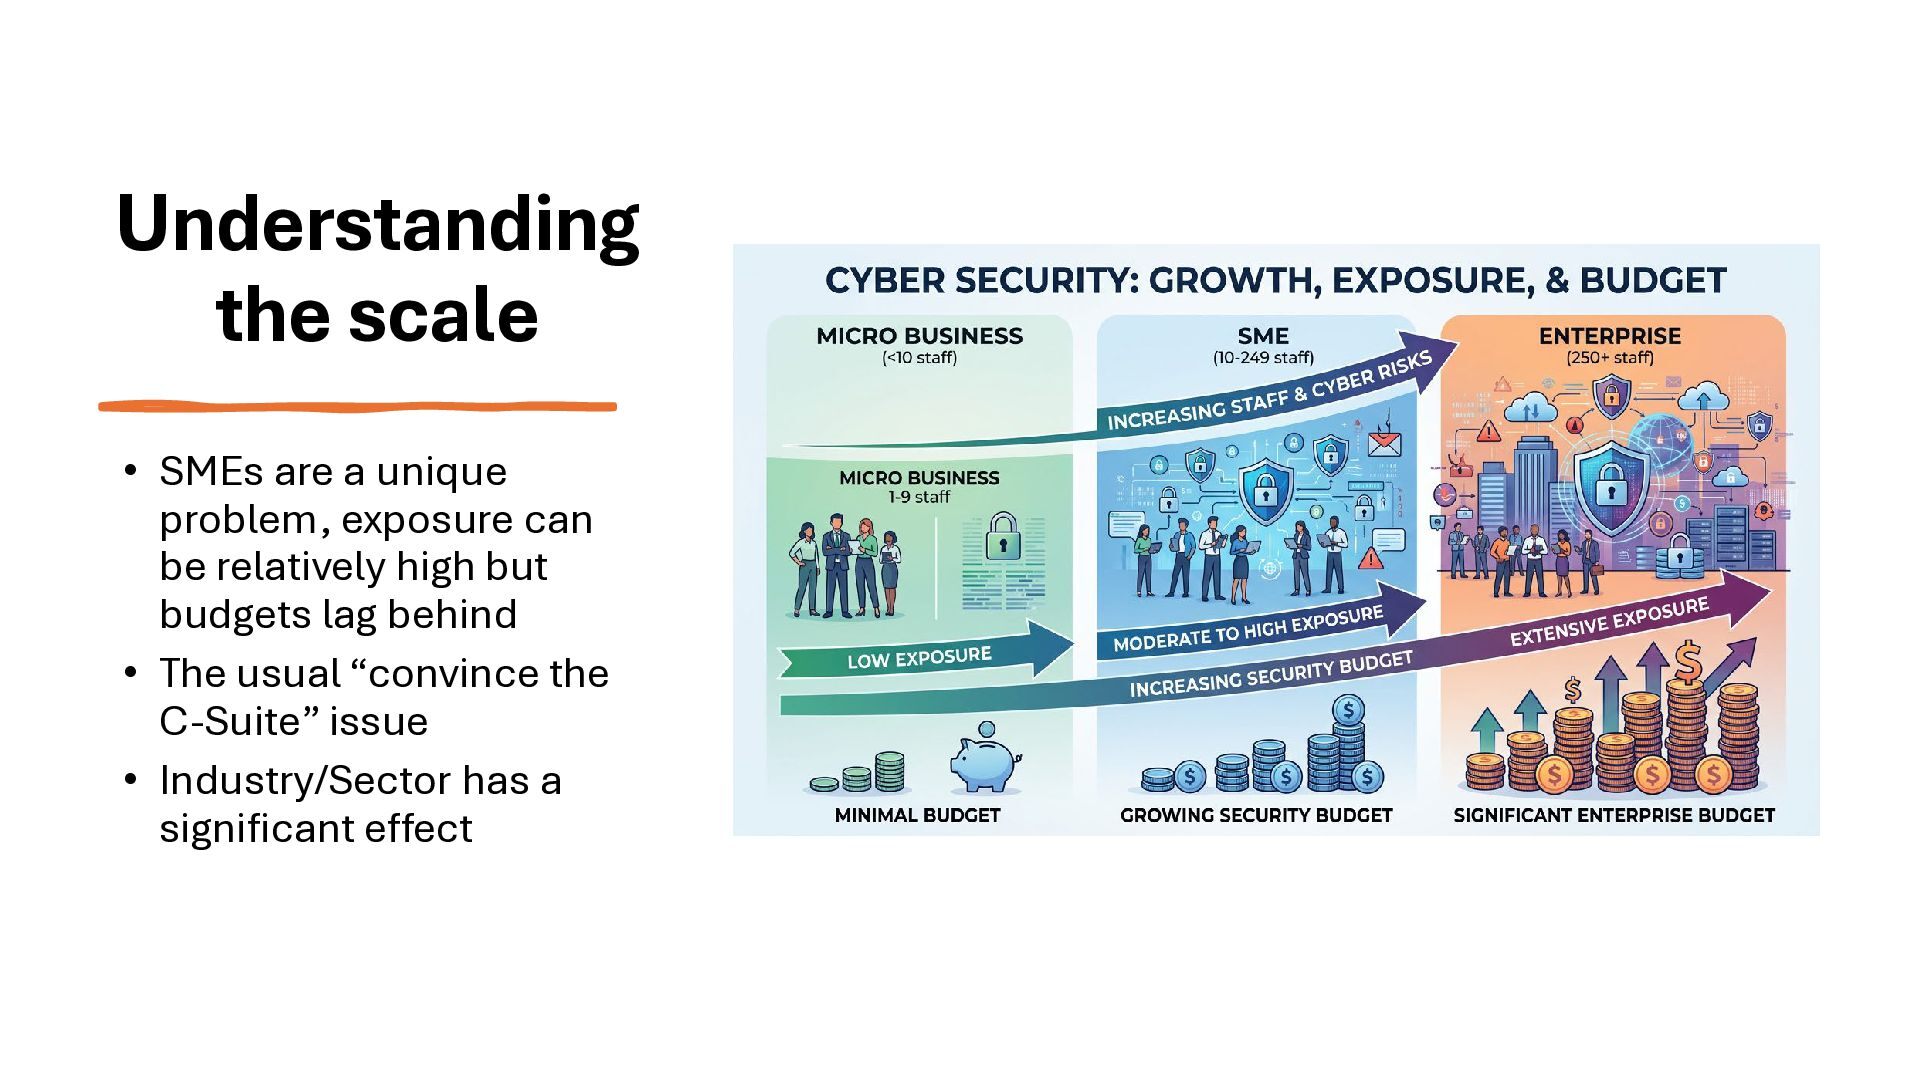
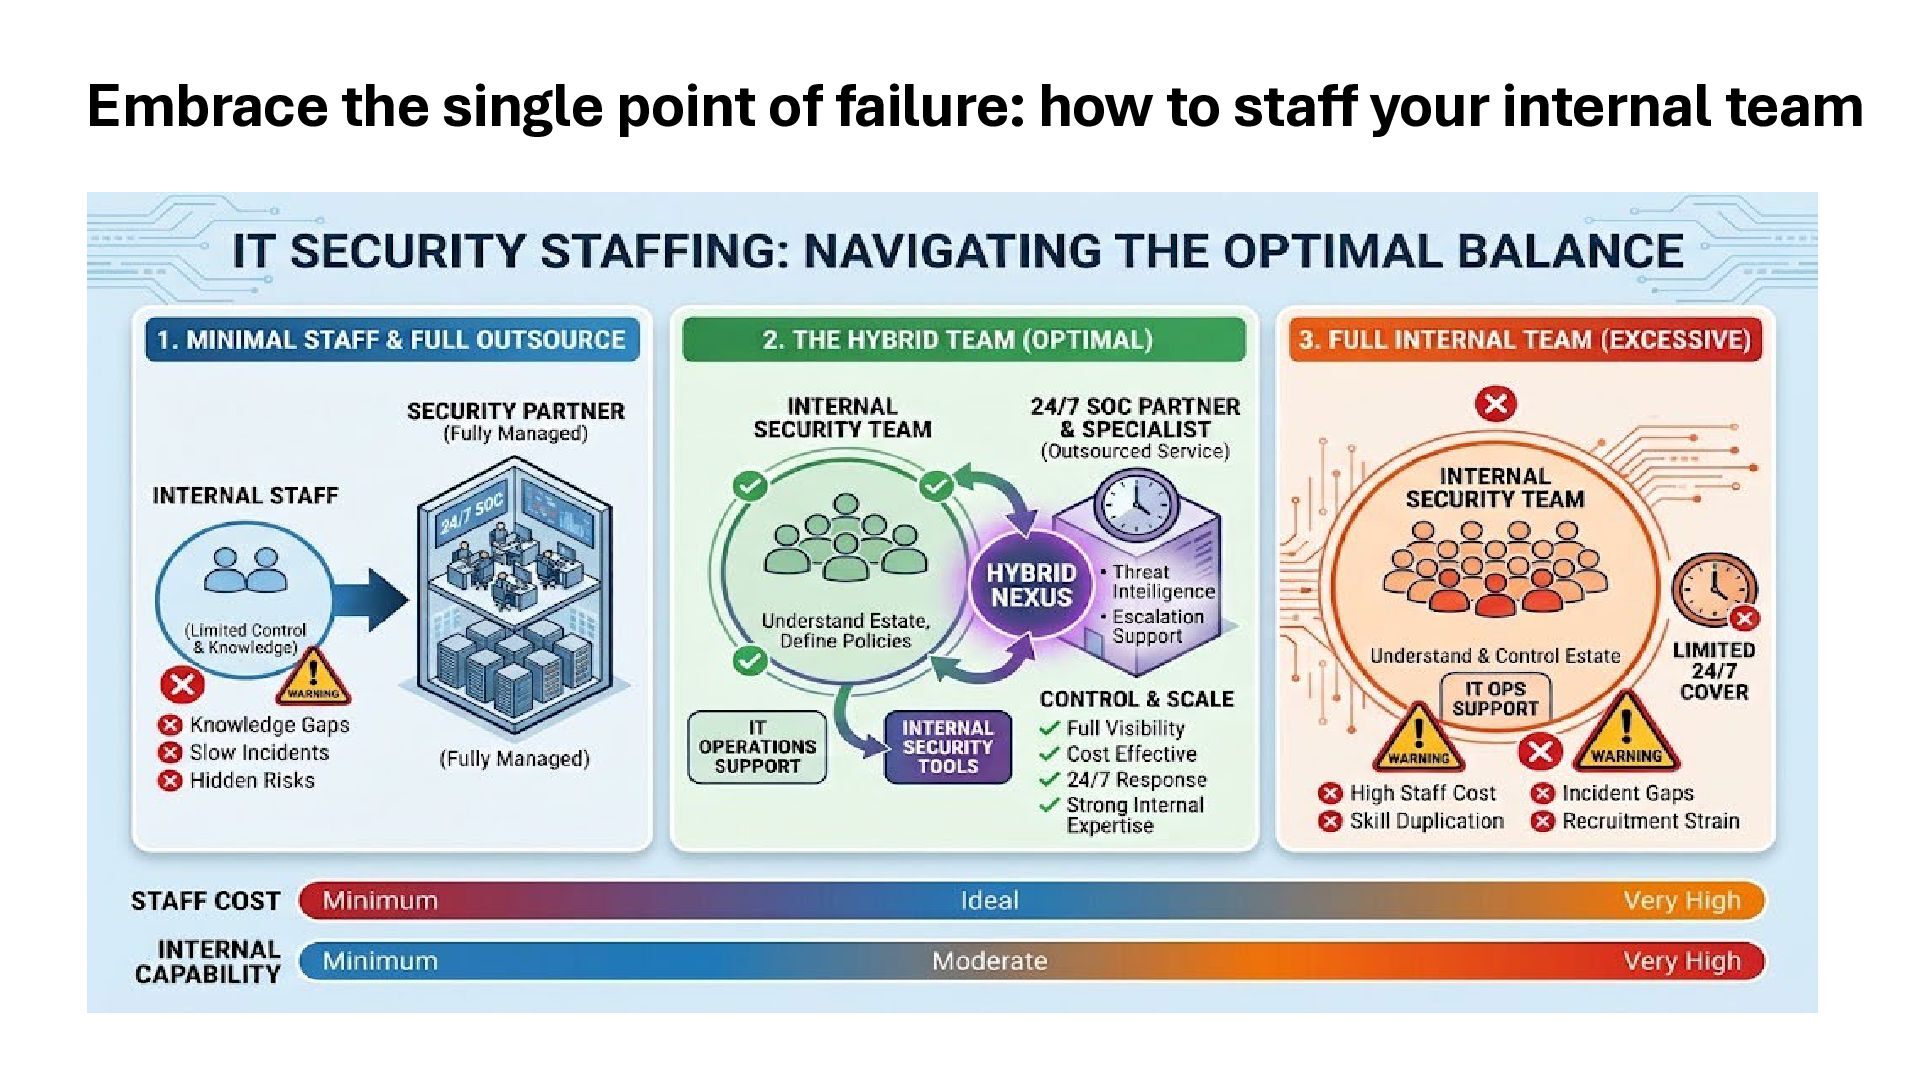
  152. Understanding the scale • SMEs are a unique problem, exposure

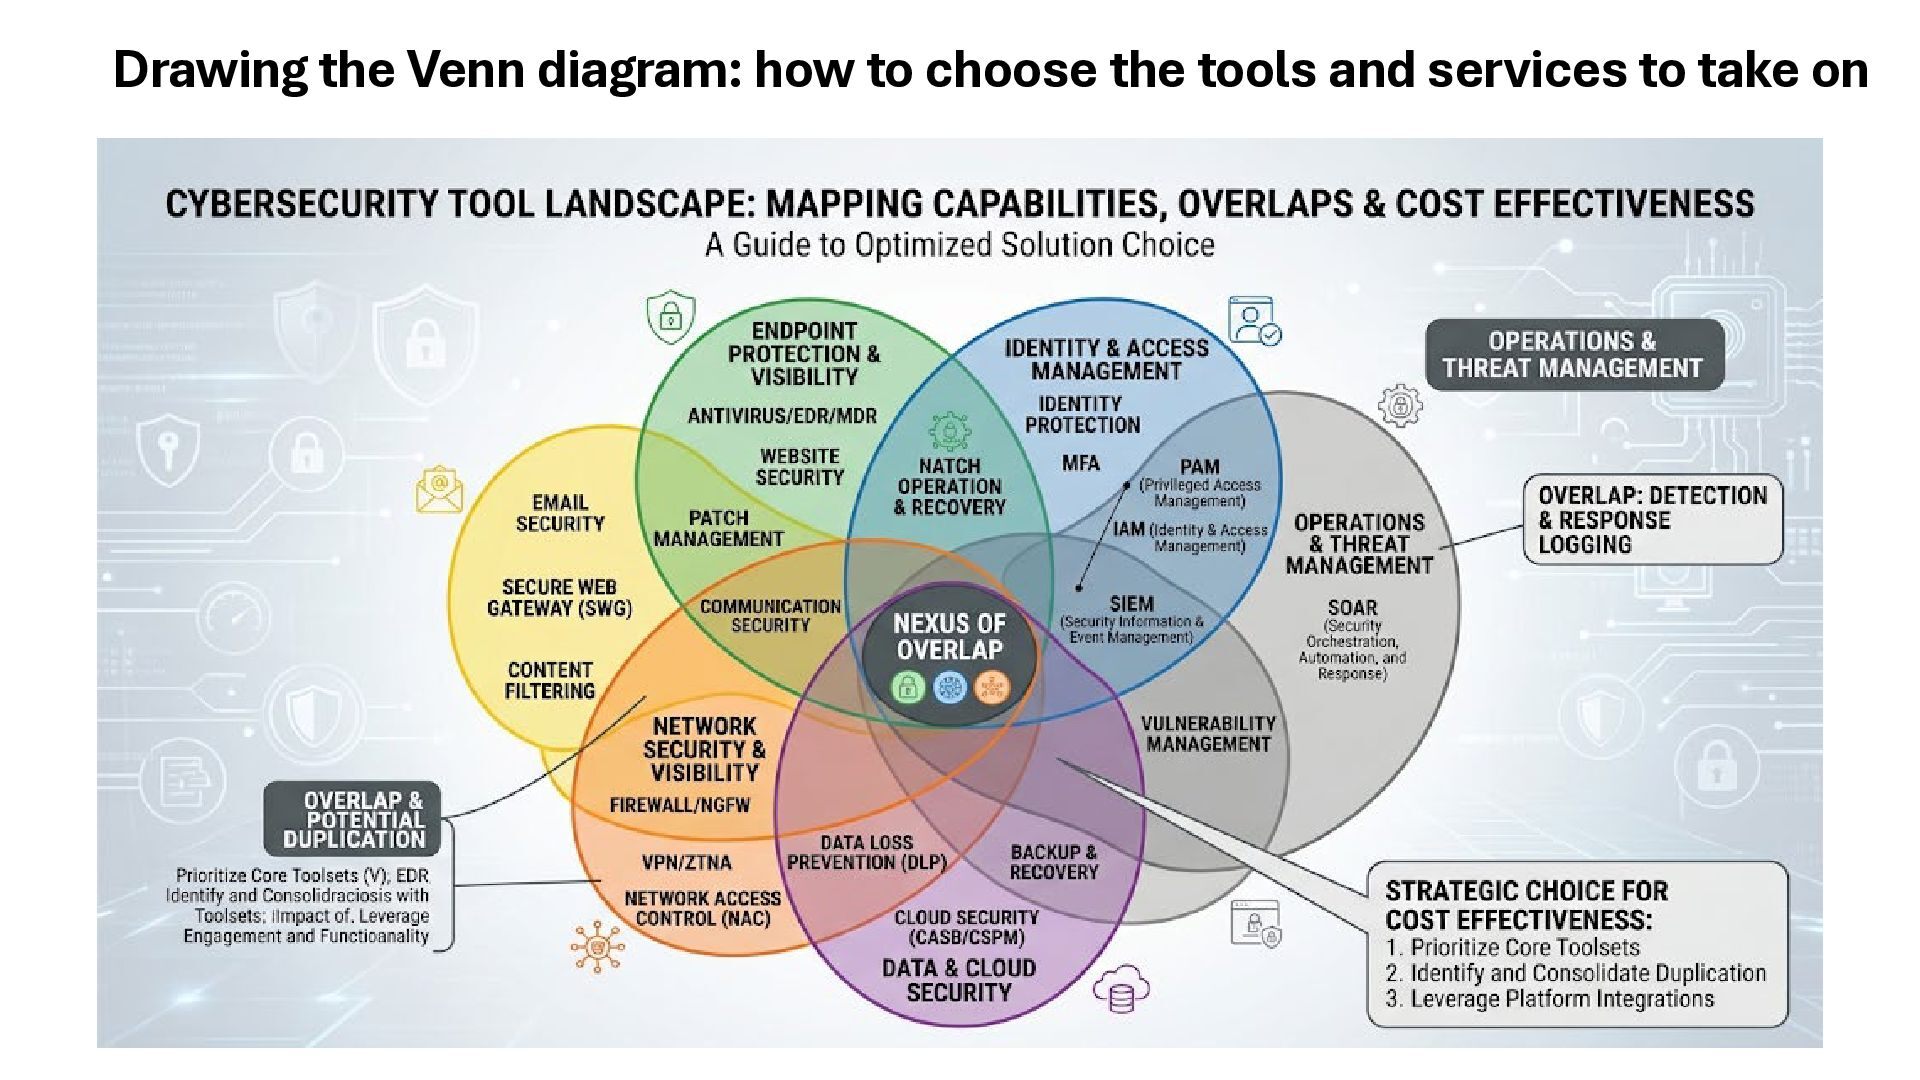
    can be relatively high but budgets lag behind • The usual “convince the C-Suite” issue • Industry/Sector has a significant effect
  153. Changes in security landscape • Scale of attacks is much

    broader due to increased resources & bandwidth • AI has introduced intense acceleration of phishing complexity, attack automation, and hacking accessibility to non-technical actors • OSINT sources have grown rapidly (LinkedIn / socials / breaches) • Nation state threats can catch private industry in the crossfire (e.g. NotPetya) • Consequences of a breach have become more serious, especially when involving personal data. ICO can fine up to 4% of turnover, and a key factor in determining fines is whether reasonable security measures were in place.
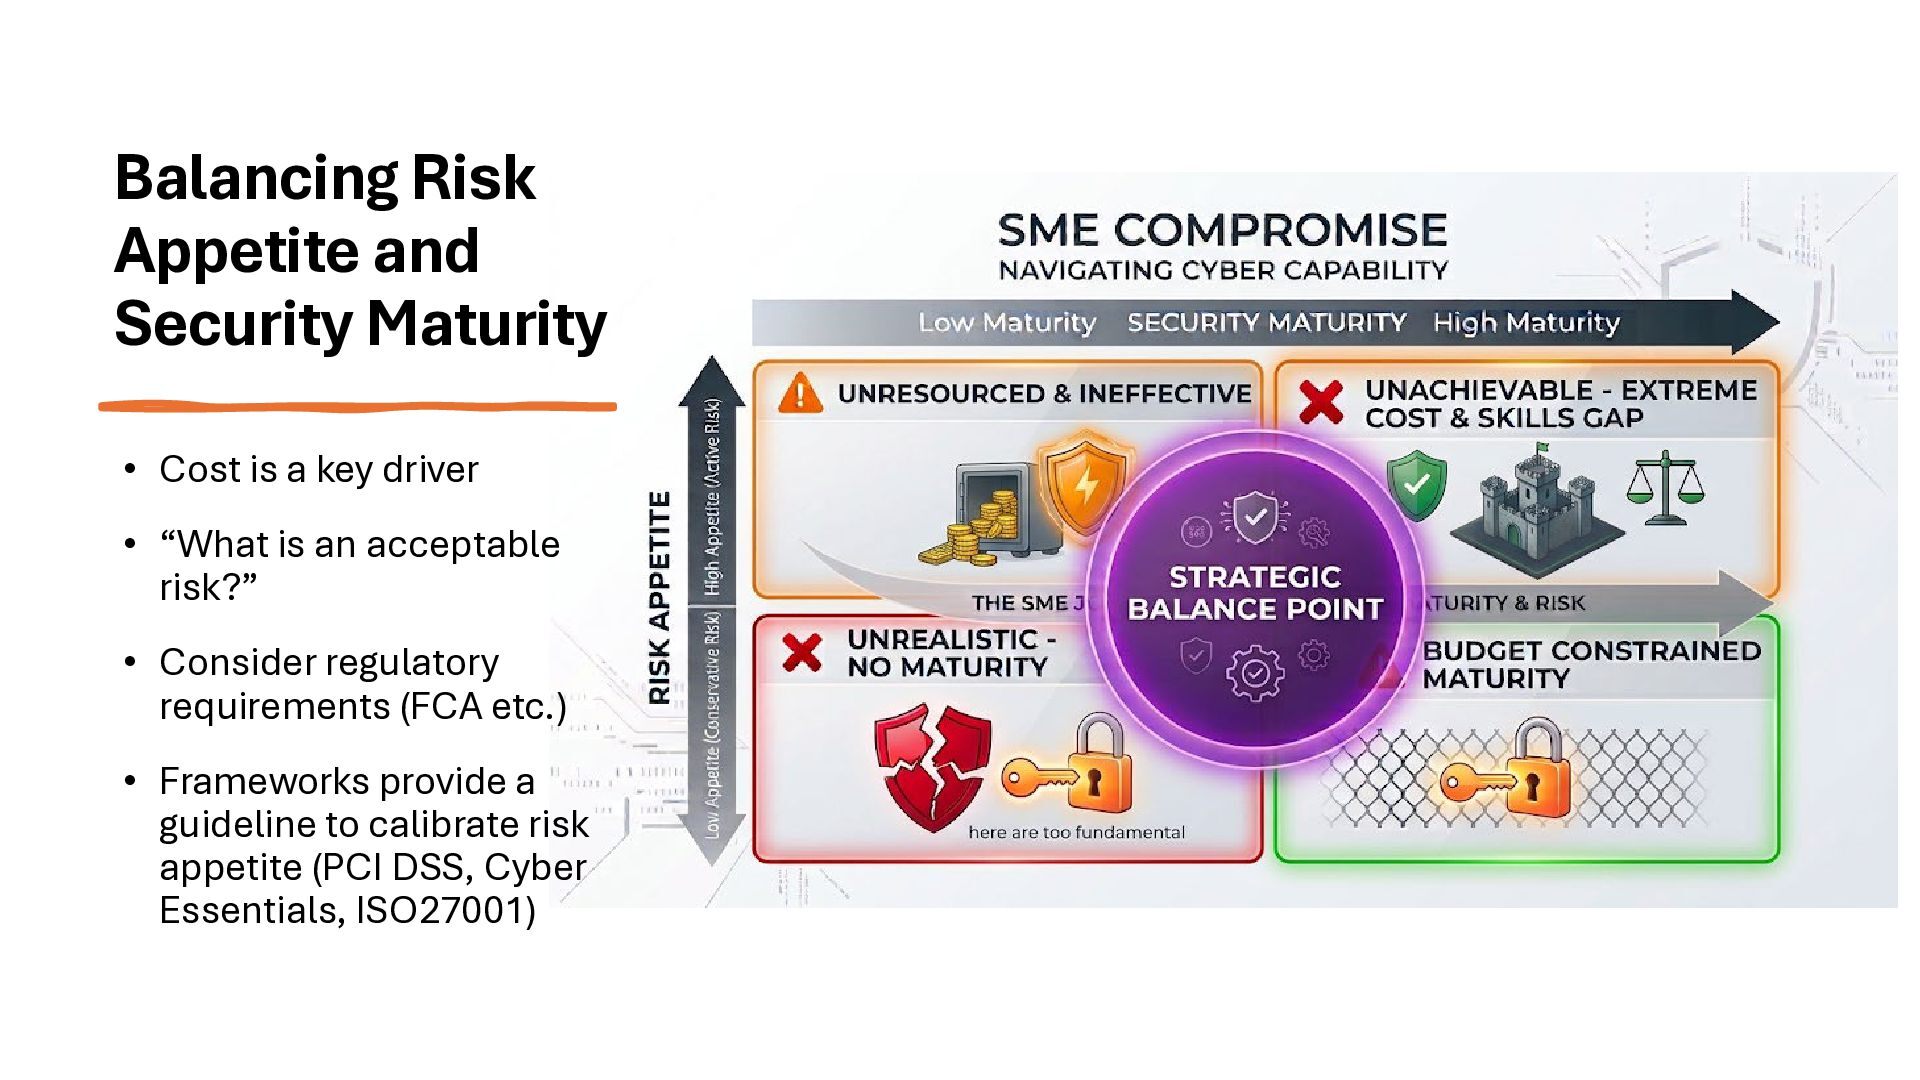
  154. Balancing Risk Appetite and Security Maturity • Cost is a

    key driver • “What is an acceptable risk?” • Consider regulatory requirements (FCA etc.) • Frameworks provide a guideline to calibrate risk appetite (PCI DSS, Cyber Essentials, ISO27001)
  155. Training: use scale to your advantage People are the biggest

    risk, so therefore people are the most effective defence. SMEs have the advantage of a closer-knit user community. Phishing training is critical, but pitched correctly; it’s no longer “embarrassing” to fall for them. Regular IT staff training needs to focus on securityminded architecture, best practices and vigilance. A small team is an asset in maintaining high standards.
  156. Preparing for incidents Have an incident response plan! Great, you

    have a SOC…do they have playbooks? Incident response vendor – you don’t want to wait for contract reviews and PO approvals in an incident. Cyber insurance or security software guarantees. Is your DR and backup strategy fit for purpose? Simulated incidents and tabletop exercises
  157. Summary • SMEs face a unique challenge, just the same

    as everyone else.. Understand what makes your organisation different and lean into it. • Limited FTE is a challenge but also an opportunity – find ways to use it to your advantage. • Costs are a reality that won’t go away, spend wisely and you can cover a very broad selection of angles. • Don’t allow “it’ll happen to someone else, not us” to creep in. • If the worst happens, be prepared and it will be fine…