on a phishing link within the first hour In 60% of cases, attackers are able to compromise an organisation within minutes 99.9% of the exploited vulnerabilities were compromised more than a year after the CVE was published 95% of malware types showed up for less than a month, and 80% didn’t last beyond a week Most affected industries: Financial services and Retail Source: Verizon 2015 Data Breach Investigation Report
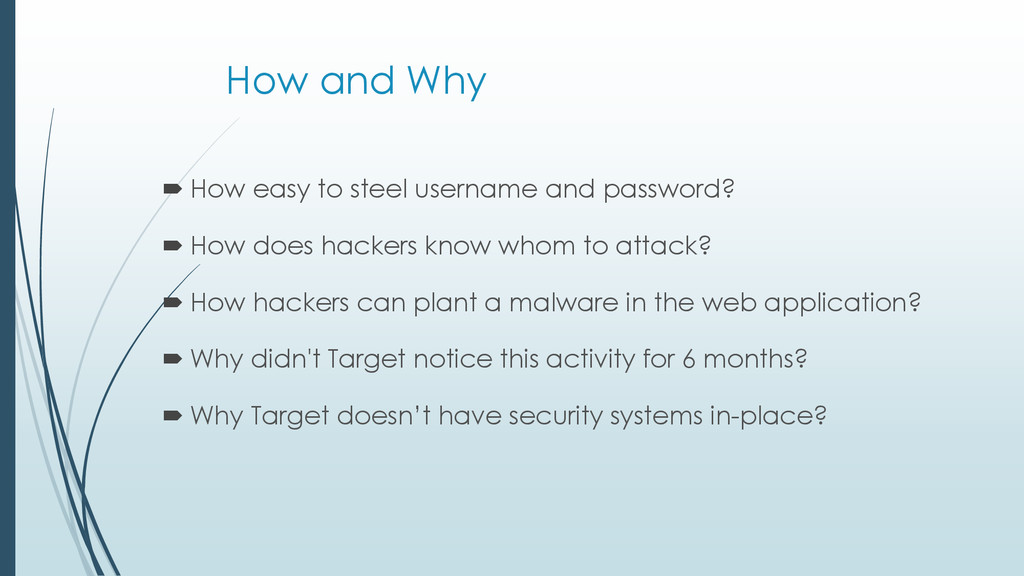
password? How does hackers know whom to attack? How hackers can plant a malware in the web application? Why didn't Target notice this activity for 6 months? Why Target doesn’t have security systems in-place?
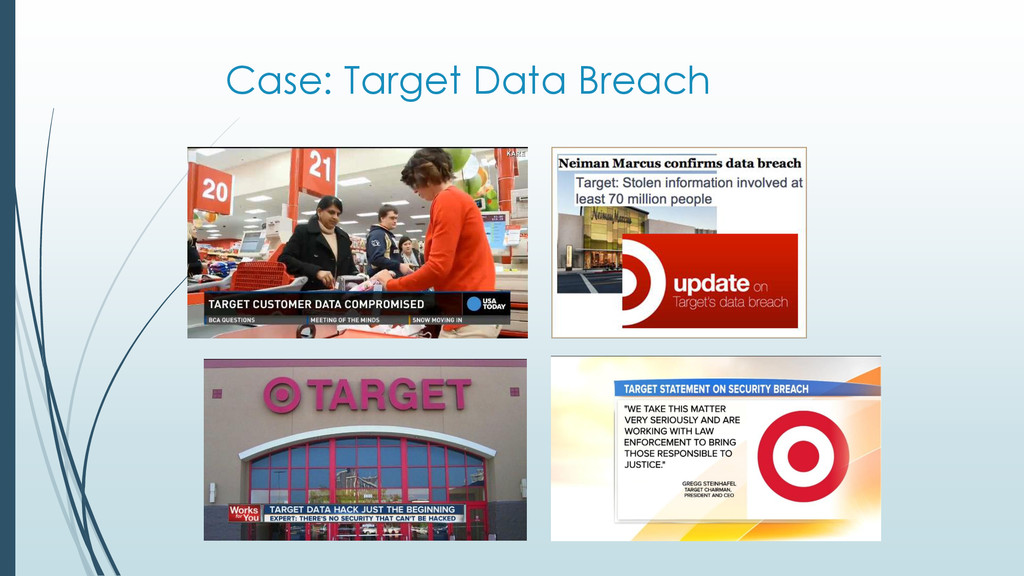
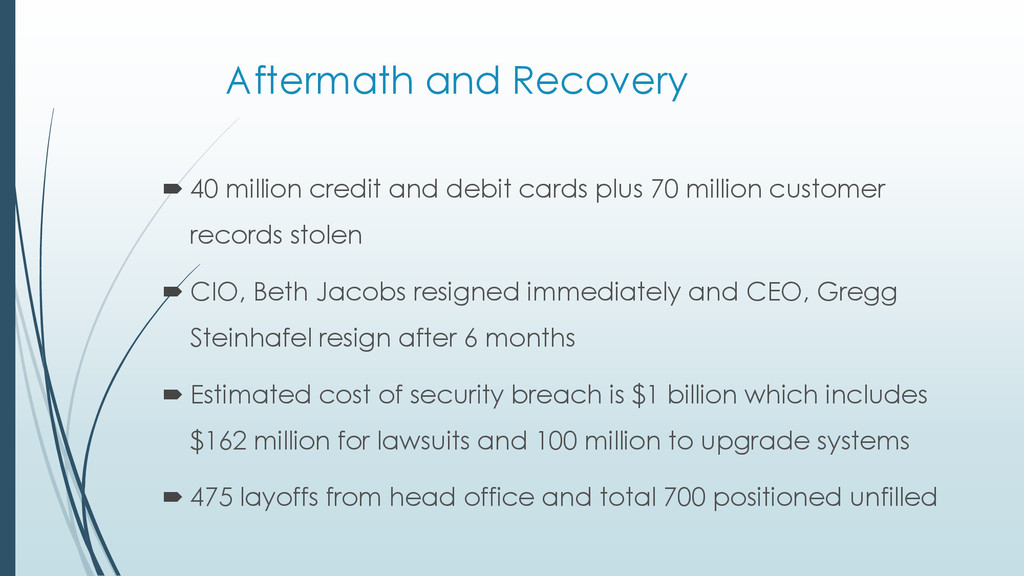
plus 70 million customer records stolen CIO, Beth Jacobs resigned immediately and CEO, Gregg Steinhafel resign after 6 months Estimated cost of security breach is $1 billion which includes $162 million for lawsuits and 100 million to upgrade systems 475 layoffs from head office and total 700 positioned unfilled
and technology shall use appropriately. Cautious when allowing access to 3rd parties, ensure appropriate security controls in-place. Consider security over convenience. Temporary means temporary, disable temporary logins after expiration. Do periodic security checks, specially on public facing web applications. Be vigilant, set notifications when creating new privilege user accounts. Consider security at design, proper isolation of networks and access controls. Be prepared, security incidents can happen any time
Define what is security incident for the company Identify incident categories Develop incident response procedures Preparation, Identification, Containment, Eradication, Recovery and Wrap-up Identify Security Incident Response Team (SIRT) members A cross-functional team representing all business units Define and communicate roles and responsibilities Communicate to rest of the organization Conduct regular tests and drills


 pfn
 masakiokuda
 yamad
 kairim0
 iktakahiro
 kaminashi
 koukihosaka
 shogo4131
 tomokusaba
 glaforge
 kzkhykw1991
 terapyon
 kastner
 productmarketing
 mfonobong
 cassininazir
 caitiem20
 sugarenia
 tmiket
 katiecoart
 inesmontani
 ipullrank
 chikuwait
 kimpetersen