Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Automated Evil Driven Development

Avatar for Serranos Serranos
November 30, 2017

Automated Evil Driven Development

Includes behavior driven development, creation of evil user stories, definition of security baselines and how we can embed them in the CI/CD pipelines in an automated way. Presents some security tools that can help us, their pros/cons and how we can use them to create security tests. The demo focuses mainly on BDD-Security from "Continuum Security".

Avatar for Serranos

Serranos

November 30, 2017

More Decks by Serranos

Other Decks in Technology

Transcript

  1. Agenda 7 Security at fast-paced environments Empathy and behavior driven

    development Being Evil Evil utility belt Automating Evil Let’s do it with BDD-Security
  2. Agenda 8 Security at fast-paced environments Empathy and behavior driven

    development Being Evil Evil utility belt Automating Evil Let’s do it with BDD-Security Demo
  3. Too many challenges DevOp”ish” organizations promote self-service Let’s all deploy

    to production! Clash of cultures Security at fast-paced environments 13
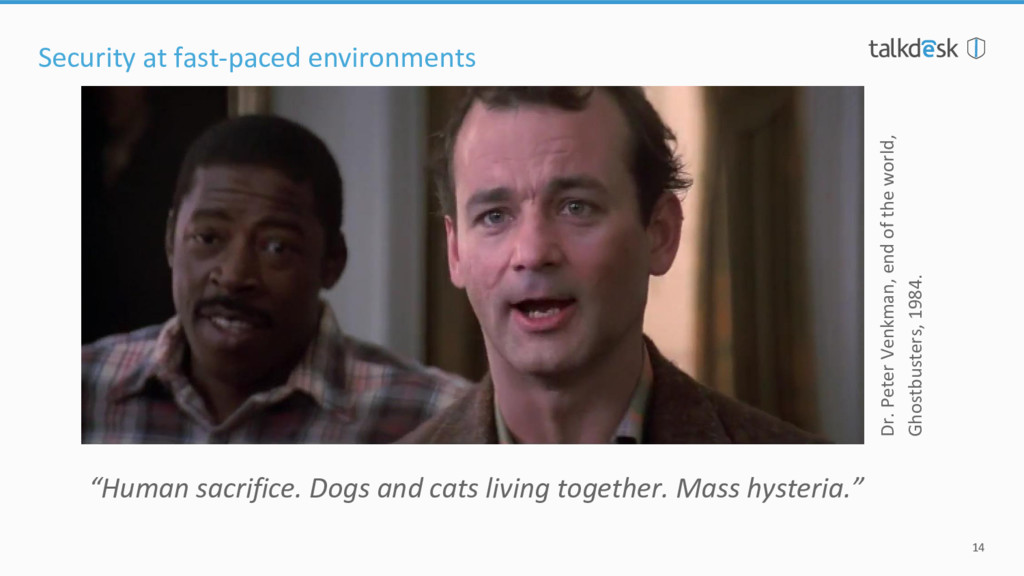
  4. “Human sacrifice. Dogs and cats living together. Mass hysteria.” Security

    at fast-paced environments 14 Dr. Peter Venkman, end of the world, Ghostbusters, 1984.
  5. Security at fast-paced environments 15 Developers... let’s write down their

    names… Death Note Manga series by Tsugumi Ohba and illustrated by Takeshi Obata
  6. Security at fast-paced environments 16 Product people... let’s write down

    their names… Death Note Manga series by Tsugumi Ohba and illustrated by Takeshi Obata
  7. The Amazing World of Gumball TV series from Cartoon Network.

    Created by Ben Bocquelet. Security at fast-paced environments 18
  8. Let’s all try not to become John Pesche, the alcoholic

    Security Guy... Security at fast-paced environments 19
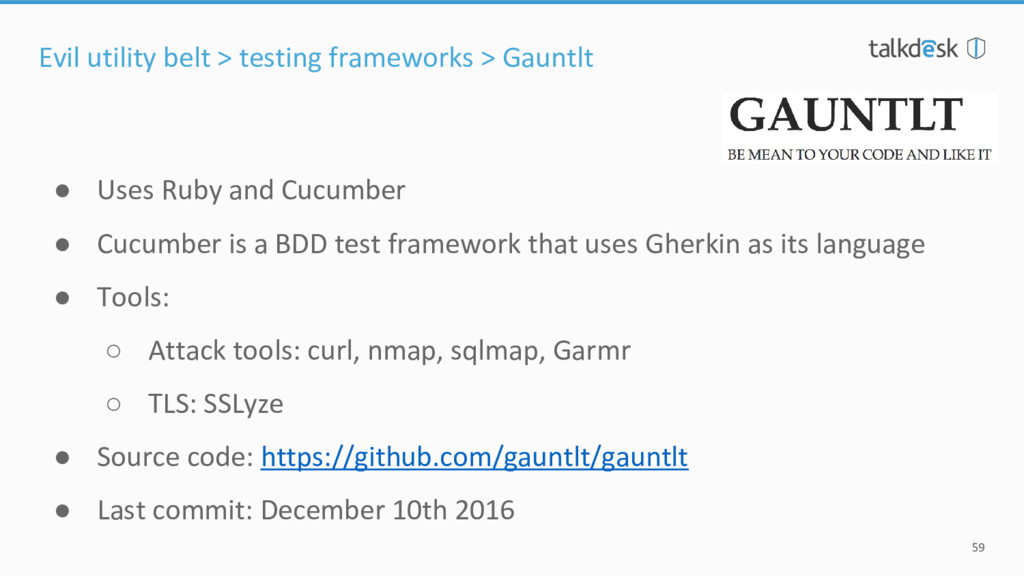
  9. All stakeholders should be called to participate A common language

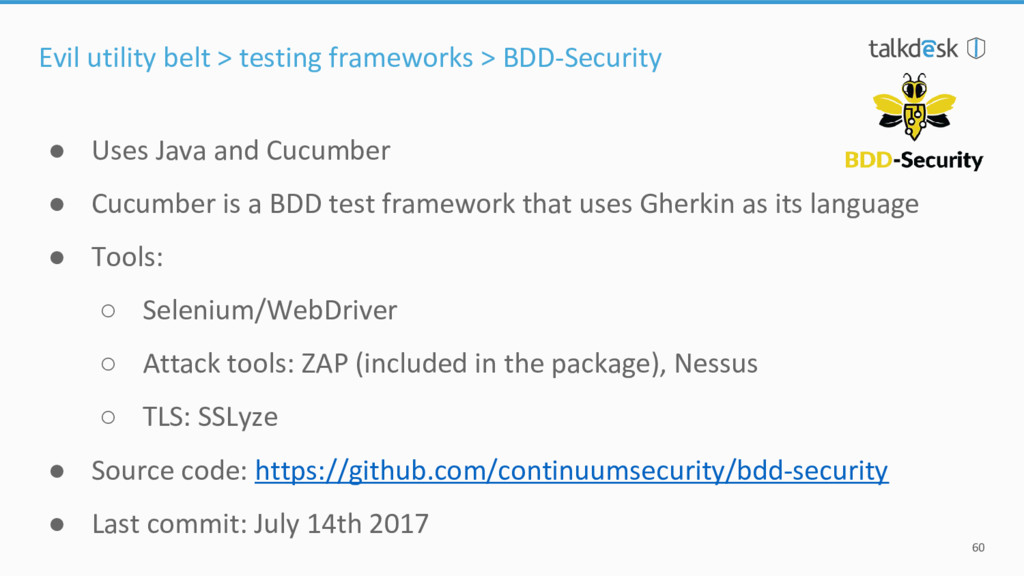
    to describe features is key Empathy and behavior driven development 28
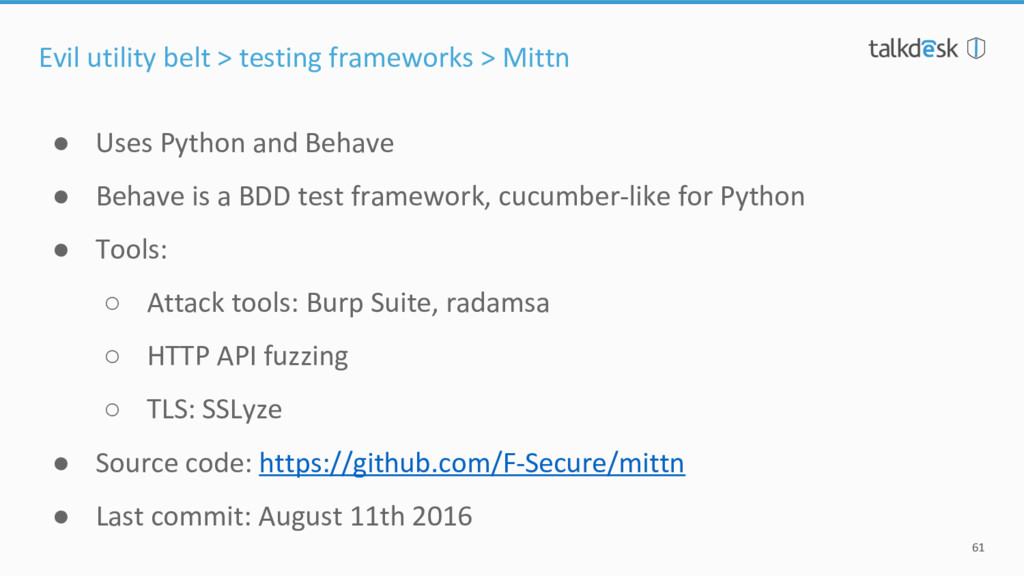
  10. All stakeholders should be called to participate A common language

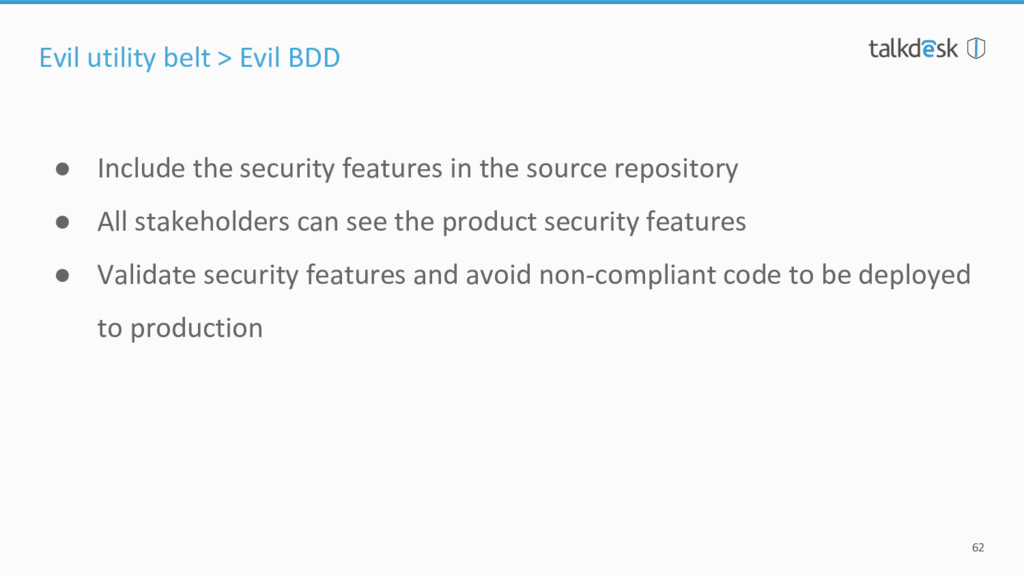
    to describe features is key All in all, everyone is interested in the same end goal... Empathy and behavior driven development 29
  11. Goto is not your friend and the security team should

    handle it with care Empathy and behavior driven development > consistency 31
  12. Goto is not your friend and the security team should

    handle it with care Bake security concerns in the Software Development Life Cycle (SDLC)* * not really something new... Empathy and behavior driven development > consistency 32
  13. Goto is not your friend and the security team should

    handle it with care Bake security concerns in the Software Development Life Cycle (SDLC)* Scale security with security champions * not really something new... Empathy and behavior driven development > consistency 33
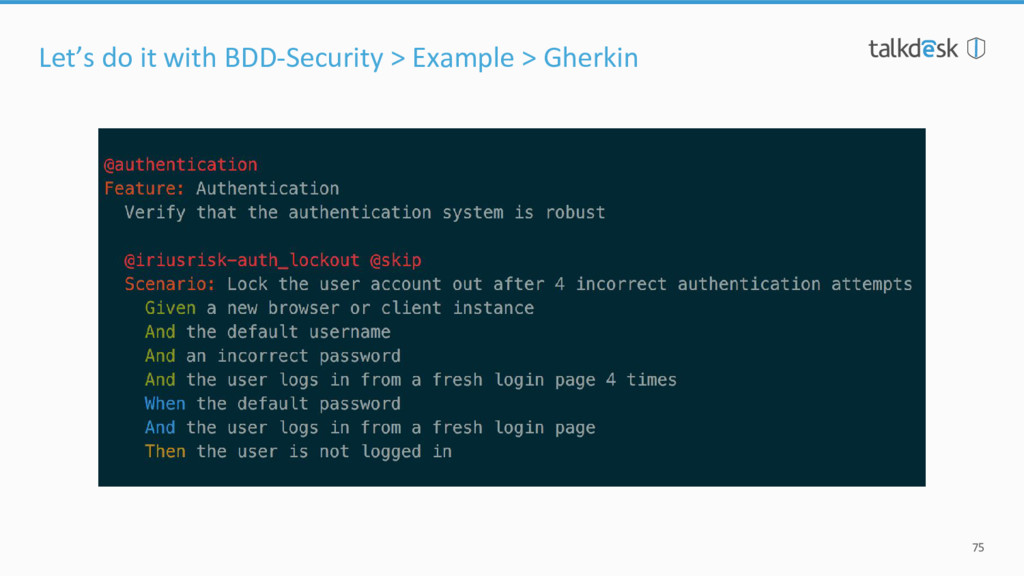
  14. Goto is not your friend and the security team should

    handle it with care Bake security concerns in the Software Development Life Cycle (SDLC)* Scale security with security champions Scale security by providing self-services for teams * not really something new... Empathy and behavior driven development > consistency 34
  15. Goto is not your friend and the security team should

    handle it with care Bake security concerns in the Software Development Life Cycle (SDLC)* Scale security with security champions Scale security by providing self-services for teams Develop product features with security in mind * not really something new... Empathy and behavior driven development > consistency 35
  16. Empathy and behavior driven development > teams 36 We still

    need to find a better way to get everyone working as a team
  17. Stephen King, The Rolling Stone Interview, 2014 Evil is innate
    Evil is inside us. The older I get, the less I think there’s some sort of outside devilish influence; it comes from people. “
  18. The usual approach goes something like this: 1. Develop the

    product 2. Hire an external company to do the pentesting (if you're lucky) Being Evil 43
  19. The usual approach goes something like this: 1. Develop the

    product 2. Hire an external company to do the pentesting (if you're lucky) 3. Fix whatever was found (if you're REALLY lucky) Being Evil 44
  20. User stories are short descriptions of a feature Descriptions are

    from the point of view of the customer The customer can be external or internal Being Evil > User Stories 47
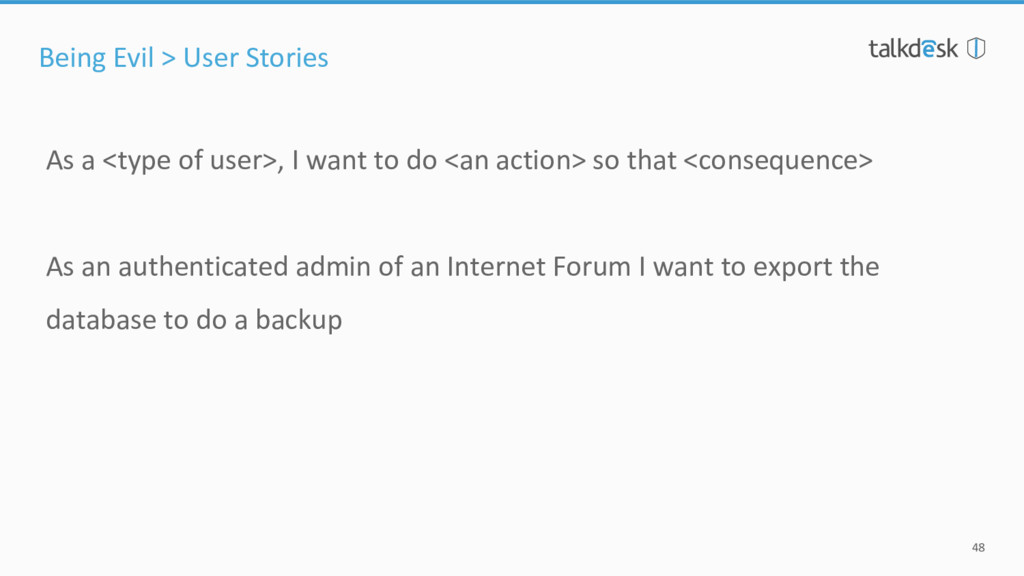
  21. As a <type of user>, I want to do <an

    action> so that <consequence> As an authenticated admin of an Internet Forum I want to export the database to do a backup Being Evil > User Stories 48
  22. Evil Stories are User Stories for Evil which by definition

    are: • Used to express threats from a bad actor perspective • Incorporated in Agile development • Used in the product backlog for including security concerns Being Evil > Evil User Stories 49
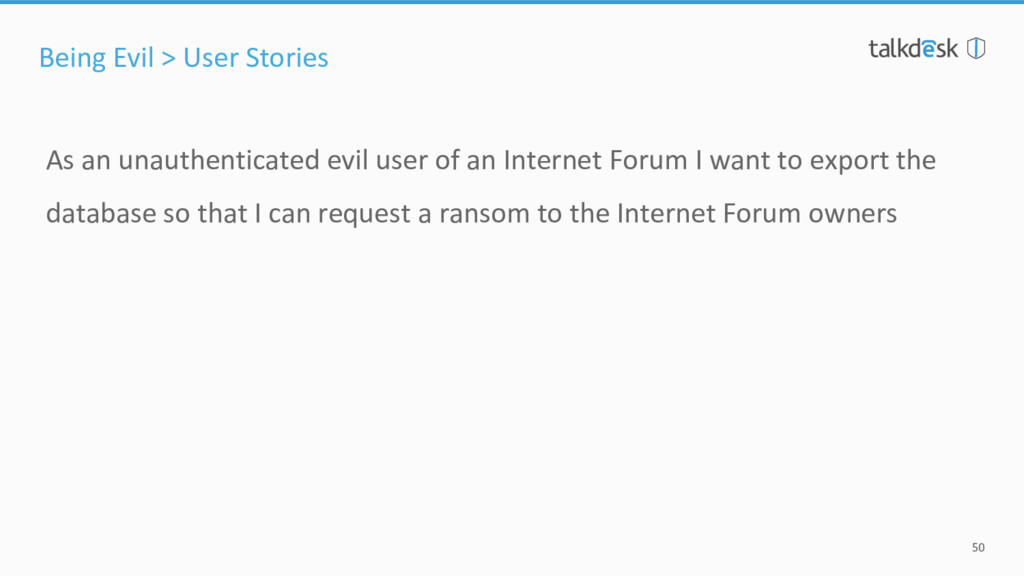
  23. As an unauthenticated evil user of an Internet Forum I

    want to export the database so that I can request a ransom to the Internet Forum owners Being Evil > User Stories 50
  24. 1. Know your system 2. Select a security topic 3.

    Create Evil User Story 4. Add Evil User Story to the Product Backlog Being Evil > How to create one 51
  25. Authentication Session management Access control Input validation Output encoding/escaping Cryptography

    Being Evil > Security topics 52 Error handling Logging Data protection Communication security HTTP security features
  26. • As an Evil Duck, I want to send bad

    data in HTTP headers, so I can access data and functions for which I'm not authorized • As an Evil Duck, I want to access multiple ports in the webserver other than port 80 or port 443 • As an Evil Duck, I want to use a revoked token to access protected resources Being Evil > Examples 53
  27. • Mittn • Gauntlt • BDD-Security Include all of the

    above in CI/CD pipelines Evil utility belt > BDD testing frameworks 58
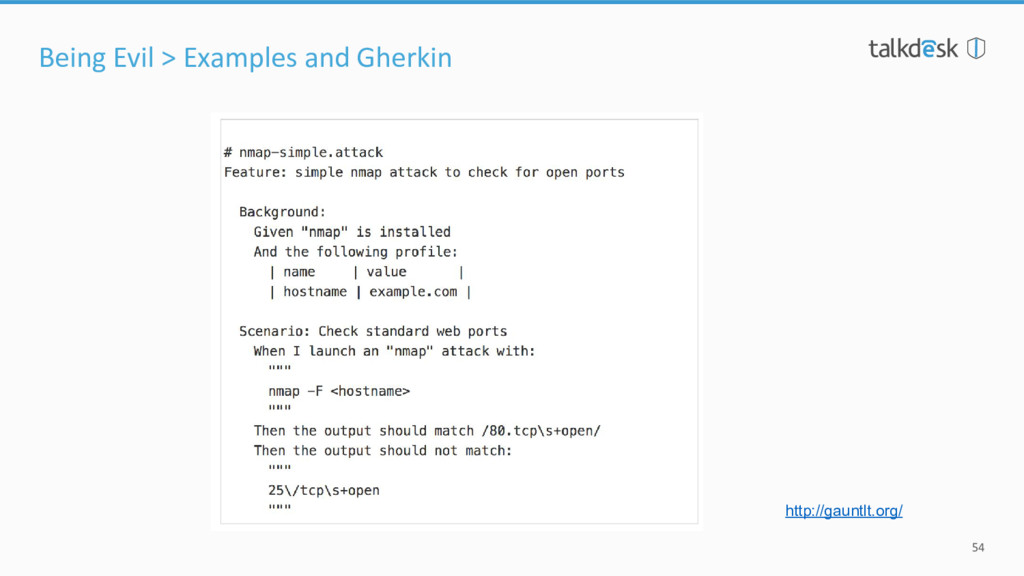
  28. Evil utility belt > testing frameworks > Gauntlt 59 •

    Uses Ruby and Cucumber • Cucumber is a BDD test framework that uses Gherkin as its language • Tools: ◦ Attack tools: curl, nmap, sqlmap, Garmr ◦ TLS: SSLyze • Source code: https://github.com/gauntlt/gauntlt • Last commit: December 10th 2016
  29. Evil utility belt > testing frameworks > BDD-Security 60 •

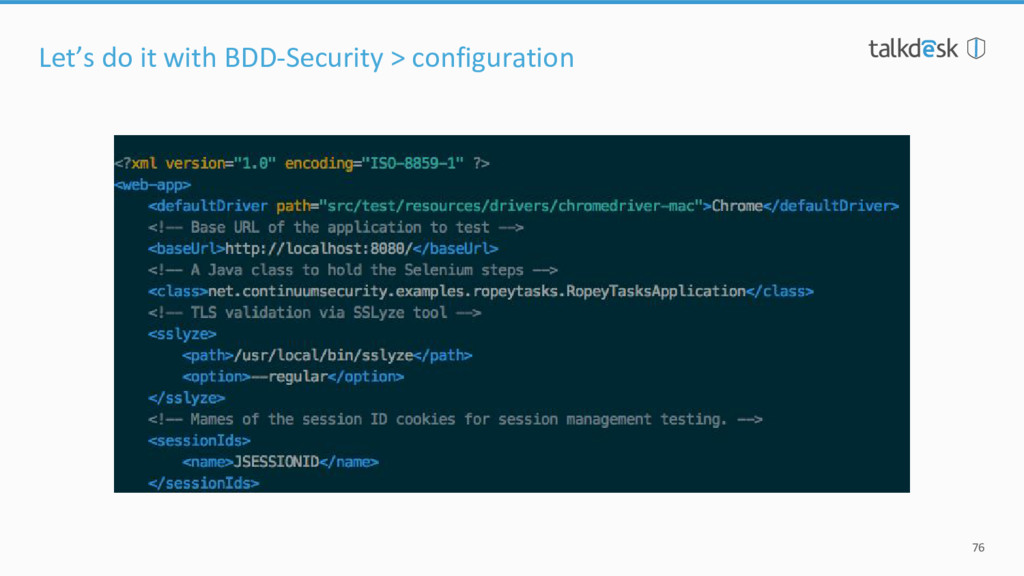
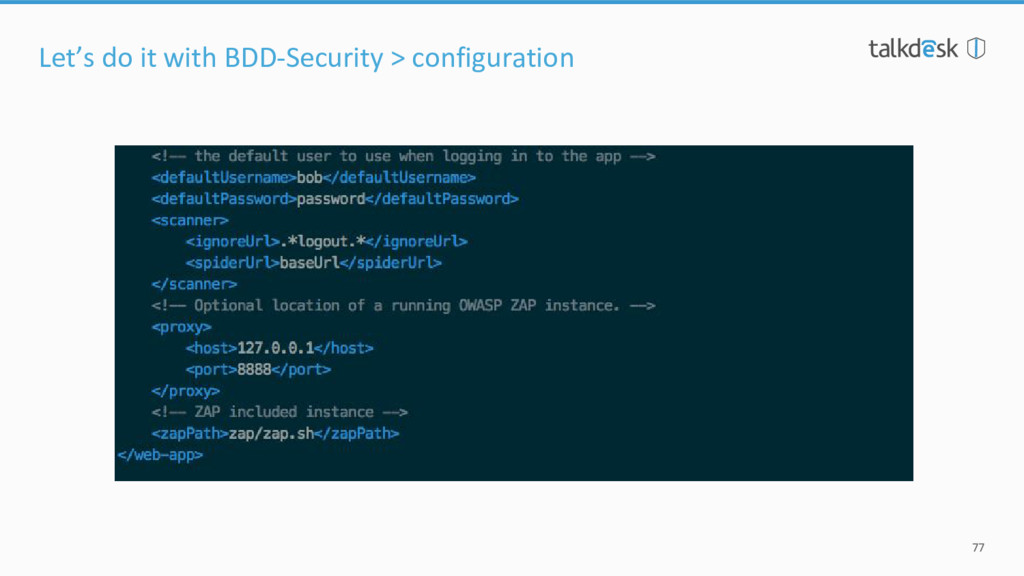
    Uses Java and Cucumber • Cucumber is a BDD test framework that uses Gherkin as its language • Tools: ◦ Selenium/WebDriver ◦ Attack tools: ZAP (included in the package), Nessus ◦ TLS: SSLyze • Source code: https://github.com/continuumsecurity/bdd-security • Last commit: July 14th 2017
  30. • Uses Python and Behave • Behave is a BDD

    test framework, cucumber-like for Python • Tools: ◦ Attack tools: Burp Suite, radamsa ◦ HTTP API fuzzing ◦ TLS: SSLyze • Source code: https://github.com/F-Secure/mittn • Last commit: August 11th 2016 Evil utility belt > testing frameworks > Mittn 61
  31. • Include the security features in the source repository •

    All stakeholders can see the product security features • Validate security features and avoid non-compliant code to be deployed to production Evil utility belt > Evil BDD 62
  32. • Reuse the stories for other systems • Extend current

    test frameworks: ◦ add new features ◦ add new scenarios ◦ add new tools • Community: contribute to common set of security features Evil utility belt > Evil BDD 63
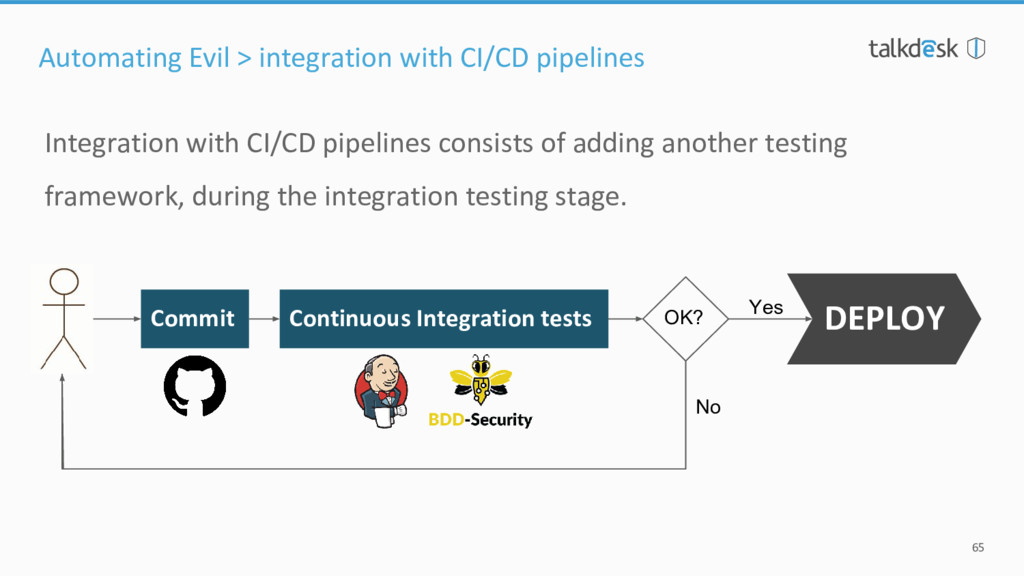
  33. Integration with CI/CD pipelines consists of adding another testing framework,

    during the integration testing stage. Automating Evil > integration with CI/CD pipelines 65 DEPLOY Commit Continuous Integration tests OK? Yes No
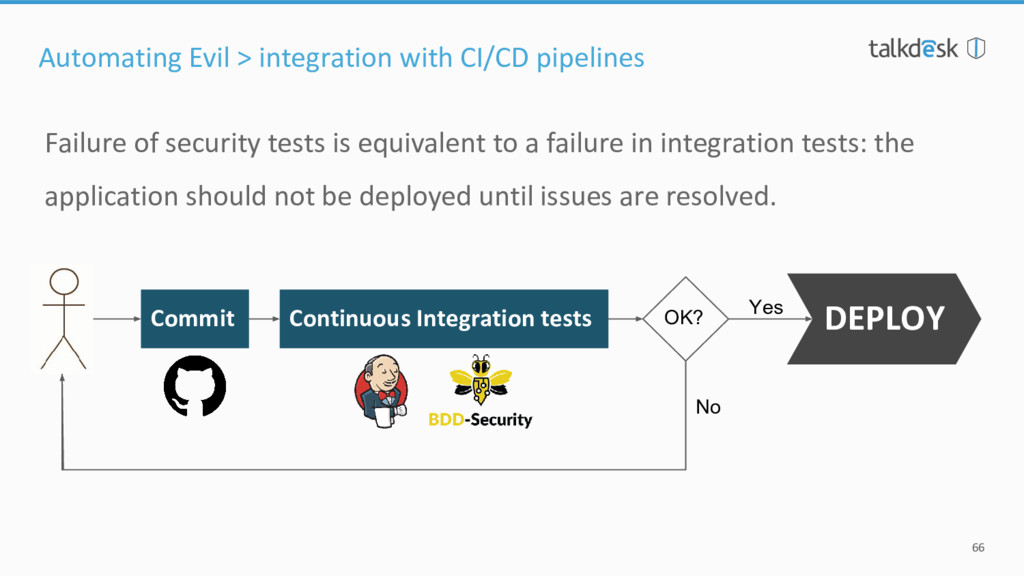
  34. Failure of security tests is equivalent to a failure in

    integration tests: the application should not be deployed until issues are resolved. Automating Evil > integration with CI/CD pipelines 66 DEPLOY Commit Continuous Integration tests OK? Yes No
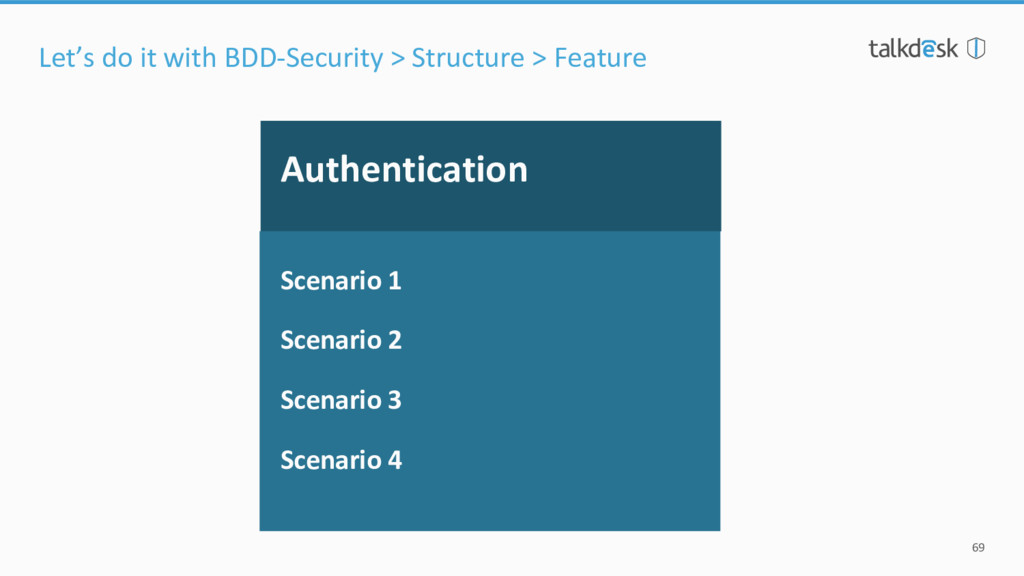
  35. Let’s do it with BDD-Security > Structure > Feature 69

    Authentication Scenario 2 Scenario 3 Scenario 4 Scenario 1
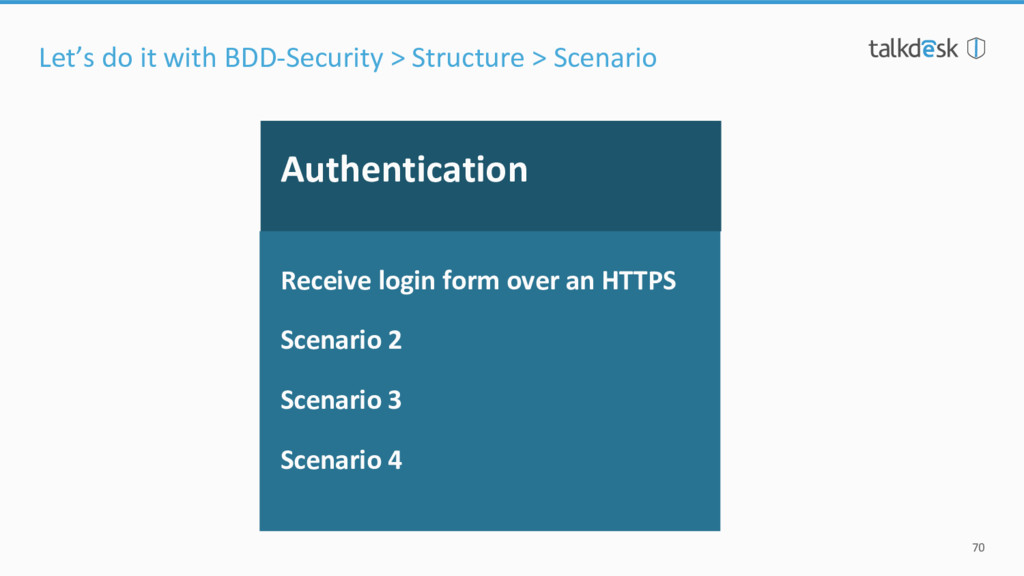
  36. Let’s do it with BDD-Security > Structure > Scenario 70

    Authentication Receive login form over an HTTPS Scenario 2 Scenario 3 Scenario 4
  37. Let’s do it with BDD-Security > Structure > Scenario 71

    Authentication Receive login form over an HTTPS Send auth credentials via HTTPS Scenario 3 Scenario 4
  38. Let’s do it with BDD-Security > Structure > Scenario 72

    Authentication Receive login form over an HTTPS Send auth credentials via HTTPS Throttle user after N failed logins Scenario 4
  39. Let’s do it with BDD-Security > Structure > Scenario 73

    Authentication Receive login form over an HTTPS Send auth credentials via HTTPS Throttle user after N failed logins Passwords should be case sensitive
  40. Feature: Session Management Scenario: Issue a new session ID after

    authentication Scenario: Invalidate the session when the user logs out Scenario: Invalidate the session after a period of inactivity Scenario: Set the 'secure' flag on the session cookie Scenario: Set the 'httpOnly' flag on the session cookie Let’s do it with BDD-Security > Example > Natural language 74
  41. Continuous Security in the DevOps World by Julien Vehent from

    Mozilla https://jvehent.github.io/continuous-security-talk/ Continuous Security Testing in a DevOps World by Stephen de Vries https://www.youtube.com/watch?v=M_uZPArkln4 References 79