Share
Embed
GitHub Universe 26 Sony
ソニー株式会社
October 29, 2026
Transcript
19 slides
-
GitHub configuration as code Scaling org management with Terraform Yasuhiro
Osaki Software Engineer Sony -
Approach 01 Codify every GitHub setting in Terraform. 02 Make
admin work transparent through pull requests. 03 Centralized control, no bottleneck. -
Session Agenda 01 Governance Policy 02 Infrastructure as Code 03
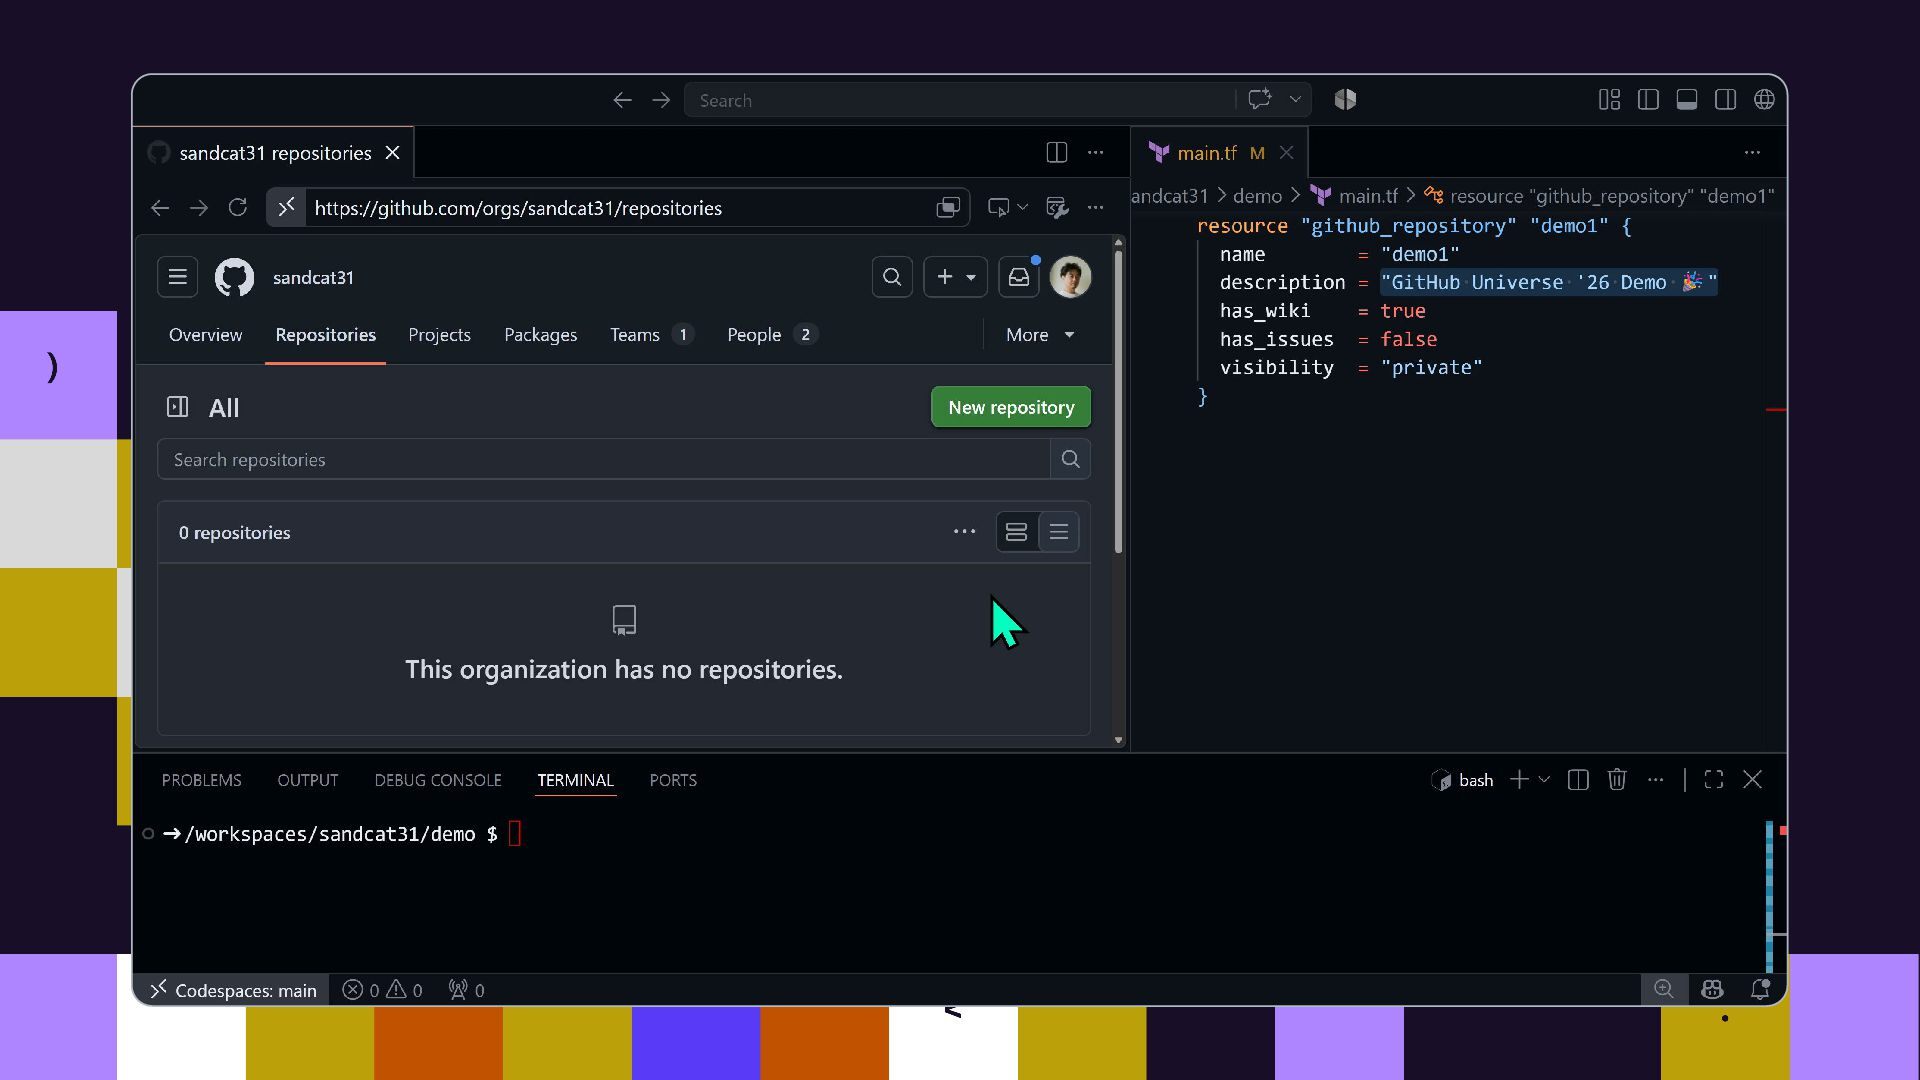
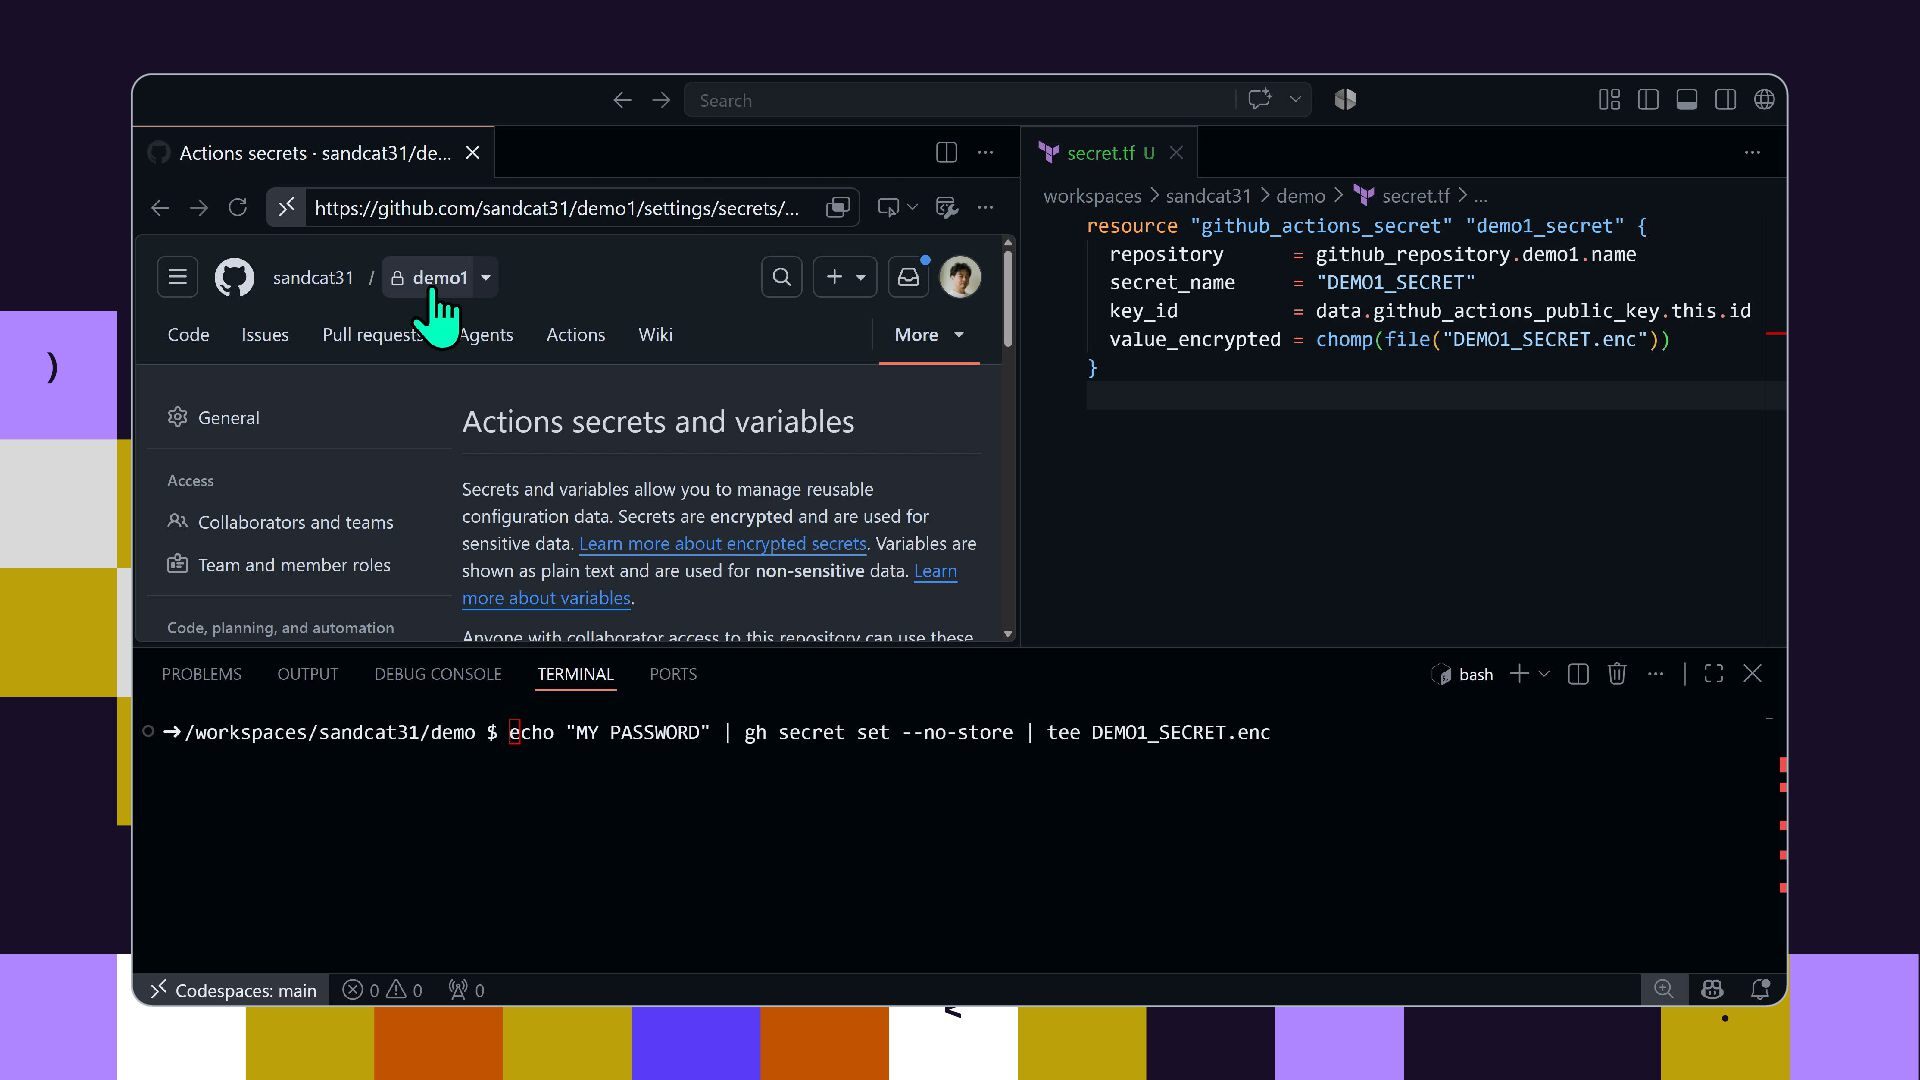
Live Demo 04 Tips -
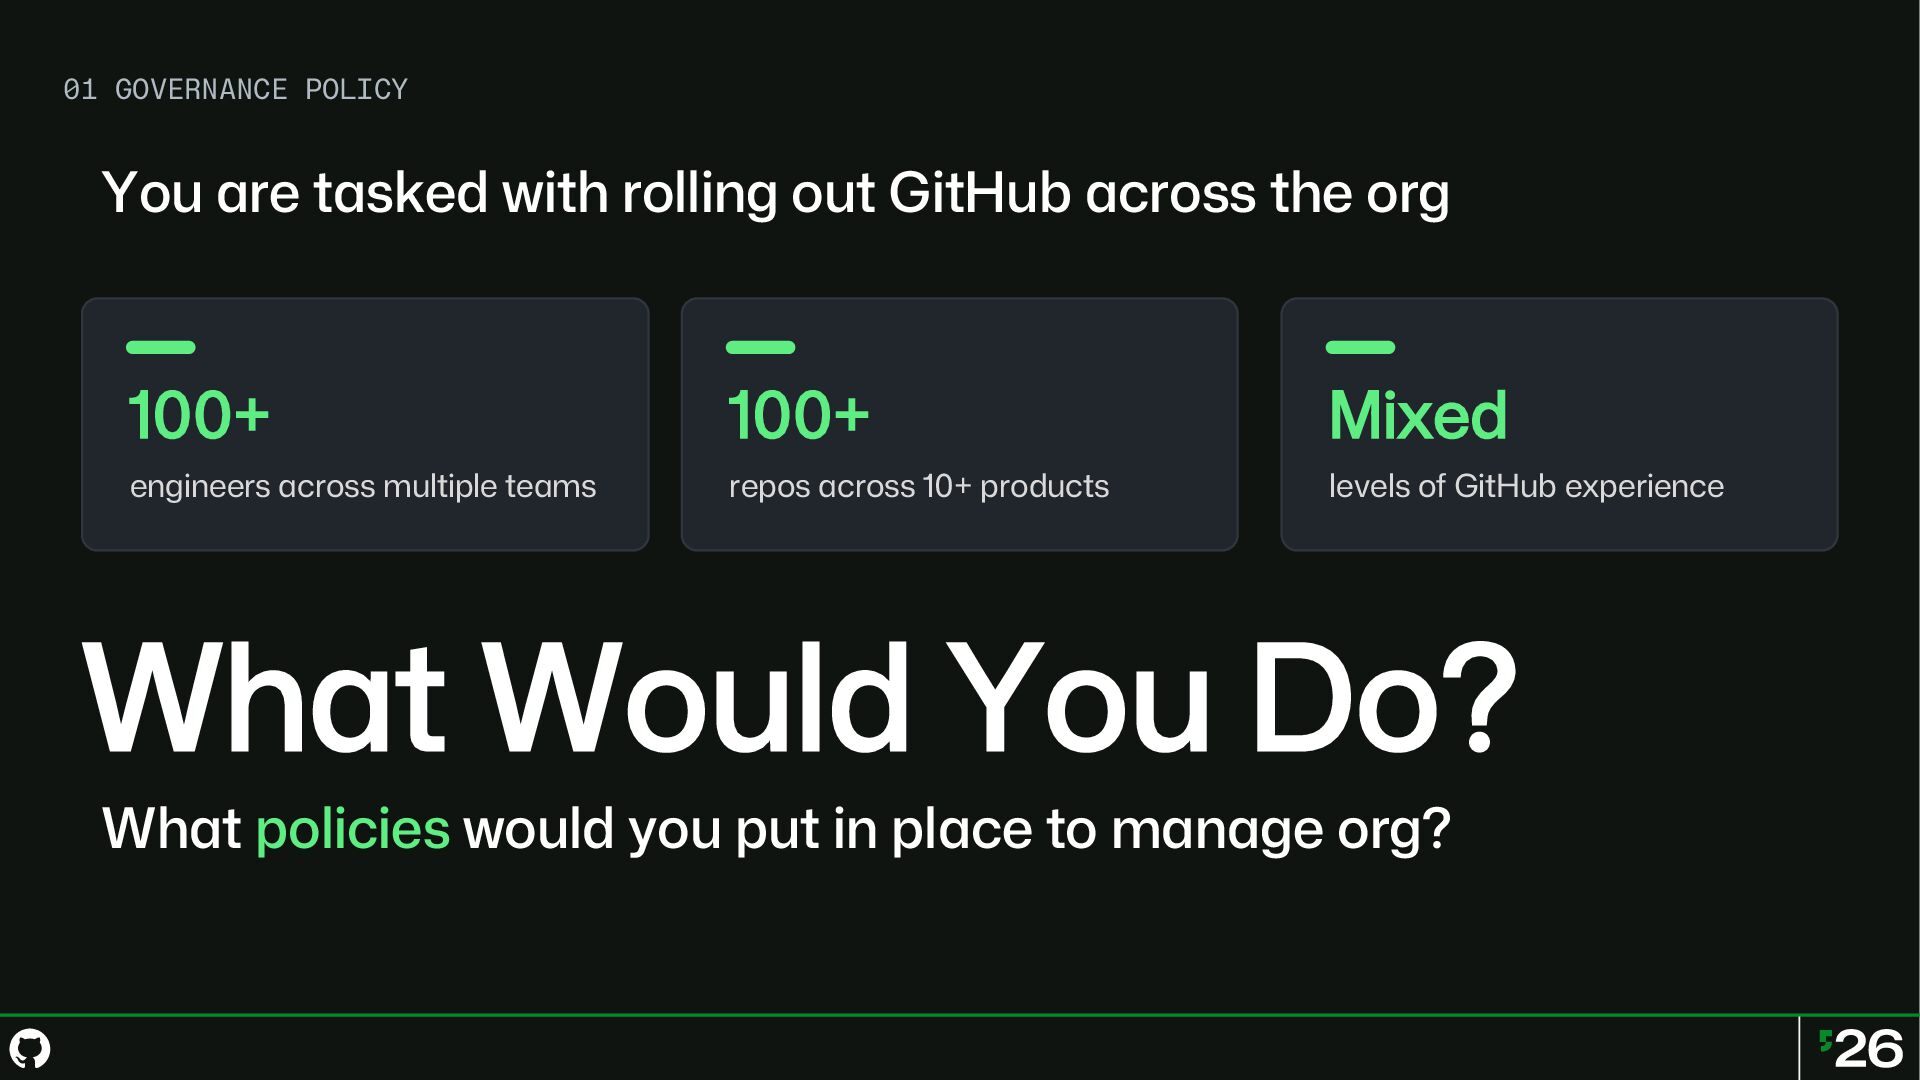
01 GOVERNANCE POLICY You are tasked with rolling out GitHub
across the org 100+ 100+ Mixed engineers across multiple teams repos across 10+ products levels of GitHub experience What Would You Do? What policies would you put in place to manage org? -
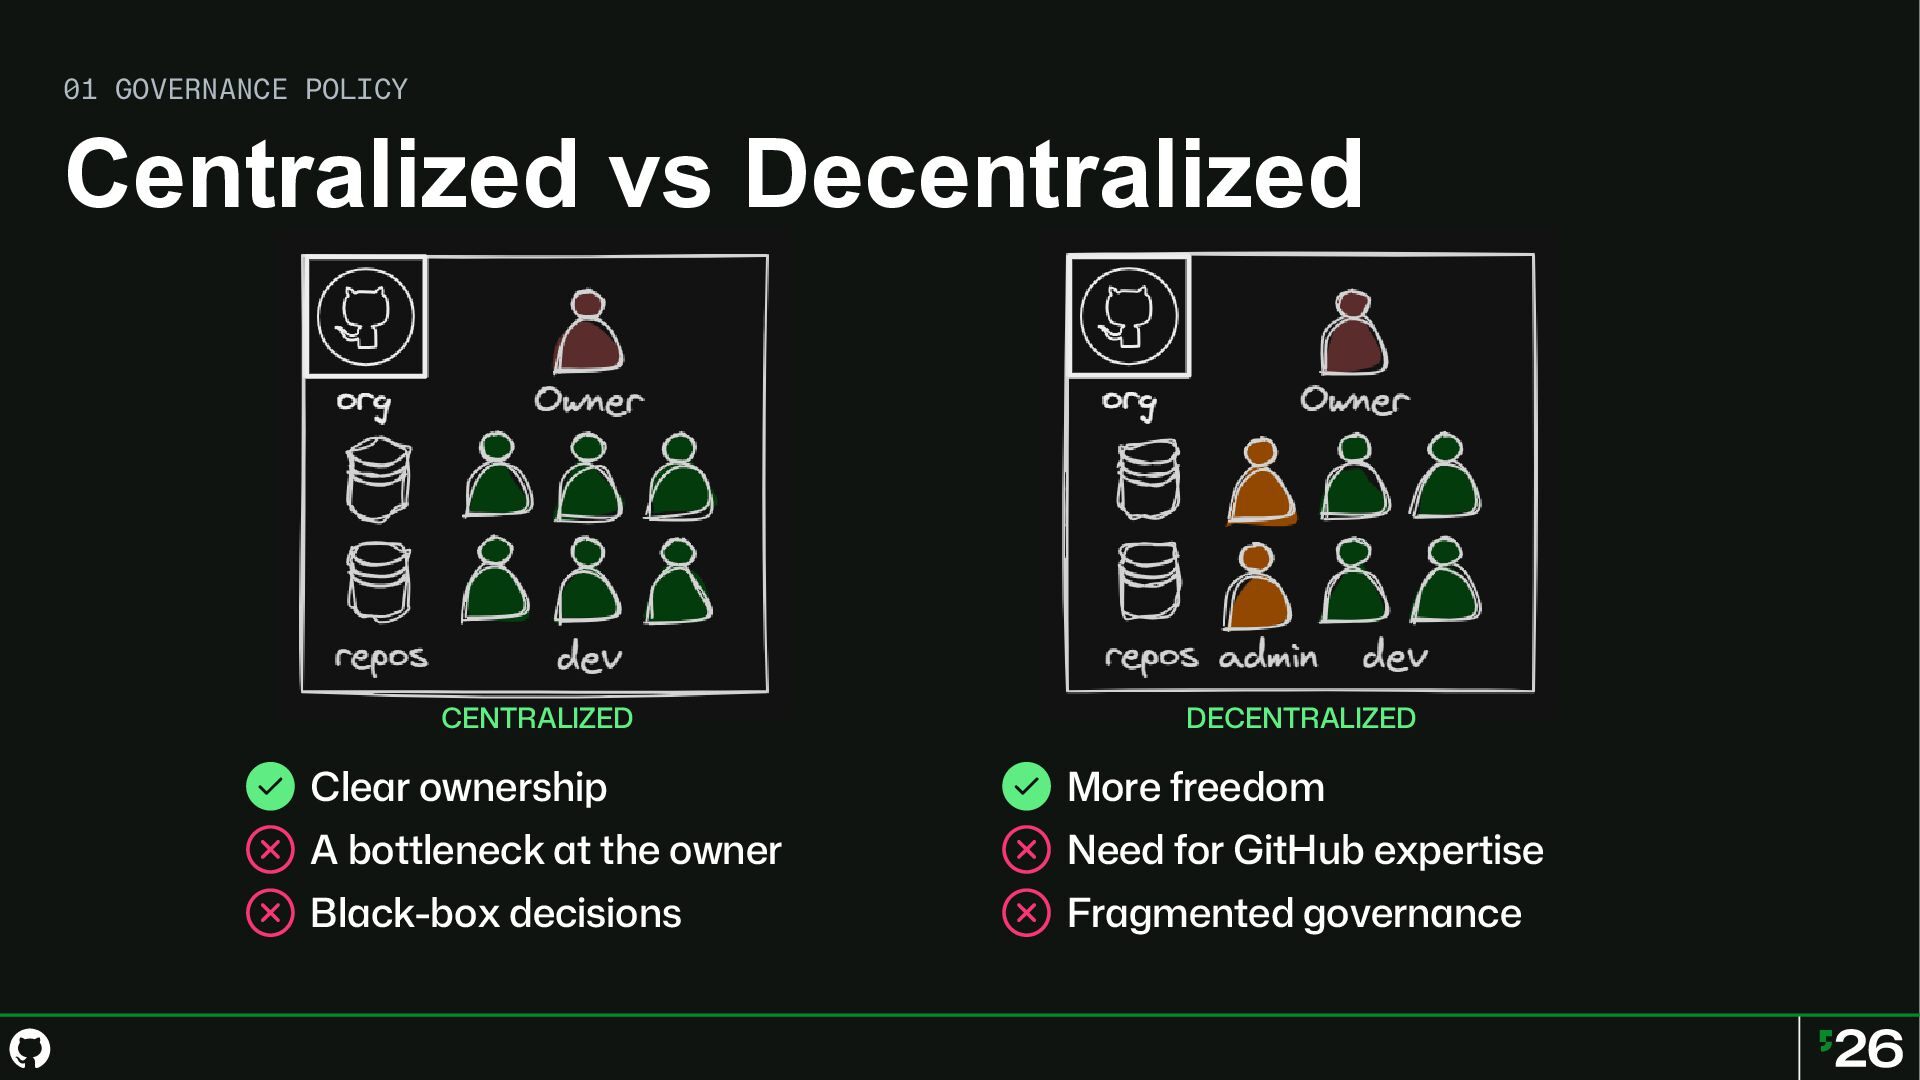
01 GOVERNANCE POLICY Centralized vs Decentralized CENTRALIZED DECENTRALIZED Clear ownership
More freedom A bottleneck at the owner Need for GitHub expertise Black-box decisions Fragmented governance -
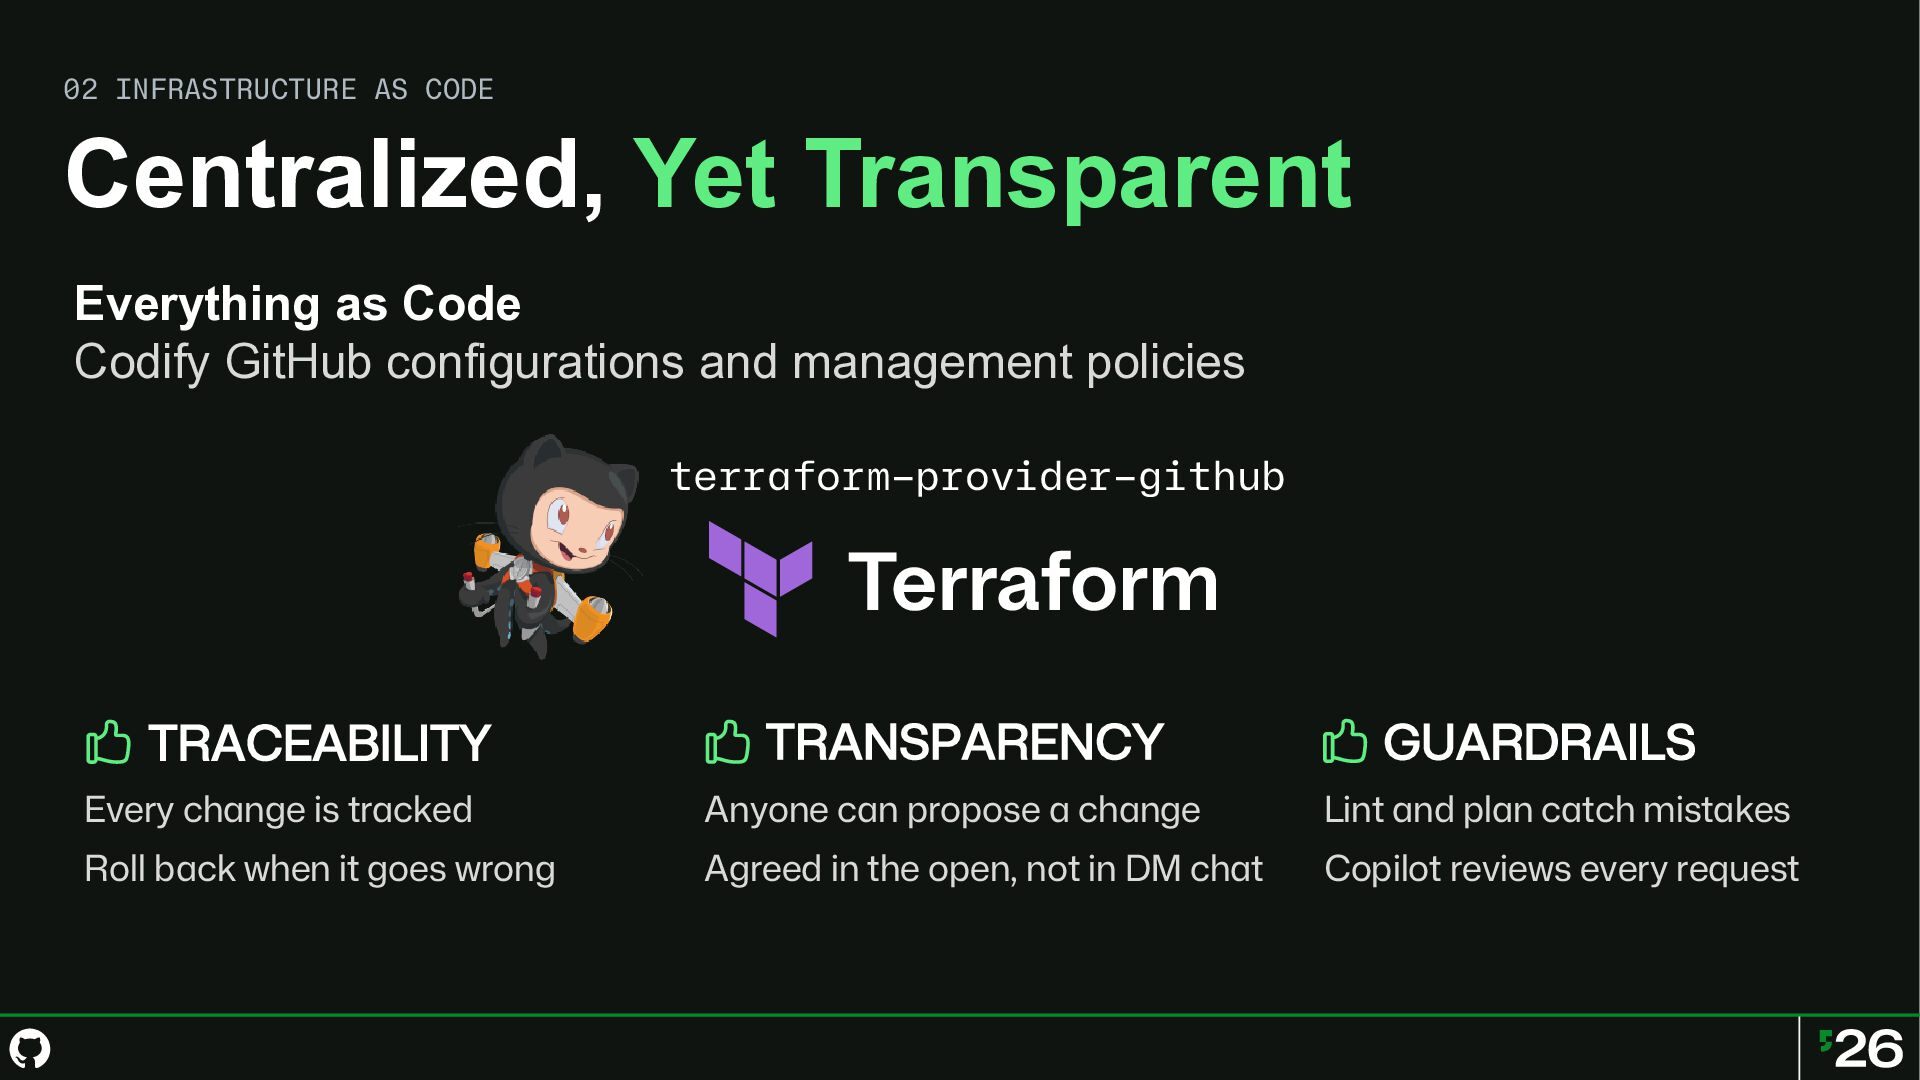
02 INFRASTRUCTURE AS CODE Centralized, Yet Transparent Everything as Code
Codify GitHub configurations and management policies terraform-provider-github TRANSPARENCY GUARDRAILS Every change is tracked Anyone can propose a change Lint and plan catch mistakes Roll back when it goes wrong Agreed in the open, not in DM chat Copilot reviews every request TRACEABILITY -
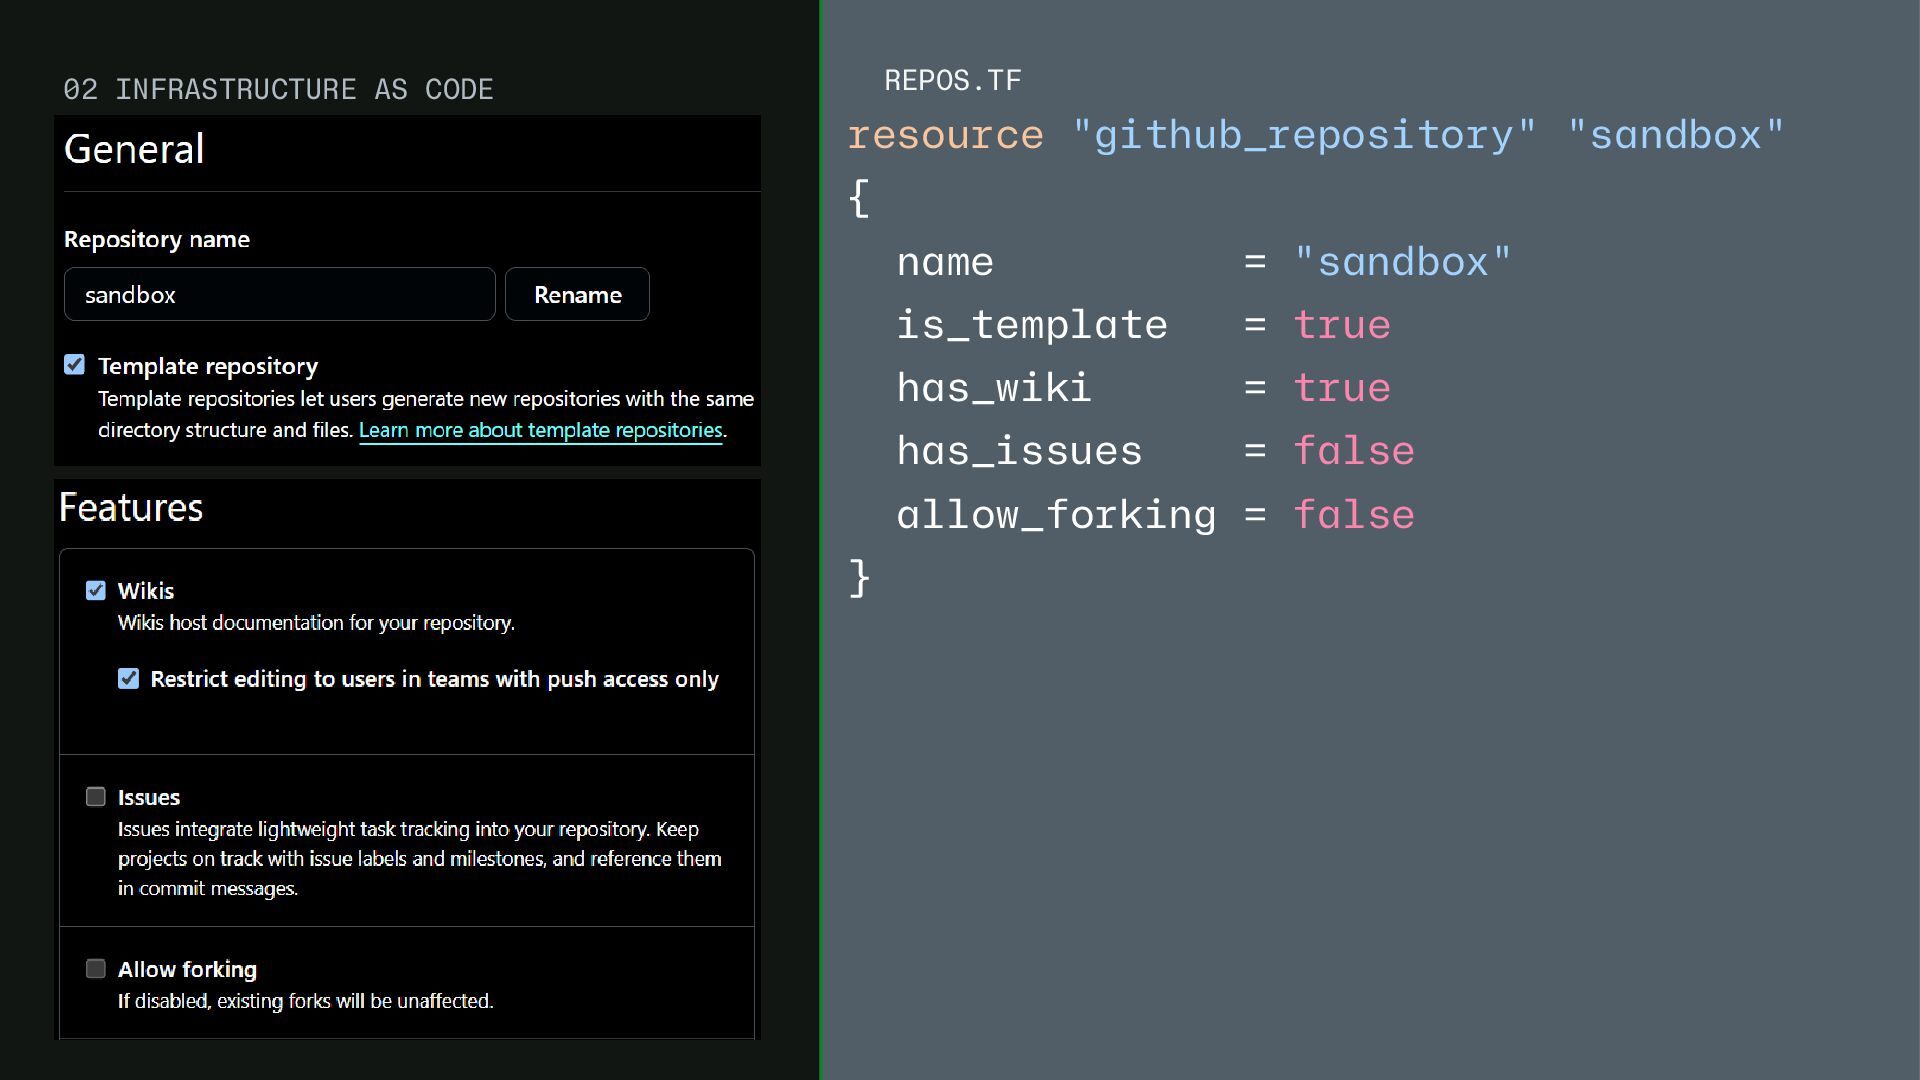
02 INFRASTRUCTURE AS CODE REPOS.TF resource "github_repository" "sandbox" { name
= "sandbox" is_template = true has_wiki = true has_issues = false allow_forking = false } -
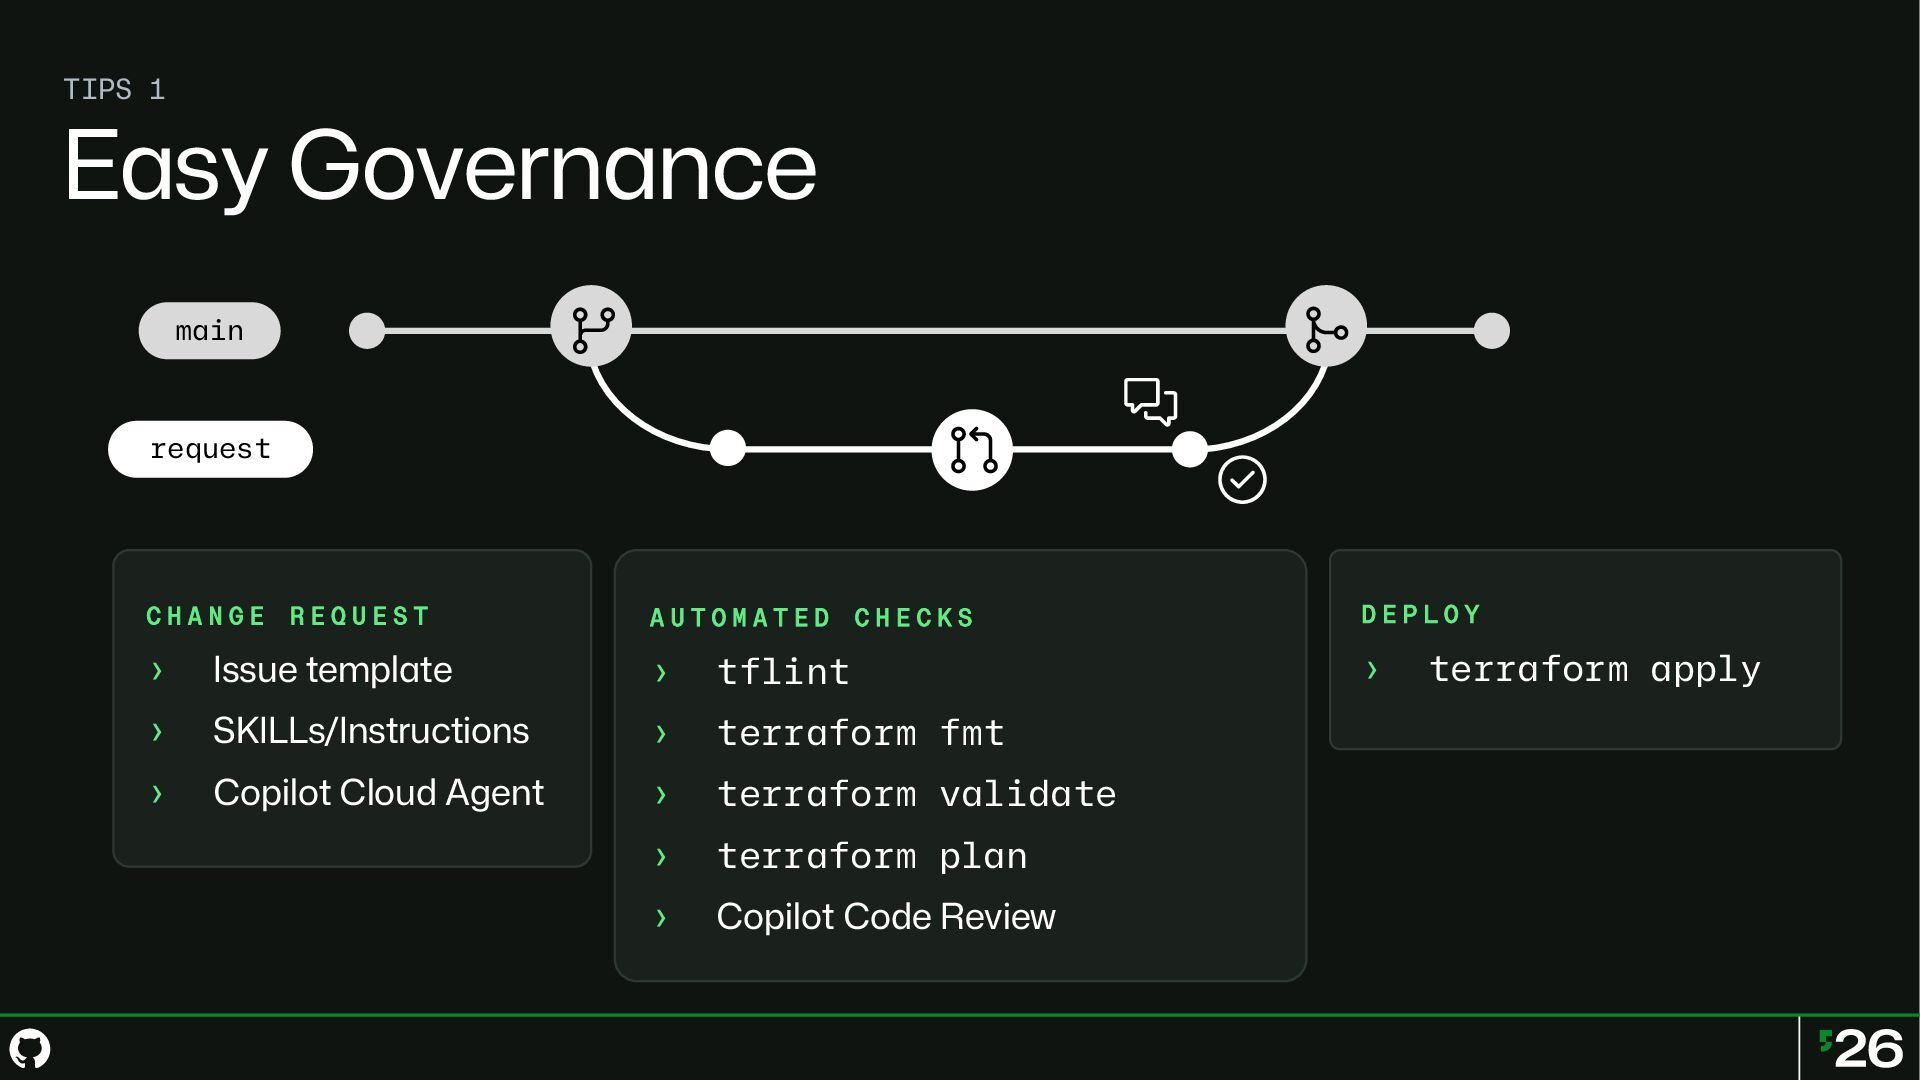
TIPS 1 Easy Governance main request CHANGE REQUEST AUTOMATED CHECKS
› Issue template › tflint › SKILLs/Instructions › terraform fmt › Copilot Cloud Agent › terraform validate › terraform plan › Copilot Code Review DEPLOY › terraform apply -
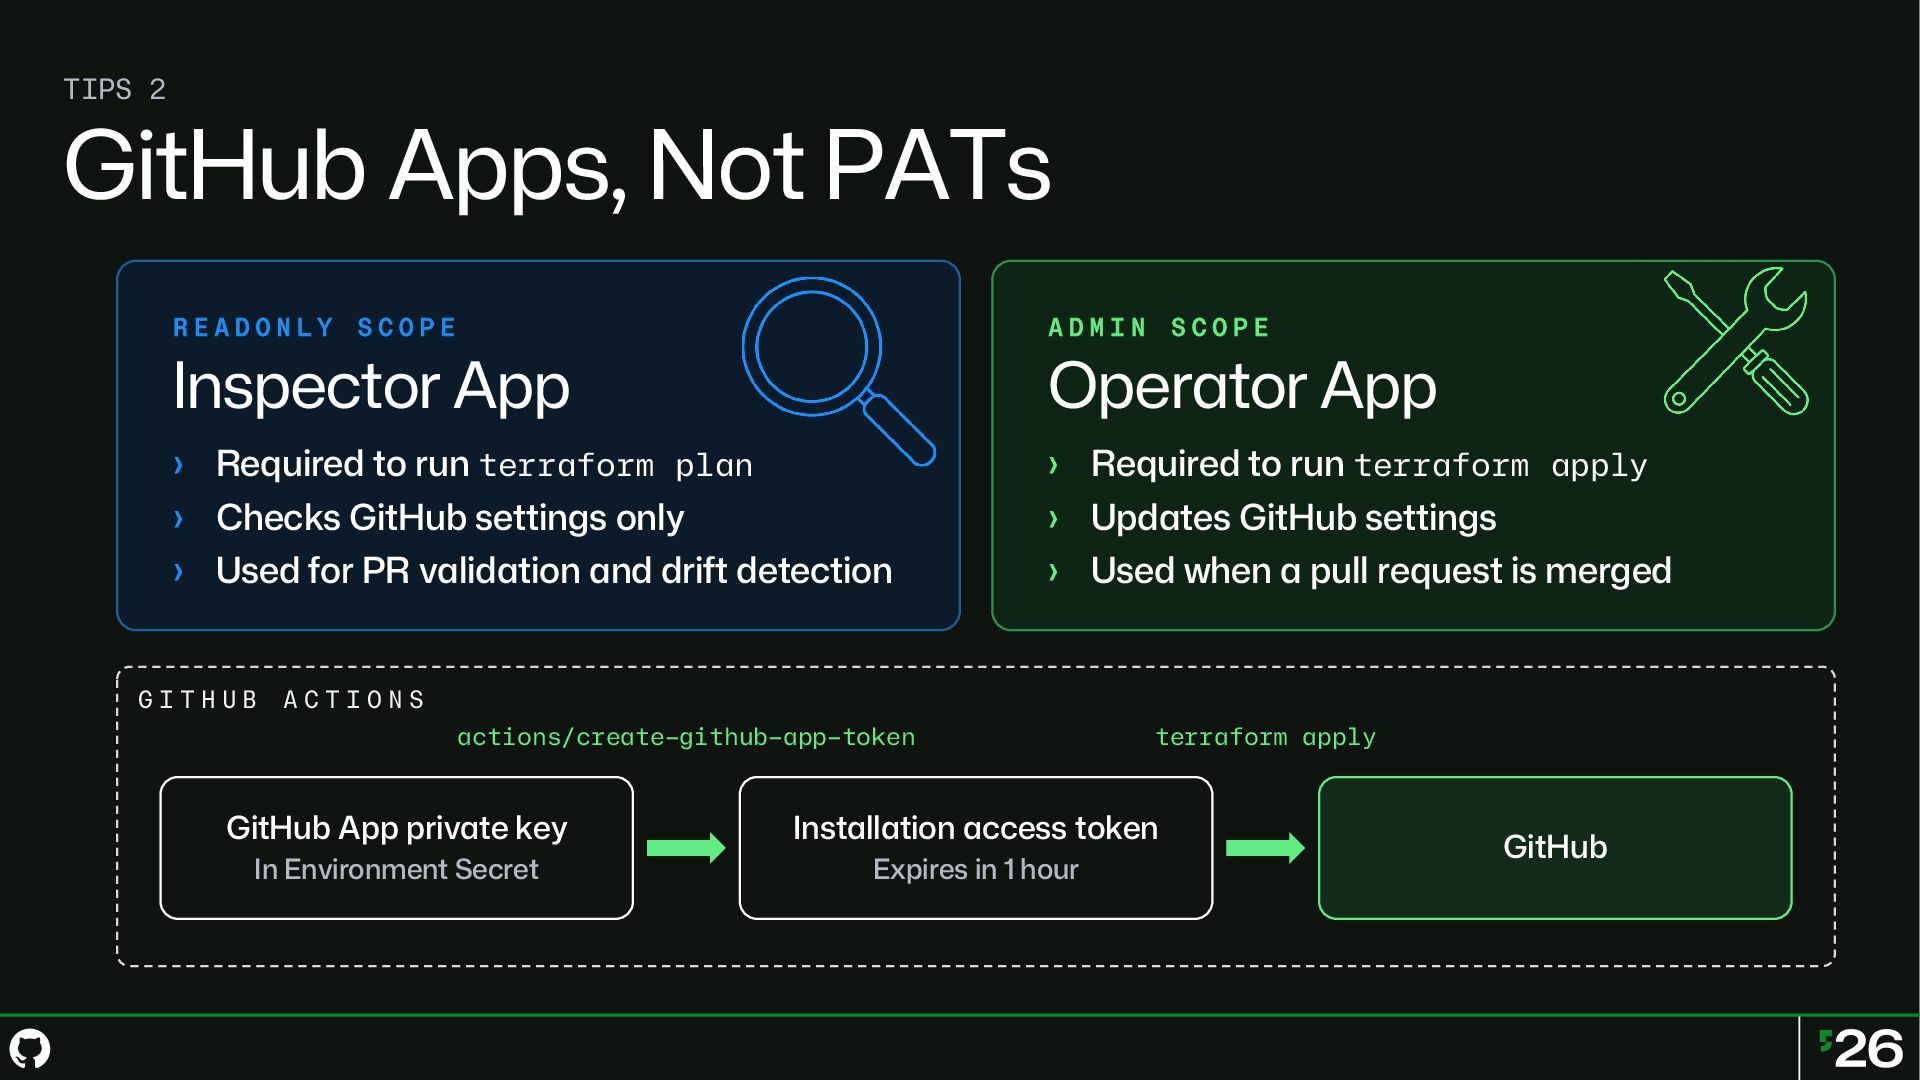
TIPS 2 GitHub Apps, Not PATs READONLY SCOPE ADMIN Inspector
App Operator App › Required to run terraform plan › Checks GitHub settings only › Used for PR validation and drift detection GITHUB SCOPE › Required to run terraform apply › Updates GitHub settings › Used when a pull request is merged ACTIONS actions/create-github-app-token terraform apply GitHub App private key Installation access token In Environment Secret Expires in 1 hour GitHub -
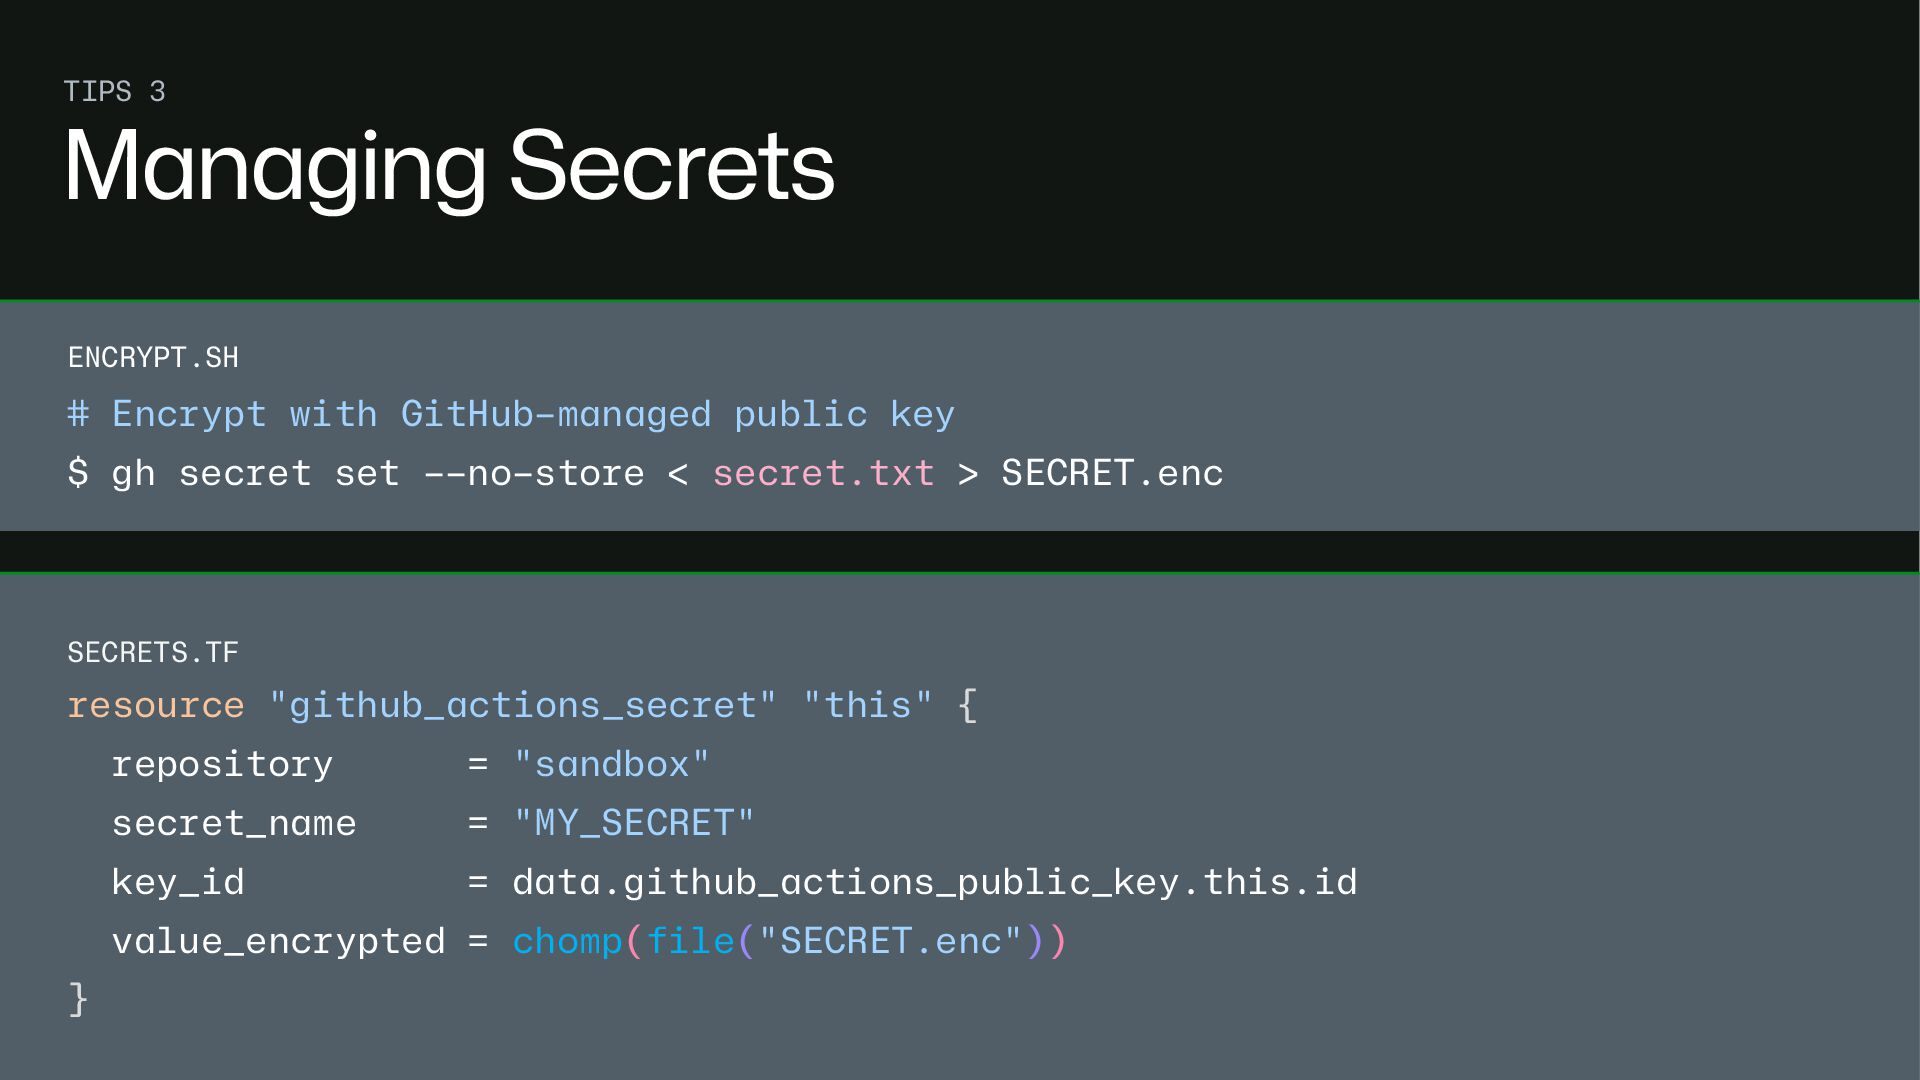
TIPS 3 Managing Secrets ENCRYPT.SH # Encrypt with GitHub-managed public
key $ gh secret set --no-store < secret.txt > SECRET.enc SECRETS.TF resource "github_actions_secret" "this" { repository = "sandbox" secret_name = "MY_SECRET" key_id = data.github_actions_public_key.this.id value_encrypted = chomp(file("SECRET.enc")) } -
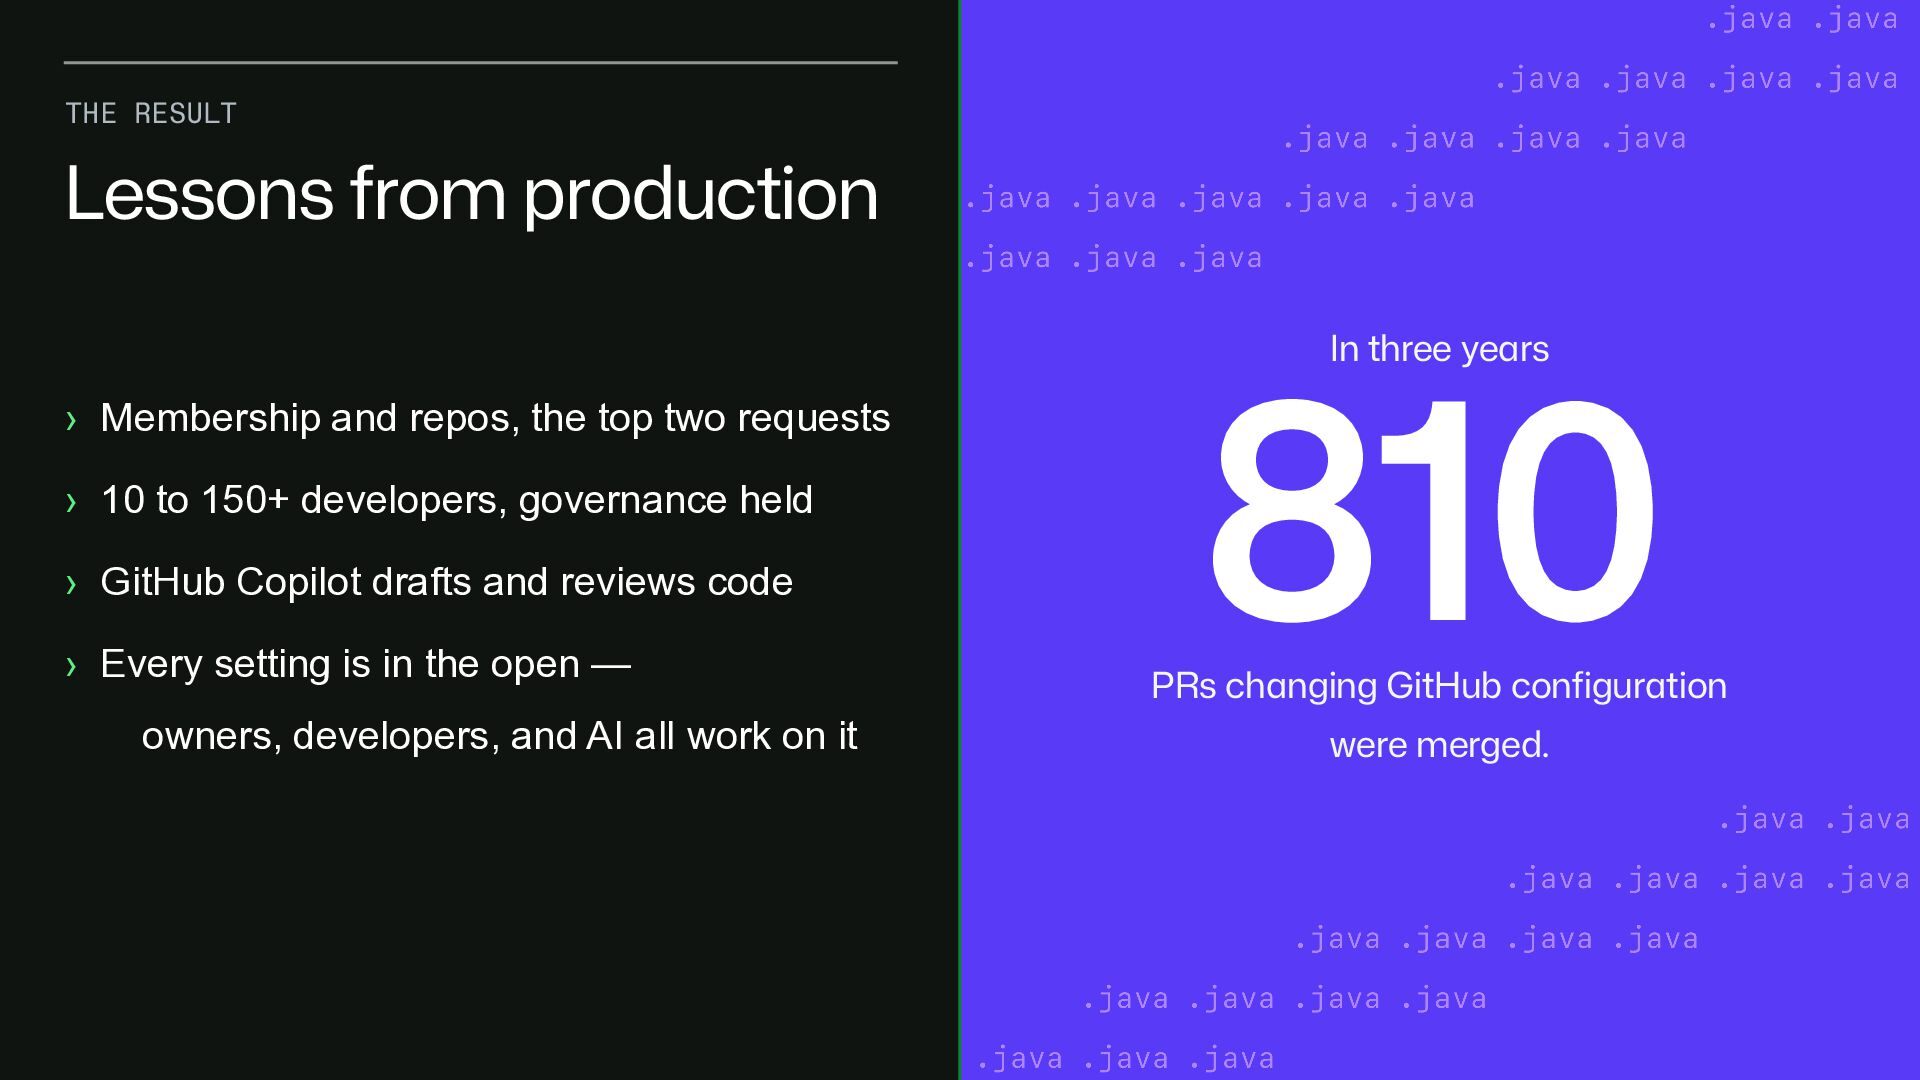
THE RESULT Lessons from production 810 In three years ›
Membership and repos, the top two requests › 10 to 150+ developers, governance held › GitHub Copilot drafts and reviews code › Every setting is in the open — owners, developers, and AI all work on it PRs changing GitHub configuration were merged. -
WRAP UP Centralized, yet transparent. Infrastructure as Code with Terraform.
We manage GitHub with confidence. -
How was this session? We do actually read these. It's
how Universe gets better every year. Scan to review.