Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
full page caching in general and Django
Search
Denis Cornehl
May 19, 2015
Technology
120
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
full page caching in general and Django
Denis Cornehl
May 19, 2015
More Decks by Denis Cornehl
See All by Denis Cornehl
PDF generation techniques in Python and Django
syphar
0
96
Other Decks in Technology
See All in Technology
Conditional PED-ANOVA: Hyperparameter Importance in Hierarchical & Dynamic Search Spaces
pfn
PRO
0
130
会社説明資料
persolserverworks
0
9.8k
AIにシークレットを見せない、WSL2で安全な開発環境
yazm
0
300
Getting Started with Google Antigravity
glaforge
0
310
オントロジーって 結局なにもの? AI エージェントに「意味」を渡す知識設計の話
greenmidori
0
200
遠藤な_めぐろLT #38 「社内のAI活用推進」@麻布台_20261009
endonanana
0
130
AI × アーキテクト 第1・2章|生成AIの課題とアーキテクトの素養
daidaidai
0
170
TinyGoでオブザーバビリティ?OpenTelemetryはTinyGoで使えるのか / Is OpenTelemetry available in TinyGo environment?
ymotongpoo
2
140
re:Invent初参加で変わったこと、2回目にやってみたいこと(JAWS-UG彩の国埼玉 #12)
mhrtech
2
230
ソフトウェア ファクトリー - 再現性のあるソフトウェアの工場づくり / Software factory
iktakahiro
6
4.9k
二歩目のフロントエンド・ウェブアクセシビリティ
camiha
2
590
20261017福岡devIO 「AIは"良いダッシュボード"を作れるか?
jtakeda
0
150
Featured
See All Featured
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Leveraging LLMs for student feedback in introductory data science courses - posit::conf(2025)
minecr
1
440
The Hidden Cost of Media on the Web [PixelPalooza 2025]
tammyeverts
2
530
Organizational Design Perspectives: An Ontology of Organizational Design Elements
kimpetersen
PRO
1
850
The State of eCommerce SEO: How to Win in Today's Products SERPs - #SEOweek
aleyda
2
12k
Why Your Marketing Sucks and What You Can Do About It - Sophie Logan
marketingsoph
0
430
Why You Should Never Use an ORM
jnunemaker
PRO
61
10k
A Modern Web Designer's Workflow
chriscoyier
699
190k
The Anti-SEO Checklist Checklist. Pubcon Cyber Week
ryanjones
0
270
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Navigating Team Friction
lara
192
16k
Agile Leadership in an Agile Organization
kimpetersen
PRO
0
280
Transcript
Things Caches Do HTTP / Headers
kinds of web caches • Browser Caches • Proxy Caches
• Gateway Caches
Gateway caches • Varnish on your server • CDN •
„reverse proxy“
expiration • Cache-Control: max-age=N • Expires (for your CDN) •
Surrogate-Control: max-age=N • Cache-Control: s-max-age=N
expiration
expiration
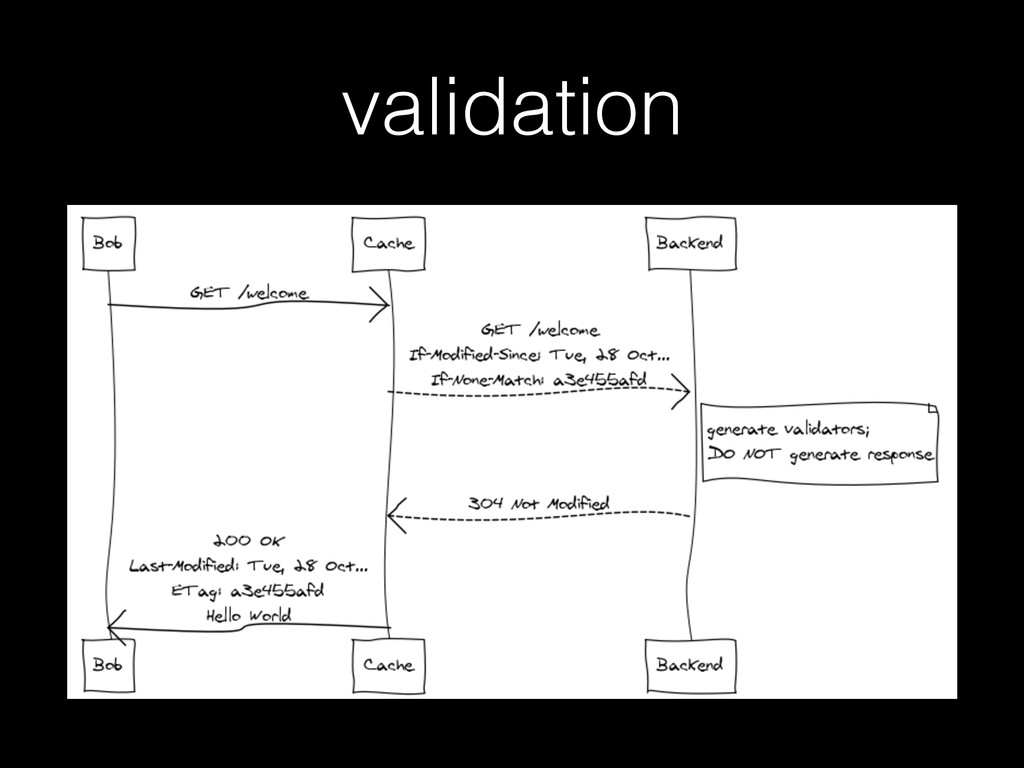
validation • Last-Modified / If-Modified-Since • ETag / If-None-Match •
HTTP Response: 304 Not Modified
validation
validation
cache key
cache key https://api.thermondo.de/settings/
cache key https://api.thermondo.de/settings/ • method (GET) • path (/api/settings/) •
GET arguments (most times) • more?
cache key https://api.thermondo.de/settings/ • method (GET) • path (/api/settings/) •
GET arguments (most times) • Language • Encoding • more?
cache key https://api.thermondo.de/settings/ • method (GET) • path (/api/settings/) •
GET arguments (most times) • Language • Encoding • User Session
vary $ http -h https://api.thermondo.de/settings/ „Authorization: Token secrettoken" HTTP/1.1 200
OK Allow: GET, HEAD, OPTIONS Api-Version: 1.0.0 Connection: keep-alive Content-Encoding: gzip Content-Language: en-us Content-Length: 646 Content-Type: application/json Date: Mon, 30 Mar 2015 12:48:31 GMT Etag: "9987fab5ec7adb7c70be2a24e3665a5b;gzip" Server: waitress Vary: Accept, Accept-Language, Cookie, Accept-Encoding Via: 1.1 vegur
vary $ http -h https://api.thermondo.de/settings/ „Authorization: Token secrettoken" HTTP/1.1 200
OK Allow: GET, HEAD, OPTIONS Api-Version: 1.0.0 Connection: keep-alive Content-Encoding: gzip Content-Language: en-us Content-Length: 646 Content-Type: application/json Date: Mon, 30 Mar 2015 12:48:31 GMT Etag: "9987fab5ec7adb7c70be2a24e3665a5b;gzip" Vary: Accept, Accept-Language, Cookie, Accept-Encoding Via: 1.1 vegur
on cookies
on cookies • session • google analytics • often breaks
caching
on csrf • different content per session • often breaks
caching
Static Files js / css / images
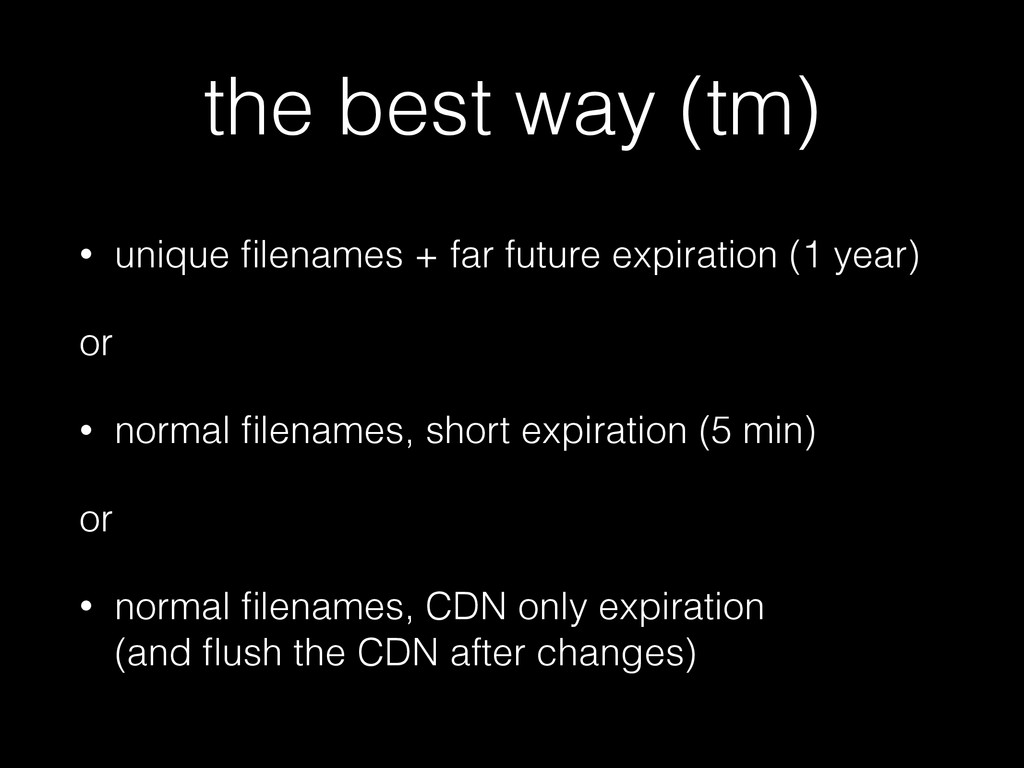
the best way (tm) • unique filenames + far future
expiration (1 year) or • normal filenames, short expiration (5 min) or • normal filenames, CDN only expiration (and flush the CDN after changes)
Page Caching in Django
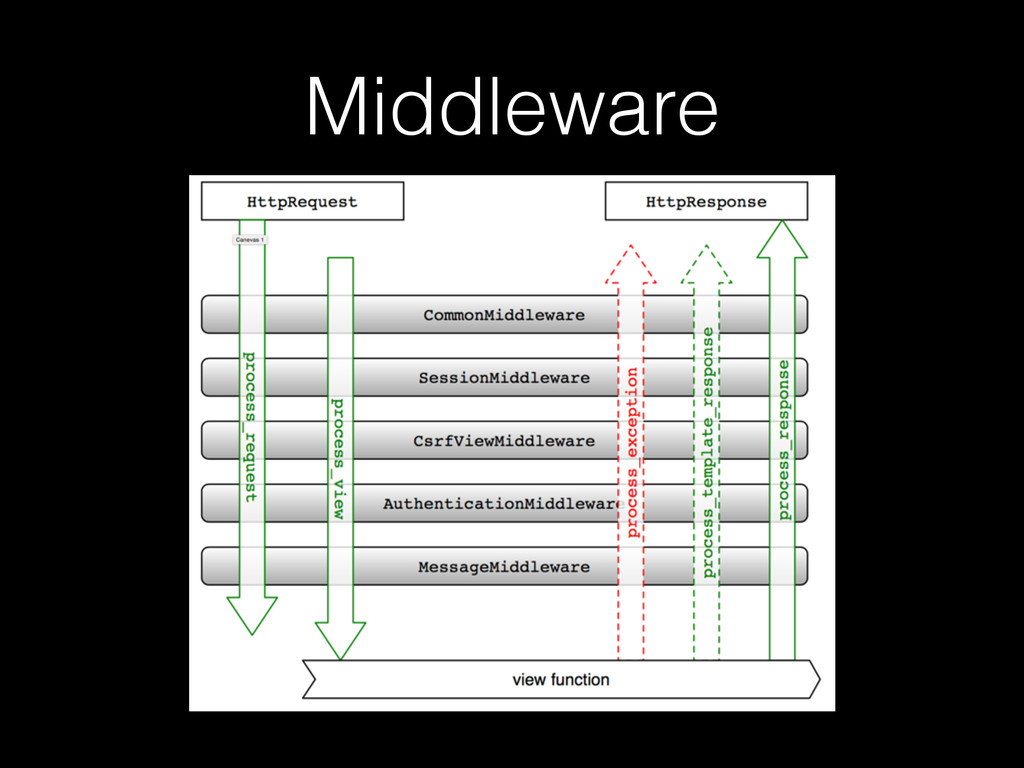
Middleware
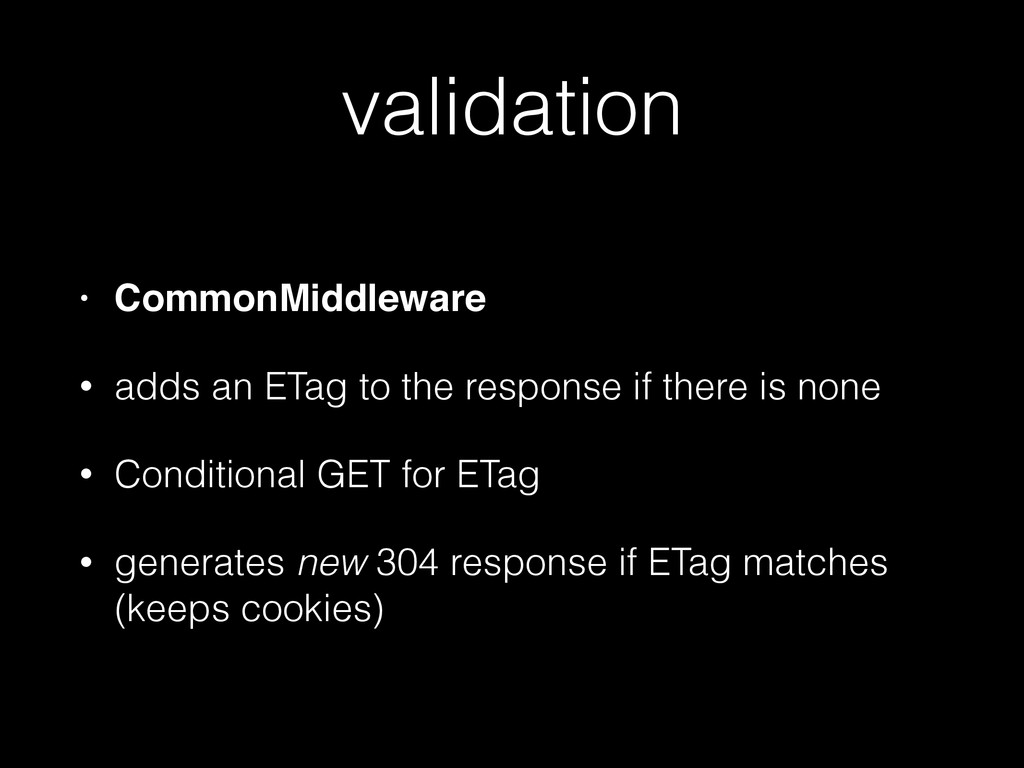
validation • CommonMiddleware • adds an ETag to the response
if there is none • Conditional GET for ETag • generates new 304 response if ETag matches (keeps cookies)
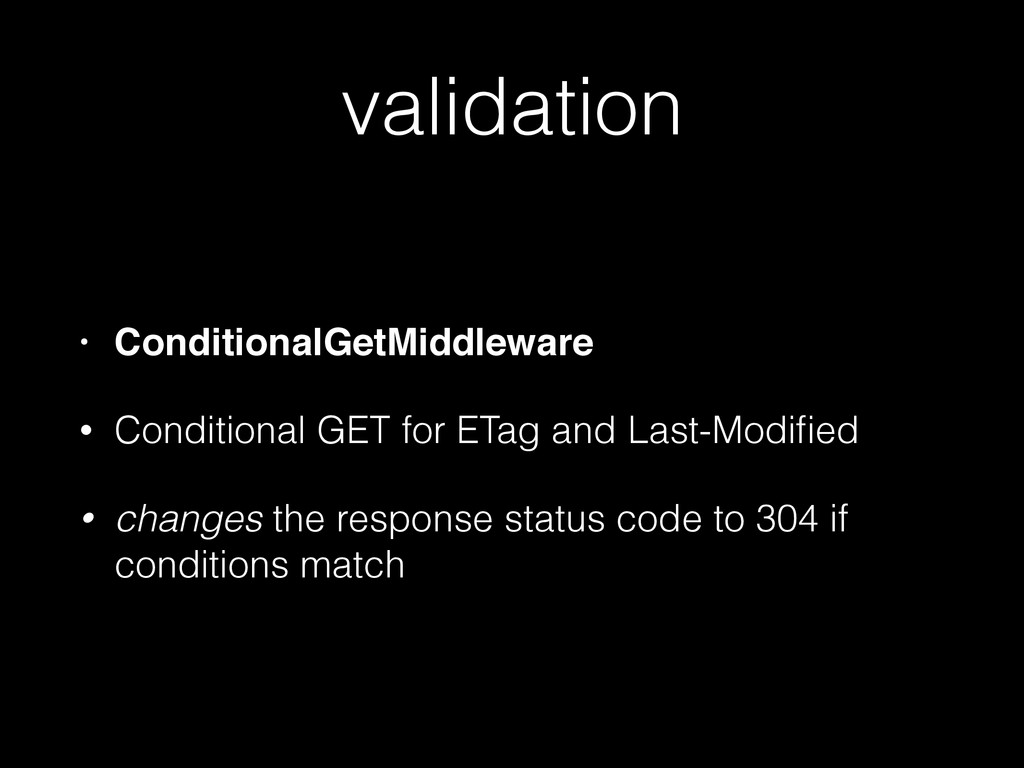
validation • ConditionalGetMiddleware • Conditional GET for ETag and Last-Modified
• changes the response status code to 304 if conditions match
validation • @etag, @last_modified, @condition • callables for ETag or
Last-Modified calculation • best server performance • most RFC compliant
validation • GZipMiddleware • breaks Django’s ETag handling • changes
ETag in response
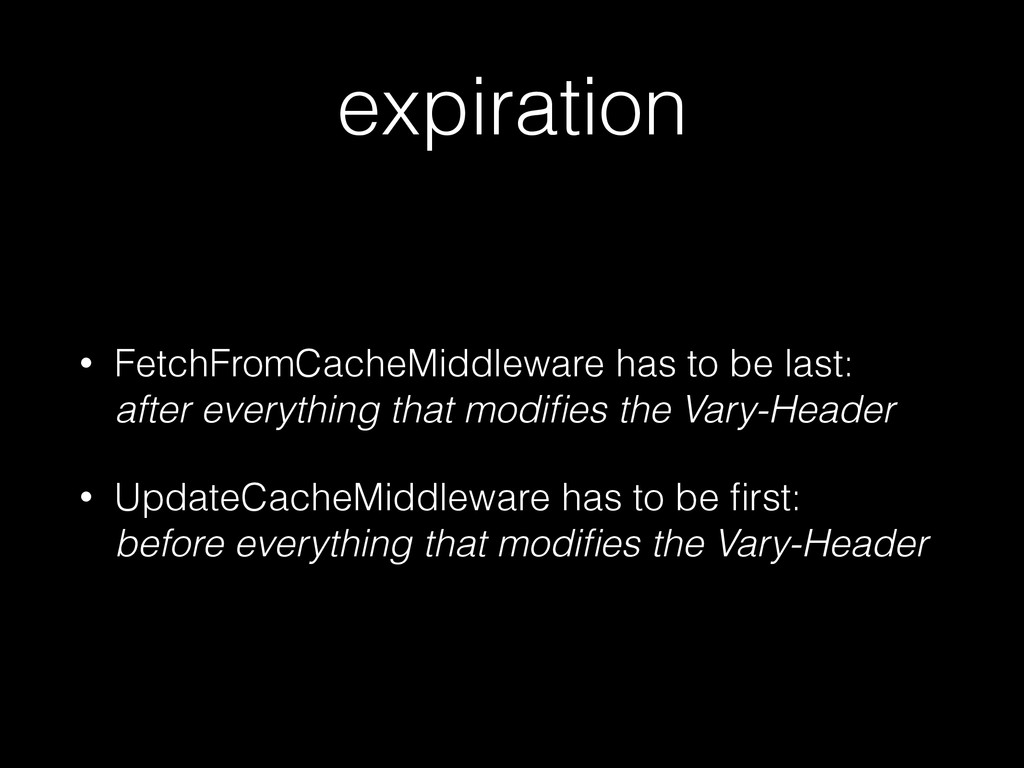
expiration • FetchFromCacheMiddleware has to be last: after everything
that modifies the Vary-Header • UpdateCacheMiddleware has to be first: before everything that modifies the Vary-Header
Middleware
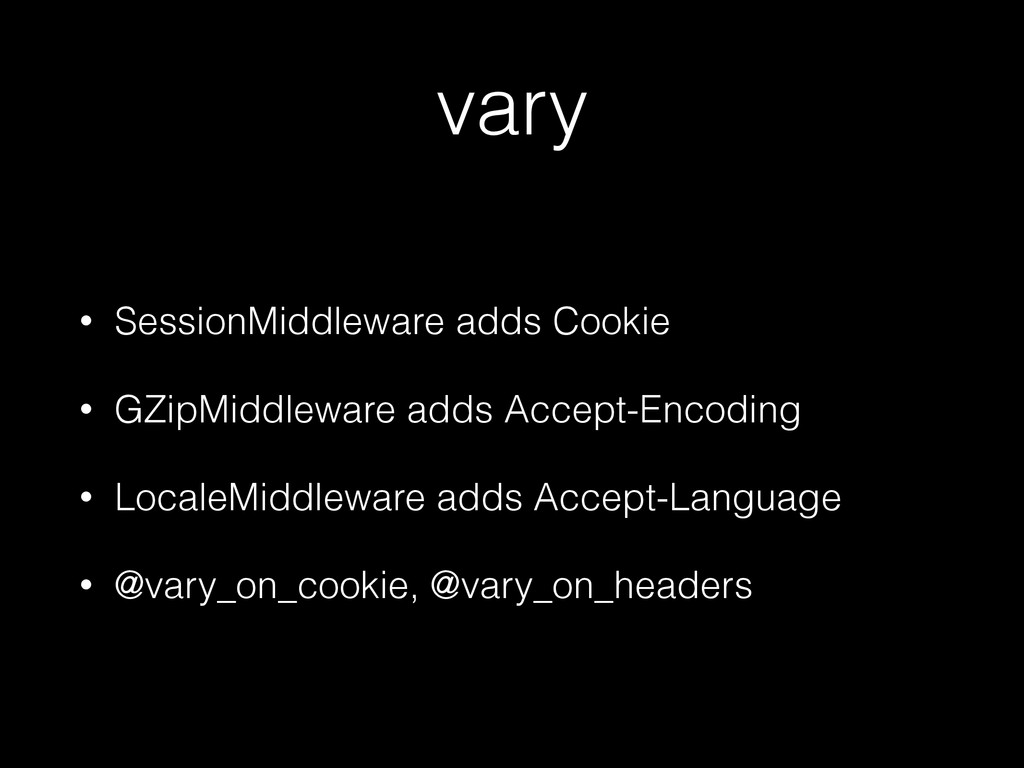
vary • SessionMiddleware adds Cookie • GZipMiddleware adds Accept-Encoding •
LocaleMiddleware adds Accept-Language • @vary_on_cookie, @vary_on_headers
Django sucks here but it’s right
expiration breaks • when you use sessions • when you
use CSRF protection (which uses cookies) • when you use google analytics
easy (wrong) way • drop vary header in custom middleware
(security risk, wrong data)
possible but hard way • Middleware to filter google analytics
cookies and add them back later they have no effect on the content • be very careful with using the session / user in your views • be very careful with using forms (which use CSRF Protection)
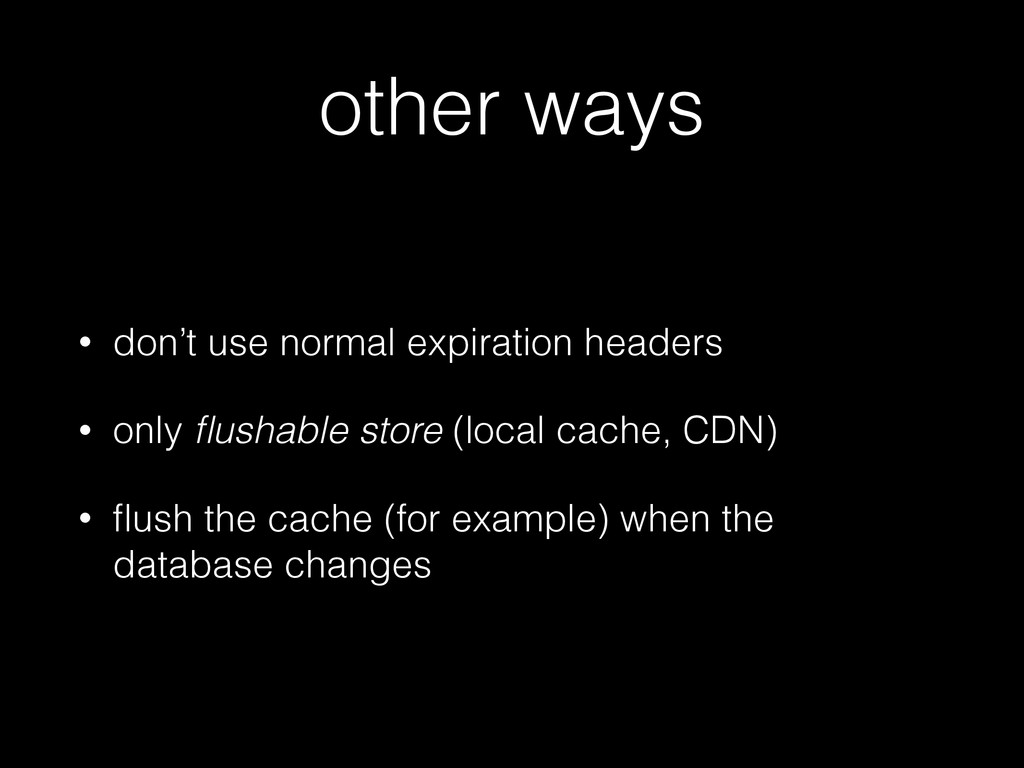
other ways • don’t use normal expiration headers • only
flushable store (local cache, CDN) • flush the cache (for example) when the database changes
not included • @cache_control (private, public, revalidate, …) • stale
expire headers


 syphar
 pfn
 persolserverworks
 yazm
 glaforge
 greenmidori
 endonanana
 daidaidai
 ymotongpoo
 mhrtech
 iktakahiro
 camiha
 jtakeda
 aki_iinuma
 minecr
 tammyeverts
 kimpetersen
 aleyda
 marketingsoph
 jnunemaker
 chriscoyier
 ryanjones
 eileencodes
 lara