Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
GitHub ActionsのOIDC認証
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Tomofumi Kondo
March 01, 2022
Programming
260
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
GitHub ActionsのOIDC認証
2021年に新しく発表された、GitHub ActionsのOIDC認証機能についての紹介。
Tomofumi Kondo
March 01, 2022
More Decks by Tomofumi Kondo
See All by Tomofumi Kondo
半永久的に提供し続けられるプライベートクラウドを目指して ― 利用者の認知負荷を抑えるAPI抽象化とハードウェア世代交代の基盤設計
tomokon
0
520
OVSとLinuxネットワークで実現するHVの透過的プロキシとセキュアなVPCネットワーク
tomokon
0
48
kagentとMCPで実現するKubernetes-nativeなAIアラート自動応答システム
tomokon
0
36
Cinder Backupを活用したユーザー負担の少ないクロスリージョンボリューム移行システム
tomokon
0
27
Tinkerbellから学ぶ、Podで DHCPをリッスンする手法
tomokon
0
260
Goで作る!ストレージ筐体間での安全なCinder volume移行システムの開発と運用
tomokon
0
200
Goによるインタプリタ開発
tomokon
1
110
初めてのTerraform
tomokon
1
65
ハッカソンで便利なインフラ構築サービス
tomokon
0
290
Other Decks in Programming
See All in Programming
[2026-10-09]一枚の布で作らなくてもいい。 信頼性は「パッチワーク」で紡がれる~既存の運用と新しい可能性をつなぎ合わせてきたCREの話~
tosite
0
110
現場と育てるRailsモデリング 〜Spreadsheetから始めたモデル設計〜
siroemk
2
910
Vue Fes Japan の “作る側”に関わってみて
naokihaba
1
180
月間100万人のサービス刷新で、 技術選定をHonoに振り切った話
yutobara
8
6.9k
AWS CDKのカスタムリソースでContinuum(旧Security Agent)を実装した話 | Implementing Continuum (formerly Security Agent) via AWS CDK Custom Resource
akihisaikeda
2
160
Lambda durable functionsでHuman in the Loopを楽に…楽に……
har1101
1
190
[JA] Domain Modeling with Vanilla Rails: 「操作」から再考するRailsの設計論
yasaichi
4
830
우리의 Nitro Modules는 당신의 Turbo Modules보다 아름답다
l2hyunwoo
0
180
残高管理から台帳サービスへの進化
artoy
1
210
AI-Powered Domain-Driven Design
ziobrando
0
280
【加筆修正版】Laravel のアプリケーションをどこにデプロイするか #phpcon_ehime
akase244
0
160
When benchmarks go bad - what I learned from measuring performance wrong
hollycummins
0
240
Featured
See All Featured
Design of three-dimensional binary manipulators for pick-and-place task avoiding obstacles (IECON2024)
konakalab
0
630
"I'm Feeling Lucky" - Building Great Search Experiences for Today's Users (#IAC19)
danielanewman
230
23k
Google's AI Overviews - The New Search
badams
0
1.6k
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.1k
Practical Tips for Bootstrapping Information Extraction Pipelines
honnibal
25
2.1k
Leadership Guide Workshop - DevTernity 2021
reverentgeek
1
400
GraphQLの誤解/rethinking-graphql
sonatard
75
12k
How to Talk to Developers About Accessibility
jct
2
590
It's Worth the Effort
3n
188
29k
Chasing Engaging Ingredients in Design
codingconduct
0
370
Leading Effective Engineering Teams in the AI Era
addyosmani
9
2.8k
[RailsConf 2023] Rails as a piece of cake
palkan
59
7.1k
Transcript
GitHub ActionsのOIDC認証 東北大学4年 近藤智文 @tomokon_0314
目次 1. OIDCとは 2. GitHub ActionsのOIDC認証機能 3. デモ 4. まとめ
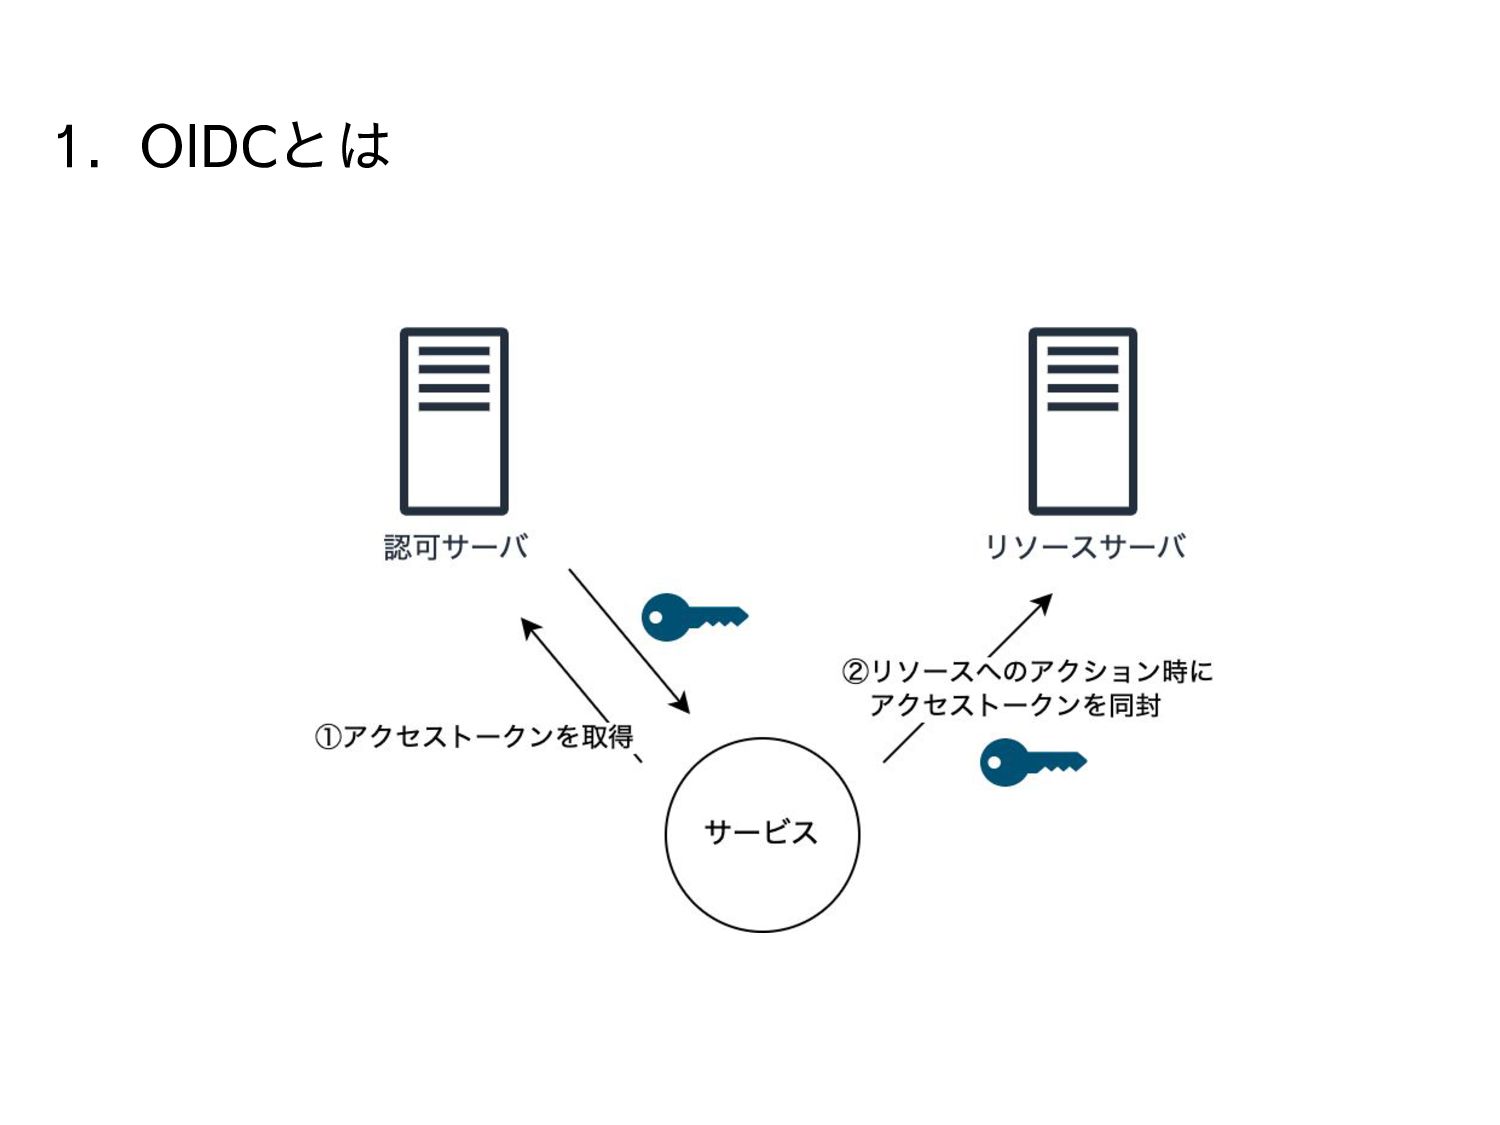
1. OIDCとは Open ID Connectの略 信頼されたOIDCプロバイダーが提供するトークンによって認証・認可を行う仕組 み。 OIDCのユーザーとなるサービスは、認証された主体の情報を示す「IDトークン」 や、認可されたアクションを示す「アクセストークン」というトークンを認可 サーバーに発行してもらう。
リソースサーバーに対するリクエストにそれらのトークンを含めることで、リ ソースに対して許可されたアクションを行うことができる。
1. OIDCとは
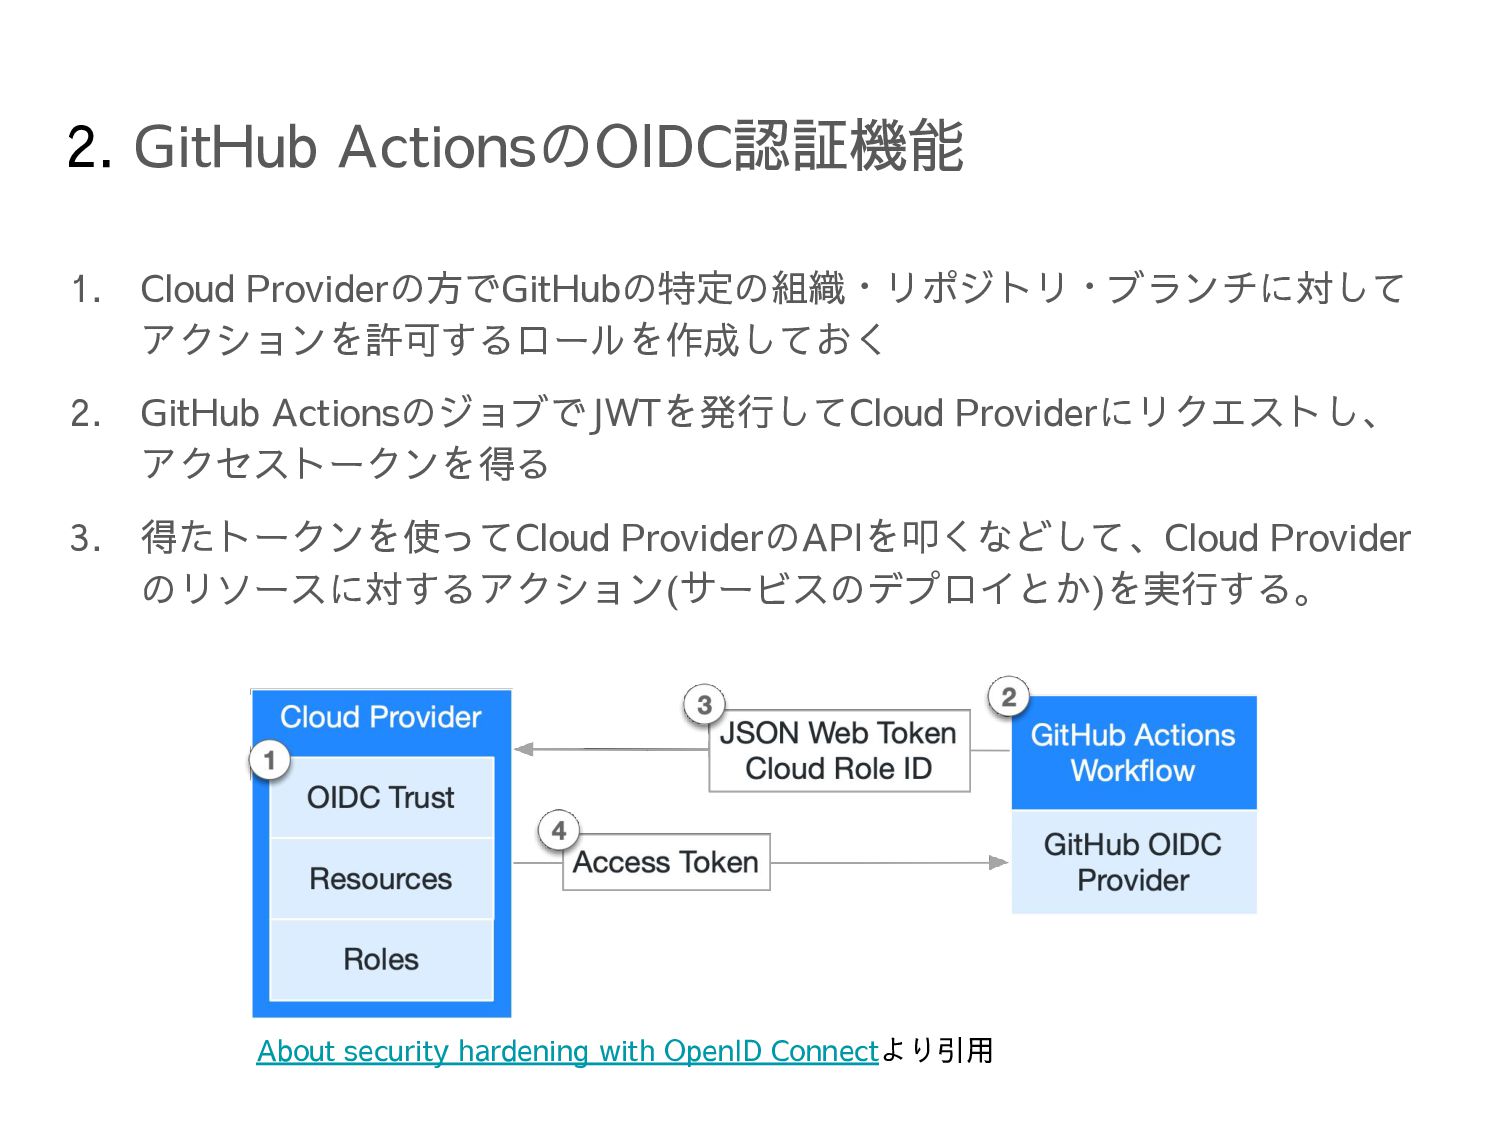
2. GitHub ActionsのOIDC認証機能 1. Cloud Providerの方でGitHubの特定の組織・リポジトリ・ブランチに対して アクションを許可するロールを作成しておく 2. GitHub ActionsのジョブでJWTを発行してCloud
Providerにリクエストし、 アクセストークンを得る 3. 得たトークンを使ってCloud ProviderのAPIを叩くなどして、Cloud Provider のリソースに対するアクション(サービスのデプロイとか)を実行する。 About security hardening with OpenID Connectより引用
2. GitHub ActionsのOIDC認証機能 メリット 従来は、AWSのリソースに対して特定のアクションを実行できるユーザーを作成 し、そのユーザーのアクセスキーとシークレットキー(IDとパスワードみたいなも の)をGitHubのsecretsに登録してGitHub Actionsで利用していた。 しかし、それでは認証情報をAWSの外部に置くことになるので流出の危険があり セキュリティ的に良くない。
OIDC認証を使うことで、workflow実行時に毎度発行される短命なトークンを利 用して認証を行えるため、secretsに認証情報を保存しなくてよくなる
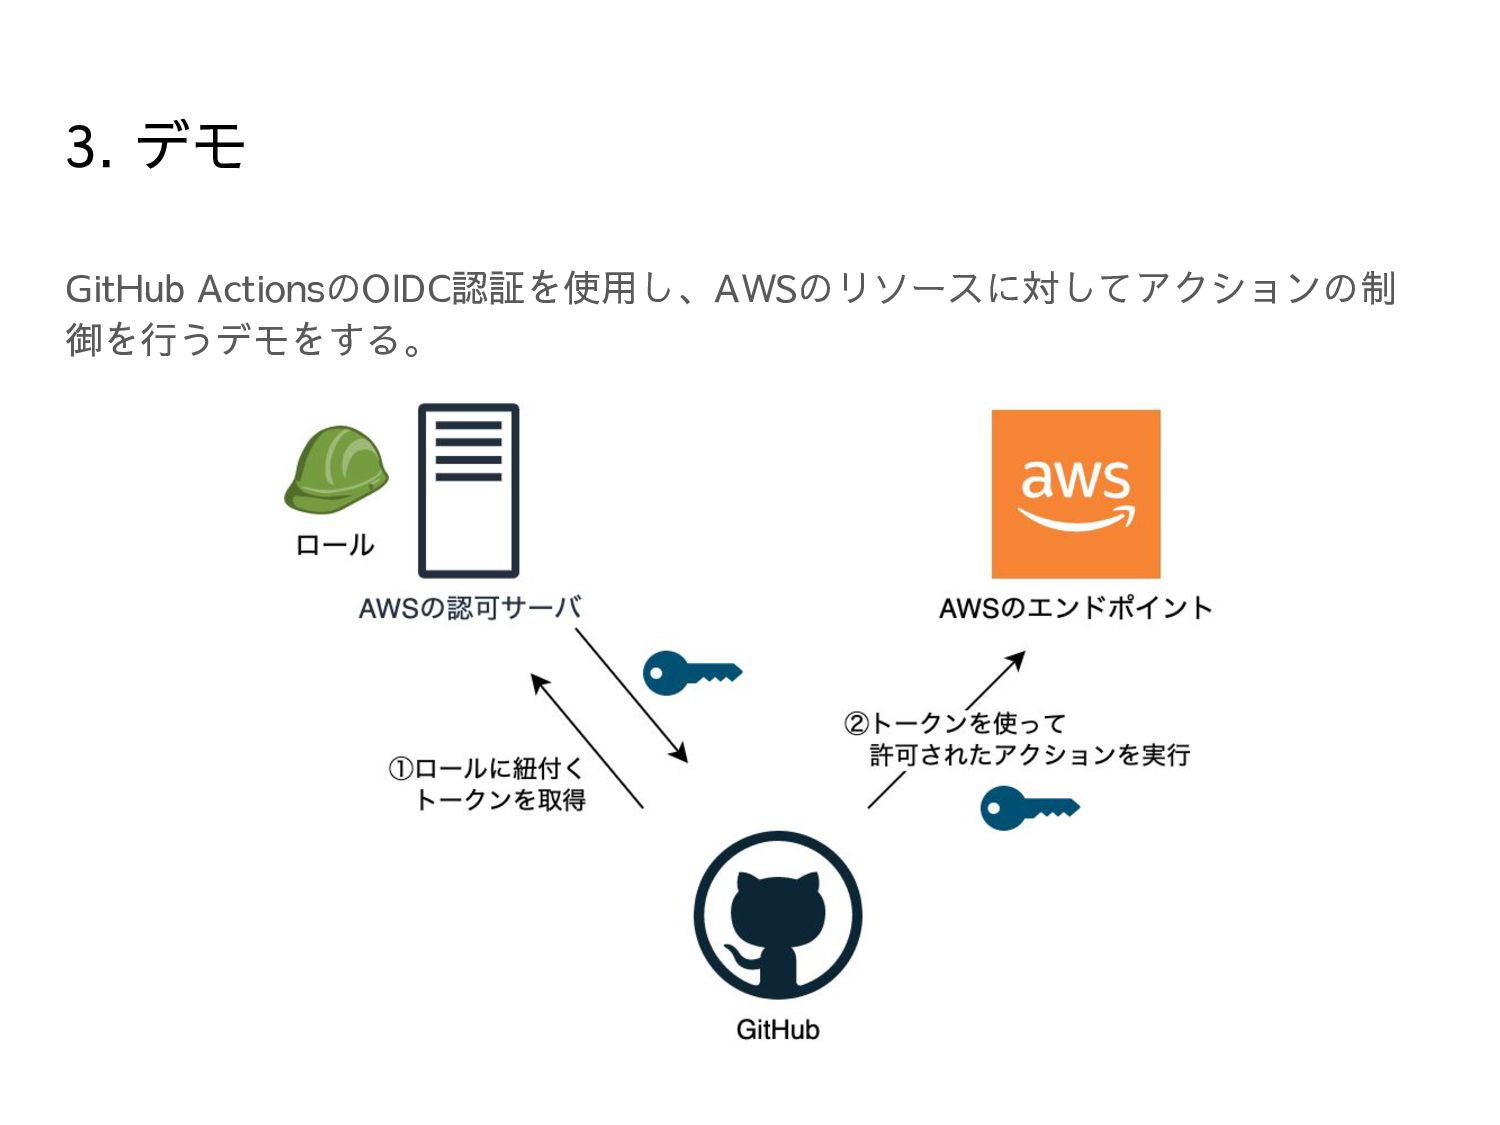
3. デモ GitHub ActionsのOIDC認証を使用し、AWSのリソースに対してアクションの制 御を行うデモをする。
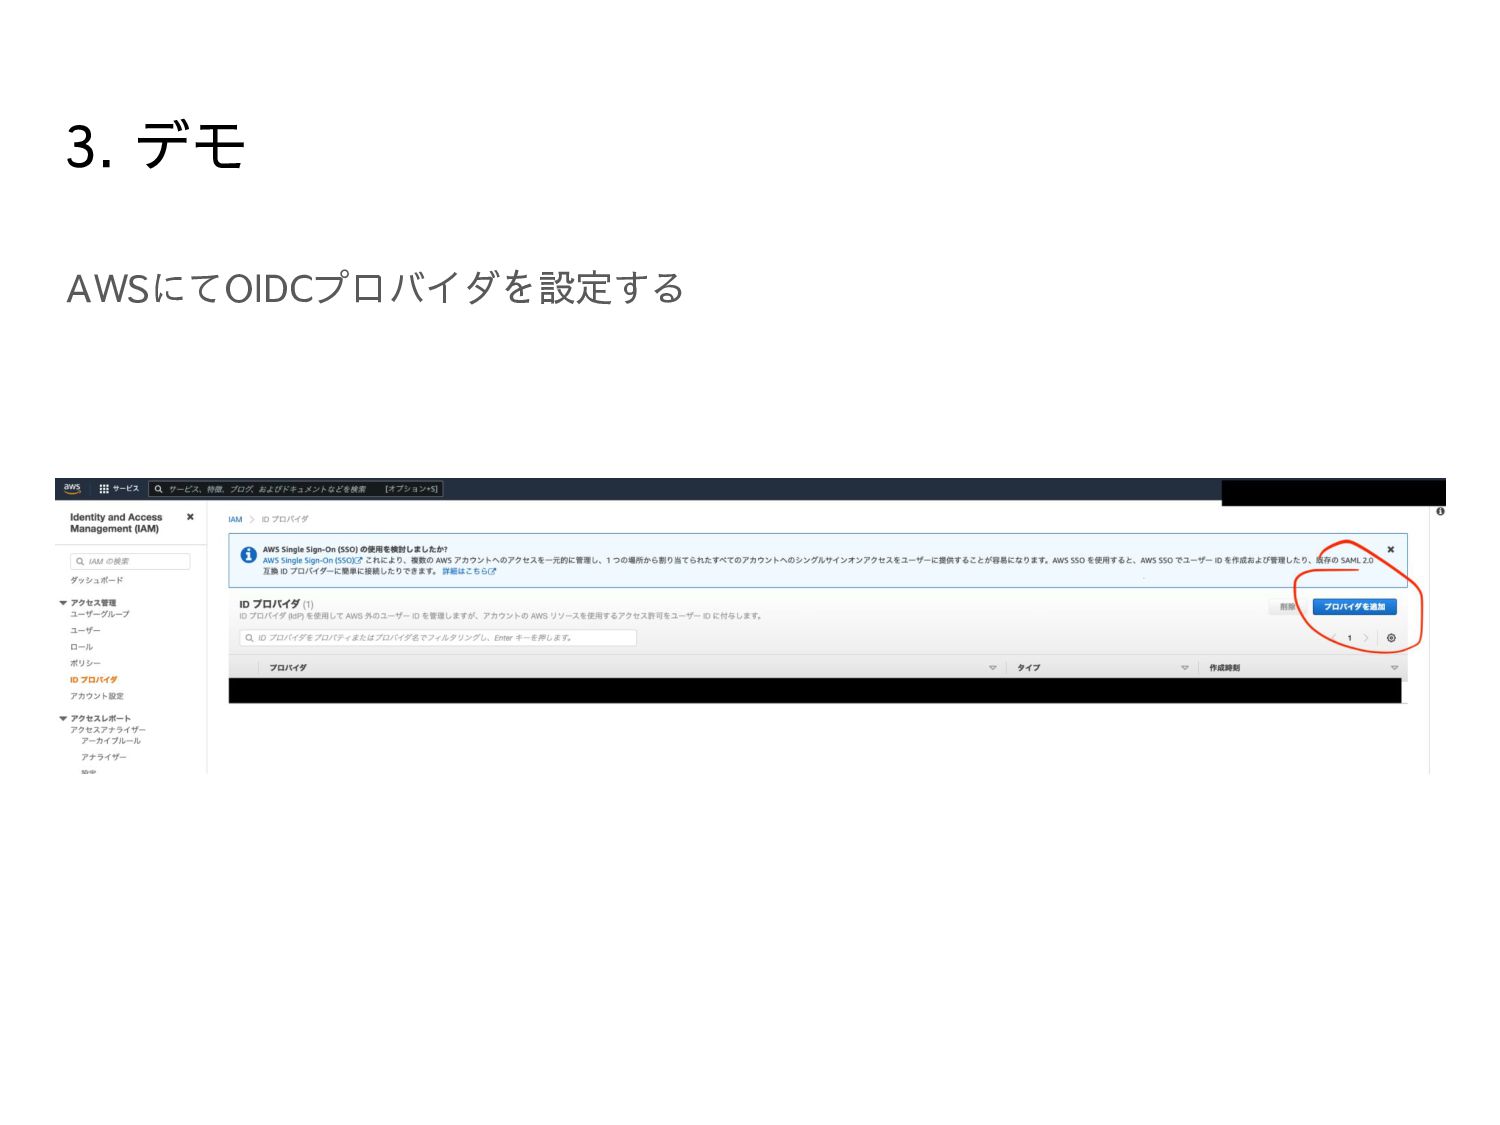
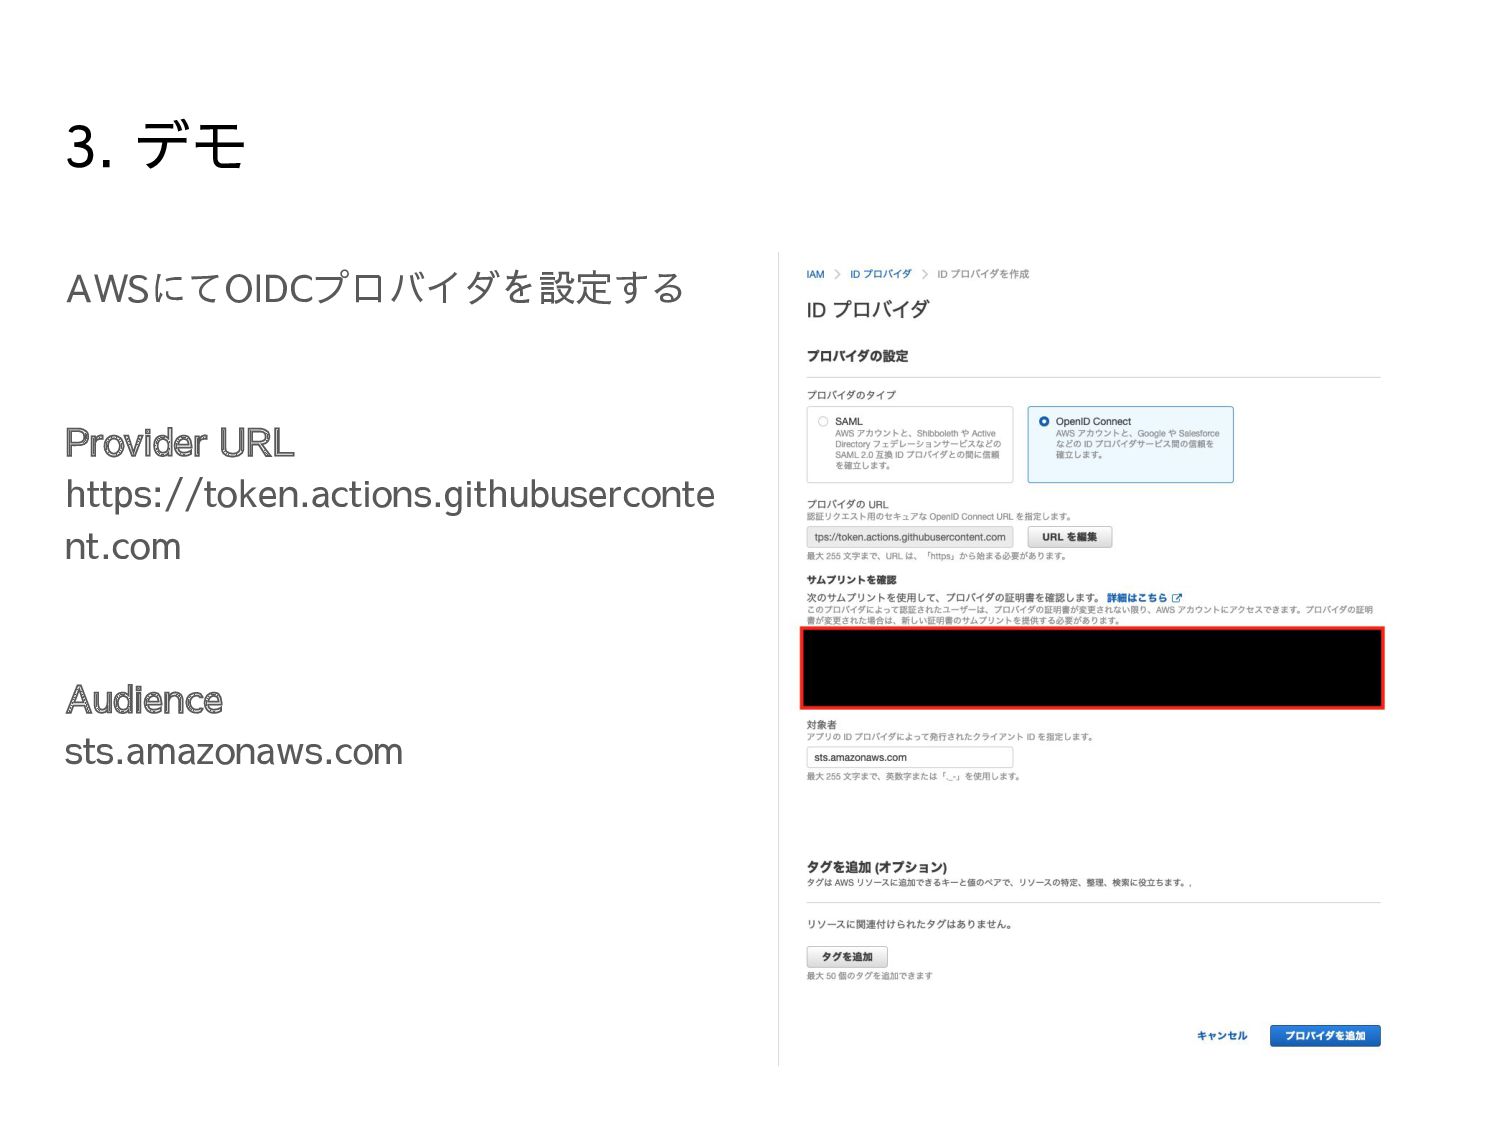
3. デモ AWSにてOIDCプロバイダを設定する
3. デモ AWSにてOIDCプロバイダを設定する Provider URL https://token.actions.githubuserconte nt.com Audience sts.amazonaws.com
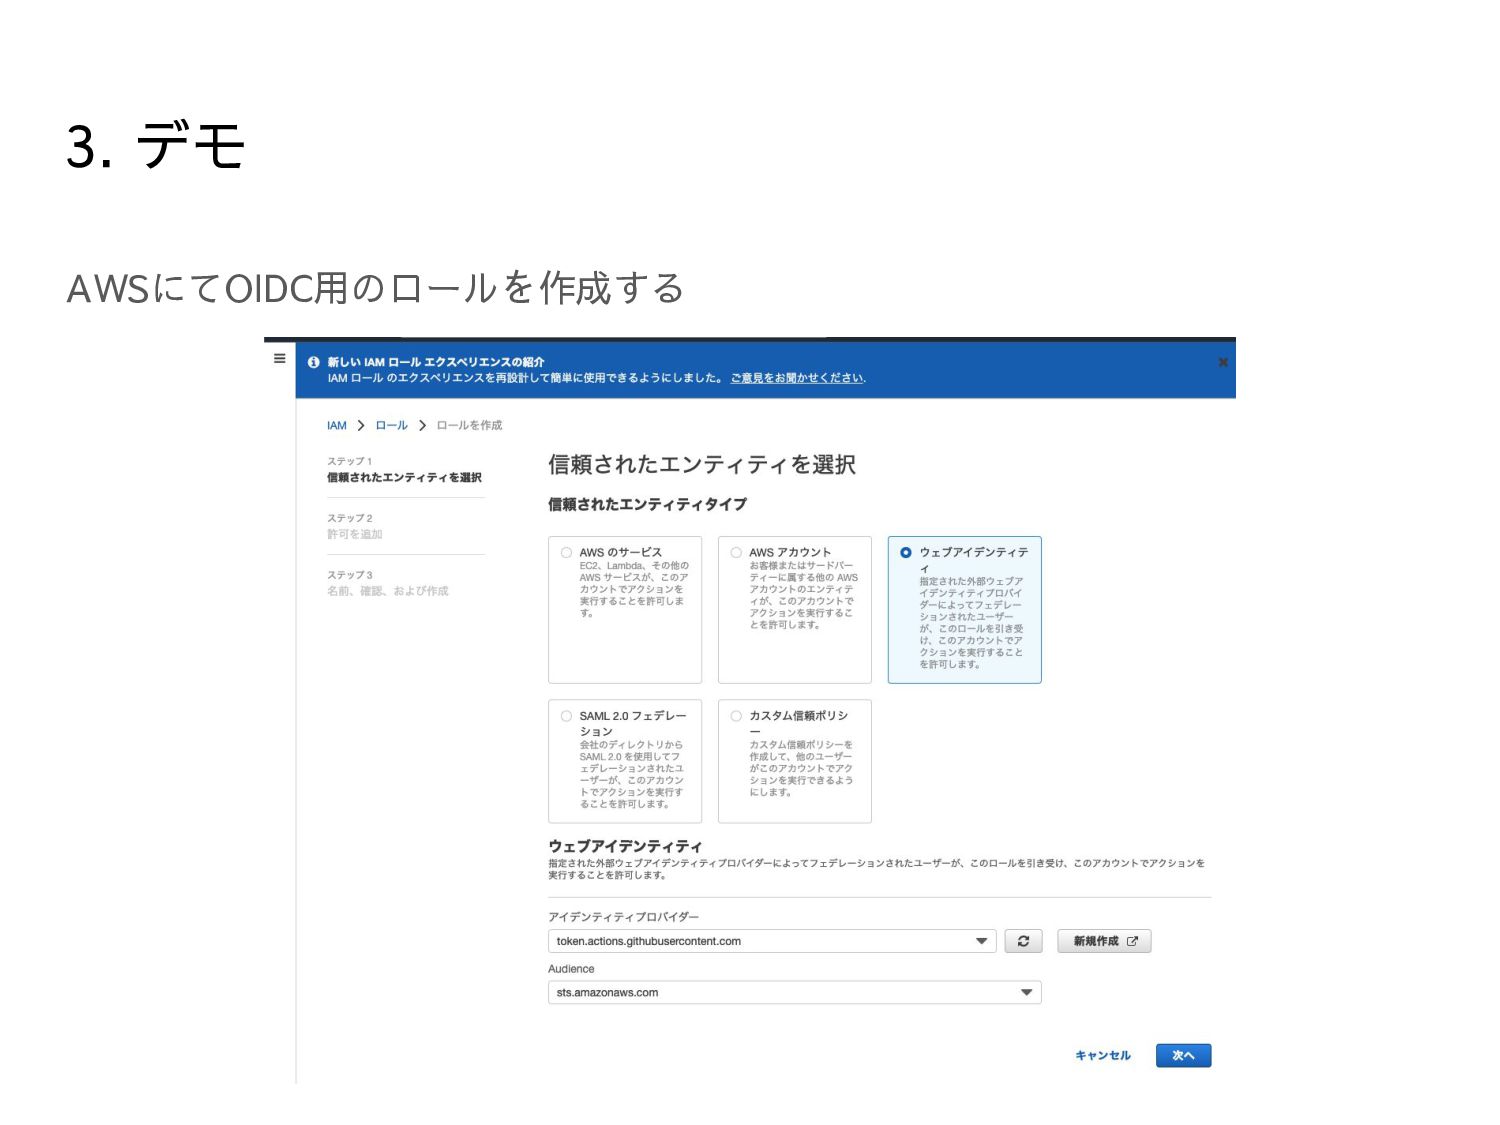
3. デモ AWSにてOIDC用のロールを作成する
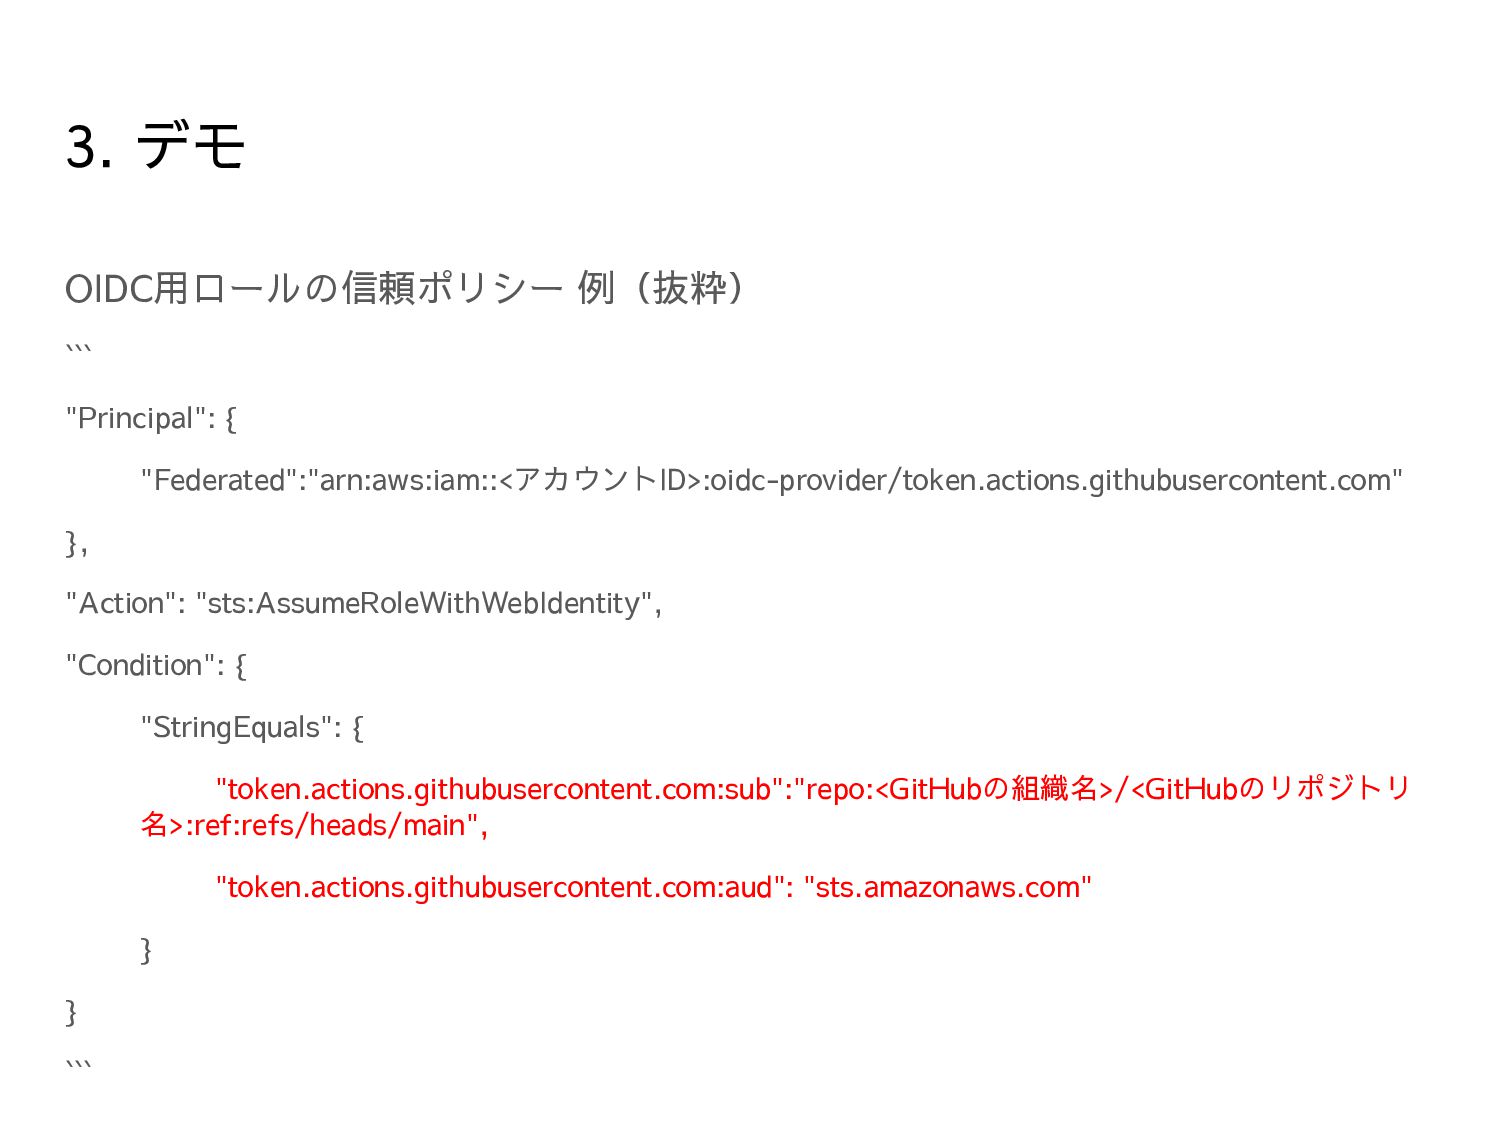
3. デモ OIDC用ロールの信頼ポリシー 例(抜粋) ``` "Principal": { "Federated":"arn:aws:iam::<アカウントID>:oidc-provider/token.actions.githubusercontent.com" }, "Action":
"sts:AssumeRoleWithWebIdentity", "Condition": { "StringEquals": { "token.actions.githubusercontent.com:sub":"repo:<GitHubの組織名>/<GitHubのリポジトリ 名>:ref:refs/heads/main", "token.actions.githubusercontent.com:aud": "sts.amazonaws.com" } } ```
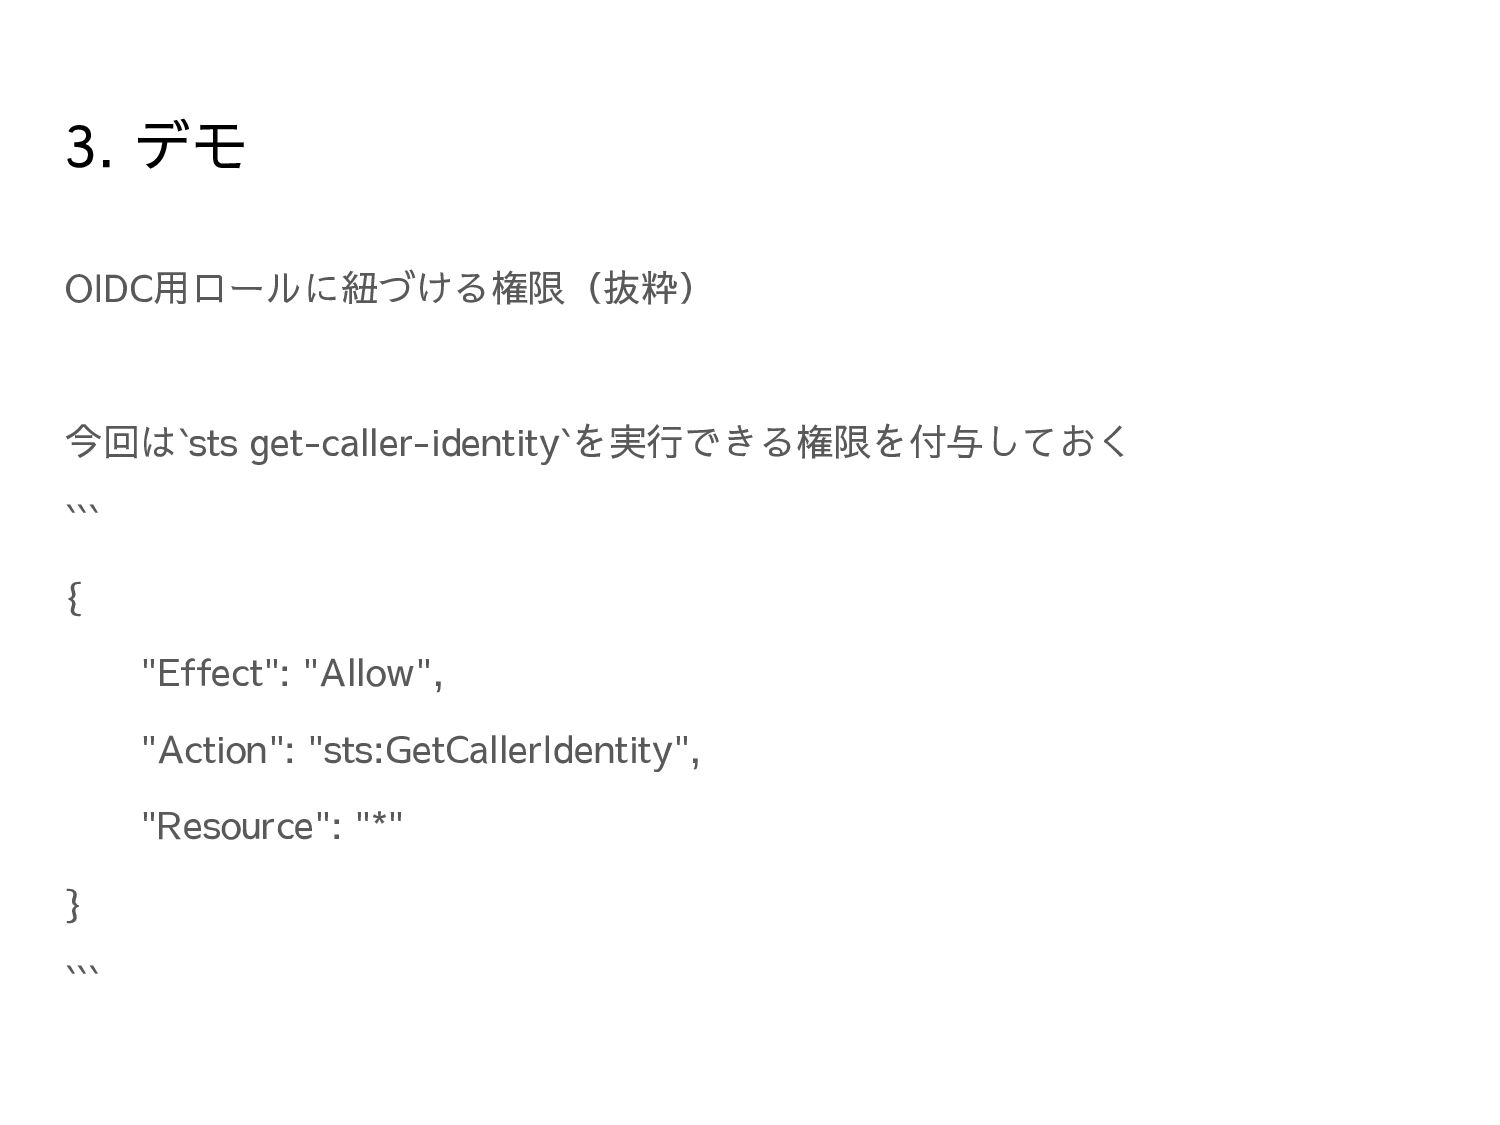
3. デモ OIDC用ロールに紐づける権限(抜粋) 今回は`sts get-caller-identity`を実行できる権限を付与しておく ``` { "Effect": "Allow", "Action":
"sts:GetCallerIdentity", "Resource": "*" } ```
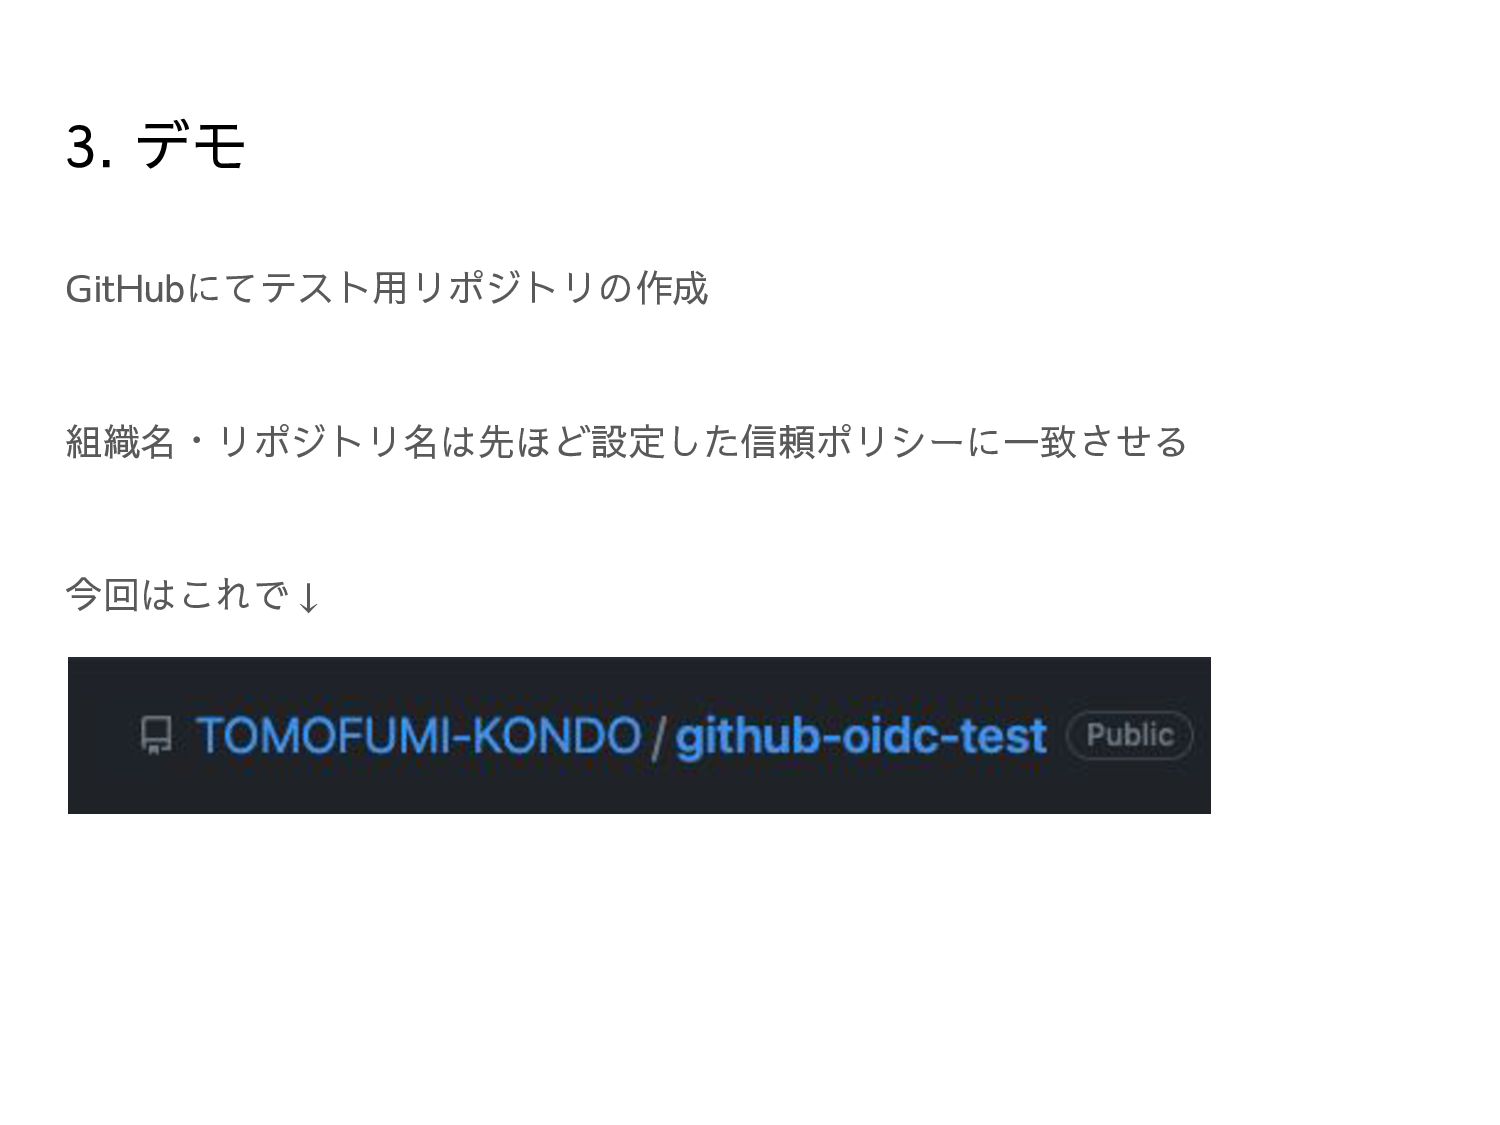
3. デモ GitHubにてテスト用リポジトリの作成 組織名・リポジトリ名は先ほど設定した信頼ポリシーに一致させる 今回はこれで↓
3. デモ OIDC認証を使うGitHub Actionsのworkflow(抜粋) GitHub OIDC Providerが発行するOIDC認証用のJWTを使うための権限の設定 ``` permissions: id-token:
write ```
3. デモ OIDC認証を使うGitHub Actionsのworkflow(抜粋) AWSから先ほど作ったロールに紐づくトークンを取得する ``` - name: configure AWS
credentials uses: aws-actions/configure-aws-credentials@v1 with: role-to-assume: arn:aws:iam::${{ secrets.AWS_ACCOUNT_ID }}:role/github-oidc-test role-session-name: testrolesession aws-region: ${{ env.AWS_REGION }} ```
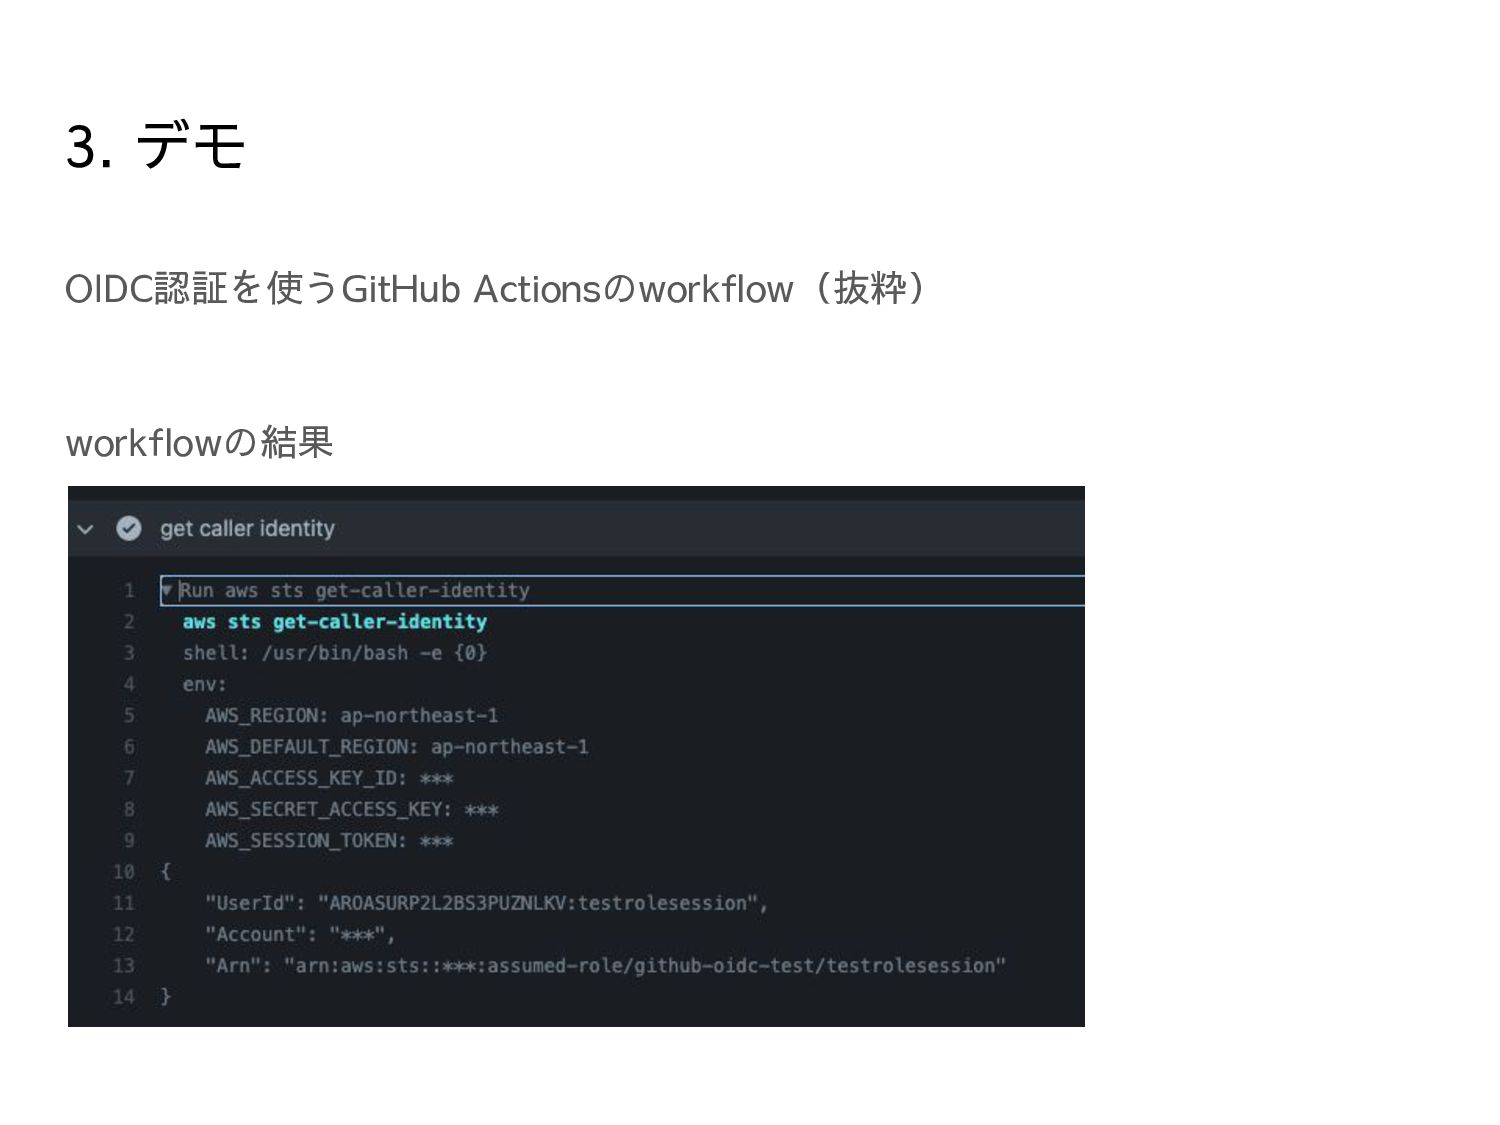
OIDC認証を使うGitHub Actionsのworkflow(抜粋) 前のステップで取得したトークンを同封してAWSのAPIを叩く ``` - name: get caller identity run:
| aws sts get-caller-identity ``` 3. デモ
3. デモ OIDC認証を使うGitHub Actionsのworkflow(抜粋) workflowの結果
4. まとめ • GitHub ActionsのOIDC認証を使うことで、secretsに認証情報を保存しなく てよくなるため、認証情報の流出の危険性がなくなる。 • GitHub ActionsのworkflowからAWSのリソースに対するアクセス制御を柔軟 に行うことができる。


 tomokon
 tosite
 siroemk
 naokihaba
 yutobara
 akihisaikeda
 har1101
 yasaichi
 l2hyunwoo
 artoy
 ziobrando
 akase244
 hollycummins
 konakalab
 danielanewman
 badams
 reverentgeek
 honnibal
 sonatard
 jct
 3n
 codingconduct
 addyosmani
 palkan