Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Comey Crypto [BSidesLDN 2015 Lightning]

Avatar for Mikey Mikey
June 03, 2015

Comey Crypto [BSidesLDN 2015 Lightning]

Slightly modified version of the talk given at SecuriTayIV in February 2015. BSides London 2015 Lightning track 11am-12pm slot.

Origingal Abstract: This talk will examine the spread of and subsequent resistance of cryptography by governments, in particular the United States. I will briefly discuss the origins of modern cryptography and follow with the events and actors of the first ‘crypto wars’ before examining the more recent revelations regarding government mass surveillance. In particular we will examine the efforts by intelligence agencies to weaken and subvert public cryptography. The talk will conclude on a slightly more positive note; how can we make mass surveillance harder and some of the mitigations we can employ.

Avatar for Mikey

Mikey

June 03, 2015

More Decks by Mikey

Other Decks in Technology

Transcript

  1. mikey$ whoami • Michael Jack • 2nd Year Ethical Hacking

    BSc @ Abertay • Member Abertay Ethical Hacking Society • I ❤ Cryptography • @MikeyJck • mikeyjck.io
  2. - Brendan O’Connor Defcon 21 “At ever single level we

    as a community have forgotten that privacy as well as security need to be a goal” What’s all this then?
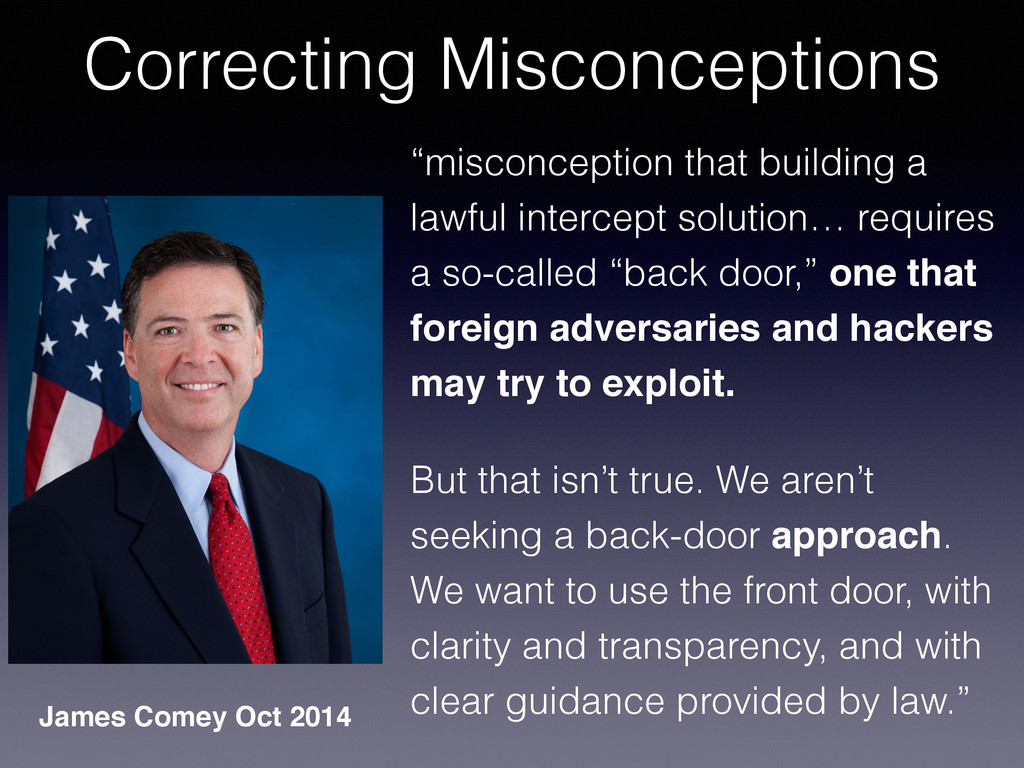
  3. Correcting Misconceptions “misconception that building a lawful intercept solution… requires

    a so-called “back door,” one that foreign adversaries and hackers may try to exploit. But that isn’t true. We aren’t seeking a back-door approach. We want to use the front door, with clarity and transparency, and with clear guidance provided by law.” James Comey Oct 2014
  4. – David Cameron January 2015 “One is communications data, that

    is not the content of a phone call. It is just who made which call to which person and when… And what matters, in simple terms is that we can access this data [on all platforms]… I have a very simple principle to apply here… in our country do we want to allow a means of communication that in extremis we can’t read with a signed warrant…”
  5. • Never roll your own crypto! • Crypto is a

    tool not a security silver bullet • Security of crypto is not binary Cryptography 101
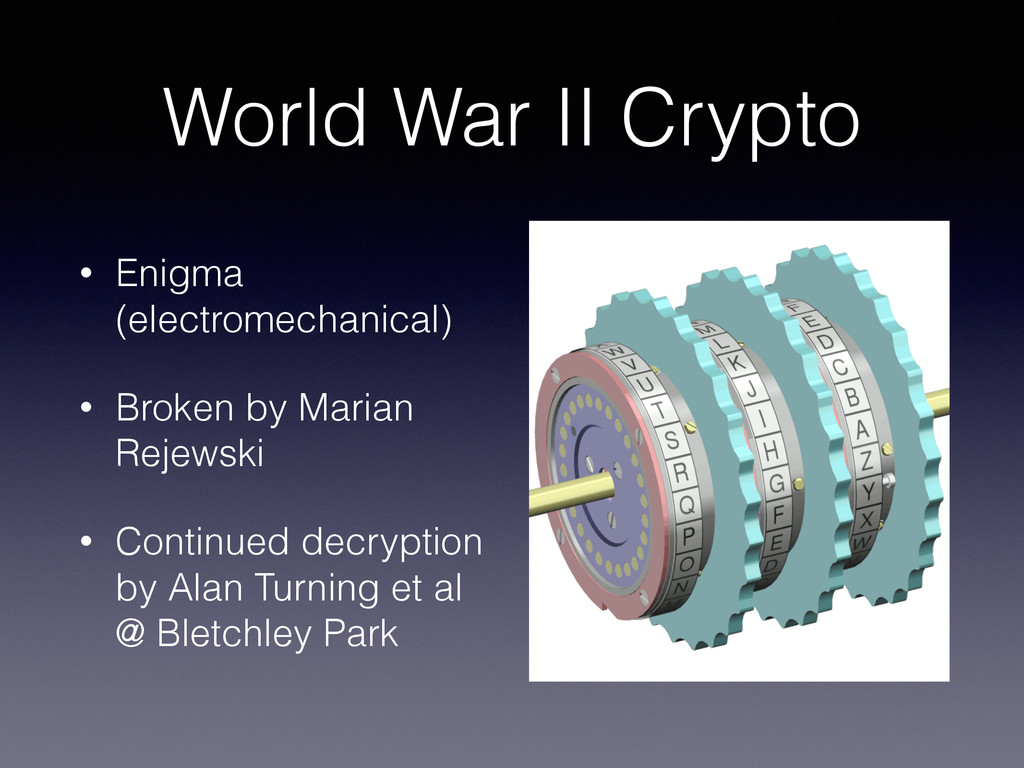
  6. World War II Crypto • Enigma (electromechanical) • Broken by

    Marian Rejewski • Continued decryption by Alan Turning et al @ Bletchley Park
  7. Modern Crypto - Timeline • 1971 - IBM Lucifer Block

    Cipher (Watson Lab) • 1973 - NBS asks for Data Encryption Standard (DES) designs • 1973-4 - IBM develop & submit DES candidate • 1976 - Diffie & Hellman publish “New Directions in Cryptography” • 1976 - After alterations by NSA IBMs design chosen as DES • 1977 - “Method for Obtaining Digital Signatures and Public-Key Cryptosystems" by Rivest, Shamir & Adleman (RSA) @ MIT
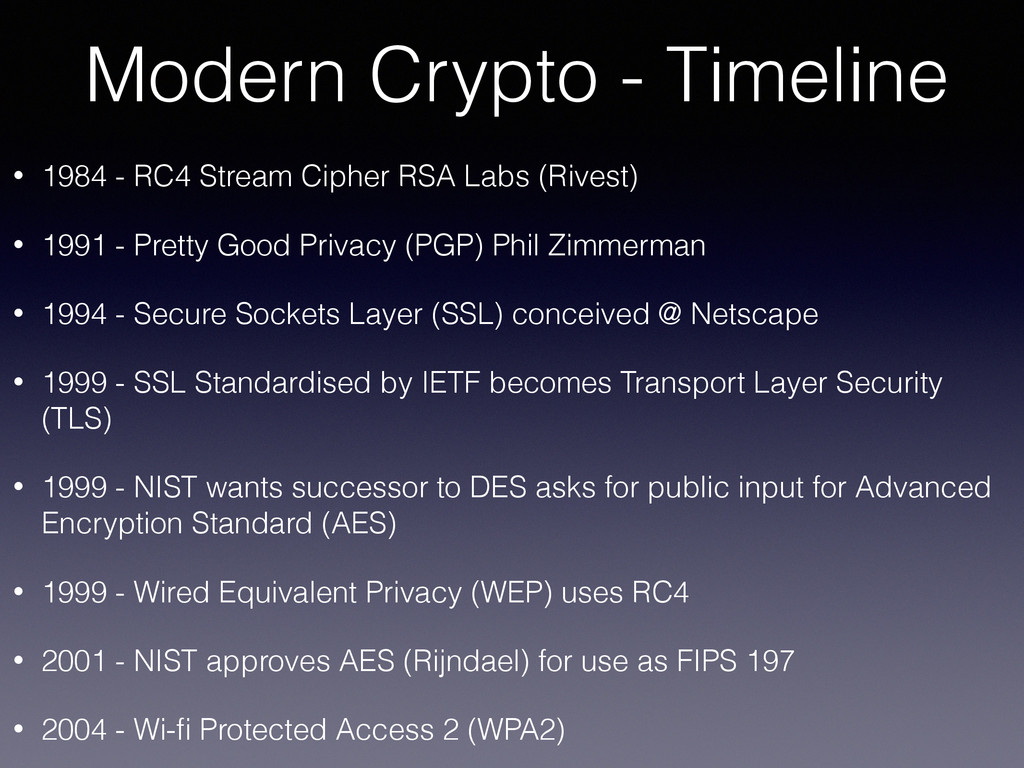
  8. • 1984 - RC4 Stream Cipher RSA Labs (Rivest) •

    1991 - Pretty Good Privacy (PGP) Phil Zimmerman • 1994 - Secure Sockets Layer (SSL) conceived @ Netscape • 1999 - SSL Standardised by IETF becomes Transport Layer Security (TLS) • 1999 - NIST wants successor to DES asks for public input for Advanced Encryption Standard (AES) • 1999 - Wired Equivalent Privacy (WEP) uses RC4 • 2001 - NIST approves AES (Rijndael) for use as FIPS 197 • 2004 - Wi-fi Protected Access 2 (WPA2) Modern Crypto - Timeline
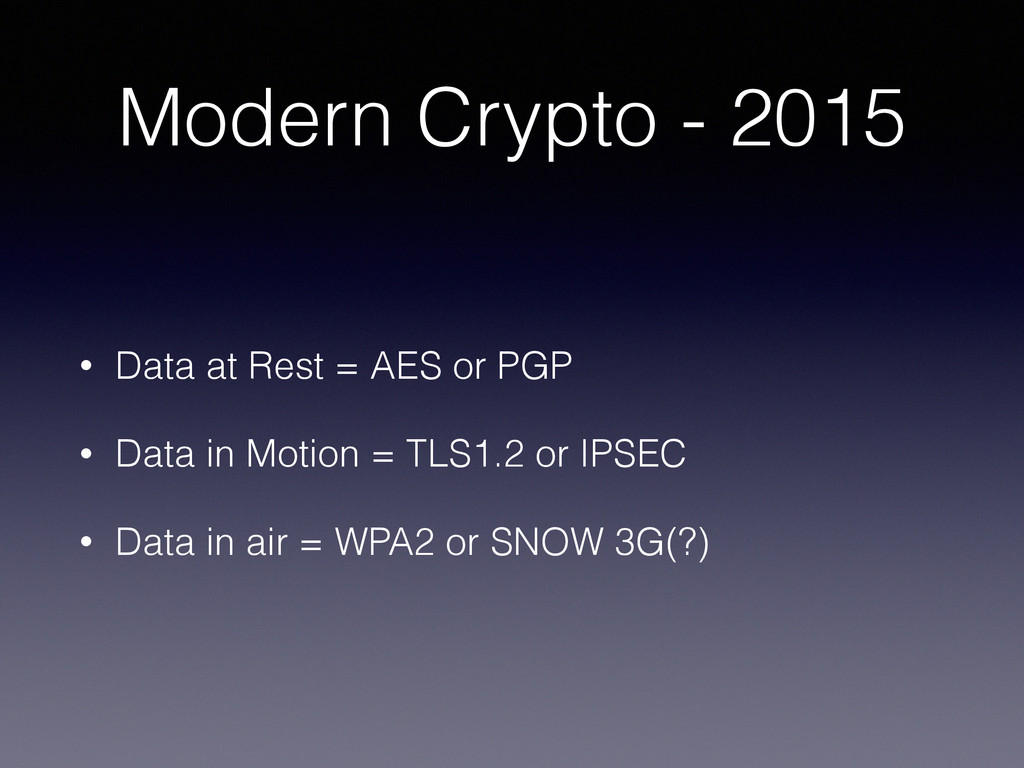
  9. Modern Crypto - 2015 • Data at Rest = AES

    or PGP • Data in Motion = TLS1.2 or IPSEC • Data in air = WPA2 or SNOW 3G(?)
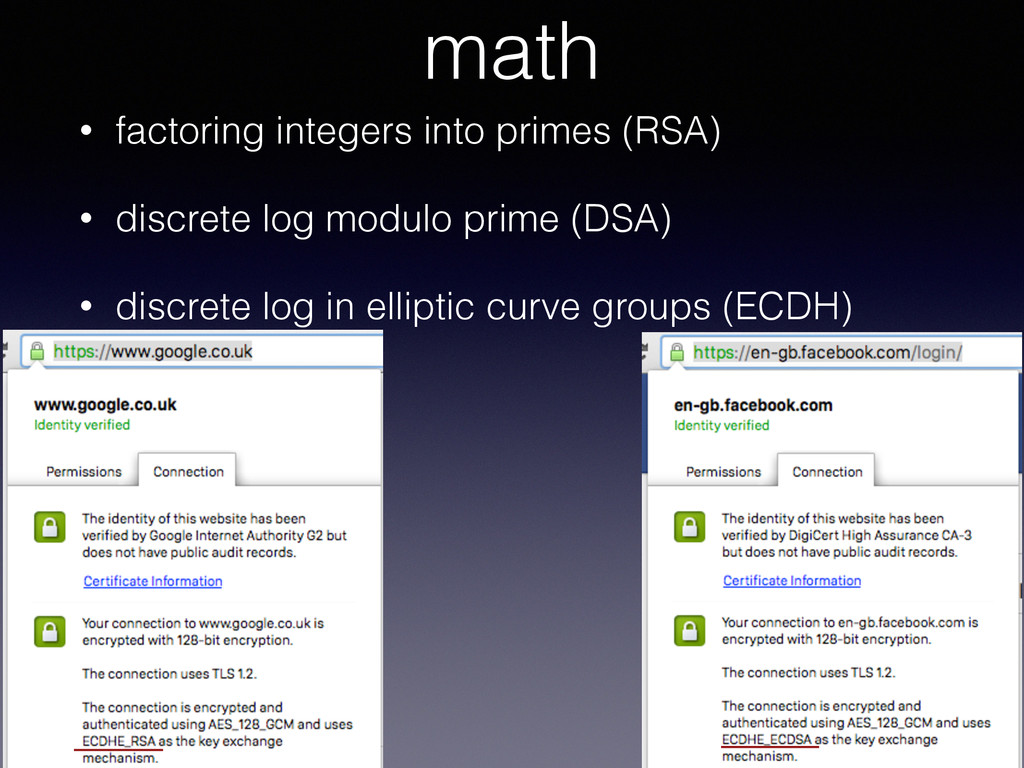
  10. math • factoring integers into primes (RSA) • discrete log

    modulo prime (DSA) • discrete log in elliptic curve groups (ECDH)
  11. Export Controls • 1970s Crypto is added to US Munitions

    List • USML part of International Traffic in Arms Regulations (ITAR) • ITAR licensing requires case by case consideration for export of munitions on USML • Justice Department told White House in 1978 that ITAR restriction on crypto is unconstitutional.
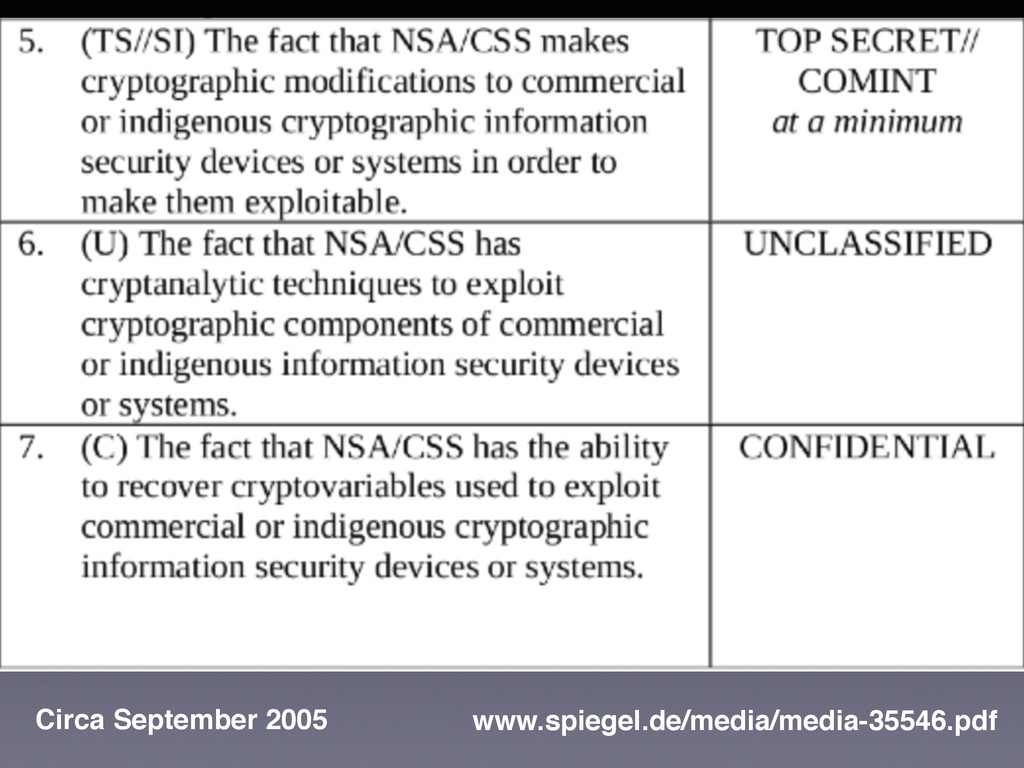
  12. NSA Controls • 1974 - IBM discover differential cryptanalysis NSA

    ask them to keep it secret • Limit on key size of exported crypto systems • IBM Notes Int version 64-bit key, 24-bits know to NSA
  13. Clipper Chip • Announced 1993 by NSA • Skipjack algorithm

    + DH for key distribution • Built in Key escrow :( • Matt Blaze et al • US Govt offered export easing if you included key escrow • Dead by 1996
  14. Export Controls • December 1996 - Bureau of Export Administration

    transfers jurisdiction over "commercial encryption products” to the Commerce Department • Encryption products specifically designed or modified for military use remain subject to ITAR controls.
  15. nsa$ whoami National Security Agency • 2013 Budget: $10.8B •

    $2.5B on data collection • $1.6B on processing/ exploitation • Upwards of 40k employees • Created by Truman in secret 1952 • FISA/ National Security Letters/CALEA
  16. gchq$ whoami Government Communications HQ • Originally founded 1919 as

    GC&CS • Unique access to backbone infrastructure • Upwards of 6k employees • RIPA
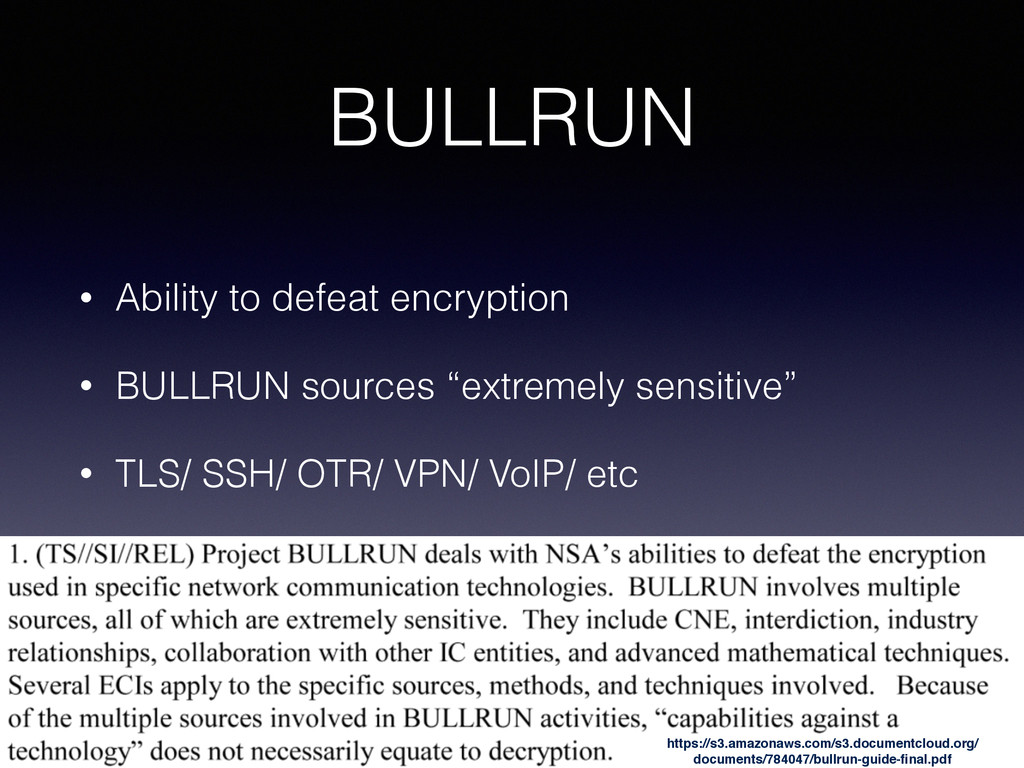
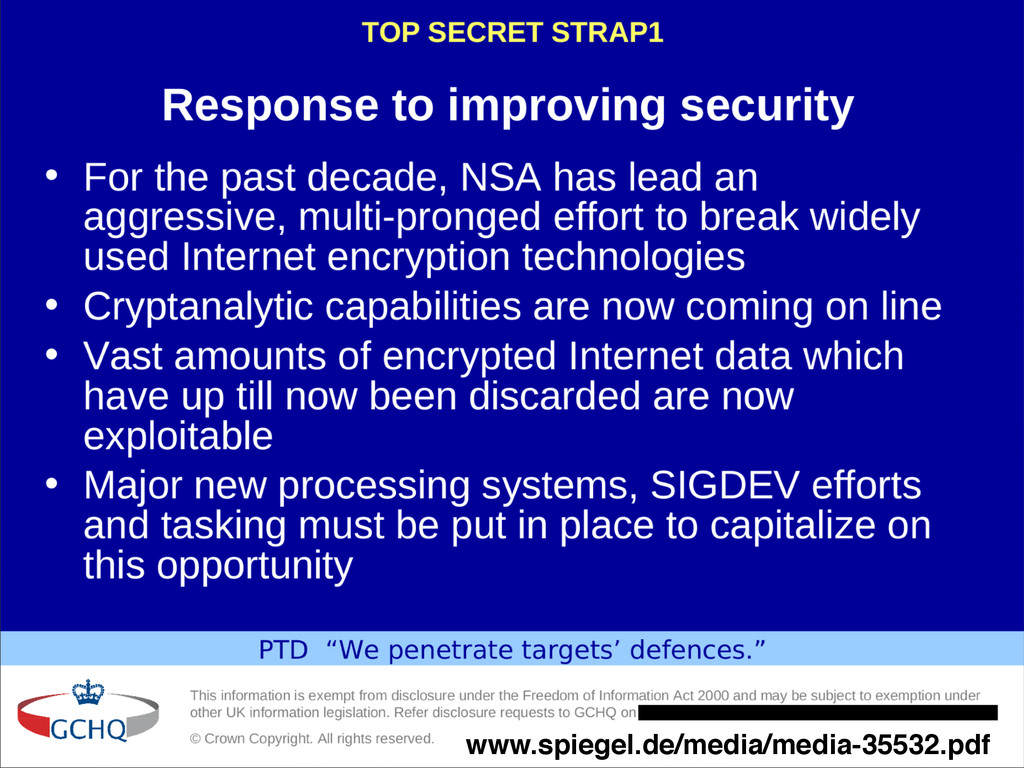
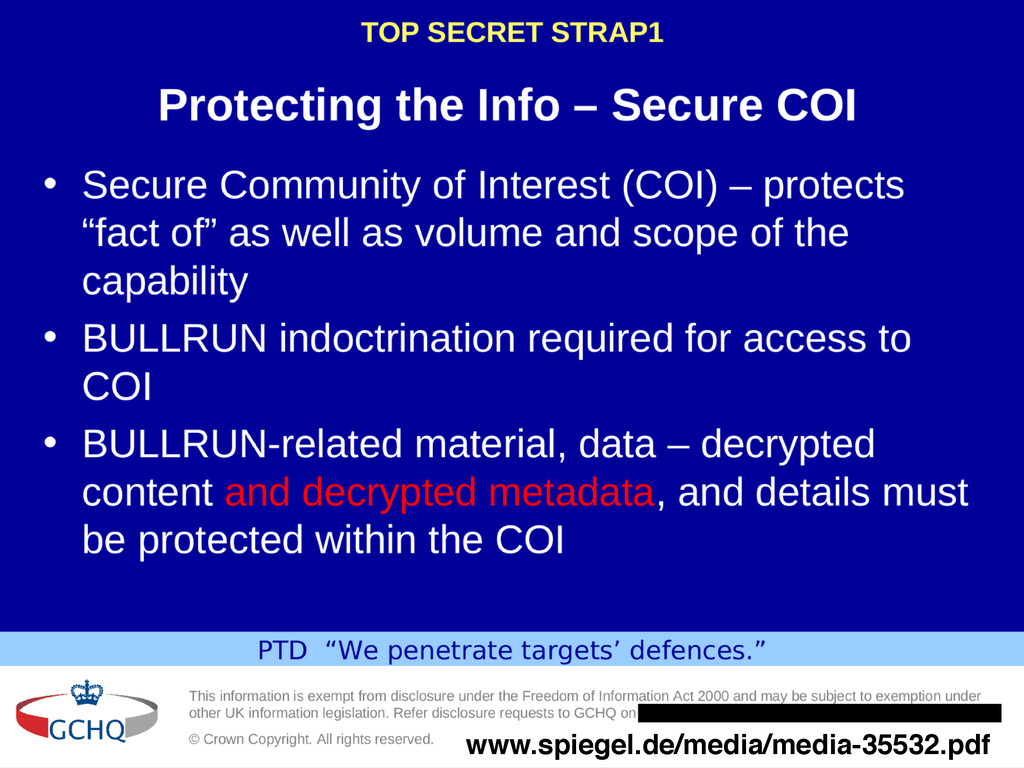
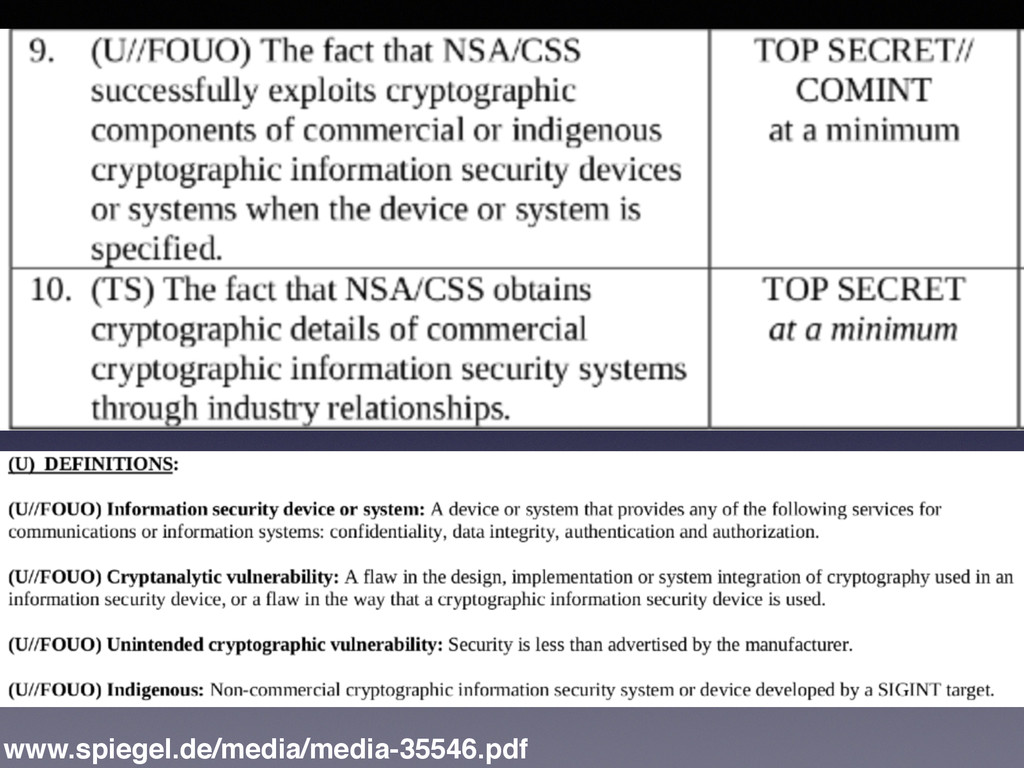
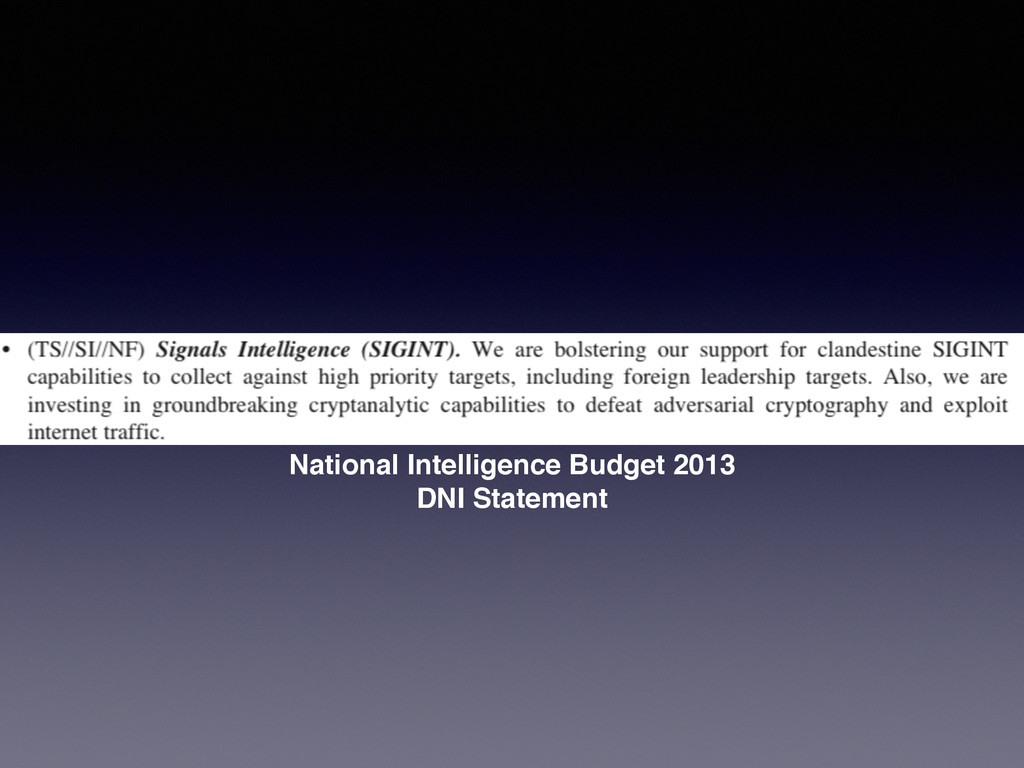
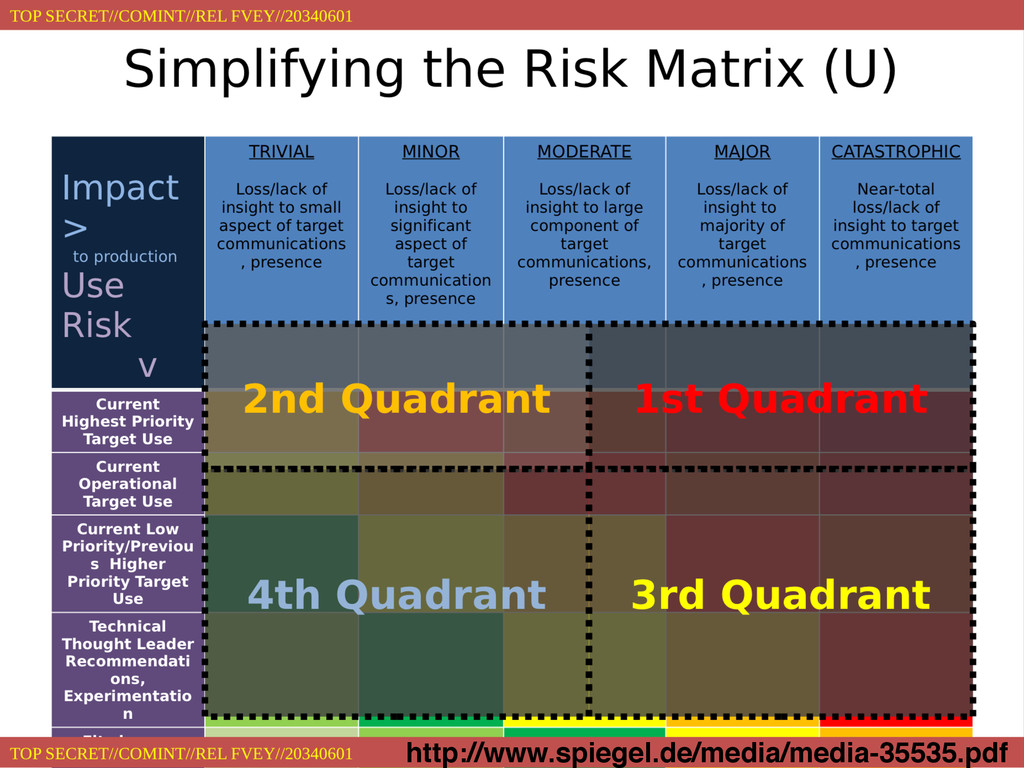
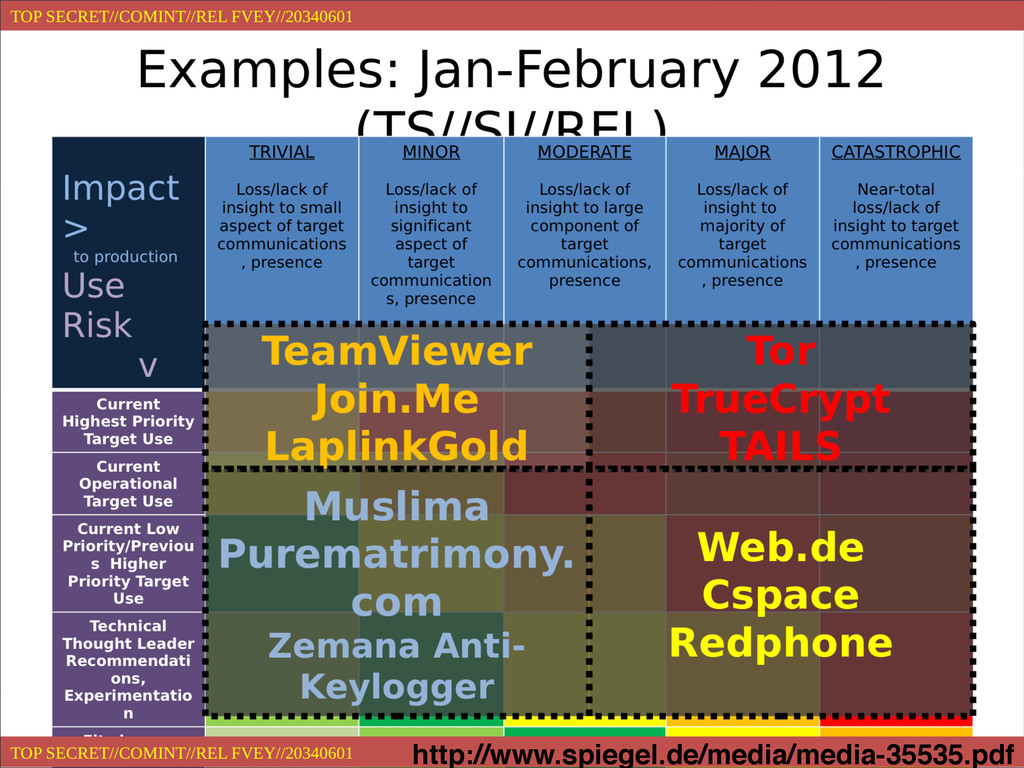
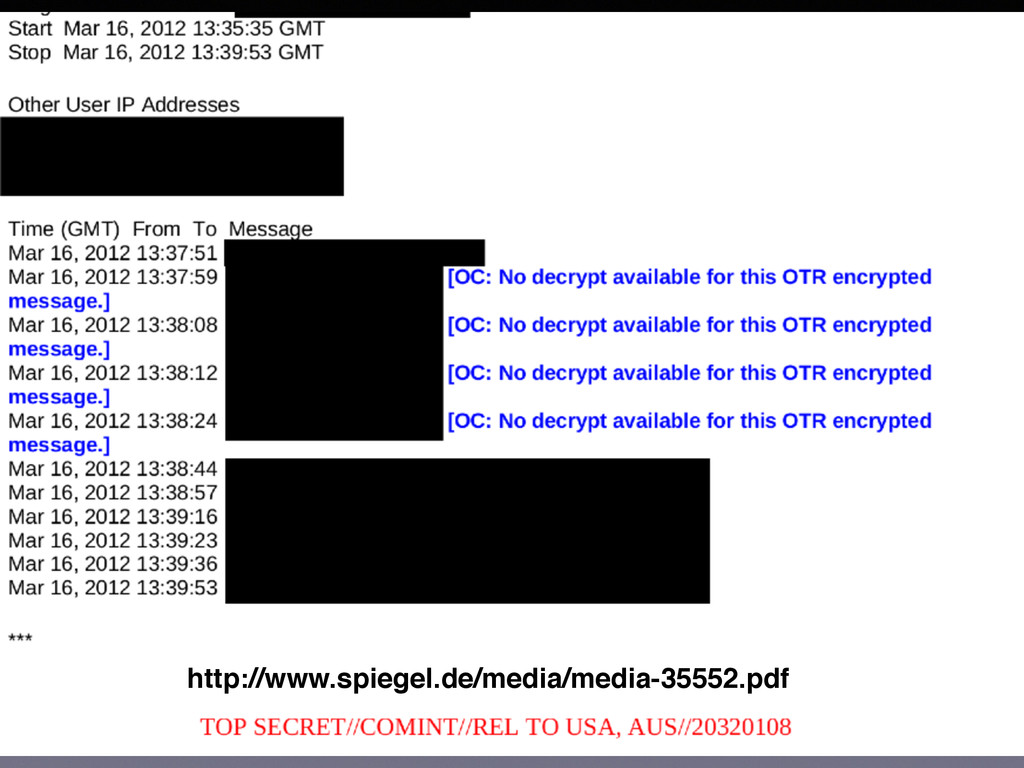
  17. BULLRUN • Ability to defeat encryption • BULLRUN sources “extremely

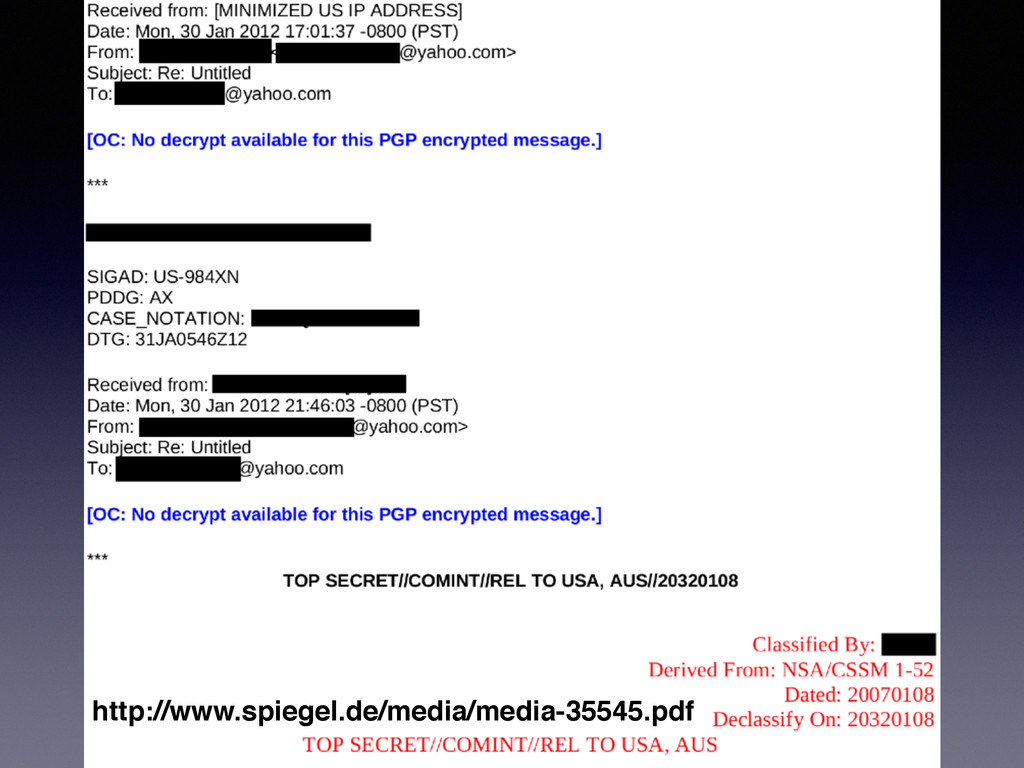
    sensitive” • TLS/ SSH/ OTR/ VPN/ VoIP/ etc https://s3.amazonaws.com/s3.documentcloud.org/ documents/784047/bullrun-guide-final.pdf
  18. here be backdoors • RSA accepted $10M from NSA to

    use Dual EC DRBG as default in BSAFE library (2004/5) • RSA “relied on guidance from NIST” • RSA claim they didn’t know it was weakened or contained a backdoor • Dual_EC_DRBG withdrawn after NIST issues new guidlines Sept 2013
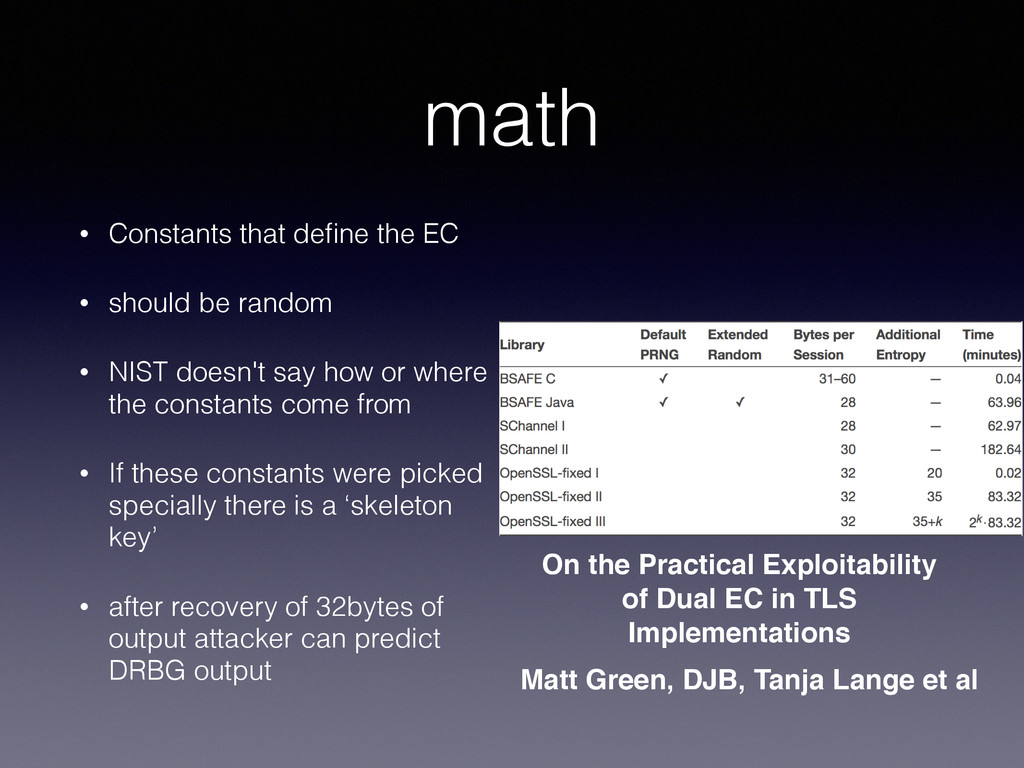
  19. math • Constants that define the EC • should be

    random • NIST doesn't say how or where the constants come from • If these constants were picked specially there is a ‘skeleton key’ • after recovery of 32bytes of output attacker can predict DRBG output On the Practical Exploitability of Dual EC in TLS Implementations Matt Green, DJB, Tanja Lange et al
  20. Sys Admins • GCHQ/ CSEC venture to ‘automate’ NOC hunting

    • identifying sys admins and NOCs • compromise privileged users, fight smart right?
  21. Conclusion • Undermining encryption is a terrible plan • Step

    the fuck away from our crypto • Education & discussion
  22. Regin Malware • ‘nation state’ • US(NSA?) & GCHQ •

    months/ years to develop • designed to gather ‘intelligence’ • focus on remaining undetected
  23. Regin Malware • ‘nation state’ • NSA & GCHQ •

    months/ years to develop • designed to gather ‘intelligence’ • focus on remaining undetected Why? UK uses CNE against close ally(s) within the EU
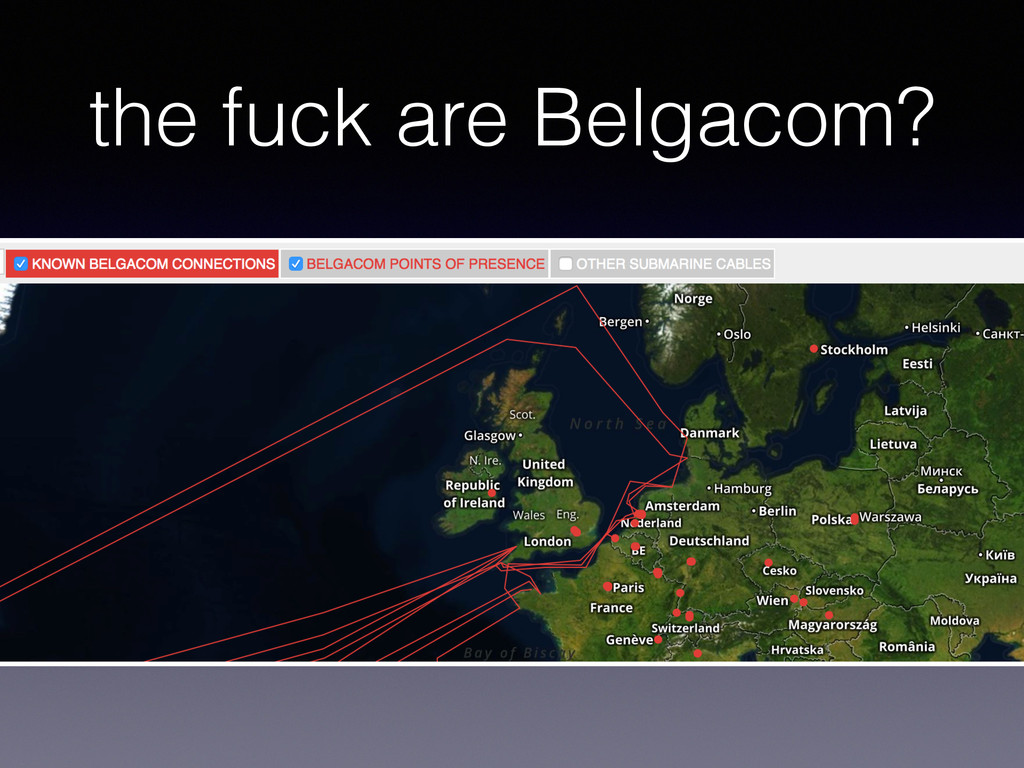
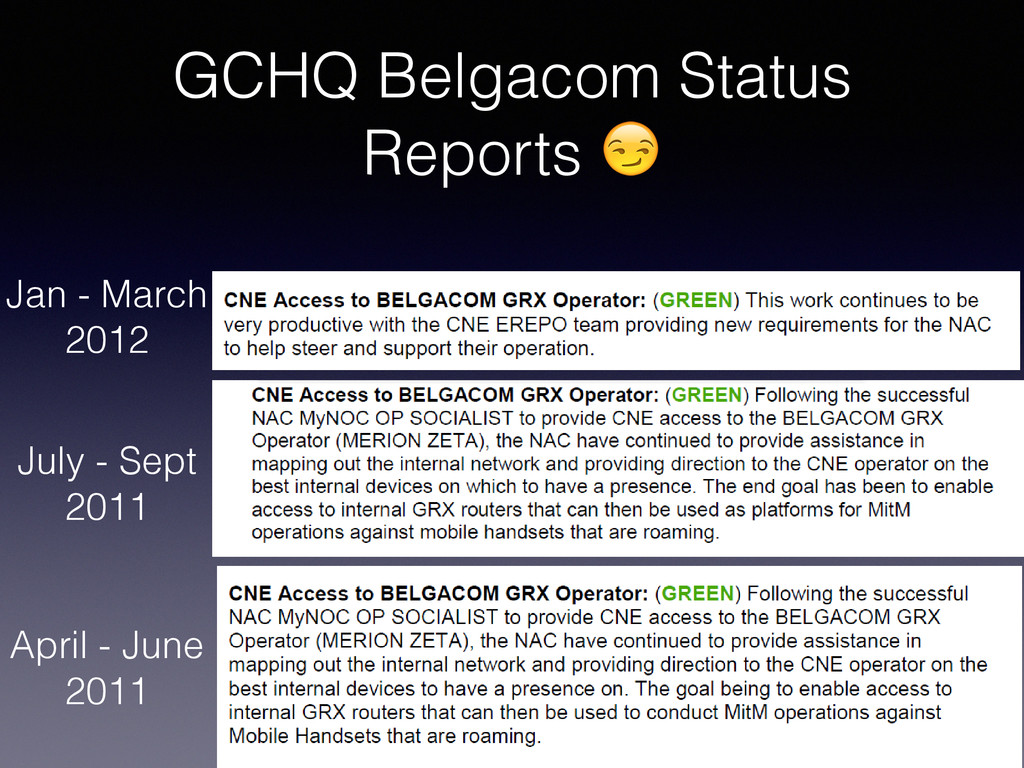
  24. Belgacom - Timeline • At some point before March 2011

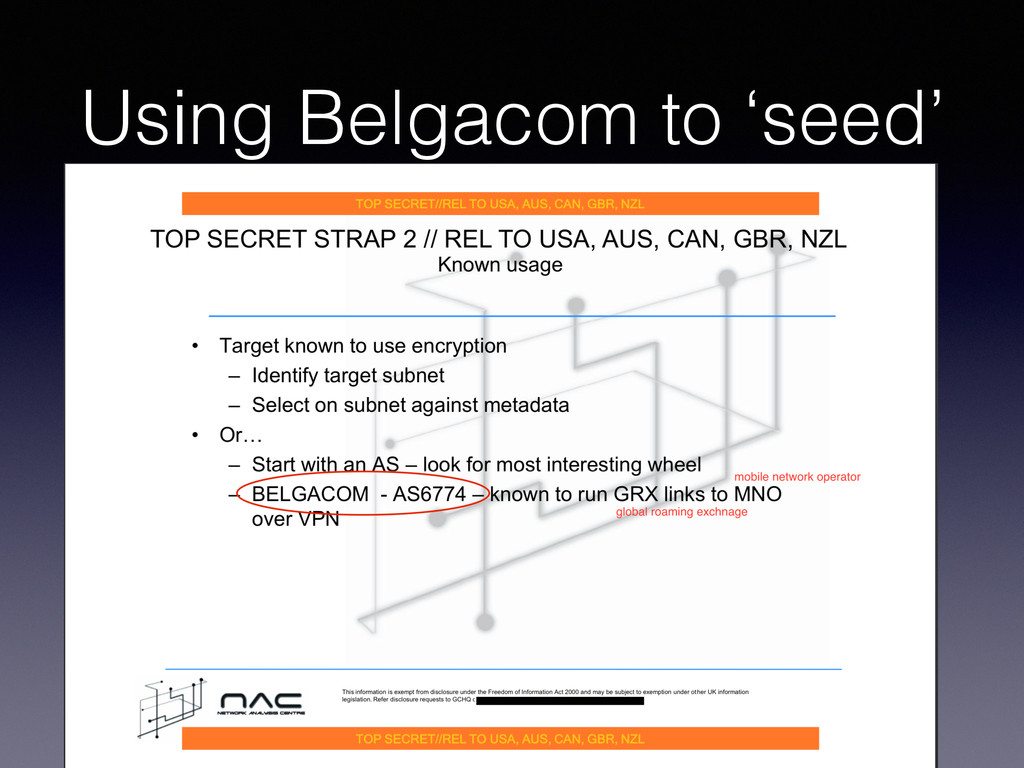
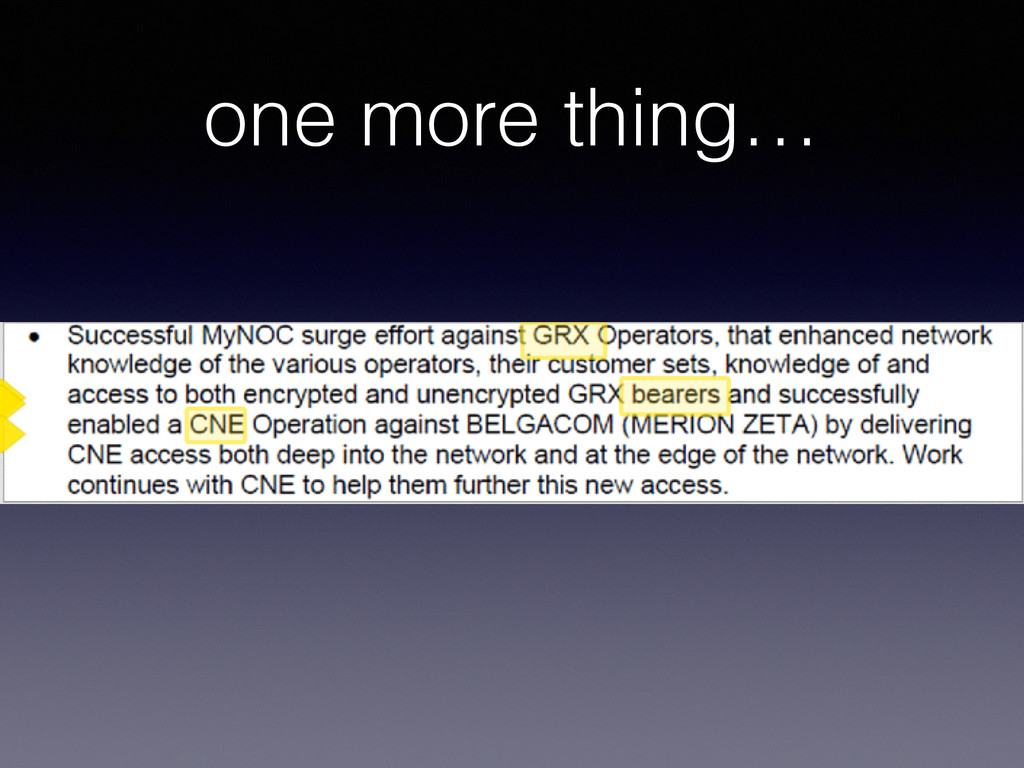
    GCHQ had compromised Belgacom with what would later be discovered as Regin • the name appeared for the first time on the VirusTotal website on March 9th 2011 • Undetected in Belgacoms networks until symptoms in Summer 2012 • June 2013 - after an update exchange falls over Belgacom contact M$ who had no clue? • Belgacom sys admins suspect virus > hire Fox IT • Belgacom informs authorities & Belgian MI get involved
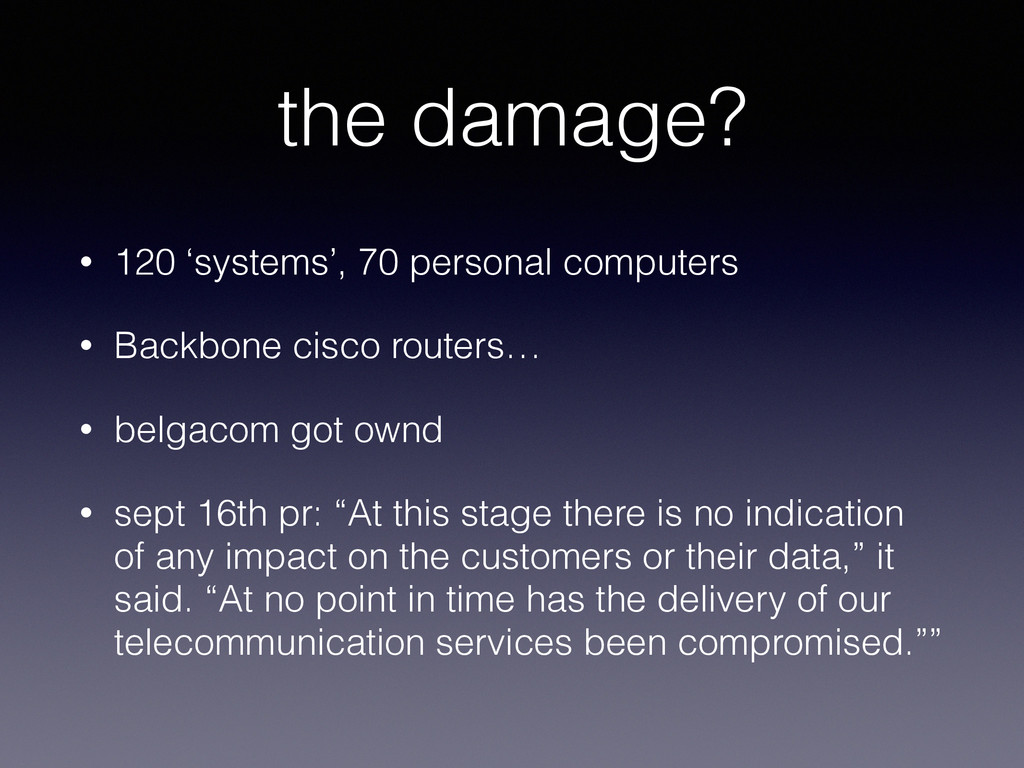
  25. the damage? • 120 ‘systems’, 70 personal computers • Backbone

    cisco routers… • belgacom got ownd • sept 16th pr: “At this stage there is no indication of any impact on the customers or their data,” it said. “At no point in time has the delivery of our telecommunication services been compromised.””