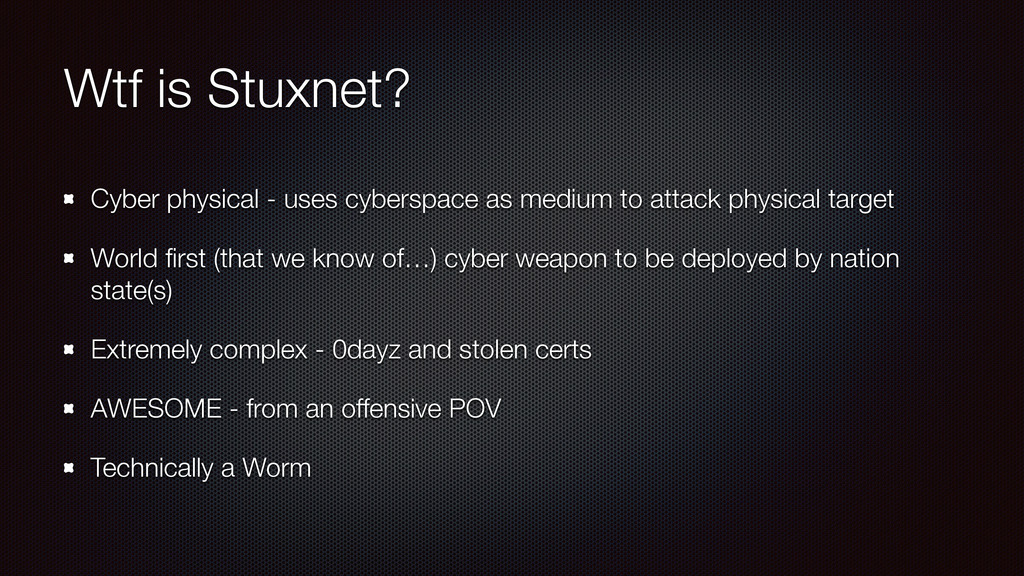
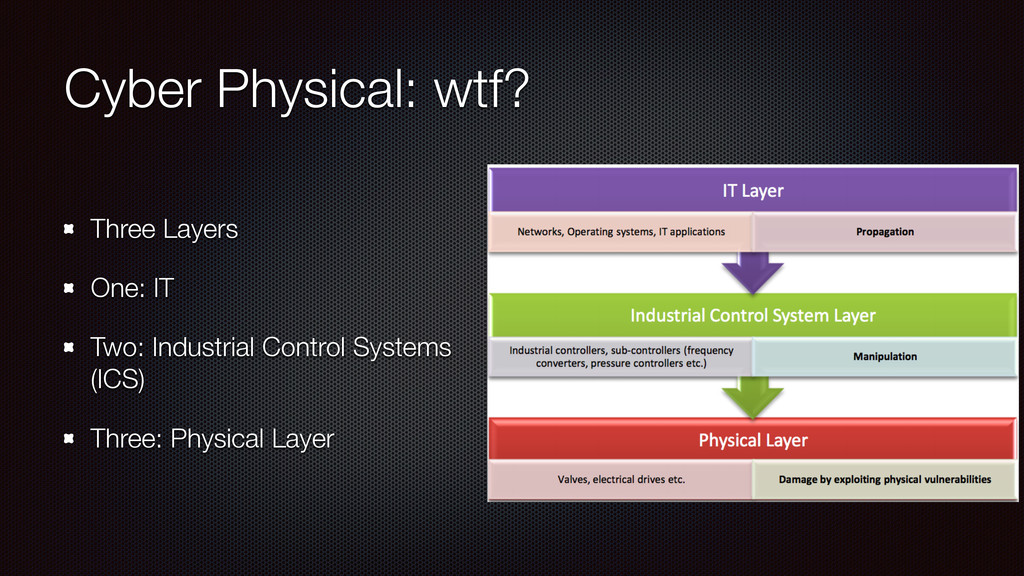
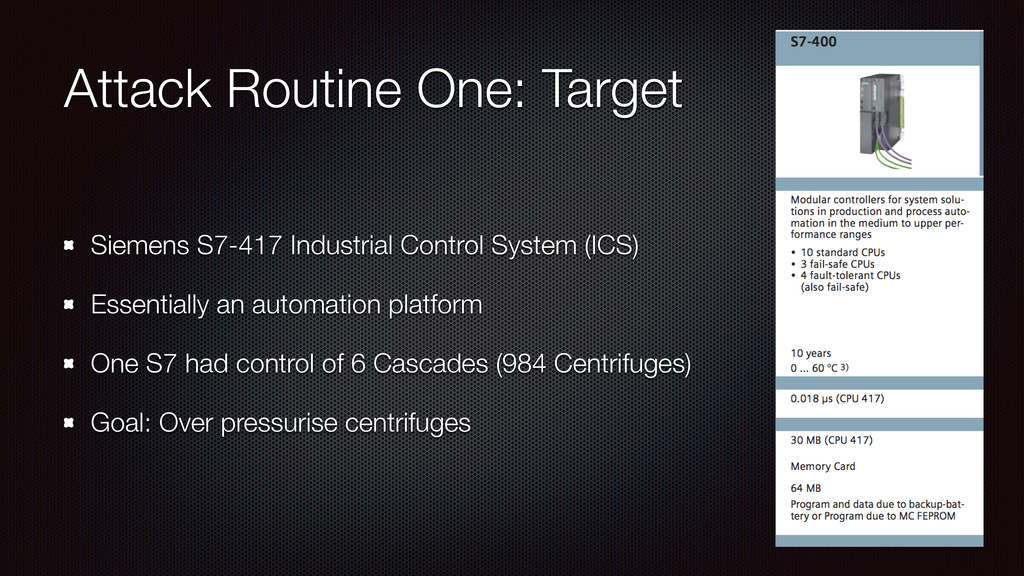
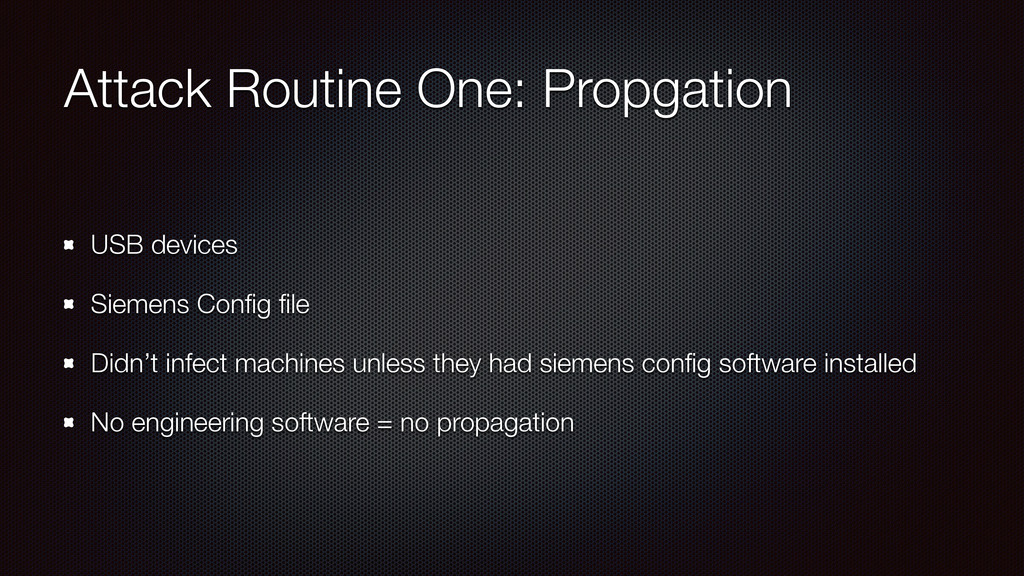
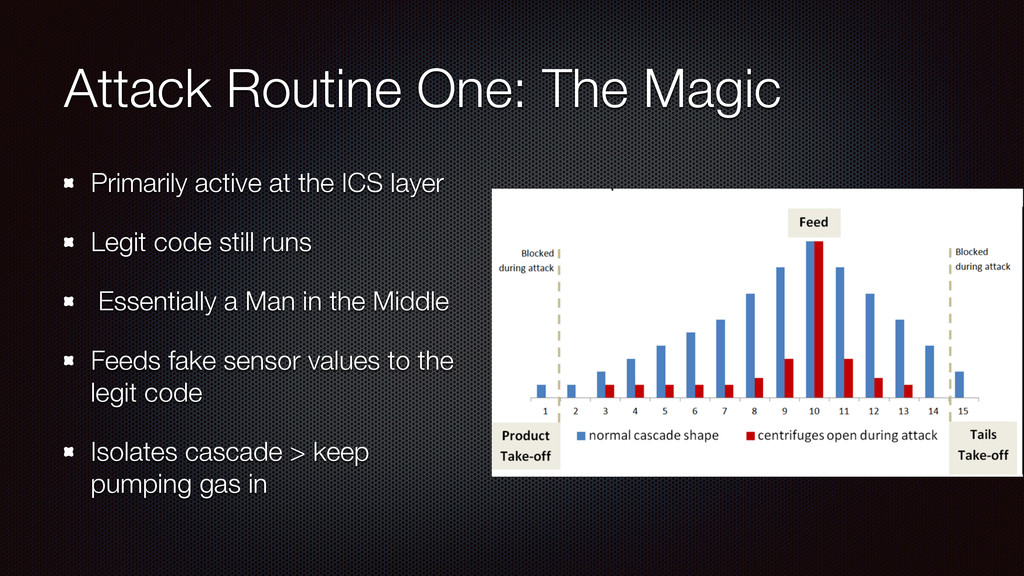
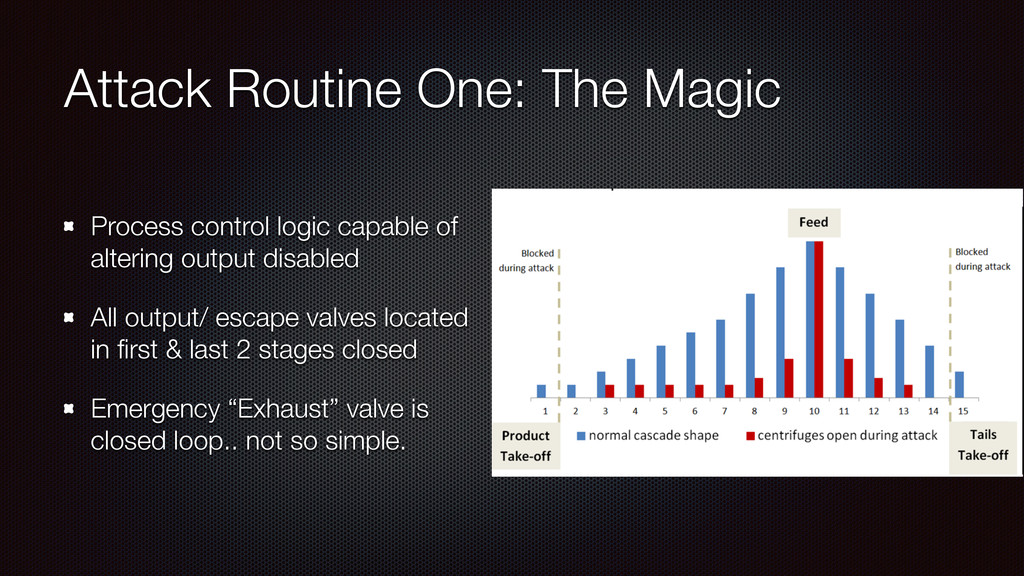
to attack physical target World first (that we know of…) cyber weapon to be deployed by nation state(s) Extremely complex - 0dayz and stolen certs AWESOME - from an offensive POV Technically a Worm
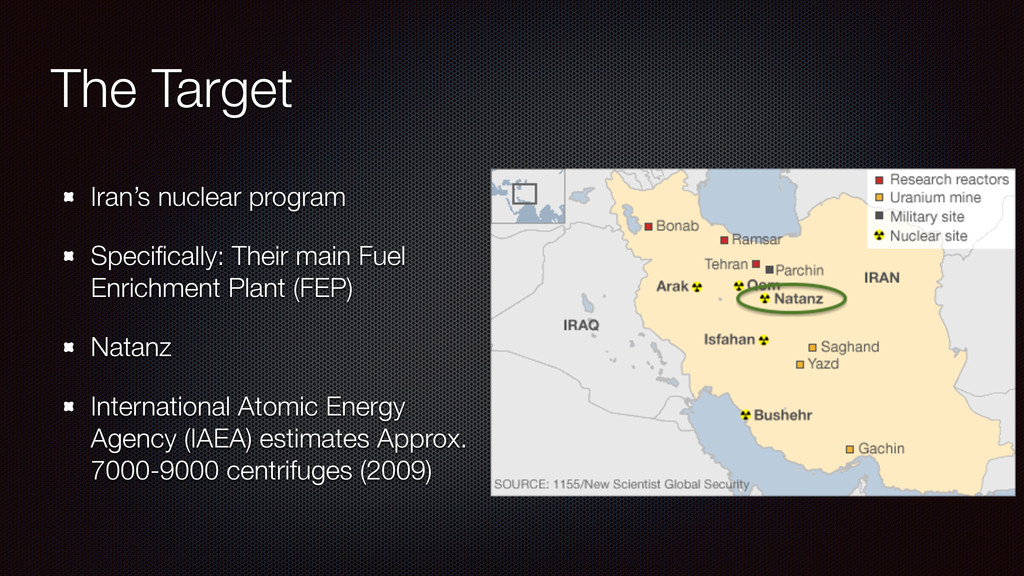
late 60’s/ 70’s Plans bought from former pakistanti nuclear scientist Design of IR-1 obsolete - reliability issues as early as late 80’s Most technology used obsolete
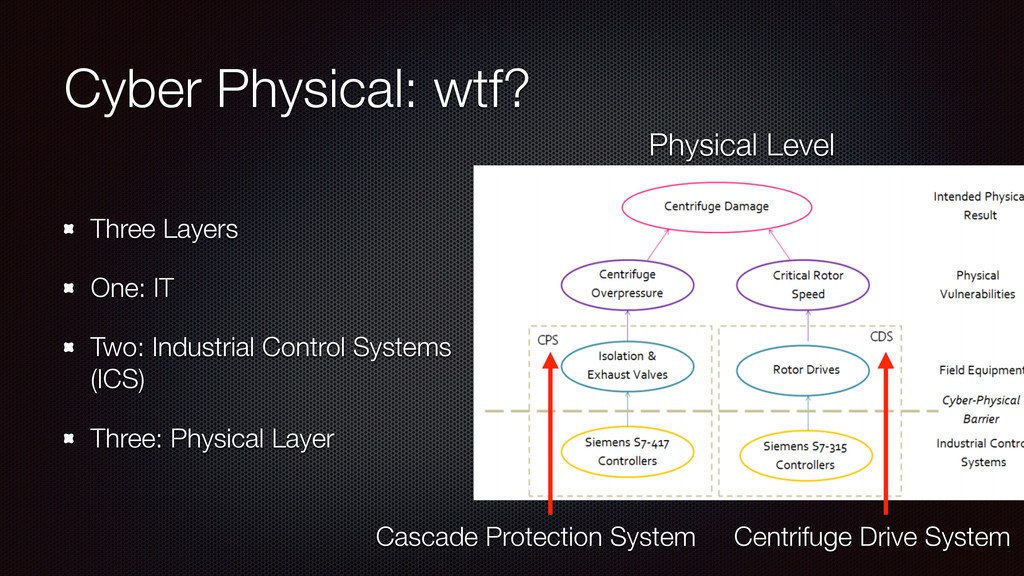
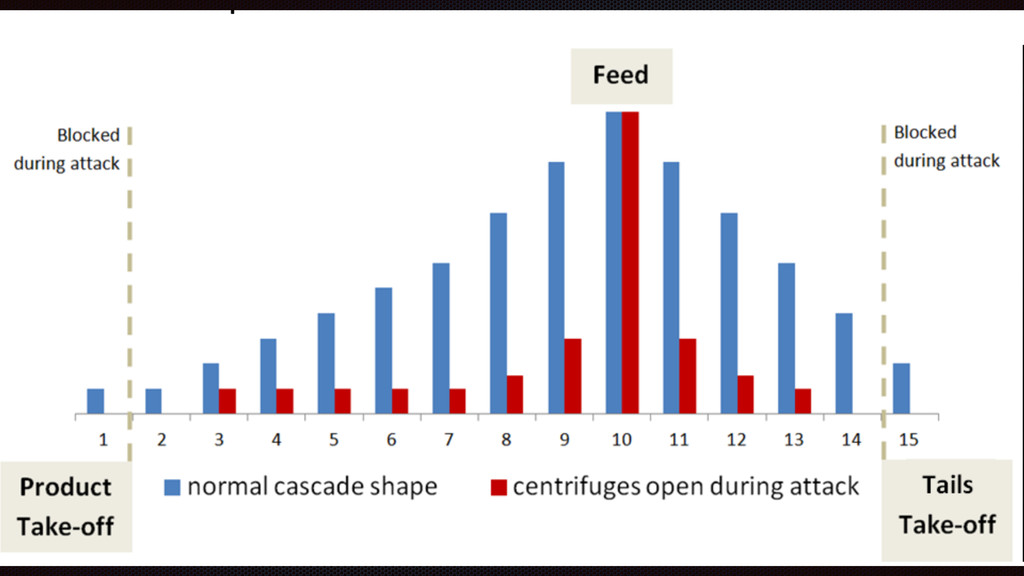
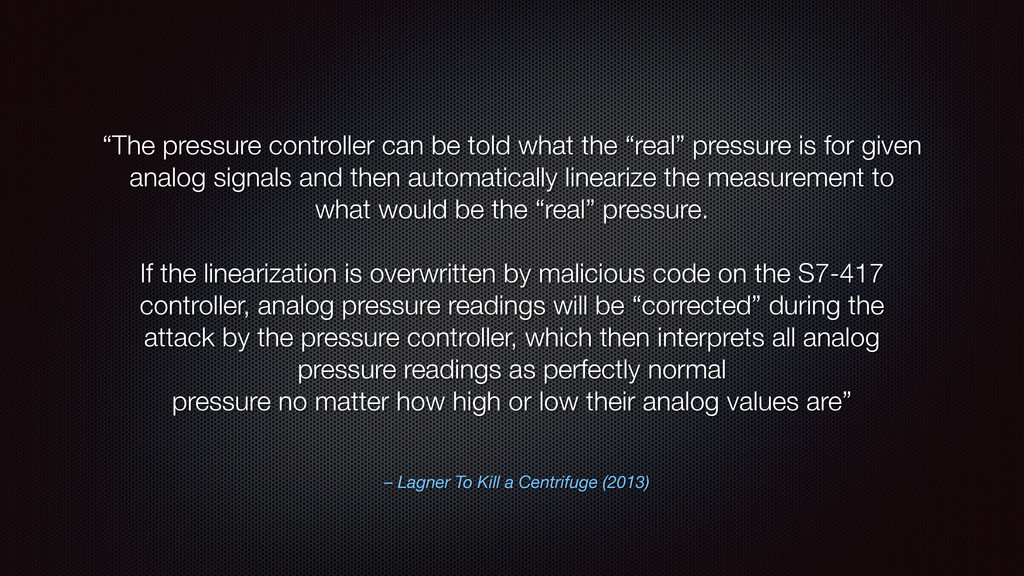
can be told what the “real” pressure is for given analog signals and then automatically linearize the measurement to what would be the “real” pressure. If the linearization is overwritten by malicious code on the S7-417 controller, analog pressure readings will be “corrected” during the attack by the pressure controller, which then interprets all analog pressure readings as perfectly normal pressure no matter how high or low their analog values are”
rotor speed Much smaller Siemens S7-315 ICS (164 Centrifuges) Goal: Take centrifuges through critical resonance (make them spin too fast) New code still contained first attack routine however is was dormant
(4, like seriously 4) Stolen Driver certs (RealTek & JMicron) Exploits SCADA vulns New team? First routine probably made by ICS sec experts. This time probably real hackerz
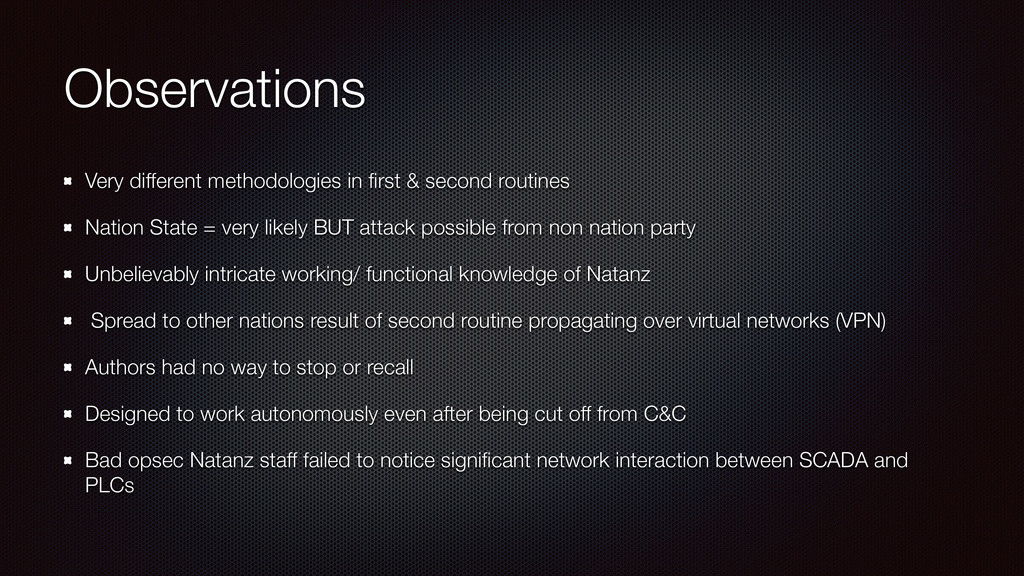
State = very likely BUT attack possible from non nation party Unbelievably intricate working/ functional knowledge of Natanz Spread to other nations result of second routine propagating over virtual networks (VPN) Authors had no way to stop or recall Designed to work autonomously even after being cut off from C&C Bad opsec Natanz staff failed to notice significant network interaction between SCADA and PLCs
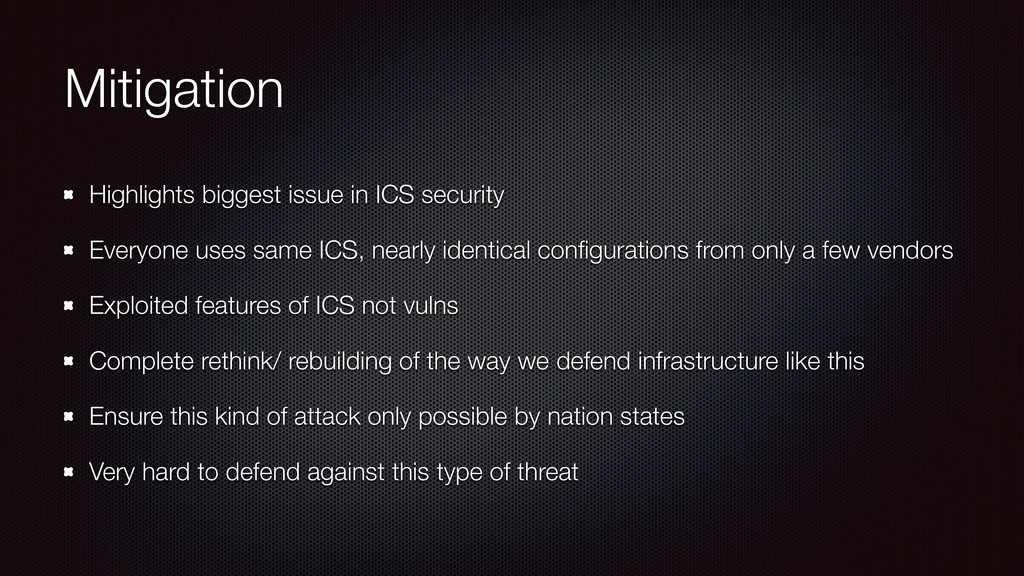
ICS, nearly identical configurations from only a few vendors Exploited features of ICS not vulns Complete rethink/ rebuilding of the way we defend infrastructure like this Ensure this kind of attack only possible by nation states Very hard to defend against this type of threat


 0xmikey
 ymotongpoo
 shugo
 pfn
 jyouryuusui
 kash1064
 sansantech
 kzkhykw1991
 rfdnxbro
 syuchimu
 satoshi7
 odashi
 shogo4131
 chrislema
 kneath
 tmiket
 pwiseman
 jonyablonski
 csswizardry
 joshbly
 marktimemedia
 tammyeverts
 shpigford
 ipullrank