Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Dissecting TLS [HackSoc]

Sponsored · SiteGround - Reliable hosting with speed, security, and support you can count on. →
Avatar for Mikey Mikey
March 23, 2015

Dissecting TLS [HackSoc]

Introduction to and overview of the SSL/TLS protocols. Given at Abertay Ethical Hacking Society at some point.

Avatar for Mikey

Mikey

March 23, 2015

More Decks by Mikey

Other Decks in Technology

Transcript

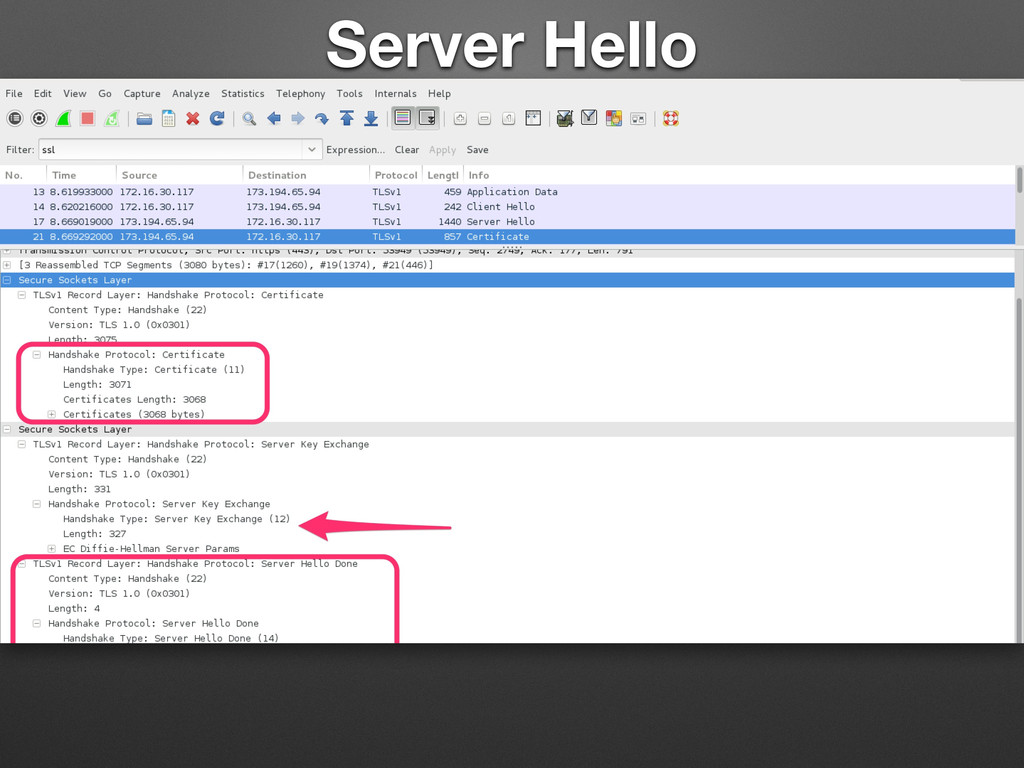
  1. contents • fucks tls? • explain some shit - hashing

    - RSA - ECC • how it works • ws to goog • whats wrong? sha1 shit - dodgy curves - bruce & goog • cool secure stuff • sha2
  2. running order 1. What is TLS, Brief History 2. How

    does TLS work? 3. Version Differences 4. Previous attacks
  3. • Transport Layer Security • most widely used public key

    crypto in the world • normally appears between a browser and web server • used to secure TCP based apps • evolutionary brother of SSL • SHOULD be the protocol being used when you see > The Fuck’s TLS?
  4. The Fucks TLS - History • 1994 - SSL 1.0

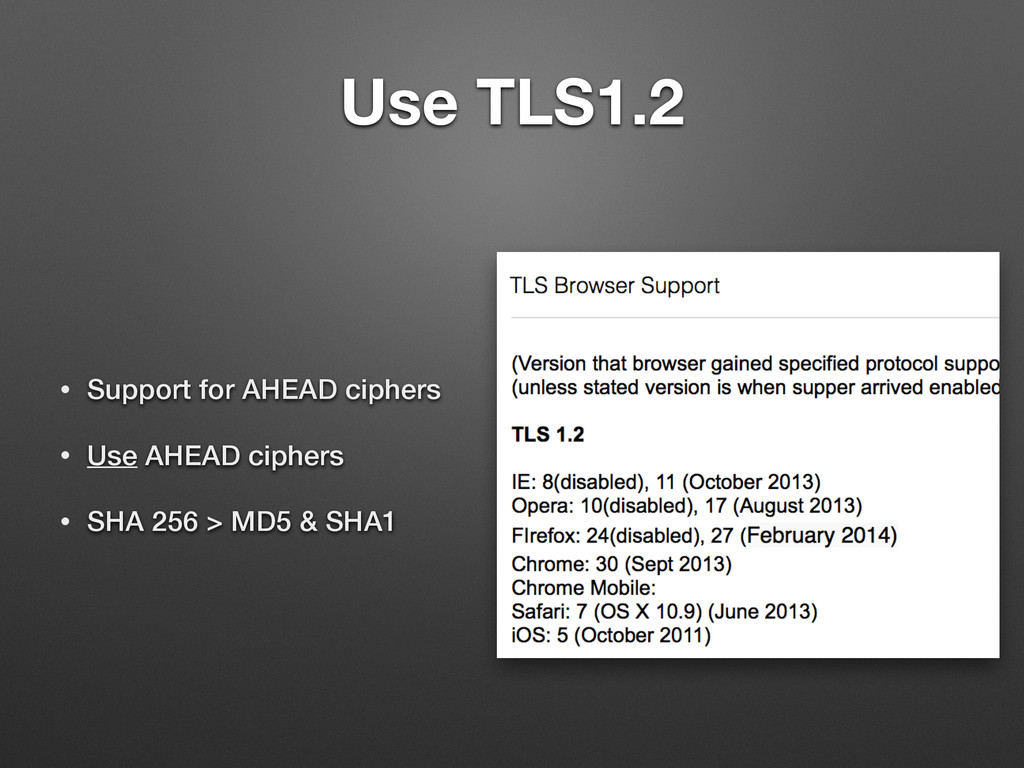
    developed by Netscape • Feb 1995 - SSL 2.0 along with Netscape Navigator • 1995 - PCT specification from MS • 1996 - SSL 3.0 Total redesign by Netscape et al • Demand for standardisation - IETF • 1999 - TLS 1.0 (RFC 2246) - upgrade of SSL 3.0 • 2006 - TLS 1.1 • 2008 - TLS 1.2 - the good shit • 2011 - Latest TLS RFC 6176 • TLS 1.3 - DRAFT
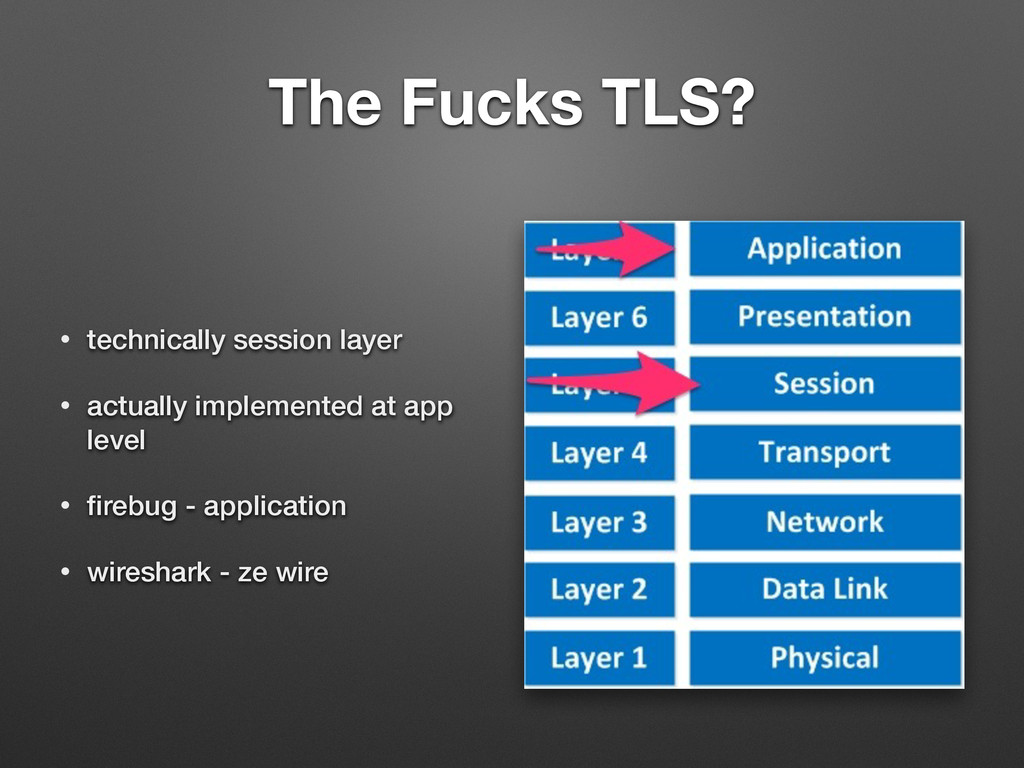
  5. The Fucks TLS? • technically session layer • actually implemented

    at app level • firebug - application • wireshark - ze wire
  6. • bi-directional encrypted tunnel • any arbitrary data can be
    tunnelled through TLS • HTTPS != TLS • TLS tunnel established then HTTP kicks in The Fucks TLS?
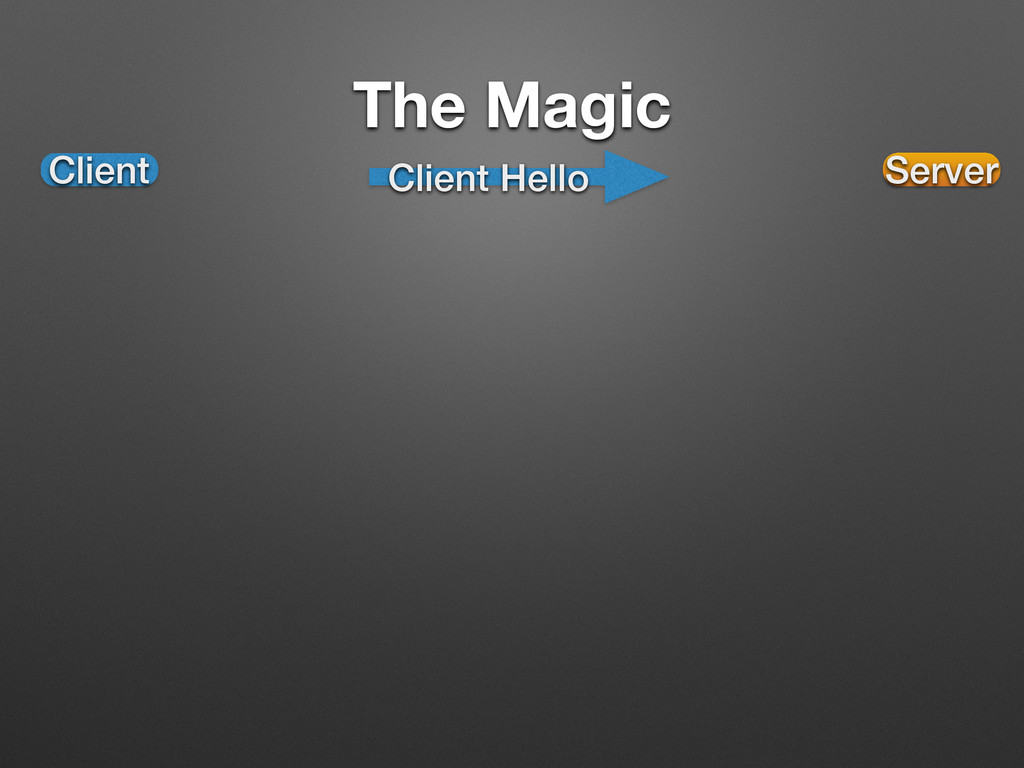
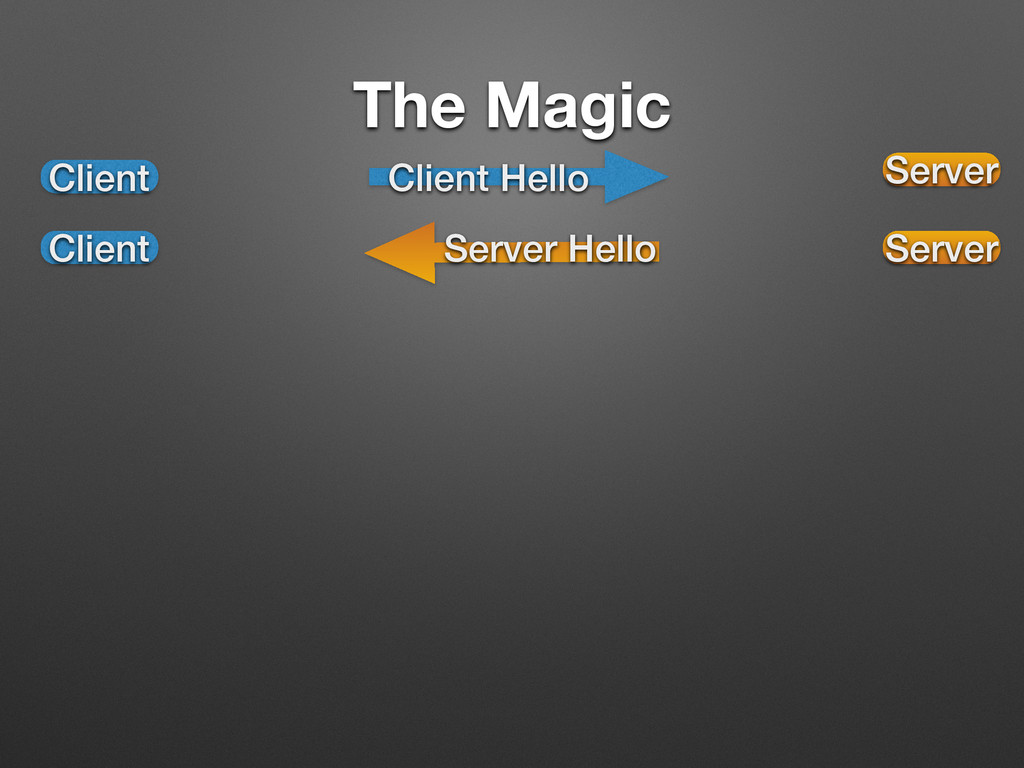
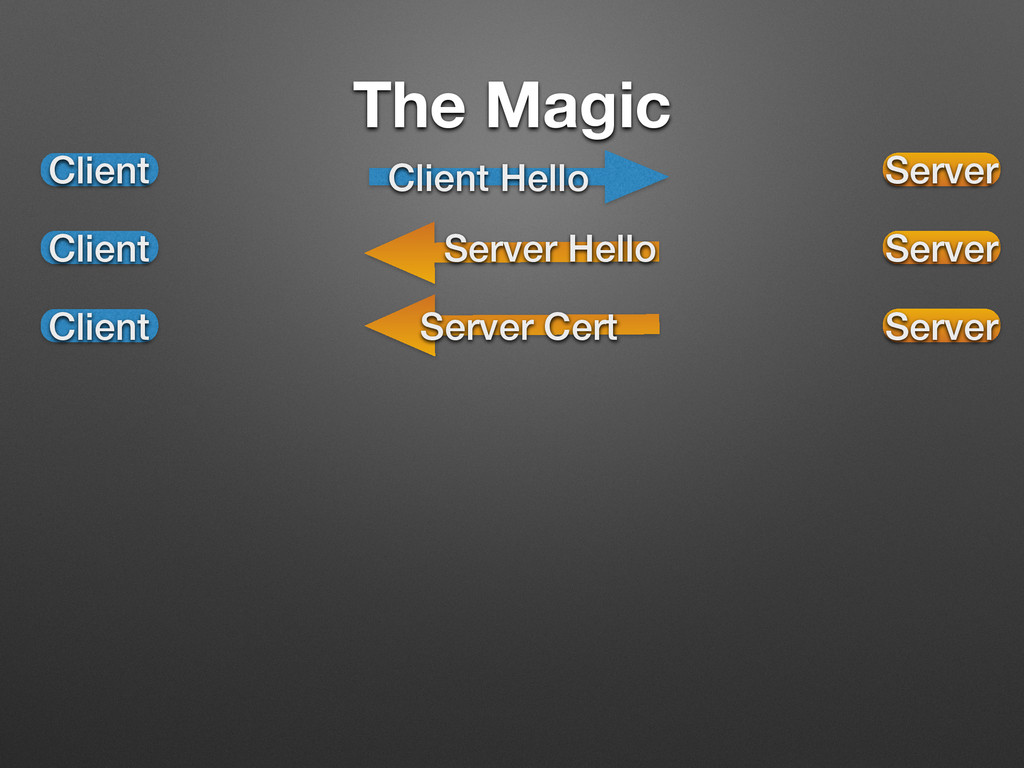
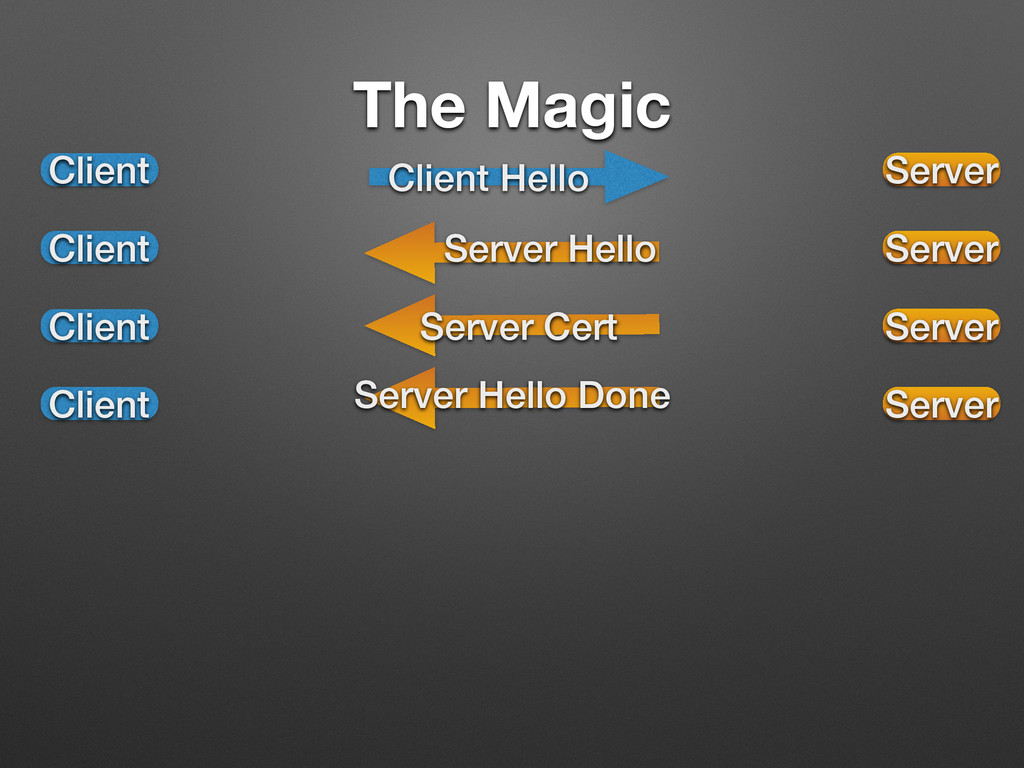
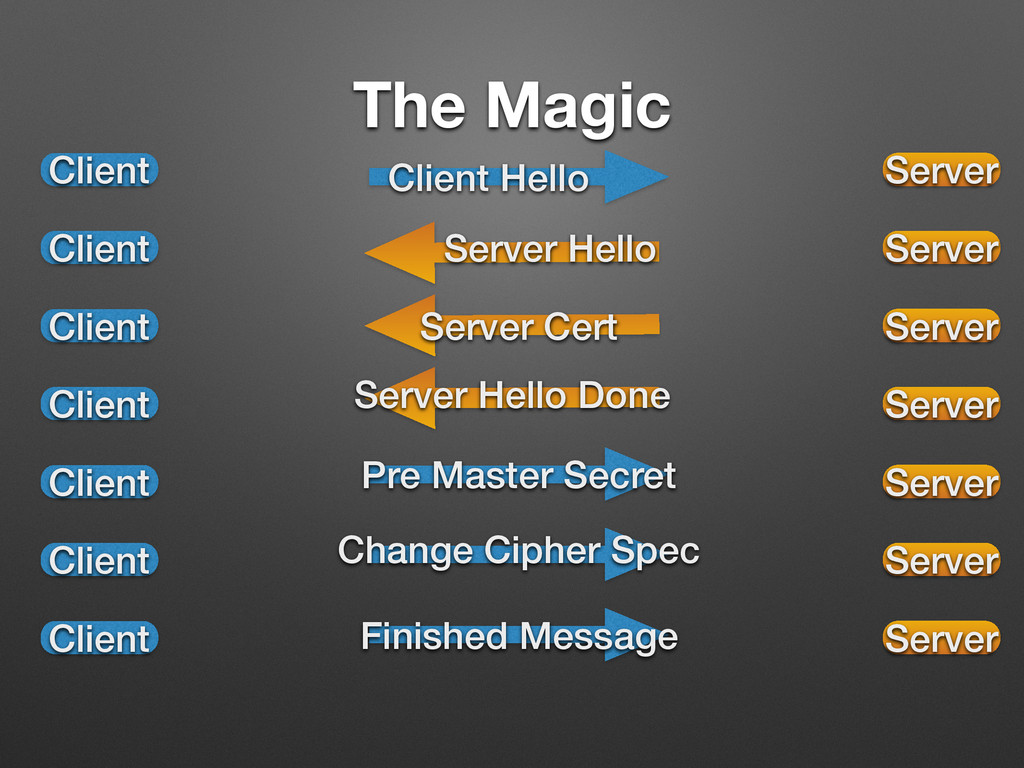
  7. The Magic Client Server Server Client Client Hello Server Hello

    Client Server Server Cert Client Server Server Hello Done
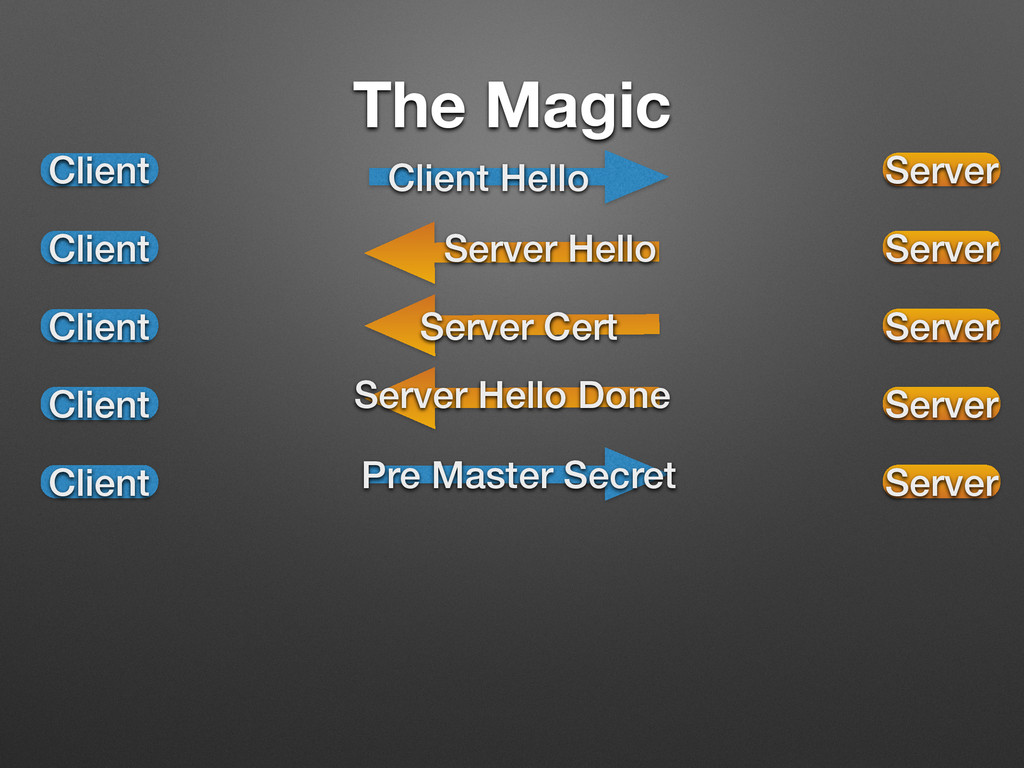
  8. The Magic Client Server Server Client Client Hello Server Hello

    Client Server Server Cert Client Server Server Hello Done Client Server Pre Master Secret
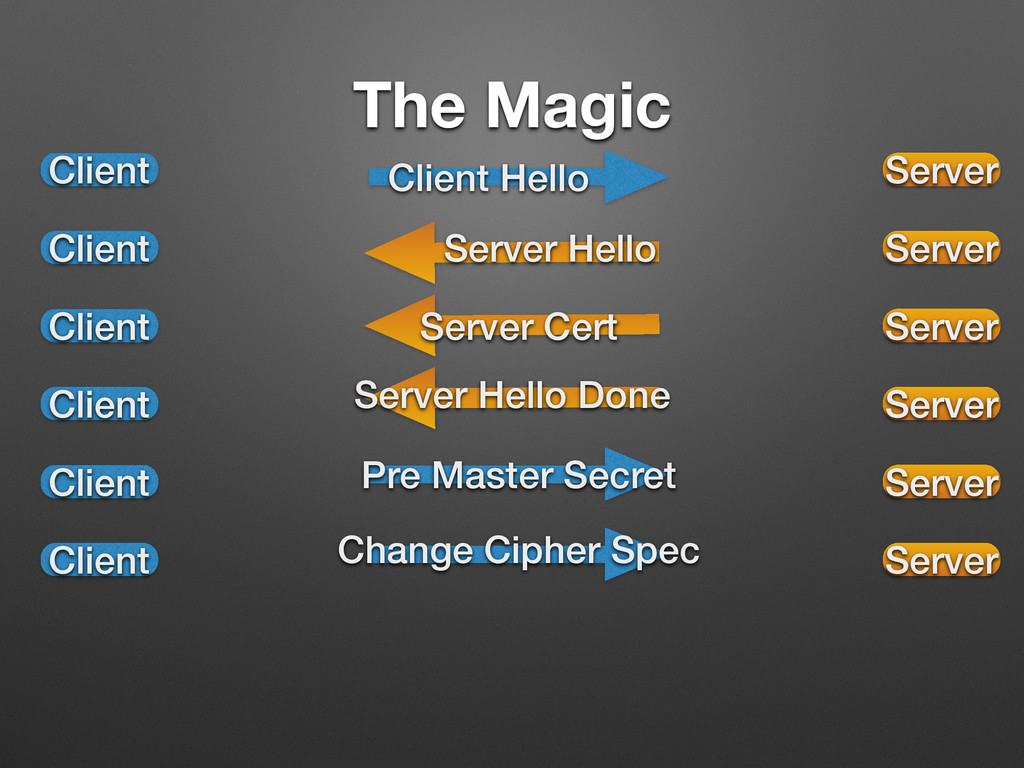
  9. The Magic Client Server Server Client Client Hello Server Hello

    Client Server Server Cert Client Server Server Hello Done Client Server Pre Master Secret Client Server Change Cipher Spec
  10. The Magic Client Server Server Client Client Hello Server Hello

    Client Server Server Cert Client Server Server Hello Done Client Server Pre Master Secret Client Server Client Server Change Cipher Spec Finished Message
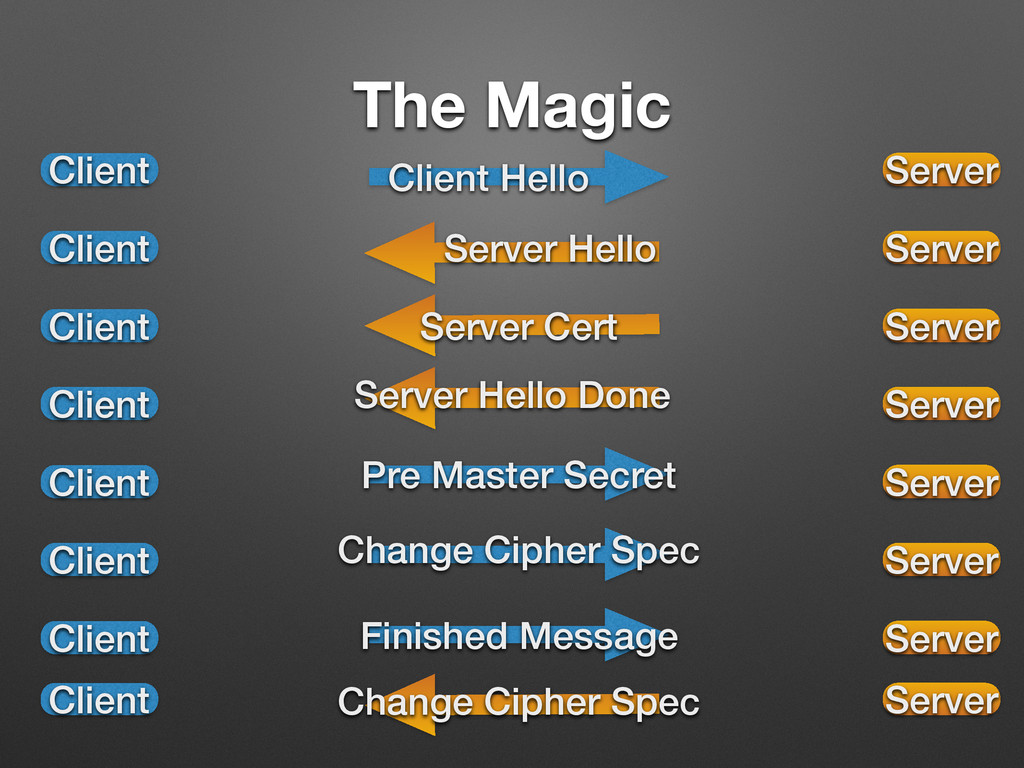
  11. The Magic Client Server Server Client Client Hello Server Hello

    Client Server Server Cert Client Server Server Hello Done Client Server Pre Master Secret Client Server Client Server Change Cipher Spec Finished Message Client Server Change Cipher Spec
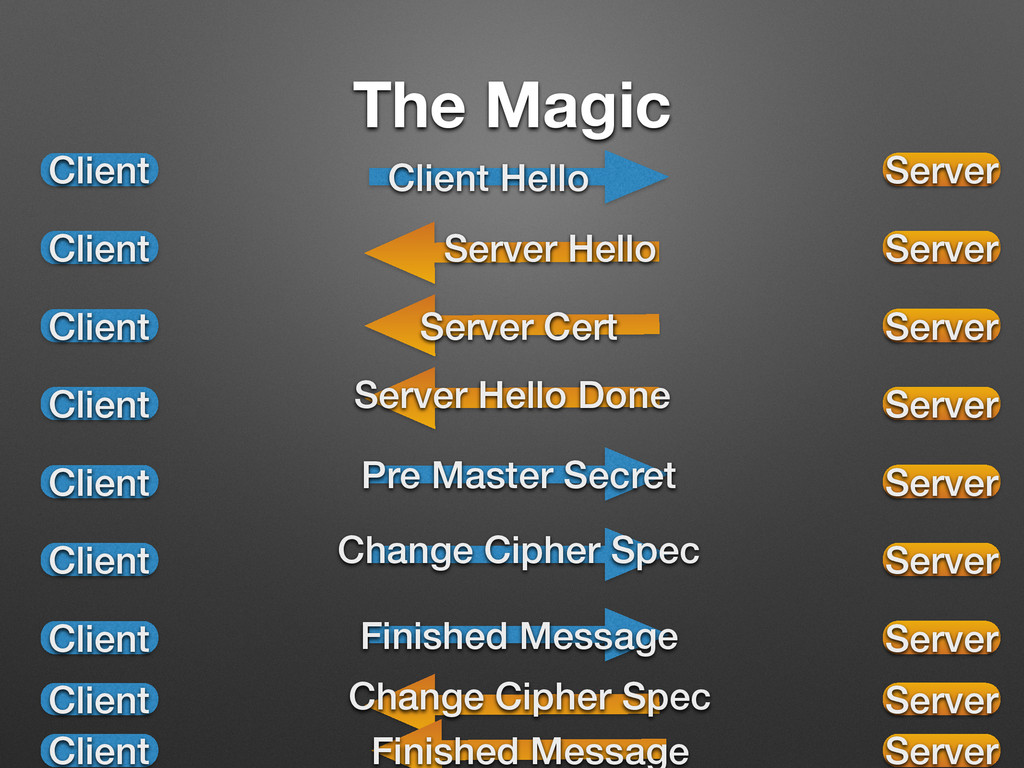
  12. The Magic Client Server Server Client Client Hello Server Hello

    Client Server Server Cert Client Server Server Hello Done Client Server Pre Master Secret Client Server Client Server Change Cipher Spec Finished Message Client Server Change Cipher Spec Client Server Finished Message
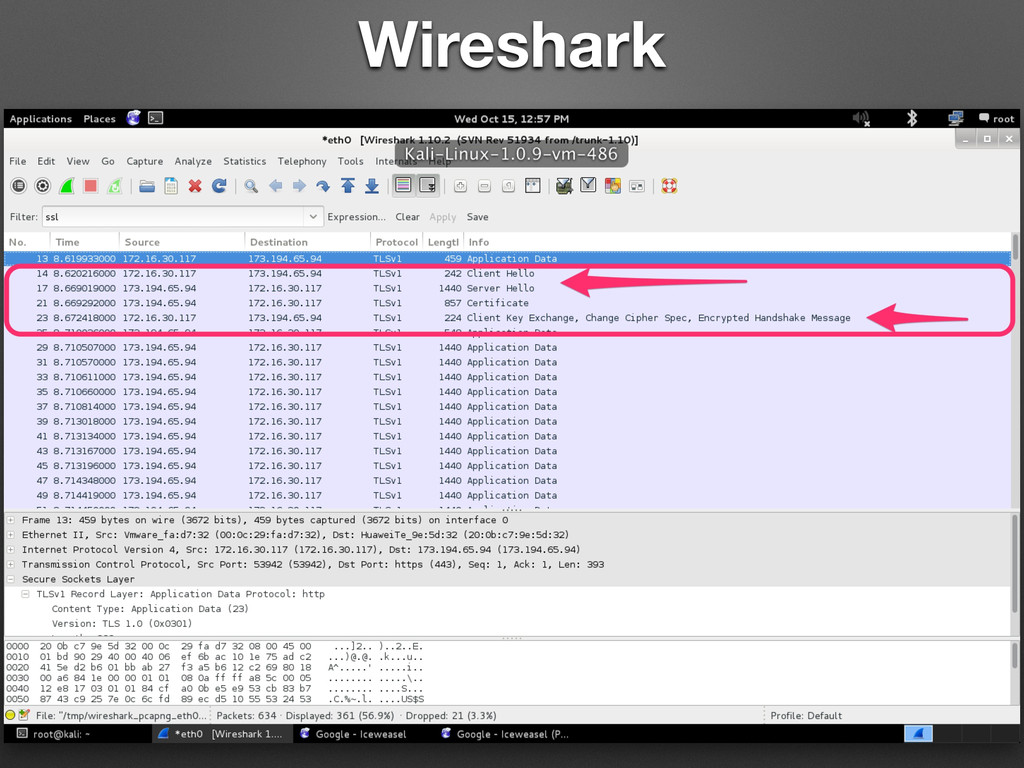
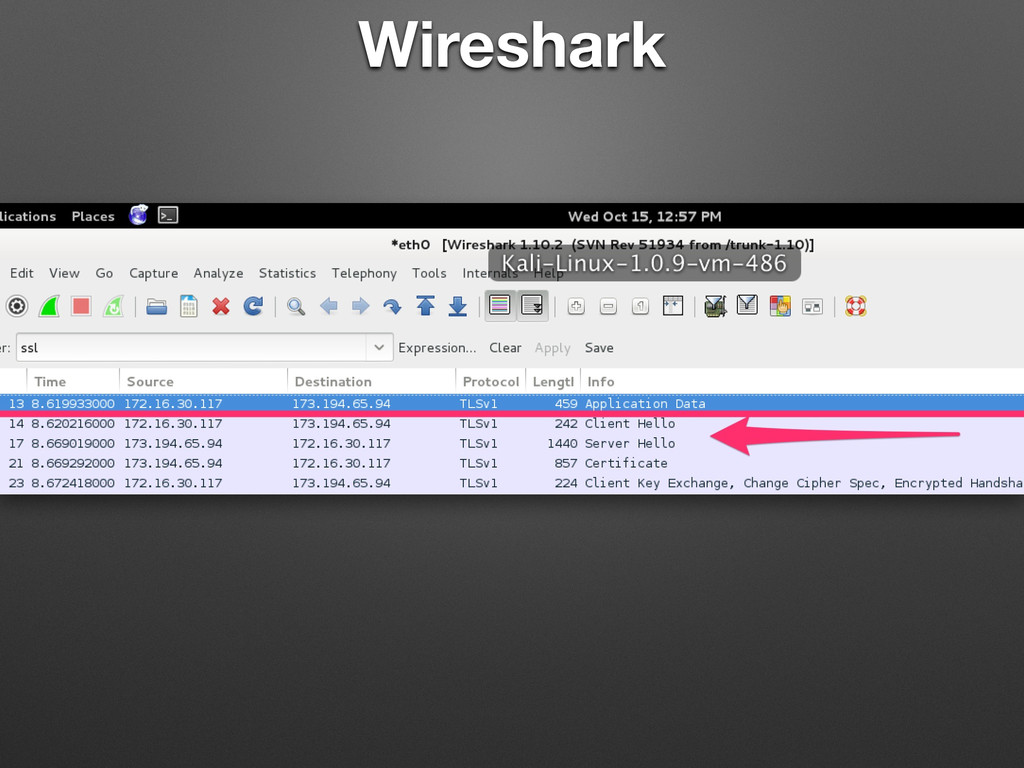
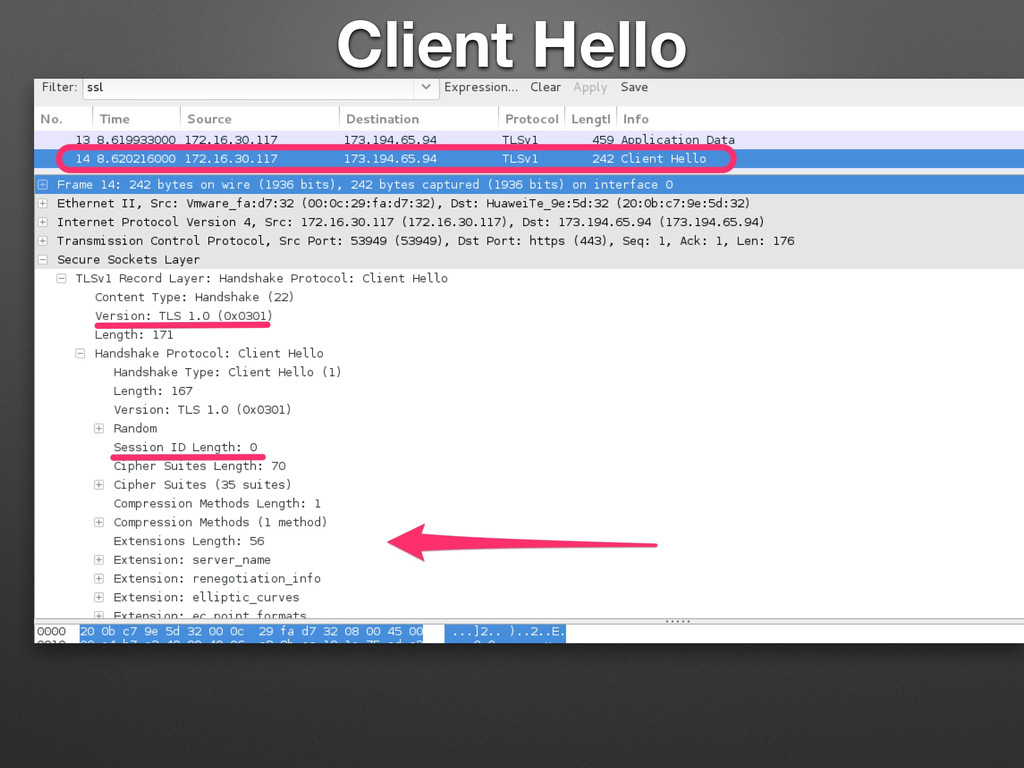
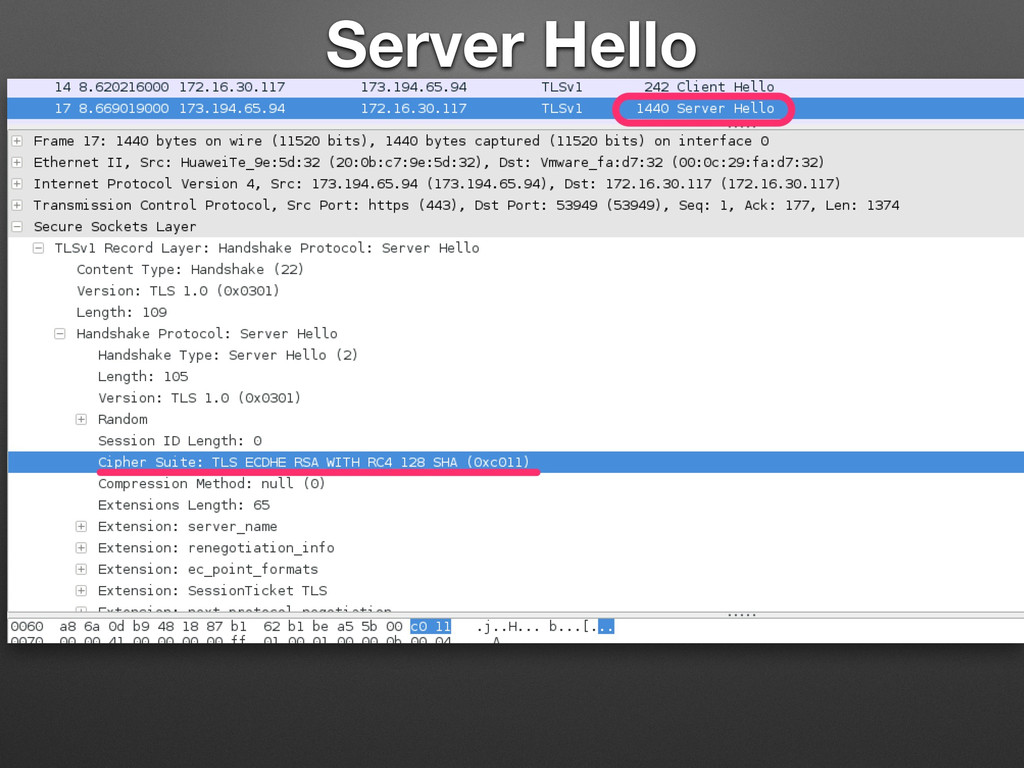
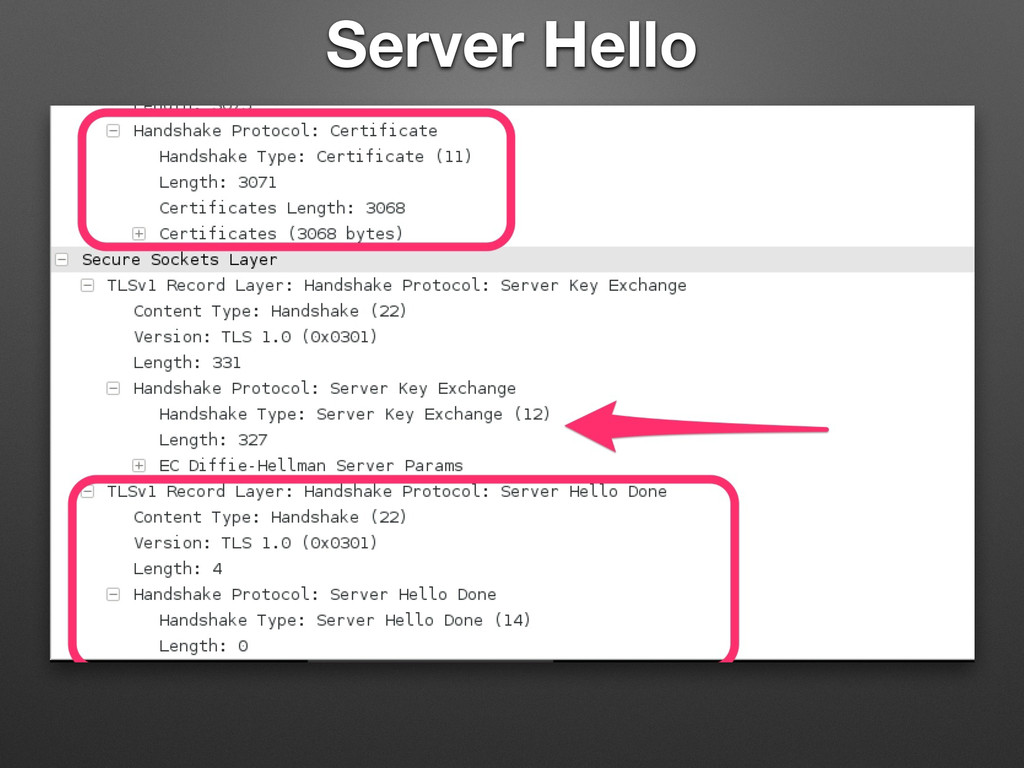
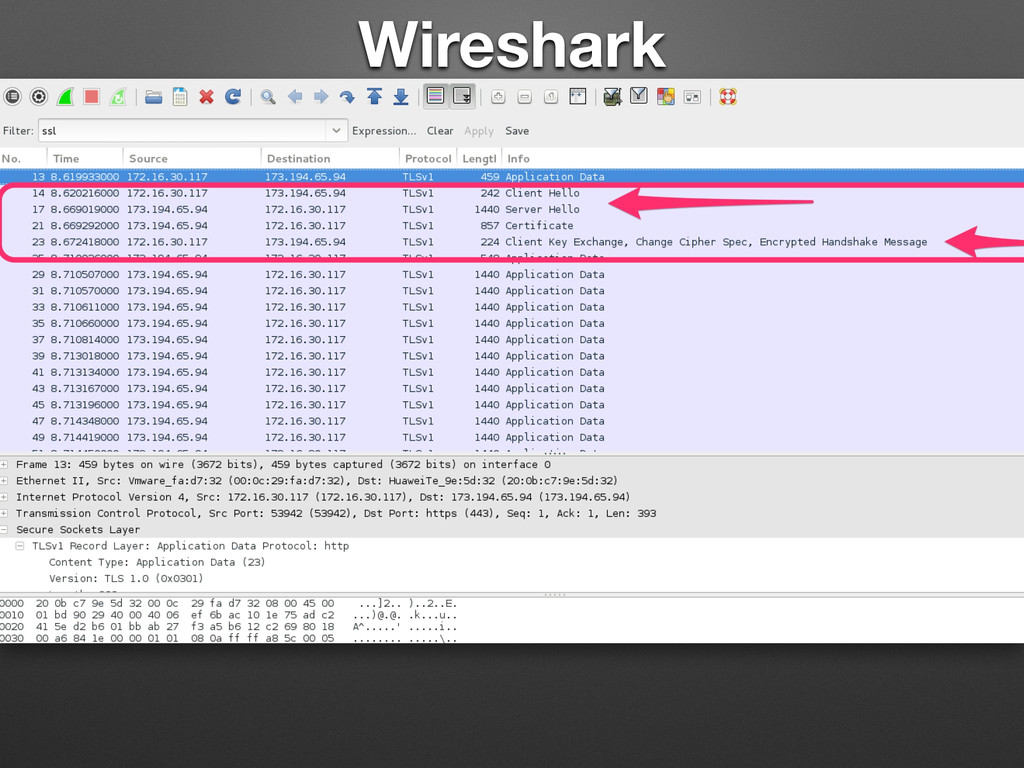
  13. Wireshark • hopefully that was a nice visual overview •

    lets look at what happens on the wire • establishing a new TLS connection to google.co.uk
  14. SSL V2 • uses same keys for encryption and authentication

    • weak MAC construction uses MD5 (len extension attack) • doesn't protect handshake.. downgrade attacks • no virtual hosting support
  15. SSL V3 • This thing needs to die.. • POODLE

    (new today..) • multiple attacks against CBC ciphers • when attacking SSL/ TLS usual step is to first downgrade to SSL v3
  16. TLS • protection against downgrade attacks • number subsequent application

    data packets • Finished message contains MAC of all handshake messages • PRF splits the input hashes one with SHA1 + MD5 then XOR the digests together
  17. TLS 1.0 (1999) • BEAST attack (2011) • BEAST originally

    from 2002… no public practical exploits til 2011 • in theory could have been exploited in wild (no evidence) since 2002
  18. While we’re here.. • SHA1 should be considered cryptographically insecure

    • Use SHA3 Keccak • Google et al depreciating SSL certs signed w/ SHA1 (to be complete Jan 2017) • chrome will throw warnings
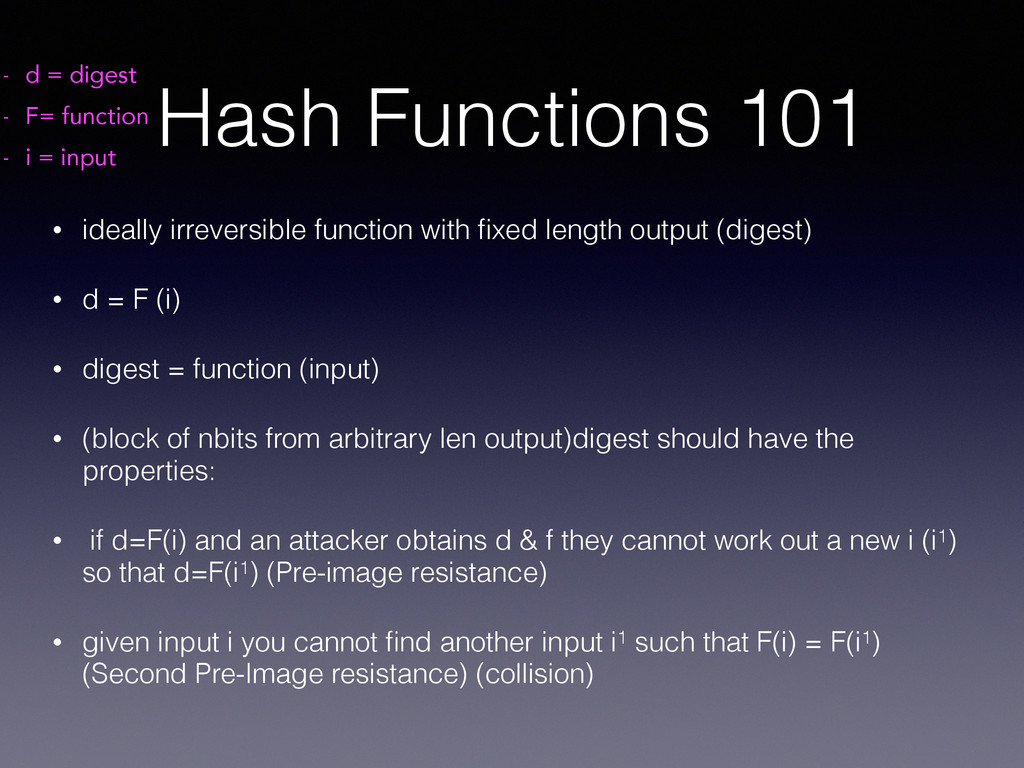
  19. Hash Functions 101 • ideally irreversible function with fixed length

    output (digest) • d = F (i) • digest = function (input) • (block of nbits from arbitrary len output)digest should have the properties: • if d=F(i) and an attacker obtains d & f they cannot work out a new i (i1) so that d=F(i1) (Pre-image resistance) • given input i you cannot find another input i1 such that F(i) = F(i1) (Second Pre-Image resistance) (collision) - d = digest - F= function - i = input
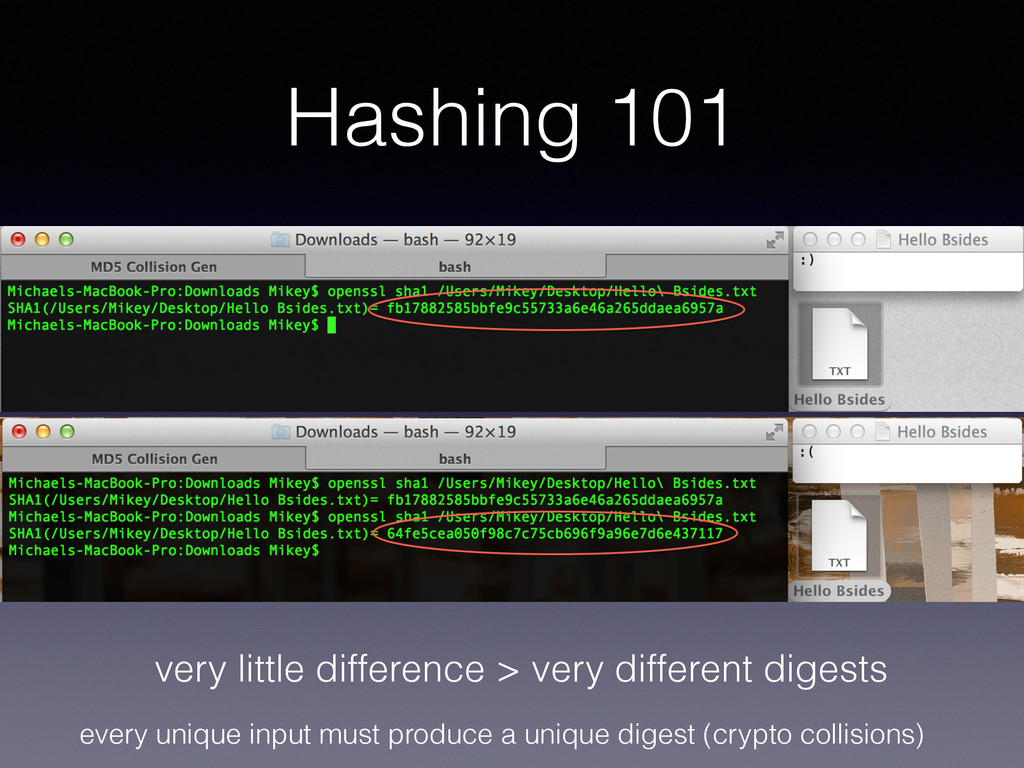
  20. Hashing 101 every unique input must produce a unique digest

    (crypto collisions) very little difference > very different digests
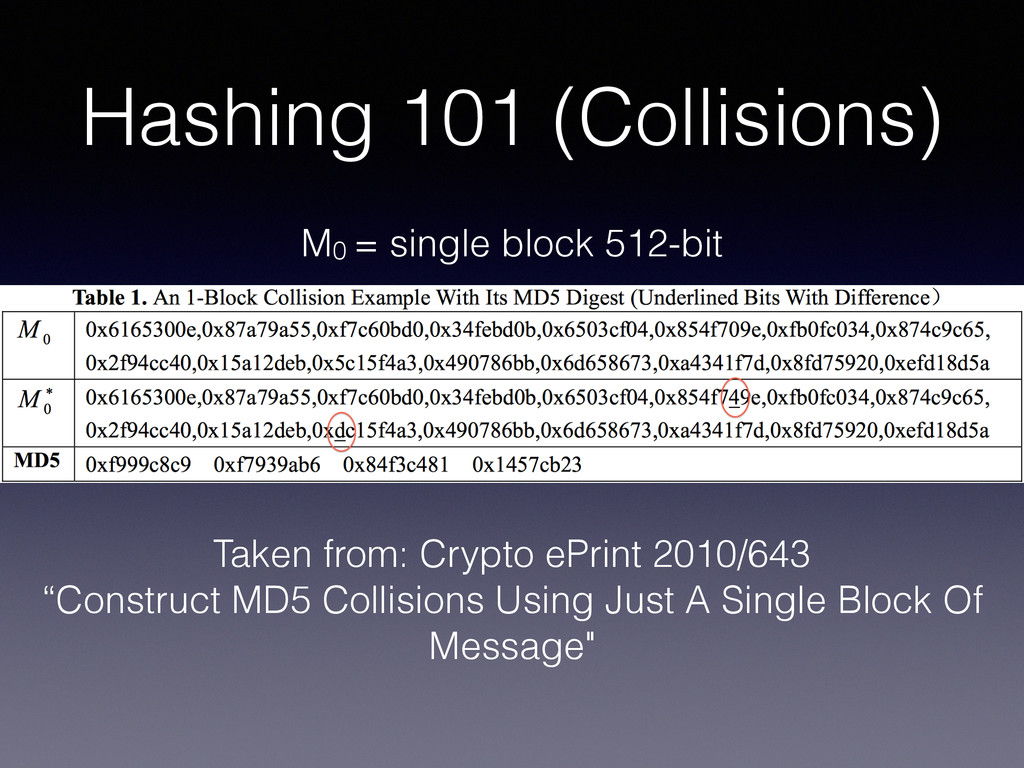
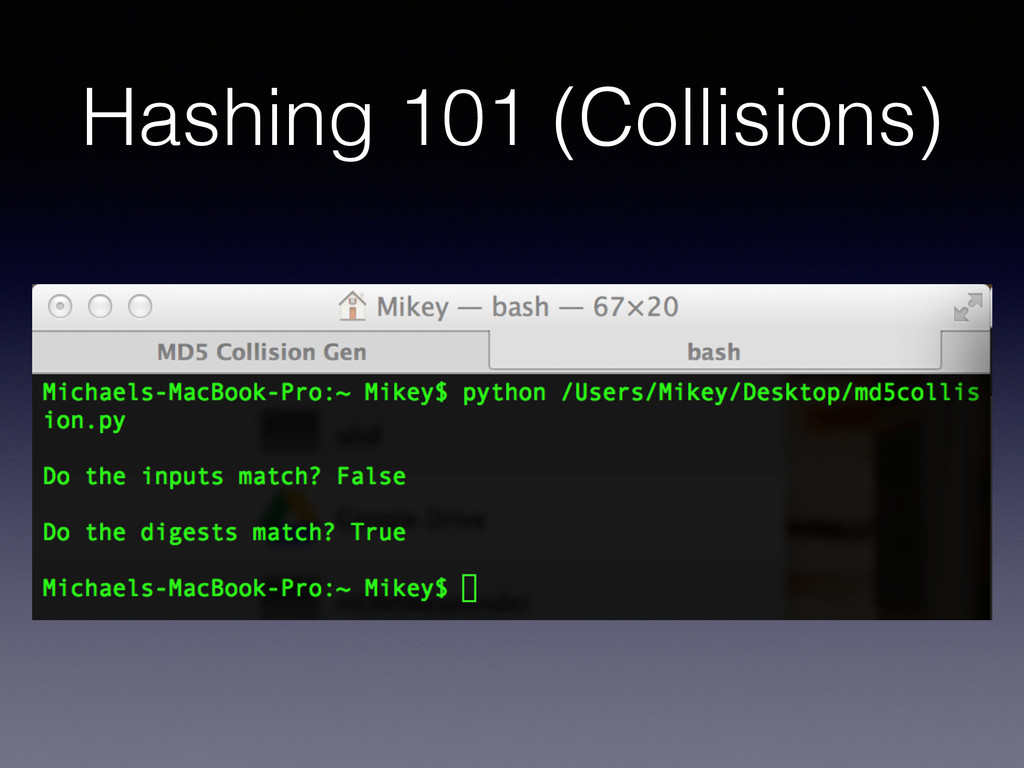
  21. Hashing 101 (Collisions) Taken from: Crypto ePrint 2010/643 “Construct MD5

    Collisions Using Just A Single Block Of Message" M0 = single block 512-bit
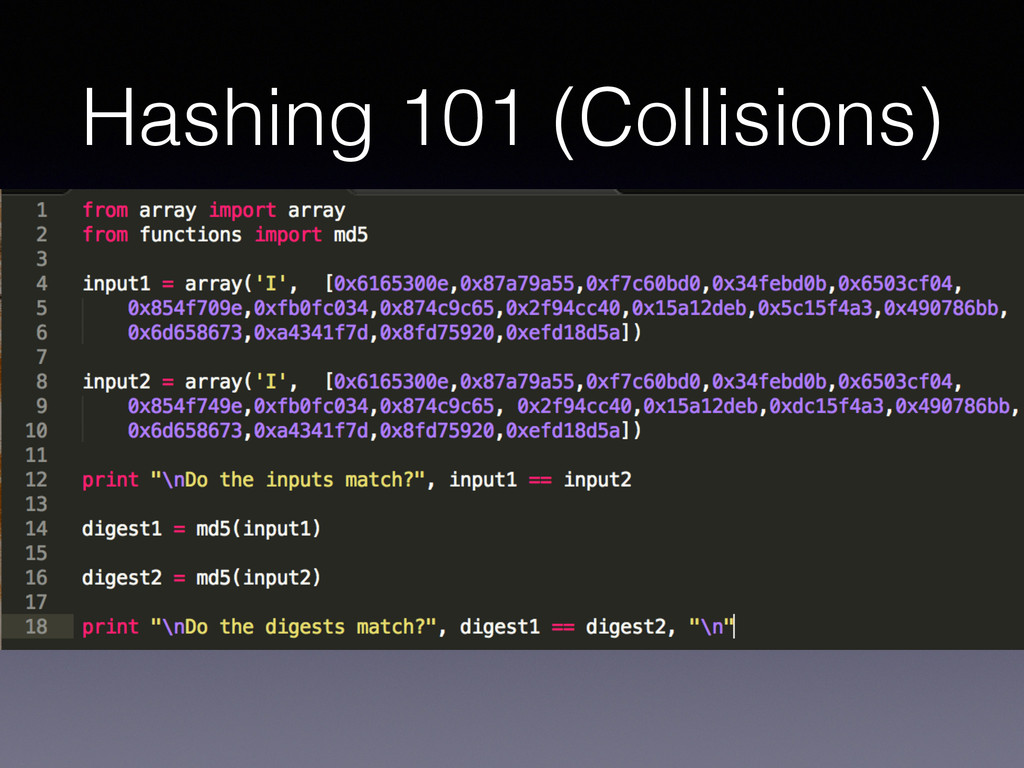
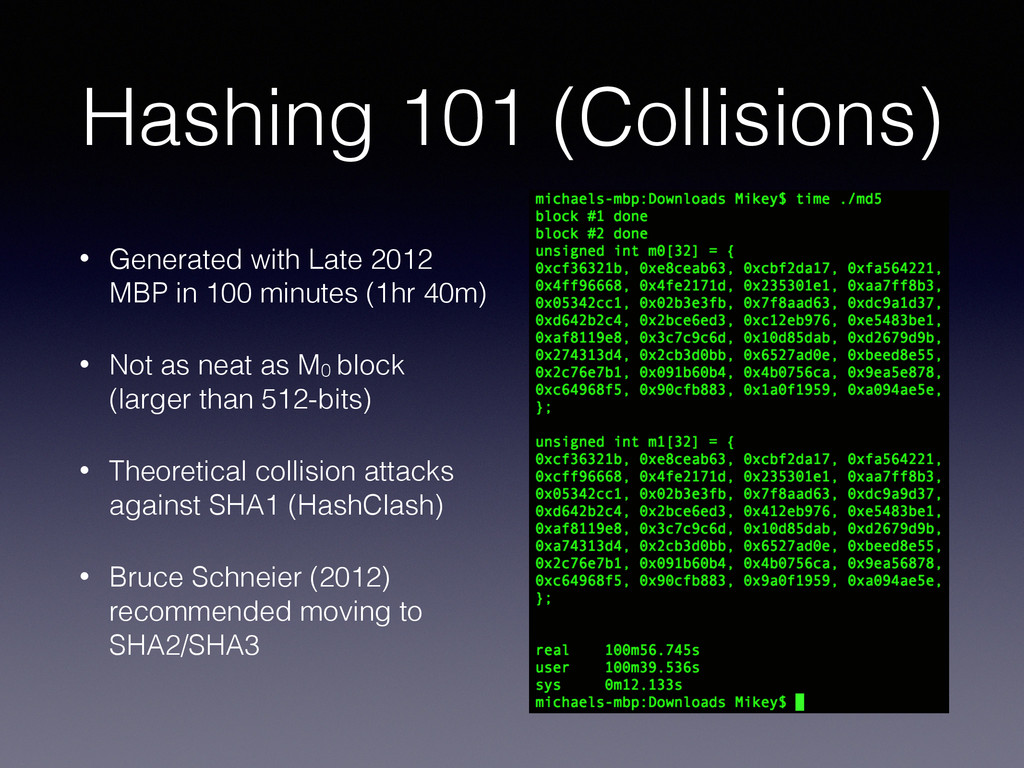
  22. Hashing 101 (Collisions) • Generated with Late 2012 MBP in

    100 minutes (1hr 40m) • Not as neat as M0 block (larger than 512-bits) • Theoretical collision attacks against SHA1 (HashClash) • Bruce Schneier (2012) recommended moving to SHA2/SHA3
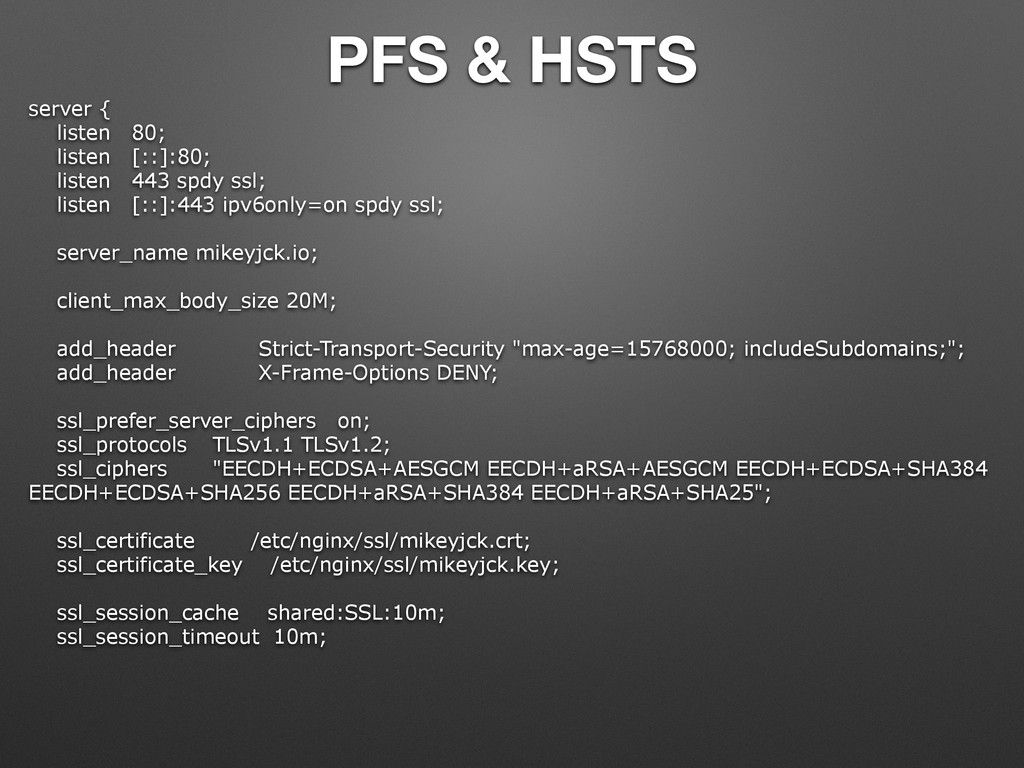
  23. PFS & HSTS server { listen 80; listen [::]:80; listen

    443 spdy ssl; listen [::]:443 ipv6only=on spdy ssl; server_name mikeyjck.io; client_max_body_size 20M; add_header Strict-Transport-Security "max-age=15768000; includeSubdomains;"; add_header X-Frame-Options DENY; ssl_prefer_server_ciphers on; ssl_protocols TLSv1.1 TLSv1.2; ssl_ciphers "EECDH+ECDSA+AESGCM EECDH+aRSA+AESGCM EECDH+ECDSA+SHA384 EECDH+ECDSA+SHA256 EECDH+aRSA+SHA384 EECDH+aRSA+SHA25"; ssl_certificate /etc/nginx/ssl/mikeyjck.crt; ssl_certificate_key /etc/nginx/ssl/mikeyjck.key; ssl_session_cache shared:SSL:10m; ssl_session_timeout 10m;
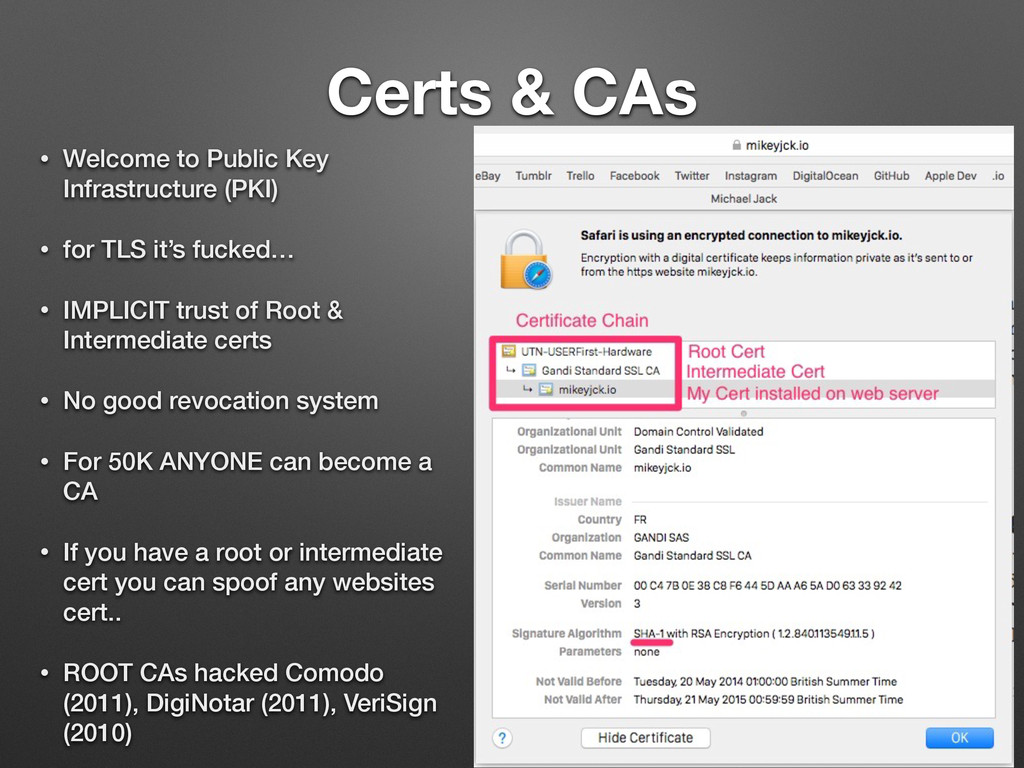
  24. Certs & CAs • Welcome to Public Key Infrastructure (PKI)

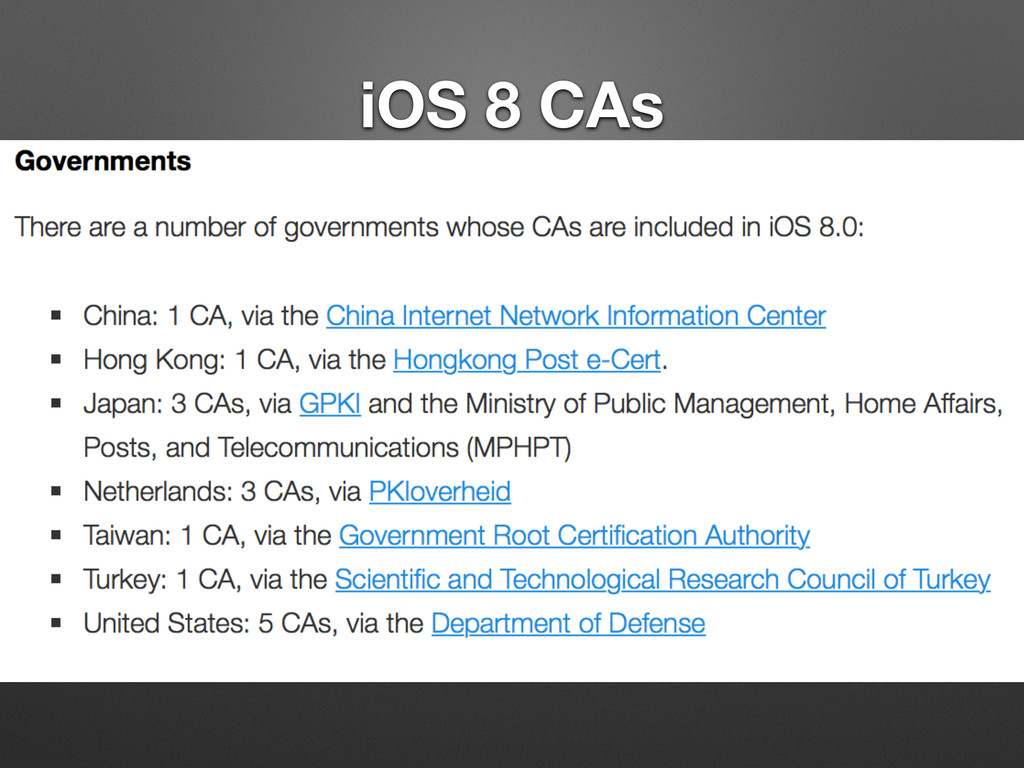
    • for TLS it’s fucked… • IMPLICIT trust of Root & Intermediate certs • No good revocation system • For 50K ANYONE can become a CA • If you have a root or intermediate cert you can spoof any websites cert.. • ROOT CAs hacked Comodo (2011), DigiNotar (2011), VeriSign (2010)
  25. Cool Shit • Moxie Marlinspike loves to break SSL/ TLS

    multiple DEFCON talks on the subject • SSLSniff & SSLStrip • Projects to decentralise CAs (tack.io, convergence.io) • TOR hidden services now have TLS Certs • Imperial Violet (blog) - Google crypto/ network engineer