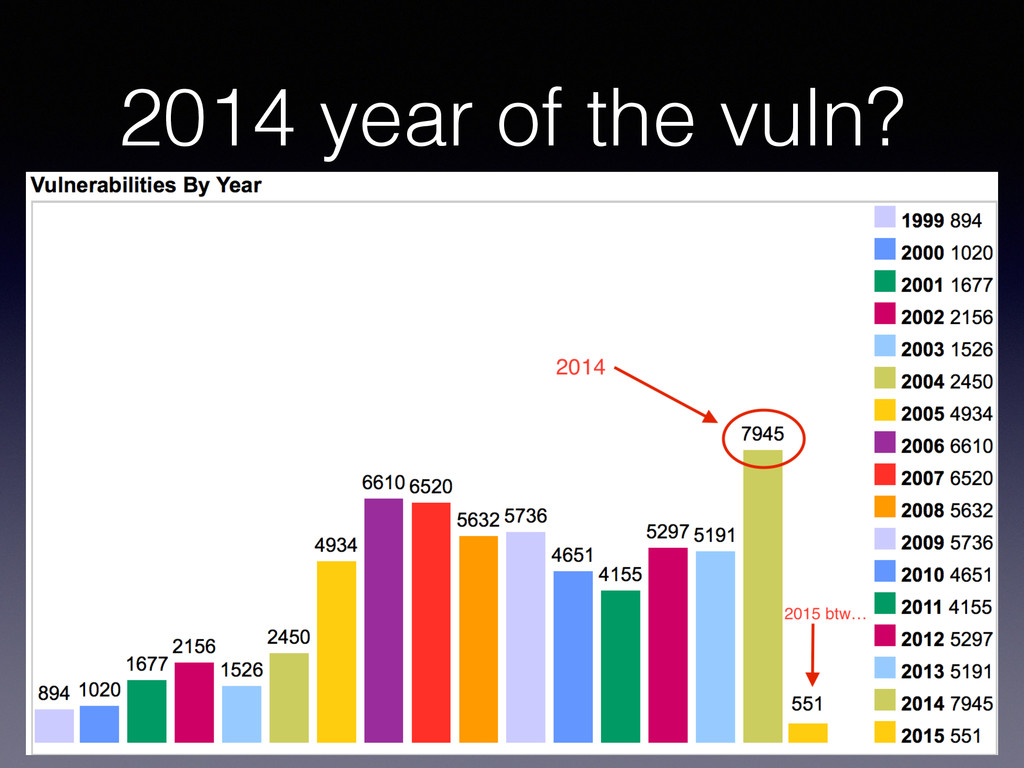
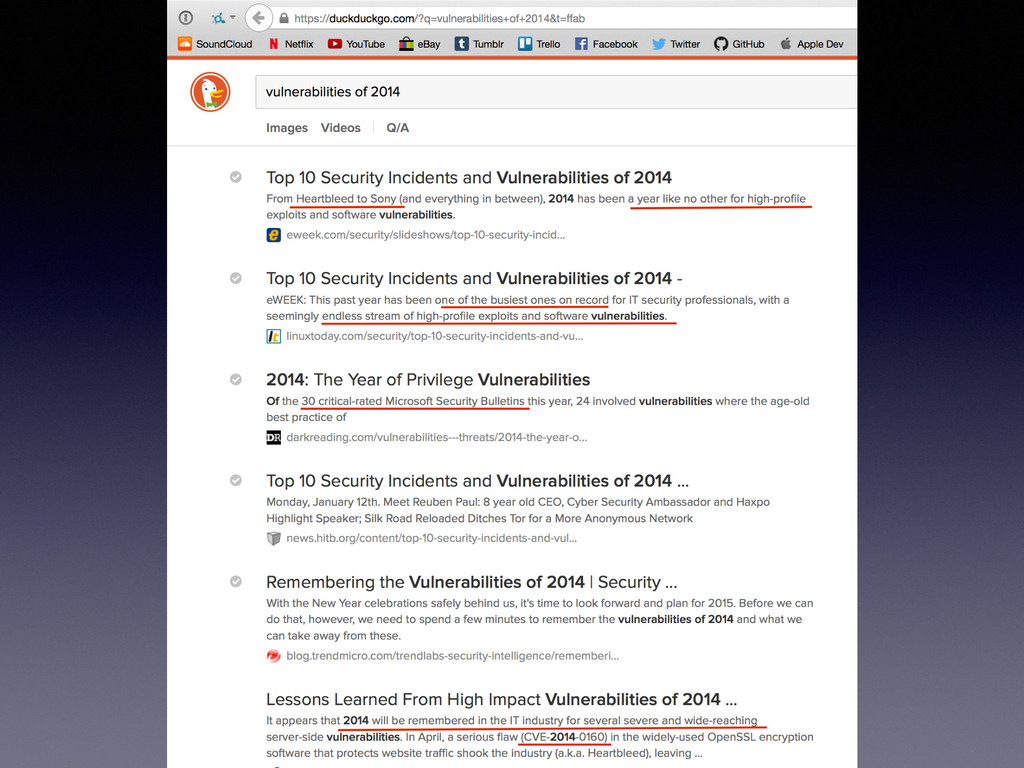
A lookback at some of the interesting infosec events of 2014, overview of 5 topics. POODLE, Regain, BadUSB, Sony Hack & FDE. Given at Abertay Ethical Hacking Society.
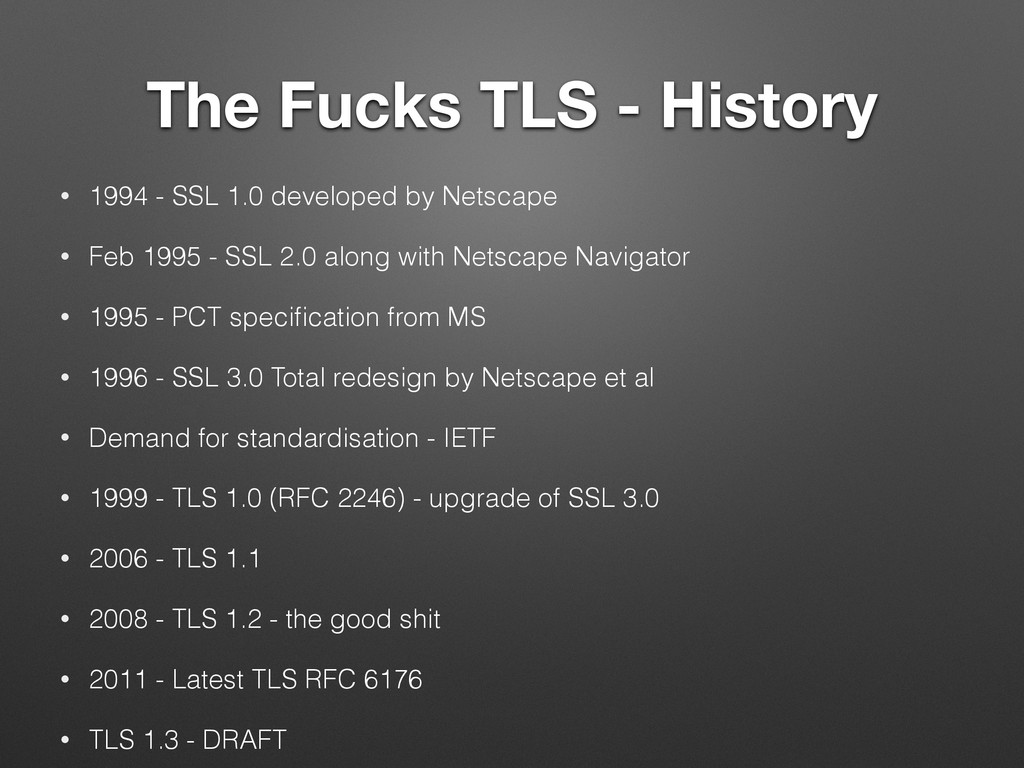
developed by Netscape • Feb 1995 - SSL 2.0 along with Netscape Navigator • 1995 - PCT specification from MS • 1996 - SSL 3.0 Total redesign by Netscape et al • Demand for standardisation - IETF • 1999 - TLS 1.0 (RFC 2246) - upgrade of SSL 3.0 • 2006 - TLS 1.1 • 2008 - TLS 1.2 - the good shit • 2011 - Latest TLS RFC 6176 • TLS 1.3 - DRAFT
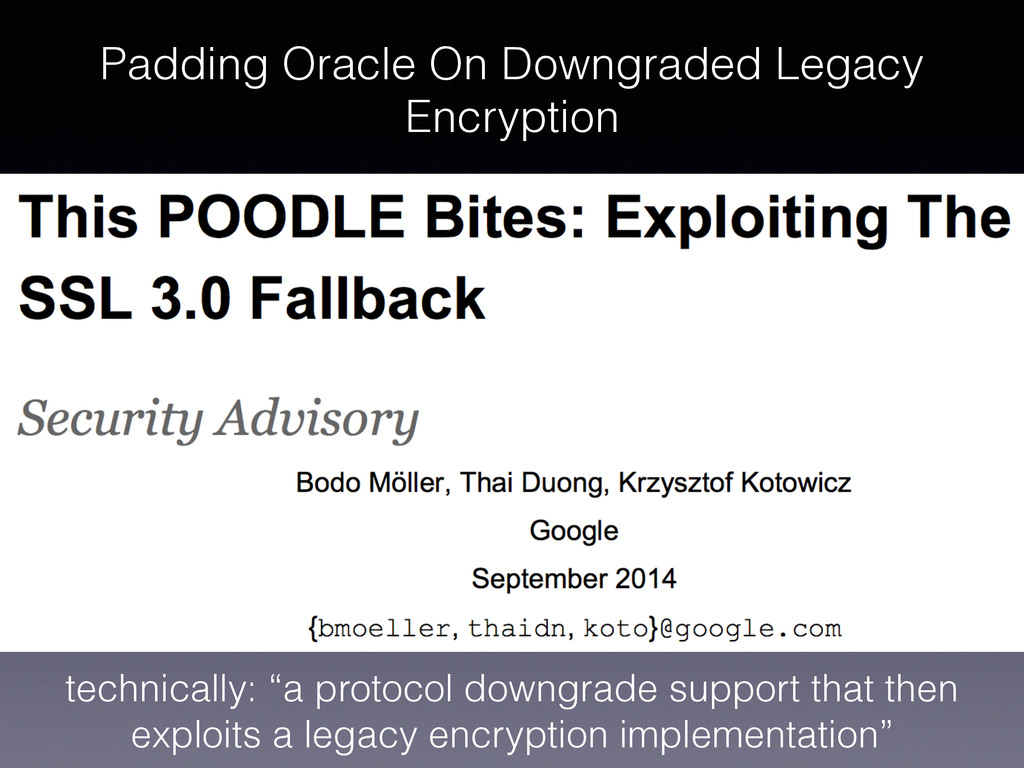
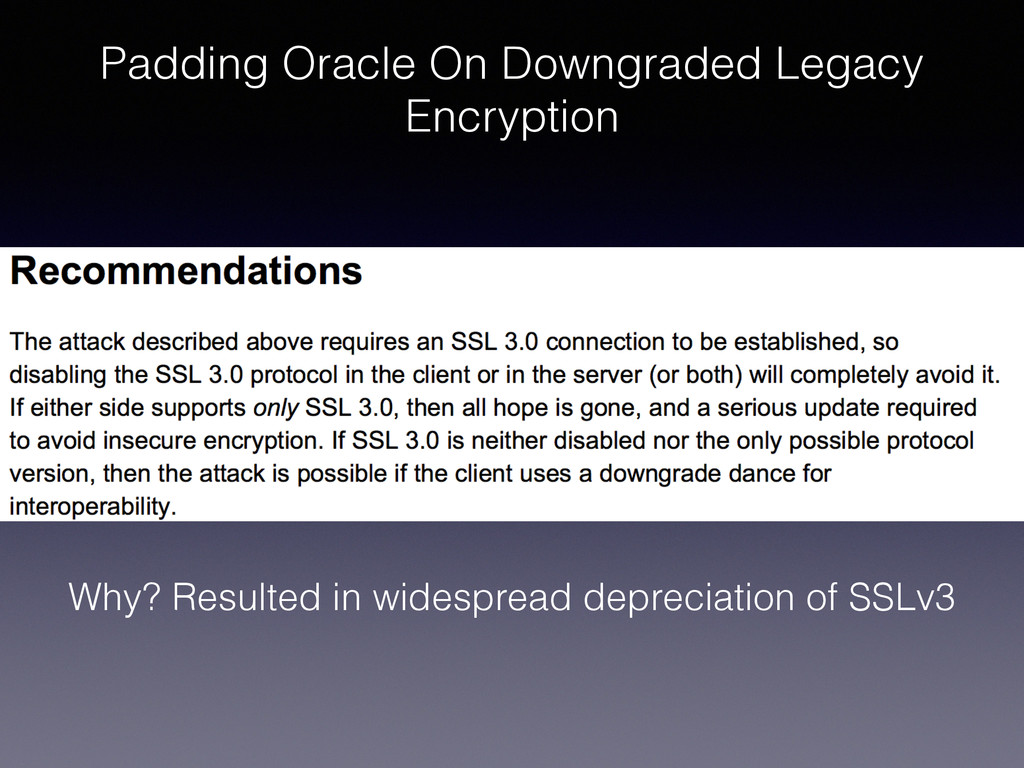
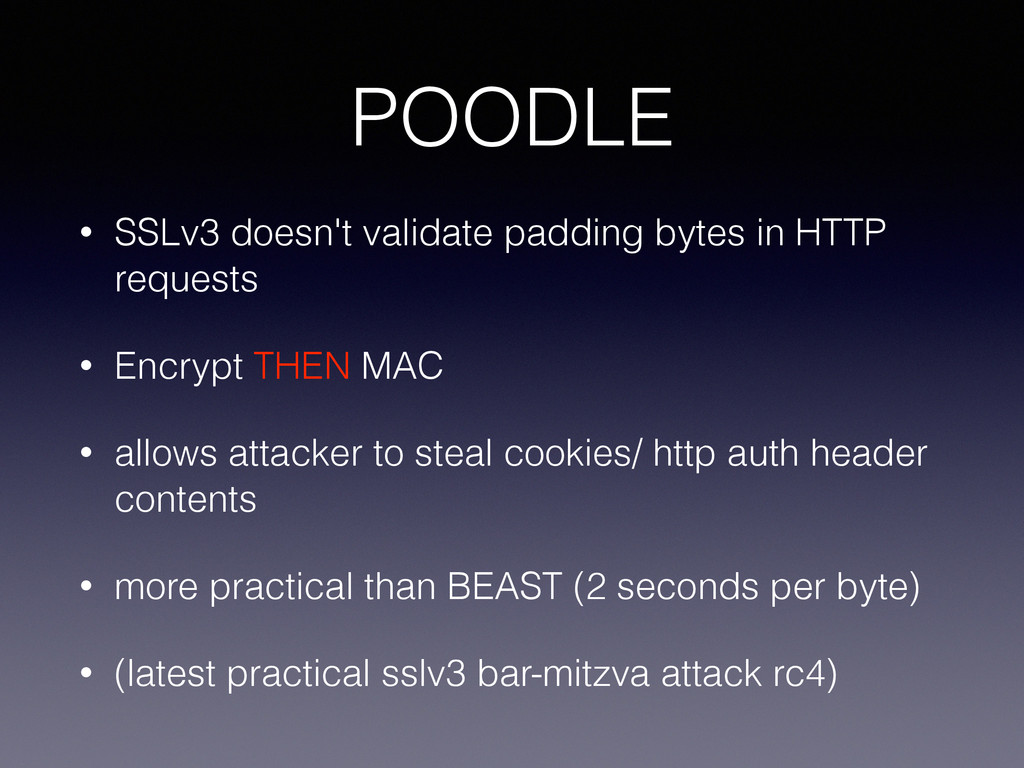
• Encrypt THEN MAC • allows attacker to steal cookies/ http auth header contents • more practical than BEAST (2 seconds per byte) • (latest practical sslv3 bar-mitzva attack rc4)
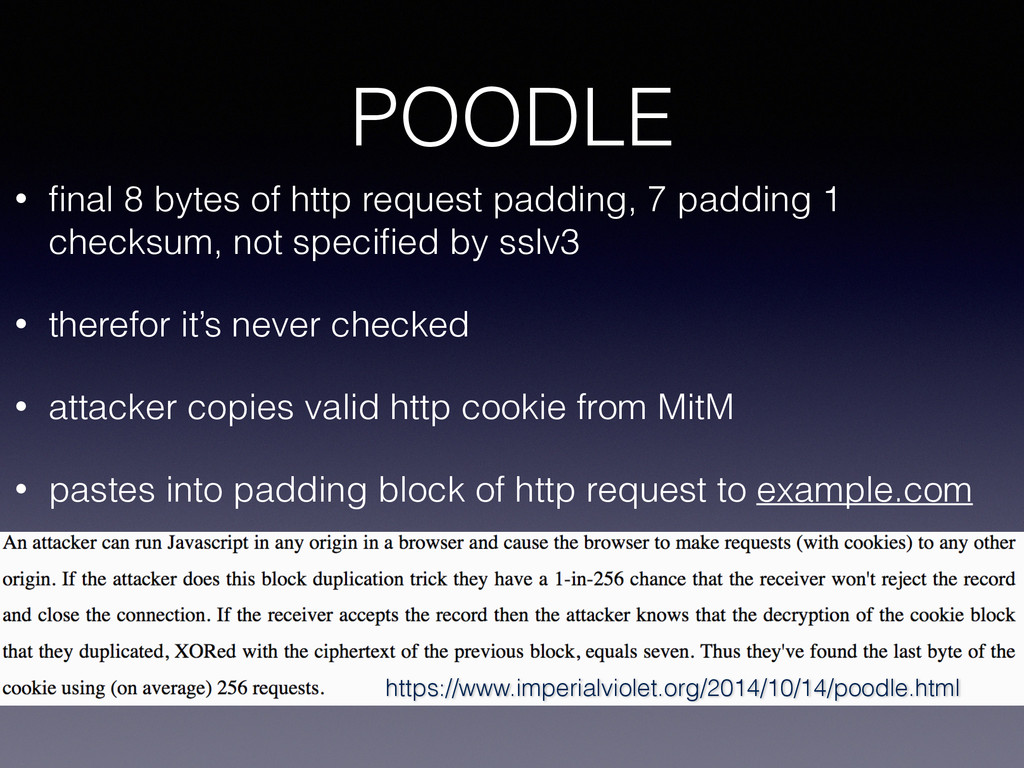
padding 1 checksum, not specified by sslv3 • therefor it’s never checked • attacker copies valid http cookie from MitM • pastes into padding block of http request to example.com https://www.imperialviolet.org/2014/10/14/poodle.html
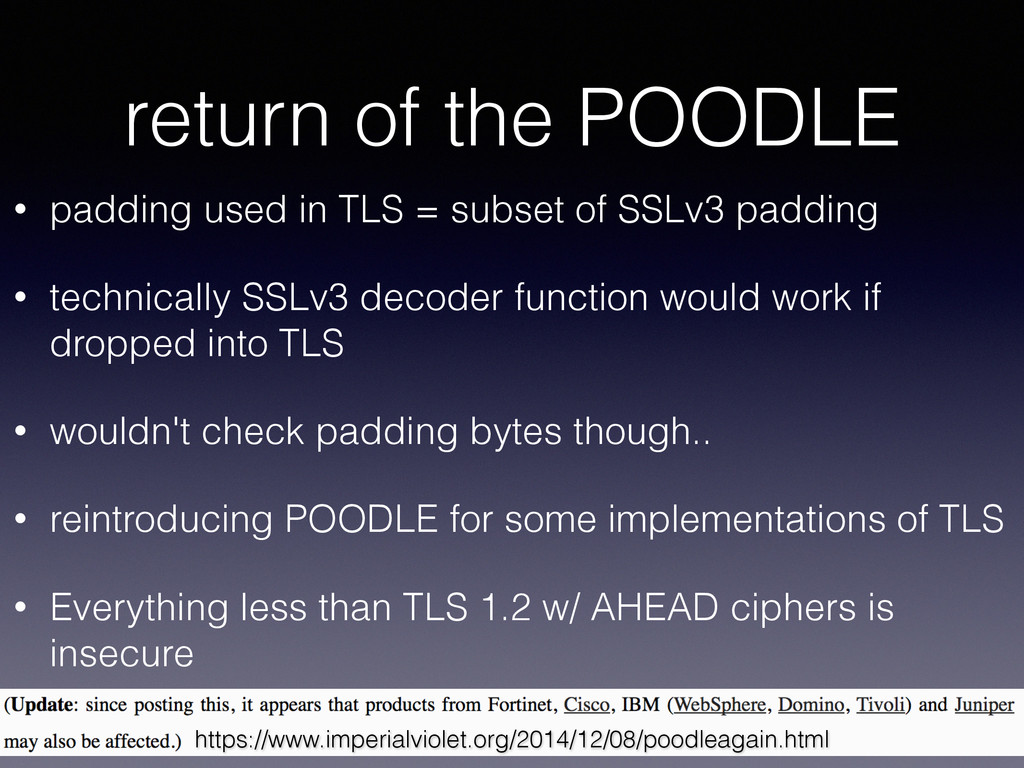
subset of SSLv3 padding • technically SSLv3 decoder function would work if dropped into TLS • wouldn't check padding bytes though.. • reintroducing POODLE for some implementations of TLS • Everything less than TLS 1.2 w/ AHEAD ciphers is insecure https://www.imperialviolet.org/2014/12/08/poodleagain.html
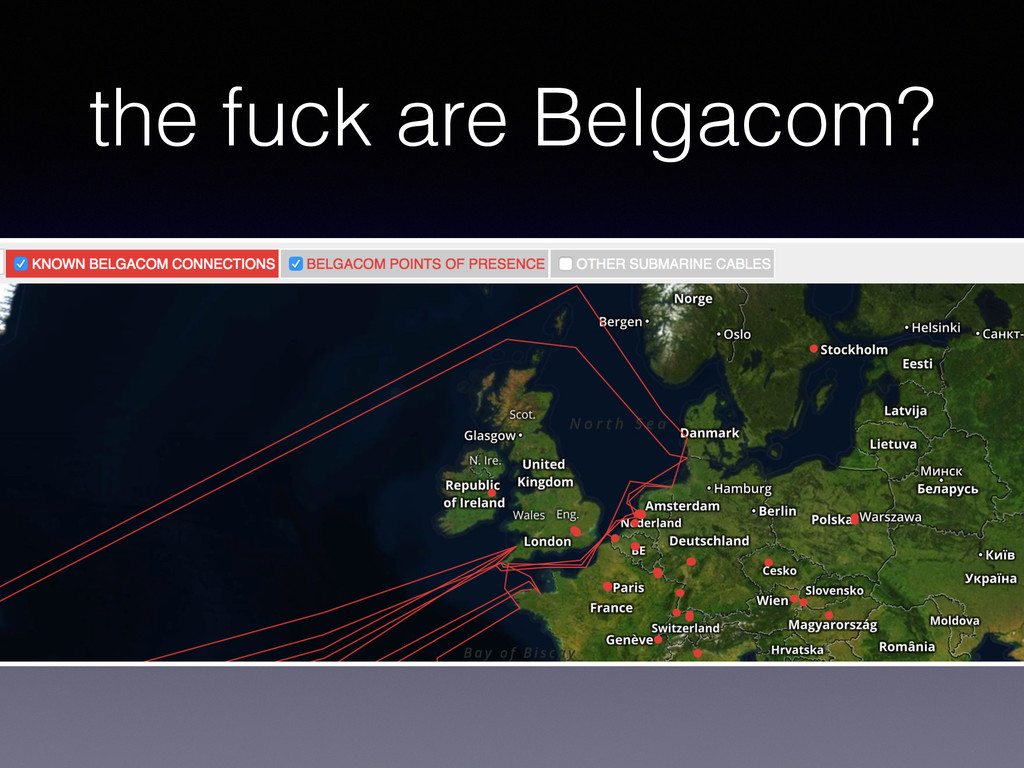
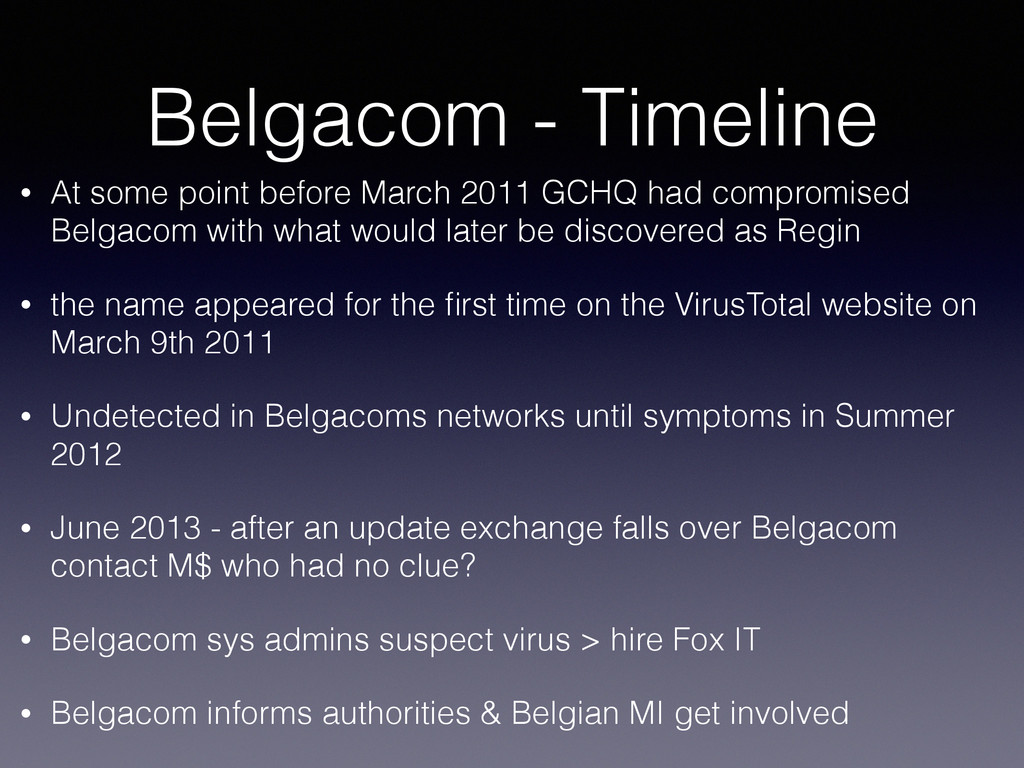
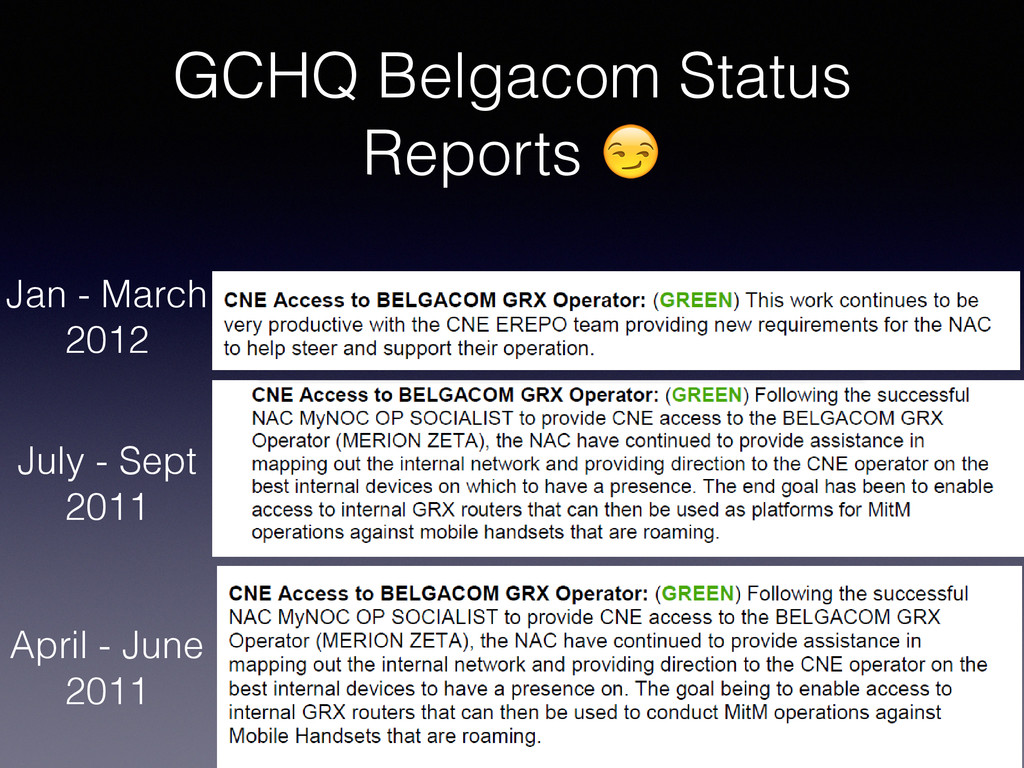
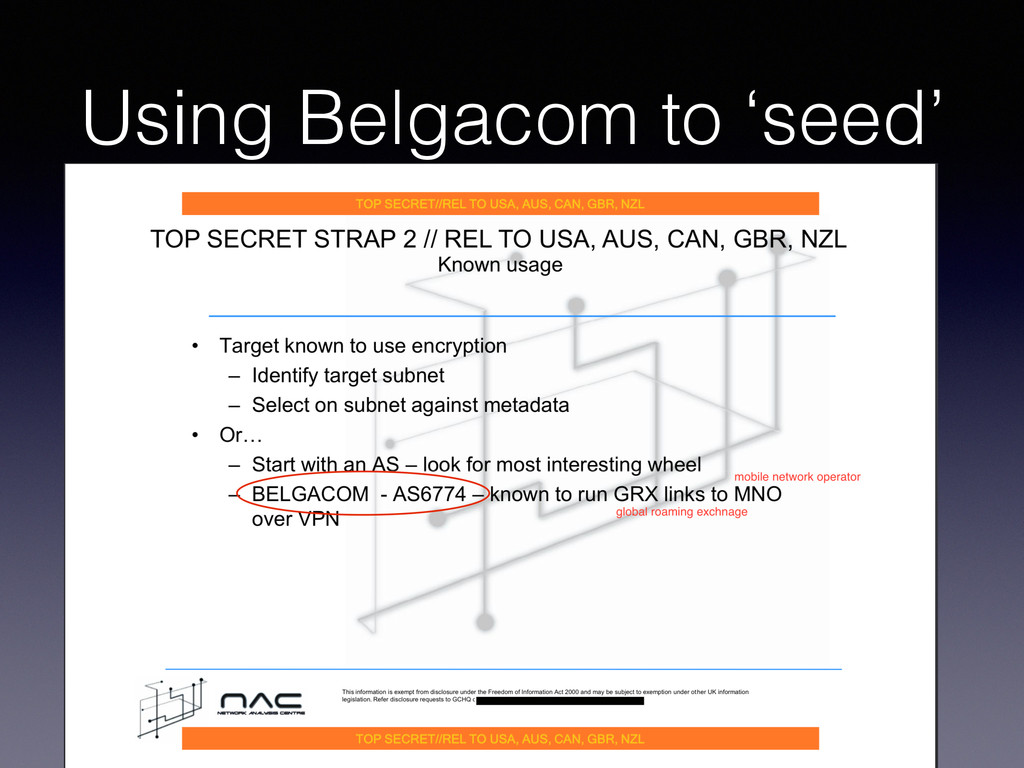
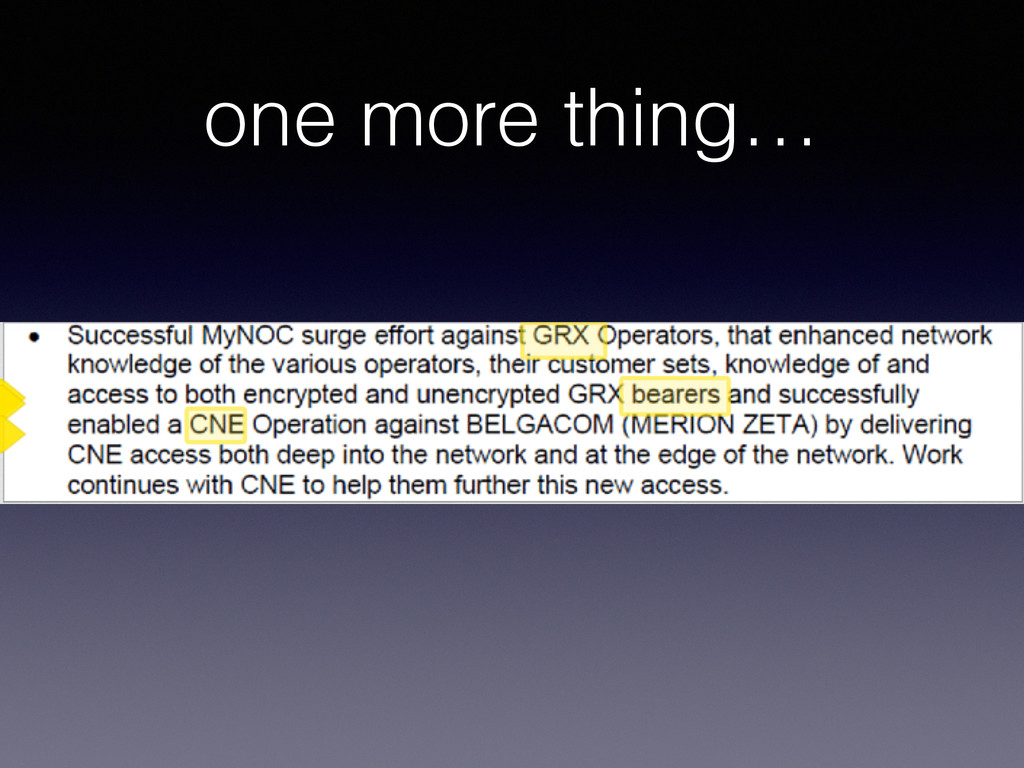
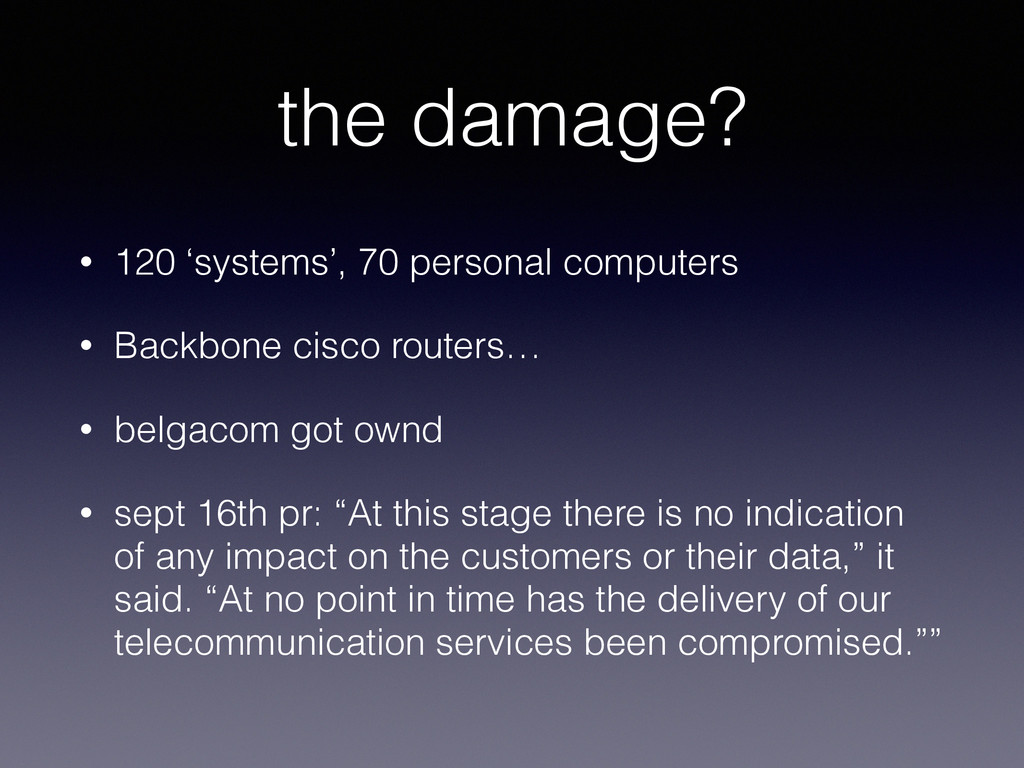
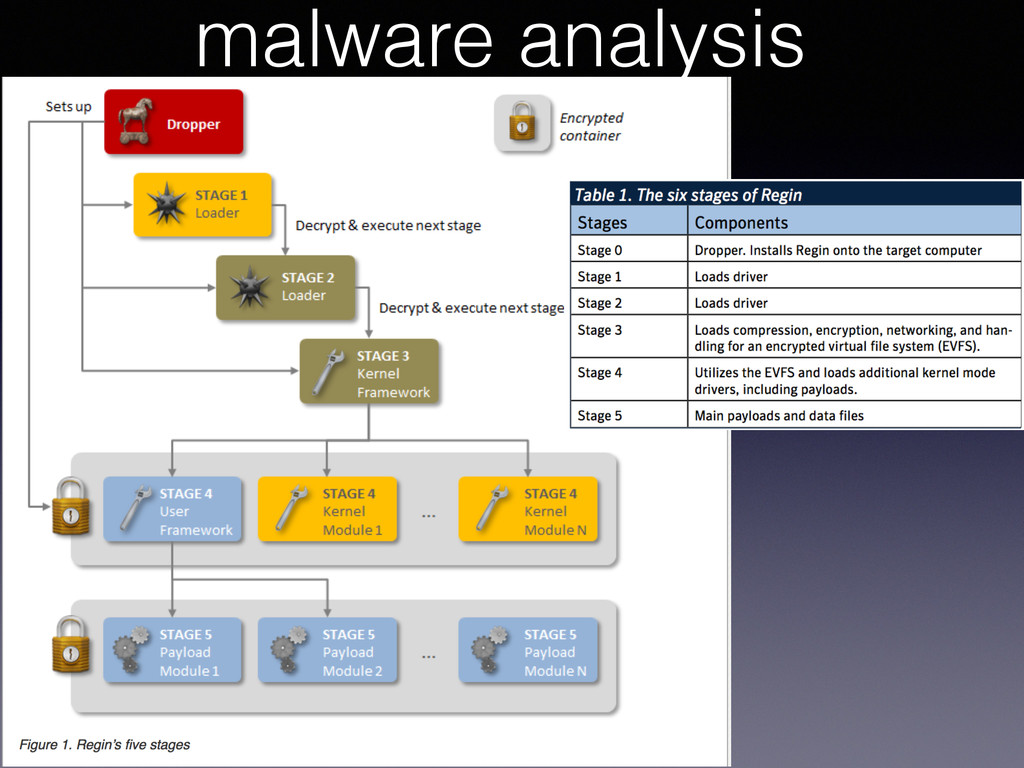
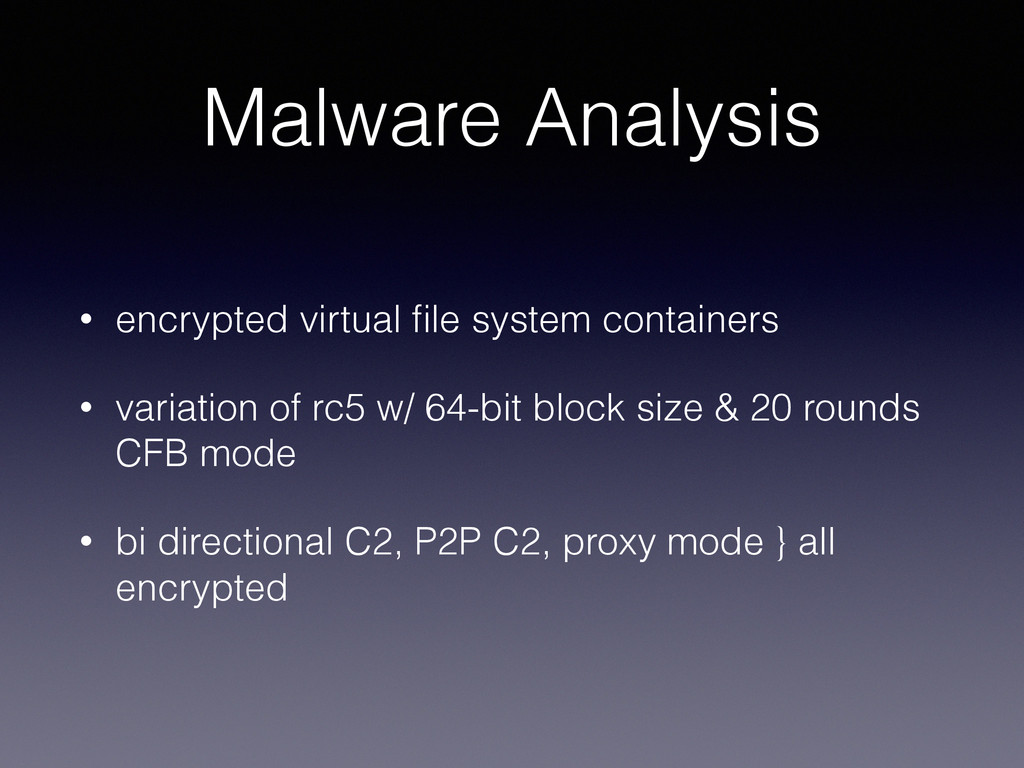
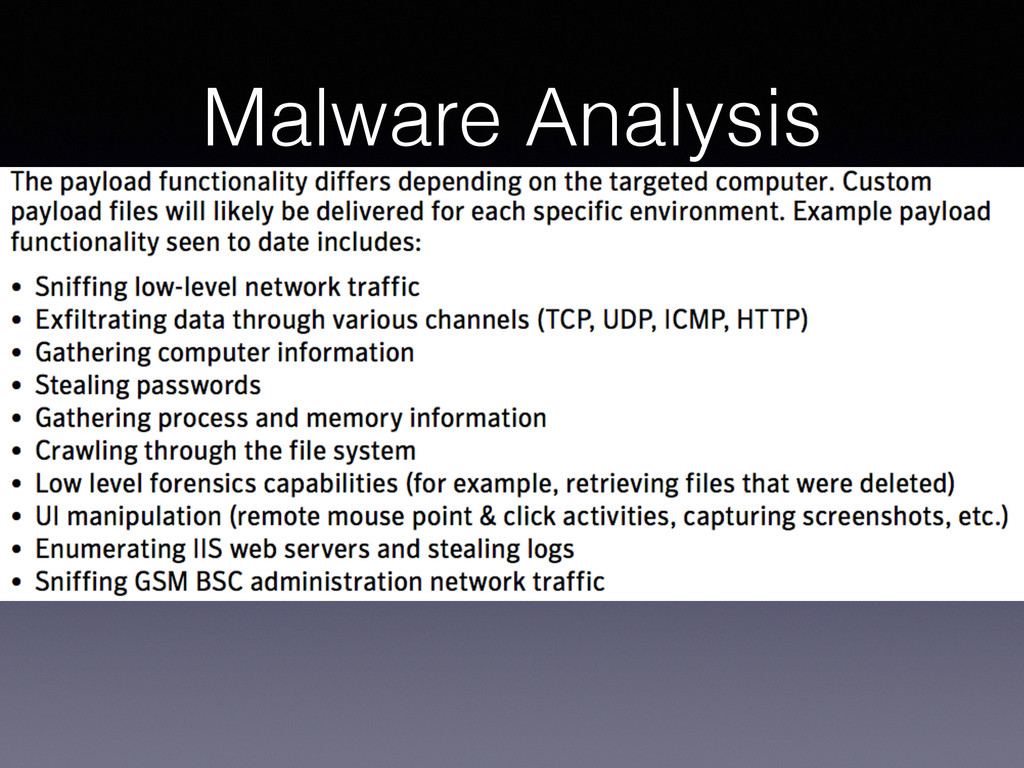
GCHQ had compromised Belgacom with what would later be discovered as Regin • the name appeared for the first time on the VirusTotal website on March 9th 2011 • Undetected in Belgacoms networks until symptoms in Summer 2012 • June 2013 - after an update exchange falls over Belgacom contact M$ who had no clue? • Belgacom sys admins suspect virus > hire Fox IT • Belgacom informs authorities & Belgian MI get involved
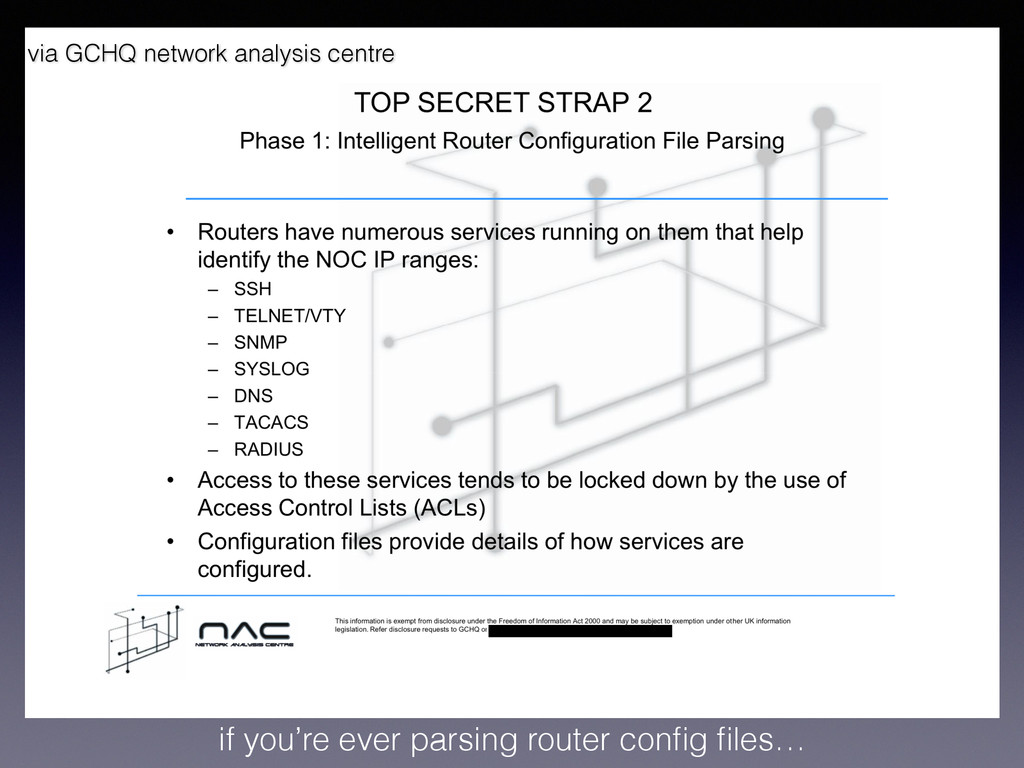
cisco routers… • belgacom got ownd • sept 16th pr: “At this stage there is no indication of any impact on the customers or their data,” it said. “At no point in time has the delivery of our telecommunication services been compromised.””
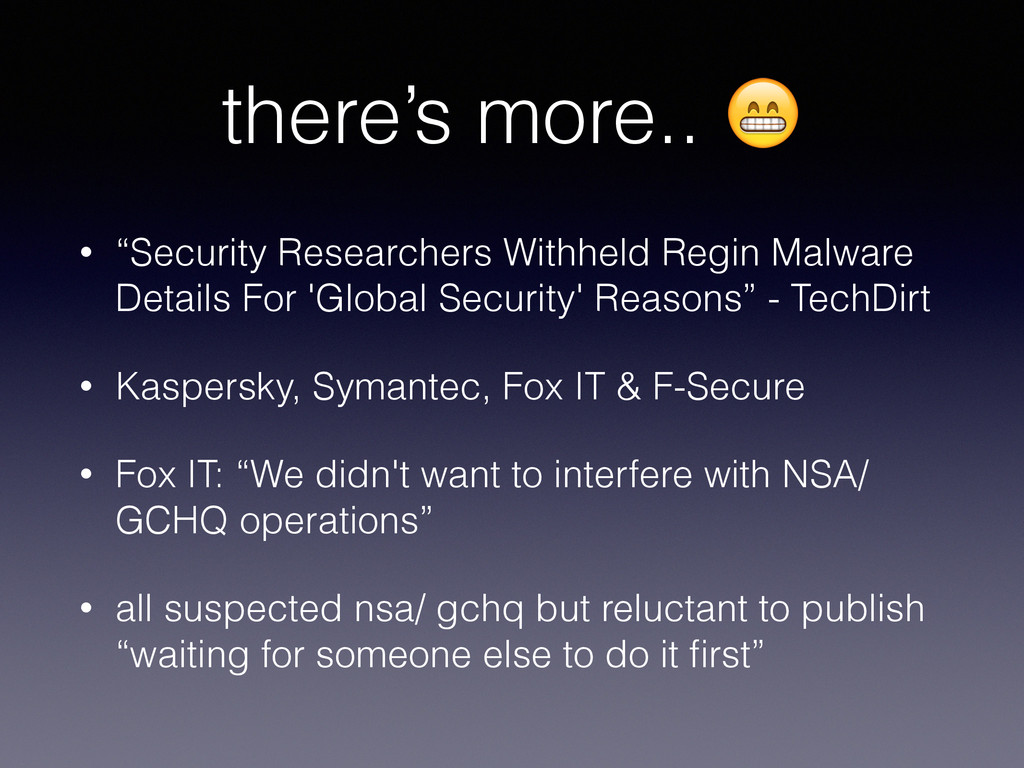
'Global Security' Reasons” - TechDirt • Kaspersky, Symantec, Fox IT & F-Secure • Fox IT: “We didn't want to interfere with NSA/ GCHQ operations” • all suspected nsa/ gchq but reluctant to publish “waiting for someone else to do it first”
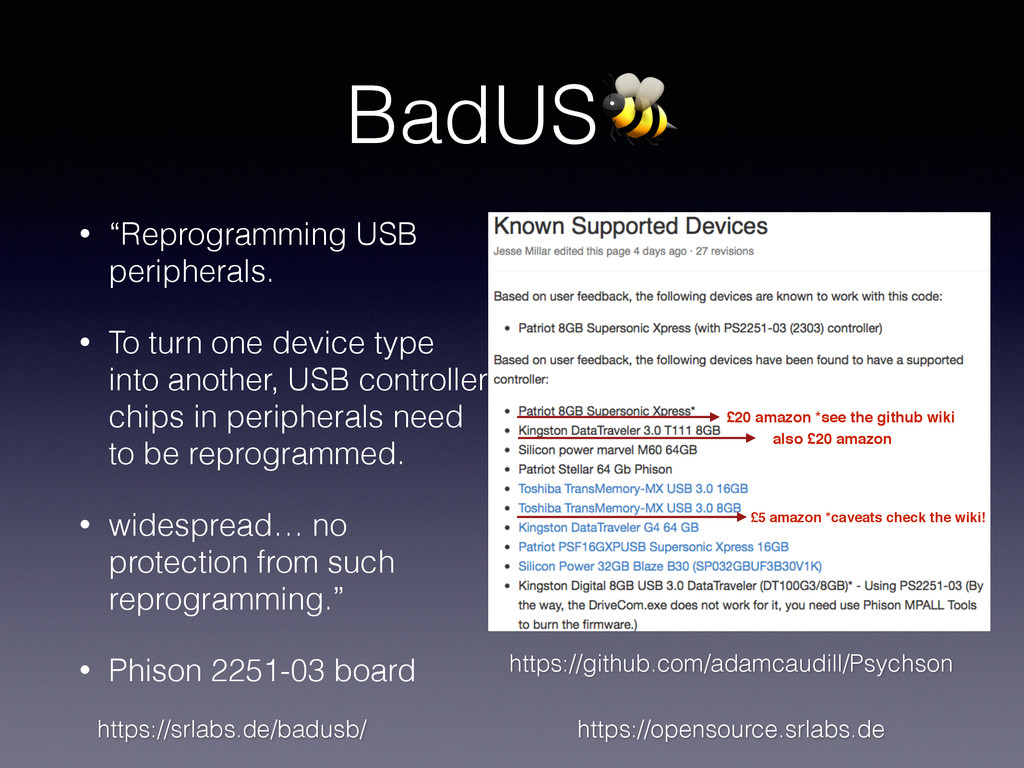
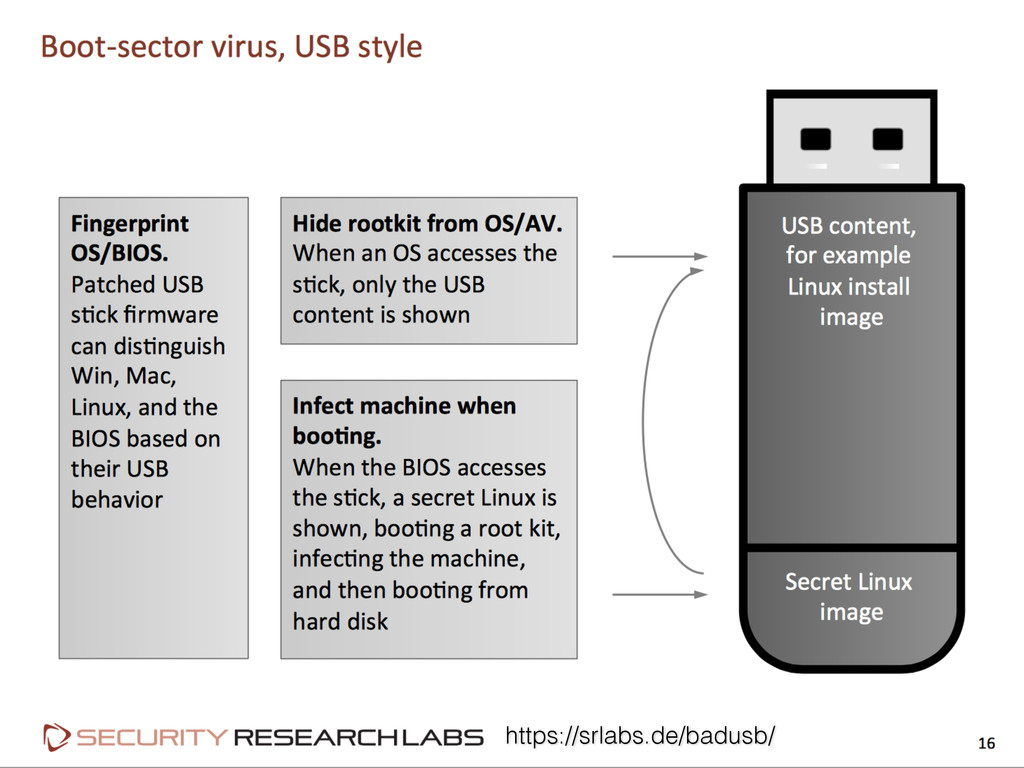
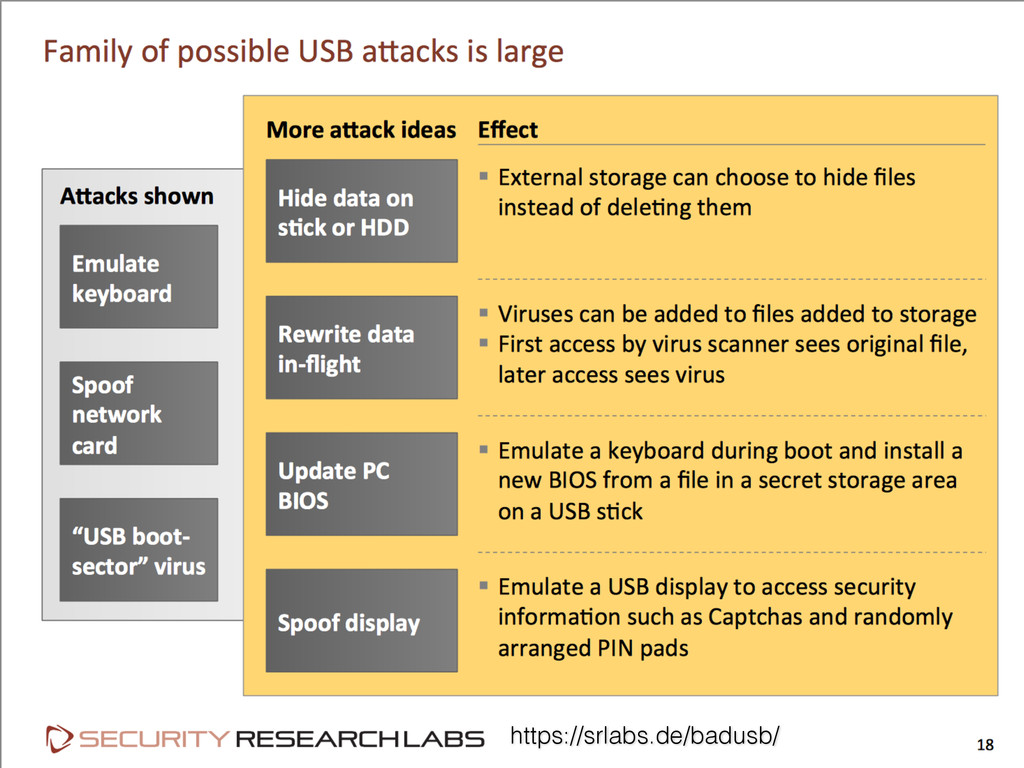
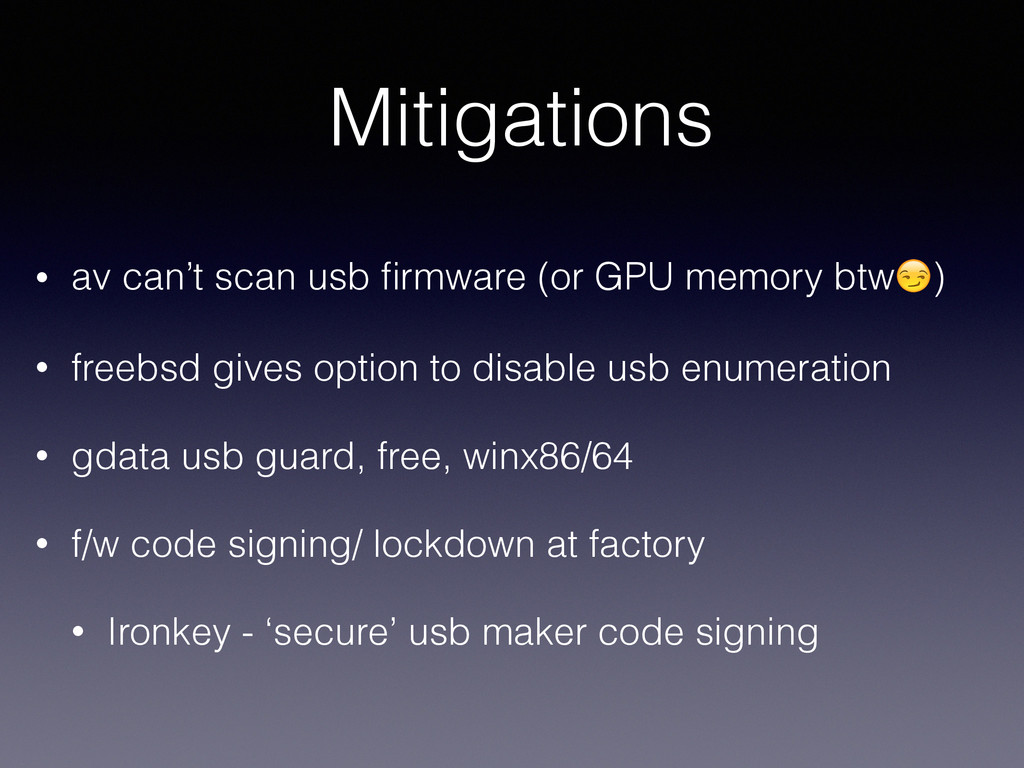
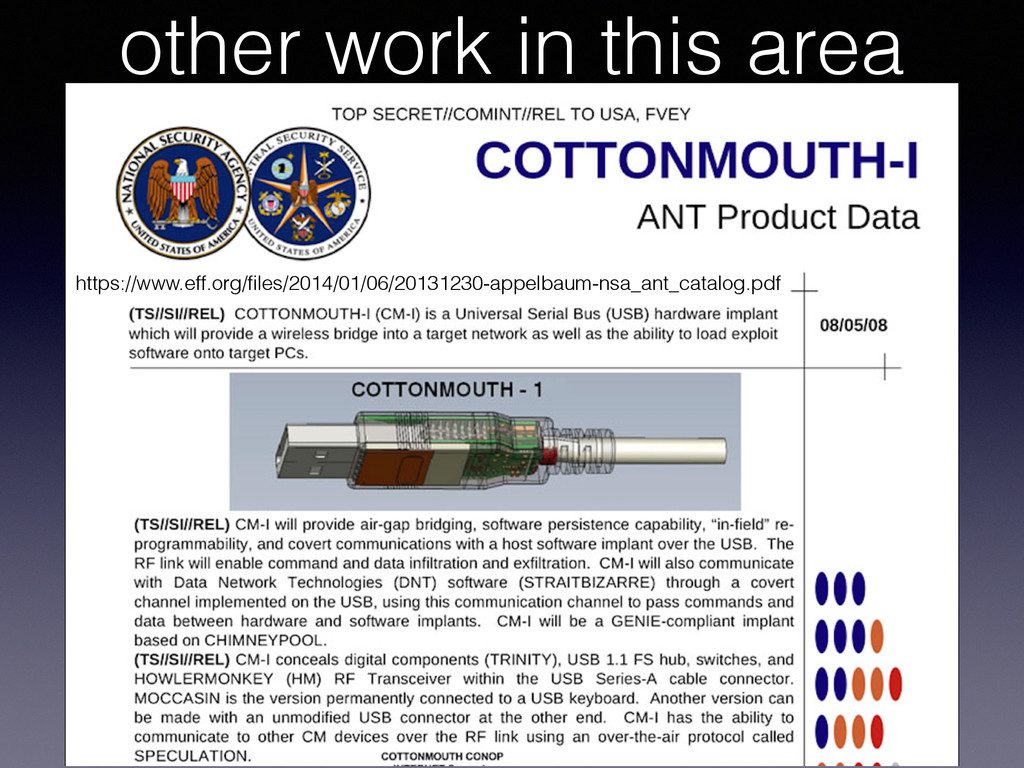
into another, USB controller chips in peripherals need to be reprogrammed. • widespread… no protection from such reprogramming.” • Phison 2251-03 board BadUS https://srlabs.de/badusb/ https://github.com/adamcaudill/Psychson also £20 amazon £20 amazon *see the github wiki £5 amazon *caveats check the wiki! https://opensource.srlabs.de
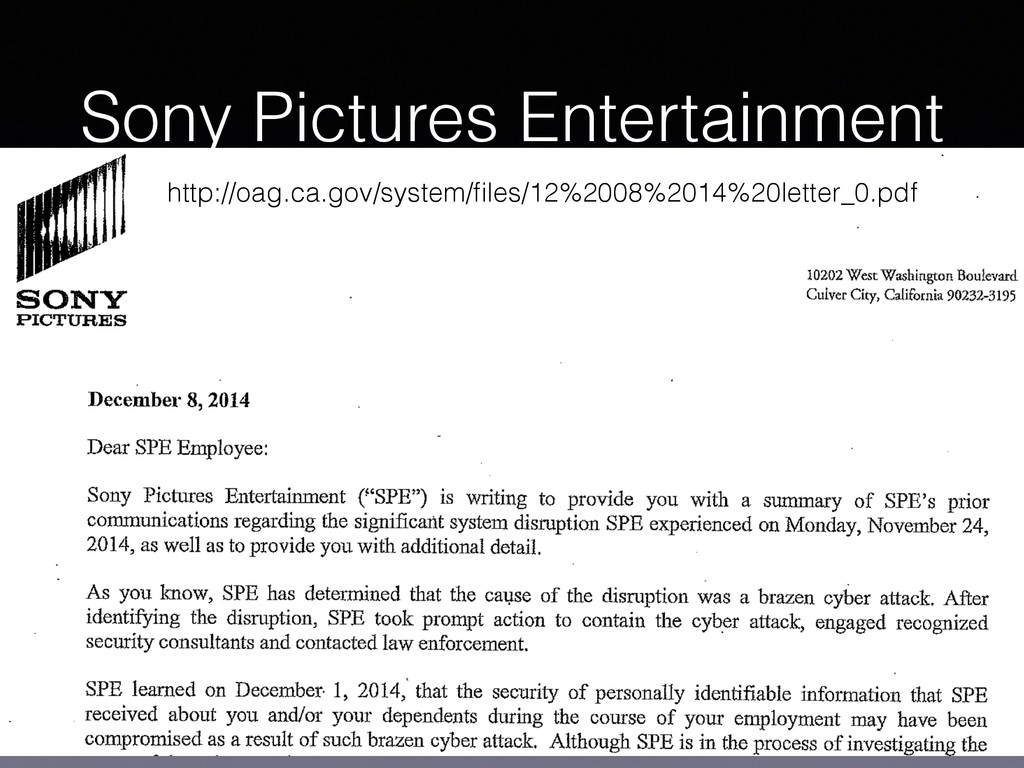
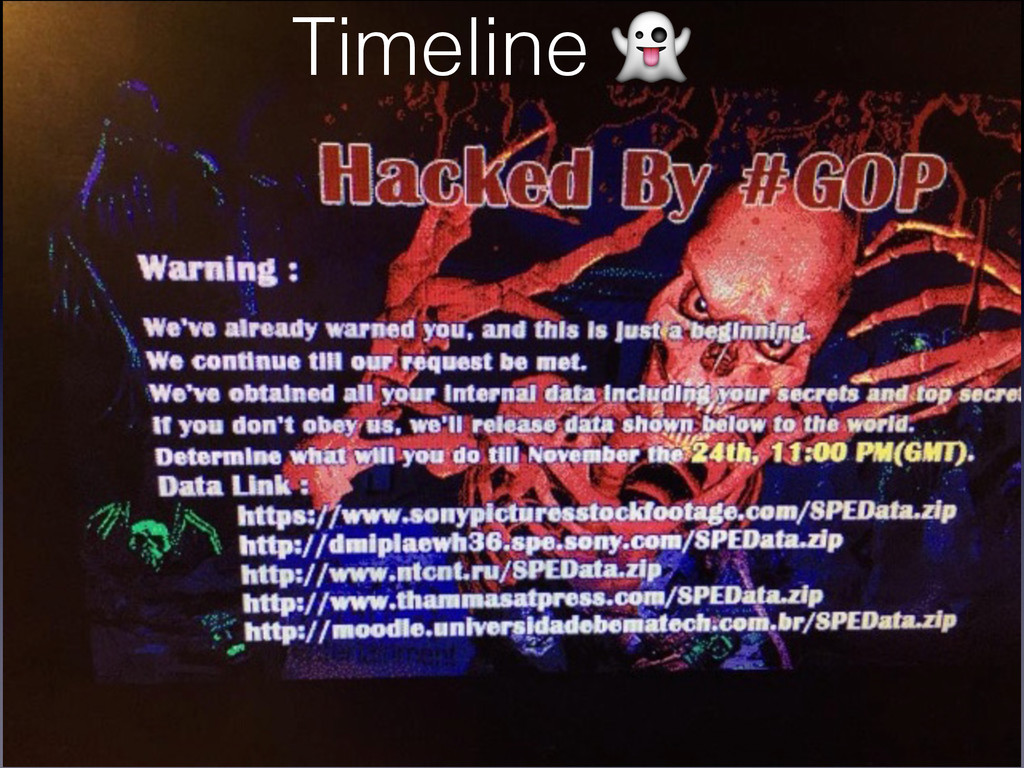
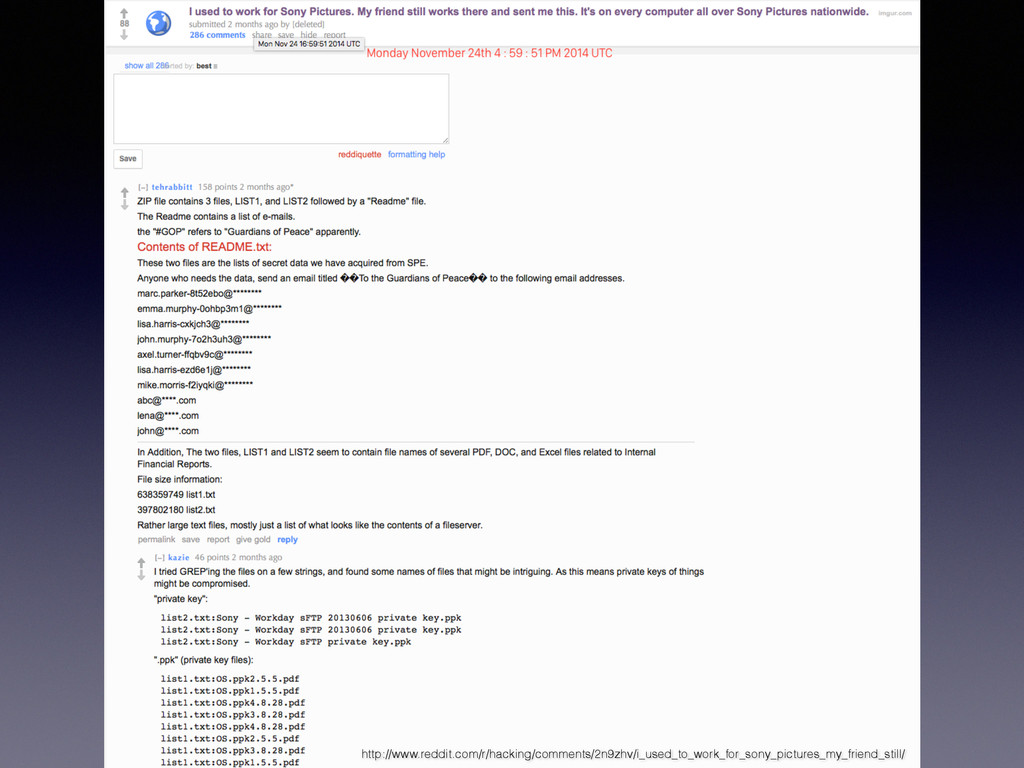
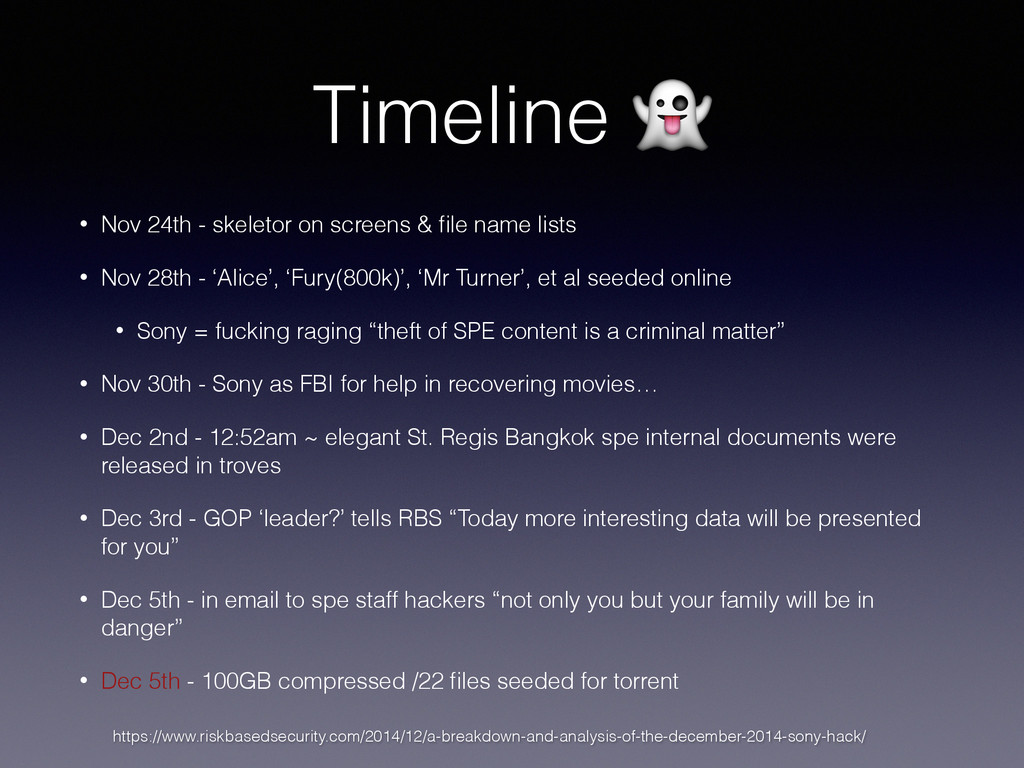
name lists • Nov 28th - ‘Alice’, ‘Fury(800k)’, ‘Mr Turner’, et al seeded online • Sony = fucking raging “theft of SPE content is a criminal matter” • Nov 30th - Sony as FBI for help in recovering movies…
name lists • Nov 28th - ‘Alice’, ‘Fury(800k)’, ‘Mr Turner’, et al seeded online • Sony = fucking raging “theft of SPE content is a criminal matter” • Nov 30th - Sony as FBI for help in recovering movies… • Dec 2nd - 12:52am* ~ elegant St. Regis Bangkok spe internal documents were released in troves https://www.riskbasedsecurity.com/2014/12/a-breakdown-and-analysis-of-the-december-2014-sony-hack/ *http://www.bloomberg.com/news/2014-12-07/sony-s-darkseoul-breach-stretched-from-thai-hotel-to-hollywood.html
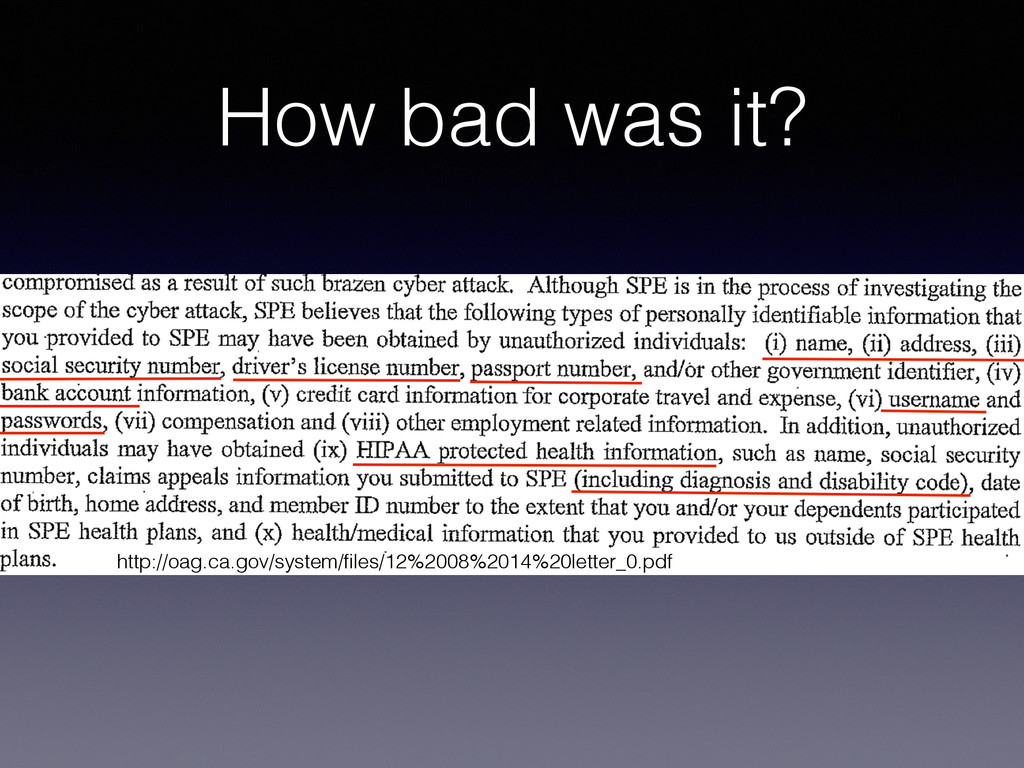
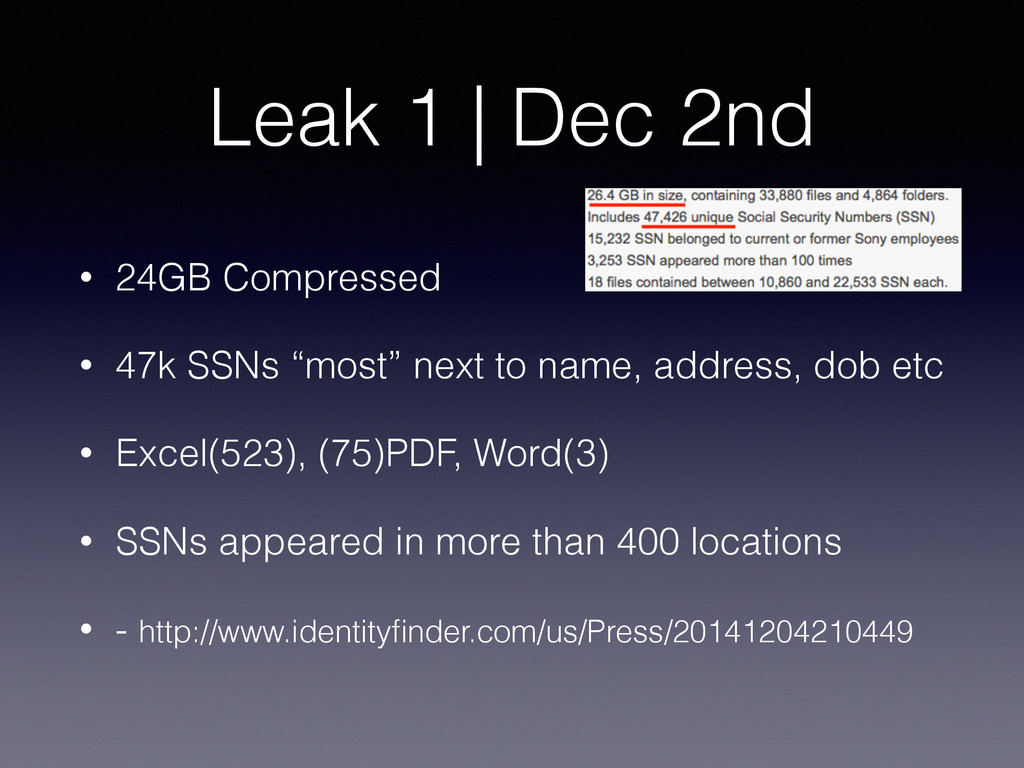
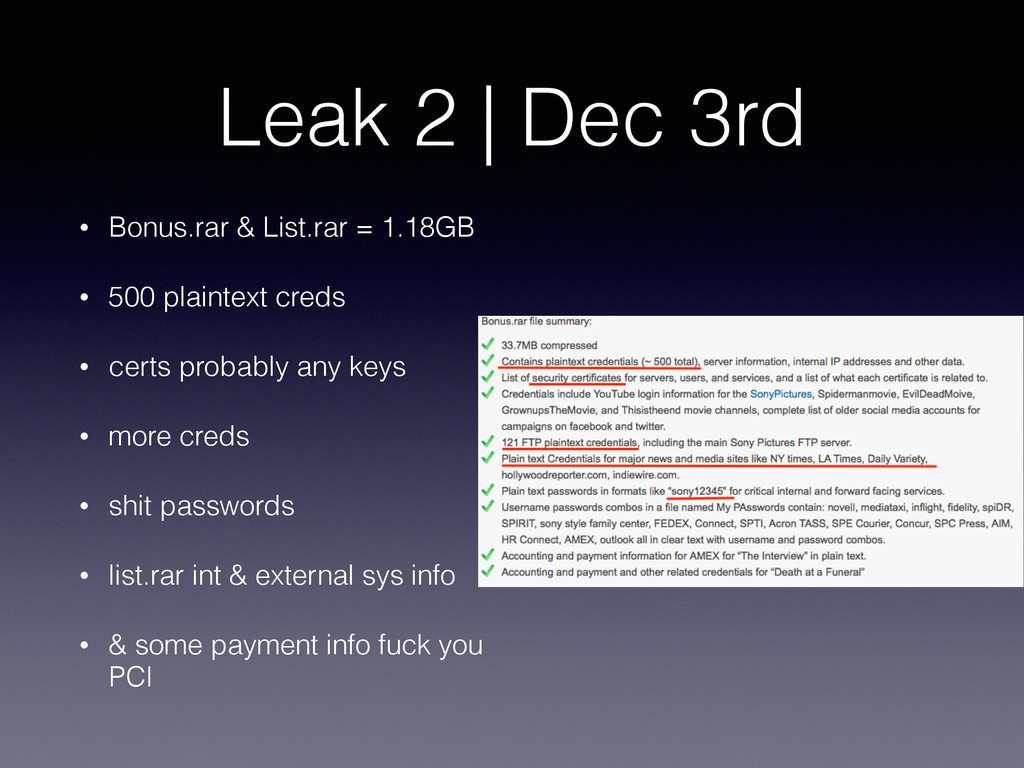
SSNs “most” next to name, address, dob etc • Excel(523), (75)PDF, Word(3) • SSNs appeared in more than 400 locations • - http://www.identityfinder.com/us/Press/20141204210449
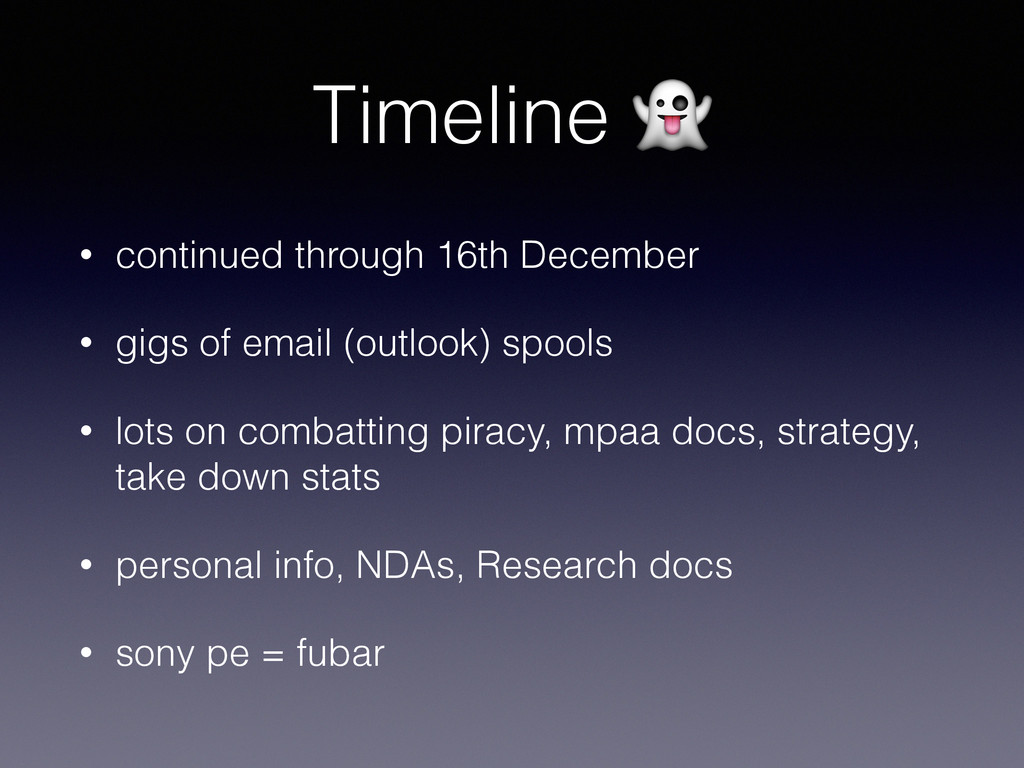
companies that “destructive” cyber attack has occurred • “The report said the malware overrides all data on hard drives of computers, including the master boot record, which prevents them from booting up” • Don’t name victim SOP http://www.reuters.com/article/2014/12/02/us-sony-cybersecurity-malware-idUSKCN0JF3FE20141202
name lists • Nov 28th - ‘Alice’, ‘Fury(800k)’, ‘Mr Turner’, et al seeded online • Sony = fucking raging “theft of SPE content is a criminal matter” • Nov 30th - Sony as FBI for help in recovering movies… • Dec 2nd - 12:52am ~ elegant St. Regis Bangkok spe internal documents were released in troves • Dec 3rd - GOP ‘leader?’ tells RBS “Today more interesting data will be presented for you” https://www.riskbasedsecurity.com/2014/12/a-breakdown-and-analysis-of-the-december-2014-sony-hack/
name lists • Nov 28th - ‘Alice’, ‘Fury(800k)’, ‘Mr Turner’, et al seeded online • Sony = fucking raging “theft of SPE content is a criminal matter” • Nov 30th - Sony as FBI for help in recovering movies… • Dec 2nd - 12:52am ~ elegant St. Regis Bangkok spe internal documents were released in troves • Dec 3rd - GOP ‘leader?’ tells RBS “Today more interesting data will be presented for you” • Dec 5th - in email to spe staff hackers “not only you but your family will be in danger” https://www.riskbasedsecurity.com/2014/12/a-breakdown-and-analysis-of-the-december-2014-sony-hack/
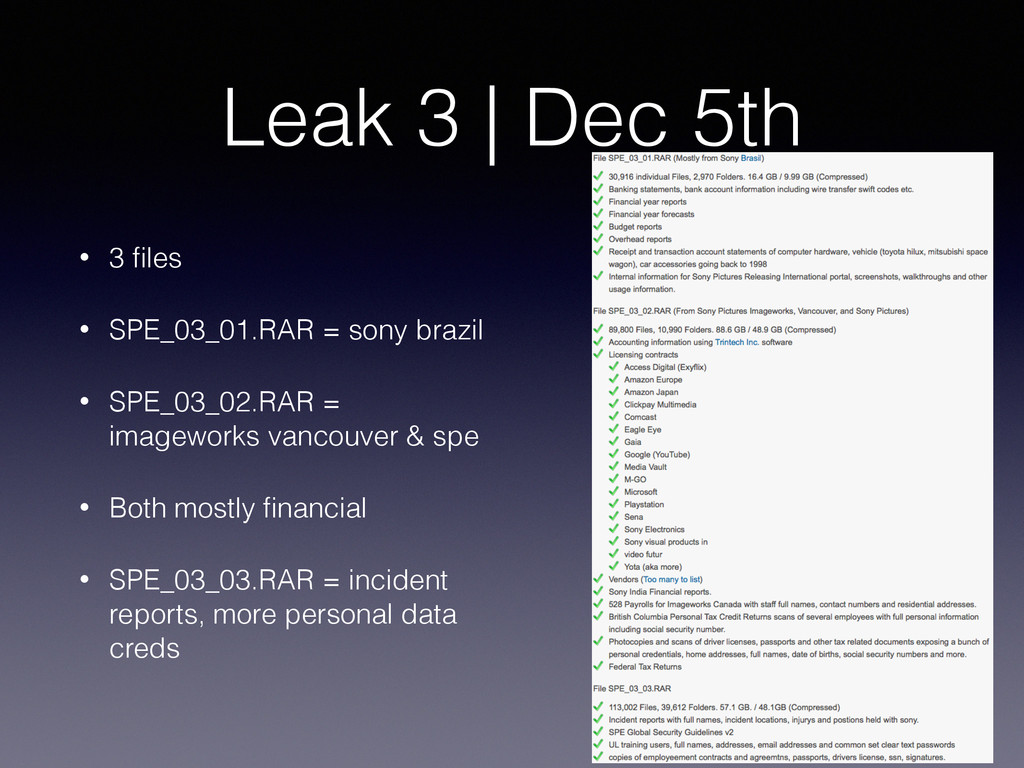
name lists • Nov 28th - ‘Alice’, ‘Fury(800k)’, ‘Mr Turner’, et al seeded online • Sony = fucking raging “theft of SPE content is a criminal matter” • Nov 30th - Sony as FBI for help in recovering movies… • Dec 2nd - 12:52am ~ elegant St. Regis Bangkok spe internal documents were released in troves • Dec 3rd - GOP ‘leader?’ tells RBS “Today more interesting data will be presented for you” • Dec 5th - in email to spe staff hackers “not only you but your family will be in danger” • Dec 5th - 100GB compressed /22 files seeded for torrent https://www.riskbasedsecurity.com/2014/12/a-breakdown-and-analysis-of-the-december-2014-sony-hack/
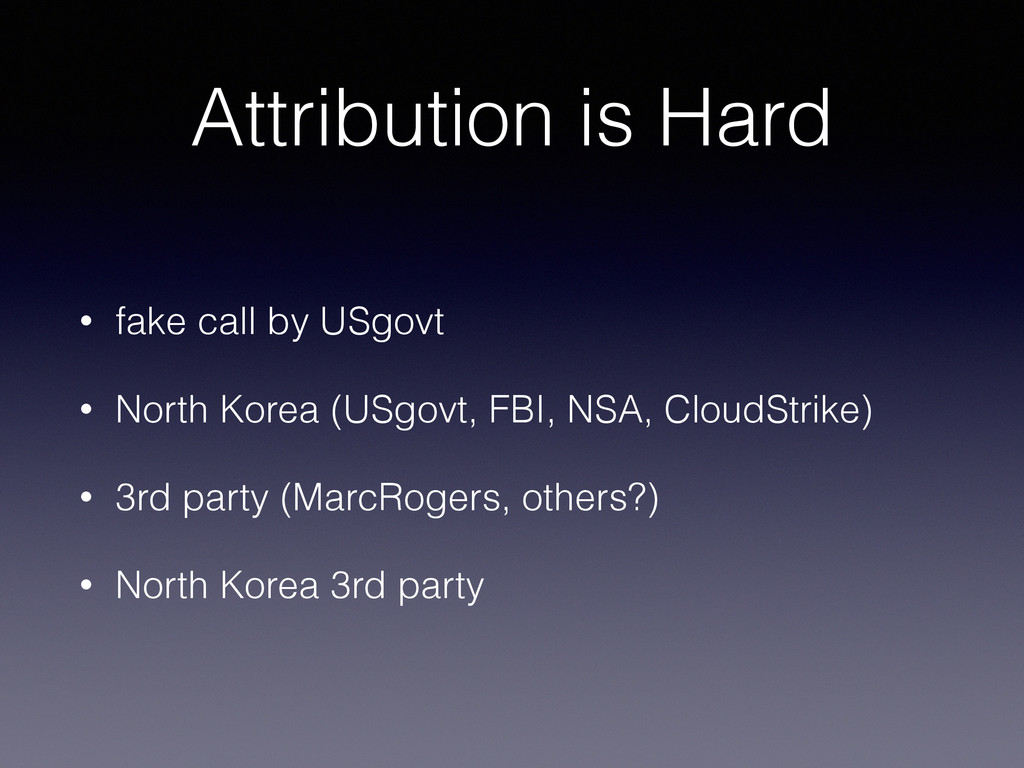
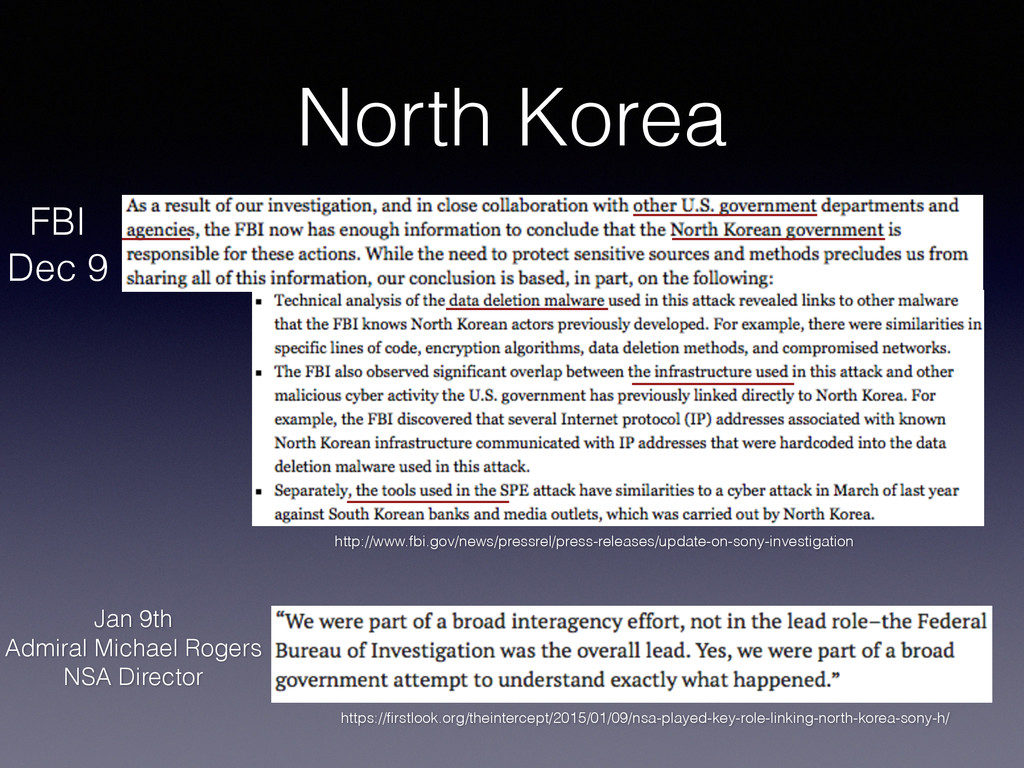
NSA Director https://firstlook.org/theintercept/2015/01/09/nsa-played-key-role-linking-north-korea-sony-h/ http://www.fbi.gov/news/pressrel/press-releases/update-on-sony-investigation


 0xmikey
 takonda
 mohab1
 nttcom
 kentarofujii
 raspython3
 usanchuu
 carta_engineering
 sh_fk2
 prog893
 akitoshiga
 terapyon
 akhino
 tamaranovitovic
 lara
 tammyeverts
 axbom
 signer
 konakalab
 thekraken
 tenderlove
 danielanewman
 jct