Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Catching_Low_Hanging_Fruits.pdf
Search
Alfred
June 29, 2018
21
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Catching_Low_Hanging_Fruits.pdf
Johanna on OWASP-ZAP during Amsterdam secure software development meetup 22-6-2018
Alfred
June 29, 2018
More Decks by Alfred
See All by Alfred
Henry Been - Secure Deployments - Keeping your application secrets private
afoltin
0
44
Compliance_and_Agile.pdf
afoltin
0
12
Featured
See All Featured
Lessons Learnt from Crawling 1000+ Websites
charlesmeaden
PRO
1
1.6k
SEO in 2025: How to Prepare for the Future of Search
ipullrank
3
3.9k
[Rails World 2026] Durable orchestration on Rails: from continuation to workflow
palkan
1
750
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
490
Building Flexible Design Systems
yeseniaperezcruz
330
41k
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
69
67k
Evolution of real-time – Irina Nazarova, EuRuKo, 2024
irinanazarova
9
1.6k
Building AI with AI
inesmontani
PRO
1
1.3k
Visual Storytelling: How to be a Superhuman Communicator
reverentgeek
2
710
How To Speak Unicorn (iThemes Webinar)
marktimemedia
1
600
Creating an realtime collaboration tool: Agile Flush - .NET Oxford
marcduiker
35
2.6k
Claude Code のすすめ
schroneko
67
230k
Transcript
Catching Low Hanging Fruits How attack proxies and automation can
help you catch those before the pentester (or attacker!) does Johanna Curiel
Confidential Customized for Lorem Ipsum LLC Version 1.0 TOC What
are easy to catch vulnerabilities? Quick and Dirty proxies Automation is your friend Putting all together About me : just a little Why you should care!
About me A Developer turned Security Engineer. Passionate about Security
OWASP contributor Working as Security Engineer @Mobiquity
Low hanging fruits: Easy to catch vulnerabilities You do unit
tests ...right? You test your code...right? Why not quick and dirty security tests?
Catching Low hanging vulnerabilities: Pentester doing Script Kiddie work CVE’S
XSS SQL INJECTIONS RFI… PATH TRAVERSAL.. YOU NAME IT!
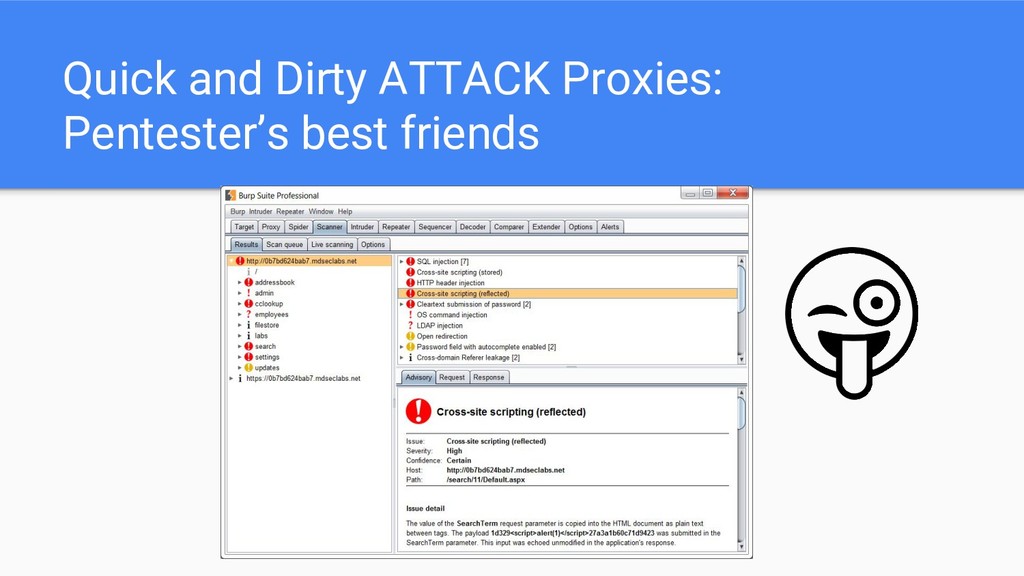
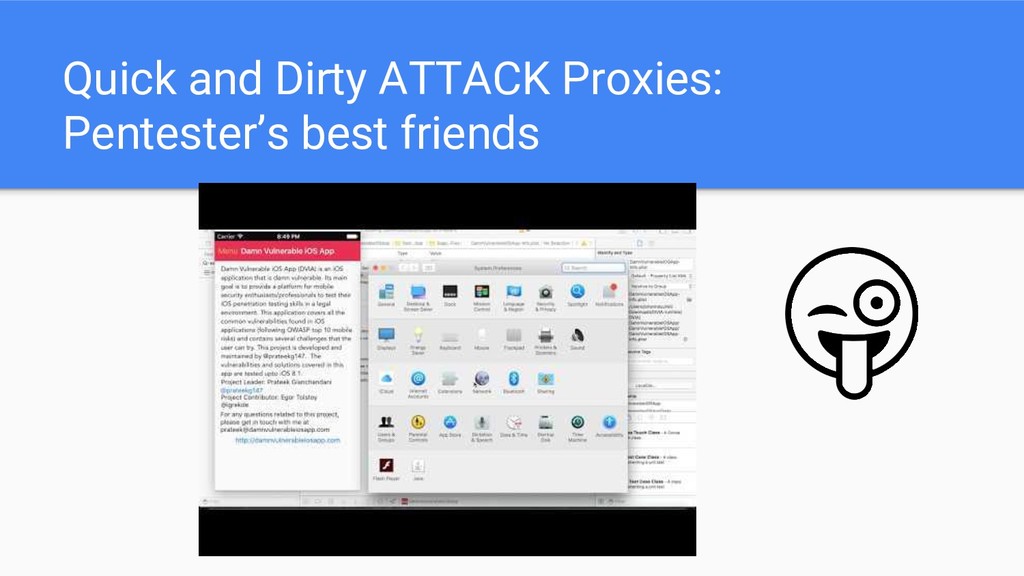
Quick and Dirty ATTACK Proxies: Pentester’s best friends
Quick and Dirty ATTACK Proxies: Pentester’s best friends
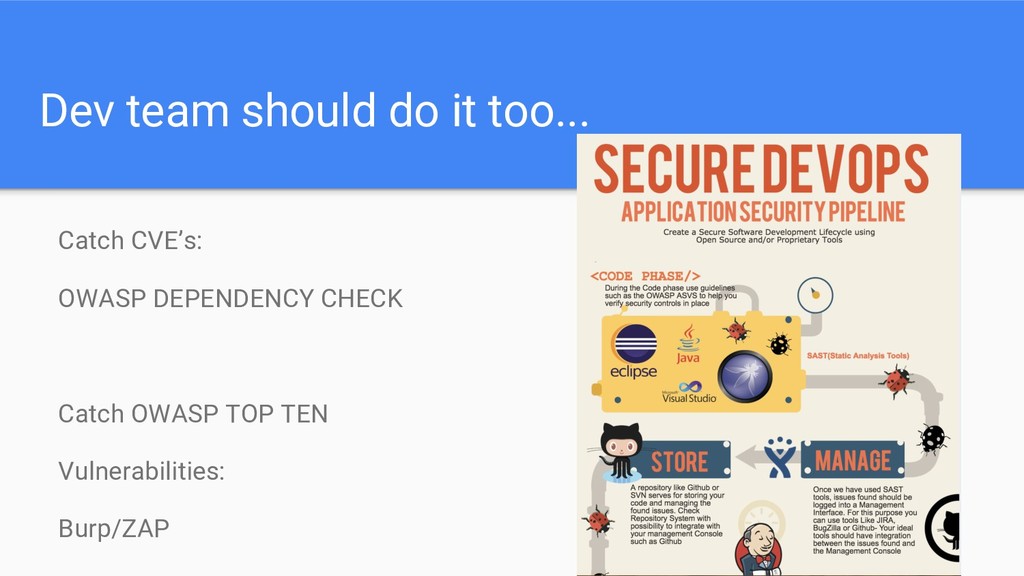
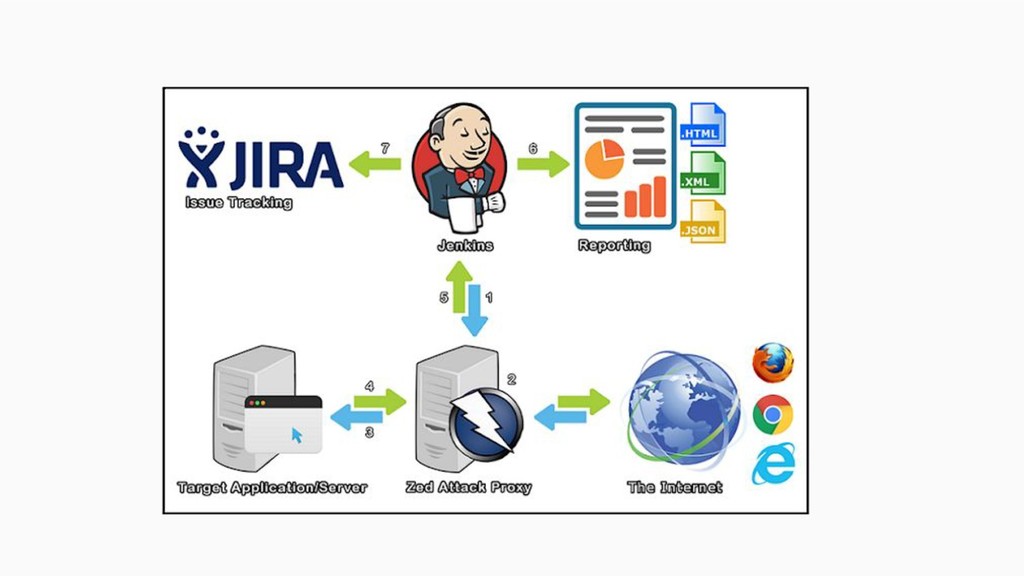
Dev team should do it too... Catch CVE’s: OWASP DEPENDENCY
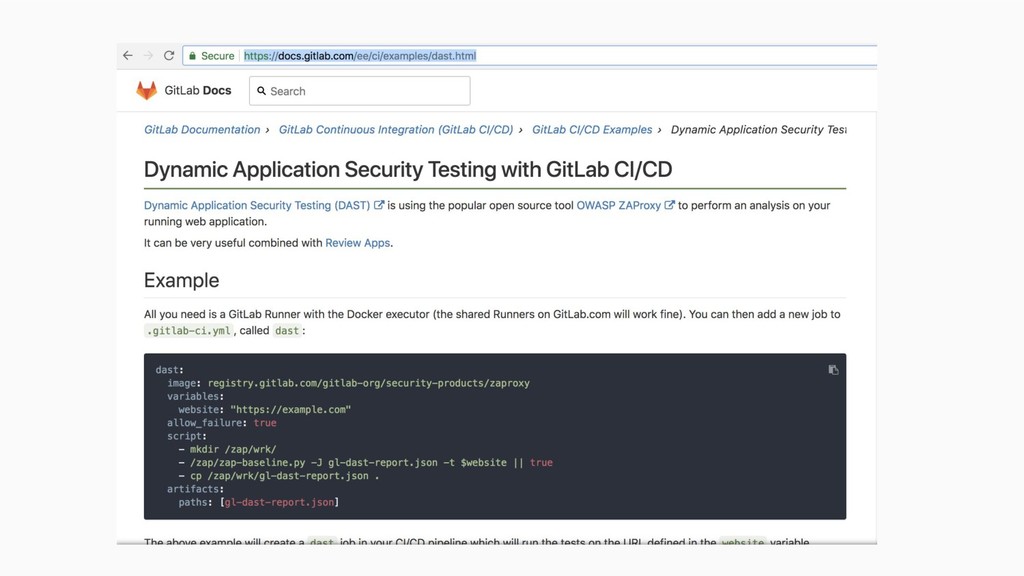
CHECK Catch OWASP TOP TEN Vulnerabilities: Burp/ZAP
None
None
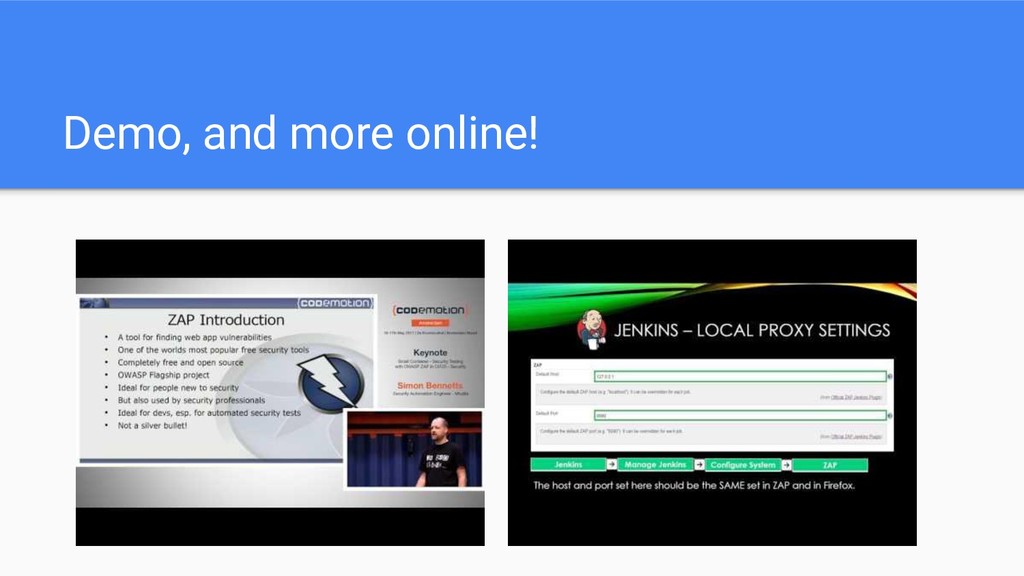
Demo, and more online!
THANK YOU
[email protected]
https://www.owasp.org/index.php/Main_Page https://www.owasp.org/index.php/OWASP_Dependency_Check https://zaproxy.blogspot.com/2016/02/#Contributor


 afoltin
 charlesmeaden
 ipullrank
 palkan
 techseoconnect
 yeseniaperezcruz
 madoxten
 irinanazarova
 inesmontani
 reverentgeek
 marktimemedia
 marcduiker
 schroneko